

#defi
defi
57.6M views
305,123 Discussing
Hot
Latest
·
--
💰 DEFI WATCHLIST: THREE DIFFERENT ROLES
🦄 $UNI — A major decentralized exchange protocol.
🏦 $AAVE — A decentralized lending and borrowing protocol.
🔧 $MKR — Historically associated with Maker's decentralized stablecoin ecosystem; check current token and governance arrangements.
Before considering any DeFi token, investigate protocol revenue, token utility, governance, and smart-contract risk.
Which DeFi model interests you most?
#DeFi #Uniswap #Aave
1
2
·
--
$HYPE
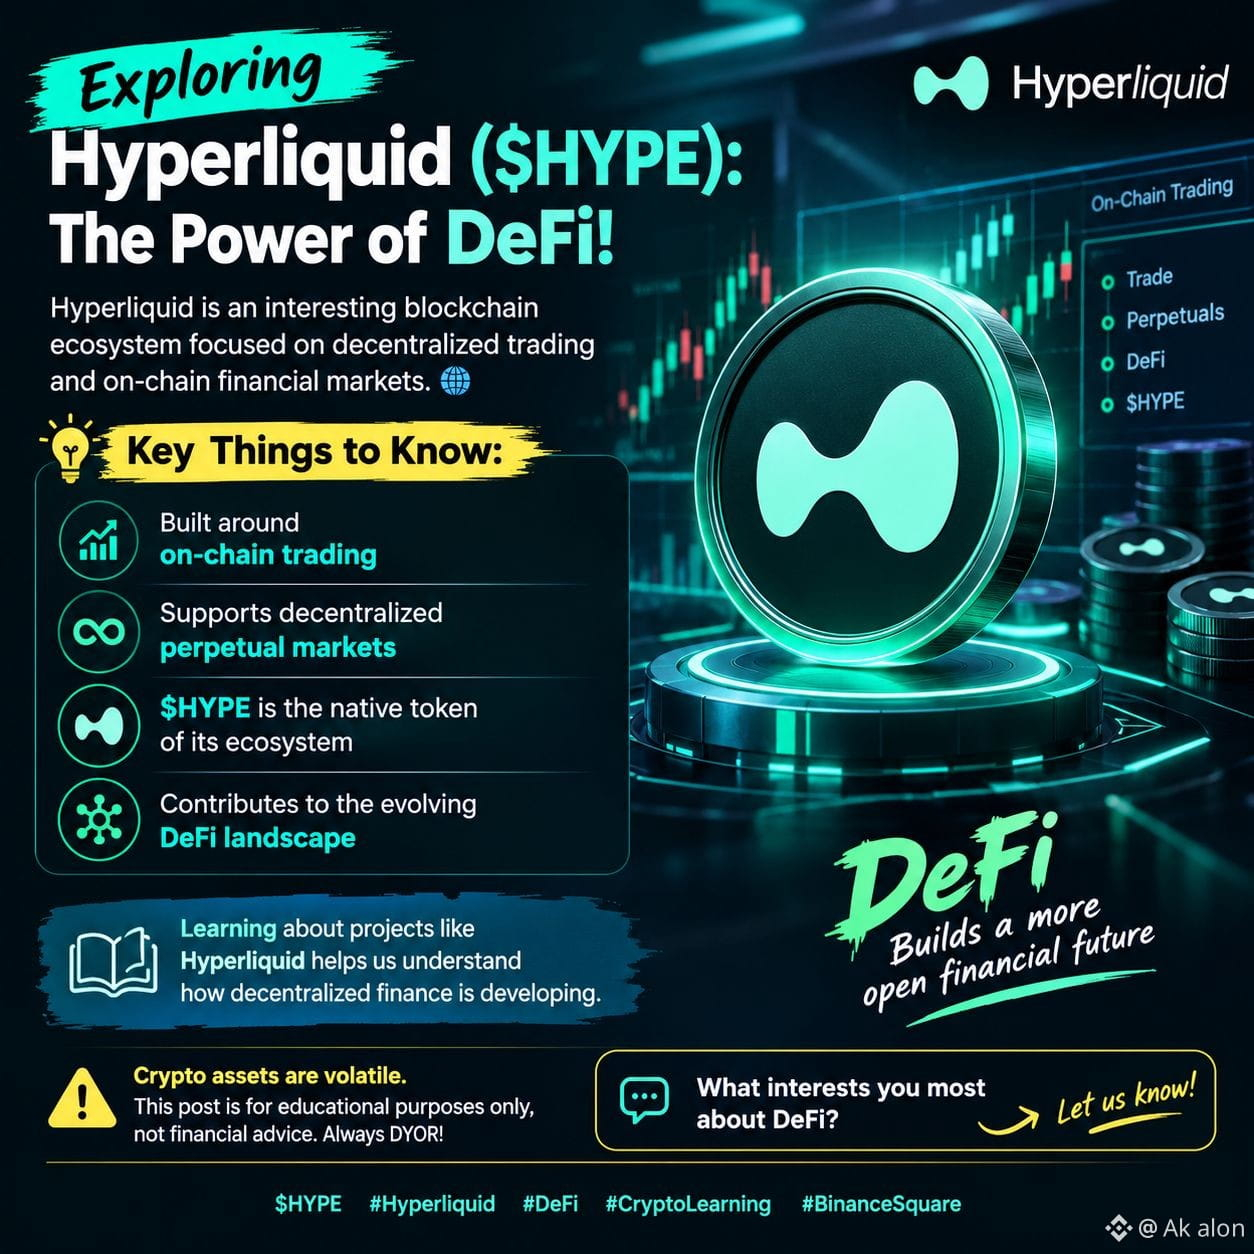
🚀 Exploring Hyperliquid (HYPE): The Power of DeFi!
Hyperliquid is an interesting blockchain ecosystem focused on decentralized trading and on-chain financial markets. 🌐
💡 Key Things to Know:
🔹 Built around on-chain trading
🔹 Supports decentralized perpetual markets
🔹 $HYPE is the native token of its ecosystem
🔹 Contributes to the evolving DeFi landscape
📚 Learning about projects like Hyperliquid helps us understand how decentralized finance is developing.
⚠️ Crypto assets are volatile. This post is for educational purposes only, not financial advice. Always DYOR!
What interests you most about DeFi? 👇
$HYPE #DeFi #CryptoLearning #BinanceSquare
94
·
--
Article
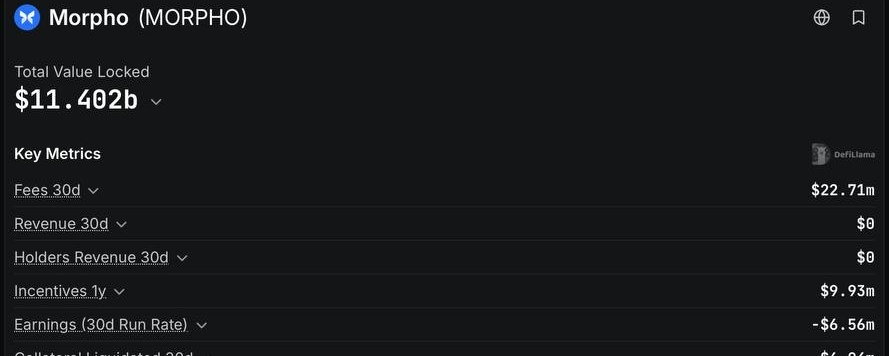
Morpho Generated $22.71M in Fees. So Why Is Its Revenue $0?Morpho has billions in locked assets, millions in fees, and one number that deserves investors’ attention: $0 in recorded protocol revenue.
According to the DeFiLlama
• TVL: $11.402B
• Active loans: $5.819B
• 30-day fees: $22.71M
• 30-day protocol revenue: $0
• MORPHO price: $2.01
• Market cap: $1.416B
• FDV: $2.014B
So, what’s happening?
Fees and revenue are not the same thing. Morpho Blue’s fee configuration allows the protocol to facilitate lending activity without currently recording protocol revenue under the displayed metric.
That doesn’t mean Morpho generates no fees. It means investors must understand who captures the economic value.
Is MORPHO undervalued?
Its market cap is approximately 12.4% of TVL, but that ratio alone proves nothing. TVL is not profit, and gross fees do not automatically belong to token holders.
MORPHO is a governance token. Any potential benefit from protocol fees depends on actual governance decisions and implemented mechanisms, not assumptions.
My take: Morpho’s adoption is impressive, but its token valuation needs more than a TVL comparison. Watch fee-switch decisions, sustainable lending demand, and token unlocks before drawing conclusions.
Because a successful protocol and a valuable token are two different investment theses.
$MORPHO #Morpho #DeFi
Morpho Generated $22.71M in Fees. So Why Is Its Revenue $0?
Morpho has billions in locked assets, millions in fees, and one number that deserves investors’ attention: $0 in recorded protocol revenue.
According to the DeFiLlama
• TVL: $11.402B
• Active loans: $5.819B
• 30-day fees: $22.71M
• 30-day protocol revenue: $0
• MORPHO price: $2.01
• Market cap: $1.416B
• FDV: $2.014B
So, what’s happening?
Fees and revenue are not the same thing. Morpho Blue’s fee configuration allows the protocol to facilitate lending activity without currently recording protocol revenue under the displayed metric.
That doesn’t mean Morpho generates no fees. It means investors must understand who captures the economic value.
Is MORPHO undervalued?
Its market cap is approximately 12.4% of TVL, but that ratio alone proves nothing. TVL is not profit, and gross fees do not automatically belong to token holders.
MORPHO is a governance token. Any potential benefit from protocol fees depends on actual governance decisions and implemented mechanisms, not assumptions.
My take: Morpho’s adoption is impressive, but its token valuation needs more than a TVL comparison. Watch fee-switch decisions, sustainable lending demand, and token unlocks before drawing conclusions.
Because a successful protocol and a valuable token are two different investment theses.
$MORPHO #Morpho #DeFi
1
159
·
--
🚀 JUPITER (JUP): THE SOLANA TOKEN I WOULDN’T IGNORE
Why did we put JUP on our radar before — and why could it still be worth watching?
Most traders chase coins after they pump. I prefer looking at projects that are building something people actually use.
1. What is Jupiter?
Jupiter is one of the major DeFi platforms in the Solana ecosystem.
It started as a DEX aggregator — a technology that searches across different exchanges to find efficient swap routes and competitive prices.
Instead of manually checking multiple platforms, users can swap tokens through one interface.
But Jupiter has expanded beyond simple swaps into a broader on-chain finance ecosystem, including perpetual trading, lending and other products.
2. What makes the technology interesting?
⚙️ Smart trade routing: Jupiter can compare liquidity across multiple venues and route trades to improve execution.
🌐 Solana infrastructure: Fast transactions and relatively low network fees make Solana attractive for active on-chain trading.
📈 A growing product ecosystem: More products can mean more opportunities to attract users, trading activity and liquidity.
The key is adoption. Technology alone doesn’t make a token valuable — real usage matters.
3. Why look at JUP as a potential investment?
The investment thesis has three parts:
• Ecosystem growth: If Solana DeFi expands, Jupiter could benefit from increased activity.
• Governance and staking: JUP gives holders a role in protocol governance, while active staking participants may qualify for rewards under the applicable program rules.
• Market sentiment: If capital rotates back into Solana ecosystem tokens, JUP could attract renewed attention.
That creates a potential opportunity — not a guarantee.
A strong project does not automatically mean a good entry price.
My takeaway:
JUP is worth researching because it sits at the intersection of Solana, DeFi trading and on-chain financial products.
The opportunity is in the thesis — but the entry price and risk management still matter.
#JUP #DeFi
107
Article
Can a DAO Be Hijacked in Minutes? What the X100 Exploit Teaches Every DeFi UserA flash loan bought enough votes to drain $4.85M with no governance delay. Here's the attack step by step, and three red flags to look for before you deposit.
🏛️ On Saturday, an attacker borrowed money, bought a controlling vote in a DeFi project, and drained its treasury, all inside one transaction.
X100, a project on Ethereum, lost about $4.75M to $4.85M on October 24. Its token fell more than 96% as liquidity disappeared. The scary part isn't a coding bug. The contracts did exactly what they were built to do.
🔍 How the attack worked, step by step.
The attacker borrowed about 1.94M USDT through an Aave flash loan, a loan that must be repaid within the same transaction.They bought X tokens and split them across two contracts they controlled.Each contract staked slightly more than 19,000 X into X100's Freezer, which gave them two of the project's three "Senate" seats.With a majority, they passed a proposal forcing the treasury to sell 400,000 X into a pool they had created, accepting a payout of about 36 USDT.They pulled the liquidity back out, sold the tokens, repaid the loan and kept roughly $4.75M. A second attacker repeated the trick about 24 minutes later.
🧠 Why it worked.
New Senate members could approve and execute proposals immediately, with no waiting period. A delay of even a few hours would have broken the attack, because a flash loan has to be repaid in the same transaction. Voting power was also something anyone could rent for a few cents of fees.
🚩 Three red flags to check before you deposit.
No delay. Can governance changes execute instantly, or is there a timelock?Votes you can borrow. If voting power comes from tokens that can be bought or borrowed in seconds, it can be attacked.A tiny council. When two or three seats control a treasury, taking the majority is cheap.
✅ What this means for you
If you use DeFi, read the governance section of a project's docs before you deposit, and look for timelocks, audits and the number of signers.
If you're on the sidelines, this is a reminder that "audited" doesn't always cover how governance is designed.
If you hold X100 tokens, the project hadn't published an incident report or recovery plan in the first hours, so watch its official channels and be careful with anyone offering "recovery" links.
🟢 Bullish scenario
The team publishes a clear report, adds a timelock and redesigns governance, and the incident becomes a case study that other projects learn from.
🔴 Risk scenario
Copycats target similar designs, stolen funds are mixed and moved out, and holders get no recovery.
👀 Three things to watch
1️⃣ An official incident report from X100
2️⃣ Where the stolen funds, reportedly converted to about 2,022 ETH, move next
3️⃣ Similar governance designs getting audited or patched
💡 The key takeaway
X100 wasn't hacked through a typo in the code. It was hacked through its own rules, which let anyone buy a majority and act on it instantly.
The real question isn't whether the code is audited. It's whether governance can be rented for a minute.
That is the part worth watching.
This post is for informational and educational purposes only and is not financial advice. Crypto markets are volatile. Always conduct your own research before making financial decisions.
#BinanceSquare #DeFi #Ethereum #CryptoSecurity #FlashLoan
{spot}(AAVEUSDT)
{spot}(ETHUSDT)
Can a DAO Be Hijacked in Minutes? What the X100 Exploit Teaches Every DeFi User
A flash loan bought enough votes to drain $4.85M with no governance delay. Here's the attack step by step, and three red flags to look for before you deposit.
🏛️ On Saturday, an attacker borrowed money, bought a controlling vote in a DeFi project, and drained its treasury, all inside one transaction.
X100, a project on Ethereum, lost about $4.75M to $4.85M on October 24. Its token fell more than 96% as liquidity disappeared. The scary part isn't a coding bug. The contracts did exactly what they were built to do.
🔍 How the attack worked, step by step.
The attacker borrowed about 1.94M USDT through an Aave flash loan, a loan that must be repaid within the same transaction.They bought X tokens and split them across two contracts they controlled.Each contract staked slightly more than 19,000 X into X100's Freezer, which gave them two of the project's three "Senate" seats.With a majority, they passed a proposal forcing the treasury to sell 400,000 X into a pool they had created, accepting a payout of about 36 USDT.They pulled the liquidity back out, sold the tokens, repaid the loan and kept roughly $4.75M. A second attacker repeated the trick about 24 minutes later.
🧠 Why it worked.
New Senate members could approve and execute proposals immediately, with no waiting period. A delay of even a few hours would have broken the attack, because a flash loan has to be repaid in the same transaction. Voting power was also something anyone could rent for a few cents of fees.
🚩 Three red flags to check before you deposit.
No delay. Can governance changes execute instantly, or is there a timelock?Votes you can borrow. If voting power comes from tokens that can be bought or borrowed in seconds, it can be attacked.A tiny council. When two or three seats control a treasury, taking the majority is cheap.
✅ What this means for you
If you use DeFi, read the governance section of a project's docs before you deposit, and look for timelocks, audits and the number of signers.
If you're on the sidelines, this is a reminder that "audited" doesn't always cover how governance is designed.
If you hold X100 tokens, the project hadn't published an incident report or recovery plan in the first hours, so watch its official channels and be careful with anyone offering "recovery" links.
🟢 Bullish scenario
The team publishes a clear report, adds a timelock and redesigns governance, and the incident becomes a case study that other projects learn from.
🔴 Risk scenario
Copycats target similar designs, stolen funds are mixed and moved out, and holders get no recovery.
👀 Three things to watch
1️⃣ An official incident report from X100
2️⃣ Where the stolen funds, reportedly converted to about 2,022 ETH, move next
3️⃣ Similar governance designs getting audited or patched
💡 The key takeaway
X100 wasn't hacked through a typo in the code. It was hacked through its own rules, which let anyone buy a majority and act on it instantly.
The real question isn't whether the code is audited. It's whether governance can be rented for a minute.
That is the part worth watching.
This post is for informational and educational purposes only and is not financial advice. Crypto markets are volatile. Always conduct your own research before making financial decisions.
#BinanceSquare #DeFi #Ethereum #CryptoSecurity #FlashLoan
1
1
133
·
--
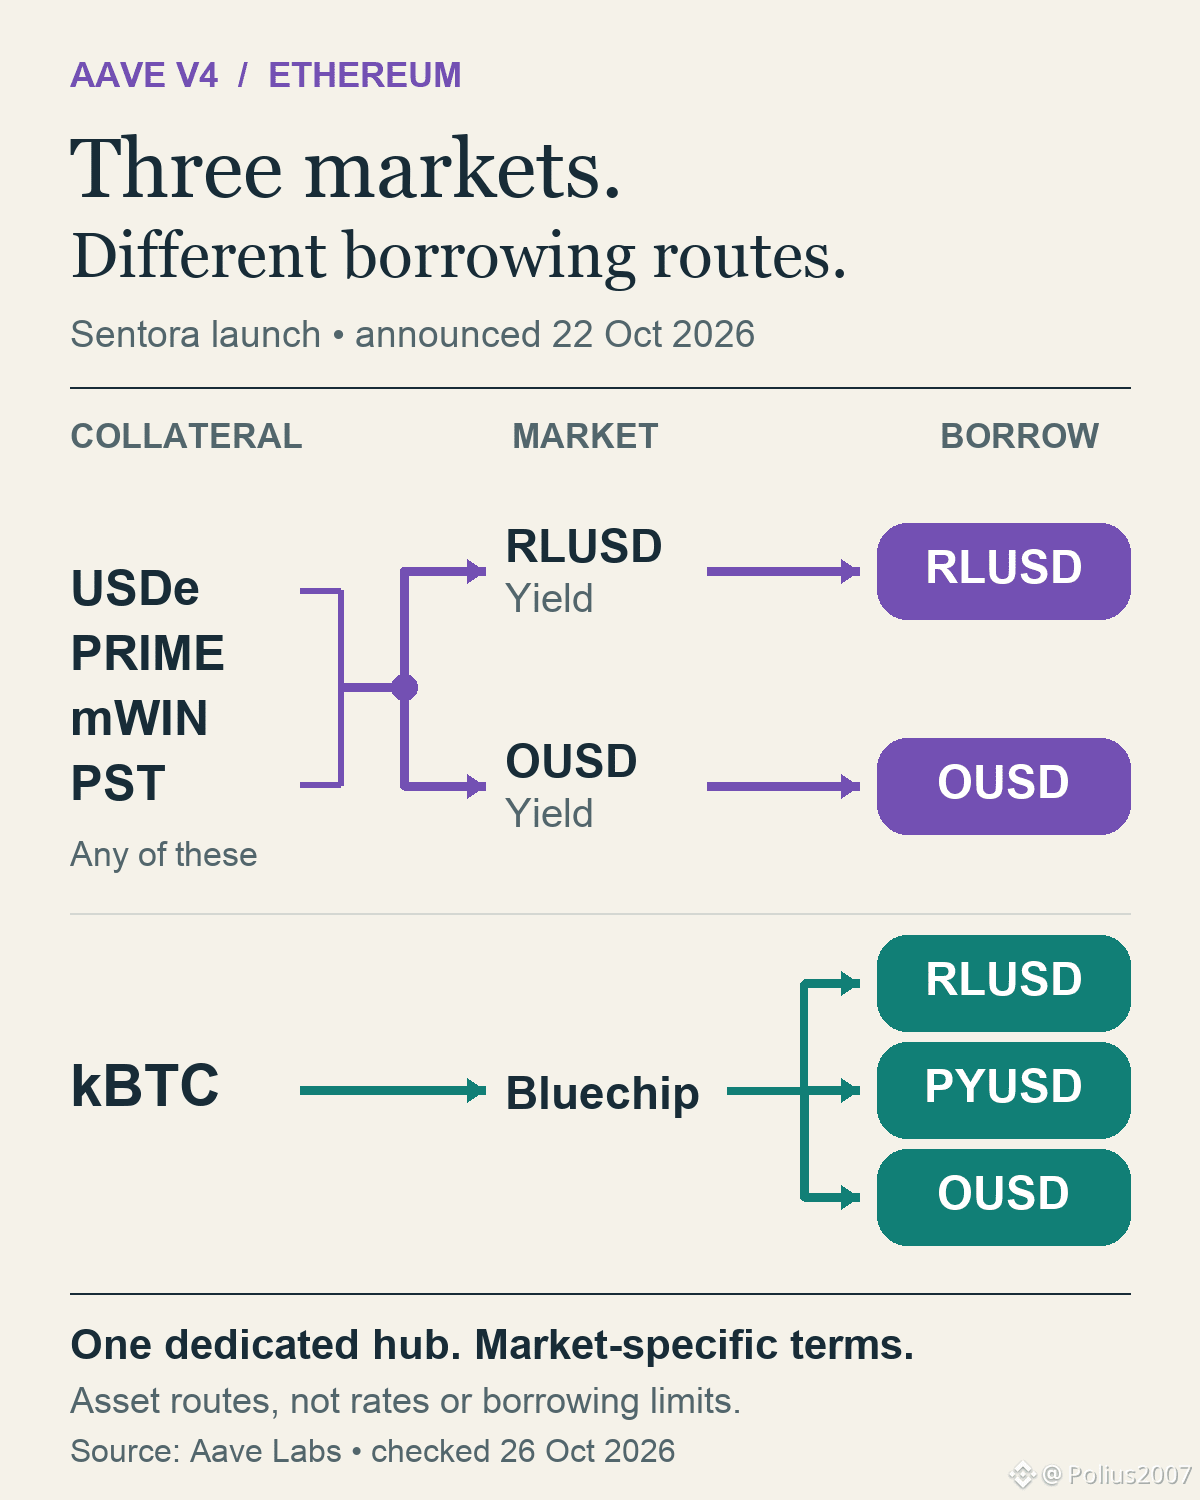
Aave's new Sentora markets give the same collateral two different borrowing routes: USDe, PRIME, mWIN or PST can back an RLUSD loan or an OUSD loan, depending on the market chosen.
Aave Labs' October 22 announcement describes three externally curated markets on Ethereum. The two Yield markets accept those four assets. The third, Bluechip, accepts kBTC as collateral and lets users borrow RLUSD, PYUSD or OUSD.
The distinction matters before depositing: the list of assets supported by the launch is not a menu of interchangeable collateral and loan combinations. The illustration maps which collateral opens which route.
Sentora runs a dedicated liquidity hub and chooses collateral and risk parameters for its markets. Aave supplies the V4 infrastructure and retains governance safeguards. According to the announcement, the Aave DAO owns the contracts, risk-increasing changes face a 48-hour timelock, and new assets need Aave governance review.
For borrowers, the useful change is more ways to borrow against these holdings without selling them. The next comparison is market-specific: the borrowing rate, how much the collateral lets you borrow, and when liquidation can begin. A shared codebase doesn't make those terms identical.
Source: Aave Labs, October 22, 2026; checked October 26. Availability is as announced, not a live transaction test.
https://aave.com/blog/sentora-aave-launch
#Aave #DeFi
103

·
--
Have you noticed how most traders ignore DeFi setups until it's too late to get in?
The pain of missing a clean surge like this one on $CAP is real. You sit on the sidelines waiting for confirmation, then FOMO at the highs and have no idea when to exit before the token event dumps it.
$CAP just surged 39.33% on strong DeFi momentum heading into a key token event. The crowd still thinks DeFi is dead, but price action like this tells a different story. Utility tokens with upcoming catalysts don't wait for your permission to move.
Look at how $UNI and $AAVE reacted around similar events. The approach that works is to map the date, enter with a defined size, and set your take profit before the news cycle peaks. Waiting for the tweet is how accounts get rekt.
Where do you think this $CAP momentum heads after the token event?
#DeFi #Altcoins #CryptoTrading
6

·
--
One Price For Everyone Who Bid 💰
A sealed auction clears at one price for every winning bidder, which is the mechanism that stops the people who bid earliest from paying the most.
$JUP made buying into a new token on $SOL a matter of one swap, and that convenience is also the problem, because a queue of visible buys means the price moves as the queue grows and the last buyer pays for the enthusiasm of the first.
Sealed bidding works the other way. Everyone submits what they think it is worth, nobody reacts to anyone else, and the clearing price is what the market actually believed rather than what the queue produced.
Crafts runs that on Arcium as a sealed-bid launchpad. No bid is readable anywhere until the auction closes, not by the other bidders and not by whoever is running the sale, and the clearing price still comes out correct.
That price posts to Solana like any other transaction, so anyone can check what cleared and at what level once it is done.
Token launches have rewarded speed over judgement, and Arcium is what lets a Solana sale reward the judgement instead.
#altcoins #defi
1
173

⚡ $GMGN SWELLS PAST PUMP.FUN AND a decentralized exchange WITH $2.46M REVENUE IN 24 HOURS! 💥
Smart money order flow is shifting rapidly. GMGN just posted a monster $2.46 million in 24-hour protocol revenue, effortlessly flipping heavyweight earners like a decentralized exchange at $1.76M and Pump.fun at $1.12M. 📊
When an emerging protocol out-earns the market's favorite liquidity hubs, it signals massive user retention and underlying volume velocity. 🔍 Smart capital follows real cash flow, not empty speculation. ⚡
This revenue flip could mark a pivotal rotation in decentralized trading infrastructure. 💡 Is $GMGN poised to permanently unseat the incumbents, or will Pump.fun strike back with a liquidity counter-offensive? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #GMGN #ProtocolRevenue #DeFi #Crypto
🔥 💎
12
FIL, ZRO and REZ: Infrastructure and DeFi Momentum Take Center Stage
FIL is trading near $0.9262, down about 0.9% over the latest 24 hours after moving between $0.9057 and $0.9446. Filecoin is holding above its session low, but stronger volume would be needed to rebuild momentum toward the upper end of the range.
ZRO is trading near $1.765, up about 1.6% over the latest 24 hours and close to its session high of $1.800. LayerZero is showing constructive short term strength as cross chain infrastructure remains a closely watched theme across the market.
REZ is trading near $0.004717, up about 12.2% over the latest 24 hours after reaching $0.004894. Renzo is leading this group on price momentum, with elevated activity reflecting renewed interest in liquid restaking and DeFi related narratives. The sharp move also means volatility remains high.
The current setup highlights three different market stories: FIL represents decentralized storage infrastructure, ZRO reflects cross chain connectivity, and REZ is attracting higher beta DeFi participation. Strong narratives can capture attention quickly, but sustained momentum still depends on liquidity, volume and disciplined risk management.
#Filecoin #LayerZero #Renzo #CryptoMarket #DeFi
$FIL
{spot}(FILUSDT)
$ZRO
{spot}(ZROUSDT)
$REZ
{spot}(REZUSDT)
FIL, ZRO and REZ: Infrastructure and DeFi Momentum Take Center Stage
FIL is trading near $0.9262, down about 0.9% over the latest 24 hours after moving between $0.9057 and $0.9446. Filecoin is holding above its session low, but stronger volume would be needed to rebuild momentum toward the upper end of the range.
ZRO is trading near $1.765, up about 1.6% over the latest 24 hours and close to its session high of $1.800. LayerZero is showing constructive short term strength as cross chain infrastructure remains a closely watched theme across the market.
REZ is trading near $0.004717, up about 12.2% over the latest 24 hours after reaching $0.004894. Renzo is leading this group on price momentum, with elevated activity reflecting renewed interest in liquid restaking and DeFi related narratives. The sharp move also means volatility remains high.
The current setup highlights three different market stories: FIL represents decentralized storage infrastructure, ZRO reflects cross chain connectivity, and REZ is attracting higher beta DeFi participation. Strong narratives can capture attention quickly, but sustained momentum still depends on liquidity, volume and disciplined risk management.
#Filecoin #LayerZero #Renzo #CryptoMarket #DeFi
$FIL
$ZRO
$REZ
28
SUI, LINK and AAVE: Strength Is Shifting Toward Quality Narratives
SUI is trading near $0.9202, down about 1.3% over the latest 24 hours after moving between $0.9040 and $0.9427. The price remains close to the lower half of its daily range, showing that buyers need stronger participation to reclaim short term momentum.
LINK is trading near $11.466, down roughly 0.8% in the latest 24 hours. After reaching $11.650, Chainlink has seen a controlled pullback while maintaining an active market structure. Its position across oracle infrastructure, DeFi and RWA continues to keep it on the radar during broader market rotations.
AAVE is trading near $136.64, down about 0.4% over the latest 24 hours after ranging from $134.92 to $139.02. The narrower decline compared with SUI and LINK suggests relatively balanced demand, with DeFi liquidity and protocol activity remaining important drivers for sentiment.
The current setup highlights three different narratives: SUI represents Layer 1 growth potential, LINK reflects infrastructure demand, and AAVE remains closely tied to DeFi liquidity conditions. Short term volatility is still present, so volume confirmation and disciplined risk management matter more than hype.
#SUI #Chainlink #Aave #CryptoMarket #DeFi
$SUI
{spot}(SUIUSDT)
$LINK
{spot}(LINKUSDT)
$AAVE
{spot}(AAVEUSDT)
SUI, LINK and AAVE: Strength Is Shifting Toward Quality Narratives
SUI is trading near $0.9202, down about 1.3% over the latest 24 hours after moving between $0.9040 and $0.9427. The price remains close to the lower half of its daily range, showing that buyers need stronger participation to reclaim short term momentum.
LINK is trading near $11.466, down roughly 0.8% in the latest 24 hours. After reaching $11.650, Chainlink has seen a controlled pullback while maintaining an active market structure. Its position across oracle infrastructure, DeFi and RWA continues to keep it on the radar during broader market rotations.
AAVE is trading near $136.64, down about 0.4% over the latest 24 hours after ranging from $134.92 to $139.02. The narrower decline compared with SUI and LINK suggests relatively balanced demand, with DeFi liquidity and protocol activity remaining important drivers for sentiment.
The current setup highlights three different narratives: SUI represents Layer 1 growth potential, LINK reflects infrastructure demand, and AAVE remains closely tied to DeFi liquidity conditions. Short term volatility is still present, so volume confirmation and disciplined risk management matter more than hype.
#SUI #Chainlink #Aave #CryptoMarket #DeFi
$SUI
$LINK
$AAVE
8

·
--
Bullish
The decentralized finance (DeFi) landscape is witnessing a massive structural shift, and Hyperliquid is leading the charge. 🚀
While major layer-1 networks experience typical market consolidation, $HYPE has emerged as a top performer this year, solidifying its place in the global market cap rankings.
Why is it gaining so much momentum?
1️⃣ Institutional Perpetual Volume: Hyperliquid has captured a massive share of the on-chain perpetual futures volume, rivaling many centralized alternatives.
2️⃣ Scarcity Mechanics: Unlike platforms with unchecked emissions, a vast majority of protocol trading fees are designated for token buybacks, creating aggressive deflationary pressure as trading volume grows.
Traders are migrating toward deep liquidity and execution speed. Are you holding any bags, or waiting for a deeper pullback? Let's discuss in the comments! 👇
#DeFi #trading #Hyperliquid #WriteToEarn
147
·
--
🏦 WHAT IF FINANCIAL SERVICES RAN 24/7? 🌍
Decentralized finance is changing how people interact with digital assets.
With DeFi, users can potentially:
💰 Lend digital assets through protocols
🔄 Exchange tokens on decentralized platforms
🌊 Provide liquidity to trading pools
🔐 Interact directly with programmable smart contracts
📊 Monitor transactions through public blockchain explorers
But decentralization doesn't eliminate risk.
⚠️ Smart contract exploits, liquidation, oracle failures, and unstable yields can cause serious losses.
💡 DeFi's greatest strength is programmable financial access. Its greatest challenge is making that access safer and easier to use.
👇 Do you think DeFi and traditional finance will eventually work together?
#defi #BinanceSquare #Web3 #SmartContracts #crypto
·
--
Bullish
Verified
Aptos DeFi is gaining momentum! 🚀
Decibel has crossed $8.5B+ in trading volume and 31M+ trades since mainnet launch.
With 80+ markets, including NVIDIA, Tesla, Apple, and Microsoft stock perpetuals, it’s expanding on-chain trading.
🔥 Every trade burns APT, adding a deflationary mechanism to the ecosystem.
More activity. More utility. More eyes on Aptos. 👀
#defi
162
·
--
DeFi should make moving between tokens feel simple, not complicated. 🌐That’s one reason I find @ston_fi interesting.
Built on TON, STON.fi makes token swaps accessible through a decentralized exchange integrated with the TON ecosystem. Users can exchange assets while keeping control of their own wallets.
What matters to me is how infrastructure like this helps make onchain activity easier for everyday users. As more people explore TON apps, simple and reliable swap experiences become increasingly important.
The next stage of DeFi isn’t just about adding more tokens. It’s about making decentralized finance easier to understand and use.
I’m watching how @ston_fi continues to contribute to the TON ecosystem.
#STONfi #tonecoin #DeFi
DeFi should make moving between tokens feel simple, not complicated. 🌐
That’s one reason I find @ston_fi interesting.
Built on TON, STON.fi makes token swaps accessible through a decentralized exchange integrated with the TON ecosystem. Users can exchange assets while keeping control of their own wallets.
What matters to me is how infrastructure like this helps make onchain activity easier for everyday users. As more people explore TON apps, simple and reliable swap experiences become increasingly important.
The next stage of DeFi isn’t just about adding more tokens. It’s about making decentralized finance easier to understand and use.
I’m watching how @ston_fi continues to contribute to the TON ecosystem.
#STONfi #tonecoin #DeFi
94

·
--
🚨 $AAVE REJECTS KEY 134.90 RESISTANCE WITH HEAVY SELLING PRESSURE MOUNTING! 📉
Entry: 134.60 - 134.90 ⚡
Target: 130.44 🎯
Stop Loss: 136.57 ⚠️
📌 The rejection off the 134.90 ceiling was swift and decisive, leaving late buyers trapped right at resistance. 📊 Momentum is shifting sharply as supply overwhelms bid depth, clearing the runway for a rapid flush down toward key demand.
💡 Risk parameters are clean and defined, offering a sharp setup as bear pressure accelerates toward the target zone at 130.44. 💬 Are you riding this downward momentum to support, or looking for a reversal? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AAVE #ShortSetup #DeFi #CryptoTrading
🐻 ⚡
11
·
--
Bullish
🚨 $AERO : FROM 2% TO 55% MARKET SHARE. THAT'S REAL MOMENTUM! 📈🔥
Aerodrome is making serious moves in the tokenized stock market.
According to Dromos Labs CEO Alex Cutler, Aerodrome now captures 55% of tokenized stock trading volume across Ethereum and its Layer 2 networks, up from roughly 2% in early September.
That's a massive 53-percentage-point increase. 👀
Here's what makes this interesting:
📈 Tokenized stock activity has roughly quadrupled this year.
🌐 Aerodrome is expanding across seven networks following the Aerodrome–Velodrome merger.
⚡ Growing market share could strengthen its position as tokenized equities gain traction across DeFi.
The bigger story isn't just the numbers. It's the potential convergence of traditional financial markets and decentralized infrastructure.
If tokenized stocks continue gaining adoption, platforms capturing liquidity early could be positioned for significant growth.
The real question is: how much bigger can this market become? 🚀
$AERO deserves attention. Keep watching the fundamentals, liquidity, and actual revenue as the ecosystem evolves.
#AERO #DeFi #RWA #Crypto
{future}(AEROUSDT)
🚨 $AERO : FROM 2% TO 55% MARKET SHARE. THAT'S REAL MOMENTUM! 📈🔥
Aerodrome is making serious moves in the tokenized stock market.
According to Dromos Labs CEO Alex Cutler, Aerodrome now captures 55% of tokenized stock trading volume across Ethereum and its Layer 2 networks, up from roughly 2% in early September.
That's a massive 53-percentage-point increase. 👀
Here's what makes this interesting:
📈 Tokenized stock activity has roughly quadrupled this year.
🌐 Aerodrome is expanding across seven networks following the Aerodrome–Velodrome merger.
⚡ Growing market share could strengthen its position as tokenized equities gain traction across DeFi.
The bigger story isn't just the numbers. It's the potential convergence of traditional financial markets and decentralized infrastructure.
If tokenized stocks continue gaining adoption, platforms capturing liquidity early could be positioned for significant growth.
The real question is: how much bigger can this market become? 🚀
$AERO deserves attention. Keep watching the fundamentals, liquidity, and actual revenue as the ecosystem evolves.
#AERO #DeFi #RWA #Crypto
310
·
--
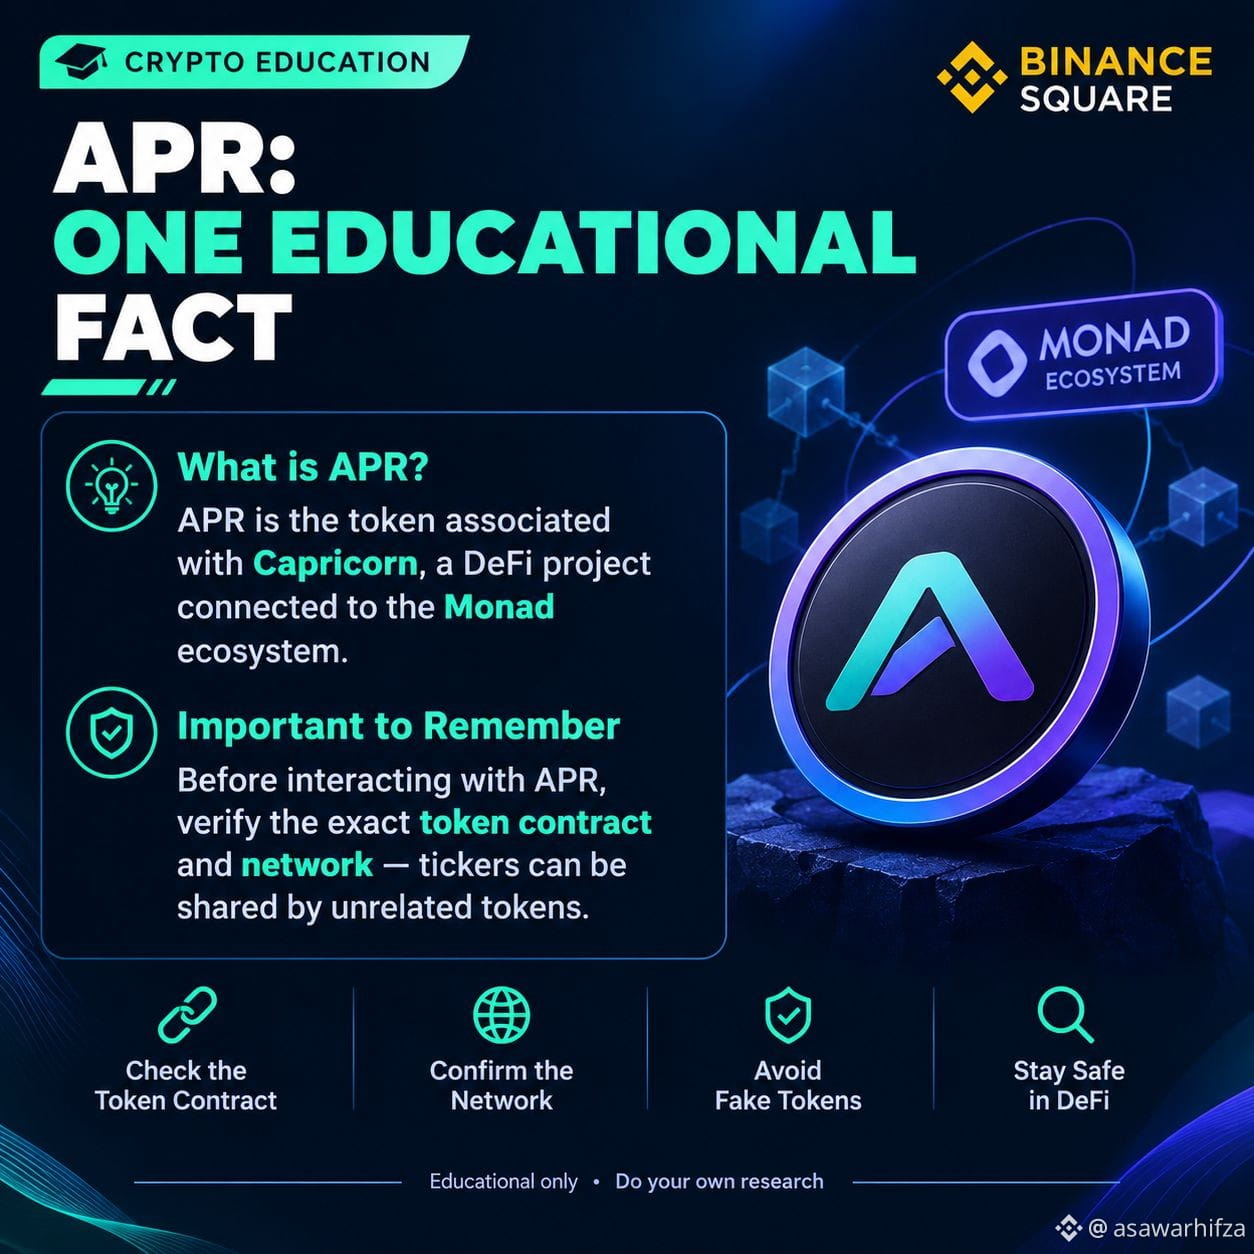
$APR APR is the token associated with Capricorn, a DeFi project connected to the Monad ecosystem. Always verify the token contract and network before interacting with any crypto asset. 🔐$APR
{future}(APRUSDT)
$APR #APR #Capricorn #Monad #CryptoEducation #defi
$APR APR is the token associated with Capricorn, a DeFi project connected to the Monad ecosystem. Always verify the token contract and network before interacting with any crypto asset. 🔐$APR
$APR #APR #Capricorn #Monad #CryptoEducation #defi
$APR #APR #Capricorn #Monad #CryptoEducation #defi
1
273
·
--
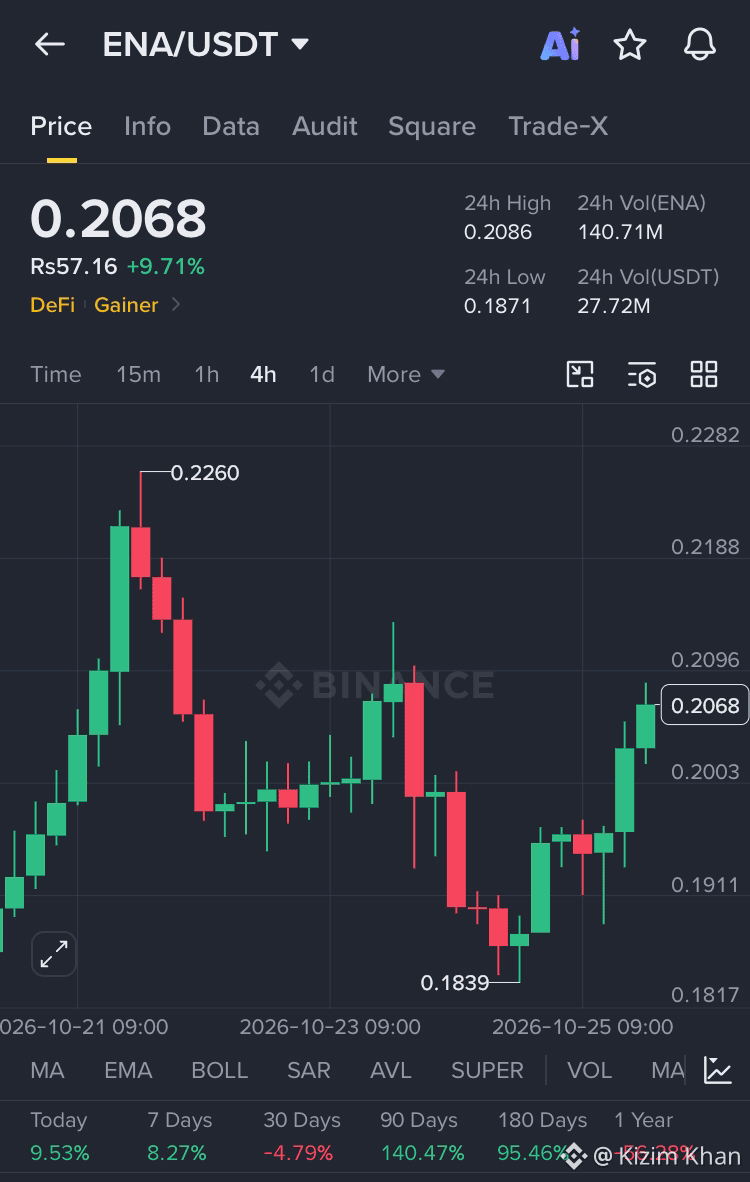
$ENA +9.71% - DeFi Comeback Started? 🚀
After dumping to $0.1839 support, ENA bounced hard +12% and broke $0.2003 resistance. Previous top was $0.2260.
Now setup:
Entry: $0.2000 - $0.2030
TP1: $0.2086 (24H High)
TP2: $0.2188
TP3: $0.2260
SL: $0.1911
DeFi narrative is back + 140% gain in 90 days. If $ENA holds above $0.2096, next target $0.2282.
#ENA #ENAUSDT #defi #CryptoGainers
1
24
🚨 APTOS IS BUILDING REAL MOMENTUM!
@Aptos is gaining traction as Decibel, an onchain exchange built on Aptos, surpasses $8.5 BILLION in trading volume across 31M+ trades since its mainnet launch. 🔥
📊 80+ markets available
📈 Stock-linked perpetuals for NVIDIA, Tesla, Apple & Microsoft
🔥 Every trade burns $APT, connecting exchange activity directly to token supply mechanics.
This is more than just trading volume. It's a growing DeFi ecosystem bringing traditional market exposure onchain.
If Decibel keeps expanding, Aptos could strengthen its position in the onchain trading economy.
Real usage. Growing markets. A deflationary mechanism tied to activity.
Keep $APT on your watchlist. 👀
#Aptos #APT #DeFi
{spot}(APTUSDT)
🚨 APTOS IS BUILDING REAL MOMENTUM!
@Aptos is gaining traction as Decibel, an onchain exchange built on Aptos, surpasses $8.5 BILLION in trading volume across 31M+ trades since its mainnet launch. 🔥
📊 80+ markets available
📈 Stock-linked perpetuals for NVIDIA, Tesla, Apple & Microsoft
🔥 Every trade burns $APT , connecting exchange activity directly to token supply mechanics.
This is more than just trading volume. It's a growing DeFi ecosystem bringing traditional market exposure onchain.
If Decibel keeps expanding, Aptos could strengthen its position in the onchain trading economy.
Real usage. Growing markets. A deflationary mechanism tied to activity.
Keep $APT on your watchlist. 👀
#Aptos #APT #DeFi
237
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
2.8M views
148,446 Discussing
2
#EarningsSeason
5.1M views
25,363 Discussing
3
#AnthropicTTMRevenueGrewAbout1200%
4,424 views
172 Discussing
4
#AnthropicS1ExpectedToday
7,630 views
172 Discussing
5
#SouthKoreaReportedlyWeighsFourthCryptoTaxDelay
16,113 views
323 Discussing
6
#FranklinTempletonFilesForTwoDividendToBitcoinETFs
23,174 views
436 Discussing
7
#StrategyMSTRSurpassesNasdaqInMarketCap
18,403 views
326 Discussing
8
#CanadaProposesStablecoinRedemptionWithin3BusinessDays
799 views
32 Discussing
9
#ElectrumWalletBugLetRogueServersStealFunds
21,499 views
414 Discussing
10
#ArgentineCourtDismissesLIBRACaseAgainstMilei
32,958 views
507 Discussing