Binance Square

cryptosecurity

8.8M views
13,080 Discussing
SanjiHunter — Crypto Market Intelligence
·
--
Bullish
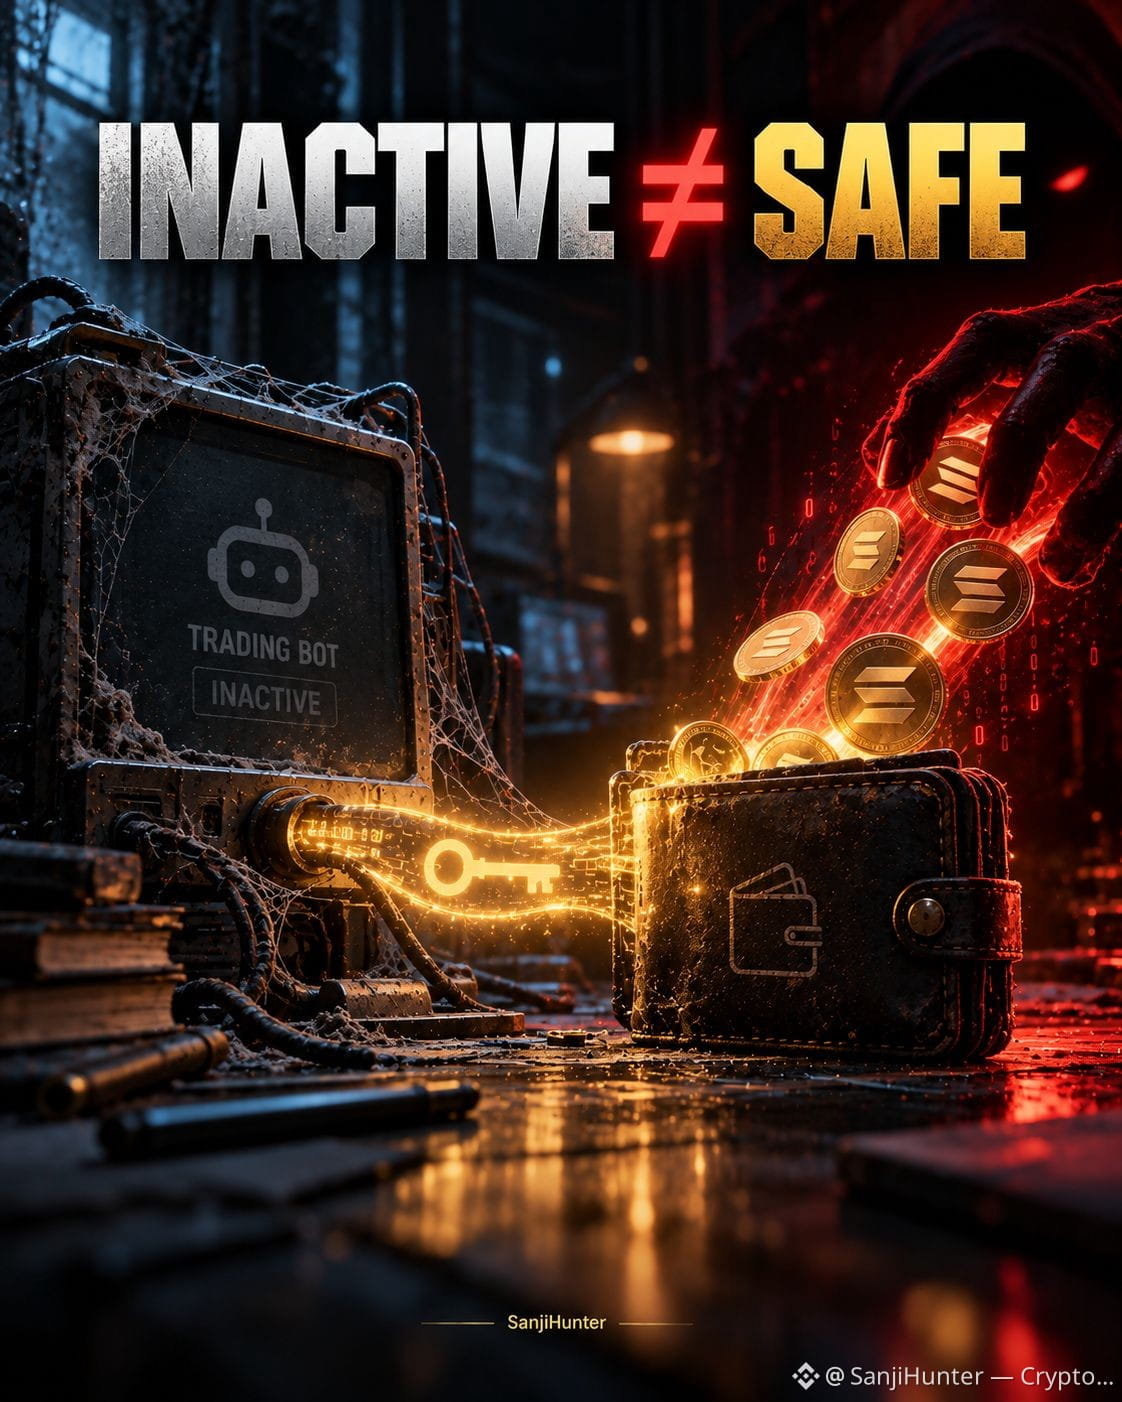
🔐 The wallet was inactive — but its private key still worked On October 26, 48 wallets linked to Bloom Trading lost 9,408 SOL in just 94 seconds, according to Bitquery's on-chain investigation Five hadn't traded on Bloom since early 2025 Here's the part that matters 👇 $SOL {future}(SOLUSDT) Every drain was signed with the affected wallet's own key — no malicious token approval or smart contract exploit required ⚠️ The source of the key exposure is still unconfirmed But the security lesson is clear Stopping a bot doesn't make a previously shared private key safe again {spot}(SOLUSDT) 📌 If a trading bot has ever held your wallet's private key, moving remaining funds to a fresh wallet with a new key is safer than simply disconnecting the bot An inactive wallet isn't necessarily a secure wallet #solana #CryptoSecurity
🔐 The wallet was inactive — but its private key still worked

On October 26, 48 wallets linked to Bloom Trading lost 9,408 SOL in just 94 seconds, according to Bitquery's on-chain investigation
Five hadn't traded on Bloom since early 2025
Here's the part that matters 👇

$SOL

Every drain was signed with the affected wallet's own key — no malicious token approval or smart contract exploit required

⚠️ The source of the key exposure is still unconfirmed
But the security lesson is clear
Stopping a bot doesn't make a previously shared private key safe again


📌 If a trading bot has ever held your wallet's private key, moving remaining funds to a fresh wallet with a new key is safer than simply disconnecting the bot
An inactive wallet isn't necessarily a secure wallet

#solana #CryptoSecurity
·
--
Bearish
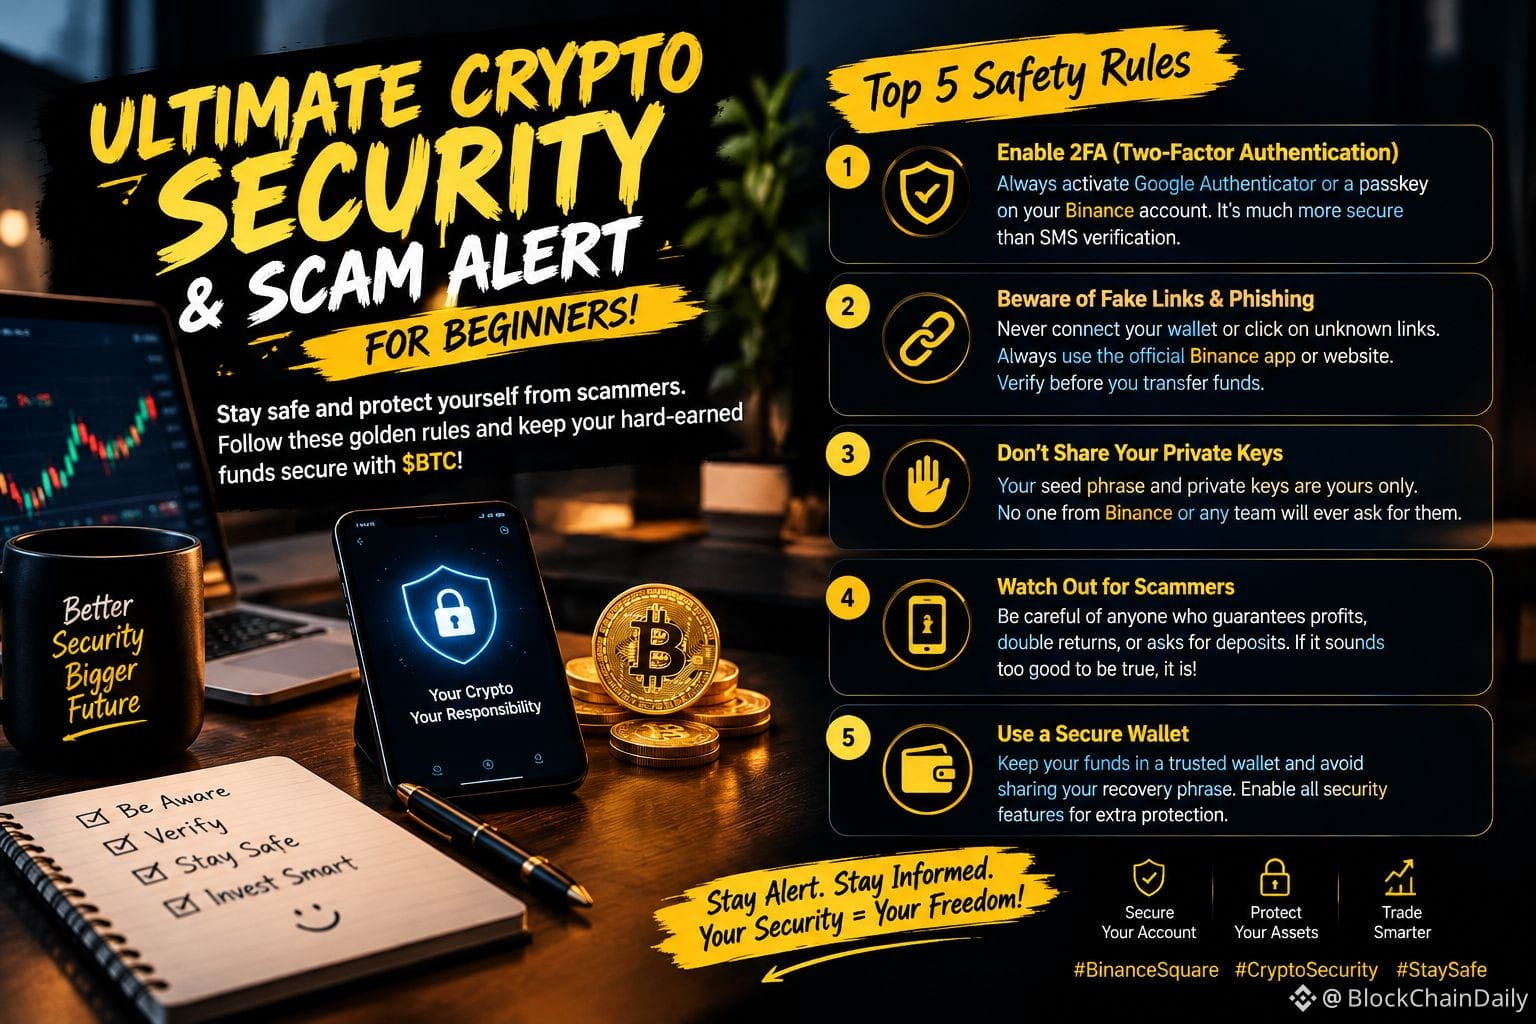
🚨 Ultimate Crypto Security & Scam Alert for Beginners! Staying safe and protecting yourself from scammers should be every crypto trader's top priority. Keep these golden rules in mind to secure your hard-earned funds with $BTC and $BNB {spot}(BNBUSDT) : 📌 Top 5 Safety Rules: • Never Share Private Keys or Seed Phrases: No official admin or support team will ever ask for your seed phrase. Anyone who asks is 100% a scammer! • Enable 2FA (Two-Factor Authentication): Always activate Google Authenticator or a passkey on your Binance account. It is much more secure than SMS verification. • Beware of Fake Links & Phishing: Never connect your wallet or click on unknown links. Always use the official Binance app or website. • Verify Before You Transfer: Always send a small test transaction before transferring funds to a new coin or network. • Ignore "Too Good to Be True" Offers: If someone promises double profits or guaranteed giveaways, recognize it as a trap immediately! 💡 Pro Tip: Security is your own responsibility. One small mistake can wipe out your entire portfolio! 💬 Have you enabled 2FA on your account yet? Let me know in the comments below! 👇 $BTC$BNB #CryptoSecurity #ScamAlert #BinanceSquare #CryptoSafety #ProtectYourFunds
🚨 Ultimate Crypto Security & Scam Alert for Beginners!
Staying safe and protecting yourself from scammers should be every crypto trader's top priority. Keep these golden rules in mind to secure your hard-earned funds with $BTC and $BNB
:
📌 Top 5 Safety Rules: • Never Share Private Keys or Seed Phrases: No official admin or support team will ever ask for your seed phrase. Anyone who asks is 100% a scammer! • Enable 2FA (Two-Factor Authentication): Always activate Google Authenticator or a passkey on your Binance account. It is much more secure than SMS verification. • Beware of Fake Links & Phishing: Never connect your wallet or click on unknown links. Always use the official Binance app or website. • Verify Before You Transfer: Always send a small test transaction before transferring funds to a new coin or network. • Ignore "Too Good to Be True" Offers: If someone promises double profits or guaranteed giveaways, recognize it as a trap immediately!
💡 Pro Tip: Security is your own responsibility. One small mistake can wipe out your entire portfolio!
💬 Have you enabled 2FA on your account yet? Let me know in the comments below! 👇
$BTC $BNB
#CryptoSecurity #ScamAlert #BinanceSquare #CryptoSafety #ProtectYourFunds
·
--
Bearish
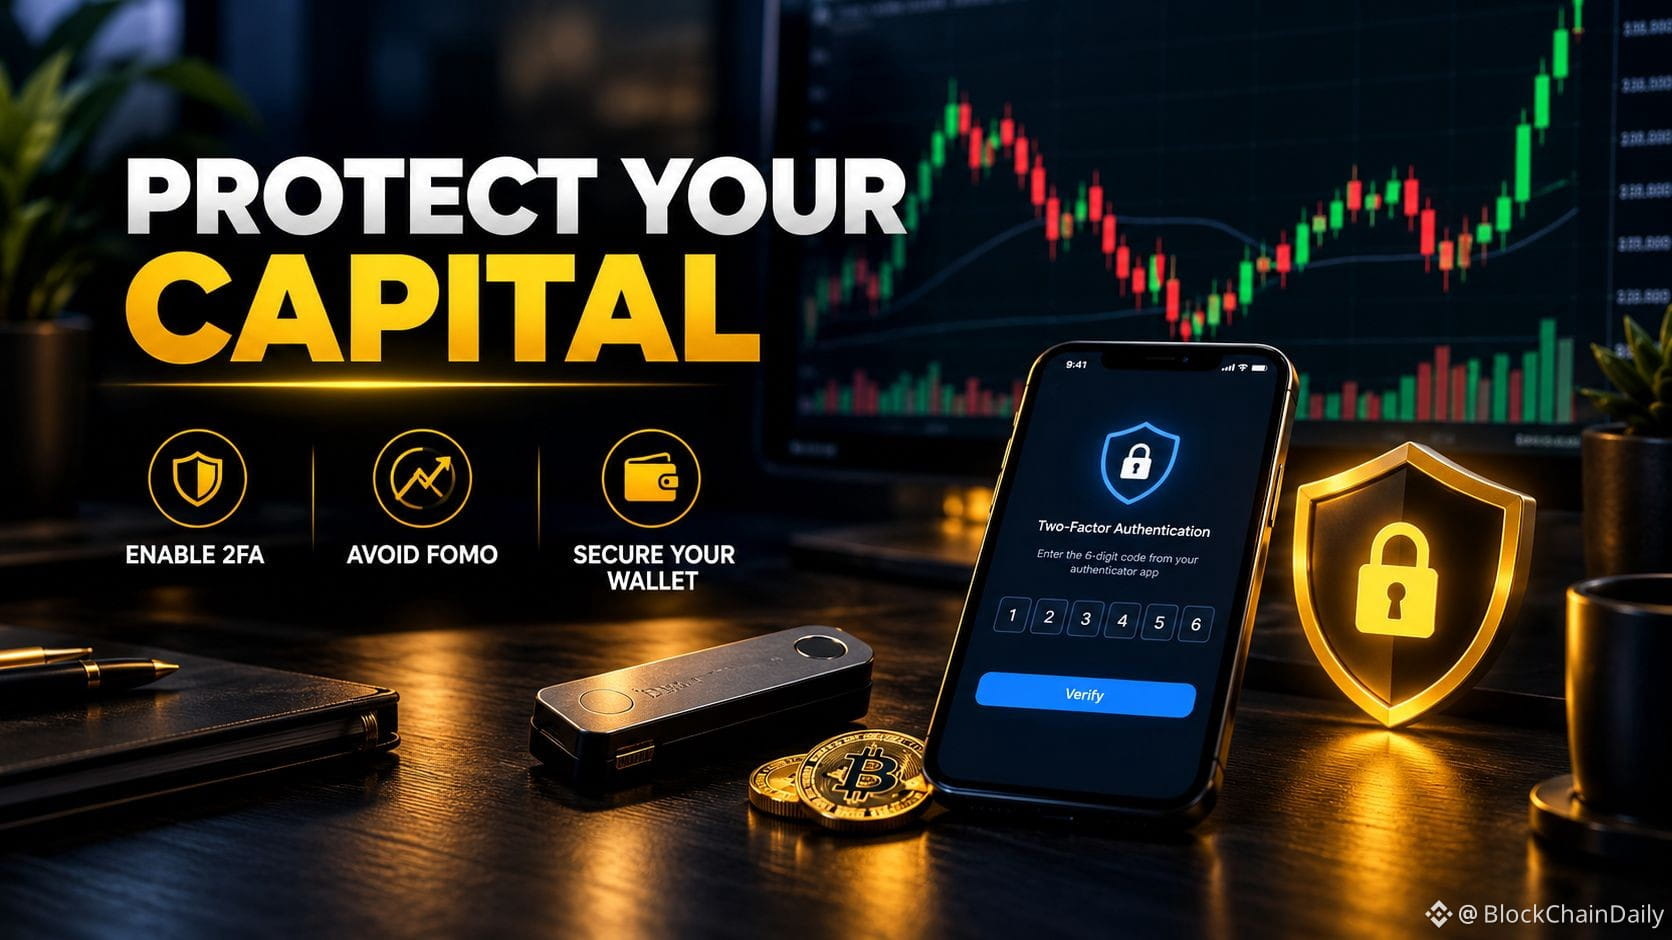
🛡️ Rule #1 of Crypto: Protect Your Capital! In the $crypto world, security and risk management are far more important than chasing quick pumps. 💡 Quick Tips for Daily Traders: • Always enable 2FA on your accounts. • Never FOMO into a green candle without a plan. • Keep long-term holdings in a secure wallet. 💬 What is the biggest lesson you've learned in your crypto journey so far? Share your thoughts! 👇 #CryptoSecurity #TradingTips #BinanceSquare #HODL
🛡️ Rule #1 of Crypto: Protect Your Capital!
In the $crypto world, security and risk management are far more important than chasing quick pumps.
💡 Quick Tips for Daily Traders: • Always enable 2FA on your accounts. • Never FOMO into a green candle without a plan. • Keep long-term holdings in a secure wallet.
💬 What is the biggest lesson you've learned in your crypto journey so far? Share your thoughts! 👇
#CryptoSecurity #TradingTips #BinanceSquare #HODL
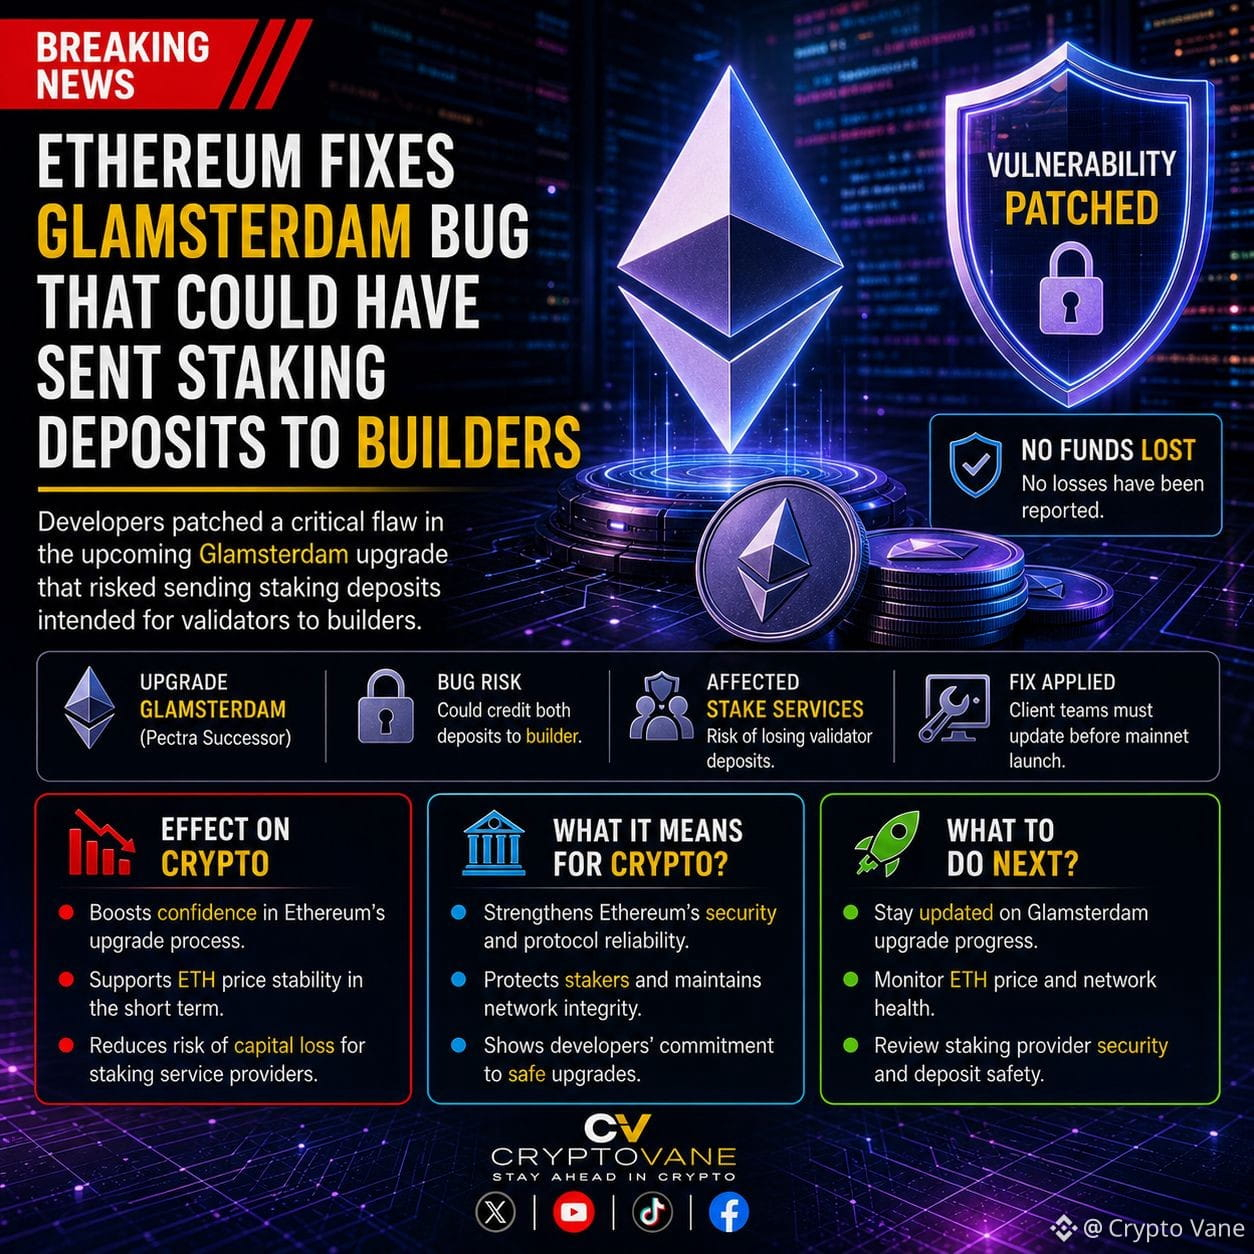
$ETH Fixes Critical Glamsterdam Bug Before It Could Put Staking Deposits at Risk 🚨 $ETH developers have patched a vulnerability in the upcoming Glamsterdam upgrade that could have redirected validator deposits to builders. No losses have been reported, and client teams must implement revised rules before the upgrade can progress toward mainnet launch. #Ethereum #ETH #CryptoNews #blockchain #CryptoSecurity {spot}(ETHUSDT)
$ETH Fixes Critical Glamsterdam Bug Before It Could Put Staking Deposits at Risk 🚨

$ETH developers have patched a vulnerability in the upcoming Glamsterdam upgrade that could have redirected validator deposits to builders. No losses have been reported, and client teams must implement revised rules before the upgrade can progress toward mainnet launch.

#Ethereum #ETH #CryptoNews #blockchain #CryptoSecurity
Ethereum Up or Down on October 27?

Ethereum Up or Down on October 27?

39%Up61%Down
Volume $44,485.99
🚨 SOL bug bounties now cost 1 SOL per report. AI spam overwhelmed security teams, forcing the permanent burn of 809 submissions in a single month. This move protects network integrity but signals extreme strain on Solana's developer infrastructure. Market Implication: Increased operational costs may dampen short-term developer sentiment, but strengthens long-term network resilience. Will this curb the AI influx or drive vulnerability research underground? #CryptoSecurity $SOL #TradingSignal #CryptoAnalysis
🚨 SOL bug bounties now cost 1 SOL per report. AI spam overwhelmed security teams, forcing the permanent burn of 809 submissions in a single month. This move protects network integrity but signals extreme strain on Solana's developer infrastructure.

Market Implication: Increased operational costs may dampen short-term developer sentiment, but strengthens long-term network resilience.

Will this curb the AI influx or drive vulnerability research underground? #CryptoSecurity

$SOL #TradingSignal #CryptoAnalysis
🚨 LEDGER FACES CLASS-ACTION LAWSUIT AS LEAKED DATA ENDANGERS $BTC HOLDINGS! 💣 Lawyer Ariel Givner just revealed that Ledger is hit with a class-action lawsuit in New York following undisclosed security failures. The complaint alleges a December 2023 breach leaked sensitive customer data, including emails and phone numbers, which quickly surfaced on dark web channels. 🔍 Malicious actors utilized this stolen metadata to launch surgical social engineering attacks, impersonating official representatives to drain self-custody wallets. 🌊 Securing your $BTC off exchanges is only half the battle when personal data vulnerabilities open backdoors for attackers. 🛡️ With phishing tactics becoming far more targeted, what steps are you taking to audit your personal operational security? 🤔 ⚠️ Not financial advice. Always manage your risk. 🛡️ 🏷️ #BTC #CryptoSecurity #HardwareWallet #SelfCustody 🚨 🛡️
🚨 LEDGER FACES CLASS-ACTION LAWSUIT AS LEAKED DATA ENDANGERS $BTC HOLDINGS! 💣

Lawyer Ariel Givner just revealed that Ledger is hit with a class-action lawsuit in New York following undisclosed security failures. The complaint alleges a December 2023 breach leaked sensitive customer data, including emails and phone numbers, which quickly surfaced on dark web channels. 🔍

Malicious actors utilized this stolen metadata to launch surgical social engineering attacks, impersonating official representatives to drain self-custody wallets. 🌊 Securing your $BTC off exchanges is only half the battle when personal data vulnerabilities open backdoors for attackers. 🛡️

With phishing tactics becoming far more targeted, what steps are you taking to audit your personal operational security? 🤔

⚠️ Not financial advice. Always manage your risk. 🛡️

🏷️ #BTC #CryptoSecurity #HardwareWallet #SelfCustody

🚨 🛡️
September 2026 hack losses: about $768M. 🛡️ Two events drove most of it: Bitget ($387.5M, wallet system breach) and Liquid Network ($318.7M, code flaw that allowed fake coins to be created). The lesson for traders: exchange size is not a security guarantee. Concentrated funds mean concentrated risk. Quick survival checklist: Move idle coins to your own wallet. Split funds across more than one platform. Turn on 2FA and withdrawal whitelists. Keep on exchanges only what you’re actively trading. Backtest before you deploy... #CryptoSecurity #Bitcoin #CryptoTrading
September 2026 hack losses: about $768M. 🛡️

Two events drove most of it: Bitget ($387.5M, wallet system breach) and Liquid Network ($318.7M, code flaw that allowed fake coins to be created).

The lesson for traders: exchange size is not a security guarantee. Concentrated funds mean concentrated risk.

Quick survival checklist:

Move idle coins to your own wallet.
Split funds across more than one platform.
Turn on 2FA and withdrawal whitelists.

Keep on exchanges only what you’re actively trading.

Backtest before you deploy...

#CryptoSecurity #Bitcoin #CryptoTrading
FULL RECOVERY CONFIRMED AFTER $ETH VAULT EXPLOIT AS CORE DEFI CONTRACTS HOLD STRONG 🛡️ Smart money moves fast when crisis strikes, but full asset recovery is a rare victory in DeFi security battles. 🏦 Term Labs just finalized the complete retrieval of affected vault positions following a sophisticated governance delay exploit on their ETH and USDC strategies. 📊 Crucially, core direct lending contracts, V1/V2 protocols, and liquidation engines held up without a scratch, showing true structural resilience. 🔍 With contracts upgraded, affected vaults closed, and security firms tracking the attacker's Tornado Cash trail, confidence is rotating back into the ecosystem. 💬 Does a successful 100% fund recovery restore your appetite for fixed-rate DeFi yields, or are you waiting for full audits before moving capital? 👇 ⚠️ Not financial advice. Always manage your risk. 🛡️ 🏷️ #ETH #DeFi #CryptoSecurity #Crypto 🛡️ 🔍
FULL RECOVERY CONFIRMED AFTER $ETH VAULT EXPLOIT AS CORE DEFI CONTRACTS HOLD STRONG 🛡️

Smart money moves fast when crisis strikes, but full asset recovery is a rare victory in DeFi security battles. 🏦 Term Labs just finalized the complete retrieval of affected vault positions following a sophisticated governance delay exploit on their ETH and USDC strategies. 📊

Crucially, core direct lending contracts, V1/V2 protocols, and liquidation engines held up without a scratch, showing true structural resilience. 🔍 With contracts upgraded, affected vaults closed, and security firms tracking the attacker's Tornado Cash trail, confidence is rotating back into the ecosystem.

💬 Does a successful 100% fund recovery restore your appetite for fixed-rate DeFi yields, or are you waiting for full audits before moving capital? 👇

⚠️ Not financial advice. Always manage your risk. 🛡️

🏷️ #ETH #DeFi #CryptoSecurity #Crypto

🛡️ 🔍
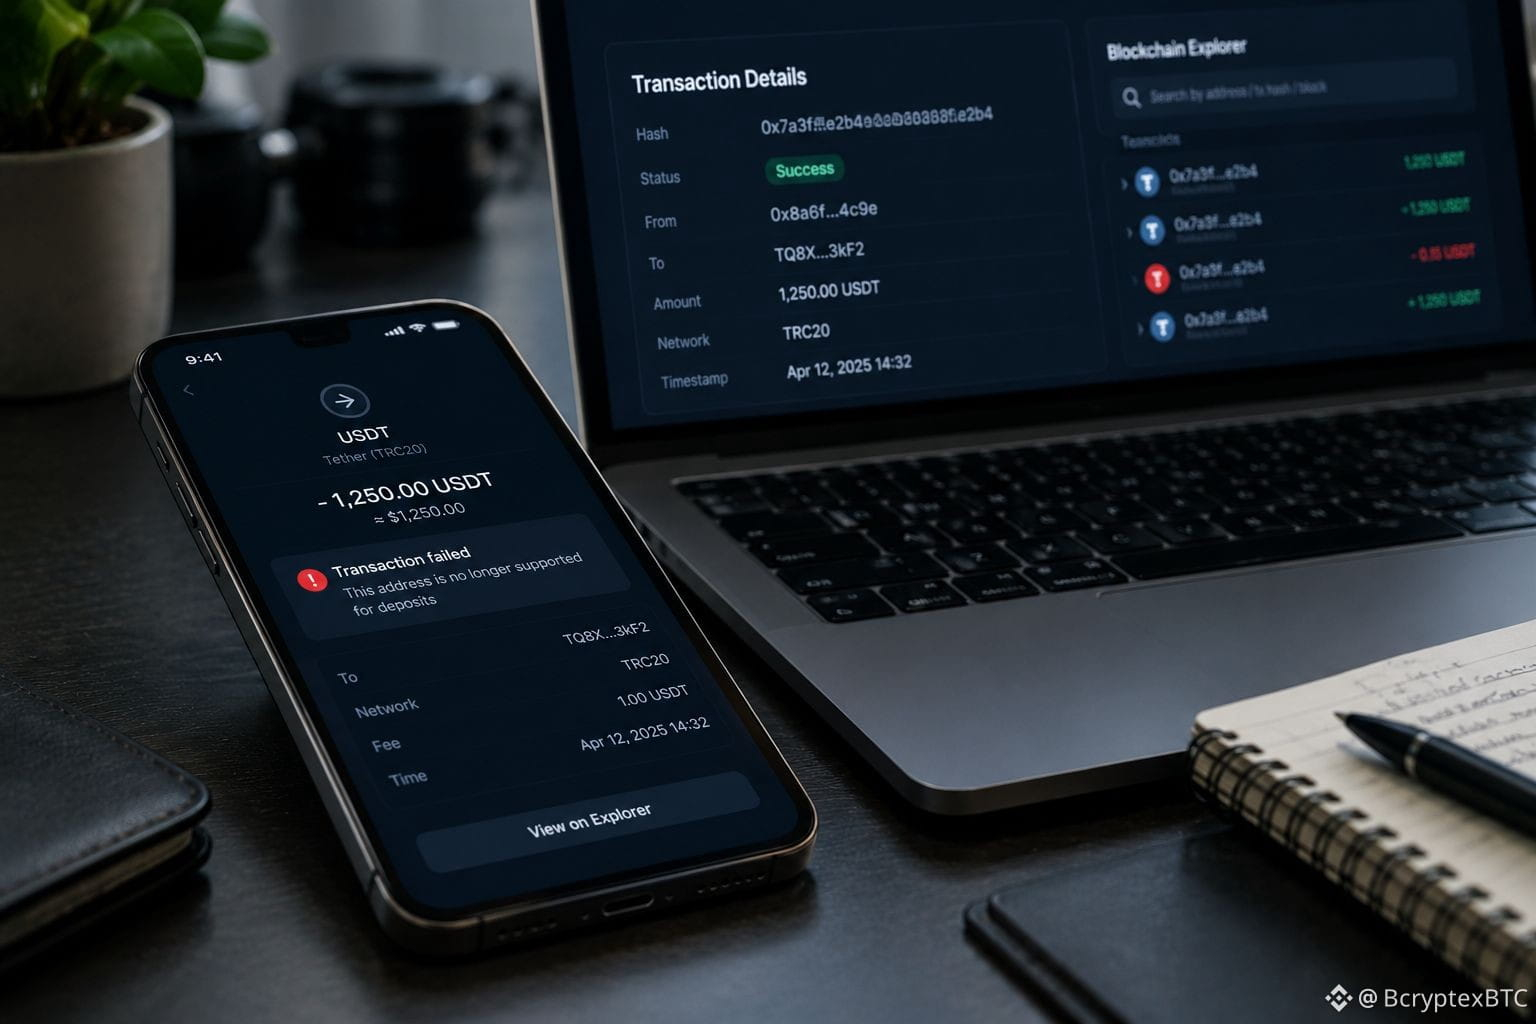
$16M Lost — Who Is Responsible When Old Deposit Addresses Still Work? CoinDCX reportedly absorbed a $15.99M $USDT loss after users sent funds to retired deposit addresses following its 2025 security breach. Customer balances reportedly remain unaffected. A retired address doesn’t disappear from the blockchain. Users may still send funds to it, even when an exchange no longer supports deposits through that address. This highlights a critical security gap: users must verify deposit details, while exchanges need clear warnings and effective recovery procedures. Should the responsibility fall on the user, the exchange, or both? #CryptoSecurity #CoinDCX #Blockchain $BTC
$16M Lost — Who Is Responsible When Old Deposit Addresses Still Work?

CoinDCX reportedly absorbed a $15.99M $USDT loss after users sent funds to retired deposit addresses following its 2025 security breach. Customer balances reportedly remain unaffected.

A retired address doesn’t disappear from the blockchain. Users may still send funds to it, even when an exchange no longer supports deposits through that address.

This highlights a critical security gap: users must verify deposit details, while exchanges need clear warnings and effective recovery procedures.

Should the responsibility fall on the user, the exchange, or both?

#CryptoSecurity #CoinDCX #Blockchain $BTC
🔥 Social engineering attacks aren't just phishing—they're the new frontier for crypto theft. 📊 Ripple just released North Korea‑linked threat intel after the $280 million Drift hack, underscoring how criminal groups are moving from raw exploits to crafted lures. #CryptoSecurity #NorthKorea 💡 When attackers master human psychology, the whole market feels the pressure—Bitcoin slipped to $79,879 with RSI 38.2 and a bullish MACD crossover, while ETH sits at $2,308, RSI 37.3, highlighting that technical safeguards alone won’t protect assets. #MarketRisk #OnChain 🛠️ Start treating every unsolicited link or Discord invite as a potential trap; verify contracts on‑chain—smart wallets are already piling into Solana’s DNA (+4.1%) and BSC’s ZIG (+2.3%), proving that vigilant investors stay one step ahead. ❓ How are you adjusting your security habits now that social engineering is the hottest weapon in the crypto arsenal?
🔥 Social engineering attacks aren't just phishing—they're the new frontier for crypto theft.

📊 Ripple just released North Korea‑linked threat intel after the $280 million Drift hack, underscoring how criminal groups are moving from raw exploits to crafted lures. #CryptoSecurity #NorthKorea

💡 When attackers master human psychology, the whole market feels the pressure—Bitcoin slipped to $79,879 with RSI 38.2 and a bullish MACD crossover, while ETH sits at $2,308, RSI 37.3, highlighting that technical safeguards alone won’t protect assets. #MarketRisk #OnChain

🛠️ Start treating every unsolicited link or Discord invite as a potential trap; verify contracts on‑chain—smart wallets are already piling into Solana’s DNA (+4.1%) and BSC’s ZIG (+2.3%), proving that vigilant investors stay one step ahead.

❓ How are you adjusting your security habits now that social engineering is the hottest weapon in the crypto arsenal?
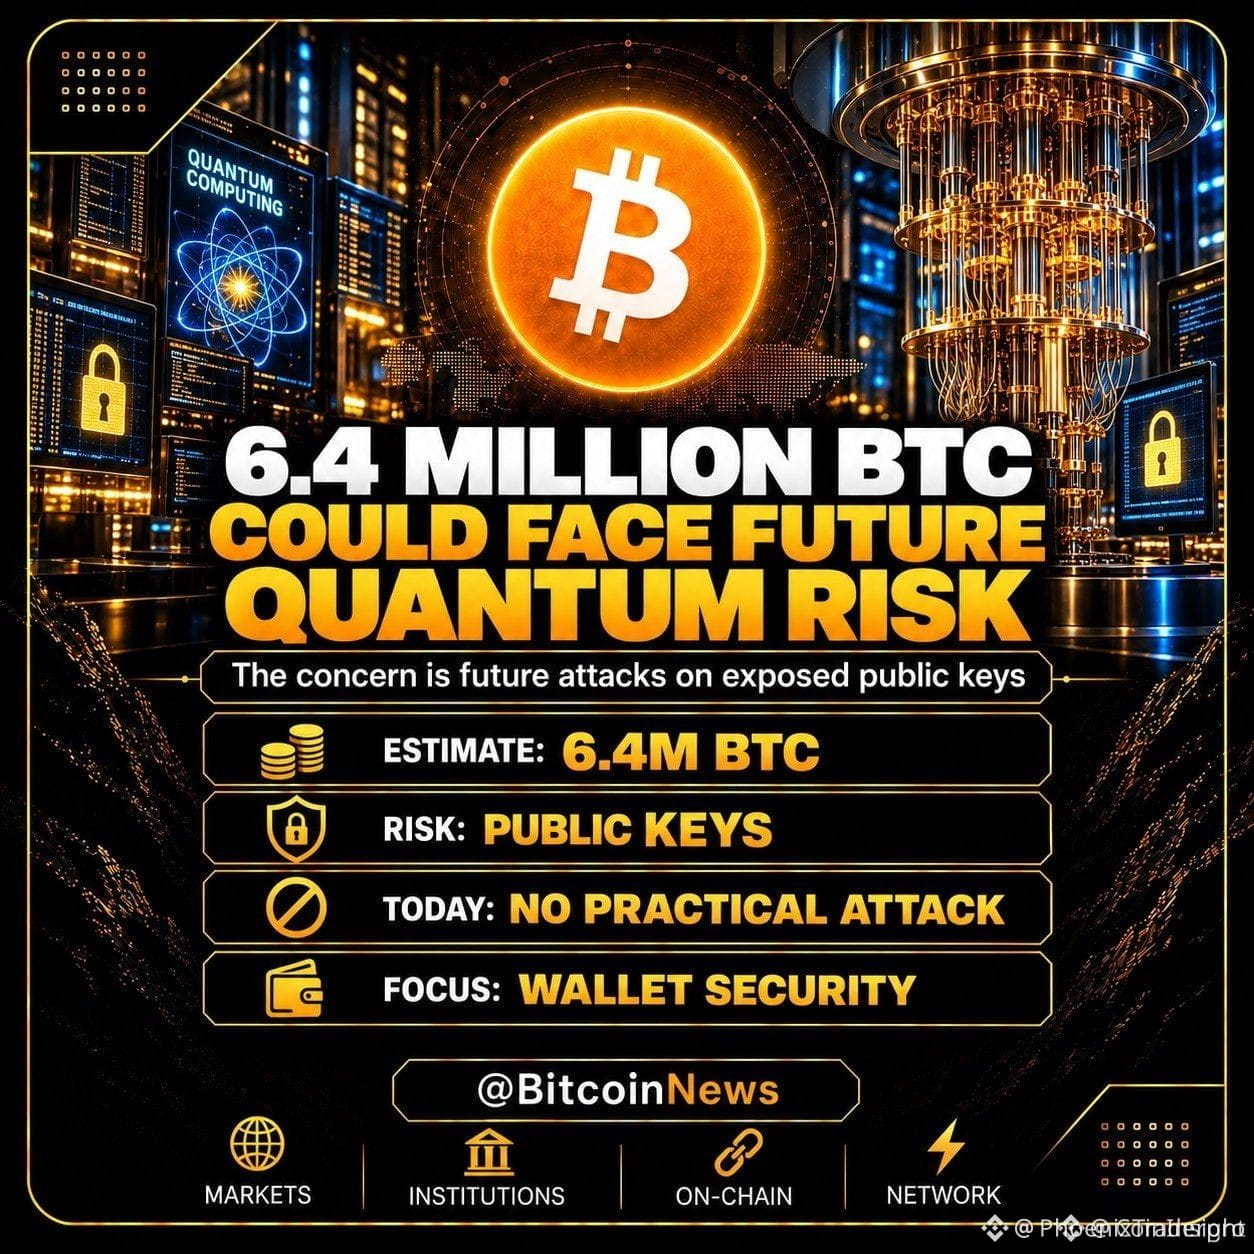
🚨 $BTC QUANTUM THREAT LOOMS: 6.4M BTC AT RISK 🦈 The newly‑formed QUANTUM ALLIANCE – nine heavyweight labs teaming up – is already mapping the future battlefield where quantum computers could pry open public‑key cryptography. 📊 Roughly 6.4 million $BTC sit in addresses whose public keys are exposed on‑chain, a silent pool that could become prime loot if a sufficiently powerful quantum machine emerges. 🦈 Today no quantum rig can crack Bitcoin, but the discussion is shifting from “if” to “when,” sparking a debate over wallet freezes, forced migrations, or leaving ownership untouched. ⚡ The market’s perception of this existential risk could tilt sentiment, especially as smart‑money eyes the vulnerable slice. 💡 Are you positioning now or waiting for a protocol safeguard? 💬 ⚠️ Not financial advice. Always manage your risk. 🛡️ 🏷️ #BTC #QuantumRisk #CryptoSecurity #LongSetup 🚀 ⚡
🚨 $BTC QUANTUM THREAT LOOMS: 6.4M BTC AT RISK 🦈

The newly‑formed QUANTUM ALLIANCE – nine heavyweight labs teaming up – is already mapping the future battlefield where quantum computers could pry open public‑key cryptography. 📊 Roughly 6.4 million $BTC sit in addresses whose public keys are exposed on‑chain, a silent pool that could become prime loot if a sufficiently powerful quantum machine emerges. 🦈

Today no quantum rig can crack Bitcoin, but the discussion is shifting from “if” to “when,” sparking a debate over wallet freezes, forced migrations, or leaving ownership untouched. ⚡ The market’s perception of this existential risk could tilt sentiment, especially as smart‑money eyes the vulnerable slice. 💡 Are you positioning now or waiting for a protocol safeguard? 💬

⚠️ Not financial advice. Always manage your risk. 🛡️

🏷️ #BTC #QuantumRisk #CryptoSecurity #LongSetup

🚀 ⚡
🔐 YOUR SECURITY COMES FIRST! Before joining any crypto airdrop, remember these rules: ✅ Use official websites and apps. ✅ Never share your password or OTP. ✅ Never send crypto to claim a promised reward without verifying the offer. ✅ Research unfamiliar projects carefully. ✅ Read all terms and conditions. 🚨 No guaranteed profits. No blind trust. Always DYOR! Protect your assets. Protect your future. 💛 #CryptoSecurity #Binance #DYOR!!
🔐 YOUR SECURITY COMES FIRST!

Before joining any crypto airdrop, remember these rules:

✅ Use official websites and apps.
✅ Never share your password or OTP.
✅ Never send crypto to claim a promised reward without verifying the offer.
✅ Research unfamiliar projects carefully.
✅ Read all terms and conditions.

🚨 No guaranteed profits. No blind trust. Always DYOR!

Protect your assets. Protect your future. 💛

#CryptoSecurity #Binance #DYOR!!
- No markdown (so plain text, no formatting like **, *, #? Actually hashtags are allowed at end, they are part of text. No markdown formatting like bold, italics, code blocks.) - 150-200 words. - Warning-style tone (serious but not panic-inducing). - Give 3 clear actionable steps. - End with: "Share this with someone new to crypto — it could save them!" - Final line: "#CryptoStrategy #TokenomicsExplained #CryptoSecurity #StaySafe" - Must start directly with first word, no preamble. We need to count words. Let's aim for ~170 words. We need to include 3 actionable steps, likely bullet points but no markdown bullet points? Could use numbers with periods. That's okay plain text. We must not use markdown, so no bullet points with hyphens? Hyphens are okay but might be considered markdown? Probably fine. Safer to use "1." "2." "3." lines. Word count: Let's draft ~170 words. Count words manually. Draft: "Warning: many DeFi projects promise impossible yields while hiding a classic Ponzi structure. Look for these red flags before committing funds. 1. Verify the revenue model. Legitimate protocols generate income from real activity — fees, lending interest, or service charges. If the only source of returns is new investor deposits, walk away. 2. Check tokenomics transparency. A credible project publishes a clear emission schedule, vesting periods, and audit reports. Opaque supply mechanics or unlimited minting authority are major warning signs. 3. Test withdrawal flexibility. Try moving a small amount out of the platform. Delayed or blocked withdrawals, mandatory lock‑ups, or penalties for early exit indicate the operator is recycling capital rather than earning it. Always research the team,
- No markdown (so plain text, no formatting like **, *, #? Actually hashtags are allowed at end, they are part of text. No markdown formatting like bold, italics, code blocks.)
- 150-200 words.
- Warning-style tone (serious but not panic-inducing).
- Give 3 clear actionable steps.
- End with: "Share this with someone new to crypto — it could save them!"
- Final line: "#CryptoStrategy #TokenomicsExplained #CryptoSecurity #StaySafe"
- Must start directly with first word, no preamble.

We need to count words. Let's aim for ~170 words.

We need to include 3 actionable steps, likely bullet points but no markdown bullet points? Could use numbers with periods. That's okay plain text.

We must not use markdown, so no bullet points with hyphens? Hyphens are okay but might be considered markdown? Probably fine. Safer to use "1." "2." "3." lines.

Word count: Let's draft ~170 words.

Count words manually.

Draft:

"Warning: many DeFi projects promise impossible yields while hiding a classic Ponzi structure. Look for these red flags before committing funds.

1. Verify the revenue model. Legitimate protocols generate income from real activity — fees, lending interest, or service charges. If the only source of returns is new investor deposits, walk away.

2. Check tokenomics transparency. A credible project publishes a clear emission schedule, vesting periods, and audit reports. Opaque supply mechanics or unlimited minting authority are major warning signs.

3. Test withdrawal flexibility. Try moving a small amount out of the platform. Delayed or blocked withdrawals, mandatory lock‑ups, or penalties for early exit indicate the operator is recycling capital rather than earning it.

Always research the team,
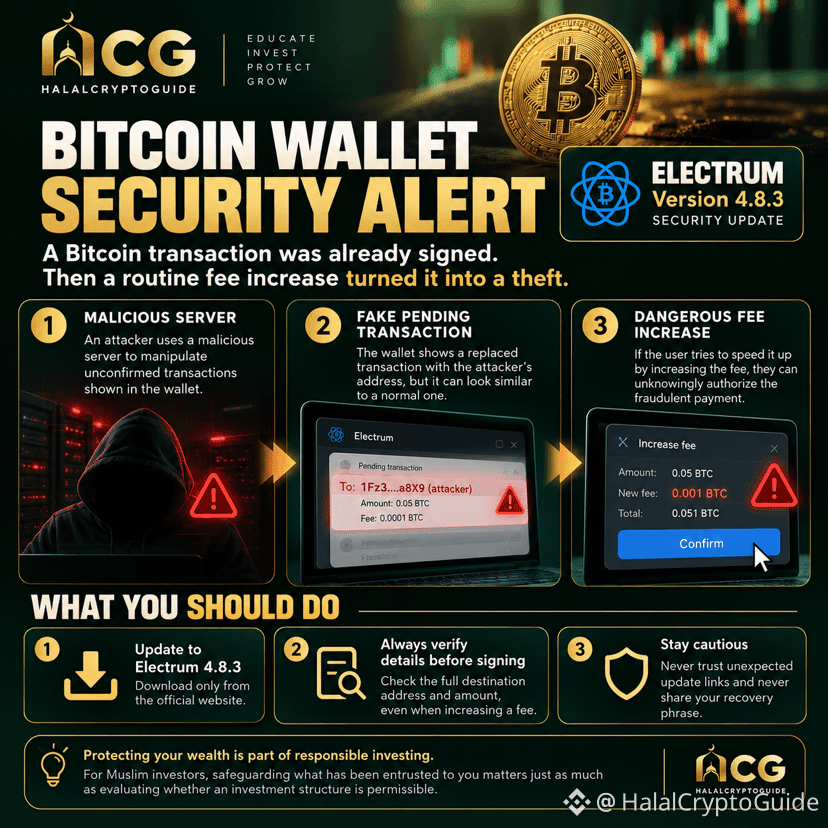
A simple Bitcoin fee increase cost someone their funds. Here’s what happened. Electrum, a popular Bitcoin wallet, has patched a serious security vulnerability after malicious servers exploited a weakness in how the wallet handled unconfirmed transactions. The dangerous part? Users didn’t need to reveal their seed phrases. An attacker could replace a pending transaction displayed in the wallet with a fraudulent one. If the user tried to speed it up by increasing the fee, they could unknowingly authorize a payment to the attacker. At least one user reportedly lost Bitcoin. Three precautions worth remembering: 1. If you use Electrum, upgrade to version 4.8.3 from its official website. 2. Verify the complete destination address and amount before signing—even when simply increasing a transaction fee. 3. Never trust unexpected wallet-update links or share your recovery phrase. For Muslim investors, protecting entrusted wealth matters just as much as evaluating whether an investment structure is permissible. Security isn’t only about protecting your private keys. It’s also about understanding what you’re signing. Have you checked when your crypto wallet was last updated? #Bitcoin #CryptoSecurity #CryptoEducation #SelfCustody
A simple Bitcoin fee increase cost someone their funds. Here’s what happened.

Electrum, a popular Bitcoin wallet, has patched a serious security vulnerability after malicious servers exploited a weakness in how the wallet handled unconfirmed transactions.

The dangerous part? Users didn’t need to reveal their seed phrases.

An attacker could replace a pending transaction displayed in the wallet with a fraudulent one. If the user tried to speed it up by increasing the fee, they could unknowingly authorize a payment to the attacker.

At least one user reportedly lost Bitcoin.

Three precautions worth remembering:

1. If you use Electrum, upgrade to version 4.8.3 from its official website.
2. Verify the complete destination address and amount before signing—even when simply increasing a transaction fee.
3. Never trust unexpected wallet-update links or share your recovery phrase.

For Muslim investors, protecting entrusted wealth matters just as much as evaluating whether an investment structure is permissible.

Security isn’t only about protecting your private keys. It’s also about understanding what you’re signing.

Have you checked when your crypto wallet was last updated?

#Bitcoin #CryptoSecurity #CryptoEducation #SelfCustody
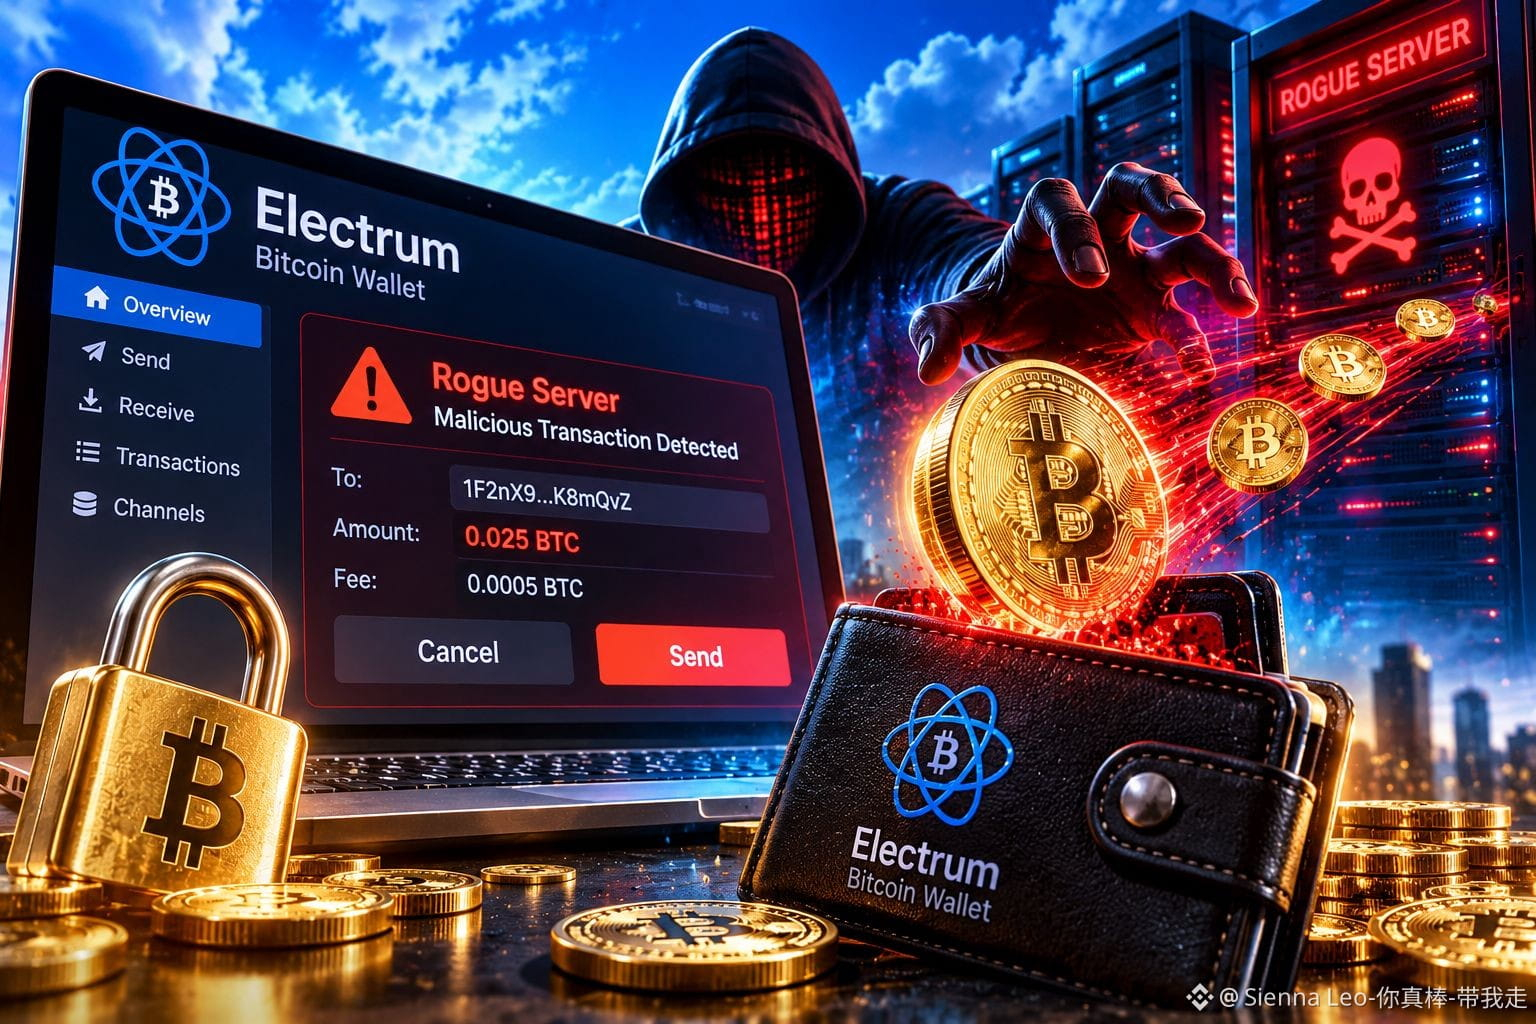
#electrumwalletbugletrogueserversstealfunds 🔐 ⚠️ Electrum Wallet Bug: How Rogue Servers Could Steal $BITCOIN ⚠️ 🔐 Imagine checking a Bitcoin payment, seeing it stuck, and deciding to increase the transaction fee. One click later, your attempt to speed up the payment could help an attacker redirect your funds. A security flaw in Electrum, a popular Bitcoin wallet, allowed malicious servers to substitute fraudulent unconfirmed transactions when users tried to speed up payments using Replace-by-Fee (RBF). At least one user reported losing Bitcoin. Electrum relies on external servers to retrieve transaction information. The flaw meant a malicious server could provide a fake transaction that the wallet failed to validate properly, turning a routine fee adjustment into a potential theft. Developers released Electrum version 4.8.3 on October 24, 2026, adding signature verification to address the vulnerability. Users should upgrade rather than assume older versions are safe. The deeper lesson is that self-custody does not eliminate every security risk. Your private keys may remain yours, but wallet software and server connections can still influence the transaction you are asked to approve. Protect your Bitcoin: Update Electrum, verify the complete recipient address and amount on your signing device, and use trusted servers. Never approve a transaction simply because the wallet labels it as a fee increase. In crypto, one careful verification can matter more than a hundred rushed clicks. Do you think wallet users should be warned more clearly whenever a transaction's destination changes? Disclaimer: For educational purposes only. This is not financial or cybersecurity advice. #Bitcoin #CryptoSecurity #GrowWithSAC $BTC $QNT #ElectrumWalletBugLetRogueServersStealFunds
#electrumwalletbugletrogueserversstealfunds
🔐 ⚠️ Electrum Wallet Bug: How Rogue Servers Could Steal $BITCOIN ⚠️ 🔐

Imagine checking a Bitcoin payment, seeing it stuck, and deciding to increase the transaction fee. One click later, your attempt to speed up the payment could help an attacker redirect your funds.

A security flaw in Electrum, a popular Bitcoin wallet, allowed malicious servers to substitute fraudulent unconfirmed transactions when users tried to speed up payments using Replace-by-Fee (RBF). At least one user reported losing Bitcoin.

Electrum relies on external servers to retrieve transaction information. The flaw meant a malicious server could provide a fake transaction that the wallet failed to validate properly, turning a routine fee adjustment into a potential theft.

Developers released Electrum version 4.8.3 on October 24, 2026, adding signature verification to address the vulnerability. Users should upgrade rather than assume older versions are safe.

The deeper lesson is that self-custody does not eliminate every security risk. Your private keys may remain yours, but wallet software and server connections can still influence the transaction you are asked to approve.

Protect your Bitcoin: Update Electrum, verify the complete recipient address and amount on your signing device, and use trusted servers. Never approve a transaction simply because the wallet labels it as a fee increase.

In crypto, one careful verification can matter more than a hundred rushed clicks.

Do you think wallet users should be warned more clearly whenever a transaction's destination changes?

Disclaimer: For educational purposes only. This is not financial or cybersecurity advice.

#Bitcoin #CryptoSecurity #GrowWithSAC $BTC $QNT #ElectrumWalletBugLetRogueServersStealFunds
🔥 THE CRYPTO SECURITY FLOOD JUST BREACHED THE DAM — LEVEL3 CERTIFICATION LANDED ON COINSPAYED. 📊 CoinsPaid’s CryptoProcessing cleared the toughest CCSS hurdle, earning the elite Level 3 badge for institutional‑grade wallet protection. That same day, #BNB surged 0.41% to $745 with a bullish RSI of 56.9, while BTC futures showed $7.68 B open interest and a +0.0097% funding rate, signaling long‑side confidence. Smart‑money on Solana pumped RAYPAD wallets up 6.28%, proving the market rewards iron‑clad security. #CryptoSecurity #Institutional #DeFi 💡 This win means enterprises can now lock assets behind the highest guardrail, likely spurring fresh institutional inflows and nudging the broader market toward a security‑first rally. #CryptoAdoption ❓ Are you ready to ride the next wave of secure crypto growth, or will you watch it pass by?
🔥 THE CRYPTO SECURITY FLOOD JUST BREACHED THE DAM — LEVEL3 CERTIFICATION LANDED ON COINSPAYED.

📊 CoinsPaid’s CryptoProcessing cleared the toughest CCSS hurdle, earning the elite Level 3 badge for institutional‑grade wallet protection. That same day, #BNB surged 0.41% to $745 with a bullish RSI of 56.9, while BTC futures showed $7.68 B open interest and a +0.0097% funding rate, signaling long‑side confidence. Smart‑money on Solana pumped RAYPAD wallets up 6.28%, proving the market rewards iron‑clad security. #CryptoSecurity #Institutional #DeFi

💡 This win means enterprises can now lock assets behind the highest guardrail, likely spurring fresh institutional inflows and nudging the broader market toward a security‑first rally. #CryptoAdoption

❓ Are you ready to ride the next wave of secure crypto growth, or will you watch it pass by?
🔐 A crypto wallet can stay safe even when a company gets hacked, but your personal information might not. Recent data breaches remind us that names, home addresses, and purchase records can become valuable targets for scammers. Once they know you own crypto, they may try to trick you with fake support calls, replacement wallet offers, or suspicious delivery messages. Here’s one rule I’ll never ignore: Never enter your old recovery phrase into a device just because someone claims to be from the company. 🚨 Real support teams don’t need your seed phrase to help you. Stay alert, protect your privacy, and never trust unexpected crypto-related calls or messages. Personally, I’d rather have people think my packages contain boring shopping than know what’s inside. 😂📦 #CryptoSecurity #HardwareWallets #Web3 $SHOP {future}(SHOPUSDT)
🔐 A crypto wallet can stay safe even when a company gets hacked, but your personal information might not.

Recent data breaches remind us that names, home addresses, and purchase records can become valuable targets for scammers. Once they know you own crypto,

they may try to trick you with fake support calls, replacement wallet offers, or suspicious delivery messages.

Here’s one rule I’ll never ignore: Never enter your old recovery phrase into a device just because someone claims to be from the company. 🚨

Real support teams don’t need your seed phrase to help you.

Stay alert, protect your privacy, and never trust unexpected crypto-related calls or messages.

Personally, I’d rather have people think my packages contain boring shopping than know what’s inside. 😂📦

#CryptoSecurity #HardwareWallets #Web3

$SHOP
Electrum 4.8.3 patches a high-severity malicious-server fee-bump trap disclosed on October 24, 2026. On October 24, 2026, Electrum released 4.8.3 (advisory GHSA-6jp4-8v48-cc5v). A malicious Electrum server can swallow a just-broadcast $BTC tx and show a conflicting fake unconfirmed payment to the attacker — older clients did not check those invalid signatures. If the user RBF fee-bumps the fake tx, they sign a real payment to the attacker. Some servers were already exploiting this; two users reported it and one lost funds. Attackers also ground the last four characters of the destination address to look similar. Upgrade to 4.8.3 or newer — all older versions are affected. The fix verifies signatures on wallet-owned inputs for mempool txs before adding them to history. Download only from electrum.org and verify signatures. Until upgraded, check the full destination address and amount before any fee bump. Trusted or self-run server users are less exposed; incoming unconfirmed txs are still not fully validated. #Bitcoin #Electrum #CryptoSecurity #Wallet DYOR. Not financial advice. {spot}(BTCUSDT)
Electrum 4.8.3 patches a high-severity malicious-server fee-bump trap disclosed on October 24, 2026.

On October 24, 2026, Electrum released 4.8.3 (advisory GHSA-6jp4-8v48-cc5v). A malicious Electrum server can swallow a just-broadcast $BTC tx and show a conflicting fake unconfirmed payment to the attacker — older clients did not check those invalid signatures. If the user RBF fee-bumps the fake tx, they sign a real payment to the attacker. Some servers were already exploiting this; two users reported it and one lost funds. Attackers also ground the last four characters of the destination address to look similar.

Upgrade to 4.8.3 or newer — all older versions are affected. The fix verifies signatures on wallet-owned inputs for mempool txs before adding them to history. Download only from electrum.org and verify signatures. Until upgraded, check the full destination address and amount before any fee bump. Trusted or self-run server users are less exposed; incoming unconfirmed txs are still not fully validated.

#Bitcoin #Electrum #CryptoSecurity #Wallet
DYOR. Not financial advice.
🚨 A Bitcoin Hacking Challenge Fell in Less Than 3 Hours! Sometimes, one small vulnerability is all it takes to bring down an entire security setup. The Steal My Bitcoin challenge server was breached less than three hours after an accessible PHP page was added. Security researcher Killa published a proof of concept, and the server operator confirmed the breach through server logs. What stands out to me is how quickly things went wrong. A system can appear secure on the surface, but one overlooked weakness can change everything. 🔍 My takeaway: Security is not just about protecting private keys or using strong encryption. Every entry point, every new feature, and every line of code needs proper testing. In crypto, trust should never replace verification. Even a challenge designed around security can become a real-world lesson in vulnerability management. One question worth asking: If a controlled Bitcoin challenge can fall this quickly, how prepared are real-world crypto platforms for unexpected exploits? $BULLA $ARIA #Bitcoin #BTC #CyberSecurity #CryptoSecurity #blockchain
🚨 A Bitcoin Hacking Challenge Fell in Less Than 3 Hours!

Sometimes, one small vulnerability is all it takes to bring down an entire security setup.

The Steal My Bitcoin challenge server was breached less than three hours after an accessible PHP page was added. Security researcher Killa published a proof of concept, and the server operator confirmed the breach through server logs.

What stands out to me is how quickly things went wrong. A system can appear secure on the surface, but one overlooked weakness can change everything.

🔍 My takeaway: Security is not just about protecting private keys or using strong encryption. Every entry point, every new feature, and every line of code needs proper testing.

In crypto, trust should never replace verification. Even a challenge designed around security can become a real-world lesson in vulnerability management.

One question worth asking: If a controlled Bitcoin challenge can fall this quickly, how prepared are real-world crypto platforms for unexpected exploits?

$BULLA $ARIA

#Bitcoin #BTC #CyberSecurity #CryptoSecurity #blockchain
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🔐⚠️ Keystone Website Breach Exposes Crypto Buyers’ Shipping Addresses ⚠️🔐 Sometimes, the biggest security risk isn't inside your wallet. It's the address where you keep it. Keystone, a cryptocurrency hardware wallet manufacturer, has disclosed a website breach that exposed customers’ names, contact details, shipping addresses, and order information. The company detected unauthorized access on October 20 and confirmed the data exposure on October 23, 2026, after reviewing activity involving its Shopify-powered store. Keystone says payment details, recovery phrases, private keys, and wallet passwords were not exposed. It has blocked the unauthorized access, fixed the vulnerability, and begun notifying affected customers. The number of affected users remains undisclosed. But here's the bigger concern: knowing someone's identity, home address, and hardware wallet purchase can help criminals craft convincing phishing attacks or potentially target crypto holders in the real world. My Take: Self-custody protects control over your crypto, but it cannot protect personal information leaked by a third-party service. Your security is only as strong as the weakest link connecting your digital assets to your real identity. If you purchased from Keystone, verify alerts through official channels, ignore unsolicited refund or replacement offers, and never share your recovery phrase. No legitimate support agent needs it. True crypto security means protecting both your assets and the personal information that could make you a target. Should hardware wallet companies be held to stricter data-deletion standards after a customer's order is completed? Disclaimer: This post is for educational purposes only and is not financial or security advice. #CryptoSecurity #DataBreach #GrowWithSAC $QNT $ENA $PYTH
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🔐⚠️ Keystone Website Breach Exposes Crypto Buyers’ Shipping Addresses ⚠️🔐

Sometimes, the biggest security risk isn't inside your wallet. It's the address where you keep it.

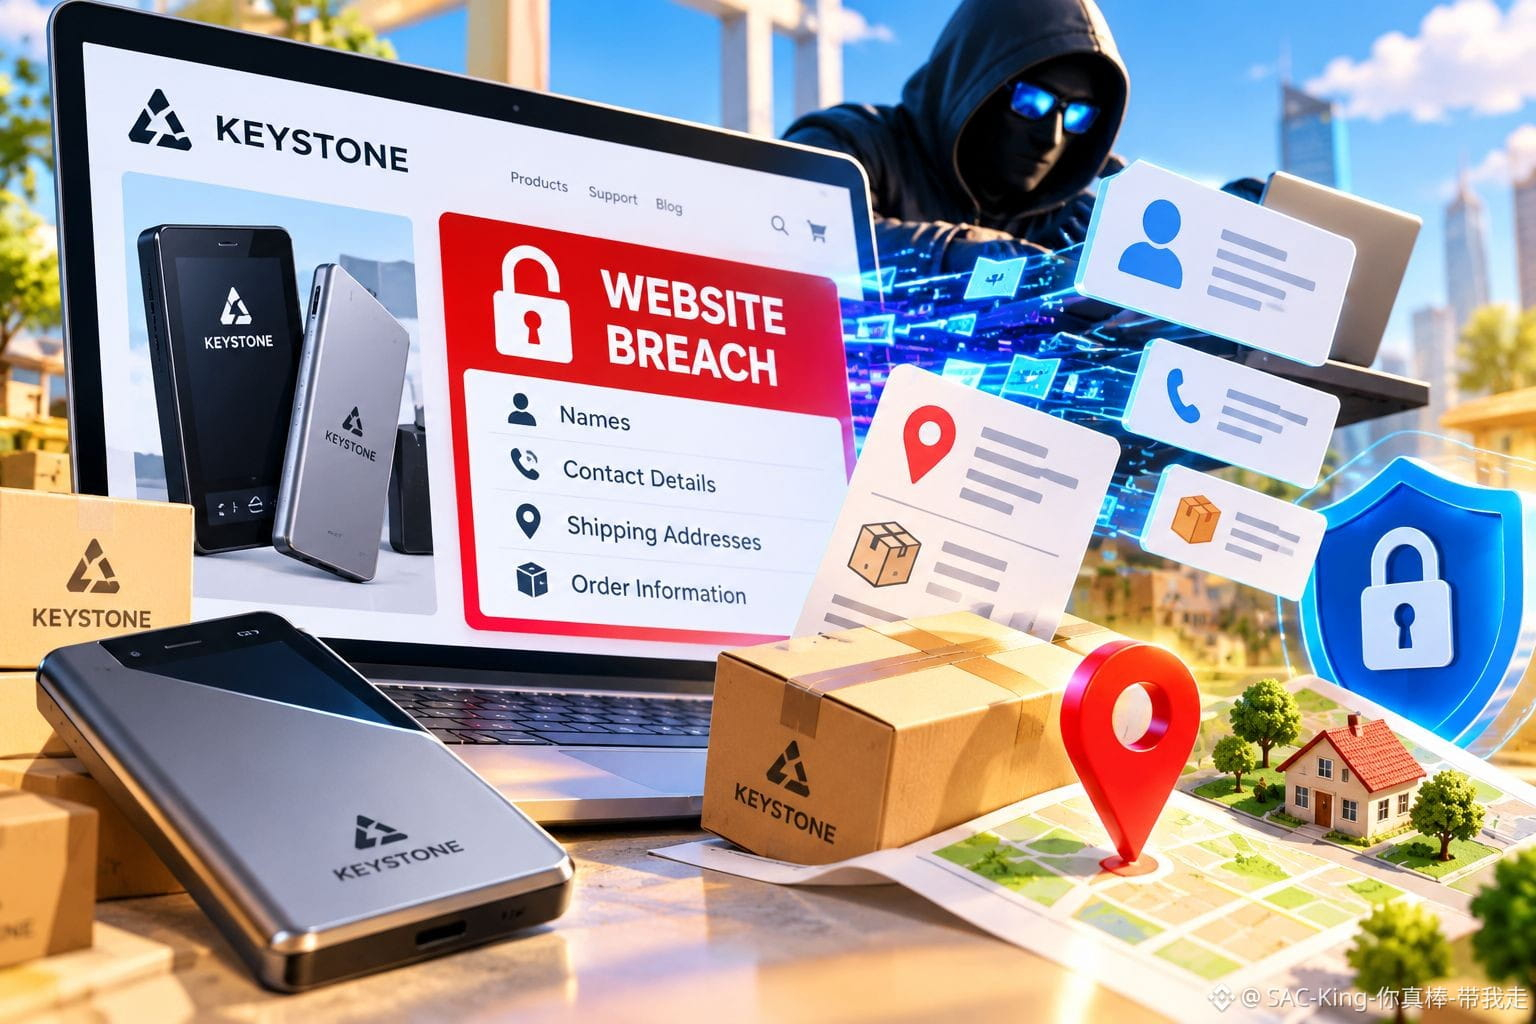
Keystone, a cryptocurrency hardware wallet manufacturer, has disclosed a website breach that exposed customers’ names, contact details, shipping addresses, and order information.

The company detected unauthorized access on October 20 and confirmed the data exposure on October 23, 2026, after reviewing activity involving its Shopify-powered store.

Keystone says payment details, recovery phrases, private keys, and wallet passwords were not exposed. It has blocked the unauthorized access, fixed the vulnerability, and begun notifying affected customers. The number of affected users remains undisclosed.

But here's the bigger concern: knowing someone's identity, home address, and hardware wallet purchase can help criminals craft convincing phishing attacks or potentially target crypto holders in the real world.

My Take: Self-custody protects control over your crypto, but it cannot protect personal information leaked by a third-party service. Your security is only as strong as the weakest link connecting your digital assets to your real identity.

If you purchased from Keystone, verify alerts through official channels, ignore unsolicited refund or replacement offers, and never share your recovery phrase. No legitimate support agent needs it.

True crypto security means protecting both your assets and the personal information that could make you a target.

Should hardware wallet companies be held to stricter data-deletion standards after a customer's order is completed?

Disclaimer: This post is for educational purposes only and is not financial or security advice.

#CryptoSecurity #DataBreach #GrowWithSAC $QNT $ENA $PYTH
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number