

#electrumwalletbugletrogueserversstealfunds
electrumwalletbugletrogueserversstealfunds
Hot
Latest

#ElectrumWalletBugLetRogueServersStealFunds
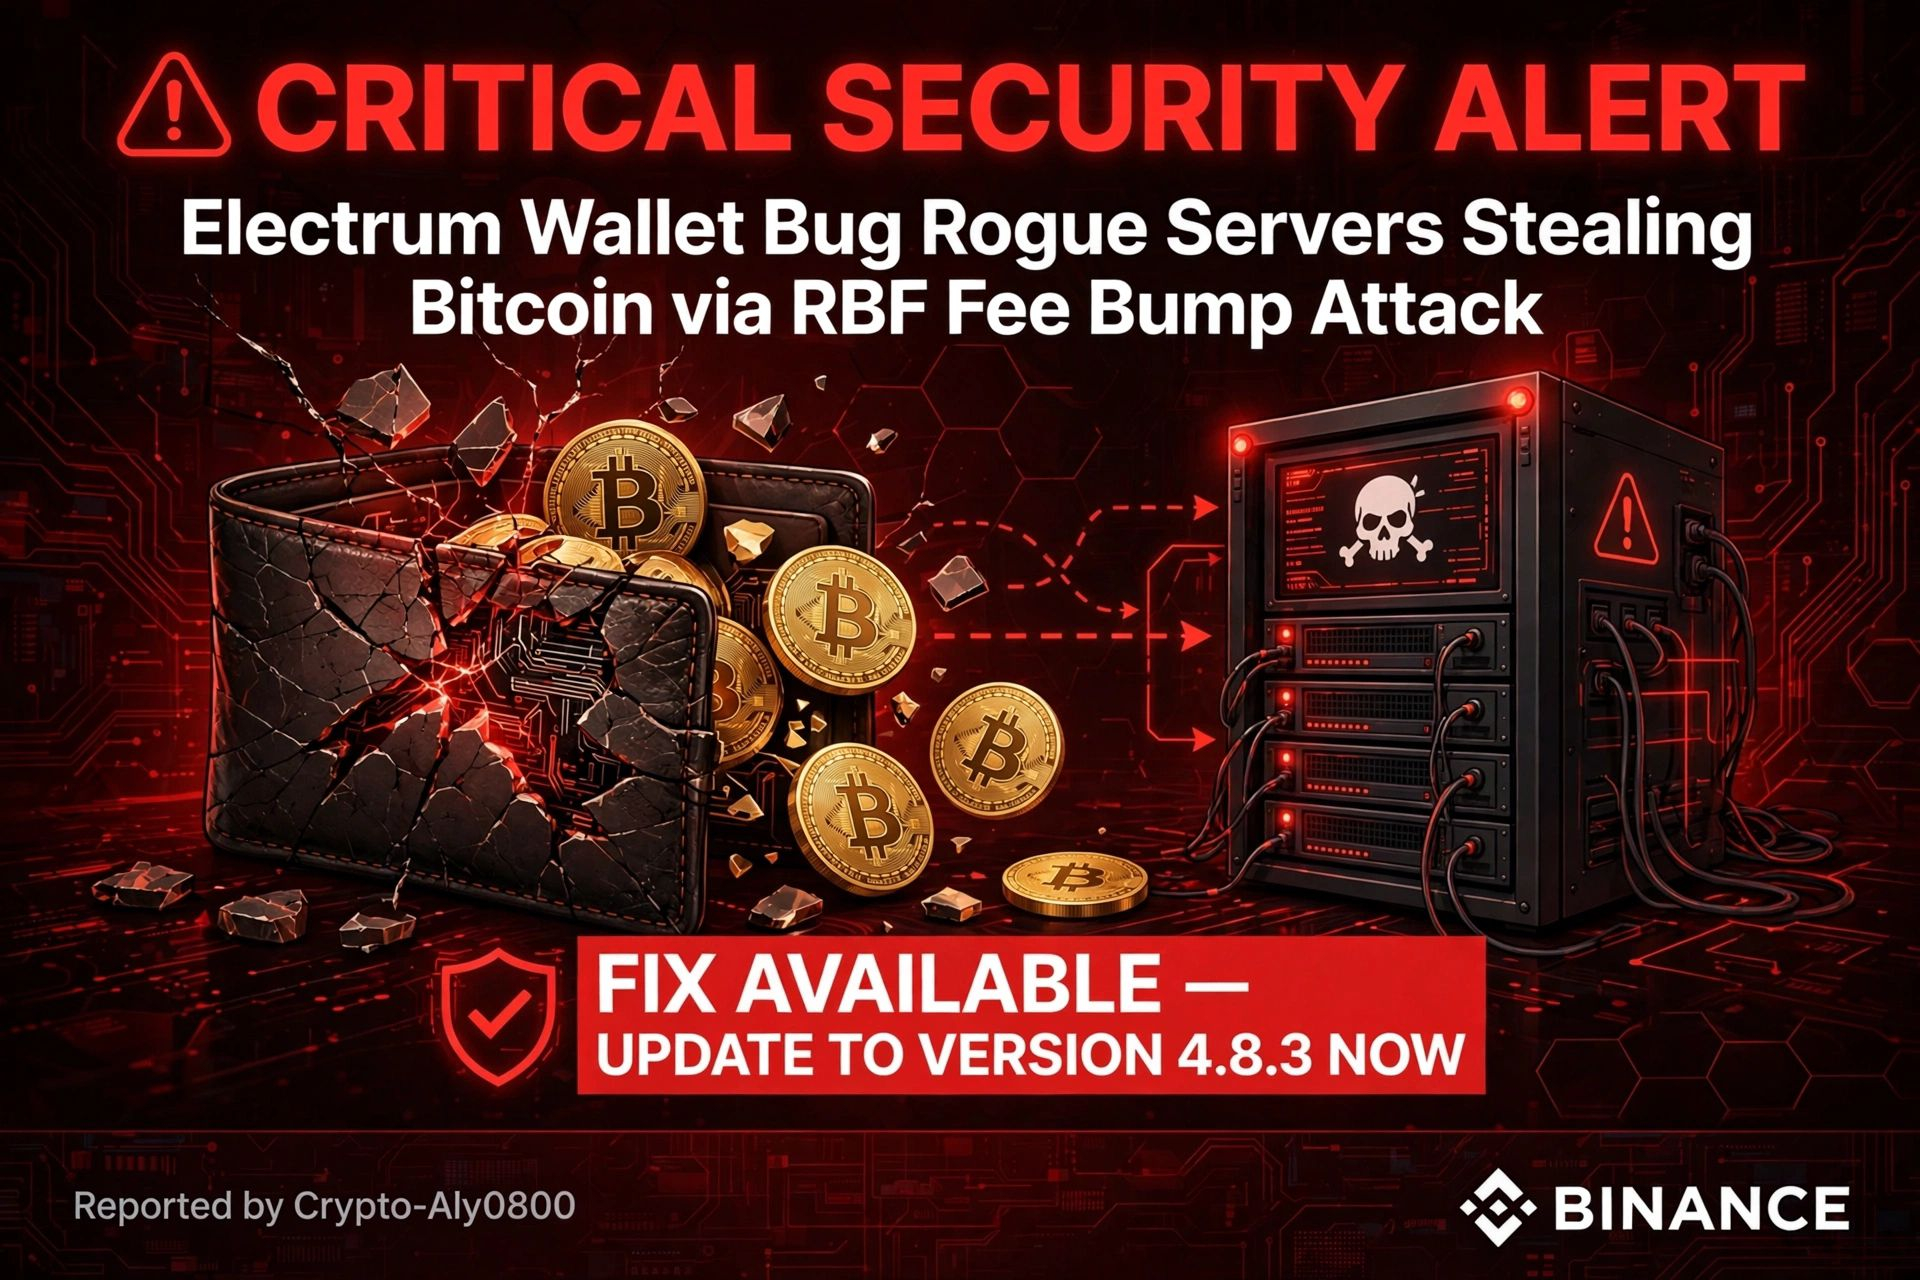
Important: Electrum Wallet has addressed a significant vulnerability that was already being exploited.
1. A user broadcasts a typical BTC transaction.
2. A malicious Electrum server intercepts the transaction and does not transmit it to the network.
3. The server inserts a fraudulent transaction in the wallet history, directing funds to the attacker's address with an invalid signature.
4. This fake transaction appears as "stuck" with a zero fee.
5. When the user attempts to expedite the transaction using Replace-By-Fee (RBF), they unintentionally sign the fraudulent transaction.
Attackers also employed lookalike addresses that matched the last four characters of the genuine destination, causing quick checks to fail.
Two cases reported in October.
One user confirmed the loss of funds following a fee increase.
One multisig user utilizing two Trezor devices identified the fake transaction in time. - All versions prior to 4.8.3 are vulnerable. - Version 4.8.3 introduces signature verification for unconfirmed spending transactions.
Download only from http://electrum.org
and verify the signature.
Connect only to trusted or self-hosted servers.
Always verify the full address and amount before signing any RBF.
Avoid rushing a fee increase.
This information is provided for educational purposes.
Please update your wallet.
#electrumwalletbug #BitcoinSecurity
36

·
--
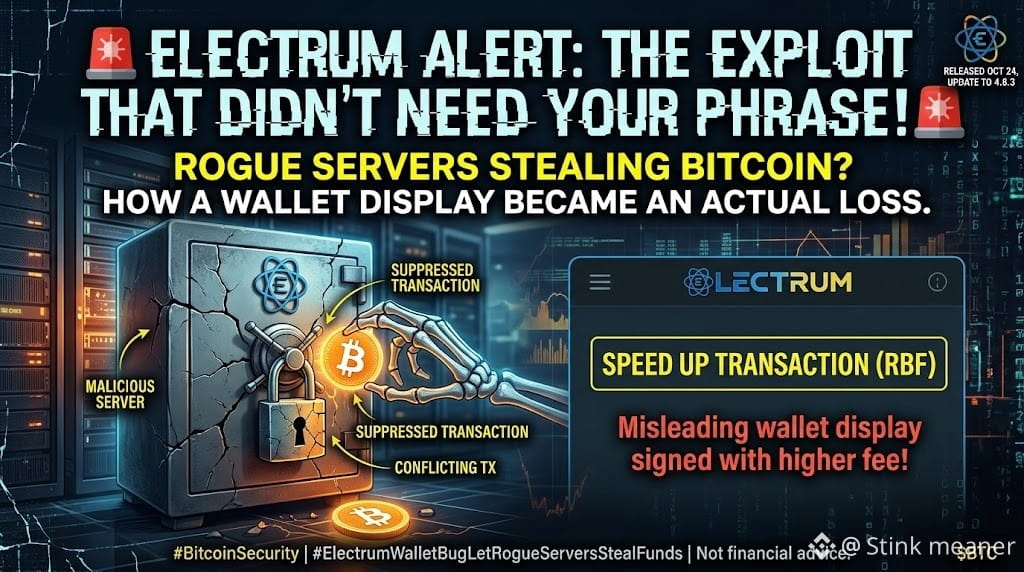
🚨 The Electrum exploit didn't require a stolen recovery phrase. It targeted users trying to speed up a Bitcoin transaction.
#electrumwalletbugletrogueserversstealfunds
Electrum disclosed a vulnerability affecting versions earlier than 4.8.3. The patched version was released on October 24.
Here's how the attack worked.
A malicious server could suppress a legitimate outgoing transaction and replace it in the wallet's history with a conflicting, invalid transaction directing funds to the attacker's address.
The transaction appeared pending. If the user tried to speed it up using Replace-by-Fee, Electrum could sign the replacement transaction with a higher fee—turning a misleading wallet display into an actual loss.
The developers received two reports. In one, a user lost funds after increasing the fee. The amount has not been disclosed.
This was not evidence that every Electrum user was exposed: the advisory says clients connected only to trusted servers, including their own, were not affected.
The immediate lesson is to update to version 4.8.3 or later and verify transaction addresses and amounts before signing, particularly when replacing an unconfirmed transaction.
Should users place more trust in wallet software—or in independent verification of every transaction they authorize?
DYOR: Not financial advice.
$BTC $DASH
{future}(BTCUSDT)
{future}(DASHUSDT)
#ElectrumWalletBugLetRogueServersStealFunds #ElectrumFixesHighRiskExploitInVersionsBefore4.8.3 #BitcoinSecurity #SAFU🙏
🚨 The Electrum exploit didn't require a stolen recovery phrase. It targeted users trying to speed up a Bitcoin transaction.
#electrumwalletbugletrogueserversstealfunds
Electrum disclosed a vulnerability affecting versions earlier than 4.8.3. The patched version was released on October 24.
Here's how the attack worked.
A malicious server could suppress a legitimate outgoing transaction and replace it in the wallet's history with a conflicting, invalid transaction directing funds to the attacker's address.
The transaction appeared pending. If the user tried to speed it up using Replace-by-Fee, Electrum could sign the replacement transaction with a higher fee—turning a misleading wallet display into an actual loss.
The developers received two reports. In one, a user lost funds after increasing the fee. The amount has not been disclosed.
This was not evidence that every Electrum user was exposed: the advisory says clients connected only to trusted servers, including their own, were not affected.
The immediate lesson is to update to version 4.8.3 or later and verify transaction addresses and amounts before signing, particularly when replacing an unconfirmed transaction.
Should users place more trust in wallet software—or in independent verification of every transaction they authorize?
DYOR: Not financial advice.
$BTC $DASH
#ElectrumWalletBugLetRogueServersStealFunds #ElectrumFixesHighRiskExploitInVersionsBefore4.8.3 #BitcoinSecurity #SAFU🙏
2
224
·
--
Bullish
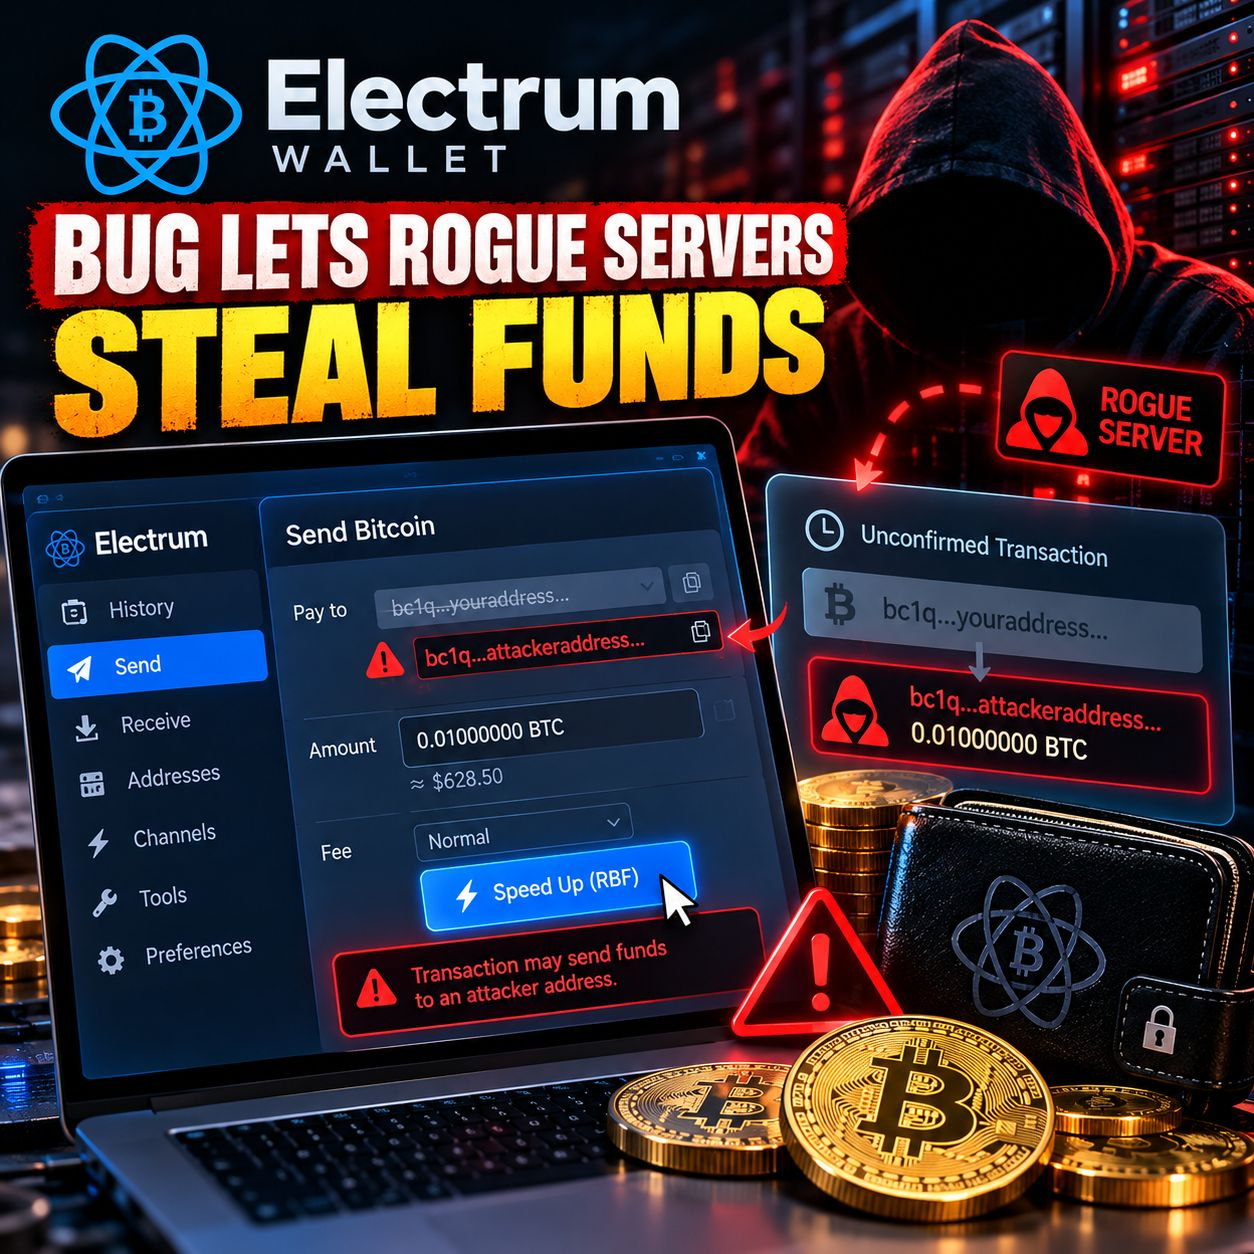
#electrumwalletbugletrogueserversstealfunds 🚨 Electrum Wallet Bug: A Routine Fee Increase Became a Bitcoin Theft Risk
A high-severity vulnerability in Electrum has exposed a critical weakness in how some Bitcoin transactions were handled. On October 24, developers released version 4.8.3 after reports that malicious servers were exploiting the flaw. At least one user confirmed losing funds.
Here’s how the attack worked:
⚠️ Rogue servers could hide a legitimate unconfirmed payment and display a fake transaction sending funds to an attacker. When users tried to speed up the supposedly stuck payment by increasing its fee, the vulnerable wallet could sign a replacement that transferred Bitcoin to the attacker.
The issue affected Electrum versions earlier than 4.8.3 when connected to malicious servers. Developers received two incident reports, including one involving an actual loss. The total amount stolen has not been disclosed.
🔐 What users should do:
• Update Electrum to version 4.8.3 or later, using the official Electrum website.
• Verify the complete recipient address and amount before signing any transaction.
• Double-check pending payments before using Replace-by-Fee (RBF).
• Consider connecting only to trusted servers, including your own.
This incident highlights an important self-custody lesson: even legitimate wallet software can face risks when it relies on external servers for unconfirmed transaction data.
Security is not just about protecting private keys. It also means checking what you authorize before signing.
Have you ever verified a transaction’s full address before increasing its fee? 🔎
#Bitcoin #ElectrumWallet #CryptoSecurity #BTC #BinanceSquareCreatorA
$ENA $REZ $BABY
{future}(BABYUSDT)
{future}(REZUSDT)
{future}(ENAUSDT)
#electrumwalletbugletrogueserversstealfunds 🚨 Electrum Wallet Bug: A Routine Fee Increase Became a Bitcoin Theft Risk
A high-severity vulnerability in Electrum has exposed a critical weakness in how some Bitcoin transactions were handled. On October 24, developers released version 4.8.3 after reports that malicious servers were exploiting the flaw. At least one user confirmed losing funds.
Here’s how the attack worked:
⚠️ Rogue servers could hide a legitimate unconfirmed payment and display a fake transaction sending funds to an attacker. When users tried to speed up the supposedly stuck payment by increasing its fee, the vulnerable wallet could sign a replacement that transferred Bitcoin to the attacker.
The issue affected Electrum versions earlier than 4.8.3 when connected to malicious servers. Developers received two incident reports, including one involving an actual loss. The total amount stolen has not been disclosed.
🔐 What users should do:
• Update Electrum to version 4.8.3 or later, using the official Electrum website.
• Verify the complete recipient address and amount before signing any transaction.
• Double-check pending payments before using Replace-by-Fee (RBF).
• Consider connecting only to trusted servers, including your own.
This incident highlights an important self-custody lesson: even legitimate wallet software can face risks when it relies on external servers for unconfirmed transaction data.
Security is not just about protecting private keys. It also means checking what you authorize before signing.
Have you ever verified a transaction’s full address before increasing its fee? 🔎
#Bitcoin #ElectrumWallet #CryptoSecurity #BTC #BinanceSquareCreatorA
$ENA $REZ $BABY
207
·
--
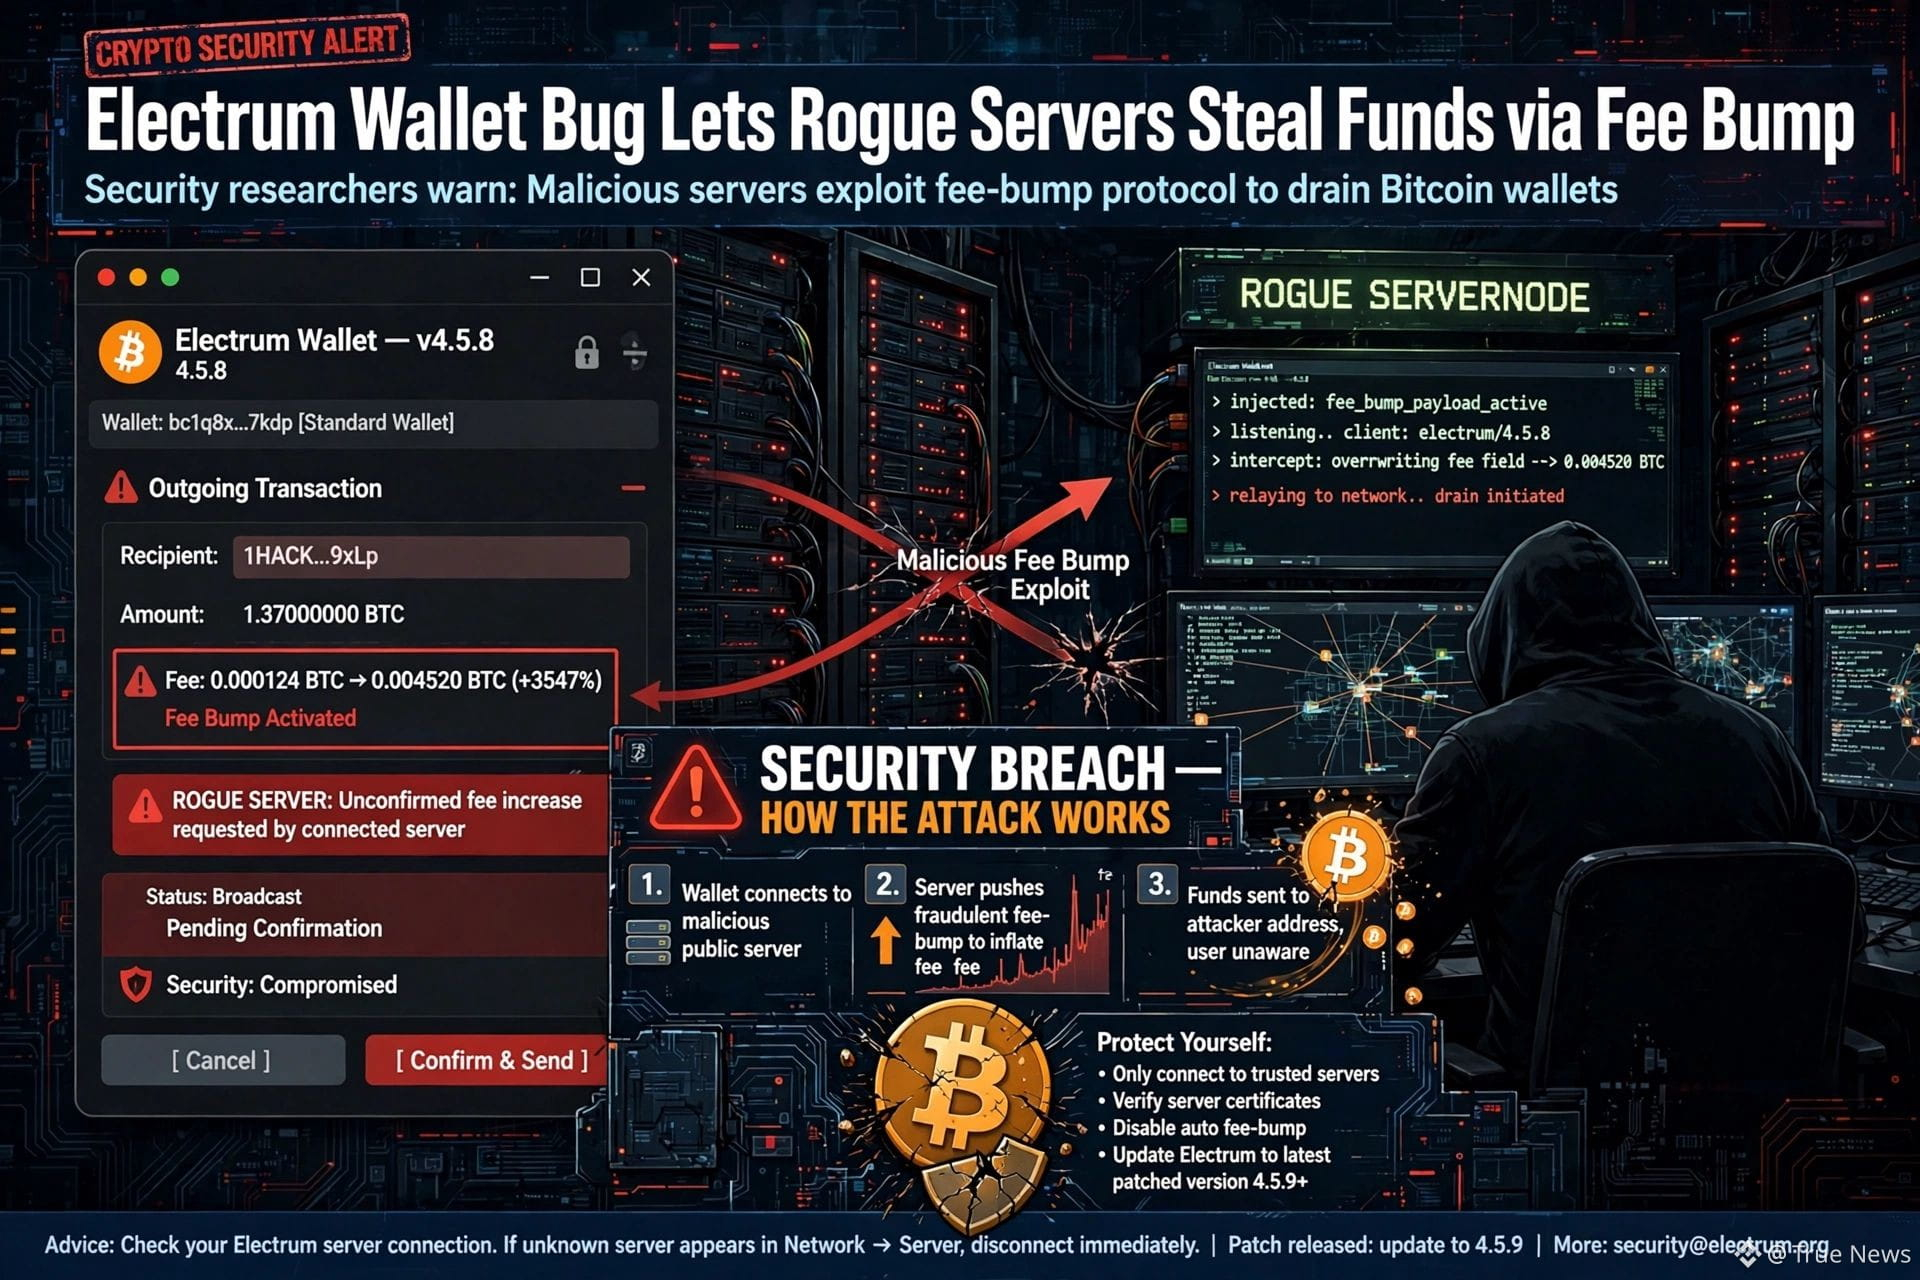
🚨 ELECTRUM WALLET BUG LETS ROGUE SERVERS STEAL FUNDS! 🚨
Critical security alert! Electrum, one of Bitcoin's oldest wallets, disclosed on Oct 24 a high-severity bug where malicious ElectrumX servers could trick users into signing payments to attackers when they tried to speed up payments via fee bump.
How? When you tried to increase fee for unconfirmed transaction, rogue server would swap your real payment with a fake one with invalid signatures, but wallet showed it as normal. Once you approved fee bump, funds went to attacker. At least one user lost funds in October.
Fix is live: Update to Electrum v4.8.3 released Oct 24, 2026 which adds signature verification. Always verify downloads from electrum.org, compare full destination addresses, and prefer trusted or self-hosted servers. Only connect to servers you run yourself to stay safe.
Related: $BTC $ETH $SOL are affected as Electrum is mainly Bitcoin wallet but phishing risk spreads.
#ElectrumBug #BitcoinSecurity #CryptoHack #WalletSecurity #BinanceSquare#electrumwalletbugletrogueserversstealfunds
2
872

·
--
Bearish
would you hit "speed up" on a $BTC
{future}(BTCUSDT)
payment stuck at zero fee?
I would have. that's the whole Electrum attack
the setup, per Electrum's advisory:
a malicious server swallows the transaction you just broadcast and never lets it reach the network
then shows your wallet a conflicting fake, outputs redirected to the attacker
the fake's signatures are invalid. as a light client, Electrum doesn't check them
on its own the fake does nothing
the theft is your Replace-by-Fee bump: Electrum signs a valid replacement with a higher fee, paying the attacker
nice touch: in both reported cases the fake address matched the last four characters of the real one 🙃
the amount stolen isn't disclosed. the lesson is free: read the whole address, most of all when you're in a hurry
#ElectrumWalletBugLetRogueServersStealFunds
would you hit "speed up" on a $BTC
payment stuck at zero fee?
I would have. that's the whole Electrum attack
the setup, per Electrum's advisory:
a malicious server swallows the transaction you just broadcast and never lets it reach the network
then shows your wallet a conflicting fake, outputs redirected to the attacker
the fake's signatures are invalid. as a light client, Electrum doesn't check them
on its own the fake does nothing
the theft is your Replace-by-Fee bump: Electrum signs a valid replacement with a higher fee, paying the attacker
nice touch: in both reported cases the fake address matched the last four characters of the real one 🙃
the amount stolen isn't disclosed. the lesson is free: read the whole address, most of all when you're in a hurry
#ElectrumWalletBugLetRogueServersStealFunds
22
·
--
🚨 BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN USERS AT RISK!
#ElectrumWalletBugLetRogueServersStealFunds
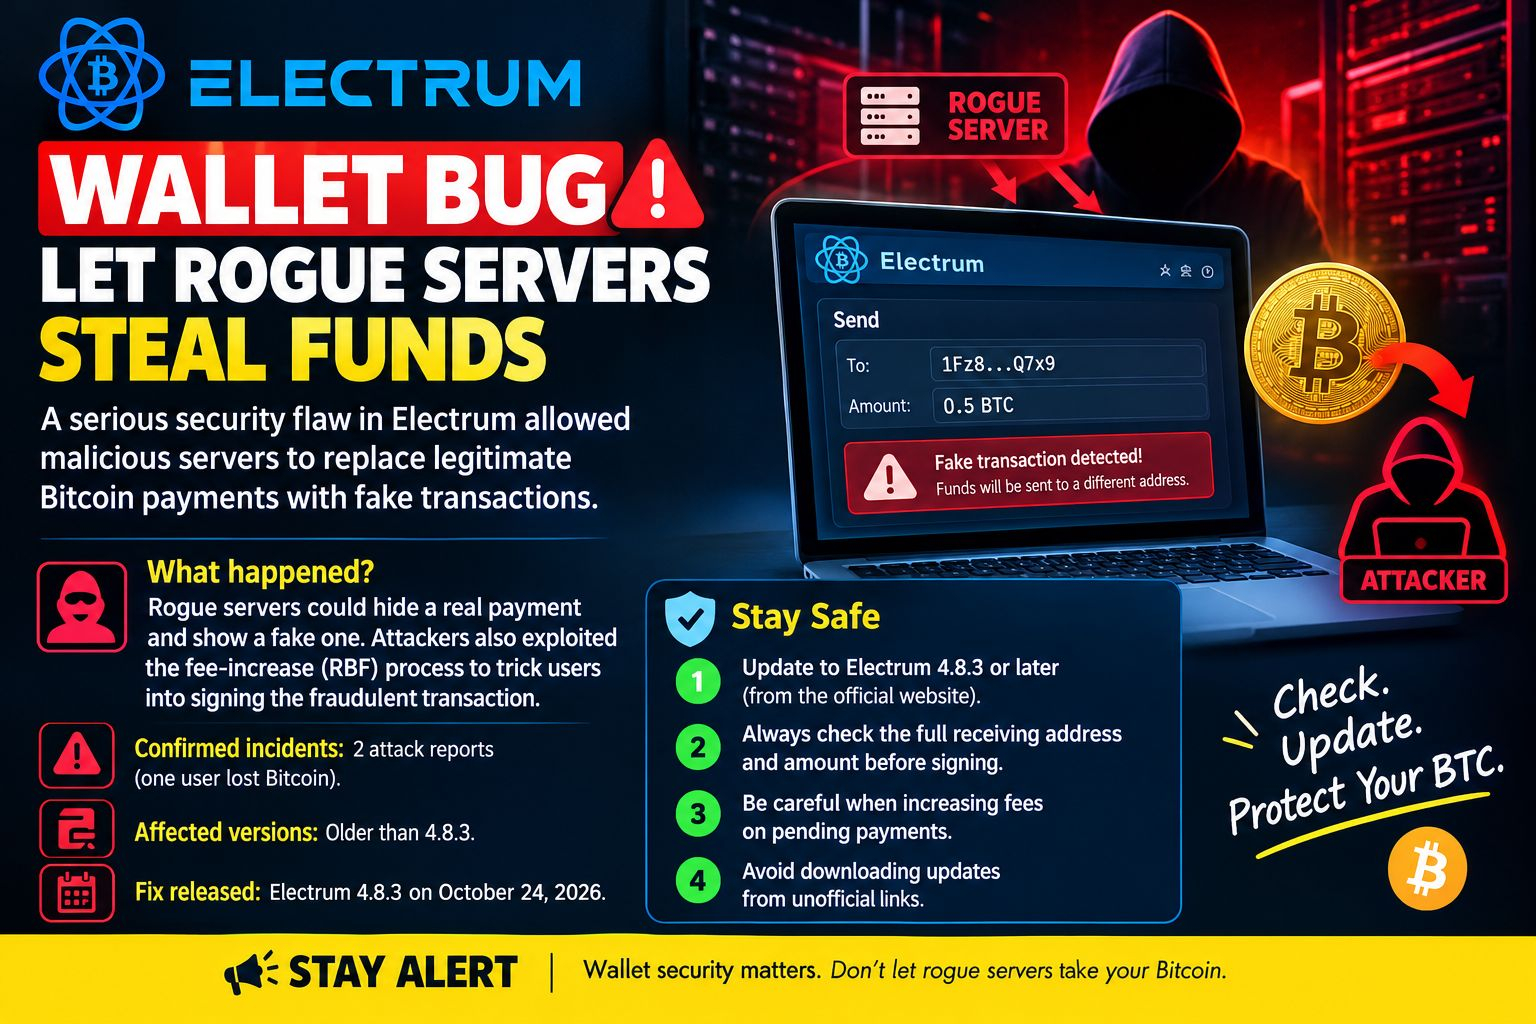
A serious security flaw in Electrum allowed malicious servers to replace legitimate Bitcoin payments with fake transactions.
⚠️ Attackers exploited the fee-increase process to trick users into signing transactions that sent$BTC to the wrong address.
🔴 Key updates:
• Versions before Electrum 4.8.3 are affected.
• Two attack reports have been received.
• At least one user reportedly lost Bitcoin.
• The developers released version 4.8.3 on October 24, 2026.
🛡️ Protect your$BTC : Update your wallet and always verify the complete recipient address before signing any transaction.
💬 Are wallet security risks becoming a bigger concern for crypto users? Share your thoughts below!
#Bitcoin #BTC #BitcoinETFs
{spot}(BTCUSDT)
🚨 BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN USERS AT RISK!
#ElectrumWalletBugLetRogueServersStealFunds
A serious security flaw in Electrum allowed malicious servers to replace legitimate Bitcoin payments with fake transactions.
⚠️ Attackers exploited the fee-increase process to trick users into signing transactions that sent$BTC to the wrong address.
🔴 Key updates:
• Versions before Electrum 4.8.3 are affected.
• Two attack reports have been received.
• At least one user reportedly lost Bitcoin.
• The developers released version 4.8.3 on October 24, 2026.
🛡️ Protect your$BTC : Update your wallet and always verify the complete recipient address before signing any transaction.
💬 Are wallet security risks becoming a bigger concern for crypto users? Share your thoughts below!
#Bitcoin #BTC #BitcoinETFs
99
·
--
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
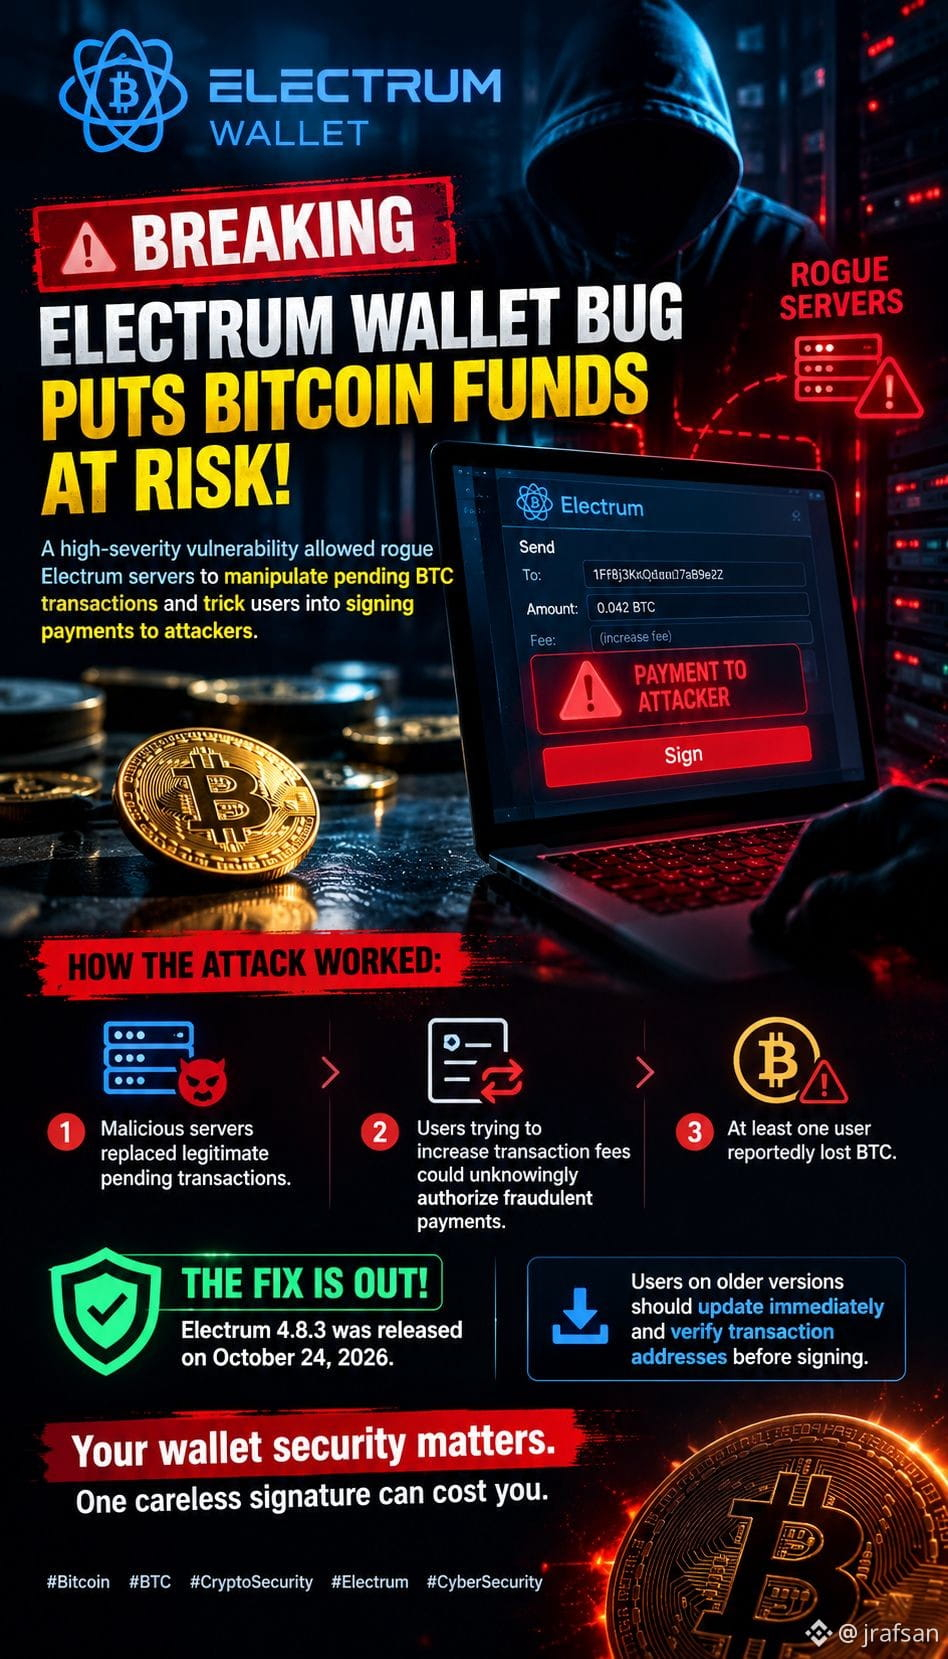
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
{future}(TRUMPUSDT)
$TRX
{future}(TRXUSDT)
$XRP
{future}(XRPUSDT)
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
$TRX
$XRP
168

A critical bug in the Electrum Bitcoin wallet has been exploited by malicious servers, leading to the theft of user funds. This vulnerability allowed attackers to trick users into downloading malicious versions of the wallet or revealing sensitive information. The exploit highlights the ongoing cat-and-mouse game between security researchers and malicious actors in the crypto space. Users are strongly advised to ensure they are running the latest, legitimate version of Electrum and to be extremely cautious about any prompts or requests for private keys or seed phrases. This incident underscores the importance of robust security practices and staying informed about potential threats within the cryptocurrency ecosystem.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#ElectrumWalletBugLetRogueServersStealFunds $BTC
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#ElectrumWalletBugLetRogueServersStealFunds $BTC
50

·
--
Bullish
#ElectrumWalletBugLetRogueServersStealFunds
🚨 URGENT SECURITY ALERT: #ElectrumWalletBug 🚨
A critical security flaw associated with #ElectrumWalletBugLetRogueServersStealFunds has been highlighted. Malicious or rogue Electrum servers can exploit communication vulnerabilities to manipulate transaction prompts and potentially drain user funds!
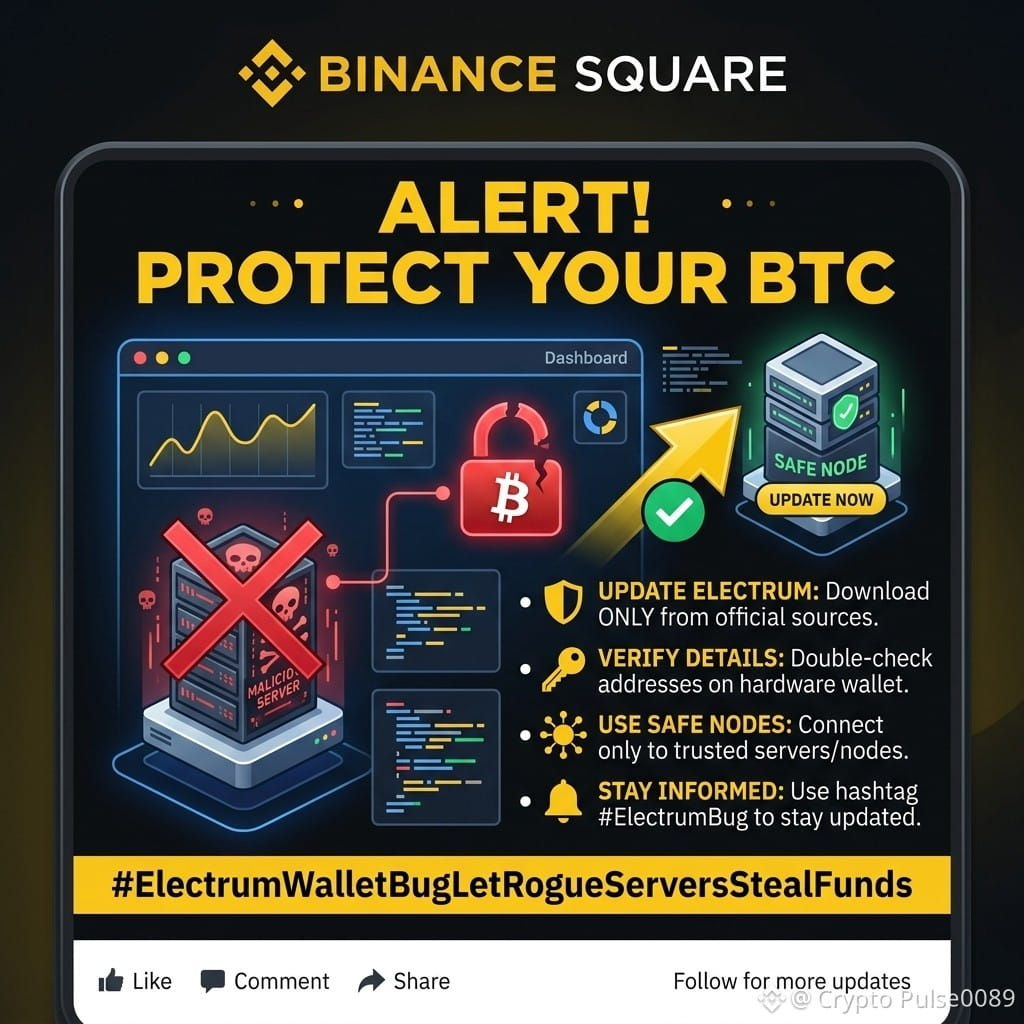
If you are using the Electrum Bitcoin wallet, protect your assets by following these steps immediately:
⚠️ WHAT YOU NEED TO DO NOW:
Update Your Wallet: Ensure you are using the latest official version of Electrum downloaded strictly from the official site (electrum.org).
Avoid Unknown Servers: Do not connect to unverified public servers.
Run Your Own Node/Server: If possible, connect Electrum to your own private backend (like Electrum Personal Server or ElectrumX).
Verify on Hardware: Always double-check recipient addresses on your hardware wallet screen before confirming any transaction.
Spread Awareness: Share this alert to protect the community!
🛡️ Stay safe, stay secure, and double-check your connections!
#CryptoSecurity #Bitcoin #Electrum #BTC #CryptoSafety #WalletSecurity
$AMZNB $TSLAB $SQQQB
40
·
--
#ElectrumWalletBugLetRogueServersStealFunds
🚨 Electrum just patched a high-severity flaw that let malicious servers steal $BTC .
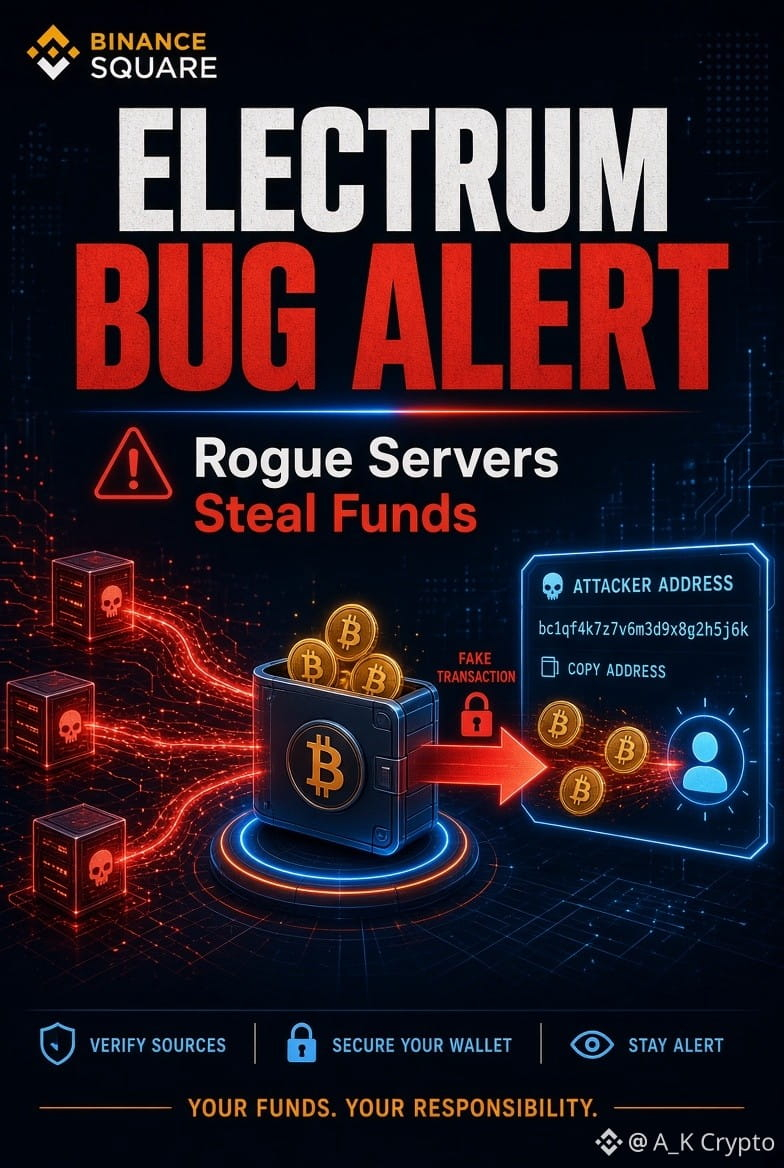
Rogue Electrum servers intercepted just-broadcast transactions and swapped them with fake ones (often zero-fee) sending funds to lookalike addresses. When users tried to speed things up with Replace-by-Fee, they unknowingly signed the attacker’s transaction.
At least two cases reported in October — one user lost funds. Electrum released v4.8.3 on Oct 24 that now verifies signatures on unconfirmed transactions. Update immediately if you’re still on an older version.
This is a classic reminder that light clients trade convenience for trust. Relying on random public servers is a silent risk. Always verify the full recipient address and amount before signing anything — especially fee bumps. Running your own server or using hardware wallets with careful checks remains the safer path. Security is never “set and forget” in $BTC .
Stay sharp, update now, and double-check every detail.
#Bitcoin #Electrum #CryptoSecurity #SelfCustody
{spot}(BTCUSDT)
#ElectrumWalletBugLetRogueServersStealFunds
🚨 Electrum just patched a high-severity flaw that let malicious servers steal $BTC .
Rogue Electrum servers intercepted just-broadcast transactions and swapped them with fake ones (often zero-fee) sending funds to lookalike addresses. When users tried to speed things up with Replace-by-Fee, they unknowingly signed the attacker’s transaction.
At least two cases reported in October — one user lost funds. Electrum released v4.8.3 on Oct 24 that now verifies signatures on unconfirmed transactions. Update immediately if you’re still on an older version.
This is a classic reminder that light clients trade convenience for trust. Relying on random public servers is a silent risk. Always verify the full recipient address and amount before signing anything — especially fee bumps. Running your own server or using hardware wallets with careful checks remains the safer path. Security is never “set and forget” in $BTC .
Stay sharp, update now, and double-check every detail.
#Bitcoin #Electrum #CryptoSecurity #SelfCustody
99
#ElectrumWalletBugLetRogueServersStealFunds
A security vulnerability in Electrum Wallet could allow rogue servers to trick users and steal their crypto assets.
Keep your wallet updated, avoid suspicious server connections, and never approve unexpected payment requests. #SAFU🙏
In crypto, protecting your wallet is just as important as protecting your private keys !
#Mahanadi 🔐
I had convert to $IOTA , details below.

Like Share 💛 💛
From Digital Mahanadi
82

·
--
#ElectrumWalletBugLetRogueServersStealFunds
🪤 The Electrum Trap Was Hidden in the "Speed Up" Button
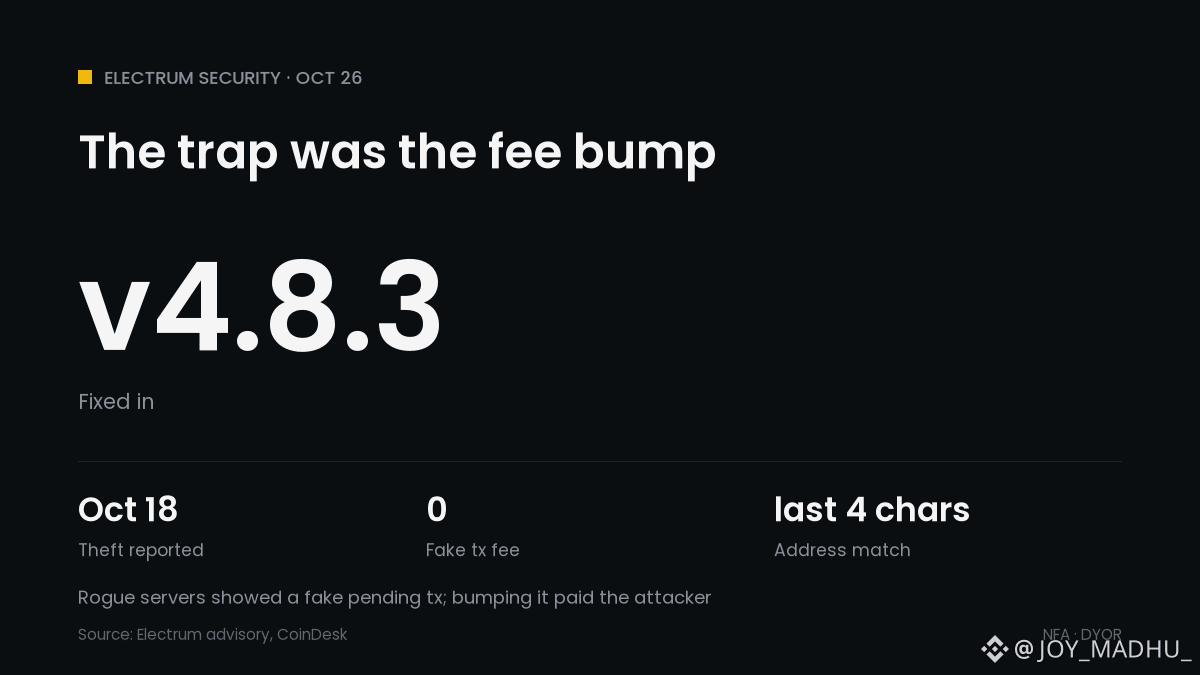
📅 Oct 11: first report. A multisig user verified on two Trezors, then saw a different tx in history
💸 Oct 18: a second user raised the fee on a fake pending tx and lost funds
🕵️ The rogue server held the real tx and showed a zero-fee fake, so it looked stuck
🔤 The attacker's address matched the last 4 characters of the real one
🛡️ Oct 24: Electrum 4.8.3 now checks signatures on pending txs spending your coins
⚠️ Incoming pending txs still aren't validated. Self-run servers were not exposed
What it means for crypto: no flaw in $BTC itself, but a hardware wallet can't protect a fee bump you approve without rechecking. BTC is near $80.2K.
Do you recheck the full address before every fee bump? 👇
$BTC
#ElectrumWalletBugLetRogueServersStealFunds #CryptoNews #Bitcoin #WalletSecurity
34
·
--
#ElectrumWalletBugLetRogueServersStealFunds
Electrum Wallet Security Alert: A Fee Increase Could Put Your BTC at Risk ⚠️
A serious security flaw in Electrum exposed Bitcoin users to malicious servers that could manipulate pending transactions.
Here’s how the attack worked: a rogue server could replace a legitimate pending payment with a fake transaction directing funds to an attacker. If the user then tried to speed up the payment by increasing its fee, the wallet could sign the fraudulent replacement.
Electrum developers confirmed reports of the attack, including at least one case of lost funds. The good news: Electrum 4.8.3, released on October 24, fixes this specific vulnerability.
My takeaway: update your wallet, download updates only from the official Electrum website, and carefully verify the full recipient address and amount before signing any transaction or fee increase.
In crypto, security is not just about protecting private keys. It’s also about checking what you are actually authorizing.
Do you check the full transaction details before approving a Bitcoin fee increase?
#Bitcoin #BTC #CryptoSecurity
1
130
·
--
Bullish
#electrumwalletbugletrogueserversstealfunds 🚨 Electrum Wallet Bug: A Fee Increase Could Put BTC at Risk
A Bitcoin wallet security incident highlights an important lesson: even routine transaction management can carry risks when software relies on external servers.
Electrum developers disclosed a high-severity vulnerability affecting versions earlier than 4.8.3. Malicious servers could hide a legitimate unconfirmed payment and display a fake transaction directing funds to an attacker. If users tried to speed it up using Replace-by-Fee (RBF), they could unknowingly sign a valid replacement that sent BTC to the wrong address.
According to the official security advisory, two incidents were reported, including one confirmed loss. The total amount stolen has not been disclosed.
🔎 What matters for users?
• Update Electrum to version 4.8.3 or later when available.
• Verify the complete recipient address and amount before signing any transaction or fee increase.
• Avoid trusting a transaction merely because it appears in your wallet history.
• Download wallet updates only from the official Electrum website and verify signatures where possible.
This was not a Bitcoin blockchain failure. The vulnerability involved how affected wallet versions handled unconfirmed transactions received from servers.
📊 My market perspective: Security incidents can affect confidence in individual wallet providers, but they do not automatically indicate a weakness in Bitcoin itself. Price impact depends on the scale of losses, user response, and broader market conditions.
Self-custody means controlling your assets, but it also means taking software security seriously.
Have you updated your wallet security practices recently?
#Bitcoin #Electrum #CryptoSecurity #BTC #CryptoNews
$ENA $REZ $BABY
{future}(BABYUSDT)
{future}(REZUSDT)
{future}(ENAUSDT)
#electrumwalletbugletrogueserversstealfunds 🚨 Electrum Wallet Bug: A Fee Increase Could Put BTC at Risk
A Bitcoin wallet security incident highlights an important lesson: even routine transaction management can carry risks when software relies on external servers.
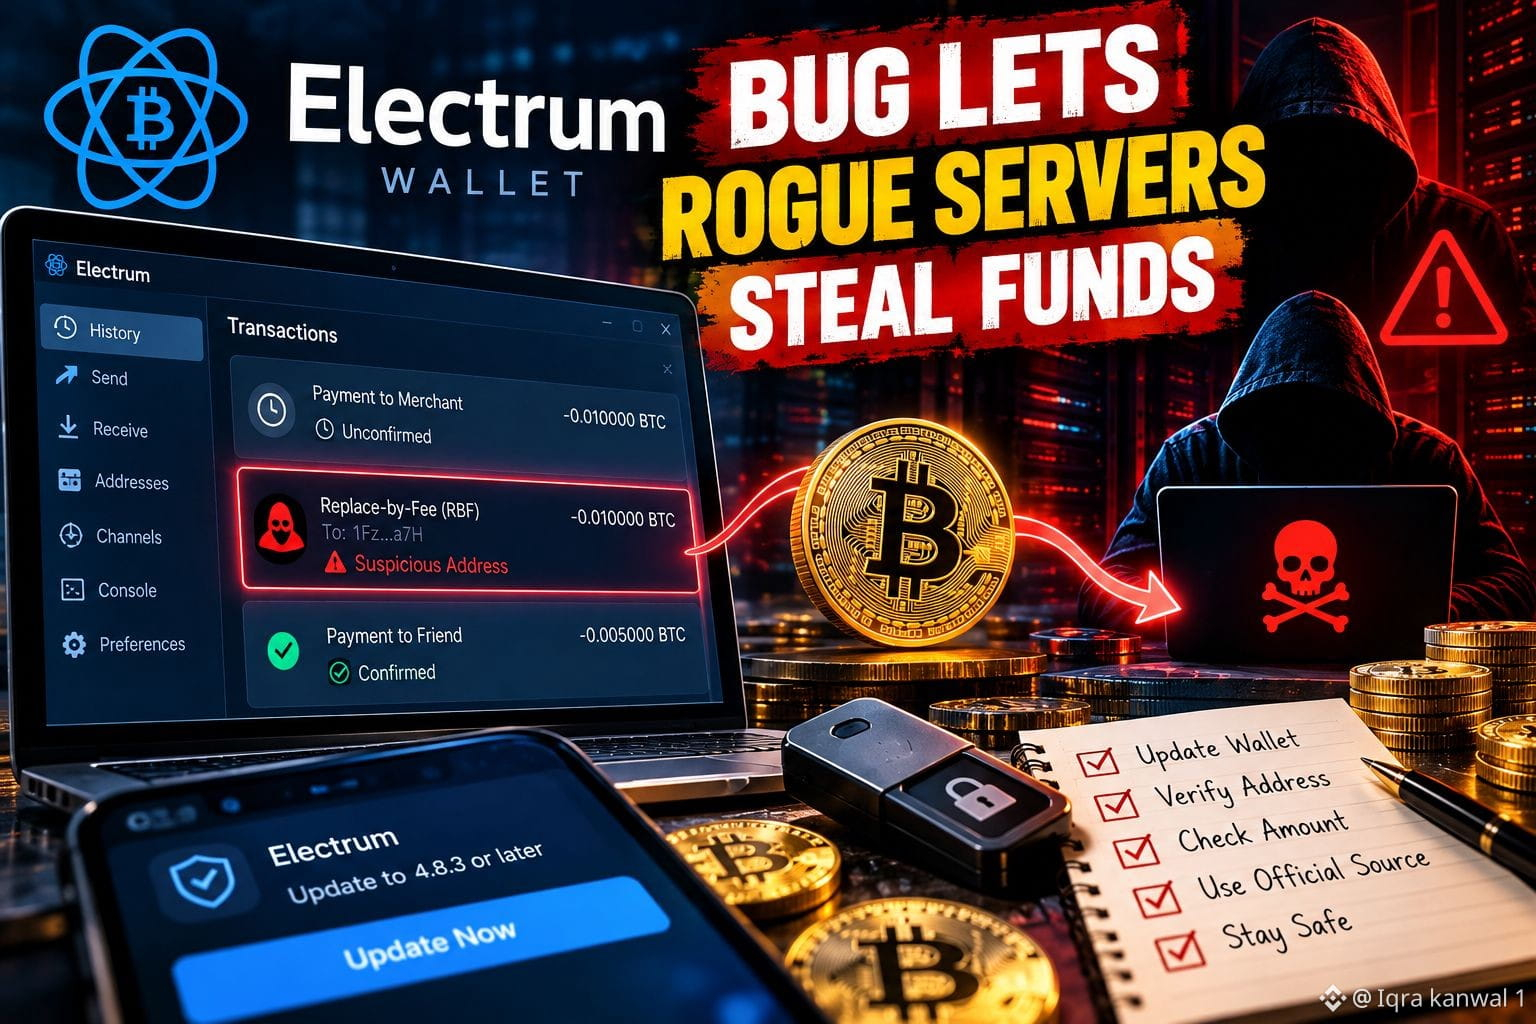
Electrum developers disclosed a high-severity vulnerability affecting versions earlier than 4.8.3. Malicious servers could hide a legitimate unconfirmed payment and display a fake transaction directing funds to an attacker. If users tried to speed it up using Replace-by-Fee (RBF), they could unknowingly sign a valid replacement that sent BTC to the wrong address.
According to the official security advisory, two incidents were reported, including one confirmed loss. The total amount stolen has not been disclosed.
🔎 What matters for users?
• Update Electrum to version 4.8.3 or later when available.
• Verify the complete recipient address and amount before signing any transaction or fee increase.
• Avoid trusting a transaction merely because it appears in your wallet history.
• Download wallet updates only from the official Electrum website and verify signatures where possible.
This was not a Bitcoin blockchain failure. The vulnerability involved how affected wallet versions handled unconfirmed transactions received from servers.
📊 My market perspective: Security incidents can affect confidence in individual wallet providers, but they do not automatically indicate a weakness in Bitcoin itself. Price impact depends on the scale of losses, user response, and broader market conditions.
Self-custody means controlling your assets, but it also means taking software security seriously.
Have you updated your wallet security practices recently?
#Bitcoin #Electrum #CryptoSecurity #BTC #CryptoNews
$ENA $REZ $BABY
1
259
·
--
Bullish
Trying to speed up Bitcoin, but ended up losing your assets! 🤦♂️
Here we go again with another security drama, folks. Vulnerability #electrumwalletbugletrogueserversstealfunds has now hit Electrum wallets. Here’s what happens: when you use the Replace-by-Fee feature to increase the fee and “race the clock” for a faster transaction, rogue servers can quickly swap the original transaction for a fake payment. The result? You blindly approve and sign—and just like that, your money goes straight to the attacker!
What can traders do to avoid being the “fool” here?
1. Update your Electrum wallet to version 4.8.3 now to enable signature verification.
2. Carefully check the address and amount before signing.
3. Connect only to trusted servers, or run your own node to be safe.
⚠️ This is not financial advice! Want to stay safe and avoid the traps? Sign up for a new account now at this link: [https://www.binance.com/register?ref=VINHTOCDO](https://www.binance.com/register?ref=VINHTOCDO) (Referral code: VINHTOCDO) so we can learn from each other!
Click the transactions below to support me:
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
$BNB
{spot}(BNBUSDT)
#VINHTOCDO #bitcoin #CryptoSafety #ElectrumWallet #CryptoSecurity
Trying to speed up Bitcoin, but ended up losing your assets! 🤦♂️
Here we go again with another security drama, folks. Vulnerability #electrumwalletbugletrogueserversstealfunds has now hit Electrum wallets. Here’s what happens: when you use the Replace-by-Fee feature to increase the fee and “race the clock” for a faster transaction, rogue servers can quickly swap the original transaction for a fake payment. The result? You blindly approve and sign—and just like that, your money goes straight to the attacker!
What can traders do to avoid being the “fool” here?
1. Update your Electrum wallet to version 4.8.3 now to enable signature verification.
2. Carefully check the address and amount before signing.
3. Connect only to trusted servers, or run your own node to be safe.
⚠️ This is not financial advice! Want to stay safe and avoid the traps? Sign up for a new account now at this link: https://www.binance.com/register?ref=VINHTOCDO (Referral code: VINHTOCDO) so we can learn from each other!
Click the transactions below to support me:
$BTC
$ETH
$BNB
#VINHTOCDO #bitcoin #CryptoSafety #ElectrumWallet #CryptoSecurity
2
109

Article
Following the release of Electrum version 4.8.3, mandatory instructions have been established⚠️#electrumwalletbugletrogueserversstealfunds ⚠️ Obfuscation Tactic: To prevent the change of destination from being noticed at a glance during quick checks on small screens, the attackers used computer tools to pregenerate millions of mass-target wallets until they found addresses whose last four characters exactly matched those of the real recipient's original address
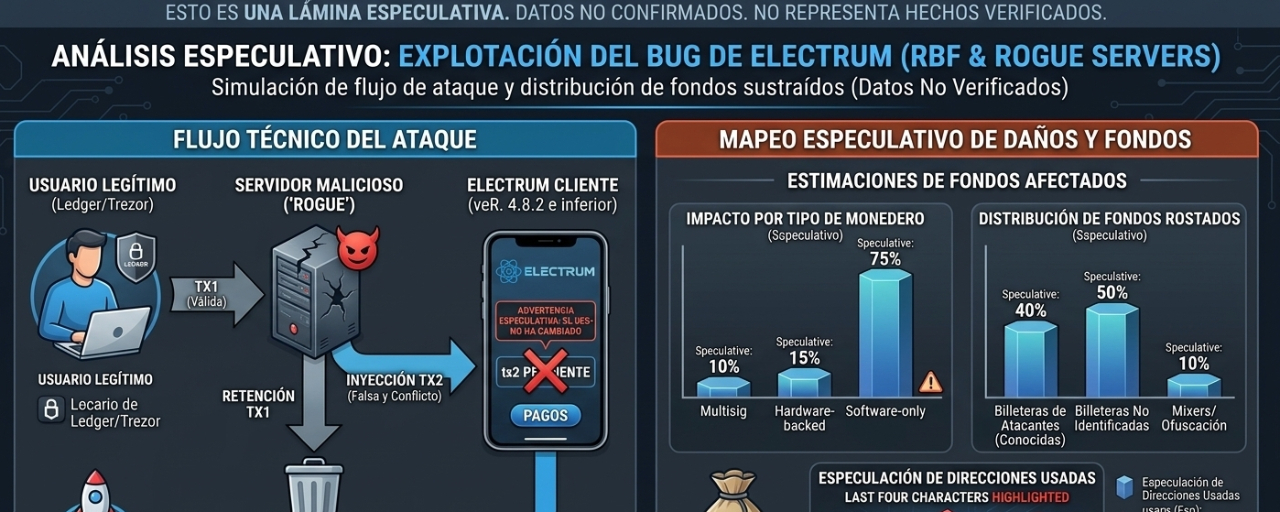
The generated visual panel presents a digital forensics and technical analysis infographic illustrating, in a simulated and speculative manner, how the exploit that affected older versions of the Electrum Bitcoin wallet worked
Following the release of Electrum version 4.8.3, mandatory instructions have been established
⚠️#electrumwalletbugletrogueserversstealfunds ⚠️ Obfuscation Tactic: To prevent the change of destination from being noticed at a glance during quick checks on small screens, the attackers used computer tools to pregenerate millions of mass-target wallets until they found addresses whose last four characters exactly matched those of the real recipient's original address
The generated visual panel presents a digital forensics and technical analysis infographic illustrating, in a simulated and speculative manner, how the exploit that affected older versions of the Electrum Bitcoin wallet worked
The generated visual panel presents a digital forensics and technical analysis infographic illustrating, in a simulated and speculative manner, how the exploit that affected older versions of the Electrum Bitcoin wallet worked
1
107
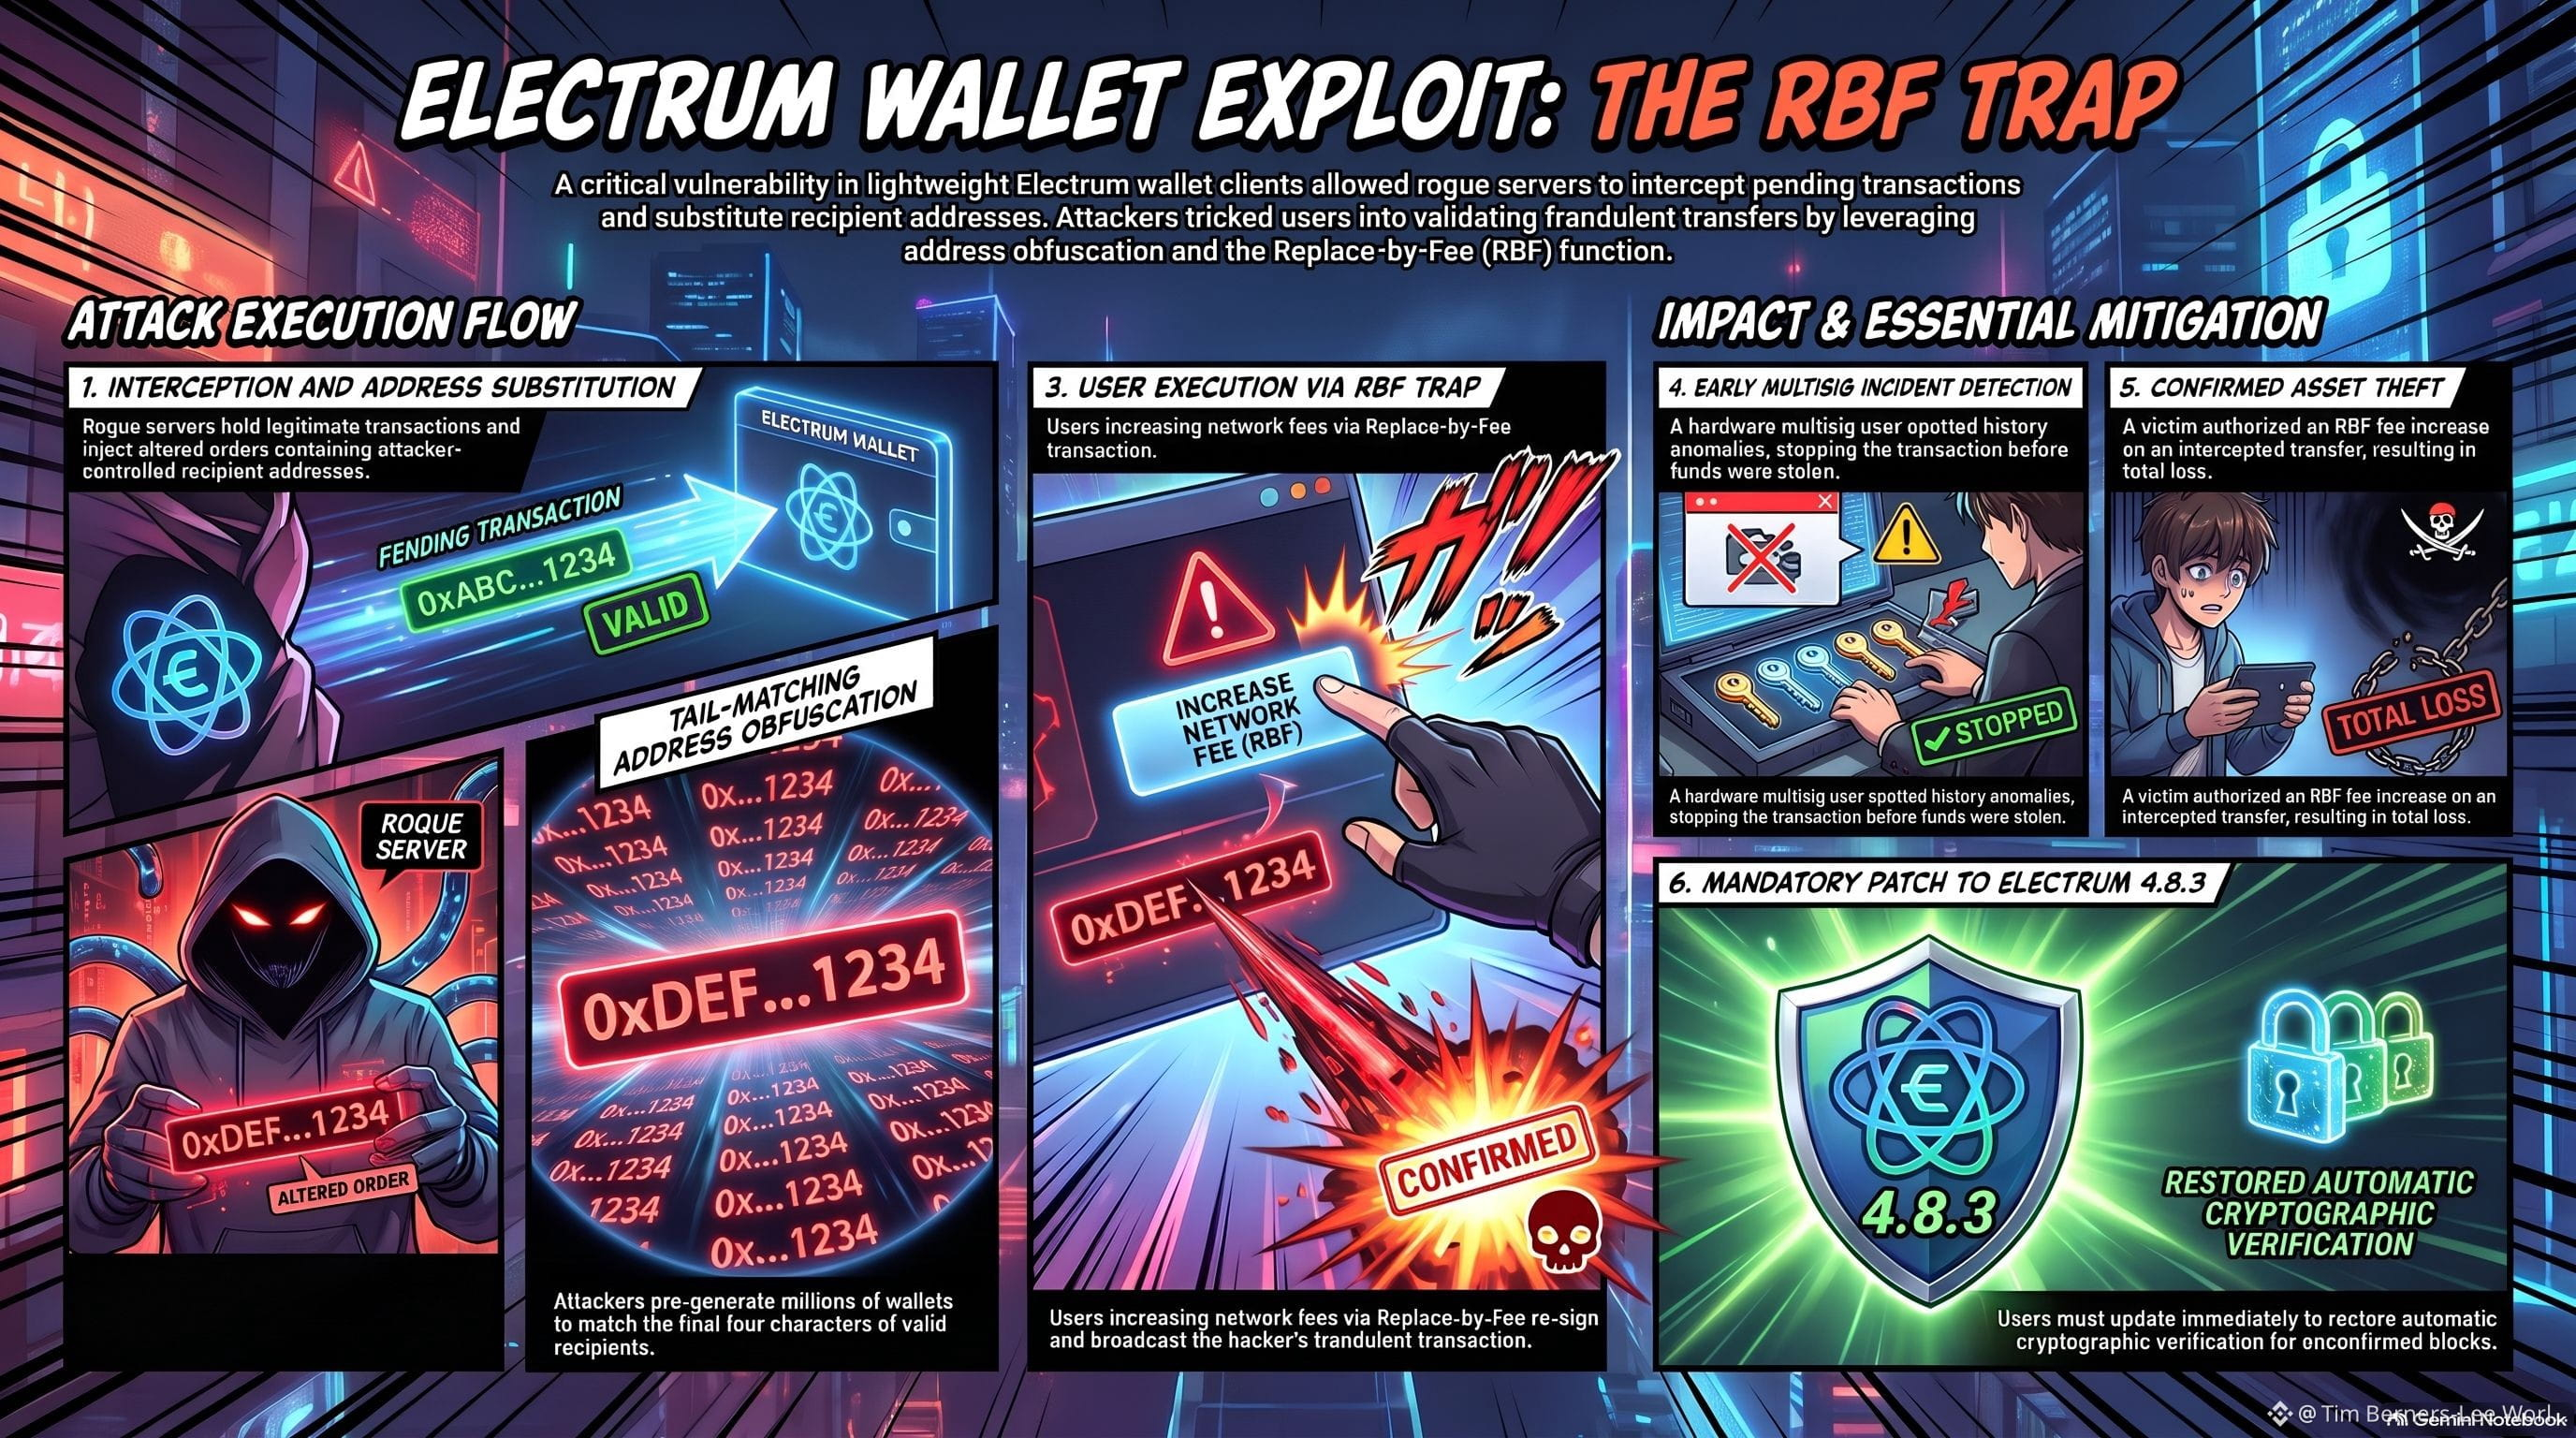
⚠️Following the release of Electrum version 4.8.3, mandatory instructions have been established to safeguard holders’ digital assets⚠️
⚠️#electrumwalletbugletrogueserversstealfunds ⚠️1. Trap Activation via RBF: When a transaction appears to be delayed, the user naturally turns to the built-in Replace-by-Fee (RBF) feature to increase the network fee and speed up processing. ⚠️When this button is pressed, the wallet software reads the modified data (tx2), rebuilds the structure, calculates the new fee, and asks the user for a final signature. The moment the victim approves the fee increase using their private keys or hardware wallet, they effectively authorize the hacker’s address and propagate the irreversible theft to the blockchain, The Defiant reports.
⚠️ Obfuscation Tactic: To prevent the change of destination from being noticed at a glance during quick checks on small screens, ⚠️the attackers used computer tools to pregenerate millions of destination wallets until they found addresses whose last four characters matched exactly those of the original address of the intended recipient
2
174
·
--
#electrumwalletbugletrogueserversstealfunds
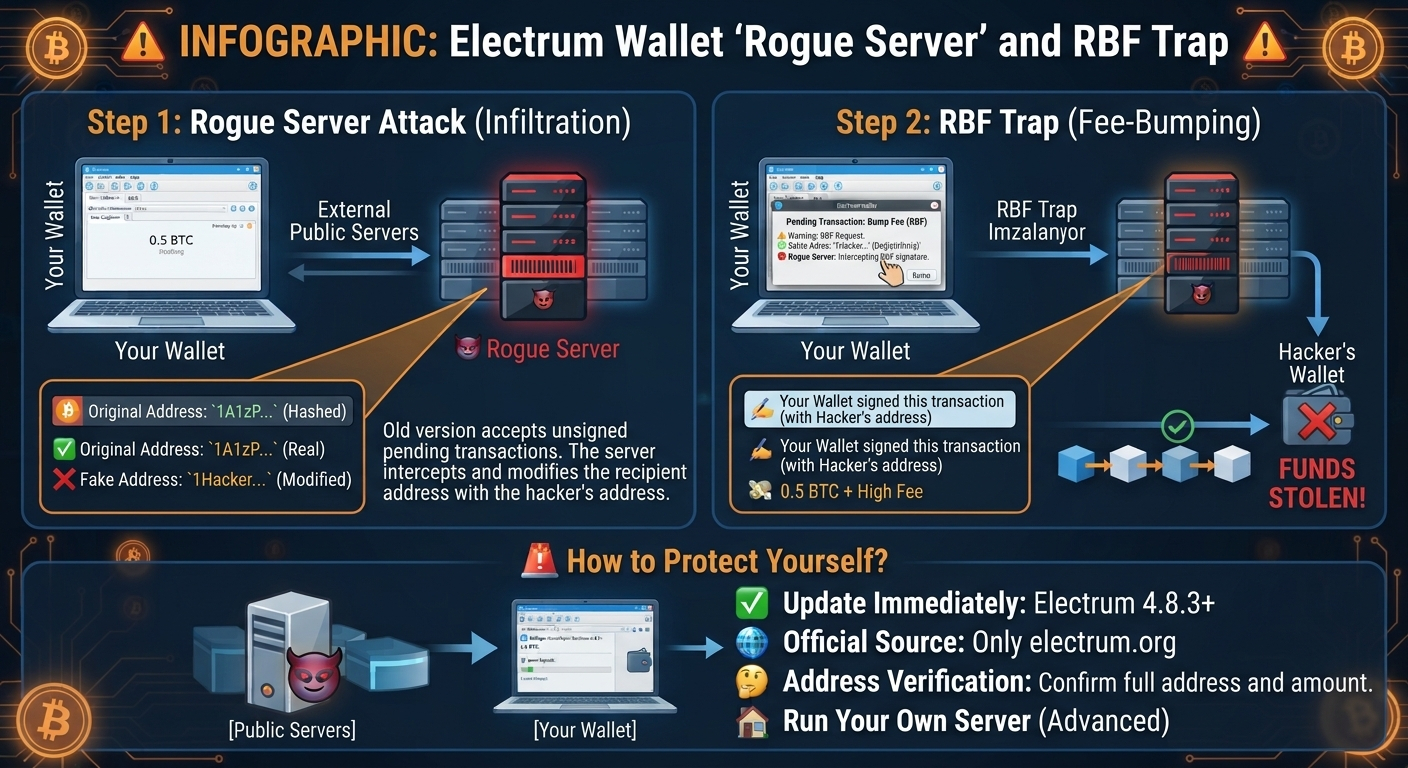
How Does the Fake Server Trap Work?
Open Door: Older versions of Electrum accepted unconfirmed (pending) transactions without checking signatures. 🔓Hacker Infiltration: A malicious server intercepted the transfer you sent and secretly replaced the recipient address with its own. To avoid detection, it even made the last 4 digits of the address match yours! 😈🕵️♂️Fee Trap: When your transaction was taking too long and you pressed the RBF (Increase Fee) button to speed it up, your wallet signed the hacker’s fake address in the background, and your Bitcoins were stolen! 📉💸
How Can You Protect Yourself?
Upgrade Your Version: Update to Electrum 4.8.3 immediately to close this critical vulnerability. 🆕Use Official Sources: Download the update only from the official website, electrum.org. 🌐Check Addresses: When making a transfer or increasing the fee, always visually verify the recipient address in full. 🧐
$BTC $BCH $BSV
188
·
--
Bullish
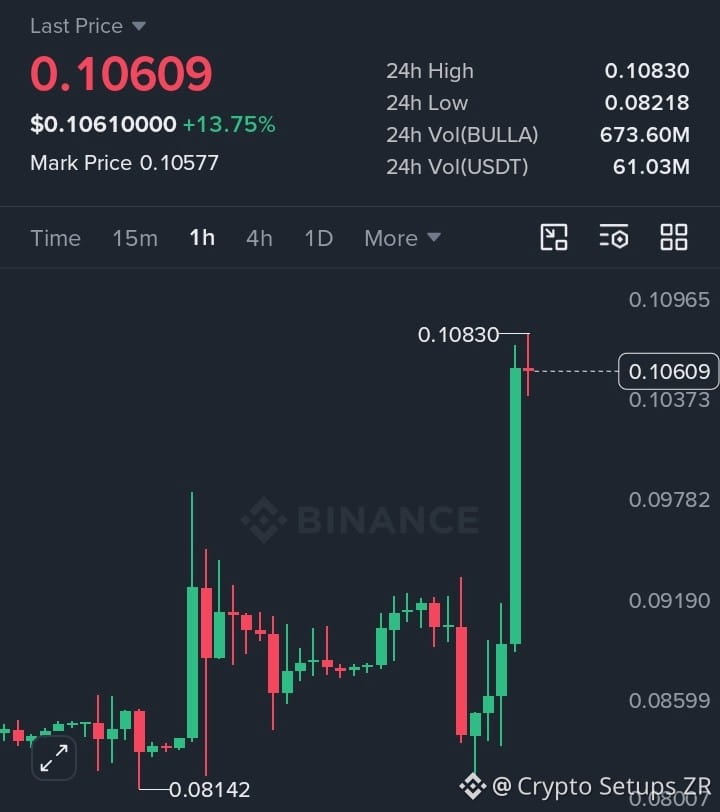
$BULLA woke up with zero warning 🟢‼️From 0.085 straight into 0.108 in a single candle🟢💥 0.12 next liquidity target loading fast.. 🎯‼️Don't miss it ‼️🎯
{future}(BULLAUSDT)
$APR
{future}(APRUSDT)
$JCT
{future}(JCTUSDT)
#BinancePick #SouthKoreaDelaysCryptoIncomeTax #ElectrumWalletBugLetRogueServersStealFunds
$BULLA woke up with zero warning 🟢‼️From 0.085 straight into 0.108 in a single candle🟢💥 0.12 next liquidity target loading fast.. 🎯‼️Don't miss it ‼️🎯
$APR
$JCT
#BinancePick #SouthKoreaDelaysCryptoIncomeTax #ElectrumWalletBugLetRogueServersStealFunds
$APR
$JCT
#BinancePick #SouthKoreaDelaysCryptoIncomeTax #ElectrumWalletBugLetRogueServersStealFunds
Crypto Setups ZR
·
--
Bearish$APR Dumping Faster Than Waterfall..⁉️🔴 0.05490 Top Rejected Without Mercy 🔴‼️ Now 0.03328.. What A Brutal Fall !!
0.030 Next.. Don't Miss The Fall 🔴
$JCT
$BTW
#BinancePick #USQ3GDPAndSeptemberPCEDueNextWeek #SouthKoreaDelaysCryptoIncomeTax
0.030 Next.. Don't Miss The Fall 🔴
$JCT
$BTW
#BinancePick #USQ3GDPAndSeptemberPCEDueNextWeek #SouthKoreaDelaysCryptoIncomeTax
AI Signal بركة:
0.12 next 🟢🟢 👀
25
2
3
2k
·
--
Bullish
🚀 $NEAR BULLS ARE WAKING UP — BREAKOUT INCOMING? 🔥👀
$NEAR is looking interesting around the $4.50 zone. If buyers hold their ground, another push higher could be on the table.
🟢 LONG $NEAR/USDT SETUP
🎯 Entry: $4.51 – $4.53
✅ TP1: $4.57
✅ TP2: $4.60
🚀 Final Target: $4.636
🛑 Stop Loss: $4.456
HERE'S THE SETUP 👇
🐂 BULLISH: Buyers defend $4.51 → Momentum builds → $4.60 and $4.636 come into play.
🐻 BEARISH: Price loses $4.456 → Long setup invalidated, with further downside risk.
⚠️ DON'T CHASE THE GREEN CANDLES!
A clean entry near support beats jumping in after the pump.
💥 THE BIG QUESTION:
Can NEAR break through $4.60, or will sellers shut down the rally?
👇 LONG $NEAR OR WAIT FOR A BETTER ENTRY?
{future}(NEARUSDT)
#BinancePick #EarningsSeason #ElectrumWalletBugLetRogueServersStealFunds #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale
🚀 $NEAR BULLS ARE WAKING UP — BREAKOUT INCOMING? 🔥👀
$NEAR is looking interesting around the $4.50 zone. If buyers hold their ground, another push higher could be on the table.
🟢 LONG $NEAR /USDT SETUP
🎯 Entry: $4.51 – $4.53
✅ TP1: $4.57
✅ TP2: $4.60
🚀 Final Target: $4.636
🛑 Stop Loss: $4.456
HERE'S THE SETUP 👇
🐂 BULLISH: Buyers defend $4.51 → Momentum builds → $4.60 and $4.636 come into play.
🐻 BEARISH: Price loses $4.456 → Long setup invalidated, with further downside risk.
⚠️ DON'T CHASE THE GREEN CANDLES!
A clean entry near support beats jumping in after the pump.
💥 THE BIG QUESTION:
Can NEAR break through $4.60, or will sellers shut down the rally?
👇 LONG $NEAR OR WAIT FOR A BETTER ENTRY?
#BinancePick #EarningsSeason #ElectrumWalletBugLetRogueServersStealFunds #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale
109
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
2.6M views
140,222 Discussing
2
#EarningsSeason
5M views
24,187 Discussing
3
#FranklinTempletonFilesForTwoDividendToBitcoinETFs
0 views
12 Discussing
4
#StrategyMSTRSurpassesNasdaqInMarketCap
262 views
33 Discussing
5
#CanadaProposesStablecoinRedemptionWithin3BusinessDays
35 views
3 Discussing
6
#ElectrumWalletBugLetRogueServersStealFunds
6,236 views
196 Discussing
7
#ArgentineCourtDismissesLIBRACaseAgainstMilei
14,855 views
274 Discussing
8
#SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale
2,844 views
43 Discussing
9
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
1,556 views
35 Discussing
10
#USQ3GDPAndSeptemberPCEDueNextWeek
90,260 views
1,091 Discussing