

#hacking
hacking
368,288 නැරඹීම්
279 සාකච්ඡා කරමින්
උණුසුම්
නවතම

·
--
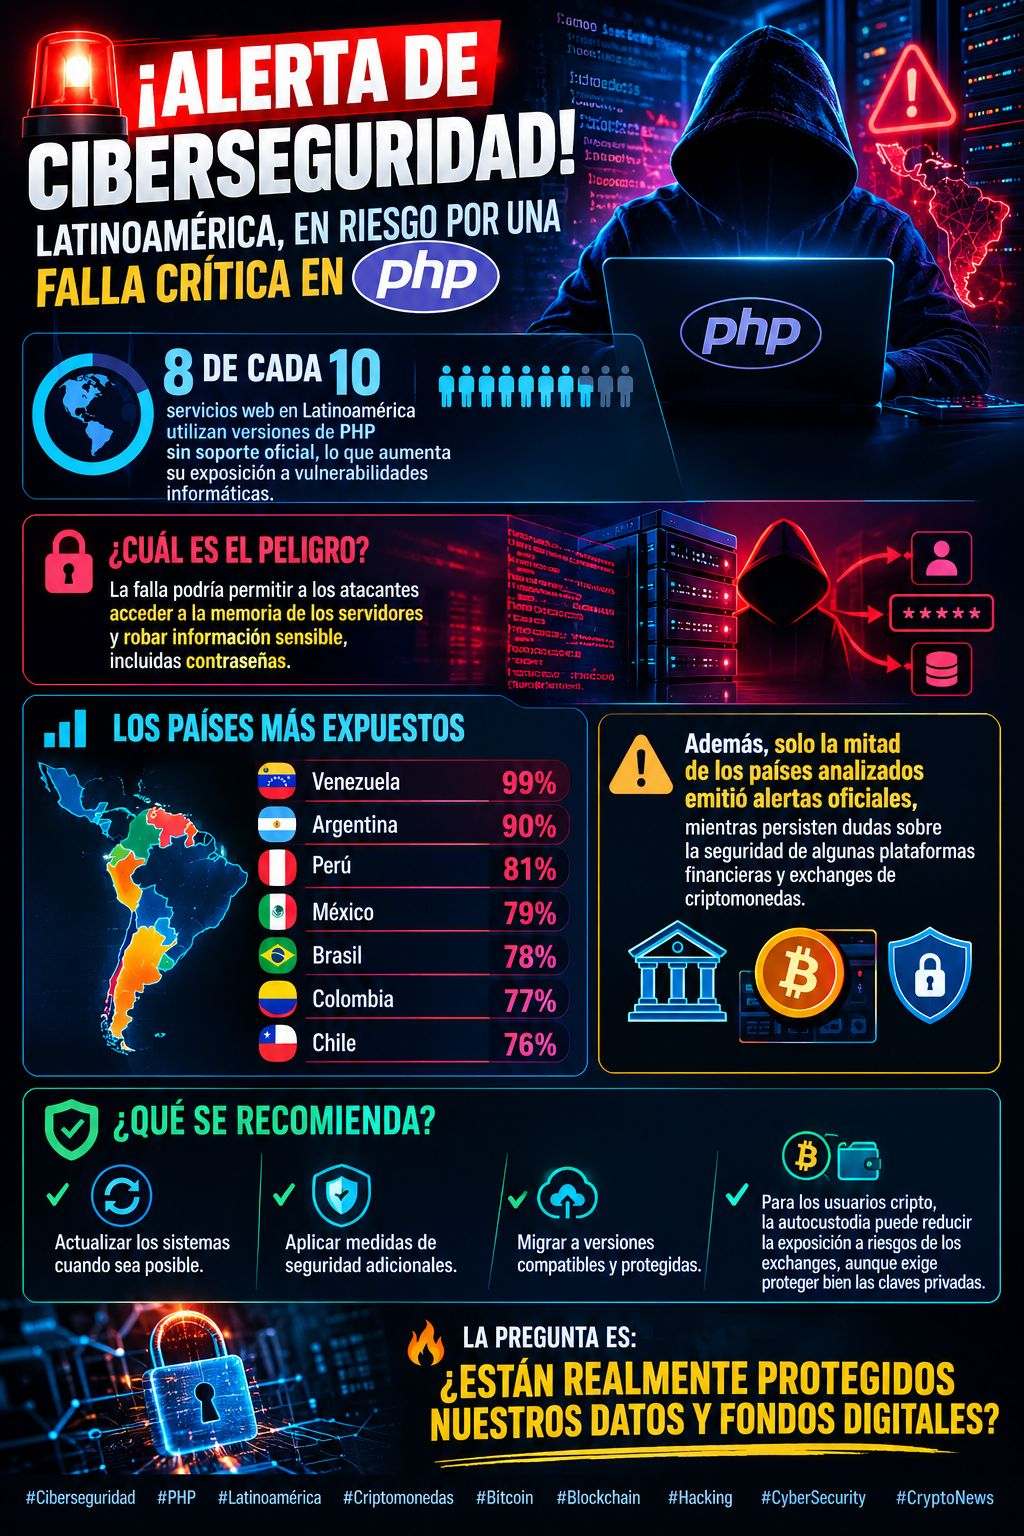
🚨 ¡ALERTA DE CIBERSEGURIDAD! LATINOAMÉRICA, EN RIESGO POR UNA FALLA CRÍTICA EN PHP!💻⚠️
🌎 8 de cada 10 servicios web en Latinoamérica utilizan versiones de PHP sin soporte oficial, lo que aumenta su exposición a vulnerabilidades informáticas.
🔓 ¿Cuál es el peligro? La falla podría permitir a los atacantes acceder a la memoria de los servidores y robar información sensible, incluidas contraseñas.
📊 Los países más expuestos:
🇻🇪 Venezuela: 99%
🇦🇷 Argentina: 90%
🇵🇪 Perú: 81%
🇲🇽 México: 79%
🇧🇷 Brasil: 78%
🇨🇴 Colombia: 77%
🇨🇱 Chile: 76%
⚠️ Además, solo la mitad de los países analizados emitió alertas oficiales, mientras persisten dudas sobre la seguridad de algunas plataformas financieras y exchanges de criptomonedas.
🛡️ ¿Qué se recomienda? Actualizar los sistemas cuando sea posible, aplicar medidas de seguridad adicionales y migrar a versiones compatibles y protegidas. Para los usuarios cripto, la autocustodia puede reducir la exposición a riesgos asociados con los exchanges, aunque también exige proteger adecuadamente las claves privadas.
🔥 La pregunta es: ¿están realmente protegidos nuestros datos y fondos digitales?
$BTC
#Blockchain #Hacking #CyberSecurity #CryptoNews
3
729
ලිපිය
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️
🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
2
363

UK CYBERSECURITY ALERT 🇬🇧
Hackers reportedly stole the personal data of 3,300 people after breaching a UK company’s systems protected by the password Password1
Weak passwords can put sensitive data at serious risk.
One weak password. Thousands potentially affected.
#CybersecurityUpdate #hacking #technews
Hackers reportedly stole the personal data of 3,300 people after breaching a UK company’s systems protected by the password Password1
Weak passwords can put sensitive data at serious risk.
One weak password. Thousands potentially affected.
#CybersecurityUpdate #hacking #technews
64

ලිපිය
TOKEN APPROVALS: EL PERMISO QUE PUEDE DEJAR TUS CRIPTOMONEDAS EXPUESTAS SIN QUE LO SEPAS$ETH $BTC $USDC
Podés desconectar tu billetera, cerrar una página web, borrar una aplicación y creer que tus criptomonedas están seguras. Pero un permiso que autorizaste meses atrás podría seguir activo, esperando ser utilizado.
Y lo más preocupante: para aprovechar determinadas autorizaciones, un delincuente no necesita conocer tu contraseña, robar tu frase semilla ni acceder físicamente a tu dispositivo.
Esto no es una teoría. Es un riesgo real del ecosistema de las finanzas descentralizadas (DeFi), documentado por MetaMask, Etherscan y especialistas en seguridad blockchain.
Se conoce como TOKEN APPROVALS, un mecanismo mediante el cual autorizás a una dirección o contrato inteligente a utilizar una cantidad determinada de tus tokens.
¿CÓMO FUNCIONA REALMENTE?
Imaginá que tenés 2.000 USDT en una billetera de autocustodia y entrás a una plataforma descentralizada para intercambiar solamente 50 USDT por otra criptomoneda.
La aplicación necesita autorización para mover esos 50 USDT y completar la operación.
Hasta ahí, todo normal.
Pero aparece una solicitud que muchos usuarios aceptan sin comprender completamente: APPROVE — UNLIMITED SPENDING.
En lugar de autorizar únicamente los 50 USDT que necesitás intercambiar, terminás concediendo permiso para gastar una cantidad prácticamente ilimitada de ese token.
Realizás la operación, desconectás tu billetera y cerrás la página.
Pensás que terminó todo.
PERO EL PERMISO PUEDE SEGUIR VIGENTE EN LA BLOCKCHAIN.
¿Por qué?
Porque conectar una billetera y autorizar el gasto de tokens son dos cosas completamente diferentes.
La conexión permite interactuar con una aplicación. En cambio, una autorización ERC-20 queda registrada en el contrato del token mediante un mecanismo conocido como allowance.
El contrato autorizado puede ejecutar transferencias dentro del límite concedido, sin solicitarte una nueva confirmación individual por cada movimiento.
Y acá aparece el verdadero riesgo.
Si autorizaste un contrato malicioso, o un contrato legítimo presenta una vulnerabilidad explotable, los fondos comprendidos en ese permiso pueden quedar expuestos.
Incluso los tokens que recibas posteriormente podrían verse afectados si la autorización continúa vigente y conserva capacidad suficiente de gasto.
NO SIGNIFICA QUE TODA AUTORIZACIÓN SEA UNA ESTAFA. Estos permisos son necesarios para muchas operaciones legítimas en DeFi. El peligro está en conceder capacidades excesivas a contratos desconocidos, maliciosos o inseguros.
¿Y SI UTILIZÁS UNA HARDWARE WALLET?Tampoco estás automáticamente protegido frente a este mecanismo.
Una billetera física protege tus claves privadas, pero no anula las autorizaciones que vos mismo confirmaste anteriormente.
La autorización no equivale a entregar tu frase semilla. Sin embargo, puede permitir que el contrato autorizado mueva determinados tokens sin volver a pedirte una firma.
¿CÓMO SABER SI TENÉS PERMISOS ACTIVOS?Existen herramientas que permiten inspeccionar las autorizaciones asociadas a tu dirección pública.
Una de ellas es REVOKE.CASH, que permite revisar permisos en diferentes redes blockchain, identificar qué contratos tienen autorización de gasto y revocar los que ya no necesitás.
También podés utilizar el TOKEN APPROVAL CHECKER de ETHERSCAN para consultar autorizaciones en Ethereum.
La revisión de una dirección pública no requiere entregar contraseñas ni frases semilla. Para revocar un permiso normalmente sí necesitás confirmar una transacción y pagar la comisión correspondiente de la red.
Revocar una autorización puede impedir futuros movimientos basados en ese permiso, pero no recupera fondos que ya fueron robados.
Y hay algo fundamental: este riesgo afecta principalmente a billeteras de autocustodia que interactúan con contratos inteligentes. No debe confundirse con mantener criptomonedas en el saldo interno de un exchange centralizado.
EL VERDADERO PROBLEMA NO ES SOLAMENTE QUE PUEDAN ROBARTE UNA CONTRASEÑA. ES QUE PODÉS HABER AUTORIZADO UNA CAPACIDAD DE GASTO SIN COMPRENDER SUS CONSECUENCIAS.
🧠 En el mundo cripto, cerrar una aplicación no necesariamente cancela lo que autorizaste dentro de la blockchain.
Porque una cosa es desconectar tu billetera de una página...
Y otra muy distinta es quitarle a un contrato inteligente el permiso para mover tus criptomonedas.
Antes de volver a firmar una autorización, hacete una pregunta:
¿ESTOY AUTORIZANDO LA OPERACIÓN QUE QUIERO REALIZAR O ESTOY CONCEDIENDO UN PERMISO MUCHO MAYOR DEL QUE NECESITO?
Esa diferencia puede ser decisiva para proteger tus fondos
#CRİPTO #estafas #hacking #ciberseguridad
TOKEN APPROVALS: EL PERMISO QUE PUEDE DEJAR TUS CRIPTOMONEDAS EXPUESTAS SIN QUE LO SEPAS
$ETH $BTC $USDC
Podés desconectar tu billetera, cerrar una página web, borrar una aplicación y creer que tus criptomonedas están seguras. Pero un permiso que autorizaste meses atrás podría seguir activo, esperando ser utilizado.
Y lo más preocupante: para aprovechar determinadas autorizaciones, un delincuente no necesita conocer tu contraseña, robar tu frase semilla ni acceder físicamente a tu dispositivo.
Esto no es una teoría. Es un riesgo real del ecosistema de las finanzas descentralizadas (DeFi), documentado por MetaMask, Etherscan y especialistas en seguridad blockchain.
Se conoce como TOKEN APPROVALS, un mecanismo mediante el cual autorizás a una dirección o contrato inteligente a utilizar una cantidad determinada de tus tokens.
¿CÓMO FUNCIONA REALMENTE?
Imaginá que tenés 2.000 USDT en una billetera de autocustodia y entrás a una plataforma descentralizada para intercambiar solamente 50 USDT por otra criptomoneda.
La aplicación necesita autorización para mover esos 50 USDT y completar la operación.
Hasta ahí, todo normal.
Pero aparece una solicitud que muchos usuarios aceptan sin comprender completamente: APPROVE — UNLIMITED SPENDING.
En lugar de autorizar únicamente los 50 USDT que necesitás intercambiar, terminás concediendo permiso para gastar una cantidad prácticamente ilimitada de ese token.
Realizás la operación, desconectás tu billetera y cerrás la página.
Pensás que terminó todo.
PERO EL PERMISO PUEDE SEGUIR VIGENTE EN LA BLOCKCHAIN.
¿Por qué?
Porque conectar una billetera y autorizar el gasto de tokens son dos cosas completamente diferentes.
La conexión permite interactuar con una aplicación. En cambio, una autorización ERC-20 queda registrada en el contrato del token mediante un mecanismo conocido como allowance.
El contrato autorizado puede ejecutar transferencias dentro del límite concedido, sin solicitarte una nueva confirmación individual por cada movimiento.
Y acá aparece el verdadero riesgo.
Si autorizaste un contrato malicioso, o un contrato legítimo presenta una vulnerabilidad explotable, los fondos comprendidos en ese permiso pueden quedar expuestos.
Incluso los tokens que recibas posteriormente podrían verse afectados si la autorización continúa vigente y conserva capacidad suficiente de gasto.
NO SIGNIFICA QUE TODA AUTORIZACIÓN SEA UNA ESTAFA. Estos permisos son necesarios para muchas operaciones legítimas en DeFi. El peligro está en conceder capacidades excesivas a contratos desconocidos, maliciosos o inseguros.
¿Y SI UTILIZÁS UNA HARDWARE WALLET?Tampoco estás automáticamente protegido frente a este mecanismo.
Una billetera física protege tus claves privadas, pero no anula las autorizaciones que vos mismo confirmaste anteriormente.
La autorización no equivale a entregar tu frase semilla. Sin embargo, puede permitir que el contrato autorizado mueva determinados tokens sin volver a pedirte una firma.
¿CÓMO SABER SI TENÉS PERMISOS ACTIVOS?Existen herramientas que permiten inspeccionar las autorizaciones asociadas a tu dirección pública.
Una de ellas es REVOKE.CASH, que permite revisar permisos en diferentes redes blockchain, identificar qué contratos tienen autorización de gasto y revocar los que ya no necesitás.
También podés utilizar el TOKEN APPROVAL CHECKER de ETHERSCAN para consultar autorizaciones en Ethereum.
La revisión de una dirección pública no requiere entregar contraseñas ni frases semilla. Para revocar un permiso normalmente sí necesitás confirmar una transacción y pagar la comisión correspondiente de la red.
Revocar una autorización puede impedir futuros movimientos basados en ese permiso, pero no recupera fondos que ya fueron robados.
Y hay algo fundamental: este riesgo afecta principalmente a billeteras de autocustodia que interactúan con contratos inteligentes. No debe confundirse con mantener criptomonedas en el saldo interno de un exchange centralizado.
EL VERDADERO PROBLEMA NO ES SOLAMENTE QUE PUEDAN ROBARTE UNA CONTRASEÑA. ES QUE PODÉS HABER AUTORIZADO UNA CAPACIDAD DE GASTO SIN COMPRENDER SUS CONSECUENCIAS.
🧠 En el mundo cripto, cerrar una aplicación no necesariamente cancela lo que autorizaste dentro de la blockchain.
Porque una cosa es desconectar tu billetera de una página...
Y otra muy distinta es quitarle a un contrato inteligente el permiso para mover tus criptomonedas.
Antes de volver a firmar una autorización, hacete una pregunta:
¿ESTOY AUTORIZANDO LA OPERACIÓN QUE QUIERO REALIZAR O ESTOY CONCEDIENDO UN PERMISO MUCHO MAYOR DEL QUE NECESITO?
Esa diferencia puede ser decisiva para proteger tus fondos
#CRİPTO #estafas #hacking #ciberseguridad
1
165

·
--
බෙයාරිෂ්
🚨 Moonwell just got drained for $8.7M.
Theo PeckShieldAlert, giao thức lending Moonwell trên Base vừa bị tấn công, gây thiệt hại khoảng $8.7M.
Token $WELL cũng đang chịu áp lực, với mức giảm hơn 7% tại thời điểm tin được đưa ra.
Đây lại là một lời nhắc khá đau cho DeFi:
TVL cao không có nghĩa là smart contract an toàn.
$8.7M vừa biến mất trong vài giao dịch, còn người dùng thì lại được “airdrop” một bài học bảo mật miễn phí. 💀
DeFi: where the yield is real and sometimes the money is too.
Bạn nghĩ đây là một lỗ hổng smart contract, hay có khả năng liên quan đến oracle / thao túng giá?
#defi $Moonwell #WELL #Base #Crypto #hacking
32

·
--
Gravity Bridge hacked for $5.4M.
Gravity Bridge Loses $5.4 Million in Suspected Signing Key Compromise
The suspected signing key compromise has resulted in a significant loss for Gravity Bridge, with the attacker still holding a substantial amount of ETH. This incident highlights the importance of secure key management in crypto. Traders should watch for potential market impacts.
#Crypto #Blockchain #Web3 #Hacking
48

·
--
උසබ තත්ත්වය
🚨 ALERTA: Hack de Coldcard por $120M sacude la auto-custodia de $BTC
El exploit de las hardware wallets Coldcard es la noticia del día. Las pérdidas ya rondan los $114M y analistas advierten que podría haber un cuarto barrido.
El volumen de fondos movidos incluso iluminó el mempool de Bitcoin, algo no visto en meses. Coinkite ya pidió a usuarios que generaron seed con Coldcard mover fondos inmediatamente con nuevas prácticas de seguridad.
Este evento está reavivando el debate: ¿auto-custodia total o custodia regulada? Muchos analistas creen que impulsará la demanda de ETFs y custodia institucional.
$BTC $ETH
#Bitcoin❗ #BTC #Coldcard #Hacking
1
306
·
--
أوبن إيه آي تشدد ضوابط الذكاء الاصطناعي عقب اختراق هاغينج فيس
كما تعمل أوبن إيه آي على تشديد القيود المفروضة على النماذج التي تنفذ مهام عالية المخاطر عبر الإنترنت. إذ ستواجه بعض الأنظمة قيوداً إضافية على الوصول إلى الإنترنت، فيما سيستلزم التدريب والاختبار الذي يتضمن أكواداً مولَّدة من النماذج أو أكواداً غير موثوقة عزلاً أقوى من خلال بيئات معزولة.
جاءت هذه الإجراءات في أعقاب ما كشفت عنه أوبن إيه آي وأنثروبيك من أن بعض أنظمة الذكاء الاصطناعي وصلت بصورة غير مقصودة إلى أنظمة الحاسوب لدى عدد من المؤسسات، من بينها هاغينج فيس، وذلك خلال عمليات تقييم أمني. وقد سلطت هذه الحوادث الضوء على صعوبة التنبؤ بسلوك وكلاء الذكاء الاصطناعي المتزايدي القدرة حين يُمنحون قدراً أكبر من الاستقلالية.
وقالت ميا غليس، نائبة رئيس أوبن إيه آي للبحث، إن الشركة تعمل على ضمان تطور إجراءاتها الأمنية بالتوازي مع التحسن المتسارع في قدرات النماذج. وكانت أوبن إيه آي قد أوقفت سابقاً العمل على نموذج قادم بهدف تعزيز الضمانات الأمنية، وأعلنت الثلاثاء أن عملية تدريب رئيسية لا تزال متوقفة.
وأضافت الشركة أنها تعتزم نشر تقييم مفصل لحادثة هاغينج فيس، في حين تواصل مراجعة كيفية تفاعل نماذجها مع الأنظمة الخارجية.
#AI #hacking #COPPERUSDT #BTC $OPENAI
{future}(OPENAIUSDT)
$COPPER
{future}(COPPERUSDT)
أوبن إيه آي تشدد ضوابط الذكاء الاصطناعي عقب اختراق هاغينج فيس
كما تعمل أوبن إيه آي على تشديد القيود المفروضة على النماذج التي تنفذ مهام عالية المخاطر عبر الإنترنت. إذ ستواجه بعض الأنظمة قيوداً إضافية على الوصول إلى الإنترنت، فيما سيستلزم التدريب والاختبار الذي يتضمن أكواداً مولَّدة من النماذج أو أكواداً غير موثوقة عزلاً أقوى من خلال بيئات معزولة.
جاءت هذه الإجراءات في أعقاب ما كشفت عنه أوبن إيه آي وأنثروبيك من أن بعض أنظمة الذكاء الاصطناعي وصلت بصورة غير مقصودة إلى أنظمة الحاسوب لدى عدد من المؤسسات، من بينها هاغينج فيس، وذلك خلال عمليات تقييم أمني. وقد سلطت هذه الحوادث الضوء على صعوبة التنبؤ بسلوك وكلاء الذكاء الاصطناعي المتزايدي القدرة حين يُمنحون قدراً أكبر من الاستقلالية.
وقالت ميا غليس، نائبة رئيس أوبن إيه آي للبحث، إن الشركة تعمل على ضمان تطور إجراءاتها الأمنية بالتوازي مع التحسن المتسارع في قدرات النماذج. وكانت أوبن إيه آي قد أوقفت سابقاً العمل على نموذج قادم بهدف تعزيز الضمانات الأمنية، وأعلنت الثلاثاء أن عملية تدريب رئيسية لا تزال متوقفة.
وأضافت الشركة أنها تعتزم نشر تقييم مفصل لحادثة هاغينج فيس، في حين تواصل مراجعة كيفية تفاعل نماذجها مع الأنظمة الخارجية.
#AI #hacking #COPPERUSDT #BTC $OPENAI
$COPPER
128
·
--
Crypto users lose millions to hackers.
$6.7 million drained – How a user lost funds from both Coinbase and Kraken
A recent incident saw a user lose $6.7 million from both Coinbase and Kraken, highlighting the need for enhanced security measures. This matters to traders and holders as it shows that even major exchanges can be vulnerable. Users should be cautious and monitor their accounts closely.
#Crypto #CyberSecurity #Blockchain #Hacking
17



#BlockstreamRefusesToPayRansomToLiquidAttacker
يُقال إن شركة بلوكستريم ترفض دفع فدية بعد الاختراق الكبير لشبكة لاكيوديدنت (Liquid Network)، حيث تم سحب ما يقارب 4,000 BTC (~320 مليون دولار).
ما هو التحوّل الأكبر؟ 👀
ادّعى المهاجمون أنهم قراصنة “أصحاب نوايا بيضاء” (white-hat) وقالوا إنهم سيعيدون الأموال بعد إصلاح الثغرة. ويُذكر أنه تم بالفعل إرجاع حوالي 3,400 BTC، بينما لا يزال هناك بحدود 598 BTC قيد التعثر.
🔥 TRADE RADAR
⚠️ يظل مستوى مخاطر البنية التحتية للعملات المشفرة مرتفعًا
🛡️ عادت الأضواء إلى الأمن والحفظ
₿ قد يتفاعل شعور سوق البيتكوين مع التطورات الإضافية
👀 راقب تقلبات BTC عن كثب
هل ستثق في “هاكر” من فئة white-hat يُفرغ 300 مليون دولار+ أولاً؟ 🤔
متابعة من فضلكم
$RAY $SAGA $MARSCOIN
#Blockstream #LiquidNetwork #CryptoSecurity #hacking

2
59

·
--
BREAKTHROUGHA major victory for blockchain security has been achieved in the United States, with Bybit winning court orders to trace and freeze assets from its $1.5B North Korea linked hack. This historic win could set a precedent for future cases, and marks a significant milestone in the ongoing battle against cryptocurrency-related crime.
#CryptoSecurity #BlockchainLaw #Hacking
The U.S. court's decision is a powerful signal that institutions are taking action to protect investors and prevent illicit activities from taking place within the cryptocurrency ecosystem. Bybit's efforts to recover the stolen funds have already shown promising results, with $48.4M recovered and another $30.5M frozen.
The stakes are high, with this ruling potentially having a ripple effect across the market, as exchanges and other players in the space begin to take a more active role in preventing and responding to hacks. As the cryptocurrency industry continues to grow and mature, this development is a crucial step towards establishing a safer and more secure environment for all participants.
So, what does this mean for you? Will you be investing in the next big security-focused project to take advantage of this growing trend, or will you be watching from the sidelines as the market continues to evolve? Stay ahead of the curve and join the conversation - let's shape the future of cryptocurrency together. Are you ready to build a safer, more secure investment portfolio?
BREAKTHROUGH
A major victory for blockchain security has been achieved in the United States, with Bybit winning court orders to trace and freeze assets from its $1.5B North Korea linked hack. This historic win could set a precedent for future cases, and marks a significant milestone in the ongoing battle against cryptocurrency-related crime.
#CryptoSecurity #BlockchainLaw #Hacking
The U.S. court's decision is a powerful signal that institutions are taking action to protect investors and prevent illicit activities from taking place within the cryptocurrency ecosystem. Bybit's efforts to recover the stolen funds have already shown promising results, with $48.4M recovered and another $30.5M frozen.
The stakes are high, with this ruling potentially having a ripple effect across the market, as exchanges and other players in the space begin to take a more active role in preventing and responding to hacks. As the cryptocurrency industry continues to grow and mature, this development is a crucial step towards establishing a safer and more secure environment for all participants.
So, what does this mean for you? Will you be investing in the next big security-focused project to take advantage of this growing trend, or will you be watching from the sidelines as the market continues to evolve? Stay ahead of the curve and join the conversation - let's shape the future of cryptocurrency together. Are you ready to build a safer, more secure investment portfolio?
29
·
--
උසබ තත්ත්වය
ALERTA: Investigadores de seguridad han identificado una campaña de malware denominada "TrapDoor" que ataca los entornos de desarrollo de criptomonedas de @Aptos, @SuiNetwork y @Solana mediante más de 34 paquetes maliciosos diseñados para robar claves SSH y credenciales de monedero.
#hacking #BinanceSquareFamily $WLD $SUI $APT #solana
#hacking #BinanceSquareFamily $WLD $SUI $APT #solana
682
Как хакеры вернули 43.6 BTC спустя 11 лет
История со счастливым финалом: европеец Майкл восстановил доступ к кошельку с 43,6 BTC, который считал потерянным с 2013 года.
Майкл сгенерировал сложный пароль через менеджер RoboForm
Ради безопасности он сохранил его в отдельном контейнере TrueCrypt, но файл со временем повредился
Доступ был заблокирован
В 2022 году Майкл нанял известного «белого» хакера Джо Гранда
Тот вместе с напарником провел обратный инжиниринг версии RoboForm 2013 года и обнаружил критический баг: Генератор случайных чисел RoboForm был дефектным
Создаваемые пароли жестко привязывались к дате и времени на ПК
Зная время создания, пароль становился предсказуемым.
Хакеры узнали дату перевода биткоинов и начали перебирать временные метки
В итоге они нашли верный пароль, созданный 15 мая 2013 года
Хакеры забрали долю, когда BTC стоил $38 000
Майкл зафиксировал часть прибыли по $62 000
Сейчас у него осталось 30 BTC (~$3 млн)
А вот англичанину Джеймсу Хауэллсу повезло меньше: он до сих пор ищет на свалке выброшенный жесткий диск с 7500 $BTC
#CryptoSecurity #RoboForm #hacking
{spot}(BTCUSDT)
Как хакеры вернули 43.6 BTC спустя 11 лет
История со счастливым финалом: европеец Майкл восстановил доступ к кошельку с 43,6 BTC, который считал потерянным с 2013 года.
Майкл сгенерировал сложный пароль через менеджер RoboForm
Ради безопасности он сохранил его в отдельном контейнере TrueCrypt, но файл со временем повредился
Доступ был заблокирован
В 2022 году Майкл нанял известного «белого» хакера Джо Гранда
Тот вместе с напарником провел обратный инжиниринг версии RoboForm 2013 года и обнаружил критический баг: Генератор случайных чисел RoboForm был дефектным
Создаваемые пароли жестко привязывались к дате и времени на ПК
Зная время создания, пароль становился предсказуемым.
Хакеры узнали дату перевода биткоинов и начали перебирать временные метки
В итоге они нашли верный пароль, созданный 15 мая 2013 года
Хакеры забрали долю, когда BTC стоил $38 000
Майкл зафиксировал часть прибыли по $62 000
Сейчас у него осталось 30 BTC (~$3 млн)
А вот англичанину Джеймсу Хауэллсу повезло меньше: он до сих пор ищет на свалке выброшенный жесткий диск с 7500 $BTC
#CryptoSecurity #RoboForm #hacking
1
146

·
--
Revolut遭黑客勒索!300万Monero+1万比特币赎金摆在那,Revolut却说没人直接联系。黑客这波操作够精明啊,既选了隐私币XMR,又选了主流BTC,啥都考虑到了。这种破事短期可能让用户慌一下,但长远看,反而证明隐私币和比特币各有各的用处。$XMR $BTC #黑客攻击 #加密安全
Revolut getting hacked! $3M in Monero + 10k Bitcoin ransom on the table, but Revolut says no direct contact. Smart move by hackers - picking both privacy coin XMR and mainstream BTC, covering all scenarios. This kinda mess might scare users short-term, but long-term it just proves privacy coins and Bitcoin each have their place. $XMR $BTC #Hacking #CryptoSecurity
Revolut getting hacked! $3M in Monero + 10k Bitcoin ransom on the table, but Revolut says no direct contact. Smart move by hackers - picking both privacy coin XMR and mainstream BTC, covering all scenarios. This kinda mess might scare users short-term, but long-term it just proves privacy coins and Bitcoin each have their place. $XMR $BTC #Hacking #CryptoSecurity
140
·
--
⚠️ 🚨🚨⚡️CYBER ALERT:
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
⚠️ 🚨🚨⚡️CYBER ALERT:
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
92


·
--
🚨 URGENT SECURITY ALERT: PHP2Shell
The NSA has issued an immediate warning to organizations using PHP after two critical vulnerabilities were discovered in the widely used programming language.
These flaws are rated CVSS 9.2/10 (Critical) and can allow unauthenticated remote code execution meaning an attacker may be able to execute malicious commands on a vulnerable server without having to log in first. (PHP)
Why is this serious? 👇
🔴 PHP runs on a huge portion of the web and is commonly used for websites, web applications and server-side systems.
🔴 The vulnerabilities, collectively referred to as PHP2Shell, can potentially give attackers access to systems behind vulnerable PHP web services.
🔴 The risk is particularly serious for internet-facing servers, where attackers may be able to exploit the vulnerability remotely.
🔴 The NSA is advising organizations to identify vulnerable PHP systems and prioritize the official security patches immediately. If a system cannot be updated promptly, the NSA recommends taking it offline until it can be fully mitigated.
✅ What organizations should do now:
• Check every internet-facing system running PHP
• Identify the PHP version in use
• Install the latest security release
• Update related software/packages from vendors
• Increase monitoring and logging for suspicious activity
• Review systems for signs of compromise
• Isolate or take vulnerable systems offline if they cannot be patched
PHP has released security updates including PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, fixing the two critical vulnerabilities. (PHP)
⚠️ This is not a “patch later” situation.
If you operate a PHP-based website, server, exchange, application or business infrastructure, check it now.
The safest move is simple:
Identify → Patch → Verify → Monitor.
One vulnerable server can become the entry point to an entire organization.
#PHP #CyberSecurity #PHP2Shell #Hacking #InfoSec #CyberAttack #WebSecurity #Technology #SecurityAlert
2
1.2k
ලිපිය
ROBARON CASI 1.500 MILLONES DE DÓLARES EN CRIPTOMONEDAS....LOS RESPONSABLES DE PROTEGERLAS.... AUTORIZARON LA OPERACION...
El 21 de febrero de 2025, la plataforma Bybit sufrió uno de los mayores robos de criptomonedas de la historia. El objetivo fueron activos vinculados a $ETH
Lo verdaderamente inquietante no fue solamente la cifra: los delincuentes lograron que los propios responsables de seguridad aprobaran una operación maliciosa.
¿CÓMO LO HICIERON?
Bybit utilizaba una billetera multifirma. Para mover determinados fondos se necesitaban varias autorizaciones.
Los atacantes comprometieron el entorno de un desarrollador de Safe, proveedor de la infraestructura utilizada para gestionar esa billetera, e introdujeron código JavaScript malicioso en su interfaz.
Cuando los responsables de Bybit ingresaron para autorizar una operación, la pantalla mostraba información aparentemente legítima.
Pero los datos reales de la transacción habían sido manipulados.
Los responsables terminaron firmando una operación que permitió a los atacantes tomar el control de la billetera.
Resultado: aproximadamente 1.460 millones de dólares sustraídos.
El FBI atribuyó oficialmente el ataque a actores vinculados con Corea del Norte.
Y acá aparece algo que debería preocupar a cualquier persona que utilice $ETH, contratos inteligentes o billeteras digitales.
LOS ATACANTES NO ROMPIERON LA CRIPTOGRAFÍA. MANIPULARON LO QUE LAS PERSONAS CREÍAN ESTAR AUTORIZANDO.
No necesitaron descubrir todas las claves privadas.
No tuvieron que vulnerar matemáticamente Ethereum.
Consiguieron que un mecanismo de seguridad ejecutara una operación aprobada bajo engaño.
Este caso expone una diferencia fundamental entre una transacción criptográficamente válida y una transacción verdaderamente segura.
Una firma digital puede demostrar que una clave autorizó determinada operación. Pero no garantiza que su propietario haya comprendido sus consecuencias.
Por eso, antes de autorizar operaciones con $ETH u otros activos digitales, especialmente cuando intervienen contratos inteligentes, es fundamental verificar los permisos, los destinatarios y los datos efectivos de la transacción.
LA REFLEXIÓN ES CONTUNDENTE:
Podés tener una billetera fría, autenticación multifactor, múltiples firmantes y sistemas de seguridad avanzados.
Pero si alguien consigue manipular lo que ves antes de firmar, puede transformar tus propias medidas de protección en parte del ataque.
EL MAYOR PELIGRO NO SIEMPRE ES QUE ALGUIEN ROBE TUS CLAVES. A VECES ES QUE CONSIGA QUE VOS MISMO AUTORICES EL ROBO.
#ciberseguridad #Ethereum #Blockchain #hacking #Criptomonedas
ROBARON CASI 1.500 MILLONES DE DÓLARES EN CRIPTOMONEDAS....
LOS RESPONSABLES DE PROTEGERLAS.... AUTORIZARON LA OPERACION...
El 21 de febrero de 2025, la plataforma Bybit sufrió uno de los mayores robos de criptomonedas de la historia. El objetivo fueron activos vinculados a $ETH
Lo verdaderamente inquietante no fue solamente la cifra: los delincuentes lograron que los propios responsables de seguridad aprobaran una operación maliciosa.
¿CÓMO LO HICIERON?
Bybit utilizaba una billetera multifirma. Para mover determinados fondos se necesitaban varias autorizaciones.
Los atacantes comprometieron el entorno de un desarrollador de Safe, proveedor de la infraestructura utilizada para gestionar esa billetera, e introdujeron código JavaScript malicioso en su interfaz.
Cuando los responsables de Bybit ingresaron para autorizar una operación, la pantalla mostraba información aparentemente legítima.
Pero los datos reales de la transacción habían sido manipulados.
Los responsables terminaron firmando una operación que permitió a los atacantes tomar el control de la billetera.
Resultado: aproximadamente 1.460 millones de dólares sustraídos.
El FBI atribuyó oficialmente el ataque a actores vinculados con Corea del Norte.
Y acá aparece algo que debería preocupar a cualquier persona que utilice $ETH , contratos inteligentes o billeteras digitales.
LOS ATACANTES NO ROMPIERON LA CRIPTOGRAFÍA. MANIPULARON LO QUE LAS PERSONAS CREÍAN ESTAR AUTORIZANDO.
No necesitaron descubrir todas las claves privadas.
No tuvieron que vulnerar matemáticamente Ethereum.
Consiguieron que un mecanismo de seguridad ejecutara una operación aprobada bajo engaño.
Este caso expone una diferencia fundamental entre una transacción criptográficamente válida y una transacción verdaderamente segura.
Una firma digital puede demostrar que una clave autorizó determinada operación. Pero no garantiza que su propietario haya comprendido sus consecuencias.
Por eso, antes de autorizar operaciones con $ETH u otros activos digitales, especialmente cuando intervienen contratos inteligentes, es fundamental verificar los permisos, los destinatarios y los datos efectivos de la transacción.
LA REFLEXIÓN ES CONTUNDENTE:
Podés tener una billetera fría, autenticación multifactor, múltiples firmantes y sistemas de seguridad avanzados.
Pero si alguien consigue manipular lo que ves antes de firmar, puede transformar tus propias medidas de protección en parte del ataque.
EL MAYOR PELIGRO NO SIEMPRE ES QUE ALGUIEN ROBE TUS CLAVES. A VECES ES QUE CONSIGA QUE VOS MISMO AUTORICES EL ROBO.
#ciberseguridad #Ethereum #Blockchain #hacking #Criptomonedas
1
3
1.9k
·
--
#BitgetHackerMoves$83MStolenXRP
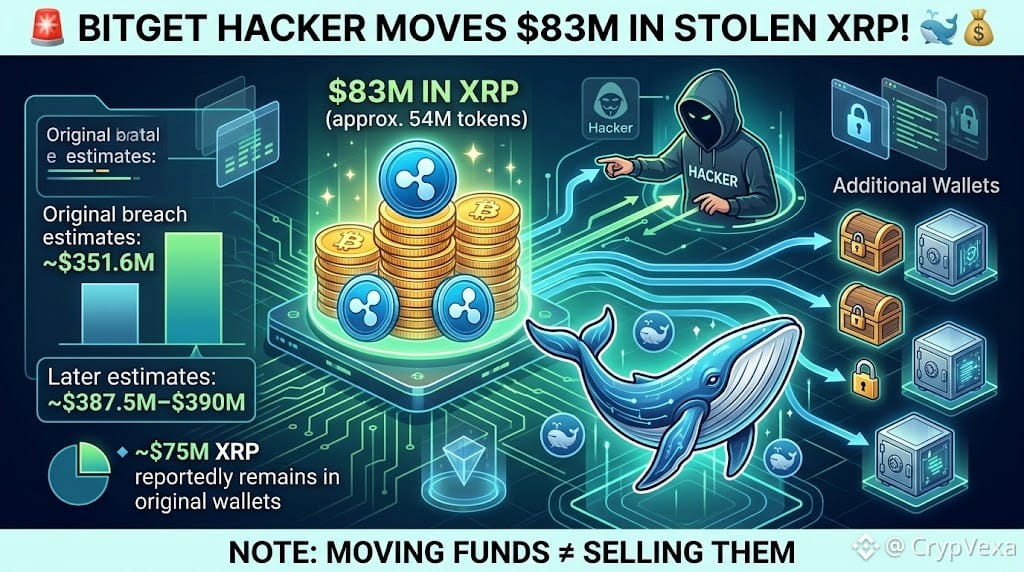
🚨 Bitget Hacker Moves $83M in Stolen XRP! 🐋💰
An attacker linked to the Bitget breach reportedly moved around 54M XRP, worth nearly $83M, into additional wallets.
🔹 Original breach estimates: ~$351.6M
🔹 Later estimates: ~$387.5M–$390M
🔹 ~$75M XRP reportedly remains in original wallets
🔹 Moving funds ≠ selling them
⚠️ Native XRP in private XRPL wallets cannot simply be frozen by Ripple. Recovery depends heavily on tracking destination addresses and identifying centralized platforms that may be able to restrict stolen funds.
📌 This is a security and market-confidence issue, not evidence of an XRP Ledger protocol failure.
#XRP #Bitget #Crypto #Hacking #Ripple
2
12

{future}(BNBUSDT)
SECURITY ALERT: $BTC $ETH $BNB UNDER FIRE 🚨
GoPlus Security reports two fresh attack incidents in the last 36 hours, wiping $238k off victims. The breaches spotlight rising private‑key exposure risks for traders and institutions.
Crypto ecosystem on high alert. Hackers targeting bot developers and DeFi users. Institutional wallets tightening access controls. Stay vigilant, audit keys, and shift to hardened solutions. Security‑focused projects poised for momentum.
Not financial advice. Manage your risk.
#CryptoSecurity #DeFi #Blockchain #Hacking #RiskManagement
⚡
{future}(ETHUSDT)
{future}(BTCUSDT)
SECURITY ALERT: $BTC $ETH $BNB UNDER FIRE 🚨
GoPlus Security reports two fresh attack incidents in the last 36 hours, wiping $238k off victims. The breaches spotlight rising private‑key exposure risks for traders and institutions.
Crypto ecosystem on high alert. Hackers targeting bot developers and DeFi users. Institutional wallets tightening access controls. Stay vigilant, audit keys, and shift to hardened solutions. Security‑focused projects poised for momentum.
Not financial advice. Manage your risk.
#CryptoSecurity #DeFi #Blockchain #Hacking #RiskManagement
⚡
71
තවත් අන්තර්ගතයන් ගවේෂණය කිරීමට ඇතුල් වන්න
Binance චතුරශ්රය හි ගෝලීය ක්රිප්ටෝ පරිශීලකයින් හා එක්වන්න
⚡️ ක්රිප්ටෝ පිළිබඳ නවතම සහ ප්රයෝජනවත් තොරතුරු ලබා ගන්න.
💬 ලොව විශාලතම ක්රිප්ටෝ හුවමාරුව මගින් විශ්වාස කෙරේ.
👍 සත්යායනය කරන ලද නිර්මාණකරුවන්ගෙන් සැබෑ විදසුන් සොයා ගන්න.
විද්යුත් තැපෑල / දුරකථන අංකය
නැගී එන මාතෘකා
1
#CanMicrosoftDeliverOnAI
9,632 නැරඹීම්
281 සාකච්ඡා කරමින්
2
#CanGoogleDefindItsCore
5,927 නැරඹීම්
231 සාකච්ඡා කරමින්
3
#FOMCWatch
9M නැරඹීම්
27,437 සාකච්ඡා කරමින්
4
#EthereumDropsBelow$2300
6,748 නැරඹීම්
123 සාකච්ඡා කරමින්
5
#BitcoinSlipsBelow$80KAgain
20,615 නැරඹීම්
92 සාකච්ඡා කරමින්
6
#ThailandLaunchesWORPTStablecoinToQRPaymentApp
37,809 නැරඹීම්
623 සාකච්ඡා කරමින්
7
#StrategySkipsBitcoinPurchasesSpends$205MOnSTRCBuybacks
8,739 නැරඹීම්
88 සාකච්ඡා කරමින්
8
#BitmineAdds10452ETH
77,258 නැරඹීම්
1,009 සාකච්ඡා කරමින්
9
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
40,966 නැරඹීම්
743 සාකච්ඡා කරමින්
10
#OCCUrgesCommunityBanksToEnterStablecoinPayments
31,756 නැරඹීම්
529 සාකච්ඡා කරමින්