
#coldcard
coldcard
135,095 views
474 Discussing
Hot
Latest

·
--
🚨 $BTC HACKER MOVES 45% THROUGH THORCHAIN TO ETH! 🦈
🦈 The Coldcard breach continues to ripple through the ecosystem as the attacker redirected 45% of the stolen 97.09 BTC (~$7.8 M) via THORChain into $ETH and layered CoinJoin mixers, a classic liquidity‑hunt play. 📊 This cross‑chain sweep underscores how bridges become the fastest conduit for laundering high‑value vaults.
🔍 With 82% of the loot still parked in hacker‑controlled addresses, the remaining stash is primed for another round of obfuscation. 💡 Expect intensified CoinJoin activity and potential pressure on bridge fees as smart money scrubs its trail.
🤔 Will regulators tighten bridge monitoring after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Coldcard #Hack #Liquidity #Crypto
🦈 🔥
🚨 $BTC HACKER MOVES 45% THROUGH THORCHAIN TO ETH! 🦈
🦈 The Coldcard breach continues to ripple through the ecosystem as the attacker redirected 45% of the stolen 97.09 BTC (~$7.8 M) via THORChain into $ETH and layered CoinJoin mixers, a classic liquidity‑hunt play. 📊 This cross‑chain sweep underscores how bridges become the fastest conduit for laundering high‑value vaults.
🔍 With 82% of the loot still parked in hacker‑controlled addresses, the remaining stash is primed for another round of obfuscation. 💡 Expect intensified CoinJoin activity and potential pressure on bridge fees as smart money scrubs its trail.
🤔 Will regulators tighten bridge monitoring after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Coldcard #Hack #Liquidity #Crypto
🦈 🔥
🦈 The Coldcard breach continues to ripple through the ecosystem as the attacker redirected 45% of the stolen 97.09 BTC (~$7.8 M) via THORChain into $ETH and layered CoinJoin mixers, a classic liquidity‑hunt play. 📊 This cross‑chain sweep underscores how bridges become the fastest conduit for laundering high‑value vaults.
🔍 With 82% of the loot still parked in hacker‑controlled addresses, the remaining stash is primed for another round of obfuscation. 💡 Expect intensified CoinJoin activity and potential pressure on bridge fees as smart money scrubs its trail.
🤔 Will regulators tighten bridge monitoring after this wave?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Coldcard #Hack #Liquidity #Crypto
🦈 🔥
27
·
--
Hacker Coldcard has transferred 45% of the stolen BTC in Wave 3!
According to Galaxy Research, the attacker has moved 45% of the stolen Bitcoin, equivalent to about 97.09 BTC (~$7.8 million), via THORChain to Ethereum and CoinJoin transactions to conceal the source of the funds.
Notably, the hacker is dealing with the “vaults” with the highest values one by one. Meanwhile, across all the attack waves, around 82% of the stolen BTC remains in addresses controlled by the hacker, while 18% has been moved.
The exploitation stems from a Coldcard firmware vulnerability that has persisted for many years, causing some wallets’ seed phrases to have weak randomness and be susceptible to brute-force attacks.
What is worrying right now is: how many remaining BTC will continue to be laundered through CoinJoin and cross-chain bridges?
#Bitcoin #Coldcard #Crypto #Cybersecurity
Hacker Coldcard has transferred 45% of the stolen BTC in Wave 3!
According to Galaxy Research, the attacker has moved 45% of the stolen Bitcoin, equivalent to about 97.09 BTC (~$7.8 million), via THORChain to Ethereum and CoinJoin transactions to conceal the source of the funds.
Notably, the hacker is dealing with the “vaults” with the highest values one by one. Meanwhile, across all the attack waves, around 82% of the stolen BTC remains in addresses controlled by the hacker, while 18% has been moved.
The exploitation stems from a Coldcard firmware vulnerability that has persisted for many years, causing some wallets’ seed phrases to have weak randomness and be susceptible to brute-force attacks.
What is worrying right now is: how many remaining BTC will continue to be laundered through CoinJoin and cross-chain bridges?
#Bitcoin #Coldcard #Crypto #Cybersecurity
According to Galaxy Research, the attacker has moved 45% of the stolen Bitcoin, equivalent to about 97.09 BTC (~$7.8 million), via THORChain to Ethereum and CoinJoin transactions to conceal the source of the funds.
Notably, the hacker is dealing with the “vaults” with the highest values one by one. Meanwhile, across all the attack waves, around 82% of the stolen BTC remains in addresses controlled by the hacker, while 18% has been moved.
The exploitation stems from a Coldcard firmware vulnerability that has persisted for many years, causing some wallets’ seed phrases to have weak randomness and be susceptible to brute-force attacks.
What is worrying right now is: how many remaining BTC will continue to be laundered through CoinJoin and cross-chain bridges?
#Bitcoin #Coldcard #Crypto #Cybersecurity
72
·
--
Article
Coldcard Hackers Move 45% of Stolen BTC, Galaxy SaysA recent wave of Bitcoin thefts has left 190 victims scrambling, but a new twist shows how attackers are moving the loot.
The Coldcard wallet, a popular hardware device for secure Bitcoin storage, has been exploited to siphon off a staggering 1,779 BTC—about 45% of the total stolen in what experts call “Wave 3” attacks. Galaxy, a leading blockchain analytics firm, uncovered the move as of mid‑August, revealing that the stolen coins have been shuffled through more than 8,600 addresses.
**What’s going on?**
Think of Bitcoin as a bank account that anyone can see, but only the owner has the keys. Coldcard is like a high‑security safe that many users trust to keep their keys offline. The recent exploit shows that attackers can break into the safe, grab the keys, and then move the money to a maze of addresses—making it hard for law‑enforcement to trace the trail. The 45% figure means almost half of the stolen funds are already on the move, which could signal a larger payout plan or a strategy to launder the coins.
**How the theft unfolded**
1. **Initial breach** – Hackers targeted Coldcard users, likely through phishing or supply‑chain attacks, gaining access to the device’s firmware.
2. **Stolen coins** – 1,779 BTC were extracted from 190 victims, a sum that would have made headlines if it stayed in one place.
3. **Moving the loot** – Galaxy traced the coins to over 8,600 addresses, showing a complex chain of transactions that spread the value across the network.
4. **Current status** – The coins are still circulating, and the attackers may be waiting for a market dip or a strategic moment to sell or swap them into other assets.
**Why this matters**
- **For users**: Even the most secure hardware wallets can be compromised if the supply chain or firmware is tampered with.
- **For the ecosystem**: Large‑scale thefts like this test the resilience of blockchain analytics and law‑enforcement tools.
- **For the market**: Moving large amounts of BTC can create volatility, especially if the coins are dumped in a short period.
**What you can do**
- Keep your firmware up to date and only download updates from the official Coldcard website.
- Use multi‑signature setups or additional layers of security, such as a second hardware wallet or a cold storage strategy.
- Stay informed: follow reputable analytics firms like Galaxy for real‑time alerts on suspicious activity.
#Bitcoin #Coldcard #CryptoSecurity
What steps are you taking to protect your crypto assets, and how do you feel about the current state of hardware wallet security?
Coldcard Hackers Move 45% of Stolen BTC, Galaxy Says
A recent wave of Bitcoin thefts has left 190 victims scrambling, but a new twist shows how attackers are moving the loot.
The Coldcard wallet, a popular hardware device for secure Bitcoin storage, has been exploited to siphon off a staggering 1,779 BTC—about 45% of the total stolen in what experts call “Wave 3” attacks. Galaxy, a leading blockchain analytics firm, uncovered the move as of mid‑August, revealing that the stolen coins have been shuffled through more than 8,600 addresses.
**What’s going on?**
Think of Bitcoin as a bank account that anyone can see, but only the owner has the keys. Coldcard is like a high‑security safe that many users trust to keep their keys offline. The recent exploit shows that attackers can break into the safe, grab the keys, and then move the money to a maze of addresses—making it hard for law‑enforcement to trace the trail. The 45% figure means almost half of the stolen funds are already on the move, which could signal a larger payout plan or a strategy to launder the coins.
**How the theft unfolded**
1. **Initial breach** – Hackers targeted Coldcard users, likely through phishing or supply‑chain attacks, gaining access to the device’s firmware.
2. **Stolen coins** – 1,779 BTC were extracted from 190 victims, a sum that would have made headlines if it stayed in one place.
3. **Moving the loot** – Galaxy traced the coins to over 8,600 addresses, showing a complex chain of transactions that spread the value across the network.
4. **Current status** – The coins are still circulating, and the attackers may be waiting for a market dip or a strategic moment to sell or swap them into other assets.
**Why this matters**
- **For users**: Even the most secure hardware wallets can be compromised if the supply chain or firmware is tampered with.
- **For the ecosystem**: Large‑scale thefts like this test the resilience of blockchain analytics and law‑enforcement tools.
- **For the market**: Moving large amounts of BTC can create volatility, especially if the coins are dumped in a short period.
**What you can do**
- Keep your firmware up to date and only download updates from the official Coldcard website.
- Use multi‑signature setups or additional layers of security, such as a second hardware wallet or a cold storage strategy.
- Stay informed: follow reputable analytics firms like Galaxy for real‑time alerts on suspicious activity.
#Bitcoin #Coldcard #CryptoSecurity
What steps are you taking to protect your crypto assets, and how do you feel about the current state of hardware wallet security?
The Coldcard wallet, a popular hardware device for secure Bitcoin storage, has been exploited to siphon off a staggering 1,779 BTC—about 45% of the total stolen in what experts call “Wave 3” attacks. Galaxy, a leading blockchain analytics firm, uncovered the move as of mid‑August, revealing that the stolen coins have been shuffled through more than 8,600 addresses.
**What’s going on?**
Think of Bitcoin as a bank account that anyone can see, but only the owner has the keys. Coldcard is like a high‑security safe that many users trust to keep their keys offline. The recent exploit shows that attackers can break into the safe, grab the keys, and then move the money to a maze of addresses—making it hard for law‑enforcement to trace the trail. The 45% figure means almost half of the stolen funds are already on the move, which could signal a larger payout plan or a strategy to launder the coins.
**How the theft unfolded**
1. **Initial breach** – Hackers targeted Coldcard users, likely through phishing or supply‑chain attacks, gaining access to the device’s firmware.
2. **Stolen coins** – 1,779 BTC were extracted from 190 victims, a sum that would have made headlines if it stayed in one place.
3. **Moving the loot** – Galaxy traced the coins to over 8,600 addresses, showing a complex chain of transactions that spread the value across the network.
4. **Current status** – The coins are still circulating, and the attackers may be waiting for a market dip or a strategic moment to sell or swap them into other assets.
**Why this matters**
- **For users**: Even the most secure hardware wallets can be compromised if the supply chain or firmware is tampered with.
- **For the ecosystem**: Large‑scale thefts like this test the resilience of blockchain analytics and law‑enforcement tools.
- **For the market**: Moving large amounts of BTC can create volatility, especially if the coins are dumped in a short period.
**What you can do**
- Keep your firmware up to date and only download updates from the official Coldcard website.
- Use multi‑signature setups or additional layers of security, such as a second hardware wallet or a cold storage strategy.
- Stay informed: follow reputable analytics firms like Galaxy for real‑time alerts on suspicious activity.
#Bitcoin #Coldcard #CryptoSecurity
What steps are you taking to protect your crypto assets, and how do you feel about the current state of hardware wallet security?
11

·
--
📰 Coldcard “Wave 3” money is still being moved out. Galaxy Research found that a previously unknown, identically structured 2-of-2 multisig vault made up of 58 addresses is very likely also a victim. Including it, the related vault count may have increased from 293 to 294, and the total stolen amount has been pushed up to about 1806 BTC.
🔥 Since September 2, the attacker has been using THORChain to bridge some funds to Ethereum, and more recently has moved them into CoinJoin mixing. To be honest, this operation is not about moving everything out at once; it is being handled slowly according to amount size, clearly splitting up the fund trail.
💡 At present, the vaults ranked 1 to 11 have already been processed. The next 10 untouched vaults still hold 30.81 BTC, and the vaults ranked 61 to 293 still hold a combined 33.77 BTC.
⚠️ Don’t mix up the two percentages: for Wave 3 alone, about 45% of the stolen coins have been moved; across the entire Coldcard attack scope, about 82% is still sitting in the attacker-controlled original addresses, while 18% has been moved for laundering.
🤔 If the remaining vaults also start moving into CoinJoin in order of amount, how many useful on-chain clues do you think can still be traced?
#Coldcard #BTC #链上安全 #cryptowallet
📰 Coldcard “Wave 3” money is still being moved out. Galaxy Research found that a previously unknown, identically structured 2-of-2 multisig vault made up of 58 addresses is very likely also a victim. Including it, the related vault count may have increased from 293 to 294, and the total stolen amount has been pushed up to about 1806 BTC.
🔥 Since September 2, the attacker has been using THORChain to bridge some funds to Ethereum, and more recently has moved them into CoinJoin mixing. To be honest, this operation is not about moving everything out at once; it is being handled slowly according to amount size, clearly splitting up the fund trail.
💡 At present, the vaults ranked 1 to 11 have already been processed. The next 10 untouched vaults still hold 30.81 BTC, and the vaults ranked 61 to 293 still hold a combined 33.77 BTC.
⚠️ Don’t mix up the two percentages: for Wave 3 alone, about 45% of the stolen coins have been moved; across the entire Coldcard attack scope, about 82% is still sitting in the attacker-controlled original addresses, while 18% has been moved for laundering.
🤔 If the remaining vaults also start moving into CoinJoin in order of amount, how many useful on-chain clues do you think can still be traced?
#Coldcard #BTC #链上安全 #cryptowallet
🔥 Since September 2, the attacker has been using THORChain to bridge some funds to Ethereum, and more recently has moved them into CoinJoin mixing. To be honest, this operation is not about moving everything out at once; it is being handled slowly according to amount size, clearly splitting up the fund trail.
💡 At present, the vaults ranked 1 to 11 have already been processed. The next 10 untouched vaults still hold 30.81 BTC, and the vaults ranked 61 to 293 still hold a combined 33.77 BTC.
⚠️ Don’t mix up the two percentages: for Wave 3 alone, about 45% of the stolen coins have been moved; across the entire Coldcard attack scope, about 82% is still sitting in the attacker-controlled original addresses, while 18% has been moved for laundering.
🤔 If the remaining vaults also start moving into CoinJoin in order of amount, how many useful on-chain clues do you think can still be traced?
#Coldcard #BTC #链上安全 #cryptowallet
60
·
--
Article
Coldcard, Trezor, SafePal hacks... Is Crypto Self-Custody Dead Now?August 2026 was a rollercoaster for the crypto space. Kind of a bad one. Just before the start of that month, some unknown attackers managed to take advantage of a bug in the Coldcard hardware wallets to steal up to 2,055 $BTC (~$130 million) directly from users. This is being considered the largest hardware wallet exploit to date. And it was followed by more attacks on Trezor and SafePal, two other major hardware wallet providers. Self-custody is thus called into question for many.
We’ve been told, repeatedly, that our private keys must remain offline, out of reach for hackers and scammers. Therefore, numerous crypto users have chosen to invest in more security and purchase specialized hardware devices to safeguard their coins. Now, among those who chose a Coldcard as this specialized device, several have lost their funds without even doing anything about it, because the attack was completely remote and out of their control.
It feels unfair. But wait, because there are still things to unpack before losing faith in self-custody.
So, What Happened to Coldcard and Company?
The first thing we must understand is that no, crypto networks aren’t just insecure now. The recent attacks weren’t against strong distributed ledgers, but against specific companies and their products. Let’s start with the Coldcard case: the problem came from the way certain devices generated wallet seeds or private keys.
In an average crypto wallet, just “guessing” seeds by applying brute force (many repetitive attempts) is impossible. A 12-word phrase alone has about 340 undecillion possibilities. This implies, as Knowing Bitcoin explains, that “if every computer on Earth tried a billion seed phrases per second, it would take trillions of times the current age of the universe to try them all." Unfortunately, it wasn’t like that for some Coldcard devices.
A software change introduced in 2021 caused certain devices to use a software-based pseudo-random number generator instead of the hardware-based random number generator intended for creating secure seeds. In other words, the wallet's security relied on insufficient randomness. Attackers were able to guess the private keys when they should never have been able to.
Even after applying a firmware fix, those seeds are just not suitable to use anymore. Anyone who has generated seeds on a Coldcard between 2021 and 2026 is advised to withdraw all their funds to a more secure wallet.
What about Trezor and SafePal?
At the very least, no funds were compromised in these two attacks. However, they can be considered equally serious, because personal data and physical addresses were, indeed, leaked. On August 12, Trezor informed that ShipMonk, one of their shipping providers, suffered a severe data breach that exposed the full names, phone numbers, email addresses, and physical addresses of almost 12,000 of its customers.
In the same fashion, barely some days later, SafePal announced the discovery of a bug that could let someone access or track customer order information without having the proper permission. Which some hackers did. Confidential data like names, phone numbers, emails, and physical addresses from almost 40,000 customers was stolen.
It seems "better" than having funds or private keys taken away, but it isn't. With all this information, hackers can easily find customers, carry out targeted attacks, phishing, and even plan "wrench attacks" or physical break-ins at their homes. Indeed, according to Certik, violent physical attacks against crypto users have increased by 33% in 2026, compared to the previous year.
Should we rush to crypto exchanges, then?
According to CMC, "Coldcard Hack Sends Bitcoiners Scrambling for CEXes." So, are they safer for us, after all? Is that a real solution in the long-term for crypto users? The answer isn't that simple. Centralized exchanges, even with tons of investment in security, can and have been hacked.
In 2025, Coinbase, one of the largest exchanges worldwide, suffered the same type of leak as Trezor and SafePal. In previous years, other firms like Liquid, KeepChange, Celsius, and OpenSea faced major data breaches, too. Beyond that, numerous crypto exchanges have been robbed or bankrupted over the years —or they were just scams from the beginning. Mt. Gox, QuadrigaCX, Cryptopia, and FTX are only some of them. Thousands of users globally suffered massive losses from these cases. That’s why this motto is so common in crypto: Not your keys? Not your coins.
However, now that self-custody appears to be threatened, what is the alternative? Where do we run to? You may think that, well, the flaws were limited to certain brands, so we just change brands and that’s it…! And that’s still not the answer. The answer is that nothing and no one is exempt from failure. Self-custody requires more responsibility, while external custody presents a different set of risks. That’s the thing, though.
Neither arrangement removes risk. They put different risks on different sides of the table, and you need to choose which of these risks is “less risky” for your own circumstances. Which benefits do you prefer (i.e., full ownership vs. convenience) and what are you willing to risk for them? Even fiat currencies and banks have their own risks and disadvantages, and their pitfalls are the whole reason why cryptocurrencies exist. Sad, but true.
New Lesson: Don't Put All Your Eggs in One Basket
Decentralize, like crypto networks themselves! If one device, one manufacturer, one backup, one company, or one process can determine whether your entire stash survives, that's a single point of failure you need to fix ASAP, no matter how secure you believe it is. There are several solutions for this.
A simple starting point is backup redundancy, with copies stored in separate locations so one fire, flood, or defective device doesn't wipe out everything. In Obyte, you can create several textcoins with different amounts in them, and store them offline. However, you’ll have to take care of noting down your textcoins (seeds), copying them to different secure locations, and taking care of them to the best of your ability. The only way for self-custody is high responsibility.
For stronger protection, multisignature wallets can require two or more separate keys before coins can be moved. A 2-of-3 setup, for example, uses three keys but requires any two to approve a transaction. That means losing one key doesn’t automatically lock you out, while compromising one key doesn’t give an attacker enough control. You can also spread keys across different devices or manufacturers, reducing dependence on one technology.
In Obyte, you can create a multisignature (multidevice) account in just a few steps to increase your security and, if you wish, include other people as co-signers, not just your own devices.
There’s also value in testing recovery. A backup that has never been checked is a plan on paper. A successful recovery test provides evidence that the plan works. And complexity deserves its own warning label. Every extra passphrase, device, location, and backup adds another thing to remember and maintain.
So, Is Crypto Self-Custody Dead?
No. If anything, the bumps along the road make the idea more mature. Self-custody avoids potential financial censorship and can give people full control, but control comes with homework, from understanding how keys are created to knowing where backups live and what happens when a device fails. To be prepared for a device to fail, even.
Self-custody means taking ownership of the entire security model, not just buying a device with the words “hardware wallet” on the box. Do your own research (DYOR) on every brand, every software, and every process. This is worth repeating: the only way for self-custody is high responsibility!
Originally Published on Hackernoon
#Coldcard #TrezorWallet #DataLeak #cryptohacks #Obyte
Coldcard, Trezor, SafePal hacks... Is Crypto Self-Custody Dead Now?
August 2026 was a rollercoaster for the crypto space. Kind of a bad one. Just before the start of that month, some unknown attackers managed to take advantage of a bug in the Coldcard hardware wallets to steal up to 2,055 $BTC (~$130 million) directly from users. This is being considered the largest hardware wallet exploit to date. And it was followed by more attacks on Trezor and SafePal, two other major hardware wallet providers. Self-custody is thus called into question for many.
We’ve been told, repeatedly, that our private keys must remain offline, out of reach for hackers and scammers. Therefore, numerous crypto users have chosen to invest in more security and purchase specialized hardware devices to safeguard their coins. Now, among those who chose a Coldcard as this specialized device, several have lost their funds without even doing anything about it, because the attack was completely remote and out of their control.
It feels unfair. But wait, because there are still things to unpack before losing faith in self-custody.
So, What Happened to Coldcard and Company?
The first thing we must understand is that no, crypto networks aren’t just insecure now. The recent attacks weren’t against strong distributed ledgers, but against specific companies and their products. Let’s start with the Coldcard case: the problem came from the way certain devices generated wallet seeds or private keys.
In an average crypto wallet, just “guessing” seeds by applying brute force (many repetitive attempts) is impossible. A 12-word phrase alone has about 340 undecillion possibilities. This implies, as Knowing Bitcoin explains, that “if every computer on Earth tried a billion seed phrases per second, it would take trillions of times the current age of the universe to try them all." Unfortunately, it wasn’t like that for some Coldcard devices.
A software change introduced in 2021 caused certain devices to use a software-based pseudo-random number generator instead of the hardware-based random number generator intended for creating secure seeds. In other words, the wallet's security relied on insufficient randomness. Attackers were able to guess the private keys when they should never have been able to.
Even after applying a firmware fix, those seeds are just not suitable to use anymore. Anyone who has generated seeds on a Coldcard between 2021 and 2026 is advised to withdraw all their funds to a more secure wallet.
What about Trezor and SafePal?
At the very least, no funds were compromised in these two attacks. However, they can be considered equally serious, because personal data and physical addresses were, indeed, leaked. On August 12, Trezor informed that ShipMonk, one of their shipping providers, suffered a severe data breach that exposed the full names, phone numbers, email addresses, and physical addresses of almost 12,000 of its customers.
In the same fashion, barely some days later, SafePal announced the discovery of a bug that could let someone access or track customer order information without having the proper permission. Which some hackers did. Confidential data like names, phone numbers, emails, and physical addresses from almost 40,000 customers was stolen.
It seems "better" than having funds or private keys taken away, but it isn't. With all this information, hackers can easily find customers, carry out targeted attacks, phishing, and even plan "wrench attacks" or physical break-ins at their homes. Indeed, according to Certik, violent physical attacks against crypto users have increased by 33% in 2026, compared to the previous year.
Should we rush to crypto exchanges, then?
According to CMC, "Coldcard Hack Sends Bitcoiners Scrambling for CEXes." So, are they safer for us, after all? Is that a real solution in the long-term for crypto users? The answer isn't that simple. Centralized exchanges, even with tons of investment in security, can and have been hacked.
In 2025, Coinbase, one of the largest exchanges worldwide, suffered the same type of leak as Trezor and SafePal. In previous years, other firms like Liquid, KeepChange, Celsius, and OpenSea faced major data breaches, too. Beyond that, numerous crypto exchanges have been robbed or bankrupted over the years —or they were just scams from the beginning. Mt. Gox, QuadrigaCX, Cryptopia, and FTX are only some of them. Thousands of users globally suffered massive losses from these cases. That’s why this motto is so common in crypto: Not your keys? Not your coins.
However, now that self-custody appears to be threatened, what is the alternative? Where do we run to? You may think that, well, the flaws were limited to certain brands, so we just change brands and that’s it…! And that’s still not the answer. The answer is that nothing and no one is exempt from failure. Self-custody requires more responsibility, while external custody presents a different set of risks. That’s the thing, though.
Neither arrangement removes risk. They put different risks on different sides of the table, and you need to choose which of these risks is “less risky” for your own circumstances. Which benefits do you prefer (i.e., full ownership vs. convenience) and what are you willing to risk for them? Even fiat currencies and banks have their own risks and disadvantages, and their pitfalls are the whole reason why cryptocurrencies exist. Sad, but true.
New Lesson: Don't Put All Your Eggs in One Basket
Decentralize, like crypto networks themselves! If one device, one manufacturer, one backup, one company, or one process can determine whether your entire stash survives, that's a single point of failure you need to fix ASAP, no matter how secure you believe it is. There are several solutions for this.
A simple starting point is backup redundancy, with copies stored in separate locations so one fire, flood, or defective device doesn't wipe out everything. In Obyte, you can create several textcoins with different amounts in them, and store them offline. However, you’ll have to take care of noting down your textcoins (seeds), copying them to different secure locations, and taking care of them to the best of your ability. The only way for self-custody is high responsibility.
For stronger protection, multisignature wallets can require two or more separate keys before coins can be moved. A 2-of-3 setup, for example, uses three keys but requires any two to approve a transaction. That means losing one key doesn’t automatically lock you out, while compromising one key doesn’t give an attacker enough control. You can also spread keys across different devices or manufacturers, reducing dependence on one technology.
In Obyte, you can create a multisignature (multidevice) account in just a few steps to increase your security and, if you wish, include other people as co-signers, not just your own devices.
There’s also value in testing recovery. A backup that has never been checked is a plan on paper. A successful recovery test provides evidence that the plan works. And complexity deserves its own warning label. Every extra passphrase, device, location, and backup adds another thing to remember and maintain.
So, Is Crypto Self-Custody Dead?
No. If anything, the bumps along the road make the idea more mature. Self-custody avoids potential financial censorship and can give people full control, but control comes with homework, from understanding how keys are created to knowing where backups live and what happens when a device fails. To be prepared for a device to fail, even.
Self-custody means taking ownership of the entire security model, not just buying a device with the words “hardware wallet” on the box. Do your own research (DYOR) on every brand, every software, and every process. This is worth repeating: the only way for self-custody is high responsibility!
Originally Published on Hackernoon
#Coldcard #TrezorWallet #DataLeak #cryptohacks #Obyte
We’ve been told, repeatedly, that our private keys must remain offline, out of reach for hackers and scammers. Therefore, numerous crypto users have chosen to invest in more security and purchase specialized hardware devices to safeguard their coins. Now, among those who chose a Coldcard as this specialized device, several have lost their funds without even doing anything about it, because the attack was completely remote and out of their control.
It feels unfair. But wait, because there are still things to unpack before losing faith in self-custody.
So, What Happened to Coldcard and Company?
The first thing we must understand is that no, crypto networks aren’t just insecure now. The recent attacks weren’t against strong distributed ledgers, but against specific companies and their products. Let’s start with the Coldcard case: the problem came from the way certain devices generated wallet seeds or private keys.
In an average crypto wallet, just “guessing” seeds by applying brute force (many repetitive attempts) is impossible. A 12-word phrase alone has about 340 undecillion possibilities. This implies, as Knowing Bitcoin explains, that “if every computer on Earth tried a billion seed phrases per second, it would take trillions of times the current age of the universe to try them all." Unfortunately, it wasn’t like that for some Coldcard devices.
A software change introduced in 2021 caused certain devices to use a software-based pseudo-random number generator instead of the hardware-based random number generator intended for creating secure seeds. In other words, the wallet's security relied on insufficient randomness. Attackers were able to guess the private keys when they should never have been able to.
Even after applying a firmware fix, those seeds are just not suitable to use anymore. Anyone who has generated seeds on a Coldcard between 2021 and 2026 is advised to withdraw all their funds to a more secure wallet.
What about Trezor and SafePal?
At the very least, no funds were compromised in these two attacks. However, they can be considered equally serious, because personal data and physical addresses were, indeed, leaked. On August 12, Trezor informed that ShipMonk, one of their shipping providers, suffered a severe data breach that exposed the full names, phone numbers, email addresses, and physical addresses of almost 12,000 of its customers.
In the same fashion, barely some days later, SafePal announced the discovery of a bug that could let someone access or track customer order information without having the proper permission. Which some hackers did. Confidential data like names, phone numbers, emails, and physical addresses from almost 40,000 customers was stolen.
It seems "better" than having funds or private keys taken away, but it isn't. With all this information, hackers can easily find customers, carry out targeted attacks, phishing, and even plan "wrench attacks" or physical break-ins at their homes. Indeed, according to Certik, violent physical attacks against crypto users have increased by 33% in 2026, compared to the previous year.
Should we rush to crypto exchanges, then?
According to CMC, "Coldcard Hack Sends Bitcoiners Scrambling for CEXes." So, are they safer for us, after all? Is that a real solution in the long-term for crypto users? The answer isn't that simple. Centralized exchanges, even with tons of investment in security, can and have been hacked.
In 2025, Coinbase, one of the largest exchanges worldwide, suffered the same type of leak as Trezor and SafePal. In previous years, other firms like Liquid, KeepChange, Celsius, and OpenSea faced major data breaches, too. Beyond that, numerous crypto exchanges have been robbed or bankrupted over the years —or they were just scams from the beginning. Mt. Gox, QuadrigaCX, Cryptopia, and FTX are only some of them. Thousands of users globally suffered massive losses from these cases. That’s why this motto is so common in crypto: Not your keys? Not your coins.
However, now that self-custody appears to be threatened, what is the alternative? Where do we run to? You may think that, well, the flaws were limited to certain brands, so we just change brands and that’s it…! And that’s still not the answer. The answer is that nothing and no one is exempt from failure. Self-custody requires more responsibility, while external custody presents a different set of risks. That’s the thing, though.
Neither arrangement removes risk. They put different risks on different sides of the table, and you need to choose which of these risks is “less risky” for your own circumstances. Which benefits do you prefer (i.e., full ownership vs. convenience) and what are you willing to risk for them? Even fiat currencies and banks have their own risks and disadvantages, and their pitfalls are the whole reason why cryptocurrencies exist. Sad, but true.
New Lesson: Don't Put All Your Eggs in One Basket
Decentralize, like crypto networks themselves! If one device, one manufacturer, one backup, one company, or one process can determine whether your entire stash survives, that's a single point of failure you need to fix ASAP, no matter how secure you believe it is. There are several solutions for this.
A simple starting point is backup redundancy, with copies stored in separate locations so one fire, flood, or defective device doesn't wipe out everything. In Obyte, you can create several textcoins with different amounts in them, and store them offline. However, you’ll have to take care of noting down your textcoins (seeds), copying them to different secure locations, and taking care of them to the best of your ability. The only way for self-custody is high responsibility.
For stronger protection, multisignature wallets can require two or more separate keys before coins can be moved. A 2-of-3 setup, for example, uses three keys but requires any two to approve a transaction. That means losing one key doesn’t automatically lock you out, while compromising one key doesn’t give an attacker enough control. You can also spread keys across different devices or manufacturers, reducing dependence on one technology.
In Obyte, you can create a multisignature (multidevice) account in just a few steps to increase your security and, if you wish, include other people as co-signers, not just your own devices.
There’s also value in testing recovery. A backup that has never been checked is a plan on paper. A successful recovery test provides evidence that the plan works. And complexity deserves its own warning label. Every extra passphrase, device, location, and backup adds another thing to remember and maintain.
So, Is Crypto Self-Custody Dead?
No. If anything, the bumps along the road make the idea more mature. Self-custody avoids potential financial censorship and can give people full control, but control comes with homework, from understanding how keys are created to knowing where backups live and what happens when a device fails. To be prepared for a device to fail, even.
Self-custody means taking ownership of the entire security model, not just buying a device with the words “hardware wallet” on the box. Do your own research (DYOR) on every brand, every software, and every process. This is worth repeating: the only way for self-custody is high responsibility!
Originally Published on Hackernoon
#Coldcard #TrezorWallet #DataLeak #cryptohacks #Obyte
24
·
--
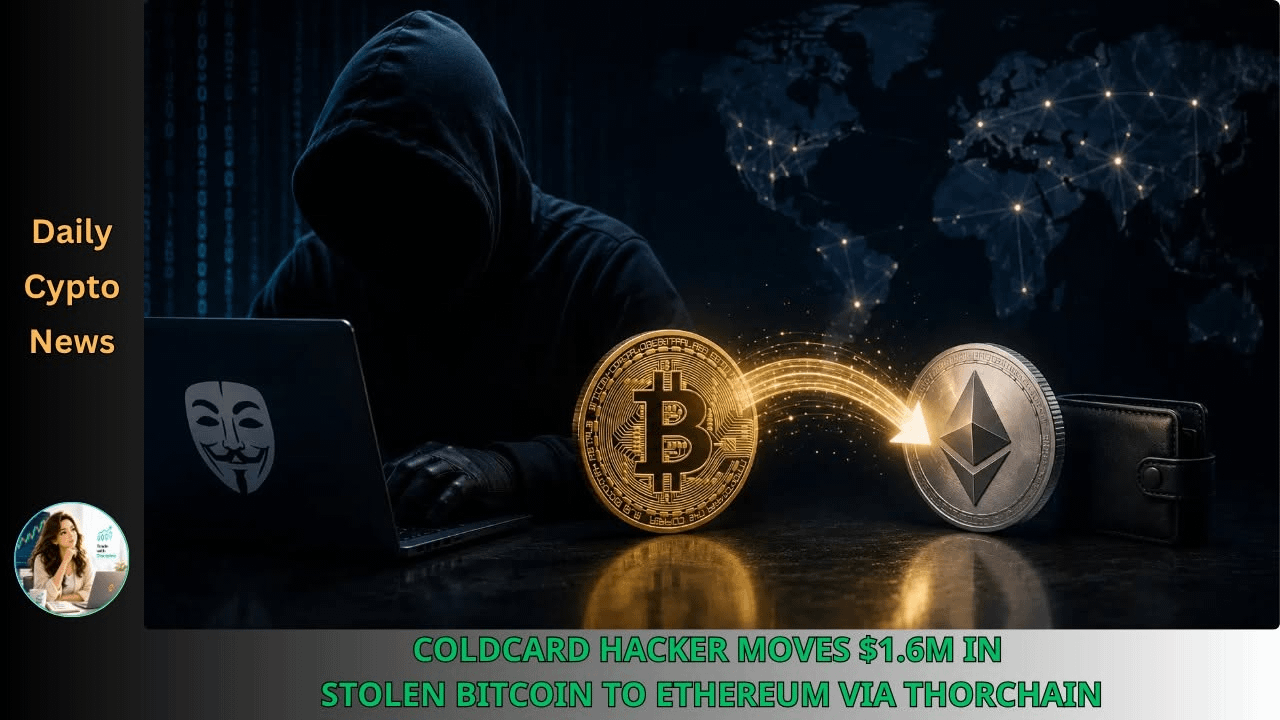
💥 COLDCARD HACKER SWAPS $1.6M BTC INTO ETHEREUM VIA THORCHAIN
Roughly 20.5 BTC ($1.6M) tied to the 2026 Coldcard hardware-wallet theft moved through 34 THORChain swaps into Ethereum on Sept. 2-3, per blockchain tracker Bitquery.
It's the first confirmed on-chain movement from the Wave 3 attacker's addresses.
The transfers turned a mostly dormant case into an active cross-chain trail — Galaxy Research says this represents roughly 10% of that wave's stolen funds, with about 90% still parked.
Most identified Bitcoin from the broader theft, over 1,400 BTC, remains unmoved and traceable.
Investigators have flagged the new Ethereum address to authorities and exchanges.
Do you think moving funds through THORChain actually help attackers cash out? Or does it just create a clearer trail for trackers to follow? 🧑
#Coldcard #BTC #THORChain #security
#ThuyBNB
$BTC $ETH $BNB
💥 COLDCARD HACKER SWAPS $1.6M BTC INTO ETHEREUM VIA THORCHAIN
Roughly 20.5 BTC ($1.6M) tied to the 2026 Coldcard hardware-wallet theft moved through 34 THORChain swaps into Ethereum on Sept. 2-3, per blockchain tracker Bitquery.
It's the first confirmed on-chain movement from the Wave 3 attacker's addresses.
The transfers turned a mostly dormant case into an active cross-chain trail — Galaxy Research says this represents roughly 10% of that wave's stolen funds, with about 90% still parked.
Most identified Bitcoin from the broader theft, over 1,400 BTC, remains unmoved and traceable.
Investigators have flagged the new Ethereum address to authorities and exchanges.
Do you think moving funds through THORChain actually help attackers cash out? Or does it just create a clearer trail for trackers to follow? 🧑
#Coldcard #BTC #THORChain #security
#ThuyBNB
$BTC $ETH $BNB
Roughly 20.5 BTC ($1.6M) tied to the 2026 Coldcard hardware-wallet theft moved through 34 THORChain swaps into Ethereum on Sept. 2-3, per blockchain tracker Bitquery.
It's the first confirmed on-chain movement from the Wave 3 attacker's addresses.
The transfers turned a mostly dormant case into an active cross-chain trail — Galaxy Research says this represents roughly 10% of that wave's stolen funds, with about 90% still parked.
Most identified Bitcoin from the broader theft, over 1,400 BTC, remains unmoved and traceable.
Investigators have flagged the new Ethereum address to authorities and exchanges.
Do you think moving funds through THORChain actually help attackers cash out? Or does it just create a clearer trail for trackers to follow? 🧑
#Coldcard #BTC #THORChain #security
#ThuyBNB
$BTC $ETH $BNB
84

·
--
Chinese:
The Coldcard hacker has started laundering money! The previously stolen bitcoins have finally moved; the $1.6 million in BTC was split into 34 cross-chain exchanges, and everything was converted into ETH. On-chain sleuths at Bitquery are watching the whole process.
The amount isn’t large and it doesn’t have any real impact on the trading screen, but it delivers another blow to trust in hardware wallets. What’s interesting is that the hacker is rushing to cash out—meaning he’s also afraid of getting stuck with them. That indirectly confirms that the current market isn’t very stable. In a choppy market, keeping control of your private keys is king.
#Coldcard黑客 #链上追踪 $BTC $ETH
English:
The Coldcard hacker is on the move! That stolen stash finally woke up - $1.6M in BTC split across 34 cross-chain swaps into ETH, and Bitquery is tracking every step.
Small money, no real market impact, but hardware wallet trust takes another hit. Funny how the thief is rushing to cash out - even he's scared of holding right now. That tells you something about the market. Guard your keys, folks.
#Coldcard #BitcoinSecurity $BTC $ETH
Chinese:
The Coldcard hacker has started laundering money! The previously stolen bitcoins have finally moved; the $1.6 million in BTC was split into 34 cross-chain exchanges, and everything was converted into ETH. On-chain sleuths at Bitquery are watching the whole process.
The amount isn’t large and it doesn’t have any real impact on the trading screen, but it delivers another blow to trust in hardware wallets. What’s interesting is that the hacker is rushing to cash out—meaning he’s also afraid of getting stuck with them. That indirectly confirms that the current market isn’t very stable. In a choppy market, keeping control of your private keys is king.
#Coldcard黑客 #链上追踪 $BTC $ETH
English:
The Coldcard hacker is on the move! That stolen stash finally woke up - $1.6M in BTC split across 34 cross-chain swaps into ETH, and Bitquery is tracking every step.
Small money, no real market impact, but hardware wallet trust takes another hit. Funny how the thief is rushing to cash out - even he's scared of holding right now. That tells you something about the market. Guard your keys, folks.
#Coldcard #BitcoinSecurity $BTC $ETH
The Coldcard hacker has started laundering money! The previously stolen bitcoins have finally moved; the $1.6 million in BTC was split into 34 cross-chain exchanges, and everything was converted into ETH. On-chain sleuths at Bitquery are watching the whole process.
The amount isn’t large and it doesn’t have any real impact on the trading screen, but it delivers another blow to trust in hardware wallets. What’s interesting is that the hacker is rushing to cash out—meaning he’s also afraid of getting stuck with them. That indirectly confirms that the current market isn’t very stable. In a choppy market, keeping control of your private keys is king.
#Coldcard黑客 #链上追踪 $BTC $ETH
English:
The Coldcard hacker is on the move! That stolen stash finally woke up - $1.6M in BTC split across 34 cross-chain swaps into ETH, and Bitquery is tracking every step.
Small money, no real market impact, but hardware wallet trust takes another hit. Funny how the thief is rushing to cash out - even he's scared of holding right now. That tells you something about the market. Guard your keys, folks.
#Coldcard #BitcoinSecurity $BTC $ETH
94
·
--
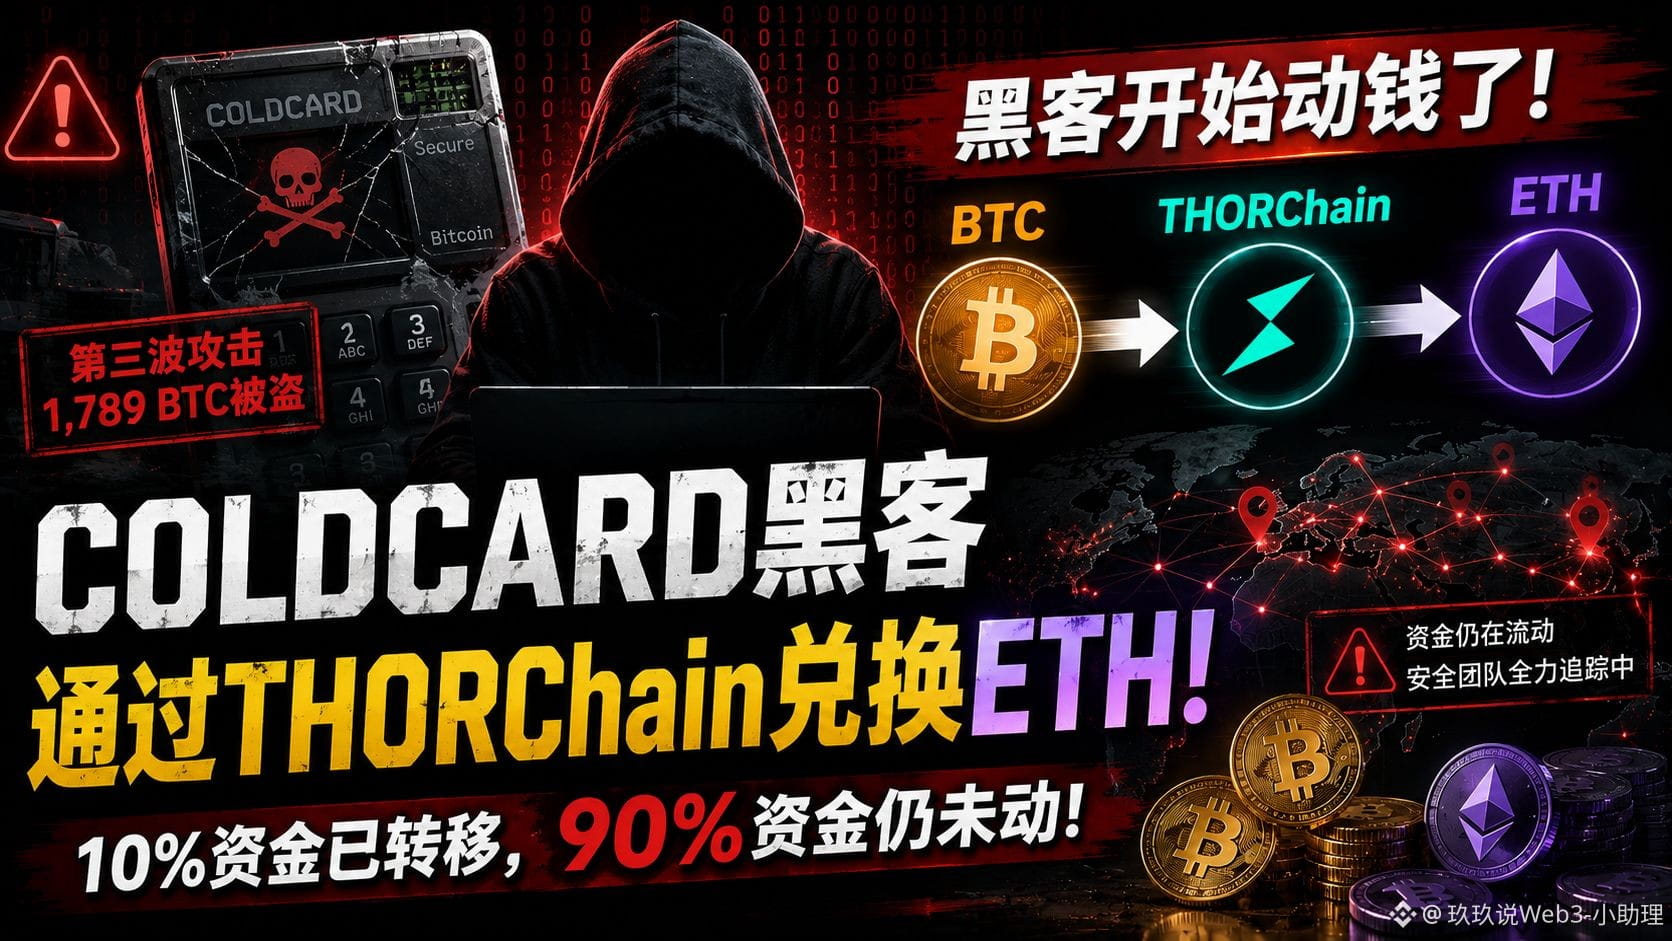
🚨 Coldcard hackers have started taking action!
The first stolen BTC has been swapped into ETH via THORChain, and the remaining 90% of the funds still haven’t moved!
Group: [点击进入玖玖的粉丝群](https://app.binance.com/uni-qr/YXXQJrPb)
The Coldcard hackers’ funds have finally begun to show clear activity.
Galaxy Research director Alex Thorn revealed that the hackers involved in the third wave of Coldcard attacks have started exchanging some of the stolen BTC into ETH via THORChain.
So far, about 10% of the funds have been transferred, while roughly 90% remains unmoved.
This is also the first time since the three waves of attacks that funds have been observed moving out from the original hacker address. ⚠️
What’s even more interesting is that this time the funds aren’t simply sent to an exchange.
On-chain analysis shows the attackers attempted to perform a cross-chain exchange through THORChain, converting BTC into ETH. But the process doesn’t seem to go smoothly.
Some transactions keep getting returned, forcing the hacker to try repeatedly. In the end, the on-chain analyst tracked the funds into a new Ethereum address.
What does this mean?
At the very least, it indicates the attacker has begun trying to change the on-chain form and transaction path of the stolen assets.
And this is exactly what the security team is paying the most attention to right now. Because once BTC is cross-chain converted into other assets, and then further split and transferred across multiple addresses, the difficulty of subsequent tracking may increase even more. However, it’s still not possible to determine what the hacker will do next.
They may continue with cross-chain operations, or they may try transferring assets in other ways.
Previously, Coldcard-related attacks were already believed to have caused large-scale BTC losses.
Galaxy Research linked the vulnerability to losses involving at least 1,789 BTC, sourced from 8,865 addresses, at the time worth about $114.7 million.
And this isn’t the first time the hackers have tried to hide funds.
Earlier, some BTC and ETH related to the attacks were deposited into crypto mixing services.
So this time, the funds becoming active again is a very important signal for the on-chain security team. 👀
Click the avatar to join the Jiujiu chat group for daily strategies 🚀
#BTC #Coldcard #THORChain
🚨 Coldcard hackers have started taking action!
The first stolen BTC has been swapped into ETH via THORChain, and the remaining 90% of the funds still haven’t moved!
Group: 点击进入玖玖的粉丝群
The Coldcard hackers’ funds have finally begun to show clear activity.
Galaxy Research director Alex Thorn revealed that the hackers involved in the third wave of Coldcard attacks have started exchanging some of the stolen BTC into ETH via THORChain.
So far, about 10% of the funds have been transferred, while roughly 90% remains unmoved.
This is also the first time since the three waves of attacks that funds have been observed moving out from the original hacker address. ⚠️
What’s even more interesting is that this time the funds aren’t simply sent to an exchange.
On-chain analysis shows the attackers attempted to perform a cross-chain exchange through THORChain, converting BTC into ETH. But the process doesn’t seem to go smoothly.
Some transactions keep getting returned, forcing the hacker to try repeatedly. In the end, the on-chain analyst tracked the funds into a new Ethereum address.
What does this mean?
At the very least, it indicates the attacker has begun trying to change the on-chain form and transaction path of the stolen assets.
And this is exactly what the security team is paying the most attention to right now. Because once BTC is cross-chain converted into other assets, and then further split and transferred across multiple addresses, the difficulty of subsequent tracking may increase even more. However, it’s still not possible to determine what the hacker will do next.
They may continue with cross-chain operations, or they may try transferring assets in other ways.
Previously, Coldcard-related attacks were already believed to have caused large-scale BTC losses.
Galaxy Research linked the vulnerability to losses involving at least 1,789 BTC, sourced from 8,865 addresses, at the time worth about $114.7 million.
And this isn’t the first time the hackers have tried to hide funds.
Earlier, some BTC and ETH related to the attacks were deposited into crypto mixing services.
So this time, the funds becoming active again is a very important signal for the on-chain security team. 👀
Click the avatar to join the Jiujiu chat group for daily strategies 🚀
#BTC #Coldcard #THORChain
The first stolen BTC has been swapped into ETH via THORChain, and the remaining 90% of the funds still haven’t moved!
Group: 点击进入玖玖的粉丝群
The Coldcard hackers’ funds have finally begun to show clear activity.
Galaxy Research director Alex Thorn revealed that the hackers involved in the third wave of Coldcard attacks have started exchanging some of the stolen BTC into ETH via THORChain.
So far, about 10% of the funds have been transferred, while roughly 90% remains unmoved.
This is also the first time since the three waves of attacks that funds have been observed moving out from the original hacker address. ⚠️
What’s even more interesting is that this time the funds aren’t simply sent to an exchange.
On-chain analysis shows the attackers attempted to perform a cross-chain exchange through THORChain, converting BTC into ETH. But the process doesn’t seem to go smoothly.
Some transactions keep getting returned, forcing the hacker to try repeatedly. In the end, the on-chain analyst tracked the funds into a new Ethereum address.
What does this mean?
At the very least, it indicates the attacker has begun trying to change the on-chain form and transaction path of the stolen assets.
And this is exactly what the security team is paying the most attention to right now. Because once BTC is cross-chain converted into other assets, and then further split and transferred across multiple addresses, the difficulty of subsequent tracking may increase even more. However, it’s still not possible to determine what the hacker will do next.
They may continue with cross-chain operations, or they may try transferring assets in other ways.
Previously, Coldcard-related attacks were already believed to have caused large-scale BTC losses.
Galaxy Research linked the vulnerability to losses involving at least 1,789 BTC, sourced from 8,865 addresses, at the time worth about $114.7 million.
And this isn’t the first time the hackers have tried to hide funds.
Earlier, some BTC and ETH related to the attacks were deposited into crypto mixing services.
So this time, the funds becoming active again is a very important signal for the on-chain security team. 👀
Click the avatar to join the Jiujiu chat group for daily strategies 🚀
#BTC #Coldcard #THORChain
199
·
--
[Coldcard hackers have finally moved! $11 million worth of BTC was swapped for ETH, and the funds are starting to be transferred🚨]
[🖥 进来跟进黑客最新动向](https://app.binance.com/uni-qr/7EcYBtCj)
A new development has emerged in the Coldcard wallet incident that has been steadily escalating.
According to on-chain data tracking, the Coldcard attacker has for the first time begun transferring the funds previously stolen. About $11 million worth of BTC was exchanged for ETH via THORChain.👀
What does this mean?
A large amount of stolen BTC had been sitting in wallets controlled by the hacker. Now, it’s starting to be converted across chains, suggesting the attacker is trying to get the money moving—and also bringing greater attention to subsequent tracking and fund security issues.⚠️
The Coldcard incident itself is also not small. Previous on-chain analysis showed the attack involved thousands of wallet addresses. More than a thousand BTC have already been confirmed as transferred, though the exact loss figure still varies due to different counting methodologies.
Even more noteworthy is that this isn’t a typical exchange hack—it’s a security issue related to a hardware wallet.
📌 So this is yet another reminder: so-called “cold wallets” don’t mean absolute security. If anything goes wrong—hardware, firmware, randomness generation, or private key management—massive losses can occur.🔐
📲 Jump into the fan group to keep up with the hacker’s moves!🔥
Every day, I’ll help you understand BTC, ETH, on-chain funds, and major crypto market hotspots—so you can catch the key signals that truly impact the market!🚀
#Coldcard
[Coldcard hackers have finally moved! $11 million worth of BTC was swapped for ETH, and the funds are starting to be transferred🚨]
🖥 进来跟进黑客最新动向
A new development has emerged in the Coldcard wallet incident that has been steadily escalating.
According to on-chain data tracking, the Coldcard attacker has for the first time begun transferring the funds previously stolen. About $11 million worth of BTC was exchanged for ETH via THORChain.👀
What does this mean?
A large amount of stolen BTC had been sitting in wallets controlled by the hacker. Now, it’s starting to be converted across chains, suggesting the attacker is trying to get the money moving—and also bringing greater attention to subsequent tracking and fund security issues.⚠️
The Coldcard incident itself is also not small. Previous on-chain analysis showed the attack involved thousands of wallet addresses. More than a thousand BTC have already been confirmed as transferred, though the exact loss figure still varies due to different counting methodologies.
Even more noteworthy is that this isn’t a typical exchange hack—it’s a security issue related to a hardware wallet.
📌 So this is yet another reminder: so-called “cold wallets” don’t mean absolute security. If anything goes wrong—hardware, firmware, randomness generation, or private key management—massive losses can occur.🔐
📲 Jump into the fan group to keep up with the hacker’s moves!🔥
Every day, I’ll help you understand BTC, ETH, on-chain funds, and major crypto market hotspots—so you can catch the key signals that truly impact the market!🚀
#Coldcard
🖥 进来跟进黑客最新动向
A new development has emerged in the Coldcard wallet incident that has been steadily escalating.
According to on-chain data tracking, the Coldcard attacker has for the first time begun transferring the funds previously stolen. About $11 million worth of BTC was exchanged for ETH via THORChain.👀
What does this mean?
A large amount of stolen BTC had been sitting in wallets controlled by the hacker. Now, it’s starting to be converted across chains, suggesting the attacker is trying to get the money moving—and also bringing greater attention to subsequent tracking and fund security issues.⚠️
The Coldcard incident itself is also not small. Previous on-chain analysis showed the attack involved thousands of wallet addresses. More than a thousand BTC have already been confirmed as transferred, though the exact loss figure still varies due to different counting methodologies.
Even more noteworthy is that this isn’t a typical exchange hack—it’s a security issue related to a hardware wallet.
📌 So this is yet another reminder: so-called “cold wallets” don’t mean absolute security. If anything goes wrong—hardware, firmware, randomness generation, or private key management—massive losses can occur.🔐
📲 Jump into the fan group to keep up with the hacker’s moves!🔥
Every day, I’ll help you understand BTC, ETH, on-chain funds, and major crypto market hotspots—so you can catch the key signals that truly impact the market!🚀
#Coldcard
1
2k


🔐 A Coldcard vulnerability may have put millions in Bitcoin at risk.
BTC Sessions said their team spent weeks helping Bitcoin holders affected by a Coldcard vulnerability move their assets to safety.
According to BTC Sessions, they estimate they helped protect tens of millions of USD worth of Bitcoin during this process.
But for some people, the move came too late.
A member of the community is said to have lost 90% of their BTC, while another person lost all of their Bitcoin.
The most frightening part here is not only the amount of money lost.
This is a very clear reminder that self-custody means you are the final layer of security.
A cold wallet is not a magic box.
Seed phrase, firmware, devices, and backup procedures can all become vulnerabilities if exploited.
The biggest lesson from this incident is probably not to put all your assets into a single security layer.
“Not your keys, not your coins.”
But if your keys are compromised… not your coins either. 💀
Do you think self-custody is becoming too complicated for everyday users, or is this the price of taking control of your own assets?
#bitcoin $BTC
{spot}(BTCUSDT)
#Coldcard #SelfCustody #CryptoSecurity
🔐 A Coldcard vulnerability may have put millions in Bitcoin at risk.
BTC Sessions said their team spent weeks helping Bitcoin holders affected by a Coldcard vulnerability move their assets to safety.
According to BTC Sessions, they estimate they helped protect tens of millions of USD worth of Bitcoin during this process.
But for some people, the move came too late.
A member of the community is said to have lost 90% of their BTC, while another person lost all of their Bitcoin.
The most frightening part here is not only the amount of money lost.
This is a very clear reminder that self-custody means you are the final layer of security.
A cold wallet is not a magic box.
Seed phrase, firmware, devices, and backup procedures can all become vulnerabilities if exploited.
The biggest lesson from this incident is probably not to put all your assets into a single security layer.
“Not your keys, not your coins.”
But if your keys are compromised… not your coins either. 💀
Do you think self-custody is becoming too complicated for everyday users, or is this the price of taking control of your own assets?
#bitcoin $BTC
#Coldcard #SelfCustody #CryptoSecurity
BTC Sessions said their team spent weeks helping Bitcoin holders affected by a Coldcard vulnerability move their assets to safety.
According to BTC Sessions, they estimate they helped protect tens of millions of USD worth of Bitcoin during this process.
But for some people, the move came too late.
A member of the community is said to have lost 90% of their BTC, while another person lost all of their Bitcoin.
The most frightening part here is not only the amount of money lost.
This is a very clear reminder that self-custody means you are the final layer of security.
A cold wallet is not a magic box.
Seed phrase, firmware, devices, and backup procedures can all become vulnerabilities if exploited.
The biggest lesson from this incident is probably not to put all your assets into a single security layer.
“Not your keys, not your coins.”
But if your keys are compromised… not your coins either. 💀
Do you think self-custody is becoming too complicated for everyday users, or is this the price of taking control of your own assets?
#bitcoin $BTC
#Coldcard #SelfCustody #CryptoSecurity
189

·
--
A day-by-day juxtaposition of the Coldcard vulnerability and the U.S. custody rules: the former exposes the risk in the key-seed generation process, while the latter brings back regulatory scrutiny over how institutions should hold digital assets.
According to a report by Bitcoin Magazine, Galaxy Research said the Bitcoin losses from the Coldcard theft incident reached $115 million. The report cites Coinkite as saying that some Coldcard Mk3 firmware causes seed generation to fall back to a weaker software pseudo-random number generator, which may allow an attacker to guess the seed phrase. Updating the device does not fix seeds that have already been generated; key generation, fund transfers, and subsequent signing are distinct security boundaries.
According to The Block, the U.S. Securities and Exchange Commission’s rule changes on how investment advisers hold digital assets have been submitted to the White House for review. The SEC said the rulemaking is intended to clarify the framework for investment advisers and investment companies to custody crypto assets and to modernize parts of the provisions. For now, it can only be confirmed that the rules have entered the review process; it cannot be written as already effective, nor can it be used to infer specific custody institutions or control measures.
The common issue in both stories is the control layer: how keys are generated, who can trigger transfers, whether transfers can be paused in abnormal situations, and how to confirm after migration that old credentials no longer control assets. Self-custody does not replace key-lifecycle management, and a regulatory framework does not replace engineering design for authorization, verification, and migration.
Position disclosure: This article is published by the operator of CoWallet and is for organizing industry information only, not investment advice.
Sources: The Block; Bitcoin Magazine
#自托管 #密钥安全 #加密监管 #Coldcard
A day-by-day juxtaposition of the Coldcard vulnerability and the U.S. custody rules: the former exposes the risk in the key-seed generation process, while the latter brings back regulatory scrutiny over how institutions should hold digital assets.
According to a report by Bitcoin Magazine, Galaxy Research said the Bitcoin losses from the Coldcard theft incident reached $115 million. The report cites Coinkite as saying that some Coldcard Mk3 firmware causes seed generation to fall back to a weaker software pseudo-random number generator, which may allow an attacker to guess the seed phrase. Updating the device does not fix seeds that have already been generated; key generation, fund transfers, and subsequent signing are distinct security boundaries.
According to The Block, the U.S. Securities and Exchange Commission’s rule changes on how investment advisers hold digital assets have been submitted to the White House for review. The SEC said the rulemaking is intended to clarify the framework for investment advisers and investment companies to custody crypto assets and to modernize parts of the provisions. For now, it can only be confirmed that the rules have entered the review process; it cannot be written as already effective, nor can it be used to infer specific custody institutions or control measures.
The common issue in both stories is the control layer: how keys are generated, who can trigger transfers, whether transfers can be paused in abnormal situations, and how to confirm after migration that old credentials no longer control assets. Self-custody does not replace key-lifecycle management, and a regulatory framework does not replace engineering design for authorization, verification, and migration.
Position disclosure: This article is published by the operator of CoWallet and is for organizing industry information only, not investment advice.
Sources: The Block; Bitcoin Magazine
#自托管 #密钥安全 #加密监管 #Coldcard
According to a report by Bitcoin Magazine, Galaxy Research said the Bitcoin losses from the Coldcard theft incident reached $115 million. The report cites Coinkite as saying that some Coldcard Mk3 firmware causes seed generation to fall back to a weaker software pseudo-random number generator, which may allow an attacker to guess the seed phrase. Updating the device does not fix seeds that have already been generated; key generation, fund transfers, and subsequent signing are distinct security boundaries.
According to The Block, the U.S. Securities and Exchange Commission’s rule changes on how investment advisers hold digital assets have been submitted to the White House for review. The SEC said the rulemaking is intended to clarify the framework for investment advisers and investment companies to custody crypto assets and to modernize parts of the provisions. For now, it can only be confirmed that the rules have entered the review process; it cannot be written as already effective, nor can it be used to infer specific custody institutions or control measures.
The common issue in both stories is the control layer: how keys are generated, who can trigger transfers, whether transfers can be paused in abnormal situations, and how to confirm after migration that old credentials no longer control assets. Self-custody does not replace key-lifecycle management, and a regulatory framework does not replace engineering design for authorization, verification, and migration.
Position disclosure: This article is published by the operator of CoWallet and is for organizing industry information only, not investment advice.
Sources: The Block; Bitcoin Magazine
#自托管 #密钥安全 #加密监管 #Coldcard
125
·
--
Coldcard hacking incident: approximately 1,789.28 BTC stolen, of which 87% of the stolen funds have not moved to date.
#BTC #Coldcard
Coldcard hacking incident: approximately 1,789.28 BTC stolen, of which 87% of the stolen funds have not moved to date.
#BTC #Coldcard
#BTC #Coldcard
70

Galaxy: Loses 1,789 BTC from Coldcard Hack, 87% Still Not Moved
- Galaxy Research updates 221 reports of victims of the Coldcard hack
- Over 50% of cases involve losses exceeding 1 Bitcoin
- Total losses amount to 1,789 BTC
- 87% of victims still have not moved their assets
#BinanceSquare #CryptoNews #Coldcard #Bitcoin #CryptoSecurity
$btc btc
vlikevn Titanbot
Source: CoinTelegraph
Galaxy: Loses 1,789 BTC from Coldcard Hack, 87% Still Not Moved
- Galaxy Research updates 221 reports of victims of the Coldcard hack
- Over 50% of cases involve losses exceeding 1 Bitcoin
- Total losses amount to 1,789 BTC
- 87% of victims still have not moved their assets
#BinanceSquare #CryptoNews #Coldcard #Bitcoin #CryptoSecurity
$btc btc
vlikevn Titanbot
Source: CoinTelegraph
- Galaxy Research updates 221 reports of victims of the Coldcard hack
- Over 50% of cases involve losses exceeding 1 Bitcoin
- Total losses amount to 1,789 BTC
- 87% of victims still have not moved their assets
#BinanceSquare #CryptoNews #Coldcard #Bitcoin #CryptoSecurity
$btc btc
vlikevn Titanbot
Source: CoinTelegraph
132
·
--
Bullish
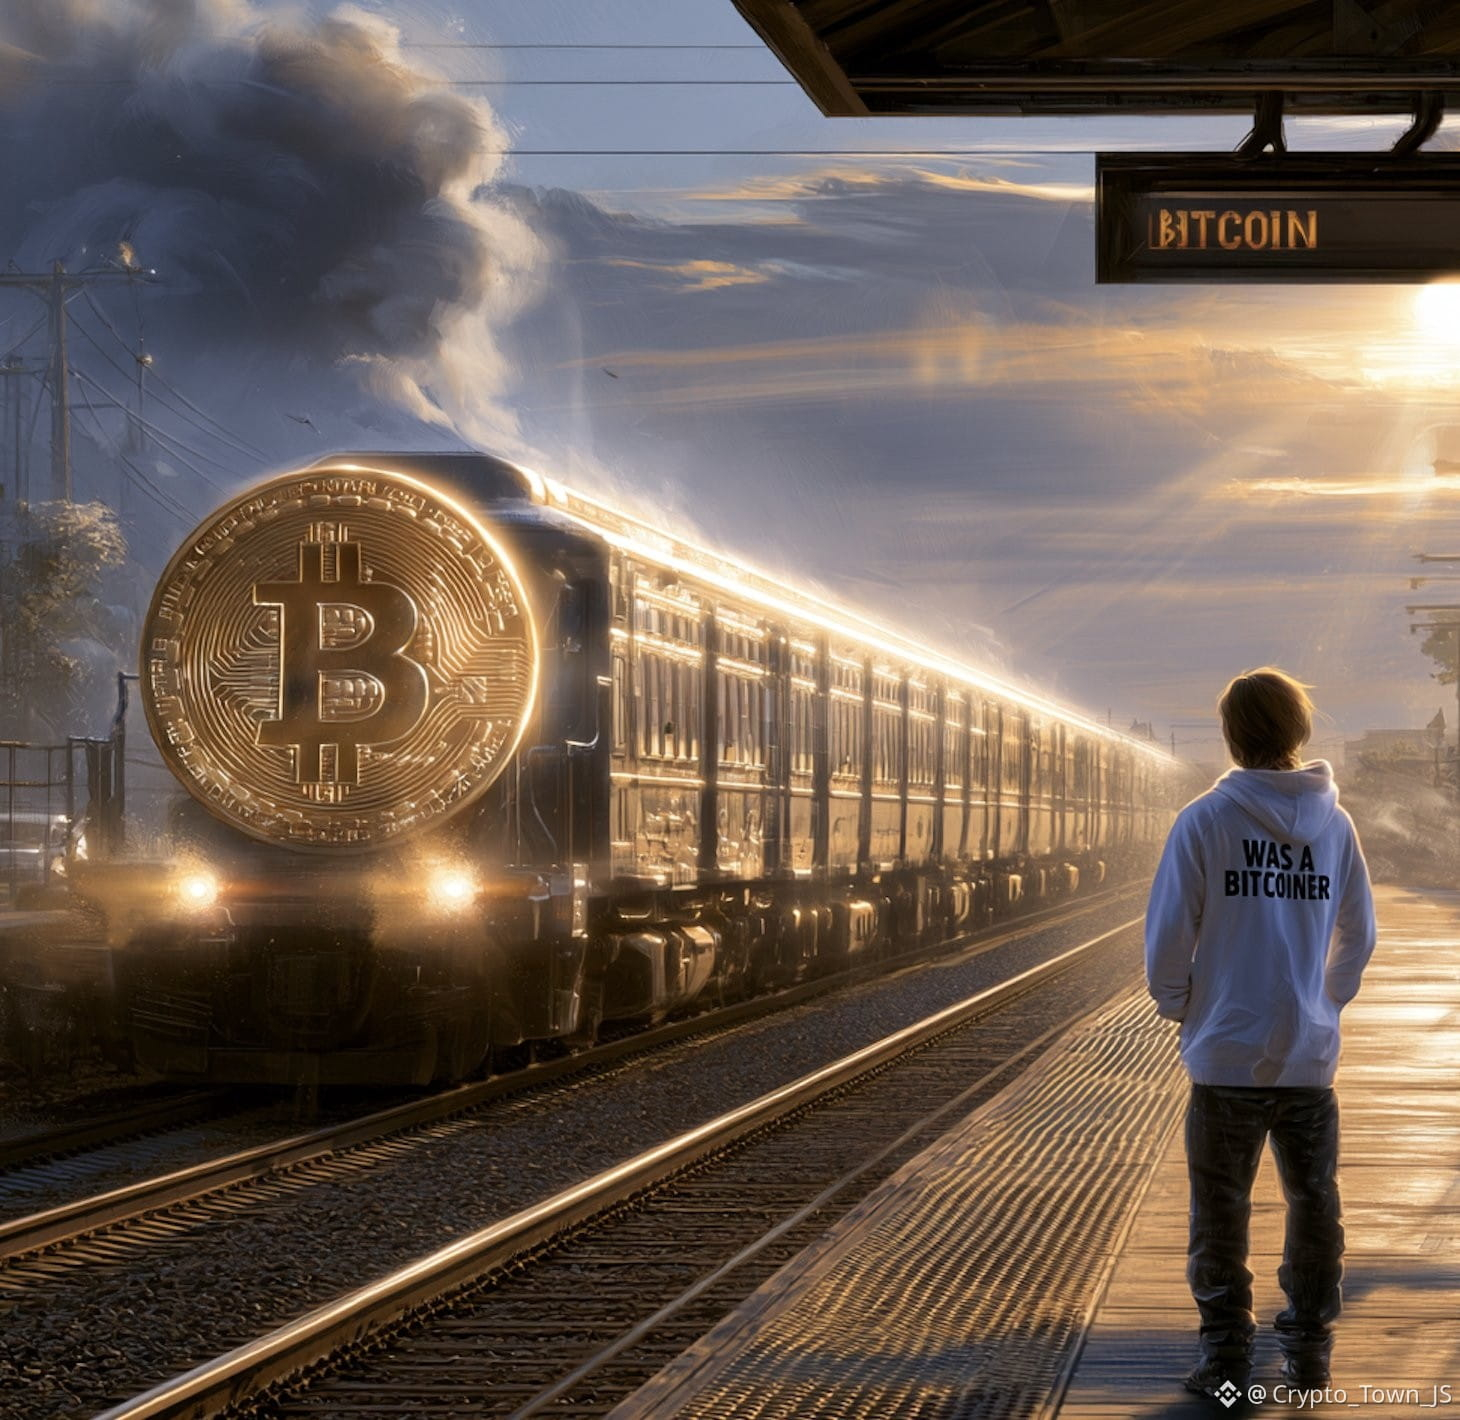
All aboard the Bitcoin train! 🚂🔥
Except... well, looking at the recent security nightmare, the poor Coldcarders are left standing on the platform like "Was a Bitcoiner". 💀📉
Hardware wallet security is no joke, fam. Always double-check your setups, stay safe out there, and protect your stack! 🛡️💼
What are your thoughts on this? Drop a comment below! 👇
#Bitcoin #crypto #Coldcard #BinanceSquare #CryptoSecurity
$BTC $ETH $BNB
{future}(BNBUSDT)
{future}(ETHUSDT)
{future}(BTCUSDT)
All aboard the Bitcoin train! 🚂🔥
Except... well, looking at the recent security nightmare, the poor Coldcarders are left standing on the platform like "Was a Bitcoiner". 💀📉
Hardware wallet security is no joke, fam. Always double-check your setups, stay safe out there, and protect your stack! 🛡️💼
What are your thoughts on this? Drop a comment below! 👇
#Bitcoin #crypto #Coldcard #BinanceSquare #CryptoSecurity
$BTC $ETH $BNB
Except... well, looking at the recent security nightmare, the poor Coldcarders are left standing on the platform like "Was a Bitcoiner". 💀📉
Hardware wallet security is no joke, fam. Always double-check your setups, stay safe out there, and protect your stack! 🛡️💼
What are your thoughts on this? Drop a comment below! 👇
#Bitcoin #crypto #Coldcard #BinanceSquare #CryptoSecurity
$BTC $ETH $BNB
89

⚠️ User expresses dissatisfaction over a security flaw in a ColdCard Q wallet
Reports indicate that a user destroyed their ColdCard Q wallet as a form of protest over a potential security flaw in the device’s firmware. This incident highlights the importance of robust firmware security and the need to educate users to maintain trust in hardware wallet solutions.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#ColdCard #HardwareWallet #Security #Firmware #Crypto
📰 Source: cryptobriefing.com
⚠️ User expresses dissatisfaction over a security flaw in a ColdCard Q wallet
Reports indicate that a user destroyed their ColdCard Q wallet as a form of protest over a potential security flaw in the device’s firmware. This incident highlights the importance of robust firmware security and the need to educate users to maintain trust in hardware wallet solutions.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#ColdCard #HardwareWallet #Security #Firmware #Crypto
📰 Source: cryptobriefing.com
Reports indicate that a user destroyed their ColdCard Q wallet as a form of protest over a potential security flaw in the device’s firmware. This incident highlights the importance of robust firmware security and the need to educate users to maintain trust in hardware wallet solutions.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#ColdCard #HardwareWallet #Security #Firmware #Crypto
📰 Source: cryptobriefing.com
19
·
--
Article
Coldcard Tightens Security After $130M BTC Breach – What It Means for Your WalletsMost traders focus on price, but the real signal is how the biggest wallets adapt to threats.
Coldcard, the hardware wallet brand that has long been the gold standard for institutional holders, just rolled out a firmware update that forces users to inject their own randomness when generating seed phrases. The move follows a $130 million Bitcoin exploit that exposed vulnerabilities in the device’s seed‑generation process.
#Coldcard #BTC #HardwareWallet
The new firmware requires a user‑supplied entropy source, effectively eliminating the risk of predictable seed generation that attackers exploited. In addition, the update patches several other cryptographic flaws uncovered during a three‑week audit that included both internal and external security teams.
What does this mean for the market?
1️⃣ Institutional confidence in hardware wallets is likely to rise, as the upgrade removes a major attack vector that could have undermined trust in custodial solutions.
2️⃣ The $BTC price may see a short‑term uptick as whale activity shifts toward more secure storage, reducing the risk of large‑scale thefts that historically have triggered panic selling.
3️⃣ On‑chain analytics show a spike in cold storage addresses after the breach, suggesting that many users are already migrating their holdings to more robust devices.
Watch List: Keep an eye on the #Coldcard firmware release notes and the on‑chain activity of addresses that have recently upgraded. A sudden surge in new seed‑generation transactions could signal a wave of users moving their assets out of vulnerable wallets.
If you’re still using a legacy hardware wallet, now is the time to upgrade. Are you ready to lock in the next layer of security before the next wave of exploits hits?
Coldcard Tightens Security After $130M BTC Breach – What It Means for Your Wallets
Most traders focus on price, but the real signal is how the biggest wallets adapt to threats.
Coldcard, the hardware wallet brand that has long been the gold standard for institutional holders, just rolled out a firmware update that forces users to inject their own randomness when generating seed phrases. The move follows a $130 million Bitcoin exploit that exposed vulnerabilities in the device’s seed‑generation process.
#Coldcard #BTC #HardwareWallet
The new firmware requires a user‑supplied entropy source, effectively eliminating the risk of predictable seed generation that attackers exploited. In addition, the update patches several other cryptographic flaws uncovered during a three‑week audit that included both internal and external security teams.
What does this mean for the market?
1️⃣ Institutional confidence in hardware wallets is likely to rise, as the upgrade removes a major attack vector that could have undermined trust in custodial solutions.
2️⃣ The $BTC price may see a short‑term uptick as whale activity shifts toward more secure storage, reducing the risk of large‑scale thefts that historically have triggered panic selling.
3️⃣ On‑chain analytics show a spike in cold storage addresses after the breach, suggesting that many users are already migrating their holdings to more robust devices.
Watch List: Keep an eye on the #Coldcard firmware release notes and the on‑chain activity of addresses that have recently upgraded. A sudden surge in new seed‑generation transactions could signal a wave of users moving their assets out of vulnerable wallets.
If you’re still using a legacy hardware wallet, now is the time to upgrade. Are you ready to lock in the next layer of security before the next wave of exploits hits?
Coldcard, the hardware wallet brand that has long been the gold standard for institutional holders, just rolled out a firmware update that forces users to inject their own randomness when generating seed phrases. The move follows a $130 million Bitcoin exploit that exposed vulnerabilities in the device’s seed‑generation process.
#Coldcard #BTC #HardwareWallet
The new firmware requires a user‑supplied entropy source, effectively eliminating the risk of predictable seed generation that attackers exploited. In addition, the update patches several other cryptographic flaws uncovered during a three‑week audit that included both internal and external security teams.
What does this mean for the market?
1️⃣ Institutional confidence in hardware wallets is likely to rise, as the upgrade removes a major attack vector that could have undermined trust in custodial solutions.
2️⃣ The $BTC price may see a short‑term uptick as whale activity shifts toward more secure storage, reducing the risk of large‑scale thefts that historically have triggered panic selling.
3️⃣ On‑chain analytics show a spike in cold storage addresses after the breach, suggesting that many users are already migrating their holdings to more robust devices.
Watch List: Keep an eye on the #Coldcard firmware release notes and the on‑chain activity of addresses that have recently upgraded. A sudden surge in new seed‑generation transactions could signal a wave of users moving their assets out of vulnerable wallets.
If you’re still using a legacy hardware wallet, now is the time to upgrade. Are you ready to lock in the next layer of security before the next wave of exploits hits?
28
·
--
Coldcard mandates 65 key presses after seed exploit affected wallets must migrate funds #Coldcard #HardwareWallet #Security
Coldcard mandates 65 key presses after seed exploit affected wallets must migrate funds #Coldcard #HardwareWallet #Security
7
·
--
Coldcard Hardware Wallet Now Requires 65 Key Presses After Seed ExploitPopular hardware wallet manufacturer Coldcard has released new firmware versions to address a seed phrase exposure vulnerability. According to CryptoSlate, versions 5.6.1 and 1.5.1Q significantly harden the new wallet creation process. Users must now press keys 65 times when initializing a new wallet, a measure designed to strengthen entropy sources and narrow potential attack vectors.
The most critical aspect of the update is the warning that seed phrases created on affected firmware versions cannot be repaired. Users who initialized wallets using the vulnerable releases must move their funds to a secure wallet. This highlights that hardware wallet security requires both software patches and user action.
Security researchers note that such vulnerabilities typically require physical access but still pose serious risks. The Coldcard team maintained transparent communication throughout the detection and patching process. Users can download firmware updates through official channels to secure their devices.
This incident demonstrates that security auditing of crypto custody solutions is an ongoing process. For hardware wallet users, regular firmware monitoring and following official announcements remains essential.
#Coldcard #HardwareWallet #Security
Sources: CryptoSlate
This news digest was compiled with AI assistance; it is not financial advice. Always do your own research (DYOR).
Coldcard Hardware Wallet Now Requires 65 Key Presses After Seed Exploit
Popular hardware wallet manufacturer Coldcard has released new firmware versions to address a seed phrase exposure vulnerability. According to CryptoSlate, versions 5.6.1 and 1.5.1Q significantly harden the new wallet creation process. Users must now press keys 65 times when initializing a new wallet, a measure designed to strengthen entropy sources and narrow potential attack vectors.
The most critical aspect of the update is the warning that seed phrases created on affected firmware versions cannot be repaired. Users who initialized wallets using the vulnerable releases must move their funds to a secure wallet. This highlights that hardware wallet security requires both software patches and user action.
Security researchers note that such vulnerabilities typically require physical access but still pose serious risks. The Coldcard team maintained transparent communication throughout the detection and patching process. Users can download firmware updates through official channels to secure their devices.
This incident demonstrates that security auditing of crypto custody solutions is an ongoing process. For hardware wallet users, regular firmware monitoring and following official announcements remains essential.
#Coldcard #HardwareWallet #Security
Sources: CryptoSlate
This news digest was compiled with AI assistance; it is not financial advice. Always do your own research (DYOR).
The most critical aspect of the update is the warning that seed phrases created on affected firmware versions cannot be repaired. Users who initialized wallets using the vulnerable releases must move their funds to a secure wallet. This highlights that hardware wallet security requires both software patches and user action.
Security researchers note that such vulnerabilities typically require physical access but still pose serious risks. The Coldcard team maintained transparent communication throughout the detection and patching process. Users can download firmware updates through official channels to secure their devices.
This incident demonstrates that security auditing of crypto custody solutions is an ongoing process. For hardware wallet users, regular firmware monitoring and following official announcements remains essential.
#Coldcard #HardwareWallet #Security
Sources: CryptoSlate
This news digest was compiled with AI assistance; it is not financial advice. Always do your own research (DYOR).
14
·
--
Coldcard forced 65 key presses after the seed phrase leakage; affected wallets must be moved #Coldcard #HardwareWallet #Security
Coldcard forced 65 key presses after the seed phrase leakage; affected wallets must be moved #Coldcard #HardwareWallet #Security
14
·
--
Coldcard Hardware Wallet Security Flaw Now Requires 65 Button PressesPopular hardware wallet manufacturer Coldcard has released new firmware versions to address a seed disclosure security vulnerability. According to CryptoSlate, the 5.6.1 and 1.5.1Q releases significantly harden the new wallet creation process. Users now have to press the button 65 times when starting a new wallet; this is intended to strengthen randomness sources and narrow possible attack vectors.
The most critical point of the update is the warning that seed phrases created with the affected firmware versions cannot be repaired. It emphasizes that users who set up a wallet using one of the affected versions should move their funds to a secure wallet. This serves as a reminder that hardware wallet security must be ensured not only through software updates, but also through user actions.
Coldcard Hardware Wallet Security Flaw Now Requires 65 Button Presses
Popular hardware wallet manufacturer Coldcard has released new firmware versions to address a seed disclosure security vulnerability. According to CryptoSlate, the 5.6.1 and 1.5.1Q releases significantly harden the new wallet creation process. Users now have to press the button 65 times when starting a new wallet; this is intended to strengthen randomness sources and narrow possible attack vectors.
The most critical point of the update is the warning that seed phrases created with the affected firmware versions cannot be repaired. It emphasizes that users who set up a wallet using one of the affected versions should move their funds to a secure wallet. This serves as a reminder that hardware wallet security must be ensured not only through software updates, but also through user actions.
The most critical point of the update is the warning that seed phrases created with the affected firmware versions cannot be repaired. It emphasizes that users who set up a wallet using one of the affected versions should move their funds to a secure wallet. This serves as a reminder that hardware wallet security must be ensured not only through software updates, but also through user actions.
19
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#AnthropicCEOCallsForAISlowdown
89,431 views
1,391 Discussing
2
#BitcoinThirdSingleBlockReorgInFourWeeks
15,108 views
485 Discussing
3
#EthereumFallsBelow$2500
1,123 views
60 Discussing
4
#BitcoinDropsToIntradayLow$76367
544 views
22 Discussing
5
#WhiteHouseRejectsAISlowdownCalls
2,352 views
141 Discussing
6
#UKMayExemptTokenizedGoldFromFundRules
1,756 views
101 Discussing
7
#BitcoinSpotETFsRecord$463MNetOutflowLastWeek
132 views
9 Discussing
8
#LSKSurgesOver515%In24Hours
13,456 views
273 Discussing
9
#ClarityActLawIn2026OddsRiseTo30%
10,930 views
160 Discussing
10
#KoreaCryptoTaxDelayPetitionMeetsReviewThreshold
2,745 views
84 Discussing