
#bugbounty
bugbounty
6,481 නැරඹීම්
46 සාකච්ඡා කරමින්
උණුසුම්
නවතම
·
--
A bug bounty doesn't pay by the browser tab. Otherwise, research would be a very different profession.
Immunefi's own program offers conditional rewards for qualifying security findings. You'll need a proof of concept and an in-scope impact. Known issues, duplicate reports and findings that don't qualify can earn nothing.
Payout requires KYC, and residents of countries restricted by OFAC or UN Security Council resolutions are excluded. Rewards are paid in USDC on Ethereum.
Budget research time and computing costs. No token purchase is listed as an entry requirement. Smart-contract testing must use local forks; third-party systems and disruptive testing are prohibited.
Read the scope first, then choose one permitted asset and one testable question. More tabs are optional.
https://immunefi.com/bug-bounty/immunefi/information/
$ETH
#BugBounty #SmartContractSecurity
A bug bounty doesn't pay by the browser tab. Otherwise, research would be a very different profession.
Immunefi's own program offers conditional rewards for qualifying security findings. You'll need a proof of concept and an in-scope impact. Known issues, duplicate reports and findings that don't qualify can earn nothing.
Payout requires KYC, and residents of countries restricted by OFAC or UN Security Council resolutions are excluded. Rewards are paid in USDC on Ethereum.
Budget research time and computing costs. No token purchase is listed as an entry requirement. Smart-contract testing must use local forks; third-party systems and disruptive testing are prohibited.
Read the scope first, then choose one permitted asset and one testable question. More tabs are optional.
https://immunefi.com/bug-bounty/immunefi/information/
$ETH
#BugBounty #SmartContractSecurity
Immunefi's own program offers conditional rewards for qualifying security findings. You'll need a proof of concept and an in-scope impact. Known issues, duplicate reports and findings that don't qualify can earn nothing.
Payout requires KYC, and residents of countries restricted by OFAC or UN Security Council resolutions are excluded. Rewards are paid in USDC on Ethereum.
Budget research time and computing costs. No token purchase is listed as an entry requirement. Smart-contract testing must use local forks; third-party systems and disruptive testing are prohibited.
Read the scope first, then choose one permitted asset and one testable question. More tabs are optional.
https://immunefi.com/bug-bounty/immunefi/information/
$ETH
#BugBounty #SmartContractSecurity
109

$ETH ATTACKER RETURNS $2M IN ETH — BUG BOUNTY OR FEAR FACTOR? 💎
The TrustedVolumes exploiter has sent back 1,122 ETH worth over $2 million after initially draining $5.8 million in assets on May 7. The attacker converted the stolen funds into roughly 2,513 ETH and has now returned nearly half, keeping about $2 million as a "bug bounty."
This creates an interesting liquidity event — nearly half the stolen ETH is back in play, which could add selling pressure or signal a shift in attacker sentiment. The market often reacts to sudden on-chain movements like this.
Are you watching wallet activity more closely right now?
Not financial advice. Always manage your risk.
#ETH #OnChain #CryptoNews #BugBounty
💎
$ETH ATTACKER RETURNS $2M IN ETH — BUG BOUNTY OR FEAR FACTOR? 💎
The TrustedVolumes exploiter has sent back 1,122 ETH worth over $2 million after initially draining $5.8 million in assets on May 7. The attacker converted the stolen funds into roughly 2,513 ETH and has now returned nearly half, keeping about $2 million as a "bug bounty."
This creates an interesting liquidity event — nearly half the stolen ETH is back in play, which could add selling pressure or signal a shift in attacker sentiment. The market often reacts to sudden on-chain movements like this.
Are you watching wallet activity more closely right now?
Not financial advice. Always manage your risk.
#ETH #OnChain #CryptoNews #BugBounty
💎
The TrustedVolumes exploiter has sent back 1,122 ETH worth over $2 million after initially draining $5.8 million in assets on May 7. The attacker converted the stolen funds into roughly 2,513 ETH and has now returned nearly half, keeping about $2 million as a "bug bounty."
This creates an interesting liquidity event — nearly half the stolen ETH is back in play, which could add selling pressure or signal a shift in attacker sentiment. The market often reacts to sudden on-chain movements like this.
Are you watching wallet activity more closely right now?
Not financial advice. Always manage your risk.
#ETH #OnChain #CryptoNews #BugBounty
💎
17

·
--
Crypto Hacks Surpass $100M in July Amid Soaring Bug ReportsThe crypto market is witnessing a concerning trend, with a staggering $110 million lost to hacks in July alone, according to Immunefi's latest report. This alarming figure highlights the increasing vulnerability of projects, especially those opting for private audits over public ones. What's even more eye-opening is that bug bounty reports skyrocketed in the same period, indicating a significant jump in confirmed vulnerabilities.
Immunefi's data reveals that private audits, often touted as more secure, actually uncovered fewer critical issues compared to public audit competitions. This discrepancy underscores the importance of transparency in identifying potential security threats early on. As a result, smart money is taking notice – the influx of new, innovative security-focused solutions is witnessing a surge in adoption, indicating that investors are increasingly prioritizing secure infrastructure #CryptoSecurity #BugBounty.
The $110 million lost in July puts 2026 on track for a record-breaking year in crypto hacks. This disturbing pattern should serve as a wake-up call for projects to reassess their security protocols and consider implementing more comprehensive audit measures. With hackers becoming increasingly sophisticated and a growing number of bug bounty reports, it's imperative for projects to stay vigilant.
As we move forward, look out for $SOL as a major cryptocurrency that has been actively investing in improving its security infrastructure. The Solana Network has already taken steps to enhance its security and prevent such hacks in the future. This move is a step in the right direction and could potentially safeguard users' assets, ultimately driving more confidence in the market.
What does this trend say about the state of crypto security, and how should investors respond?
Crypto Hacks Surpass $100M in July Amid Soaring Bug Reports
The crypto market is witnessing a concerning trend, with a staggering $110 million lost to hacks in July alone, according to Immunefi's latest report. This alarming figure highlights the increasing vulnerability of projects, especially those opting for private audits over public ones. What's even more eye-opening is that bug bounty reports skyrocketed in the same period, indicating a significant jump in confirmed vulnerabilities.
Immunefi's data reveals that private audits, often touted as more secure, actually uncovered fewer critical issues compared to public audit competitions. This discrepancy underscores the importance of transparency in identifying potential security threats early on. As a result, smart money is taking notice – the influx of new, innovative security-focused solutions is witnessing a surge in adoption, indicating that investors are increasingly prioritizing secure infrastructure #CryptoSecurity #BugBounty.
The $110 million lost in July puts 2026 on track for a record-breaking year in crypto hacks. This disturbing pattern should serve as a wake-up call for projects to reassess their security protocols and consider implementing more comprehensive audit measures. With hackers becoming increasingly sophisticated and a growing number of bug bounty reports, it's imperative for projects to stay vigilant.
As we move forward, look out for $SOL as a major cryptocurrency that has been actively investing in improving its security infrastructure. The Solana Network has already taken steps to enhance its security and prevent such hacks in the future. This move is a step in the right direction and could potentially safeguard users' assets, ultimately driving more confidence in the market.
What does this trend say about the state of crypto security, and how should investors respond?
Immunefi's data reveals that private audits, often touted as more secure, actually uncovered fewer critical issues compared to public audit competitions. This discrepancy underscores the importance of transparency in identifying potential security threats early on. As a result, smart money is taking notice – the influx of new, innovative security-focused solutions is witnessing a surge in adoption, indicating that investors are increasingly prioritizing secure infrastructure #CryptoSecurity #BugBounty.
The $110 million lost in July puts 2026 on track for a record-breaking year in crypto hacks. This disturbing pattern should serve as a wake-up call for projects to reassess their security protocols and consider implementing more comprehensive audit measures. With hackers becoming increasingly sophisticated and a growing number of bug bounty reports, it's imperative for projects to stay vigilant.
As we move forward, look out for $SOL as a major cryptocurrency that has been actively investing in improving its security infrastructure. The Solana Network has already taken steps to enhance its security and prevent such hacks in the future. This move is a step in the right direction and could potentially safeguard users' assets, ultimately driving more confidence in the market.
What does this trend say about the state of crypto security, and how should investors respond?
23
🔥 $334K vanished in seconds as ZetaChain brushed off a pre‑reported bug, turning a preventable exploit into a headline‑grabbing loss.
📊 With market sentiment still in Greed territory (71/100) and BTC slipping to $79,069 (‑1.06% 24h) while futures OI holds at $8.46B, any breach that shakes confidence can tip the delicate risk balance.
💡 Smart money is already recalibrating: top BTC futures traders remain net long at 66.4% despite the dip, and the lingering $334K loss fuels a surge in #SecurityTokens scrutiny, #CrossChain risk assessments, and a renewed #BugBounty appetite across DeFi projects.
🚀 Watch the BTC $78,500 support – a break below it could accelerate margin squeezes, while a clean retest may reaffirm that institutional longs are still in control; the next funding tick (+0.0045%) will be the litmus test for whether the market absorbs the shock.
❓ Are we witnessing a turning point where ignored security signals become the new catalyst for capital flight, or will the long bias in futures absorb the fallout and keep the rally intact?
🔥 $334K vanished in seconds as ZetaChain brushed off a pre‑reported bug, turning a preventable exploit into a headline‑grabbing loss.
📊 With market sentiment still in Greed territory (71/100) and BTC slipping to $79,069 (‑1.06% 24h) while futures OI holds at $8.46B, any breach that shakes confidence can tip the delicate risk balance.
💡 Smart money is already recalibrating: top BTC futures traders remain net long at 66.4% despite the dip, and the lingering $334K loss fuels a surge in #SecurityTokens scrutiny, #CrossChain risk assessments, and a renewed #BugBounty appetite across DeFi projects.
🚀 Watch the BTC $78,500 support – a break below it could accelerate margin squeezes, while a clean retest may reaffirm that institutional longs are still in control; the next funding tick (+0.0045%) will be the litmus test for whether the market absorbs the shock.
❓ Are we witnessing a turning point where ignored security signals become the new catalyst for capital flight, or will the long bias in futures absorb the fallout and keep the rally intact?
📊 With market sentiment still in Greed territory (71/100) and BTC slipping to $79,069 (‑1.06% 24h) while futures OI holds at $8.46B, any breach that shakes confidence can tip the delicate risk balance.
💡 Smart money is already recalibrating: top BTC futures traders remain net long at 66.4% despite the dip, and the lingering $334K loss fuels a surge in #SecurityTokens scrutiny, #CrossChain risk assessments, and a renewed #BugBounty appetite across DeFi projects.
🚀 Watch the BTC $78,500 support – a break below it could accelerate margin squeezes, while a clean retest may reaffirm that institutional longs are still in control; the next funding tick (+0.0045%) will be the litmus test for whether the market absorbs the shock.
❓ Are we witnessing a turning point where ignored security signals become the new catalyst for capital flight, or will the long bias in futures absorb the fallout and keep the rally intact?
62

·
--
🚨 $SOL BUG BOUNTY ALERT: SPAM FILTER REQUIRES 1 SOL FEE! 💥
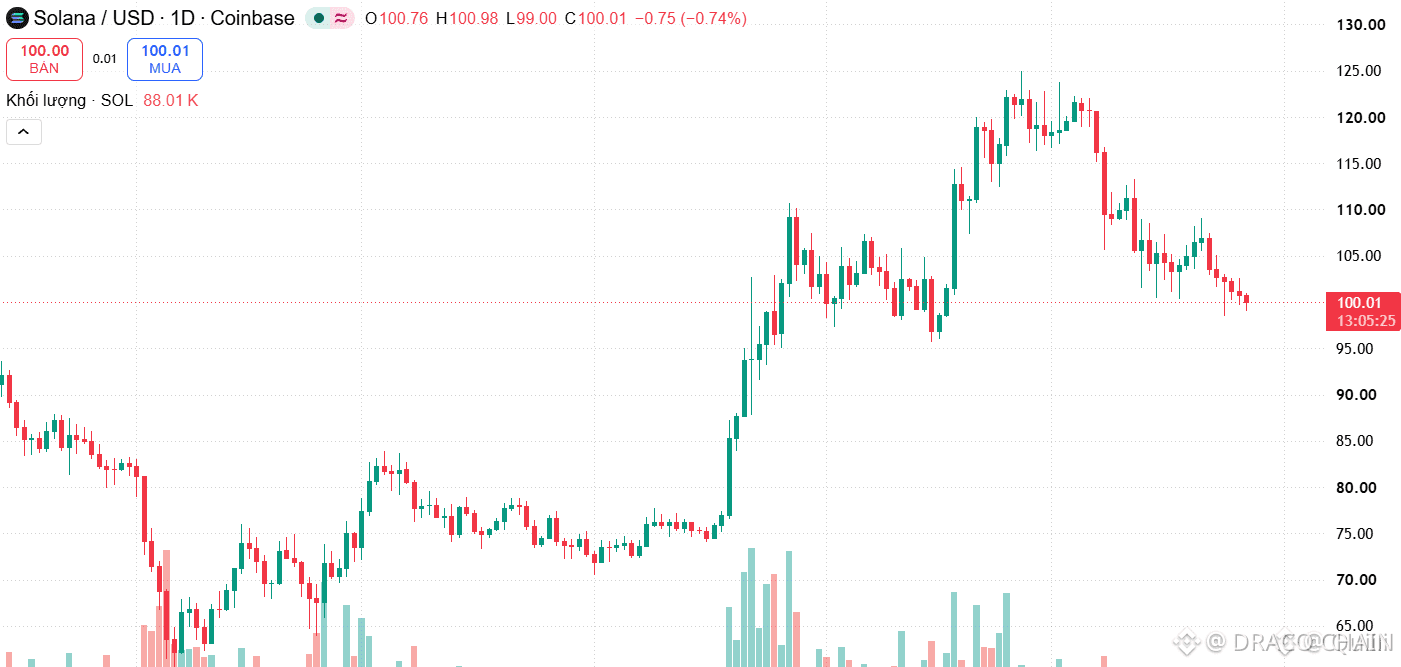
📊 The latest Solana audit round logged 809 submissions, yet only 127 unique bugs emerged, highlighting a near‑50% duplication rate that the network’s anti‑spam shield is aggressively pruning. 🦈
⚡ Firedancer now enforces a 1 SOL burn per report, a liquidity‑drain tweak aimed at filtering AI‑generated noise, while Jump Crypto expands its bounty pool to $1 M, with severe Alpenglow voting exploits rewarding up to $300k. 📈
💬 How will this fee shift reshape reporting quality and smart‑money participation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #CryptoSecurity #JumpCrypto #Alpenglow
🦈 🔥
🚨 $SOL BUG BOUNTY ALERT: SPAM FILTER REQUIRES 1 SOL FEE! 💥
📊 The latest Solana audit round logged 809 submissions, yet only 127 unique bugs emerged, highlighting a near‑50% duplication rate that the network’s anti‑spam shield is aggressively pruning. 🦈
⚡ Firedancer now enforces a 1 SOL burn per report, a liquidity‑drain tweak aimed at filtering AI‑generated noise, while Jump Crypto expands its bounty pool to $1 M, with severe Alpenglow voting exploits rewarding up to $300k. 📈
💬 How will this fee shift reshape reporting quality and smart‑money participation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #CryptoSecurity #JumpCrypto #Alpenglow
🦈 🔥
📊 The latest Solana audit round logged 809 submissions, yet only 127 unique bugs emerged, highlighting a near‑50% duplication rate that the network’s anti‑spam shield is aggressively pruning. 🦈
⚡ Firedancer now enforces a 1 SOL burn per report, a liquidity‑drain tweak aimed at filtering AI‑generated noise, while Jump Crypto expands its bounty pool to $1 M, with severe Alpenglow voting exploits rewarding up to $300k. 📈
💬 How will this fee shift reshape reporting quality and smart‑money participation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #CryptoSecurity #JumpCrypto #Alpenglow
🦈 🔥
7

🚨 $SOL BUG BOUNTY ALERT: CLAIM UP TO $300K REWARDS BEFORE NOV 20! 💥
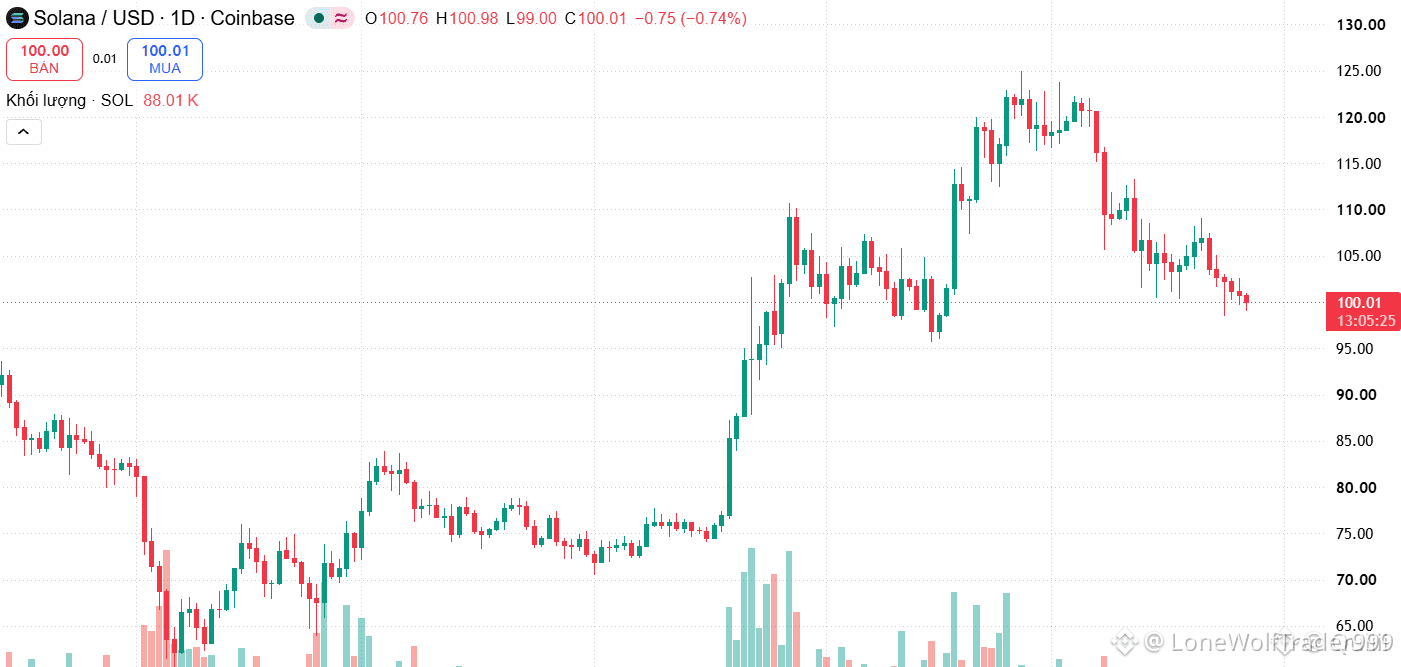
Firedancer now forces researchers to burn 1 SOL (≈ $100) per bug report, a non‑refundable fee designed to choke AI‑generated spam. 🟢 This move pushes serious hunters to the front line rather than littering the inbox.
The $1 M audit contest logged 809 submissions but only 127 distinct flaws, with almost half the tickets duplicated. 📊 Jump Crypto has lifted rewards through Nov 20, and the critical Alpenglow voting exploit can net up to $300 k. 💡
💬 Who’s gearing up to turn those bugs into a payday? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #Security #JumpCrypto #Alpenglow
🔥 💎
🚨 $SOL BUG BOUNTY ALERT: CLAIM UP TO $300K REWARDS BEFORE NOV 20! 💥
Firedancer now forces researchers to burn 1 SOL (≈ $100) per bug report, a non‑refundable fee designed to choke AI‑generated spam. 🟢 This move pushes serious hunters to the front line rather than littering the inbox.
The $1 M audit contest logged 809 submissions but only 127 distinct flaws, with almost half the tickets duplicated. 📊 Jump Crypto has lifted rewards through Nov 20, and the critical Alpenglow voting exploit can net up to $300 k. 💡
💬 Who’s gearing up to turn those bugs into a payday? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #Security #JumpCrypto #Alpenglow
🔥 💎
Firedancer now forces researchers to burn 1 SOL (≈ $100) per bug report, a non‑refundable fee designed to choke AI‑generated spam. 🟢 This move pushes serious hunters to the front line rather than littering the inbox.
The $1 M audit contest logged 809 submissions but only 127 distinct flaws, with almost half the tickets duplicated. 📊 Jump Crypto has lifted rewards through Nov 20, and the critical Alpenglow voting exploit can net up to $300 k. 💡
💬 Who’s gearing up to turn those bugs into a payday? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #BugBounty #Security #JumpCrypto #Alpenglow
🔥 💎
·
--
Firedancer: quemar 1 SOL es condición para optar a una recompensa por fallos
Firedancer es un cliente validador independiente para Solana. En un artículo publicado el 16 de octubre, Jump explicó el costo de revisar envíos masivos al programa de seguridad.
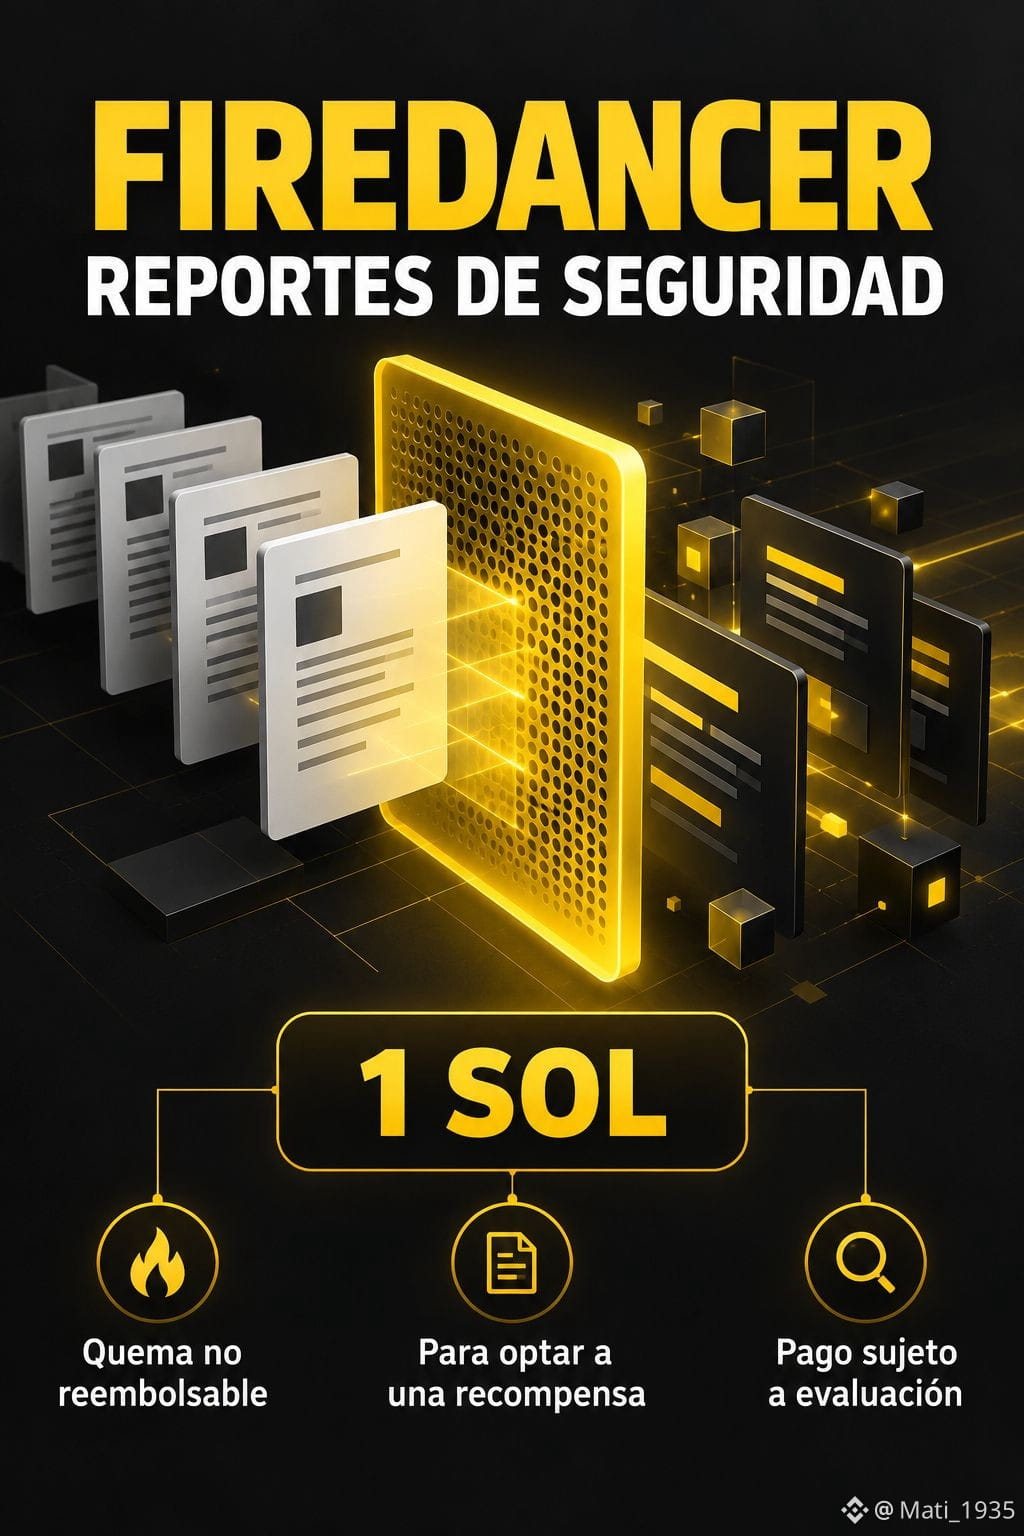
Los términos consultados el 27 de octubre, en su versión vigente desde el 26, exigen quemar 1 SOL por reporte para ser elegible para una recompensa. Esa fecha identifica la versión del documento, no cuándo apareció por primera vez el requisito.
La quema es irreversible y no reembolsable, incluso si el reporte resulta inválido, duplicado o fuera de alcance. Un reporte sin quema puede revisarse a discreción del equipo, pero no optar a un premio.
Los pagos aceptados se realizan en USDC y requieren verificación de identidad. Hasta el 20 de noviembre hay incentivos de 2 veces el pago estándar, o 3 veces para hallazgos específicos de Alpenglow, sujetos a elegibilidad y evaluación. El incentivo temporal no significa que el programa termine ese día.
Estas condiciones corresponden al programa de Firedancer; no son una regla para todos los reportes de seguridad de Solana.
Dato de mercado: el 27 de octubre a las 19:56 UTC, SOL cotizaba en Binance Spot a 101,16 USDT, con +0,577% en 24 horas.
Lectura de mercado: el filtro puede reducir ruido, pero también impone un costo a investigadores legítimos. Quemar SOL no garantiza cobrar. Sin datos sobre su escala, tampoco permite deducir un efecto relevante en la oferta o en el precio de SOL.
$SOL $USDC $USDT
Contenido Educativo. No asesoramiento financiero.
#Firedancer #Solana #Seguridad #BugBounty #Blockchain
Firedancer: quemar 1 SOL es condición para optar a una recompensa por fallos
Firedancer es un cliente validador independiente para Solana. En un artículo publicado el 16 de octubre, Jump explicó el costo de revisar envíos masivos al programa de seguridad.
Los términos consultados el 27 de octubre, en su versión vigente desde el 26, exigen quemar 1 SOL por reporte para ser elegible para una recompensa. Esa fecha identifica la versión del documento, no cuándo apareció por primera vez el requisito.
La quema es irreversible y no reembolsable, incluso si el reporte resulta inválido, duplicado o fuera de alcance. Un reporte sin quema puede revisarse a discreción del equipo, pero no optar a un premio.
Los pagos aceptados se realizan en USDC y requieren verificación de identidad. Hasta el 20 de noviembre hay incentivos de 2 veces el pago estándar, o 3 veces para hallazgos específicos de Alpenglow, sujetos a elegibilidad y evaluación. El incentivo temporal no significa que el programa termine ese día.
Estas condiciones corresponden al programa de Firedancer; no son una regla para todos los reportes de seguridad de Solana.
Dato de mercado: el 27 de octubre a las 19:56 UTC, SOL cotizaba en Binance Spot a 101,16 USDT, con +0,577% en 24 horas.
Lectura de mercado: el filtro puede reducir ruido, pero también impone un costo a investigadores legítimos. Quemar SOL no garantiza cobrar. Sin datos sobre su escala, tampoco permite deducir un efecto relevante en la oferta o en el precio de SOL.
$SOL $USDC $USDT
Contenido Educativo. No asesoramiento financiero.
#Firedancer #Solana #Seguridad #BugBounty #Blockchain
Firedancer es un cliente validador independiente para Solana. En un artículo publicado el 16 de octubre, Jump explicó el costo de revisar envíos masivos al programa de seguridad.
Los términos consultados el 27 de octubre, en su versión vigente desde el 26, exigen quemar 1 SOL por reporte para ser elegible para una recompensa. Esa fecha identifica la versión del documento, no cuándo apareció por primera vez el requisito.
La quema es irreversible y no reembolsable, incluso si el reporte resulta inválido, duplicado o fuera de alcance. Un reporte sin quema puede revisarse a discreción del equipo, pero no optar a un premio.
Los pagos aceptados se realizan en USDC y requieren verificación de identidad. Hasta el 20 de noviembre hay incentivos de 2 veces el pago estándar, o 3 veces para hallazgos específicos de Alpenglow, sujetos a elegibilidad y evaluación. El incentivo temporal no significa que el programa termine ese día.
Estas condiciones corresponden al programa de Firedancer; no son una regla para todos los reportes de seguridad de Solana.
Dato de mercado: el 27 de octubre a las 19:56 UTC, SOL cotizaba en Binance Spot a 101,16 USDT, con +0,577% en 24 horas.
Lectura de mercado: el filtro puede reducir ruido, pero también impone un costo a investigadores legítimos. Quemar SOL no garantiza cobrar. Sin datos sobre su escala, tampoco permite deducir un efecto relevante en la oferta o en el precio de SOL.
$SOL $USDC $USDT
Contenido Educativo. No asesoramiento financiero.
#Firedancer #Solana #Seguridad #BugBounty #Blockchain
25
·
--
🚨 **ZachXBT slams $250K XRP bug bounty: "Low payouts discourage whitehats!"** A critical vulnerability on the XRP ledger was just reported, and the whitehat walked away with $250K. Sounds like a lot? Not even close, says ZachXBT. Here’s the ugly math: If a bug puts billions at risk, but the "good guy" payout is only $250K, the financial incentive to sell it to blackhats is massive. Top protocols now offer $1M–$10M+ for critical bugs. Underpaying security researchers doesn't save money—it pushes them to the dark side. 🔓 💬 **Is $250K enough for a critical L1 bug, or is XRP being cheap?** Drop your take! 👇 #XRP #CryptoSecurity #ZachXBT #BugBounty #BinanceSquare
🚨 **ZachXBT slams $250K XRP bug bounty: "Low payouts discourage whitehats!"** A critical vulnerability on the XRP ledger was just reported, and the whitehat walked away with $250K. Sounds like a lot? Not even close, says ZachXBT. Here’s the ugly math: If a bug puts billions at risk, but the "good guy" payout is only $250K, the financial incentive to sell it to blackhats is massive. Top protocols now offer $1M–$10M+ for critical bugs. Underpaying security researchers doesn't save money—it pushes them to the dark side. 🔓 💬 **Is $250K enough for a critical L1 bug, or is XRP being cheap?** Drop your take! 👇 #XRP #CryptoSecurity #ZachXBT #BugBounty #BinanceSquare
64

#xrpledgerpatchesxrpcreationbug
XRP's Fixed Supply Just Survived a Bug That Sat in the Code for About a Decade
"Fixed supply" is one of the strongest claims in crypto. This week, XRP Ledger disclosed a flaw that could have tested it.
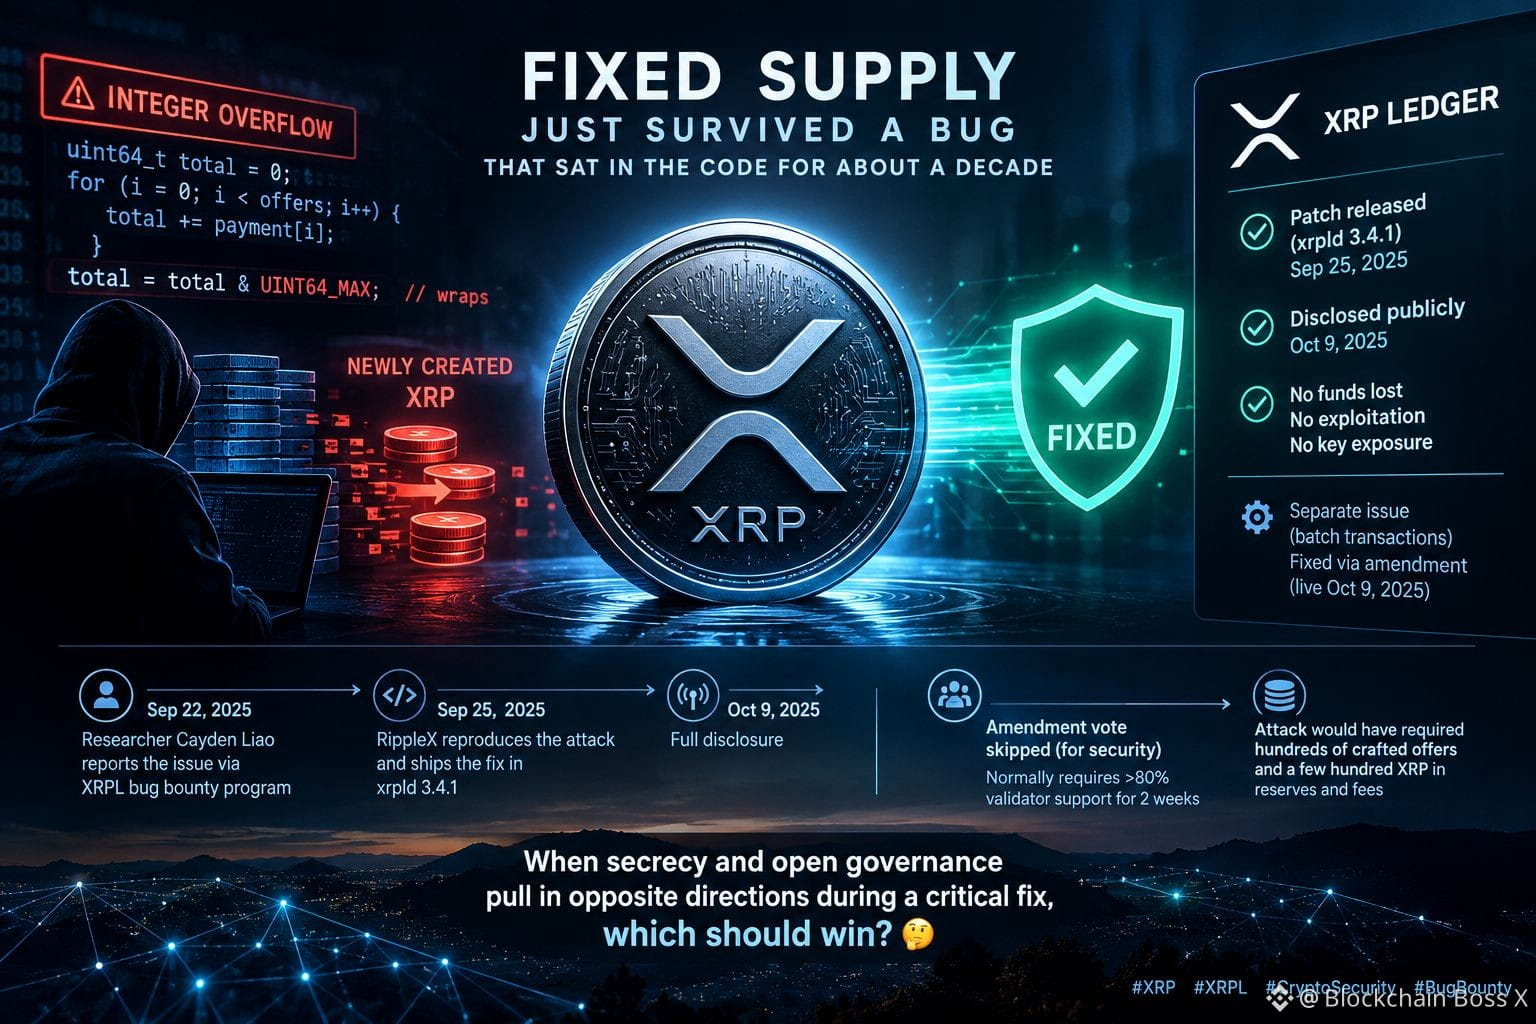
Here's the timeline: researcher Cayden Liao reported the issue through the XRPL bug bounty program on September 22. It was a payment-engine integer overflow: when one payment consumed many DEX offers, unchecked 64-bit arithmetic could wrap the total to a smaller number while sellers still received the full amounts, with the difference becoming newly created, spendable XRP. The flaw may date to 2015. RippleX reproduced the attack and shipped a fix in xrpld 3.4.1 on September 25, then disclosed everything on October 9. It reportedly required hundreds of crafted offers and a few hundred XRP in reserves and fees, and the team found no evidence of exploitation, loss of funds, or key exposure. A separate, lower-severity batch-transaction issue was fixed through an amendment that went live the same day.
Why does this matter? The patch skipped the usual amendment vote, which normally requires over 80% validator support for two weeks, since public voting would have advertised the weakness. That's a reasonable security call, but it shows how much trust rests with core developers and with operators upgrading quickly. It also shows a bug bounty doing its job.
When secrecy and open governance pull in opposite directions during a critical fix, which should win? 🤔
#xrp #XRPL #CryptoSecurity #BugBounty
$XRP $MAGIC $LUMIA
{future}(LUMIAUSDT)
{future}(MAGICUSDT)
{future}(XRPUSDT)
#xrpledgerpatchesxrpcreationbug
XRP's Fixed Supply Just Survived a Bug That Sat in the Code for About a Decade
"Fixed supply" is one of the strongest claims in crypto. This week, XRP Ledger disclosed a flaw that could have tested it.
Here's the timeline: researcher Cayden Liao reported the issue through the XRPL bug bounty program on September 22. It was a payment-engine integer overflow: when one payment consumed many DEX offers, unchecked 64-bit arithmetic could wrap the total to a smaller number while sellers still received the full amounts, with the difference becoming newly created, spendable XRP. The flaw may date to 2015. RippleX reproduced the attack and shipped a fix in xrpld 3.4.1 on September 25, then disclosed everything on October 9. It reportedly required hundreds of crafted offers and a few hundred XRP in reserves and fees, and the team found no evidence of exploitation, loss of funds, or key exposure. A separate, lower-severity batch-transaction issue was fixed through an amendment that went live the same day.
Why does this matter? The patch skipped the usual amendment vote, which normally requires over 80% validator support for two weeks, since public voting would have advertised the weakness. That's a reasonable security call, but it shows how much trust rests with core developers and with operators upgrading quickly. It also shows a bug bounty doing its job.
When secrecy and open governance pull in opposite directions during a critical fix, which should win? 🤔
#xrp #XRPL #CryptoSecurity #BugBounty
$XRP $MAGIC $LUMIA
XRP's Fixed Supply Just Survived a Bug That Sat in the Code for About a Decade
"Fixed supply" is one of the strongest claims in crypto. This week, XRP Ledger disclosed a flaw that could have tested it.
Here's the timeline: researcher Cayden Liao reported the issue through the XRPL bug bounty program on September 22. It was a payment-engine integer overflow: when one payment consumed many DEX offers, unchecked 64-bit arithmetic could wrap the total to a smaller number while sellers still received the full amounts, with the difference becoming newly created, spendable XRP. The flaw may date to 2015. RippleX reproduced the attack and shipped a fix in xrpld 3.4.1 on September 25, then disclosed everything on October 9. It reportedly required hundreds of crafted offers and a few hundred XRP in reserves and fees, and the team found no evidence of exploitation, loss of funds, or key exposure. A separate, lower-severity batch-transaction issue was fixed through an amendment that went live the same day.
Why does this matter? The patch skipped the usual amendment vote, which normally requires over 80% validator support for two weeks, since public voting would have advertised the weakness. That's a reasonable security call, but it shows how much trust rests with core developers and with operators upgrading quickly. It also shows a bug bounty doing its job.
When secrecy and open governance pull in opposite directions during a critical fix, which should win? 🤔
#xrp #XRPL #CryptoSecurity #BugBounty
$XRP $MAGIC $LUMIA
1.6k
$ETH AI FOUND A REAL BUG — BUT MOST FLAGGED ISSUES ARE WRONG 💎
Ethereum Foundation’s Protocol Security team deployed coordinated AI agents to test system software, cryptographic code, and smart contracts. The technology did uncover a remotely exploitable crash in libp2p’s gossipsub component — already patched. Yet the overwhelming majority of AI-generated bug reports are either false positives, duplicates, or out of scope.
The bottleneck has shifted from generating hypotheses to verifying correctness. A finding is only valid after a human researcher independently reproduces it against live code. AI is a powerful search tool, not a security oracle.
Are you trusting AI audits or waiting for human confirmation before entering a position?
Not financial advice. Always manage your risk.
#ETH #AISecurity #SmartContracts #BugBounty #Crypto
💎
$ETH AI FOUND A REAL BUG — BUT MOST FLAGGED ISSUES ARE WRONG 💎
Ethereum Foundation’s Protocol Security team deployed coordinated AI agents to test system software, cryptographic code, and smart contracts. The technology did uncover a remotely exploitable crash in libp2p’s gossipsub component — already patched. Yet the overwhelming majority of AI-generated bug reports are either false positives, duplicates, or out of scope.
The bottleneck has shifted from generating hypotheses to verifying correctness. A finding is only valid after a human researcher independently reproduces it against live code. AI is a powerful search tool, not a security oracle.
Are you trusting AI audits or waiting for human confirmation before entering a position?
Not financial advice. Always manage your risk.
#ETH #AISecurity #SmartContracts #BugBounty #Crypto
💎
Ethereum Foundation’s Protocol Security team deployed coordinated AI agents to test system software, cryptographic code, and smart contracts. The technology did uncover a remotely exploitable crash in libp2p’s gossipsub component — already patched. Yet the overwhelming majority of AI-generated bug reports are either false positives, duplicates, or out of scope.
The bottleneck has shifted from generating hypotheses to verifying correctness. A finding is only valid after a human researcher independently reproduces it against live code. AI is a powerful search tool, not a security oracle.
Are you trusting AI audits or waiting for human confirmation before entering a position?
Not financial advice. Always manage your risk.
#ETH #AISecurity #SmartContracts #BugBounty #Crypto
💎
11
·
--
🚨 A linha de frente invisível: Como os caçadores de bugs protegem o seu capital! 🚨
Muitos olham apenas para o sobe e desce do preço do $BTC ou do $ETH, mas o que realmente mantém a confiança nesses ecossistemas são as auditorias contínuas e os programas de Bug Bounty.
Ao analisar lógicas de contratos e integrações de API em busca de vulnerabilidades, percebo um padrão claro: os projetos mais sólidos e com maior potencial de valorização a longo prazo (especialmente no ecossistema do $BNB) são aqueles que investem pesado em segurança e recompensam pesquisadores independentes (White Hats) por encontrarem falhas antes dos cibercriminosos.
🛡️ A dica de ouro: Antes de investir pesado em um protocolo, verifique se eles possuem um programa de Bug Bounty ativo em plataformas reconhecidas. Um código fechado e sem testes é uma bomba-relógio para o seu dinheiro.
Você costuma pesquisar sobre a segurança e as auditorias de um projeto antes de comprar o token? Comenta aí! 👇
#BugBounty $ETH #CyberSecurity #Web3 #SmartContracts #CryptoNews
🚨 A linha de frente invisível: Como os caçadores de bugs protegem o seu capital! 🚨
Muitos olham apenas para o sobe e desce do preço do $BTC ou do $ETH , mas o que realmente mantém a confiança nesses ecossistemas são as auditorias contínuas e os programas de Bug Bounty.
Ao analisar lógicas de contratos e integrações de API em busca de vulnerabilidades, percebo um padrão claro: os projetos mais sólidos e com maior potencial de valorização a longo prazo (especialmente no ecossistema do $BNB) são aqueles que investem pesado em segurança e recompensam pesquisadores independentes (White Hats) por encontrarem falhas antes dos cibercriminosos.
🛡️ A dica de ouro: Antes de investir pesado em um protocolo, verifique se eles possuem um programa de Bug Bounty ativo em plataformas reconhecidas. Um código fechado e sem testes é uma bomba-relógio para o seu dinheiro.
Você costuma pesquisar sobre a segurança e as auditorias de um projeto antes de comprar o token? Comenta aí! 👇
#BugBounty $ETH #CyberSecurity #Web3 #SmartContracts #CryptoNews
Muitos olham apenas para o sobe e desce do preço do $BTC ou do $ETH , mas o que realmente mantém a confiança nesses ecossistemas são as auditorias contínuas e os programas de Bug Bounty.
Ao analisar lógicas de contratos e integrações de API em busca de vulnerabilidades, percebo um padrão claro: os projetos mais sólidos e com maior potencial de valorização a longo prazo (especialmente no ecossistema do $BNB) são aqueles que investem pesado em segurança e recompensam pesquisadores independentes (White Hats) por encontrarem falhas antes dos cibercriminosos.
🛡️ A dica de ouro: Antes de investir pesado em um protocolo, verifique se eles possuem um programa de Bug Bounty ativo em plataformas reconhecidas. Um código fechado e sem testes é uma bomba-relógio para o seu dinheiro.
Você costuma pesquisar sobre a segurança e as auditorias de um projeto antes de comprar o token? Comenta aí! 👇
#BugBounty $ETH #CyberSecurity #Web3 #SmartContracts #CryptoNews
97
·
--
🚨 ZETACHAIN: TEAM IGNORED WARNING BEFORE $334K HACK! 🛑💸
💥 THE INCIDENT:
It has been revealed that the team DISMISSED a bug report before the exploit happened! 🚨🙈
Hackers managed to drain approximately $334,000 from the protocol.
📄 THE POSTMORTEM:
The official report points out the critical failure in communication and security checks.
They missed the red flag that could have prevented the loss entirely! ⚠️🔍
⚠️ LESSON:
Even big projects can fail if they don't listen to security alerts! 🛡️📉
$ZETA
#ZetaChain #Hack #Security #BugBounty #PostMortem
🚨 ZETACHAIN: TEAM IGNORED WARNING BEFORE $334K HACK! 🛑💸
💥 THE INCIDENT:
It has been revealed that the team DISMISSED a bug report before the exploit happened! 🚨🙈
Hackers managed to drain approximately $334,000 from the protocol.
📄 THE POSTMORTEM:
The official report points out the critical failure in communication and security checks.
They missed the red flag that could have prevented the loss entirely! ⚠️🔍
⚠️ LESSON:
Even big projects can fail if they don't listen to security alerts! 🛡️📉
$ZETA
#ZetaChain #Hack #Security #BugBounty #PostMortem
💥 THE INCIDENT:
It has been revealed that the team DISMISSED a bug report before the exploit happened! 🚨🙈
Hackers managed to drain approximately $334,000 from the protocol.
📄 THE POSTMORTEM:
The official report points out the critical failure in communication and security checks.
They missed the red flag that could have prevented the loss entirely! ⚠️🔍
⚠️ LESSON:
Even big projects can fail if they don't listen to security alerts! 🛡️📉
$ZETA
#ZetaChain #Hack #Security #BugBounty #PostMortem
30

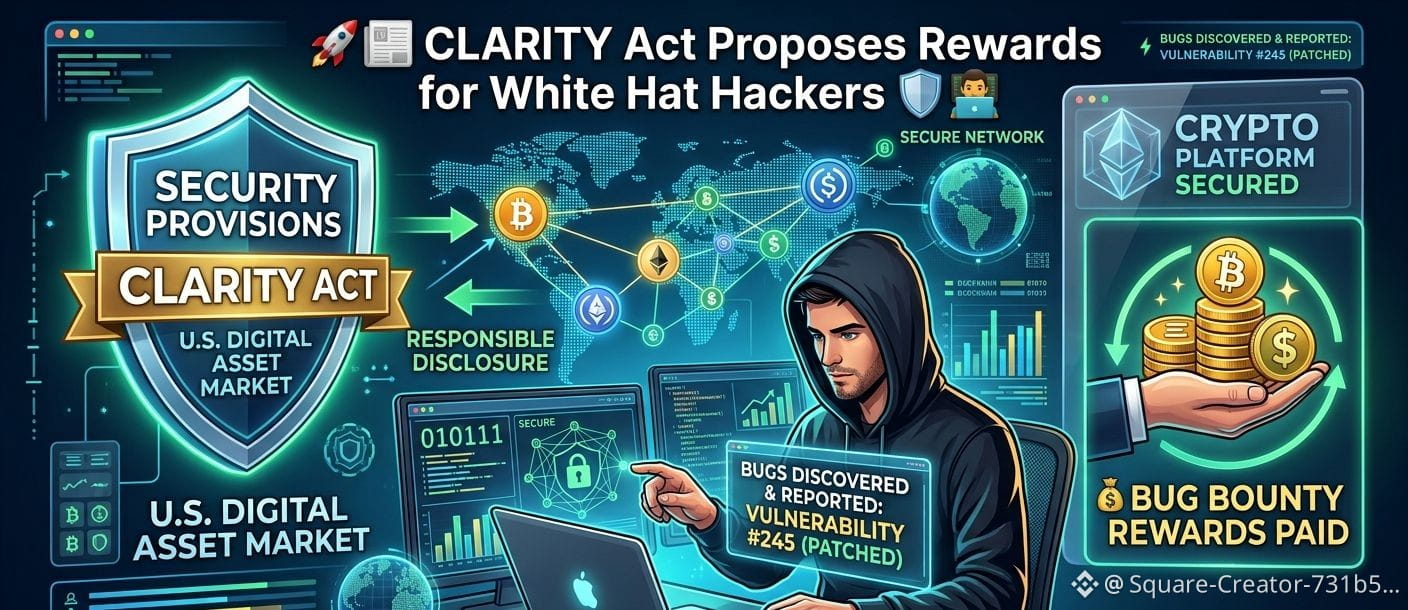
🚀📰 CLARITY Act Proposes Rewards for White Hat Hackers 🛡️👨💻
🚨 A new draft of the U.S. Digital Asset Market CLARITY Act includes provisions that would encourage and protect white hat hackers who responsibly discover and report security vulnerabilities in blockchain networks and crypto platforms. 🛡️🔍 The proposal aims to strengthen cybersecurity across the digital asset industry by promoting responsible disclosure instead of exploitation.
💰 Under the proposal, crypto projects could reward ethical security researchers through structured bug bounty programs, giving white hat hackers incentives to report vulnerabilities before they can be exploited by malicious actors. Supporters say this would improve trust, protect users' funds, and make the crypto ecosystem more secure.
#CLARITYAct 🏛️ #WhiteHatHackers 🛡️#Blockchain 🌐 #CyberSecurity 🔐#BugBounty #Innovation ✨
🚀📰 CLARITY Act Proposes Rewards for White Hat Hackers 🛡️👨💻
🚨 A new draft of the U.S. Digital Asset Market CLARITY Act includes provisions that would encourage and protect white hat hackers who responsibly discover and report security vulnerabilities in blockchain networks and crypto platforms. 🛡️🔍 The proposal aims to strengthen cybersecurity across the digital asset industry by promoting responsible disclosure instead of exploitation.
💰 Under the proposal, crypto projects could reward ethical security researchers through structured bug bounty programs, giving white hat hackers incentives to report vulnerabilities before they can be exploited by malicious actors. Supporters say this would improve trust, protect users' funds, and make the crypto ecosystem more secure.
#CLARITYAct 🏛️ #WhiteHatHackers 🛡️#Blockchain 🌐 #CyberSecurity 🔐#BugBounty #Innovation ✨
🚨 A new draft of the U.S. Digital Asset Market CLARITY Act includes provisions that would encourage and protect white hat hackers who responsibly discover and report security vulnerabilities in blockchain networks and crypto platforms. 🛡️🔍 The proposal aims to strengthen cybersecurity across the digital asset industry by promoting responsible disclosure instead of exploitation.
💰 Under the proposal, crypto projects could reward ethical security researchers through structured bug bounty programs, giving white hat hackers incentives to report vulnerabilities before they can be exploited by malicious actors. Supporters say this would improve trust, protect users' funds, and make the crypto ecosystem more secure.
#CLARITYAct 🏛️ #WhiteHatHackers 🛡️#Blockchain 🌐 #CyberSecurity 🔐#BugBounty #Innovation ✨
1
77
🔥 While crypto Twitter screams “ZetaChain hack” and urges panic selling, the on‑chain metrics most smart wallets watch tell a very different story.
📊 The exploit siphoned $334K, yet BSC’s top trending tokens are still rallying – HONon +1.3% and AKE +8.5% – while #Solana smart wallets like MINI and GTAVI are net buying, with MINI up 5.07% on three wallets. Meanwhile #BTC sits at $80,710 with RSI 65.2 and a bullish MACD crossover, and #ETH at $2,509, RSI 64.5, both flirting with the upper Bollinger band. #BugBounty fallout hasn’t dented the broader risk‑on sentiment, which stays at Greed 74/100.
💡 This suggests capital is reallocating from vulnerable cross‑chain protocols to higher‑confidence layer‑1 assets, reinforcing the current bullish cycle rather than triggering a crash.
👀 Keep an eye on the #Solana smart‑wallet inflow ratio this week – a rising net‑buy signal could spell the next leg of the rally.
❓ If smart money is already shifting gears, what does that say about the next wave of institutional entry points?
🔥 While crypto Twitter screams “ZetaChain hack” and urges panic selling, the on‑chain metrics most smart wallets watch tell a very different story.
📊 The exploit siphoned $334K, yet BSC’s top trending tokens are still rallying – HONon +1.3% and AKE +8.5% – while #Solana smart wallets like MINI and GTAVI are net buying, with MINI up 5.07% on three wallets. Meanwhile #BTC sits at $80,710 with RSI 65.2 and a bullish MACD crossover, and #ETH at $2,509, RSI 64.5, both flirting with the upper Bollinger band. #BugBounty fallout hasn’t dented the broader risk‑on sentiment, which stays at Greed 74/100.
💡 This suggests capital is reallocating from vulnerable cross‑chain protocols to higher‑confidence layer‑1 assets, reinforcing the current bullish cycle rather than triggering a crash.
👀 Keep an eye on the #Solana smart‑wallet inflow ratio this week – a rising net‑buy signal could spell the next leg of the rally.
❓ If smart money is already shifting gears, what does that say about the next wave of institutional entry points?
📊 The exploit siphoned $334K, yet BSC’s top trending tokens are still rallying – HONon +1.3% and AKE +8.5% – while #Solana smart wallets like MINI and GTAVI are net buying, with MINI up 5.07% on three wallets. Meanwhile #BTC sits at $80,710 with RSI 65.2 and a bullish MACD crossover, and #ETH at $2,509, RSI 64.5, both flirting with the upper Bollinger band. #BugBounty fallout hasn’t dented the broader risk‑on sentiment, which stays at Greed 74/100.
💡 This suggests capital is reallocating from vulnerable cross‑chain protocols to higher‑confidence layer‑1 assets, reinforcing the current bullish cycle rather than triggering a crash.
👀 Keep an eye on the #Solana smart‑wallet inflow ratio this week – a rising net‑buy signal could spell the next leg of the rally.
❓ If smart money is already shifting gears, what does that say about the next wave of institutional entry points?
109
·
--
උසබ තත්ත්වය
සත්යායනය කළ
#ZcashApproves$1.5MBugBounty
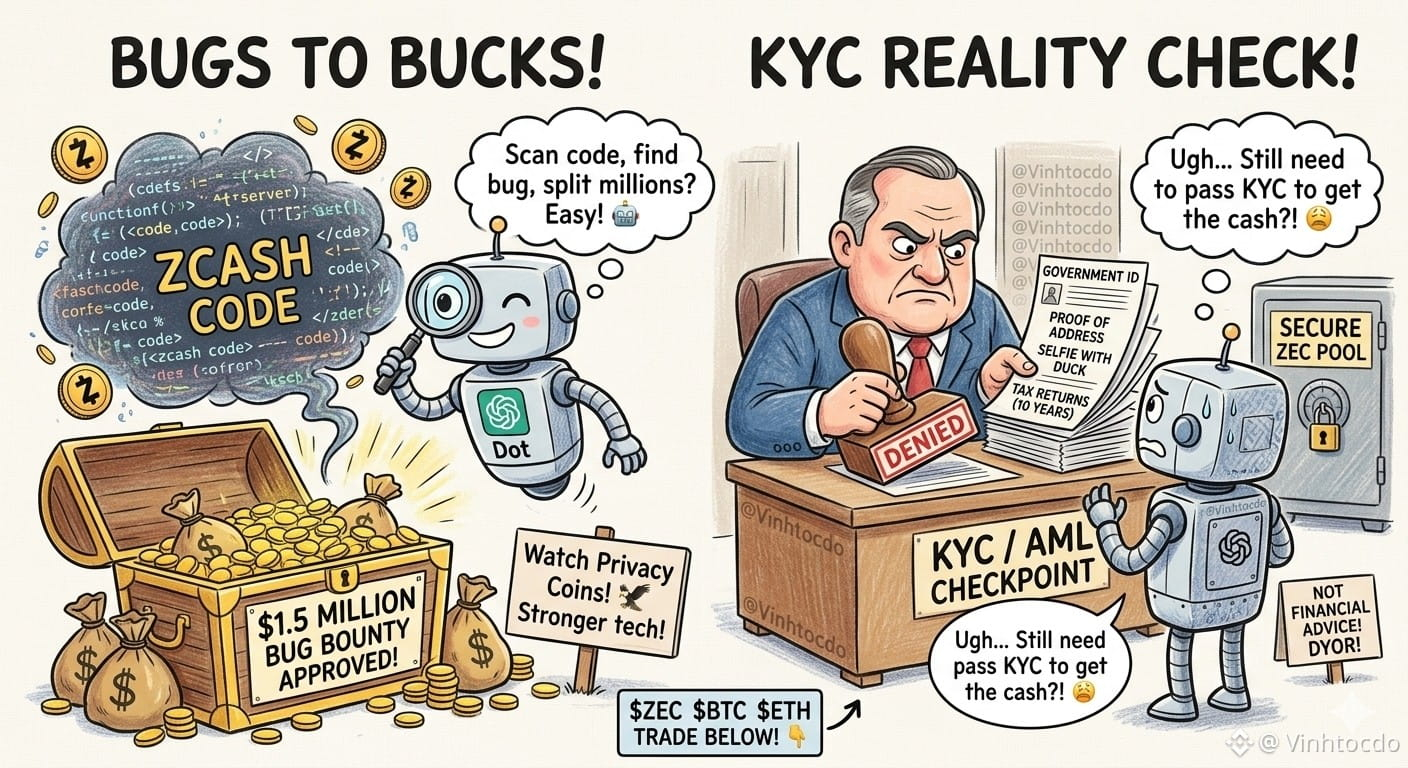
Big news: Zcash just approved a massive $1.5 million bug bounty for researcher Taylor Hornby! 💰 Wait, can we just deploy OpenAI’s new "Dots" agent to scan the code, find the bugs, and split the millions? If only it were that easy! 🤖 The tech giants are upgrading security, and Zcash is paying top dollar to keep its privacy pool safe.
Traders, remember the recipient still needs to pass KYC to get that cash.
What should traders do?
1️⃣ Watch privacy sector coins like a hawk as security upgrades roll out.
2️⃣ Keep an eye on network milestones—stronger tech means stronger fundamentals.
Not financial advice! DYOR!
Click trade below to support me!👇
$ZEC
{future}(ZECUSDT)
$BTC
{future}(BTCUSDT)
$ETH
{future}(ETHUSDT)
Use code VINHTOCDO or link: [https://www.binance.com/register?ref=VINHTOCDO](https://www.binance.com/register?ref=VINHTOCDO)
#zcash #CryptoSecurity #BugBounty #PrivacyCoins #VINHTOCDO
#ZcashApproves$1.5MBugBounty
Big news: Zcash just approved a massive $1.5 million bug bounty for researcher Taylor Hornby! 💰 Wait, can we just deploy OpenAI’s new "Dots" agent to scan the code, find the bugs, and split the millions? If only it were that easy! 🤖 The tech giants are upgrading security, and Zcash is paying top dollar to keep its privacy pool safe.
Traders, remember the recipient still needs to pass KYC to get that cash.
What should traders do?
1️⃣ Watch privacy sector coins like a hawk as security upgrades roll out.
2️⃣ Keep an eye on network milestones—stronger tech means stronger fundamentals.
Not financial advice! DYOR!
Click trade below to support me!👇
$ZEC
$BTC
$ETH
Use code VINHTOCDO or link: https://www.binance.com/register?ref=VINHTOCDO
#zcash #CryptoSecurity #BugBounty #PrivacyCoins #VINHTOCDO
Big news: Zcash just approved a massive $1.5 million bug bounty for researcher Taylor Hornby! 💰 Wait, can we just deploy OpenAI’s new "Dots" agent to scan the code, find the bugs, and split the millions? If only it were that easy! 🤖 The tech giants are upgrading security, and Zcash is paying top dollar to keep its privacy pool safe.
Traders, remember the recipient still needs to pass KYC to get that cash.
What should traders do?
1️⃣ Watch privacy sector coins like a hawk as security upgrades roll out.
2️⃣ Keep an eye on network milestones—stronger tech means stronger fundamentals.
Not financial advice! DYOR!
Click trade below to support me!👇
$ZEC
$BTC
$ETH
Use code VINHTOCDO or link: https://www.binance.com/register?ref=VINHTOCDO
#zcash #CryptoSecurity #BugBounty #PrivacyCoins #VINHTOCDO
2
248

$APT VULNERABILITY EXPOSED $700B RISK – BUT FIXED IN HOURS 🔥
A critical "stale-cache" bug was found in Aptos Move VM back in February. Theoretically, it put $700 billion in crypto assets at risk — including bridges, stablecoins, and DeFi protocols. But here's the key: the Aptos team patched mainnet within hours of disclosure. Zero user funds lost.
Independent security firm Grego AI estimated $250 million of TVL was directly at risk, yet the exploitability in real-world conditions was minimal. A team with just a $3,000 server could simulate a 90% success rate — but the vulnerability never reached attackers.
Speed and transparency like this builds trust in a project's security culture. Does this change your conviction on $APT ?
Not financial advice. Always manage your risk.
#APT #Security #BugBounty #CryptoNews #Vulnerability
⚡
$APT VULNERABILITY EXPOSED $700B RISK – BUT FIXED IN HOURS 🔥
A critical "stale-cache" bug was found in Aptos Move VM back in February. Theoretically, it put $700 billion in crypto assets at risk — including bridges, stablecoins, and DeFi protocols. But here's the key: the Aptos team patched mainnet within hours of disclosure. Zero user funds lost.
Independent security firm Grego AI estimated $250 million of TVL was directly at risk, yet the exploitability in real-world conditions was minimal. A team with just a $3,000 server could simulate a 90% success rate — but the vulnerability never reached attackers.
Speed and transparency like this builds trust in a project's security culture. Does this change your conviction on $APT ?
Not financial advice. Always manage your risk.
#APT #Security #BugBounty #CryptoNews #Vulnerability
⚡
A critical "stale-cache" bug was found in Aptos Move VM back in February. Theoretically, it put $700 billion in crypto assets at risk — including bridges, stablecoins, and DeFi protocols. But here's the key: the Aptos team patched mainnet within hours of disclosure. Zero user funds lost.
Independent security firm Grego AI estimated $250 million of TVL was directly at risk, yet the exploitability in real-world conditions was minimal. A team with just a $3,000 server could simulate a 90% success rate — but the vulnerability never reached attackers.
Speed and transparency like this builds trust in a project's security culture. Does this change your conviction on $APT ?
Not financial advice. Always manage your risk.
#APT #Security #BugBounty #CryptoNews #Vulnerability
⚡
40
තවත් අන්තර්ගතයන් ගවේෂණය කිරීමට ඇතුල් වන්න
Binance චතුරශ්රය හි ගෝලීය ක්රිප්ටෝ පරිශීලකයින් හා එක්වන්න
⚡️ ක්රිප්ටෝ පිළිබඳ නවතම සහ ප්රයෝජනවත් තොරතුරු ලබා ගන්න.
💬 ලොව විශාලතම ක්රිප්ටෝ හුවමාරුව මගින් විශ්වාස කෙරේ.
👍 සත්යායනය කරන ලද නිර්මාණකරුවන්ගෙන් සැබෑ විදසුන් සොයා ගන්න.
විද්යුත් තැපෑල / දුරකථන අංකය
නැගී එන මාතෘකා
1
#USMidterms-WhatAreMarketsExpecting?
83,475 නැරඹීම්
734 සාකච්ඡා කරමින්
2
#USOctoberNFP-AreRateCutsStillPossible
244,394 නැරඹීම්
1,910 සාකච්ඡා කරමින්
3
#AMDBeatsExpectations-AINarrativeContinues
19,617 නැරඹීම්
281 සාකච්ඡා කරමින්
4
#BinanceIncidentReport
243,178 නැරඹීම්
1,342 සාකච්ඡා කරමින්
5
#AnthropicIPOPricedDownasInvestorsEye$1.5T
15,245 නැරඹීම්
105 සාකච්ඡා කරමින්
6
#37thQuarterlyBNBBurnRemoves1.64MillionBNB
11 නැරඹීම්
7 සාකච්ඡා කරමින්
7
#BinanceReopensWithdrawalsForMoreAssets
358,596 නැරඹීම්
2,348 සාකච්ඡා කරමින්
8
#HongKongToLicenseVirtualAssetCustodyAndAdvisory
2,610 නැරඹීම්
79 සාකච්ඡා කරමින්
9
#BinanceHourlyDepositsExceedWithdrawals
151,729 නැරඹීම්
1,154 සාකච්ඡා කරමින්
10
#SouthKoreaRulingPartyLeaderSeeksCryptoTaxDelay
4,027 නැරඹීම්
59 සාකච්ඡා කරමින්