
#cryptosecurity
cryptosecurity
8.4M рет көрілді
10,867 адам талқылап жатыр
Қызу саудада
Ең соңғы
🚨 THE MOST EXPENSIVE "WHITE HAT" BOUNTY IN HISTORY? 🚨
Liquid Network just got drained of $320 MILLION. And the attacker walked away with $47M for free. 💀
Here's what actually happened — and why this should scare every single person holding wrapped or bridged assets right now. 👇
🔓 The Scariest Part: No private keys were stolen. No multisig was bypassed. The attacker exploited a bug in the Elements software to MINT ~4,000 FAKE L-BTC out of thin air — then cashed them out for REAL Bitcoin through the normal peg-out system .
The federation wallet went from 4,205 $BTC to 197 BTC in 23 minutes. That's 95% of the reserve — GONE .
📅 The Timeline That Should Terrify You:
• Sept 6, 13:53 UTC — Attacker mints 4,000 unbacked L-BTC
• Sept 6, 14:28 UTC — Federation releases 3,996 REAL BTC
• Total elapsed: 35 minutes
The software told every validator the transaction was clean. Every signature was valid. The system worked exactly as designed — except it was designed to be fooled.
💬 Then things got WEIRD:
The attacker left an on-chain message: "we are whitehats. contact us on chain." They demanded Blockstream patch the bug FIRST, then they'd return the funds .
They returned 3,400 BTC — and kept 598.5 BTC (~$47M) for themselves .
🔴 Blockstream's response: "We will not pay a ransom. Taking assets without authorization and withholding their return is a crime, not white-hat activity."
🔴 Ledger CTO's take: "White hats don't drain a bridge and then solicit an 'on-chain' contact." Called it closer to extortion .
⚡ THE REAL LESSON: Bitcoin itself was never hacked. The base layer stayed perfect. The exploit happened in the layer built on top of it — the sidechain, the bridge, the "wrapped" asset .
Every bridge. Every sidechain. Every wrapped token. New functionality = new attack surface.
And this time, someone minted $320 million from nothing— and walked away with $47 million as a "tip."
DYOR. Understand what you're actually trusting. 🎯
#LiquidNetwork #Bitcoin #Blockstream #CryptoSecurity
🚨 THE MOST EXPENSIVE "WHITE HAT" BOUNTY IN HISTORY? 🚨
Liquid Network just got drained of $320 MILLION. And the attacker walked away with $47M for free. 💀
Here's what actually happened — and why this should scare every single person holding wrapped or bridged assets right now. 👇
🔓 The Scariest Part: No private keys were stolen. No multisig was bypassed. The attacker exploited a bug in the Elements software to MINT ~4,000 FAKE L-BTC out of thin air — then cashed them out for REAL Bitcoin through the normal peg-out system .
The federation wallet went from 4,205 $BTC to 197 BTC in 23 minutes. That's 95% of the reserve — GONE .
📅 The Timeline That Should Terrify You:
• Sept 6, 13:53 UTC — Attacker mints 4,000 unbacked L-BTC
• Sept 6, 14:28 UTC — Federation releases 3,996 REAL BTC
• Total elapsed: 35 minutes
The software told every validator the transaction was clean. Every signature was valid. The system worked exactly as designed — except it was designed to be fooled.
💬 Then things got WEIRD:
The attacker left an on-chain message: "we are whitehats. contact us on chain." They demanded Blockstream patch the bug FIRST, then they'd return the funds .
They returned 3,400 BTC — and kept 598.5 BTC (~$47M) for themselves .
🔴 Blockstream's response: "We will not pay a ransom. Taking assets without authorization and withholding their return is a crime, not white-hat activity."
🔴 Ledger CTO's take: "White hats don't drain a bridge and then solicit an 'on-chain' contact." Called it closer to extortion .
⚡ THE REAL LESSON: Bitcoin itself was never hacked. The base layer stayed perfect. The exploit happened in the layer built on top of it — the sidechain, the bridge, the "wrapped" asset .
Every bridge. Every sidechain. Every wrapped token. New functionality = new attack surface.
And this time, someone minted $320 million from nothing— and walked away with $47 million as a "tip."
DYOR. Understand what you're actually trusting. 🎯
#LiquidNetwork #Bitcoin #Blockstream #CryptoSecurity
Liquid Network just got drained of $320 MILLION. And the attacker walked away with $47M for free. 💀
Here's what actually happened — and why this should scare every single person holding wrapped or bridged assets right now. 👇
🔓 The Scariest Part: No private keys were stolen. No multisig was bypassed. The attacker exploited a bug in the Elements software to MINT ~4,000 FAKE L-BTC out of thin air — then cashed them out for REAL Bitcoin through the normal peg-out system .
The federation wallet went from 4,205 $BTC to 197 BTC in 23 minutes. That's 95% of the reserve — GONE .
📅 The Timeline That Should Terrify You:
• Sept 6, 13:53 UTC — Attacker mints 4,000 unbacked L-BTC
• Sept 6, 14:28 UTC — Federation releases 3,996 REAL BTC
• Total elapsed: 35 minutes
The software told every validator the transaction was clean. Every signature was valid. The system worked exactly as designed — except it was designed to be fooled.
💬 Then things got WEIRD:
The attacker left an on-chain message: "we are whitehats. contact us on chain." They demanded Blockstream patch the bug FIRST, then they'd return the funds .
They returned 3,400 BTC — and kept 598.5 BTC (~$47M) for themselves .
🔴 Blockstream's response: "We will not pay a ransom. Taking assets without authorization and withholding their return is a crime, not white-hat activity."
🔴 Ledger CTO's take: "White hats don't drain a bridge and then solicit an 'on-chain' contact." Called it closer to extortion .
⚡ THE REAL LESSON: Bitcoin itself was never hacked. The base layer stayed perfect. The exploit happened in the layer built on top of it — the sidechain, the bridge, the "wrapped" asset .
Every bridge. Every sidechain. Every wrapped token. New functionality = new attack surface.
And this time, someone minted $320 million from nothing— and walked away with $47 million as a "tip."
DYOR. Understand what you're actually trusting. 🎯
#LiquidNetwork #Bitcoin #Blockstream #CryptoSecurity
14
A lingering three-year-old security flaw recently triggered a $1.3 million exploit and forced an agonizing 10-day network shutdown. This shocking incident highlights a harsh reality in Web3: even code that survives professional audits can harbor ticking time bombs. Security reviews are crucial, but they are never bulletproof. Protocols need continuous runtime monitoring and more robust defensive architecture to catch deep-seated vulnerabilities before malicious actors do. Vigilance is everything. #CryptoSecurity #Blockchain #Web3
A lingering three-year-old security flaw recently triggered a $1.3 million exploit and forced an agonizing 10-day network shutdown. This shocking incident highlights a harsh reality in Web3: even code that survives professional audits can harbor ticking time bombs. Security reviews are crucial, but they are never bulletproof. Protocols need continuous runtime monitoring and more robust defensive architecture to catch deep-seated vulnerabilities before malicious actors do. Vigilance is everything. #CryptoSecurity #Blockchain #Web3
The XRP Ledger is taking a rigorous approach to DeFi security by using formal verification and mathematical proofs for its upcoming lending protocol. Instead of relying solely on post-launch patches, developers are leveraging Lean 4 to ensure the system cannot be drained or driven into insolvency under any scenario. This proactive, science-backed risk management could set a powerful new gold standard for institutional-grade lending architecture across the entire crypto ecosystem. $XRP #XRPL #DeFi #CryptoSecurity
The XRP Ledger is taking a rigorous approach to DeFi security by using formal verification and mathematical proofs for its upcoming lending protocol. Instead of relying solely on post-launch patches, developers are leveraging Lean 4 to ensure the system cannot be drained or driven into insolvency under any scenario. This proactive, science-backed risk management could set a powerful new gold standard for institutional-grade lending architecture across the entire crypto ecosystem. $XRP #XRPL #DeFi #CryptoSecurity
29
The recent cyberattack on crypto tech provider Haruko serves as a stark reminder that infrastructure security is just as critical as exchange safety. While major institutional players usually weather these storms due to robust defenses, smaller hedge funds with lax protocols are paying the price. This incident highlights a widening security gap in digital assets. As the industry matures, third-party risk management must become a top priority to prevent cascading vulnerabilities across the market ecosystem. $SOL $BNB #CryptoSecurity #RiskManagement #DeFi
The recent cyberattack on crypto tech provider Haruko serves as a stark reminder that infrastructure security is just as critical as exchange safety. While major institutional players usually weather these storms due to robust defenses, smaller hedge funds with lax protocols are paying the price. This incident highlights a widening security gap in digital assets. As the industry matures, third-party risk management must become a top priority to prevent cascading vulnerabilities across the market ecosystem. $SOL $BNB #CryptoSecurity #RiskManagement #DeFi
22

·
--
XRPL团队用数学证明来验证新借贷协议的安全性,Common Prefix用Lean 4语言测试其借贷市场是否会被耗尽。这种严谨的数学方法展示了对系统稳定性的重视。技术面上看,这明显增强了投资者信心,减少了潜在风险。短期可能推动$XRP价格上涨,长期看XRPL的技术成熟度将提升其在DeFi领域的竞争力。
XRPL devs are using mathematical proofs to verify their new lending protocol can't be drained. Common Prefix is testing with Lean 4 language whether the lending market can become insolvent. This rigorous approach shows serious commitment to security. Technically, this should boost investor confidence and reduce risk exposure. Could see $XRP price moving up short-term, while XRPL's technical maturity enhances its position in DeFi long-term.
$XRP #DeFi #区块链安全 #CryptoSecurity
XRPL团队用数学证明来验证新借贷协议的安全性,Common Prefix用Lean 4语言测试其借贷市场是否会被耗尽。这种严谨的数学方法展示了对系统稳定性的重视。技术面上看,这明显增强了投资者信心,减少了潜在风险。短期可能推动$XRP 价格上涨,长期看XRPL的技术成熟度将提升其在DeFi领域的竞争力。
XRPL devs are using mathematical proofs to verify their new lending protocol can't be drained. Common Prefix is testing with Lean 4 language whether the lending market can become insolvent. This rigorous approach shows serious commitment to security. Technically, this should boost investor confidence and reduce risk exposure. Could see $XRP price moving up short-term, while XRPL's technical maturity enhances its position in DeFi long-term.
$XRP #DeFi #区块链安全 #CryptoSecurity
XRPL devs are using mathematical proofs to verify their new lending protocol can't be drained. Common Prefix is testing with Lean 4 language whether the lending market can become insolvent. This rigorous approach shows serious commitment to security. Technically, this should boost investor confidence and reduce risk exposure. Could see $XRP price moving up short-term, while XRPL's technical maturity enhances its position in DeFi long-term.
$XRP #DeFi #区块链安全 #CryptoSecurity
32
·
--
🚨 Cardano founder warns IOG’s YouTube channel compromised amid rising crypto security threats.
This breach highlights ongoing risks to project infrastructure, potentially undermining trust in ADA’s ecosystem.
Smart money may reassess exposure until security is verified and communications restored.
Market implication: heightened caution around project-linked channels could trigger short-term volatility.
Is your crypto portfolio resilient to infrastructure-level attacks?
#CryptoSecurity
$ADA #TradingSignal #CryptoAnalysis
🚨 Cardano founder warns IOG’s YouTube channel compromised amid rising crypto security threats.
This breach highlights ongoing risks to project infrastructure, potentially undermining trust in ADA’s ecosystem.
Smart money may reassess exposure until security is verified and communications restored.
Market implication: heightened caution around project-linked channels could trigger short-term volatility.
Is your crypto portfolio resilient to infrastructure-level attacks?
#CryptoSecurity
$ADA #TradingSignal #CryptoAnalysis
This breach highlights ongoing risks to project infrastructure, potentially undermining trust in ADA’s ecosystem.
Smart money may reassess exposure until security is verified and communications restored.
Market implication: heightened caution around project-linked channels could trigger short-term volatility.
Is your crypto portfolio resilient to infrastructure-level attacks?
#CryptoSecurity
$ADA #TradingSignal #CryptoAnalysis
85
Many panic when software signing or vendor servers fail, but true self-custody resilience goes deeper than the hardware device itself. Your physical wallet might remain impenetrable, yet a compromised companion app or leaked shipping database can still expose you to targeted phishing. Security isn't just about cold storage; it is about operational hygiene across your entire digital footprint. Always verify transaction data on the physical screen and isolate your communications. #SelfCustody #CryptoSecurity #HardwareWallet
Many panic when software signing or vendor servers fail, but true self-custody resilience goes deeper than the hardware device itself. Your physical wallet might remain impenetrable, yet a compromised companion app or leaked shipping database can still expose you to targeted phishing. Security isn't just about cold storage; it is about operational hygiene across your entire digital footprint. Always verify transaction data on the physical screen and isolate your communications. #SelfCustody #CryptoSecurity #HardwareWallet
A staggering 440% surge in blockchain malware highlights a harsh reality: AI tools are making advanced cyberattacks dangerously accessible to state-sponsored actors like North Korea and Iran. Because public chains permanently store malicious instructions, traditional domain takedowns no longer work. Defense strategies must evolve toward proactive wallet tracking, smart contract auditing, and off-chain server monitoring. The crypto security landscape is changing fast. #CryptoSecurity #ArtificialIntelligence #Blockchain
A staggering 440% surge in blockchain malware highlights a harsh reality: AI tools are making advanced cyberattacks dangerously accessible to state-sponsored actors like North Korea and Iran. Because public chains permanently store malicious instructions, traditional domain takedowns no longer work. Defense strategies must evolve toward proactive wallet tracking, smart contract auditing, and off-chain server monitoring. The crypto security landscape is changing fast. #CryptoSecurity #ArtificialIntelligence #Blockchain

🚨 $NIM POLYGON CONTRACT EXPLOITED FOR $50K AFTER CRITICAL SIGNATURE VERIFICATION FAILURE! 🔻
🔍 A zero-signature verification oversight in $NIM OpenGSN paymaster architecture allowed a targeted liquidity drain on Polygon worth $50.4k. The exploit vector forged an open HTLC request, systematically extracting USDC, USDT0, and USDC.e from liquidity pools via precomputed hash locks.
📌 While Nimiq has halted Gas Abstraction stablecoin functions to mitigate further exposure, contract-level security vulnerabilities highlight how institutional liquidity remains vulnerable to unchecked relay execution parameters. 💬 Do you double-check smart contract audit reports before providing liquidity to cross-chain protocols? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NIM #Polygon #DeFi #CryptoSecurity
🚨 🛡️
🚨 $NIM POLYGON CONTRACT EXPLOITED FOR $50K AFTER CRITICAL SIGNATURE VERIFICATION FAILURE! 🔻
🔍 A zero-signature verification oversight in $NIM OpenGSN paymaster architecture allowed a targeted liquidity drain on Polygon worth $50.4k. The exploit vector forged an open HTLC request, systematically extracting USDC, USDT0, and USDC.e from liquidity pools via precomputed hash locks.
📌 While Nimiq has halted Gas Abstraction stablecoin functions to mitigate further exposure, contract-level security vulnerabilities highlight how institutional liquidity remains vulnerable to unchecked relay execution parameters. 💬 Do you double-check smart contract audit reports before providing liquidity to cross-chain protocols? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NIM #Polygon #DeFi #CryptoSecurity
🚨 🛡️
🔍 A zero-signature verification oversight in $NIM OpenGSN paymaster architecture allowed a targeted liquidity drain on Polygon worth $50.4k. The exploit vector forged an open HTLC request, systematically extracting USDC, USDT0, and USDC.e from liquidity pools via precomputed hash locks.
📌 While Nimiq has halted Gas Abstraction stablecoin functions to mitigate further exposure, contract-level security vulnerabilities highlight how institutional liquidity remains vulnerable to unchecked relay execution parameters. 💬 Do you double-check smart contract audit reports before providing liquidity to cross-chain protocols? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NIM #Polygon #DeFi #CryptoSecurity
🚨 🛡️

·
--
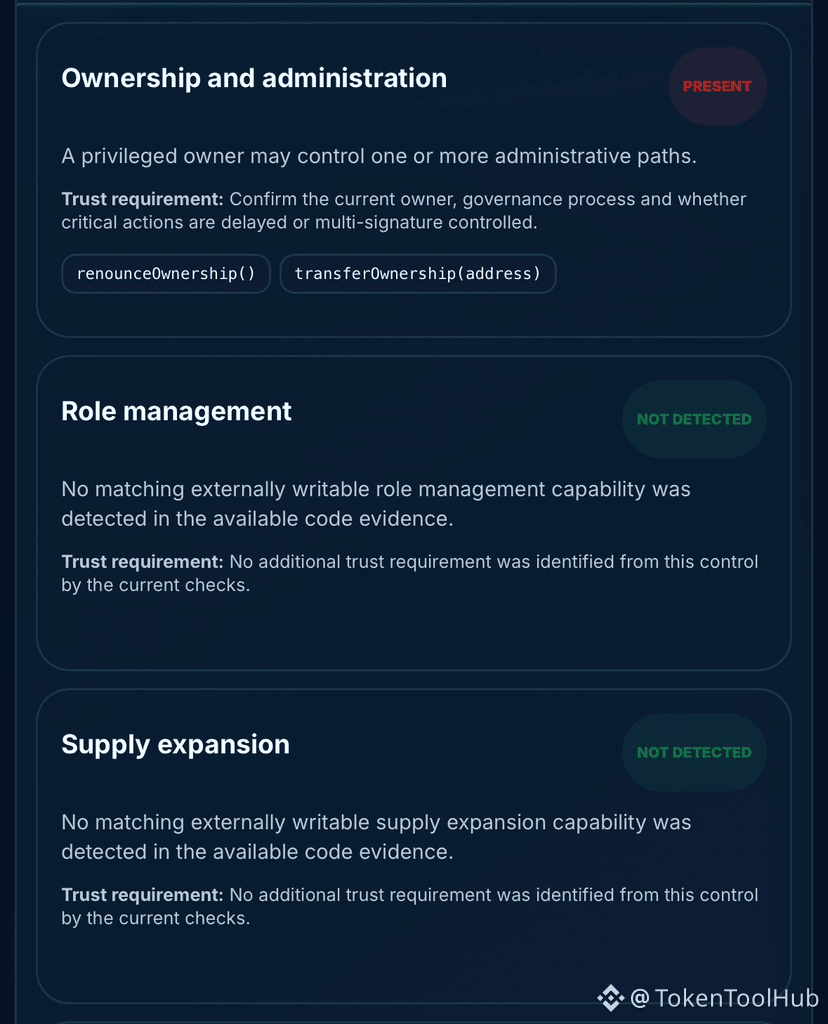
$Mysoul returned 90/100 on both the quick public-risk layer and deeper TokenToolHub contract intelligence.
Contract:
0x5B69C011e62243eFa77631523dde8F5c7643Df63
Network: BNB Smart Chain
Key findings:
• Honeypot: Not detected
• Buy tax: 0%
• Sell tax: 0%
• Ownership: Renounced
• Proxy: Not detected
• Total supply: 1B $Mysoul
• Supply expansion: Not detected
• Supply reduction: Not detected
• Wallet restrictions: Not detected
• Mutable fees/taxes: Not detected
• Trading switches: Not detected
• Emergency pause: Not detected
• Upgrade authority: Not detected
• Generic external execution: Not detected
The current control surface is comparatively clean.
The live owner() call returns the zero address, confirming ownership is currently renounced.
TokenToolHub also found no material indication of:
• Holder lockout
• Supply dilution
• Post-purchase fee escalation
• Implementation replacement
• Generic execution abuse
But there is one important caveat.
The explorer supplied a Similar Match rather than exact verified source for this deployment.
Runtime bytecode similarity is useful evidence, but constructor parameters and initialization state can still differ from the matched source.
That means the next step is not chasing an obvious dangerous control.
It is confirming that the matched code accurately represents this specific deployment and that initialization did not introduce different behavior.
Recent contract activity, token transfers and creation context were unavailable, so those areas remain unresolved.
90/100 quick.
90/100 deeper.
Clean current evidence, with source provenance still worth verifying.
Full $Mysoul scan:
https://tokentoolhub.com/token-safety-checker/?net=bsc&address=0x5B69C011e62243eFa77631523dde8F5c7643Df63
#BNBChain #crypto #Web3 #blockchain #CryptoSecurity
$Mysoul returned 90/100 on both the quick public-risk layer and deeper TokenToolHub contract intelligence.
Contract:
0x5B69C011e62243eFa77631523dde8F5c7643Df63
Network: BNB Smart Chain
Key findings:
• Honeypot: Not detected
• Buy tax: 0%
• Sell tax: 0%
• Ownership: Renounced
• Proxy: Not detected
• Total supply: 1B $Mysoul
• Supply expansion: Not detected
• Supply reduction: Not detected
• Wallet restrictions: Not detected
• Mutable fees/taxes: Not detected
• Trading switches: Not detected
• Emergency pause: Not detected
• Upgrade authority: Not detected
• Generic external execution: Not detected
The current control surface is comparatively clean.
The live owner() call returns the zero address, confirming ownership is currently renounced.
TokenToolHub also found no material indication of:
• Holder lockout
• Supply dilution
• Post-purchase fee escalation
• Implementation replacement
• Generic execution abuse
But there is one important caveat.
The explorer supplied a Similar Match rather than exact verified source for this deployment.
Runtime bytecode similarity is useful evidence, but constructor parameters and initialization state can still differ from the matched source.
That means the next step is not chasing an obvious dangerous control.
It is confirming that the matched code accurately represents this specific deployment and that initialization did not introduce different behavior.
Recent contract activity, token transfers and creation context were unavailable, so those areas remain unresolved.
90/100 quick.
90/100 deeper.
Clean current evidence, with source provenance still worth verifying.
Full $Mysoul scan:
https://tokentoolhub.com/token-safety-checker/?net=bsc&address=0x5B69C011e62243eFa77631523dde8F5c7643Df63
#BNBChain #crypto #Web3 #blockchain #CryptoSecurity
Contract:
0x5B69C011e62243eFa77631523dde8F5c7643Df63
Network: BNB Smart Chain
Key findings:
• Honeypot: Not detected
• Buy tax: 0%
• Sell tax: 0%
• Ownership: Renounced
• Proxy: Not detected
• Total supply: 1B $Mysoul
• Supply expansion: Not detected
• Supply reduction: Not detected
• Wallet restrictions: Not detected
• Mutable fees/taxes: Not detected
• Trading switches: Not detected
• Emergency pause: Not detected
• Upgrade authority: Not detected
• Generic external execution: Not detected
The current control surface is comparatively clean.
The live owner() call returns the zero address, confirming ownership is currently renounced.
TokenToolHub also found no material indication of:
• Holder lockout
• Supply dilution
• Post-purchase fee escalation
• Implementation replacement
• Generic execution abuse
But there is one important caveat.
The explorer supplied a Similar Match rather than exact verified source for this deployment.
Runtime bytecode similarity is useful evidence, but constructor parameters and initialization state can still differ from the matched source.
That means the next step is not chasing an obvious dangerous control.
It is confirming that the matched code accurately represents this specific deployment and that initialization did not introduce different behavior.
Recent contract activity, token transfers and creation context were unavailable, so those areas remain unresolved.
90/100 quick.
90/100 deeper.
Clean current evidence, with source provenance still worth verifying.
Full $Mysoul scan:
https://tokentoolhub.com/token-safety-checker/?net=bsc&address=0x5B69C011e62243eFa77631523dde8F5c7643Df63
#BNBChain #crypto #Web3 #blockchain #CryptoSecurity
49
🚨 Blockstream: No pagarán rescate tras hack Liquid Network
Blockstream se niega a pagar el rescate exigido por los hackers tras el ataque al Liquid Network. La empresa ha adoptado una postura firme contra los responsables del incidente.
¿Crees que Blockstream tomó la decisión correcta? 🤔
$BTC #CryptoSecurity
Contenido informativo. No constituye asesoría financiera.
🚨 Blockstream: No pagarán rescate tras hack Liquid Network
Blockstream se niega a pagar el rescate exigido por los hackers tras el ataque al Liquid Network. La empresa ha adoptado una postura firme contra los responsables del incidente.
¿Crees que Blockstream tomó la decisión correcta? 🤔
$BTC #CryptoSecurity
Contenido informativo. No constituye asesoría financiera.
Blockstream se niega a pagar el rescate exigido por los hackers tras el ataque al Liquid Network. La empresa ha adoptado una postura firme contra los responsables del incidente.
¿Crees que Blockstream tomó la decisión correcta? 🤔
$BTC #CryptoSecurity
Contenido informativo. No constituye asesoría financiera.
2
Security alert for the Cardano community! IOG has flagged a potential compromise of its official YouTube channel after unauthorized streams featuring deepfaked Hoskinson content started pushing crypto giveaway scams. This incident highlights a recurring vulnerability in major crypto platforms. Always verify official announcements through verified community channels and never trust links promising unrealistically high returns. Stay vigilant out there! $ADA #Cardano #CryptoSecurity #ScamAlert
Security alert for the Cardano community! IOG has flagged a potential compromise of its official YouTube channel after unauthorized streams featuring deepfaked Hoskinson content started pushing crypto giveaway scams. This incident highlights a recurring vulnerability in major crypto platforms. Always verify official announcements through verified community channels and never trust links promising unrealistically high returns. Stay vigilant out there! $ADA #Cardano #CryptoSecurity #ScamAlert
29
Asia crypto news highlights a persistent security threat as nation-state actors like North Korea and Iran drive a major surge in onchain malware targeting users. Beyond the threats, regional adoption metrics show fascinating shifts, including Malaysia emerging as a deeply crypto-curious Islamic nation. This duality proves that while Web3 education and user curiosity are expanding rapidly across Asia, robust operational security remains more critical than ever for every trader. #CryptoSecurity #Web3 #AsiaCrypto
Asia crypto news highlights a persistent security threat as nation-state actors like North Korea and Iran drive a major surge in onchain malware targeting users. Beyond the threats, regional adoption metrics show fascinating shifts, including Malaysia emerging as a deeply crypto-curious Islamic nation. This duality proves that while Web3 education and user curiosity are expanding rapidly across Asia, robust operational security remains more critical than ever for every trader. #CryptoSecurity #Web3 #AsiaCrypto
54
·
--
Мақала
North Korea Fuels Onchain Malware Surge, CoinEx Shuts Down OperationsThe latest data shows that North Korea and Iran now account for 68% of all onchain malware activity, while Malaysia emerges as a surprisingly crypto‑savvy Islamic nation. This shift is reshaping risk profiles for institutional traders and regulators alike.
Why this matters now: Onchain malware is no longer a niche threat. In the past 24 hours alone, malicious actors have siphoned over $1.4 B from exchanges, with CoinEx reporting a 35% spike in suspicious outbound transactions before shutting its platform. The concentration of attacks in the DPRK and IRAN regions coincides with a 12% uptick in their respective blockchain traffic, indicating a coordinated effort to exploit emerging protocols.
Smart money is already reacting. Hedge funds are tightening controls on exposure to high‑risk chains, and several major custodians have announced new AML filters targeting IP addresses linked to North Korean nodes. #CryptoSecurity #AML #BlockchainRisk
Forward signal: Watch the 0.0005 BTC threshold on the BNB Chain. If malicious activity crosses this level, we anticipate a 20%+ correction in the next 48 hours as liquidity providers pull back. #BNB
Are you prepared to adjust your portfolio in light of this new threat landscape?
North Korea Fuels Onchain Malware Surge, CoinEx Shuts Down Operations
The latest data shows that North Korea and Iran now account for 68% of all onchain malware activity, while Malaysia emerges as a surprisingly crypto‑savvy Islamic nation. This shift is reshaping risk profiles for institutional traders and regulators alike.
Why this matters now: Onchain malware is no longer a niche threat. In the past 24 hours alone, malicious actors have siphoned over $1.4 B from exchanges, with CoinEx reporting a 35% spike in suspicious outbound transactions before shutting its platform. The concentration of attacks in the DPRK and IRAN regions coincides with a 12% uptick in their respective blockchain traffic, indicating a coordinated effort to exploit emerging protocols.
Smart money is already reacting. Hedge funds are tightening controls on exposure to high‑risk chains, and several major custodians have announced new AML filters targeting IP addresses linked to North Korean nodes. #CryptoSecurity #AML #BlockchainRisk
Forward signal: Watch the 0.0005 BTC threshold on the BNB Chain. If malicious activity crosses this level, we anticipate a 20%+ correction in the next 48 hours as liquidity providers pull back. #BNB
Are you prepared to adjust your portfolio in light of this new threat landscape?
Why this matters now: Onchain malware is no longer a niche threat. In the past 24 hours alone, malicious actors have siphoned over $1.4 B from exchanges, with CoinEx reporting a 35% spike in suspicious outbound transactions before shutting its platform. The concentration of attacks in the DPRK and IRAN regions coincides with a 12% uptick in their respective blockchain traffic, indicating a coordinated effort to exploit emerging protocols.
Smart money is already reacting. Hedge funds are tightening controls on exposure to high‑risk chains, and several major custodians have announced new AML filters targeting IP addresses linked to North Korean nodes. #CryptoSecurity #AML #BlockchainRisk
Forward signal: Watch the 0.0005 BTC threshold on the BNB Chain. If malicious activity crosses this level, we anticipate a 20%+ correction in the next 48 hours as liquidity providers pull back. #BNB
Are you prepared to adjust your portfolio in light of this new threat landscape?
88
·
--
🔐 A HACKER WITH YOUR PASSWORD SHOULD STILL NOT BE ABLE TO STEAL A SINGLE DOLLAR.
Here's how to make that true. 5 settings, 10 minutes, once.
1️⃣ WITHDRAWAL WHITELIST (the most ignored feature on Binance)
→ Profile → Security → Withdrawal Whitelist → ON
→ Withdrawals can ONLY go to addresses YOU pre-approved
→ New address added? Mandatory waiting period before it works
→ A hacker inside your account literally can't send funds anywhere
2️⃣ ANTI-PHISHING CODE
→ Security → Anti-Phishing Code → create a word only you know
→ Every real Binance email will contain it
→ Email doesn't have your code? It's fake. Delete it.
3️⃣ PASSKEY instead of SMS 2FA
→ SMS can be SIM-swapped. Passkeys (Face ID / fingerprint / hardware key) can't.
→ Security → Passkeys → add your phone or a YubiKey
4️⃣ DEVICE MANAGEMENT
→ Security → Device Management → remove every device you don't recognise
→ Do this once a month
5️⃣ SEPARATE EMAIL for your exchange
→ One email used ONLY for Binance. Never posted anywhere.
→ Most account takeovers start from a leaked email, not a hacked exchange
Binance itself just warned about a wave of phishing texts this month.
Binance will NEVER text you a link to "secure your account."
Your keys, your crypto. Your settings, your safety.
Which of these were you missing? Be honest 👇
$BNB $BTC
#CryptoSecurity #BinanceTips #security #Phishing #Bitcoin
🔐 A HACKER WITH YOUR PASSWORD SHOULD STILL NOT BE ABLE TO STEAL A SINGLE DOLLAR.
Here's how to make that true. 5 settings, 10 minutes, once.
1️⃣ WITHDRAWAL WHITELIST (the most ignored feature on Binance)
→ Profile → Security → Withdrawal Whitelist → ON
→ Withdrawals can ONLY go to addresses YOU pre-approved
→ New address added? Mandatory waiting period before it works
→ A hacker inside your account literally can't send funds anywhere
2️⃣ ANTI-PHISHING CODE
→ Security → Anti-Phishing Code → create a word only you know
→ Every real Binance email will contain it
→ Email doesn't have your code? It's fake. Delete it.
3️⃣ PASSKEY instead of SMS 2FA
→ SMS can be SIM-swapped. Passkeys (Face ID / fingerprint / hardware key) can't.
→ Security → Passkeys → add your phone or a YubiKey
4️⃣ DEVICE MANAGEMENT
→ Security → Device Management → remove every device you don't recognise
→ Do this once a month
5️⃣ SEPARATE EMAIL for your exchange
→ One email used ONLY for Binance. Never posted anywhere.
→ Most account takeovers start from a leaked email, not a hacked exchange
Binance itself just warned about a wave of phishing texts this month.
Binance will NEVER text you a link to "secure your account."
Your keys, your crypto. Your settings, your safety.
Which of these were you missing? Be honest 👇
$BNB $BTC
#CryptoSecurity #BinanceTips #security #Phishing #Bitcoin
Here's how to make that true. 5 settings, 10 minutes, once.
1️⃣ WITHDRAWAL WHITELIST (the most ignored feature on Binance)
→ Profile → Security → Withdrawal Whitelist → ON
→ Withdrawals can ONLY go to addresses YOU pre-approved
→ New address added? Mandatory waiting period before it works
→ A hacker inside your account literally can't send funds anywhere
2️⃣ ANTI-PHISHING CODE
→ Security → Anti-Phishing Code → create a word only you know
→ Every real Binance email will contain it
→ Email doesn't have your code? It's fake. Delete it.
3️⃣ PASSKEY instead of SMS 2FA
→ SMS can be SIM-swapped. Passkeys (Face ID / fingerprint / hardware key) can't.
→ Security → Passkeys → add your phone or a YubiKey
4️⃣ DEVICE MANAGEMENT
→ Security → Device Management → remove every device you don't recognise
→ Do this once a month
5️⃣ SEPARATE EMAIL for your exchange
→ One email used ONLY for Binance. Never posted anywhere.
→ Most account takeovers start from a leaked email, not a hacked exchange
Binance itself just warned about a wave of phishing texts this month.
Binance will NEVER text you a link to "secure your account."
Your keys, your crypto. Your settings, your safety.
Which of these were you missing? Be honest 👇
$BNB $BTC
#CryptoSecurity #BinanceTips #security #Phishing #Bitcoin
4
🔒 حماية محفظتك الرقمية تبدأ من تفاصيل صغيرة!
الكثير من المستخدمين يقعون في فخاخ بسيطة بسبب التهاون في إعدادات الأمان. إليك أبرز الأخطاء التي يجب تجنبها تماماً:
مشاركة العبارة السرية (Seed Phrase): لا تعطِ هذه العبارة لأي شخص تحت أي ظرف، حتى لو ادعى أنه دعم فني للمنصة.
الروابط المشبوهة: تجنب النقر على الروابط التي تصلك عبر الرسائل أو وسائل التواصل وتعدك بأرباح مجانية أو مسابقات وهمية.
المصادقة الثنائية: احرص دائماً على ربط حسابك بتطبيقات التحقق وتفعيل كافة طبقات الحماية المتاحة.
الأمان الإلكتروني مسؤوليتك الشخصية أولاً واخيراً. هل قمت بتفعيل كافة ميزات الأمان على حسابك اليوم؟ 👇
#BinanceSquare #CryptoSecurity
#أمان #تداول_آمن
🔒 حماية محفظتك الرقمية تبدأ من تفاصيل صغيرة!
الكثير من المستخدمين يقعون في فخاخ بسيطة بسبب التهاون في إعدادات الأمان. إليك أبرز الأخطاء التي يجب تجنبها تماماً:
مشاركة العبارة السرية (Seed Phrase): لا تعطِ هذه العبارة لأي شخص تحت أي ظرف، حتى لو ادعى أنه دعم فني للمنصة.
الروابط المشبوهة: تجنب النقر على الروابط التي تصلك عبر الرسائل أو وسائل التواصل وتعدك بأرباح مجانية أو مسابقات وهمية.
المصادقة الثنائية: احرص دائماً على ربط حسابك بتطبيقات التحقق وتفعيل كافة طبقات الحماية المتاحة.
الأمان الإلكتروني مسؤوليتك الشخصية أولاً واخيراً. هل قمت بتفعيل كافة ميزات الأمان على حسابك اليوم؟ 👇
#BinanceSquare #CryptoSecurity
#أمان #تداول_آمن
الكثير من المستخدمين يقعون في فخاخ بسيطة بسبب التهاون في إعدادات الأمان. إليك أبرز الأخطاء التي يجب تجنبها تماماً:
مشاركة العبارة السرية (Seed Phrase): لا تعطِ هذه العبارة لأي شخص تحت أي ظرف، حتى لو ادعى أنه دعم فني للمنصة.
الروابط المشبوهة: تجنب النقر على الروابط التي تصلك عبر الرسائل أو وسائل التواصل وتعدك بأرباح مجانية أو مسابقات وهمية.
المصادقة الثنائية: احرص دائماً على ربط حسابك بتطبيقات التحقق وتفعيل كافة طبقات الحماية المتاحة.
الأمان الإلكتروني مسؤوليتك الشخصية أولاً واخيراً. هل قمت بتفعيل كافة ميزات الأمان على حسابك اليوم؟ 👇
#BinanceSquare #CryptoSecurity
#أمان #تداول_آمن
75

Personal AI agents can handle your entire crypto workflow from research to execution, yet most users have no idea how easily they can be compromised.
The real pain is watching an AI agent you trusted dump your $MIRA bags at the worst time or worse, leak your seed because you gave it too much access. Traders keep getting rugged by tools that promised to make everything natural and easy.
Mira is built as a personal AI agent that lets you interact with digital tasks and workflows more naturally, like chatting instead of clicking through 10 DeFi dashboards. It sounds great on paper. You tell it to rebalance your portfolio or check on-chain data and it just does it.
But here's the catch most people miss. These agents need deep access to your wallets, APIs, and data feeds to work. One bad prompt or a supply chain attack and your funds are gone. We've seen similar setups with $FET agents go sideways when the model hallucinates a safe yield farm that's actually a honeypot.
Over-reliance is the silent killer. You stop checking the on-chain data yourself because the agent knows better. Then $OCEAN data oracles get manipulated and the whole thing snowballs into a loss you can't recover from.
What's your take on giving AI this much control over your bags?
#AIAgents #CryptoSecurity #Web3
Personal AI agents can handle your entire crypto workflow from research to execution, yet most users have no idea how easily they can be compromised.
The real pain is watching an AI agent you trusted dump your $MIRA bags at the worst time or worse, leak your seed because you gave it too much access. Traders keep getting rugged by tools that promised to make everything natural and easy.
Mira is built as a personal AI agent that lets you interact with digital tasks and workflows more naturally, like chatting instead of clicking through 10 DeFi dashboards. It sounds great on paper. You tell it to rebalance your portfolio or check on-chain data and it just does it.
But here's the catch most people miss. These agents need deep access to your wallets, APIs, and data feeds to work. One bad prompt or a supply chain attack and your funds are gone. We've seen similar setups with $FET agents go sideways when the model hallucinates a safe yield farm that's actually a honeypot.
Over-reliance is the silent killer. You stop checking the on-chain data yourself because the agent knows better. Then $OCEAN data oracles get manipulated and the whole thing snowballs into a loss you can't recover from.
What's your take on giving AI this much control over your bags?
#AIAgents #CryptoSecurity #Web3
The real pain is watching an AI agent you trusted dump your $MIRA bags at the worst time or worse, leak your seed because you gave it too much access. Traders keep getting rugged by tools that promised to make everything natural and easy.
Mira is built as a personal AI agent that lets you interact with digital tasks and workflows more naturally, like chatting instead of clicking through 10 DeFi dashboards. It sounds great on paper. You tell it to rebalance your portfolio or check on-chain data and it just does it.
But here's the catch most people miss. These agents need deep access to your wallets, APIs, and data feeds to work. One bad prompt or a supply chain attack and your funds are gone. We've seen similar setups with $FET agents go sideways when the model hallucinates a safe yield farm that's actually a honeypot.
Over-reliance is the silent killer. You stop checking the on-chain data yourself because the agent knows better. Then $OCEAN data oracles get manipulated and the whole thing snowballs into a loss you can't recover from.
What's your take on giving AI this much control over your bags?
#AIAgents #CryptoSecurity #Web3
112
Vitalik just dropped a game-changing take on AI and crypto security. While many worry about AI-driven exploits, he argues the tech will ultimately favor defenders. By helping developers mathematically verify complex codebases, AI could eliminate entire classes of smart contract bugs. It flips the narrative from vulnerability to absolute resilience. $ETH #Ethereum #AI #CryptoSecurity
Vitalik just dropped a game-changing take on AI and crypto security. While many worry about AI-driven exploits, he argues the tech will ultimately favor defenders. By helping developers mathematically verify complex codebases, AI could eliminate entire classes of smart contract bugs. It flips the narrative from vulnerability to absolute resilience. $ETH #Ethereum #AI #CryptoSecurity
12

·
--
everyone thinks storing bags in popular wallets means you are 100% safe, but actually convenience is usually the biggest trap in crypto.
most traders keep their entire stack sitting in everyday interfaces, only to get caught off guard by custody risks or frozen balances when they need liquidity the most. watching your hard-earned gains get stuck or drained because of custody blindspots is the worst feeling in this space.
take a look at how users treated top solutions like my wallet and gram wallet across the $TON ecosystem. these two handled massive daily volume and held millions in liquidity, serving as default hubs for moving native assets alongside tokens like $GRAM and standard pairs with $USDT. people blindly trusted them simply because everyone else was using them.
ngl ser, when an ecosystem expands rapidly, the line between convenient access and third-party exposure gets blurry fast. if you are not actively separating your daily degen trading balance from a dedicated cold vault, you are taking unnecessary risks with your capital. scale alone does not guarantee total protection.
how much of your stack do you actually keep in active hot wallets versus cold storage?
#CryptoSecurity #TON #Web3Wallets
everyone thinks storing bags in popular wallets means you are 100% safe, but actually convenience is usually the biggest trap in crypto.
most traders keep their entire stack sitting in everyday interfaces, only to get caught off guard by custody risks or frozen balances when they need liquidity the most. watching your hard-earned gains get stuck or drained because of custody blindspots is the worst feeling in this space.
take a look at how users treated top solutions like my wallet and gram wallet across the $TON ecosystem. these two handled massive daily volume and held millions in liquidity, serving as default hubs for moving native assets alongside tokens like $GRAM and standard pairs with $USDT. people blindly trusted them simply because everyone else was using them.
ngl ser, when an ecosystem expands rapidly, the line between convenient access and third-party exposure gets blurry fast. if you are not actively separating your daily degen trading balance from a dedicated cold vault, you are taking unnecessary risks with your capital. scale alone does not guarantee total protection.
how much of your stack do you actually keep in active hot wallets versus cold storage?
#CryptoSecurity #TON #Web3Wallets
most traders keep their entire stack sitting in everyday interfaces, only to get caught off guard by custody risks or frozen balances when they need liquidity the most. watching your hard-earned gains get stuck or drained because of custody blindspots is the worst feeling in this space.
take a look at how users treated top solutions like my wallet and gram wallet across the $TON ecosystem. these two handled massive daily volume and held millions in liquidity, serving as default hubs for moving native assets alongside tokens like $GRAM and standard pairs with $USDT. people blindly trusted them simply because everyone else was using them.
ngl ser, when an ecosystem expands rapidly, the line between convenient access and third-party exposure gets blurry fast. if you are not actively separating your daily degen trading balance from a dedicated cold vault, you are taking unnecessary risks with your capital. scale alone does not guarantee total protection.
how much of your stack do you actually keep in active hot wallets versus cold storage?
#CryptoSecurity #TON #Web3Wallets
60
·
--
Төмен (кемімелі)
30 күндегі $ETH сауда көлемі: 50 USDT
اختراق خطير على Reddit!
تم اختراق الحساب الموثق لـ HBO Max على Reddit واستخدامه لنشر 108 إعلانات خبيثة خلال 48 ساعة.
الهدف؟ دفع المستخدمين إلى تنزيل برمجيات ضارة، بينها تطبيقات محافظ كريبتو مزيفة يمكنها سرقة عبارات الاسترداد (Seed Phrase) ومعلومات حساسة.
⚠️ التوثيق وحده لا يعني أن الرابط آمن.
لا تُدخل Seed Phrase في أي تطبيق أو موقع تم الوصول إليه عبر إعلان أو رابط مشبوه.
$BTC $ETH $RDDT
#CryptoSecurity #CyberSecurity #bitcoin
اختراق خطير على Reddit!
تم اختراق الحساب الموثق لـ HBO Max على Reddit واستخدامه لنشر 108 إعلانات خبيثة خلال 48 ساعة.
الهدف؟ دفع المستخدمين إلى تنزيل برمجيات ضارة، بينها تطبيقات محافظ كريبتو مزيفة يمكنها سرقة عبارات الاسترداد (Seed Phrase) ومعلومات حساسة.
⚠️ التوثيق وحده لا يعني أن الرابط آمن.
لا تُدخل Seed Phrase في أي تطبيق أو موقع تم الوصول إليه عبر إعلان أو رابط مشبوه.
$BTC $ETH $RDDT
#CryptoSecurity #CyberSecurity #bitcoin
تم اختراق الحساب الموثق لـ HBO Max على Reddit واستخدامه لنشر 108 إعلانات خبيثة خلال 48 ساعة.
الهدف؟ دفع المستخدمين إلى تنزيل برمجيات ضارة، بينها تطبيقات محافظ كريبتو مزيفة يمكنها سرقة عبارات الاسترداد (Seed Phrase) ومعلومات حساسة.
⚠️ التوثيق وحده لا يعني أن الرابط آمن.
لا تُدخل Seed Phrase في أي تطبيق أو موقع تم الوصول إليه عبر إعلان أو رابط مشبوه.
$BTC $ETH $RDDT
#CryptoSecurity #CyberSecurity #bitcoin
Ali_BTC_77:
شكرا على المعلومات اختي
7
4
358
Көбірек контент көру үшін кіріңіз
Binance Square платформасында әлемдік криптоқоғамдастыққа қосылыңыз
⚡️ Криптовалюта туралы ең соңғы және пайдалы ақпаратты алыңыз.
💬 Әлемдегі ең ірі криптобиржаның сеніміне ие.
👍 Расталған авторлардың нақты пікірлерін табыңыз.
Электрондық пошта/телефон нөмірі
Трендтегі тақырыптар
1
#BTCBreaks80K
48,529 рет көрілді
1,212 адам талқылап жатыр
2
#比特币突破8万
50,812 рет көрілді
173 адам талқылап жатыр
3
#BuffettBecomesBerkshireChairmanEmeritus
10,053 рет көрілді
407 адам талқылап жатыр
4
#ZcashSpotETFTops$230MMonthlyInflow
3,148 рет көрілді
63 адам талқылап жатыр
5
#HYPEJumpsOver11%
51,871 рет көрілді
996 адам талқылап жатыр
6
#ZcashDevelopersTargetNU7MainnetActivationNov5
22,324 рет көрілді
471 адам талқылап жатыр
7
#BitcoinSpotETFsNetInflow$159M
19,540 рет көрілді
98 адам талқылап жатыр
8
#HKMAPlansWholesaleCBDCByYearEnd
39,789 рет көрілді
883 адам талқылап жатыр
9
#NEARSurges26%Past$3.45
19,997 рет көрілді
146 адам талқылап жатыр
10
#BOJHikesRatesTo31YearHigh
70,004 рет көрілді
1,273 адам талқылап жатыр