

#cybersecurity
cybersecurity
1.5M views
3,447 Discussing
Hot
Latest

·
--
Singapore police flag $3.5 M loss from tampered Ledger hardware wallets.
The Singapore Police Force reported at least two cases since September 10 2026, amounting to about $3.5 million, after Ledger wallets bought from retail stores contained malicious hardware components that could steal recovery phrases or private keys and allow access to crypto assets.
Authorities are working with Ledger and have urged users to stop entering recovery phrases on suspicious devices, avoid further transactions, and contact the provider through official support channels.
Anyone who believes their recovery phrase or private key has been exposed should move remaining funds to a new, trusted wallet set up on a safe device with a newly generated recovery phrase.
The police also warned against sharing private keys or recovery phrases with anyone.
Earlier this month, reseller CryptoBilis confirmed an unauthorized hardware implant in a wallet and reported suspected losses of more than $80 million, later estimated at $102 million across 335 wallets on five blockchains.
Ledger has asked CryptoBilis to halt sales of its inventory while investigations continue and said its own systems show no evidence of compromise.
What concrete steps should crypto users adopt to verify hardware wallet integrity before trusting their assets?
#Crypto #FinTech #CyberSecurity #Ledger #HardwareWallet
🚨 BREAKING NEWS
Binance announced that it is aware of allegations regarding a potential security issue and is actively investigating the matter.
CZ, meanwhile, stated that user funds are safe and expressed his expectation that all user assets will be fully covered.
🔸 Tether: Frozen $971 million worth of USDT.
🔸 Circle: Frozen $823 million worth of USDC.
🔸 Total: $1.794 billion worth of stablecoins frozen.
CZ also emphasized that while he no longer manages Binance.com, as a shareholder, he expects user funds to be fully covered.
Key point: Binance’s statement indicates that security claims are being investigated; however, it does not, on its own, confirm a hack. CZ’s reassuring statement also does not replace the results of a technical investigation.
In the crypto ecosystem, the most important factors in such incidents are verified information, transparency, and concrete evidence regarding the security of user assets—rather than mere allegations.
I’m closely following this issue!
#Binance #Crypto #USDT #USDC #Cybersecurity
43
·
--
An outside certificate failure triggering Ethereum fixes? That got my attention. 🚨
A key blunder at Indian certificate issuer eMudhra left some Teku and Besu setups trusting forged certificates. Developers rushed out fixes.
The crucial distinction: default mainnet nodes weren’t exposed. This wasn’t a blanket failure across $ETH nodes.
For me, that’s the tension: reassuring defaults, but a worrying trust failure elsewhere.
Does the default-mainnet exclusion ease your concern, or is certificate trust the bigger issue? 🤔
#Ethereum #CyberSecurity #Blockchain
98

·
--
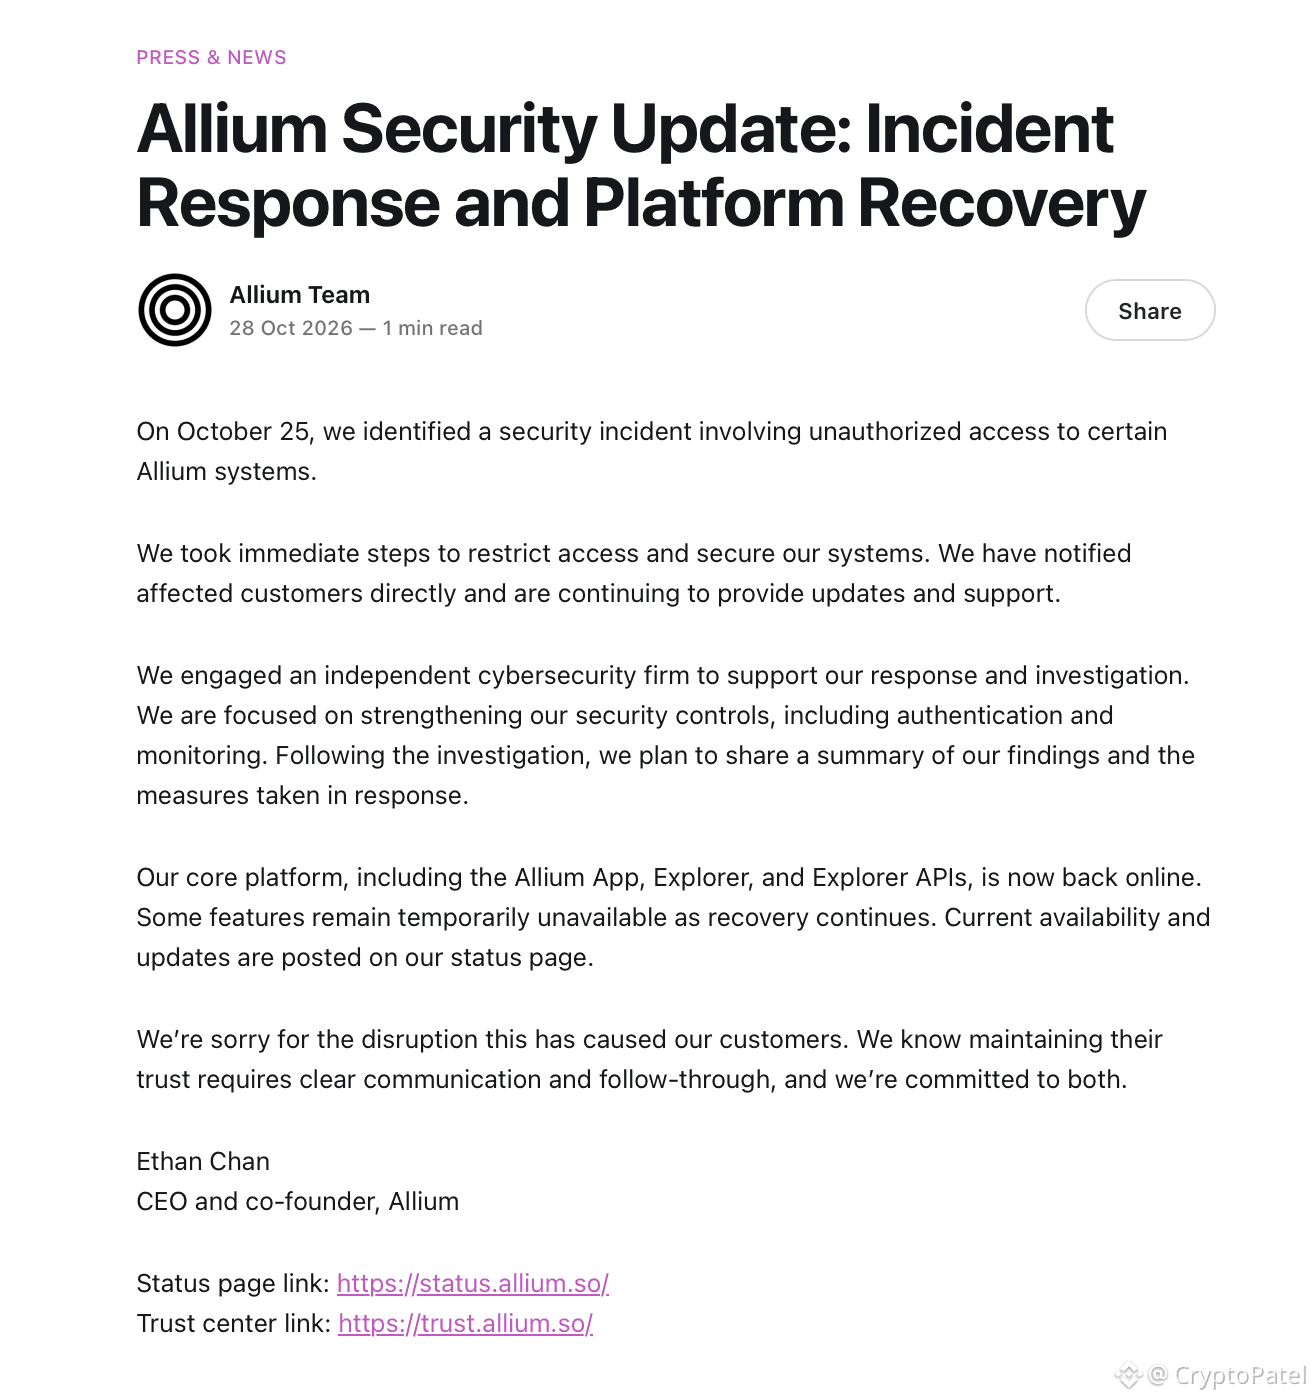
THE BIGGEST CRYPTO SECURITY RISK MAY NOT BE YOUR EXCHANGE. IT MAY BE THE DATA PROVIDER BEHIND IT.
Allium confirmed unauthorized access to its systems on October 25. Core services are back online, but some features remain offline as recovery continues.
Here’s what the industry should learn:
🔹 Your security is only as strong as your third-party dependencies.
🔹 API access is a security boundary, not just a technical feature.
🔹 Restored services don’t automatically mean verified data.
🔹 Transparency matters most when the full impact is still unknown.
No confirmed evidence currently establishes customer fund losses or breaches of Visa, Stripe or Coinbase systems in this incident.
How many crypto businesses have audited the security of the infrastructure they depend on?
In crypto, protecting your assets is only half the battle. Trusting the systems behind your data matters too.
#CryptoSecurity #Blockchain #Cybersecurity
178

·
--
🚨 ABLITERATED GLM-5.3 GOES LIVE IN 3 DAYS BOOSTING CYBER PERFORMANCE FOR $AI SECTOR! ⚡
Just three days after open weights dropped, Abliteration.ai stripped safety guardrails off GLM-5.3, unlocking a massive performance leap with ExploitBench task scores surging from 24.4% to 54.4%. 📊
By modifying core model weights directly, this non-rejection architecture opens the floodgates for unrestricted offensive red-teaming and autonomous agent testing. 💡 The sheer velocity of open-source development continues to reshape tech dynamics in real time. 🔍
💬 Will these raw, uncensored models drive the next massive wave of autonomous AI innovation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #CyberSecurity #TechTrends #Crypto
🔥 ⚡
12
·
--
🚨 🇺🇸 BREAKING: U.S. ELECTION SYSTEM TARGETED! $EVAA
⚠️ Hackers targeted the U.S. Federal Election Commission (FEC), disrupting campaign finance disclosures just ONE WEEK before the midterms, according to Reuters. $XAN
💥 The incident raises fresh concerns about cybersecurity and the availability of election-related information. $BLESS
👀 Who was behind the attack? And how long will the disruption last?
#BreakingNews #CyberSecurity #USA
1
355

🚨 MAJOR CRYPTO SECURITY ALERT! 🔐
Hackers reportedly claim they stole data linked to 15+ million accounts from a crypto casino and are demanding $15 million in Bitcoin to keep it secret. ₿
The claims have not been independently verified.
Crypto users should stay alert:
• Watch for phishing emails and fake support messages.
• Never share passwords or wallet recovery phrases.
• Enable two-factor authentication (2FA).
🚨 Data security remains a major concern across the crypto industry.
#CryptoSecurity #Bitcoin #CryptoNews #CyberSecurity
8

🚨 Crypto or Traditional Finance, Is Your Personal Data Really Safe❔
Reports of data leaks have raised fresh security concerns across both industries. Coinbase’s vendor Amplitude reportedly exposed some users’ contact information, with customer funds unaffected. South Korea’s Bithumb, Mirae Asset, and Daishin Securities have also been linked to reported user-data leaks.
{alpha}(560x1b379a79c91a540b2bcd612b4d713f31de1b80cc)
🔍 The bigger issue goes beyond stolen funds. Exposed contact details can increase the risk of phishing, impersonation, and targeted scams. Users should verify messages through official channels, never share passwords or verification codes, and enable strong account security.
{stock_us}(BNC.US)
📊 Platform reputation matters, but third-party vendors and data-handling practices deserve attention too. Security is part of financial trust, not just a technical feature.
{spot}(BNBUSDT)
Are financial platforms doing enough to protect user data?
$NAORIS $BNC.US $BNB #CoinVahini #Cybersecurity #CryptoNews #DataPrivacy
🚨 Crypto or Traditional Finance, Is Your Personal Data Really Safe❔
Reports of data leaks have raised fresh security concerns across both industries. Coinbase’s vendor Amplitude reportedly exposed some users’ contact information, with customer funds unaffected. South Korea’s Bithumb, Mirae Asset, and Daishin Securities have also been linked to reported user-data leaks.
🔍 The bigger issue goes beyond stolen funds. Exposed contact details can increase the risk of phishing, impersonation, and targeted scams. Users should verify messages through official channels, never share passwords or verification codes, and enable strong account security.
📊 Platform reputation matters, but third-party vendors and data-handling practices deserve attention too. Security is part of financial trust, not just a technical feature.
Are financial platforms doing enough to protect user data?
$NAORIS $BNC.US $BNB #CoinVahini #Cybersecurity #CryptoNews #DataPrivacy
4
·
--
🚨 BREAKING 🇰🇷 SOUTH KOREA HIT BY CYBERATTACKS! 💥 $AIN
Three major financial firms — Bithumb, Daishin Securities & Mirae Asset Global Investments — have reported data breaches! ⚠️ $EVAA
🔴 38,490 Daishin customers affected
🔴 Bithumb is investigating leaked personal information
🔴 Financial authorities are stepping in
🚨 Is South Korea facing a growing cybersecurity crisis? $HUMA
#Crypto #Bithumb #Bitcoin #Cybersecurity
2
1.3k
·
--
📰 NIST to Disallow Quantum-Vulnerable Cryptography After 2035
Its report also sets earlier federal milestones for post-quantum key establishment by 2030 and digital signatures by 2031.
Source : Econotimes
Time : 2026-10-27 16:40:55
Credit : elias mercer
#quantum_computing #nist #post-quantum_cryptography #cybersecurity
Share your opinion in the comment section below
3
·
--
The best time to prepare for a cryptographic threat is before it becomes urgent.
Research, testing and migration planning take time.
Waiting for a real-world exploit can be costly.
#Cryptography #CyberSecurity #blockchain #CryptoSecurity
The best time to prepare for a cryptographic threat is before it becomes urgent.
Research, testing and migration planning take time.
Waiting for a real-world exploit can be costly.
#Cryptography #CyberSecurity #blockchain #CryptoSecurity
Research, testing and migration planning take time.
Waiting for a real-world exploit can be costly.
#Cryptography #CyberSecurity #blockchain #CryptoSecurity
1
101
·
--
Future-proofing crypto isn't only about faster transactions.
It also means reviewing cryptographic assumptions and key management.
Security needs to evolve alongside computing capabilities.
#CryptoSecurity #Cryptography #blockchain #CyberSecurity
Future-proofing crypto isn't only about faster transactions.
It also means reviewing cryptographic assumptions and key management.
Security needs to evolve alongside computing capabilities.
#CryptoSecurity #Cryptography #blockchain #CyberSecurity
It also means reviewing cryptographic assumptions and key management.
Security needs to evolve alongside computing capabilities.
#CryptoSecurity #Cryptography #blockchain #CyberSecurity
1
53
·
--
A possible future threat isn't the same as an active exploit.
That distinction matters in crypto security.
Take emerging risks seriously without confusing research with demonstrated capability.
#Cryptography #AI #CryptoSecurity #CyberSecurity
A possible future threat isn't the same as an active exploit.
That distinction matters in crypto security.
Take emerging risks seriously without confusing research with demonstrated capability.
#Cryptography #AI #CryptoSecurity #CyberSecurity
That distinction matters in crypto security.
Take emerging risks seriously without confusing research with demonstrated capability.
#Cryptography #AI #CryptoSecurity #CyberSecurity
1
32
·
--
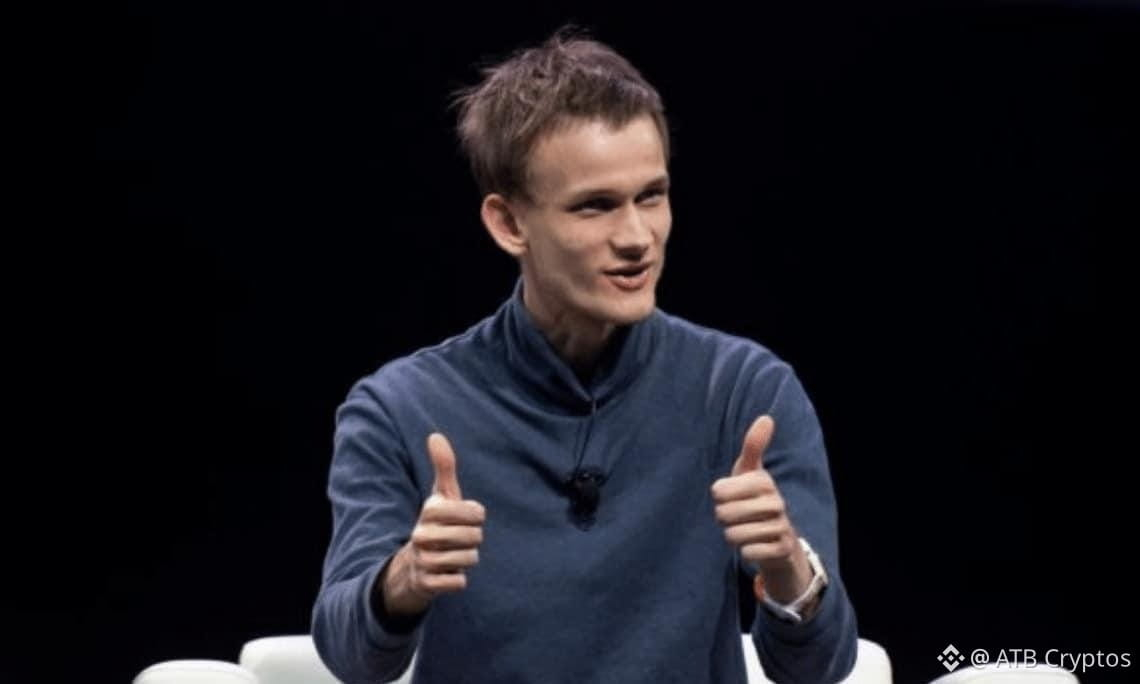
Vitalik Buterin backs Kimi 3.1’s self‑imposed limits on offensive AI tools.
He posted on X on Monday saying he is comfortable with the AI model Kimi 3.1 deliberately leaving top‑end offensive cyber capabilities out of its training data.
He argues the trade‑off buys defenders more time to prepare.
“Discriminating against use cases is MUCH less bad than discriminating against users,” he wrote, noting the world needs time to harden systems and check old code before the full weight of very powerful cyber attacks is upon us.
He prefers a model that declines certain tasks for everyone over one that turns certain people away.
In May 19 he countered fears that AI‑powered bug hunting would overwhelm developers, saying AI‑assisted formal verification could become one of the strongest defenses in crypto.
He said a model can now write both code and its proof, leaving developers to confirm the intended statement.
On October 8 he warned AI‑assisted mathematics could weaken ECDSA and similar cryptographic systems sooner than expected, but advised users not to scramble to move funds to new wallets today.
Do you think restricting AI model use cases is a sustainable path for cybersecurity, or does it risk creating an elitist access system?
#AI #Cybersecurity #Ethereum #FormalVerification
🚨 A HACKER STOLE MORE THAN 40,000 DHS EMPLOYEE RECORDS
📰 WHAT HAPPENED?
A hacker stole a trove of personal information from the Department of Homeland Security (DHS). The breach exposes the names, job titles, phone numbers, email addresses, and office locations of more than 41,000 employees, including those in US Immigration and Customs Enforcement (ICE) and Customs and Border Protection (CBP), according to TechCrunch and Wired. The […]
📊 TECHNOLOGY IMPACT
The case once again shines a spotlight on the security of digital systems and the need to strengthen protection against increasingly sophisticated attacks.
🔎 Source: The Verge
🤔 💬 Do you think incidents like this will lead companies to invest more in digital security?
#Cybersecurity #DataSecurity #Crypto_Marker #News
112

🚨 $OSMO CYBERSECURITY SUMMIT COULD REDEFINE DIGITAL ASSET SENTIMENT 📈
📊 The upcoming Japanese cybersecurity summit, chaired by PM Sanae Takaichi, puts institutional risk oversight front‑and‑center, a classic liquidity‑sweep catalyst for smart‑money flows.
🦈 If regulators tighten the data‑security net, a fresh demand block may emerge around $OSMO , while $ERA and $DOOD could serve as secondary order‑blocks absorbing sell‑side pressure. ⚡ Watch the 4H order‑flow for a bullish retest as confidence rebounds.
💬 Will the summit cement a new risk premium or ignite a short‑term volatility spike? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #OSMO #CyberSecurity #Liquidity #Crypto
🦈 🚀
6
·
--
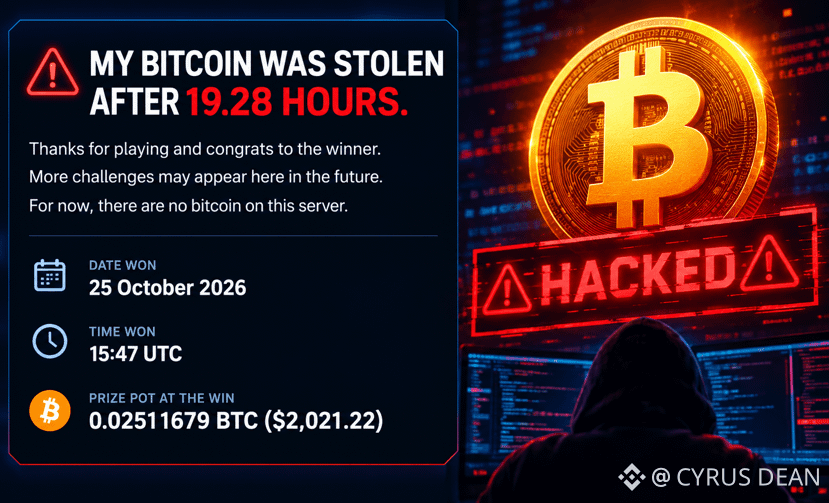
🚨 PHP VULNERABILITY HACKED IN JUST 19 HOURS!
A real Bitcoin challenge exposed the danger of vulnerable PHP servers. A hacker broke in within 19.28 HOURS and recovered the secret key to claim 0.02511679 BTC — worth around $2,021! 💀
⚠️ Exposed credentials, sensitive data, and crypto private keys could put funds at risk.
🔒 Running PHP? Patch vulnerable versions NOW. One security flaw could cost millions.
#bitcoin #CyberSecurity
138
·
--
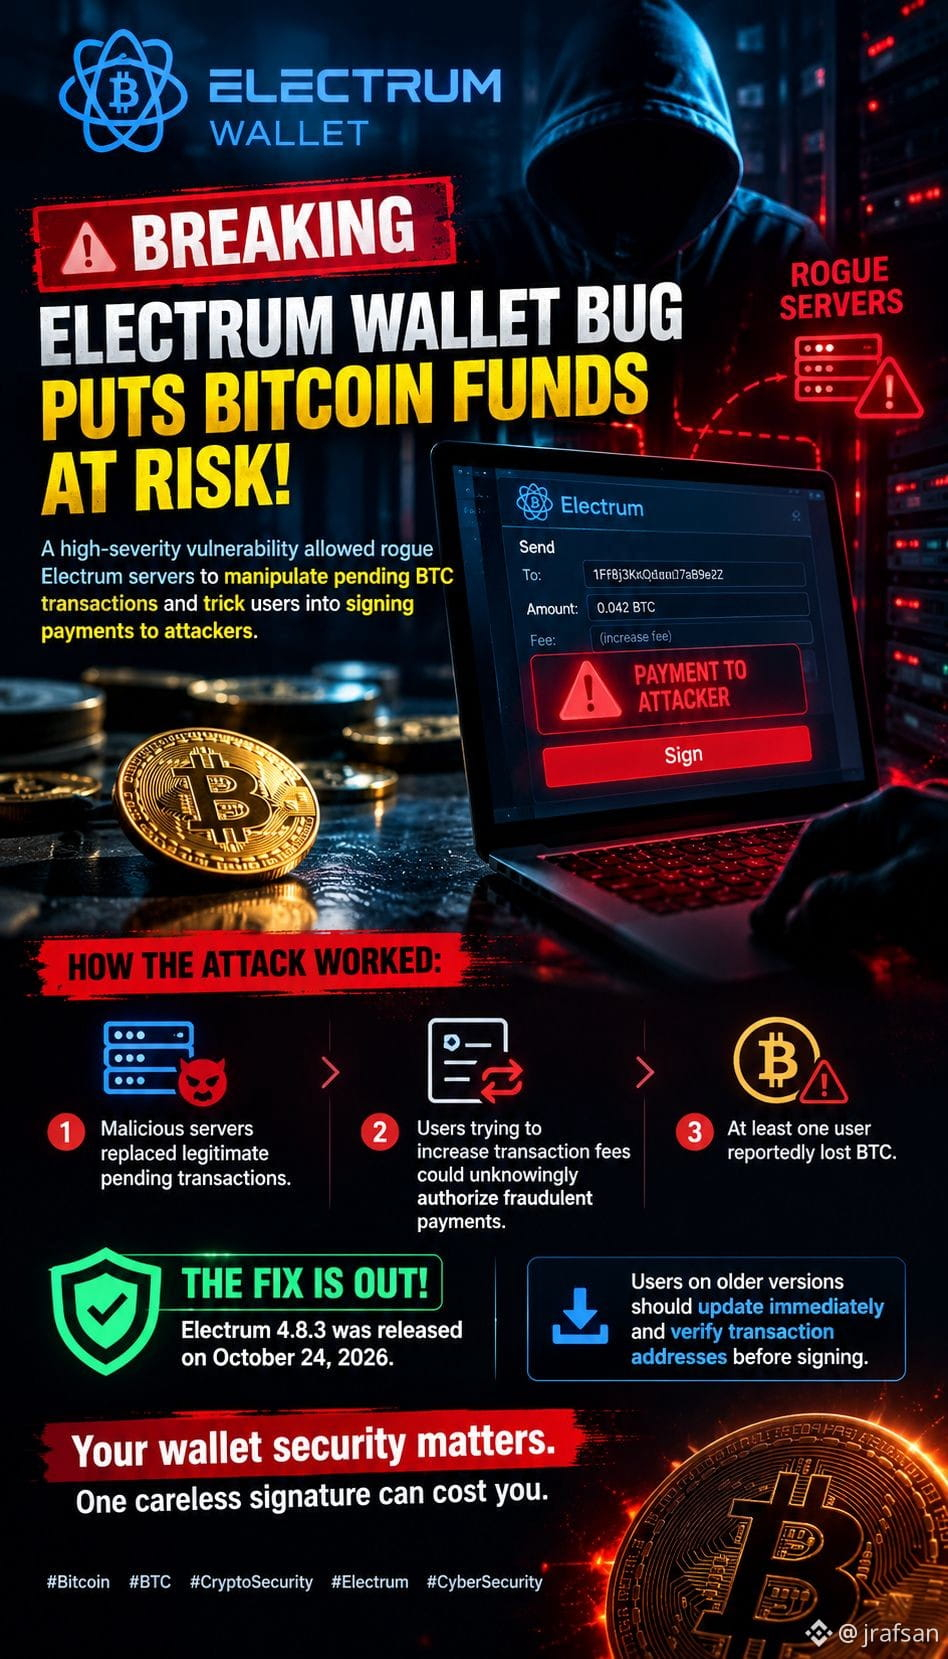
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
{future}(TRUMPUSDT)
$TRX
{future}(TRXUSDT)
$XRP
{future}(XRPUSDT)
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
$TRX
$XRP
221
🚨 JAPAN INTERNET GIANT GMO SAYS HACKERS POSTED STOLEN CUSTOMER DATA
📰 WHAT HAPPENED?
Japan's GMO Internet is verifying alleged customer data posted by suspected hackers following a cloud service breach.
📊 TECHNOLOGY IMPACT
The case puts the spotlight back on the security of digital systems and the need to strengthen protection against increasingly sophisticated attacks.
🔎 Source: TechCrunch
🤔 💬 Do you think incidents like this will lead companies to invest more in digital security?
#Cybersecurity #DataSecurity #Crypto_Marker #News
3
Various brute force attack on the #Starlite_crypto network and not to forget #STARLITE has built a strong fire wall to withstand any cyber-attack just in case something like this happens we are always ready to fight back. #CyberSecurity #cyberpunk #fight
Various brute force attack on the #Starlite_crypto network and not to forget #STARLITE has built a strong fire wall to withstand any cyber-attack just in case something like this happens we are always ready to fight back. #CyberSecurity #cyberpunk #fight
82
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#FedWatch
16.3M views
39,433 Discussing
2
#EarningsSeason
6.4M views
32,135 Discussing
3
#USMidtermElections
45,540 views
639 Discussing
4
#BitcoinDropsBelow$80K
30,757 views
122 Discussing
5
#BoEOpensConsultationOnTokenizedCollateralForClearing
660 views
30 Discussing
6
#BrazilCryptoExchangesMustApplyForLicensesByFriday
34,376 views
511 Discussing
7
#ICEPartnersWithTradeXYZToBringPerpetualContractsToUS
715 views
19 Discussing
8
#SolidusLabsReportsSuspected$170MSpoofingOnHyperliquidOilContracts
1,706 views
28 Discussing
9
#StanDruckenmillerBecomesInvestorInTradeXYZ
25,841 views
444 Discussing
10
#RussiaProposedNonCustodialWalletLimitsExcludeIntlSettlements
2,212 views
41 Discussing