

#cryptosecurit
cryptosecurit
779 views
24 Discussing
Hot
Latest
·
--
Bullish
🔐 YOUR CRYPTO SECURITY CHECKLIST
Before you trade today:
✅ Enable 2FA
✅ Use a strong unique password
✅ Check website URLs carefully
✅ Never share your seed phrase
✅ Don't click suspicious links
✅ Verify wallet addresses
✅ Be careful with fake support accounts
Remember:
If someone asks for your seed phrase, it's a huge red flag. 🚩
#CryptoSecurit #bitcoin #BinanceSquare #Web3
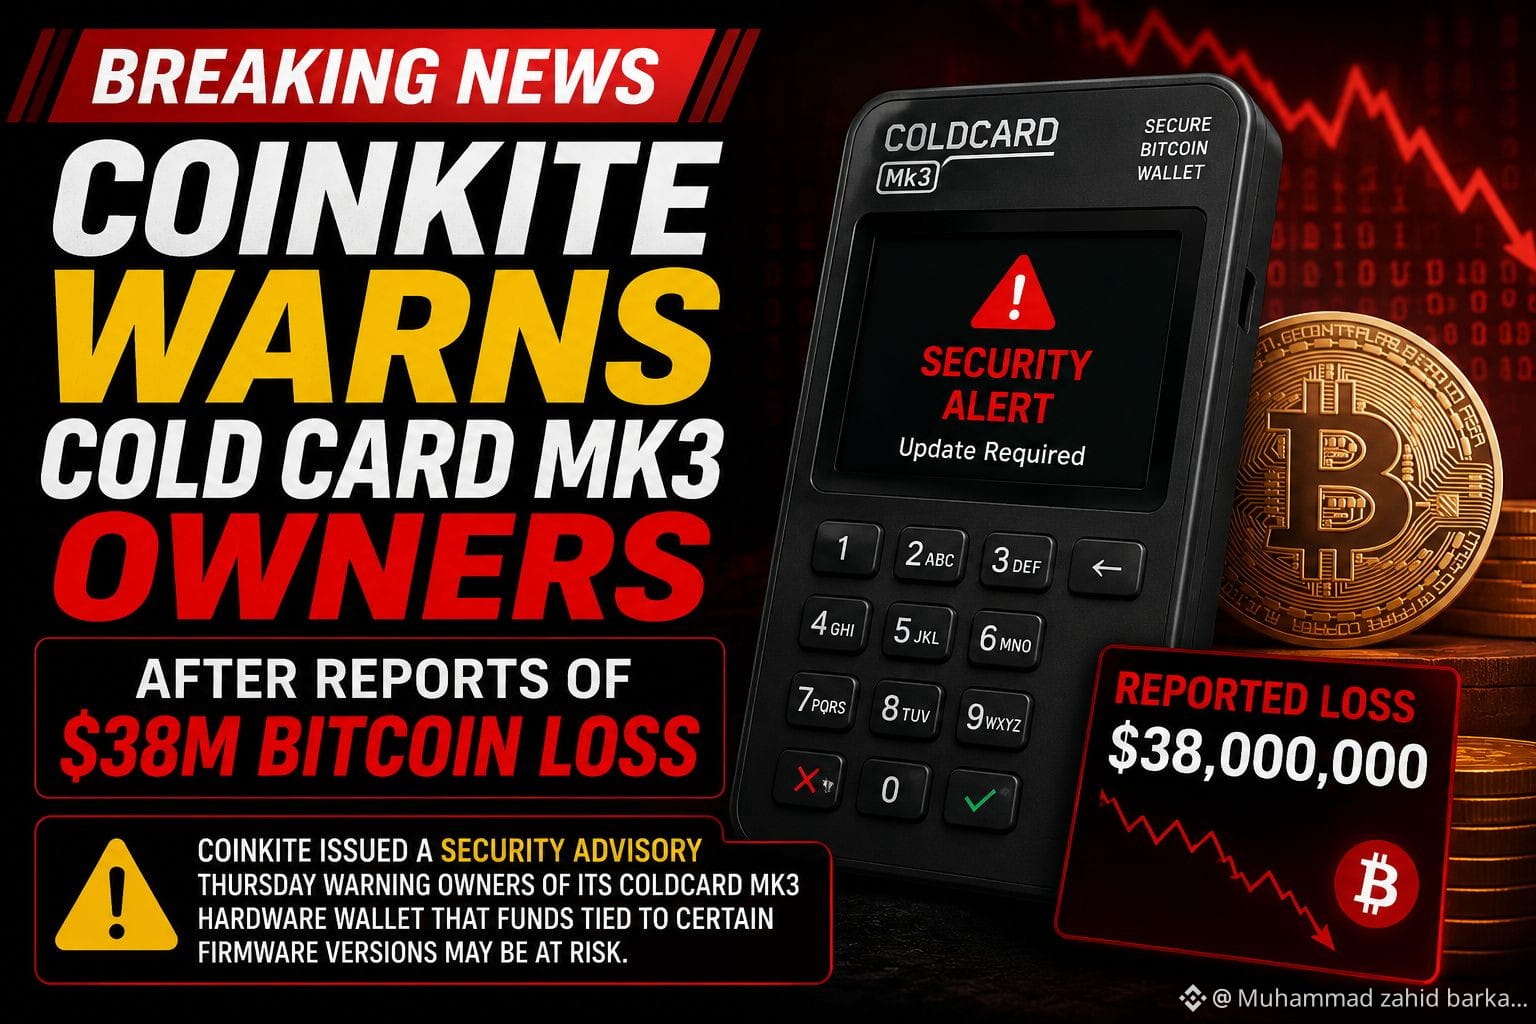
Coinkite Issues Urgent Warning to Coldcard Mk3 Users After $38M Bitcoin Loss
Breaking News!
If you own a Coldcard Mk3 Bitcoin hardware wallet, pay close attention.
Coinkite has issued an urgent security advisory warning that certain firmware versions may put users' Bitcoin funds at risk.
The warning follows reports linked to an estimated $38 million Bitcoin loss, raising serious concerns about wallet security.
If you're using a Coldcard Mk3, check your firmware version immediately, follow Coinkite's official security guidance, and never share your recovery seed phrase with anyone.
This is a reminder that even hardware wallets require regular security updates and careful maintenance.
Follow for more Bitcoin and crypto security news!
Hashtags:
#bitcoinhakving #bitcoin #Coldcard #coinrocco #CryptoSecurit
$NVDAB
{spot}(NVDABUSDT)
$AAPL.US
{stock_us}(AAPL.US)
Coinkite Issues Urgent Warning to Coldcard Mk3 Users After $38M Bitcoin Loss
Breaking News!
If you own a Coldcard Mk3 Bitcoin hardware wallet, pay close attention.
Coinkite has issued an urgent security advisory warning that certain firmware versions may put users' Bitcoin funds at risk.
The warning follows reports linked to an estimated $38 million Bitcoin loss, raising serious concerns about wallet security.
If you're using a Coldcard Mk3, check your firmware version immediately, follow Coinkite's official security guidance, and never share your recovery seed phrase with anyone.
This is a reminder that even hardware wallets require regular security updates and careful maintenance.
Follow for more Bitcoin and crypto security news!
Hashtags:
#bitcoinhakving #bitcoin #Coldcard #coinrocco #CryptoSecurit
$NVDAB
$AAPL.US
99
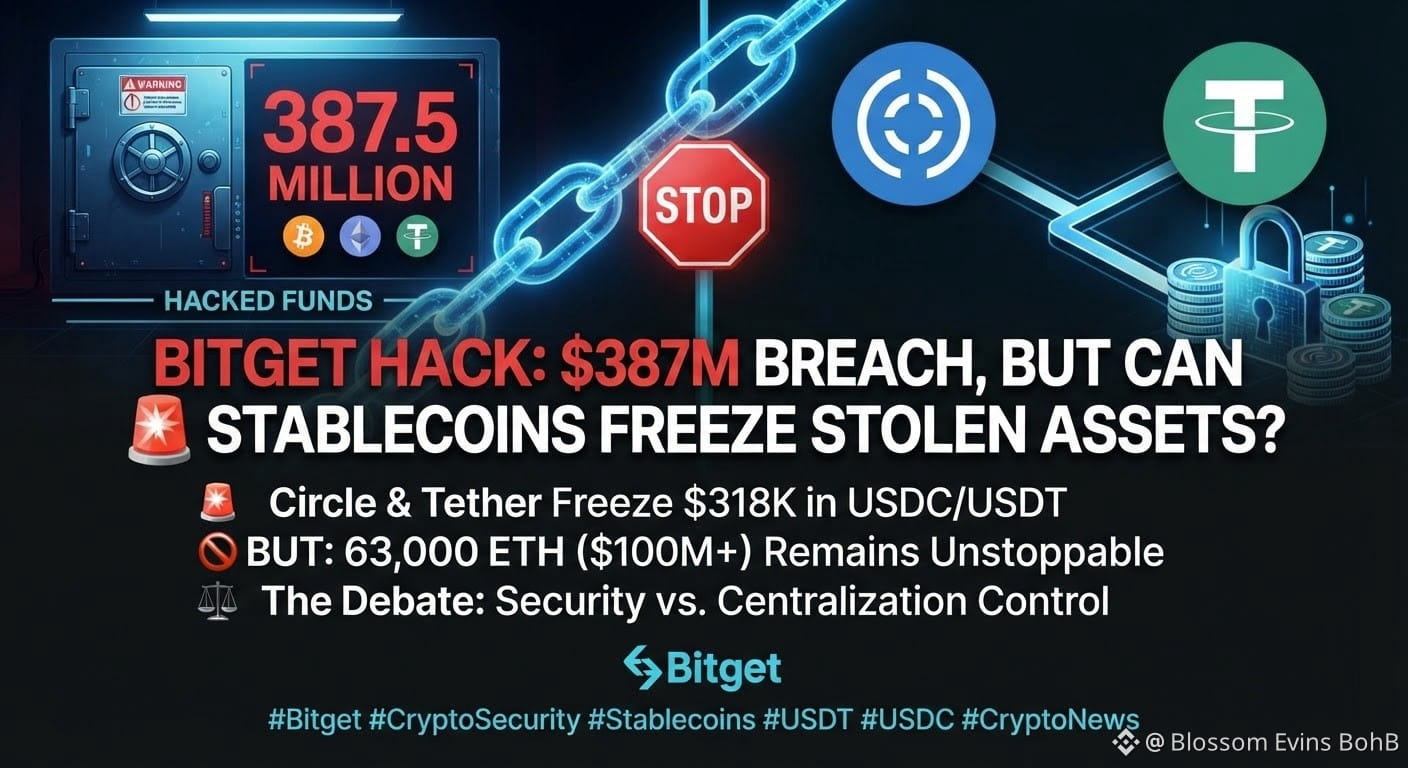
🚨 A $387M HACK — BUT SOME OF THE MONEY COULD ACTUALLY BE FROZEN 👀
The Bitget security breach has raised a bigger question for the crypto market:
How much control do stablecoin issuers really have over stolen funds?
Bitget initially estimated the September 24 incident at around $351.6M, before revising the figure to approximately $387.5M after including additional assets such as Zcash and TRON.
Now here’s where things get interesting. 👇
🔒 Circle and Tether stepped in
A wallet identified as “Bitget Exploiter 8” was blacklisted by Circle, and Tether later blocked the same address.
That wallet reportedly contained around:
• 99,990 USDC
• 218,023 USDT
• 170.47 ETH
So, roughly $318K worth of USDC and USDT was effectively frozen.
But there’s a catch. ⚠️
Circle and Tether can freeze their own tokens at the contract level.
They cannot freeze native ETH.
Reports indicate other exploiter wallets still contained more than 63,000 ETH, showing just how different the control mechanisms are between stablecoins and assets like ETH.
Bitget CEO Gracy Chen said the attackers compromised a backend system connected to the exchange’s wallet infrastructure and manipulated transaction data, rather than taking users’ private keys.
Bitget also said its cold wallets were unaffected and that its User Protection Fund holds over $464M.
👀 The bigger question:
Does this incident show the strength of stablecoin security — or the risks of centralized control?
$BTC • $ETH • $XRP
#CryptoSecurit #Circle #USDC✅ #USDT #CryptoNewss
109
·
--
🚨 5 CRYPTO SCAMS YOU SHOULD KNOW
⚠️ Fake giveaways
⚠️ Fake customer support
⚠️ Phishing websites
⚠️ Fake investment platforms
⚠️ "Send crypto and receive double" scams
If someone promises guaranteed returns, stop.
If someone pressures you to act immediately, stop.
If someone asks for your seed phrase, STOP.
Stay safe. 🔐
#CryptoScams #CryptoSecurit #BinanceSquare
9
·
--
594 BTC stolen in just 25 minutes — How did hackers breach a cold wallet?
The recent headlines reporting 594 BTC stolen within 25 minutes are a stark reminder: "cold wallet" does not mean "invulnerable."
In most security breaches, attackers don't crack the hardware itself—they target human and software vulnerabilities. Common exploits include leaked seed phrases, rogue firmware updates, fake wallet apps, phishing scams, and targeted social engineering. Ultimately, your security is only as strong as how well you guard your private keys.
Despite the shocking news, Bitcoin remains resilient, hovering around $63.4K with modest gains as buyers brush off the negative sentiment. The market's stability proves that isolated security breaches don't alter Bitcoin’s core fundamentals—though they do underline the critical need for strict self-custody habits.
Key takeaways:
- Safeguard your private keys at all costs.
- Always double check and verify every transaction detail.
- Never under any circumstances, reveal your recovery phrase.
#Bitcoin #CryptoSecurit #BTC #SelfCustody #Blockchain $BTC
70
·
--
#kelpdaoexploitfreeze
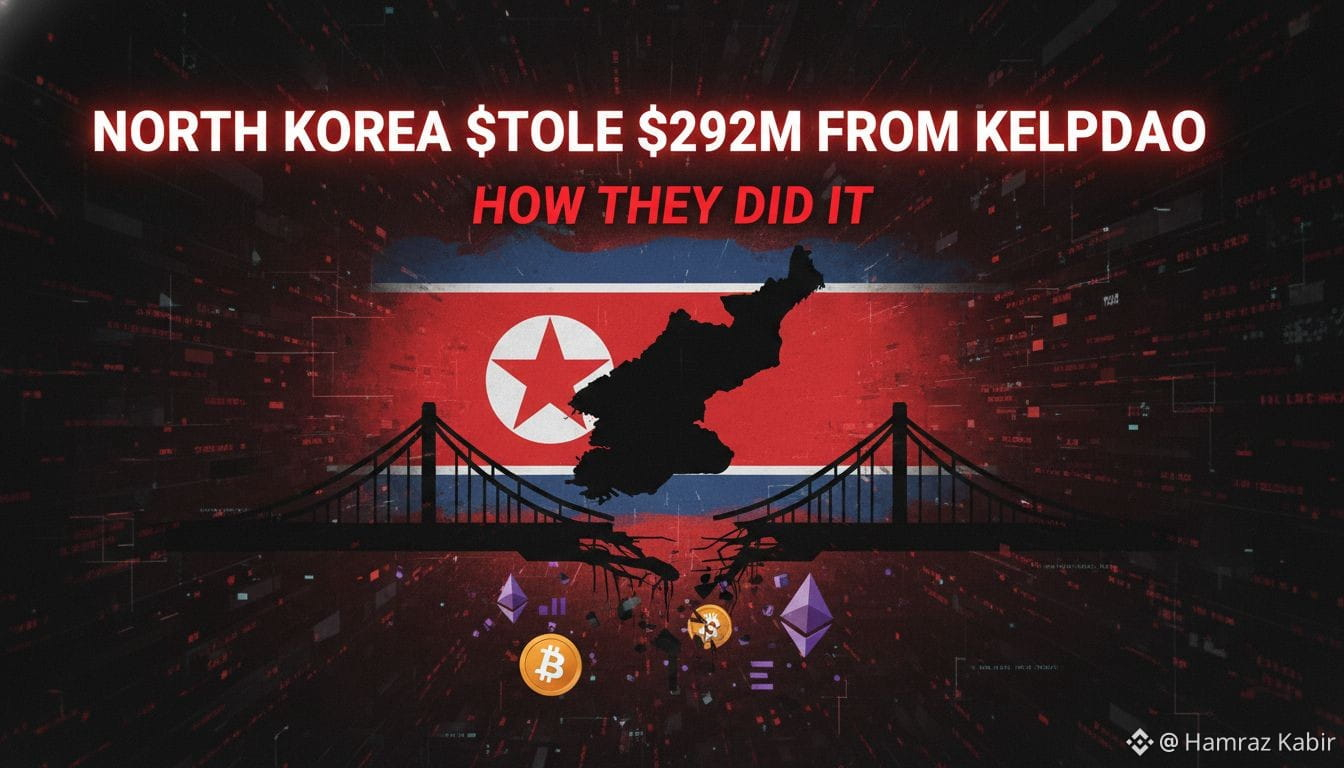
🚨 North Korea Stole $292M from KelpDAO — Here's Exactly How They Did It!
The biggest DeFi hack of 2026 has been linked to North Korea's Lazarus Group — and the attack method was unlike anything we've seen before!
What Happened on April 18, 2026:
Hackers exploited KelpDAO's LayerZero cross-chain bridge — but this was NOT a typical smart contract bug. Every single on-chain transaction looked completely valid!
The Attack Method — Step by Step:
1️⃣ Lazarus Group compromised KelpDAO's internal RPC nodes
2️⃣ DDoS'd external nodes to eliminate any second check
3️⃣ Fed false data to a single-point-of-failure verification system
4️⃣ Tricked the Ethereum contract into releasing 116,500 rsETH
5️⃣ Deposited 90,000 stolen rsETH into Aave as collateral
6️⃣ Borrowed $190M+ in real ETH against worthless collateral
7️⃣ Laundered $176M through THORChain into Bitcoin
The Freeze Response:
On April 20, Arbitrum's Security Council executed an emergency action — freezing 30,766 ETH worth ~$71M tied to the exploiter. This was one of the fastest governance responses in DeFi history!
$ETH $AAVE
The root cause? A "1-of-1" single verifier setup — meaning only ONE validator needed to approve cross-chain messages. No second check. No backup. A single point of failure that North Korea's best hackers exploited perfectly.
Not Financial Advice. DYOR 📊
#DeFiHack #NorthKorea #CryptoSecurit
{spot}(ETHUSDT)
{spot}(AAVEUSDT)
#kelpdaoexploitfreeze
🚨 North Korea Stole $292M from KelpDAO — Here's Exactly How They Did It!
The biggest DeFi hack of 2026 has been linked to North Korea's Lazarus Group — and the attack method was unlike anything we've seen before!
What Happened on April 18, 2026:
Hackers exploited KelpDAO's LayerZero cross-chain bridge — but this was NOT a typical smart contract bug. Every single on-chain transaction looked completely valid!
The Attack Method — Step by Step:
1️⃣ Lazarus Group compromised KelpDAO's internal RPC nodes
2️⃣ DDoS'd external nodes to eliminate any second check
3️⃣ Fed false data to a single-point-of-failure verification system
4️⃣ Tricked the Ethereum contract into releasing 116,500 rsETH
5️⃣ Deposited 90,000 stolen rsETH into Aave as collateral
6️⃣ Borrowed $190M+ in real ETH against worthless collateral
7️⃣ Laundered $176M through THORChain into Bitcoin
The Freeze Response:
On April 20, Arbitrum's Security Council executed an emergency action — freezing 30,766 ETH worth ~$71M tied to the exploiter. This was one of the fastest governance responses in DeFi history!
$ETH $AAVE
The root cause? A "1-of-1" single verifier setup — meaning only ONE validator needed to approve cross-chain messages. No second check. No backup. A single point of failure that North Korea's best hackers exploited perfectly.
Not Financial Advice. DYOR 📊
#DeFiHack #NorthKorea #CryptoSecurit
170
·
--
🔐 How to Keep Your Crypto Safe: A Simple Guide for New Users
Security should always come before profits. Start with a strong, unique password and enable 2FA on every crypto account. Never share your recovery phrase, private keys, or OTPs with anyone. Double-check website URLs, avoid suspicious links and messages, and stay alert to phishing scams pretending to be trusted platforms.
Before investing, take time to learn. A few minutes of caution can protect years of savings.
Stay secure. Stay informed. Always DYOR. 🛡️
#IndiaCreatesOnSquare #CryptoSecurit #BinanceSquare #DYOR
65
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#DriftHackVictimsBeginClaims
6,034 views
120 Discussing
2
#SolanaTokenizedStockVolumeTops$4.4BInSeptember
1,385 views
17 Discussing
3
#BitcoinSpotETFsDraw$6.34BInflowsInQ3
9,143 views
130 Discussing
4
#EthereumValidatorExitQueueJumps392%
172,869 views
1,316 Discussing
5
#IMFApprovesElSalvador$138MWithBitcoinWaiver
16,117 views
81 Discussing
6
#SECHaltsCryptoETFReviewsAmidFundingLapse
306,347 views
2,116 Discussing
7
#ZcashETFPostsFirstWeeklyOutflow$93.6M
101,846 views
266 Discussing
8
#GreekPoliceBustCryptoScamRingArrest17
422,471 views
2,711 Discussing
9
#BitcoinRejectedAt$87K
235,290 views
334 Discussing
10
#FedOctoberRateHikeOddsFallTo17%
438,008 views
2,825 Discussing