

#lazarus
lazarus
446,624 views
115 Discussing
Hot
Latest

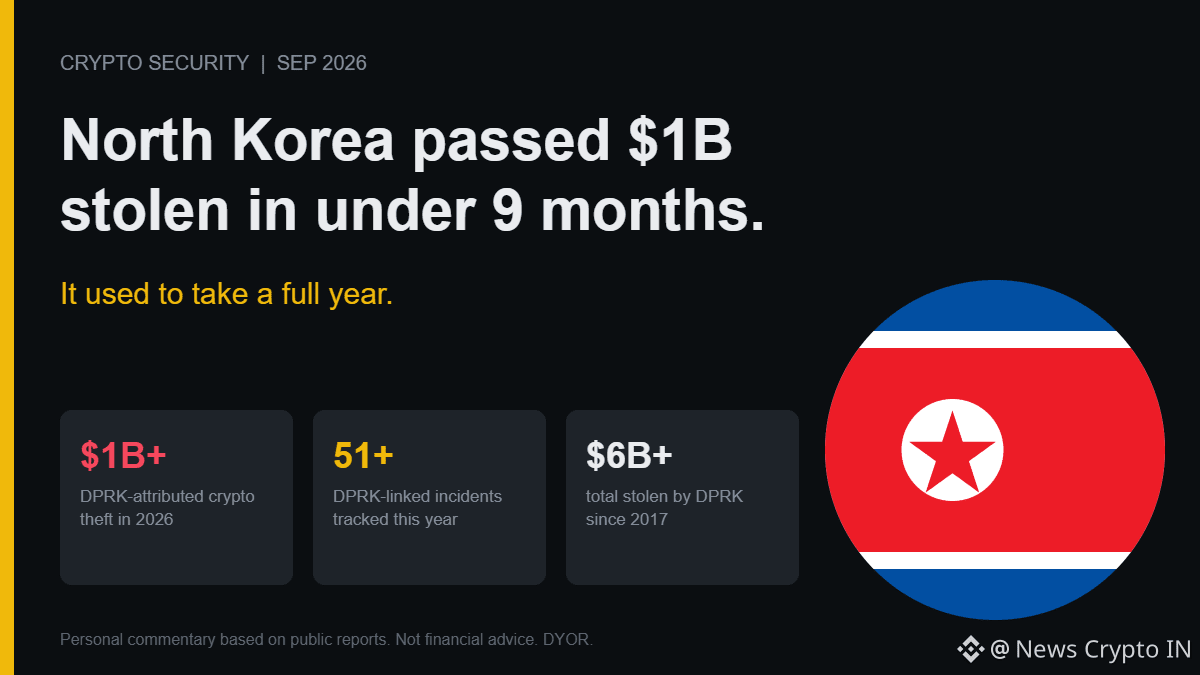
North Korea just crossed $1 billion in crypto theft for 2026, and did it in under 9 months. Last year that milestone took a full 12.
The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes.
The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access.
Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence.
At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis?
#Lazarus #CryptoSecurity
1
1.3k

·
--
📰 On September 24, abnormal transfers occurred involving some of Bitget’s hot wallets and warm wallets. The platform initially disclosed losses of about $351.6 million, and later confirmed that the amount of assets that were transferred had been adjusted to $387.5 million.
🔥 TRM Labs found that the laundering path of the partially stolen funds overlaps with previous North Korea–linked attacks such as those involving Bybit and AFX Bridge. Elliptic also believes there is a “highly likely” connection between this incident and North Korean hackers, and the investigation focus points again toward the Lazarus Group.
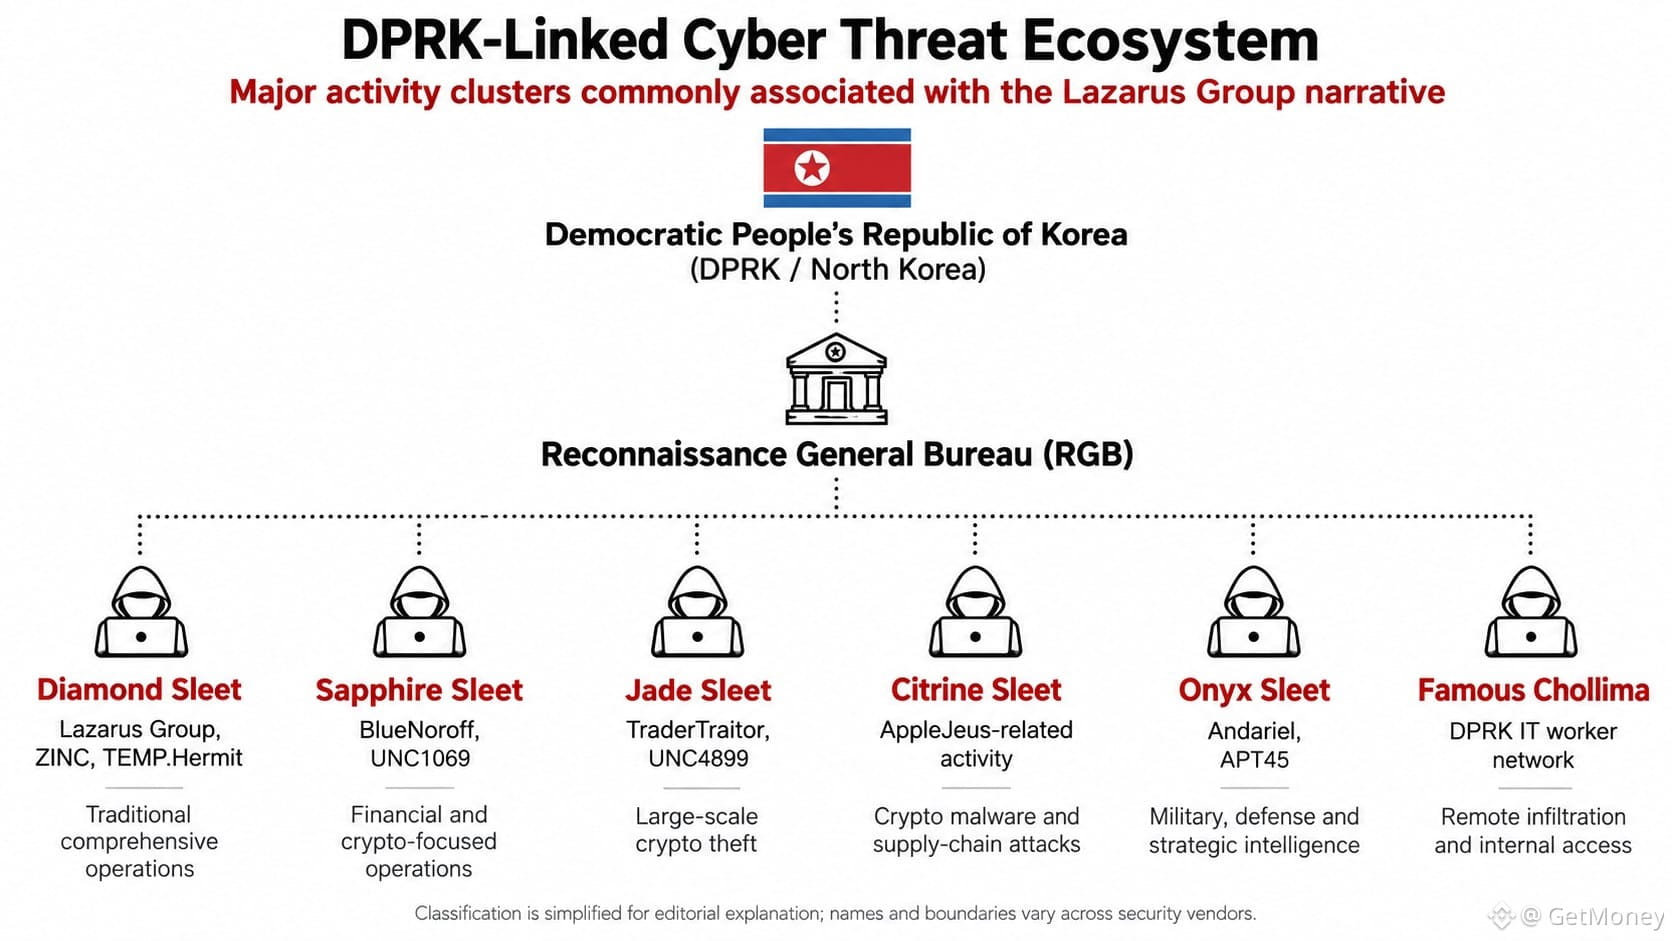
Honestly, Lazarus doesn’t really look like a single organization with clear boundaries—it’s more like an umbrella term used externally for North Korea’s state-level cyberattack apparatus. In 2019, the U.S. Treasury named Lazarus, BlueNoroff, and Andariel, saying they are all under the control of North Korea’s Reconnaissance General Bureau (RGB).
💡 In this ecosystem, different entities use different names: BlueNoroff has long targeted financial institutions and crypto assets; TraderTraitor focuses on exchanges, custodians, and large crypto targets; Citrine Sleet leans toward malware and supply-chain attacks; and Famous Chollima infiltrates technology and crypto companies through fake identities.
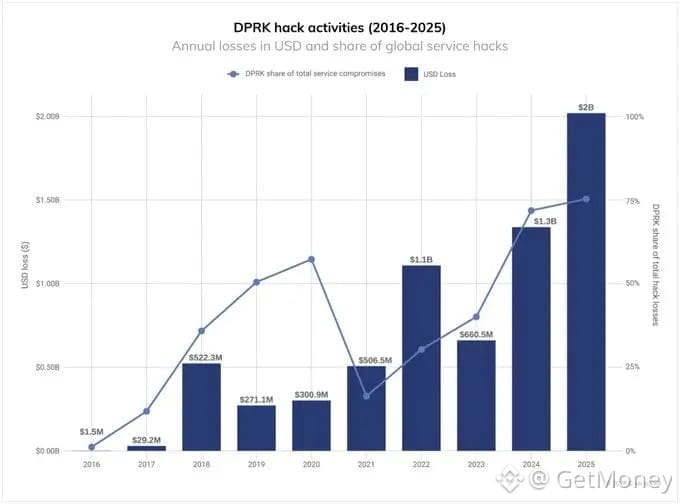
👀 From Ronin Bridge, Harmony, Atomic Wallet, to Stake, WazirX, DMM Bitcoin, and then the Bybit incident in 2025—if we also include the Bitget case, which is currently highly suspected to be carried out by North Korea—the scale of related theft is already close to $7.8 billion. This figure is no longer just a security incident for a single platform.
🤔 When the same attack framework keeps changing names and entry points, how can exchanges and project teams ultimately determine which group they’re really dealing with?
#Lazarus #Bitget #加密安全 #On-chain security
18
·
--
🎯 The biggest crypto heist this year—allegedly the protagonist is North Korea
📰 Bitget was siphoned off $388 million, and the CEO directly points to the Lazarus Group; XRP was moved for $157 million, and the exchange temporarily suspended withdrawals
💬 The methods aren’t anything new, but the amounts are maxed out. Centralized exchanges are always the weak link—no matter how fast the money moves on-chain, once the entry point is compromised, it’s all for nothing. Don’t just treat self-custody as a slogan.
🏷️ #Bitget #Lazarus #安全事件 #self-custody
235
·
--
Bullish
$BTC $ETH
🚨 FLASH HACK : What really happened at Bitget? 🚨
A major security incident has rocked the crypto ecosystem. Here’s the full rundown on the situation 🧵👇
💥 The Attack, in Brief
On September 24, 2026, Bitget suffered a vulnerability in its backend infrastructure. The attackers forged internal system permissions to approve fraudulent transfers and drain the hot wallets.
💰 Loss Amount: ~387.5 million $
Major cryptocurrencies were diverted across multiple blockchains: ETH, XRP, USDT, TRX, AVAX, BNB, and ZEC.
🛡️ What’s the impact on users?
• ❄️ Cold Wallets: 100% secured (the cold wallets were not affected).
• 👤 Client balances: No direct impact on your accounts.
• 🛡️ Protection Funds: The Bitget guarantee fund (estimated at over $460M) will cover the entirety of the losses.
🕵️ Who’s behind the hack?
According to CEO Gracy Chen, the IP addresses and the modus operandi point to North Korean hackers (the Lazarus group). Cybersecurity giants Mandiant and SlowMist are working on the case.
🗓️ Withdrawal Recovery Timeline:
✅ Vulnerability fixed & trading operational
📌 Sept. 28: BTC withdrawals
📌 Sept. 29: ETH withdrawals (Ethereum, BSC, Arbitrum, Base, OP)
📌 Sept. 30: USDT withdrawals (Ethereum, BSC, Solana, Tron)
📌 Oct. 2: Other altcoins, fiat, and P2P
Stay cautious and always verify your sources officially! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
{spot}(BTCUSDT)
{spot}(ETHUSDT)
$BTC $ETH
🚨 FLASH HACK : What really happened at Bitget? 🚨
A major security incident has rocked the crypto ecosystem. Here’s the full rundown on the situation 🧵👇
💥 The Attack, in Brief
On September 24, 2026, Bitget suffered a vulnerability in its backend infrastructure. The attackers forged internal system permissions to approve fraudulent transfers and drain the hot wallets.
💰 Loss Amount: ~387.5 million $
Major cryptocurrencies were diverted across multiple blockchains: ETH, XRP, USDT, TRX, AVAX, BNB, and ZEC.
🛡️ What’s the impact on users?
• ❄️ Cold Wallets: 100% secured (the cold wallets were not affected).
• 👤 Client balances: No direct impact on your accounts.
• 🛡️ Protection Funds: The Bitget guarantee fund (estimated at over $460M) will cover the entirety of the losses.
🕵️ Who’s behind the hack?
According to CEO Gracy Chen, the IP addresses and the modus operandi point to North Korean hackers (the Lazarus group). Cybersecurity giants Mandiant and SlowMist are working on the case.
🗓️ Withdrawal Recovery Timeline:
✅ Vulnerability fixed & trading operational
📌 Sept. 28: BTC withdrawals
📌 Sept. 29: ETH withdrawals (Ethereum, BSC, Arbitrum, Base, OP)
📌 Sept. 30: USDT withdrawals (Ethereum, BSC, Solana, Tron)
📌 Oct. 2: Other altcoins, fiat, and P2P
Stay cautious and always verify your sources officially! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
172

🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
28

·
--
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
5
85
💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
3
637
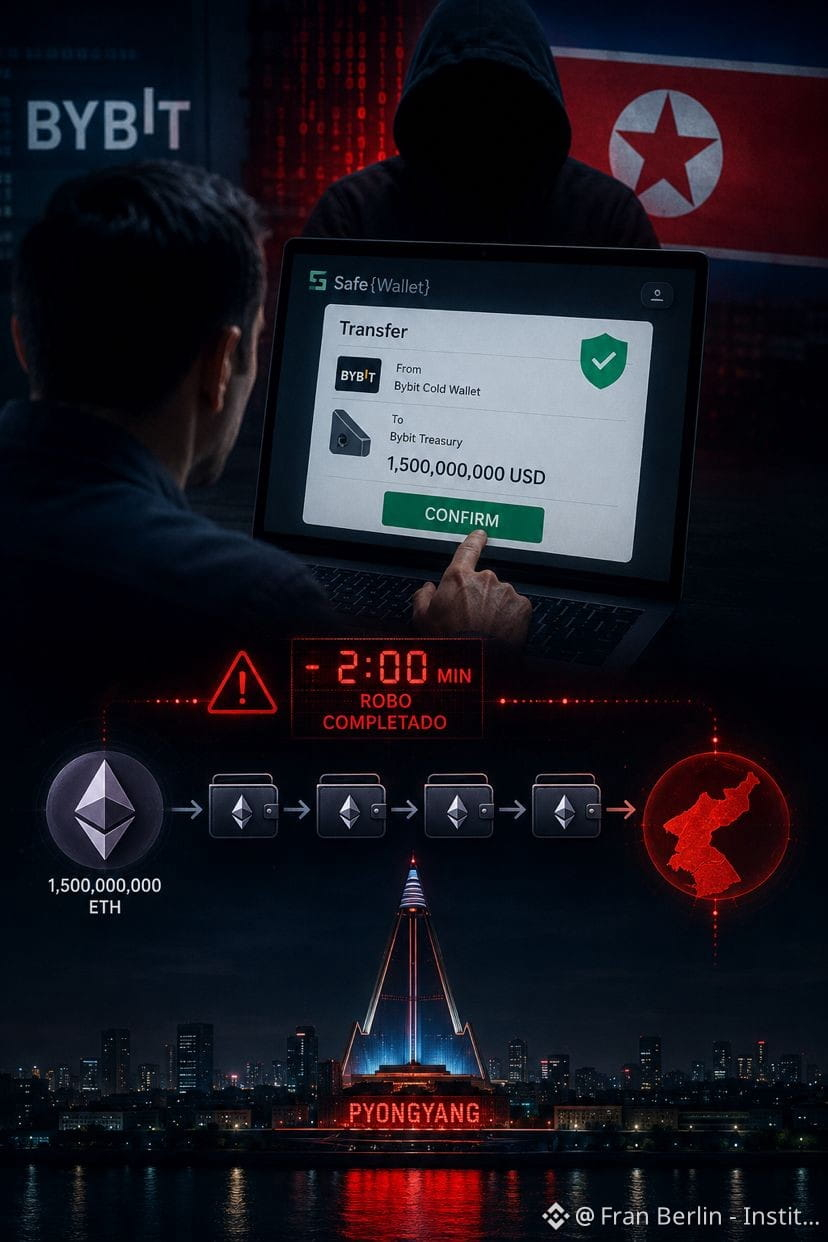
It was a routine transfer.
February 20, 2025. A Bybit employee opens his screen, checks the transaction details, and signs.
Everything looks normal.
Minutes later, $1.5 billion $USDT in Ethereum had vanished.
But the most terrifying part isn’t the amount.
The most terrifying part is how they did it.
The elite North Korean government hackers of the Lazarus Group didn’t attack the blockchain. They didn’t break any private keys. They didn’t need any of that.
They simply… falsified what the employee saw on the screen.
Months earlier, they infiltrated the system of a Safe Wallet developer—the platform Bybit used to sign transactions. They injected a malicious code that slept quietly, waiting.
When the employee opened his wallet that day, the code activated. The screen showed a legitimate transfer. In reality, the funds were going to Pyongyang.
The employee signed. His coworkers signed. Nobody saw anything unusual.
Two minutes after the theft, the malicious code deleted itself. No trace.
It took the FBI days to confirm what everyone already suspected: it was North Korea, using stolen Ethereum to fund its nuclear weapons program.
The lesson nobody wants to hear: the weakest link isn’t the code. It’s you.
Do you trust the screen you see when you sign a transaction?
Fran Berlin | Blockchain Institute
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
{spot}(ETHUSDT)
{spot}(USDCUSDT)
It was a routine transfer.
February 20, 2025. A Bybit employee opens his screen, checks the transaction details, and signs.
Everything looks normal.
Minutes later, $1.5 billion $USDT in Ethereum had vanished.
But the most terrifying part isn’t the amount.
The most terrifying part is how they did it.
The elite North Korean government hackers of the Lazarus Group didn’t attack the blockchain. They didn’t break any private keys. They didn’t need any of that.
They simply… falsified what the employee saw on the screen.
Months earlier, they infiltrated the system of a Safe Wallet developer—the platform Bybit used to sign transactions. They injected a malicious code that slept quietly, waiting.
When the employee opened his wallet that day, the code activated. The screen showed a legitimate transfer. In reality, the funds were going to Pyongyang.
The employee signed. His coworkers signed. Nobody saw anything unusual.
Two minutes after the theft, the malicious code deleted itself. No trace.
It took the FBI days to confirm what everyone already suspected: it was North Korea, using stolen Ethereum to fund its nuclear weapons program.
The lesson nobody wants to hear: the weakest link isn’t the code. It’s you.
Do you trust the screen you see when you sign a transaction?
Fran Berlin | Blockchain Institute
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
654


·
--
Bearish
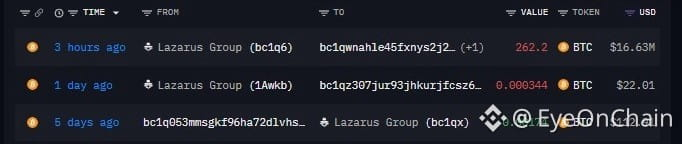
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
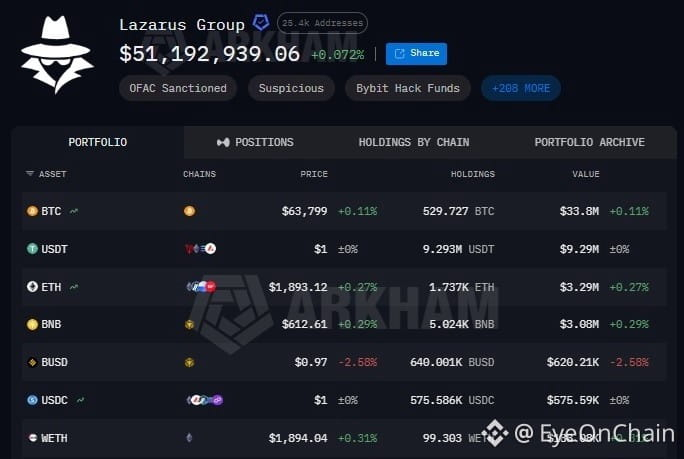
The group still has more than $73M in assets on-chain, mainly held in $BTC, $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
{future}(BTCUSDT)
{spot}(BTCUSDT)
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
1
1.3k


·
--
📰 BlockBeats Daily Report 2026-08-15 | 2 articles in total
1. Security firm ANY.RUN created a fake DeFi project, successfully infiltrated the Famous Chollima agents under North Korea’s Lazarus Group, and exposed its complete toolchain and social engineering attack workflow.
2. TMT Breakout estimates that SanDisk CY2030 EPS could approach $700, relying on NAND’s high profit margin and ongoing share buybacks of about $1,500 per share; HBF mass production may ramp up in 2028.
Keywords:$BTC $ETH $SOL #BlockBeats #Web3 #Lazarus #NAND
184

🚨 $BTC WALLET MOVE JUST ECHOED THE 2024 LAUNDERING PLAYBOOK 💥
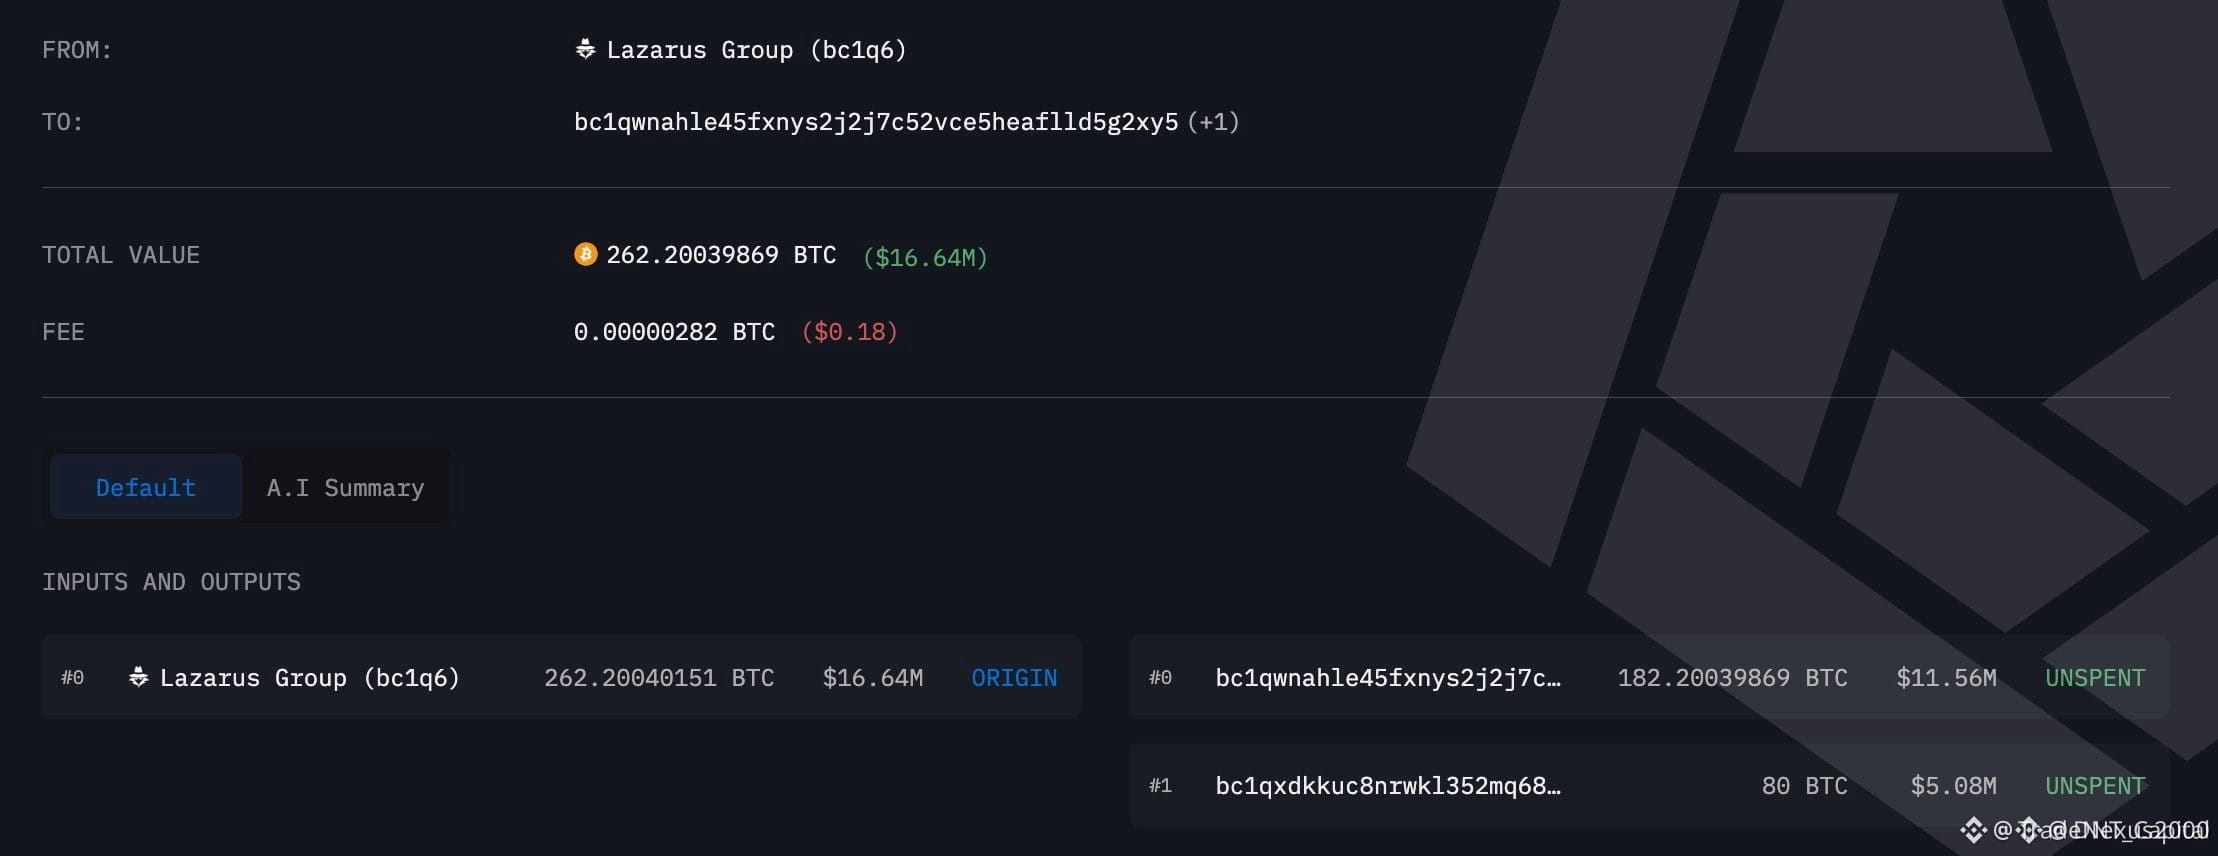
262.2 BTC just crossed wallets in 2 hours — same fingerprint as the group's darkest exchanges. Not a transaction. It's a signal. Whether they bridge, swap, or mix tells us if sell pressure is imminent. 🔍
Over $73M still parked across $BTC , $USDT and $ETH . Until that liquidity touches a top-tier exchange, we're watching a shadow play. 📊 No confirmed sale — but the market has a long memory for these wallets. 💡
💬 If those funds move to an exchange — how quickly do you think market makers would shadow that liquidity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #OnChain #Lazarus #CryptoAnalysis
🦈 👁️
21
·
--
█▓▒▒░░░THE BITGET HACK: The ONE Detail Everyone Is Missing (And Why It Changes Crypto Security Forever)░░░▒▒▓█
Most people looking at the $351.6M Bitget exploit are asking the wrong questions. They are tracking the Lazarus Group, looking at the $464M Protection Fund, or worrying about an ETH sell-off.
But here is what nobody is talking about, and it should terrify every crypto holder.
The Lie: "They stole the private keys."
The Reality: The keys were completely untouched.
Bitget CEO Gracy Chen confirmed the hackers bypassed key management entirely. Instead, they breached a internal wallet backend system. They fed fake, spoofed transaction data directly into the exchange's automated system.
Think about what this means: The exchange's own system willingly authorized the theft, thinking it was just a routine payout.
This marks a massive structural shift in crypto crime. Hackers are no longer wasting time trying to brute-force multisig keys or find smart contract bugs. They are using backend data spoofing to make the defense infrastructure work for them.
The Bottom Line:
Your funds on Bitget are covered by the protection fund. But if the industry's most advanced automated approval systems can be tricked into giving away $350M+ over dinner, no centralized automated hot wallet layer is truly safe right now.
The era of "safe because of multisig keys" is dead. Infrastructure security is the new battleground.
Are you keeping your capital on CEXs right now, or migrating to hard-walled cold storage? 👇
#Bitget $BTC
{future}(BTCUSDT)
#CryptoSecurity #Lazarus #Web3 #BinanceSquare
█▓▒▒░░░THE BITGET HACK: The ONE Detail Everyone Is Missing (And Why It Changes Crypto Security Forever)░░░▒▒▓█
Most people looking at the $351.6M Bitget exploit are asking the wrong questions. They are tracking the Lazarus Group, looking at the $464M Protection Fund, or worrying about an ETH sell-off.
But here is what nobody is talking about, and it should terrify every crypto holder.
The Lie: "They stole the private keys."
The Reality: The keys were completely untouched.
Bitget CEO Gracy Chen confirmed the hackers bypassed key management entirely. Instead, they breached a internal wallet backend system. They fed fake, spoofed transaction data directly into the exchange's automated system.
Think about what this means: The exchange's own system willingly authorized the theft, thinking it was just a routine payout.
This marks a massive structural shift in crypto crime. Hackers are no longer wasting time trying to brute-force multisig keys or find smart contract bugs. They are using backend data spoofing to make the defense infrastructure work for them.
The Bottom Line:
Your funds on Bitget are covered by the protection fund. But if the industry's most advanced automated approval systems can be tricked into giving away $350M+ over dinner, no centralized automated hot wallet layer is truly safe right now.
The era of "safe because of multisig keys" is dead. Infrastructure security is the new battleground.
Are you keeping your capital on CEXs right now, or migrating to hard-walled cold storage? 👇
#Bitget $BTC
#CryptoSecurity #Lazarus #Web3 #BinanceSquare
71
·
--
0926 Diary · A person straddling Crypto and the US stock market
Today’s market is quieter than the news; the news is more vicious than the market.
The amount stolen from Bitget has been revised upward for the third time: $351.6 million → $387.5 million. On-chain attribution points to Lazarus/TraderTraitor, and Tether has frozen the related addresses. The cold wallets are unharmed, and a $464 million protection fund is standing by—but “excluding a private key leak” is still only an initial conclusion. Don’t jump to conclusions until the full report comes out. I also went ahead and revoked all historical authorizations on the old wallets: 3,832 NFTs on Magic Eden are simply gone. Remember: canceling an order ≠ revoking authorization.
Over on the AI side, things are increasingly about repairing infrastructure rather than showing off models. Docker packages all Agent permissions into a standard OCI image (Sandbox Kit v3). Google open-sources AX, positioning it as “Kubernetes for Agents.” And in the community, people have also wrapped Claude Code / Codex / Cursor into a unified persistent GUI (Zuse). One sentence: it’s not hard to get agents running; the hard parts are permissions, environments, orchestration, and who manages costs. Oh, and Opus 5.5 has already enabled Microduck to design 1,113 real LEGO parts and a 141-page building manual—AI is moving from “can draw” to “can deliver.”
AI in US stocks is still charging: META has surged to 777, setting an all-time high, with market cap nearing $2 trillion. But @web3annie reminds everyone that AMD and TSM have already shown top-side divergence, and AVGO is pulling back by 40%. The risk of a false breakout in semiconductors needs to be watched closely. Circle (CRCL) co-founder resigns as a director; the CFO resigns the same day, and the stock fell sharply after hours.
In reality, the two lines point in the same direction: extreme optimism—paired with a world you must personally backstop. You can ride the momentum in the market, but risk is something you have to keep for yourself.
$BTC #Openclaw #Bitget #DeFi #AI #Lazarus
266
🚨 BITGET SUFFERS A $351.6 MILLION HACK: IS Lazarus BEHIND IT? 🇰🇵💰
One of the biggest security blows in the crypto sector in 2026. The platform confirmed that approximately $351.6 million in assets were affected after unauthorized transfers from part of its hot wallets and intermediate wallets.
👀 Who would be behind it?
Bitget CEO Gracy Chen said that initial analyses show patterns consistent with attacks linked to North Korean hacker groups.
Among the hypotheses is Lazarus, known for being associated with large cryptocurrency thefts, although attribution is still under investigation.
🔓 And there’s an even more striking detail: according to Chen, the private keys were not compromised. The attackers would have gained access to a backend system related to the wallet infrastructure, manipulated transaction information, and caused the authorization process itself to execute the transfers.
🛑 Bitget temporarily suspended withdrawals while investigating the attack, although deposits and other operations continued to work. The company also claims that its cold wallets remained secure and that its User Protection Fund exceeds $464 million—an amount greater than the impacted sum.
⚠️ And here comes another debate: Hapi.
Hapi’s current documents specify that the cryptocurrencies handled through its services are not insured by the FDIC and are not protected by the SIPC.
SIPC protection of up to $500,000 relates to certain assets and cash in the brokerage account—not to cryptocurrencies.
This leaves a question on the table for anyone who holds Bitcoin on a centralized platform:
What really happens to your $BTC if the platform suffers a hack and the crypto funds are stolen? 🔐₿
EASY ➡️ REMEMBER TO HAVE YOUR COLD WALLET :)
#Bitget #Lazarus #crypto #HackerAlert #CyberSecurity
241
·
--
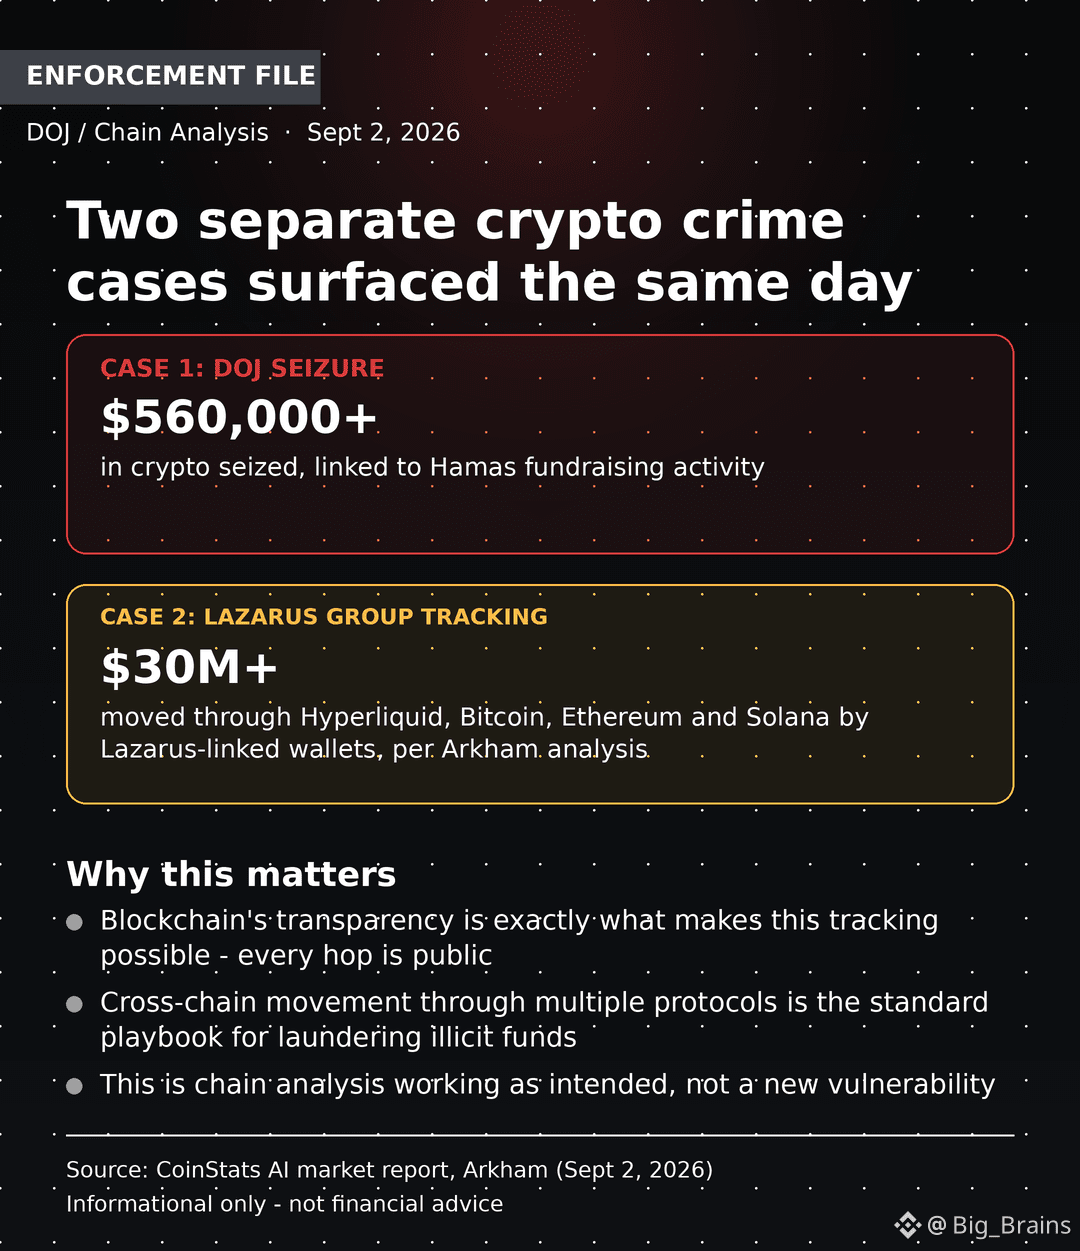
DOJ/Lazarus enforcement (case-file style) — Informational
Two crypto crime cases same day: $560K+ seized (Hamas-linked), $30M+ tracked moving through Hyperliquid/BTC/ETH/SOL (Lazarus Group). Blockchain transparency is exactly what made both traceable.
#CryptoSecurity #Lazarus #ChainAnalysis #BinanceSquare #crptonews
Two crypto crime cases same day: $560K+ seized (Hamas-linked), $30M+ tracked moving through Hyperliquid/BTC/ETH/SOL (Lazarus Group). Blockchain transparency is exactly what made both traceable.
#CryptoSecurity #Lazarus #ChainAnalysis #BinanceSquare #crptonews
63
·
--
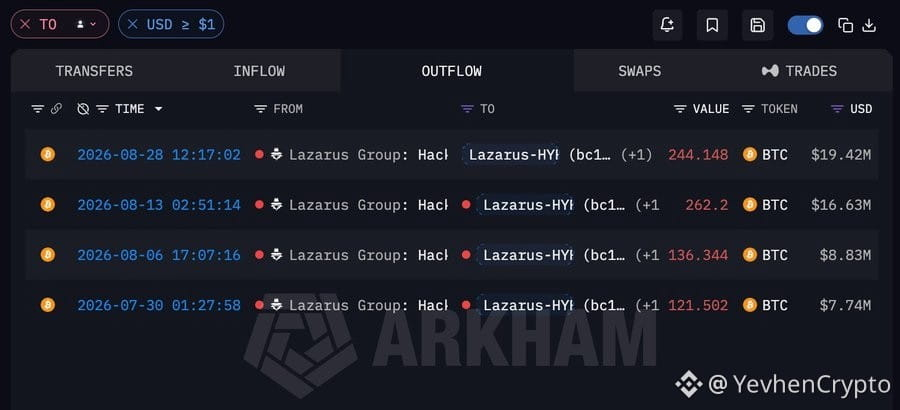
🚨 Lazarus is back in focus, over $30M may be routed through Hyperliquid
The North Korean Lazarus Group has once again drawn the attention of on-chain analysts.
According to researchers, addresses linked to Lazarus are moving $30M+ through Hyperliquid infrastructure
🔍 What the money route looks like:
➡️ BTC flows into HyperUnit
➡️ BTC is converted into ETH and SOL
➡️ assets are moved via bridges across Ethereum, Solana, and Tron
➡️ some of the funds ultimately end up on centralized exchanges and other services
What’s interesting is that some of the addresses have already appeared in previous investigations related to crypto asset theft.
🧩 What does this mean for the market?
This does not mean that Hyperliquid is "laundering" funds or that the protocol is directly involved in the crimes.
💬 Do you think DeFi can maintain its openness while also blocking similar schemes?
#Crypto #Hyperliquid #DeFi #Lazarus #Ethereum
1
288
🚨 LAZARUS GROUP SHUFFLES $30M STOLEN FUNDS VIA $HYPE AS ON-CHAIN RADARS TRIGGER 🦈
On-chain traces just caught the Lazarus Group funneling over $30 million through Hyperliquid rails. 🔍 These specific sanctioned addresses were flagged by ZachXBT after routing $61 million in exploited capital, showing institutional-scale laundering mechanics in real time. 📊
When bad actors push multi-million dollar flows across decentralized venues, it creates localized liquidity distortion and heightened compliance scrutiny across bridged assets. 🛡️ Smart money watches these capital routes closely before sizing into adjacent setups. 💬 Are you adjusting your order book strategies while these rogue funds circulate? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HYPE #OnChain #CryptoSecurity #Lazarus #DeFi
🔍 ⚡
75

·
--
🦈 $ETH TOP-TIER EXCHANGE SUES NORTH KOREA FOR $1.5B HACK – LAZARUS ASSETS FROZEN ⚖️
📊 A U.S. federal judge just slammed a preliminary injunction on unidentified wallets tied to the largest crypto heist in history — turning the Lazarus Group’s stolen $1.5B into a frozen liability instead of dry powder. 🔍
🛡️ Smart money reads this as sovereign-grade legal pressure targeting the laundering pipeline, not just the exploit. This isn’t a PR move — it’s a structural attempt to claw back liquidity that was violently extracted from the ecosystem. 🌊
💬 Could this freeze push $ETH sell pressure through alternative rails, or will trapped funds simply shadow the market until trial? Where do you see the real impact? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Lazarus #CryptoNews #Institutional #SmartMoney
🔒 🦈
35
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#EtherGains70.9%InQ3
61,860 views
716 Discussing
2
#TreasuryLetsStatesFileStablecoinCertificationsEarly
2,588 views
33 Discussing
3
#US10YearYieldNears5.3%
93,824 views
864 Discussing
4
#DollarIndexHitsHighestSinceMay2025
18,970 views
440 Discussing
5
#USWeeklyJoblessClaimsFallTo197000
20,769 views
387 Discussing
6
#BitcoinETFsTake$6.34BillionInQ3
6,923 views
57 Discussing
7
#KoreaProposesTokenizingStocksAndBonds
53,227 views
715 Discussing
8
#MetaMaskExitsLidoValidatorsAfterSecurityIncident
147,430 views
1,424 Discussing
9
#MicronBeatsEarningsLiftsGuidance
73,994 views
1,029 Discussing
10
#CFTCSubmitsTwoEventContractRulesToWhiteHouse
50,340 views
775 Discussing