

#seguridad
seguridad
409,644 views
566 Discussing
Hot
Latest
If you have money on Binance, read this before opening any message.
There was a security incident today, and withdrawals are paused. You already know that.
What comes next is what can really cost you: the wave of scams.
In the coming hours, you’ll get emails about “urgent verification,” links to “protect your funds,” and people messaging you on Telegram or WhatsApp claiming to be support.
None of them are real.
Three rules, no exceptions:
Support will never ask for your password, your 2FA code, or your seed phrase. No one. Ever.
Don’t use links. Open the app or type in the address yourself.
If a message rushes you, it’s a scam. Urgency is the tool, not a minor detail.
The hack cost Binance. Tomorrow’s scams will cost users who haven’t lost anything today.
Stay safe, and look out for anyone just getting started.
#Binance #Seguridad #Web3
58
·
--
If you have money on Binance, read this before opening any message.
There was a security incident today, and withdrawals are paused. You already know that.
What comes next is what can really cost you: the wave of scams.
In the coming hours, you’ll get emails about “urgent verification,” links to “protect your funds,” and people messaging you on Telegram or WhatsApp claiming to be support.
None of them are real.
Three rules, no exceptions:
Support will never ask for your password, your 2FA code, or your seed phrase. No one. Ever.
Don’t use links. Open the app or type in the address yourself.
If a message rushes you, it’s a scam. Urgency is the tool, not a minor detail.
The hack cost Binance. Tomorrow’s scams will cost users who haven’t lost anything today.
Stay safe, and look out for anyone just getting started.
#Binance #Seguridad #Web3
Feed-Creator-246831f75 halima noori:
TRwpYKYhogQsLJZvDDHpR5mc2rLETr1sNE
For help
24
21
319
217k

·
--
Article
Binance confirms hack and theft of more than 6.3 billion dollarsThe exchange suspended withdrawals after the incident, although it assures users that their funds are safe.
The bitcoin (BTC) and cryptocurrency exchange was the victim of a security incident that resulted in the unauthorized theft of funds worth an estimated 6.3 billion dollars.
According to the preliminary investigation reported by the company through its official channels, the attack may have been possible because a DevOps engineer’s laptop was compromised. This unauthorized access allowed the attackers to enter a service container and execute withdrawal transactions without the required authorization.
Binance confirms hack and theft of more than 6.3 billion dollars
The exchange suspended withdrawals after the incident, although it assures users that their funds are safe.
The bitcoin (BTC) and cryptocurrency exchange was the victim of a security incident that resulted in the unauthorized theft of funds worth an estimated 6.3 billion dollars.
According to the preliminary investigation reported by the company through its official channels, the attack may have been possible because a DevOps engineer’s laptop was compromised. This unauthorized access allowed the attackers to enter a service container and execute withdrawal transactions without the required authorization.
132

·
--
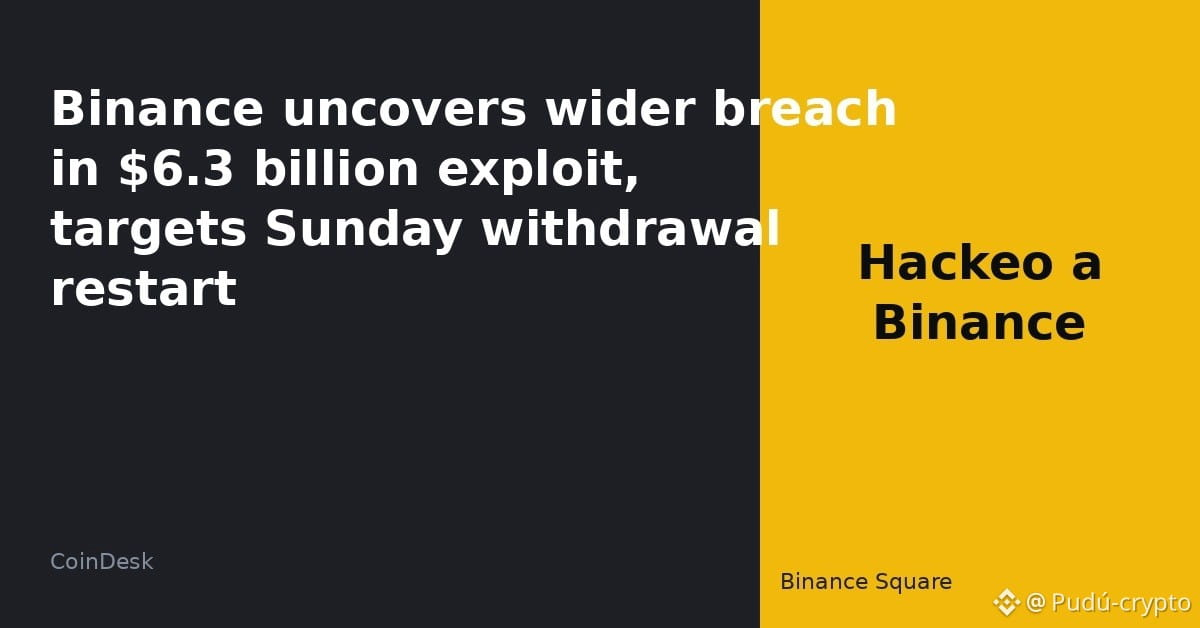
The $6.3 billion hack runs deeper than expected.
Richard Teng confirmed that those responsible erased evidence and managed to bypass security checks.
The platform is trying to resume withdrawals this Sunday.
On Monday, they will publish the proof of reserves in an attempt to calm things down.
It’s quite a complicated situation to follow.
What do you think of the exchange’s response?
$BNB $BTC
#Binance #Security
33
·
--
How do hacks affect cryptocurrencies? ⚠️📉
It’s common to see the market react immediately when a major hack occurs in the crypto ecosystem. Why does this happen?
•Temporary panic: The news causes fear, and many investors decide to sell quickly as a precaution, causing prices to drop temporarily.
•Doubts about security: The strength of the affected platforms or networks is temporarily called into question.
•Recovery: These drops are generally alarming in the short term, but the market usually stabilizes once the alert has passed.
The key is to keep a cool head and not let fear get the better of you! What do you do when the market falls? I’m listening! 👇 $BTC
#Criptomonedas #Seguridad #BinanceSquare
1
126
·
--
Article
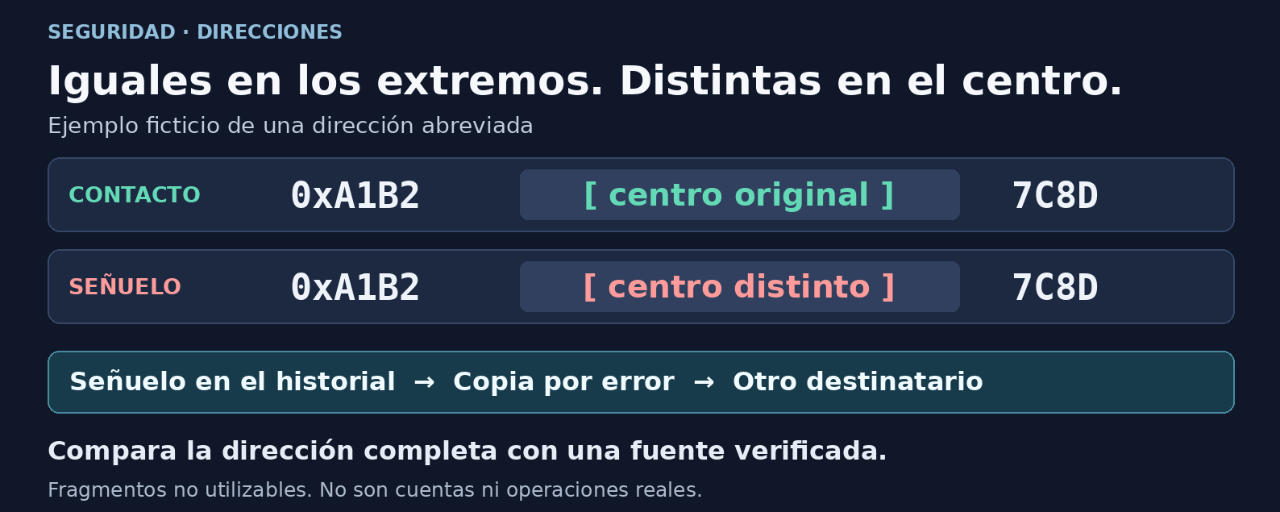
Why is there an almost identical address in your history?An address can look like a contact’s without belonging to them. If you only check the beginning and end, copying it from your history could send it to a different recipient.
The deception starts before you send
In an address poisoning attack, someone creates an address with similar beginnings and endings to one you’ve used before. Then they make a tiny transfer so the decoy appears among your visible transactions.
The goal is for you to copy that address by mistake next time. The contact’s address stays the same; it’s the added entry that could be confused with it.
Why is there an almost identical address in your history?
An address can look like a contact’s without belonging to them. If you only check the beginning and end, copying it from your history could send it to a different recipient.
The deception starts before you send
In an address poisoning attack, someone creates an address with similar beginnings and endings to one you’ve used before. Then they make a tiny transfer so the decoy appears among your visible transactions.
The goal is for you to copy that address by mistake next time. The contact’s address stays the same; it’s the added entry that could be confused with it.
78
·
--
🛡️ #Seguridad Preventive
💡 Better Safe Than Sorry
As Noelia Robles reflects in depth, protective measures should be activated for general and preventive security, never as a belated reaction after an incident has occurred.
The Common Mistake: Many users put off securing their accounts until they have already been compromised or their assets stolen.
The Advantage: Preventive security is infinitely more affordable, less stressful, and much more effective than reactive security.
Tip: Don’t wait until a monster is lurking before you lock the door and protect your assets.
🔗 https://www.binance.com/blog/comunidad/3912968241066805549?ref=CPA_00U38V0AIV
Rëy Nömhäs
·
--
⏱️ 5-Minute Checklist
✅ Quick Guide to Protect Your Account
No digital monster gets in on its own: they all need a door left open first (a careless click, excessive permissions, or artificial urgency). The good news is that your security is entirely in your hands.
Essential Checklist:
✔️Enable and set up two-factor authentication (2FA).
✔️Set up your personalized Anti-Phishing Code.
✔️Periodically review your devices and active sessions.
✔️Clear the permissions list for external applications.
✔️Enable facial recognition and biometrics.
Carefully verify addresses before sending funds. Five minutes that could save your savings!
🔗 https://www.binance.com/blog/comunidad/3912968241066805549?ref=CPA_00U38V0AIV
#BinanceHalloween
$BNB $BNSOL $BNCB
1
53
·
--
Article
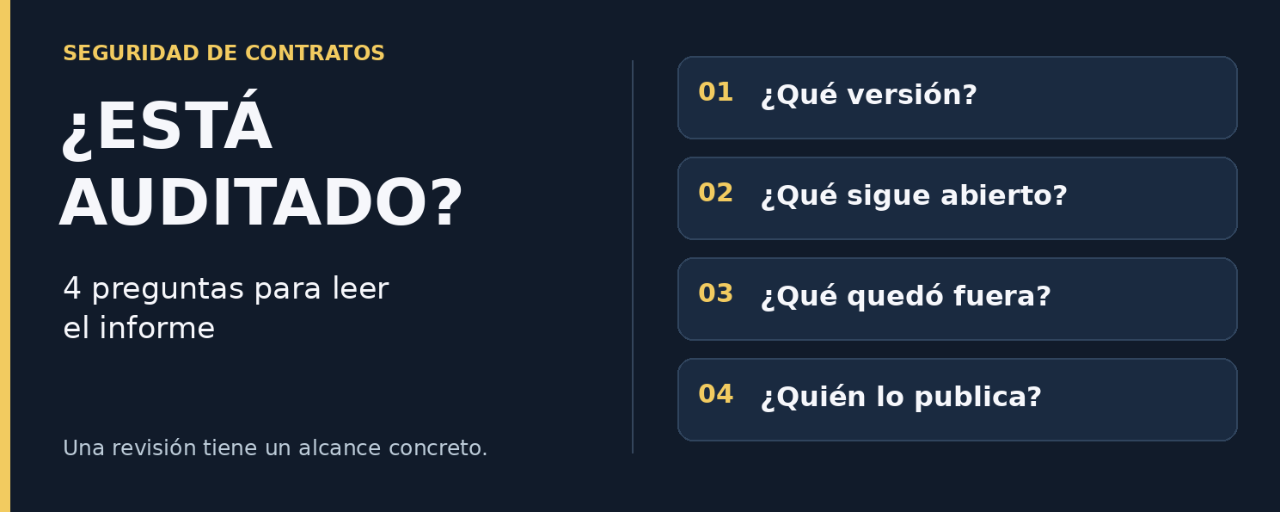
Is it audited? Four questions to ask when reading the reportA contract can still have open issues after an audit. Reading the report helps you distinguish what was reviewed, what was fixed, and what remains unresolved.
On Ethereum, contracts program how applications interact with assets such as $ETH and other tokens. A security review examines that code within a defined scope.
1. What version does it cover?
The report should identify the reviewed code. A “commit” is a reference to a specific version. If the contract was modified afterward, you need to know whether those changes were examined too.
Is it audited? Four questions to ask when reading the report
A contract can still have open issues after an audit. Reading the report helps you distinguish what was reviewed, what was fixed, and what remains unresolved.
On Ethereum, contracts program how applications interact with assets such as $ETH and other tokens. A security review examines that code within a defined scope.
1. What version does it cover?
The report should identify the reviewed code. A “commit” is a reference to a specific version. If the contract was modified afterward, you need to know whether those changes were examined too.
43

Article
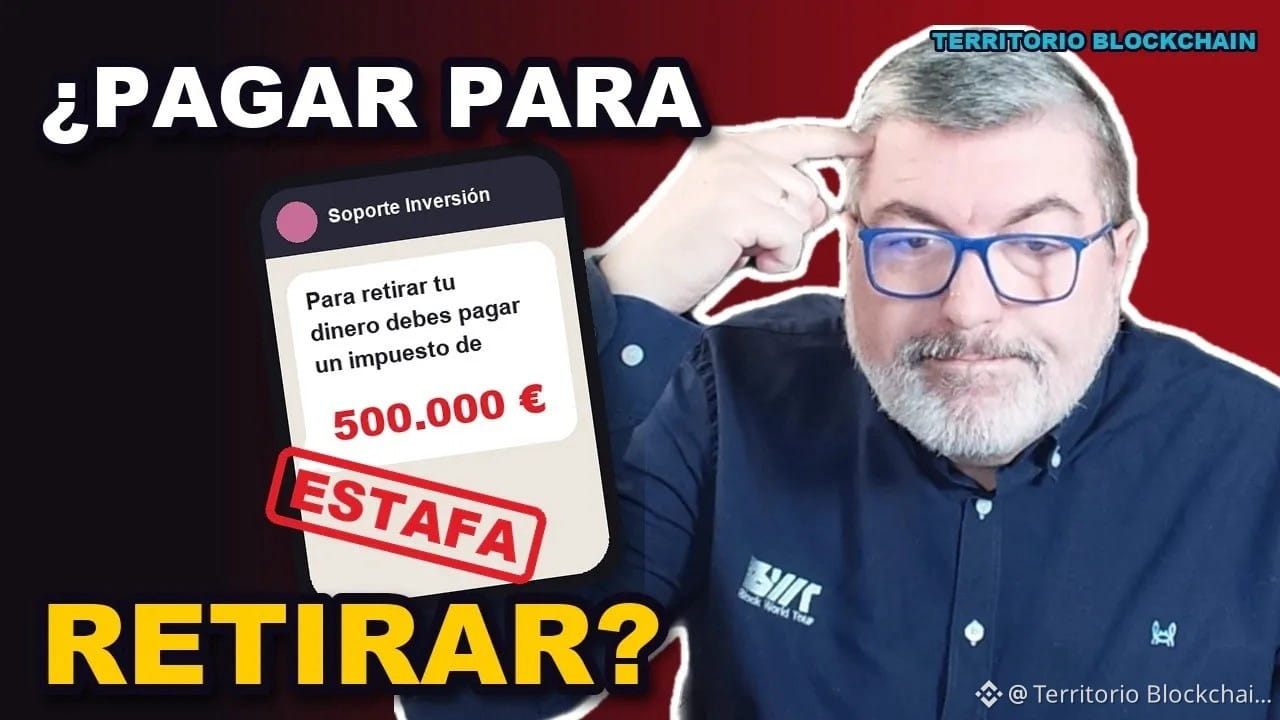
They lost €1.5 million after a Tinder match: how crypto pig butchering worksA Tinder match, weeks of conversation, and a supposed cryptocurrency investment opportunity. The result: €1.5 million lost. In the latest video from Territorio Blockchain, we break down pig butchering step by step—the romance scam that combines emotional manipulation with fake investment platforms.
It’s not a technical attack or a blockchain failure. Trust is the way in.
The stages of the scam:
• The match or first contact.
• Weeks spent building trust.
They lost €1.5 million after a Tinder match: how crypto pig butchering works
A Tinder match, weeks of conversation, and a supposed cryptocurrency investment opportunity. The result: €1.5 million lost. In the latest video from Territorio Blockchain, we break down pig butchering step by step—the romance scam that combines emotional manipulation with fake investment platforms.
It’s not a technical attack or a blockchain failure. Trust is the way in.
The stages of the scam:
• The match or first contact.
• Weeks spent building trust.
It’s not a technical attack or a blockchain failure. Trust is the way in.
The stages of the scam:
• The match or first contact.
• Weeks spent building trust.
1
1.7k
·
--
🔓 Closing the page doesn’t erase a permission on the blockchain.
Connecting a wallet to an app and authorizing it to spend tokens are two different permissions.
For example, an approval of $USDC on Ethereum allows a specific address to spend up to the authorized amount. It doesn’t automatically authorize all other tokens.
Disconnecting the app doesn’t revoke that approval: it may remain active even if you no longer visit the site.
Before signing, check the authorized address, the token, and the limit. Unlimited approvals increase your exposure if the contract is malicious or compromised.
Have you ever confused disconnecting with revoking?
Source: [Binance — Aprobaciones en blockchain](https://www.binance.com/es-LA/support/faq/detail/78def429ca0c470abb60a852f8fbef75)
#Seguridad #Web3 #Criptomonedas
The author may receive rewards from Binance.
🔓 Closing the page doesn’t erase a permission on the blockchain.
Connecting a wallet to an app and authorizing it to spend tokens are two different permissions.
For example, an approval of $USDC on Ethereum allows a specific address to spend up to the authorized amount. It doesn’t automatically authorize all other tokens.
Disconnecting the app doesn’t revoke that approval: it may remain active even if you no longer visit the site.
Before signing, check the authorized address, the token, and the limit. Unlimited approvals increase your exposure if the contract is malicious or compromised.
Have you ever confused disconnecting with revoking?
Source: Binance — Aprobaciones en blockchain
#Seguridad #Web3 #Criptomonedas
The author may receive rewards from Binance.
41
·
--
Artificial intelligence learned to find bugs in Bitcoin’s code.
Bitcoin Core developers have just changed the security rules.
Before, they kept detected bugs secret for months.
Now, that waiting period is being eliminated.
The reason is simple: this summer, AI tools found hundreds of bugs in $BTC before humans did.
If AI detects a vulnerability, there’s no point in hiding it.
It’s better to fix the code quickly before someone else notices the weak point.
What do you think of this change in strategy?
#Bitcoin #Cripto #Security
26
·
--
🔐 Three concepts to understand your wallet at $BTC
1️⃣ Public address: lets you receive funds. You can share it, although its activity can be viewed on the blockchain.
2️⃣ Private key: authorizes transactions. It must remain secret.
3️⃣ Recovery phrase: in wallets that use one, it lets you restore access. It should not be shared either.
There’s another important difference: with custodial wallets, a third party manages the keys; with non-custodial wallets, that responsibility is yours.
Which concept did you have the most questions about?
Source: [Binance Academy — Billeteras de criptomonedas](https://www.binance.com/es/academy/articles/crypto-wallet-types-explained)
#bitcoin #Criptomonedas #Seguridad
The author may receive rewards from Binance.
🔐 Three concepts to understand your wallet at $BTC
1️⃣ Public address: lets you receive funds. You can share it, although its activity can be viewed on the blockchain.
2️⃣ Private key: authorizes transactions. It must remain secret.
3️⃣ Recovery phrase: in wallets that use one, it lets you restore access. It should not be shared either.
There’s another important difference: with custodial wallets, a third party manages the keys; with non-custodial wallets, that responsibility is yours.
Which concept did you have the most questions about?
Source: Binance Academy — Billeteras de criptomonedas
#bitcoin #Criptomonedas #Seguridad
The author may receive rewards from Binance.
1
126
·
--
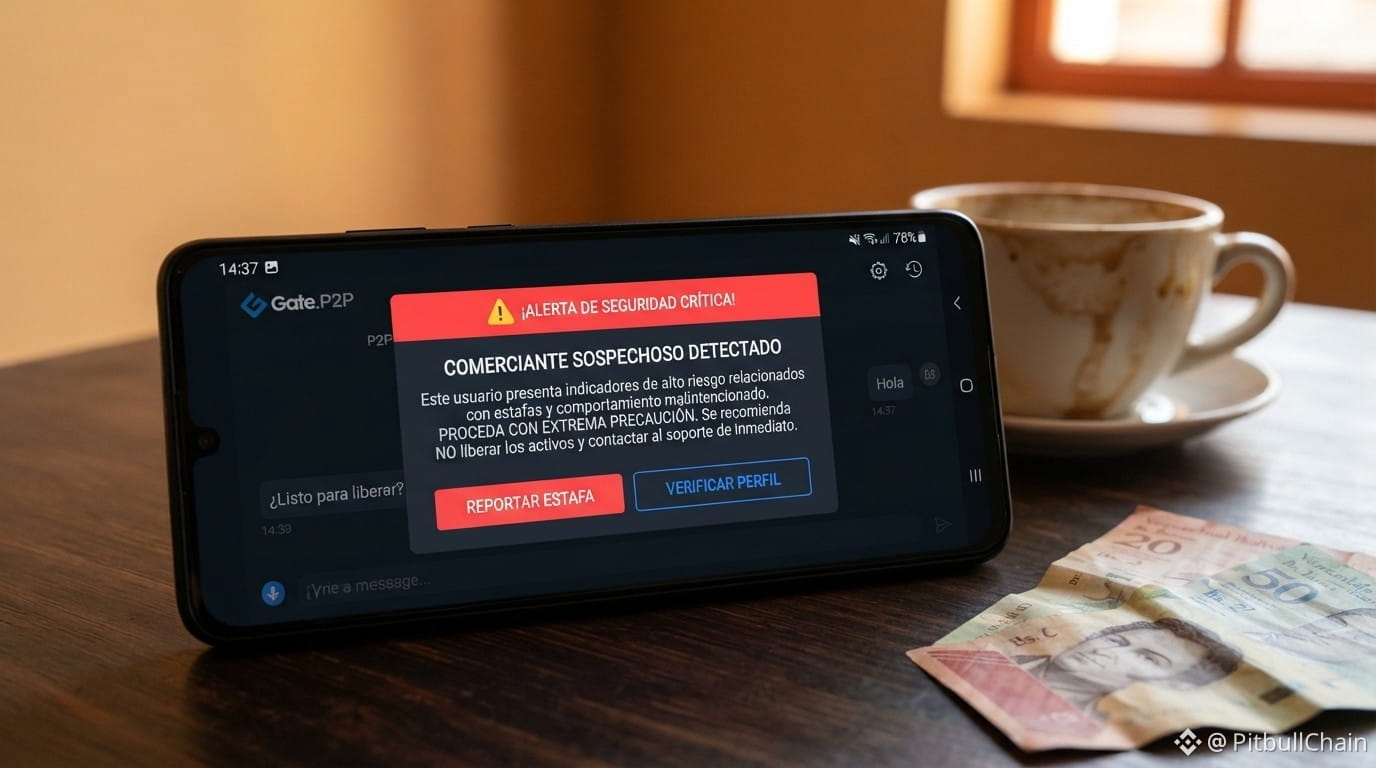
34 seconds. That's how long it takes a scammer to send you an edited screenshot of a mobile payment. 🚨
Before releasing $USDT:
✅ Open YOUR banking app, not the image
✅ Check the available balance, not “in transit”
✅ Verify that the account holder’s name matches
✅ If anything doesn’t add up, cancel and open a dispute
There are 256 offers today and a spread of Bs. 37.67. With so many offers, being in a hurry is no excuse.
📊 Live rates and analysis at https://pitbullchain.com
$USDT #P2P #Seguridad #BinanceSquare #Venezuela
151
·
--
Security audits aren’t the shield many people think they are.
A recent report by Hacken paints a stark picture.
In the third quarter, $1.18 billion was lost to hacks.
The surprising finding is that 77% of those losses occurred outside the scope of current reviews.
Often, the problem isn’t in the core code.
The failure stems from compromised vendors or patches that were never installed.
Having a security seal doesn’t guarantee everything is protected.
Blind trust seems to be the biggest risk in the sector.
Are you surprised by this level of negligence in these projects?
$BTC #Cripto #Security
39
·
--
Hacks in the crypto sector remain a serious problem.
During the third quarter, losses reached nearly $1.2 billion.
This was driven mainly by incidents at Bitget and Liquid.
Interestingly, 77% of these losses were not caused by direct flaws in the protocols.
The problem came from compromised providers, development tools, and infrastructure components that were outside the scope of routine security audits.
It seems attackers found a backdoor that nobody was watching.
What do you think of this way of attacking the market?
$BTC #Cripto #Security
59
🚨 A spy chip was found INSIDE Ledger wallets!!!
When you entered your 24 words, the chip read them and sent them to the attacker over a mobile network. - 300+ wallets drained - Up to USD 93M stolen - MediaMarkt suspended Ledger sales in Europe All confirmed losses came from one reseller (CryptoBilis). Ledger says it has not confirmed any thefts from devices bought on its official website. If you did NOT buy your wallet from ledger.com: create a new seed phrase on another device and move your funds. Where did you buy yours? 👇 🟢 Official website 🟡 Amazon / store 🔴 Reseller #Ledger #Seguridad #ledgertech
When you entered your 24 words, the chip read them and sent them to the attacker over a mobile network. - 300+ wallets drained - Up to USD 93M stolen - MediaMarkt suspended Ledger sales in Europe All confirmed losses came from one reseller (CryptoBilis). Ledger says it has not confirmed any thefts from devices bought on its official website. If you did NOT buy your wallet from ledger.com: create a new seed phrase on another device and move your funds. Where did you buy yours? 👇 🟢 Official website 🟡 Amazon / store 🔴 Reseller #Ledger #Seguridad #ledgertech
1
128
·
--
Buying hardware from unofficial sources can be very costly.
Ledger detected LTE-connected implants in wallets sold by CryptoBilis. These devices were able to extract users’ recovery phrases.
CryptoBilis has stopped selling them. Meanwhile, brands such as Trezor and OneKey have cut all business ties with this reseller.
It’s an important reminder to be careful where we buy our security devices. It’s always best to go straight to the official source.
What extra security measures do you take when buying hardware?
$BTC #Ledger #Security
66
·
--
Bullish
⚠️ THE THREAT TO YOUR CRYPTO MAY NOT BE THE PRICE.
An Ethereum researcher warned about future AI risks to the cryptography that protects wallets. Vitalik urged caution: there is no evidence that keys are broken today.
Is crypto security ready for the AI era?
#Ethereum✅ #Seguridad
⚠️ THE THREAT TO YOUR CRYPTO MAY NOT BE THE PRICE.
An Ethereum researcher warned about future AI risks to the cryptography that protects wallets. Vitalik urged caution: there is no evidence that keys are broken today.
Is crypto security ready for the AI era?
#Ethereum✅ #Seguridad
An Ethereum researcher warned about future AI risks to the cryptography that protects wallets. Vitalik urged caution: there is no evidence that keys are broken today.
Is crypto security ready for the AI era?
#Ethereum✅ #Seguridad
120

You legends! Today we're learning how to stay SAFE online 🛡️
At Binance, we learn by playing—and we even get prizes.
Want to play with me?
Join here 👇
https://www.binance.com/activity/word-of-the-day/Proactive-Security-Wins?ref=CPA_00XZ7X05TH
#CriptoParaNinos #Seguridad #XRPLedgerPatchesXRPCreationBug #seguir
At Binance, we learn by playing—and we even get prizes.
Want to play with me?
Join here 👇
https://www.binance.com/activity/word-of-the-day/Proactive-Security-Wins?ref=CPA_00XZ7X05TH
#CriptoParaNinos #Seguridad #XRPLedgerPatchesXRPCreationBug #seguir
1
145
🚨 BITCOIN ALERT: AN OFFICIAL ACCOUNT SHARED A FRAUDULENT LINK
On October 11, COLDCARD, a manufacturer of hardware wallets for $BTC, reported that a fraudulent link had been shared from its official X account.
⚠️ WHAT HAPPENED?
🔸 The message posed as an urgent security warning.
🔸 It directed users to a fake page for a supposed funds migration.
🔸 COLDCARD removed the post and is investigating how it appeared.
🚨 WERE THE WALLETS HACKED?
There is no confirmed evidence that the devices were compromised or that the link resulted in financial losses.
🛡️ HOW TO PROTECT YOUR FUNDS
1️⃣ Don’t click migration links shared in suspicious posts.
2️⃣ Never enter your recovery phrase (the words that give access to your funds) on a website.
3️⃣ Verify alerts by going directly to the manufacturer’s website yourself.
4️⃣ If you revealed your phrase, consider it compromised and move your funds to a new, secure wallet.
📌 OUR TAKE
Following our coverage of Ledger, another, different risk has emerged: phishing (deception aimed at stealing data or funds) through seemingly official channels.
A legitimate account doesn’t guarantee that every link it posts is safe.
🔎 WHAT WE’RE WATCHING
🔴 Risk: confirmed victims or new fraudulent posts.
🟡 Monitoring: investigation ongoing.
🟢 Improvement: source clarified and security measures strengthened.
⚠️ Don’t confuse a fraudulent link with a confirmed device hack.
📌 ALERT / SECURITY
#bitcoin #BTC #Coldcard #Security
131
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#UniswapA16zSeekDeFiExemptionFromIllinoisCryptoTax
24,328 views
744 Discussing
2
#HKDollarStablecoinHKDAPToLaunchOnSolana
18,721 views
471 Discussing
3
#$1.5BInLeveragedCryptoBetsLiquidated
39,999 views
245 Discussing
4
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
2,865 views
68 Discussing
5
#KOSPIFalls3.53%BackBelow6000
62,307 views
1,089 Discussing
6
#AmazonSharesFallAbout7%InPremarketTrading
28,129 views
582 Discussing
7
#USMidtermElections
244,486 views
2,345 Discussing
8
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
25,730 views
94 Discussing
9
#BinanceWillListPredictPREDICT
93,445 views
1,389 Discussing
10
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
3,132 views
110 Discussing