
#safepal
safepal
108,392 views
260 Discussing
Hot
Latest

SafePal $SFP — the wallet token that can't keep itself safe 😅
SFP is at ~$0.19 — right on its ALL-TIME LOW, set today. Down ~6% in 24h, -28% in 30 days, and ~96% below its $4.37 ATH from 2021.
The irony writes itself: SafePal secures crypto for millions of users, but its own token needs a safe.
📊 Price: ~$0.19
📉 24h: -6% | 30d: -28%
💰 Market cap: ~$94M (rank ~#267)
🔑 Support: $0.185 (ATL zone) | Resistance: $0.195
BTC is at ~$68,900, still under $70K after $1.41B in liquidations. When the market bleeds, even the wallet tokens need a wallet.
Would you hold a wallet token at its all-time low?
Not financial advice. DYOR.
#SafePal #Crypto #Altcoins
SafePal $SFP — the wallet token that can't keep itself safe 😅
SFP is at ~$0.19 — right on its ALL-TIME LOW, set today. Down ~6% in 24h, -28% in 30 days, and ~96% below its $4.37 ATH from 2021.
The irony writes itself: SafePal secures crypto for millions of users, but its own token needs a safe.
📊 Price: ~$0.19
📉 24h: -6% | 30d: -28%
💰 Market cap: ~$94M (rank ~#267)
🔑 Support: $0.185 (ATL zone) | Resistance: $0.195
BTC is at ~$68,900, still under $70K after $1.41B in liquidations. When the market bleeds, even the wallet tokens need a wallet.
Would you hold a wallet token at its all-time low?
Not financial advice. DYOR.
#SafePal #Crypto #Altcoins
SFP is at ~$0.19 — right on its ALL-TIME LOW, set today. Down ~6% in 24h, -28% in 30 days, and ~96% below its $4.37 ATH from 2021.
The irony writes itself: SafePal secures crypto for millions of users, but its own token needs a safe.
📊 Price: ~$0.19
📉 24h: -6% | 30d: -28%
💰 Market cap: ~$94M (rank ~#267)
🔑 Support: $0.185 (ATL zone) | Resistance: $0.195
BTC is at ~$68,900, still under $70K after $1.41B in liquidations. When the market bleeds, even the wallet tokens need a wallet.
Would you hold a wallet token at its all-time low?
Not financial advice. DYOR.
#SafePal #Crypto #Altcoins
3

·
--
🚨 SAFEPAL USERS TARGETED BY PHYSICAL MAIL PHISHING AFTER DATA BREACH!
Scammers are reportedly sending fake SafePal security letters to hardware wallet users in Italy.
The letters contain real customer names, addresses and order details, making them look legitimate.
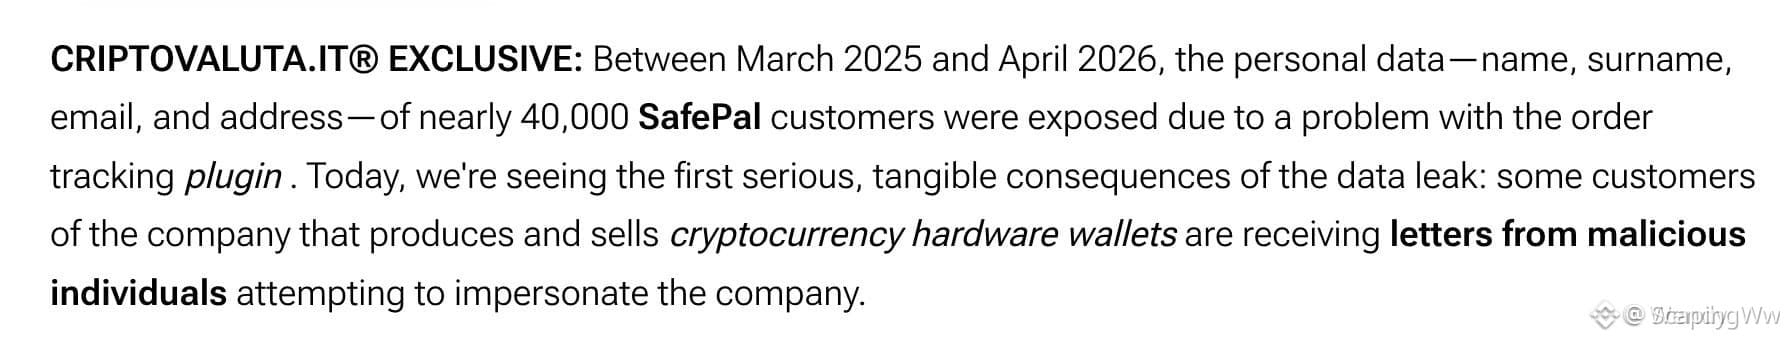
According to Italian crypto outlet Criptovaluta.it:
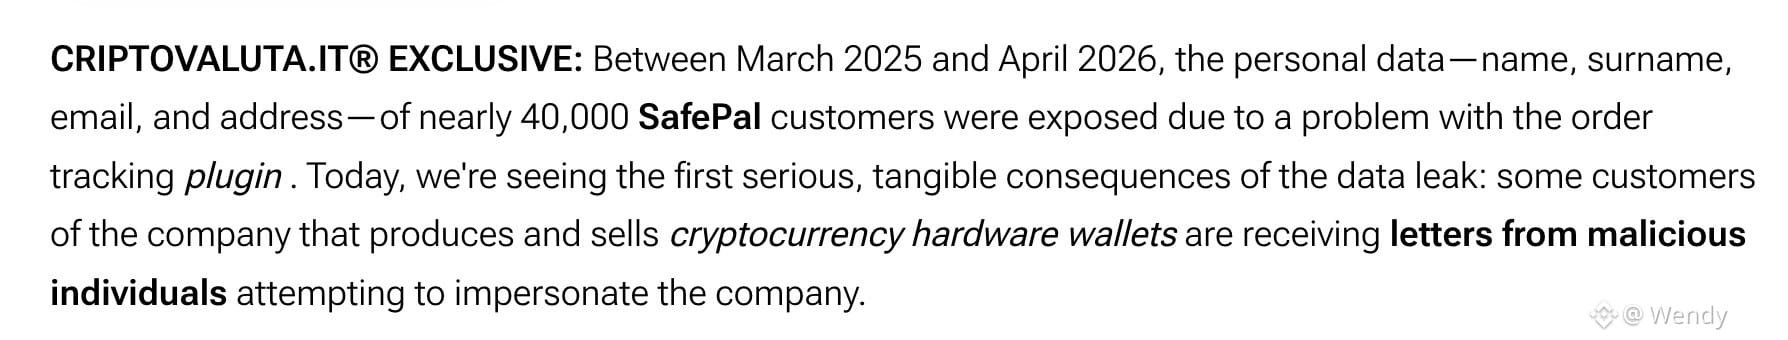
• Nearly 40,000 customers had personal data exposed.
• The leak involved an order-tracking plugin between March 2025 and April 2026.
• Fake letters warn of a firmware vulnerability.
• QR codes redirect users to a phishing website impersonating SafePal.
SafePal previously confirmed that leaked customer information was being used in phishing attempts.
⚠️ If you receive a SafePal security letter, don’t scan its QR code or enter your recovery phrase. Verify any security notice through SafePal’s official channels.
Have you ever received a crypto phishing letter?
#SafePal #CryptoSecurity
🚨 SAFEPAL USERS TARGETED BY PHYSICAL MAIL PHISHING AFTER DATA BREACH!
Scammers are reportedly sending fake SafePal security letters to hardware wallet users in Italy.
The letters contain real customer names, addresses and order details, making them look legitimate.
According to Italian crypto outlet Criptovaluta.it:
• Nearly 40,000 customers had personal data exposed.
• The leak involved an order-tracking plugin between March 2025 and April 2026.
• Fake letters warn of a firmware vulnerability.
• QR codes redirect users to a phishing website impersonating SafePal.
SafePal previously confirmed that leaked customer information was being used in phishing attempts.
⚠️ If you receive a SafePal security letter, don’t scan its QR code or enter your recovery phrase. Verify any security notice through SafePal’s official channels.
Have you ever received a crypto phishing letter?
#SafePal #CryptoSecurity
Scammers are reportedly sending fake SafePal security letters to hardware wallet users in Italy.
The letters contain real customer names, addresses and order details, making them look legitimate.
According to Italian crypto outlet Criptovaluta.it:
• Nearly 40,000 customers had personal data exposed.
• The leak involved an order-tracking plugin between March 2025 and April 2026.
• Fake letters warn of a firmware vulnerability.
• QR codes redirect users to a phishing website impersonating SafePal.
SafePal previously confirmed that leaked customer information was being used in phishing attempts.
⚠️ If you receive a SafePal security letter, don’t scan its QR code or enter your recovery phrase. Verify any security notice through SafePal’s official channels.
Have you ever received a crypto phishing letter?
#SafePal #CryptoSecurity
3
841

·
--
🚨 PHYSICAL MAIL PHISHING TARGETS $SFP USERS IN A BLISTERING NEW ATTACK VECTOR
When bad actors pivot from digital screens to your physical mailbox, the threat landscape shifts entirely. A recent data breach exposed order details for thousands of hardware wallet owners, leading to targeted physical letters featuring convincing firmware warnings 📊.
Scammers are weaponizing real home addresses and names to drive traffic to malicious credential-harvesting portals via QR codes. Never trust unsolicited correspondence demanding recovery phrase inputs or sudden security upgrades 💡.
🛡️ How are you currently verifying the authenticity of external hardware security notices before interacting? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #CryptoSecurity #Phishing #SafePal
⚡
🚨 PHYSICAL MAIL PHISHING TARGETS $SFP USERS IN A BLISTERING NEW ATTACK VECTOR
When bad actors pivot from digital screens to your physical mailbox, the threat landscape shifts entirely. A recent data breach exposed order details for thousands of hardware wallet owners, leading to targeted physical letters featuring convincing firmware warnings 📊.
Scammers are weaponizing real home addresses and names to drive traffic to malicious credential-harvesting portals via QR codes. Never trust unsolicited correspondence demanding recovery phrase inputs or sudden security upgrades 💡.
🛡️ How are you currently verifying the authenticity of external hardware security notices before interacting? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #CryptoSecurity #Phishing #SafePal
⚡
When bad actors pivot from digital screens to your physical mailbox, the threat landscape shifts entirely. A recent data breach exposed order details for thousands of hardware wallet owners, leading to targeted physical letters featuring convincing firmware warnings 📊.
Scammers are weaponizing real home addresses and names to drive traffic to malicious credential-harvesting portals via QR codes. Never trust unsolicited correspondence demanding recovery phrase inputs or sudden security upgrades 💡.
🛡️ How are you currently verifying the authenticity of external hardware security notices before interacting? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #CryptoSecurity #Phishing #SafePal
⚡
21
·
--
🚨 SafePal customers are receiving fake letters with QR codes
On November 12, 2026, reports emerged of fraudulent paper letters received by some buyers of SafePal hardware wallets. The letters claim that a firmware issue has been detected in the device and invite recipients to scan a QR code to fix it. In reality, the code leads to a fake website where scammers attempt to obtain the wallet’s secret recovery phrase.
SafePal confirmed the scam and linked it to a previously disclosed leak of customer order data. The company emphasized that it does not send such letters and never asks for seed phrases. According to SafePal, its wallet infrastructure remains secure.
Do not scan QR codes in unexpected letters, and never enter your recovery phrase on third-party websites. Source: SafePal statement, BeInCrypto, November 12, 2026.
#CryptoSecurity #SafePal
🚨 SafePal customers are receiving fake letters with QR codes
On November 12, 2026, reports emerged of fraudulent paper letters received by some buyers of SafePal hardware wallets. The letters claim that a firmware issue has been detected in the device and invite recipients to scan a QR code to fix it. In reality, the code leads to a fake website where scammers attempt to obtain the wallet’s secret recovery phrase.
SafePal confirmed the scam and linked it to a previously disclosed leak of customer order data. The company emphasized that it does not send such letters and never asks for seed phrases. According to SafePal, its wallet infrastructure remains secure.
Do not scan QR codes in unexpected letters, and never enter your recovery phrase on third-party websites. Source: SafePal statement, BeInCrypto, November 12, 2026.
#CryptoSecurity #SafePal
On November 12, 2026, reports emerged of fraudulent paper letters received by some buyers of SafePal hardware wallets. The letters claim that a firmware issue has been detected in the device and invite recipients to scan a QR code to fix it. In reality, the code leads to a fake website where scammers attempt to obtain the wallet’s secret recovery phrase.
SafePal confirmed the scam and linked it to a previously disclosed leak of customer order data. The company emphasized that it does not send such letters and never asks for seed phrases. According to SafePal, its wallet infrastructure remains secure.
Do not scan QR codes in unexpected letters, and never enter your recovery phrase on third-party websites. Source: SafePal statement, BeInCrypto, November 12, 2026.
#CryptoSecurity #SafePal
1

·
--
🚨 $SFP DATA BREACH AFFECTING NEARLY 40,000 CUSTOMERS
SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin.
Here’s what they’re not telling you:
→ SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin — with no access to wallets or funds compromised, according to the company.
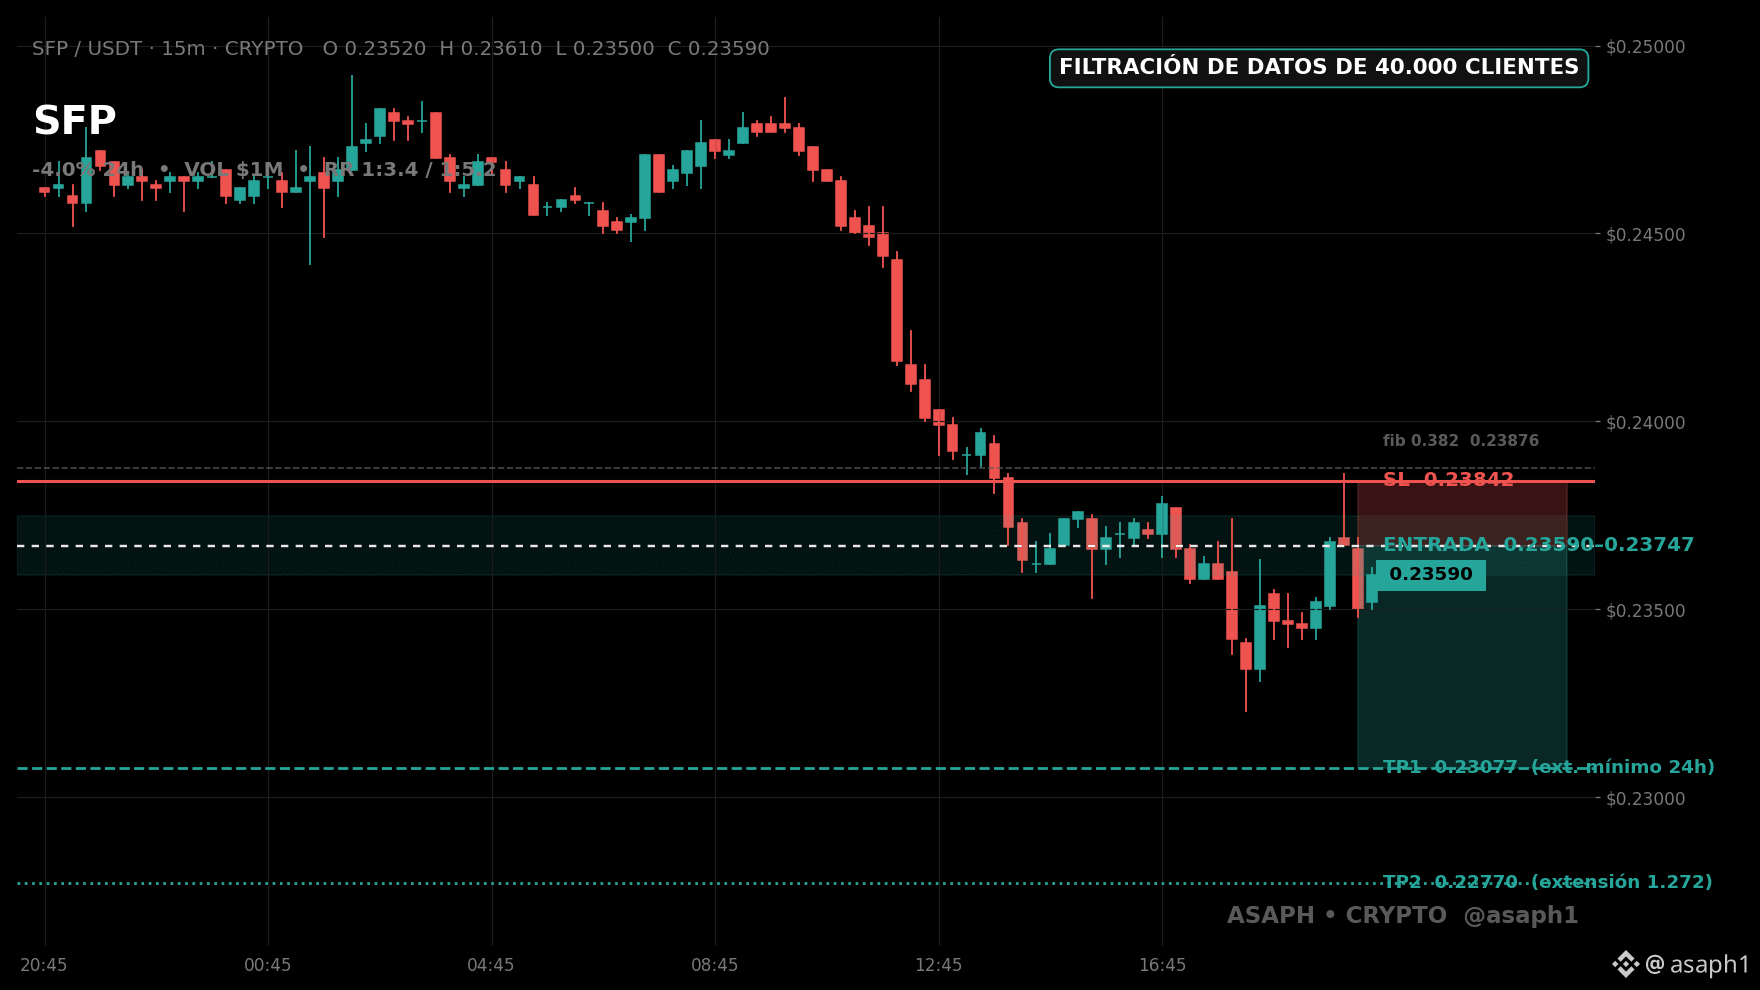
→ Divergence: SFP -4.02% today, while $TWT is up +1.03% and $CAKE +1.71%.
→ Progression: breach revealed → confidence shaken → price seeks the extended 24h low.
Entry: $0.2359–$0.237475
SL: $0.23842
TP1: $0.2307725
TP2: $0.2277032
The company says funds are safe, but the market is already pricing in the news. Trade with your SL in place: this story could still make more headlines.
Can SFP take the hit, or is this just the beginning? 👇
$SFP #SafePal #Filtracion #Trading
🚨 $SFP DATA BREACH AFFECTING NEARLY 40,000 CUSTOMERS
SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin.
Here’s what they’re not telling you:
→ SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin — with no access to wallets or funds compromised, according to the company.
→ Divergence: SFP -4.02% today, while $TWT is up +1.03% and $CAKE +1.71%.
→ Progression: breach revealed → confidence shaken → price seeks the extended 24h low.
Entry: $0.2359–$0.237475
SL: $0.23842
TP1: $0.2307725
TP2: $0.2277032
The company says funds are safe, but the market is already pricing in the news. Trade with your SL in place: this story could still make more headlines.
Can SFP take the hit, or is this just the beginning? 👇
$SFP #SafePal #Filtracion #Trading
SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin.
Here’s what they’re not telling you:
→ SafePal revealed today that a breach exposed order data belonging to nearly 40,000 customers due to a flaw in its tracking plugin — with no access to wallets or funds compromised, according to the company.
→ Divergence: SFP -4.02% today, while $TWT is up +1.03% and $CAKE +1.71%.
→ Progression: breach revealed → confidence shaken → price seeks the extended 24h low.
Entry: $0.2359–$0.237475
SL: $0.23842
TP1: $0.2307725
TP2: $0.2277032
The company says funds are safe, but the market is already pricing in the news. Trade with your SL in place: this story could still make more headlines.
Can SFP take the hit, or is this just the beginning? 👇
$SFP #SafePal #Filtracion #Trading
40
·
--
Bearish
SafePal reveals a data breach involving around 40,000 customers
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
{future}(SFPUSDT)
#SafePal #CryptoSecurity
#CyberSecurity #Web3
SafePal reveals a data breach involving around 40,000 customers
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
#SafePal #CryptoSecurity
#CyberSecurity #Web3
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
#SafePal #CryptoSecurity
#CyberSecurity #Web3
2
227

SafePal's data breach is a massive wake-up call. 40,000 users' info leaked is no joke. This kind of security slip-up is exactly why self-custody and cold storage are non-negotiable.
#SafePal #CyberSecurity
SafePal's data breach is a massive wake-up call. 40,000 users' info leaked is no joke. This kind of security slip-up is exactly why self-custody and cold storage are non-negotiable.
#SafePal #CyberSecurity
#SafePal #CyberSecurity
33
·
--
Three hardware-wallet incidents in three weeks: the exposure surface has shifted from keys to identityOn August 16, SafePal disclosed an authorization flaw in its order lookup system: by modifying the order number, users can view other people’s order information. About 39,798 customers are affected. The leaked content includes names, email addresses, phone numbers, shipping addresses, and purchase details, covering orders placed between March 2, 2025 and April 11, 2026. Private keys, recovery mnemonics, and wallet passwords were not affected.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
Three hardware-wallet incidents in three weeks: the exposure surface has shifted from keys to identity
On August 16, SafePal disclosed an authorization flaw in its order lookup system: by modifying the order number, users can view other people’s order information. About 39,798 customers are affected. The leaked content includes names, email addresses, phone numbers, shipping addresses, and purchase details, covering orders placed between March 2, 2025 and April 11, 2026. Private keys, recovery mnemonics, and wallet passwords were not affected.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
1
115
·
--
Bullish
$SFP
{spot}(SFPUSDT)
/USDT — STRONG BULLISH SETUP
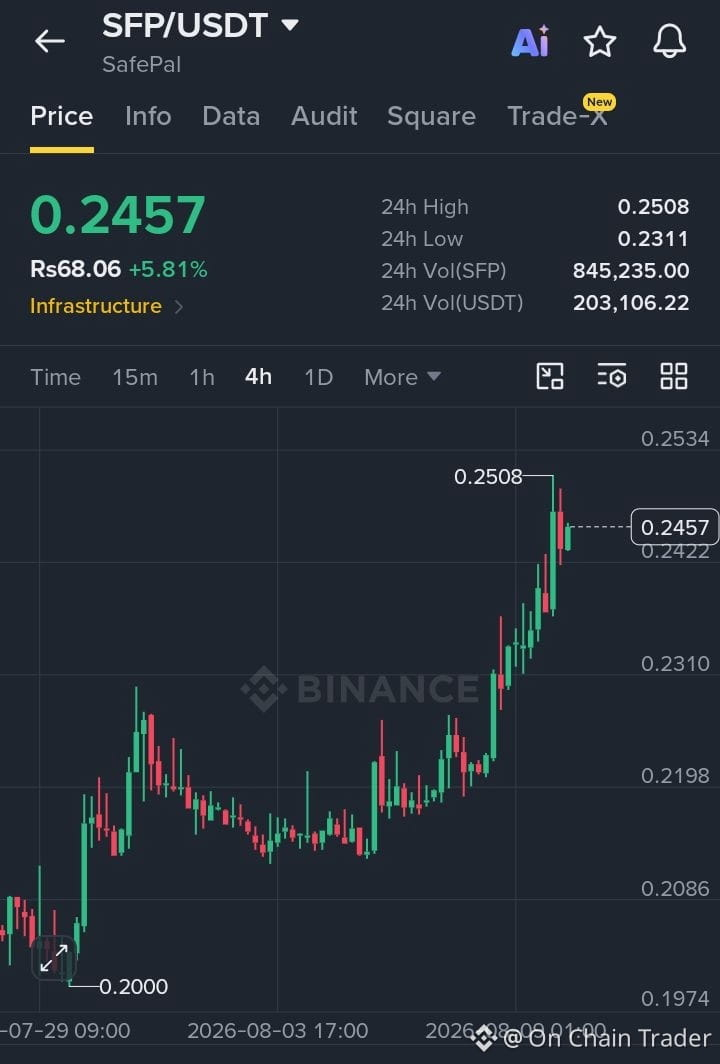
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
$SFP
/USDT — STRONG BULLISH SETUP
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
/USDT — STRONG BULLISH SETUP
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
1
113

·
--
🚨 SAFEPAL DATA EXPOSURE AFFECTS 40K USERS — $PORTAL & $DOLO WATCHED CLOSELY ⚡
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
🚨 SAFEPAL DATA EXPOSURE AFFECTS 40K USERS — $PORTAL & $DOLO WATCHED CLOSELY ⚡
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
129
SafePal officially integrates the Robinhood L2 mainnet, making the RWAFi path wider and wider.
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
SafePal officially integrates the Robinhood L2 mainnet, making the RWAFi path wider and wider.
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
10
·
--
🚨 SAFEPAL VENDOR BREACH EXPOSES 40K CUSTOMERS WHILE $SFP FUNDS REMAIN SAFE! 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
🚨 SAFEPAL VENDOR BREACH EXPOSES 40K CUSTOMERS WHILE $SFP FUNDS REMAIN SAFE! 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
41

SafePal data leak affects 40k customers
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
SafePal data leak affects 40k customers
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
116
·
--
BIG NEWS😐
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
BIG NEWS😐
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
75

SafePal Official Twitter Discloses: Its Order Tracking Plugin Reportedly Has a Security Vulnerability, With 39,798 Customers’ Information Accessed Without Authorization Between March 2, 2025 and April 11, 2026.
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
SafePal Official Twitter Discloses: Its Order Tracking Plugin Reportedly Has a Security Vulnerability, With 39,798 Customers’ Information Accessed Without Authorization Between March 2, 2025 and April 11, 2026.
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
41
🚨 SafePal is bringing in outside security firms after the data leak incident.
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
🚨 SafePal is bringing in outside security firms after the data leak incident.
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
474
·
--
Bullish
🚨 ALERT: @SafePal has disclosed a data breach affecting 39,798 customers.
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
🚨 ALERT: @SafePal has disclosed a data breach affecting 39,798 customers.
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
1
4
108
SafePal Wallet has recently disclosed a data security incident. In a post, its official account stated that a vulnerability was found in an order-tracking plugin, which led to unauthorized access to some customers’ information.
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
SafePal Wallet has recently disclosed a data security incident. In a post, its official account stated that a vulnerability was found in an order-tracking plugin, which led to unauthorized access to some customers’ information.
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
34
·
--
Bullish
🚀 $SFP
{spot}(SFPUSDT)
— BREAKOUT MOMENTUM 🔥
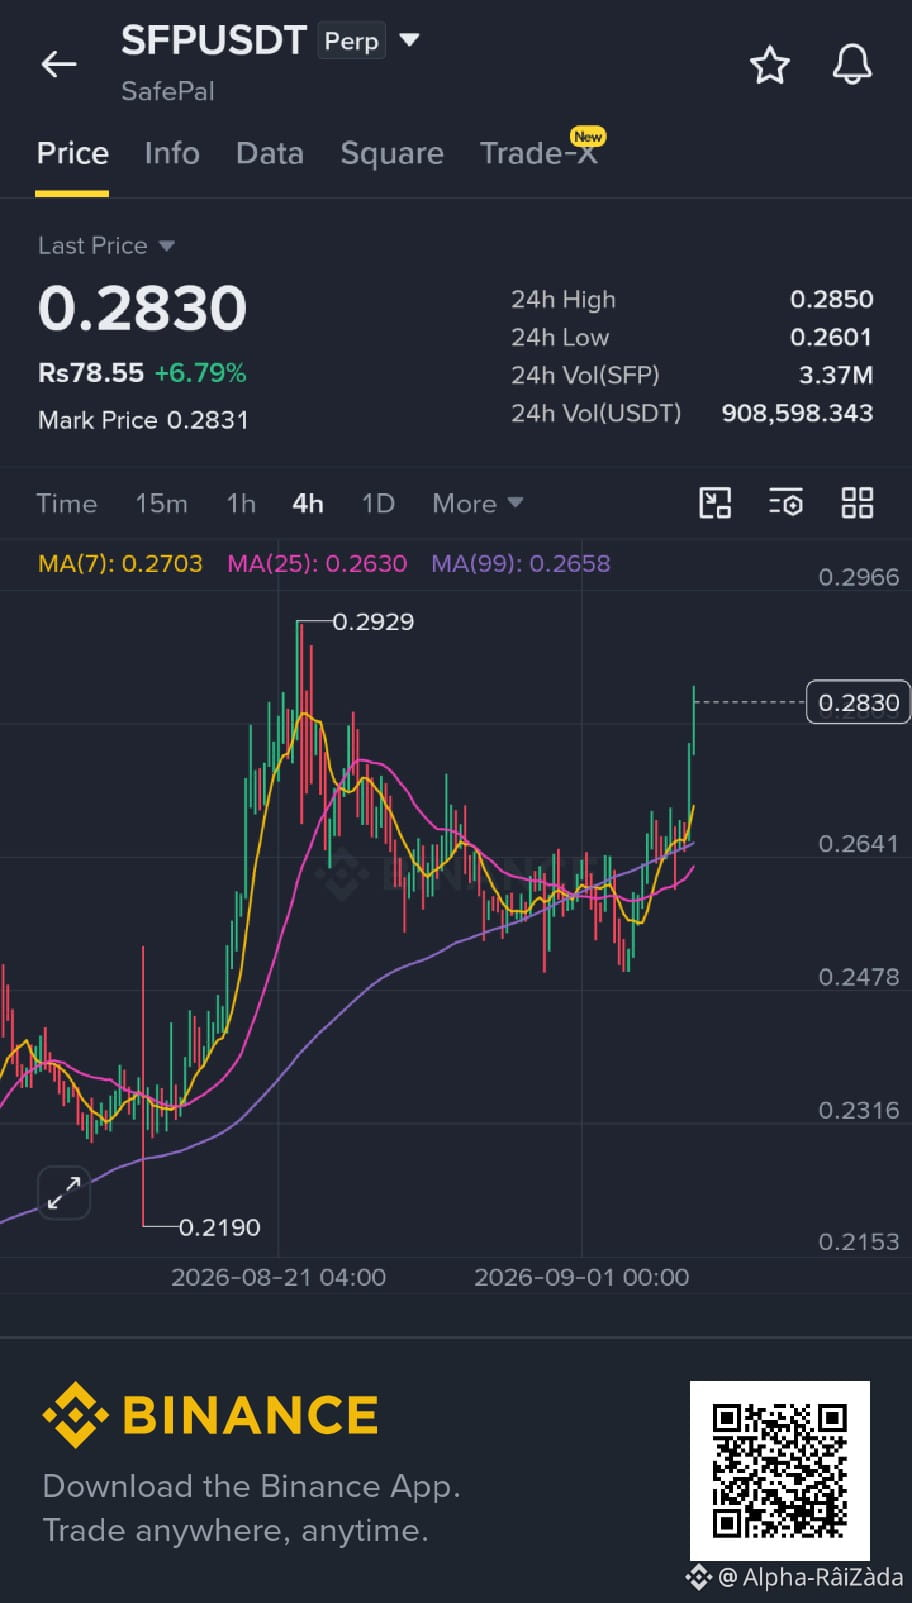
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
🚀 $SFP
— BREAKOUT MOMENTUM 🔥
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
— BREAKOUT MOMENTUM 🔥
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
4
SafePal has officially integrated with the Robinhood L2 mainnet, pushing the RWAFi roadmap forward another big step.
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
SafePal has officially integrated with the Robinhood L2 mainnet, pushing the RWAFi roadmap forward another big step.
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
8
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#WhoWillSucceedJensenHuangatNvidia?
114,037 views
1,371 Discussing
2
#WhatWillDriveCryptoandStocks’NextRebound?
490,348 views
3,250 Discussing
3
#BitcoinActiveSupplyInProfitDropsBelow45%
43,464 views
526 Discussing
4
#KavaSaysAbnormalActivityLimitedToKavaLend
20,909 views
285 Discussing
5
#USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
16,754 views
245 Discussing
6
#USPPIMissMayEaseBTCPressure
241,081 views
2,138 Discussing
7
#WORPTLetsTouristsConvertCryptoToThaiBaht
5,202 views
72 Discussing
8
#TONStrategyReports$23.97MQ3NetLoss
6,442 views
41 Discussing
9
#PolkadotCommunityApprovesNewStrategyWith97%Vote
22,587 views
266 Discussing
10
#dYdXPlansV9.9UpgradeToShiftUSDCToInjective
16,705 views
219 Discussing