

#mpc
mpc
15,046 views
141 Discussing
Hot
Latest

·
--
𝗘𝘃𝗲𝗿 𝘄𝗼𝗻𝗱𝗲𝗿𝗲𝗱 𝗵𝗼𝘄 𝗺𝗮𝗷𝗼𝗿 𝗪𝗲𝗯𝟯 𝗼𝗿𝗴𝗮𝗻𝗶𝘇𝗮𝘁𝗶𝗼𝗻𝘀 𝗮𝗻𝗱 𝗶𝗻𝘀𝘁𝗶𝘁𝘂𝘁𝗶𝗼𝗻𝗮𝗹 𝘁𝗿𝗲𝗮𝘀𝘂𝗿𝗶𝗲𝘀 𝘀𝗲𝗰𝘂𝗿𝗲 𝗺𝗶𝗹𝗹𝗶𝗼𝗻𝘀 𝗼𝗳 𝗱𝗼𝗹𝗹𝗮𝗿𝘀 𝘄𝗶𝘁𝗵𝗼𝘂𝘁 𝗿𝗲𝗹𝘆𝗶𝗻𝗴 𝗼𝗻 𝗮 𝘀𝗶𝗻𝗴𝗹𝗲 𝗽𝗲𝗿𝘀𝗼𝗻'𝘀 𝗽𝗿𝗶𝘃𝗮𝘁𝗲 𝗸𝗲𝘆? 𝗘𝗻𝘁𝗲𝗿 𝗠𝘂𝗹𝘁𝗶-𝗦𝗶𝗴 & 𝗠𝗣𝗖 🔐🛡️
𝘋𝘳𝘢𝘸𝘪𝘯𝘨 𝘧𝘳𝘰𝘮 𝘧𝘰𝘶𝘯𝘥𝘢𝘵𝘪𝘰𝘯𝘢𝘭 𝘭𝘦𝘴𝘴𝘰𝘯𝘴 𝘰𝘯 #BinanceAcademy, 𝘩𝘦𝘳𝘦 𝘪𝘴 𝘺𝘰𝘶𝘳 𝘲𝘶𝘪𝘤𝘬 𝘖𝘗𝘚𝘌𝘊 𝘣𝘳𝘦𝘢𝘬𝘥𝘰𝘸𝘯:
1️⃣ 𝗧𝗵𝗲 𝗦𝗶𝗻𝗴𝗹𝗲 𝗣𝗼𝗶𝗻𝘁 𝗼𝗳 𝗙𝗮𝗶𝗹𝘂𝗿𝗲:
• Traditional wallets (EOAs) rely on one private key, if that key is compromised, all funds can be permanently lost.
2️⃣ 𝗠𝘂𝗹𝘁𝗶-𝗦𝗶𝗴𝗻𝗮𝘁𝘂𝗿𝗲 (𝗠𝘂𝗹𝘁𝗶-𝗦𝗶𝗴) 𝗦𝗺𝗮𝗿𝘁 𝗖𝗼𝗻𝘁𝗿𝗮𝗰𝘁𝘀:
• Require multiple independent signatures (e.g., 3 out of 5 stakeholders) to approve a transaction, distributing trust across a team or multiple devices.
3️⃣ 𝗠𝘂𝗹𝘁𝗶-𝗣𝗮𝗿𝘁𝘆 𝗖𝗼𝗺𝗽𝘂𝘁𝗮𝘁𝗶𝗼𝗻 (𝗠𝗣𝗖):
• Splits a single private key into mathematical "shards" distributed across different servers or devices, the shards compute the signature collaboratively without the full key ever being assembled in one place.
📖 Learn more on Binance Academy: https://www.binance.com/en/academy/glossary/multisignature
Expand your technical literacy, upgrade your operational security 🛡️
Crypto involves risk, this is not financial advice, Always DYOR 💡
#MultiSig #MPC #CryptoEducation
Follow me for more 💛
Noobie Trader:
Binance Wallet is MCP wallet
1
4
85
·
--
$MPC.US caught traders' eyes today by showing up among the strongest 24-hour gainers. When a smaller token spikes like this, check volume, liquidity, and the project's recent updates before making any move.
What is your first check before buying a fast mover?
Not financial advice. Crypto is volatile, so always do your own research and only invest what you can afford to lose.
#MPC #Binance #altcoins #DYOR #CryptoTrending
{stock_us}(MPC.US)
$MPC.US caught traders' eyes today by showing up among the strongest 24-hour gainers. When a smaller token spikes like this, check volume, liquidity, and the project's recent updates before making any move.
What is your first check before buying a fast mover?
Not financial advice. Crypto is volatile, so always do your own research and only invest what you can afford to lose.
#MPC #Binance #altcoins #DYOR #CryptoTrending
What is your first check before buying a fast mover?
Not financial advice. Crypto is volatile, so always do your own research and only invest what you can afford to lose.
#MPC #Binance #altcoins #DYOR #CryptoTrending
MPCUS-1.46%
53
·
--
Bullish
$GENIUS
🔄Cross-Chain Velocity and the MPC Execution Paradigm🤧
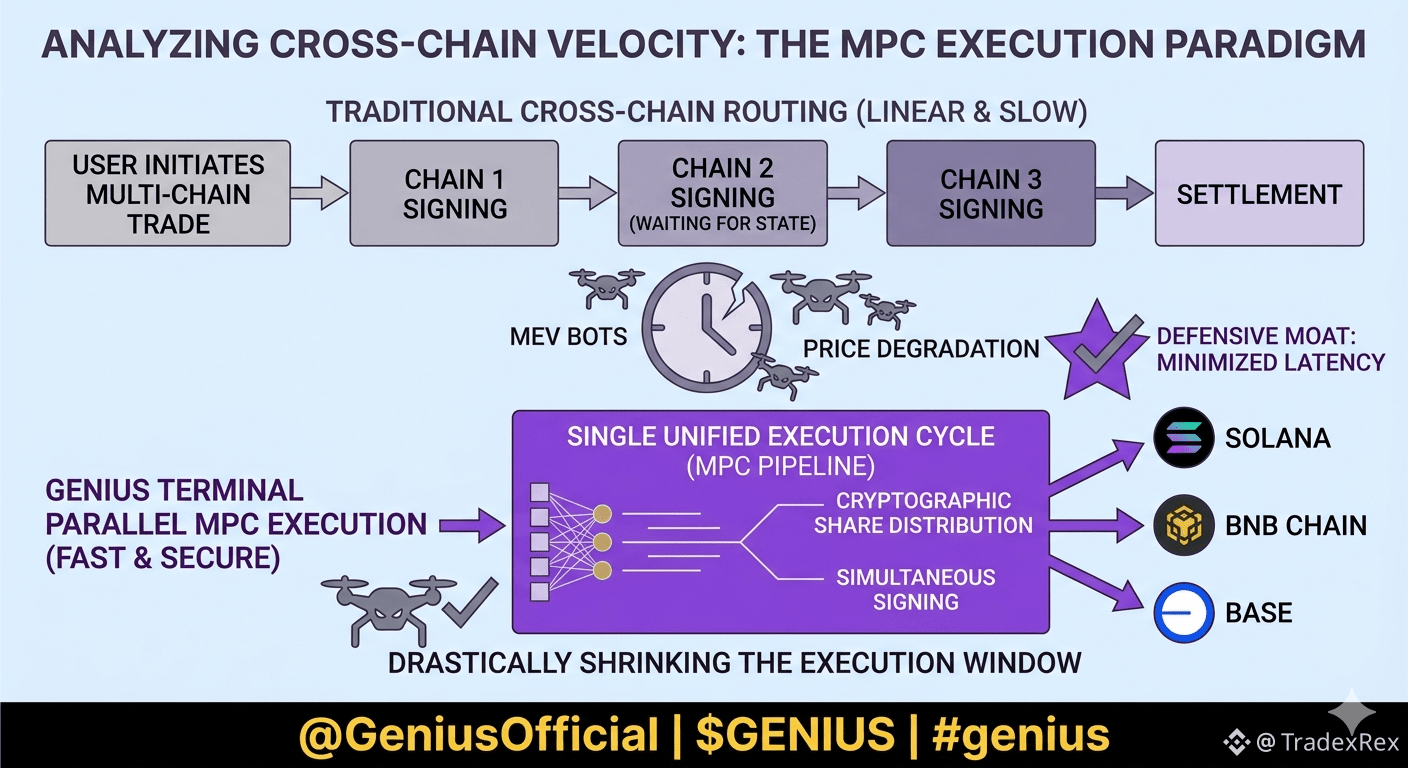
When evaluating decentralized trading infrastructure, most participants focus entirely on frontend speed, completely ignoring backend latency. But in high-volatility environments, the true bottleneck isn't how fast a UI renders—it's the time it takes to securely sign and route cross-chain payloads across separate distributed ledgers. Traditional multi-chain routing requires linear, state-dependent transaction signing, adding vital seconds of exposure to price degradation and front-running bots.
To achieve true capital optimization, the system architecture has to eliminate these structural bottlenecks entirely. This is where @GeniusOfficial introduces a fundamental shift through parallel Multi-Party Computation (#MPC ) execution pipelines.
Instead of processing complex multi-route trades sequentially, the terminal breaks down the transaction payload into distributed, cryptographic shares. By running these cryptographic pieces simultaneously across isolated execution nodes, the terminal can authorize and settle a split order across disparate chains (like #solana , #bnb Chain, and Base) in a single unified execution cycle.
For anyone tracking the long-term structural value of $GENIUS , this isn't just a minor optimization—it’s a defensive moat. By minimizing cross-chain signing latency, the platform drastically shrinks the execution window where MEV bots can exploit slippage. True institutional-grade decentralized trading isn't just about aggregating deep liquidity; it’s about moving that liquidity faster than the predatory bots scanning the mempool. #genius
{future}(GENIUSUSDT)
$GENIUS
🔄Cross-Chain Velocity and the MPC Execution Paradigm🤧
When evaluating decentralized trading infrastructure, most participants focus entirely on frontend speed, completely ignoring backend latency. But in high-volatility environments, the true bottleneck isn't how fast a UI renders—it's the time it takes to securely sign and route cross-chain payloads across separate distributed ledgers. Traditional multi-chain routing requires linear, state-dependent transaction signing, adding vital seconds of exposure to price degradation and front-running bots.
To achieve true capital optimization, the system architecture has to eliminate these structural bottlenecks entirely. This is where @GeniusOfficial introduces a fundamental shift through parallel Multi-Party Computation (#MPC ) execution pipelines.
Instead of processing complex multi-route trades sequentially, the terminal breaks down the transaction payload into distributed, cryptographic shares. By running these cryptographic pieces simultaneously across isolated execution nodes, the terminal can authorize and settle a split order across disparate chains (like #solana , #bnb Chain, and Base) in a single unified execution cycle.
For anyone tracking the long-term structural value of $GENIUS , this isn't just a minor optimization—it’s a defensive moat. By minimizing cross-chain signing latency, the platform drastically shrinks the execution window where MEV bots can exploit slippage. True institutional-grade decentralized trading isn't just about aggregating deep liquidity; it’s about moving that liquidity faster than the predatory bots scanning the mempool. #genius
129

Sui ecosystem privacy layer gets an upgrade: Seal MPC officially goes live on the mainnet.
Seal is positioned as a programmable access layer for data, AI, and digital assets. The highlight of this update is the flexibility in deployment—developers can choose to use standalone key servers, an MPC committee, or a hybrid of both, creating stronger trust assumptions.
The first mainnet MPC committee employs a 5-of-8 threshold scheme, composed of 8 node operators: Mysten Labs, Unconfirmed Labs, H2O Nodes, Ruby Nodes, Natsai, Triton One, Nodeinfra, and OverclockSol, significantly enhancing signature security and resistance to collusion.
My take: In the current climate where AI agents and on-chain data authorization scenarios are heating up, whoever cracks the "fine-grained access control + trustlessness" puzzle holds the key to the next narrative. Seal's approach of making MPC a plug-and-play module rather than a single fixed solution is much more friendly for real business applications.
It’s worth keeping an eye on whether the Sui ecosystem will see more AI and RWA projects integrating Seal for key management and data authorization.
#Sui #Seal #MPC $SUI
224

🔐 Multi-Party Computation (MPC) Wallets: An Evolution in Crypto Security
Multi-party computation (MPC) wallets are seeing growing interest as a potential alternative to traditional seed phrases for storing cryptocurrencies. This technology aims to enhance security by splitting the private key into multiple parts and distributing them, reducing single points of failure and hacking risks.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#MPC #CryptoSecurity #WalletTech #Blockchain
📰 Source: bitcoinfoundation.org
38
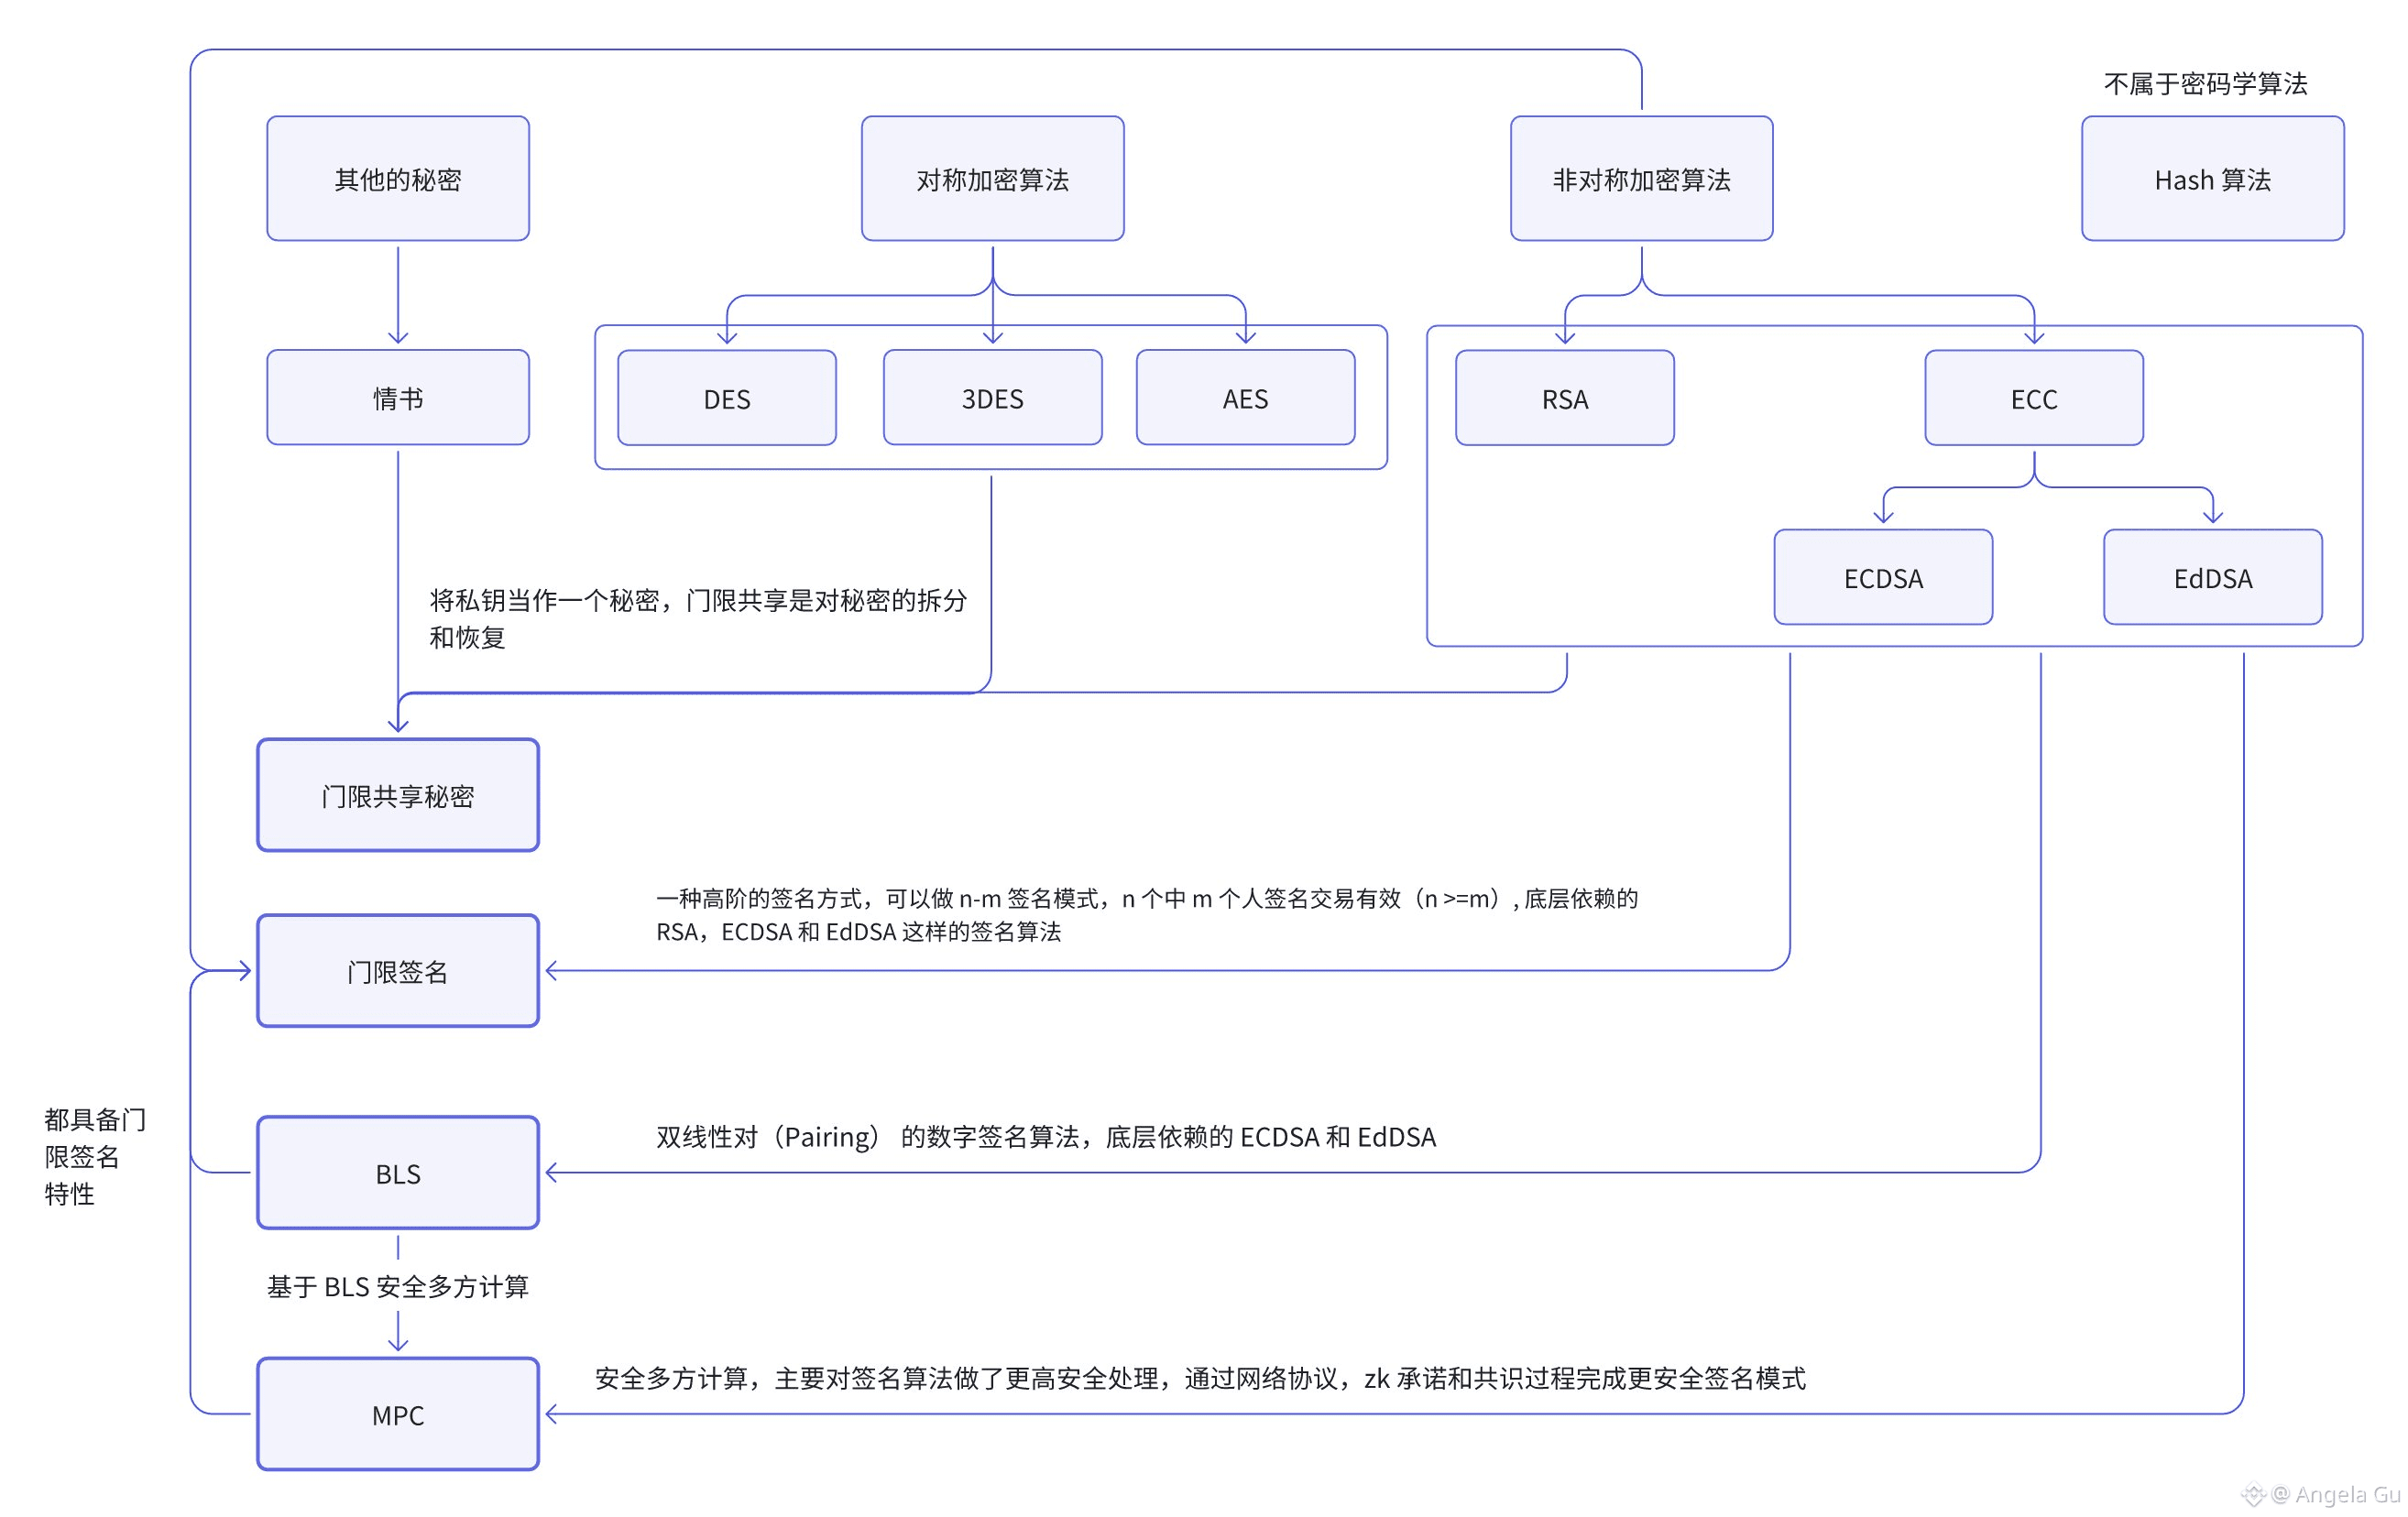
A lot of folks see cryptographic algorithms as mere 'knowledge points', but in Web3, they're actually part of a skillset:
Symmetric Encryption (AES)
👉 responsible for 'speed'
Asymmetric Encryption (RSA / ECC)
👉 responsible for 'identity'
Hash
👉 responsible for 'immutability'
But the real backbone supporting blockchain security is this evolutionary chain:
Private Key → Threshold Secret Sharing → Threshold Signature → BLS → MPC
This is a path from 'individual control' to 'collective consensus security'.
Threshold Secret Sharing breaks a private key into n parts, where any k parts can restore it.
👉 Solves: The private key is no longer controlled by just one person.
Threshold Signature (Threshold Signature) allows k individuals among n to collectively sign, appearing on-chain as 'one signature'.
👉 Security shifts from 'single point' to 'organizational level'.
BLS Signature: Based on bilinear pairing, inherently supports signature aggregation and threshold characteristics, serving as core infrastructure for PoS, public chain consensus, DA, and Rollup validator systems.
MPC (Multi-Party Computation): Not a new signing algorithm, but rather: completing signature calculations without reconstructing the complete private key. Combining network protocols, ZK, and consensus mechanisms transforms 'signing rights' into a 'collaborative process'.
In conclusion:
ECDSA / EdDSA solve 'I can sign'
Threshold Signatures solve 'we sign together'
BLS solves 'many sign efficiently'
MPC solves 'everyone signs but no one actually holds the complete private key'
This is why exchanges, custodians, L2s, validators, and Rollup Sequencers are moving from the 'private key' era to a security architecture of Threshold + BLS + MPC.
Cryptography isn't just algorithms; it's also the design of organizational security structures. #密码学 #安全 #MPC
174

·
--
The Sui mainnet is rolling out a crucial infrastructure upgrade — Seal MPC is officially live.
As a programmable access layer geared towards data, AI, and digital assets, Seal is offering developers three choices: independent key servers, MPC committees, or a hybrid deployment of both. Behind this flexibility lies a stronger trust assumption — you can define your own security boundaries based on the application scenario.
The first mainnet MPC committee adopts a 5-of-8 threshold scheme, and the lineup of node operators is quite noteworthy: Mysten Labs, Unconfirmed Labs, H2O Nodes, Ruby Nodes, Natsai, Triton One, Nodeinfra, and OverclockSol. With decentralization at play, any three parties cannot collude to unlock the keys.
Why is this worth watching?
With the rise of on-chain AI, privacy computing, and custodianship of confidential assets, single-point key management is no longer sufficient. The MPC committee model spreads trust across multiple independent operators, while hybrid deployment allows projects to find a balance between decentralization and performance.
For the $SUI ecosystem, this marks a step from 'programmable assets' to 'programmable access control'. As the access layer thickens, the boundaries for applications on top can naturally expand.
Next, it will be interesting to observe how many new projects will be built on Seal and whether the committee nodes will further expand.
#Sui #Seal #MPC
226

·
--
Threshold Escrow Is Moving from On-Chain Assets to Online Payment Infrastructure2026-08-23
Last week’s lesson was that key security can’t be judged by a one-time generation or a one-time update. Today’s signal is different at another layer: threshold signatures are being embedded into more complex, continuously online payment protocols, and the protocol’s security boundaries must be redesigned as well.
According to an IACR ePrint report, a new paper starts from Lightning’s real-world constraints: the channel endpoint depends on a single online key, and existing on-chain Bitcoin threshold signature experience cannot directly solve Lightning’s message-flow problem. The paper proposes nested threshold multisignatures and uses an Iceberg construction as an example, so that the Lightning side runs as a threshold group, while the counterparty still sees it as a standard MuSig2 participant.
Threshold Escrow Is Moving from On-Chain Assets to Online Payment Infrastructure
2026-08-23
Last week’s lesson was that key security can’t be judged by a one-time generation or a one-time update. Today’s signal is different at another layer: threshold signatures are being embedded into more complex, continuously online payment protocols, and the protocol’s security boundaries must be redesigned as well.
According to an IACR ePrint report, a new paper starts from Lightning’s real-world constraints: the channel endpoint depends on a single online key, and existing on-chain Bitcoin threshold signature experience cannot directly solve Lightning’s message-flow problem. The paper proposes nested threshold multisignatures and uses an Iceberg construction as an example, so that the Lightning side runs as a threshold group, while the counterparty still sees it as a standard MuSig2 participant.
145
·
--
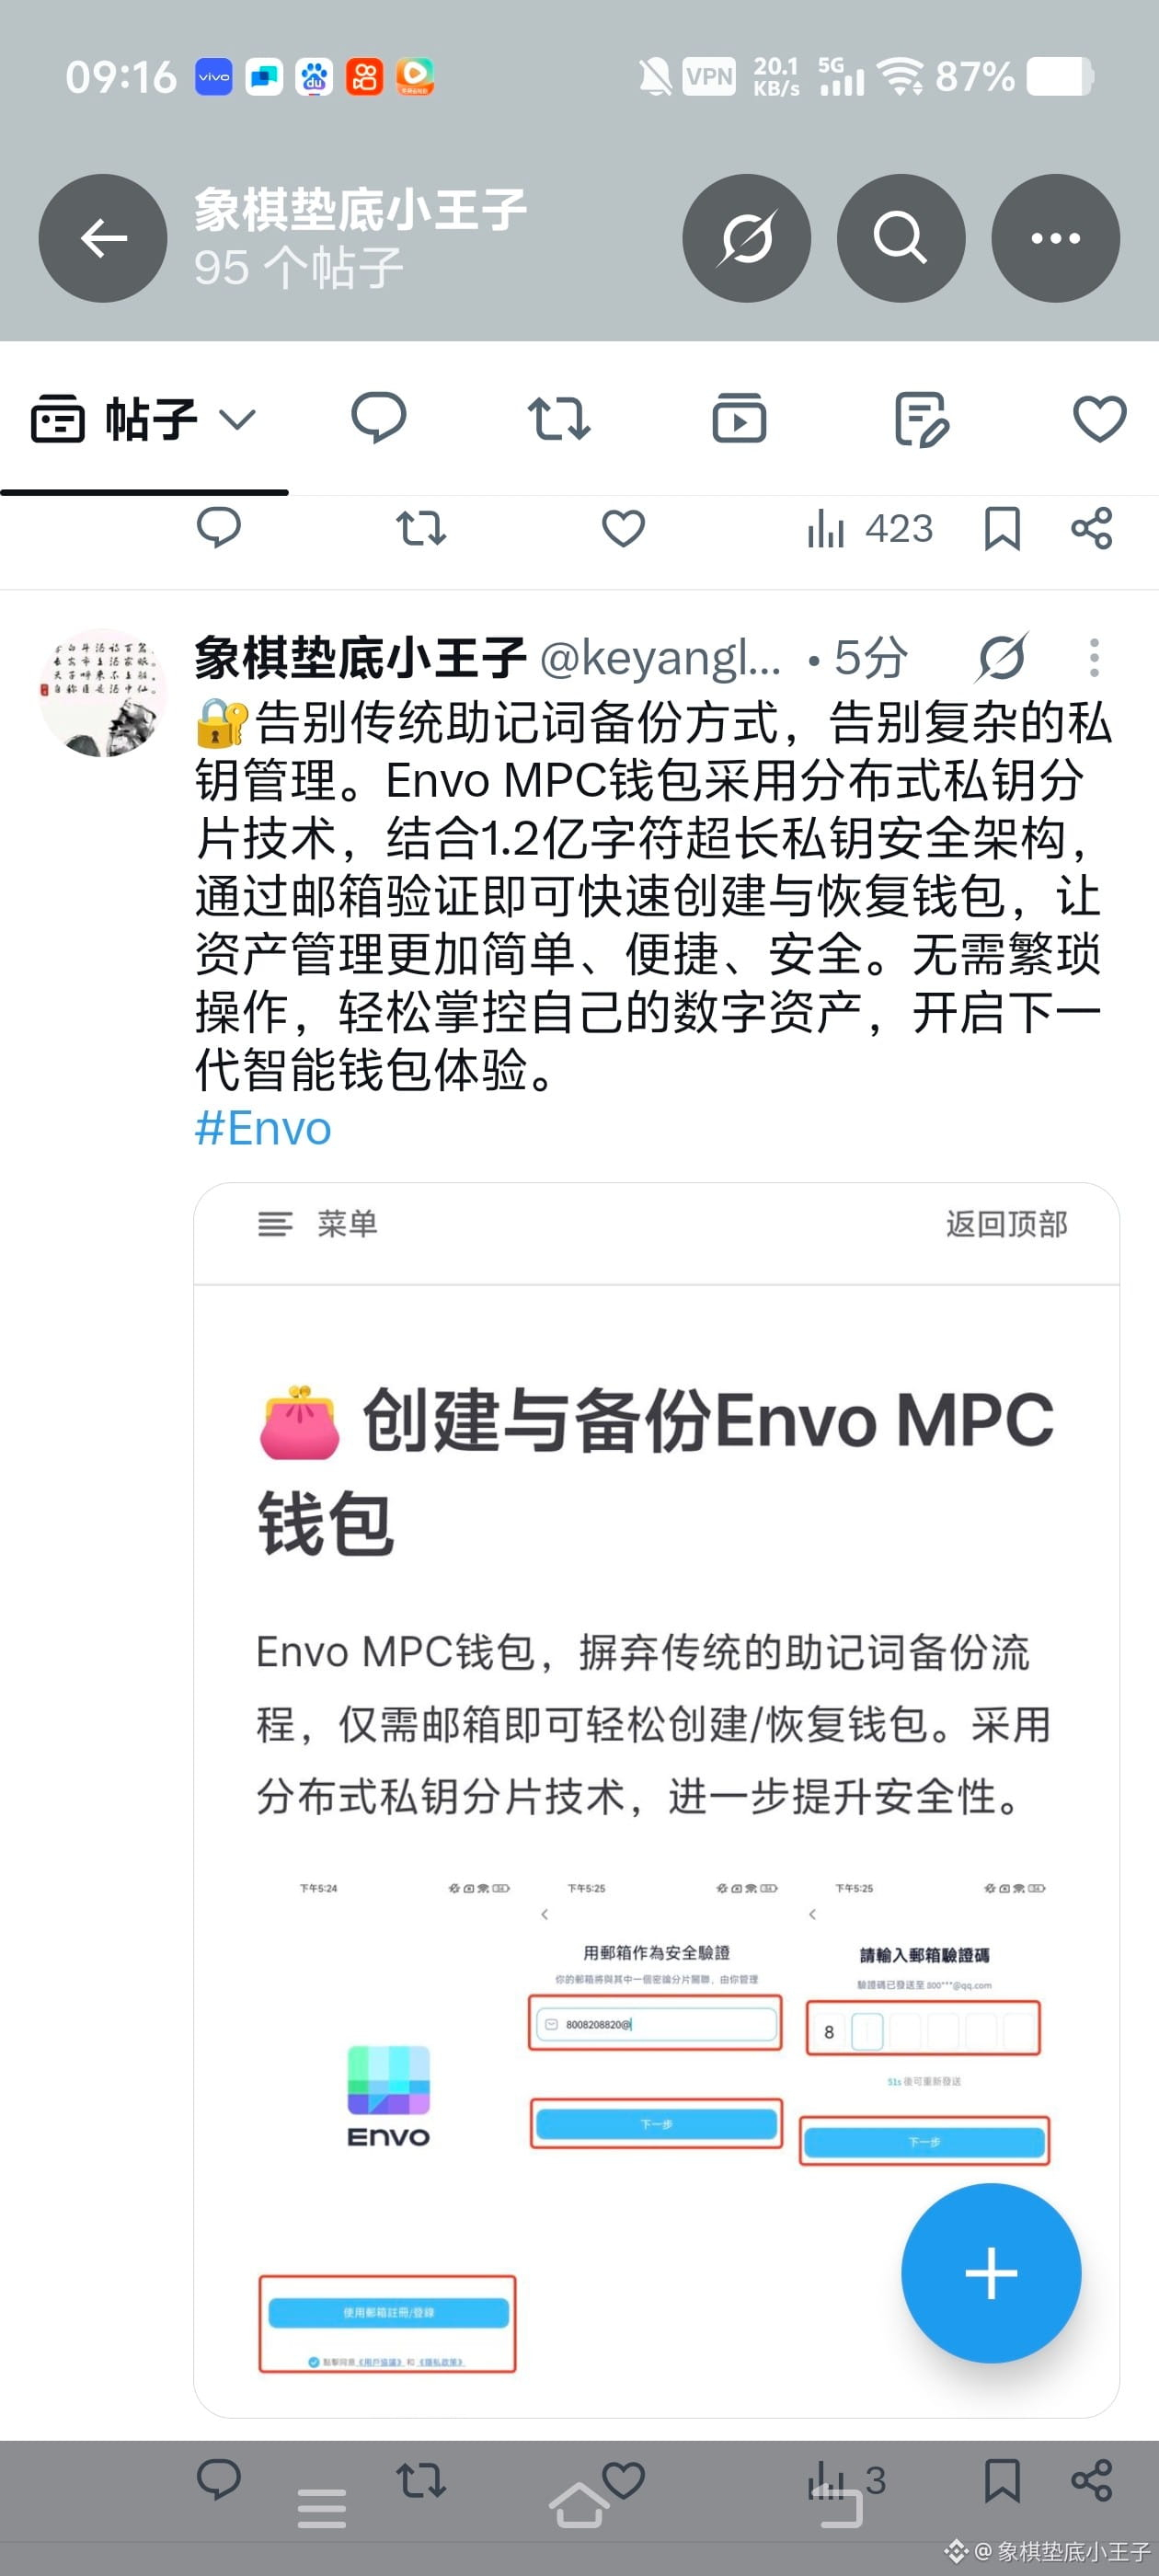
Your assets need a more powerful guardian.🛡️
The Envo MPC wallet breaks through the limitations of traditional wallets with MPC technology + a 120-million-character ultra-long private-key system, offering a safer and smarter asset protection solution. Simple backup, secure storage—so every on-chain operation feels more安心.
#Envo #MPC
The Envo MPC wallet breaks through the limitations of traditional wallets with MPC technology + a 120-million-character ultra-long private-key system, offering a safer and smarter asset protection solution. Simple backup, secure storage—so every on-chain operation feels more安心.
#Envo #MPC
1
81
·
--
After RFI and Safeheron launch their quantum digital asset pilot this week, participating institutions will test wallet generation and on-chain transfers on the NEAR testnet. Its signature layer uses the ML-DSA-65 specified in the NIST FIPS 204 standard and is integrated with a multiparty computation (MPC) process.
The technical focus of this test is not to prove that quantum computing can already break existing wallets. Instead, it verifies whether a wallet can switch its cryptographic algorithm without rebuilding the entire custodial infrastructure.
Conventional wallets typically bind the address, private key format, transaction encoding, and signature verification rules to the same elliptic-curve cryptography stack. After migrating to ML-DSA, the public key and signature sizes will increase significantly. Hardware security modules (HSMs), MPC nodes, transaction parsers, and on-chain verification logic all need to be updated in parallel. Simply replacing the signing function in the client is not enough to complete the migration.
MPC also does not automatically provide quantum security. What it addresses is the problem that the private key does not appear as a single complete point. If the parties still jointly execute a traditional signature algorithm, the underlying mathematical assumptions do not change.
This pilot incorporates post-quantum signatures directly into the distributed key generation and signing workflow. It tests the full key lifecycle, including key generation, share storage, joint signing, and on-chain verification.
Post-quantum wallets need to have “cryptographic agility”: accounts can upgrade the signature scheme, old assets can be migrated, new and old algorithms can coexist during the transition period, and recovery and auditing processes remain effective.
The real engineering challenge is not generating a new key, but securely updating the keys across the entire authorization chain.
#钱包技术 #后量子密码 #MPC
205
·
--
Blockchain did not bypass the basic boundaries of MPC, and regulation did not bypass record control2026-09-04
Two signals today: one from cryptography research, and one from U.S. securities regulation. Blockchain can provide persistence and finality, but it does not automatically change the classical fault-tolerance threshold for asynchronous MPC. Meanwhile, the SEC has proposed updating the rules for registered transfer agents, bringing electronic records, blockchain records, and risk management under the same modernized framework. [1][2]
According to IACR ePrint 2026/1860, researchers separately analyze asynchronous verifiable secret sharing and asynchronous multi-party computation in blockchain hybrid models. The paper points out that in the absence of a trusted setup, or when relying only on the Minicrypt assumption, asynchronous MPC is still subject to the classical fault-tolerance boundary constraints. Under a public-key assumption with a trusted setup, the authors construct a scheme that tolerates Byzantine adversaries and make the on-chain communication complexity independent of the circuit size. [1]
Blockchain did not bypass the basic boundaries of MPC, and regulation did not bypass record control
2026-09-04
Two signals today: one from cryptography research, and one from U.S. securities regulation. Blockchain can provide persistence and finality, but it does not automatically change the classical fault-tolerance threshold for asynchronous MPC. Meanwhile, the SEC has proposed updating the rules for registered transfer agents, bringing electronic records, blockchain records, and risk management under the same modernized framework. [1][2]
According to IACR ePrint 2026/1860, researchers separately analyze asynchronous verifiable secret sharing and asynchronous multi-party computation in blockchain hybrid models. The paper points out that in the absence of a trusted setup, or when relying only on the Minicrypt assumption, asynchronous MPC is still subject to the classical fault-tolerance boundary constraints. Under a public-key assumption with a trusted setup, the authors construct a scheme that tolerates Byzantine adversaries and make the on-chain communication complexity independent of the circuit size. [1]
114

·
--
Verified
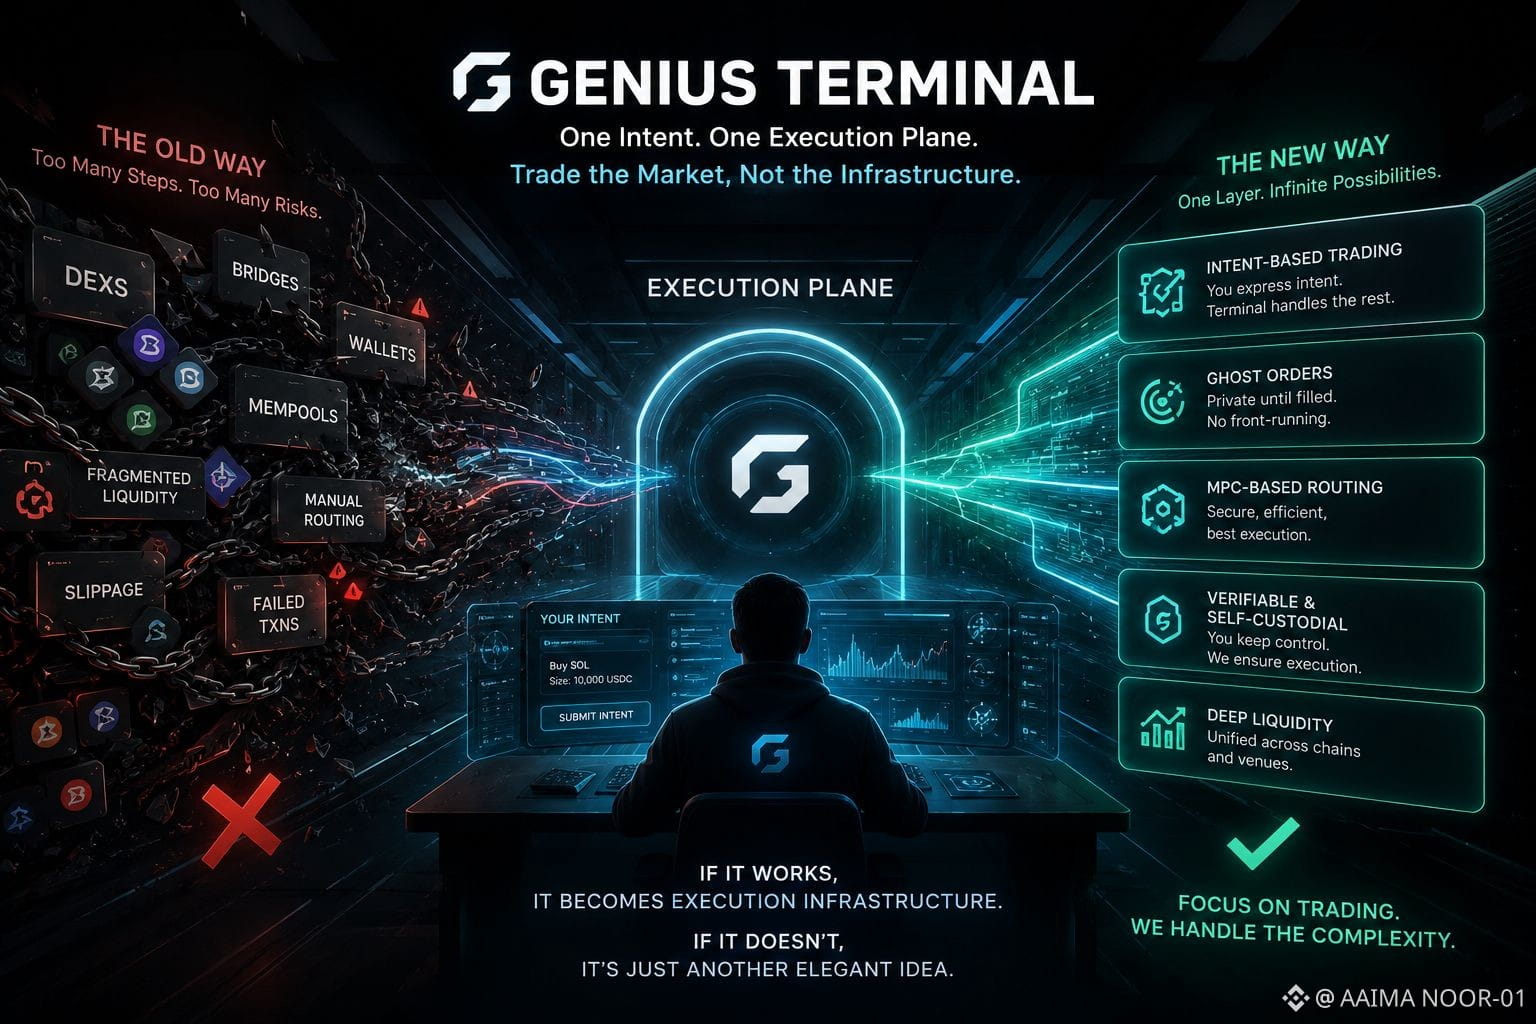
#genius $GENIUS Genius Terminal looks like a serious attempt to compress the mess of on-chain trading into a single execution layer.
Instead of forcing users to deal with DEXs, bridges, wallets, and mempools separately, it shifts everything into an “execution plane” where you interact through intent, not infrastructure. Ghost Orders and MPC-based routing are the core ideas here—not just UX upgrades, but a change in how exposure itself is handled.
What I find interesting isn’t the feature list, but the direction: hiding operational complexity while still trying to keep things verifiable and self-custodial.
That said, I’m cautious. Private execution always creates a tension—less transparency in a system that was built on openness. The real question is whether it can stay fair and liquid when things get volatile and high-volume.
If it works, it’s not just another trading interface—it becomes execution infrastructure.
If it doesn’t, it’s just another elegant idea that couldn’t survive real market stress.
#DeFi #Blockchain #MPC
@GeniusOfficial
$GENIUS
#genius
{future}(GENIUSUSDT)
#genius $GENIUS Genius Terminal looks like a serious attempt to compress the mess of on-chain trading into a single execution layer.
Instead of forcing users to deal with DEXs, bridges, wallets, and mempools separately, it shifts everything into an “execution plane” where you interact through intent, not infrastructure. Ghost Orders and MPC-based routing are the core ideas here—not just UX upgrades, but a change in how exposure itself is handled.
What I find interesting isn’t the feature list, but the direction: hiding operational complexity while still trying to keep things verifiable and self-custodial.
That said, I’m cautious. Private execution always creates a tension—less transparency in a system that was built on openness. The real question is whether it can stay fair and liquid when things get volatile and high-volume.
If it works, it’s not just another trading interface—it becomes execution infrastructure.
If it doesn’t, it’s just another elegant idea that couldn’t survive real market stress.
#DeFi #Blockchain #MPC
@GeniusOfficial
$GENIUS
#genius
38
20
736

INSTITUTIONAL GRADE SECURITY FLIPS THE SCRIPT AS BIOMETRIC MPC WALLETS GO LIVE FOR $ETH ! 🔒
Smart money infrastructure just took a major leap forward during TOKEN2049 week. ChainIT released its production-ready organizational MPC wallets, eliminating password vulnerabilities by tying biometric liveness directly to transaction-specific signing authorities. 🦈
Instead of static passphrases that can be phished, isolated dual enclave tech inside AWS Nitro verifies member identity and explicit permissions before any signature executes on $ETH -compatible chains. 📊 This bridges institutional treasury governance with agentic Web3 commerce without ever exposing full private keys. 💡
With passwordless liveness checks setting a new security standard for corporate treasuries, are you holding funds on legacy setups or moving toward biometric MPC control? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Web3 #Security #TOKEN2049 #MPC
🔥 💎
28

·
--
🚨 INSTITUTIONAL INFRASTRUCTURE SHIFT: $CHAINIT UNVEILS MPC WALLETS FOR AGENTIC COMMERCE 🛡️
Smart money capital demands institutional-grade security before committing serious liquidity to agentic Web3 frameworks. 🦈 $CHAINIT is addressing key execution risks by launching dual-enclave MPC wallets that integrate biometric identity verification directly into transaction-level authority checks.
By eliminating static passphrases and enforcing single-use, time-bound approvals, this architecture plugs major structural vulnerabilities in enterprise treasury management across $ETH compatible chains. 🔒 This focus on provable authority establishes a vital foundation as automated AI agents begin executing high-value transactions. 📊
💬 Will biometrically governed MPC wallets become the standard protocol for institutional Web3 treasuries this year? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #CHAINIT #Web3 #CryptoSecurity #MPC #Infrastructure
🔒 💎
30
·
--
MPC Does Not Replace PolicyMulti-party computation can remove one complete private key as a single point of failure. Several participants hold separate shares and cooperate to produce one valid signature only when the threshold is met.
That is valuable, but the threshold is not the complete security model.
The operational question is what causes those shares to participate. If an internal service can create a signing request without passing the expected checks, or if the signers accept a vague instruction that is not bound to the exact transaction, the system can produce a cryptographically valid signature for an unauthorized action.
A serious MPC design should bind approval to the chain, destination, value, calldata, fees, nonce policy and expiry. Signers should verify the approval bundle before participating. Shares should be separated across real failure domains, not placed under one cloud account, one administrator or one vendor-controlled path.
Policy changes need stronger controls than routine transactions. Emergency recovery should be slower, separately governed and tested. Monitoring should compare approved intent with the transaction that was actually broadcast.
MPC protects key control. It does not automatically prove that the request is legitimate or economically safe.
TokenToolHub explains threshold signing, policy bypass, share refresh, monitoring and recovery design:
https://tokentoolhub.com/multi-party-computation-mpc-web3/
#CryptoSecurity #MPC #blockchain #Web3 #wallets
MPC Does Not Replace Policy
Multi-party computation can remove one complete private key as a single point of failure. Several participants hold separate shares and cooperate to produce one valid signature only when the threshold is met.
That is valuable, but the threshold is not the complete security model.
The operational question is what causes those shares to participate. If an internal service can create a signing request without passing the expected checks, or if the signers accept a vague instruction that is not bound to the exact transaction, the system can produce a cryptographically valid signature for an unauthorized action.
A serious MPC design should bind approval to the chain, destination, value, calldata, fees, nonce policy and expiry. Signers should verify the approval bundle before participating. Shares should be separated across real failure domains, not placed under one cloud account, one administrator or one vendor-controlled path.
Policy changes need stronger controls than routine transactions. Emergency recovery should be slower, separately governed and tested. Monitoring should compare approved intent with the transaction that was actually broadcast.
MPC protects key control. It does not automatically prove that the request is legitimate or economically safe.
TokenToolHub explains threshold signing, policy bypass, share refresh, monitoring and recovery design:
https://tokentoolhub.com/multi-party-computation-mpc-web3/
#CryptoSecurity #MPC #blockchain #Web3 #wallets
106
·
--
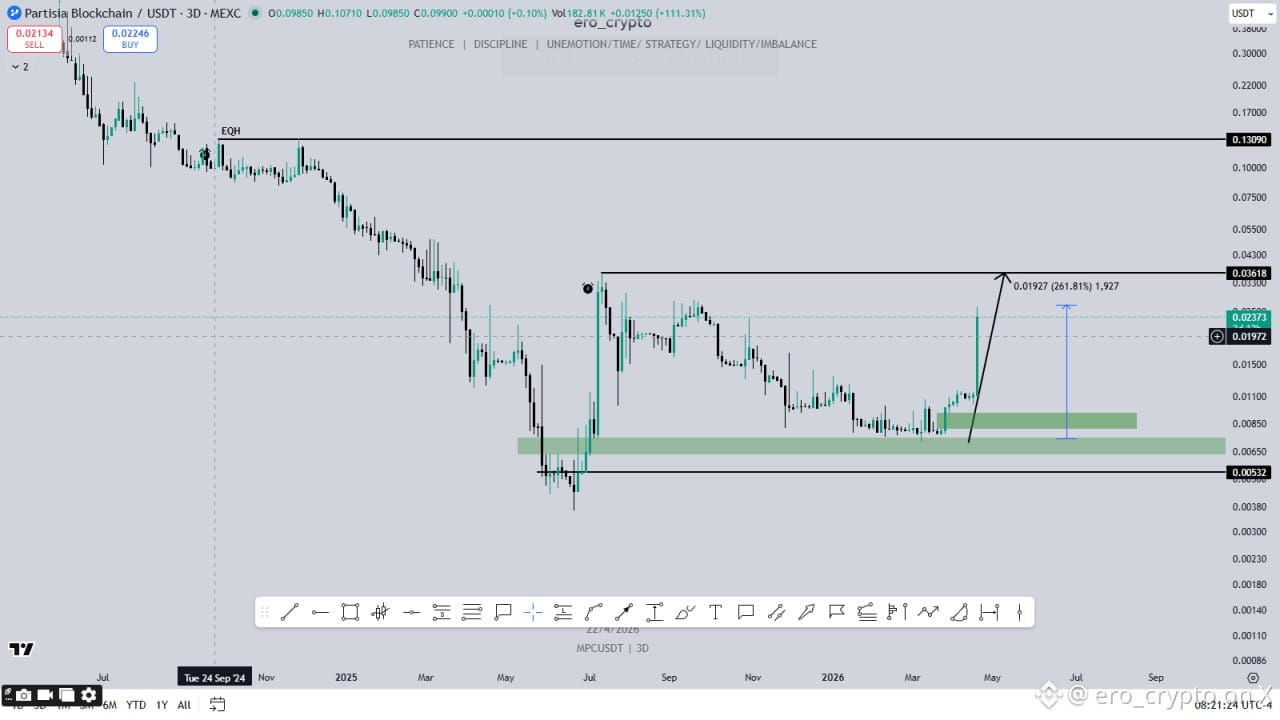
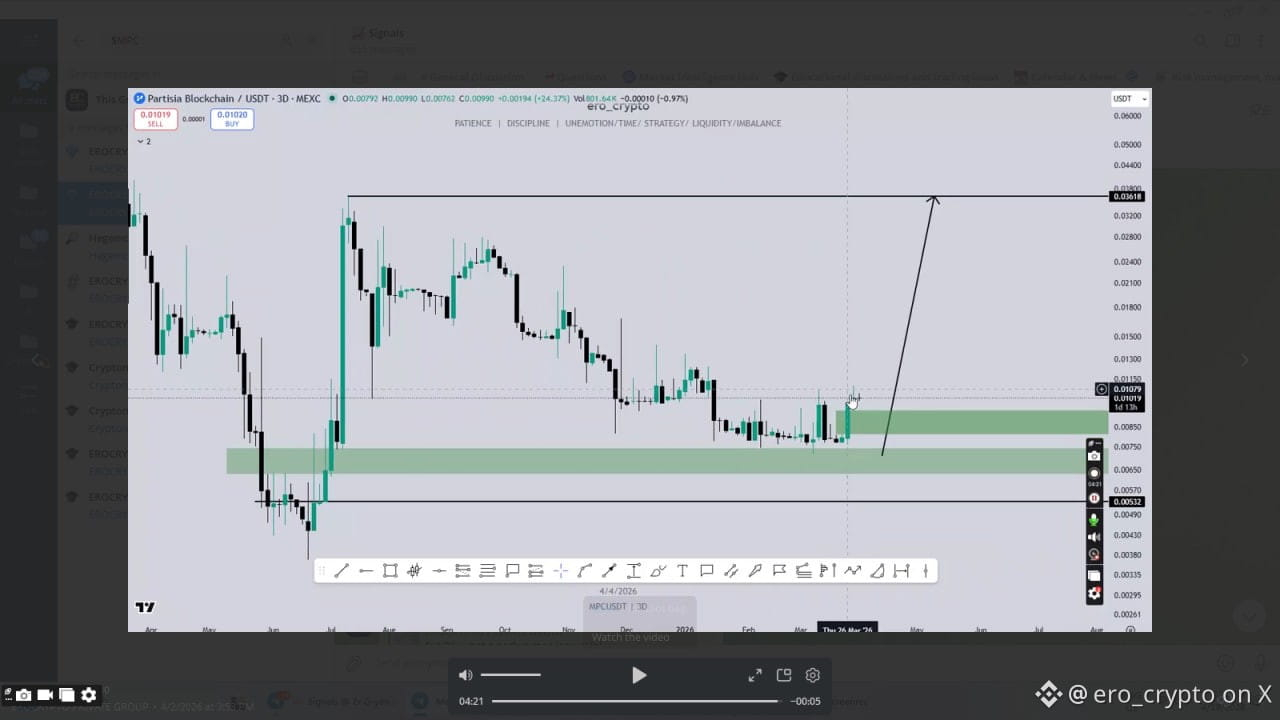
$MPC/ #MPC / @partisiampc - spot bag 260% up after my tweet
1st pic. from my premium video posted on April 2
My premium members always a few steps ahead of 99%
Hit follow here, on X and join my TG channel for Calls, TA and insights like this .
$MPC/ #MPC / @partisiampc - spot bag 260% up after my tweet
1st pic. from my premium video posted on April 2
My premium members always a few steps ahead of 99%
Hit follow here, on X and join my TG channel for Calls, TA and insights like this .
1st pic. from my premium video posted on April 2
My premium members always a few steps ahead of 99%
Hit follow here, on X and join my TG channel for Calls, TA and insights like this .
69

1
402
·
--
The attack surface of a hardware wallet isn’t just inside the device2026-08-17 · Observations on self-custody and key security
No key leakage does not mean there is no risk. According to SafePal’s disclosure on August 16, its order-tracking plugin has an authorization flaw that, under certain conditions, could allow an unauthorized party to access other customers’ order information. Affected data includes name, email, shipping address, phone number, and purchase details, impacting approximately 39,798 customers.
SafePal states that the event does not involve a mnemonic phrase, private key, wallet password, bank card information, or government-issued identification documents, and there is no evidence showing that the wallet or funds were compromised as a result. However, order data turns the fact that “someone owns a hardware wallet” into a profile that can be used for targeted phishing: attackers know how to contact them, where the hardware might be shipped, and how to disguise themselves using after-sales support, replacement services, or firmware reminders.
The attack surface of a hardware wallet isn’t just inside the device
2026-08-17 · Observations on self-custody and key security
No key leakage does not mean there is no risk. According to SafePal’s disclosure on August 16, its order-tracking plugin has an authorization flaw that, under certain conditions, could allow an unauthorized party to access other customers’ order information. Affected data includes name, email, shipping address, phone number, and purchase details, impacting approximately 39,798 customers.
SafePal states that the event does not involve a mnemonic phrase, private key, wallet password, bank card information, or government-issued identification documents, and there is no evidence showing that the wallet or funds were compromised as a result. However, order data turns the fact that “someone owns a hardware wallet” into a profile that can be used for targeted phishing: attackers know how to contact them, where the hardware might be shipped, and how to disguise themselves using after-sales support, replacement services, or firmware reminders.
84
·
--
Robinhood August Data: Crypto Trading Rebounds, Event Contracts Still Amplifying2026-09-22
This isn’t a sudden development today; it’s the August operating data that Robinhood released on September 10. The announcement shows that in August, crypto notional trading volume was $17.5 billion, up 61% quarter over quarter, but down 38% year over year. Of that, crypto notional trading volume on the Robinhood App was $7.4 billion, up 72% quarter over quarter, but down 46% year over year.
Another set of data makes it easier to understand how users perceive the product structure: in August, event-contract trading volume was 4.7 billion shares, up about 15x year over year, but down 23% quarter over quarter. This means that “trading activity” can’t be judged by a single total figure alone—different asset classes and statistical methodologies can produce completely different readings.
Robinhood August Data: Crypto Trading Rebounds, Event Contracts Still Amplifying
2026-09-22
This isn’t a sudden development today; it’s the August operating data that Robinhood released on September 10. The announcement shows that in August, crypto notional trading volume was $17.5 billion, up 61% quarter over quarter, but down 38% year over year. Of that, crypto notional trading volume on the Robinhood App was $7.4 billion, up 72% quarter over quarter, but down 46% year over year.
Another set of data makes it easier to understand how users perceive the product structure: in August, event-contract trading volume was 4.7 billion shares, up about 15x year over year, but down 23% quarter over quarter. This means that “trading activity” can’t be judged by a single total figure alone—different asset classes and statistical methodologies can produce completely different readings.
81

Article
Interview with Adrienne Youngman, CEO of Partisia, about Multi-Party Computation (MPC) and Partisia.Partisia Blockchain (MPC) is redefining the crypto ecosystem with cutting-edge multi-party computation (MPC) technology that enables secure and privacy-preserving collaborations. Its scalable solutions are transforming DeFi, secure voting, and confidential computing. CEO Adrienne Youngman answered our questions about the MPC token and Partisia’s vision.
What drives Partia Blockchain, and what long-term impact does it aim to achieve?
Partisia Blockchain is to data what Bitcoin is to money: a revolution in trust and control.
Before Bitcoin, you had to entrust financial institutions with your money or hide it under the mattress. Similarly, before Partisia, you either shared your data indiscriminately or disconnected from the digital world entirely.
Using Multi-Party Computation (MPC), individuals and organizations can retain ownership of their data while enabling secure, selective interactions. For instance, a bank could perform a custom Know Your Customer (KYC) check that meets regulatory standards without requiring users to upload sensitive information into another opaque system.
Where Zero-Knowledge (ZK) Proofs allow you to query a single data point for a binary yes/no response, MPC enables queries across multiple secure data sources and supports rich computations.
Examples:
A ZK Proof could verify if someone holds a credential proving they’re over 18.MPC could calculate a credit score from encrypted financial data or run AI models on prompts containing an encrypted file for private information.Retaining ownership of data empowers us, enabling us to control what we reveal. At Partisia Blockchain, we enable data owners to safely embrace technological advances, for a more empowered digital future.
How does Partia Blockchain stand out in the competitive blockchain ecosystem?
Our unmatched expertise in privacy-enhancing technologies sets us apart.
One of our founders authored the first paper on Multi-Party Computation (MPC) in 1988 and co-invented the Merkle-Damgård hash function, a cornerstone of modern cryptography. Since then, we've published over 1,000 research papers and helped shape regulations like the European Digital Identity regulation (eIDAS) and emerging standards for tokenized real-world assets (ERC-3643).
For over 16 years, our development company has implemented privacy enhancing technologies at scale, delivering solutions for clients like the Danish government (Project Oscar), enterprises such as Bosch, and organizations like the Red Cross.
As AI continues its exponential growth, privacy-enhancing technology like MPC will be critical. Only Partisia combines the depth of expertise and technology necessary to empower developers to create the solutions that will re-empower humanity.
What mechanisms are in place to protect users' data and ensure platform security?
Partisia Blockchain employs advanced cryptographic techniques to secure data at every stage. MPC ensures data remains encrypted during computations, preventing unauthorized access while enabling seamless interactions. Combined with robust consensus protocols, these mechanisms deliver unparalleled data security without compromising usability.
Key Use Cases:
As blockchain expands into real-world use cases, MPC will play a pivotal role at that real-world intersect. This might include:
Sovereign Identity Solutions: increasing trust in decentralized environments.Privacy-Preserving Compliance: enabling KYC, KYB, and AML without compromising privacy.Confidential Data Sharing: enabling confidential information to come on-chain.
MPC allows data owners to retain custody of their information while selectively sharing insights and information with those who need them.
However, in the mid to long term, MPC’s greatest potential lies in its intersection with AI.
Our lack of concern about our digital footprint could have grave consequences in a world where data can be scraped, organised, and analysed like never before. When it can be harnessed within models that increasingly control access to services and products. As AI evolves, retaining control over our digital footprint will be essential.
Privacy Preserving Inference could enable us to interact with models on encrypted data - gaining the insight we need without surrendering sensitive information In future we may even be able to train AI models on encrypted datasets, unlocking innovation without sacrificing privacy.
What consensus protocol powers Partia Blockchain, and why was it chosen?
Partisia Blockchain utilizes the FastTrack consensus protocol, designed for high-speed transaction finalization and robust network security.
FastTrack employs an optimistic "trust but verify" model. A designated proposer generates blocks that are immediately executed by nodes once signed. When two-thirds of nodes sign off, the network achieves Proof-of-Justification (PoJ), ensuring block validity.
This approach delivers real-time transaction finalization while addressing limitations of traditional Byzantine Fault Tolerance (BFT) systems, offering both speed and scalability.
How does the platform handle high transaction volumes and ensure seamless scalability?
Partisia Blockchain’s complete sharding architecture enables each shard to operate as an independent blockchain, processing transactions in parallel.
Horizontal scaling ensures new shards can be added dynamically to meet demand, maintaining performance even during peak activity. Combined with the FastTrack consensus protocol, this design delivers unparalleled scalability and throughput, ensuring seamless user experiences under heavy load.
Which partnerships have been crucial, and how do they enhance the ecosystem?
Partisia Blockchain was designed to deliver MPC-as-a-Service across chains. We support multiple tokens for gas (e.g., POL, ETH, wBTC, BNB, USDC, USDT), enabling projects to leverage our privacy infrastructure while driving value to the primary chain.
Examples of collaboration:
Profila (built on Cardano): Utilizing Partisia for privacy-preserving data interactions.
Varmeta (on BNB): Implementing data privacy solutions for their ecosystem.
For native projects, we’ve partnered with DeFi builders, including:
zkCross: Launching a DEX.Boosty Labs: Developing a lending protocol.A liquid staking protocol (launching soon).
Our hybrid approach, combining private and public blockchain solutions through partnership with our Development Company (Partisia Inc), has also attracted large Web2 enterprise discussions. We anticipate announcing high-impact partnerships in the coming months.
What exciting developments or expansions can we expect in the near future?
The primary focus for the next 6 months is facilitating and accelerating adoption.
Key initiatives include:
Streamlining user journeys for node operations and delegated stakers.Relaunching documentation and toolkits to better empower developers.Following a successful proof of concept for running AI models on encrypted data, we’re expanding functionality and engaging with partners to explore new applications.
What initiatives are in place to empower developers and engage the community
We’re currently reviewing and expanding our community initiatives, with significant announcements expected before Christmas.
#MPC #Partisia #PartisiaBlockchain #AdrienneYoungman #MultiPartyComputation
Interview with Adrienne Youngman, CEO of Partisia, about Multi-Party Computation (MPC) and Partisia.
Partisia Blockchain (MPC) is redefining the crypto ecosystem with cutting-edge multi-party computation (MPC) technology that enables secure and privacy-preserving collaborations. Its scalable solutions are transforming DeFi, secure voting, and confidential computing. CEO Adrienne Youngman answered our questions about the MPC token and Partisia’s vision.
What drives Partia Blockchain, and what long-term impact does it aim to achieve?
Partisia Blockchain is to data what Bitcoin is to money: a revolution in trust and control.
Before Bitcoin, you had to entrust financial institutions with your money or hide it under the mattress. Similarly, before Partisia, you either shared your data indiscriminately or disconnected from the digital world entirely.
Using Multi-Party Computation (MPC), individuals and organizations can retain ownership of their data while enabling secure, selective interactions. For instance, a bank could perform a custom Know Your Customer (KYC) check that meets regulatory standards without requiring users to upload sensitive information into another opaque system.
Where Zero-Knowledge (ZK) Proofs allow you to query a single data point for a binary yes/no response, MPC enables queries across multiple secure data sources and supports rich computations.
Examples:
A ZK Proof could verify if someone holds a credential proving they’re over 18.MPC could calculate a credit score from encrypted financial data or run AI models on prompts containing an encrypted file for private information.Retaining ownership of data empowers us, enabling us to control what we reveal. At Partisia Blockchain, we enable data owners to safely embrace technological advances, for a more empowered digital future.
How does Partia Blockchain stand out in the competitive blockchain ecosystem?
Our unmatched expertise in privacy-enhancing technologies sets us apart.
One of our founders authored the first paper on Multi-Party Computation (MPC) in 1988 and co-invented the Merkle-Damgård hash function, a cornerstone of modern cryptography. Since then, we've published over 1,000 research papers and helped shape regulations like the European Digital Identity regulation (eIDAS) and emerging standards for tokenized real-world assets (ERC-3643).
For over 16 years, our development company has implemented privacy enhancing technologies at scale, delivering solutions for clients like the Danish government (Project Oscar), enterprises such as Bosch, and organizations like the Red Cross.
As AI continues its exponential growth, privacy-enhancing technology like MPC will be critical. Only Partisia combines the depth of expertise and technology necessary to empower developers to create the solutions that will re-empower humanity.
What mechanisms are in place to protect users' data and ensure platform security?
Partisia Blockchain employs advanced cryptographic techniques to secure data at every stage. MPC ensures data remains encrypted during computations, preventing unauthorized access while enabling seamless interactions. Combined with robust consensus protocols, these mechanisms deliver unparalleled data security without compromising usability.
Key Use Cases:
As blockchain expands into real-world use cases, MPC will play a pivotal role at that real-world intersect. This might include:
Sovereign Identity Solutions: increasing trust in decentralized environments.Privacy-Preserving Compliance: enabling KYC, KYB, and AML without compromising privacy.Confidential Data Sharing: enabling confidential information to come on-chain.
MPC allows data owners to retain custody of their information while selectively sharing insights and information with those who need them.
However, in the mid to long term, MPC’s greatest potential lies in its intersection with AI.
Our lack of concern about our digital footprint could have grave consequences in a world where data can be scraped, organised, and analysed like never before. When it can be harnessed within models that increasingly control access to services and products. As AI evolves, retaining control over our digital footprint will be essential.
Privacy Preserving Inference could enable us to interact with models on encrypted data - gaining the insight we need without surrendering sensitive information In future we may even be able to train AI models on encrypted datasets, unlocking innovation without sacrificing privacy.
What consensus protocol powers Partia Blockchain, and why was it chosen?
Partisia Blockchain utilizes the FastTrack consensus protocol, designed for high-speed transaction finalization and robust network security.
FastTrack employs an optimistic "trust but verify" model. A designated proposer generates blocks that are immediately executed by nodes once signed. When two-thirds of nodes sign off, the network achieves Proof-of-Justification (PoJ), ensuring block validity.
This approach delivers real-time transaction finalization while addressing limitations of traditional Byzantine Fault Tolerance (BFT) systems, offering both speed and scalability.
How does the platform handle high transaction volumes and ensure seamless scalability?
Partisia Blockchain’s complete sharding architecture enables each shard to operate as an independent blockchain, processing transactions in parallel.
Horizontal scaling ensures new shards can be added dynamically to meet demand, maintaining performance even during peak activity. Combined with the FastTrack consensus protocol, this design delivers unparalleled scalability and throughput, ensuring seamless user experiences under heavy load.
Which partnerships have been crucial, and how do they enhance the ecosystem?
Partisia Blockchain was designed to deliver MPC-as-a-Service across chains. We support multiple tokens for gas (e.g., POL, ETH, wBTC, BNB, USDC, USDT), enabling projects to leverage our privacy infrastructure while driving value to the primary chain.
Examples of collaboration:
Profila (built on Cardano): Utilizing Partisia for privacy-preserving data interactions.
Varmeta (on BNB): Implementing data privacy solutions for their ecosystem.
For native projects, we’ve partnered with DeFi builders, including:
zkCross: Launching a DEX.Boosty Labs: Developing a lending protocol.A liquid staking protocol (launching soon).
Our hybrid approach, combining private and public blockchain solutions through partnership with our Development Company (Partisia Inc), has also attracted large Web2 enterprise discussions. We anticipate announcing high-impact partnerships in the coming months.
What exciting developments or expansions can we expect in the near future?
The primary focus for the next 6 months is facilitating and accelerating adoption.
Key initiatives include:
Streamlining user journeys for node operations and delegated stakers.Relaunching documentation and toolkits to better empower developers.Following a successful proof of concept for running AI models on encrypted data, we’re expanding functionality and engaging with partners to explore new applications.
What initiatives are in place to empower developers and engage the community
We’re currently reviewing and expanding our community initiatives, with significant announcements expected before Christmas.
#MPC #Partisia #PartisiaBlockchain #AdrienneYoungman #MultiPartyComputation
4
968
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinSlipsBelow$80KAgain
27 views
3 Discussing
2
#StrategySkipsBitcoinPurchasesSpends$205MOnSTRCBuybacks
2,264 views
60 Discussing
3
#BitmineAdds10452ETH
21,876 views
415 Discussing
4
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
15,239 views
353 Discussing
5
#OCCUrgesCommunityBanksToEnterStablecoinPayments
12,035 views
211 Discussing
6
#RippleWinsFullApprovalAsNationalTrustBank
12,967 views
216 Discussing
7
#AkashSelectsSolanaAsMigrationTarget
8,688 views
107 Discussing
8
#OndoToOpenSubscriptionsForOpenAIPreIPOTokenizedNotes
466 views
21 Discussing
9
#AnthropicTTMRevenueGrewAbout1200%
65,665 views
643 Discussing
10
#AnthropicS1ExpectedToday
47,201 views
434 Discussing