

#lazarus
lazarus
Просмотров: 453,215
142 обсуждают
Популярные
Новые
·
--
🚨🚨 AO VIVO: BINANCE LIBERA SAQUES AGORA
Pare tudo que você está fazendo.
Domingo, 1º de Novembro de 2026 - A Binance acabou de confirmar:
✅ 90% dos $6.3B JÁ REPOSTOS (subiu de 80% ontem)
✅ $5.67B de $6.3B recuperados com dinheiro PRÓPRIO
✅ Top 10 moedas 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Snapshot de Proof-of-Reserves de ontem 00:00 UTC = 100%
✅ Prova ZK completa sai dia 3 de Nov - verificação pública
✅ $3B dos hackers congelados por Tether, Circle e parceiros
✅ SAFU sendo restaurado para $1B
O que aconteceu? Quinta, 29 Out, Lazarus Group (Coreia do Norte) invadiu. FBI + Secret Service entraram.
O que a Binance fez? Não passou prejuízo pro usuário. Pagou do bolso. $6.34B reservados.
Isso NUNCA aconteceu na história crypto. Nem FTX, nem Mt. Gox fizeram isso.
RETWEETA se você ainda confia na Binance 🟡
Fonte oficial: Binance X @ 08:15 AM hoje.
#Binance #BreakingNews #BTC #SAFU #Lazarus
🚨🚨 AO VIVO: BINANCE LIBERA SAQUES AGORA
Pare tudo que você está fazendo.
Domingo, 1º de Novembro de 2026 - A Binance acabou de confirmar:
✅ 90% dos $6.3B JÁ REPOSTOS (subiu de 80% ontem)
✅ $5.67B de $6.3B recuperados com dinheiro PRÓPRIO
✅ Top 10 moedas 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Snapshot de Proof-of-Reserves de ontem 00:00 UTC = 100%
✅ Prova ZK completa sai dia 3 de Nov - verificação pública
✅ $3B dos hackers congelados por Tether, Circle e parceiros
✅ SAFU sendo restaurado para $1B
O que aconteceu? Quinta, 29 Out, Lazarus Group (Coreia do Norte) invadiu. FBI + Secret Service entraram.
O que a Binance fez? Não passou prejuízo pro usuário. Pagou do bolso. $6.34B reservados.
Isso NUNCA aconteceu na história crypto. Nem FTX, nem Mt. Gox fizeram isso.
RETWEETA se você ainda confia na Binance 🟡
Fonte oficial: Binance X @ 08:15 AM hoje.
#Binance #BreakingNews #BTC #SAFU #Lazarus
Pare tudo que você está fazendo.
Domingo, 1º de Novembro de 2026 - A Binance acabou de confirmar:
✅ 90% dos $6.3B JÁ REPOSTOS (subiu de 80% ontem)
✅ $5.67B de $6.3B recuperados com dinheiro PRÓPRIO
✅ Top 10 moedas 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Snapshot de Proof-of-Reserves de ontem 00:00 UTC = 100%
✅ Prova ZK completa sai dia 3 de Nov - verificação pública
✅ $3B dos hackers congelados por Tether, Circle e parceiros
✅ SAFU sendo restaurado para $1B
O que aconteceu? Quinta, 29 Out, Lazarus Group (Coreia do Norte) invadiu. FBI + Secret Service entraram.
O que a Binance fez? Não passou prejuízo pro usuário. Pagou do bolso. $6.34B reservados.
Isso NUNCA aconteceu na história crypto. Nem FTX, nem Mt. Gox fizeram isso.
RETWEETA se você ainda confia na Binance 🟡
Fonte oficial: Binance X @ 08:15 AM hoje.
#Binance #BreakingNews #BTC #SAFU #Lazarus
23
·
--
🚨 Did Binance really absorb a $6.3B loss? Withdrawals may reopen today, but understand this first;
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
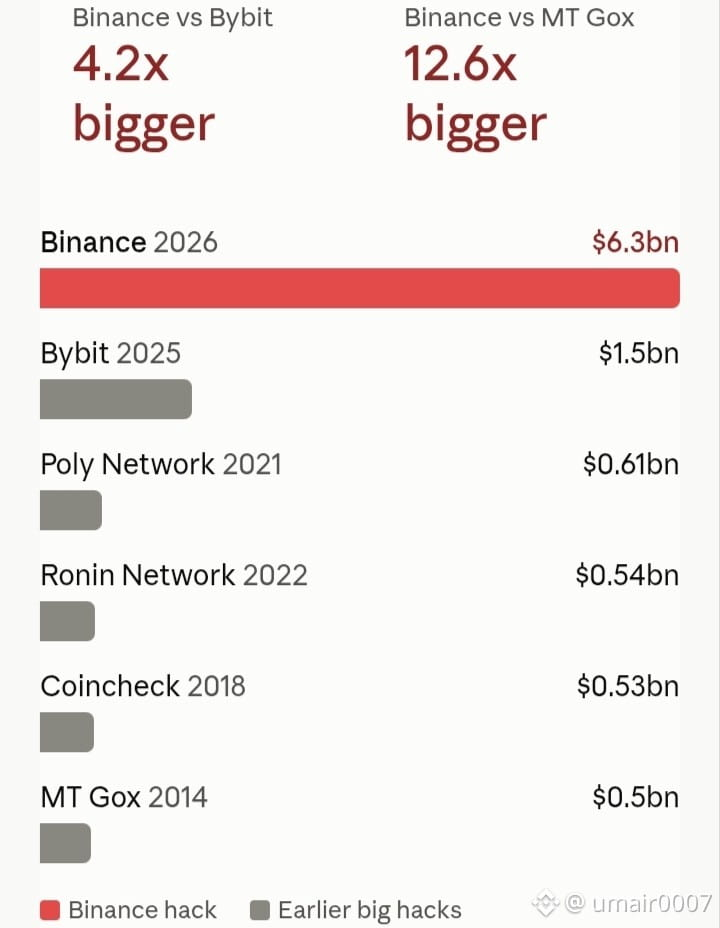
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
🚨 Did Binance really absorb a $6.3B loss? Withdrawals may reopen today, but understand this first;
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
94
·
--
Padfoot:
韭菜负责充值,黑客负责提现,真成反向打工了😂 不过BTC跌不跌还得看资金,别把所有阴线都算黑客头上。
1
7.3k
·
--
Падение
🇰🇵 JUST IN: North Korea is the prime suspect in the record $6 billion Binance hack, per CNN and blockchain investigators.
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
🇰🇵 JUST IN: North Korea is the prime suspect in the record $6 billion Binance hack, per CNN and blockchain investigators.
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
1
64
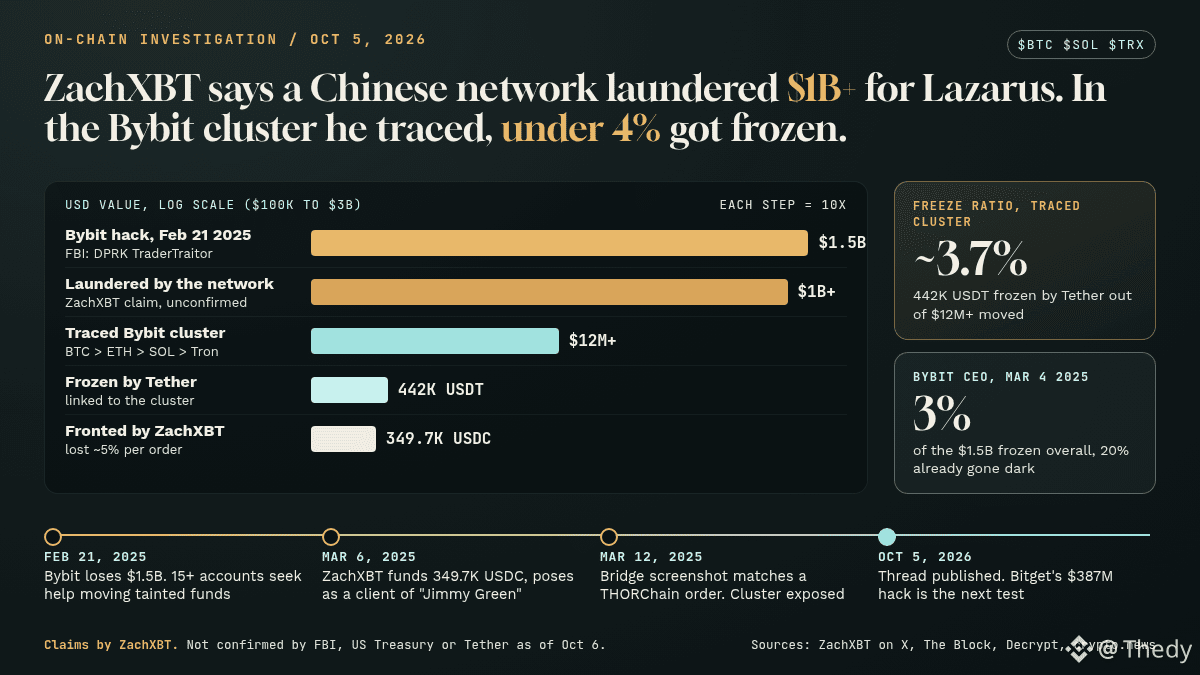
ZachXBT spent $349,700 of his own money to go undercover inside a crypto laundering ring.
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
ZachXBT spent $349,700 of his own money to go undercover inside a crypto laundering ring.
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
1
107


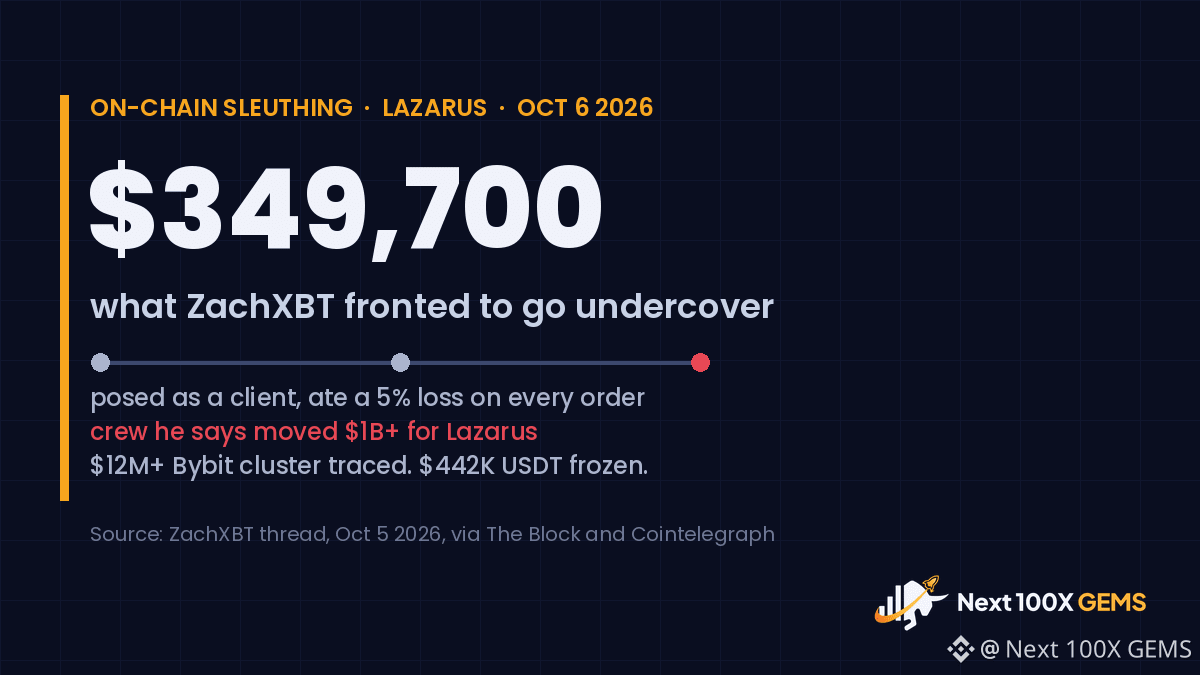
ZachXBT says he put up $349,700 and took a 5% loss on every order to pose as a client of a Chinese laundering crew.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
ZachXBT says he put up $349,700 and took a 5% loss on every order to pose as a client of a Chinese laundering crew.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
1
1.4k

·
--
Рост
ZachXBT платив відмивачам Lazarus 5% з кожної угоди. сам, своїми грошима
з кінця лютого 2025 він грав клієнта
завів у їхню мережу 349700 $USDC
{future}(USDCUSDT)
і на кожному ордері свідомо губив 5%, поки йому не почали довіряти
довіра там, виходить, коштує 5%. заплатив - і тобі самі розказують, куди йдуть крадені гроші
шо вийшло:
- кластер з понад $12 млн коштів з хаку Bybit
- Tether заморозив 442000 USDT
за його оцінкою, мережа відмила для Lazarus "$1B+". це його цифра, не поліції. розповів він усе лише 5 жовтня 2026
частина моїх стейблів у Flexible теж в USDT, тож приємно бачити, шо крадений USDT таки морозять
відмивання - це сервіс з комісією, як обмінник. ZachXBT цю комісію просто заплатив, шоб зайти всередину
#zachxbt #Lazarus #bybit
ZachXBT платив відмивачам Lazarus 5% з кожної угоди. сам, своїми грошима
з кінця лютого 2025 він грав клієнта
завів у їхню мережу 349700 $USDC
і на кожному ордері свідомо губив 5%, поки йому не почали довіряти
довіра там, виходить, коштує 5%. заплатив - і тобі самі розказують, куди йдуть крадені гроші
шо вийшло:
- кластер з понад $12 млн коштів з хаку Bybit
- Tether заморозив 442000 USDT
за його оцінкою, мережа відмила для Lazarus "$1B+". це його цифра, не поліції. розповів він усе лише 5 жовтня 2026
частина моїх стейблів у Flexible теж в USDT, тож приємно бачити, шо крадений USDT таки морозять
відмивання - це сервіс з комісією, як обмінник. ZachXBT цю комісію просто заплатив, шоб зайти всередину
#zachxbt #Lazarus #bybit
з кінця лютого 2025 він грав клієнта
завів у їхню мережу 349700 $USDC
і на кожному ордері свідомо губив 5%, поки йому не почали довіряти
довіра там, виходить, коштує 5%. заплатив - і тобі самі розказують, куди йдуть крадені гроші
шо вийшло:
- кластер з понад $12 млн коштів з хаку Bybit
- Tether заморозив 442000 USDT
за його оцінкою, мережа відмила для Lazarus "$1B+". це його цифра, не поліції. розповів він усе лише 5 жовтня 2026
частина моїх стейблів у Flexible теж в USDT, тож приємно бачити, шо крадений USDT таки морозять
відмивання - це сервіс з комісією, як обмінник. ZachXBT цю комісію просто заплатив, шоб зайти всередину
#zachxbt #Lazarus #bybit
10
446

·
--
L'enquêteur on-chain ZachXBT affirme avoir infiltré un réseau chinois de blanchiment qui aurait traité plus de 1 Md$ pour le groupe nord-coréen Lazarus. Pour y entrer, il a avancé 349 700 USDC de sa poche.
Son thread du 5 octobre, repris par The Block et Decrypt :
21 février 2025 : Bybit perd 1,5 Md$, vol attribué par le FBI aux hackers nord-coréens TraderTraitor. Plus de 15 comptes Telegram et Discord cherchent alors de l'aide pour écouler les fonds.
6 mars 2025 : il se fait passer pour client d'un certain "Jimmy Green", en perdant 5% par ordre. L'adresse de réception était alimentée en gas par un wallet de la liste noire Bybit.
12 mars 2025 : une capture envoyée par Jimmy colle à un ordre THORChain créé dans les minutes suivantes. Trois adresses Solana révèlent un cluster de plus de 12 M$ passé de $BTC à ETH, puis $SOL et enfin Tron. Tether gèle ensuite 442 000 USDT.
À noter : au 6 octobre, ni le FBI, ni le Trésor US, ni Tether n'ont confirmé publiquement le chiffre de 1 Md$ ni l'identité du réseau (crypto.news).
Ma lecture : ce qui compte, c'est le ratio. Environ 3,7% du cluster tracé a été gelé. Et début mars 2025, Ben Zhou (Bybit) chiffrait les gels à 3% du total volé. Le blocage ne marche qu'au dernier maillon, quand l'argent redevient du USDT sur Tron ($TRX), qu'un émetteur peut figer. Bridges et swaps restent quasi hors d'atteinte.
Prochain test : le hack Bitget de 387 M$ fin septembre, relié à la Corée du Nord par Elliptic et Chainalysis. Même schéma sur Telegram, selon lui. Soit ces infos déclenchent des gels rapides, soit le réseau a déjà changé de rails.
Qui devrait bloquer ces flux en premier : les émetteurs de stablecoins, les protocoles cross-chain comme THORChain, ou les exchanges où l'argent finit par sortir ?
#Lazarus #CryptoSecurity
L'enquêteur on-chain ZachXBT affirme avoir infiltré un réseau chinois de blanchiment qui aurait traité plus de 1 Md$ pour le groupe nord-coréen Lazarus. Pour y entrer, il a avancé 349 700 USDC de sa poche.
Son thread du 5 octobre, repris par The Block et Decrypt :
21 février 2025 : Bybit perd 1,5 Md$, vol attribué par le FBI aux hackers nord-coréens TraderTraitor. Plus de 15 comptes Telegram et Discord cherchent alors de l'aide pour écouler les fonds.
6 mars 2025 : il se fait passer pour client d'un certain "Jimmy Green", en perdant 5% par ordre. L'adresse de réception était alimentée en gas par un wallet de la liste noire Bybit.
12 mars 2025 : une capture envoyée par Jimmy colle à un ordre THORChain créé dans les minutes suivantes. Trois adresses Solana révèlent un cluster de plus de 12 M$ passé de $BTC à ETH, puis $SOL et enfin Tron. Tether gèle ensuite 442 000 USDT.
À noter : au 6 octobre, ni le FBI, ni le Trésor US, ni Tether n'ont confirmé publiquement le chiffre de 1 Md$ ni l'identité du réseau (crypto.news).
Ma lecture : ce qui compte, c'est le ratio. Environ 3,7% du cluster tracé a été gelé. Et début mars 2025, Ben Zhou (Bybit) chiffrait les gels à 3% du total volé. Le blocage ne marche qu'au dernier maillon, quand l'argent redevient du USDT sur Tron ($TRX ), qu'un émetteur peut figer. Bridges et swaps restent quasi hors d'atteinte.
Prochain test : le hack Bitget de 387 M$ fin septembre, relié à la Corée du Nord par Elliptic et Chainalysis. Même schéma sur Telegram, selon lui. Soit ces infos déclenchent des gels rapides, soit le réseau a déjà changé de rails.
Qui devrait bloquer ces flux en premier : les émetteurs de stablecoins, les protocoles cross-chain comme THORChain, ou les exchanges où l'argent finit par sortir ?
#Lazarus #CryptoSecurity
Son thread du 5 octobre, repris par The Block et Decrypt :
21 février 2025 : Bybit perd 1,5 Md$, vol attribué par le FBI aux hackers nord-coréens TraderTraitor. Plus de 15 comptes Telegram et Discord cherchent alors de l'aide pour écouler les fonds.
6 mars 2025 : il se fait passer pour client d'un certain "Jimmy Green", en perdant 5% par ordre. L'adresse de réception était alimentée en gas par un wallet de la liste noire Bybit.
12 mars 2025 : une capture envoyée par Jimmy colle à un ordre THORChain créé dans les minutes suivantes. Trois adresses Solana révèlent un cluster de plus de 12 M$ passé de $BTC à ETH, puis $SOL et enfin Tron. Tether gèle ensuite 442 000 USDT.
À noter : au 6 octobre, ni le FBI, ni le Trésor US, ni Tether n'ont confirmé publiquement le chiffre de 1 Md$ ni l'identité du réseau (crypto.news).
Ma lecture : ce qui compte, c'est le ratio. Environ 3,7% du cluster tracé a été gelé. Et début mars 2025, Ben Zhou (Bybit) chiffrait les gels à 3% du total volé. Le blocage ne marche qu'au dernier maillon, quand l'argent redevient du USDT sur Tron ($TRX ), qu'un émetteur peut figer. Bridges et swaps restent quasi hors d'atteinte.
Prochain test : le hack Bitget de 387 M$ fin septembre, relié à la Corée du Nord par Elliptic et Chainalysis. Même schéma sur Telegram, selon lui. Soit ces infos déclenchent des gels rapides, soit le réseau a déjà changé de rails.
Qui devrait bloquer ces flux en premier : les émetteurs de stablecoins, les protocoles cross-chain comme THORChain, ou les exchanges où l'argent finit par sortir ?
#Lazarus #CryptoSecurity
157

Mạng tội phạm Trung Quốc rửa hơn 1 tỷ USD cho Lazarus: ZachXBT
- ZachXBT tuyên bố đã thâm nhập vào mạng lưới tội phạm Trung Quốc bằng cách giả làm khách hàng.
- Thông tin thu thập được giúp truy vết dòng tiền từ vụ hack Bybit trị giá 1,5 tỷ USD.
- Mạng lưới này bị cáo buộc rửa hơn 1 tỷ USD cho nhóm hacker Lazarus.
- Nguồn RSS chưa cung cấp thêm chi tiết về danh tính hoặc phương thức hoạt động của mạng lưới.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Nguồn: CoinTelegraph
Mạng tội phạm Trung Quốc rửa hơn 1 tỷ USD cho Lazarus: ZachXBT
- ZachXBT tuyên bố đã thâm nhập vào mạng lưới tội phạm Trung Quốc bằng cách giả làm khách hàng.
- Thông tin thu thập được giúp truy vết dòng tiền từ vụ hack Bybit trị giá 1,5 tỷ USD.
- Mạng lưới này bị cáo buộc rửa hơn 1 tỷ USD cho nhóm hacker Lazarus.
- Nguồn RSS chưa cung cấp thêm chi tiết về danh tính hoặc phương thức hoạt động của mạng lưới.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Nguồn: CoinTelegraph
- ZachXBT tuyên bố đã thâm nhập vào mạng lưới tội phạm Trung Quốc bằng cách giả làm khách hàng.
- Thông tin thu thập được giúp truy vết dòng tiền từ vụ hack Bybit trị giá 1,5 tỷ USD.
- Mạng lưới này bị cáo buộc rửa hơn 1 tỷ USD cho nhóm hacker Lazarus.
- Nguồn RSS chưa cung cấp thêm chi tiết về danh tính hoặc phương thức hoạt động của mạng lưới.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Nguồn: CoinTelegraph
25
·
--
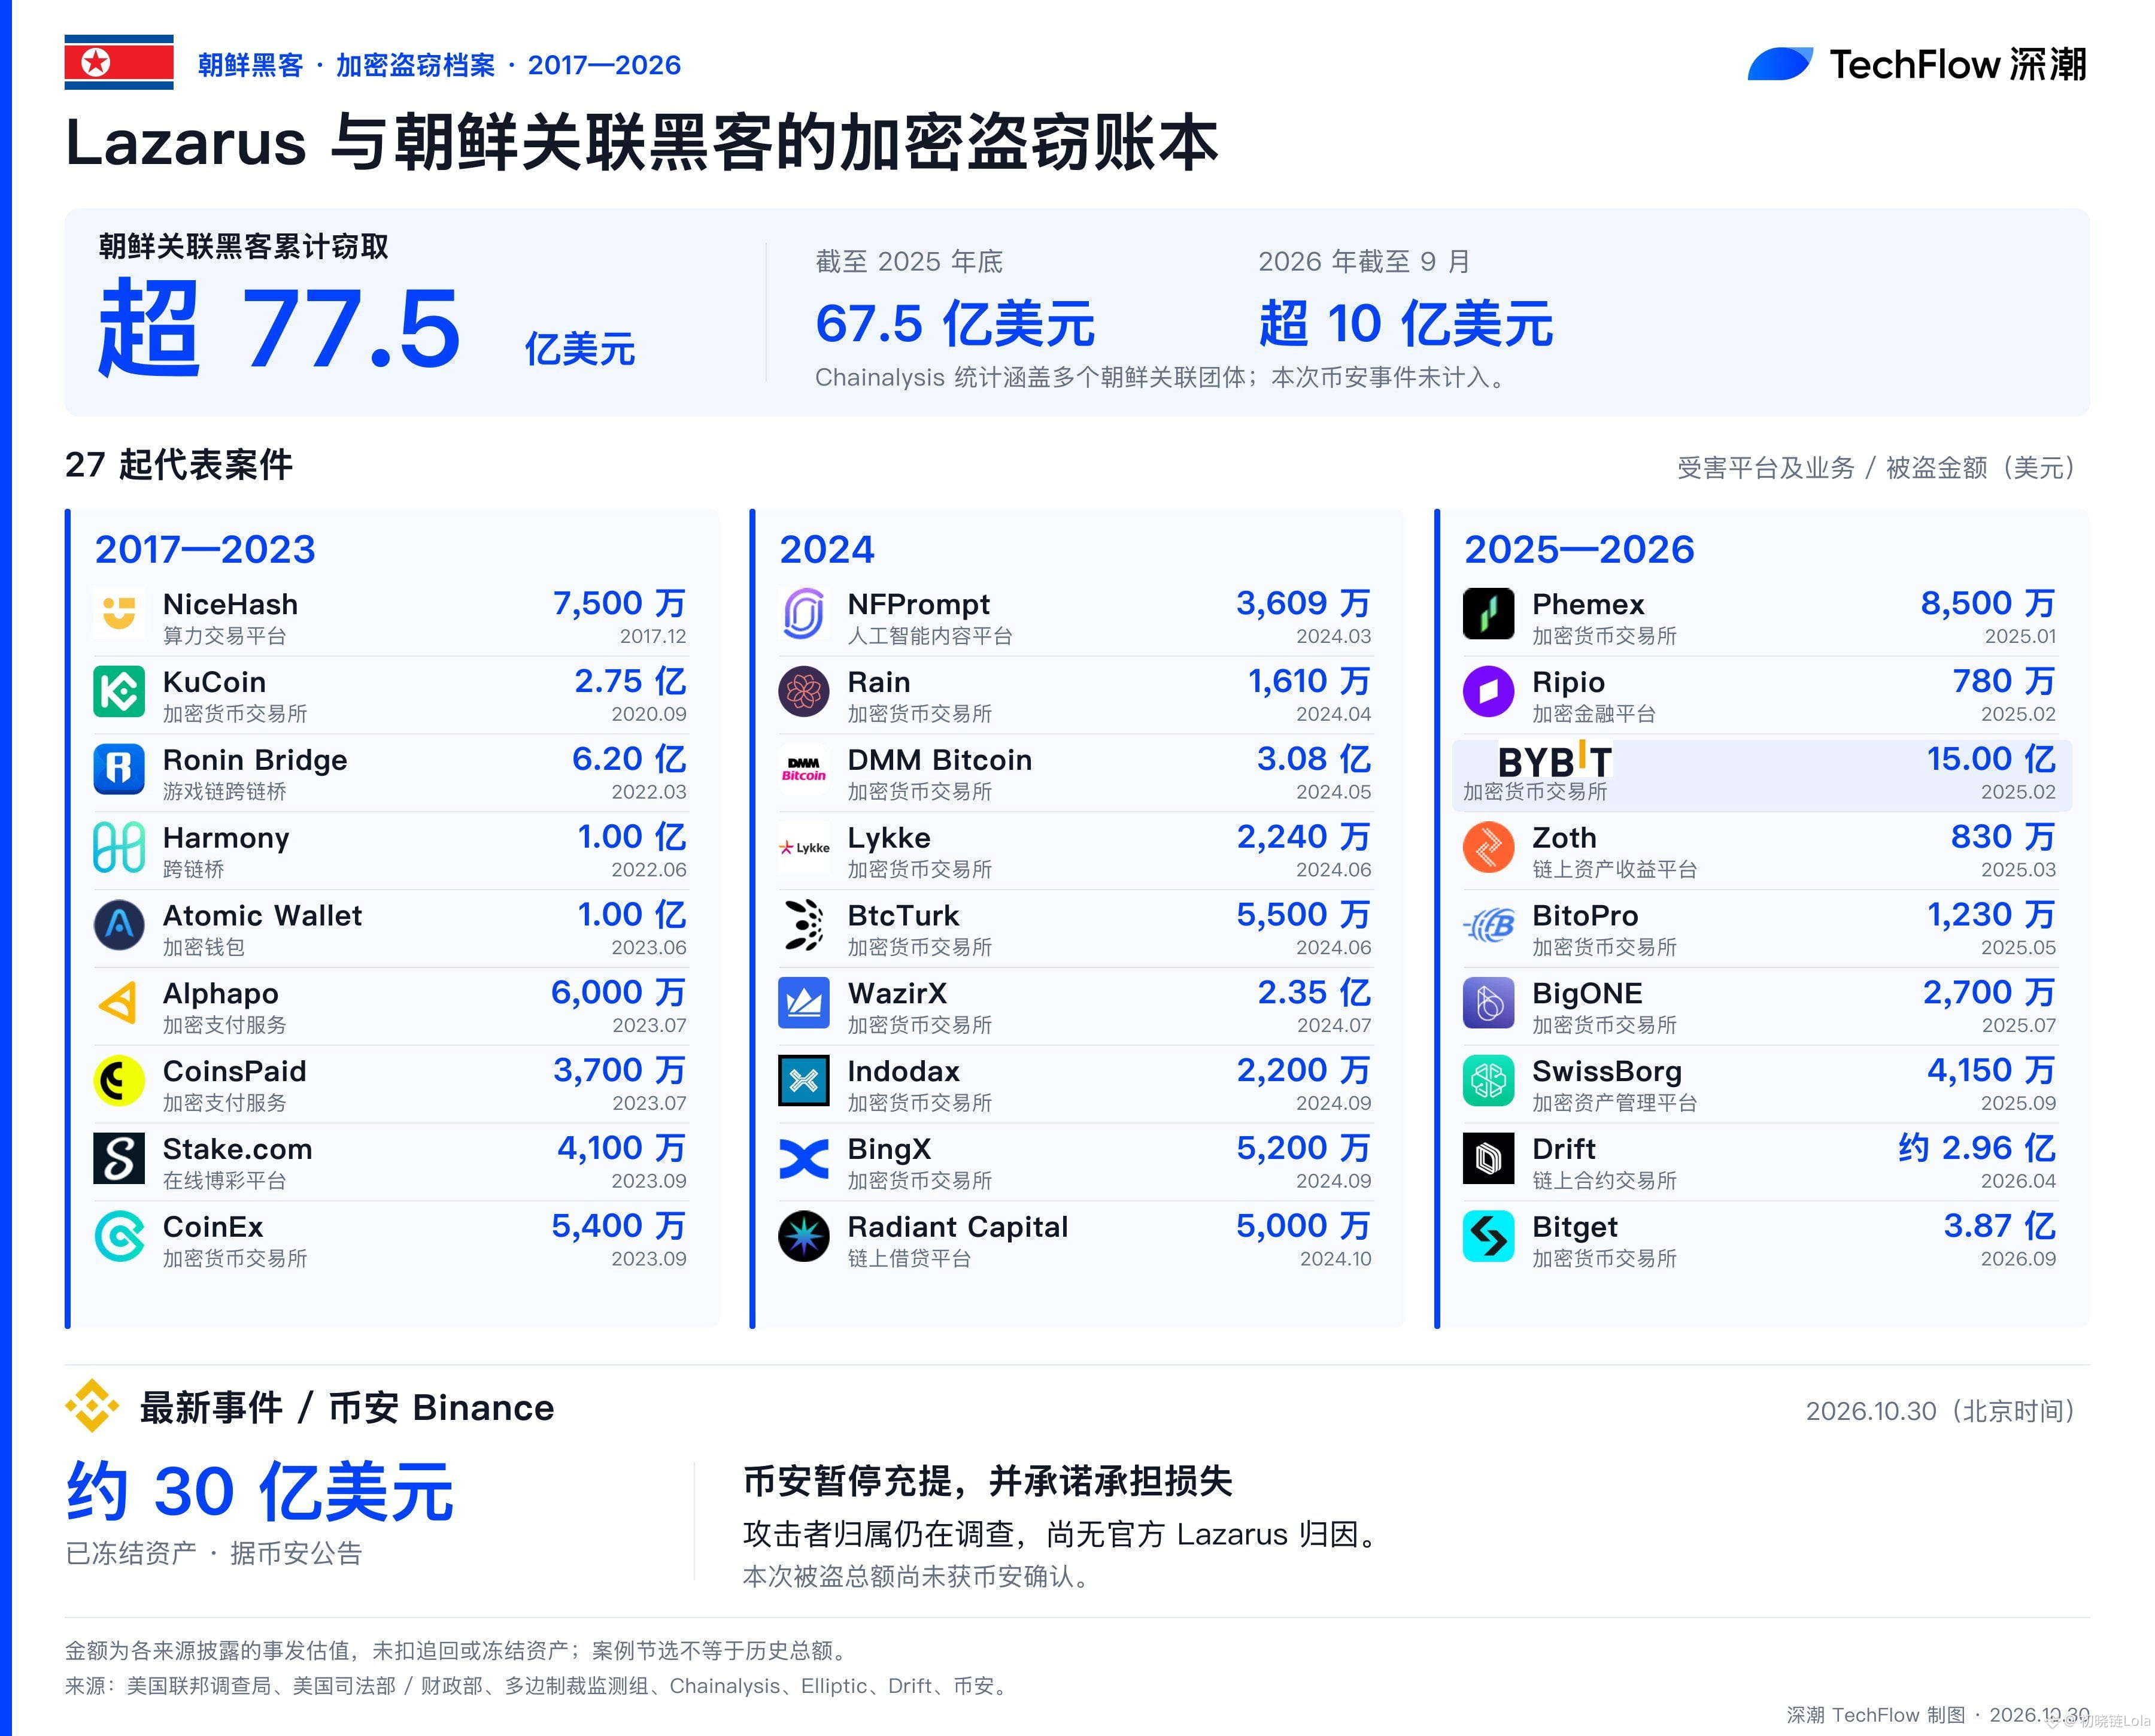
📰 9月24日,Bitget部分热钱包和暖钱包出现异常转账,平台最初披露损失约3.516亿美元,随后确认被转移的资产规模调整到3.875亿美元。
🔥 TRM Labs发现,这次部分被盗资金的清洗路径,与此前 Bybit、AFX Bridge 等朝鲜相关攻击存在重合。Elliptic也认为,本次事件与朝鲜相关黑客存在“高度可能”的关联,调查矛头再次指向 Lazarus Group。
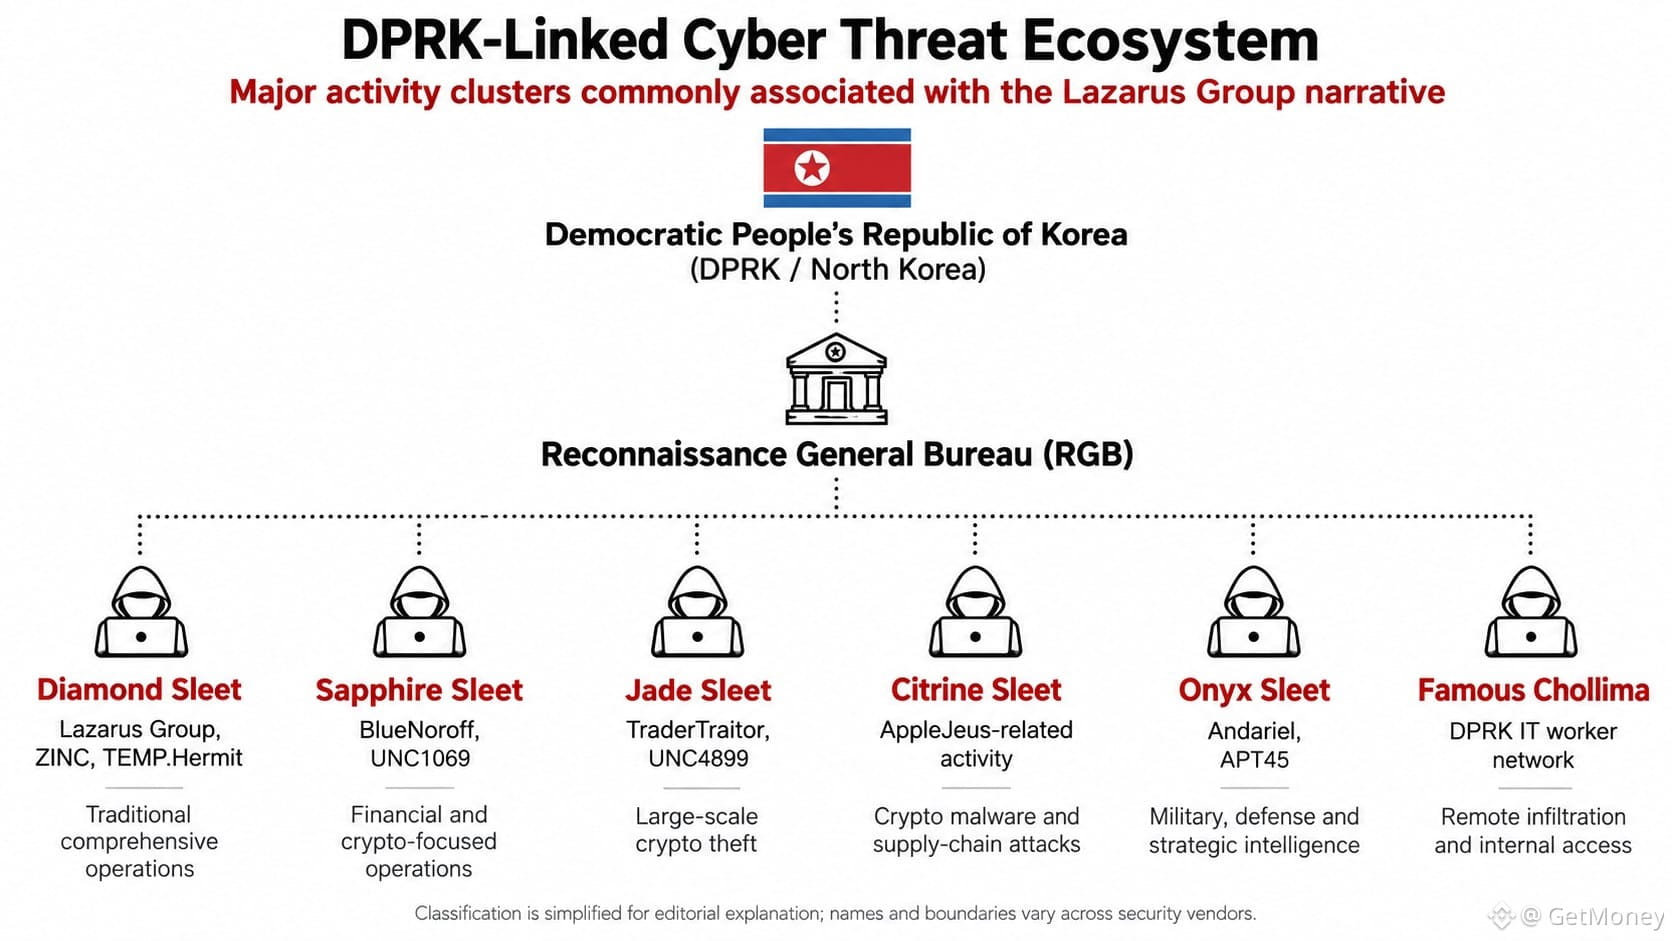
说实话,Lazarus不太像一个边界清晰的单独组织,更像外界对朝鲜国家级网络攻击体系的统称。美国财政部在2019年点名 Lazarus、BlueNoroff 和 Andariel,认为它们都受到朝鲜侦察总局 RGB 控制。
💡 这个体系里,不同机构会使用不同名字:BlueNoroff长期盯金融机构和加密资产,TraderTraitor针对交易所、托管商和大型加密目标,Citrine Sleet偏向恶意软件与供应链攻击,Famous Chollima则通过虚假身份进入科技和加密企业。
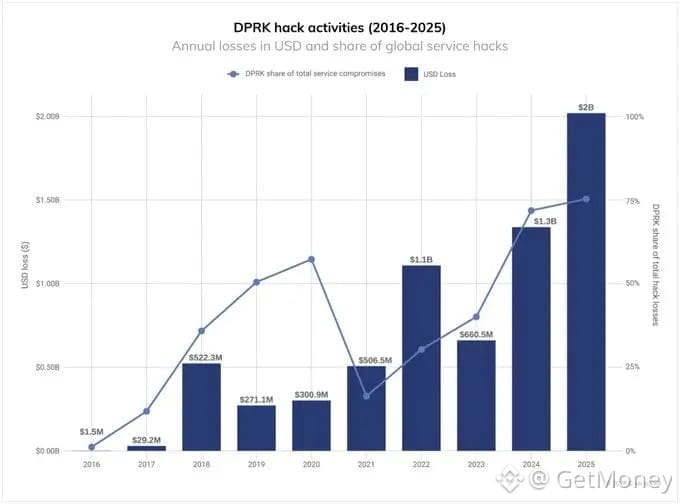
👀 从 Ronin Bridge、Harmony、Atomic Wallet,到 Stake、WazirX、DMM Bitcoin,再到2025年的 Bybit事件,若把目前高度疑似朝鲜所为的 Bitget 事件也算进去,相关盗窃规模已经接近78亿美元。这个数字,已经不是单一平台的安全事故了。
🤔 当同一套攻击体系不断换名字、换入口,交易所和项目方到底该怎么判断自己面对的是哪一拨人?
#Lazarus #Bitget #加密安全 #链上安全
📰 9月24日,Bitget部分热钱包和暖钱包出现异常转账,平台最初披露损失约3.516亿美元,随后确认被转移的资产规模调整到3.875亿美元。
🔥 TRM Labs发现,这次部分被盗资金的清洗路径,与此前 Bybit、AFX Bridge 等朝鲜相关攻击存在重合。Elliptic也认为,本次事件与朝鲜相关黑客存在“高度可能”的关联,调查矛头再次指向 Lazarus Group。
说实话,Lazarus不太像一个边界清晰的单独组织,更像外界对朝鲜国家级网络攻击体系的统称。美国财政部在2019年点名 Lazarus、BlueNoroff 和 Andariel,认为它们都受到朝鲜侦察总局 RGB 控制。
💡 这个体系里,不同机构会使用不同名字:BlueNoroff长期盯金融机构和加密资产,TraderTraitor针对交易所、托管商和大型加密目标,Citrine Sleet偏向恶意软件与供应链攻击,Famous Chollima则通过虚假身份进入科技和加密企业。
👀 从 Ronin Bridge、Harmony、Atomic Wallet,到 Stake、WazirX、DMM Bitcoin,再到2025年的 Bybit事件,若把目前高度疑似朝鲜所为的 Bitget 事件也算进去,相关盗窃规模已经接近78亿美元。这个数字,已经不是单一平台的安全事故了。
🤔 当同一套攻击体系不断换名字、换入口,交易所和项目方到底该怎么判断自己面对的是哪一拨人?
#Lazarus #Bitget #加密安全 #链上安全
🔥 TRM Labs发现,这次部分被盗资金的清洗路径,与此前 Bybit、AFX Bridge 等朝鲜相关攻击存在重合。Elliptic也认为,本次事件与朝鲜相关黑客存在“高度可能”的关联,调查矛头再次指向 Lazarus Group。
说实话,Lazarus不太像一个边界清晰的单独组织,更像外界对朝鲜国家级网络攻击体系的统称。美国财政部在2019年点名 Lazarus、BlueNoroff 和 Andariel,认为它们都受到朝鲜侦察总局 RGB 控制。
💡 这个体系里,不同机构会使用不同名字:BlueNoroff长期盯金融机构和加密资产,TraderTraitor针对交易所、托管商和大型加密目标,Citrine Sleet偏向恶意软件与供应链攻击,Famous Chollima则通过虚假身份进入科技和加密企业。
👀 从 Ronin Bridge、Harmony、Atomic Wallet,到 Stake、WazirX、DMM Bitcoin,再到2025年的 Bybit事件,若把目前高度疑似朝鲜所为的 Bitget 事件也算进去,相关盗窃规模已经接近78亿美元。这个数字,已经不是单一平台的安全事故了。
🤔 当同一套攻击体系不断换名字、换入口,交易所和项目方到底该怎么判断自己面对的是哪一拨人?
#Lazarus #Bitget #加密安全 #链上安全
53
💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
3
649
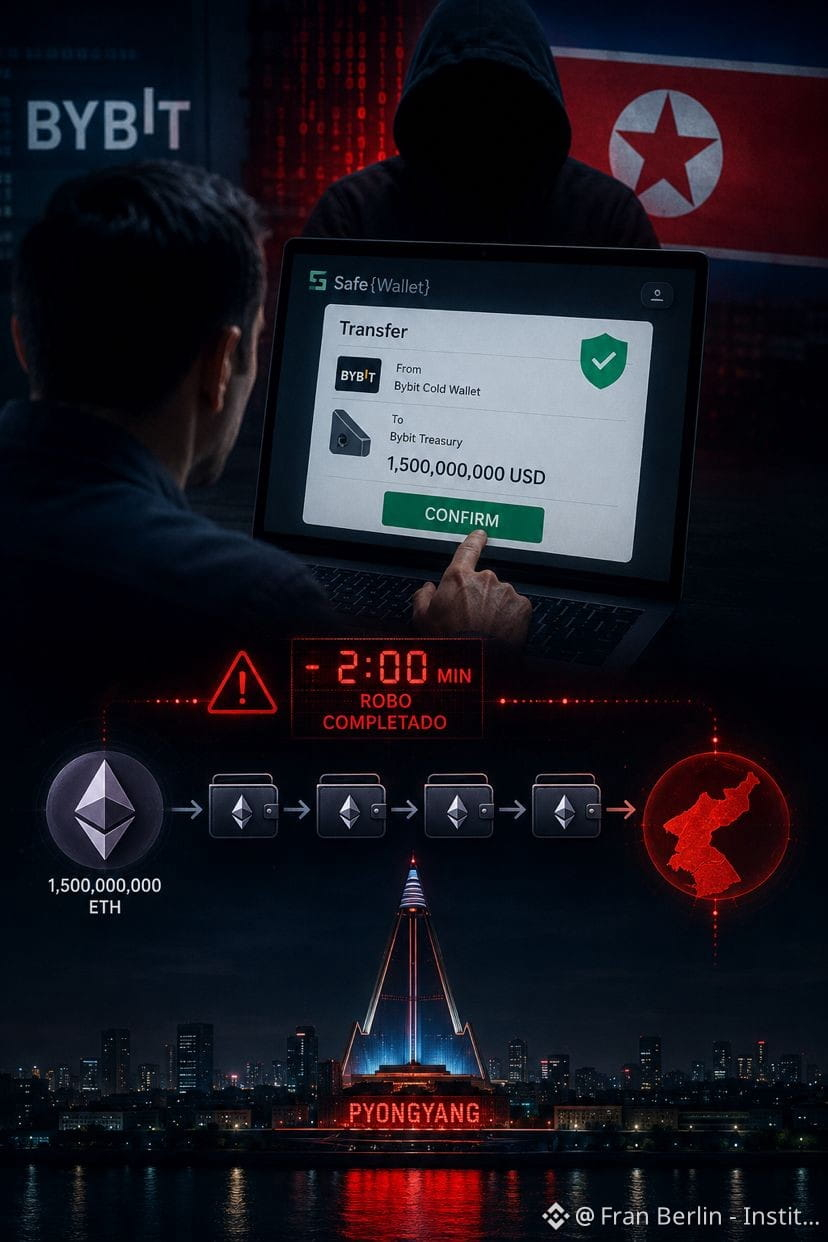
Era una transferencia de rutina.
Febrero 20, 2025. Un empleado de Bybit abre su pantalla, revisa los detalles de la transacción, y firma.
Todo se ve normal.
Minutos después, 1.500 millones de dólares $USDT en Ethereum habían desaparecido.
Pero lo más aterrador no es el monto.
Lo más aterrador es cómo lo hicieron.
El Grupo Lazarus hackers de élite del gobierno de Corea del Norte no atacó el blockchain. No rompió ninguna clave privada. No necesitó nada de eso.
Simplemente… falsificó lo que el empleado veía en pantalla.
Meses antes, infiltraron el sistema de un desarrollador de Safe Wallet, la plataforma que Bybit usaba para firmar transacciones. Inyectaron un código malicioso que dormía en silencio, esperando.
Cuando el empleado abrió su billetera ese día, el código se activó. La pantalla mostraba una transferencia legítima. En realidad, los fondos iban a Pyongyang.
El empleado firmó. Sus compañeros firmaron. Nadie vio nada raro.
Dos minutos después del robo, el código malicioso se borró solo. Sin rastro.
El FBI tardó días en confirmar lo que ya todos sospechaban: fue Corea del Norte, financiando su programa de armas nucleares con Ethereum robado.
La lección que nadie quiere escuchar: el eslabón más débil no es el código. Eres tú.
¿Confías en la pantalla que ves cuando firmas una transacción?
Fran Berlín | Instituto Blockchain
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
{spot}(ETHUSDT)
{spot}(USDCUSDT)
Era una transferencia de rutina.
Febrero 20, 2025. Un empleado de Bybit abre su pantalla, revisa los detalles de la transacción, y firma.
Todo se ve normal.
Minutos después, 1.500 millones de dólares $USDT en Ethereum habían desaparecido.
Pero lo más aterrador no es el monto.
Lo más aterrador es cómo lo hicieron.
El Grupo Lazarus hackers de élite del gobierno de Corea del Norte no atacó el blockchain. No rompió ninguna clave privada. No necesitó nada de eso.
Simplemente… falsificó lo que el empleado veía en pantalla.
Meses antes, infiltraron el sistema de un desarrollador de Safe Wallet, la plataforma que Bybit usaba para firmar transacciones. Inyectaron un código malicioso que dormía en silencio, esperando.
Cuando el empleado abrió su billetera ese día, el código se activó. La pantalla mostraba una transferencia legítima. En realidad, los fondos iban a Pyongyang.
El empleado firmó. Sus compañeros firmaron. Nadie vio nada raro.
Dos minutos después del robo, el código malicioso se borró solo. Sin rastro.
El FBI tardó días en confirmar lo que ya todos sospechaban: fue Corea del Norte, financiando su programa de armas nucleares con Ethereum robado.
La lección que nadie quiere escuchar: el eslabón más débil no es el código. Eres tú.
¿Confías en la pantalla que ves cuando firmas una transacción?
Fran Berlín | Instituto Blockchain
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
Febrero 20, 2025. Un empleado de Bybit abre su pantalla, revisa los detalles de la transacción, y firma.
Todo se ve normal.
Minutos después, 1.500 millones de dólares $USDT en Ethereum habían desaparecido.
Pero lo más aterrador no es el monto.
Lo más aterrador es cómo lo hicieron.
El Grupo Lazarus hackers de élite del gobierno de Corea del Norte no atacó el blockchain. No rompió ninguna clave privada. No necesitó nada de eso.
Simplemente… falsificó lo que el empleado veía en pantalla.
Meses antes, infiltraron el sistema de un desarrollador de Safe Wallet, la plataforma que Bybit usaba para firmar transacciones. Inyectaron un código malicioso que dormía en silencio, esperando.
Cuando el empleado abrió su billetera ese día, el código se activó. La pantalla mostraba una transferencia legítima. En realidad, los fondos iban a Pyongyang.
El empleado firmó. Sus compañeros firmaron. Nadie vio nada raro.
Dos minutos después del robo, el código malicioso se borró solo. Sin rastro.
El FBI tardó días en confirmar lo que ya todos sospechaban: fue Corea del Norte, financiando su programa de armas nucleares con Ethereum robado.
La lección que nadie quiere escuchar: el eslabón más débil no es el código. Eres tú.
¿Confías en la pantalla que ves cuando firmas una transacción?
Fran Berlín | Instituto Blockchain
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
675

·
--
Падение
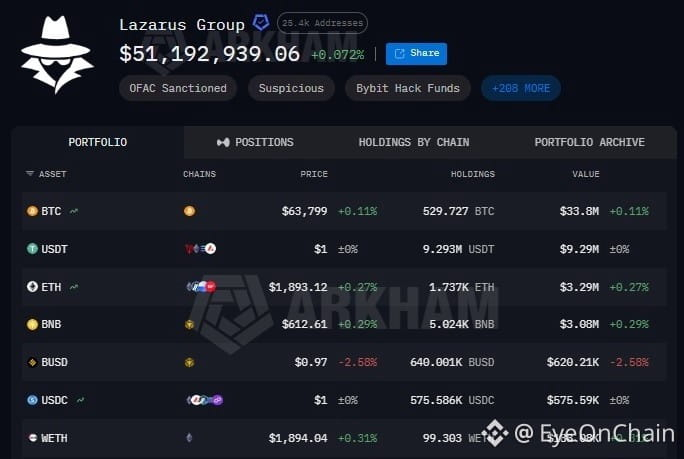
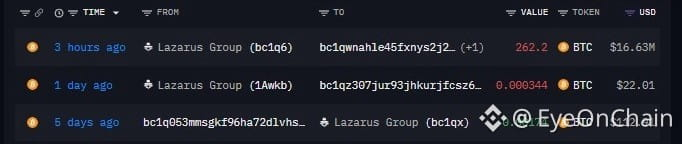
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC, $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
{future}(BTCUSDT)
{spot}(BTCUSDT)
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
1
1.3k
·
--
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
5
94

🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
33
·
--
Рост
$BTC $ETH
🚨 FLASH HACK : Que s'est-il vraiment passé chez Bitget ? 🚨
Un incident de sécurité majeur vient de secouer l'écosystème crypto. Voici le point complet sur la situation 🧵👇
💥 L'Attaque en Bref
Le 24 septembre 2026, Bitget a subi une faille au niveau de son infrastructure backend. Les pirates ont falsifié des autorisations système internes pour valider de faux transferts et siphoner les portefeuilles chauds (hot wallets).
💰 Montant des Pertes : ~387,5 millions $
Des cryptos majeures ont été détournées vers plusieurs blockchains : ETH, XRP, USDT, TRX, AVAX, BNB et ZEC.
🛡️ Quel impact pour les utilisateurs ?
• ❄️ Cold Wallets : 100 % sécurisés (les portefeuilles froids n'ont pas été touchés).
• 👤 Soldes clients : Aucun impact direct sur vos comptes.
• 🛡️ Fonds de Protection : Le fonds de garantie Bitget (évalué à +460M$) couvrira l'intégralité des pertes.
🕵️ Qui est derrière le Hack ?
Selon la PDG Gracy Chen, les adresses IP et le mode opératoire pointent vers des hackers nord-coréens (groupe Lazarus). Les géants de la cybersécurité Mandiant et SlowMist sont sur le dossier.
🗓️ Calendrier de Reprise des Retraits :
✅ Faille corrigée & Trading opérationnel
📌 28 Sept. : Retraits BTC
📌 29 Sept. : Retraits ETH (Ethereum, BSC, Arbitrum, Base, OP)
📌 30 Sept. : Retraits USDT (Ethereum, BSC, Solana, Tron)
📌 02 Oct. : Autres altcoins, fiat et P2P
Restez prudents et vérifiez toujours vos sources officiellement ! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
{spot}(BTCUSDT)
{spot}(ETHUSDT)
$BTC $ETH
🚨 FLASH HACK : Que s'est-il vraiment passé chez Bitget ? 🚨
Un incident de sécurité majeur vient de secouer l'écosystème crypto. Voici le point complet sur la situation 🧵👇
💥 L'Attaque en Bref
Le 24 septembre 2026, Bitget a subi une faille au niveau de son infrastructure backend. Les pirates ont falsifié des autorisations système internes pour valider de faux transferts et siphoner les portefeuilles chauds (hot wallets).
💰 Montant des Pertes : ~387,5 millions $
Des cryptos majeures ont été détournées vers plusieurs blockchains : ETH, XRP, USDT, TRX, AVAX, BNB et ZEC.
🛡️ Quel impact pour les utilisateurs ?
• ❄️ Cold Wallets : 100 % sécurisés (les portefeuilles froids n'ont pas été touchés).
• 👤 Soldes clients : Aucun impact direct sur vos comptes.
• 🛡️ Fonds de Protection : Le fonds de garantie Bitget (évalué à +460M$) couvrira l'intégralité des pertes.
🕵️ Qui est derrière le Hack ?
Selon la PDG Gracy Chen, les adresses IP et le mode opératoire pointent vers des hackers nord-coréens (groupe Lazarus). Les géants de la cybersécurité Mandiant et SlowMist sont sur le dossier.
🗓️ Calendrier de Reprise des Retraits :
✅ Faille corrigée & Trading opérationnel
📌 28 Sept. : Retraits BTC
📌 29 Sept. : Retraits ETH (Ethereum, BSC, Arbitrum, Base, OP)
📌 30 Sept. : Retraits USDT (Ethereum, BSC, Solana, Tron)
📌 02 Oct. : Autres altcoins, fiat et P2P
Restez prudents et vérifiez toujours vos sources officiellement ! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
🚨 FLASH HACK : Que s'est-il vraiment passé chez Bitget ? 🚨
Un incident de sécurité majeur vient de secouer l'écosystème crypto. Voici le point complet sur la situation 🧵👇
💥 L'Attaque en Bref
Le 24 septembre 2026, Bitget a subi une faille au niveau de son infrastructure backend. Les pirates ont falsifié des autorisations système internes pour valider de faux transferts et siphoner les portefeuilles chauds (hot wallets).
💰 Montant des Pertes : ~387,5 millions $
Des cryptos majeures ont été détournées vers plusieurs blockchains : ETH, XRP, USDT, TRX, AVAX, BNB et ZEC.
🛡️ Quel impact pour les utilisateurs ?
• ❄️ Cold Wallets : 100 % sécurisés (les portefeuilles froids n'ont pas été touchés).
• 👤 Soldes clients : Aucun impact direct sur vos comptes.
• 🛡️ Fonds de Protection : Le fonds de garantie Bitget (évalué à +460M$) couvrira l'intégralité des pertes.
🕵️ Qui est derrière le Hack ?
Selon la PDG Gracy Chen, les adresses IP et le mode opératoire pointent vers des hackers nord-coréens (groupe Lazarus). Les géants de la cybersécurité Mandiant et SlowMist sont sur le dossier.
🗓️ Calendrier de Reprise des Retraits :
✅ Faille corrigée & Trading opérationnel
📌 28 Sept. : Retraits BTC
📌 29 Sept. : Retraits ETH (Ethereum, BSC, Arbitrum, Base, OP)
📌 30 Sept. : Retraits USDT (Ethereum, BSC, Solana, Tron)
📌 02 Oct. : Autres altcoins, fiat et P2P
Restez prudents et vérifiez toujours vos sources officiellement ! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
183
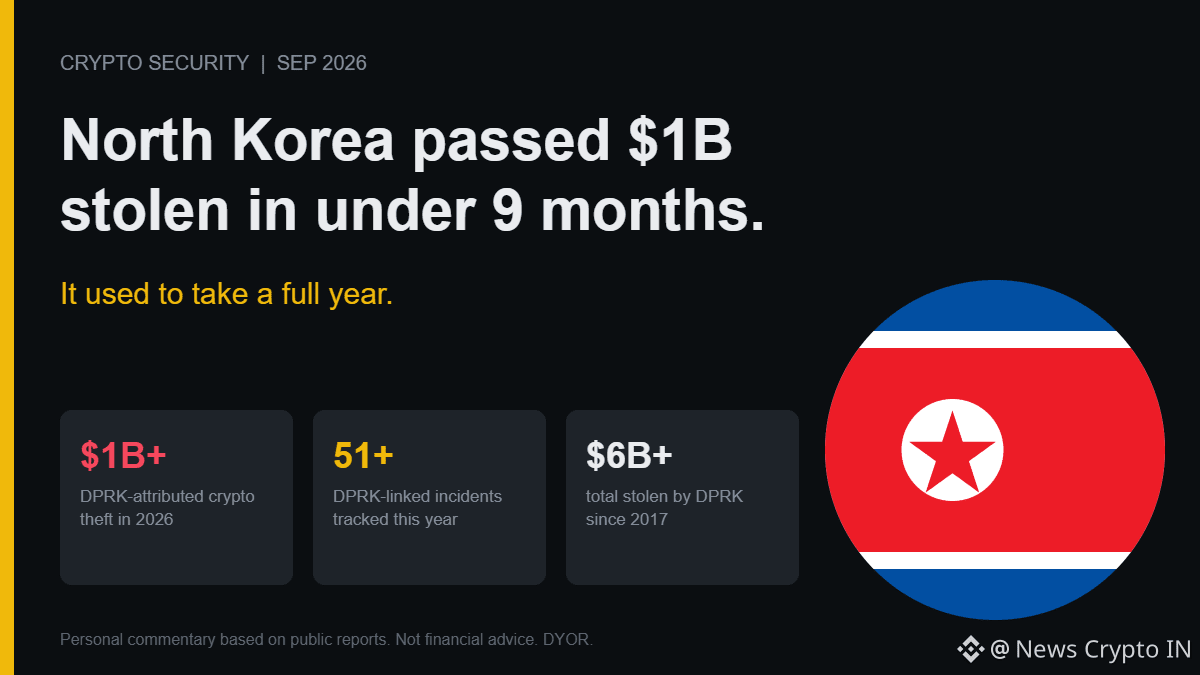
North Korea just crossed $1 billion in crypto theft for 2026, and did it in under 9 months. Last year that milestone took a full 12.
The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes.
The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access.
Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence.
At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis?
#Lazarus #CryptoSecurity
North Korea just crossed $1 billion in crypto theft for 2026, and did it in under 9 months. Last year that milestone took a full 12.
The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes.
The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access.
Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence.
At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis?
#Lazarus #CryptoSecurity
The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes.
The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access.
Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence.
At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis?
#Lazarus #CryptoSecurity
2
1.3k
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#BinanceProcesses$4.65BWithdrawals
Просмотров: 48,045
196 обсуждают
2
#WithdrawalsBack: 15 networks live
Просмотров: 10,631
155 обсуждают
3
#EthereumSurpasses$2300
Просмотров: 15
25 обсуждают
4
#BitcoinSpotETFsPost$203MWeeklyOutflow
Просмотров: 169
8 обсуждают
5
#SouthKoreanLawmakerProposesReviewOfAllListedDigitalAssets
Просмотров: 286
12 обсуждают
6
#BrazilVirtualAssetLicenseDeadlineDrawsAbout40Firms
Просмотров: 9,709
190 обсуждают
7
#BTCPayServerUrgesOperatorsToShutDownInstances
Просмотров: 9,226
179 обсуждают
8
#BankOfKoreaSurveysFinancialFirmsOnVirtualAssetRisks
Просмотров: 429
12 обсуждают
9
#BinanceUpdatesProofofReservesAddresses
Просмотров: 181,467
1,874 обсуждают
10
#StudyFindsCircleAIAgentWalletLimitsCanBeBypassed
Просмотров: 3,697
102 обсуждают