Binance Square
#cryptosecurity

cryptosecurity

8.5M рет көрілді
11,625 адам талқылап жатыр
黑僵尸
·
--
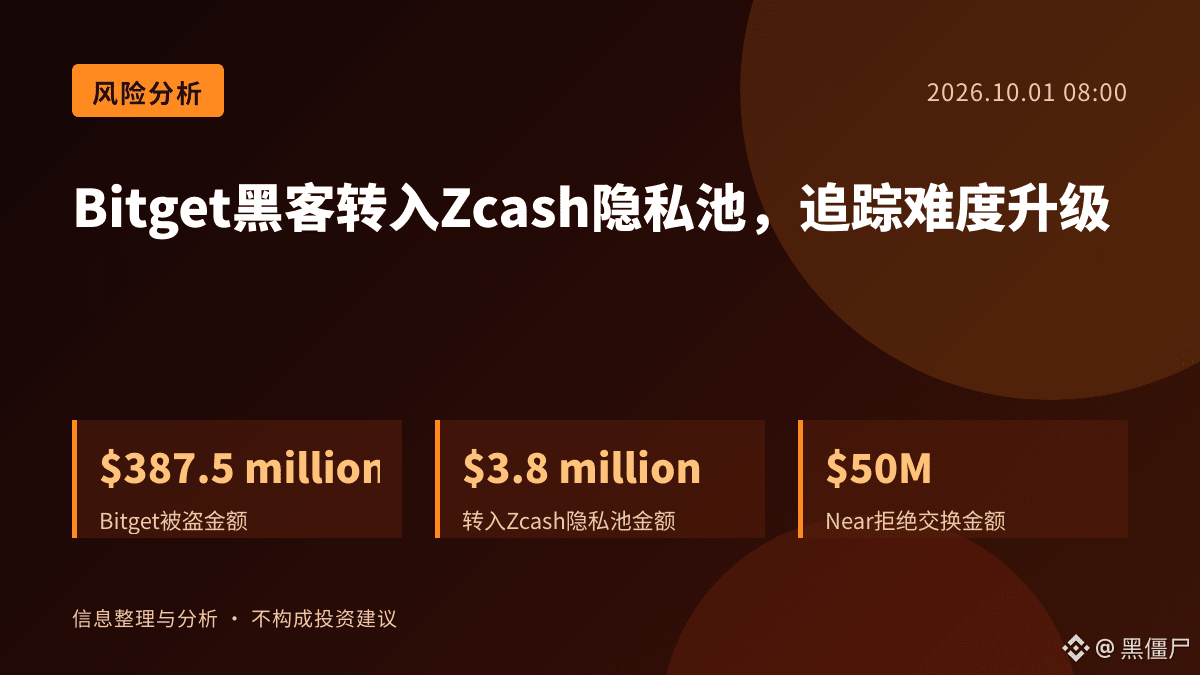
Bitget黑客转入Zcash隐私池,追踪难度升级 据Decrypt报道,Bitget黑客在Near拒绝5000万美元交换后,已将约380万美元转入Zcash Ironwood隐私池。这一转移路径表明,黑客正主动利用隐私功能增加资产追踪难度。 Zcash的隐私池机制可能使链上分析工具难以直接识别资金流向,这对安全团队构成挑战。但黑客资金仍可能被后续链上分析识别,隐私功能并非绝对屏障。 Near拒绝交换事件或影响市场对跨链资产安全的预期。若黑客持续使用隐私池,可能引发投资者对Zcash隐私功能的关注,进而影响$ZEC的市场情绪。 风险在于,隐私池可能延缓追踪进度,但不代表资金完全消失。市场需要观察黑客后续是否继续转移资产,以及安全团队能否突破隐私层。 接下来观察Zcash隐私池的资金流动情况,以及Near是否调整交换策略。若隐私池资金持续增加,可能反映黑客对追踪压力的应对策略。 #Zcash #Bitget #CryptoSecurity 以上为信息整理与个人分析,不构成投资建议。
Bitget黑客转入Zcash隐私池,追踪难度升级

据Decrypt报道,Bitget黑客在Near拒绝5000万美元交换后,已将约380万美元转入Zcash Ironwood隐私池。这一转移路径表明,黑客正主动利用隐私功能增加资产追踪难度。

Zcash的隐私池机制可能使链上分析工具难以直接识别资金流向,这对安全团队构成挑战。但黑客资金仍可能被后续链上分析识别,隐私功能并非绝对屏障。

Near拒绝交换事件或影响市场对跨链资产安全的预期。若黑客持续使用隐私池,可能引发投资者对Zcash隐私功能的关注,进而影响$ZEC 的市场情绪。

风险在于,隐私池可能延缓追踪进度,但不代表资金完全消失。市场需要观察黑客后续是否继续转移资产,以及安全团队能否突破隐私层。

接下来观察Zcash隐私池的资金流动情况,以及Near是否调整交换策略。若隐私池资金持续增加,可能反映黑客对追踪压力的应对策略。

#Zcash #Bitget #CryptoSecurity

以上为信息整理与个人分析,不构成投资建议。
·
--
Жоғары (өспелі)
˗ˋˏ$💸ˎˊ˗ 12,4 MILHÕES DE $XRP FORAM DRENADOS❓🔥💸⃤ (◞‸ ◟)💧 O caso da D’CENT App Wallet ficou muito maior do que parecia inicialmente. No primeiro episódio identificado, aproximadamente: 💰 2,009 milhões de XRP 👥 1.552 wallets ⏱️ pouco mais de 2 horas foram atingidos em 15 de setembro. Mas novas análises do XRP Ledger rastrearam várias ondas posteriores. Segundo a XRPL.to, até 25 de setembro o mesmo operador teria alcançado: 🔥 12.402.589 XRP 🚨 7.393 wallets 🗑️ 6.095 contas deletadas 🌉 6,27 milhões de $XRP convertidos via THORChain E existe um detalhe assustador: As transações foram assinadas com as próprias chaves das carteiras afetadas. Isso indica que o atacante aparentemente já tinha acesso às credenciais necessárias antes dos saques mas a forma exata pela qual essas chaves foram obtidas ainda não foi confirmada publicamente. A D’CENT reconheceu transferências anormais envolvendo sua App Wallet e orientou usuários potencialmente afetados a mover os ativos para uma carteira criada com uma nova recovery phrase. ⚠️ A empresa afirma que não confirmou comprometimento originado diretamente de seus hardware wallets. Mas existe uma exceção crítica: Se a mesma seed de um hardware wallet tiver sido inserida anteriormente na App Wallet, essa carteira também deve ser tratada como potencialmente exposta. {spot}(XRPUSDT) 👩🏻‍🏫A lição é Brutal:👨🏻‍🏫 🤦🏽‍♀️HARDWARE WALLET NÃO PROTEGE UMA SEED QUE JÁ FOI EXPOSTA EM SOFTWARE. Rip 💐 SE A CHAVE É A CARTEIRA, ONDE VOCÊ GUARDA SUA SEED? #XRPHACKED #CryptoSecurity
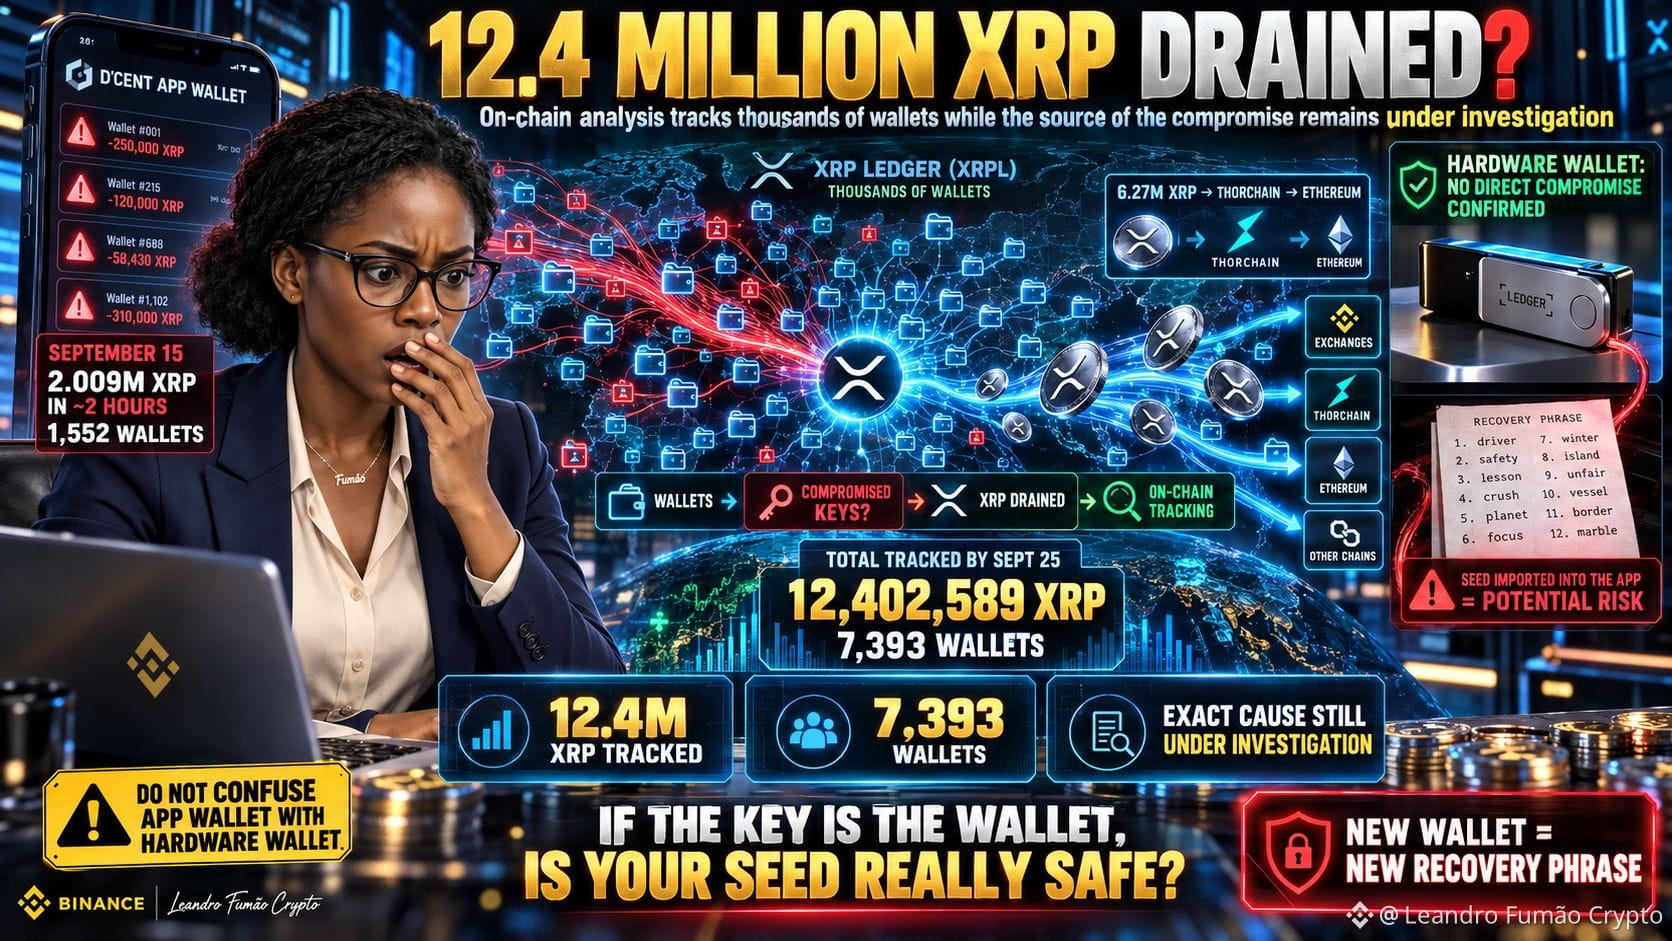
˗ˋˏ$💸ˎˊ˗ 12,4 MILHÕES DE $XRP FORAM DRENADOS❓🔥💸⃤

(◞‸ ◟)💧 O caso da D’CENT App Wallet ficou muito maior do que parecia inicialmente.
No primeiro episódio identificado, aproximadamente:

💰 2,009 milhões de XRP
👥 1.552 wallets
⏱️ pouco mais de 2 horas
foram atingidos em 15 de setembro.
Mas novas análises do XRP Ledger rastrearam várias ondas posteriores.

Segundo a XRPL.to, até 25 de setembro o mesmo operador teria alcançado:
🔥 12.402.589 XRP
🚨 7.393 wallets
🗑️ 6.095 contas deletadas
🌉 6,27 milhões de $XRP convertidos via THORChain

E existe um detalhe assustador:
As transações foram assinadas com as próprias chaves das carteiras afetadas.
Isso indica que o atacante aparentemente já tinha acesso às credenciais necessárias antes dos saques mas a forma exata pela qual essas chaves foram obtidas ainda não foi confirmada publicamente.
A D’CENT reconheceu transferências anormais envolvendo sua App Wallet e orientou usuários potencialmente afetados a mover os ativos para uma carteira criada com uma nova recovery phrase.

⚠️ A empresa afirma que não confirmou comprometimento originado diretamente de seus hardware wallets.
Mas existe uma exceção crítica:
Se a mesma seed de um hardware wallet tiver sido inserida anteriormente na App Wallet, essa carteira também deve ser tratada como potencialmente exposta.
👩🏻‍🏫A lição é Brutal:👨🏻‍🏫
🤦🏽‍♀️HARDWARE WALLET NÃO PROTEGE UMA SEED QUE JÁ FOI EXPOSTA EM SOFTWARE.
Rip 💐 SE A CHAVE É A CARTEIRA, ONDE VOCÊ GUARDA SUA SEED?

#XRPHACKED #CryptoSecurity
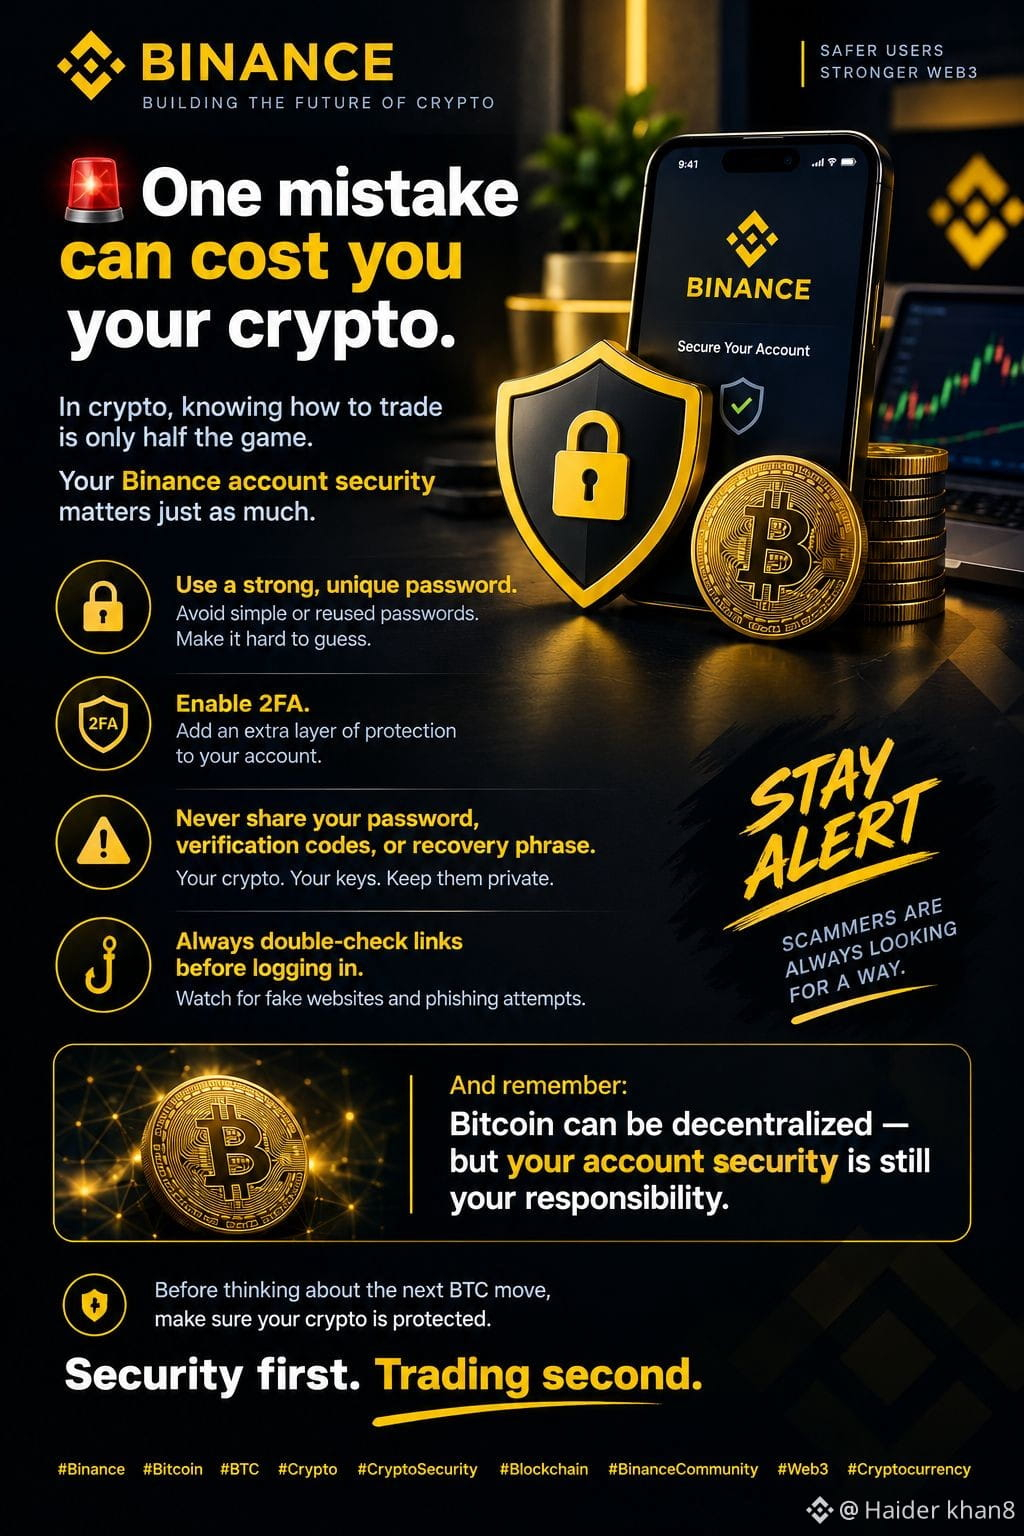
🚨 One mistake can cost you your crypto. In crypto, knowing how to trade is only half the game. Your Binance account security matters just as much. 🔐 Use a strong, unique password. 🛡️ Enable 2FA. ⚠️ Never share your password, verification codes, or recovery phrase. 🎣 Always double-check links before logging in. And remember: Bitcoin can be decentralized — but your account security is still your responsibility. Before thinking about the next BTC move, make sure your crypto is protected. Security first. Trading second. #crypto #CryptoSecurity #blockchain #BinanceCommunity #Web3
🚨 One mistake can cost you your crypto.
In crypto, knowing how to trade is only half the game.
Your Binance account security matters just as much.
🔐 Use a strong, unique password.
🛡️ Enable 2FA.
⚠️ Never share your password, verification codes, or recovery phrase.
🎣 Always double-check links before logging in.
And remember:
Bitcoin can be decentralized — but your account security is still your responsibility.
Before thinking about the next BTC move, make sure your crypto is protected.
Security first. Trading second.
#crypto #CryptoSecurity #blockchain #BinanceCommunity #Web3
Boston Red Sox vs. New York Yankees

Boston Red Sox vs. New York Yankees

1%BOS99%NYY
Көлем $138,080.35
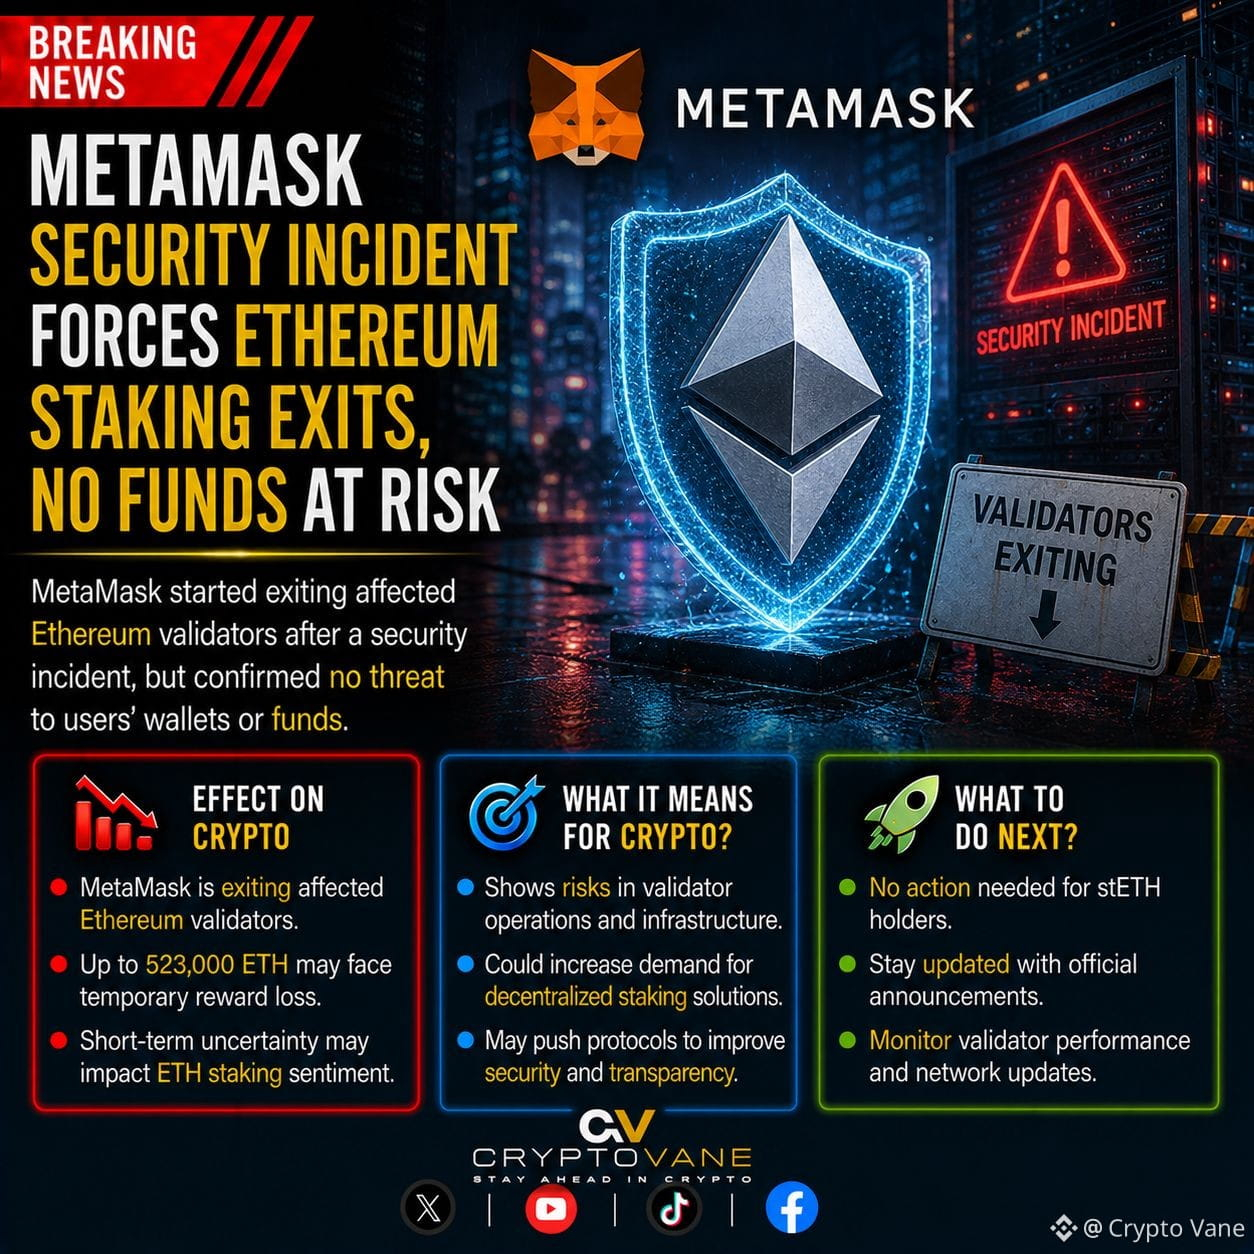
MetaMask Security Incident Triggers $ETH Validator Exits 🚨 MetaMask began exiting affected $ETH validators after a security incident involving staking infrastructure, while saying user wallets and funds were not at risk. The event highlights validator security concerns and potential short-term effects on Ethereum staking rewards. #Ethereum #MetaMask #ETH #CryptoNews #CryptoSecurity {spot}(ETHUSDT)
MetaMask Security Incident Triggers $ETH Validator Exits 🚨

MetaMask began exiting affected $ETH validators after a security incident involving staking infrastructure, while saying user wallets and funds were not at risk. The event highlights validator security concerns and potential short-term effects on Ethereum staking rewards.
#Ethereum #MetaMask #ETH #CryptoNews #CryptoSecurity
A crypto wallet is more than an app on your phone. It is an important part of managing digital assets, which is why understanding wallet security and private keys is essential. Stay informed. 🔐 #CryptoSecurity #Wallet #cryptoeducation
A crypto wallet is more than an app on your phone.

It is an important part of managing digital assets, which is why understanding wallet security and private keys is essential.

Stay informed. 🔐

#CryptoSecurity #Wallet #cryptoeducation
قد تخسر عملاتك دون أن يهبط سعرها! ⚠️ الروابط المزيفة، والتوكنات الوهمية، ورسائل الجوائز المجانية قد تعرض محفظتك للخطر. 🔐 لا تشارك عبارة الاسترداد مع أي شخص. 🔐 لا توقع معاملة لا تفهمها. 🔐 تحقّق من عنوان الموقع والعقد الذكي. 🔐 لا تثق في وعد يضمن لك مضاعفة أموالك. أمان المحفظة جزء أساسي من الاستثمار، وليس تفصيلًا ثانويًا. 💬 هل تريدون سلسلة منشورات عن حماية محافظ Binance وWeb3؟ #Web3 #CryptoSecurity
قد تخسر عملاتك دون أن يهبط سعرها! ⚠️

الروابط المزيفة، والتوكنات الوهمية، ورسائل الجوائز المجانية قد تعرض محفظتك للخطر.

🔐 لا تشارك عبارة الاسترداد مع أي شخص.
🔐 لا توقع معاملة لا تفهمها.
🔐 تحقّق من عنوان الموقع والعقد الذكي.
🔐 لا تثق في وعد يضمن لك مضاعفة أموالك.

أمان المحفظة جزء أساسي من الاستثمار، وليس تفصيلًا ثانويًا.

💬 هل تريدون سلسلة منشورات عن حماية محافظ Binance وWeb3؟

#Web3 #CryptoSecurity
·
--
Hardware wallet best practices 🛡️ Keep your Ledger/Trezor offline most of the time ✅ Only connect when making transactions 🔌 Never enter PIN on public WiFi or shared computers 📵 Store seed phrase in a safe (not on your phone!) 🏠 #HardwareWallet #CryptoSecurity #BestPractices .
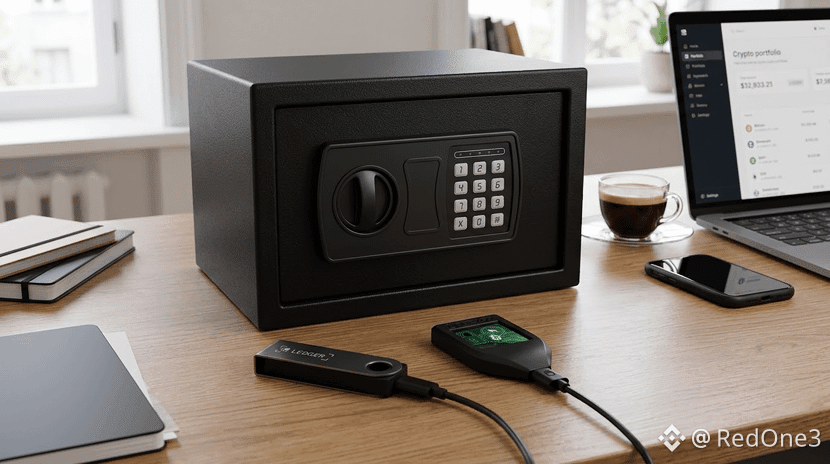
Hardware wallet best practices 🛡️

Keep your Ledger/Trezor offline most of the time ✅
Only connect when making transactions 🔌

Never enter PIN on public WiFi or shared computers 📵

Store seed phrase in a safe (not on your phone!) 🏠

#HardwareWallet #CryptoSecurity #BestPractices .
MPC Does Not Replace PolicyMulti-party computation can remove one complete private key as a single point of failure. Several participants hold separate shares and cooperate to produce one valid signature only when the threshold is met. That is valuable, but the threshold is not the complete security model. The operational question is what causes those shares to participate. If an internal service can create a signing request without passing the expected checks, or if the signers accept a vague instruction that is not bound to the exact transaction, the system can produce a cryptographically valid signature for an unauthorized action. A serious MPC design should bind approval to the chain, destination, value, calldata, fees, nonce policy and expiry. Signers should verify the approval bundle before participating. Shares should be separated across real failure domains, not placed under one cloud account, one administrator or one vendor-controlled path. Policy changes need stronger controls than routine transactions. Emergency recovery should be slower, separately governed and tested. Monitoring should compare approved intent with the transaction that was actually broadcast. MPC protects key control. It does not automatically prove that the request is legitimate or economically safe. TokenToolHub explains threshold signing, policy bypass, share refresh, monitoring and recovery design: https://tokentoolhub.com/multi-party-computation-mpc-web3/ #CryptoSecurity #MPC #blockchain #Web3 #wallets

MPC Does Not Replace Policy

Multi-party computation can remove one complete private key as a single point of failure. Several participants hold separate shares and cooperate to produce one valid signature only when the threshold is met.
That is valuable, but the threshold is not the complete security model.
The operational question is what causes those shares to participate. If an internal service can create a signing request without passing the expected checks, or if the signers accept a vague instruction that is not bound to the exact transaction, the system can produce a cryptographically valid signature for an unauthorized action.
A serious MPC design should bind approval to the chain, destination, value, calldata, fees, nonce policy and expiry. Signers should verify the approval bundle before participating. Shares should be separated across real failure domains, not placed under one cloud account, one administrator or one vendor-controlled path.
Policy changes need stronger controls than routine transactions. Emergency recovery should be slower, separately governed and tested. Monitoring should compare approved intent with the transaction that was actually broadcast.
MPC protects key control. It does not automatically prove that the request is legitimate or economically safe.
TokenToolHub explains threshold signing, policy bypass, share refresh, monitoring and recovery design:
https://tokentoolhub.com/multi-party-computation-mpc-web3/
#CryptoSecurity #MPC #blockchain #Web3 #wallets
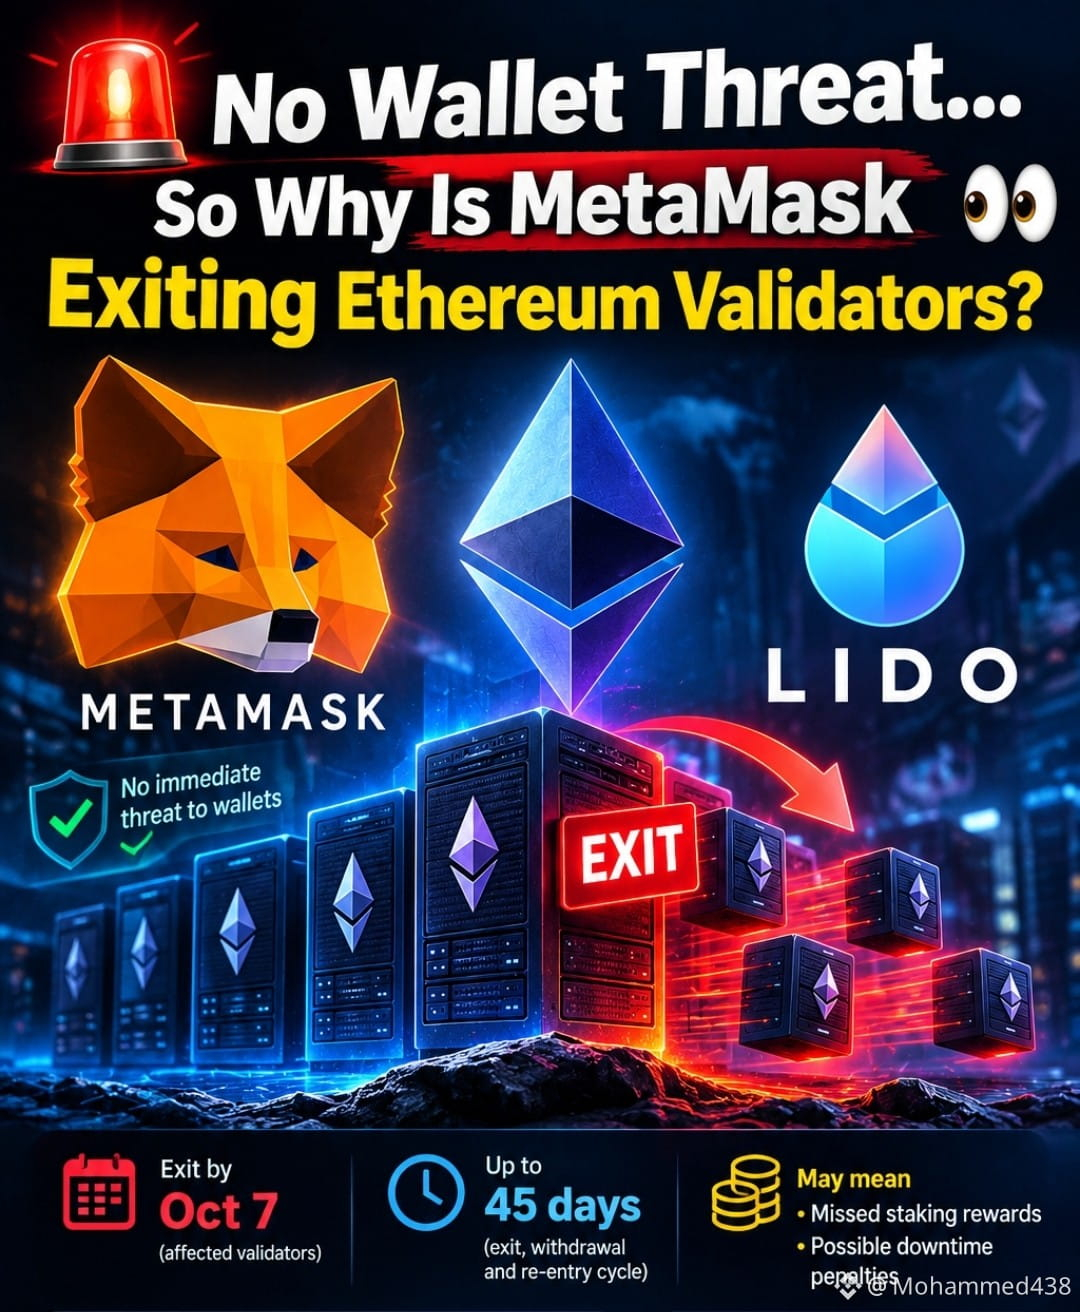
#metamaskexitslidovalidatorsaftersecurityincident 🚨 No Wallet Threat… So Why Is MetaMask Exiting Ethereum Validators? 👀 MetaMask is responding to a security incident affecting part of its infrastructure and has started proactively exiting affected Ethereum validators connected to its non-custodial staking operations. MetaMask says it has identified no immediate threat to its wallets. But here’s the part traders should watch Lido says the affected validators are expected to exit by October 7, while the ETH could take up to around 45 days to complete the exit, withdrawal and re-entry cycle. The process may also mean missed staking rewards and possible downtime penalties. The key market question now: Could this remain an isolated infrastructure issue, or will the investigation create broader caution around Ethereum staking and DeFi? For $ETH {spot}(ETHUSDT) and $LDO {spot}(LDOUSDT) , the next security update could matter more than the initial headline. The incident is still developing. 👀 #Lido #LDO #CryptoSecurity
#metamaskexitslidovalidatorsaftersecurityincident 🚨 No Wallet Threat… So Why Is MetaMask Exiting Ethereum Validators? 👀
MetaMask is responding to a security incident affecting part of its infrastructure and has started proactively exiting affected Ethereum validators connected to its non-custodial staking operations. MetaMask says it has identified no immediate threat to its wallets.
But here’s the part traders should watch
Lido says the affected validators are expected to exit by October 7, while the ETH could take up to around 45 days to complete the exit, withdrawal and re-entry cycle. The process may also mean missed staking rewards and possible downtime penalties.
The key market question now:
Could this remain an isolated infrastructure issue, or will the investigation create broader caution around Ethereum staking and DeFi?
For $ETH
and $LDO
, the next security update could matter more than the initial headline.
The incident is still developing. 👀
#Lido #LDO #CryptoSecurity
🚨 MetaMask has exited Ethereum validators while investigating a security incident, stating no immediate threat to wallets was found. This move may signal caution among infrastructure players, potentially affecting short-term ETH staking sentiment. Watch for further updates on validator activity and network security developments. How might this influence ETH’s near-term price action? #CryptoSecurity $ETH #TradingSignal #CryptoAnalysis
🚨 MetaMask has exited Ethereum validators while investigating a security incident, stating no immediate threat to wallets was found.
This move may signal caution among infrastructure players, potentially affecting short-term ETH staking sentiment.
Watch for further updates on validator activity and network security developments.
How might this influence ETH’s near-term price action?
#CryptoSecurity

$ETH #TradingSignal #CryptoAnalysis
🚨 Major Crypto Hacks Have Shaken the Industry in 2026 2026 has been marked by several major security incidents across the crypto industry. Billions of dollars in digital assets have been affected by exploits and hacks, highlighting the importance of security in both DeFi protocols and centralized exchanges. One of the biggest incidents involved KelpDAO, which lost approximately $292 million in April. Attackers exploited a vulnerability in its LayerZero-powered bridge and drained around 116,500 rsETH, representing roughly 18% of the token's circulating supply. Drift Protocol was also hit by a major attack, with approximately $285 million drained from its vaults. Blockaid described it as a sophisticated governance-layer attack that exploited weaknesses in the protocol's operational security. In September, Liquid Network suffered an exploit involving approximately $320 million worth of Bitcoin. Attackers exploited a vulnerability in the transaction-validation system to withdraw BTC from the network's reserves. Around 85% of the withdrawn Bitcoin was later returned. Most recently, Bitget suffered a major security incident on September 24. The exchange initially estimated the loss at around $351.6 million, with subsequent analysis putting the figure at approximately $387.5 million. Bitget stated that its cold wallets remained secure and that the loss would be covered by its User Protection Fund. The investigation is ongoing. These incidents are a reminder that crypto security remains one of the most important issues in the industry. What do you think is the biggest security risk in crypto today — DeFi bridges, smart contracts, governance systems, or centralized exchanges? #Crypto #Bitcoin #BTC #Ethereum #ETH #DeFi #CryptoSecurity
🚨 Major Crypto Hacks Have Shaken the Industry in 2026

2026 has been marked by several major security incidents across the crypto industry. Billions of dollars in digital assets have been affected by exploits and hacks, highlighting the importance of security in both DeFi protocols and centralized exchanges.

One of the biggest incidents involved KelpDAO, which lost approximately $292 million in April. Attackers exploited a vulnerability in its LayerZero-powered bridge and drained around 116,500 rsETH, representing roughly 18% of the token's circulating supply.

Drift Protocol was also hit by a major attack, with approximately $285 million drained from its vaults. Blockaid described it as a sophisticated governance-layer attack that exploited weaknesses in the protocol's operational security.

In September, Liquid Network suffered an exploit involving approximately $320 million worth of Bitcoin. Attackers exploited a vulnerability in the transaction-validation system to withdraw BTC from the network's reserves. Around 85% of the withdrawn Bitcoin was later returned.

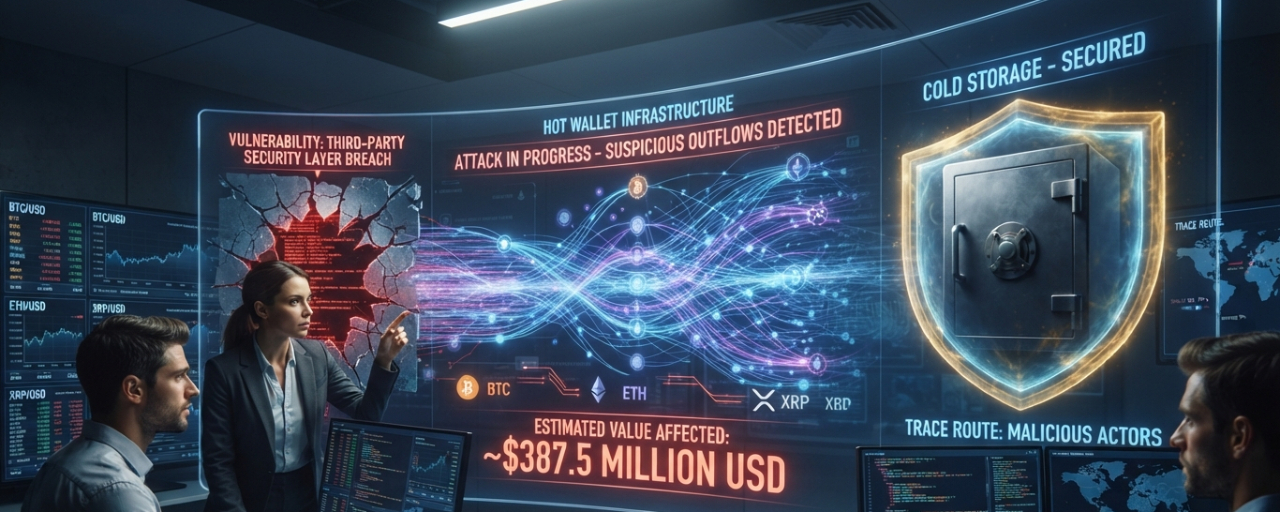
Most recently, Bitget suffered a major security incident on September 24. The exchange initially estimated the loss at around $351.6 million, with subsequent analysis putting the figure at approximately $387.5 million. Bitget stated that its cold wallets remained secure and that the loss would be covered by its User Protection Fund. The investigation is ongoing.

These incidents are a reminder that crypto security remains one of the most important issues in the industry.

What do you think is the biggest security risk in crypto today — DeFi bridges, smart contracts, governance systems, or centralized exchanges?

#Crypto #Bitcoin #BTC #Ethereum #ETH #DeFi #CryptoSecurity
·
--
📚 **Hardware Wallets: Do You Really Need One?** If you hold more than a few hundred dollars in crypto, the answer is likely yes. While hot wallets (apps/exchanges) offer convenience, they are vulnerable to online attacks. A hardware wallet is a physical device (like a USB stick) that stores your private keys offline. **How it works:** Your keys never leave the device. To sign a transaction, you connect to a computer or phone via USB or Bluetooth. The device generates the signature internally, ensuring your secret keys remain isolated from the internet. It’s like a digital safe that only opens when you physically press a button. **Key Benefits:** 1. **Security:** Keeps keys offline, protecting them from hackers, malware, and phishing. 2. **Control:** You are the bank. No third party can freeze your assets. 3. **Multi-Asset Support:** Most devices support BTC, ETH, and thousands of tokens. **Common Mistakes to Avoid:** ❌ Buying from unofficial resellers (risk of pre-seeded malware). ❌ Losing your recovery seed. **Write it on paper.** Never take a photo or store it digitally. If you lose the seed and the device, your funds are gone forever. ❌ Trusting "free" giveaways. Always buy directly from official websites. **Pro Tip:** Treat your recovery phrase like a nuclear code. Store it in a fireproof safe or split it between two secure locations. If you are a long-term holder, the small cost of a hardware wallet is the best insurance premium you will ever pay. Don't let convenience compromise security. Are you ready to take full control of your digital assets? $BTC #CryptoSecurity #HardwareWallet $OCEAN #DYOR #BitcoinNews
📚 **Hardware Wallets: Do You Really Need One?** If you hold more than a few hundred dollars in crypto, the answer is likely yes. While hot wallets (apps/exchanges) offer convenience, they are vulnerable to online attacks. A hardware wallet is a physical device (like a USB stick) that stores your private keys offline. **How it works:** Your keys never leave the device. To sign a transaction, you connect to a computer or phone via USB or Bluetooth. The device generates the signature internally, ensuring your secret keys remain isolated from the internet. It’s like a digital safe that only opens when you physically press a button. **Key Benefits:** 1. **Security:** Keeps keys offline, protecting them from hackers, malware, and phishing. 2. **Control:** You are the bank. No third party can freeze your assets. 3. **Multi-Asset Support:** Most devices support BTC, ETH, and thousands of tokens. **Common Mistakes to Avoid:** ❌ Buying from unofficial resellers (risk of pre-seeded malware). ❌ Losing your recovery seed. **Write it on paper.** Never take a photo or store it digitally. If you lose the seed and the device, your funds are gone forever. ❌ Trusting "free" giveaways. Always buy directly from official websites. **Pro Tip:** Treat your recovery phrase like a nuclear code. Store it in a fireproof safe or split it between two secure locations. If you are a long-term holder, the small cost of a hardware wallet is the best insurance premium you will ever pay. Don't let convenience compromise security. Are you ready to take full control of your digital assets? $BTC #CryptoSecurity #HardwareWallet

$OCEAN
#DYOR #BitcoinNews
🔷 Bitget is getting back to normal — but the real test is still ahead. After the $388M breach, withdrawals are being restored and the Protection Fund has reached $309M. But recovery ≠ resolution. ~$3.8M in stolen $ZEC was reportedly moved into Ironwood, showing that the fund-tracing process is still active. The next signal to watch isn’t just withdrawals reopening. It’s how much of the stolen funds can actually be recovered — and whether confidence fully returns. #Bitget #CryptoSecurity #ZEC $ZEC
🔷 Bitget is getting back to normal — but the real test is still ahead.

After the $388M breach, withdrawals are being restored and the Protection Fund has reached $309M.

But recovery ≠ resolution.

~$3.8M in stolen $ZEC was reportedly moved into Ironwood, showing that the fund-tracing process is still active.

The next signal to watch isn’t just withdrawals reopening.

It’s how much of the stolen funds can actually be recovered — and whether confidence fully returns.

#Bitget #CryptoSecurity #ZEC $ZEC
·
--
Crypto Security Is Back In Focus After a Major Exchange Breach 🎯   A major crypto-platform security incident has put exchange and wallet risk back at the center of the market conversation.   Public reports indicate hundreds of millions of dollars in customer withdrawals were affected, while investigations focused on compromised internal access and infrastructure vulnerabilities. The incident is a reminder of a basic rule in crypto:   Market risk is not the only risk. Operational security matters too.   For users, that means treating account protection as seriously as price volatility:   Use strong, unique passwords   Enable two-factor authentication   Review withdrawal and device settings   Be cautious with phishing links and impersonation messages   Understand where and how assets are held   This does not change the underlying blockchain technology—but it reinforces why custody, platform controls, and user security habits remain critical.   #CryptoSecurity #Web3Safety #Write2Earn Follow For more Update News... @5ur1d @Square-Creator-4f1968b4bd55 @Square-Creator-e36956b8e5e4f @crypto_inquiad    
Crypto Security Is Back In Focus After a Major Exchange Breach 🎯

A major crypto-platform security incident has put exchange and wallet risk back at the center of the market conversation.

Public reports indicate hundreds of millions of dollars in customer withdrawals were affected, while investigations focused on compromised internal access and infrastructure vulnerabilities. The incident is a reminder of a basic rule in crypto:

Market risk is not the only risk. Operational security matters too.

For users, that means treating account protection as seriously as price volatility:

Use strong, unique passwords

Enable two-factor authentication

Review withdrawal and device settings

Be cautious with phishing links and impersonation messages

Understand where and how assets are held

This does not change the underlying blockchain technology—but it reinforces why custody, platform controls, and user security habits remain critical.

#CryptoSecurity #Web3Safety #Write2Earn

Follow For more Update News...

@TAJBI
@Marco cryptos
@NIRJHOR CRYPTO
@CRYPTO INQUIAD

Мақала
🕵️‍♂️ Анатомия крипто-мошенничества: 5 уловок, на которые до сих пор попадаются новичкиКрипторынок дает невероятные возможности для заработка, но у этой медали есть и обратная, очень темная сторона. Из-за необратимости блокчейн-транзакций (если вы отправили монеты мошеннику, их уже никто не сможет вернуть) крипта стала излюбленным местом для скамеров всех мастей. Каждый день в сети появляются изощренные схемы, созданные с одной целью — опустошить ваши кошельки. И чаще всего под удар попадают новички, ослепленные жаждой легких денег. 🚨 1. Фальшивая «Служба поддержки» в Telegram и Discord Вы заходите в официальный чат криптопроекта или биржи, чтобы задать технический вопрос. Буквально через минуту вам в личные сообщения пишет человек с официальным логотипом на аватарке и никнеймом вроде Binance_Support_Robot. Он очень вежлив, предлагает помочь и просит вас... «верифицировать кошелек», прислав ему вашу сид-фразу (12-24 слова) или перейдя по специальной ссылке. 🧠 В чем суть: Официальная поддержка НИКОГДА не пишет первой в личные сообщения и НИКОГДА не запрашивает ваши пароли, приватные ключи или сид-фразы. Всё, что вам написали в ЛС без вашего запроса — это 100% скам. 🌐 2. Фишинг: Сайты-двойники Вы хотите зайти на любимую биржу, децентрализованный кошелек или платформу для стейкинга. Вбиваете название в поисковике, кликаете на первую ссылку, вводите логин, пароль и код двухфакторной аутентификации (2FA). Но вместо личного кабинета видите ошибку. В этот момент мошенники на другом конце провода уже получили ваши данные и выводят деньги. 🧠 В чем суть: Злоумышленники создают идеальные копии сайтов, которые отличаются от оригинала всего одной незаметной буквой в веб-адресе (например, biinance.com вместо binance.com).🛠 Защита: Всегда проверяйте адресную строку и сохраняйте официальные сайты в закладки браузера. 🎁 3. Фальшивые эирдропы (Giveaways) от имени Илона Маска или Виталика Бутерина Вы листаете соцсети или YouTube и видите «прямую трансляцию» с известной крипто-персоной. На экране горит заманчивое предложение: «В честь праздника мы раздаем 1000 BTC! Отправь от 0.1 до 1 $BTC на этот кошелек, и мы мгновенно вернем тебе сумму в двойном размере!». 🧠 В чем суть: Это классическая схема «аттракциона невиданной щедрости». Никакой трансляции нет — это крутится старая видеозапись (часто сгенерированная или измененная с помощью ИИ/дипфейков). Все отправленные монеты уходят мошенникам навсегда. Помните: бесплатного сыра в крипте не бывает. 📈 4. Метод Rug Pull («Выдергивание ковра») Вам предлагают купить совершенно новый, «инновационный» мем-коин или токен, который вот-вот сделает 1000х. График монеты летит строго вверх, в соцсегментах дикий хайп. Вы покупаете токен, цена растет, вы хотите его продать и зафиксировать прибыль... но кнопка «Продать» просто не работает в смарт-контракте, либо создатели проекта внезапно забирают всю ликвидность из пула и исчезают. 🧠 В чем суть: Мошенники сами раскручивают цену своего токена, привлекают деньги доверчивых инвесторов, а затем мгновенно обесценивают монету до нуля, оставляя вас с кучей бесполезных фантиков. 🤖 5. Скам-боты для «автоматического заработка» Вам рекламируют чудо-бота в Telegram или секретную торговую стратегию (например, «арбитражная связка с доходностью 20% в день»). Всё, что нужно — перевести деньги на баланс бота, и он начнет генерировать вам пассивный доход. Первые пару дней вам даже могут рисовать красивую прибыль на экране, но при попытке вывода средств бот потребует «оплатить налог», а затем вас просто заблокируют. 🧠 В чем суть: Любой бот или платформа, гарантирующие фиксированный высокий доход в крипте без риска — это финансовая пирамида (хайп) или прямой грабеж. 🗒 Главное золотое правило безопасности Криптобезопасность держится на одном ментальном правиле: подвергайте сомнению всё. Никогда и никому не передавайте свою сид-фразу (храните её только на бумаге в надежном месте), не переходите по подозрительным ссылкам из чатов и всегда проводите собственный анализ проектов (DYOR). Ваша безопасность — исключительно в ваших руках.$BNB ⚠️ Дисклеймер: Не финансовая рекомендация (DYOR). Данный материал создан исключительно в образовательных целях, чтобы повысить финансовую грамотность сообщества и защитить пользователей от потенциальных потерь. #CryptoSecurity #SAFU🙏 #ScamAlert #cryptoeducation #cryptoland_88 $SOL {spot}(SOLUSDT)

🕵️‍♂️ Анатомия крипто-мошенничества: 5 уловок, на которые до сих пор попадаются новички

Крипторынок дает невероятные возможности для заработка, но у этой медали есть и обратная, очень темная сторона. Из-за необратимости блокчейн-транзакций (если вы отправили монеты мошеннику, их уже никто не сможет вернуть) крипта стала излюбленным местом для скамеров всех мастей.
Каждый день в сети появляются изощренные схемы, созданные с одной целью — опустошить ваши кошельки. И чаще всего под удар попадают новички, ослепленные жаждой легких денег.
🚨 1. Фальшивая «Служба поддержки» в Telegram и Discord
Вы заходите в официальный чат криптопроекта или биржи, чтобы задать технический вопрос. Буквально через минуту вам в личные сообщения пишет человек с официальным логотипом на аватарке и никнеймом вроде Binance_Support_Robot. Он очень вежлив, предлагает помочь и просит вас... «верифицировать кошелек», прислав ему вашу сид-фразу (12-24 слова) или перейдя по специальной ссылке.
🧠 В чем суть: Официальная поддержка НИКОГДА не пишет первой в личные сообщения и НИКОГДА не запрашивает ваши пароли, приватные ключи или сид-фразы. Всё, что вам написали в ЛС без вашего запроса — это 100% скам.
🌐 2. Фишинг: Сайты-двойники
Вы хотите зайти на любимую биржу, децентрализованный кошелек или платформу для стейкинга. Вбиваете название в поисковике, кликаете на первую ссылку, вводите логин, пароль и код двухфакторной аутентификации (2FA). Но вместо личного кабинета видите ошибку. В этот момент мошенники на другом конце провода уже получили ваши данные и выводят деньги.
🧠 В чем суть: Злоумышленники создают идеальные копии сайтов, которые отличаются от оригинала всего одной незаметной буквой в веб-адресе (например, biinance.com вместо binance.com).🛠 Защита: Всегда проверяйте адресную строку и сохраняйте официальные сайты в закладки браузера.
🎁 3. Фальшивые эирдропы (Giveaways) от имени Илона Маска или Виталика Бутерина
Вы листаете соцсети или YouTube и видите «прямую трансляцию» с известной крипто-персоной. На экране горит заманчивое предложение: «В честь праздника мы раздаем 1000 BTC! Отправь от 0.1 до 1 $BTC на этот кошелек, и мы мгновенно вернем тебе сумму в двойном размере!».
🧠 В чем суть: Это классическая схема «аттракциона невиданной щедрости». Никакой трансляции нет — это крутится старая видеозапись (часто сгенерированная или измененная с помощью ИИ/дипфейков). Все отправленные монеты уходят мошенникам навсегда. Помните: бесплатного сыра в крипте не бывает.
📈 4. Метод Rug Pull («Выдергивание ковра»)
Вам предлагают купить совершенно новый, «инновационный» мем-коин или токен, который вот-вот сделает 1000х. График монеты летит строго вверх, в соцсегментах дикий хайп. Вы покупаете токен, цена растет, вы хотите его продать и зафиксировать прибыль... но кнопка «Продать» просто не работает в смарт-контракте, либо создатели проекта внезапно забирают всю ликвидность из пула и исчезают.
🧠 В чем суть: Мошенники сами раскручивают цену своего токена, привлекают деньги доверчивых инвесторов, а затем мгновенно обесценивают монету до нуля, оставляя вас с кучей бесполезных фантиков.
🤖 5. Скам-боты для «автоматического заработка»
Вам рекламируют чудо-бота в Telegram или секретную торговую стратегию (например, «арбитражная связка с доходностью 20% в день»). Всё, что нужно — перевести деньги на баланс бота, и он начнет генерировать вам пассивный доход. Первые пару дней вам даже могут рисовать красивую прибыль на экране, но при попытке вывода средств бот потребует «оплатить налог», а затем вас просто заблокируют.
🧠 В чем суть: Любой бот или платформа, гарантирующие фиксированный высокий доход в крипте без риска — это финансовая пирамида (хайп) или прямой грабеж.
🗒 Главное золотое правило безопасности
Криптобезопасность держится на одном ментальном правиле: подвергайте сомнению всё. Никогда и никому не передавайте свою сид-фразу (храните её только на бумаге в надежном месте), не переходите по подозрительным ссылкам из чатов и всегда проводите собственный анализ проектов (DYOR). Ваша безопасность — исключительно в ваших руках.$BNB
⚠️ Дисклеймер: Не финансовая рекомендация (DYOR). Данный материал создан исключительно в образовательных целях, чтобы повысить финансовую грамотность сообщества и защитить пользователей от потенциальных потерь.
#CryptoSecurity #SAFU🙏 #ScamAlert #cryptoeducation #cryptoland_88 $SOL
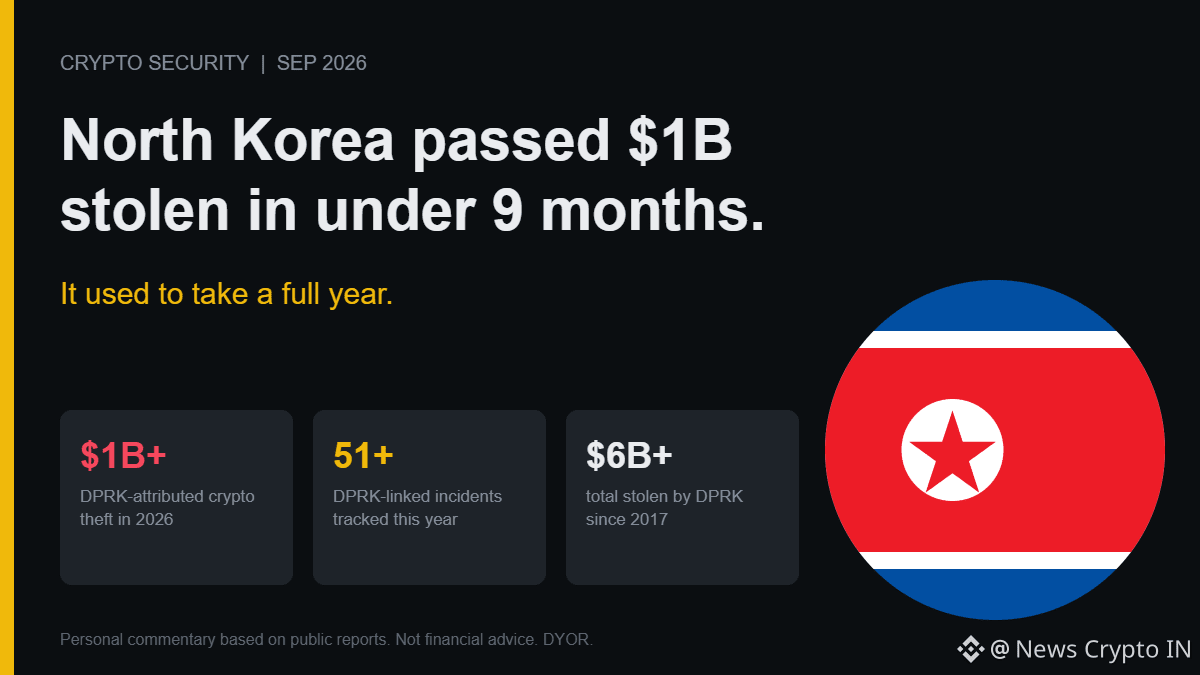
North Korea just crossed $1 billion in crypto theft for 2026, and did it in under 9 months. Last year that milestone took a full 12. The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes. The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access. Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence. At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis? #Lazarus #CryptoSecurity
North Korea just crossed $1 billion in crypto theft for 2026, and did it in under 9 months. Last year that milestone took a full 12.

The Bitget hack ($387.5M, confirmed Sept 24) pushed the total over the line. Elliptic has tracked 51+ DPRK-linked incidents this year alone, part of a cumulative haul north of $6B since 2017. Another 2026 example: the Drift Protocol attack, where social engineering moved $285M out in 12 minutes.

The acceleration matters more than the total. A state actor getting faster at extracting nine-figure sums means the industry's security model isn't just losing dollars, it's losing the race. Exchanges harden one attack surface (hot wallets, smart contract audits), and the next hit comes through a different door: spoofed transfers, social engineering, insider access.

Not every attribution is airtight; Bitget's own CEO called the tactics "consistent with" DPRK groups, not confirmed Lazarus. But the pattern across 51 incidents this year is hard to wave away as coincidence.

At this pace, when does $1B/year in state-sponsored theft become a cost the industry just prices in, instead of a crisis?

#Lazarus #CryptoSecurity
·
--
Los hackers de Bitget continúan moviendo capitales sustanciales. Recientemente, trasladaron 4 millones de dólares hacia el pool privado de Zcash, complicando severamente su trazabilidad en la cadena. 🕵️‍♂️💸 Este movimiento resalta los persistentes desafíos regulatorios y de seguridad en torno a las criptomonedas con privacidad avanzada, un vector que los exchanges y las autoridades monitorean muy de cerca ante incidentes de este calibre. ¿Qué vigilar? La respuesta de los exchanges centralizados ante protocolos de privacidad y las posibles contramedidas regulatorias que esto desencadene en el corto plazo. 🛡️ #Zcash #CryptoSecurity #DeFi #Privacidad En radar: $ETH $BTC
Los hackers de Bitget continúan moviendo capitales sustanciales. Recientemente, trasladaron 4 millones de dólares hacia el pool privado de Zcash, complicando severamente su trazabilidad en la cadena. 🕵️‍♂️💸

Este movimiento resalta los persistentes desafíos regulatorios y de seguridad en torno a las criptomonedas con privacidad avanzada, un vector que los exchanges y las autoridades monitorean muy de cerca ante incidentes de este calibre.

¿Qué vigilar? La respuesta de los exchanges centralizados ante protocolos de privacidad y las posibles contramedidas regulatorias que esto desencadene en el corto plazo. 🛡️

#Zcash #CryptoSecurity #DeFi #Privacidad

En radar: $ETH $BTC
Мақала
Bitget’s $387M Breach Exposes a Hidden Crypto Security Risk🚨 Bitget’s security breach exposed a bigger crypto risk. 👀🔐 Around $387.5M in assets were transferred from a portion of Bitget’s hot and warm wallet infrastructure on September 24. But here's the important part: 🔐 Cold wallets were not affected 🗝️ Private keys were not compromised 🛡️ User account balances remained unaffected Bitget says the attacker exploited a vulnerability in a third party security product, obtained high level internal credentials and used them to send fraudulent withdrawal commands. The vulnerability has since been remediated, while Mandiant and SlowMist are assisting with the investigation. The bigger lesson? Crypto security isn't only about protecting private keys. A weak third party dependency can become another path into critical infrastructure. 🏦 Exchanges 🔐 Security vendors ⚙️ Internal access 🛡️ Withdrawal controls The attack may be contained, but the industry question remains: 👀 How much should crypto platforms trust third party security infrastructure? $BTC $ETH $XRP #CryptoSecurity {future}(ZAMAUSDT) {future}(MARSCOINUSDT) {future}(HBARUSDT) #Bitget #CryptoNews #Web3Safety #RiskManagement

Bitget’s $387M Breach Exposes a Hidden Crypto Security Risk

🚨 Bitget’s security breach exposed a bigger crypto risk. 👀🔐
Around $387.5M in assets were transferred from a portion of Bitget’s hot and warm wallet infrastructure on September 24.
But here's the important part:
🔐 Cold wallets were not affected
🗝️ Private keys were not compromised
🛡️ User account balances remained unaffected
Bitget says the attacker exploited a vulnerability in a third party security product, obtained high level internal credentials and used them to send fraudulent withdrawal commands.
The vulnerability has since been remediated, while Mandiant and SlowMist are assisting with the investigation.
The bigger lesson?
Crypto security isn't only about protecting private keys.
A weak third party dependency can become another path into critical infrastructure.
🏦 Exchanges
🔐 Security vendors
⚙️ Internal access
🛡️ Withdrawal controls
The attack may be contained, but the industry question remains:
👀 How much should crypto platforms trust third party security infrastructure?
$BTC $ETH $XRP
#CryptoSecurity
#Bitget #CryptoNews #Web3Safety #RiskManagement
🚨 8 Crypto Transfer Mistakes You Should Avoid on Binance Sending crypto is fast and convenient, but one small mistake can sometimes lead to a transaction that is difficult or impossible to recover. Before sending $USDT, $BTC, $ETH or any other crypto, take a few seconds to check these 8 things 👇 1️⃣ Check the wallet address Always verify the destination address carefully. Never send funds to an address from an unknown or suspicious source. 2️⃣ Choose the correct network This is extremely important. Make sure the network you select is supported by the receiving wallet or platform. 3️⃣ Double-check the amount Before confirming, verify the amount, fees and final amount that will be received. 4️⃣ Check the Memo or Tag Some deposits require a Memo, Tag or similar information. If the receiving platform asks for one, make sure you enter it correctly. 5️⃣ Consider a small test transaction When using a new address for the first time, a small test transfer can help confirm that the address and network are correct before sending a larger amount. 6️⃣ Beware of fake support Binance support will never need your private key or wallet seed phrase. Never share your password, seed phrase or security codes with anyone. 7️⃣ Don't assume the same token means the same network A cryptocurrency can exist on multiple networks. Always check the network on both the sending and receiving sides. 8️⃣ Keep your transaction ID After sending crypto, save the TXID or transaction hash when available. It can help you track the transaction on the blockchain. ✅ My 30-second checklist: Address → Network → Amount → Memo/Tag → Fees → Destination Crypto transactions can be irreversible, so don't rush. Take 30 seconds to verify everything before pressing Confirm. What is the most common crypto transfer mistake you've seen? 👇 #Binance #BinanceSquare #Crypto #CryptoTips #Bitcoin #Ethereum #USDT#BTC #ETH #Web3 #CryptoSecurity
🚨 8 Crypto Transfer Mistakes You Should Avoid on Binance

Sending crypto is fast and convenient, but one small mistake can sometimes lead to a transaction that is difficult or impossible to recover.

Before sending $USDT, $BTC, $ETH or any other crypto, take a few seconds to check these 8 things 👇

1️⃣ Check the wallet address
Always verify the destination address carefully. Never send funds to an address from an unknown or suspicious source.

2️⃣ Choose the correct network
This is extremely important. Make sure the network you select is supported by the receiving wallet or platform.

3️⃣ Double-check the amount
Before confirming, verify the amount, fees and final amount that will be received.

4️⃣ Check the Memo or Tag
Some deposits require a Memo, Tag or similar information. If the receiving platform asks for one, make sure you enter it correctly.

5️⃣ Consider a small test transaction
When using a new address for the first time, a small test transfer can help confirm that the address and network are correct before sending a larger amount.

6️⃣ Beware of fake support
Binance support will never need your private key or wallet seed phrase. Never share your password, seed phrase or security codes with anyone.

7️⃣ Don't assume the same token means the same network
A cryptocurrency can exist on multiple networks. Always check the network on both the sending and receiving sides.

8️⃣ Keep your transaction ID
After sending crypto, save the TXID or transaction hash when available. It can help you track the transaction on the blockchain.

✅ My 30-second checklist:

Address → Network → Amount → Memo/Tag → Fees → Destination

Crypto transactions can be irreversible, so don't rush. Take 30 seconds to verify everything before pressing Confirm.

What is the most common crypto transfer mistake you've seen? 👇

#Binance #BinanceSquare #Crypto #CryptoTips #Bitcoin #Ethereum #USDT#BTC #ETH #Web3 #CryptoSecurity
Көбірек контент көру үшін кіріңіз
Binance Square платформасында әлемдік криптоқоғамдастыққа қосылыңыз
⚡️ Криптовалюта туралы ең соңғы және пайдалы ақпаратты алыңыз.
💬 Әлемдегі ең ірі криптобиржаның сеніміне ие.
👍 Расталған авторлардың нақты пікірлерін табыңыз.
Электрондық пошта/телефон нөмірі