
#lazarus
lazarus
453,265 views
143 Discussing
Hot
Latest
·
--
🚨 The $625M Fake Job Offer: How Lazarus Infiltrated Axie Infinity! 🎣💸
In 2022, North Korea’s notorious Lazarus Group executed one of the largest heists in crypto history, draining $625 million from the Ronin Network (the sidechain behind Axie Infinity).
They didn't break complex smart contracts. Instead, they targeted the oldest vulnerability in tech: human psychology.
The attackers set up a fake recruitment agency and spent weeks courting a senior engineer with a high-paying dream offer. The moment the engineer opened the infected "offer letter" PDF, spyware compromised the machine—handing the hackers access to validator keys and granting full control over user funds.
It stands as the most expensive file download in financial history, proving that no matter how secure your blockchain is, social engineering remains the ultimate backdoor.
How cautious are you with opsec and downloading unfamiliar files? Let’s discuss below! 👇
$HYPE $SPCXB $MUU
#RoninNetwork #Lazarus #CryptoSecurity #BinanceSquare #Web3
{future}(MUUUSDT)
{spot}(SPCXBUSDT)
{future}(HYPEUSDT)
🚨 The $625M Fake Job Offer: How Lazarus Infiltrated Axie Infinity! 🎣💸
In 2022, North Korea’s notorious Lazarus Group executed one of the largest heists in crypto history, draining $625 million from the Ronin Network (the sidechain behind Axie Infinity).
They didn't break complex smart contracts. Instead, they targeted the oldest vulnerability in tech: human psychology.
The attackers set up a fake recruitment agency and spent weeks courting a senior engineer with a high-paying dream offer. The moment the engineer opened the infected "offer letter" PDF, spyware compromised the machine—handing the hackers access to validator keys and granting full control over user funds.
It stands as the most expensive file download in financial history, proving that no matter how secure your blockchain is, social engineering remains the ultimate backdoor.
How cautious are you with opsec and downloading unfamiliar files? Let’s discuss below! 👇
$HYPE $SPCXB $MUU
#RoninNetwork #Lazarus #CryptoSecurity #BinanceSquare #Web3
In 2022, North Korea’s notorious Lazarus Group executed one of the largest heists in crypto history, draining $625 million from the Ronin Network (the sidechain behind Axie Infinity).
They didn't break complex smart contracts. Instead, they targeted the oldest vulnerability in tech: human psychology.
The attackers set up a fake recruitment agency and spent weeks courting a senior engineer with a high-paying dream offer. The moment the engineer opened the infected "offer letter" PDF, spyware compromised the machine—handing the hackers access to validator keys and granting full control over user funds.
It stands as the most expensive file download in financial history, proving that no matter how secure your blockchain is, social engineering remains the ultimate backdoor.
How cautious are you with opsec and downloading unfamiliar files? Let’s discuss below! 👇
$HYPE $SPCXB $MUU
#RoninNetwork #Lazarus #CryptoSecurity #BinanceSquare #Web3
1
47
·
--
🚨 Did Binance really absorb a $6.3B loss? Withdrawals may reopen today, but understand this first;
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
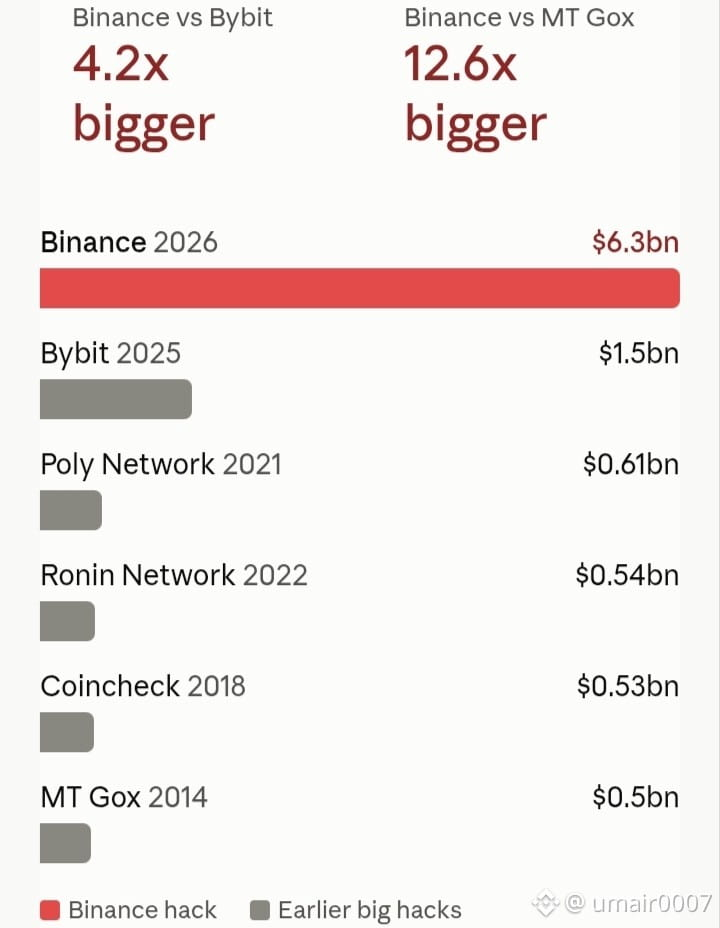
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
🚨 Did Binance really absorb a $6.3B loss? Withdrawals may reopen today, but understand this first;
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
Friends, according to the BBC, Binance says it has covered 90% of the $6.3 billion in stolen assets, and the remaining 10% will take a little longer.
The company says it will absorb the loss, not users, and has set aside more than $6.34 billion of its own funds for this.
Holdings of $BTC , $ETH and $USDT , plus 7 other major assets, are fully covered.
On Saturday the FBI said North Korea is behind the hack and named the Lazarus Group (TraderTraitor). North Korea has always denied such accusations.
An engineer's laptop was blamed at first, but more breach points were found later.
According to Richard Teng, several people were involved, and a "self-destruct mechanism" was used to hide their tracks.
About $3 billion was frozen on Thursday, and the US Secret Service is working to trace and recover the funds. The investigation is ongoing.
This is bigger than the 2025 Bybit hack ($1.5 billion), and Binance says withdrawals are on track to reopen today, November 1.
In my view, the real test is when withdrawals open. What will you do, pull your money out or keep it on Binance? Comment below 👇.
This is only information, not financial advice.
#Binance #BinanceHacks #CryptoSecurity #Lazarus #BinanceSquare
96
·
--
🚨🚨 LIVE: BINANCE OPENS WITHDRAWALS NOW
Stop everything you’re doing.
Sunday, November 1, 2026 - Binance just confirmed:
✅ 90% of the $6.3B ALREADY REPLENISHED (up from 80% yesterday)
✅ $5.67B of $6.3B recovered with its OWN funds
✅ Top 10 coins 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Yesterday’s Proof-of-Reserves snapshot at 00:00 UTC = 100%
✅ Full ZK proof coming November 3 - public verification
✅ $3B from hackers frozen by Tether, Circle, and partners
✅ SAFU being restored to $1B
What happened? Thursday, October 29, Lazarus Group (North Korea) hacked in. The FBI + Secret Service got involved.
What did Binance do? It didn’t pass the losses on to users. It paid out of pocket. $6.34B set aside.
This has NEVER happened in crypto history. Neither FTX nor Mt. Gox did this.
RETWEET if you still trust Binance 🟡
Official source: Binance X @ 08:15 AM today.
#Binance #BreakingNews #BTC #SAFU #Lazarus
🚨🚨 LIVE: BINANCE OPENS WITHDRAWALS NOW
Stop everything you’re doing.
Sunday, November 1, 2026 - Binance just confirmed:
✅ 90% of the $6.3B ALREADY REPLENISHED (up from 80% yesterday)
✅ $5.67B of $6.3B recovered with its OWN funds
✅ Top 10 coins 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Yesterday’s Proof-of-Reserves snapshot at 00:00 UTC = 100%
✅ Full ZK proof coming November 3 - public verification
✅ $3B from hackers frozen by Tether, Circle, and partners
✅ SAFU being restored to $1B
What happened? Thursday, October 29, Lazarus Group (North Korea) hacked in. The FBI + Secret Service got involved.
What did Binance do? It didn’t pass the losses on to users. It paid out of pocket. $6.34B set aside.
This has NEVER happened in crypto history. Neither FTX nor Mt. Gox did this.
RETWEET if you still trust Binance 🟡
Official source: Binance X @ 08:15 AM today.
#Binance #BreakingNews #BTC #SAFU #Lazarus
Stop everything you’re doing.
Sunday, November 1, 2026 - Binance just confirmed:
✅ 90% of the $6.3B ALREADY REPLENISHED (up from 80% yesterday)
✅ $5.67B of $6.3B recovered with its OWN funds
✅ Top 10 coins 100% backed: BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, ZEC
✅ Yesterday’s Proof-of-Reserves snapshot at 00:00 UTC = 100%
✅ Full ZK proof coming November 3 - public verification
✅ $3B from hackers frozen by Tether, Circle, and partners
✅ SAFU being restored to $1B
What happened? Thursday, October 29, Lazarus Group (North Korea) hacked in. The FBI + Secret Service got involved.
What did Binance do? It didn’t pass the losses on to users. It paid out of pocket. $6.34B set aside.
This has NEVER happened in crypto history. Neither FTX nor Mt. Gox did this.
RETWEET if you still trust Binance 🟡
Official source: Binance X @ 08:15 AM today.
#Binance #BreakingNews #BTC #SAFU #Lazarus
23
·
--
Bearish
🇰🇵 JUST IN: North Korea is the prime suspect in the record $6 billion Binance hack, per CNN and blockchain investigators.
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
🇰🇵 JUST IN: North Korea is the prime suspect in the record $6 billion Binance hack, per CNN and blockchain investigators.
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
TRM Labs attributes the attack to TraderTraitor, a North Korean state-backed unit linked to the Lazarus Group, with "high confidence." Chainalysis CEO Jonathan Levin said the firm assesses the roughly $6.4 billion theft was "likely done by DPRK group TraderTraitor due to links to previous hack," and a Chainalysis spokesperson told CNN it holds high confidence that North Korea was responsible. On-chain investigator ZachXBT independently called the attacker "likely Lazarus."
The evidence investigators cite is circumstantial. Preparations reportedly began at least 36 hours before the theft, with small Tornado Cash withdrawals funding an attacker wallet, a pattern seen in earlier North Korea-linked heists. Chainalysis and TRM also point to links with the February 2025 Bybit hack, which the FBI publicly pinned on TraderTraitor.
But it isn't settled. Binance has not named a culprit, and no government has formally attributed the attack. At least one analyst noted North Korean crews have historically laundered stolen funds faster than this attacker did.
Meanwhile, the recovery effort continues. About $3 billion has been frozen, and Binance has pledged to cover all user losses.
If confirmed, it would be the largest haul in North Korea's long campaign of crypto theft, which US and UN officials say helps fund its weapons programs. The next signal is likely to come from Washington.
#Binance #NorthKorea #Lazarus #CryptoHack #Crypto
1
66
·
--
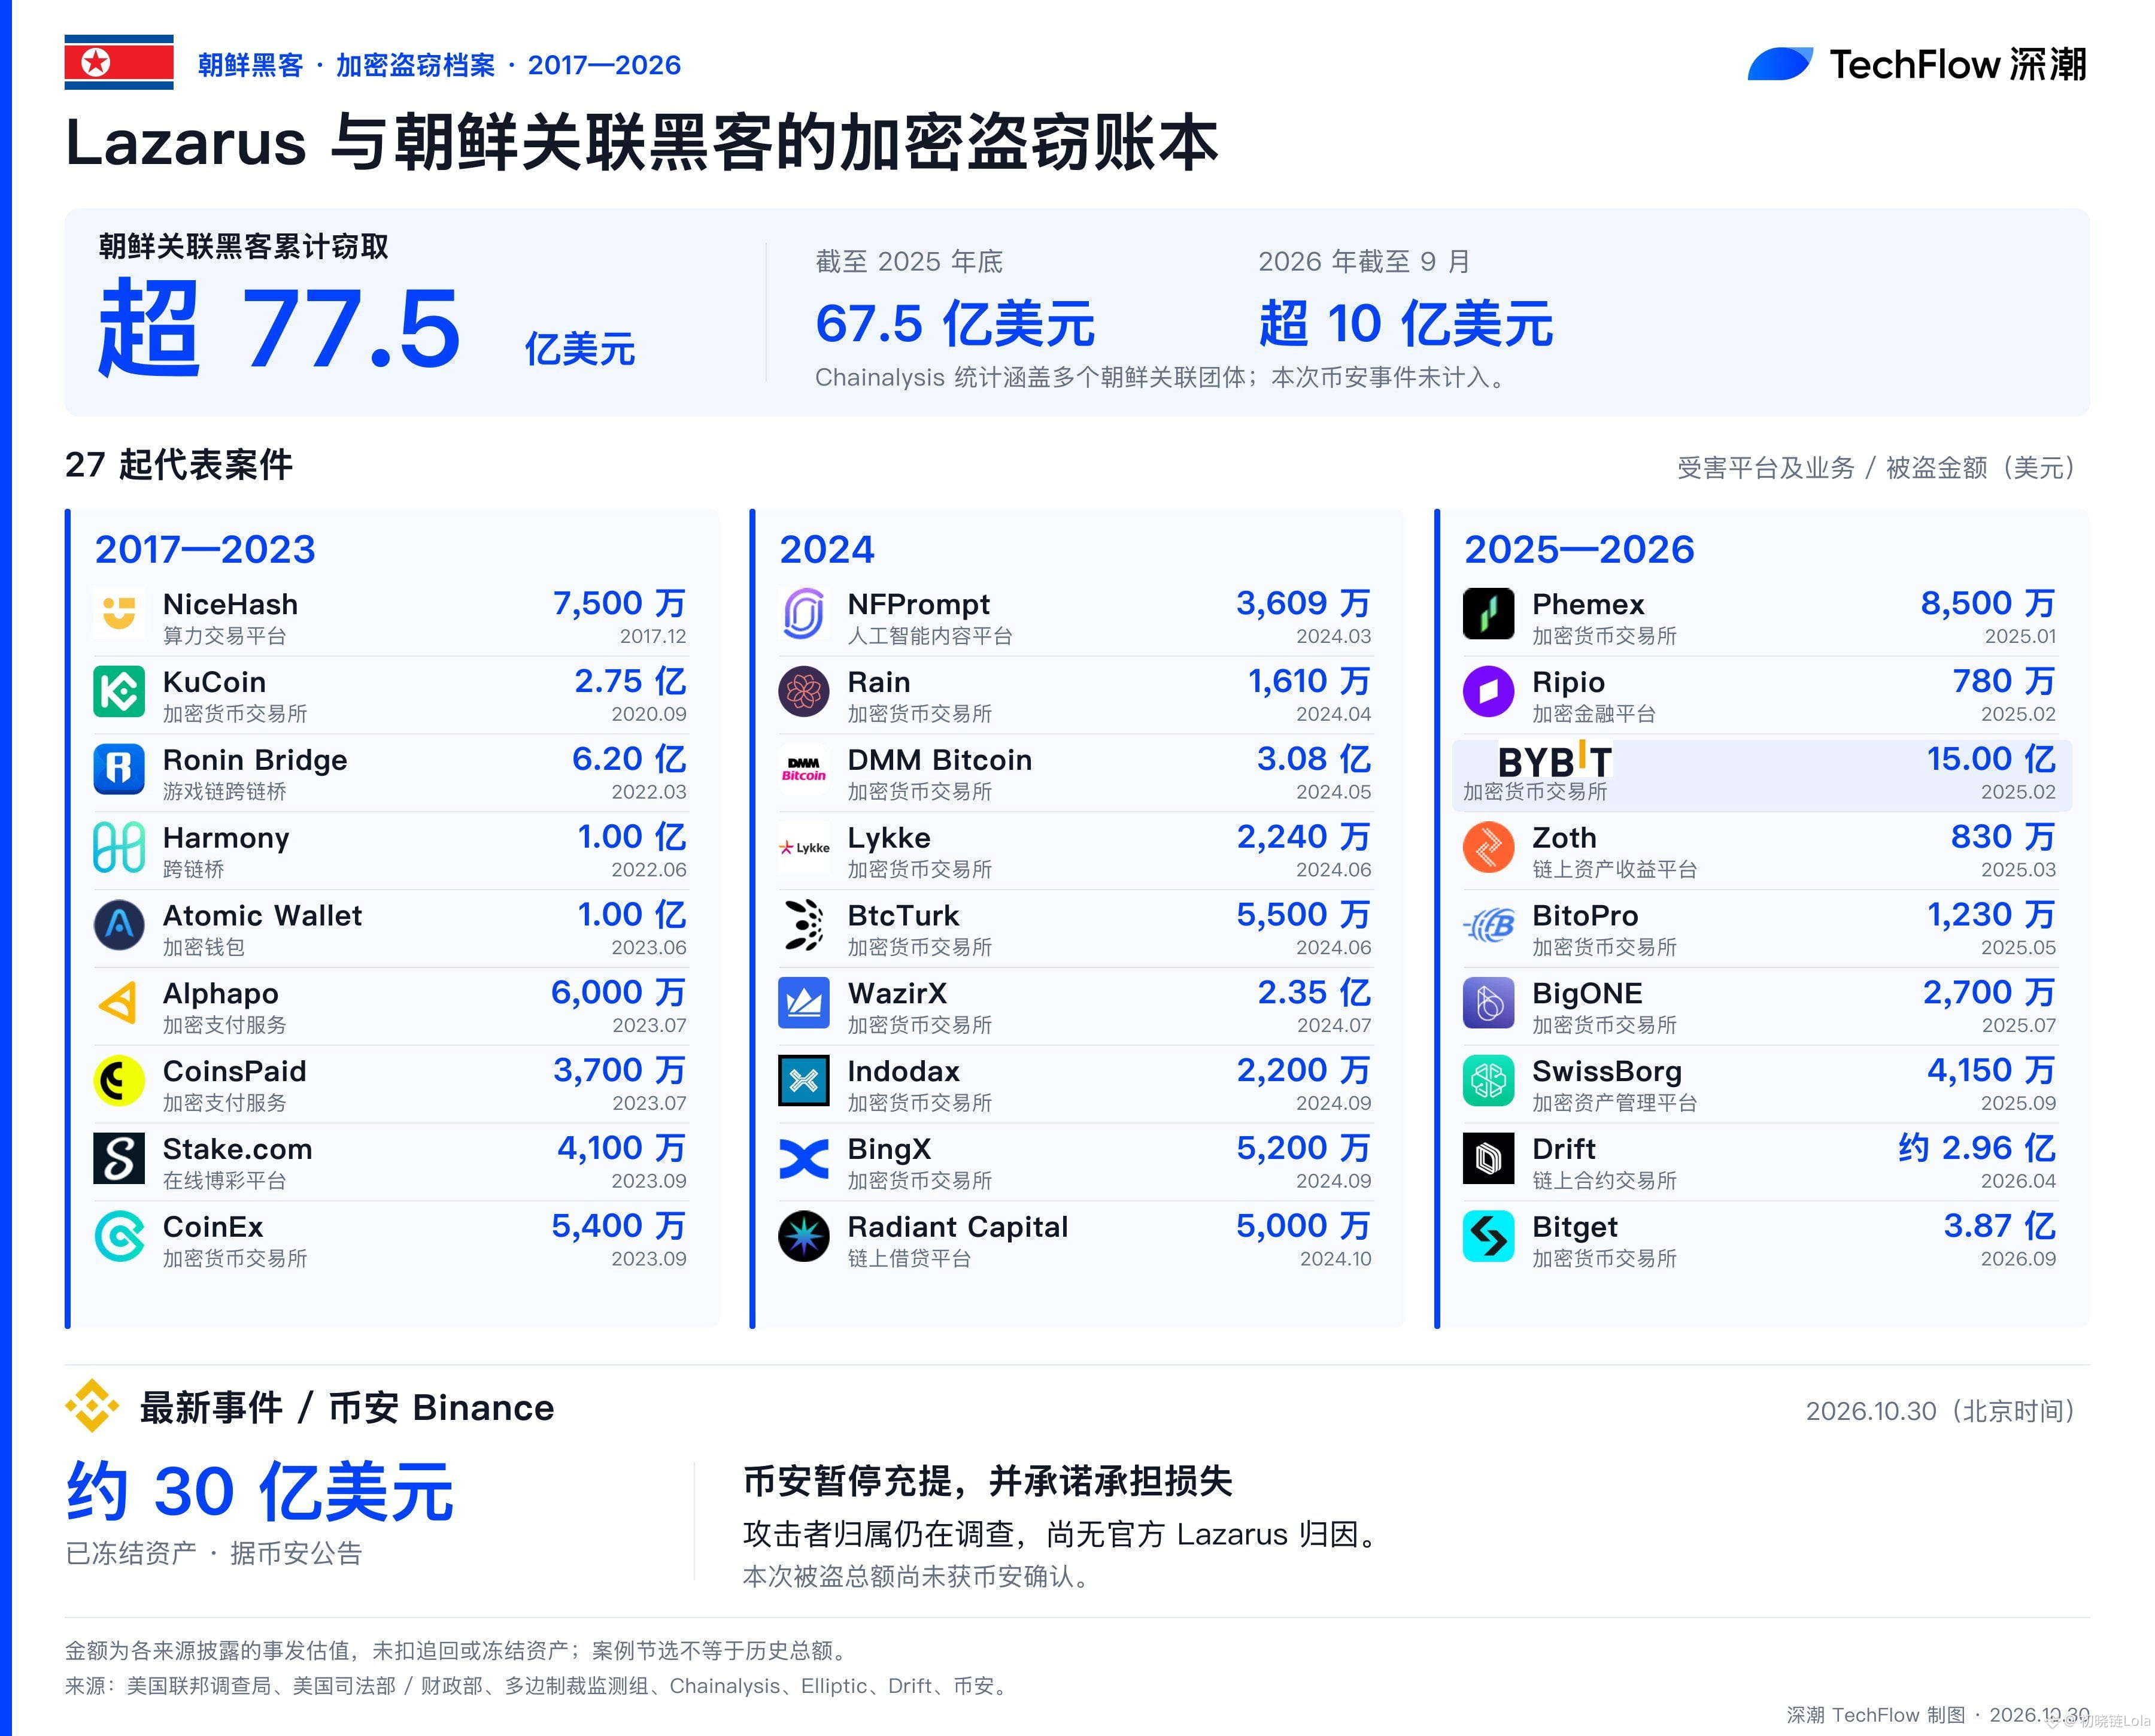
All that hard work, and we’ve just been making things easier for hackers.
A player has compiled a ledger of crypto thefts by hackers linked to North Korea: #Lazarus .
The total stolen is over $7.7 billion.
Some of the stolen funds here must be ours too, right?
I wonder if $BTC will keep falling today.
The market has lost confidence.
{spot}(BTCUSDT)
#黑客攻击 #币安被盗
All that hard work, and we’ve just been making things easier for hackers.
A player has compiled a ledger of crypto thefts by hackers linked to North Korea: #Lazarus .
The total stolen is over $7.7 billion.
Some of the stolen funds here must be ours too, right?
I wonder if $BTC will keep falling today.
The market has lost confidence.
#黑客攻击 #币安被盗
A player has compiled a ledger of crypto thefts by hackers linked to North Korea: #Lazarus .
The total stolen is over $7.7 billion.
Some of the stolen funds here must be ours too, right?
I wonder if $BTC will keep falling today.
The market has lost confidence.
#黑客攻击 #币安被盗
Padfoot:
韭菜负责充值,黑客负责提现,真成反向打工了😂 不过BTC跌不跌还得看资金,别把所有阴线都算黑客头上。
1
7.3k
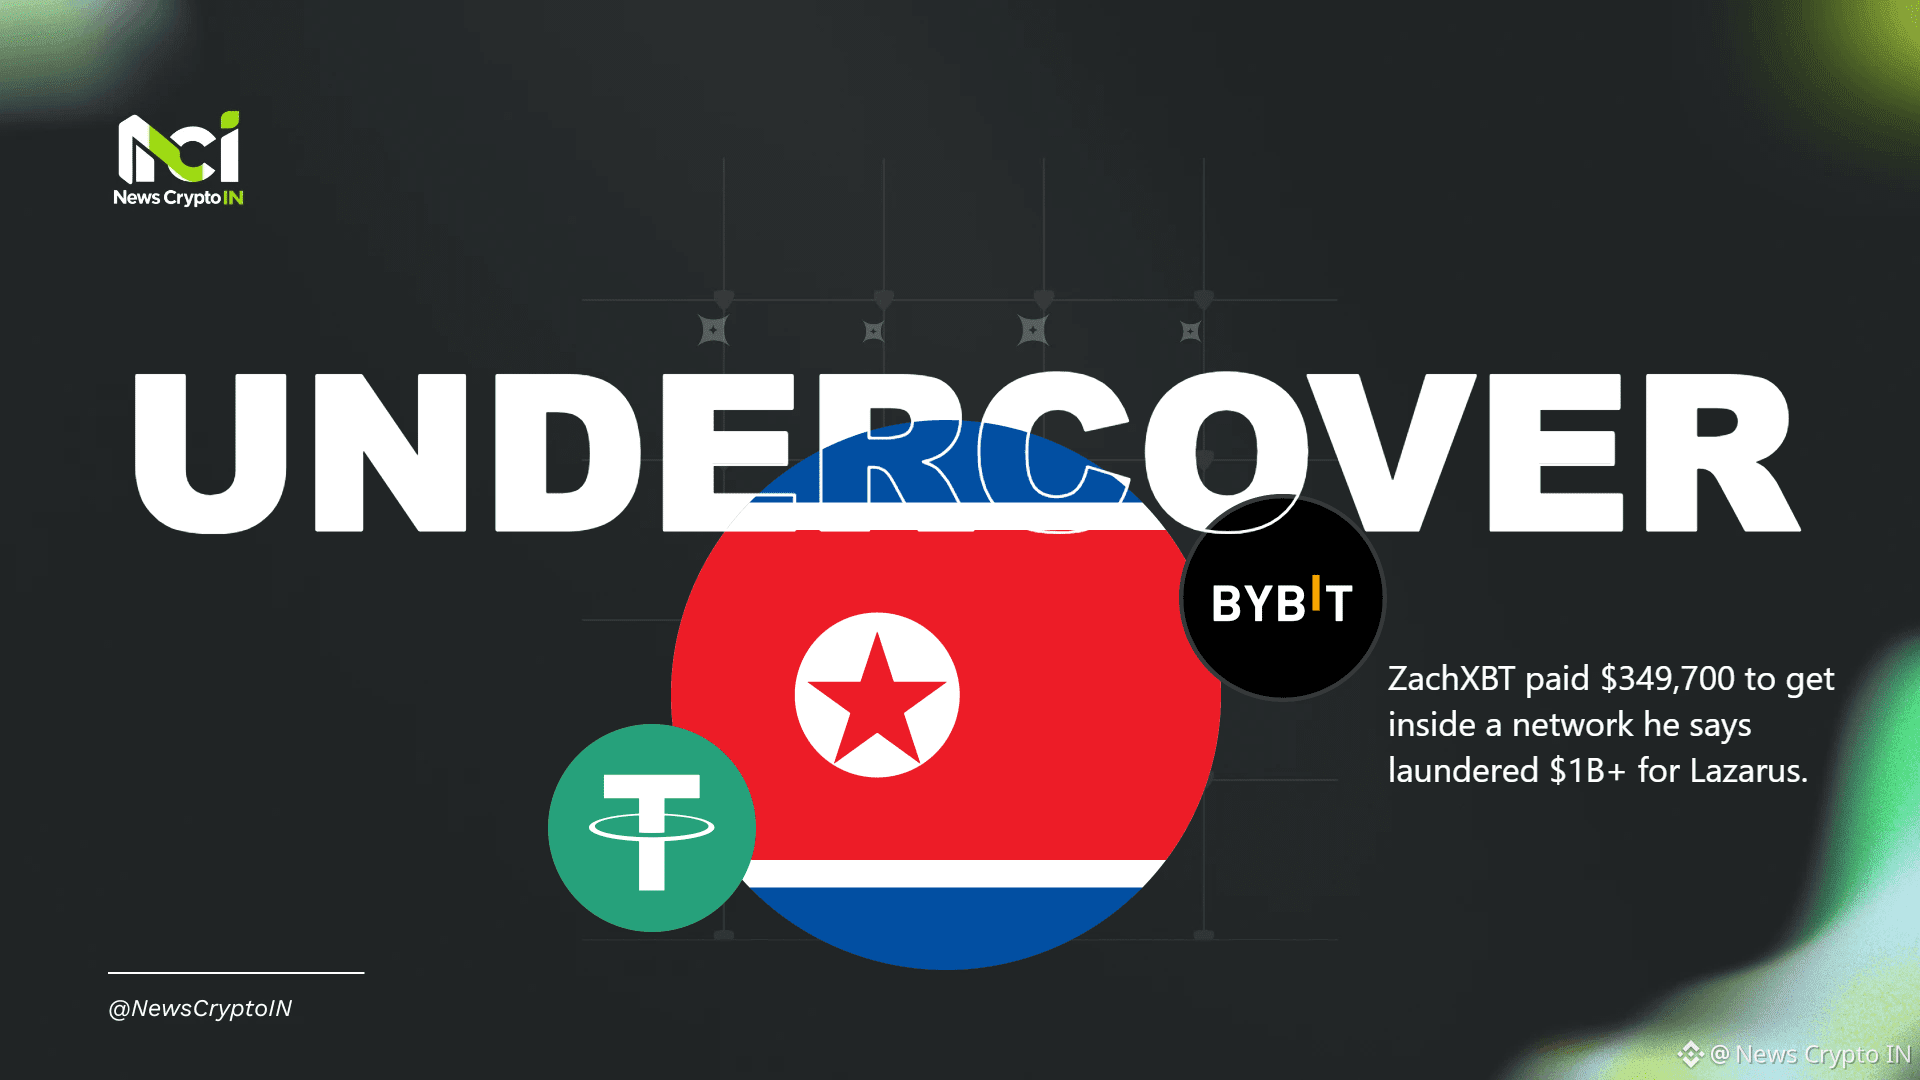
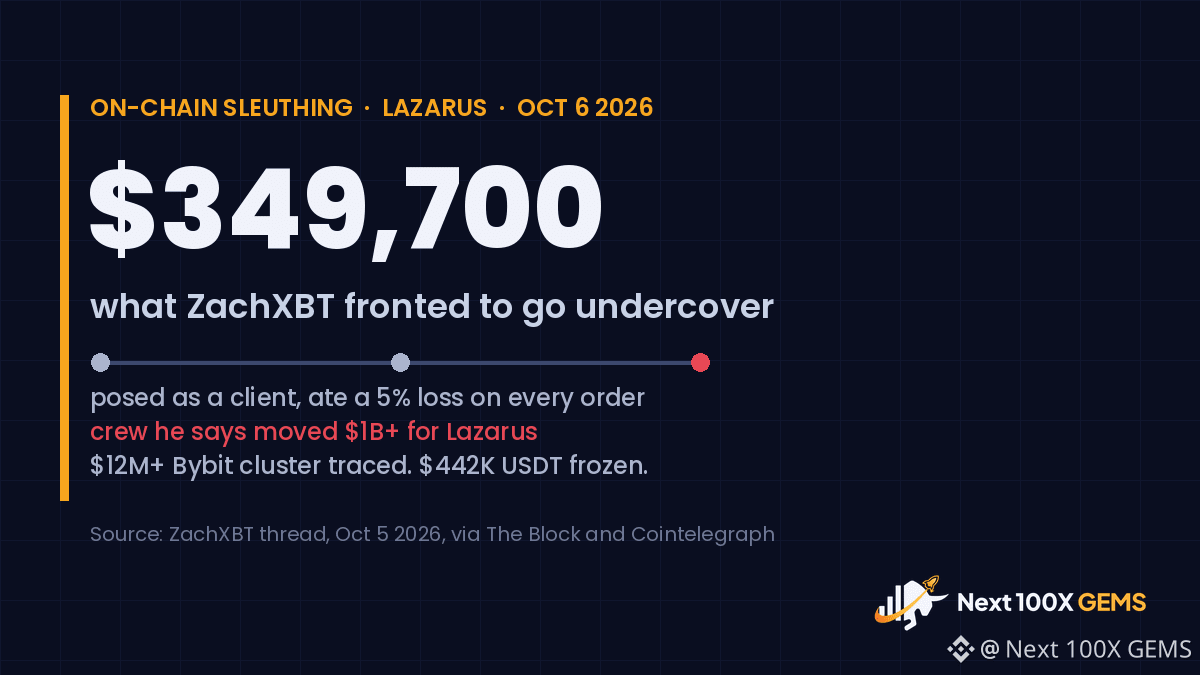
ZachXBT spent $349,700 of his own money to go undercover inside a crypto laundering ring.
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
ZachXBT spent $349,700 of his own money to go undercover inside a crypto laundering ring.
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
The on-chain sleuth says he posed as a client of a Chinese network that, by his count, has laundered more than $1 billion across multiple hacks for North Korea's Lazarus Group, including funds from the $1.5B Bybit hack in February 2025.
How he did it:
- He noticed 15+ accounts in Telegram and Discord groups asking for help moving funds tied to the Bybit exploit.
- He funded a fresh Ethereum address with 349,700 USDC and placed orders with a vendor using the name "Jimmy Green".
- He accepted roughly 5% losses on each order to look credible and watch how the network handled dirty money.
What came out of it: a cluster holding more than $12M linked to the Bybit hack, and $442,000 in USDT frozen.
Now the part worth keeping in mind. As of Oct 6, public releases from the FBI, US Treasury and Tether don't name "Jimmy Green" or confirm that one Chinese network moved $1B+ for Lazarus, and no charges or court filings identify the operator. This is a strong investigation, not a verdict.
It still says a lot. A single independent researcher, with his own money, got closer to the laundering pipeline than most official statements show. And the pipeline he describes runs through ordinary chat apps and OTC desks, not some hidden dark web.
The uncomfortable math: $442K frozen against $1B+ alleged laundered. Tracing works. Recovering is another story.
Should exchanges and stablecoin issuers be moving this fast on their own, without waiting for law enforcement?
Like and follow for more on-chain investigations explained simply.
#Lazarus #Bybit
1
108


ZachXBT says he put up $349,700 and took a 5% loss on every order to pose as a client of a Chinese laundering crew.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
ZachXBT says he put up $349,700 and took a 5% loss on every order to pose as a client of a Chinese laundering crew.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
He says that crew has moved more than $1B for North Korea's Lazarus Group across several hacks, including the $1.5B Bybit theft in Feb 2025.
The wild part: the launderer told him a day ahead that funds would move to Solana. The next day they did.
His intel exposed a $12M+ cluster of Bybit funds hopping from Bitcoin to Ethereum to Solana to Tron. Tether later froze $442K of it.
These people weren't hiding in some dark corner. They were in public Telegram and Discord groups looking for orders.
Fair to note: the $1B figure and the crew's identity are his findings. The FBI and Treasury haven't confirmed them.
He funds this work with grants and donations. Should the exchanges he helps be paying him?
$BTC $ETH $SOL
#CryptoSecurity #Lazarus #ZachXBT
NFA. DYOR.
1
1.4k

·
--
Bullish
ZachXBT paid Lazarus launderers 5% of every transaction. Himself, with his own money
Since late February 2025, he played the role of a client
put 349700 $USDC
{future}(USDCUSDT)
into their network
and knowingly lost 5% on every order until they began to trust him
Trust there, it turns out, costs 5%. Pay up—and they’ll tell you themselves where the stolen money goes
What came of it:
- a cluster containing over $12 million in funds from the Bybit hack
- Tether froze 442000 USDT
By his estimate, the network laundered "$1B+" for Lazarus. That’s his figure, not the police’s. He only revealed all this on October 5, 2026
Some of my stablecoins in Flexible are in USDT too, so it’s nice to see stolen USDT actually getting frozen
Laundering is a service with a fee, like an exchange. ZachXBT simply paid that fee to get inside
#zachxbt #Lazarus #bybit
ZachXBT paid Lazarus launderers 5% of every transaction. Himself, with his own money
Since late February 2025, he played the role of a client
put 349700 $USDC
into their network
and knowingly lost 5% on every order until they began to trust him
Trust there, it turns out, costs 5%. Pay up—and they’ll tell you themselves where the stolen money goes
What came of it:
- a cluster containing over $12 million in funds from the Bybit hack
- Tether froze 442000 USDT
By his estimate, the network laundered "$1B+" for Lazarus. That’s his figure, not the police’s. He only revealed all this on October 5, 2026
Some of my stablecoins in Flexible are in USDT too, so it’s nice to see stolen USDT actually getting frozen
Laundering is a service with a fee, like an exchange. ZachXBT simply paid that fee to get inside
#zachxbt #Lazarus #bybit
Since late February 2025, he played the role of a client
put 349700 $USDC
into their network
and knowingly lost 5% on every order until they began to trust him
Trust there, it turns out, costs 5%. Pay up—and they’ll tell you themselves where the stolen money goes
What came of it:
- a cluster containing over $12 million in funds from the Bybit hack
- Tether froze 442000 USDT
By his estimate, the network laundered "$1B+" for Lazarus. That’s his figure, not the police’s. He only revealed all this on October 5, 2026
Some of my stablecoins in Flexible are in USDT too, so it’s nice to see stolen USDT actually getting frozen
Laundering is a service with a fee, like an exchange. ZachXBT simply paid that fee to get inside
#zachxbt #Lazarus #bybit
10
447

·
--
On-chain investigator ZachXBT claims to have infiltrated a Chinese money-laundering network that allegedly processed more than $1 billion for the North Korean Lazarus Group. To get inside, he fronted 349,700 USDC out of his own pocket.
His October 5 thread, covered by The Block and Decrypt:
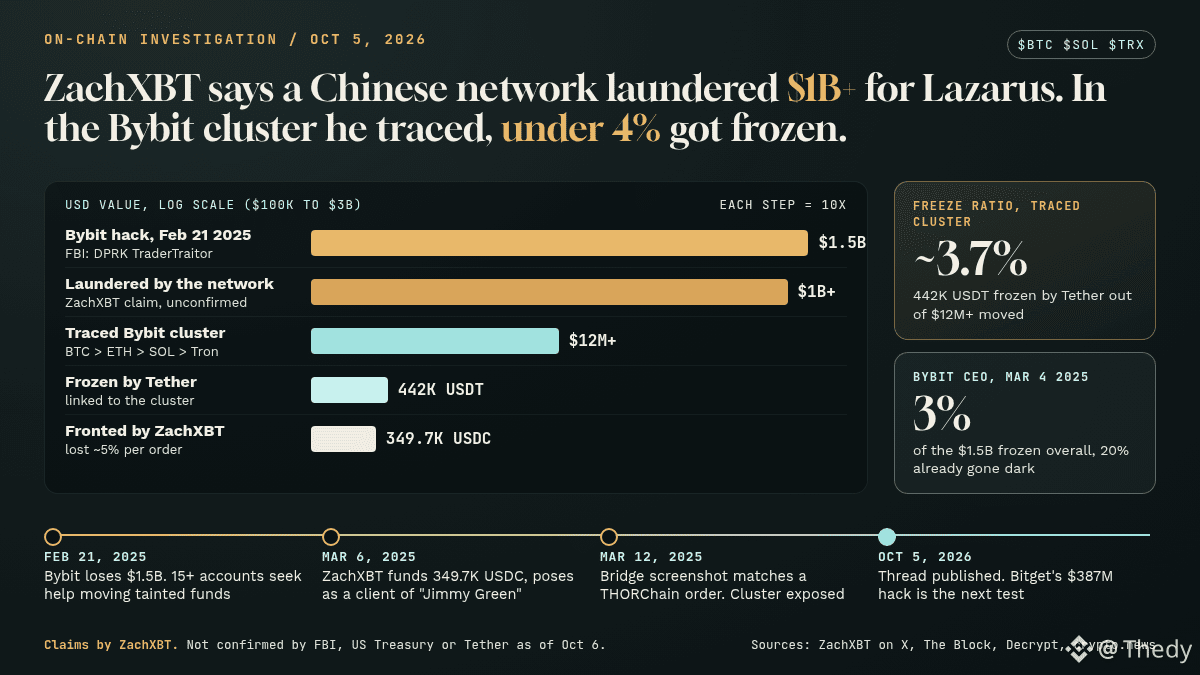
February 21, 2025: Bybit loses $1.5 billion in a theft attributed by the FBI to North Korean hackers TraderTraitor. More than 15 Telegram and Discord accounts then seek help laundering the funds.
March 6, 2025: He poses as a client of someone called “Jimmy Green,” losing 5% per order. The receiving address was funded with gas by a wallet on Bybit’s blacklist.
March 12, 2025: A screenshot sent by Jimmy matches a THORChain order created minutes later. Three Solana addresses reveal a cluster of more than $12 million that moved from $BTC to ETH, then $SOL and finally Tron. Tether later freezes 442,000 USDT.
Worth noting: as of October 6, neither the FBI, the US Treasury, nor Tether had publicly confirmed the $1 billion figure or the network’s identity (crypto.news).
My take: what matters is the ratio. About 3.7% of the traced cluster was frozen. And in early March 2025, Bybit’s Ben Zhou put freezes at 3% of the total stolen. Blocking only works at the final link, when the money becomes USDT on Tron ($TRX), which an issuer can freeze. Bridges and swaps remain almost beyond reach.
Next test: the $387 million Bitget hack in late September, linked to North Korea by Elliptic and Chainalysis. According to him, the same pattern is playing out on Telegram. Either this information triggers swift freezes, or the network has already switched rails.
Who should block these flows first: stablecoin issuers, cross-chain protocols like THORChain, or the exchanges where the money eventually cashes out?
#Lazarus #CryptoSecurity
On-chain investigator ZachXBT claims to have infiltrated a Chinese money-laundering network that allegedly processed more than $1 billion for the North Korean Lazarus Group. To get inside, he fronted 349,700 USDC out of his own pocket.
His October 5 thread, covered by The Block and Decrypt:
February 21, 2025: Bybit loses $1.5 billion in a theft attributed by the FBI to North Korean hackers TraderTraitor. More than 15 Telegram and Discord accounts then seek help laundering the funds.
March 6, 2025: He poses as a client of someone called “Jimmy Green,” losing 5% per order. The receiving address was funded with gas by a wallet on Bybit’s blacklist.
March 12, 2025: A screenshot sent by Jimmy matches a THORChain order created minutes later. Three Solana addresses reveal a cluster of more than $12 million that moved from $BTC to ETH, then $SOL and finally Tron. Tether later freezes 442,000 USDT.
Worth noting: as of October 6, neither the FBI, the US Treasury, nor Tether had publicly confirmed the $1 billion figure or the network’s identity (crypto.news).
My take: what matters is the ratio. About 3.7% of the traced cluster was frozen. And in early March 2025, Bybit’s Ben Zhou put freezes at 3% of the total stolen. Blocking only works at the final link, when the money becomes USDT on Tron ($TRX ), which an issuer can freeze. Bridges and swaps remain almost beyond reach.
Next test: the $387 million Bitget hack in late September, linked to North Korea by Elliptic and Chainalysis. According to him, the same pattern is playing out on Telegram. Either this information triggers swift freezes, or the network has already switched rails.
Who should block these flows first: stablecoin issuers, cross-chain protocols like THORChain, or the exchanges where the money eventually cashes out?
#Lazarus #CryptoSecurity
His October 5 thread, covered by The Block and Decrypt:
February 21, 2025: Bybit loses $1.5 billion in a theft attributed by the FBI to North Korean hackers TraderTraitor. More than 15 Telegram and Discord accounts then seek help laundering the funds.
March 6, 2025: He poses as a client of someone called “Jimmy Green,” losing 5% per order. The receiving address was funded with gas by a wallet on Bybit’s blacklist.
March 12, 2025: A screenshot sent by Jimmy matches a THORChain order created minutes later. Three Solana addresses reveal a cluster of more than $12 million that moved from $BTC to ETH, then $SOL and finally Tron. Tether later freezes 442,000 USDT.
Worth noting: as of October 6, neither the FBI, the US Treasury, nor Tether had publicly confirmed the $1 billion figure or the network’s identity (crypto.news).
My take: what matters is the ratio. About 3.7% of the traced cluster was frozen. And in early March 2025, Bybit’s Ben Zhou put freezes at 3% of the total stolen. Blocking only works at the final link, when the money becomes USDT on Tron ($TRX ), which an issuer can freeze. Bridges and swaps remain almost beyond reach.
Next test: the $387 million Bitget hack in late September, linked to North Korea by Elliptic and Chainalysis. According to him, the same pattern is playing out on Telegram. Either this information triggers swift freezes, or the network has already switched rails.
Who should block these flows first: stablecoin issuers, cross-chain protocols like THORChain, or the exchanges where the money eventually cashes out?
#Lazarus #CryptoSecurity
157

Chinese criminal network laundered over $1 billion for Lazarus: ZachXBT
- ZachXBT says he infiltrated a Chinese criminal network by posing as a customer.
- The information he gathered helped trace funds from the $1.5 billion Bybit hack.
- The network is accused of laundering over $1 billion for the Lazarus hacking group.
- The RSS source did not provide further details about the network’s identity or methods.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
Chinese criminal network laundered over $1 billion for Lazarus: ZachXBT
- ZachXBT says he infiltrated a Chinese criminal network by posing as a customer.
- The information he gathered helped trace funds from the $1.5 billion Bybit hack.
- The network is accused of laundering over $1 billion for the Lazarus hacking group.
- The RSS source did not provide further details about the network’s identity or methods.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
- ZachXBT says he infiltrated a Chinese criminal network by posing as a customer.
- The information he gathered helped trace funds from the $1.5 billion Bybit hack.
- The network is accused of laundering over $1 billion for the Lazarus hacking group.
- The RSS source did not provide further details about the network’s identity or methods.
#BinanceSquare #CryptoNews #Bybit #Lazarus #ZachXBT
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
26
💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
3
649
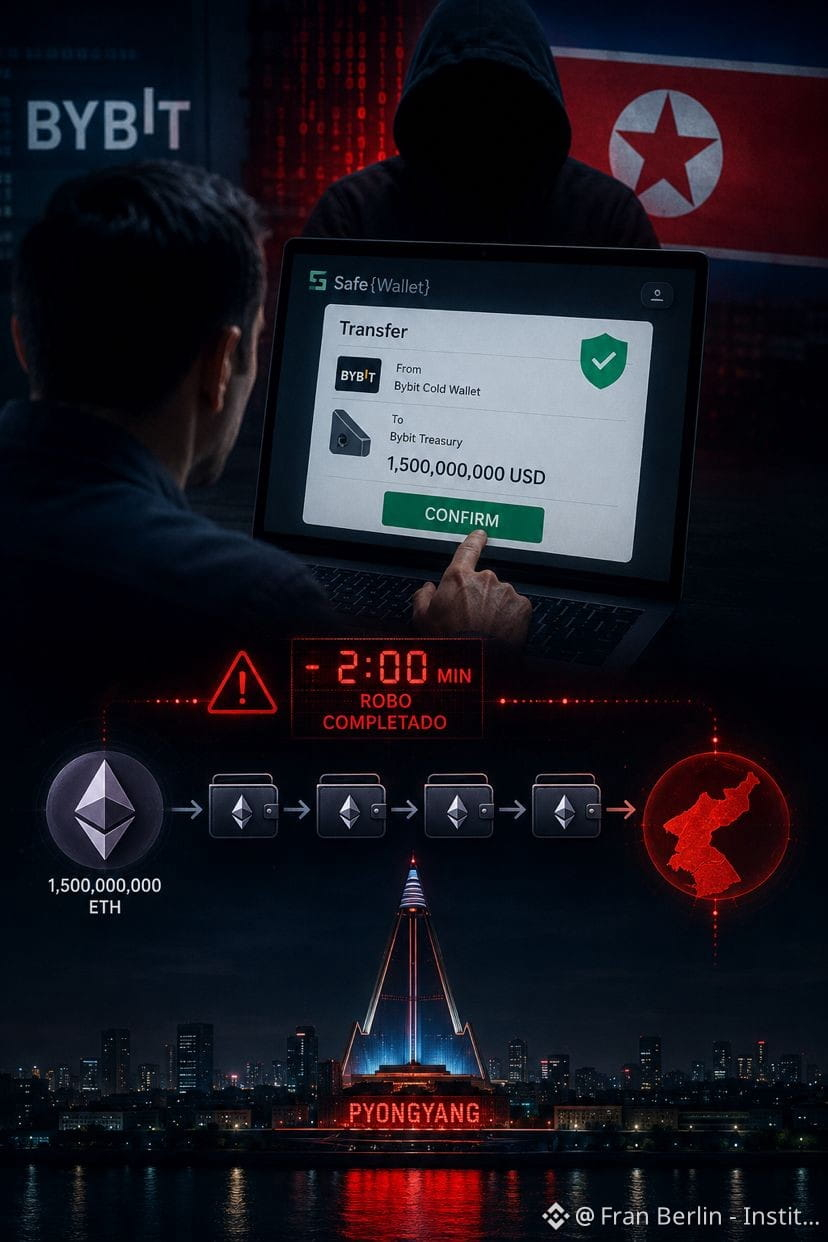
It was a routine transfer.
February 20, 2025. A Bybit employee opens his screen, checks the transaction details, and signs.
Everything looks normal.
Minutes later, $1.5 billion $USDT in Ethereum had vanished.
But the most terrifying part isn’t the amount.
The most terrifying part is how they did it.
The elite North Korean government hackers of the Lazarus Group didn’t attack the blockchain. They didn’t break any private keys. They didn’t need any of that.
They simply… falsified what the employee saw on the screen.
Months earlier, they infiltrated the system of a Safe Wallet developer—the platform Bybit used to sign transactions. They injected a malicious code that slept quietly, waiting.
When the employee opened his wallet that day, the code activated. The screen showed a legitimate transfer. In reality, the funds were going to Pyongyang.
The employee signed. His coworkers signed. Nobody saw anything unusual.
Two minutes after the theft, the malicious code deleted itself. No trace.
It took the FBI days to confirm what everyone already suspected: it was North Korea, using stolen Ethereum to fund its nuclear weapons program.
The lesson nobody wants to hear: the weakest link isn’t the code. It’s you.
Do you trust the screen you see when you sign a transaction?
Fran Berlin | Blockchain Institute
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
{spot}(ETHUSDT)
{spot}(USDCUSDT)
It was a routine transfer.
February 20, 2025. A Bybit employee opens his screen, checks the transaction details, and signs.
Everything looks normal.
Minutes later, $1.5 billion $USDT in Ethereum had vanished.
But the most terrifying part isn’t the amount.
The most terrifying part is how they did it.
The elite North Korean government hackers of the Lazarus Group didn’t attack the blockchain. They didn’t break any private keys. They didn’t need any of that.
They simply… falsified what the employee saw on the screen.
Months earlier, they infiltrated the system of a Safe Wallet developer—the platform Bybit used to sign transactions. They injected a malicious code that slept quietly, waiting.
When the employee opened his wallet that day, the code activated. The screen showed a legitimate transfer. In reality, the funds were going to Pyongyang.
The employee signed. His coworkers signed. Nobody saw anything unusual.
Two minutes after the theft, the malicious code deleted itself. No trace.
It took the FBI days to confirm what everyone already suspected: it was North Korea, using stolen Ethereum to fund its nuclear weapons program.
The lesson nobody wants to hear: the weakest link isn’t the code. It’s you.
Do you trust the screen you see when you sign a transaction?
Fran Berlin | Blockchain Institute
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
February 20, 2025. A Bybit employee opens his screen, checks the transaction details, and signs.
Everything looks normal.
Minutes later, $1.5 billion $USDT in Ethereum had vanished.
But the most terrifying part isn’t the amount.
The most terrifying part is how they did it.
The elite North Korean government hackers of the Lazarus Group didn’t attack the blockchain. They didn’t break any private keys. They didn’t need any of that.
They simply… falsified what the employee saw on the screen.
Months earlier, they infiltrated the system of a Safe Wallet developer—the platform Bybit used to sign transactions. They injected a malicious code that slept quietly, waiting.
When the employee opened his wallet that day, the code activated. The screen showed a legitimate transfer. In reality, the funds were going to Pyongyang.
The employee signed. His coworkers signed. Nobody saw anything unusual.
Two minutes after the theft, the malicious code deleted itself. No trace.
It took the FBI days to confirm what everyone already suspected: it was North Korea, using stolen Ethereum to fund its nuclear weapons program.
The lesson nobody wants to hear: the weakest link isn’t the code. It’s you.
Do you trust the screen you see when you sign a transaction?
Fran Berlin | Blockchain Institute
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
675

·
--
Bearish
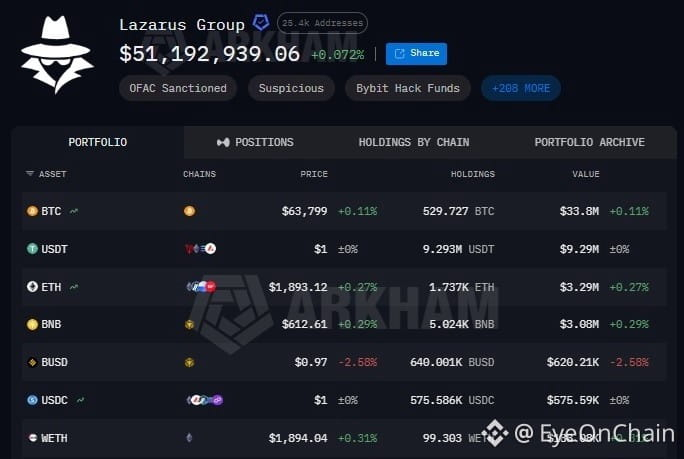
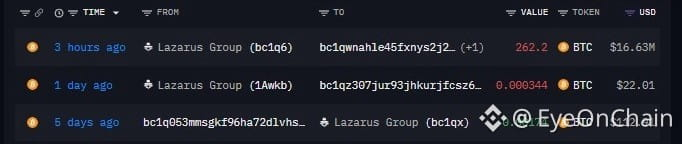
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC, $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
{future}(BTCUSDT)
{spot}(BTCUSDT)
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
1
1.3k
·
--
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
5
97

🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
34
·
--
🎯 The biggest crypto heist this year—allegedly the protagonist is North Korea
📰 Bitget was siphoned off $388 million, and the CEO directly points to the Lazarus Group; XRP was moved for $157 million, and the exchange temporarily suspended withdrawals
💬 The methods aren’t anything new, but the amounts are maxed out. Centralized exchanges are always the weak link—no matter how fast the money moves on-chain, once the entry point is compromised, it’s all for nothing. Don’t just treat self-custody as a slogan.
🏷️ #Bitget #Lazarus #安全事件 #self-custody
🎯 The biggest crypto heist this year—allegedly the protagonist is North Korea
📰 Bitget was siphoned off $388 million, and the CEO directly points to the Lazarus Group; XRP was moved for $157 million, and the exchange temporarily suspended withdrawals
💬 The methods aren’t anything new, but the amounts are maxed out. Centralized exchanges are always the weak link—no matter how fast the money moves on-chain, once the entry point is compromised, it’s all for nothing. Don’t just treat self-custody as a slogan.
🏷️ #Bitget #Lazarus #安全事件 #self-custody
📰 Bitget was siphoned off $388 million, and the CEO directly points to the Lazarus Group; XRP was moved for $157 million, and the exchange temporarily suspended withdrawals
💬 The methods aren’t anything new, but the amounts are maxed out. Centralized exchanges are always the weak link—no matter how fast the money moves on-chain, once the entry point is compromised, it’s all for nothing. Don’t just treat self-custody as a slogan.
🏷️ #Bitget #Lazarus #安全事件 #self-custody
253
·
--
📰 On September 24, abnormal transfers occurred involving some of Bitget’s hot wallets and warm wallets. The platform initially disclosed losses of about $351.6 million, and later confirmed that the amount of assets that were transferred had been adjusted to $387.5 million.
🔥 TRM Labs found that the laundering path of the partially stolen funds overlaps with previous North Korea–linked attacks such as those involving Bybit and AFX Bridge. Elliptic also believes there is a “highly likely” connection between this incident and North Korean hackers, and the investigation focus points again toward the Lazarus Group.
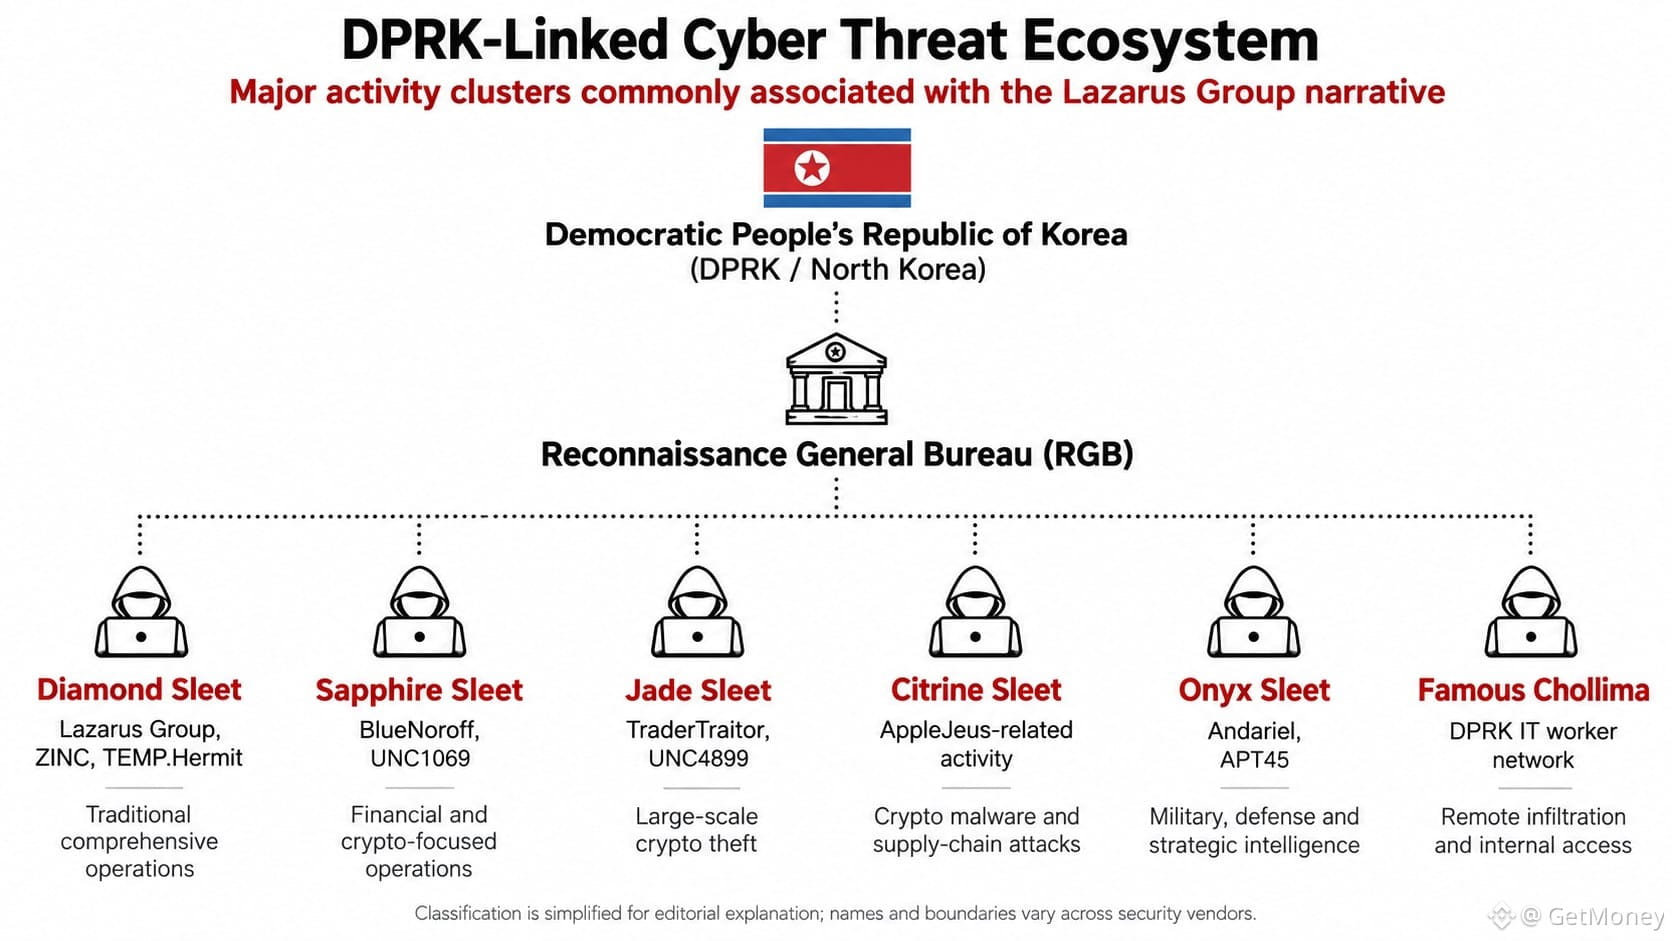
Honestly, Lazarus doesn’t really look like a single organization with clear boundaries—it’s more like an umbrella term used externally for North Korea’s state-level cyberattack apparatus. In 2019, the U.S. Treasury named Lazarus, BlueNoroff, and Andariel, saying they are all under the control of North Korea’s Reconnaissance General Bureau (RGB).
💡 In this ecosystem, different entities use different names: BlueNoroff has long targeted financial institutions and crypto assets; TraderTraitor focuses on exchanges, custodians, and large crypto targets; Citrine Sleet leans toward malware and supply-chain attacks; and Famous Chollima infiltrates technology and crypto companies through fake identities.
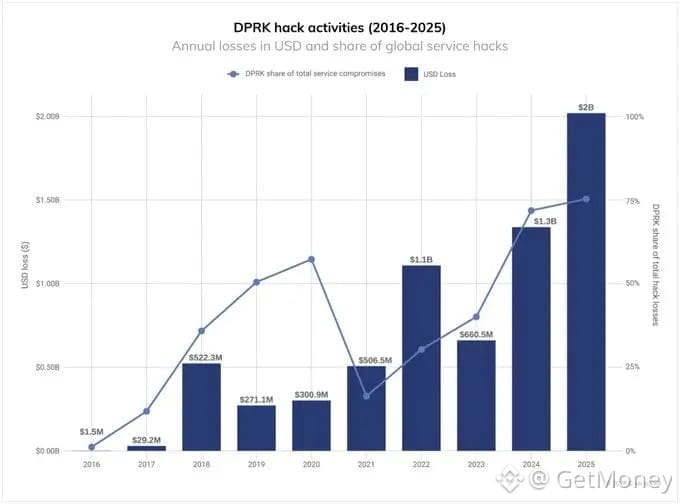
👀 From Ronin Bridge, Harmony, Atomic Wallet, to Stake, WazirX, DMM Bitcoin, and then the Bybit incident in 2025—if we also include the Bitget case, which is currently highly suspected to be carried out by North Korea—the scale of related theft is already close to $7.8 billion. This figure is no longer just a security incident for a single platform.
🤔 When the same attack framework keeps changing names and entry points, how can exchanges and project teams ultimately determine which group they’re really dealing with?
#Lazarus #Bitget #加密安全 #On-chain security
📰 On September 24, abnormal transfers occurred involving some of Bitget’s hot wallets and warm wallets. The platform initially disclosed losses of about $351.6 million, and later confirmed that the amount of assets that were transferred had been adjusted to $387.5 million.
🔥 TRM Labs found that the laundering path of the partially stolen funds overlaps with previous North Korea–linked attacks such as those involving Bybit and AFX Bridge. Elliptic also believes there is a “highly likely” connection between this incident and North Korean hackers, and the investigation focus points again toward the Lazarus Group.
Honestly, Lazarus doesn’t really look like a single organization with clear boundaries—it’s more like an umbrella term used externally for North Korea’s state-level cyberattack apparatus. In 2019, the U.S. Treasury named Lazarus, BlueNoroff, and Andariel, saying they are all under the control of North Korea’s Reconnaissance General Bureau (RGB).
💡 In this ecosystem, different entities use different names: BlueNoroff has long targeted financial institutions and crypto assets; TraderTraitor focuses on exchanges, custodians, and large crypto targets; Citrine Sleet leans toward malware and supply-chain attacks; and Famous Chollima infiltrates technology and crypto companies through fake identities.
👀 From Ronin Bridge, Harmony, Atomic Wallet, to Stake, WazirX, DMM Bitcoin, and then the Bybit incident in 2025—if we also include the Bitget case, which is currently highly suspected to be carried out by North Korea—the scale of related theft is already close to $7.8 billion. This figure is no longer just a security incident for a single platform.
🤔 When the same attack framework keeps changing names and entry points, how can exchanges and project teams ultimately determine which group they’re really dealing with?
#Lazarus #Bitget #加密安全 #On-chain security
🔥 TRM Labs found that the laundering path of the partially stolen funds overlaps with previous North Korea–linked attacks such as those involving Bybit and AFX Bridge. Elliptic also believes there is a “highly likely” connection between this incident and North Korean hackers, and the investigation focus points again toward the Lazarus Group.
Honestly, Lazarus doesn’t really look like a single organization with clear boundaries—it’s more like an umbrella term used externally for North Korea’s state-level cyberattack apparatus. In 2019, the U.S. Treasury named Lazarus, BlueNoroff, and Andariel, saying they are all under the control of North Korea’s Reconnaissance General Bureau (RGB).
💡 In this ecosystem, different entities use different names: BlueNoroff has long targeted financial institutions and crypto assets; TraderTraitor focuses on exchanges, custodians, and large crypto targets; Citrine Sleet leans toward malware and supply-chain attacks; and Famous Chollima infiltrates technology and crypto companies through fake identities.
👀 From Ronin Bridge, Harmony, Atomic Wallet, to Stake, WazirX, DMM Bitcoin, and then the Bybit incident in 2025—if we also include the Bitget case, which is currently highly suspected to be carried out by North Korea—the scale of related theft is already close to $7.8 billion. This figure is no longer just a security incident for a single platform.
🤔 When the same attack framework keeps changing names and entry points, how can exchanges and project teams ultimately determine which group they’re really dealing with?
#Lazarus #Bitget #加密安全 #On-chain security
54
·
--
Bullish
$BTC $ETH
🚨 FLASH HACK : What really happened at Bitget? 🚨
A major security incident has rocked the crypto ecosystem. Here’s the full rundown on the situation 🧵👇
💥 The Attack, in Brief
On September 24, 2026, Bitget suffered a vulnerability in its backend infrastructure. The attackers forged internal system permissions to approve fraudulent transfers and drain the hot wallets.
💰 Loss Amount: ~387.5 million $
Major cryptocurrencies were diverted across multiple blockchains: ETH, XRP, USDT, TRX, AVAX, BNB, and ZEC.
🛡️ What’s the impact on users?
• ❄️ Cold Wallets: 100% secured (the cold wallets were not affected).
• 👤 Client balances: No direct impact on your accounts.
• 🛡️ Protection Funds: The Bitget guarantee fund (estimated at over $460M) will cover the entirety of the losses.
🕵️ Who’s behind the hack?
According to CEO Gracy Chen, the IP addresses and the modus operandi point to North Korean hackers (the Lazarus group). Cybersecurity giants Mandiant and SlowMist are working on the case.
🗓️ Withdrawal Recovery Timeline:
✅ Vulnerability fixed & trading operational
📌 Sept. 28: BTC withdrawals
📌 Sept. 29: ETH withdrawals (Ethereum, BSC, Arbitrum, Base, OP)
📌 Sept. 30: USDT withdrawals (Ethereum, BSC, Solana, Tron)
📌 Oct. 2: Other altcoins, fiat, and P2P
Stay cautious and always verify your sources officially! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
{spot}(BTCUSDT)
{spot}(ETHUSDT)
$BTC $ETH
🚨 FLASH HACK : What really happened at Bitget? 🚨
A major security incident has rocked the crypto ecosystem. Here’s the full rundown on the situation 🧵👇
💥 The Attack, in Brief
On September 24, 2026, Bitget suffered a vulnerability in its backend infrastructure. The attackers forged internal system permissions to approve fraudulent transfers and drain the hot wallets.
💰 Loss Amount: ~387.5 million $
Major cryptocurrencies were diverted across multiple blockchains: ETH, XRP, USDT, TRX, AVAX, BNB, and ZEC.
🛡️ What’s the impact on users?
• ❄️ Cold Wallets: 100% secured (the cold wallets were not affected).
• 👤 Client balances: No direct impact on your accounts.
• 🛡️ Protection Funds: The Bitget guarantee fund (estimated at over $460M) will cover the entirety of the losses.
🕵️ Who’s behind the hack?
According to CEO Gracy Chen, the IP addresses and the modus operandi point to North Korean hackers (the Lazarus group). Cybersecurity giants Mandiant and SlowMist are working on the case.
🗓️ Withdrawal Recovery Timeline:
✅ Vulnerability fixed & trading operational
📌 Sept. 28: BTC withdrawals
📌 Sept. 29: ETH withdrawals (Ethereum, BSC, Arbitrum, Base, OP)
📌 Sept. 30: USDT withdrawals (Ethereum, BSC, Solana, Tron)
📌 Oct. 2: Other altcoins, fiat, and P2P
Stay cautious and always verify your sources officially! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
🚨 FLASH HACK : What really happened at Bitget? 🚨
A major security incident has rocked the crypto ecosystem. Here’s the full rundown on the situation 🧵👇
💥 The Attack, in Brief
On September 24, 2026, Bitget suffered a vulnerability in its backend infrastructure. The attackers forged internal system permissions to approve fraudulent transfers and drain the hot wallets.
💰 Loss Amount: ~387.5 million $
Major cryptocurrencies were diverted across multiple blockchains: ETH, XRP, USDT, TRX, AVAX, BNB, and ZEC.
🛡️ What’s the impact on users?
• ❄️ Cold Wallets: 100% secured (the cold wallets were not affected).
• 👤 Client balances: No direct impact on your accounts.
• 🛡️ Protection Funds: The Bitget guarantee fund (estimated at over $460M) will cover the entirety of the losses.
🕵️ Who’s behind the hack?
According to CEO Gracy Chen, the IP addresses and the modus operandi point to North Korean hackers (the Lazarus group). Cybersecurity giants Mandiant and SlowMist are working on the case.
🗓️ Withdrawal Recovery Timeline:
✅ Vulnerability fixed & trading operational
📌 Sept. 28: BTC withdrawals
📌 Sept. 29: ETH withdrawals (Ethereum, BSC, Arbitrum, Base, OP)
📌 Sept. 30: USDT withdrawals (Ethereum, BSC, Solana, Tron)
📌 Oct. 2: Other altcoins, fiat, and P2P
Stay cautious and always verify your sources officially! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
183
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#USMidterms-WhatAreMarketsExpecting?
47,694 views
520 Discussing
2
#USOctoberNFP-AreRateCutsStillPossible
223,631 views
1,777 Discussing
3
#AMDBeatsExpectations-AINarrativeContinues
9,362 views
201 Discussing
4
#BinanceIncidentReport
203,953 views
1,213 Discussing
5
#AnthropicIPOPricedDownasInvestorsEye$1.5T
9,017 views
92 Discussing
6
#BinanceReopensWithdrawalsForMoreAssets
329,622 views
2,267 Discussing
7
#HongKongToLicenseVirtualAssetCustodyAndAdvisory
1,703 views
49 Discussing
8
#BinanceHourlyDepositsExceedWithdrawals
141,593 views
1,126 Discussing
9
#SouthKoreaRulingPartyLeaderSeeksCryptoTaxDelay
1,670 views
47 Discussing
10
#MorganStanleyAmongFirstBanksToUseDTCCTokenization
1,524 views
54 Discussing