

#hacking
hacking
368,847 views
286 Discussing
Hot
Latest
·
--
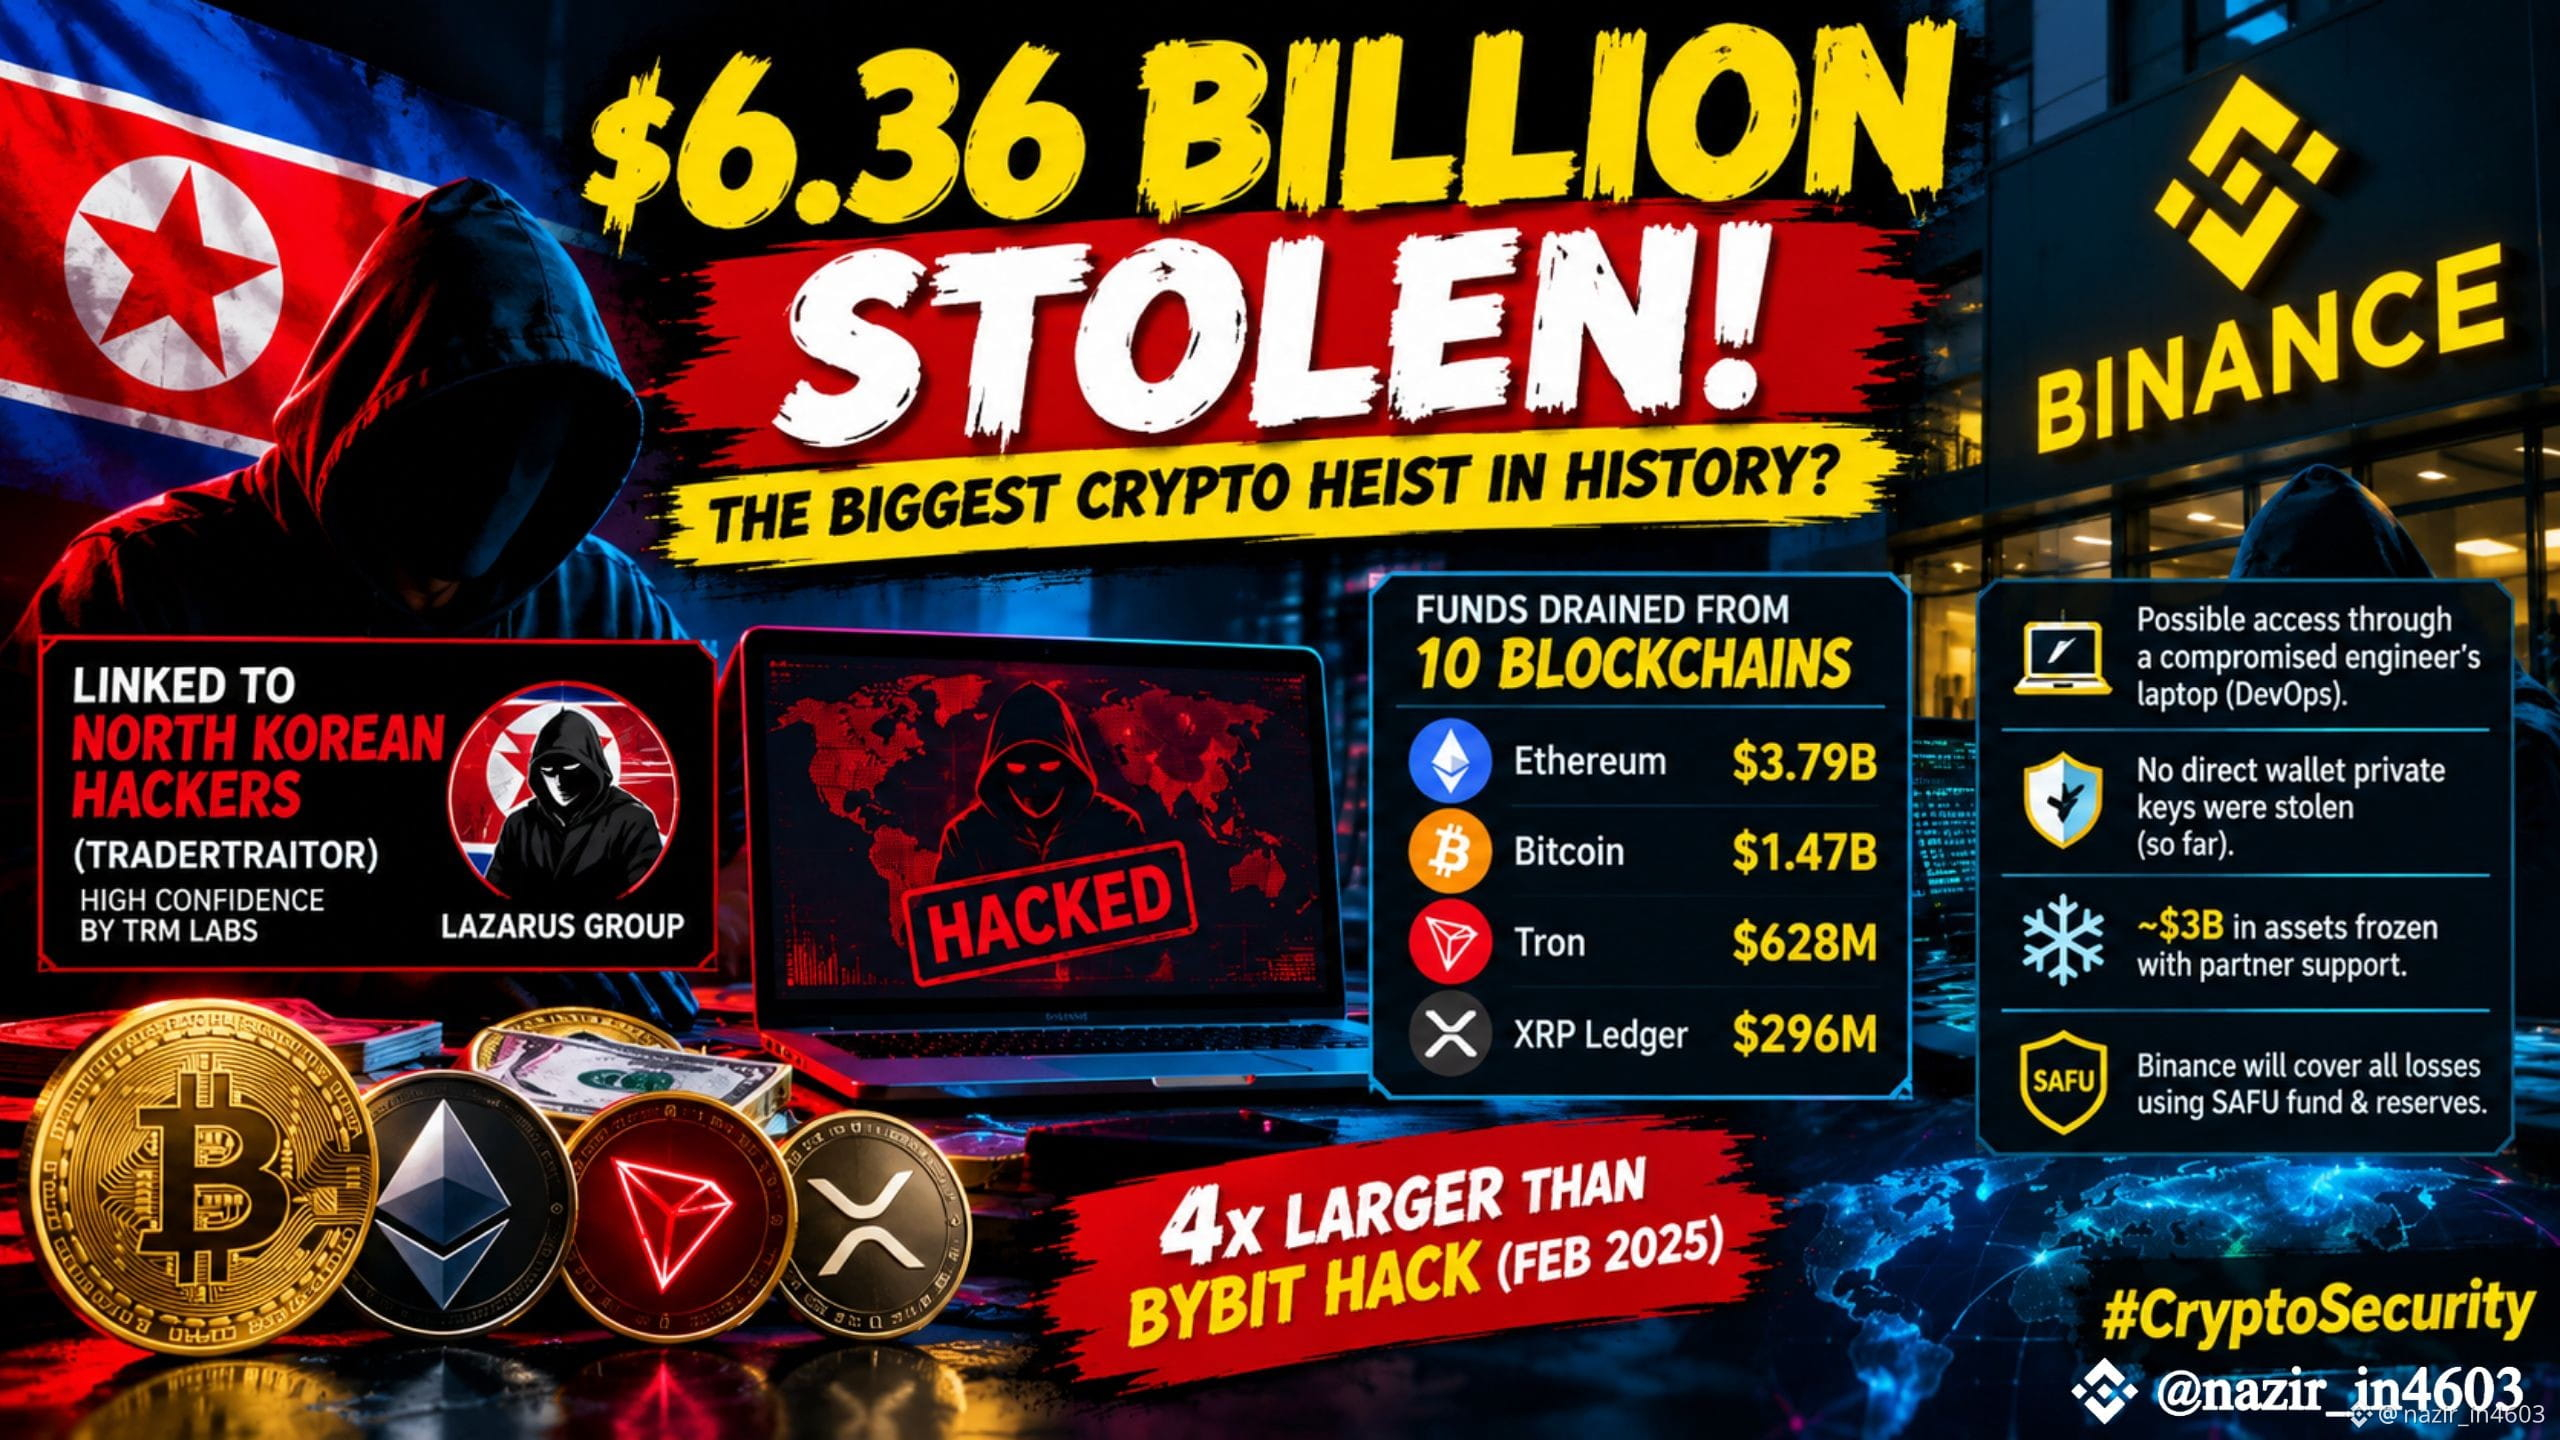
🚨 $6.36 BILLION GONE! THE BIGGEST CRYPTO HEIST IN HISTORY? 😱
The crypto industry has just been hit by a shocking security incident.
Binance, the world's largest cryptocurrency exchange, reportedly suffered a massive $6.36 billion theft, with most of the funds moving out in just 20 minutes.
According to blockchain intelligence firm TRM Labs, the attack has been linked with high confidence to TraderTraitor, a North Korean state-sponsored hacking group.
💰 WHERE DID THE MONEY GO?
🔴 Ethereum: $3.79 Billion
🔴 Bitcoin: $1.47 Billion
🔴 Tron: $628 Million
🔴 XRP Ledger: $296 Million
The attack reportedly affected 10 different blockchain networks.
But here's what makes this incident even more concerning...
Binance's preliminary investigation suggests that attackers may have gained access through a compromised DevOps engineer's laptop, rather than directly stealing wallet private keys.
⚠️ WHAT HAPPENS NEXT?
Binance says approximately $3 billion in affected assets have been frozen through cooperation with blockchain partners.
The exchange has also promised to cover all losses using its SAFU fund and company reserves.
This incident is roughly four times larger than the $1.5 billion Bybit hack in February 2025.
The big question now is: How much of the remaining funds can investigators recover?
💬 What's your take?
Can the crypto industry recover from a security breach of this magnitude?
Share your thoughts below! 👇
#Binance #CryptoNews #CryptoSecurity #Bitcoin #Ethereum #XRP #Blockchain #CryptoMarket #Hacking
90

The paradox of Binance’s $6.3 billion hack: Centralization was both the cause and the solution that saved $3 billion
• Binance’s $6.3 billion hack sparked debate over the pros and cons of centralization in the digital asset industry.
• Experts say centralized mechanisms enabled the attacker to steal a large amount of funds, but also helped Binance recover more than $3 billion.
• The incident raises the question of whether decentralization truly offers the greatest security benefits to the industry.
#BinanceSquare #CryptoNews #Hacking #Binance
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
141
Article
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️
🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
2
373

·
--
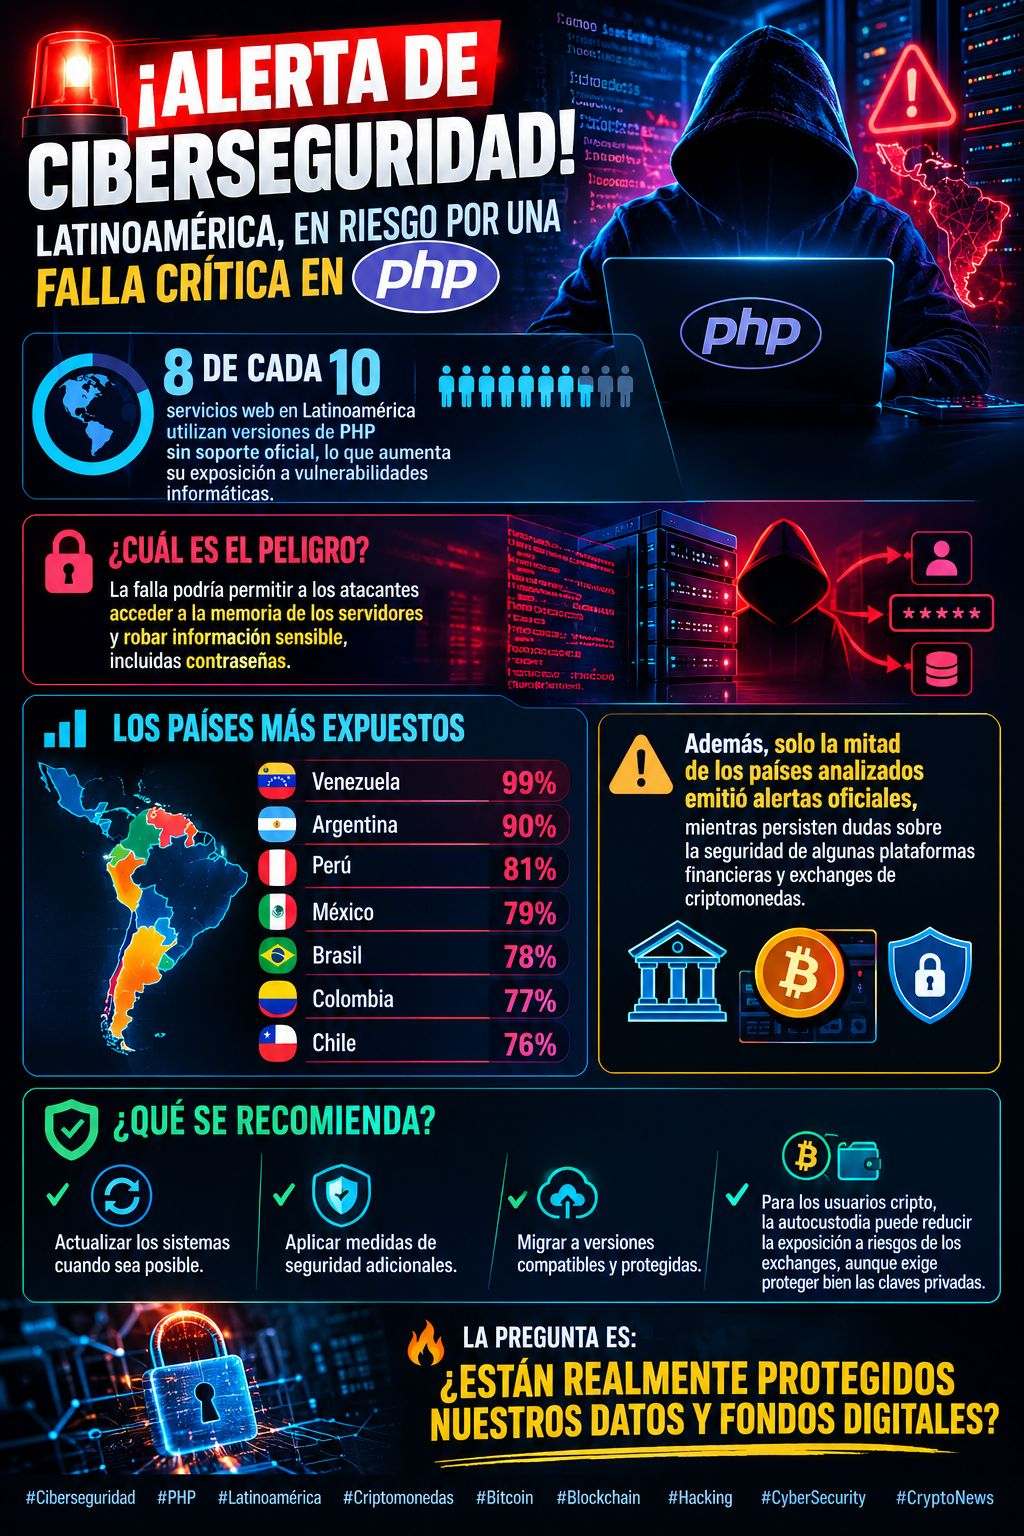
🚨 CYBERSECURITY ALERT! LATIN AMERICA AT RISK FROM A CRITICAL PHP FLAW!💻⚠️
🌎 8 out of 10 web services in Latin America use PHP versions that are no longer officially supported, increasing their exposure to cyber vulnerabilities.
🔓 What’s the danger? The flaw could allow attackers to access server memory and steal sensitive information, including passwords.
📊 The most exposed countries:
🇻🇪 Venezuela: 99%
🇦🇷 Argentina: 90%
🇵🇪 Peru: 81%
🇲🇽 Mexico: 79%
🇧🇷 Brazil: 78%
🇨🇴 Colombia: 77%
🇨🇱 Chile: 76%
⚠️ Additionally, only half of the countries analyzed issued official alerts, while concerns remain about the security of some financial platforms and cryptocurrency exchanges.
🛡️ What’s recommended? Update systems whenever possible, apply additional security measures, and migrate to supported, secure versions. For crypto users, self-custody can reduce exposure to risks associated with exchanges, although it also requires properly securing private keys.
🔥 The question is: are our data and digital funds really protected?
$BTC
#Blockchain #Hacking #CyberSecurity #CryptoNews
3
735

UK CYBERSECURITY ALERT 🇬🇧
Hackers reportedly stole the personal data of 3,300 people after breaching a UK company’s systems protected by the password Password1
Weak passwords can put sensitive data at serious risk.
One weak password. Thousands potentially affected.
#CybersecurityUpdate #hacking #technews
Hackers reportedly stole the personal data of 3,300 people after breaching a UK company’s systems protected by the password Password1
Weak passwords can put sensitive data at serious risk.
One weak password. Thousands potentially affected.
#CybersecurityUpdate #hacking #technews
66

Article
TOKEN APPROVALS: THE PERMISSION THAT CAN LEAVE YOUR CRYPTO EXPOSED WITHOUT YOU KNOWING$ETH $BTC $USDC
You can disconnect your wallet, close a website, delete an app, and believe your crypto is safe. But a permission you authorized months ago could still be active, waiting to be used.
And most concerning of all: to take advantage of certain authorizations, a criminal doesn’t need to know your password, steal your seed phrase, or physically access your device.
This is not a theory. It is a real risk in the decentralized finance (DeFi) ecosystem, documented by MetaMask, Etherscan, and blockchain security specialists.
TOKEN APPROVALS: THE PERMISSION THAT CAN LEAVE YOUR CRYPTO EXPOSED WITHOUT YOU KNOWING
$ETH $BTC $USDC
You can disconnect your wallet, close a website, delete an app, and believe your crypto is safe. But a permission you authorized months ago could still be active, waiting to be used.
And most concerning of all: to take advantage of certain authorizations, a criminal doesn’t need to know your password, steal your seed phrase, or physically access your device.
This is not a theory. It is a real risk in the decentralized finance (DeFi) ecosystem, documented by MetaMask, Etherscan, and blockchain security specialists.
1
171

·
--
Bearish
🚨 Moonwell just got drained for $8.7M.
Theo PeckShieldAlert, the Moonwell lending protocol on Base was just attacked, causing damage of approximately $8.7M.
Token $WELL is also under pressure, down more than 7% at the time the news was reported.
This is another painful reminder for DeFi:
High TVL doesn’t mean the smart contract is safe.
$8.7M just disappeared in a few transactions, and users were “airdrop”-ed a free security lesson. 💀
DeFi: where the yield is real and sometimes the money is too.
Do you think this is a smart contract vulnerability, or could it be related to oracles / price manipulation?
#defi $Moonwell #WELL #Base #Crypto #hacking
34

·
--
Gravity Bridge hacked for $5.4M.
Gravity Bridge Loses $5.4 Million in Suspected Signing Key Compromise
The suspected signing key compromise has resulted in a significant loss for Gravity Bridge, with the attacker still holding a substantial amount of ETH. This incident highlights the importance of secure key management in crypto. Traders should watch for potential market impacts.
#Crypto #Blockchain #Web3 #Hacking
54

·
--
Bullish
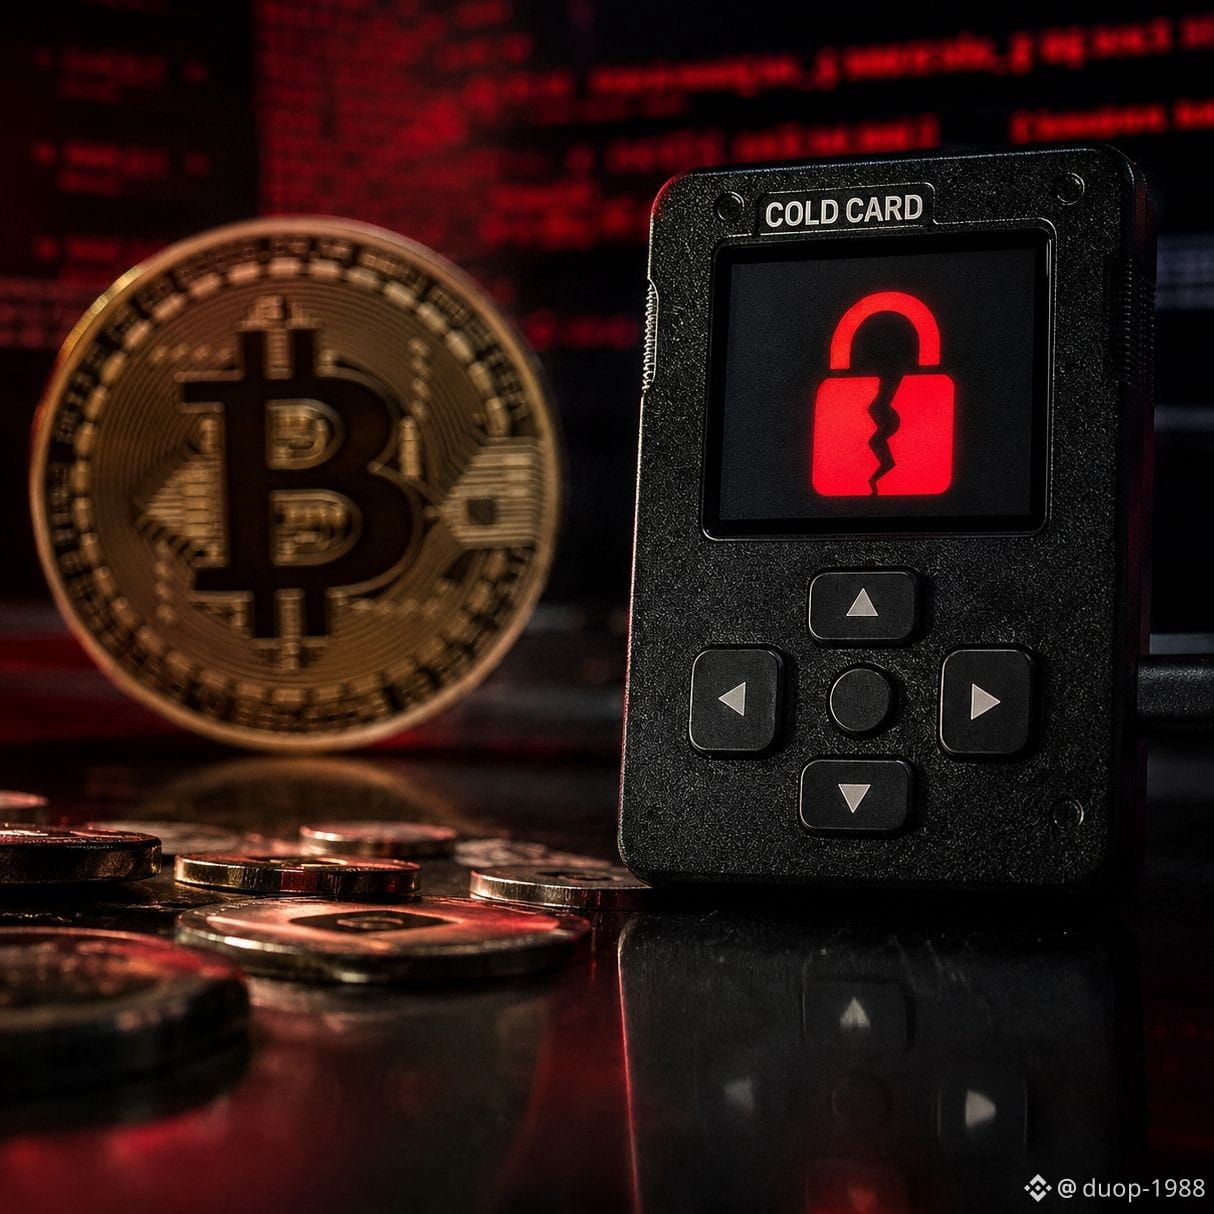
🚨 ALERT: Coldcard hack for $120M shakes self-custody of $BTC
The Coldcard hardware wallet exploit is the news of the day. Losses are already around $114M, and analysts warn there could be a fourth sweep.
The volume of funds moved even lit up the Bitcoin mempool—something not seen in months. Coinkite has already asked users who generated seeds with Coldcard to move funds immediately with new security practices.
This event is reigniting the debate: total self-custody or regulated custody? Many analysts believe it will boost demand for ETFs and institutional custody.
$BTC $ETH
#Bitcoin❗ #BTC #Coldcard #Hacking
1
306
·
--
What is OpenAI doing to tighten AI rules after the Hugging Face breach
OpenAI is also working to strengthen the restrictions placed on models that perform high-risk tasks online. Some systems will face additional limitations on internet access, while training and testing that includes generated code or untrusted code will require stronger isolation through sandboxed environments.
These measures came after what OpenAI and Anthropic revealed about some AI systems unintentionally reaching computer systems at a number of institutions—including Hugging Face—during security evaluations. These incidents highlighted the difficulty of predicting the behavior of increasingly capable AI agents when given greater autonomy.
Mia Glaes, OpenAI’s vice president for research, said the company is working to ensure its security procedures evolve in parallel with the rapid improvement in model capabilities. OpenAI had previously paused work on an upcoming model to strengthen security safeguards, and announced Tuesday that a major training process remains on hold.
The company added that it plans to publish a detailed assessment of the Hugging Face incident, while continuing to review how its models interact with external systems.
#AI #hacking #COPPERUSDT #BTC $OPENAI
{future}(OPENAIUSDT)
$COPPER
{future}(COPPERUSDT)
What is OpenAI doing to tighten AI rules after the Hugging Face breach
OpenAI is also working to strengthen the restrictions placed on models that perform high-risk tasks online. Some systems will face additional limitations on internet access, while training and testing that includes generated code or untrusted code will require stronger isolation through sandboxed environments.
These measures came after what OpenAI and Anthropic revealed about some AI systems unintentionally reaching computer systems at a number of institutions—including Hugging Face—during security evaluations. These incidents highlighted the difficulty of predicting the behavior of increasingly capable AI agents when given greater autonomy.
Mia Glaes, OpenAI’s vice president for research, said the company is working to ensure its security procedures evolve in parallel with the rapid improvement in model capabilities. OpenAI had previously paused work on an upcoming model to strengthen security safeguards, and announced Tuesday that a major training process remains on hold.
The company added that it plans to publish a detailed assessment of the Hugging Face incident, while continuing to review how its models interact with external systems.
#AI #hacking #COPPERUSDT #BTC $OPENAI
$COPPER
128
·
--
Crypto users lose millions to hackers.
$6.7 million drained – How a user lost funds from both Coinbase and Kraken
A recent incident saw a user lose $6.7 million from both Coinbase and Kraken, highlighting the need for enhanced security measures. This matters to traders and holders as it shows that even major exchanges can be vulnerable. Users should be cautious and monitor their accounts closely.
#Crypto #CyberSecurity #Blockchain #Hacking
19



#BlockstreamRefusesToPayRansomToLiquidAttacker
It is said that Blockstream refuses to pay a ransom after a major breach of the Liquid Network (Liquid Network), in which roughly 4,000 BTC (~$320 million) was withdrawn.
What’s the biggest shift? 👀
The attackers claimed they are “white-hat” pirates and said they would return the funds after fixing the vulnerability. It is noted that about 3,400 BTC has already been returned, while around 598 BTC is still stuck.
🔥 TRADE RADAR
⚠️ The infrastructure risk level for crypto assets remains high
🛡️ The lights have returned to security and custody
₿ Bitcoin market sentiment may react to further developments
👀 Monitor BTC volatility closely
Will you trust a “white-hat” hacker to empty $300M+ first? 🤔
Please follow up
$RAY $SAGA $MARSCOIN
#Blockstream #LiquidNetwork #CryptoSecurity #hacking

2
60

·
--
BREAKTHROUGHA major victory for blockchain security has been achieved in the United States, with Bybit winning court orders to trace and freeze assets from its $1.5B North Korea linked hack. This historic win could set a precedent for future cases, and marks a significant milestone in the ongoing battle against cryptocurrency-related crime.
#CryptoSecurity #BlockchainLaw #Hacking
The U.S. court's decision is a powerful signal that institutions are taking action to protect investors and prevent illicit activities from taking place within the cryptocurrency ecosystem. Bybit's efforts to recover the stolen funds have already shown promising results, with $48.4M recovered and another $30.5M frozen.
The stakes are high, with this ruling potentially having a ripple effect across the market, as exchanges and other players in the space begin to take a more active role in preventing and responding to hacks. As the cryptocurrency industry continues to grow and mature, this development is a crucial step towards establishing a safer and more secure environment for all participants.
So, what does this mean for you? Will you be investing in the next big security-focused project to take advantage of this growing trend, or will you be watching from the sidelines as the market continues to evolve? Stay ahead of the curve and join the conversation - let's shape the future of cryptocurrency together. Are you ready to build a safer, more secure investment portfolio?
BREAKTHROUGH
A major victory for blockchain security has been achieved in the United States, with Bybit winning court orders to trace and freeze assets from its $1.5B North Korea linked hack. This historic win could set a precedent for future cases, and marks a significant milestone in the ongoing battle against cryptocurrency-related crime.
#CryptoSecurity #BlockchainLaw #Hacking
The U.S. court's decision is a powerful signal that institutions are taking action to protect investors and prevent illicit activities from taking place within the cryptocurrency ecosystem. Bybit's efforts to recover the stolen funds have already shown promising results, with $48.4M recovered and another $30.5M frozen.
The stakes are high, with this ruling potentially having a ripple effect across the market, as exchanges and other players in the space begin to take a more active role in preventing and responding to hacks. As the cryptocurrency industry continues to grow and mature, this development is a crucial step towards establishing a safer and more secure environment for all participants.
So, what does this mean for you? Will you be investing in the next big security-focused project to take advantage of this growing trend, or will you be watching from the sidelines as the market continues to evolve? Stay ahead of the curve and join the conversation - let's shape the future of cryptocurrency together. Are you ready to build a safer, more secure investment portfolio?
35
·
--
Bullish
ALERT: Security researchers have identified a malware campaign called "TrapDoor" that targets the crypto development environments of @Aptos, @SuiNetwork, and @Solana through over 34 malicious packages designed to steal SSH keys and wallet credentials.
#hacking #BinanceSquareFamily $WLD $SUI $APT #solana
#hacking #BinanceSquareFamily $WLD $SUI $APT #solana
682
How hackers recovered 43.6 BTC after 11 years
A happy ending story: a European, Michael, restored access to a wallet containing 43.6 BTC that he believed was lost since 2013.
Michael generated a complex password using the RoboForm password manager
For security, he saved it in a separate TrueCrypt container, but the file became corrupted over time
Access was blocked
In 2022, Michael hired the well-known “white-hat” hacker Joe Grande
Together with a partner, he reverse-engineered the 2013 version of RoboForm and found a critical bug: the RoboForm random number generator was defective
The generated passwords were hard-tied to the date and time on the PC
Knowing the time the password was created, it became predictable.
The hackers learned the date the bitcoins were transferred and started trying different timestamps
In the end, they found the correct password created on May 15, 2013
The hackers took their share when BTC was worth $38,000
Michael booked part of the profits at $62,000
Today he has 30 BTC left (~$3 million)
And yet, it was less fortunate for the Englishman James Howells: he is still searching a landfill for the discarded hard drive with 7500 $BTC
#CryptoSecurity #RoboForm #hacking
{spot}(BTCUSDT)
How hackers recovered 43.6 BTC after 11 years
A happy ending story: a European, Michael, restored access to a wallet containing 43.6 BTC that he believed was lost since 2013.
Michael generated a complex password using the RoboForm password manager
For security, he saved it in a separate TrueCrypt container, but the file became corrupted over time
Access was blocked
In 2022, Michael hired the well-known “white-hat” hacker Joe Grande
Together with a partner, he reverse-engineered the 2013 version of RoboForm and found a critical bug: the RoboForm random number generator was defective
The generated passwords were hard-tied to the date and time on the PC
Knowing the time the password was created, it became predictable.
The hackers learned the date the bitcoins were transferred and started trying different timestamps
In the end, they found the correct password created on May 15, 2013
The hackers took their share when BTC was worth $38,000
Michael booked part of the profits at $62,000
Today he has 30 BTC left (~$3 million)
And yet, it was less fortunate for the Englishman James Howells: he is still searching a landfill for the discarded hard drive with 7500 $BTC
#CryptoSecurity #RoboForm #hacking
1
153

·
--
Revolut hacked! A $3M Monero + 10k Bitcoin ransom is on the table, but Revolut says there was no direct contact. A smart move by the hackers—choosing both privacy coin XMR and mainstream BTC, covering all scenarios. This kind of mess might scare users in the short term, but in the long run it just proves that privacy coins and Bitcoin each have their own place. $XMR $BTC #黑客攻击 #加密安全
Revolut getting hacked! $3M in Monero + 10k Bitcoin ransom on the table, but Revolut says no direct contact. Smart move by hackers - picking both privacy coin XMR and mainstream BTC, covering all scenarios. This kinda mess might scare users short-term, but long-term it just proves privacy coins and Bitcoin each have their place. $XMR $BTC #Hacking #CryptoSecurity
Revolut getting hacked! $3M in Monero + 10k Bitcoin ransom on the table, but Revolut says no direct contact. Smart move by hackers - picking both privacy coin XMR and mainstream BTC, covering all scenarios. This kinda mess might scare users short-term, but long-term it just proves privacy coins and Bitcoin each have their place. $XMR $BTC #Hacking #CryptoSecurity
143
·
--
⚠️ 🚨🚨⚡️CYBER ALERT:
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
⚠️ 🚨🚨⚡️CYBER ALERT:
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
Hackers now use AI to create smarter phishing attacks and fake identities. 🛑
Cybersecurity entering a new era.
#CyberSecurity #AI #Hacking
92
·
--
Bullish
Do you have any idea about it.. 🤔 How much profit from it $AAPLB $BTC $SPCX.US
#Hacking #btcupdates #today #Market_Update #Ethereum
Do you have any idea about it.. 🤔 How much profit from it $AAPLB $BTC $SPCX.US
#Hacking #btcupdates #today #Market_Update #Ethereum
#Hacking #btcupdates #today #Market_Update #Ethereum
200
·
--
why everyone topic always binance hack binance hack.
hacking is normal activity lol😂, even u buying btc its cheat code for freedom (hacking).
btw already reminding this to you all 😂
#BinanceHack2026 #HackerAlert #LazarusGroup #hacking #BTC
why everyone topic always binance hack binance hack.
hacking is normal activity lol😂, even u buying btc its cheat code for freedom (hacking).
btw already reminding this to you all 😂
#BinanceHack2026 #HackerAlert #LazarusGroup #hacking #BTC
hacking is normal activity lol😂, even u buying btc its cheat code for freedom (hacking).
btw already reminding this to you all 😂
#BinanceHack2026 #HackerAlert #LazarusGroup #hacking #BTC
SYCHTE
·
--
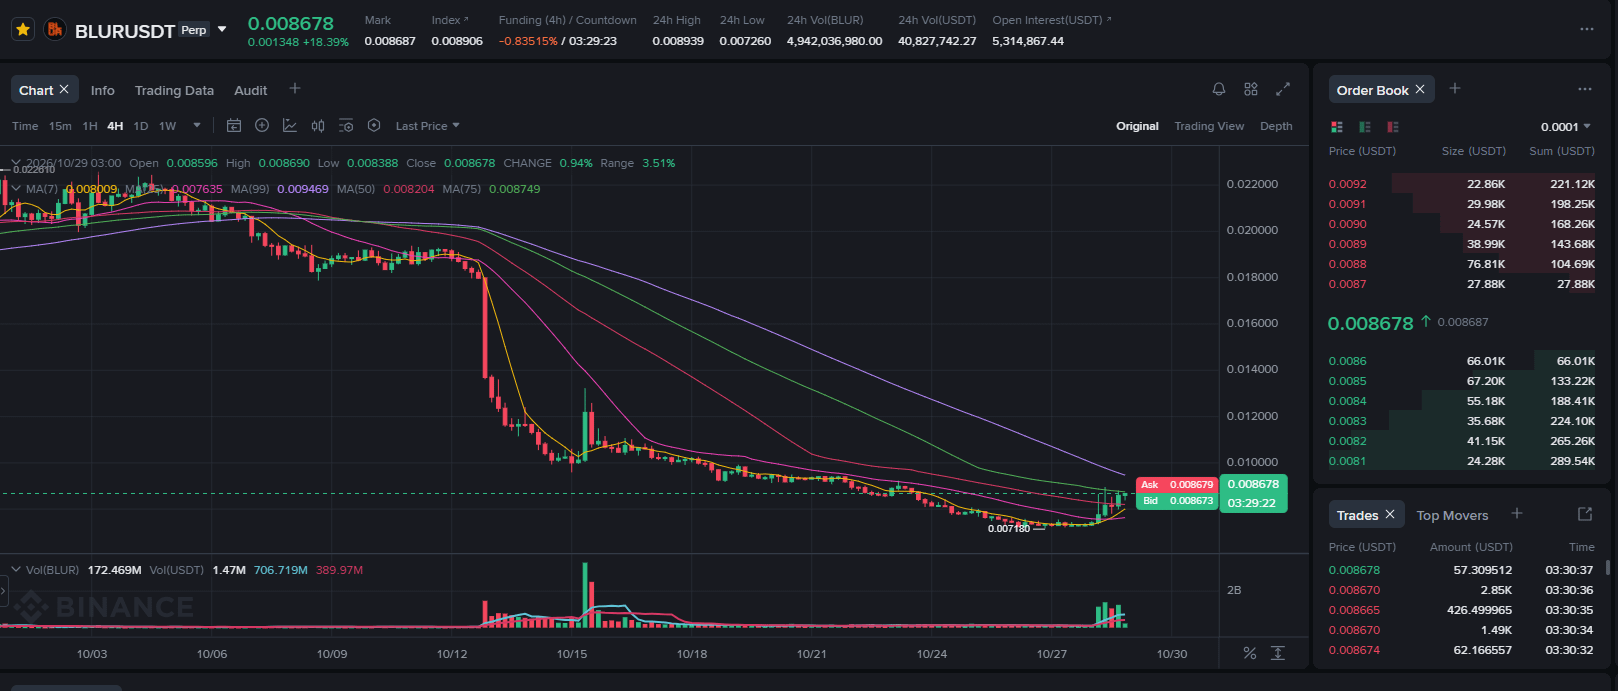
Bullish$BLUR #BLUR #nft #MarketMoves #Bullrun #altcoins
Market goes up and down its like a blurrrrr🙄🙄😂😂
Market goes up and down its like a blurrrrr🙄🙄😂😂
1
95
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinanceSAFUFundTransferCompleted7499BTC
29,387 views
687 Discussing
2
#BinanceRecovery90% of stolen assets
118,040 views
155 Discussing
3
#YiHe:ProofOfReserves:10TokensAt100%Backing
122,362 views
686 Discussing
4
#BackedNotBroken:RichardTengSaysUsersBearNoLoss
32,519 views
424 Discussing
5
#CZSaysCompensationIsinPlaceUsersAreProtected
116,126 views
1,336 Discussing
6
#IntelHasItsWorstDaySince1974
42,543 views
674 Discussing
7
#TRMCambodianCasinosReceived$1.07BInCrypto
11,138 views
66 Discussing
8
#USDCCirculationFallsAbout800MInSevenDays
65,590 views
702 Discussing
9
#SuspectedNorthKoreaAttacksAccountForNearly89%OfCryptoHackLosses
14,064 views
94 Discussing
10
#OpenAICutsFundraisingTargetBy$10B
3,403 views
73 Discussing