
#keplr
keplr
44,819 views
56 Discussing
Hot
Latest

#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
1
829
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
{future}(BTCUSDT)
$HYPE
{future}(HYPEUSDT)
$ONE
{future}(ONEUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
484
·
--
🚨 URGENT: Keplr Security Alert! 🚨
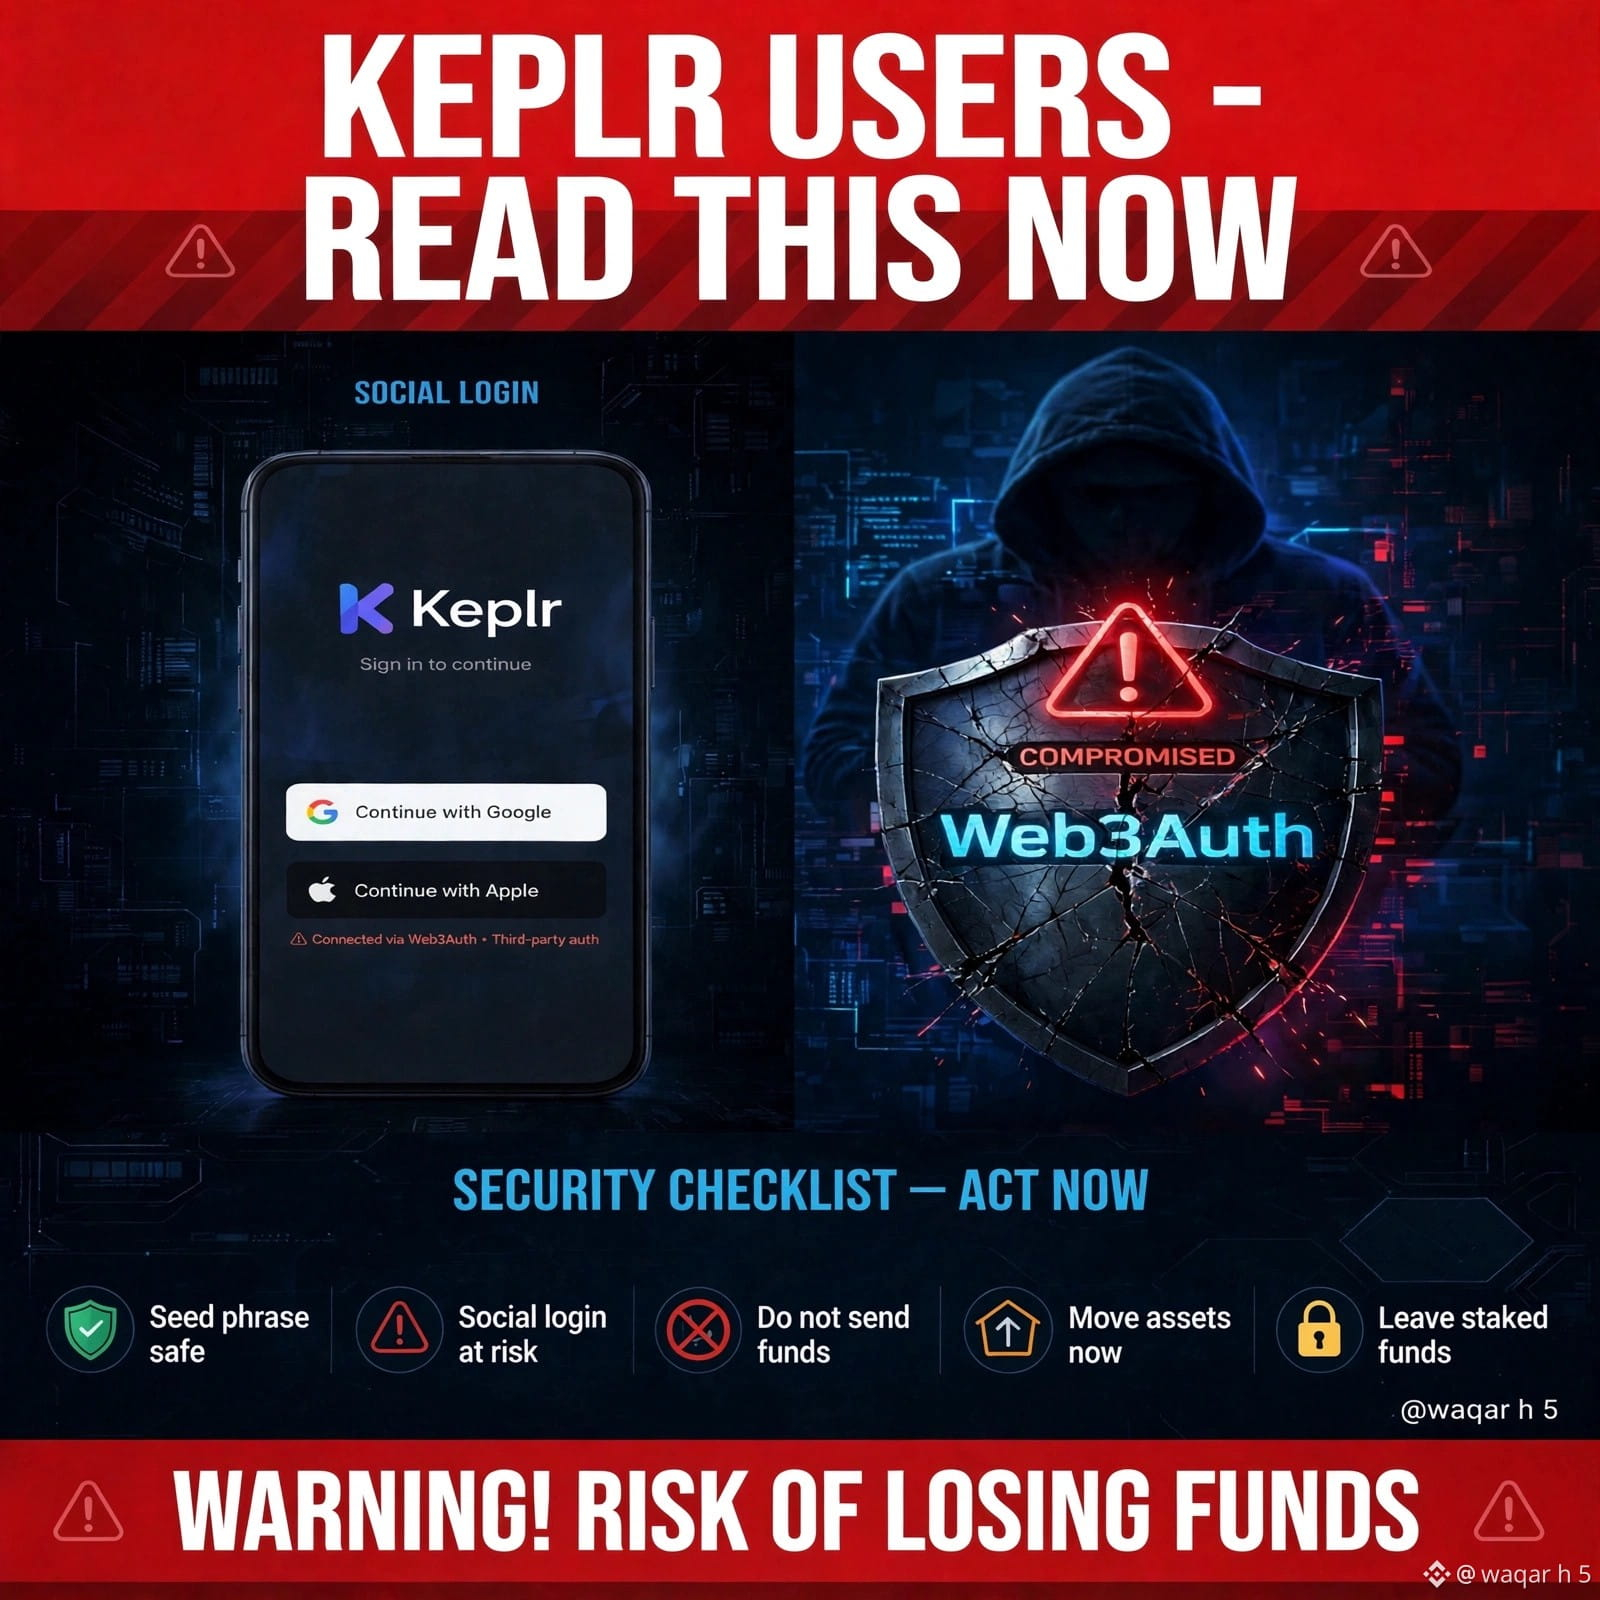
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 URGENT: Keplr Security Alert! 🚨
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
4
150

·
--
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
2
2.1k

·
--
Article
If you use your Google account to log in to your wallet, today’s news concerns youThis afternoon, Keplr, a wallet in the Cosmos ecosystem, posted an announcement. Some wallets created by signing in with a Google or Apple account have seen transfers that users did not authorize. Keplr has paused both Google and Apple sign-in while it investigates the cause with Web3Auth, the provider of its login technology. Web3Auth has also acknowledged the issue. Just after 11 p.m. last night, it issued a statement saying its service had a security issue and that its embedded wallet service had been suspended.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
If you use your Google account to log in to your wallet, today’s news concerns you
This afternoon, Keplr, a wallet in the Cosmos ecosystem, posted an announcement. Some wallets created by signing in with a Google or Apple account have seen transfers that users did not authorize. Keplr has paused both Google and Apple sign-in while it investigates the cause with Web3Auth, the provider of its login technology. Web3Auth has also acknowledged the issue. Just after 11 p.m. last night, it issued a statement saying its service had a security issue and that its embedded wallet service had been suspended.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
GOOGUS+1.10%
必备小神器888:
谷歌登录钱包本质是便利换安全,大额别放,等Web3Auth把根因查清再谈信任。
1
668
#keplradvisessocialloginuserstotransferassets
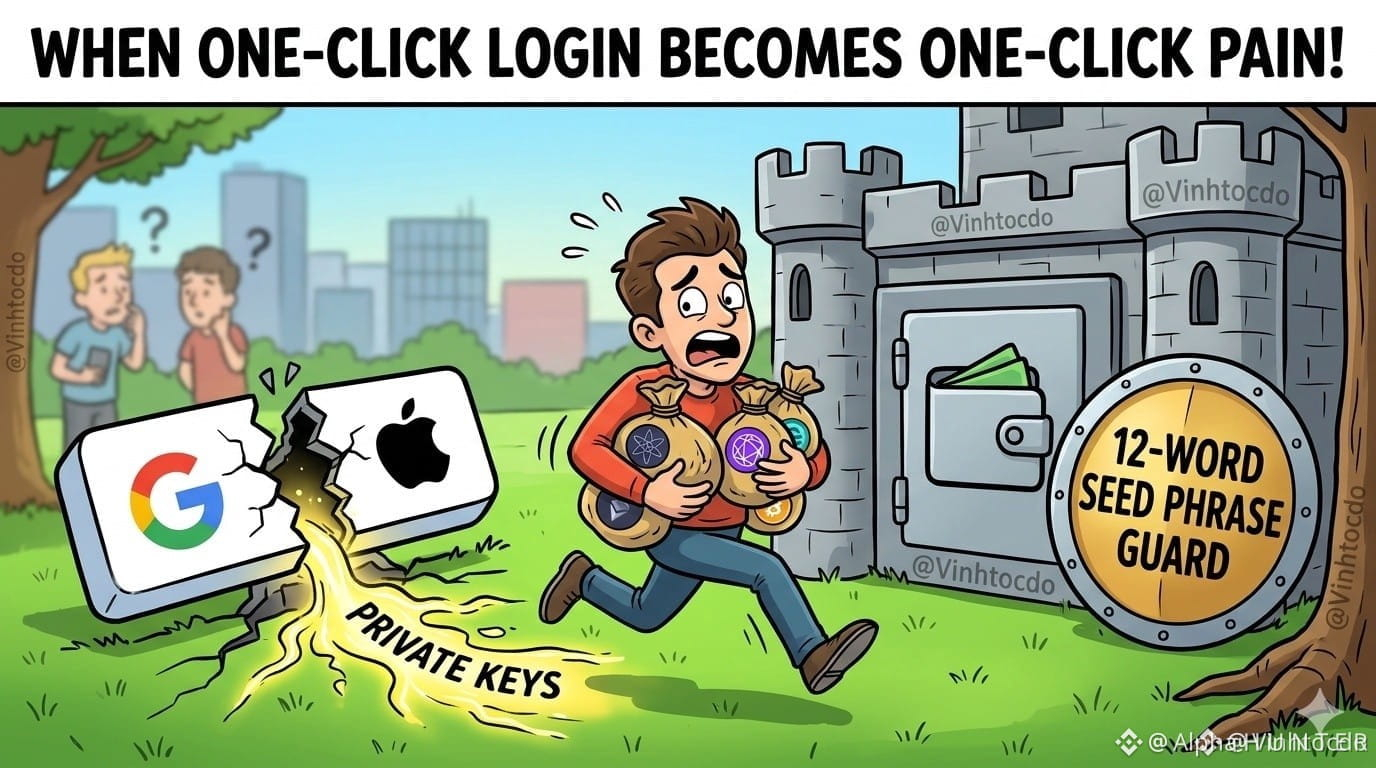
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
{future}(AIOTUSDT)
$JCT
{future}(JCTUSDT)
$IDOL
{future}(IDOLUSDT)
#keplradvisessocialloginuserstotransferassets
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
$JCT
$IDOL
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
$JCT
$IDOL
3
1.9k

·
--
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-insWallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-ins
Wallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
GOOGUS+1.10%
買不起比特幣只能買比特犬:
所有熱錢包都不要用,並移除所有㽞覽器插件
1
171
·
--
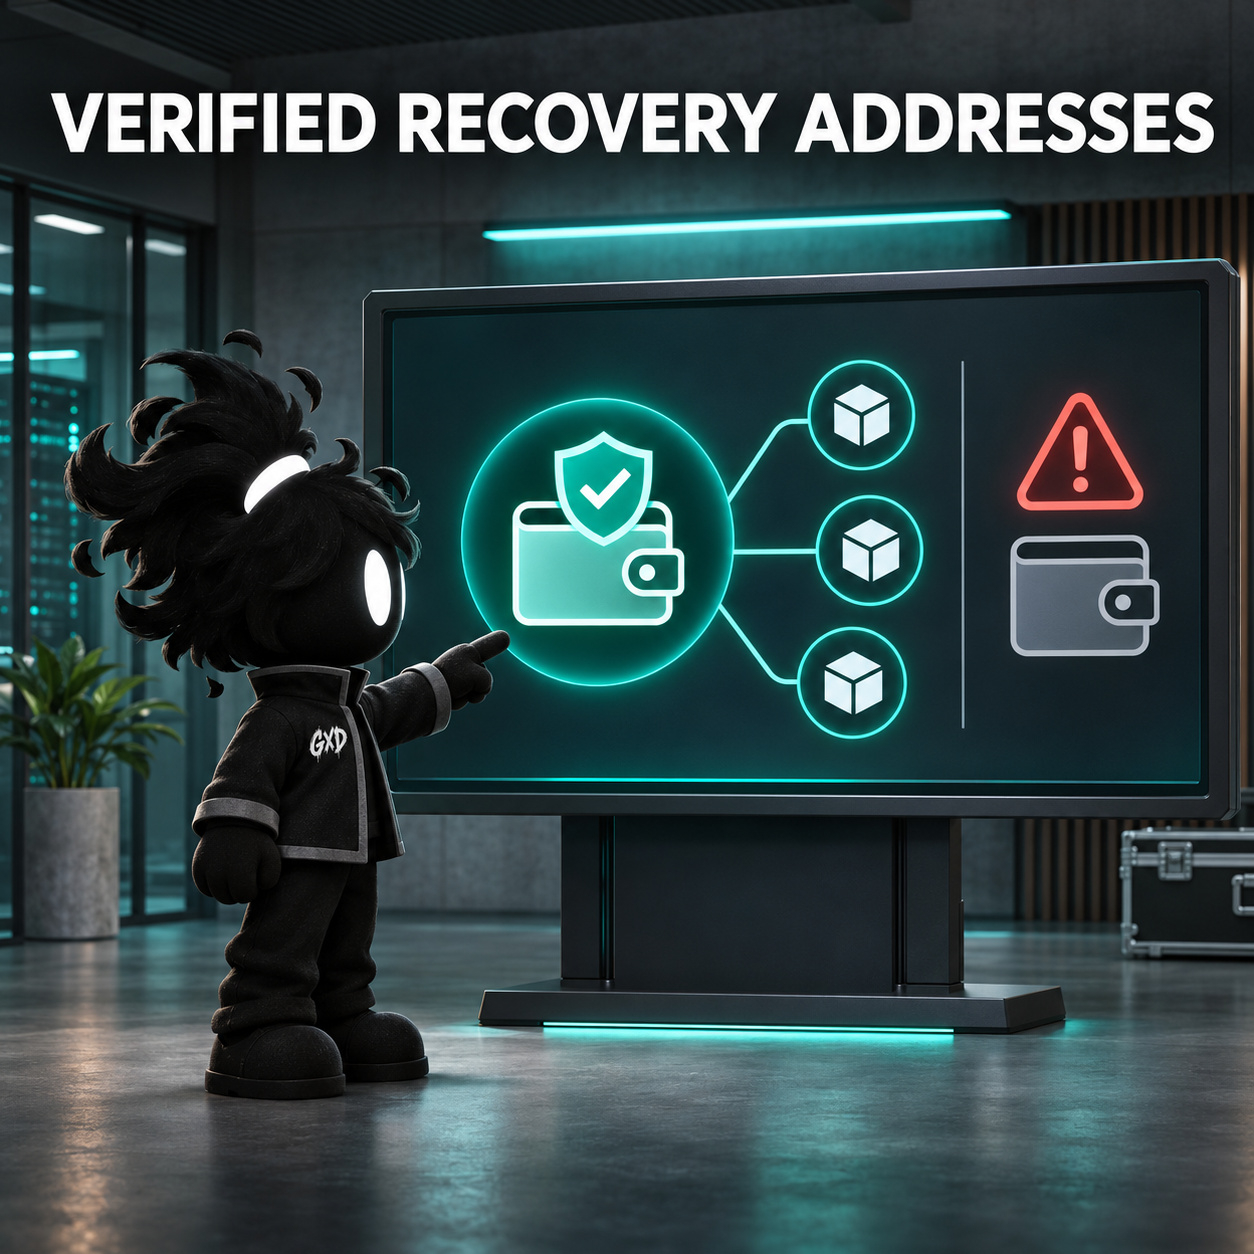
In a new update on the Keplr incident, Web3Auth published verified recovery wallet addresses and said some of the visible transfers were part of rescue efforts. Don’t judge a transfer by how it looks; match the address with the official account and ignore private recovery messages. Have you seen the update? 🛡️🔎🔐
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB. General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
In a new update on the Keplr incident, Web3Auth published verified recovery wallet addresses and said some of the visible transfers were part of rescue efforts. Don’t judge a transfer by how it looks; match the address with the official account and ignore private recovery messages. Have you seen the update? 🛡️🔎🔐
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB . General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB . General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
33
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity

Keplr got drained this time, but don’t just focus on blaming Keplr.
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
Keplr got drained this time, but don’t just focus on blaming Keplr.
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
5

·
--
【Market Alert】Keplr Private Key Leak: Social Login Users, Move Your Assets Now
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
【Market Alert】Keplr Private Key Leak: Social Login Users, Move Your Assets Now
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
9
·
--
#Keplr建议社交登录用户转移资产
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
{future}(BNBUSDT)
{web3_wallet_create}(560xc6bff31bbfa84d3c05ad61d8ec47be8b31517777)
#Keplr建议社交登录用户转移资产
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
157
🚨 Keplr crypto wallet under threat: users report missing funds
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
🚨 Keplr crypto wallet under threat: users report missing funds
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
2
631

·
--
Keplr social-login wallet incident: Who actually holds your private keys?
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
Keplr social-login wallet incident: Who actually holds your private keys?
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
4

·
--
【Google-login wallets were stolen! Keplr shuts down social logins overnight】
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
【Google-login wallets were stolen! Keplr shuts down social logins overnight】
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
40
·
--
Last week, after Binance was hacked, the whole internet was shouting “self-custody.” This week, self-custody itself took a hit: accounts created on Keplr with Google/Apple social login suffered unauthorized transfers. The team has suspended social logins and is investigating with Web3Auth. Users with seed phrases and hardware wallets are unaffected. The Akash team is urging people to move their $AKT to pure self-custody wallets, and stakers have a 21-day window to cooperate with the recovery effort.
The bottom line: social login really is convenient, but you’re entrusting a third party with the process for recovering your private keys. Last week’s problem was “letting the exchange hold your keys”; this week’s is “letting your login method hold your keys.” Different name, same underlying risk—every extra pair of hands that touches your keys is another point of failure. Write down your seed phrase and lock it in a drawer; keep large amounts in a hardware wallet. It’s old-school, but it keeps you safe.
The AI sector didn’t take the weekend off either: Marvell is acquiring Lumentum in an all-stock deal, implying an enterprise value of $115 billion, bundling up the lucrative optical-module business; Microsoft reportedly considers Nvidia chips in Oracle data centers outdated and is gradually scaling back rentals as it reassesses its commitments to external cloud providers; Intel had it worse, plunging 57% in Q4 to the bottom of the S&P 500. The AI sector is reshuffling internally, with money flowing away from those selling a vision and toward those able to deliver.
Risk alert: oil tankers in the Strait of Hormuz have repeatedly struck mines, while the Houthis claim to have hit Aramco facilities in Riyadh and Khurais. The November 9 new moon and Trump’s eight-week window are still looming. With thin weekend liquidity, position sizing matters more than opinions.
$AKT $MRVL $INTC
NFA DYOR
#比特币 #Keplr #安全事件 #AI #Crypto
Last week, after Binance was hacked, the whole internet was shouting “self-custody.” This week, self-custody itself took a hit: accounts created on Keplr with Google/Apple social login suffered unauthorized transfers. The team has suspended social logins and is investigating with Web3Auth. Users with seed phrases and hardware wallets are unaffected. The Akash team is urging people to move their $AKT to pure self-custody wallets, and stakers have a 21-day window to cooperate with the recovery effort.
The bottom line: social login really is convenient, but you’re entrusting a third party with the process for recovering your private keys. Last week’s problem was “letting the exchange hold your keys”; this week’s is “letting your login method hold your keys.” Different name, same underlying risk—every extra pair of hands that touches your keys is another point of failure. Write down your seed phrase and lock it in a drawer; keep large amounts in a hardware wallet. It’s old-school, but it keeps you safe.
The AI sector didn’t take the weekend off either: Marvell is acquiring Lumentum in an all-stock deal, implying an enterprise value of $115 billion, bundling up the lucrative optical-module business; Microsoft reportedly considers Nvidia chips in Oracle data centers outdated and is gradually scaling back rentals as it reassesses its commitments to external cloud providers; Intel had it worse, plunging 57% in Q4 to the bottom of the S&P 500. The AI sector is reshuffling internally, with money flowing away from those selling a vision and toward those able to deliver.
Risk alert: oil tankers in the Strait of Hormuz have repeatedly struck mines, while the Houthis claim to have hit Aramco facilities in Riyadh and Khurais. The November 9 new moon and Trump’s eight-week window are still looming. With thin weekend liquidity, position sizing matters more than opinions.
$AKT $MRVL $INTC
NFA DYOR
#比特币 #Keplr #安全事件 #AI #Crypto
The bottom line: social login really is convenient, but you’re entrusting a third party with the process for recovering your private keys. Last week’s problem was “letting the exchange hold your keys”; this week’s is “letting your login method hold your keys.” Different name, same underlying risk—every extra pair of hands that touches your keys is another point of failure. Write down your seed phrase and lock it in a drawer; keep large amounts in a hardware wallet. It’s old-school, but it keeps you safe.
The AI sector didn’t take the weekend off either: Marvell is acquiring Lumentum in an all-stock deal, implying an enterprise value of $115 billion, bundling up the lucrative optical-module business; Microsoft reportedly considers Nvidia chips in Oracle data centers outdated and is gradually scaling back rentals as it reassesses its commitments to external cloud providers; Intel had it worse, plunging 57% in Q4 to the bottom of the S&P 500. The AI sector is reshuffling internally, with money flowing away from those selling a vision and toward those able to deliver.
Risk alert: oil tankers in the Strait of Hormuz have repeatedly struck mines, while the Houthis claim to have hit Aramco facilities in Riyadh and Khurais. The November 9 new moon and Trump’s eight-week window are still looming. With thin weekend liquidity, position sizing matters more than opinions.
$AKT $MRVL $INTC
NFA DYOR
#比特币 #Keplr #安全事件 #AI #Crypto
329
·
--
Here's an opinion that might offend some people: “Logging into a wallet with one click using your Google/Apple account” essentially means handing a third party the keys to look after.
Keplr said early this morning that some accounts created using Google/Apple login had unauthorized transfers, and login has been suspended. Apparently, Web3Auth, the service behind it, suffered a security incident. The founder initially estimated that around 20% of social-login accounts were affected, but only some of those were actually accessed (estimate, pending confirmation). Accounts using a seed phrase or hardware wallet are not affected.
Personally, I think you really have to choose between convenience and keeping control of your own private keys. If you use a wallet with social login, don't transfer any new funds into it for now, don't rush to import it somewhere else, and definitely don't click on any DMs offering to “help you recover” your funds.
How much of what's in your wallets was created with social login? Honestly, I feel like going through and checking all of mine now. DYOR
#自托管 #钱包安全 #Keplr
Here's an opinion that might offend some people: “Logging into a wallet with one click using your Google/Apple account” essentially means handing a third party the keys to look after.
Keplr said early this morning that some accounts created using Google/Apple login had unauthorized transfers, and login has been suspended. Apparently, Web3Auth, the service behind it, suffered a security incident. The founder initially estimated that around 20% of social-login accounts were affected, but only some of those were actually accessed (estimate, pending confirmation). Accounts using a seed phrase or hardware wallet are not affected.
Personally, I think you really have to choose between convenience and keeping control of your own private keys. If you use a wallet with social login, don't transfer any new funds into it for now, don't rush to import it somewhere else, and definitely don't click on any DMs offering to “help you recover” your funds.
How much of what's in your wallets was created with social login? Honestly, I feel like going through and checking all of mine now. DYOR
#自托管 #钱包安全 #Keplr
Keplr said early this morning that some accounts created using Google/Apple login had unauthorized transfers, and login has been suspended. Apparently, Web3Auth, the service behind it, suffered a security incident. The founder initially estimated that around 20% of social-login accounts were affected, but only some of those were actually accessed (estimate, pending confirmation). Accounts using a seed phrase or hardware wallet are not affected.
Personally, I think you really have to choose between convenience and keeping control of your own private keys. If you use a wallet with social login, don't transfer any new funds into it for now, don't rush to import it somewhere else, and definitely don't click on any DMs offering to “help you recover” your funds.
How much of what's in your wallets was created with social login? Honestly, I feel like going through and checking all of mine now. DYOR
#自托管 #钱包安全 #Keplr
AAPL-0.11%
GOOGUS+1.10%
73
·
--
⚠️ Security Alert | Some Keplr social login accounts have experienced unauthorized transactions, with the issue traced to Web3Auth
Web3Auth has officially confirmed a security issue affecting its services. Some third-party platforms have been impacted, and embedded wallet services have been suspended for now. Preliminary investigations indicate that MetaMask users have not been affected so far. Further details will be announced by the official team.
Keplr Wallet also issued a statement: it has received multiple reports of unauthorized transactions involving accounts created through Google or Apple login. The issue has been reported to the Web3Auth team, and both parties are investigating together.
See which of these three account types applies to you:
1️⃣ Keplr accounts created with a recovery phrase: preliminarily assessed as unaffected
2️⃣ Hardware wallet accounts: unaffected
3️⃣ Accounts created with Google/Apple social login: may be affected; check your account immediately
Urgent advice for affected users:
▪ Check your asset balances and transaction authorization history immediately, and revoke any unfamiliar contract approvals
▪ Transfer your assets as soon as possible to a newly created recovery-phrase wallet or a hardware wallet
▪ Follow announcements only through official channels. Never click “customer support recovery links” sent via direct message
▪ Never enter your recovery phrase or social account verification code on any webpage
The underlying issue is worth reflecting on: social login lowers the barrier to Web3, but actual control of the keys rests with third-party infrastructure. When an intermediary has a problem, users have almost no safety net. Convenience and security have always involved a trade-off.
For holding significant assets long term, a hardware wallet remains the safest choice. Remember the old saying: Not your keys, not your coins.
#Web3安全 #Keplr #WalletSecurity
⚠️ Security Alert | Some Keplr social login accounts have experienced unauthorized transactions, with the issue traced to Web3Auth
Web3Auth has officially confirmed a security issue affecting its services. Some third-party platforms have been impacted, and embedded wallet services have been suspended for now. Preliminary investigations indicate that MetaMask users have not been affected so far. Further details will be announced by the official team.
Keplr Wallet also issued a statement: it has received multiple reports of unauthorized transactions involving accounts created through Google or Apple login. The issue has been reported to the Web3Auth team, and both parties are investigating together.
See which of these three account types applies to you:
1️⃣ Keplr accounts created with a recovery phrase: preliminarily assessed as unaffected
2️⃣ Hardware wallet accounts: unaffected
3️⃣ Accounts created with Google/Apple social login: may be affected; check your account immediately
Urgent advice for affected users:
▪ Check your asset balances and transaction authorization history immediately, and revoke any unfamiliar contract approvals
▪ Transfer your assets as soon as possible to a newly created recovery-phrase wallet or a hardware wallet
▪ Follow announcements only through official channels. Never click “customer support recovery links” sent via direct message
▪ Never enter your recovery phrase or social account verification code on any webpage
The underlying issue is worth reflecting on: social login lowers the barrier to Web3, but actual control of the keys rests with third-party infrastructure. When an intermediary has a problem, users have almost no safety net. Convenience and security have always involved a trade-off.
For holding significant assets long term, a hardware wallet remains the safest choice. Remember the old saying: Not your keys, not your coins.
#Web3安全 #Keplr #WalletSecurity
Web3Auth has officially confirmed a security issue affecting its services. Some third-party platforms have been impacted, and embedded wallet services have been suspended for now. Preliminary investigations indicate that MetaMask users have not been affected so far. Further details will be announced by the official team.
Keplr Wallet also issued a statement: it has received multiple reports of unauthorized transactions involving accounts created through Google or Apple login. The issue has been reported to the Web3Auth team, and both parties are investigating together.
See which of these three account types applies to you:
1️⃣ Keplr accounts created with a recovery phrase: preliminarily assessed as unaffected
2️⃣ Hardware wallet accounts: unaffected
3️⃣ Accounts created with Google/Apple social login: may be affected; check your account immediately
Urgent advice for affected users:
▪ Check your asset balances and transaction authorization history immediately, and revoke any unfamiliar contract approvals
▪ Transfer your assets as soon as possible to a newly created recovery-phrase wallet or a hardware wallet
▪ Follow announcements only through official channels. Never click “customer support recovery links” sent via direct message
▪ Never enter your recovery phrase or social account verification code on any webpage
The underlying issue is worth reflecting on: social login lowers the barrier to Web3, but actual control of the keys rests with third-party infrastructure. When an intermediary has a problem, users have almost no safety net. Convenience and security have always involved a trade-off.
For holding significant assets long term, a hardware wallet remains the safest choice. Remember the old saying: Not your keys, not your coins.
#Web3安全 #Keplr #WalletSecurity
·
--
【Security Alert】Web3Auth has suspended its embedded wallet service due to a security issue, and unauthorized transactions have been reported on some Keplr accounts using social login.
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth
【Security Alert】Web3Auth has suspended its embedded wallet service due to a security issue, and unauthorized transactions have been reported on some Keplr accounts using social login.
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth

【Security Alert】Unauthorized transactions have been reported on some Keplr Wallet accounts using social login. The source of the risk points to Web3Auth, a provider of embedded wallet infrastructure.
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
【Security Alert】Unauthorized transactions have been reported on some Keplr Wallet accounts using social login. The source of the risk points to Web3Auth, a provider of embedded wallet infrastructure.
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinanceReopensWithdrawalsForHYPE&APT
1,788 views
86 Discussing
2
#SouthKoreaDraftLawTargets15To20%ShareholderCap
5,531 views
99 Discussing
3
#KeplrAdvisesSocialLoginUsersToTransferAssets
10,112 views
207 Discussing
4
#TetherPlans€28.8MForJuventusCapitalIncrease
5,671 views
163 Discussing
5
#JobsReportRaisesHikeOdds
684,993 views
4,046 Discussing
6
#CPITestsDecemberRateOutlook
246,284 views
1,615 Discussing
7
#US Data Center Rules May Constrain AI Expansion
98,671 views
251 Discussing
8
#ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets
6,133 views
84 Discussing
9
#WillAnthropicListOnTime
220,827 views
1,737 Discussing
10
#WillUS-IranTensionsBoostSafe-HavenDemand?
122,727 views
765 Discussing