

#securityalert
securityalert
Просмотров: 535,342
1,372 обсуждают
Популярные
Новые

🚨 $PARTI DIPS ON MAJOR EXCHANGE SECURITY ALERT 🚨
📉 The platform’s surprise audit sparked a swift 1% pullback across Bitcoin and top alts, shaking short‑term sentiment. 📊 Volume thinned as traders stepped back, waiting for the next move. 🦈 Smart‑money eyes the dip as a potential liquidity sweep, but the underlying risk flag stays lit. ⚡ Keep an eye on order‑flow spikes; a clean rebound could flip the narrative once transparency clears.
💬 How are you positioning your bids amid the heightened caution? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PARTI #SecurityAlert #Crypto #RiskManagement
🔥 💎
1
🚨 $PARTI UNDER FIRE: SECURITY ALERT MAY TRIGGER QUICK REBOUND OR DIP 🟢
🔍 The alarm just rang on a top‑tier exchange, and smart‑money eyes are already scanning the order book. A security flag can ignite a liquidity sweep, but Binance’s rapid response could soak up panic. 📊
⚡ Volume is spiking on the 15‑minute chart while RSI edges toward oversold, hinting at a bounce if buyers step in fast. Keep watch on the next wave of sell orders as the market decides its next move. 🤔 Do you see a deeper dip or a swift rebound?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PARTI #ShortTerm #SecurityAlert #Crypto
🔥 💎
1

·
--
🚨 $POL UNDER PRESSURE AFTER POSSIBLE SECURITY COMPROMISE! 🔴
The community is buzzing as reports surface that the front‑end of Polymarket may have been compromised, with assets reportedly exiting without owner consent. 📊 The sudden outflow hints at a coordinated liquidity sweep, a classic move when smart money tests the depth of a platform.
If the breach holds, we could see a sharp sell‑off as risk‑averse holders scramble to protect capital. 🦈 Keep an eye on order‑book imbalances and volume spikes on a top‑tier exchange; a rapid dip could set the stage for a short‑term correction. 💬 How are you adjusting your exposure to $POL in light of this potential breach? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #POL #SecurityAlert #CryptoRisk #MarketWatch
🛡️ 🚀
14

🚨 $BTC USERS ALERT: MALICIOUS LEDGER IMPLANTS STOLEN $2.7M IN SINGAPORE 💥
📊 Singapore police uncovered hardware wallets with covert implants that siphon recovery phrases, costing investors S$3.5 million. The breach underscores a classic supply‑chain vulnerability where malicious actors infiltrate retail channels, turning trusted devices into silent liquidity hunters. 🦈
💡 To safeguard assets, source wallets directly from the manufacturer or an authorized reseller, run Ledger’s authenticity checks, and never expose your online. If you suspect tampering, halt usage and migrate funds to a fresh, verified device. 🤔 What extra steps are you taking to verify your hardware wallet’s integrity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #HardwareWallet #CryptoSafety
🔥 🦈
3
·
--
🚨 $INJ CHAIN HALTED AFTER $4.9M EXPLOIT AS GOVERNANCE TRANSPARENCY COMES UNDER FIRE ⚠️
Injective suffered a sudden four-hour network halt after an attacker manipulated a defunct oracle mechanism, draining $4.9M into Ethereum across 299 synthetic binary options markets. 🚨 The exploit leveraged a double-compensation refund loophole before transferring 1,980 ETH into a fresh wallet.
While smart money monitors that fresh address, the bigger structural concern lies in how the situation was managed. 🔍 The chain was paused and privately patched without public governance transparency, all while official channels continued posting routine marketing updates during the outage. 📉
Trust in protocol infrastructure takes months to build but seconds to erode under silent halts. 💬 Does this communication failure change your long-term outlook on $INJ , or will buyers step in to bid the dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #INJ #SecurityAlert #DeFi #Crypto
🚨 👁️
14

🚨 $ETH SMART CONTRACT EXPLOIT DRAINED BY ACCESS CONTROL VULNERABILITY! 💣
Smart contract risks strike again as an access control flaw in the GebProxyActions contract allowed an attacker to siphon nearly 6 $ETH in a silent hit. 🛡️ While 5.94 $ETH might seem modest to whales, loose smart contract logic can easily wipe out an unmindful wallet in seconds.
If you have ever interacted with GebProxyActions, treat this as an immediate priority and revoke your token allowances right now. 🔒 In a market where liquidity flows fast, protecting your capital off-charts is just as critical as managing your stops on the tape. 💬 Have you checked and cleaned up your active smart contract approvals this month? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityAlert #SmartContracts #CryptoSecurity
🛡️ 👁️
6
·
--
🚨 $INIT UNDER FIRE FROM DAY‑0 VULNERABILITY – WHALE MOVES REVEALED! 🦈
📊 The Day‑0 exploit in Initia's MoveVM opened a minting backdoor, letting a whale mint fresh $INIT and siphon $2.7M across AUSD, ETH, and USDC. The cross‑chain trail shows a classic liquidity sweep, where the attacker hit the pause button just before the net outflow hit the radar.
🦈 Smart‑money watchers see this as a red flag for the ecosystem – any lingering exposure could trigger further drains, and the pause may mask hidden order blocks waiting to be reclaimed. Keep an eye on the re‑entry zones once the chain reopens; a fresh buying surge could spin the price into a short‑term rebound. 💬 Will you stay on the sidelines or position for a post‑pause bounce? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #INIT #SecurityAlert #WhaleAction #Crypto
🔥 💎
7
🚨 $INIT MAINNET SUSPENDED – SECURITY INCIDENT SHAKES THE NETWORK 🛑
📊 The abrupt halt of Initia’s L1 and Rollup signals a serious breach, forcing validators and a top‑tier exchange to pull the plug while forensic teams scramble. ⚡ Momentum has dried up as traders dodge unofficial links and rumor mills, turning the market into a cautious waiting room.
💡 With the core infrastructure offline, smart money is likely reallocating capital to more stable layers until verified updates land. 💬 How are you adjusting exposure while the dust settles? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #INIT #SecurityAlert #NetworkSuspension #Crypto
🔥 💎
10

🚨 $INIT MAINNET SUSPENDED AFTER SECURITY INCIDENT ⚠️
📊 The abrupt halt of Initia’s L1 and Rollup signals a coordinated liquidity sweep, forcing validators to retreat from the order book. 🦈 Smart‑money nodes are now reassessing exposure as the security breach reshapes the risk matrix. 🔍 Teams are engaging top‑tier exchanges and custodians to quarantine potential fallout, meaning market depth may thin dramatically until verification clears.
📌 Vigilance is paramount: avoid unofficial links, monitor official channels for verified updates, and tighten position sizing until the incident scope is disclosed. 🤔 How are you adjusting your exposure to $INIT in light of this systemic pause? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #INIT #SecurityAlert #Crypto #Incident
🛡️ 🔥
2

·
--
🚨 $ETH SOL-LIVE BACKDOOR ALERT: MALICIOUS TERMINAL LURKS IN GITHUB ⚡
SlowMist just flagged a GitHub repo masquerading as a Solidity interview sandbox, but it hides a three‑module data‑stealing backdoor. Once the custom terminal config is launched, it can siphon browser logins, wallet extensions, and even macOS keychain files. 📊
The chain activates on macOS and Linux, while Windows remains unconfirmed due to quoting quirks. Attackers can also scan local files, run remote scripts, and monitor clipboard content, giving them full interactive shell access. ⚡
💬 Have you audited your dev dependencies today or are you still trusting unknown repos? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityAlert #DevSafety #Crypto
🛡️ 🔥
6

·
--
🚨 $ETH SOL‑LIVE BACKDOOR ALERT 🦈
📊 A GitHub repo named “sol‑live” masquerades as a Solidity interview project, yet hides a tri‑module data‑stealing payload. It can siphon browser login databases, crypto wallet extension storage, and even macOS keychain files before scanning and uploading local data. ⚡ Execution hinges on users launching a custom terminal configuration, granting remote shell access and clipboard monitoring.
🦈 Smart‑money developers must treat every third‑party script as a potential liquidity trap. Inspect terminal parameters, isolate compromised devices, and migrate assets through trusted hardware. 📌 How rigorously are you vetting external code before execution? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityAlert #DevSafety #SmartMoney #Crypto
🔥 💎
1


·
--
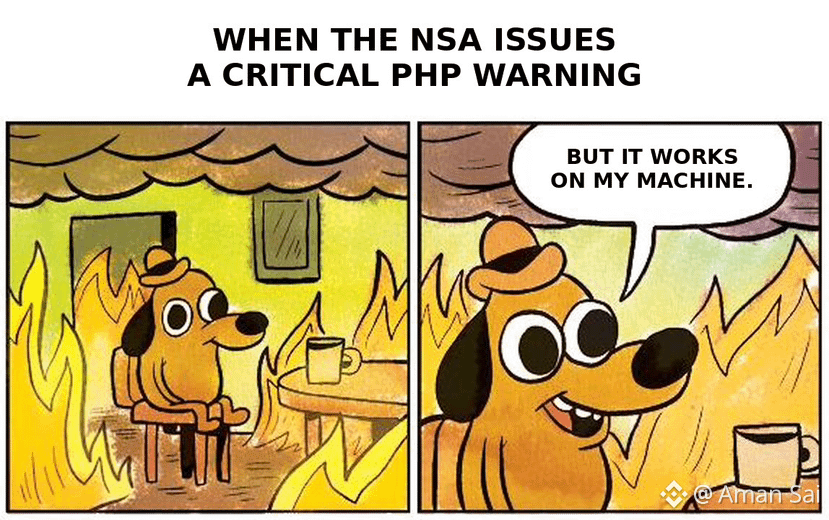
🚨 URGENT SECURITY ALERT: PHP2Shell
The NSA has issued an immediate warning to organizations using PHP after two critical vulnerabilities were discovered in the widely used programming language.
These flaws are rated CVSS 9.2/10 (Critical) and can allow unauthenticated remote code execution meaning an attacker may be able to execute malicious commands on a vulnerable server without having to log in first. (PHP)
Why is this serious? 👇
🔴 PHP runs on a huge portion of the web and is commonly used for websites, web applications and server-side systems.
🔴 The vulnerabilities, collectively referred to as PHP2Shell, can potentially give attackers access to systems behind vulnerable PHP web services.
🔴 The risk is particularly serious for internet-facing servers, where attackers may be able to exploit the vulnerability remotely.
🔴 The NSA is advising organizations to identify vulnerable PHP systems and prioritize the official security patches immediately. If a system cannot be updated promptly, the NSA recommends taking it offline until it can be fully mitigated.
✅ What organizations should do now:
• Check every internet-facing system running PHP
• Identify the PHP version in use
• Install the latest security release
• Update related software/packages from vendors
• Increase monitoring and logging for suspicious activity
• Review systems for signs of compromise
• Isolate or take vulnerable systems offline if they cannot be patched
PHP has released security updates including PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, fixing the two critical vulnerabilities. (PHP)
⚠️ This is not a “patch later” situation.
If you operate a PHP-based website, server, exchange, application or business infrastructure, check it now.
The safest move is simple:
Identify → Patch → Verify → Monitor.
One vulnerable server can become the entry point to an entire organization.
#PHP #CyberSecurity #PHP2Shell #Hacking #InfoSec #CyberAttack #WebSecurity #Technology #SecurityAlert
2
1.2k

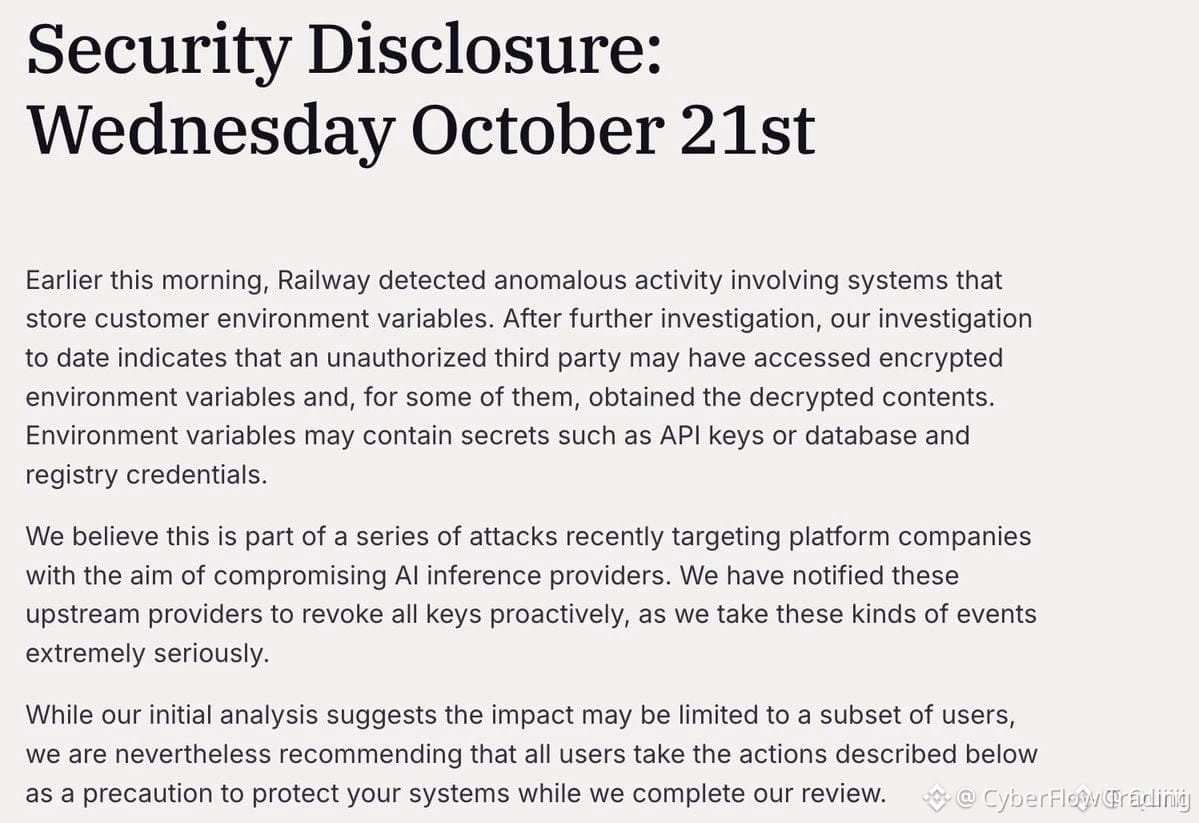
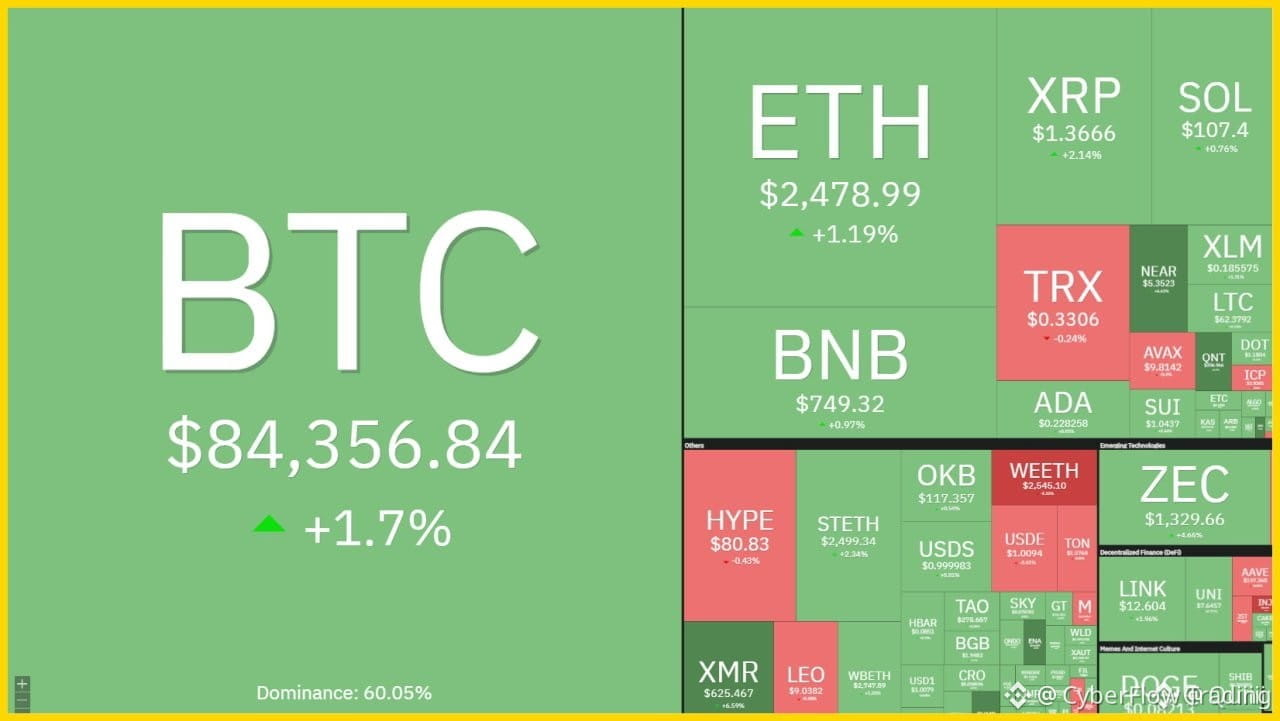
🚨 $ETH AT RISK FROM RAILWAY CLOUD BREACH! 🛑
📊 Railway’s cloud slip exposed API keys and DB credentials for several projects. While heavyweights like $AAVE , Chainlink and LayerZero report clean bills, Swell’s admin keys hint at a 2,500 ETH exposure that’s still unconfirmed. 🦈 Smart‑money eyes are likely tightening positions and scanning for any liquidity sweep before the dust settles. ⚡ Projects that have already rotated keys (infiniFi, Monad) show the first line of defense, but the timing overlap fuels speculation.
💬 How will you hedge your exposure to the potential fallout? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityAlert #CloudBreach #CryptoRisk
🔥 💎
3

·
--
🚨 $ALT UNDER SECURITY ALERT: POTENTIAL DIP OR LONG‑TERM TRUST BOOST? ⚡
🦈 CZ’s fresh warning about unpatched PHP flaws is sending a ripple through the smart‑money flow. The immediate fear factor could trigger a short‑term sell‑off as risk‑averse players scramble to protect credentials. 📊
🔍 Yet the same alert forces exchanges and projects to harden their security stack, a classic institutional confidence driver. Expect the liquidity pool to re‑price once the dust settles, giving long‑term holders a cleaner demand zone. 💡
💬 Do you think the market will bite the dip or settle into a higher trust premium? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ALT #SecurityAlert #MarketSentiment
🔥 💎
⚡ $ETH ALERT: GOVERNMENT PHP VULNERABILITY COULD RATTLE INFRASTRUCTURE 🚨
📊 The White House confirmed a critical PHP flaw surfaced on Oct 16, prompting federal agencies to scramble for a patch. Network operators and system labs are on high alert, racing to shield government and critical infrastructure from exploitation. 🦈 Smart‑money eyes are already gauging spill‑over risk to crypto nodes that rely on similar stacks.
⚡ A swift mitigation rollout could spark short‑term volatility across exchanges as traders reassess exposure. Keep an eye on liquidity sweeps and potential sell pressure on related assets. 💬 How are you adjusting your positions amid this looming patch race? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityAlert #CryptoRisk #Infrastructure
🔥 🦈
11
·
--
سلسلة كن ذكيا مع بينانس
3 إعدادات تحمي أموالك 🛡️
قائمة السحب البيضاء: لا يُسمح بالسحب إلا إلى عناوين أضفتها مسبقًا.
إدارة الأجهزة: راجع الأجهزة المتصلة بحسابك واحذف ما لا تعرفه.
مفاتيح API: إذا استخدمت بوتات تداول، عطّل صلاحية السحب وقيّد المفتاح بعنوان IP محدد.
❓ متى آخر مرة راجعت أجهزة حسابك؟
#API #SecurityAlert #BinanceAcademy
95
·
--
🚨 $FOMO MALWARE CONFUSION ALERT! 🦈
📊 SlowMist’s CISO just cleared the official $FOMO iOS app, pinning the “malware” to a rogue clone named FOMOPeek. 📌 The fake version prowled the App Store from Sep 9‑17, siphoning assets before disappearing. ⚡ Smart‑money eyes are now scanning for any lingering exposure, while genuine holders can breathe easier—provided they stay vigilant.
💡 This episode underscores the relentless liquidity sweep tactics of opportunistic actors; a single compromised download can trigger a cascade of sell pressure. 👇 How are you safeguarding your $FOMO holdings against hidden code threats?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #FOMO #SecurityAlert #Crypto #Malware
🔥 💎
5

·
--
🚨 Ledger breach hits EU as user finds tampered device from major retailer. AI uncovers a massive XRP supply bug—reported as 18 trillion tokens—but bounty payout is only $250K. This highlights ongoing security risks in hardware wallets and potential tokenomics concerns. Market may react to trust erosion in custody solutions. How will XRP holders respond to rising wallet vulnerabilities? #SecurityAlert
$XRP #TradingSignal #CryptoAnalysis
$XRP #TradingSignal #CryptoAnalysis
20
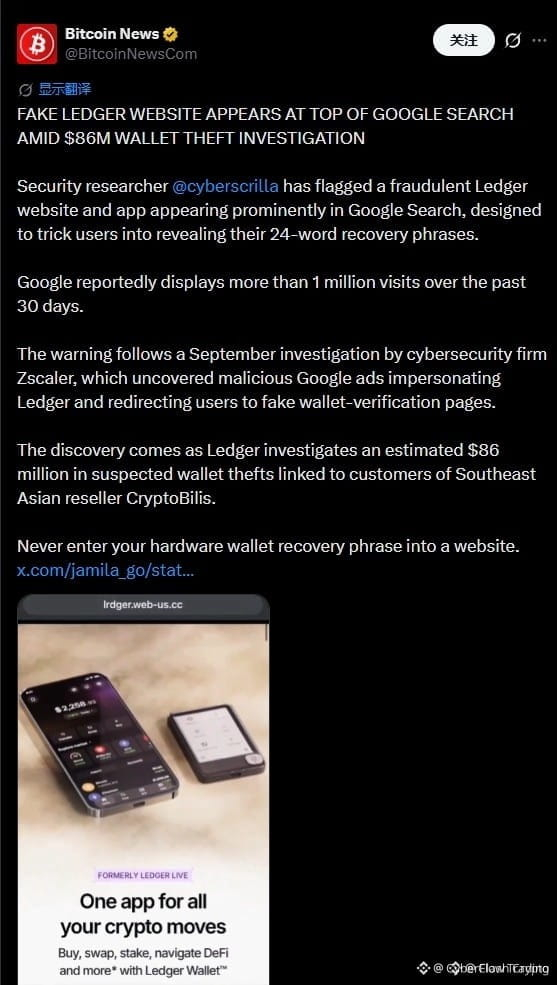
🚨 MAJOR SEARCH ENGINES THREATEN WALLET SECURITY AS PHISHING SITES TARGET $BTC HOLDERS! ⚠️
A massive phishing vector is currently targeting hardware wallet users through top search engine ad placements, racking up over 1 million visits this past month alone. 🔍 Sophisticated bad actors are actively intercepting unwary users and draining funds by capturing 24-word recovery credentials.
With over 86 million dollars already drained in connected investigations, hardware security remains useless if you expose your critical credentials on fake verification portals. 🛡️ Protect your cold storage offline, verify every web domain twice, and never type your secret phrases anywhere online. 💬 Are you double-checking your hardware app bookmarks before accessing your funds? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #Crypto #Web3 #CryptoSecurity
⚡ 🛡️
10
🚨 PHISHING ATTACK IMPERSONATING HARDWARE WALLETS DRAINS MILLIONS AMID $BTC MARKET VOLATILITY! ⚠️
Security researchers just uncovered a massive fake search trap targeting crypto holders, pulling in over one million visits this month alone. Phishing campaigns are deploying malicious wallet sites to capture recovery keys, linked to an estimated 86 million dollar loss across affected users. 📊 🚨
In a market where cold storage is your ultimate edge, falling for sponsored search redirects is a silent capital killer. Smart money locks down security and protects their treasury long before chasing the next momentum breakout. 💡 🔒
💬 Are you double-checking your hardware wallet bookmarks before approving connections? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #SecurityAlert #Crypto
🛡️ 👁️
16
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#FedWatch
Просмотров: 16.3M
39,405 обсуждают
2
#EarningsSeason
Просмотров: 6.4M
32,103 обсуждают
3
#USMidtermElections
Просмотров: 43,486
630 обсуждают
4
#BitcoinDropsBelow$80K
Просмотров: 29,346
120 обсуждают
5
#BoEOpensConsultationOnTokenizedCollateralForClearing
Просмотров: 636
30 обсуждают
6
#BrazilCryptoExchangesMustApplyForLicensesByFriday
Просмотров: 33,332
506 обсуждают
7
#ICEPartnersWithTradeXYZToBringPerpetualContractsToUS
Просмотров: 708
19 обсуждают
8
#SolidusLabsReportsSuspected$170MSpoofingOnHyperliquidOilContracts
Просмотров: 1,643
28 обсуждают
9
#StanDruckenmillerBecomesInvestorInTradeXYZ
Просмотров: 25,010
439 обсуждают
10
#RussiaProposedNonCustodialWalletLimitsExcludeIntlSettlements
Просмотров: 2,146
41 обсуждают