

#movevm
movevm
Просмотров: 8,953
34 обсуждают
Популярные
Новые


·
--
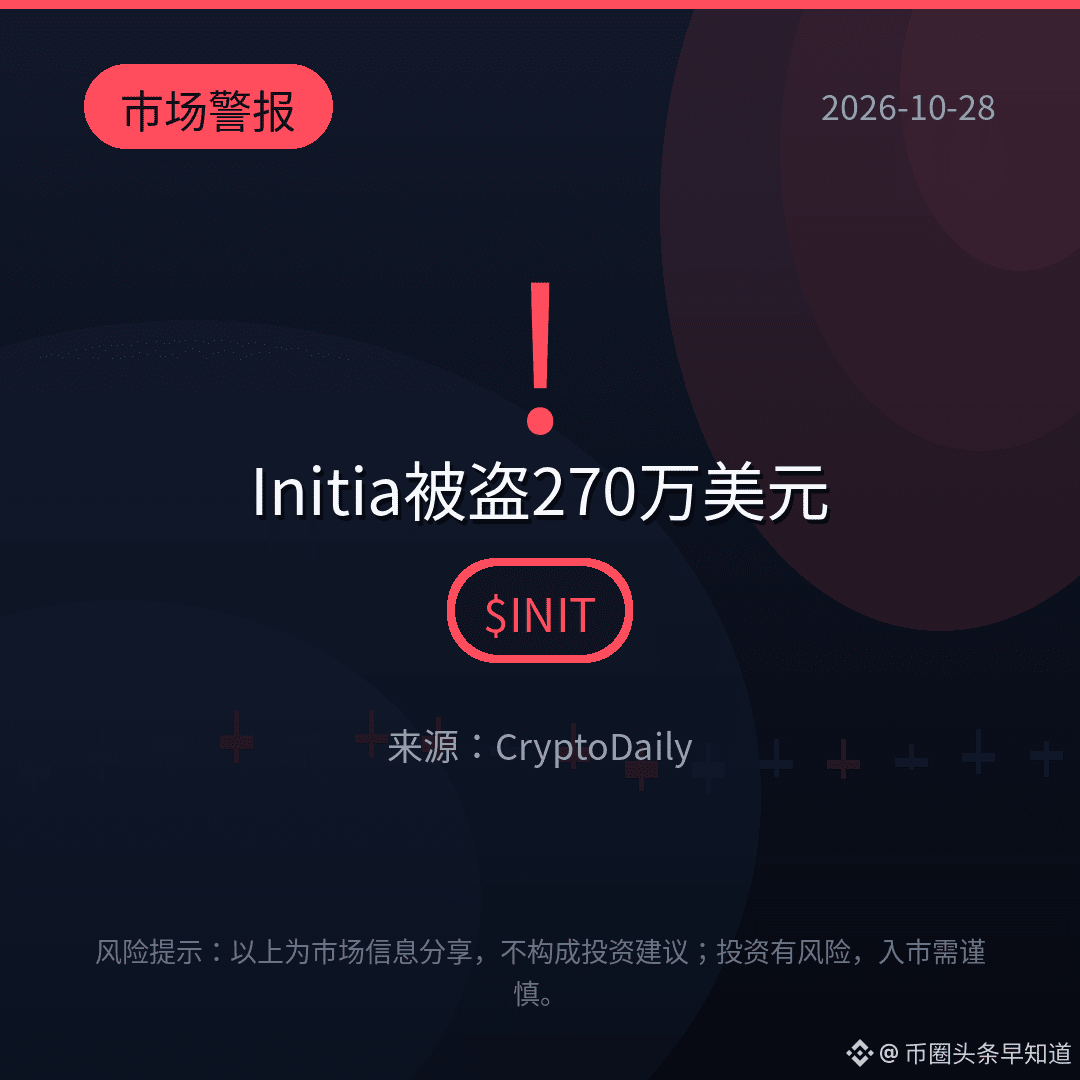
一条缓存漏洞,让 Initia 在几分钟内损失了约 270 万美元。攻击者没增发 INIT,也没改动代币总供应量,而是伪造了 MoveVM 状态,给自己记入无实际支撑的 WETH、iUSD 和 USDC——账面数字凭空出现,链上资产却被真实转走。
具体路径很清楚:10 月 23 日 22:59(UTC+8),攻击者利用 MoveVM 脚本缓存漏洞绕过安全检查。网络暂停前,约 105 枚 WETH 和 140 万枚 AUSD0 经 LayerZero 转出,另有约 108 万枚 USDC 经 Noble 和 CCTP 转出,随后统一兑换成 1135.52 枚 ETH,目前躺在一个以太坊地址上。
这件事值得注意的地方在于,总供应量没变、INIT 没被增发,但被盗资产是实打实的。L1 和 Rollup 至今仍处于暂停状态,安全修复预计数天内完成并通过审计,资产追回工作也在与安全合作伙伴推进。对跨链桥和 MoveVM 生态来说,缓存层绕过检查这个口子一旦被验证,后续复盘报告里的修复细节会比损失金额更有参考价值。$BTC #Initia #MoveVM
$ETH $USDC #以太坊

·
--
Initia 的 MoveVM 出了一个能被伪造状态的漏洞,攻击者从里面提走了约 270 万美元。
事情发生在 10 月 23 日 22:59(UTC+8)。按 Initia 披露的说法,攻击者利用的是 MoveVM 脚本缓存漏洞,绕过安全检查后伪造了 MoveVM 状态,给自己记入了没有实际支撑的 WETH、iUSD 和 USDC。难点在于这不是直接增发,而是让状态看起来像真的,安全检查被绕过去了。
链上资金被转出约 270 万美元,但 Initia 强调相关代币总供应量没变,$INIT 也没有被增发。换句话说,账面被做了手脚,代币总量本身没膨胀。对持有者来说,供应量数据干净不代表损失不存在,被盗资金的实际流向和后续处置才是接下来要看的。
MoveVM 一向以类型安全和资源模型为卖点,这次出问题的位置是脚本缓存,属于执行层实现细节。跨链和模块化项目越来越多地把 MoveVM 当执行环境选项,缓存层的校验逻辑一旦有缝,伪造状态就能绕过本应生效的检查。这条线索值得做 Move 生态的团队拿去对照自查。
$USDC #Initia #MoveVM #安全事件

·
--
1、背景
近期,安全机构 Hexens 披露其发现 Aptos 区块链 Move 虚拟机存在一项严重漏洞,相关问题在报告后很快完成修复,未造成链上资金损失。根据公开信息,漏洞核心与缓存处理缺陷有关,可能引发类型混淆问题。对以 Move 为核心执行环境的 Aptos 来说,这类底层缺陷的敏感度极高,因为它影响的不是单一协议,而是整个执行层的可信边界。⚠️
2、漏洞分析
从技术角度看,Move 一直以资源安全和权限控制著称,因此这次事件的关键不在于普通合约逻辑错误,而在于虚拟机实现层面的异常。如果缓存机制在特定条件下错误复用或识别类型,就可能让攻击者绕过原有约束,获得不应拥有的高权限角色。理论上,这意味着攻击面可从单个应用扩大到稳定币铸造、跨链桥验证、DeFi 管理模块等关键基础设施。
Hexens 还提到,研究团队以较低成本搭建接近主网的模拟环境,并多次验证了利用路径,说明该问题并非纸面风险,而是具备一定现实可操作性。不过,Aptos 官方强调真实环境中可利用性较低,这也反映出“理论高危”与“实战门槛”之间存在差异。客观看,这类分歧在安全事件中并不罕见,重点仍在于漏洞已被及时封堵。
3、市场与生态影响
这起事件对 Aptos 生态释放了两层信号。第一,底层公链安全不能只看语言设计优势,虚拟机实现、缓存机制、执行优化同样可能成为系统性风险源。第二,漏洞赏金、白帽披露和快速修复机制正在成为公链竞争力的重要组成部分。此次未出现资金损失,本质上说明生态在应急响应上是有效的。🛡️
从市场层面看,短线情绪可能受到“严重漏洞”字眼扰动,但中长期更值得关注的是修复效率、透明度和后续审计动作。如果官方能够进一步说明补丁范围、验证流程及类似风险的预防措施,反而有助于增强外界对 Aptos 技术治理能力的信心。
4、结论
整体来看,这不是一起已经造成损失的黑天鹅事件,而是一次暴露底层执行风险、同时也检验项目安全响应能力的案例。当前阶段,投资者更应关注 Aptos 后续是否加强虚拟机审计、权限隔离和关键基础设施联防。对整个行业而言,公链安全的核心已不只是“代码是否能跑”,更是“系统能否在高压场景下及时发现并化解风险”。📌
#Aptos #MoveVM #crypto
140

⚔️ ĐỐI ĐẦU RỰC LỬA: $SUI vs $APT — Ai sẽ là vua Move VM chu kỳ này?Cùng xuất thân từ dự án Diem huyền thoại của Meta và sử dụng ngôn ngữ Move tối tân, cuộc chiến giữa $SUI và $APT luôn là tâm điểm chú ý của dòng tiền Layer 1 thế hệ mới.
Đặt lên bàn cân số liệu thực tế phiên hôm nay:
• Thanh khoản Spot 24h: $SUI áp đảo hoàn toàn với 77.57M USDT, gấp hơn 6.5 lần so với $APT (chỉ đạt 11.78M USDT).
• Khối lượng Phái sinh & OI: Open Interest của $SUI nén chặt ở mức 87.95M USDT; trong khi $APT chỉ đạt 15.73M USDT.
• Dấu chân Top Trader: Tài khoản tay to trên Binance Futures của $APT đang âm thầm gom Long cực mạnh với tỷ lệ Long/Short lên tới 2.32 (69.87% Long), trong khi $SUI duy trì tỷ lệ 1.75 (63.62% Long).
• Định giá & Dư địa: $SUI (0.88 USDT, MCap ~3.1B, FDV ~8.8B USD) vs $APT (0.62 USDT, MCap ~310M, FDV ~620M USD).
Góc nhìn dòng tiền:
$SUI đang chiếm trọn sự chú ý và thanh khoản của đám đông nhờ hệ sinh thái DeFi sôi động, nhưng mức FDV lớn và lịch unlock liên tục là bài toán cần thận trọng. Ngược lại, $APT dù thanh khoản bán lẻ trầm lắng hơn nhưng với vốn hóa nhẹ và tỷ lệ Long áp đảo của Smart Money, một nhịp nén vol ở phiên London hoàn toàn có thể kích hoạt sóng hồi bất ngờ.
Nếu chỉ được chọn ALL-IN một bên từ giờ đến hết chu kỳ, anh em chọn $SUI hay $APT?
$SUI $APT #CryptoDuel #MoveVM #Altcoins #BinanceSquare
⚔️ ĐỐI ĐẦU RỰC LỬA: $SUI vs $APT — Ai sẽ là vua Move VM chu kỳ này?
Cùng xuất thân từ dự án Diem huyền thoại của Meta và sử dụng ngôn ngữ Move tối tân, cuộc chiến giữa $SUI và $APT luôn là tâm điểm chú ý của dòng tiền Layer 1 thế hệ mới.
Đặt lên bàn cân số liệu thực tế phiên hôm nay:
• Thanh khoản Spot 24h: $SUI áp đảo hoàn toàn với 77.57M USDT, gấp hơn 6.5 lần so với $APT (chỉ đạt 11.78M USDT).
• Khối lượng Phái sinh & OI: Open Interest của $SUI nén chặt ở mức 87.95M USDT; trong khi $APT chỉ đạt 15.73M USDT.
• Dấu chân Top Trader: Tài khoản tay to trên Binance Futures của $APT đang âm thầm gom Long cực mạnh với tỷ lệ Long/Short lên tới 2.32 (69.87% Long), trong khi $SUI duy trì tỷ lệ 1.75 (63.62% Long).
• Định giá & Dư địa: $SUI (0.88 USDT, MCap ~3.1B, FDV ~8.8B USD) vs $APT (0.62 USDT, MCap ~310M, FDV ~620M USD).
Góc nhìn dòng tiền:
$SUI đang chiếm trọn sự chú ý và thanh khoản của đám đông nhờ hệ sinh thái DeFi sôi động, nhưng mức FDV lớn và lịch unlock liên tục là bài toán cần thận trọng. Ngược lại, $APT dù thanh khoản bán lẻ trầm lắng hơn nhưng với vốn hóa nhẹ và tỷ lệ Long áp đảo của Smart Money, một nhịp nén vol ở phiên London hoàn toàn có thể kích hoạt sóng hồi bất ngờ.
Nếu chỉ được chọn ALL-IN một bên từ giờ đến hết chu kỳ, anh em chọn $SUI hay $APT ?
$SUI $APT #CryptoDuel #MoveVM #Altcoins #BinanceSquare
275
·
--
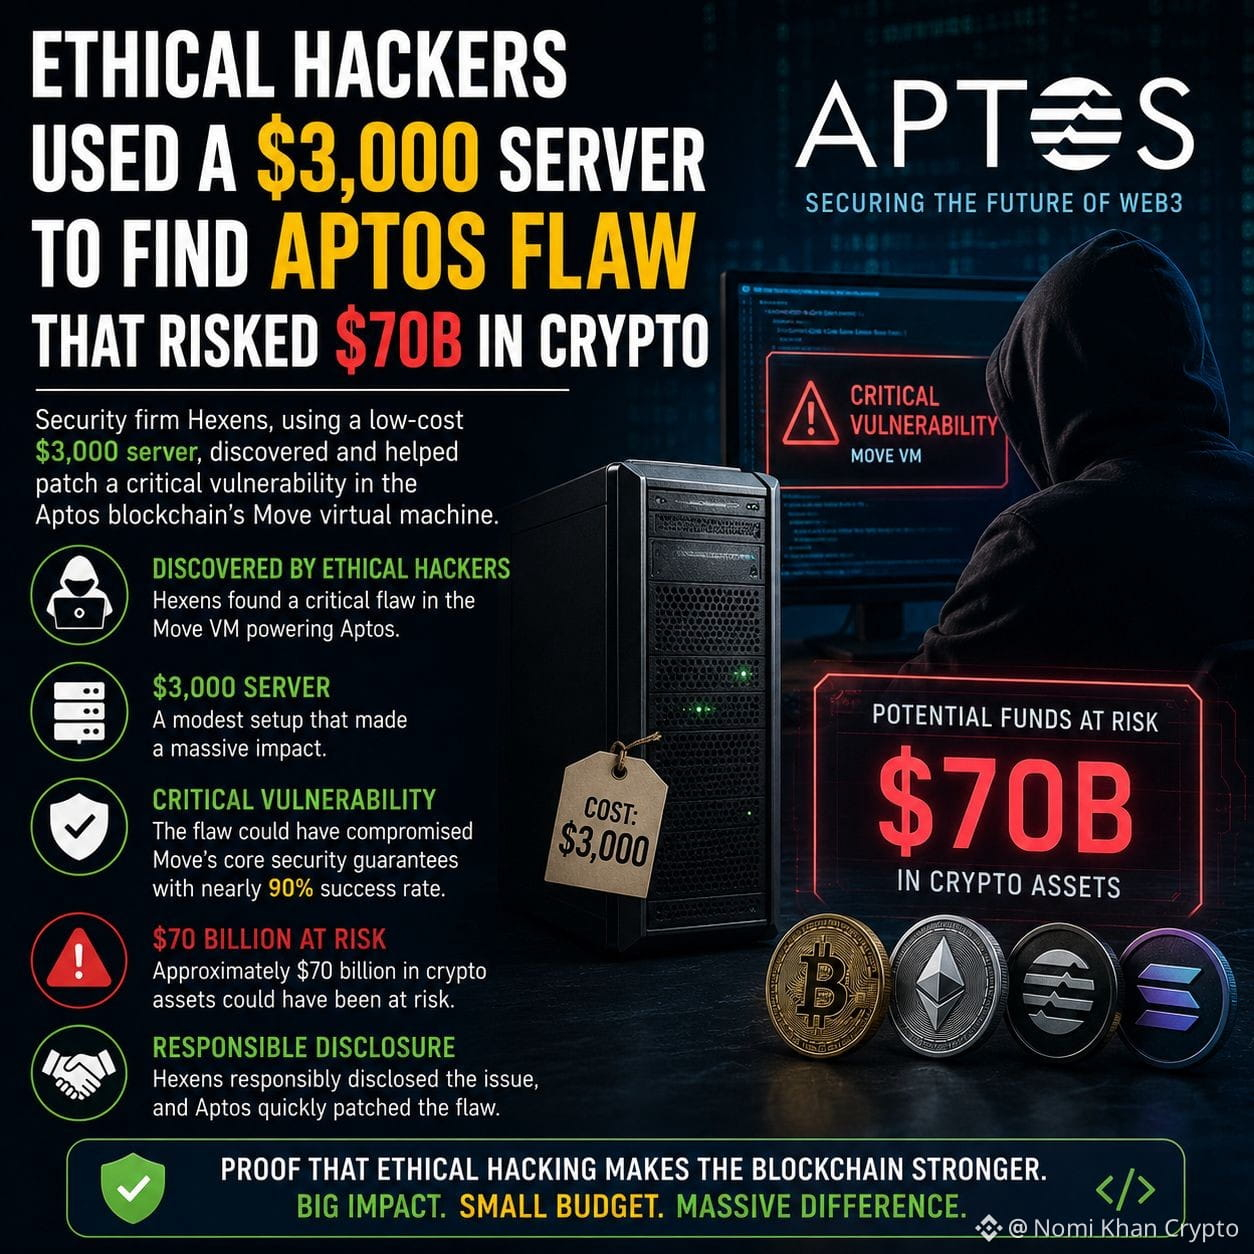
🚨 Ethical Hackers Prevented a Potential $70B Crypto Disaster
A team of ethical hackers from Hexens uncovered a critical vulnerability in the Aptos blockchain's Move Virtual Machine using nothing more than a $3,000 server.
$APT
{spot}(APTUSDT)
$DL
{alpha}(560xcd806d0eb9465020994c9e977cbe34fe430172ae)
The flaw reportedly had a nearly 90% success rate and could have undermined the core security guarantees of the Move programming language, potentially placing around $70 billion in crypto assets at risk.
Working responsibly, the researchers disclosed the issue to the Aptos team, allowing the vulnerability to be patched before it could be exploited.
This incident highlights the vital role of ethical hackers and proactive security audits in protecting the blockchain ecosystem.
#Aptos #CryptoSecurity #blockchain #EthicalHacking #MoveVM
🚨 Ethical Hackers Prevented a Potential $70B Crypto Disaster
A team of ethical hackers from Hexens uncovered a critical vulnerability in the Aptos blockchain's Move Virtual Machine using nothing more than a $3,000 server.
$APT
$DL
The flaw reportedly had a nearly 90% success rate and could have undermined the core security guarantees of the Move programming language, potentially placing around $70 billion in crypto assets at risk.
Working responsibly, the researchers disclosed the issue to the Aptos team, allowing the vulnerability to be patched before it could be exploited.
This incident highlights the vital role of ethical hackers and proactive security audits in protecting the blockchain ecosystem.
#Aptos #CryptoSecurity #blockchain #EthicalHacking #MoveVM
165

·
--
$APT VULNERABILITY COULD RISK $700 BILLION – FIXED IN HOURS 🛡️
A critical vulnerability was discovered in Aptos Move VM in February, with a theoretical risk exposure of $700 billion across the ecosystem. The Aptos team patched the mainnet within hours, and no user funds were lost.
Hexens demonstrated a 90% attack success rate using only a $3,000 server, no validator access required. While real‑world exploitability was deemed minimal, the findings highlight how single VM flaws can cascade through bridges, stablecoins, and DeFi protocols.
Are you paying enough attention to underlying infrastructure risks in layer‑1 ecosystems?
Not financial advice. Always manage your risk.
#APT #Security #Vulnerability #MoveVM #Blockchain
🛡️
28
·
--
EthicalHackersFindAptosFlawRisking$70B
🚨 Web3 Security Alert: Ethical Hackers Save Aptos from a $70B Threat
A stark reminder of how critical white-hat hackers are to the blockchain ecosystem. A massive, business-critical vulnerability was just discovered and patched in the Aptos Network, which could have put an estimated $70 Billionin assets at risk.
Here is what went down:
🛡️ The Flaw:Ethical hackers identified a severe vulnerability lurking within the Move Virtual Machine (MoveVM)—the engine that powers Aptos's smart contracts.
•📉 The Risk:If exploited, the bug could have triggered catastrophic denial-of-service (DoS) crashes across network nodes or halted operations entirely, freezing billions in value.
💰 The Asymmetry:Shockingly, researchers noted that executing the exploit would have cost an attacker as little as $3,000
✅ The Resolution:The Aptos team moved fast to deploy a patch, successfully securing the network before malicious actors could take advantage of the loophole.
💡 The Big Takeaway
This is a textbook example of why robust bug bounty programs and continuous protocol audits aren't optional—they are foundational. Security in Web3 isn't a one-time milestone; it’s an ongoing battle. Kudos to the security researchers who caught this before disaster struck.
#CryptoSecurity #Blockchain #CyberSecurity #EthicalHacking #MoveVM
133
·
--
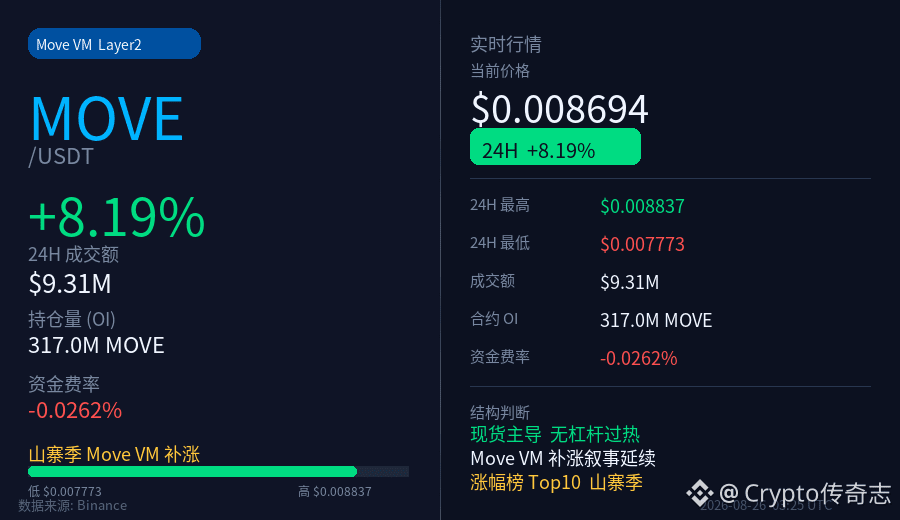
山寨季悄悄涨了个你可能没注意的币 👀
MOVE(Move VM Layer2)今天悄悄上了涨幅榜前十,+8.2%,而且结构很干净——
📌 现在在哪?
- 当前价:$0.00869
- 24H 涨幅:+8.19%
- 成交额:约 930 万 USDT
- 合约 OI:3.17 亿枚 MOVE
📌 结构怎么样?
- 资金费率 -0.026%,轻微空头补贴
- 说明这波涨是现货在推,不是合约杠杆堆上去的
- OI 没有明显异常,无追多过热信号
📌 背后在讲什么故事?
山寨季整体情绪扩散,Move VM 赛道作为下一代智能合约虚拟机叙事,这波有被资金纳入补涨序列。BNBChain Pasteur 升级带动生态情绪,整个非主流 L2/VM 层受益。
不是说一定要买,只是提醒一下:涨幅榜出现这种没什么人讨论但悄悄拉了的结构,往往是山寨季中期值得多看一眼的信号 👇
#MOVE #山寨季 #MoveVM #Layer2 #Binance广场
点击下方小卡片快速查看行情👇
1
139
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#UniswapA16zSeekDeFiExemptionFromIllinoisCryptoTax
Просмотров: 21,638
705 обсуждают
2
#HKDollarStablecoinHKDAPToLaunchOnSolana
Просмотров: 15,978
444 обсуждают
3
#$1.5BInLeveragedCryptoBetsLiquidated
Просмотров: 35,290
239 обсуждают
4
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
Просмотров: 2,365
64 обсуждают
5
#KOSPIFalls3.53%BackBelow6000
Просмотров: 59,710
1,067 обсуждают
6
#AmazonSharesFallAbout7%InPremarketTrading
Просмотров: 26,968
572 обсуждают
7
#USMidtermElections
Просмотров: 234,140
2,329 обсуждают
8
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
Просмотров: 22,451
93 обсуждают
9
#BinanceWillListPredictPREDICT
Просмотров: 88,892
1,370 обсуждают
10
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
Просмотров: 3,019
106 обсуждают