

#lazarus
lazarus
Просмотров: 446,006
113 обсуждают
Популярные
Новые
·
--
Рост
$BTC $ETH
🚨 FLASH HACK : Que s'est-il vraiment passé chez Bitget ? 🚨
Un incident de sécurité majeur vient de secouer l'écosystème crypto. Voici le point complet sur la situation 🧵👇
💥 L'Attaque en Bref
Le 24 septembre 2026, Bitget a subi une faille au niveau de son infrastructure backend. Les pirates ont falsifié des autorisations système internes pour valider de faux transferts et siphoner les portefeuilles chauds (hot wallets).
💰 Montant des Pertes : ~387,5 millions $
Des cryptos majeures ont été détournées vers plusieurs blockchains : ETH, XRP, USDT, TRX, AVAX, BNB et ZEC.
🛡️ Quel impact pour les utilisateurs ?
• ❄️ Cold Wallets : 100 % sécurisés (les portefeuilles froids n'ont pas été touchés).
• 👤 Soldes clients : Aucun impact direct sur vos comptes.
• 🛡️ Fonds de Protection : Le fonds de garantie Bitget (évalué à +460M$) couvrira l'intégralité des pertes.
🕵️ Qui est derrière le Hack ?
Selon la PDG Gracy Chen, les adresses IP et le mode opératoire pointent vers des hackers nord-coréens (groupe Lazarus). Les géants de la cybersécurité Mandiant et SlowMist sont sur le dossier.
🗓️ Calendrier de Reprise des Retraits :
✅ Faille corrigée & Trading opérationnel
📌 28 Sept. : Retraits BTC
📌 29 Sept. : Retraits ETH (Ethereum, BSC, Arbitrum, Base, OP)
📌 30 Sept. : Retraits USDT (Ethereum, BSC, Solana, Tron)
📌 02 Oct. : Autres altcoins, fiat et P2P
Restez prudents et vérifiez toujours vos sources officiellement ! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
{spot}(BTCUSDT)
{spot}(ETHUSDT)
$BTC $ETH
🚨 FLASH HACK : Que s'est-il vraiment passé chez Bitget ? 🚨
Un incident de sécurité majeur vient de secouer l'écosystème crypto. Voici le point complet sur la situation 🧵👇
💥 L'Attaque en Bref
Le 24 septembre 2026, Bitget a subi une faille au niveau de son infrastructure backend. Les pirates ont falsifié des autorisations système internes pour valider de faux transferts et siphoner les portefeuilles chauds (hot wallets).
💰 Montant des Pertes : ~387,5 millions $
Des cryptos majeures ont été détournées vers plusieurs blockchains : ETH, XRP, USDT, TRX, AVAX, BNB et ZEC.
🛡️ Quel impact pour les utilisateurs ?
• ❄️ Cold Wallets : 100 % sécurisés (les portefeuilles froids n'ont pas été touchés).
• 👤 Soldes clients : Aucun impact direct sur vos comptes.
• 🛡️ Fonds de Protection : Le fonds de garantie Bitget (évalué à +460M$) couvrira l'intégralité des pertes.
🕵️ Qui est derrière le Hack ?
Selon la PDG Gracy Chen, les adresses IP et le mode opératoire pointent vers des hackers nord-coréens (groupe Lazarus). Les géants de la cybersécurité Mandiant et SlowMist sont sur le dossier.
🗓️ Calendrier de Reprise des Retraits :
✅ Faille corrigée & Trading opérationnel
📌 28 Sept. : Retraits BTC
📌 29 Sept. : Retraits ETH (Ethereum, BSC, Arbitrum, Base, OP)
📌 30 Sept. : Retraits USDT (Ethereum, BSC, Solana, Tron)
📌 02 Oct. : Autres altcoins, fiat et P2P
Restez prudents et vérifiez toujours vos sources officiellement ! 🔍✨
#Bitget #CryptoNews #Security #BinanceSquare #Hacking #Lazarus
170

🚨 ON-CHAIN TRAIL LINKS LAZARUS GROUP TO RECENT STOLEN $XRP FUND FLOWS 🔍
On-chain tracking just exposed a direct link between the recent $XRP breach on a top-tier exchange and July's $24 million AFX hack. 🔍 Cross-chain routing confirms stolen assets flowed through identical laundering paths managed by the notorious Lazarus Group.
When sophisticated bad actors wash funds across bridges, localized market liquidity and order flow take an immediate hit. 📊 Watching these specific bridge exits gives smart money crucial lead time before secondary sell pressure hits spot markets. 💡
How do you adjust your risk exposure when on-chain alerts signal major hacker liquidations? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #XRP #OnChain #CryptoSecurity #Lazarus
👁️ 🛡️
28

·
--
Everyone will quote the $30m. That is not the number
Lazarus-linked wallets sold over $30m of $BTC through Hyperliquid across three weeks, flipped it into $ETH and $SOL , and walked out through Kraken, LBank and KuCoin. Ugly headline, zero impact on your fills
In 2024 the same kind of wallets showed up on the platform and about $250m of net outflow left in 24 hours. Nothing was hacked that day. People got scared and pulled first
That is the risk you are actually carrying. Not the laundering. The stampede after it
Trump says his CFTC chairman is working to bring Hyperliquid onshore fully regulated. Regulated venues do not let strangers trade from a raw wallet
Just know which headline empties the book before you park size there🤔
Would you sit through a week like that with real size on?
#trump #Lazarus #Hyperliquid #cftc
5
82

💥 Lazarus Group is Cooking Crypto in 2026 ⚠️
North Korean hackers just dropped some of the biggest exploits this year:
Drift Protocol → $285M
Kelp DAO → $292M
Their Dirty Tactics:
Fake job offers & deepfake calls 😈
Malware on dev laptops to steal keys
Bridge exploits & fake collateral plays
They plan attacks for months... super patient & dangerous.
Stay Safe Kings:
Hardware wallet only
Never share seed/private keys
Double-check every link & file
Projects need better security ASAP!
You teaming up against Lazarus or still clicking random links? 😂👇
#Lazarus #cryptohacks #CryptoSecurity #BinanceSquare
3
637
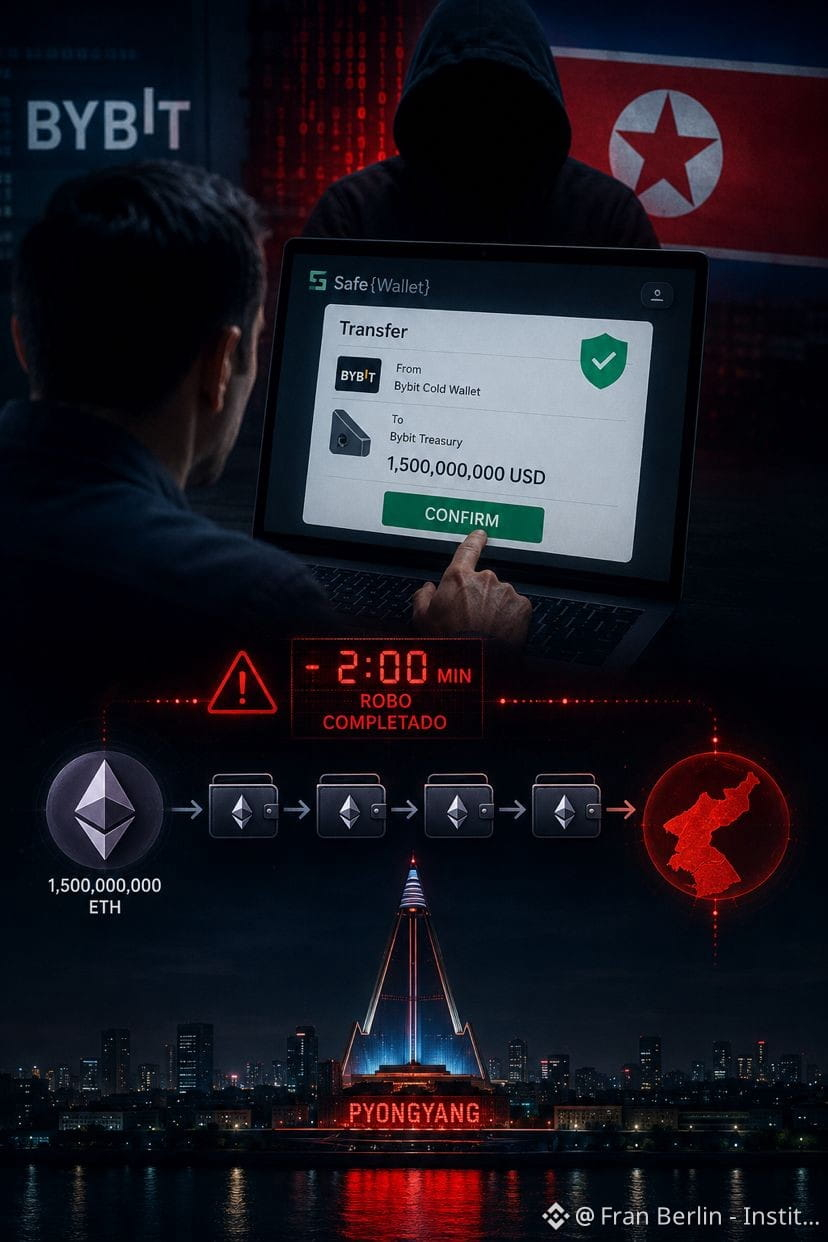
Era una transferencia de rutina.
Febrero 20, 2025. Un empleado de Bybit abre su pantalla, revisa los detalles de la transacción, y firma.
Todo se ve normal.
Minutos después, 1.500 millones de dólares $USDT en Ethereum habían desaparecido.
Pero lo más aterrador no es el monto.
Lo más aterrador es cómo lo hicieron.
El Grupo Lazarus hackers de élite del gobierno de Corea del Norte no atacó el blockchain. No rompió ninguna clave privada. No necesitó nada de eso.
Simplemente… falsificó lo que el empleado veía en pantalla.
Meses antes, infiltraron el sistema de un desarrollador de Safe Wallet, la plataforma que Bybit usaba para firmar transacciones. Inyectaron un código malicioso que dormía en silencio, esperando.
Cuando el empleado abrió su billetera ese día, el código se activó. La pantalla mostraba una transferencia legítima. En realidad, los fondos iban a Pyongyang.
El empleado firmó. Sus compañeros firmaron. Nadie vio nada raro.
Dos minutos después del robo, el código malicioso se borró solo. Sin rastro.
El FBI tardó días en confirmar lo que ya todos sospechaban: fue Corea del Norte, financiando su programa de armas nucleares con Ethereum robado.
La lección que nadie quiere escuchar: el eslabón más débil no es el código. Eres tú.
¿Confías en la pantalla que ves cuando firmas una transacción?
Fran Berlín | Instituto Blockchain
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
{spot}(ETHUSDT)
{spot}(USDCUSDT)
Era una transferencia de rutina.
Febrero 20, 2025. Un empleado de Bybit abre su pantalla, revisa los detalles de la transacción, y firma.
Todo se ve normal.
Minutos después, 1.500 millones de dólares $USDT en Ethereum habían desaparecido.
Pero lo más aterrador no es el monto.
Lo más aterrador es cómo lo hicieron.
El Grupo Lazarus hackers de élite del gobierno de Corea del Norte no atacó el blockchain. No rompió ninguna clave privada. No necesitó nada de eso.
Simplemente… falsificó lo que el empleado veía en pantalla.
Meses antes, infiltraron el sistema de un desarrollador de Safe Wallet, la plataforma que Bybit usaba para firmar transacciones. Inyectaron un código malicioso que dormía en silencio, esperando.
Cuando el empleado abrió su billetera ese día, el código se activó. La pantalla mostraba una transferencia legítima. En realidad, los fondos iban a Pyongyang.
El empleado firmó. Sus compañeros firmaron. Nadie vio nada raro.
Dos minutos después del robo, el código malicioso se borró solo. Sin rastro.
El FBI tardó días en confirmar lo que ya todos sospechaban: fue Corea del Norte, financiando su programa de armas nucleares con Ethereum robado.
La lección que nadie quiere escuchar: el eslabón más débil no es el código. Eres tú.
¿Confías en la pantalla que ves cuando firmas una transacción?
Fran Berlín | Instituto Blockchain
#Lazarus #ETH #InstitutoBlockchain #FranBerlin #BTC
654


·
--
Падение
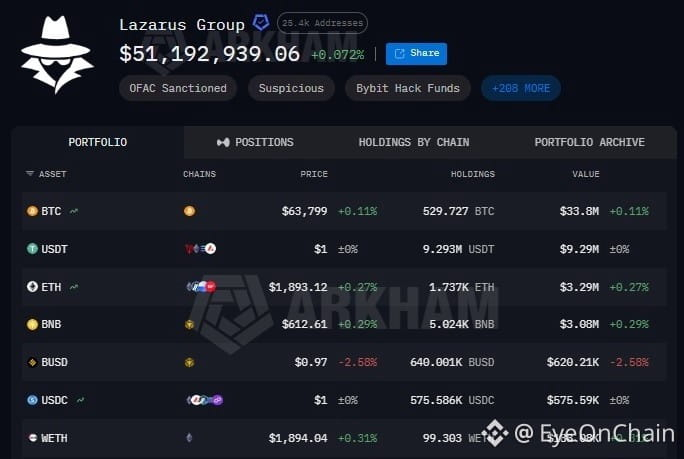
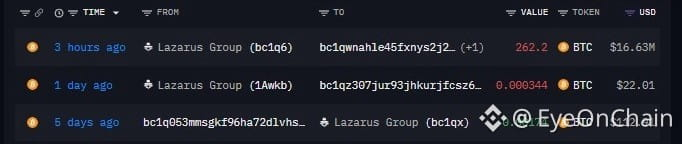
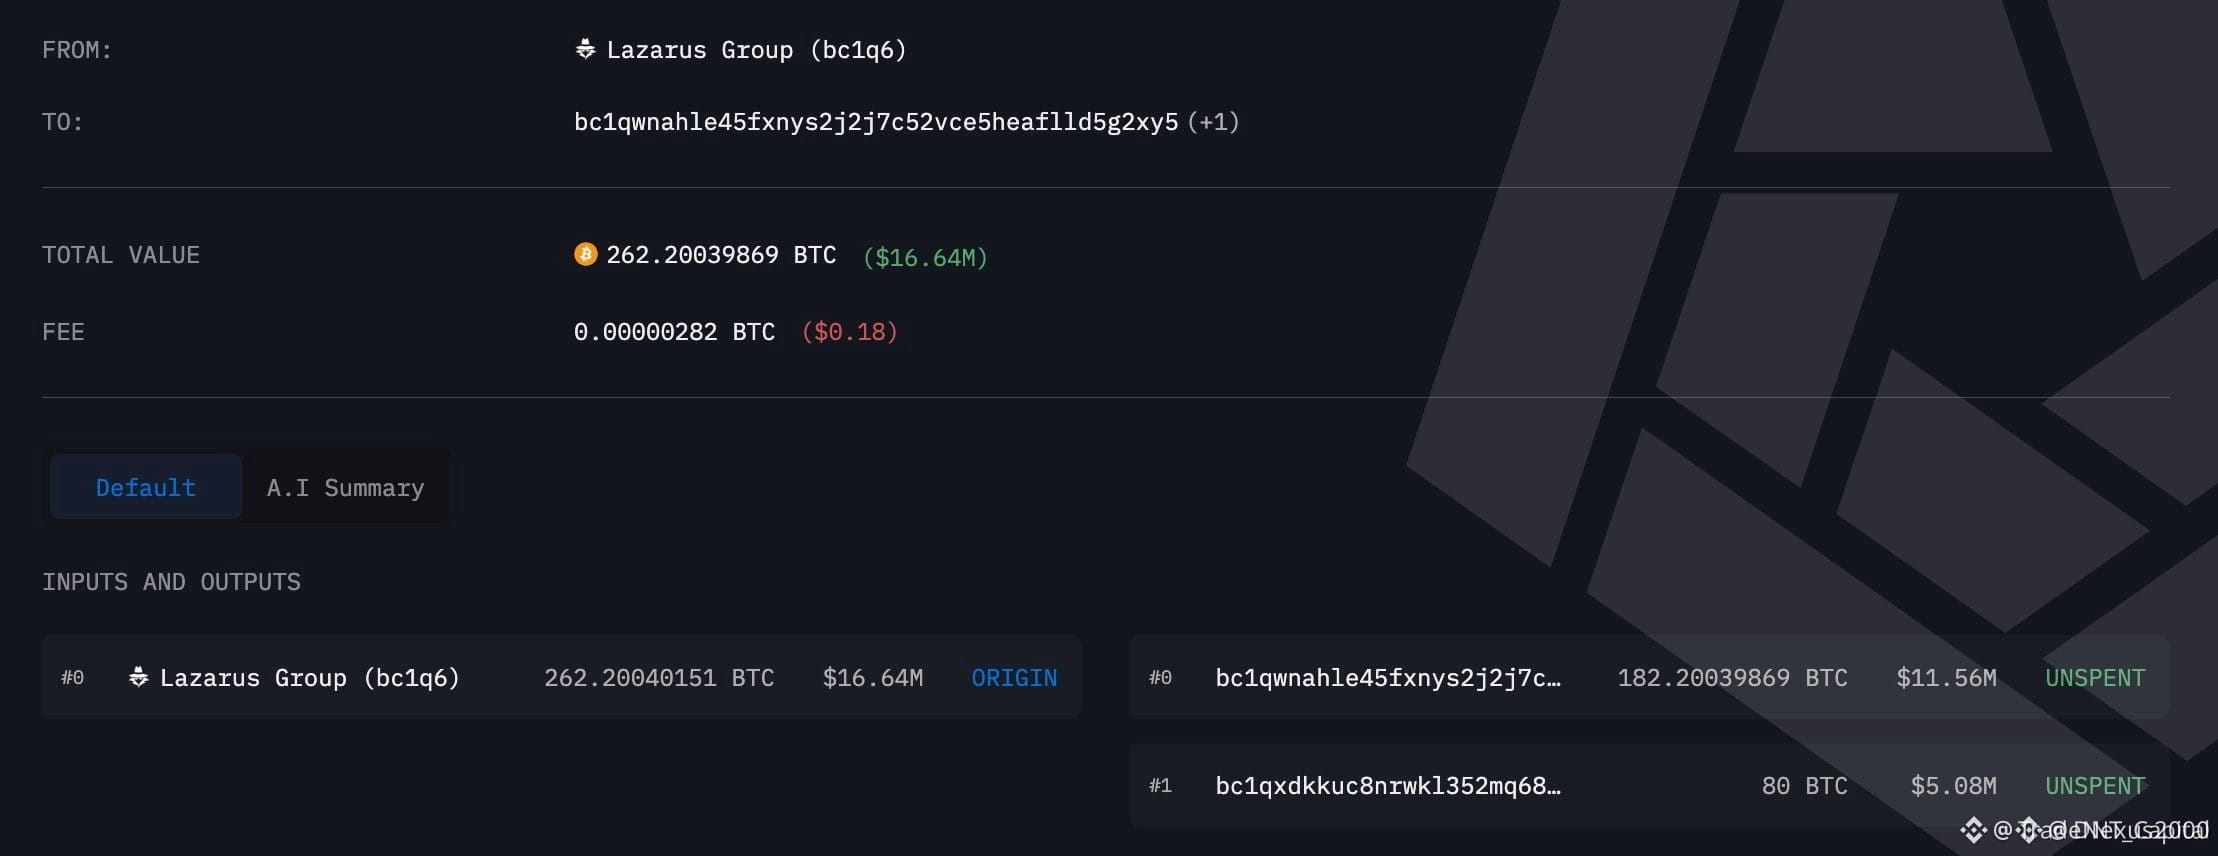
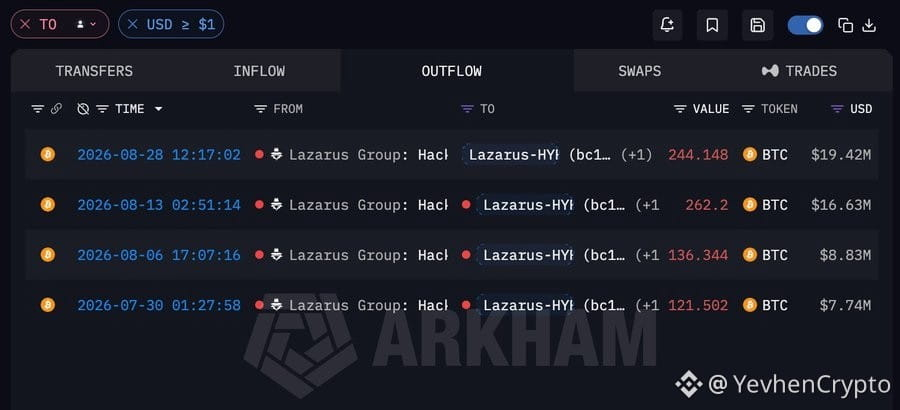
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC, $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
{future}(BTCUSDT)
{spot}(BTCUSDT)
Lazarus Group is moving some serious money again. About 3 hours ago, 262.2 $BTC , worth roughly $16.64M, was moved to a fresh wallet. No clear reason yet, but with #Lazarus , transfers like this always get attention. It could be part of an attempt to move or launder funds.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
The group still has more than $73M in assets on-chain, mainly held in $BTC , $USDT and $ETH.
Definitely a wallet cluster worth keeping an eye on.
1
1.3k

·
--
📰 BlockBeats 日报 2026-08-15 | 共 2 篇
1. 安全机构 ANY.RUN 创建假 DeFi 项目,成功渗透朝鲜 Lazarus Group 旗下 Famous Chollima 特工,揭露其完整工具链与社会工程攻击流程。
2. TMT Breakout 测算闪迪 CY2030 EPS 可逼近 700 美元,依赖 NAND 高利润率与每股约 1500 美元持续回购,HBF 量产或于 2028 年放量。
关键词:$BTC $ETH $SOL #BlockBeats #Web3 #Lazarus #NAND
📰 BlockBeats 日报 2026-08-15 | 共 2 篇
1. 安全机构 ANY.RUN 创建假 DeFi 项目,成功渗透朝鲜 Lazarus Group 旗下 Famous Chollima 特工,揭露其完整工具链与社会工程攻击流程。
2. TMT Breakout 测算闪迪 CY2030 EPS 可逼近 700 美元,依赖 NAND 高利润率与每股约 1500 美元持续回购,HBF 量产或于 2028 年放量。
关键词:$BTC $ETH $SOL #BlockBeats #Web3 #Lazarus #NAND
1. 安全机构 ANY.RUN 创建假 DeFi 项目,成功渗透朝鲜 Lazarus Group 旗下 Famous Chollima 特工,揭露其完整工具链与社会工程攻击流程。
2. TMT Breakout 测算闪迪 CY2030 EPS 可逼近 700 美元,依赖 NAND 高利润率与每股约 1500 美元持续回购,HBF 量产或于 2028 年放量。
关键词:$BTC $ETH $SOL #BlockBeats #Web3 #Lazarus #NAND
184

🚨 $BTC WALLET MOVE JUST ECHOED THE 2024 LAUNDERING PLAYBOOK 💥
262.2 BTC just crossed wallets in 2 hours — same fingerprint as the group's darkest exchanges. Not a transaction. It's a signal. Whether they bridge, swap, or mix tells us if sell pressure is imminent. 🔍
Over $73M still parked across $BTC , $USDT and $ETH . Until that liquidity touches a top-tier exchange, we're watching a shadow play. 📊 No confirmed sale — but the market has a long memory for these wallets. 💡
💬 If those funds move to an exchange — how quickly do you think market makers would shadow that liquidity? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #OnChain #Lazarus #CryptoAnalysis
🦈 👁️
21
·
--
█▓▒▒░░░THE BITGET HACK: The ONE Detail Everyone Is Missing (And Why It Changes Crypto Security Forever)░░░▒▒▓█
Most people looking at the $351.6M Bitget exploit are asking the wrong questions. They are tracking the Lazarus Group, looking at the $464M Protection Fund, or worrying about an ETH sell-off.
But here is what nobody is talking about, and it should terrify every crypto holder.
The Lie: "They stole the private keys."
The Reality: The keys were completely untouched.
Bitget CEO Gracy Chen confirmed the hackers bypassed key management entirely. Instead, they breached a internal wallet backend system. They fed fake, spoofed transaction data directly into the exchange's automated system.
Think about what this means: The exchange's own system willingly authorized the theft, thinking it was just a routine payout.
This marks a massive structural shift in crypto crime. Hackers are no longer wasting time trying to brute-force multisig keys or find smart contract bugs. They are using backend data spoofing to make the defense infrastructure work for them.
The Bottom Line:
Your funds on Bitget are covered by the protection fund. But if the industry's most advanced automated approval systems can be tricked into giving away $350M+ over dinner, no centralized automated hot wallet layer is truly safe right now.
The era of "safe because of multisig keys" is dead. Infrastructure security is the new battleground.
Are you keeping your capital on CEXs right now, or migrating to hard-walled cold storage? 👇
#Bitget $BTC
{future}(BTCUSDT)
#CryptoSecurity #Lazarus #Web3 #BinanceSquare
█▓▒▒░░░THE BITGET HACK: The ONE Detail Everyone Is Missing (And Why It Changes Crypto Security Forever)░░░▒▒▓█
Most people looking at the $351.6M Bitget exploit are asking the wrong questions. They are tracking the Lazarus Group, looking at the $464M Protection Fund, or worrying about an ETH sell-off.
But here is what nobody is talking about, and it should terrify every crypto holder.
The Lie: "They stole the private keys."
The Reality: The keys were completely untouched.
Bitget CEO Gracy Chen confirmed the hackers bypassed key management entirely. Instead, they breached a internal wallet backend system. They fed fake, spoofed transaction data directly into the exchange's automated system.
Think about what this means: The exchange's own system willingly authorized the theft, thinking it was just a routine payout.
This marks a massive structural shift in crypto crime. Hackers are no longer wasting time trying to brute-force multisig keys or find smart contract bugs. They are using backend data spoofing to make the defense infrastructure work for them.
The Bottom Line:
Your funds on Bitget are covered by the protection fund. But if the industry's most advanced automated approval systems can be tricked into giving away $350M+ over dinner, no centralized automated hot wallet layer is truly safe right now.
The era of "safe because of multisig keys" is dead. Infrastructure security is the new battleground.
Are you keeping your capital on CEXs right now, or migrating to hard-walled cold storage? 👇
#Bitget $BTC
#CryptoSecurity #Lazarus #Web3 #BinanceSquare
69
·
--
0926 日记 · 一个横跨 Crypto 与美股的人
今天盘面比新闻安静,新闻比盘面凶。
Bitget 被盗金额第三次上修,3.516 亿 → $3.875 亿,链上归因指向 Lazarus/TraderTraitor,Tether 已冻结相关地址。冷钱包无恙,4.64 亿保护基金兜底——但"排除私钥泄漏"目前只是初步结论,完整报告没出之前别急着下结论。顺手把老钱包的历史授权全 revoke 了一遍:Magic Eden 3832 个 NFT 就是这么没的,记住 取消挂单 ≠ 撤销授权。
AI 这头越来越像在修基建,而不是秀模型。Docker 把 Agent 全部权限声明打包成普通 OCI 镜像(Sandbox Kit v3),Google 开源 AX 定位"Agent 的 Kubernetes",社区还有人把 Claude Code / Codex / Cursor 们封装进统一持久化 GUI(Zuse)。一句话:让 Agent 跑起来不难,难的是权限、环境、编排、成本谁来管。顺带 Opus 5.5 已经能设计出 1113 个真实乐高零件、141 页搭建手册的 Microduck 了——AI 从"能画"走向"能交付"。
美股 AI 还在冲:META 涨到 777 创新高,市值逼近 2 万亿;但 @web3annie 提醒 AMD、TSM 已现顶背离,AVGO 回调达 40%,半导体的假突破风险要盯紧。Circle(CRCL)联创辞任董事、CFO 同日请辞,盘后应声下跌。
两条线其实同一个方向:极致的乐观,配一个必须自己兜底的世界。行情可以借势,风险只能自留。
$BTC #Openclaw #Bitget #DeFi #AI #Lazarus
266
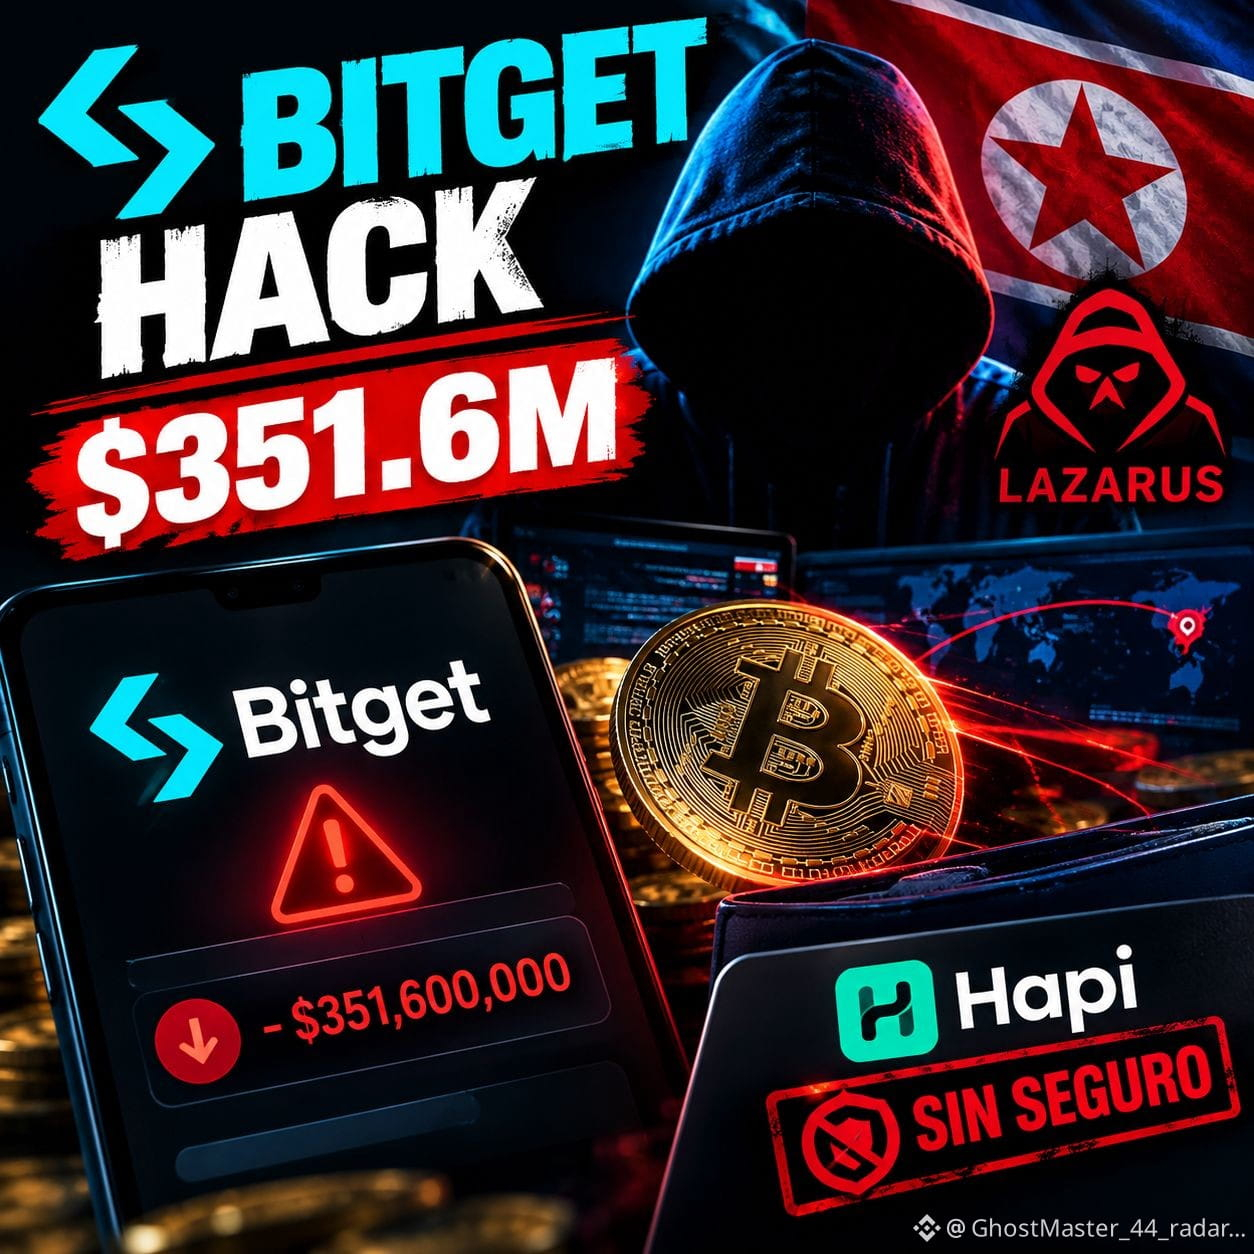
🚨 BITGET SUFRE UN HACK DE $351,6 MILLONES: ¿Lazarus ESTÁ DETRÁS? 🇰🇵💰
Uno de los mayores golpes de seguridad del sector cripto en 2026. La plataforma confirmó que aproximadamente $351,6 millones en activos fueron afectados después de transferencias no autorizadas desde parte de sus wallets calientes y wallets intermedias.
👀 ¿Quién estaría detrás?
La CEO de Bitget, Gracy Chen, señaló que los primeros análisis muestran patrones compatibles con ataques vinculados a grupos de hackers de Corea del Norte.
Entre las hipótesis aparece Lazarus, conocido por estar relacionado con grandes robos de criptomonedas, aunque la atribución todavía se encuentra bajo investigación.
🔓 Y hay un detalle todavía más llamativo: según Chen, las claves privadas no fueron comprometidas. Los atacantes habrían conseguido acceder a un sistema backend relacionado con la infraestructura de wallets, manipular información de las transacciones y conseguir que el propio proceso de autorización ejecutara las transferencias.
🛑 Bitget suspendió temporalmente los retiros mientras investiga el ataque, aunque depósitos y operaciones continuaron funcionando. La compañía afirma además que sus wallets frías permanecieron seguras y que su User Protection Fund supera los $464 millones, cantidad superior al monto afectado.
⚠️ Y aquí aparece otro debate: Hapi.
Los documentos actuales de Hapi especifican que las criptomonedas operadas mediante sus servicios no están aseguradas por FDIC ni protegidas por SIPC.
La protección SIPC de hasta $500.000 está relacionada con determinados activos y efectivo de la cuenta de corretaje, no con las criptomonedas.
Esto deja una pregunta sobre la mesa para cualquier persona que mantenga Bitcoin en una plataforma centralizada:
¿Qué ocurre realmente con tus $BTC si la plataforma sufre un hack y los fondos cripto son robados? 🔐₿
FÁCIL ➡️ RECUERDA TENER TÚ WALLET FRÍA :)
#Bitget #Lazarus #crypto #HackerAlert #CyberSecurity
236
·
--
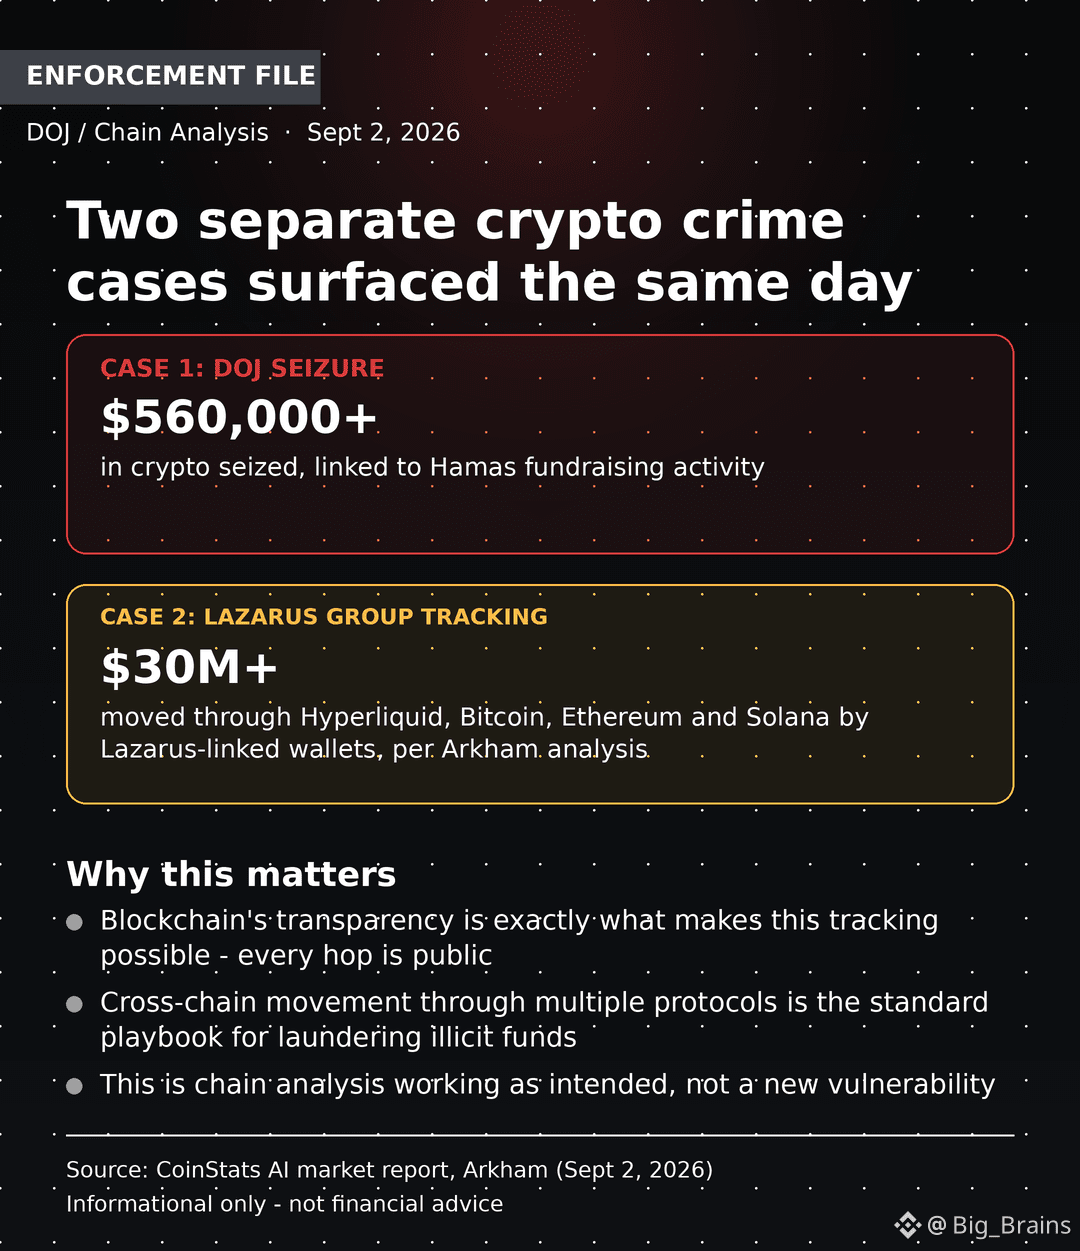
DOJ/Lazarus enforcement (case-file style) — Informational
Two crypto crime cases same day: $560K+ seized (Hamas-linked), $30M+ tracked moving through Hyperliquid/BTC/ETH/SOL (Lazarus Group). Blockchain transparency is exactly what made both traceable.
#CryptoSecurity #Lazarus #ChainAnalysis #BinanceSquare #crptonews
Two crypto crime cases same day: $560K+ seized (Hamas-linked), $30M+ tracked moving through Hyperliquid/BTC/ETH/SOL (Lazarus Group). Blockchain transparency is exactly what made both traceable.
#CryptoSecurity #Lazarus #ChainAnalysis #BinanceSquare #crptonews
63
·
--
🚨 Lazarus знову у фокусі, понад $30 млн можуть проходити через Hyperliquid
Північнокорейське угруповання Lazarus Group знову привернуло увагу ончейн-аналітиків.
За даними дослідників, пов'язані з Lazarus адреси переміщують $30M+ через інфраструктуру Hyperliquid
🔍 Як виглядає маршрут коштів:
➡️ BTC надходить у HyperUnit
➡️ BTC конвертується в ETH та SOL
➡️ активи переміщуються через мости в Ethereum, Solana та Tron
➡️ частина коштів зрештою потрапляє на централізовані біржі та інші сервіси
Цікаво, що частина адрес уже фігурувала в попередніх розслідуваннях, пов'язаних із викраденням криптоактивів.
🧩 Що це означає для ринку?
Це не означає, що Hyperliquid "відмиває" кошти або що протокол безпосередньо причетний до злочинів.
💬 Як думаєте, DeFi зможе зберегти свою відкритість, одночасно блокуючи подібні схеми?
#Crypto #Hyperliquid #DeFi #Lazarus #Ethereum
1
288
🚨 LAZARUS GROUP SHUFFLES $30M STOLEN FUNDS VIA $HYPE AS ON-CHAIN RADARS TRIGGER 🦈
On-chain traces just caught the Lazarus Group funneling over $30 million through Hyperliquid rails. 🔍 These specific sanctioned addresses were flagged by ZachXBT after routing $61 million in exploited capital, showing institutional-scale laundering mechanics in real time. 📊
When bad actors push multi-million dollar flows across decentralized venues, it creates localized liquidity distortion and heightened compliance scrutiny across bridged assets. 🛡️ Smart money watches these capital routes closely before sizing into adjacent setups. 💬 Are you adjusting your order book strategies while these rogue funds circulate? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HYPE #OnChain #CryptoSecurity #Lazarus #DeFi
🔍 ⚡
70
·
--
Arkham Intelligence published a report examining Lazarus Group’s crypto laundering network and operational tactics between 2017 and 2026.
According to the research, Lazarus-linked actors were tied to more than $6 billion in stolen cryptocurrency across exchange breaches, ransomware campaigns, bridge exploits, and decentralized finance attacks.
Arkham said North Korean-linked actors accounted for more than 70% of crypto exploit losses recorded so far in 2026.
The report described how Lazarus allegedly moves stolen assets through cross-chain bridges, mixers, centralized exchanges, OTC brokers, and fragmented wallet activity to complicate blockchain tracing efforts.
THORChain was identified as a frequently used bridge for converting stolen assets into Bitcoin. Arkham also referenced mixers including Sinbad.io and YoMix, along with Russian exchanges and Chinese OTC brokers involved in cash-out activity.
The research examined the April 2026 Drift Protocol ($DRIFT ) exploit, where attackers allegedly spent months building trust with employees through conferences, deposits exceeding $1 million, and fake partnership activity. Arkham said Lazarus later used pre-authorized Solana transactions to drain about $285 million from the protocol.
The report also covered the February 2026 KelpDAO exploit. According to Arkham, attackers compromised LayerZero RPC nodes and forged cross-chain messages, allowing the withdrawal of 116,500 $rsETH valued at about $292 million.
Arkham concluded that Lazarus continues adapting its laundering methods and attack strategies as blockchain tracing systems become more advanced.
#arkham #DRIFT #KelpDAO #LazarusGroup #Lazarus
445

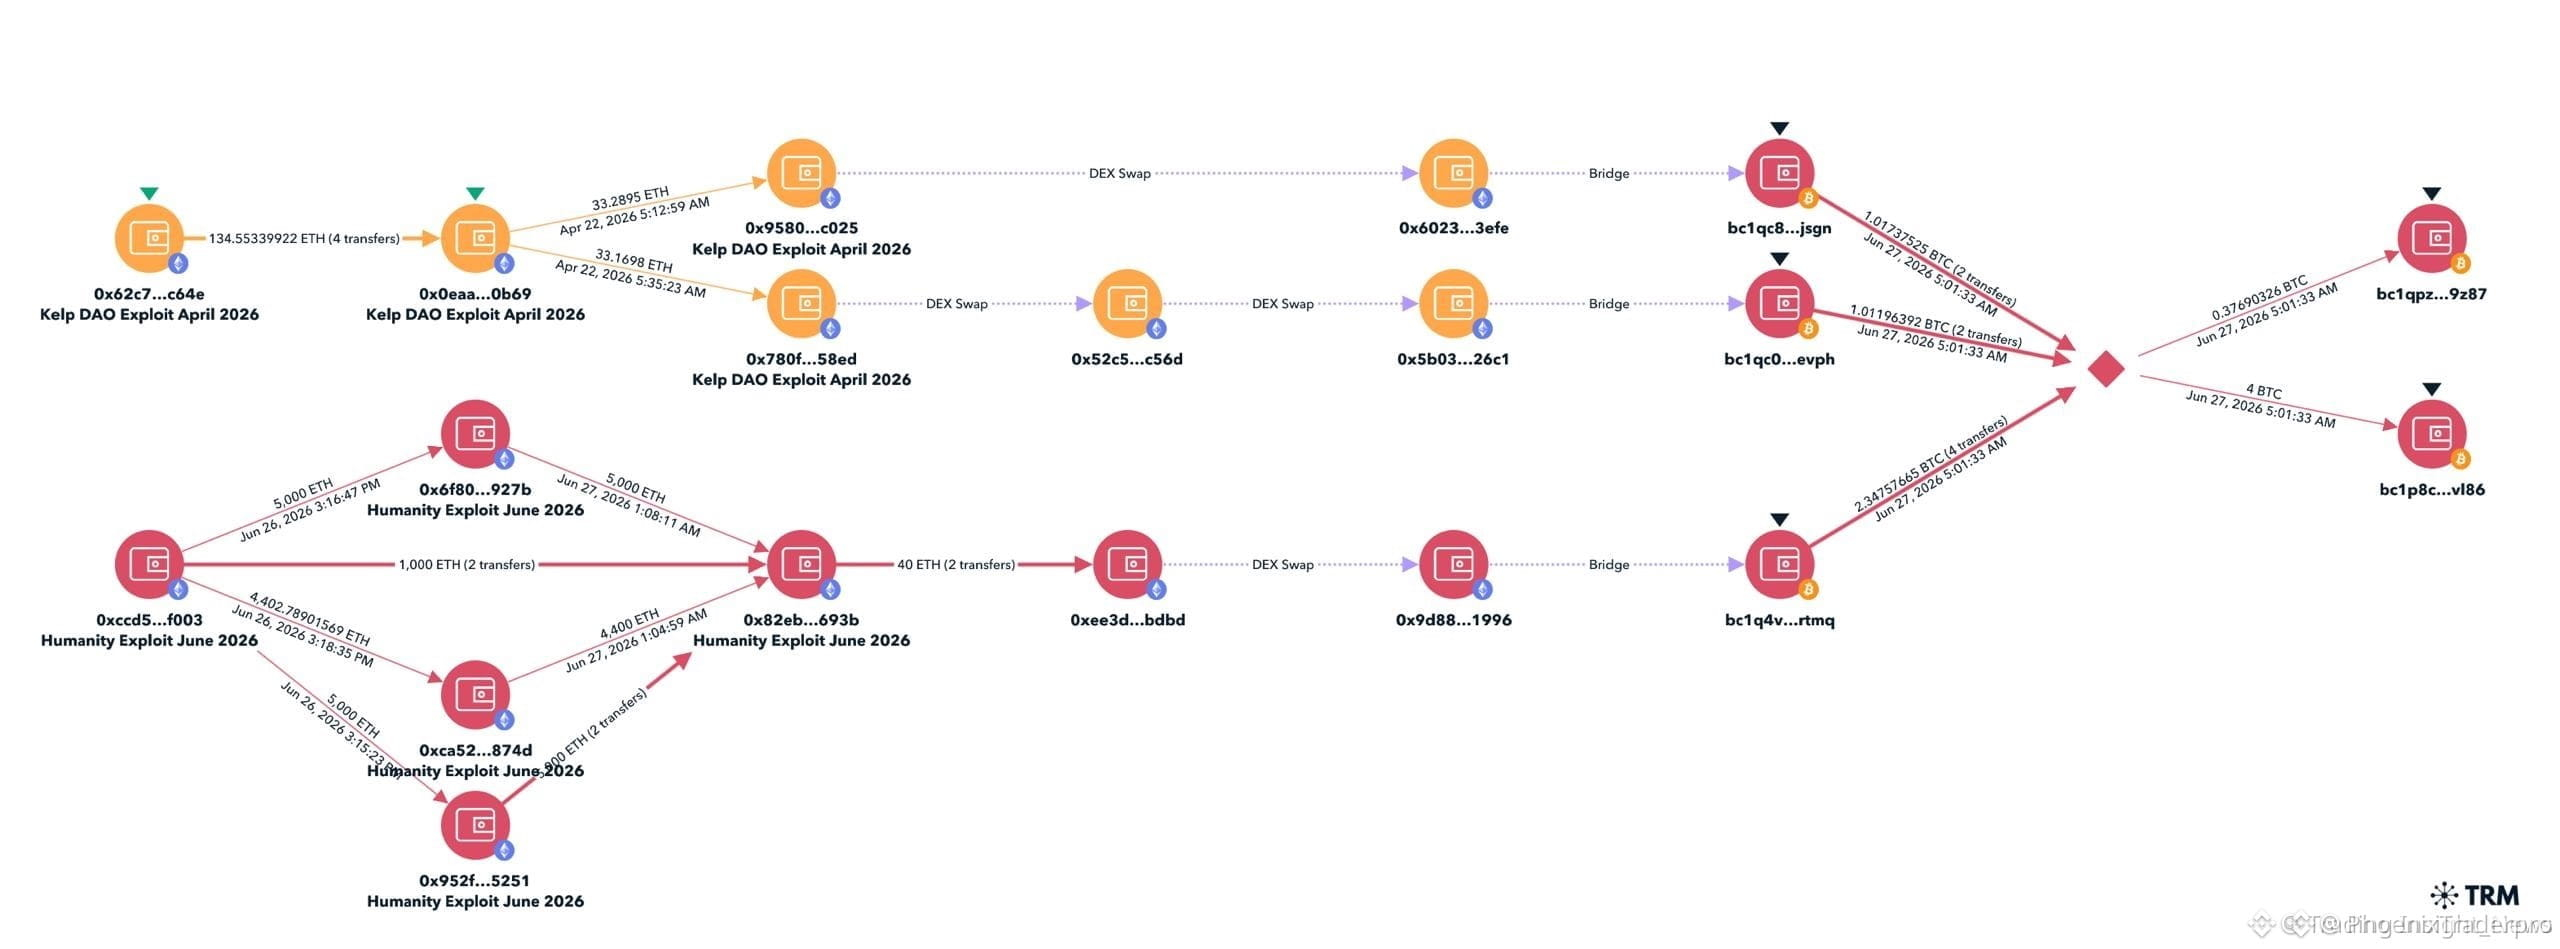
TWO MAJOR $ETH HACKS TRACED TO LAZARUS GROUP 🔥
ZachXBT just connected the dots: funds from the Kelp DAO $292M exploit and the Humanity Protocol $32M theft are converging on the same address. This isn't coincidence — it's a signature move from the Lazarus Group.
The timing is what bothers me. April 18th and June 9th, two separate attacks, same destination. That means North Korea's top hacking crew is actively expanding their DeFi campaign. If you're in a new project without a proper audit, the risk just went up.
What's your move — pull liquidity from unaudited protocols or hold through?
Not financial advice. Always manage your risk.
#ETH #Lazarus #DeFiSecurity #HackAlert #CryptoNews
🔥
35

·
--
🦈 $ETH TOP-TIER EXCHANGE SUES NORTH KOREA FOR $1.5B HACK – LAZARUS ASSETS FROZEN ⚖️
📊 A U.S. federal judge just slammed a preliminary injunction on unidentified wallets tied to the largest crypto heist in history — turning the Lazarus Group’s stolen $1.5B into a frozen liability instead of dry powder. 🔍
🛡️ Smart money reads this as sovereign-grade legal pressure targeting the laundering pipeline, not just the exploit. This isn’t a PR move — it’s a structural attempt to claw back liquidity that was violently extracted from the ecosystem. 🌊
💬 Could this freeze push $ETH sell pressure through alternative rails, or will trapped funds simply shadow the market until trial? Where do you see the real impact? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Lazarus #CryptoNews #Institutional #SmartMoney
🔒 🦈
35
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#BinanceKZ
Просмотров: 9,165
51 обсуждают
2
#EarningsSeason
Просмотров: 37,752
330 обсуждают
3
#JapanFSABacksFourthStablecoinTradeSettlementPilot
Просмотров: 68
13 обсуждают
4
#BitgetHackerFailsToMoveStolenFunds
Просмотров: 3,727
161 обсуждают
5
#BitMineETHHoldingsTop6Million
Просмотров: 6,368
320 обсуждают
6
#StrategyAdds1666BTCHoldingsReach847666
Просмотров: 6,222
250 обсуждают
7
#NvidiaApproves$150BBuyback
Просмотров: 2,868
58 обсуждают
8
#OpenAIDelaysGPT6.1OverSafetyIssues
Просмотров: 18,332
556 обсуждают
9
#AMDToAcquireWorldLabsFor$8.2B
Просмотров: 1,453
50 обсуждают
10
#AnthropicIPOProspectusCouldValueItOver$2T
Просмотров: 4,862
74 обсуждают