
#keplr
keplr
66,492 ຄັ້ງທີ່ເບິ່ງ
107 ກຳລັງສົນທະນາ
ມາແຮງ
ຫຼ້າສຸດ

·
--
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
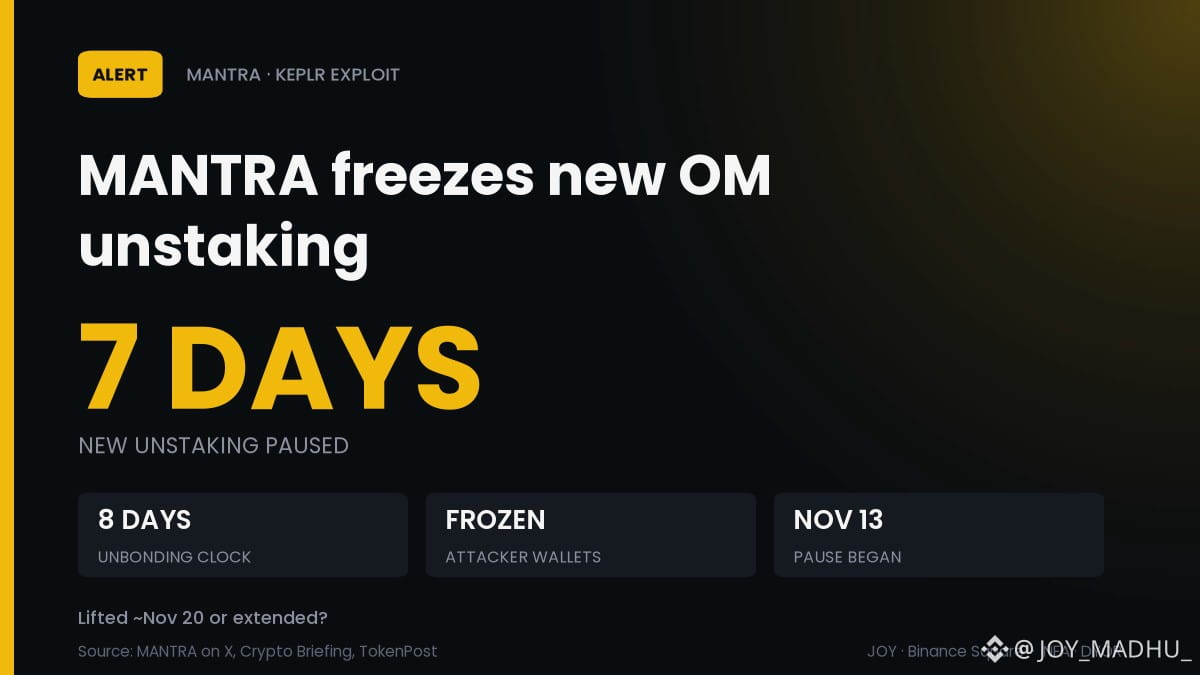
🔐 7-Day Freeze vs an 8-Day Clock
MANTRA froze new OM unstaking after attackers used leaked Keplr keys to unbond victims' stakes.
📅 Pause began Nov 13, runs 7 days, then gets reviewed
⚠️ Unbonding already underway keeps its 8-day clock
🏦 Governance Proposal 41 froze attacker-linked wallets
📊 Cause: Web3Auth flaw exposed Keplr Google/Apple login keys
Watch next: victims must redelegate before day 8. Losses still undisclosed.
Pause lifted on schedule ~Nov 20, or extended past 7 days? 👇
$OM
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #Keplr #CryptoSecurity
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🔐 7-Day Freeze vs an 8-Day Clock
MANTRA froze new OM unstaking after attackers used leaked Keplr keys to unbond victims' stakes.
📅 Pause began Nov 13, runs 7 days, then gets reviewed
⚠️ Unbonding already underway keeps its 8-day clock
🏦 Governance Proposal 41 froze attacker-linked wallets
📊 Cause: Web3Auth flaw exposed Keplr Google/Apple login keys
Watch next: victims must redelegate before day 8. Losses still undisclosed.
Pause lifted on schedule ~Nov 20, or extended past 7 days? 👇
$OM
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #Keplr #CryptoSecurity
🔐 7-Day Freeze vs an 8-Day Clock
MANTRA froze new OM unstaking after attackers used leaked Keplr keys to unbond victims' stakes.
📅 Pause began Nov 13, runs 7 days, then gets reviewed
⚠️ Unbonding already underway keeps its 8-day clock
🏦 Governance Proposal 41 froze attacker-linked wallets
📊 Cause: Web3Auth flaw exposed Keplr Google/Apple login keys
Watch next: victims must redelegate before day 8. Losses still undisclosed.
Pause lifted on schedule ~Nov 20, or extended past 7 days? 👇
$OM
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #Keplr #CryptoSecurity
35
·
--
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
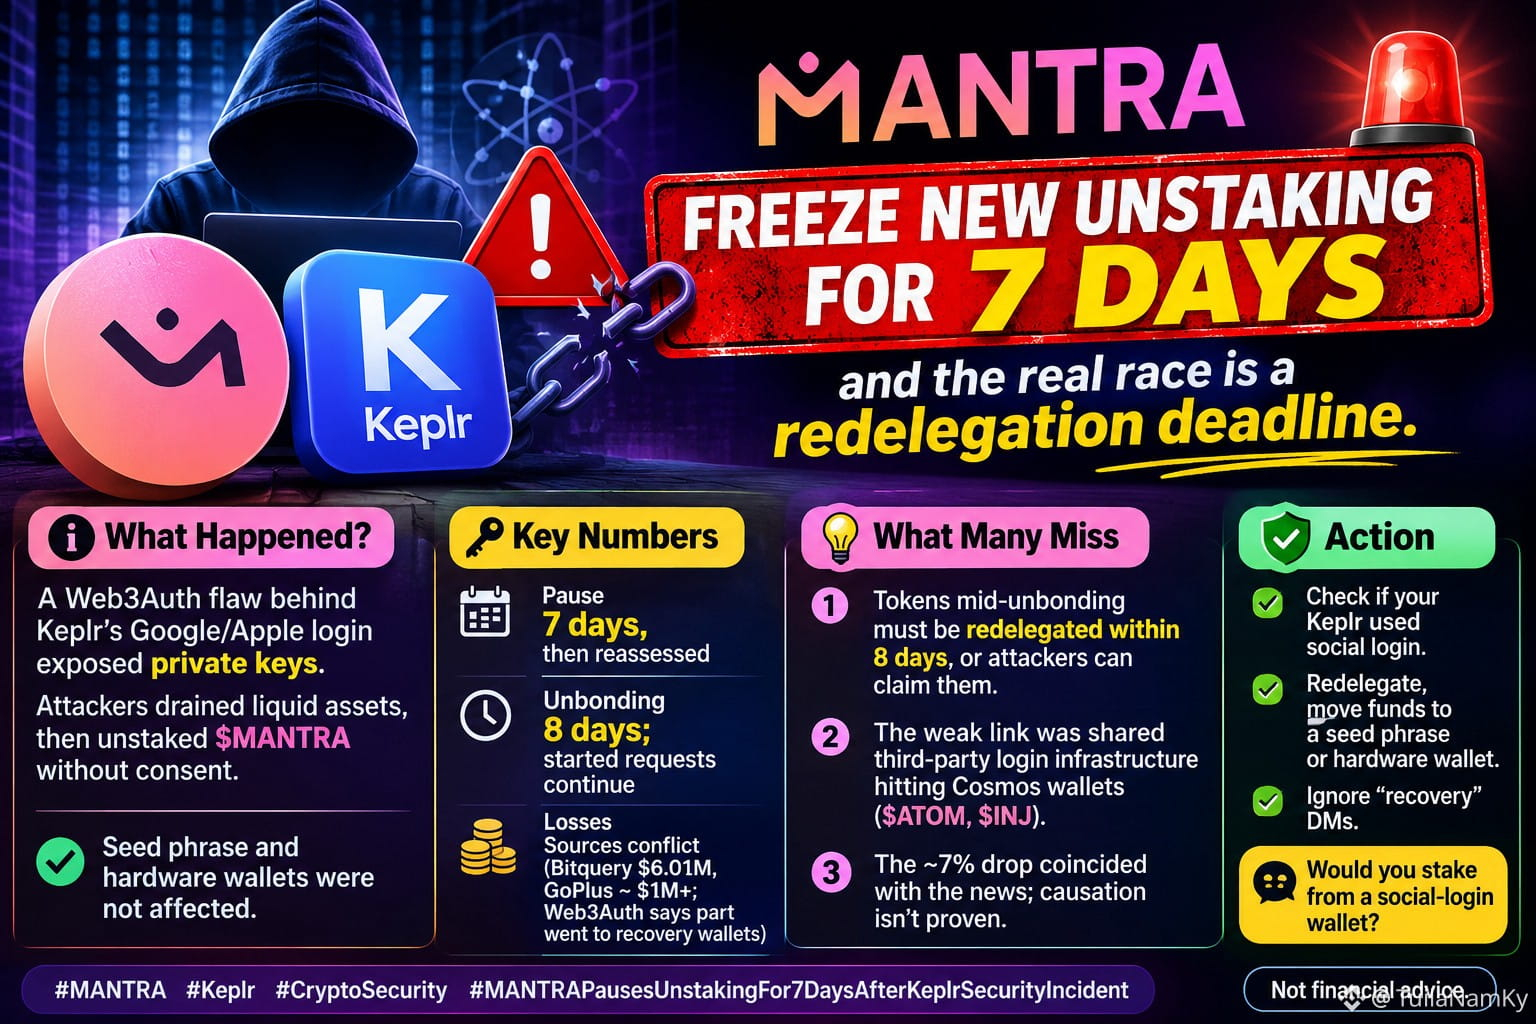
🚨 MANTRA froze new unstaking for 7 days, and the real race is a redelegation deadline.
What happened: a Web3Auth flaw behind Keplr’s Google/Apple login exposed private keys. Attackers drained liquid assets, then unstaked MANTRA without consent. Seed phrase and hardware wallets were not affected.
Key numbers:
Pause: 7 days, then reassessed Unbonding: 8 days; started requests continue Losses: sources conflict (Bitquery $6.01M, GoPlus ~$1M+; Web3Auth says part went to recovery wallets)
What many miss:
1️⃣ Tokens mid-unbonding must be redelegated within the 8 days, or attackers can claim them.
2️⃣ The weak link was shared third-party login infrastructure hitting Cosmos wallets ($ATOM, $INJ).
3️⃣ The ~7% drop coincided with the news; causation isn’t proven.
Action: check if your Keplr used social login, redelegate, move funds to a seed phrase or hardware wallet. Ignore “recovery” DMs.
Would you stake from a social-login wallet?
Not financial advice.
#MANTRA #Keplr #CryptoSecurity
$MANTRA
{future}(MANTRAUSDT)
$ATOM.US
{stock_us}(ATOM.US)
$INJ
{future}(INJUSDT)
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA froze new unstaking for 7 days, and the real race is a redelegation deadline.
What happened: a Web3Auth flaw behind Keplr’s Google/Apple login exposed private keys. Attackers drained liquid assets, then unstaked MANTRA without consent. Seed phrase and hardware wallets were not affected.
Key numbers:
Pause: 7 days, then reassessed Unbonding: 8 days; started requests continue Losses: sources conflict (Bitquery $6.01M, GoPlus ~$1M+; Web3Auth says part went to recovery wallets)
What many miss:
1️⃣ Tokens mid-unbonding must be redelegated within the 8 days, or attackers can claim them.
2️⃣ The weak link was shared third-party login infrastructure hitting Cosmos wallets ($ATOM, $INJ ).
3️⃣ The ~7% drop coincided with the news; causation isn’t proven.
Action: check if your Keplr used social login, redelegate, move funds to a seed phrase or hardware wallet. Ignore “recovery” DMs.
Would you stake from a social-login wallet?
Not financial advice.
#MANTRA #Keplr #CryptoSecurity
$MANTRA
$ATOM.US
$INJ
🚨 MANTRA froze new unstaking for 7 days, and the real race is a redelegation deadline.
What happened: a Web3Auth flaw behind Keplr’s Google/Apple login exposed private keys. Attackers drained liquid assets, then unstaked MANTRA without consent. Seed phrase and hardware wallets were not affected.
Key numbers:
Pause: 7 days, then reassessed Unbonding: 8 days; started requests continue Losses: sources conflict (Bitquery $6.01M, GoPlus ~$1M+; Web3Auth says part went to recovery wallets)
What many miss:
1️⃣ Tokens mid-unbonding must be redelegated within the 8 days, or attackers can claim them.
2️⃣ The weak link was shared third-party login infrastructure hitting Cosmos wallets ($ATOM, $INJ ).
3️⃣ The ~7% drop coincided with the news; causation isn’t proven.
Action: check if your Keplr used social login, redelegate, move funds to a seed phrase or hardware wallet. Ignore “recovery” DMs.
Would you stake from a social-login wallet?
Not financial advice.
#MANTRA #Keplr #CryptoSecurity
$MANTRA
$ATOM.US
$INJ
659
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA Pauses Unstaking for 7 Days Following Keplr Security Incident!
MANTRA has reportedly introduced a temporary seven-day pause on unstaking activities following a security incident involving Keplr.
The move highlights growing concerns around wallet security and the potential risks facing users across the crypto ecosystem.
Why It Matters:
User protection: The temporary pause may help limit risks while the incident is investigated.
Liquidity concerns: MANTRA holders may have to wait longer than expected to access their staked tokens.
Security risks: The incident highlights the importance of wallet infrastructure and protecting user assets.
My Take: Security incidents can quickly damage investor confidence, especially when staking withdrawals are affected. MANTRA's response and further details about the Keplr incident will be important for determining the impact.
Will this temporary pause protect users, or create more uncertainty around MANTRA?
#mantra #keplr #CryptoSecurity
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA Pauses Unstaking for 7 Days Following Keplr Security Incident!
MANTRA has reportedly introduced a temporary seven-day pause on unstaking activities following a security incident involving Keplr.
The move highlights growing concerns around wallet security and the potential risks facing users across the crypto ecosystem.
Why It Matters:
User protection: The temporary pause may help limit risks while the incident is investigated.
Liquidity concerns: MANTRA holders may have to wait longer than expected to access their staked tokens.
Security risks: The incident highlights the importance of wallet infrastructure and protecting user assets.
My Take: Security incidents can quickly damage investor confidence, especially when staking withdrawals are affected. MANTRA's response and further details about the Keplr incident will be important for determining the impact.
Will this temporary pause protect users, or create more uncertainty around MANTRA?
#mantra #keplr #CryptoSecurity
🚨 MANTRA Pauses Unstaking for 7 Days Following Keplr Security Incident!
MANTRA has reportedly introduced a temporary seven-day pause on unstaking activities following a security incident involving Keplr.
The move highlights growing concerns around wallet security and the potential risks facing users across the crypto ecosystem.
Why It Matters:
User protection: The temporary pause may help limit risks while the incident is investigated.
Liquidity concerns: MANTRA holders may have to wait longer than expected to access their staked tokens.
Security risks: The incident highlights the importance of wallet infrastructure and protecting user assets.
My Take: Security incidents can quickly damage investor confidence, especially when staking withdrawals are affected. MANTRA's response and further details about the Keplr incident will be important for determining the impact.
Will this temporary pause protect users, or create more uncertainty around MANTRA?
#mantra #keplr #CryptoSecurity
Jerilyn Ader VRzJ:
Not easy
1
2
394
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA PAUSES UNSTAKING FOR 7 DAYS AFTER KEPLR SECURITY INCIDENT!
A major security alert hits the MANTRA ecosystem! ⚠️
MANTRA has temporarily suspended all new unstaking transactions for seven days following a private-key security incident involving Web3Auth and certain Keplr wallets.
🔥 What Traders Need to Know:
Hackers reportedly accessed affected wallet keys.
Unauthorized MANTRA unstaking attempts were reported.
Several attacker-linked wallets have been frozen.
Existing unstaking requests are NOT automatically protected by the seven-day pause.
Affected users should follow MANTRA's official redelegation instructions before their 8-day unstaking period ends.
📊 My Market Outlook: Short-term uncertainty could increase volatility in MANTRA (OM). Watch trading volume, support levels, and official security updates.
⚠️ Trading Strategy: Avoid panic buying or selling. Wait for clear recovery signals and confirmation from the project.
🔥 Big Question: Can MANTRA restore investor confidence after this security incident?
#MANTRA #OM #Keplr #CryptoSecurity #Altcoins #cryptotrading MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA PAUSES UNSTAKING FOR 7 DAYS AFTER KEPLR SECURITY INCIDENT!
A major security alert hits the MANTRA ecosystem! ⚠️
MANTRA has temporarily suspended all new unstaking transactions for seven days following a private-key security incident involving Web3Auth and certain Keplr wallets.
🔥 What Traders Need to Know:
Hackers reportedly accessed affected wallet keys.
Unauthorized MANTRA unstaking attempts were reported.
Several attacker-linked wallets have been frozen.
Existing unstaking requests are NOT automatically protected by the seven-day pause.
Affected users should follow MANTRA's official redelegation instructions before their 8-day unstaking period ends.
📊 My Market Outlook: Short-term uncertainty could increase volatility in MANTRA (OM). Watch trading volume, support levels, and official security updates.
⚠️ Trading Strategy: Avoid panic buying or selling. Wait for clear recovery signals and confirmation from the project.
🔥 Big Question: Can MANTRA restore investor confidence after this security incident?
#MANTRA #OM #Keplr #CryptoSecurity #Altcoins #cryptotrading MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
🚨 MANTRA PAUSES UNSTAKING FOR 7 DAYS AFTER KEPLR SECURITY INCIDENT!
A major security alert hits the MANTRA ecosystem! ⚠️
MANTRA has temporarily suspended all new unstaking transactions for seven days following a private-key security incident involving Web3Auth and certain Keplr wallets.
🔥 What Traders Need to Know:
Hackers reportedly accessed affected wallet keys.
Unauthorized MANTRA unstaking attempts were reported.
Several attacker-linked wallets have been frozen.
Existing unstaking requests are NOT automatically protected by the seven-day pause.
Affected users should follow MANTRA's official redelegation instructions before their 8-day unstaking period ends.
📊 My Market Outlook: Short-term uncertainty could increase volatility in MANTRA (OM). Watch trading volume, support levels, and official security updates.
⚠️ Trading Strategy: Avoid panic buying or selling. Wait for clear recovery signals and confirmation from the project.
🔥 Big Question: Can MANTRA restore investor confidence after this security incident?
#MANTRA #OM #Keplr #CryptoSecurity #Altcoins #cryptotrading MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident
8
·
--
MANTRA Freezes Unstaking for 7 Days After Keplr Wallet Hack
Hackers exploited a Web3Auth flaw to steal private keys from Keplr users who logged in via Google or Apple — then started unbonding victims' staked $OM without consent.
MANTRA paused all new unbonding for 7 days and froze several hacker wallets via Governance Proposal 41. At least $1.82M was stolen across 7,842 Cosmos wallets, per Bitquery.
If your OM is mid-unbonding, redelegate before the 8-day window ends — or hackers can claim it.
Not financial advice.
$OM #MANTRA #Keplr #Web3Auth
MANTRA Freezes Unstaking for 7 Days After Keplr Wallet Hack
Hackers exploited a Web3Auth flaw to steal private keys from Keplr users who logged in via Google or Apple — then started unbonding victims' staked $OM without consent.
MANTRA paused all new unbonding for 7 days and froze several hacker wallets via Governance Proposal 41. At least $1.82M was stolen across 7,842 Cosmos wallets, per Bitquery.
If your OM is mid-unbonding, redelegate before the 8-day window ends — or hackers can claim it.
Not financial advice.
$OM #MANTRA #Keplr #Web3Auth
Hackers exploited a Web3Auth flaw to steal private keys from Keplr users who logged in via Google or Apple — then started unbonding victims' staked $OM without consent.
MANTRA paused all new unbonding for 7 days and froze several hacker wallets via Governance Proposal 41. At least $1.82M was stolen across 7,842 Cosmos wallets, per Bitquery.
If your OM is mid-unbonding, redelegate before the 8-day window ends — or hackers can claim it.
Not financial advice.
$OM #MANTRA #Keplr #Web3Auth
37
·
--
Your crypto wallet can be hacked without anyone knowing your password. 😳
Recent security reports have raised concerns about Keplr wallets connected through Google and Apple login.
The issue reportedly involved exposed private keys through wallet infrastructure.
Think about that...
You can use a trusted login method and still face security risks.
This is why serious crypto users should never depend on just one layer of protection.
Use hardware wallets for long-term holdings, protect your recovery phrase, and never share it with anyone.
Convenience is good.
But in crypto, security comes first. 🔐
#CryptoSecurity #Keplr #Web3 #Bitcoin
Your crypto wallet can be hacked without anyone knowing your password. 😳
Recent security reports have raised concerns about Keplr wallets connected through Google and Apple login.
The issue reportedly involved exposed private keys through wallet infrastructure.
Think about that...
You can use a trusted login method and still face security risks.
This is why serious crypto users should never depend on just one layer of protection.
Use hardware wallets for long-term holdings, protect your recovery phrase, and never share it with anyone.
Convenience is good.
But in crypto, security comes first. 🔐
#CryptoSecurity #Keplr #Web3 #Bitcoin
Recent security reports have raised concerns about Keplr wallets connected through Google and Apple login.
The issue reportedly involved exposed private keys through wallet infrastructure.
Think about that...
You can use a trusted login method and still face security risks.
This is why serious crypto users should never depend on just one layer of protection.
Use hardware wallets for long-term holdings, protect your recovery phrase, and never share it with anyone.
Convenience is good.
But in crypto, security comes first. 🔐
#CryptoSecurity #Keplr #Web3 #Bitcoin
1
6
·
--
🚨 Google/Apple一键登录钱包,一夜翻车:Keplr用户私钥泄露!
📌 经过:
• 11/7 Keplr称部分用Google/Apple登录创建的账户出现未授权转账,随即暂停两种登录
• 根源在Consensys旗下登录服务商 Web3Auth 的基础设施漏洞,不是Keplr代码
• Bitquery统计:约600万美元转账,涉及4.4万+个Cosmos钱包;GoPlus称至少约100万美元被盗,另约600万被Web3Auth转入救援地址
• Keplr联合创始人估计约20%社交登录账户可能受影响
✅ 助记词钱包、硬件钱包不受影响
⚠️ 教训:
1️⃣ 社交登录=方便,但私钥托管在第三方,多了一个单点故障
2️⃣ 大额资产放硬件钱包/自己保管助记词
3️⃣ 余额变空不一定是被盗,可能已被转入救援地址,先看官方公告,别乱授权、别点陌生"找回"链接
你的钱包是社交登录还是助记词?评论区聊聊👇
$BTC $ETH $BNB #钱包安全 #Keplr #加密市场
仅为个人观点,不构成投资建议
🚨 Google/Apple一键登录钱包,一夜翻车:Keplr用户私钥泄露!
📌 经过:
• 11/7 Keplr称部分用Google/Apple登录创建的账户出现未授权转账,随即暂停两种登录
• 根源在Consensys旗下登录服务商 Web3Auth 的基础设施漏洞,不是Keplr代码
• Bitquery统计:约600万美元转账,涉及4.4万+个Cosmos钱包;GoPlus称至少约100万美元被盗,另约600万被Web3Auth转入救援地址
• Keplr联合创始人估计约20%社交登录账户可能受影响
✅ 助记词钱包、硬件钱包不受影响
⚠️ 教训:
1️⃣ 社交登录=方便,但私钥托管在第三方,多了一个单点故障
2️⃣ 大额资产放硬件钱包/自己保管助记词
3️⃣ 余额变空不一定是被盗,可能已被转入救援地址,先看官方公告,别乱授权、别点陌生"找回"链接
你的钱包是社交登录还是助记词?评论区聊聊👇
$BTC $ETH $BNB #钱包安全 #Keplr #加密市场
仅为个人观点,不构成投资建议
📌 经过:
• 11/7 Keplr称部分用Google/Apple登录创建的账户出现未授权转账,随即暂停两种登录
• 根源在Consensys旗下登录服务商 Web3Auth 的基础设施漏洞,不是Keplr代码
• Bitquery统计:约600万美元转账,涉及4.4万+个Cosmos钱包;GoPlus称至少约100万美元被盗,另约600万被Web3Auth转入救援地址
• Keplr联合创始人估计约20%社交登录账户可能受影响
✅ 助记词钱包、硬件钱包不受影响
⚠️ 教训:
1️⃣ 社交登录=方便,但私钥托管在第三方,多了一个单点故障
2️⃣ 大额资产放硬件钱包/自己保管助记词
3️⃣ 余额变空不一定是被盗,可能已被转入救援地址,先看官方公告,别乱授权、别点陌生"找回"链接
你的钱包是社交登录还是助记词?评论区聊聊👇
$BTC $ETH $BNB #钱包安全 #Keplr #加密市场
仅为个人观点,不构成投资建议
16
·
--
ບົດຄວາມ
Keplr Wallet Security Incident: A Wake-Up Call for Crypto UsersKeplr's recent security incident has raised fresh concerns about social login wallets.
Between November 6 and 7, some Google and Apple login wallets were affected by a vulnerability involving Web3Auth.
Blockchain analytics firm Bitquery reported that over 44,000 wallets were involved, with approximately $6.01 million in assets transferred to two addresses.
However, some transfers were part of recovery efforts to protect remaining funds, not necessarily theft.
Keplr confirmed that recovery phrase and hardware wallets were not affected.
The incident highlights an important lesson: convenience should never come before control and security when managing crypto assets.
What do you think this incident teaches crypto users about wallet security? Share your thoughts in the comments.
Disclaimer: Do Your Own Research (DYOR) before making any investment decisions. This is not financial advice.
#Keplr #CryptoSecurity #Web3 #SelfCustody #Blockchain
Keplr Wallet Security Incident: A Wake-Up Call for Crypto Users
Keplr's recent security incident has raised fresh concerns about social login wallets.
Between November 6 and 7, some Google and Apple login wallets were affected by a vulnerability involving Web3Auth.
Blockchain analytics firm Bitquery reported that over 44,000 wallets were involved, with approximately $6.01 million in assets transferred to two addresses.
However, some transfers were part of recovery efforts to protect remaining funds, not necessarily theft.
Keplr confirmed that recovery phrase and hardware wallets were not affected.
The incident highlights an important lesson: convenience should never come before control and security when managing crypto assets.
What do you think this incident teaches crypto users about wallet security? Share your thoughts in the comments.
Disclaimer: Do Your Own Research (DYOR) before making any investment decisions. This is not financial advice.
#Keplr #CryptoSecurity #Web3 #SelfCustody #Blockchain
Between November 6 and 7, some Google and Apple login wallets were affected by a vulnerability involving Web3Auth.
Blockchain analytics firm Bitquery reported that over 44,000 wallets were involved, with approximately $6.01 million in assets transferred to two addresses.
However, some transfers were part of recovery efforts to protect remaining funds, not necessarily theft.
Keplr confirmed that recovery phrase and hardware wallets were not affected.
The incident highlights an important lesson: convenience should never come before control and security when managing crypto assets.
What do you think this incident teaches crypto users about wallet security? Share your thoughts in the comments.
Disclaimer: Do Your Own Research (DYOR) before making any investment decisions. This is not financial advice.
#Keplr #CryptoSecurity #Web3 #SelfCustody #Blockchain
324

Keplr Wallet has advised users who set up accounts via social logins (Google or Apple) to transfer their remaining assets due to an upstream security breach involving Web3Auth.
Key Security Update:
The Root Cause: An infrastructure flaw at Web3Auth—the third-party provider powering Keplr's embedded social login features—exposed private keys, leading to unauthorized transactions.
Who is Affected: Only accounts created using Google or Apple sign-ins are impacted. Wallets secured by a traditional seed phrase (recovery phrase) or a hardware wallet are completely unaffected.
Action Required: Keplr and security teams have urged affected users to stop depositing new funds and to transfer any remaining transferable assets to a newly secured wallet managed via a direct seed phrase or hardware device.
White-Hat Interventions: Note that some asset reductions or balance movements may also be part of authorized white-hat rescue missions launched to protect funds from malicious actors.
Safety Warning: Avoid clicking on unverified links or responding to direct messages offering "wallet recovery" assistance, as scammers are actively targeting affected users. Always rely strictly on updates published via Keplr's official channels.
#keplr #BunanceSquareTalk
Keplr Wallet has advised users who set up accounts via social logins (Google or Apple) to transfer their remaining assets due to an upstream security breach involving Web3Auth.
Key Security Update:
The Root Cause: An infrastructure flaw at Web3Auth—the third-party provider powering Keplr's embedded social login features—exposed private keys, leading to unauthorized transactions.
Who is Affected: Only accounts created using Google or Apple sign-ins are impacted. Wallets secured by a traditional seed phrase (recovery phrase) or a hardware wallet are completely unaffected.
Action Required: Keplr and security teams have urged affected users to stop depositing new funds and to transfer any remaining transferable assets to a newly secured wallet managed via a direct seed phrase or hardware device.
White-Hat Interventions: Note that some asset reductions or balance movements may also be part of authorized white-hat rescue missions launched to protect funds from malicious actors.
Safety Warning: Avoid clicking on unverified links or responding to direct messages offering "wallet recovery" assistance, as scammers are actively targeting affected users. Always rely strictly on updates published via Keplr's official channels.
#keplr #BunanceSquareTalk
Key Security Update:
The Root Cause: An infrastructure flaw at Web3Auth—the third-party provider powering Keplr's embedded social login features—exposed private keys, leading to unauthorized transactions.
Who is Affected: Only accounts created using Google or Apple sign-ins are impacted. Wallets secured by a traditional seed phrase (recovery phrase) or a hardware wallet are completely unaffected.
Action Required: Keplr and security teams have urged affected users to stop depositing new funds and to transfer any remaining transferable assets to a newly secured wallet managed via a direct seed phrase or hardware device.
White-Hat Interventions: Note that some asset reductions or balance movements may also be part of authorized white-hat rescue missions launched to protect funds from malicious actors.
Safety Warning: Avoid clicking on unverified links or responding to direct messages offering "wallet recovery" assistance, as scammers are actively targeting affected users. Always rely strictly on updates published via Keplr's official channels.
#keplr #BunanceSquareTalk
8

·
--
ບົດຄວາມ
Keplr 4.4万个钱包被掏,白帽用同一个漏洞抢跑救回560万美元11月6日深夜到7日,Keplr钱包出了一件很邪门的事。用谷歌或苹果账号登录建钱包的用户,私钥被人从Web3Auth的基础设施里翻了出来。Bitquery数过,4.4万多个钱包在18个小时里被掏,链上能对上的金额约601万美元。不过这个数里混着Web3Auth自己转走的救命钱,真正被黑客拿走多少还没法定数。更扎心的是其中一个数字,86%被掏的钱,是在Keplr发出警告之后才被转走的。警告发出去了,钥匙已经在别人手里,关登录根本拦不住。
先说清这次到底是谁的锅。Keplr联合创始人Josh Lee自己讲了,漏洞出在Web3Auth的基础设施,Keplr自己的代码没问题。用助记词建钱包、接硬件钱包的账户,这次没事,出事的是走谷歌或苹果一键登录的那批,大概占这类账户的两成。Web3Auth在6号晚上先认了服务有安全问题,暂停了嵌入式钱包服务,Keplr在7号凌晨4点38分发了警告,叫用户别再往这类账户里打钱。照Bitquery的统计,警告之后被掏的反而占了大多数,Cosmos Hub一条链上就被数出约350万美元。还有196万枚质押的ATOM,没走21天解绑期就被直接转走。
最值得写的一段,是后半程。Web3Auth发现私钥泄露的口子之后,没只顾着发公告,顺着同一个口子抢在黑客前面,把还没被掏的钱包里的钱先转出来。11月8日,它公布了12个回收地址,里面放着约560万美元。链上调查起初把其中8个地址当成了黑客的钱包,后来才确认那是Web3Auth自己的回收地址。Cosmos Hub那个回收地址里,光ATOM就有249万枚,约330万美元。漏洞本身不分好坏,谁先跑到,谁就先拿到钱。
对散户来说,教训不在Keplr,在自己手里的钱包是怎么建的。一键登录建钱包,图的是方便,代价是私钥不在自己手里,存在第三方服务商那里。服务商一出事,你连反应时间都没有,警告出来的时候,钱可能已经在路上了。还有一点容易被忽略,Web3Auth救回来的钱,官方没说什么时候、按什么流程还给用户,最终被偷走多少、根因到底是什么,到11月8日晚上都没公布。已经有人借着恢复资产的名义发钓鱼链接,Keplr和Web3Auth都提醒只认官方渠道。
我的观点就一句,钱包的钥匙只能在自己手里,一键登录的方便,迟早要拿真金白银还。
现在就打开你常用的钱包看一眼,它当初是助记词建的,还是谷歌或苹果一键登录建的?
#Keplr #Web3Auth #钱包安全 #安全复盘 #Cosmos
—— web3韭菜小凯
本文仅为个人观点分享,不构成任何投资建议,数据来源 The Block、Bitquery、Coinpaper、CryptoCompass 与公开报道,金额为链上追踪估值,行情随时变化,请自行判断风险。
Keplr 4.4万个钱包被掏,白帽用同一个漏洞抢跑救回560万美元
11月6日深夜到7日,Keplr钱包出了一件很邪门的事。用谷歌或苹果账号登录建钱包的用户,私钥被人从Web3Auth的基础设施里翻了出来。Bitquery数过,4.4万多个钱包在18个小时里被掏,链上能对上的金额约601万美元。不过这个数里混着Web3Auth自己转走的救命钱,真正被黑客拿走多少还没法定数。更扎心的是其中一个数字,86%被掏的钱,是在Keplr发出警告之后才被转走的。警告发出去了,钥匙已经在别人手里,关登录根本拦不住。
先说清这次到底是谁的锅。Keplr联合创始人Josh Lee自己讲了,漏洞出在Web3Auth的基础设施,Keplr自己的代码没问题。用助记词建钱包、接硬件钱包的账户,这次没事,出事的是走谷歌或苹果一键登录的那批,大概占这类账户的两成。Web3Auth在6号晚上先认了服务有安全问题,暂停了嵌入式钱包服务,Keplr在7号凌晨4点38分发了警告,叫用户别再往这类账户里打钱。照Bitquery的统计,警告之后被掏的反而占了大多数,Cosmos Hub一条链上就被数出约350万美元。还有196万枚质押的ATOM,没走21天解绑期就被直接转走。
最值得写的一段,是后半程。Web3Auth发现私钥泄露的口子之后,没只顾着发公告,顺着同一个口子抢在黑客前面,把还没被掏的钱包里的钱先转出来。11月8日,它公布了12个回收地址,里面放着约560万美元。链上调查起初把其中8个地址当成了黑客的钱包,后来才确认那是Web3Auth自己的回收地址。Cosmos Hub那个回收地址里,光ATOM就有249万枚,约330万美元。漏洞本身不分好坏,谁先跑到,谁就先拿到钱。
对散户来说,教训不在Keplr,在自己手里的钱包是怎么建的。一键登录建钱包,图的是方便,代价是私钥不在自己手里,存在第三方服务商那里。服务商一出事,你连反应时间都没有,警告出来的时候,钱可能已经在路上了。还有一点容易被忽略,Web3Auth救回来的钱,官方没说什么时候、按什么流程还给用户,最终被偷走多少、根因到底是什么,到11月8日晚上都没公布。已经有人借着恢复资产的名义发钓鱼链接,Keplr和Web3Auth都提醒只认官方渠道。
我的观点就一句,钱包的钥匙只能在自己手里,一键登录的方便,迟早要拿真金白银还。
现在就打开你常用的钱包看一眼,它当初是助记词建的,还是谷歌或苹果一键登录建的?
#Keplr #Web3Auth #钱包安全 #安全复盘 #Cosmos
—— web3韭菜小凯
本文仅为个人观点分享,不构成任何投资建议,数据来源 The Block、Bitquery、Coinpaper、CryptoCompass 与公开报道,金额为链上追踪估值,行情随时变化,请自行判断风险。
先说清这次到底是谁的锅。Keplr联合创始人Josh Lee自己讲了,漏洞出在Web3Auth的基础设施,Keplr自己的代码没问题。用助记词建钱包、接硬件钱包的账户,这次没事,出事的是走谷歌或苹果一键登录的那批,大概占这类账户的两成。Web3Auth在6号晚上先认了服务有安全问题,暂停了嵌入式钱包服务,Keplr在7号凌晨4点38分发了警告,叫用户别再往这类账户里打钱。照Bitquery的统计,警告之后被掏的反而占了大多数,Cosmos Hub一条链上就被数出约350万美元。还有196万枚质押的ATOM,没走21天解绑期就被直接转走。
最值得写的一段,是后半程。Web3Auth发现私钥泄露的口子之后,没只顾着发公告,顺着同一个口子抢在黑客前面,把还没被掏的钱包里的钱先转出来。11月8日,它公布了12个回收地址,里面放着约560万美元。链上调查起初把其中8个地址当成了黑客的钱包,后来才确认那是Web3Auth自己的回收地址。Cosmos Hub那个回收地址里,光ATOM就有249万枚,约330万美元。漏洞本身不分好坏,谁先跑到,谁就先拿到钱。
对散户来说,教训不在Keplr,在自己手里的钱包是怎么建的。一键登录建钱包,图的是方便,代价是私钥不在自己手里,存在第三方服务商那里。服务商一出事,你连反应时间都没有,警告出来的时候,钱可能已经在路上了。还有一点容易被忽略,Web3Auth救回来的钱,官方没说什么时候、按什么流程还给用户,最终被偷走多少、根因到底是什么,到11月8日晚上都没公布。已经有人借着恢复资产的名义发钓鱼链接,Keplr和Web3Auth都提醒只认官方渠道。
我的观点就一句,钱包的钥匙只能在自己手里,一键登录的方便,迟早要拿真金白银还。
现在就打开你常用的钱包看一眼,它当初是助记词建的,还是谷歌或苹果一键登录建的?
#Keplr #Web3Auth #钱包安全 #安全复盘 #Cosmos
—— web3韭菜小凯
本文仅为个人观点分享,不构成任何投资建议,数据来源 The Block、Bitquery、Coinpaper、CryptoCompass 与公开报道,金额为链上追踪估值,行情随时变化,请自行判断风险。
34
·
--
#KeplrAdvisesSocialLoginUsersToTransferAssets
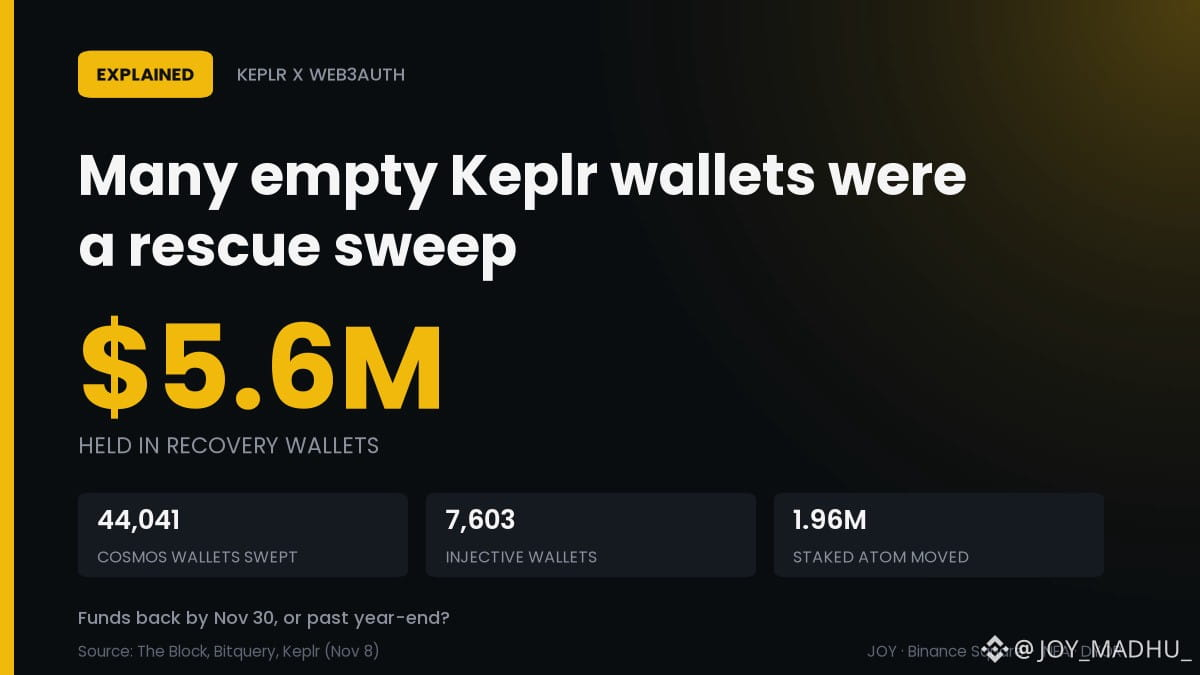
🛟 52K Keplr Wallets Swept. Much of It Was the Rescue
Web3Auth says it emptied exposed social-login wallets before the attacker could.
📊 About $5.6M sits in 12 Web3Auth recovery addresses
📉 44,041 Cosmos and 7,603 Injective wallets swept Nov 6-7
⚠️ 1.96M staked ATOM skipped the 21-day unbonding wait
📅 No return date yet for the held funds
The catch: the attacker's total is still undisclosed.
$5.6M returned by Nov 30, or past year-end? 👇
$ATOM $INJ
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Web3Auth
#KeplrAdvisesSocialLoginUsersToTransferAssets
🛟 52K Keplr Wallets Swept. Much of It Was the Rescue
Web3Auth says it emptied exposed social-login wallets before the attacker could.
📊 About $5.6M sits in 12 Web3Auth recovery addresses
📉 44,041 Cosmos and 7,603 Injective wallets swept Nov 6-7
⚠️ 1.96M staked ATOM skipped the 21-day unbonding wait
📅 No return date yet for the held funds
The catch: the attacker's total is still undisclosed.
$5.6M returned by Nov 30, or past year-end? 👇
$ATOM $INJ
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Web3Auth
🛟 52K Keplr Wallets Swept. Much of It Was the Rescue
Web3Auth says it emptied exposed social-login wallets before the attacker could.
📊 About $5.6M sits in 12 Web3Auth recovery addresses
📉 44,041 Cosmos and 7,603 Injective wallets swept Nov 6-7
⚠️ 1.96M staked ATOM skipped the 21-day unbonding wait
📅 No return date yet for the held funds
The catch: the attacker's total is still undisclosed.
$5.6M returned by Nov 30, or past year-end? 👇
$ATOM $INJ
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Web3Auth
44
·
--
用 Google 或 Apple 登录创建 Keplr 钱包的用户,损失有了数字:GoPlus 11 月 9 日监测,至少约 100 万美元资产被盗,另有约 600 万美元被转进官方确认的救援地址。助记词和硬件钱包用户不受影响。
用社交登录建钱包,钥匙就有一部分不在自己手上。你的 Keplr 钱包,当初是哪种方式建的?
#加密安全 #Keplr
用 Google 或 Apple 登录创建 Keplr 钱包的用户,损失有了数字:GoPlus 11 月 9 日监测,至少约 100 万美元资产被盗,另有约 600 万美元被转进官方确认的救援地址。助记词和硬件钱包用户不受影响。
用社交登录建钱包,钥匙就有一部分不在自己手上。你的 Keplr 钱包,当初是哪种方式建的?
#加密安全 #Keplr
用社交登录建钱包,钥匙就有一部分不在自己手上。你的 Keplr 钱包,当初是哪种方式建的?
#加密安全 #Keplr
6
·
--
Keplr 社交登录私钥泄露:560 万美元转入恢复地址,ATOM 跌 3.6%Web3Auth 基础设施漏洞波及 Keplr 钱包。Odaily 引官方更新称,部分通过 Google 或 Apple 登录创建的 Keplr 钱包私钥泄露;Web3Auth 已抢先把约 560 万美元资产转到安全地址,12 个恢复地址中含约 249 万枚 ATOM,价值约 330 万美元。
另有至少约 601 万美元跨链转账流经相关地址,实际损失尚未核实。Keplr 联合创始人 Josh Lee 估计,约 20% 的 Google、Apple 登录账户受影响,真正被利用的只是其中一小部分。Keplr 建议用户停止充值,把剩余资产转到助记词或硬件钱包,质押和锁定资产处置会更慢。
币安 11 月 9 日 12:58 快照:ATOM 1.318 美元(-3.584%),24 小时区间 1.27—1.37。个人观点:若 4 小时收回 1.335 并回踩 1.30 不破,可试多,目标 1.37、1.43,止损 1.27;跌破 1.27 且反抽不过,看 1.22、1.18,止损 1.335。
后续看损失最终认定、受影响钱包恢复进度,以及 ATOM 能否重新站上 1.37。若安全事件只影响社交登录子集且资金持续追回,抛压会缓和;若损失扩大,钱包信任与 Cosmos 资产需求会承压。你还敢用社交登录管理链上资产吗?
$ATOM
#Keplr #Web3Auth #钱包安全 #ATOM
以上内容不构成投资建议
Keplr 社交登录私钥泄露:560 万美元转入恢复地址,ATOM 跌 3.6%
Web3Auth 基础设施漏洞波及 Keplr 钱包。Odaily 引官方更新称,部分通过 Google 或 Apple 登录创建的 Keplr 钱包私钥泄露;Web3Auth 已抢先把约 560 万美元资产转到安全地址,12 个恢复地址中含约 249 万枚 ATOM,价值约 330 万美元。
另有至少约 601 万美元跨链转账流经相关地址,实际损失尚未核实。Keplr 联合创始人 Josh Lee 估计,约 20% 的 Google、Apple 登录账户受影响,真正被利用的只是其中一小部分。Keplr 建议用户停止充值,把剩余资产转到助记词或硬件钱包,质押和锁定资产处置会更慢。
币安 11 月 9 日 12:58 快照:ATOM 1.318 美元(-3.584%),24 小时区间 1.27—1.37。个人观点:若 4 小时收回 1.335 并回踩 1.30 不破,可试多,目标 1.37、1.43,止损 1.27;跌破 1.27 且反抽不过,看 1.22、1.18,止损 1.335。
后续看损失最终认定、受影响钱包恢复进度,以及 ATOM 能否重新站上 1.37。若安全事件只影响社交登录子集且资金持续追回,抛压会缓和;若损失扩大,钱包信任与 Cosmos 资产需求会承压。你还敢用社交登录管理链上资产吗?
$ATOM
#Keplr #Web3Auth #钱包安全 #ATOM
以上内容不构成投资建议
另有至少约 601 万美元跨链转账流经相关地址,实际损失尚未核实。Keplr 联合创始人 Josh Lee 估计,约 20% 的 Google、Apple 登录账户受影响,真正被利用的只是其中一小部分。Keplr 建议用户停止充值,把剩余资产转到助记词或硬件钱包,质押和锁定资产处置会更慢。
币安 11 月 9 日 12:58 快照:ATOM 1.318 美元(-3.584%),24 小时区间 1.27—1.37。个人观点:若 4 小时收回 1.335 并回踩 1.30 不破,可试多,目标 1.37、1.43,止损 1.27;跌破 1.27 且反抽不过,看 1.22、1.18,止损 1.335。
后续看损失最终认定、受影响钱包恢复进度,以及 ATOM 能否重新站上 1.37。若安全事件只影响社交登录子集且资金持续追回,抛压会缓和;若损失扩大,钱包信任与 Cosmos 资产需求会承压。你还敢用社交登录管理链上资产吗?
$ATOM
#Keplr #Web3Auth #钱包安全 #ATOM
以上内容不构成投资建议
175

·
--
« Se connecter avec Google » sur un wallet crypto, c'est pratique. Ce week-end, on a vu le prix de ce confort.
Keplr, un wallet très utilisé dans l'écosystème Cosmos, a suspendu samedi la connexion via Google et Apple. Des utilisateurs voyaient partir des fonds sans avoir rien signé. La faille ne venait pas de Keplr mais de Web3Auth, le service (propriété de Consensys, l'éditeur de MetaMask) qui gère ces connexions « sociales ».
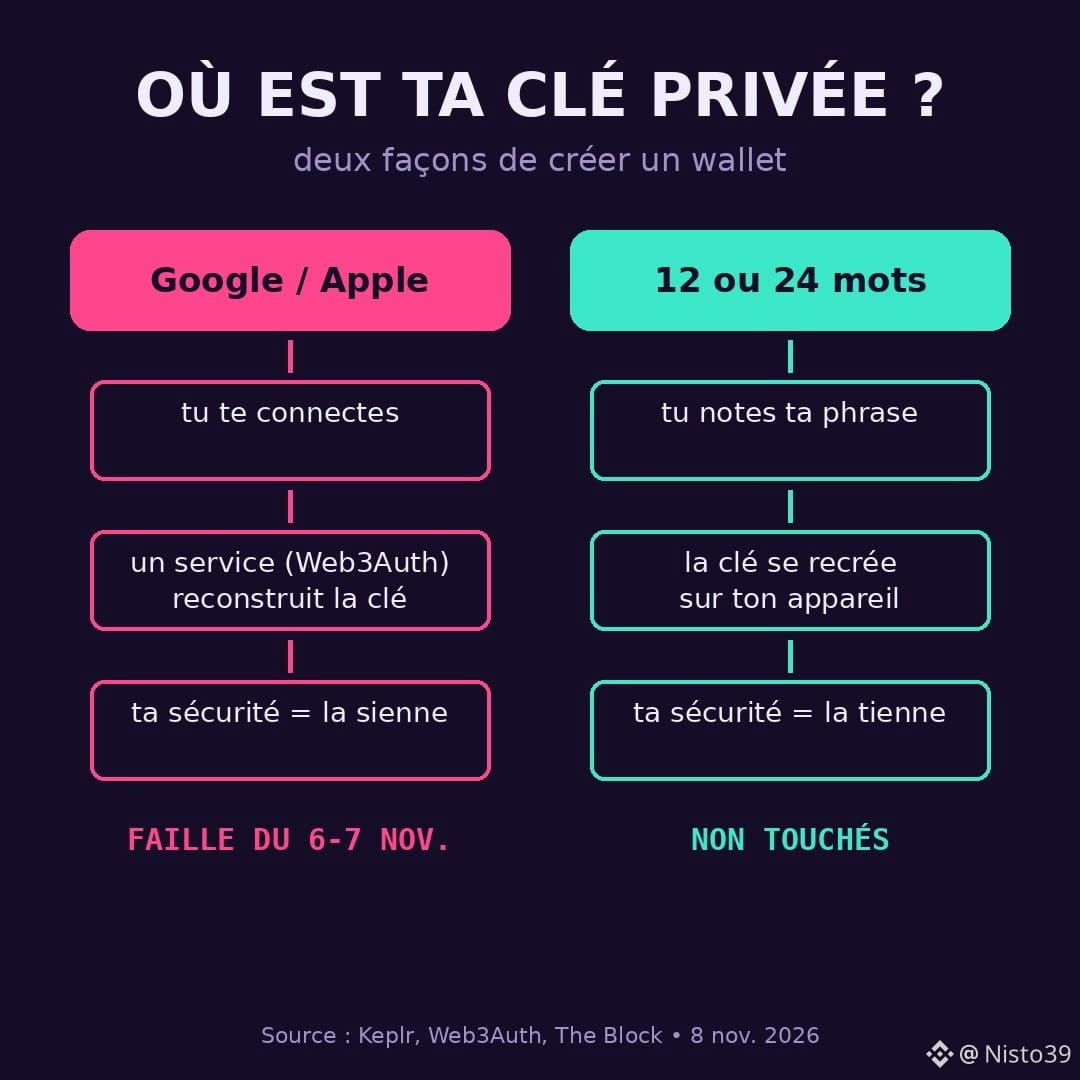
Un wallet, c'est une clé privée, un secret qui signe chaque paiement. Avec la connexion sociale, tu ne vois jamais ce secret. Un service le reconstitue pour toi à chaque connexion. Si ce service a un trou, ta clé aussi.
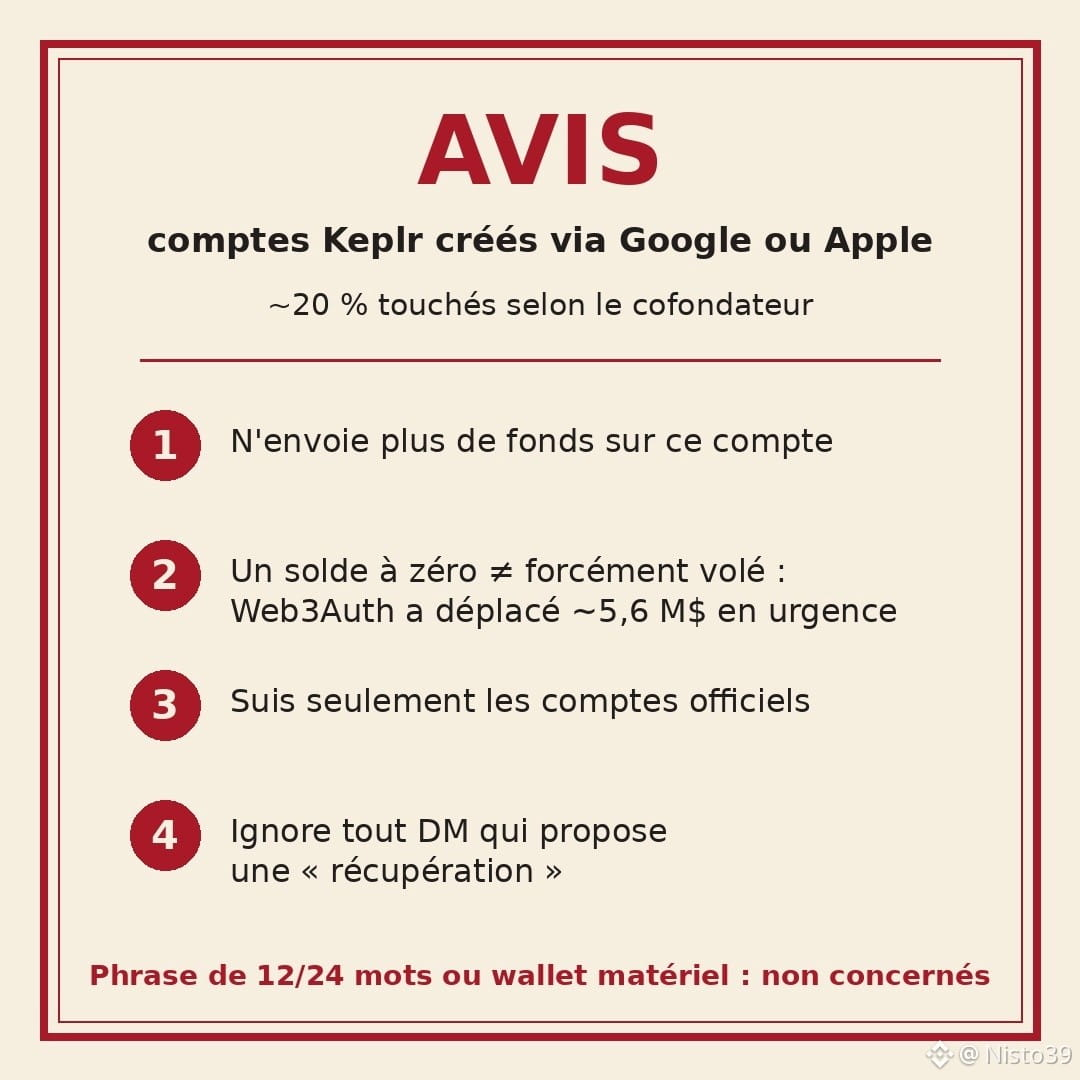
Les chiffres connus : environ 20 % des comptes Keplr créés via Google ou Apple seraient touchés, selon le cofondateur Josh Lee. Web3Auth dit avoir vidé en urgence des wallets exposés avant l'attaquant, en passant par le même chemin. Dimanche, ses 12 adresses de récupération contenaient environ 5,6 millions de dollars (The Block). Donc un solde à zéro ne veut pas forcément dire « volé ». Ni « sauvé ».
Pas touchés : les wallets créés avec une phrase de récupération (12 ou 24 mots) ou un wallet matériel.
Ce que je retiens : la connexion sociale n'est pas une arnaque, c'est un compromis. Tu échanges la peur de perdre tes 12 mots contre une dépendance à une entreprise. Des détenteurs de $ATOM et $INJ viennent de le découvrir.
Si tu es concerné : n'envoie plus rien sur ce compte, suis uniquement les comptes officiels de Keplr et Web3Auth, et ignore tout message privé qui propose une « récupération ».
Sources : The Block, Keplr, Web3Auth, 7-8 nov. 2026. Pas un conseil financier.
Tu préfères risquer d'oublier 12 mots, ou dépendre d'un service que tu ne contrôles pas ?
#Keplr #Web3Auth #CryptoSecurity #Cosmos #CryptoNews
« Se connecter avec Google » sur un wallet crypto, c'est pratique. Ce week-end, on a vu le prix de ce confort.
Keplr, un wallet très utilisé dans l'écosystème Cosmos, a suspendu samedi la connexion via Google et Apple. Des utilisateurs voyaient partir des fonds sans avoir rien signé. La faille ne venait pas de Keplr mais de Web3Auth, le service (propriété de Consensys, l'éditeur de MetaMask) qui gère ces connexions « sociales ».
Un wallet, c'est une clé privée, un secret qui signe chaque paiement. Avec la connexion sociale, tu ne vois jamais ce secret. Un service le reconstitue pour toi à chaque connexion. Si ce service a un trou, ta clé aussi.
Les chiffres connus : environ 20 % des comptes Keplr créés via Google ou Apple seraient touchés, selon le cofondateur Josh Lee. Web3Auth dit avoir vidé en urgence des wallets exposés avant l'attaquant, en passant par le même chemin. Dimanche, ses 12 adresses de récupération contenaient environ 5,6 millions de dollars (The Block). Donc un solde à zéro ne veut pas forcément dire « volé ». Ni « sauvé ».
Pas touchés : les wallets créés avec une phrase de récupération (12 ou 24 mots) ou un wallet matériel.
Ce que je retiens : la connexion sociale n'est pas une arnaque, c'est un compromis. Tu échanges la peur de perdre tes 12 mots contre une dépendance à une entreprise. Des détenteurs de $ATOM et $INJ viennent de le découvrir.
Si tu es concerné : n'envoie plus rien sur ce compte, suis uniquement les comptes officiels de Keplr et Web3Auth, et ignore tout message privé qui propose une « récupération ».
Sources : The Block, Keplr, Web3Auth, 7-8 nov. 2026. Pas un conseil financier.
Tu préfères risquer d'oublier 12 mots, ou dépendre d'un service que tu ne contrôles pas ?
#Keplr #Web3Auth #CryptoSecurity #Cosmos #CryptoNews
Keplr, un wallet très utilisé dans l'écosystème Cosmos, a suspendu samedi la connexion via Google et Apple. Des utilisateurs voyaient partir des fonds sans avoir rien signé. La faille ne venait pas de Keplr mais de Web3Auth, le service (propriété de Consensys, l'éditeur de MetaMask) qui gère ces connexions « sociales ».
Un wallet, c'est une clé privée, un secret qui signe chaque paiement. Avec la connexion sociale, tu ne vois jamais ce secret. Un service le reconstitue pour toi à chaque connexion. Si ce service a un trou, ta clé aussi.
Les chiffres connus : environ 20 % des comptes Keplr créés via Google ou Apple seraient touchés, selon le cofondateur Josh Lee. Web3Auth dit avoir vidé en urgence des wallets exposés avant l'attaquant, en passant par le même chemin. Dimanche, ses 12 adresses de récupération contenaient environ 5,6 millions de dollars (The Block). Donc un solde à zéro ne veut pas forcément dire « volé ». Ni « sauvé ».
Pas touchés : les wallets créés avec une phrase de récupération (12 ou 24 mots) ou un wallet matériel.
Ce que je retiens : la connexion sociale n'est pas une arnaque, c'est un compromis. Tu échanges la peur de perdre tes 12 mots contre une dépendance à une entreprise. Des détenteurs de $ATOM et $INJ viennent de le découvrir.
Si tu es concerné : n'envoie plus rien sur ce compte, suis uniquement les comptes officiels de Keplr et Web3Auth, et ignore tout message privé qui propose une « récupération ».
Sources : The Block, Keplr, Web3Auth, 7-8 nov. 2026. Pas un conseil financier.
Tu préfères risquer d'oublier 12 mots, ou dépendre d'un service que tu ne contrôles pas ?
#Keplr #Web3Auth #CryptoSecurity #Cosmos #CryptoNews
1
408
·
--
昨天刷到一条挺炸的新闻,同步一下 👀
Consensys 旗下的 Web3Auth(给 Keplr 做 Google/Apple 登录的那个)承认系统有漏洞,导致部分用 Google/Apple 注册的 Keplr 钱包私钥泄露。他们抢在攻击者前面把资金挪进 12 个恢复地址,链上数据显示现在共约 560 万美元。
关键数字:
· Bitquery:攻击者从 4 万多个 Keplr 钱包转走约 600 万美元
· Keplr 联创 Josh Lee:约 20% 的 Google/Apple 登录账户受影响(助记词/硬件钱包用户没事)
· 恢复资金大头是 ATOM,约 249 万枚、价值 330 万美元,多为质押状态,被换成可即时转走的代币,避开 21 天解质押期
看法:「第三方登录=托管私钥」平时图方便,出事就是灾难。后续盯两点:560 万怎么还给用户,Keplr 会不会换登录方案。
你用 Keplr 吗?哪种登录方式?评论区聊聊 🗣️
#Web3安全 #Keplr #Web3Auth
昨天刷到一条挺炸的新闻,同步一下 👀
Consensys 旗下的 Web3Auth(给 Keplr 做 Google/Apple 登录的那个)承认系统有漏洞,导致部分用 Google/Apple 注册的 Keplr 钱包私钥泄露。他们抢在攻击者前面把资金挪进 12 个恢复地址,链上数据显示现在共约 560 万美元。
关键数字:
· Bitquery:攻击者从 4 万多个 Keplr 钱包转走约 600 万美元
· Keplr 联创 Josh Lee:约 20% 的 Google/Apple 登录账户受影响(助记词/硬件钱包用户没事)
· 恢复资金大头是 ATOM,约 249 万枚、价值 330 万美元,多为质押状态,被换成可即时转走的代币,避开 21 天解质押期
看法:「第三方登录=托管私钥」平时图方便,出事就是灾难。后续盯两点:560 万怎么还给用户,Keplr 会不会换登录方案。
你用 Keplr 吗?哪种登录方式?评论区聊聊 🗣️
#Web3安全 #Keplr #Web3Auth
Consensys 旗下的 Web3Auth(给 Keplr 做 Google/Apple 登录的那个)承认系统有漏洞,导致部分用 Google/Apple 注册的 Keplr 钱包私钥泄露。他们抢在攻击者前面把资金挪进 12 个恢复地址,链上数据显示现在共约 560 万美元。
关键数字:
· Bitquery:攻击者从 4 万多个 Keplr 钱包转走约 600 万美元
· Keplr 联创 Josh Lee:约 20% 的 Google/Apple 登录账户受影响(助记词/硬件钱包用户没事)
· 恢复资金大头是 ATOM,约 249 万枚、价值 330 万美元,多为质押状态,被换成可即时转走的代币,避开 21 天解质押期
看法:「第三方登录=托管私钥」平时图方便,出事就是灾难。后续盯两点:560 万怎么还给用户,Keplr 会不会换登录方案。
你用 Keplr 吗?哪种登录方式?评论区聊聊 🗣️
#Web3安全 #Keplr #Web3Auth
484
·
--
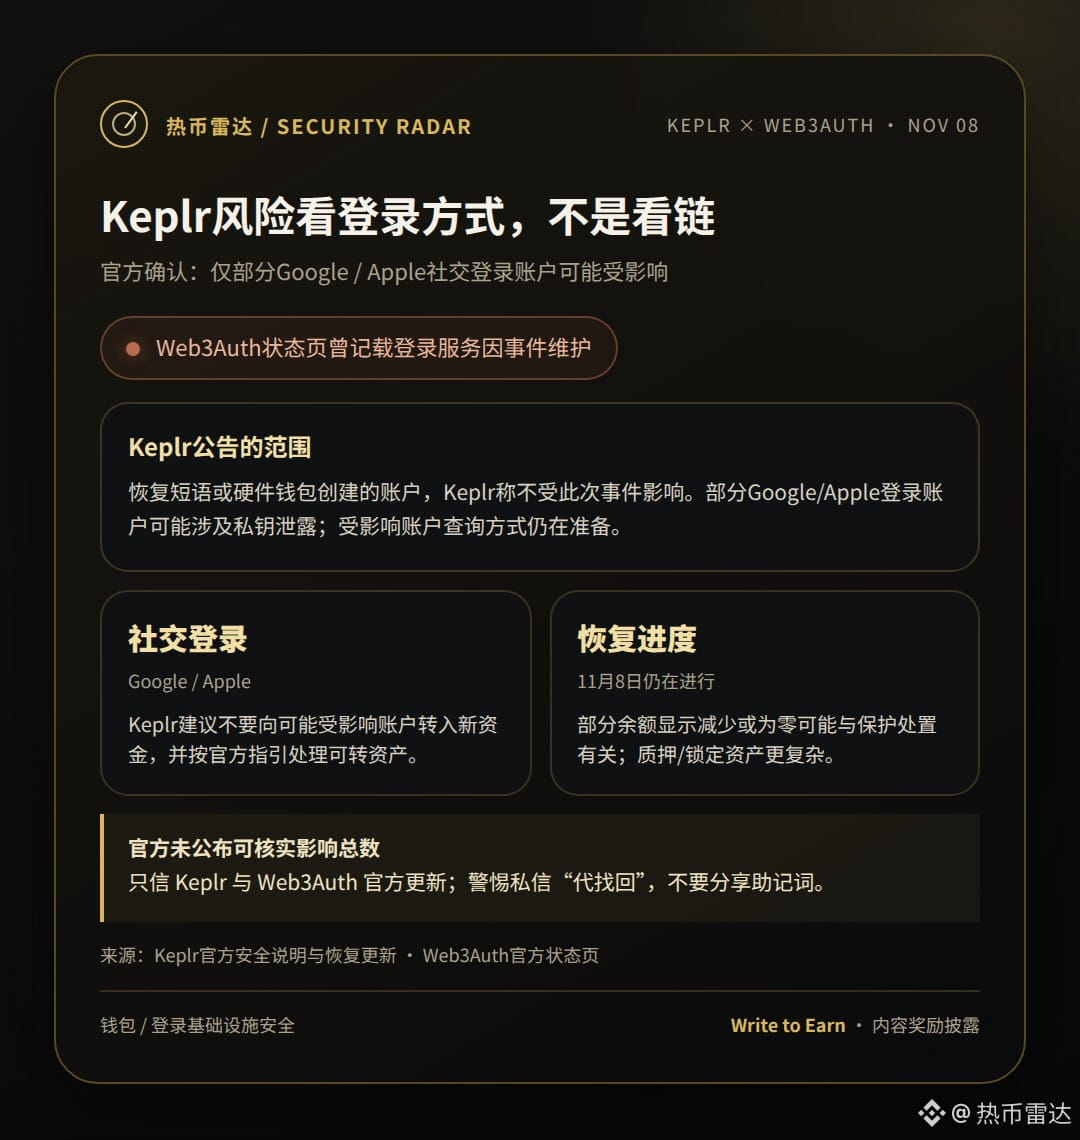
Keplr这次风险要看登录方式,不是“所有钱包都中招”:Keplr称,用恢复短语或硬件钱包创建的账户不受此次事件影响;部分Google/Apple社交登录账户可能涉及私钥泄露。
Keplr已提醒这类用户不要再向该账户转入新资金,并按官方指引处理剩余可转资产;部分余额变少或归零可能与保护处置有关,质押/锁定资产处理更慢。Keplr 11月8日仍称恢复工作在继续,受影响账户查询方式尚在准备;官方未公布可核实的受影响账户总数或损失额。
只信Keplr与Web3Auth官方更新,警惕私信“代找回”。你希望钱包在哪一步明确说明社交登录的密钥安全风险?
来源:[Keplr官方说明](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr恢复进度](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth状态页](https://status.web3auth.io/events/maintenance/461)
披露:本帖可能符合 Binance Square Write to Earn 内容奖励资格;资格与奖励以平台规则及实际结果为准。非投资建议。
#Keplr #Web3Auth #安全
Keplr这次风险要看登录方式,不是“所有钱包都中招”:Keplr称,用恢复短语或硬件钱包创建的账户不受此次事件影响;部分Google/Apple社交登录账户可能涉及私钥泄露。
Keplr已提醒这类用户不要再向该账户转入新资金,并按官方指引处理剩余可转资产;部分余额变少或归零可能与保护处置有关,质押/锁定资产处理更慢。Keplr 11月8日仍称恢复工作在继续,受影响账户查询方式尚在准备;官方未公布可核实的受影响账户总数或损失额。
只信Keplr与Web3Auth官方更新,警惕私信“代找回”。你希望钱包在哪一步明确说明社交登录的密钥安全风险?
来源:[Keplr官方说明](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr恢复进度](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth状态页](https://status.web3auth.io/events/maintenance/461)
披露:本帖可能符合 Binance Square Write to Earn 内容奖励资格;资格与奖励以平台规则及实际结果为准。非投资建议。
#Keplr #Web3Auth #安全
Keplr已提醒这类用户不要再向该账户转入新资金,并按官方指引处理剩余可转资产;部分余额变少或归零可能与保护处置有关,质押/锁定资产处理更慢。Keplr 11月8日仍称恢复工作在继续,受影响账户查询方式尚在准备;官方未公布可核实的受影响账户总数或损失额。
只信Keplr与Web3Auth官方更新,警惕私信“代找回”。你希望钱包在哪一步明确说明社交登录的密钥安全风险?
来源:[Keplr官方说明](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr恢复进度](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth状态页](https://status.web3auth.io/events/maintenance/461)
披露:本帖可能符合 Binance Square Write to Earn 内容奖励资格;资格与奖励以平台规则及实际结果为准。非投资建议。
#Keplr #Web3Auth #安全
81

Web3Auth Frontran Hackers: $5.6M Moved from Keplr Wallets
- Web3Auth báo cáo chuyển $5.6 triệu từ ví Keplr bị lộ
- Hacker được gọi là "người tấn công ban đầu"
- Một số quỹ bị đánh cắp nhưng chi tiết chưa được giải thích
#BinanceSquare #CryptoNews #Web3 #Keplr
$btc $eth
#vlikevn Titanbot
Nguồn: The Block
Web3Auth Frontran Hackers: $5.6M Moved from Keplr Wallets
- Web3Auth báo cáo chuyển $5.6 triệu từ ví Keplr bị lộ
- Hacker được gọi là "người tấn công ban đầu"
- Một số quỹ bị đánh cắp nhưng chi tiết chưa được giải thích
#BinanceSquare #CryptoNews #Web3 #Keplr
$btc $eth
#vlikevn Titanbot
Nguồn: The Block
- Web3Auth báo cáo chuyển $5.6 triệu từ ví Keplr bị lộ
- Hacker được gọi là "người tấn công ban đầu"
- Một số quỹ bị đánh cắp nhưng chi tiết chưa được giải thích
#BinanceSquare #CryptoNews #Web3 #Keplr
$btc $eth
#vlikevn Titanbot
Nguồn: The Block
35
·
--
Keplr余额减少,别把保护性转移全算成被盗
用Google或Apple创建Keplr钱包的用户,先停止向该账户转入资金。余额归零既不能直接认定全部被盗,也不代表资产已经退回,关键是核对资金去向和后续返还安排。
11月7日,Keplr称Web3Auth基础设施漏洞导致部分社交登录用户的私钥暴露;用助记词或硬件钱包创建的账户,据其初步说明不受这次事件影响。不要把风险扩大成所有Keplr钱包都出了问题。
11月8日,Web3Auth公布保护性转移所用的恢复地址,称部分转账被误认为攻击者操作。The Block当天核查称,这些地址在报道时持有约560万美元资产。这是恢复地址里的资产估值,不是最终被盗额,更不是已经退给用户的钱。
所以,要同时看见两件事:部分余额减少可能是保护性转移,但私钥暴露和用户暂时无法支配资产的风险,并未因此消失。Keplr建议把仍可转移的流动资产迁至助记词或硬件钱包账户;质押、锁定资产处置更复杂,不应照搬流动资产的处理进度。
接下来两三天,核对官方受影响账户查询、恢复地址更新和返还流程;这只是观察窗口,不是退款承诺。只有范围明确、返还可核验,才下调风险;若出现名单外异常转移或影响扩大,就上调风险。只从已知官方入口查进展,不点击私信提供的“恢复”链接。
#Keplr #Web3Auth #钱包安全
Keplr余额减少,别把保护性转移全算成被盗
用Google或Apple创建Keplr钱包的用户,先停止向该账户转入资金。余额归零既不能直接认定全部被盗,也不代表资产已经退回,关键是核对资金去向和后续返还安排。
11月7日,Keplr称Web3Auth基础设施漏洞导致部分社交登录用户的私钥暴露;用助记词或硬件钱包创建的账户,据其初步说明不受这次事件影响。不要把风险扩大成所有Keplr钱包都出了问题。
11月8日,Web3Auth公布保护性转移所用的恢复地址,称部分转账被误认为攻击者操作。The Block当天核查称,这些地址在报道时持有约560万美元资产。这是恢复地址里的资产估值,不是最终被盗额,更不是已经退给用户的钱。
所以,要同时看见两件事:部分余额减少可能是保护性转移,但私钥暴露和用户暂时无法支配资产的风险,并未因此消失。Keplr建议把仍可转移的流动资产迁至助记词或硬件钱包账户;质押、锁定资产处置更复杂,不应照搬流动资产的处理进度。
接下来两三天,核对官方受影响账户查询、恢复地址更新和返还流程;这只是观察窗口,不是退款承诺。只有范围明确、返还可核验,才下调风险;若出现名单外异常转移或影响扩大,就上调风险。只从已知官方入口查进展,不点击私信提供的“恢复”链接。
#Keplr #Web3Auth #钱包安全
用Google或Apple创建Keplr钱包的用户,先停止向该账户转入资金。余额归零既不能直接认定全部被盗,也不代表资产已经退回,关键是核对资金去向和后续返还安排。
11月7日,Keplr称Web3Auth基础设施漏洞导致部分社交登录用户的私钥暴露;用助记词或硬件钱包创建的账户,据其初步说明不受这次事件影响。不要把风险扩大成所有Keplr钱包都出了问题。
11月8日,Web3Auth公布保护性转移所用的恢复地址,称部分转账被误认为攻击者操作。The Block当天核查称,这些地址在报道时持有约560万美元资产。这是恢复地址里的资产估值,不是最终被盗额,更不是已经退给用户的钱。
所以,要同时看见两件事:部分余额减少可能是保护性转移,但私钥暴露和用户暂时无法支配资产的风险,并未因此消失。Keplr建议把仍可转移的流动资产迁至助记词或硬件钱包账户;质押、锁定资产处置更复杂,不应照搬流动资产的处理进度。
接下来两三天,核对官方受影响账户查询、恢复地址更新和返还流程;这只是观察窗口,不是退款承诺。只有范围明确、返还可核验,才下调风险;若出现名单外异常转移或影响扩大,就上调风险。只从已知官方入口查进展,不点击私信提供的“恢复”链接。
#Keplr #Web3Auth #钱包安全
79
·
--
Web3Auth把Keplr钱包里的币转走了:是救援还是被盗?
Keplr社交登录事件有后续。Web3Auth北京时间11月8日14:23发帖称,正在Keplr协助下,把受影响钱包的资产转进安全的恢复钱包。
它还专门澄清:有些转账被外界当成了攻击者操作,其实是救援;随后公布一份“已验证恢复地址”清单,覆盖Cosmos Hub、Osmosis、Celestia、Injective、dYdX等网络,外加一个EVM地址(称覆盖8条链),并说清单会继续更新。Keplr官方也转发确认,这些是恢复地址,不是攻击地址。
几件事分清:
1. 余额被转走,先对照官方清单里的收款地址,别凭感觉认定被盗。
2. 两方目前仍没公布受影响钱包数和损失金额,网上流传的数字先别当真。
3. 官方提醒只认官方渠道;私信里主动“帮你找回资产”的,一律按骗子处理。
CZ也转发提醒:用过“社交登录”钱包的人,该好好研究这件事。自托管就是自己负责,包括搞清楚钥匙到底在谁手里。
#Keplr #钱包安全 #Web3Auth
Web3Auth把Keplr钱包里的币转走了:是救援还是被盗?
Keplr社交登录事件有后续。Web3Auth北京时间11月8日14:23发帖称,正在Keplr协助下,把受影响钱包的资产转进安全的恢复钱包。
它还专门澄清:有些转账被外界当成了攻击者操作,其实是救援;随后公布一份“已验证恢复地址”清单,覆盖Cosmos Hub、Osmosis、Celestia、Injective、dYdX等网络,外加一个EVM地址(称覆盖8条链),并说清单会继续更新。Keplr官方也转发确认,这些是恢复地址,不是攻击地址。
几件事分清:
1. 余额被转走,先对照官方清单里的收款地址,别凭感觉认定被盗。
2. 两方目前仍没公布受影响钱包数和损失金额,网上流传的数字先别当真。
3. 官方提醒只认官方渠道;私信里主动“帮你找回资产”的,一律按骗子处理。
CZ也转发提醒:用过“社交登录”钱包的人,该好好研究这件事。自托管就是自己负责,包括搞清楚钥匙到底在谁手里。
#Keplr #钱包安全 #Web3Auth
Keplr社交登录事件有后续。Web3Auth北京时间11月8日14:23发帖称,正在Keplr协助下,把受影响钱包的资产转进安全的恢复钱包。
它还专门澄清:有些转账被外界当成了攻击者操作,其实是救援;随后公布一份“已验证恢复地址”清单,覆盖Cosmos Hub、Osmosis、Celestia、Injective、dYdX等网络,外加一个EVM地址(称覆盖8条链),并说清单会继续更新。Keplr官方也转发确认,这些是恢复地址,不是攻击地址。
几件事分清:
1. 余额被转走,先对照官方清单里的收款地址,别凭感觉认定被盗。
2. 两方目前仍没公布受影响钱包数和损失金额,网上流传的数字先别当真。
3. 官方提醒只认官方渠道;私信里主动“帮你找回资产”的,一律按骗子处理。
CZ也转发提醒:用过“社交登录”钱包的人,该好好研究这件事。自托管就是自己负责,包括搞清楚钥匙到底在谁手里。
#Keplr #钱包安全 #Web3Auth
55
ເຂົ້າສູ່ລະບົບເພື່ອສຳຫຼວດເນື້ອຫາເພີ່ມເຕີມ
ເຂົ້າຮ່ວມກຸ່ມຜູ້ໃຊ້ຄຣິບໂຕທົ່ວໂລກໃນ Binance Square.
⚡️ ໄດ້ຮັບຂໍ້ມູນຫຼ້າສຸດ ແລະ ທີ່ມີປະໂຫຍດກ່ຽວກັບຄຣິບໂຕ.
💬 ໄດ້ຮັບຄວາມໄວ້ວາງໃຈຈາກຕະຫຼາດແລກປ່ຽນຄຣິບໂຕທີ່ໃຫຍ່ທີ່ສຸດໃນໂລກ.
👍 ຄົ້ນຫາຂໍ້ມູນເຊີງເລິກທີ່ແທ້ຈາກນັກສ້າງທີ່ໄດ້ຮັບການຢືນຢັນ.
ອີເມວ / ເບີໂທລະສັບ
ຫົວຂໍ້ທີ່ກໍາລັງນິຍົມ
1
#A Packed Week of Earnings and Data Tests Markets
56,914 ຄັ້ງທີ່ເບິ່ງ
379 ກຳລັງສົນທະນາ
2
#AnthropicIPOTestsInvestorAppetiteForAI
102,217 ຄັ້ງທີ່ເບິ່ງ
1,299 ກຳລັງສົນທະນາ
3
#BitcoinExtendsLosingStreakToSixWeeks
70,995 ຄັ້ງທີ່ເບິ່ງ
657 ກຳລັງສົນທະນາ
4
#XRPFallsTo$0.89LowestSinceNovember2024
12,025 ຄັ້ງທີ່ເບິ່ງ
65 ກຳລັງສົນທະນາ
5
#HuangReportedlyConsidersReturnToNvidia
110,337 ຄັ້ງທີ່ເບິ່ງ
1,187 ກຳລັງສົນທະນາ
6
#SP500AndNasdaqFuturesHitQuarterlyLows
19,854 ຄັ້ງທີ່ເບິ່ງ
215 ກຳລັງສົນທະນາ
7
#CaliforniaVotersBackProp42BarringNewCryptoTaxes
14,279 ຄັ້ງທີ່ເບິ່ງ
210 ກຳລັງສົນທະນາ
8
#HKPlansDigitalAssetRegulatoryBillByYearEnd
13,019 ຄັ້ງທີ່ເບິ່ງ
147 ກຳລັງສົນທະນາ
9
#MUFGSMFGMizuhoPlanYenBackedStablecoin
28,173 ຄັ້ງທີ່ເບິ່ງ
275 ກຳລັງສົນທະນາ
10
#HKMAAndSwiftExploreTokenizedDepositInteroperability
1,536 ຄັ້ງທີ່ເບິ່ງ
18 ກຳລັງສົນທະນາ