

Selena_09
4.4k Publications
Selena_09
Signaler
Bloquer l’utilisateur
458 Suivis
1.0K+ Abonnés
3.8K+ J’aime
Publications
Tous
Citations
Vidéos
·
--
Quá trời rồi đó $Q , đúng kiểu leo cho đã rồi xả 1 mạch luôn, tới giờ $CAP $HUMA roài, cẩn thận là kill tiếp quá
Quá trời rồi đó $Q , đúng kiểu leo cho đã rồi xả 1 mạch luôn, tới giờ $CAP $HUMA roài, cẩn thận là kill tiếp quá
1
213
·
--
Nay $Q như hồi sinh vậy bữa sập chán rồi nay ngoi lên úp vòng mới à, mỗi gậy cứ kéo vài chục % ai đua nổi ? $AIN $$TAG vẫn chưa tụt mà Q đã chia 2 so với sáng rồi
Nay $Q như hồi sinh vậy bữa sập chán rồi nay ngoi lên úp vòng mới à, mỗi gậy cứ kéo vài chục % ai đua nổi ? $AIN $$TAG vẫn chưa tụt mà Q đã chia 2 so với sáng rồi
420
·
--
Chịu rồi, canh chi $AIN cho mệt, nó leo x4 rồi, thấy $BEAT cũng leo ác, con $Q thả gậy về rồi, rụng sớm zị
Chịu rồi, canh chi $AIN cho mệt, nó leo x4 rồi, thấy $BEAT cũng leo ác, con $Q thả gậy về rồi, rụng sớm zị
1
623
·
--
Gậy này của $Q hơi đau à nha, q gậy vài chục % luôn á.
Sáng giờ thấy $BEAT cung tăng lại mà $龙虾 vẫn chưa thấy gì, bữa chót đu 1 ít rồi
Gậy này của $Q hơi đau à nha, q gậy vài chục % luôn á.
Sáng giờ thấy $BEAT cung tăng lại mà $龙虾 vẫn chưa thấy gì, bữa chót đu 1 ít rồi
Sáng giờ thấy $BEAT cung tăng lại mà $龙虾 vẫn chưa thấy gì, bữa chót đu 1 ít rồi
114
·
--
Này thì gồng $AIN , bữa giờ nó cứ đẩy lên x lần cho gồng, bao giờ tới $BTW $IRYS ???
Này thì gồng $AIN , bữa giờ nó cứ đẩy lên x lần cho gồng, bao giờ tới $BTW $IRYS ???
1.2k
·
--
Ôi trời đây là $AIN X2 chứ còn gì nữa, mình thấy $BEAT và $BULLA cũng leo lại, con BEAT đêm qua sập lẹ quá không kịp làm gì luôn
Ôi trời đây là $AIN X2 chứ còn gì nữa, mình thấy $BEAT và $BULLA cũng leo lại, con BEAT đêm qua sập lẹ quá không kịp làm gì luôn
944
·
--
Cả $Q $JCT còn nào cũng đẩy vượt qua đỉnh cũ hôm trước, nay thấy cả $SOON cũng leo, con nào cũng bay mà HEMI cứ nằm im chưa nhúc nhích
Cả $Q $JCT còn nào cũng đẩy vượt qua đỉnh cũ hôm trước, nay thấy cả $SOON cũng leo, con nào cũng bay mà HEMI cứ nằm im chưa nhúc nhích
888
·
--
Trời ạ, chơi alt cap bé cỡ như $$Q $DOOD hay $TAG không đau tim cũng thành đau tim thôi à, quay xe liên tục kẻ khóc người cười :) có lời không chốt tội lỗi thật sự
Trời ạ, chơi alt cap bé cỡ như $$Q $DOOD hay $TAG không đau tim cũng thành đau tim thôi à, quay xe liên tục kẻ khóc người cười :) có lời không chốt tội lỗi thật sự
1
1.1k
·
--
11
·
--
Điên rồ thật, quay đi quay lại $Q vượt luôn đỉnh hôm trước lên hơn 0.22u, short khó thở thật đó, $JCT $AGT cũng đang tăng trở lại rồi, soon nào
Điên rồ thật, quay đi quay lại $Q vượt luôn đỉnh hôm trước lên hơn 0.22u, short khó thở thật đó, $JCT $AGT cũng đang tăng trở lại rồi, soon nào
2
1.2k
·
--
Trời ơi mới ngủ dậy nhìn $Q tưởng hoa mắt, sao mà nó x4 được trong đêm luôn vậy, bịp thực sự, $BULLA $AIN cũng tăng khiếp luôn, thị trường này luôn có những bất ngờ mà, ai short Q đêm qua không ???? toang thật
Trời ơi mới ngủ dậy nhìn $Q tưởng hoa mắt, sao mà nó x4 được trong đêm luôn vậy, bịp thực sự, $BULLA $AIN cũng tăng khiếp luôn, thị trường này luôn có những bất ngờ mà, ai short Q đêm qua không ???? toang thật
3
3
1.1k
·
--
Ái chà đêm rồi mà $Q bật tăng 50%, đứng thứ 2 trên top tăng giá sau $BULLA . liệu $AGT có làm điều tương tự không???
Ái chà đêm rồi mà $Q bật tăng 50%, đứng thứ 2 trên top tăng giá sau $BULLA . liệu $AGT có làm điều tương tự không???
1
616
·
--
Choáng thật, Ăn được ít $BULLA tưởng thơm rồi, ai dè lại non choẹt tiếp. giờ canh tiếp $BEAT $DOOD , cay cú con BULLA thật
Choáng thật, Ăn được ít $BULLA tưởng thơm rồi, ai dè lại non choẹt tiếp. giờ canh tiếp $BEAT $DOOD , cay cú con BULLA thật
1
1k
·
--
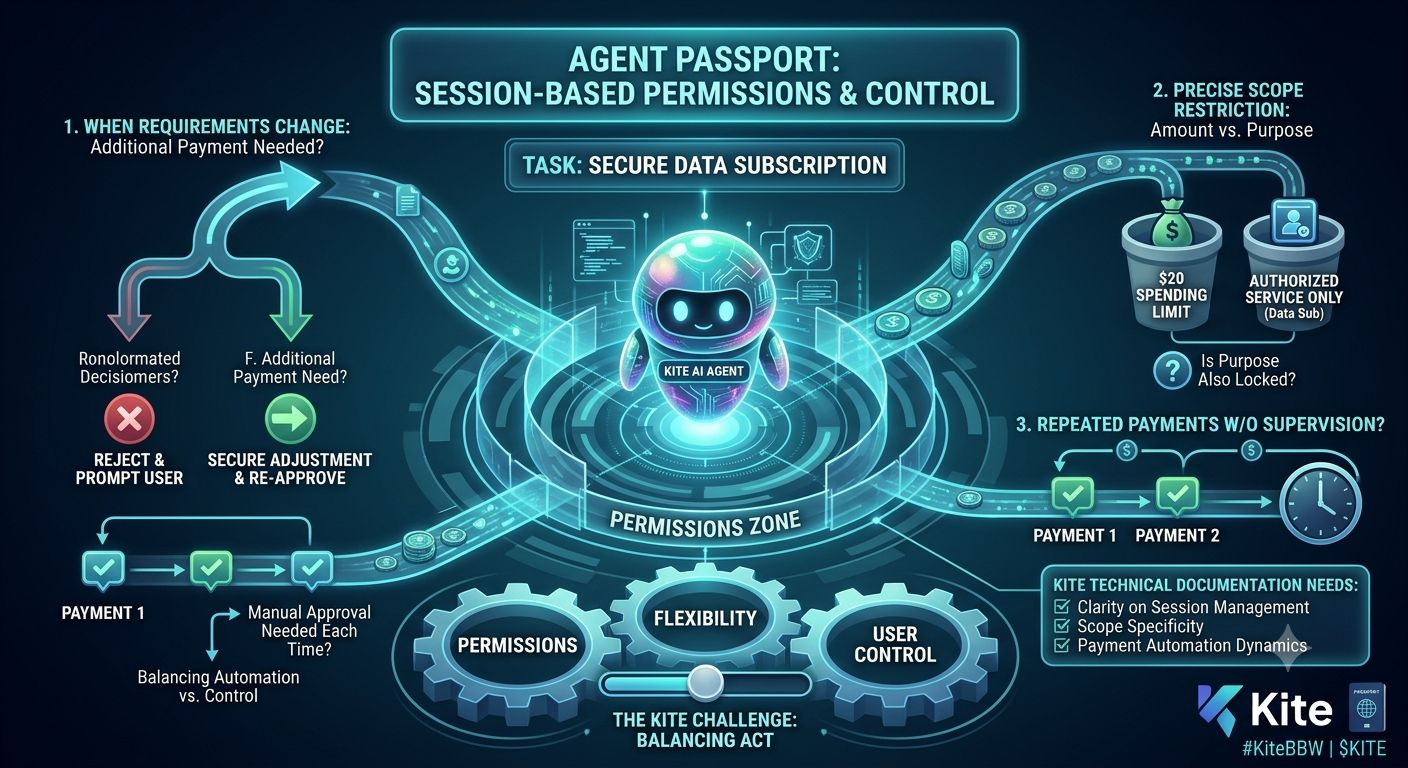
There’s a scenario I think is worth exploring with Kite: when an AI agent is authorized to make payments, how can we ensure that its permissions remain aligned with the task it was given?
What stands out to me about Agent Passport is its session-based approach to permissions, with predefined limits tied to the user’s passkey. This creates a clearer boundary for what an agent can do instead of giving it unrestricted access.
But I want to look deeper into three questions.
First, how are session limits managed when requirements change? If an agent needs to make an additional payment that wasn’t anticipated, will the system reject it, ask the user to approve it again, or allow the permissions to be adjusted? The answer directly affects the balance between automation and user control.
Second, how precisely does Agent Passport restrict the scope of authorization? Limiting the amount of money an agent can spend is one thing, but restricting what that money can be used for is equally important. If an agent is authorized to spend $20 on a specific service, could that permission be used for a different transaction as long as it stays within the spending limit? This needs to be clarified to assess the actual level of protection.
Third, what happens when an agent needs to make repeated payments without direct human supervision? If every session requires manual approval, automation becomes limited. On the other hand, if permissions remain active for too long or can be expanded too easily, the benefits of initially restricting access may gradually diminish.
To me, this is the core challenge for Kite: not simply authorizing AI agents to make payments, but balancing three essential factors: permissions, flexibility, and user control.
I’d like to see Kite’s technical documentation explain more clearly how Agent Passport handles these scenarios, rather than judging the product solely by its concept of session-based authorization.
In your view, should Kite prioritize spending limits, transaction-purpose restrictions, or a combination of both?
#KiteBBW $KITE
43
·
--
Gì đây gì đây? lâu lắm rồi mới thấy cặp bài trùng $BEAT $BR $TAG cùng xuất hiện trên top tăng giá, Maket khởi sắc hay điềm báo gì đây kk
Gì đây gì đây? lâu lắm rồi mới thấy cặp bài trùng $BEAT $BR $TAG cùng xuất hiện trên top tăng giá, Maket khởi sắc hay điềm báo gì đây kk
1
398
·
--
Toẹt vời !!! $BR lên sóng, $BTW hẹo thì tới BR và $BULLA leo ác, cố leo x lần tiếp đi nhé
Toẹt vời !!! $BR lên sóng, $BTW hẹo thì tới BR và $BULLA leo ác, cố leo x lần tiếp đi nhé
1
490
·
--
Có vẻ như maket mặc kệ cụ $BTC rồi hay sao nhỉ, giật về lại 79k6 mà $ZEC $NEAR không tụt nữa
Có vẻ như maket mặc kệ cụ $BTC rồi hay sao nhỉ, giật về lại 79k6 mà $ZEC $NEAR không tụt nữa
1
589
·
--
Tránh ra nào, tàu $BANK bắt đầu rời bến rồi, sắp tới bờ của mình rồi 😂😂 $BULLA đã chạy
khi nào tới ông nội $HEMI ?
Tránh ra nào, tàu $BANK bắt đầu rời bến rồi, sắp tới bờ của mình rồi 😂😂 $BULLA đã chạy
khi nào tới ông nội $HEMI ?
khi nào tới ông nội $HEMI ?
2
347
·
--
Tầm này canh short $DOOD $ERA được chưa nhỉ, chiều cắt long được 1 đoạn rồi. Hơi a cay mải nấu ăn thấy $QNT mà chậm tay quá tụt rồi, đợi cơ hội mới vậy
Tầm này canh short $DOOD $ERA được chưa nhỉ, chiều cắt long được 1 đoạn rồi. Hơi a cay mải nấu ăn thấy $QNT mà chậm tay quá tụt rồi, đợi cơ hội mới vậy
315
·
--
Cay thế nhỉ, vội đón hhn nên đóng lệnh $DOOD $BULLA sớm quá thành non mất rồi, còn mỗi lệnh $QNT , để tới giờ thì đẫm rồi
Cay thế nhỉ, vội đón hhn nên đóng lệnh $DOOD $BULLA sớm quá thành non mất rồi, còn mỗi lệnh $QNT , để tới giờ thì đẫm rồi
631
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
EthereumDropsBelow$2300
1,517 vues
60 mentions
CZ predicted this way before 🤣
$BTC below $80K
$ETH below $2300
$XRP below $1.3
Is this another opportunity to accumulate or you guys waiting for Bitcoin $35k bottom ❓
ParvezMayar
·8 mentions J’aime
·3.7k vues
BitcoinSlipsBelow$80KAgain
1,997 vues
33 mentions
ThailandLaunchesWORPTStablecoinToQRPaymentApp
3,550 vues
109 mentions