

#hackeralert
hackeralert
1.8M views
1,155 Discussing
Hot
Latest

Article
Hackers steal 400,000 USDT from Binance-linked prediction marketPredict.fun promised refunds to victims, but has yet to explain how the attack happened.
The incident puts the security of a platform backed by the Binance-linked investment ecosystem under scrutiny
Funds were transferred out of users’ wallets without authorization.
Independent reports estimate that between 19 and 29 wallets were affected.
Hackers stole hundreds of thousands of USDT from users’ wallets on the prediction market Predict.fun, which is integrated into Binance Wallet. The platform’s team confirmed the unauthorized transfers on October 27, 2026, and promised to reimburse all direct losses resulting from the incident.
Hackers steal 400,000 USDT from Binance-linked prediction market
Predict.fun promised refunds to victims, but has yet to explain how the attack happened.
The incident puts the security of a platform backed by the Binance-linked investment ecosystem under scrutiny
Funds were transferred out of users’ wallets without authorization.
Independent reports estimate that between 19 and 29 wallets were affected.
Hackers stole hundreds of thousands of USDT from users’ wallets on the prediction market Predict.fun, which is integrated into Binance Wallet. The platform’s team confirmed the unauthorized transfers on October 27, 2026, and promised to reimburse all direct losses resulting from the incident.
56
·
--
The internet is in code red! 🚨 A historic flaw called PHP2Shell has just knocked out the defenses of 7 out of every 10 websites on the planet, forcing banks, airlines, and governments to shut down their emergency systems.
Here’s the super-quick rundown of what’s happening and how to save your digital skin:
• The danger: It’s a critical flaw in PHP’s memory handling. It lets attackers sneak into the heart of servers without passwords, and do so at scale.
• The lifeline (ACT NOW):
• Update the interpreter: Install the official PHP patches today.
• Clean house: Remove orphaned scripts and old plugins (pre-2019).
• Monitor: Carefully check the logs for unusual PHP-FPM processes.
AI helped discover it, but hackers are already attacking at the speed of light.
If you manage servers or web projects, tell me: What version of PHP are you currently running, or which control panel (such as cPanel or Plesk) do you use? I can give you the exact commands to secure your system right away.
#HackerAlert
116
·
--
🚨 CoinDCX Faces Fresh Hack Allegations Over $16 Million Crypto Transfers
Blockchain Investigator ZachXBT Flagged Suspicious Transfers Involving Approximately $16 Million In Crypto Assets. CoinDCX Denied A New Hack, Saying The Activity Relates To Compromised Addresses From The July 2025 Incident. The Exchange Says Customer Funds Remain Safe.
#NewsAboutCrypto #HackerAlert @Binance_South_Asia @Binance_News @Binance_Square_Official
🚨 CoinDCX Faces Fresh Hack Allegations Over $16 Million Crypto Transfers
Blockchain Investigator ZachXBT Flagged Suspicious Transfers Involving Approximately $16 Million In Crypto Assets. CoinDCX Denied A New Hack, Saying The Activity Relates To Compromised Addresses From The July 2025 Incident. The Exchange Says Customer Funds Remain Safe.
#NewsAboutCrypto #HackerAlert @Binance South Asia @Binance News @Binance Square Official
1
67
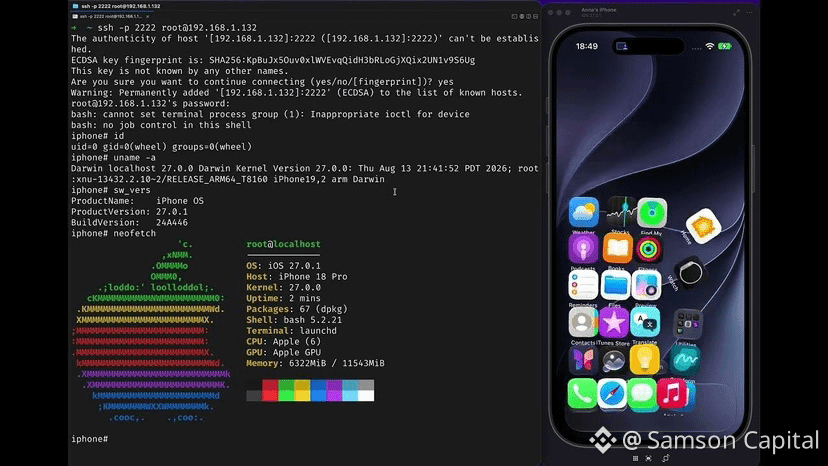
Warning: The latest iPhone can be controlled with just a PDF file - Don't open unknown PDFs: #AI is making the latest iPhones more vulnerable than ever
On October 16, 2026, at the Hexacon conference (Paris), Calif (Thai Duong & Bruce Dang) gave a live demo:
An untethered jailbreak on the iPhone 18 Pro running iOS 27.0.1: root privileges persist after rebooting.
A 1-click attack via a malicious PDF file in Signal and iMessage: simply opening the file allows code execution on the device.
This is not an attack via Gmail. Full technical details have not yet been fully disclosed.
Why is it dangerous?
iMessage/Signal are extremely popular. A PDF file from an acquaintance or a compromised account is enough to pose a risk.
Apple's security remains strong, but the gap with real-world attacks is narrowing, especially as AI helps discover vulnerabilities faster.
What to do immediately:
Update iOS to the latest version.
Do not open unknown PDFs (even from acquaintances) directly on your phone.
Consider enabling Lockdown Mode if you belong to a high-risk group.
Please share this with your loved ones. Being cautious with attachments is more critical now than ever.
Read more: https://blog.calif.io/p/iphone
#HackerAlert
1
7
#Ledger #HackerAlert
🚨 Ledger Attack: $91 Million Stolen from Compromised Devices — Investigation Details
Hardware wallet manufacturer Ledger has released an official update regarding the incident in which crypto users lost approximately $91 million (an estimate by Alex Thorn, Head of Research at Galaxy Research).
🔍 Key Investigation Facts:
Source of the problem: All confirmed breach cases are linked exclusively to devices purchased through an unofficial reseller in Southeast Asia—CryptoBilis.
Direct sales secure: All official Ledger systems and direct sales channels remain unaffected.
Physical tampering: An unauthorized hardware implant was discovered in the wallet of at least one victim. Ledger notes that the number of modified devices is limited, and the investigation is ongoing.
Seller's response: CryptoBilis has completely halted sales of hardware wallets.
🛡 What should owners of devices purchased through CryptoBilis do?
1. If the device is new (unactivated): Do NOT initialize or set it up.
2. If you have already set up the device: Urgently transfer all funds to a new wallet using a seed phrase generated on a secure device purchased directly from the official Ledger website.
3. If you have been affected: Contact official Ledger Support and file a report with law enforcement agencies.
1
3
419
⚠️ An error in the XRP Ledger, present since 2015, could have allowed unbacked XRP to be created through a mathematical overflow. XRPL fixed the flaw without a validator vote and says there is no evidence it was exploited.
🔓 Researchers detected an implant that intercepts data displayed on Ledger hardware wallets during setup. It captures the seed phrase in plain text and sends it over a cellular network. The secure chip remains intact.
#Ledger #HackerAlert #xrp #Ripple #XRPL $XRP $RLUSD
🔓 Researchers detected an implant that intercepts data displayed on Ledger hardware wallets during setup. It captures the seed phrase in plain text and sends it over a cellular network. The secure chip remains intact.
#Ledger #HackerAlert #xrp #Ripple #XRPL $XRP $RLUSD
50

·
--
Bearish
😭 $6M stolen in Base network hack
A hacker drained 1,783 wstETH from a vault on Base - it's not yet known which protocol owned the funds
Another day, another vault that wasn't quite as locked as it looked 🙁
$ETH #ETHUp70%InQ3ButLiquidityFalls
#HackerAlert
😭 $6M stolen in Base network hack
A hacker drained 1,783 wstETH from a vault on Base - it's not yet known which protocol owned the funds
Another day, another vault that wasn't quite as locked as it looked 🙁
$ETH #ETHUp70%InQ3ButLiquidityFalls
#HackerAlert
A hacker drained 1,783 wstETH from a vault on Base - it's not yet known which protocol owned the funds
Another day, another vault that wasn't quite as locked as it looked 🙁
$ETH #ETHUp70%InQ3ButLiquidityFalls
#HackerAlert
33
·
--
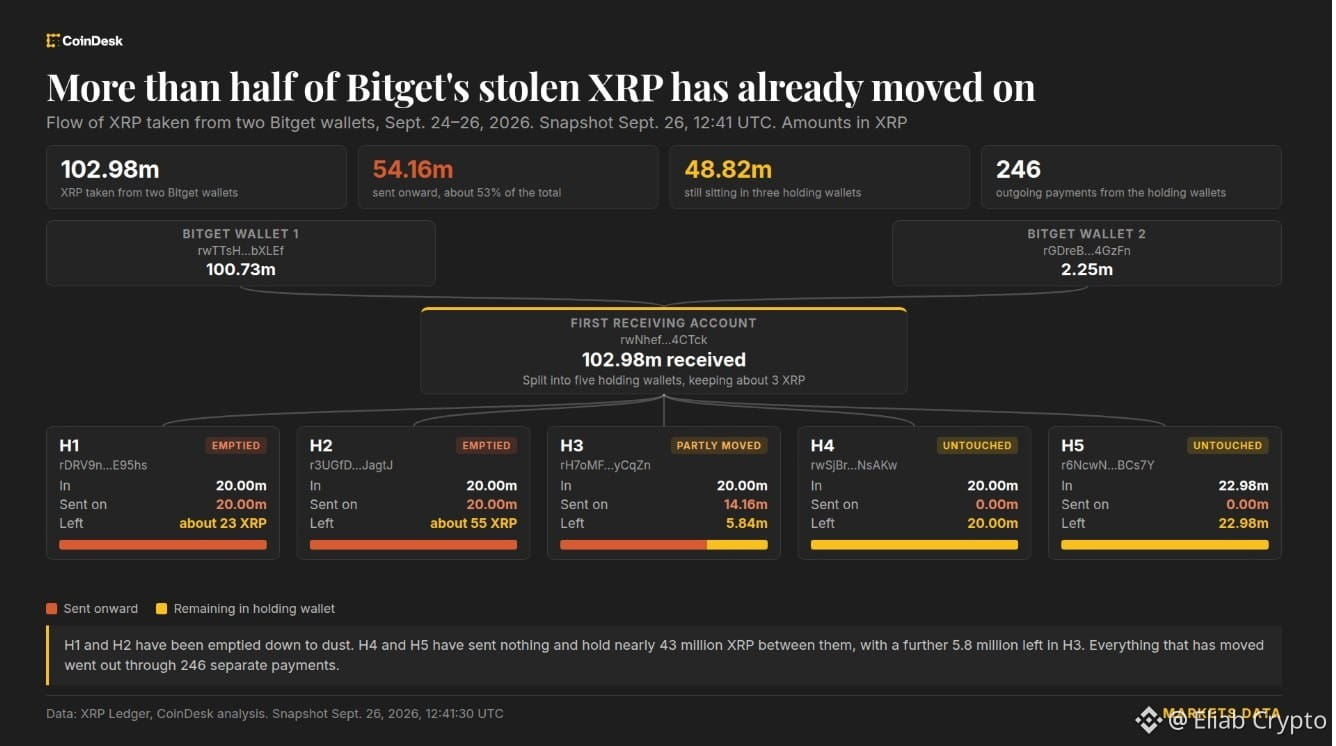
🚨 #BITGET HACKER MOVES $83M IN STOLEN XRP
The attacker has moved around $83M worth of stolen XRP -- and Ripple cannot freeze the funds
Two wallets have been almost completely emptied, while a third is still being drained.
Only about $75M remains across the five original holding wallets
The stolen XRP is moving fast
Where will it go next?
#Bitget #HackerAlert
3
266
·
--
JUST IN: THE CHINESE HACKER WHO STOLE $370M FROM BITGET EXPRESSES THAT HE NEEDS SUPPORT FROM THOR CHAIN TO LAUNDER THE FUNDS
“I’M VERY WORRIED. LOSING MY ASSETS WOULD CAUSE A LOT OF TROUBLE IN MY LIFE”
#Bitget #HackerAlert
@Square-Creator-0b3444457
JUST IN: THE CHINESE HACKER WHO STOLE $370M FROM BITGET EXPRESSES THAT HE NEEDS SUPPORT FROM THOR CHAIN TO LAUNDER THE FUNDS
“I’M VERY WORRIED. LOSING MY ASSETS WOULD CAUSE A LOT OF TROUBLE IN MY LIFE”
#Bitget #HackerAlert
@FINANCE-JACK
“I’M VERY WORRIED. LOSING MY ASSETS WOULD CAUSE A LOT OF TROUBLE IN MY LIFE”
#Bitget #HackerAlert
@FINANCE-JACK
105
·
--
Bullish
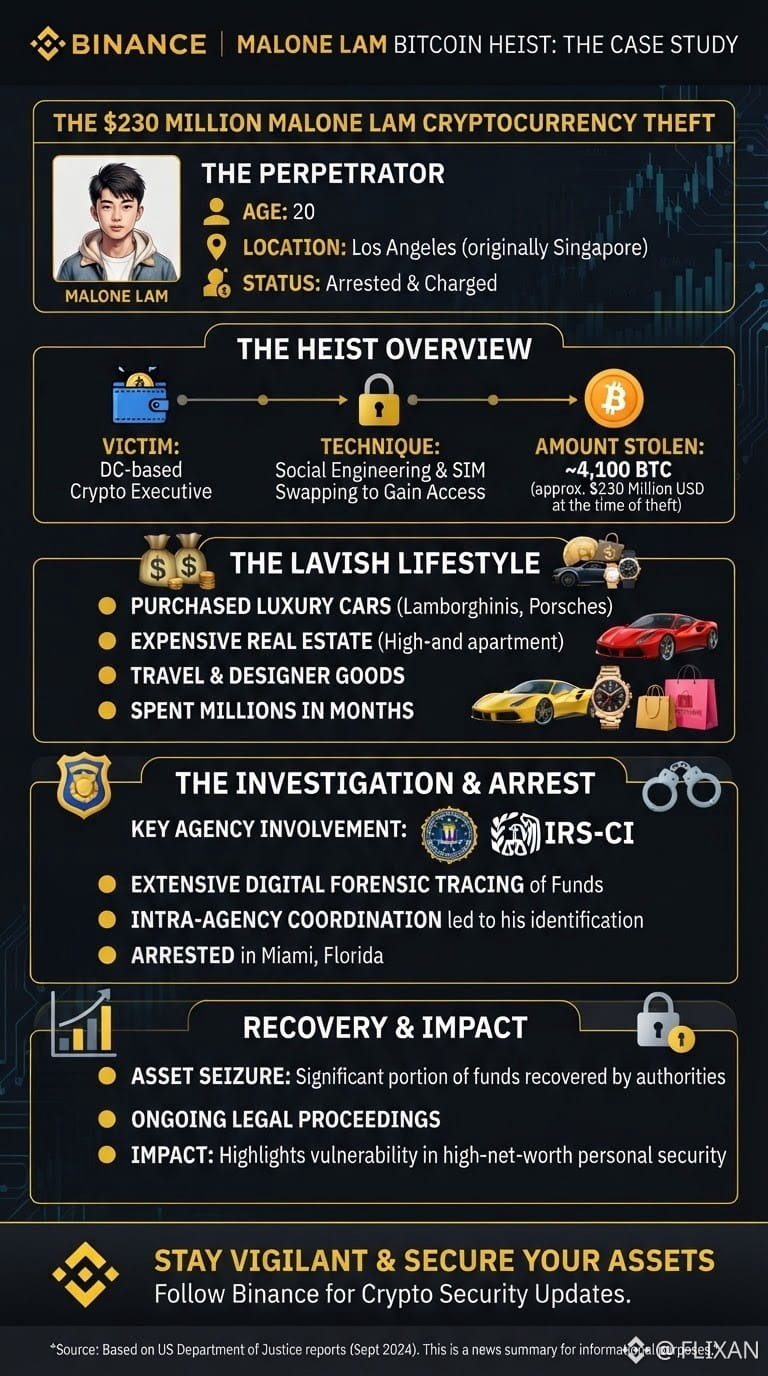
Binance Case Study: The $230M Malone Lam Crypto Heist
The 20-year-old mastermind Malone Lam, originally from Singapore, orchestrated a massive $230M cryptocurrency theft (approx. 4,100 BTC) targeting a Washington D.C. executive. Using social engineering and SIM swapping, they bypassed 2FA to drain funds in minutes. Lam and accomplice Jeandiel Serrano burned millions on luxury cars, real estate, and high-end goods in Los Angeles. FBI and IRS-CI tracked on-chain activity and spending sprees, leading to their arrest in Miami. Recovered assets are being secured, highlighting extreme vulnerabilities in high-net-worth personal crypto security. Use app-based 2FA and hardware wallets to stay protected.
#Bitcoin❗ #HackerAlert $
135
·
--
Bullish
The price of THORChain rose by 15% following the CEO of the Bitget platform’s request to ban addresses related to a hack. The price of the THORChain coin increased by more than 15% after Bitget’s CEO formally asked the protocol to block services to addresses linked to a hack worth $351.6 million. On-chain data analyses confirm that the stolen funds were routed through THORChain to carry out cross-chain swaps, increasing the clarity of fund flows on the network and sparking debate about the balance between decentralization and controls to combat illicit activity.
#THORChain #Bitget #HackerAlert #Rune
$RUNE
{future}(RUNEUSDT)
The price of THORChain rose by 15% following the CEO of the Bitget platform’s request to ban addresses related to a hack. The price of the THORChain coin increased by more than 15% after Bitget’s CEO formally asked the protocol to block services to addresses linked to a hack worth $351.6 million. On-chain data analyses confirm that the stolen funds were routed through THORChain to carry out cross-chain swaps, increasing the clarity of fund flows on the network and sparking debate about the balance between decentralization and controls to combat illicit activity.
#THORChain #Bitget #HackerAlert #Rune
$RUNE
#THORChain #Bitget #HackerAlert #Rune
$RUNE
1
23

·
--
$STO
{future}(STOUSDT)
🚨 BREAKING:
💰 Bit get founder Gracy Chen confirmed a Sept. 24 breach this week, affecting ~$351.6M from hot and warm wallet infrastructure.
Cold wallets remain secure. Bit get's $464M+ User Protection Fund covers the full loss.
Crypto suffered its largest hack of the year after Bit get lost $350 million in a single attack.
Nearly $2 billion has already been stolen across 300+ crypto hacks in 2026.
Bit get CEO Gracy Chen says North Korean hackers may be behind the exchange's $352M breach, citing IP addresses linked to VPNs used by a DPRK group.
#HackerAlert #BREAKING #CryptoNews
$STO
🚨 BREAKING:
💰 Bit get founder Gracy Chen confirmed a Sept. 24 breach this week, affecting ~$351.6M from hot and warm wallet infrastructure.
Cold wallets remain secure. Bit get's $464M+ User Protection Fund covers the full loss.
Crypto suffered its largest hack of the year after Bit get lost $350 million in a single attack.
Nearly $2 billion has already been stolen across 300+ crypto hacks in 2026.
Bit get CEO Gracy Chen says North Korean hackers may be behind the exchange's $352M breach, citing IP addresses linked to VPNs used by a DPRK group.
#HackerAlert #BREAKING #CryptoNews
751
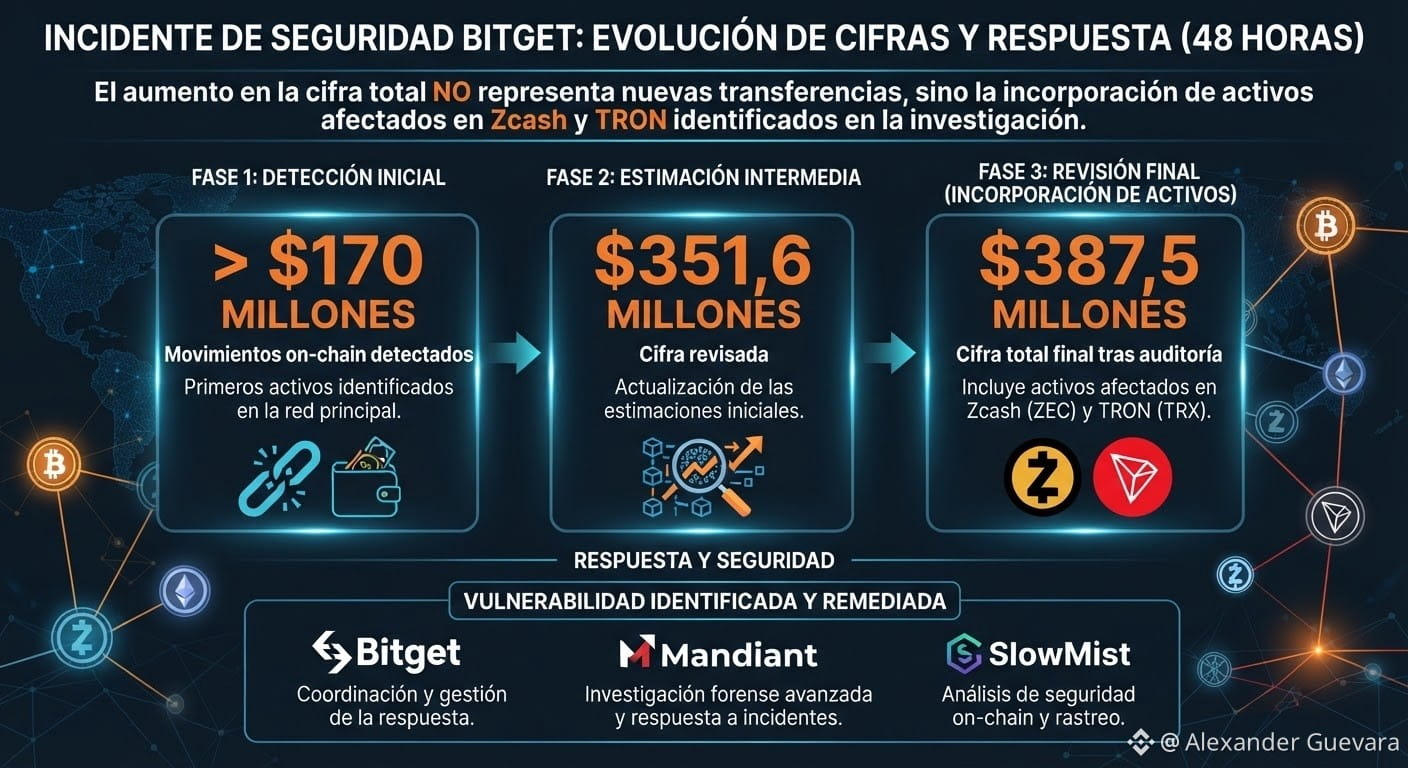
🚨 B1tg3t: from $170M to $387.5M
The B1tg3t case grew in magnitude in just 48 hours.
First, there were more than $170 million in detected on-chain movements. Then came an estimate of $351.6 million and, subsequently, a revised figure of $387.5 million after incorporating affected assets in Zcash and TRON.
But there’s a key detail: the increase in the number does not represent a new wave of transfers, according to B1tg3t.
The company states that the vulnerability was identified and fixed, while Mandiant and SlowMist continue to support the investigation.
📌 #HackerAlert #hackattack #On-chain #ciberseguridad #CircleTetherFreezeBitgetHackerWallet $TRX $ZEC
1
139
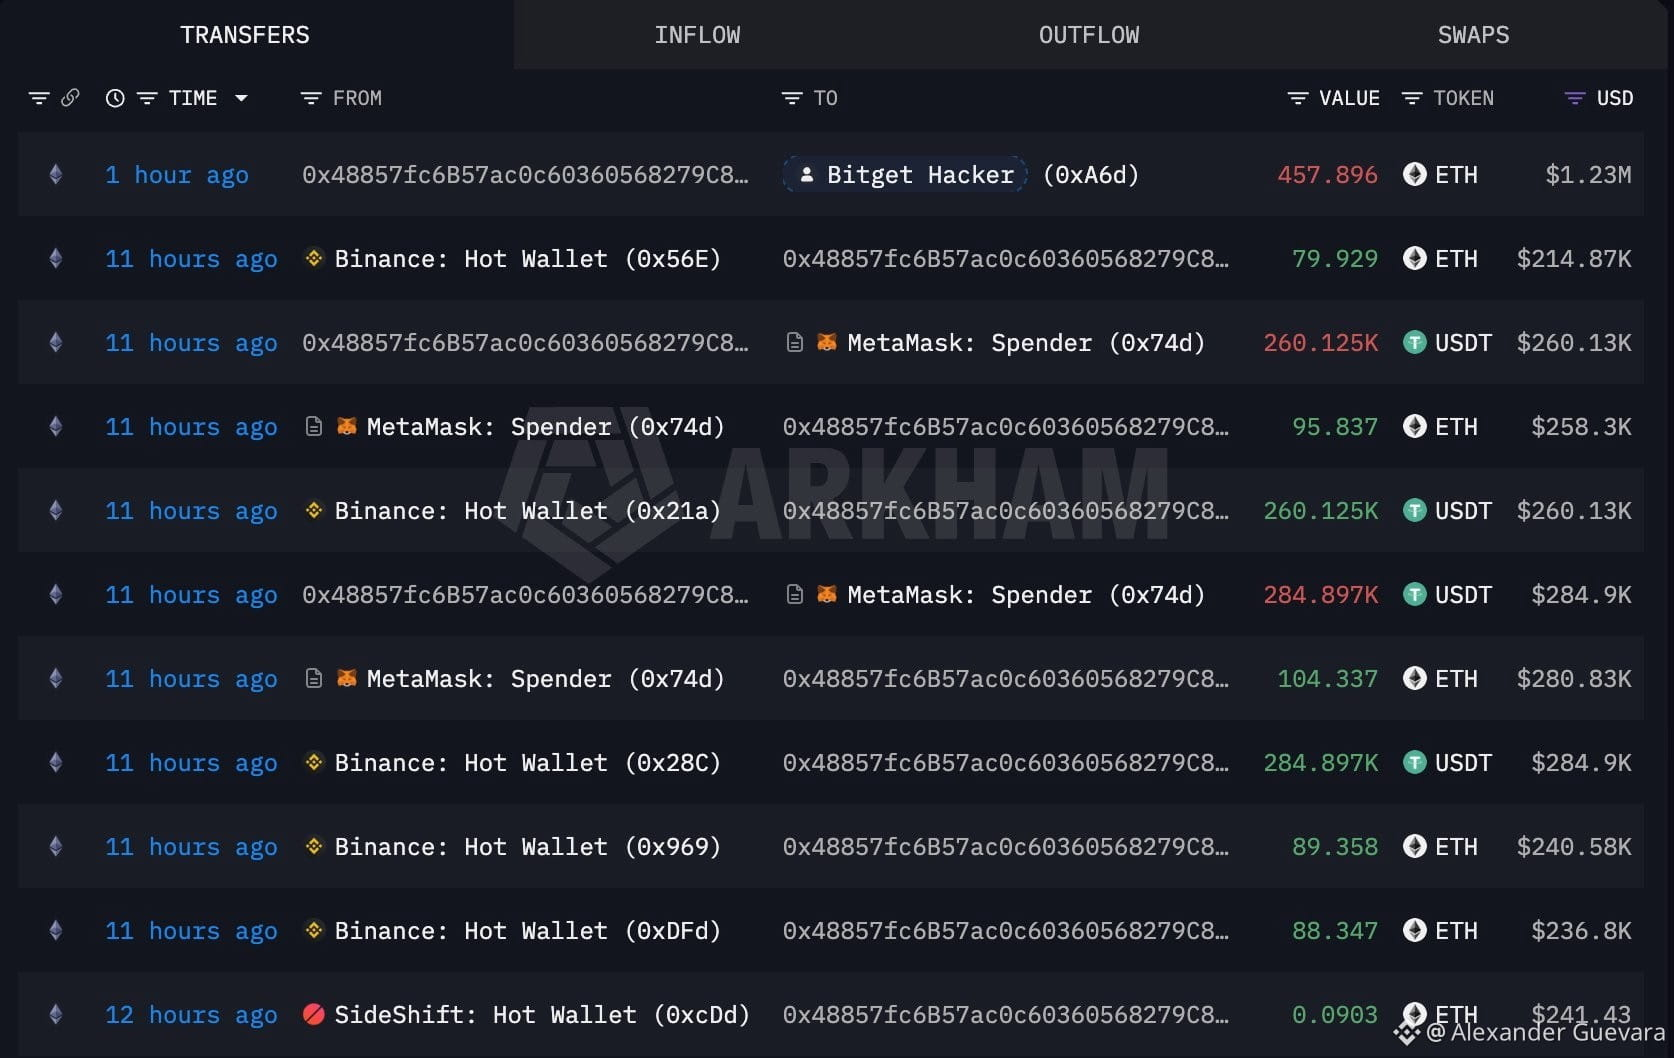
It looks like the hacker of #Bitget withdrew $1.23M from #Binance 11 hours ago.
Wallet 0x4885 withdrew 257.6 $ETH ($692K) and 545K $USDT from #Binance, then swapped the 545K $USDT for 200.2 $ETH.
Then it transferred everything—457.9 $ETH ($1.23M)—to the hacker’s wallet of #Bitget an hour ago.
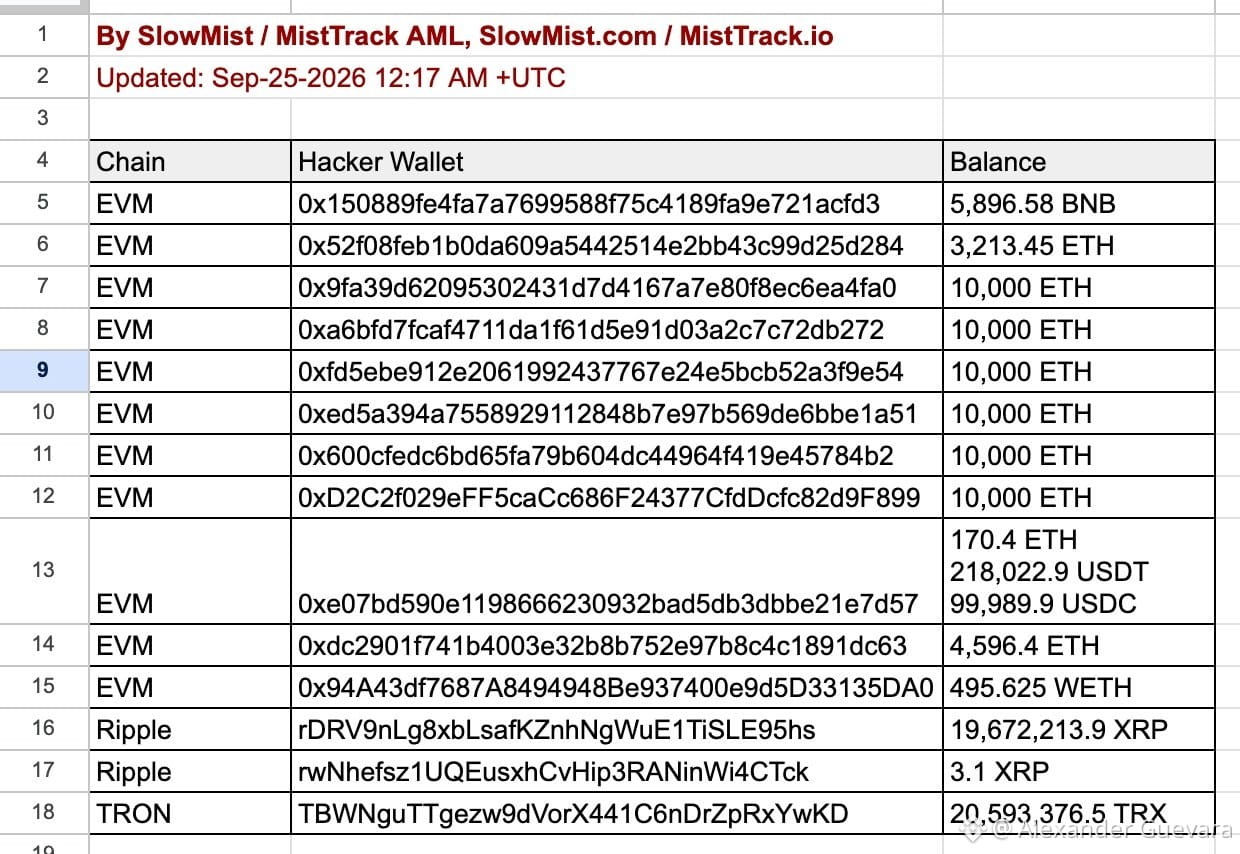
So far, we’ve identified the following addresses associated with the @bitget exploiter that still contain funds. We will continue updating this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets/d…
#HackerAlert #Hacked
It looks like the hacker of #Bitget withdrew $1.23M from #Binance 11 hours ago.
Wallet 0x4885 withdrew 257.6 $ETH ($692K) and 545K $USDT from #Binance, then swapped the 545K $USDT for 200.2 $ETH .
Then it transferred everything—457.9 $ETH ($1.23M)—to the hacker’s wallet of #Bitget an hour ago.
So far, we’ve identified the following addresses associated with the @bitget exploiter that still contain funds. We will continue updating this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets/d…
#HackerAlert #Hacked
50
Article
The MANTRA network was halted following a security incident⚠️ The MANTRA Chain network was halted following a security incident. The price of the native cryptocurrency drops.
The development team says it detected the vulnerability and is working to fully fix it.
The development team says it detected the vulnerability and is working to fix it.
Only 2 wallets on the network would have suffered losses of funds due to this incident.
The price of the MANTRA cryptocurrency falls more than 6% in the last 24 hours.
The MANTRA Chain network suffered a complete shutdown of its operations after a security incident was detected in its infrastructure. The development team decided to temporarily freeze validators, bridges, and public link points as a precaution to contain the threat and protect users’ assets.
The MANTRA network was halted following a security incident
⚠️ The MANTRA Chain network was halted following a security incident. The price of the native cryptocurrency drops.
The development team says it detected the vulnerability and is working to fully fix it.
The development team says it detected the vulnerability and is working to fix it.
Only 2 wallets on the network would have suffered losses of funds due to this incident.
The price of the MANTRA cryptocurrency falls more than 6% in the last 24 hours.
The MANTRA Chain network suffered a complete shutdown of its operations after a security incident was detected in its infrastructure. The development team decided to temporarily freeze validators, bridges, and public link points as a precaution to contain the threat and protect users’ assets.
264
#Polymarket #HackerAlert
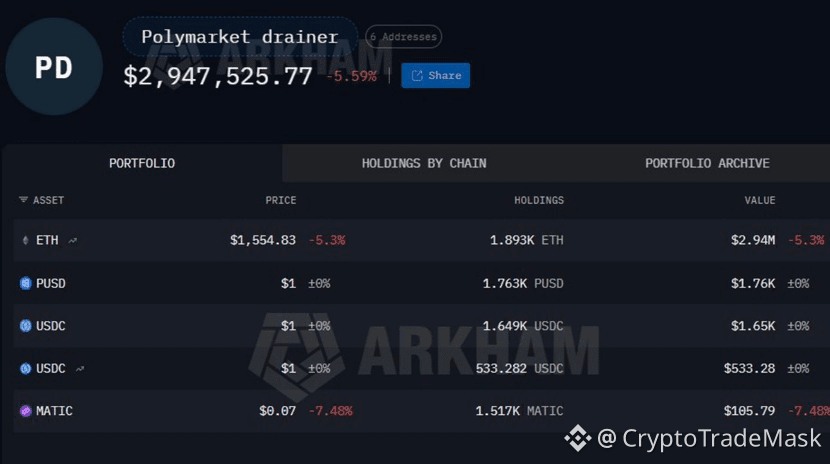
🚨 Polymarket hacked for $2.9 million via frontend: users will be refunded
The forecasting platform Polymarket has been hacked. The attackers hacked a third-party vendor and implemented a phishing script into the site's interface. As a result, at least 11 user wallets were affected, from which $2.94 million was withdrawn.
Main:
The threat has been eliminated: The malicious code has already been removed, the platform's smart contracts were not affected.
Compensation: Polymarket officially announced that they will fully refund all victims.
📉 Cryptohacks in June: in brief
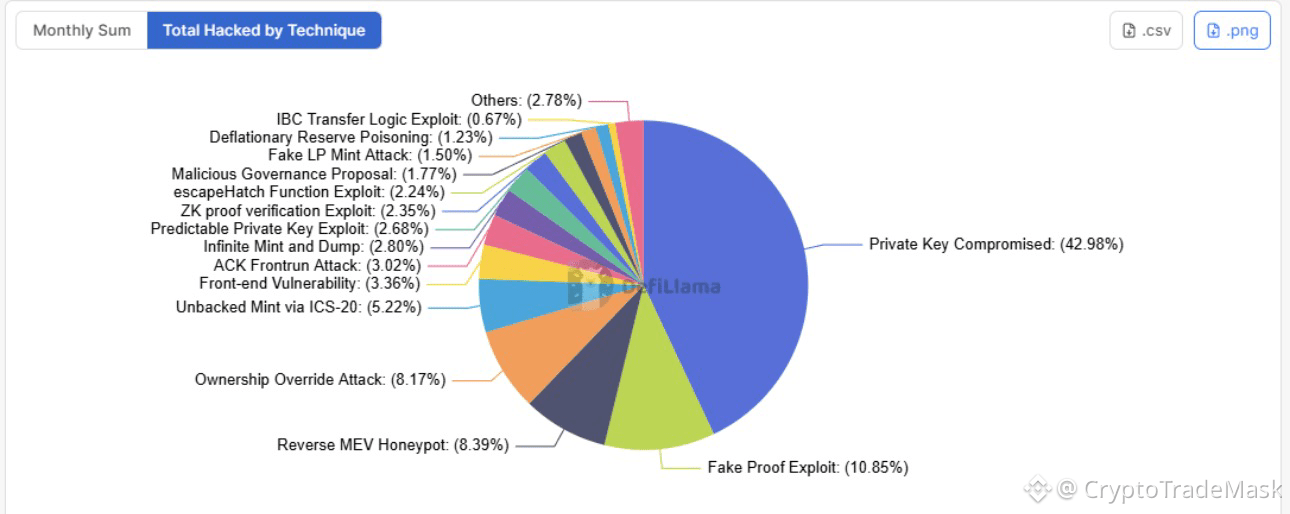
This incident added to the statistics of the worst quarter in terms of the number of hacks. In June alone, the crypto market's losses amounted to $74.9 million (29 cases).
Top 3 hacks of the month: Humanity Protocol ($36 million), Secret Network ($4.7 million) and Polymarket ($2.9 million).
Main vulnerability: 43% of all losses for the month occurred due to compromise of private keys. Despite this, Polymarket holds its ground: the platform's TVL now exceeds $450 million, which is 301% more than last year.
1
181
Article
Red alert‼️: Your cold wallet is no longer cold - $70 million vanished without touching a single device!⚠️ Urgent security alert: this is not science fiction. This actually happened.
1- What are cold wallets?
A cold wallet is a physical device, similar to a flash drive. Its only job is to keep your private keys away from the internet. Unlike hot wallets (which are on your phone or browser and stay connected at all times).
Why do people trust them? Because logic says: if the key is not connected to the internet, no hacker can access it. Big investors put their millions there and sleep peacefully. It was considered the impregnable fortress that could not be breached... until August 1, 2026.
Red alert‼️: Your cold wallet is no longer cold - $70 million vanished without touching a single device!
⚠️ Urgent security alert: this is not science fiction. This actually happened.
1- What are cold wallets?
A cold wallet is a physical device, similar to a flash drive. Its only job is to keep your private keys away from the internet. Unlike hot wallets (which are on your phone or browser and stay connected at all times).
Why do people trust them? Because logic says: if the key is not connected to the internet, no hacker can access it. Big investors put their millions there and sleep peacefully. It was considered the impregnable fortress that could not be breached... until August 1, 2026.
1
2
274
·
--
What really happened with #coldcard It wasn’t an “AI hack”—it was a 2021 firmware bug. The vulnerability was introduced in Coldcard firmware 4.0.0 in March 2021: devices bypassed their hardware random number generator and fell into key generation via software, predictable, seeded with non-secret chip data.  The specific error is in libngu: the guard uses #ifndef MICROPY_HW_ENABLE_RNG, which only checks whether the macro exists, not whether its value is different from zero.  Result: anyone can reproduce the seed candidates offline and derive addresses to compare them with the blockchain—without touching the device.
The figure keeps growing in waves: from an initial 594 BTC to 1.082 BTC (1,196 addresses) on July 31, then 1.158 BTC, and on August 2 a third wave brought the total to ~1.367 BTC (~$89M) from 4,585 addresses;  today people talk about a fourth wave. Coinkite released an emergency firmware on July 31 for all affected models, but installing it doesn’t fix an already-existing seed.  You must generate a new seed and move the funds. #HackerAlert #bitcoin $BTC
The figure keeps growing in waves: from an initial 594 BTC to 1.082 BTC (1,196 addresses) on July 31, then 1.158 BTC, and on August 2 a third wave brought the total to ~1.367 BTC (~$89M) from 4,585 addresses;  today people talk about a fourth wave. Coinkite released an emergency firmware on July 31 for all affected models, but installing it doesn’t fix an already-existing seed.  You must generate a new seed and move the funds. #HackerAlert #bitcoin $BTC
121

#coldcardexploitattackerscontrol1366btc
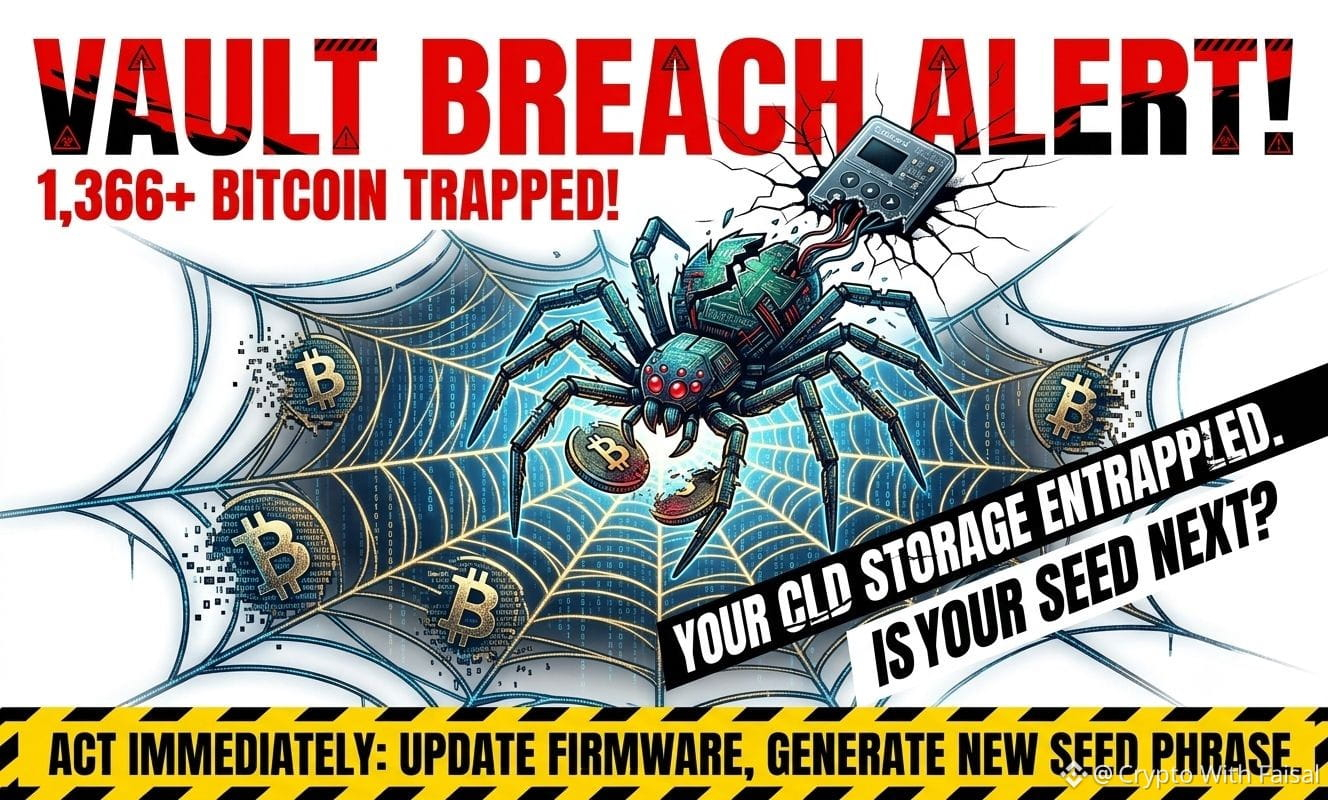
🚨 CRITICAL SECURITY ALERT: EXPANDING EXPLOIT ON COLCARD USERS 🚨
The bleeding hasn't stopped. What began with an alarming 594 BTC drained in under 30 minutes yesterday has now escalated—exploiters currently hold over 1,366.38 BTC under their control!
Analysis from Galaxy Research confirms three distinct waves of attacks so far. The burning question every holder is asking: Is the assault over, or are more breaches incoming? Whether this is a solitary hacker deploying upgraded exploit vectors or multiple attackers capitalizing on legacy vulnerabilities dating back to March 2021, the danger is real.
🛡️ IMMEDIATE ACTION PLAN (PROTECT YOUR ASSETS):
Patch Right Away: Update your device firmware to the latest official release without delay.
Generate a New Seed: Transfer your funds to a completely fresh, uncompromised seed phrase.
Stay Proactive: Cold storage is only as safe as your security hygiene—don't wait until your wallet is drained to take action!
Stay paranoid, stay secure, and protect your holdings! 🔒⚡
Disclaimer: Not financial advice. Always Do Your Own Research (DYOR).
#BTC #Coldcard #HackerAlert
$VELVET
{future}(VELVETUSDT)
$BEAT
{future}(BEATUSDT)
$BTC
{future}(BTCUSDT)
#coldcardexploitattackerscontrol1366btc
🚨 CRITICAL SECURITY ALERT: EXPANDING EXPLOIT ON COLCARD USERS 🚨
The bleeding hasn't stopped. What began with an alarming 594 BTC drained in under 30 minutes yesterday has now escalated—exploiters currently hold over 1,366.38 BTC under their control!
Analysis from Galaxy Research confirms three distinct waves of attacks so far. The burning question every holder is asking: Is the assault over, or are more breaches incoming? Whether this is a solitary hacker deploying upgraded exploit vectors or multiple attackers capitalizing on legacy vulnerabilities dating back to March 2021, the danger is real.
🛡️ IMMEDIATE ACTION PLAN (PROTECT YOUR ASSETS):
Patch Right Away: Update your device firmware to the latest official release without delay.
Generate a New Seed: Transfer your funds to a completely fresh, uncompromised seed phrase.
Stay Proactive: Cold storage is only as safe as your security hygiene—don't wait until your wallet is drained to take action!
Stay paranoid, stay secure, and protect your holdings! 🔒⚡
Disclaimer: Not financial advice. Always Do Your Own Research (DYOR).
#BTC #Coldcard #HackerAlert
$VELVET
$BEAT
$BTC
2
4
4.7k
#HackerAlert
🚨 Hacker withdraws $1.66 million from Allbridge Core cross-chain bridge through liquidity manipulation
The Allbridge Core cross-chain platform was attacked, resulting in $1.66 million in cryptocurrency being stolen from liquidity pools on the Solana network.
❓ How the scheme worked:
1. Flash loan: The attacker borrowed $1.12 million in USDC stablecoins and exchanged them for USDT.
2. Price manipulation: The hacker executed a series of 5 “same-asset swaps”, exchanging USDT for USDT. Due to an error in logic, the accounting of both sides of the transaction diverged, which significantly distorted the intra-pool price of the asset.
3. Finale of the attack: The distorted price allowed only 4,000 USDT to be exchanged for $2.24 million USDC. The attacker returned the flash loan and took about $1.66 million in profit.
Current status and consequences:
➡️ Security of funds: Private keys, user wallets, and routes without using liquidity pools were not affected.
➡️ Project actions: Allbridge plans to completely abandon pool exchanges.
➡️ Tracking: The team has already tracked transfers for $1.63 million — the funds were transferred from Solana to a consolidation address on the Ethereum network, after which they were distributed in several directions.
3
68
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanMicrosoftDeliverOnAI
298,988 views
2,368 Discussing
2
#CanGoogleDefindItsCore
172,411 views
1,690 Discussing
3
#EarningsSeason
5.8M views
28,381 Discussing
4
#$10.9BBitcoinOptionsExpireFriday
2 views
4 Discussing
5
#BitcoinSurpasses$81K
12,159 views
63 Discussing
6
#RobinhoodFalls8.4%AfterItsResults
7,254 views
156 Discussing
7
#KOSPISurges6.63%BackAbove6000
7,364 views
169 Discussing
8
#DatavaultAICantWithdrawBitcoinFromBiconomy
8,424 views
147 Discussing
9
#FOMCWatch
9.3M views
29,381 Discussing
10
#SolanaETFsPostWorstDaySinceDecember
1,599 views
39 Discussing