
#walletsecurity
walletsecurity
177,732 views
464 Discussing
Hot
Latest

🚨 $BTC $ETH $BNB ALERT: APPROVAL PHISHING OPERATION NIAGARA UNVEILED! 🦈
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
🚨 $BTC $ETH $BNB ALERT: APPROVAL PHISHING OPERATION NIAGARA UNVEILED! 🦈
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
🦈 Operation Niagara unites the OSC, U.S. Secret Service, RCMP and top analytics firms to sniff out approval phishing in real‑time. 📊 By flagging exposed token allowances before the drain, authorities turn the usual post‑mortem chase into a pre‑emptive shield for traders.
🔐 Your first line of defense remains personal: regularly revoke stale approvals, never sign contracts from unsolicited DMs, and keep cold storage isolated from active DeFi wallets. 📌 A disciplined audit routine cuts the most common leakage path used by smart‑money hunters.
💬 When was the last time you audited your wallet approvals?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ApprovalPhishing #WalletSecurity #Crypto
🛡️ 🔒
1

🚨 $BTC HOLDERS, YOUR WALLET PERMISSIONS ARE A SILENT TICKING TIME BOMB! 💣
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
🚨 $BTC HOLDERS, YOUR WALLET PERMISSIONS ARE A SILENT TICKING TIME BOMB! 💣
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
Smart money doesn't just protect capital from market corrections; we ruthlessly lock down on-chain permissions before exploiters drain our $ETH and $BNB bags. 🦈
Global law enforcement agencies and top analytics firms just launched real-time tracking to flag exposed wallets, but ultimate defense starts with your own hygiene routine. 📊
When was the last time you revoked a dead smart contract permission or audited your active allowances? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #WalletSecurity #CryptoSafety #OnChain #RiskManagement
🔥 💎
1

A matching Merkle root no longer proves the transactions are the same.
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
A matching Merkle root no longer proves the transactions are the same.
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
Advisory GHSA-8vv3-6qpc-gpw6 (CVSS 9.3): bitcoinjs-lib's checkTxRoots misses duplicated transactions that pad an odd Merkle level. A peer can send a block with a different transaction list but the same root and hash. No mining needed.
Why it matters for $BTC builders: SPV clients, explorers or deposit logic that trust checkTxRoots could credit one deposit twice.
What to do:
• Check your lockfile
• Upgrade to 5.2.1, 6.1.8 or 7.0.2
• Below v5 there is no patch
• Don't just blacklist the block hash in response: it may reject an honest block
Verdict: PROVEN, confidence: high.
Watchpoint: if the advisory still lists no fix for versions below 5 on 16 Dec 2026, those users must migrate, not wait for a patch.
The Signal #004 from Cirqus Intelligence. Nihil sine probatione.
Does your deposit logic verify the transaction list itself, or only that its root looks right?
#Bitcoin #WalletSecurity #bitcoinjs #CryptoSecurity
1
119

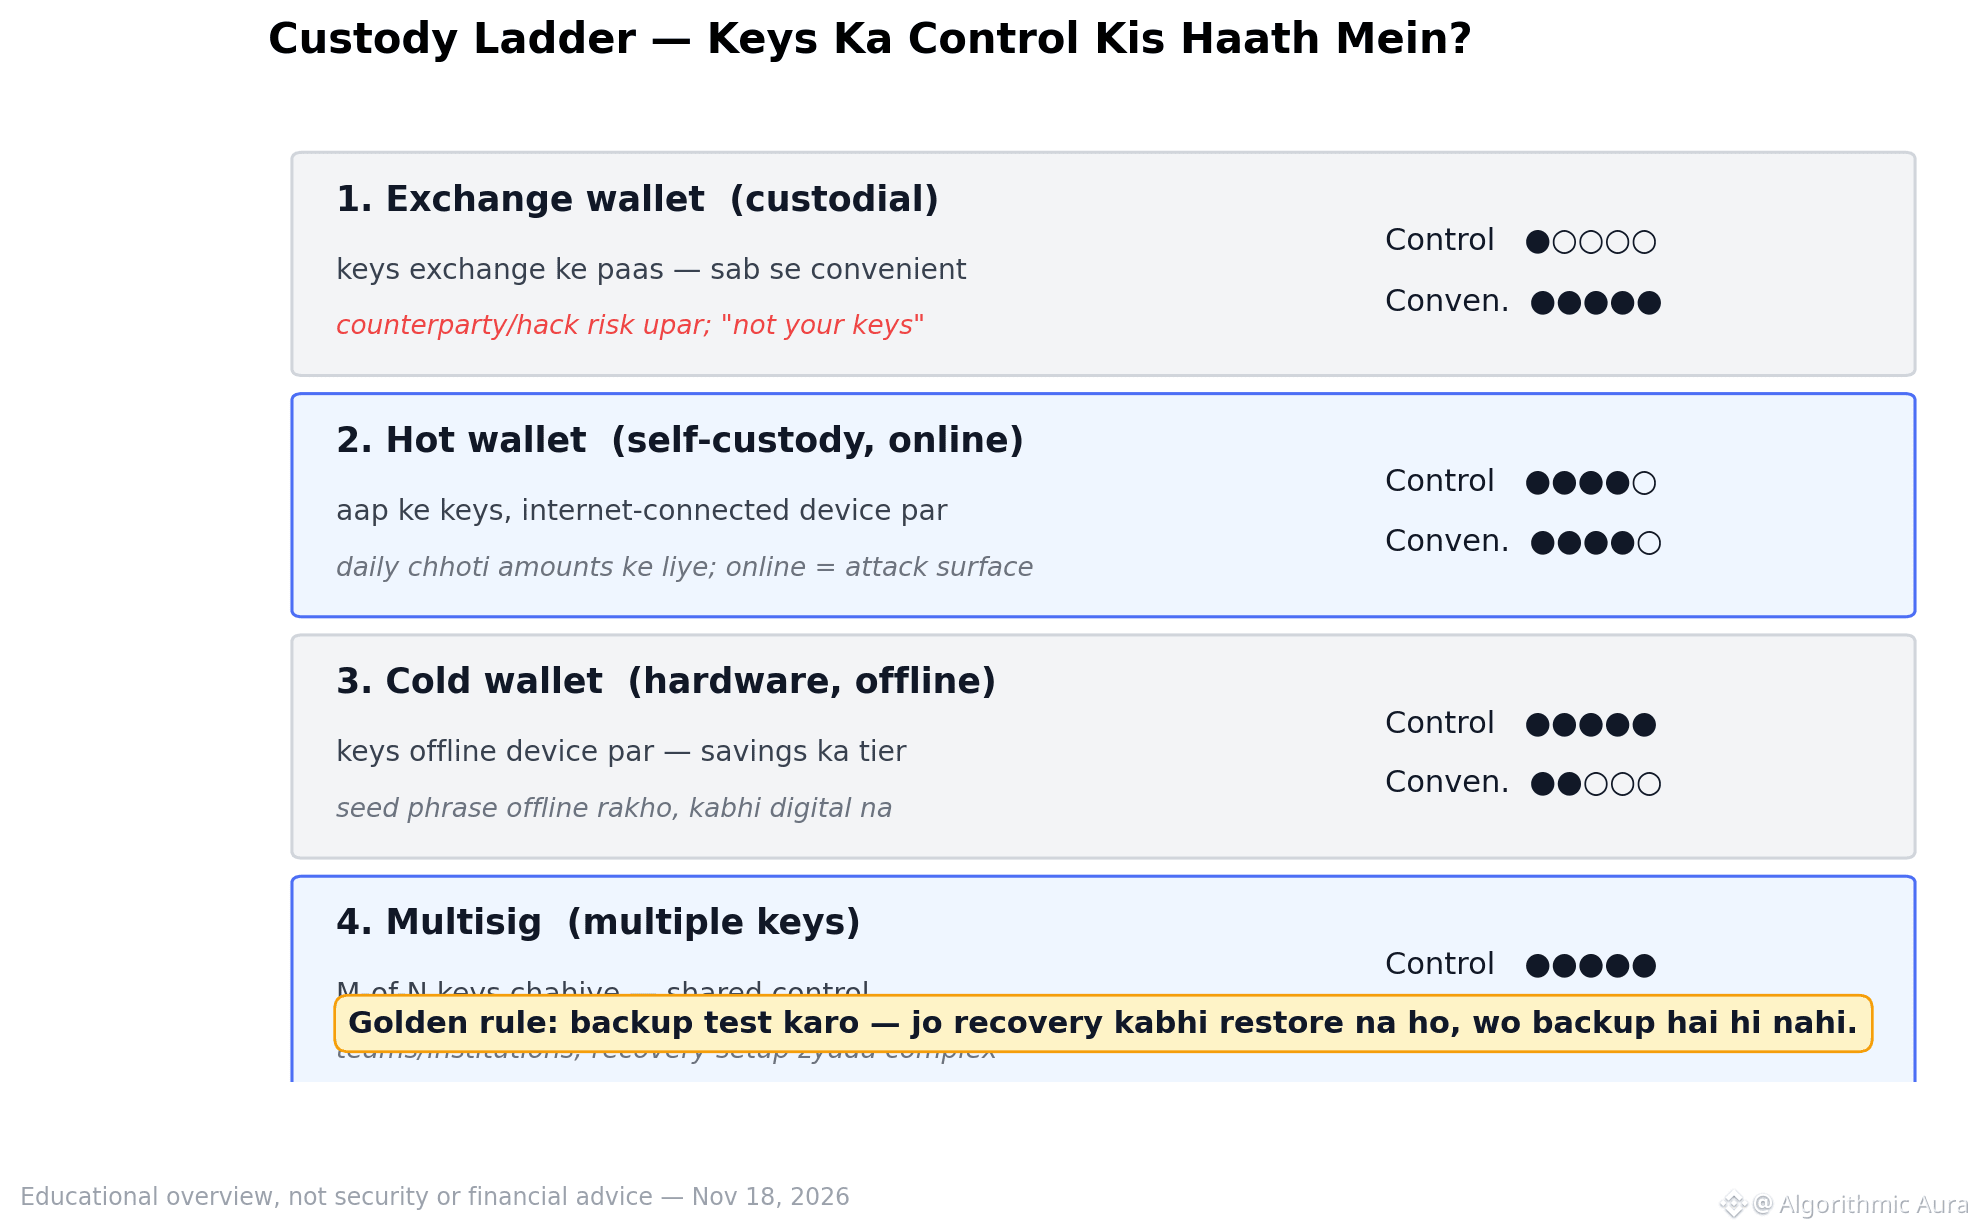
🔐 Ek chart: custody ladder — keys ka control kis haath mein?
1️⃣ Exchange (custodial): convenient, keys exchange ke paas — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; seed phrase offline, kabhi digital na
4️⃣ Multisig: multiple keys — teams; recovery zyada complex
Trade-off: convenience barhne par control ghat-ta hai, aur control par recovery ki zimmedari aap par.
Golden rule: backup test karo — jo kabhi restore na ho, wo backup hai hi nahi.
$BTC #SelfCustody #WalletSecurity #CryptoEducation
🔐 Ek chart: custody ladder — keys ka control kis haath mein?
1️⃣ Exchange (custodial): convenient, keys exchange ke paas — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; seed phrase offline, kabhi digital na
4️⃣ Multisig: multiple keys — teams; recovery zyada complex
Trade-off: convenience barhne par control ghat-ta hai, aur control par recovery ki zimmedari aap par.
Golden rule: backup test karo — jo kabhi restore na ho, wo backup hai hi nahi.
$BTC #SelfCustody #WalletSecurity #CryptoEducation
1️⃣ Exchange (custodial): convenient, keys exchange ke paas — counterparty risk
2️⃣ Hot wallet: self-custody, online — daily amounts; online = attack surface
3️⃣ Cold wallet: hardware, offline — savings; seed phrase offline, kabhi digital na
4️⃣ Multisig: multiple keys — teams; recovery zyada complex
Trade-off: convenience barhne par control ghat-ta hai, aur control par recovery ki zimmedari aap par.
Golden rule: backup test karo — jo kabhi restore na ho, wo backup hai hi nahi.
$BTC #SelfCustody #WalletSecurity #CryptoEducation

·
--
Optimizely 代码劫持波及 176 站点,钱包地址被暗中替换
一起通过第三方代码平台传导的钱包劫持事件正在蔓延,受影响站点已达 176 个,攻击链条从矿机延伸到普通网站,对散户资产安全构成系统性威胁。
据 Decrypt 报道,网站测试平台 Optimizely 被注入恶意代码,访问者在访问被污染页面时,其钱包地址会被悄悄替换为攻击者地址,导致转账资金流向对方。事件涉及 BBC 等知名站点,覆盖范围远超以往以矿机劫持为主的案例。
这一事件的重要性在于,它揭示了攻击方式的升级:过去钱包劫持多集中在算力挖矿场景,而此次通过 SaaS 代码平台传导,意味着任何使用该平台的网站都可能成为跳板。攻击链的扩散路径更加隐蔽,溯源与责任界定也更为复杂。
从数据看,被劫持站点数量为 176 个(据 Decrypt)。这意味着单个第三方服务的漏洞,可能被放大为跨站点、跨用户的规模化攻击。散户防范意识普遍不足,一旦地址被替换而未能察觉,直接损失难以追回。
对市场而言,此类安全事件的冲击通常有限,更多是局部信任扰动而非系统性风险。但考虑到加密基础设施对安全性的依赖,事件若持续扩散,或将影响用户对第三方工具与链上交互的信任。
反方因素在于,直接损失规模目前尚难量化,且事件集中在特定代码平台用户群体,未必波及主流资产价格。市场情绪暂未出现明显联动。
接下来需要观察 Optimizely 的响应与修复进度、受影响站点的清理情况,以及是否出现更大规模的资金损失案例。安全事件的传导链条值得持续追踪,而非一次性关注。
#CryptoSecurity #WalletSecurity
以上为信息整理与个人分析,不构成投资建议。
Optimizely 代码劫持波及 176 站点,钱包地址被暗中替换
一起通过第三方代码平台传导的钱包劫持事件正在蔓延,受影响站点已达 176 个,攻击链条从矿机延伸到普通网站,对散户资产安全构成系统性威胁。
据 Decrypt 报道,网站测试平台 Optimizely 被注入恶意代码,访问者在访问被污染页面时,其钱包地址会被悄悄替换为攻击者地址,导致转账资金流向对方。事件涉及 BBC 等知名站点,覆盖范围远超以往以矿机劫持为主的案例。
这一事件的重要性在于,它揭示了攻击方式的升级:过去钱包劫持多集中在算力挖矿场景,而此次通过 SaaS 代码平台传导,意味着任何使用该平台的网站都可能成为跳板。攻击链的扩散路径更加隐蔽,溯源与责任界定也更为复杂。
从数据看,被劫持站点数量为 176 个(据 Decrypt)。这意味着单个第三方服务的漏洞,可能被放大为跨站点、跨用户的规模化攻击。散户防范意识普遍不足,一旦地址被替换而未能察觉,直接损失难以追回。
对市场而言,此类安全事件的冲击通常有限,更多是局部信任扰动而非系统性风险。但考虑到加密基础设施对安全性的依赖,事件若持续扩散,或将影响用户对第三方工具与链上交互的信任。
反方因素在于,直接损失规模目前尚难量化,且事件集中在特定代码平台用户群体,未必波及主流资产价格。市场情绪暂未出现明显联动。
接下来需要观察 Optimizely 的响应与修复进度、受影响站点的清理情况,以及是否出现更大规模的资金损失案例。安全事件的传导链条值得持续追踪,而非一次性关注。
#CryptoSecurity #WalletSecurity
以上为信息整理与个人分析,不构成投资建议。
一起通过第三方代码平台传导的钱包劫持事件正在蔓延,受影响站点已达 176 个,攻击链条从矿机延伸到普通网站,对散户资产安全构成系统性威胁。
据 Decrypt 报道,网站测试平台 Optimizely 被注入恶意代码,访问者在访问被污染页面时,其钱包地址会被悄悄替换为攻击者地址,导致转账资金流向对方。事件涉及 BBC 等知名站点,覆盖范围远超以往以矿机劫持为主的案例。
这一事件的重要性在于,它揭示了攻击方式的升级:过去钱包劫持多集中在算力挖矿场景,而此次通过 SaaS 代码平台传导,意味着任何使用该平台的网站都可能成为跳板。攻击链的扩散路径更加隐蔽,溯源与责任界定也更为复杂。
从数据看,被劫持站点数量为 176 个(据 Decrypt)。这意味着单个第三方服务的漏洞,可能被放大为跨站点、跨用户的规模化攻击。散户防范意识普遍不足,一旦地址被替换而未能察觉,直接损失难以追回。
对市场而言,此类安全事件的冲击通常有限,更多是局部信任扰动而非系统性风险。但考虑到加密基础设施对安全性的依赖,事件若持续扩散,或将影响用户对第三方工具与链上交互的信任。
反方因素在于,直接损失规模目前尚难量化,且事件集中在特定代码平台用户群体,未必波及主流资产价格。市场情绪暂未出现明显联动。
接下来需要观察 Optimizely 的响应与修复进度、受影响站点的清理情况,以及是否出现更大规模的资金损失案例。安全事件的传导链条值得持续追踪,而非一次性关注。
#CryptoSecurity #WalletSecurity
以上为信息整理与个人分析,不构成投资建议。
76
You approved it once. It's still active.
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
You approved it once. It's still active.
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
A token approval doesn't expire by itself. One approval covers one contract, one token, one network, and it stays there until you remove it.
A quick check:
— Type revoke.cash yourself. Don't tap a link
— Paste your public address. No wallet connection needed
— Pick a network. Approvals are per chain, so check each one you've used, $ETH side and $BNB side alike
— Sort by Allowance and find Unlimited
— Revoke what you no longer use
Keep it honest:
— Unlimited is a bigger risk, not proof of a hack
— Some apps need their approval, so don't revoke blindly
— Each revoke costs gas
— If your seed phrase is compromised, revoking is not enough: move to a new wallet
This is a how-to, not a verdict. No hallmark, no guarantees.
When did you last look at what your wallet still trusts?
#WalletSecurity #TokenApprovals #Web3Security #Revokecash
1
56

·
--
摩根士丹利高管直言,加密圈最大的安全漏洞不在代码,而在钱包安全差、治理失控和社会工程。天天盯着代码审计,结果连私钥管理得一塌糊涂,这种“人为刀俎我为鱼肉”才最致命。
#DeFi #WalletSecurity
摩根士丹利高管直言,加密圈最大的安全漏洞不在代码,而在钱包安全差、治理失控和社会工程。天天盯着代码审计,结果连私钥管理得一塌糊涂,这种“人为刀俎我为鱼肉”才最致命。
#DeFi #WalletSecurity
#DeFi #WalletSecurity
8
🚨 SAFE钱包疑遭密钥泄露失窃650万美元 🧠
📊 | $BTC | $ETH | $BNB |
- 关注并留言,分享你的观点 📈
- Safe钱包据报因私钥疑似泄露遭盗走650万美元
- Zodiac联合创始人称问题源于密钥失守与钱包权限设置过宽
- 其强调漏洞并非来自智能合约缺陷
- 事件再度凸显钱包权限管理与密钥安全的重要性 🔥
- 此次盗币或引发市场短期谨慎情绪
- 若调查确认属单一密钥失守,对Safe整体信任影响可能有限
- 预计大资金短期保持观望,鲸鱼动向趋于中性
- 短期市场大概率维持震荡格局
- 你认为加强私钥安全管理应作为优先吗?欢迎讨论
- 欢迎关注并留言,理性探讨市场变化
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
🚨 SAFE钱包疑遭密钥泄露失窃650万美元 🧠
📊 | $BTC | $ETH | $BNB |
- 关注并留言,分享你的观点 📈
- Safe钱包据报因私钥疑似泄露遭盗走650万美元
- Zodiac联合创始人称问题源于密钥失守与钱包权限设置过宽
- 其强调漏洞并非来自智能合约缺陷
- 事件再度凸显钱包权限管理与密钥安全的重要性 🔥
- 此次盗币或引发市场短期谨慎情绪
- 若调查确认属单一密钥失守,对Safe整体信任影响可能有限
- 预计大资金短期保持观望,鲸鱼动向趋于中性
- 短期市场大概率维持震荡格局
- 你认为加强私钥安全管理应作为优先吗?欢迎讨论
- 欢迎关注并留言,理性探讨市场变化
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
📊 | $BTC | $ETH | $BNB |
- 关注并留言,分享你的观点 📈
- Safe钱包据报因私钥疑似泄露遭盗走650万美元
- Zodiac联合创始人称问题源于密钥失守与钱包权限设置过宽
- 其强调漏洞并非来自智能合约缺陷
- 事件再度凸显钱包权限管理与密钥安全的重要性 🔥
- 此次盗币或引发市场短期谨慎情绪
- 若调查确认属单一密钥失守,对Safe整体信任影响可能有限
- 预计大资金短期保持观望,鲸鱼动向趋于中性
- 短期市场大概率维持震荡格局
- 你认为加强私钥安全管理应作为优先吗?欢迎讨论
- 欢迎关注并留言,理性探讨市场变化
#Crypto #WalletSecurity #DeFi #Whales #Blockchain
124

·
--
🚨 $ETH ECOSYSTEM SHIFT: NAVIGATING THE BLAST NETWORK SUNSET AND ASSET RECOVERY PROTOCOLS 🔍
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
🚨 $ETH ECOSYSTEM SHIFT: NAVIGATING THE BLAST NETWORK SUNSET AND ASSET RECOVERY PROTOCOLS 🔍
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
Structural shifts require absolute precision in asset management as network infrastructure evolves. With the upcoming discontinuation of network support on a major wallet interface, historical balances displayed on-chain may no longer reflect true liquidity access. 📊
Smart participants understand that interface cutoffs do not invalidate base-layer ownership. Eligible holders must route claims directly through official Ethereum mainnet recovery channels rather than relying on legacy UI dashboards. 🛡️
Security remains paramount during structural migrations. Never expose private credentials or interact with unverified third-party claim links masquerading as support tools. 💡 What steps are you taking to audit your cold and hot storage exposures before the upcoming network cutoff date? 🤔
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
🦈 🔒
12

·
--
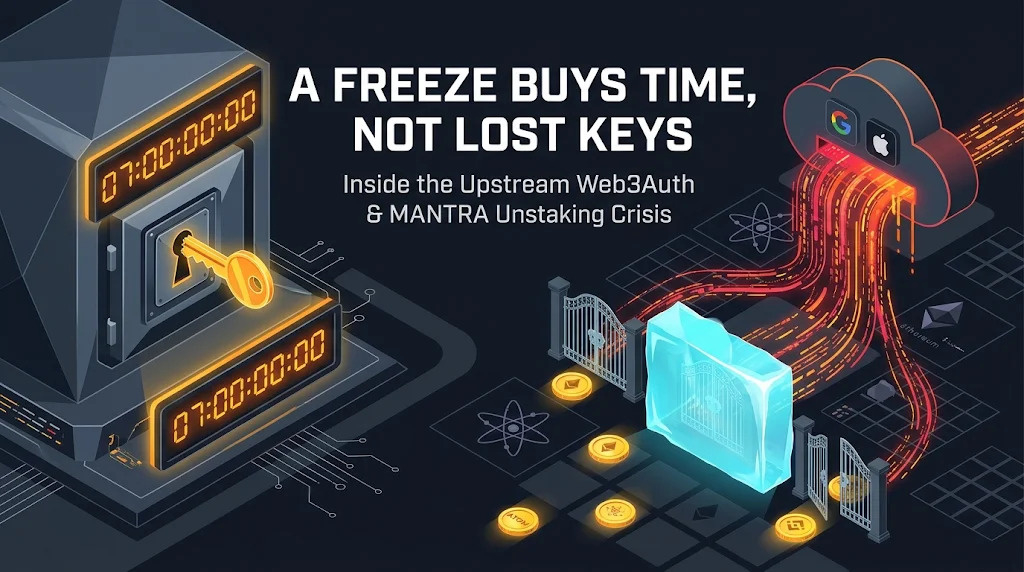
⚠️A seven-day unstaking freeze cannot reverse a stolen private key. It can only buy time.
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
{future}(MANTRAUSDT)
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
⚠️A seven-day unstaking freeze cannot reverse a stolen private key. It can only buy time.
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
On November 13, MANTRA paused all new unbonding transactions for seven days after reports that attackers were withdrawing staked MANTRA from compromised Keplr social-login wallets. It does not cancel withdrawals already in the eight-day unbonding queue.
MANTRA says affected holders must redelegate before that timer expires.
The weakness sits upstream: Web3Auth's embedded-wallet infrastructure, used by Keplr's Google/Apple login. Keplr says recovery-phrase and hardware-wallet accounts were not affected.
This is not evidence that Google or Apple accounts themselves were hacked.
Bitquery's November 12 investigation traced at least $1.82M taken between November 1–12 from 7,842 Cosmos wallets, 52 Ethereum wallets and 13 Hyperliquid accounts. More than $1.01M left before Web3Auth's first rescue sweep. Separately, Web3Auth moved roughly $6M into recovery wallets. That $6M is not a confirmed theft total.
The missing pieces are the technical root cause, final loss reconciliation and a confirmed return timetable.
MANTRA also suffered a separate upstream chain-accounting exploit in August. Different cause, but repeated security shocks across different layers matter for trust.
The freeze restricts exits; it does not repair compromised keys or protect every other chain.
Not financial advice.
$MANTRA
#MANTRAPausesUnstakingFor7DaysAfterKeplrSecurityIncident #mantra #WalletSecurity #CosmosEcosystem
1
423

·
--
Bearish
MANTRA PAUSED UNSTAKING — BUT SOME WITHDRAWAL CLOCKS ARE STILL RUNNING
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
{future}(MANTRAUSDT)
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
{spot}(MANTRAUSDT)
$MANTRA #WalletSecurity #CryptoSecurity
MANTRA PAUSED UNSTAKING — BUT SOME WITHDRAWAL CLOCKS ARE STILL RUNNING
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
$MANTRA #WalletSecurity #CryptoSecurity
Imagine having your crypto locked in staking, only to discover someone else has started withdrawing it
That's the situation MANTRA is trying to contain
$MANTRA
⚠️ Following reports of compromised Web3Auth and Keplr wallet access, MANTRA announced a 7-day emergency pause on new unstaking requests
Attackers reportedly stole liquid tokens before initiating unauthorized unstaking of $OM
But there's a dangerous exception
Existing unstaking requests are NOT frozen
The 8-day withdrawal countdown continues, potentially allowing attackers with compromised keys to claim the tokens when they become available
🔐 MANTRA has urged affected users to redelegate before that countdown ends
Redelegation may stop an ongoing withdrawal, but it cannot make an exposed private key secure again
Not every Keplr wallet is necessarily compromised
If you're affected, check your staking status and follow official recovery instructions — never enter your recovery phrase into an unsolicited website
A temporary pause buys time
What users do with that time matters
$MANTRA #WalletSecurity #CryptoSecurity
419

⚠️ $MANTRA PAUSED UNSTAKING WHILE ATTACKERS KEEP THE CLOCK TICKING 🦈
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
⚠️ $MANTRA PAUSED UNSTAKING WHILE ATTACKERS KEEP THE CLOCK TICKING 🦈
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
📊 The 7‑day emergency pause bought a narrow window, but the 8‑day withdrawal countdown stays alive, letting compromised keys still pull liquid tokens. 🕵️♂️ Smart money is already scanning the order flow for any residual exits, and volume spikes could signal a last‑minute sweep.
💡 Redelegate now if you spot an active request – it can halt the pending pull, though it won’t patch a leaked . Stay razor‑sharp, audit your Keplr access, and keep the recovery steps locked down. 🤔 Are you redelegating before the timer runs out?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #MANTRA #WalletSecurity #Staking #Crypto
🦈 🔥
14
On 31 October 2024, one SMS stopped a thief mid-withdrawal.
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB. The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
On 31 October 2024, one SMS stopped a thief mid-withdrawal.
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB . The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
About $2,000 was taken from our founder in total, including 1.088 BNB. It was stolen from MetaMask, Trust Wallet and an OKX account.
On HTX, the attacker got into the account and converted the assets to $BNB . The withdrawal still failed: an SMS confirmation went to a separate phone number.
We could not establish how they got in. Working hypothesis: the laptop, handed to a stranger for repair, running unlicensed Windows with no antivirus. Circumstances, not a proven cause.
This is not a claim that SMS is strong. SIM-swaps exist. It is one narrow observation: a separate channel stopped the withdrawal. That is all the first C·H·A·O· hallmark on HTX says. It is not a security audit of the exchange.
The lesson: don't trust, verify. Nihil sine probatione.
So Cirqus Intelligence is launching The Cirqus Register. It publishes shifts, not news. Every forecast gets a date and a criterion for whether it came true. Once a month we check our own calls, misses first. No trading signals, no price calls.
The Q is not a typo. It's the lens.
AI agents help with research, a Verifier checks the claims, and a human approves every issue.
Which of your withdrawals still depends on a single device?
#CryptoSecurity #Binance #WalletSecurity #CirqusRegister
1
134

·
--
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting Isn’t the Same as Revoking Wallet Permissions
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
Disconnecting from a DeFi app does not necessarily revoke the permission you gave it. Ethereum.org says token allowances can remain active after you disconnect—and may have no expiry. An unlimited approval can let a contract spend all of that token type held in your wallet. Binance Academy recommends reviewing approval requests carefully and revoking permissions you no longer need.
That makes approval hygiene a separate security habit: check the contract before signing, limit the amount where your wallet allows it, and review allowances on each network. Revocation is an on-chain transaction and can require a network fee.
My take: do not assume “disconnect” means “revoke.” Do you audit your wallet approvals regularly?
Sources: Ethereum.org — https://ethereum.org/guides/how-to-revoke-token-access/ | Binance Academy — https://academy.binance.com/en/articles/how-to-spot-scams-in-decentralized-finance-defi
#Cybersecurity #DeFi #WalletSecurity
7
·
--
Bearish
🚨 A $SUI hardware wallet was ready to ship — now the entire project is shutting down
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
{future}(SUIUSDT)
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
{spot}(SUIUSDT)
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
🚨 A $SUI hardware wallet was ready to ship — now the entire project is shutting down
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
Suiball has announced the cancellation of its hardware wallet launch and promised USDC refunds for all pre-orders
The team says security concerns led the Sui Foundation to withdraw support
But the most important detail for customers is HOW they paid 👇
$SUI
🔹 On-chain pre-orders — Around 80% of orders will receive automatic USDC refunds to wallets holding their soulbound reservation NFTs
No claim or wallet connection required
🔹 Credit-card pre-orders — Customers will receive an email requesting a Sui wallet address for a separate refund distribution
⚠️ Suiball says it will NEVER request seed phrases, private keys or additional payments
Verify communications through official channels before responding
A refund email can be spoofed — even when the sender looks familiar
This is a hardware wallet project shutdown, NOT evidence that the Sui blockchain itself was hacked
The next milestone is confirmed refund transactions, not another promise
A scheduled refund isn't the same as money returned
$SUI #SUİ #WalletSecurity
233
Multiple Bitcoin keys do not help much if one theft exposes all of them.
A multisignature wallet can require several independent approvals before spending $BTC. For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
Multiple Bitcoin keys do not help much if one theft exposes all of them.
A multisignature wallet can require several independent approvals before spending $BTC . For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
A multisignature wallet can require several independent approvals before spending $BTC . For example, a two-of-three setup needs any two signing keys—not just a password on one device.
The practical benefit is separation: stealing one key alone is insufficient. But keeping every key and backup together can undermine that protection.
Before choosing this setup, map which devices and locations could fail together. Then check whether enough signing keys would remain available to recover access.
The trade-off is complexity: losing access to too many keys can lock you out. Multisignature changes the security design; it does not remove the need for careful backups.
Source: Bitcoin.org — https://bitcoin.org/en/secure-your-wallet
#Bitcoin #WalletSecurity #Multisig #CryptoEducation #SelfCustody
69

AN ELEVEN-YEAR DORMANT $ETH WHALE JUST WOKE UP AND DODGED A DEADLY TRAP 🚨
When ancient capital stirs after a decade of hibernation, predatory eyes circle instantly. A dormant $ETH wallet executed a minor test transfer, and within minutes, malicious actors flooded its ledger with lookalike dust addresses designed to mimic recent counterparties 🦈.
This poisoning tactic weaponizes human habit by planting microscopic replicas inside your transaction history. While this whale spotted the counterfeit destination and secured their stack safely, trusting recent UI records without independent verification remains a dangerous blind spot.
Are you double checking the full destination address every single time, or relying blindly on your recent transaction dropdown 👇?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
💎
AN ELEVEN-YEAR DORMANT $ETH WHALE JUST WOKE UP AND DODGED A DEADLY TRAP 🚨
When ancient capital stirs after a decade of hibernation, predatory eyes circle instantly. A dormant $ETH wallet executed a minor test transfer, and within minutes, malicious actors flooded its ledger with lookalike dust addresses designed to mimic recent counterparties 🦈.
This poisoning tactic weaponizes human habit by planting microscopic replicas inside your transaction history. While this whale spotted the counterfeit destination and secured their stack safely, trusting recent UI records without independent verification remains a dangerous blind spot.
Are you double checking the full destination address every single time, or relying blindly on your recent transaction dropdown 👇?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
💎
When ancient capital stirs after a decade of hibernation, predatory eyes circle instantly. A dormant $ETH wallet executed a minor test transfer, and within minutes, malicious actors flooded its ledger with lookalike dust addresses designed to mimic recent counterparties 🦈.
This poisoning tactic weaponizes human habit by planting microscopic replicas inside your transaction history. While this whale spotted the counterfeit destination and secured their stack safely, trusting recent UI records without independent verification remains a dangerous blind spot.
Are you double checking the full destination address every single time, or relying blindly on your recent transaction dropdown 👇?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #WalletSecurity #Crypto #SmartMoney
💎
3
·
--
Bearish
🚨 An Ethereum wallet dormant for 11 YEARS moved $4.6 MILLION — and scammers were waiting within 3 minutes
On November 9, the wallet sent a small 0.05 $ETH test transaction
Almost immediately, two lookalike addresses started flooding its transaction history with tiny payments
One reportedly sent 43 dust transfers
The attack wasn't about stealing a private key 🔐
{future}(ETHUSDT)
It targeted something far simpler — copying a recipient address from recent transactions
Both fake addresses resembled the legitimate destination
But the wallet ultimately transferred 2,154.94 $ETH to the correct address, avoiding the trap
⚠️ The overlooked lesson?
A successful test transfer doesn't protect you if you copy a poisoned address for the next transaction
Before moving serious funds, compare the FULL destination address against a trusted, independently verified source
Never rely solely on recent transaction history
Your wallet can be technically secure while one copy-paste mistake puts everything at risk
{spot}(ETHUSDT)
$ETH #Ethereum #WalletSecurity
🚨 An Ethereum wallet dormant for 11 YEARS moved $4.6 MILLION — and scammers were waiting within 3 minutes
On November 9, the wallet sent a small 0.05 $ETH test transaction
Almost immediately, two lookalike addresses started flooding its transaction history with tiny payments
One reportedly sent 43 dust transfers
The attack wasn't about stealing a private key 🔐
It targeted something far simpler — copying a recipient address from recent transactions
Both fake addresses resembled the legitimate destination
But the wallet ultimately transferred 2,154.94 $ETH to the correct address, avoiding the trap
⚠️ The overlooked lesson?
A successful test transfer doesn't protect you if you copy a poisoned address for the next transaction
Before moving serious funds, compare the FULL destination address against a trusted, independently verified source
Never rely solely on recent transaction history
Your wallet can be technically secure while one copy-paste mistake puts everything at risk
$ETH #Ethereum #WalletSecurity
On November 9, the wallet sent a small 0.05 $ETH test transaction
Almost immediately, two lookalike addresses started flooding its transaction history with tiny payments
One reportedly sent 43 dust transfers
The attack wasn't about stealing a private key 🔐
It targeted something far simpler — copying a recipient address from recent transactions
Both fake addresses resembled the legitimate destination
But the wallet ultimately transferred 2,154.94 $ETH to the correct address, avoiding the trap
⚠️ The overlooked lesson?
A successful test transfer doesn't protect you if you copy a poisoned address for the next transaction
Before moving serious funds, compare the FULL destination address against a trusted, independently verified source
Never rely solely on recent transaction history
Your wallet can be technically secure while one copy-paste mistake puts everything at risk
$ETH #Ethereum #WalletSecurity
11

·
--
Binance紧急提醒!iPhone用户注意:iOS存在名为"worse_query"的安全漏洞,恶意应用可窃取你钱包的助记词和私钥!最可怕的是,苹果11月9日的更新压根没提这事!赶紧检查你的钱包安全,别让黑客轻松盗走你的$BTC和$BNB!
Binance just dropped a serious warning for iPhone users! There's an iOS flaw called "worse_query" that lets malicious apps steal your wallet seed phrases and private keys. Scariest part? Apple's Nov. 9 update doesn't even mention this bug! Check your wallet security now and don't let hackers easily grab your $BTC and $BNB!
#cryptosecurity #walletsecurity #iOSsecurity
Binance紧急提醒!iPhone用户注意:iOS存在名为"worse_query"的安全漏洞,恶意应用可窃取你钱包的助记词和私钥!最可怕的是,苹果11月9日的更新压根没提这事!赶紧检查你的钱包安全,别让黑客轻松盗走你的$BTC 和$BNB !
Binance just dropped a serious warning for iPhone users! There's an iOS flaw called "worse_query" that lets malicious apps steal your wallet seed phrases and private keys. Scariest part? Apple's Nov. 9 update doesn't even mention this bug! Check your wallet security now and don't let hackers easily grab your $BTC and $BNB !
#cryptosecurity #walletsecurity #iOSsecurity
Binance just dropped a serious warning for iPhone users! There's an iOS flaw called "worse_query" that lets malicious apps steal your wallet seed phrases and private keys. Scariest part? Apple's Nov. 9 update doesn't even mention this bug! Check your wallet security now and don't let hackers easily grab your $BTC and $BNB !
#cryptosecurity #walletsecurity #iOSsecurity
556

·
--
Keplr paused Google and Apple login after unauthorized transactions on some social-login wallets, and Web3Auth says a $6.01 million theft figure included recovery transfers.
Web3Auth disclosed a security issue at about 21:13 UTC on November 6, 2026, and paused its embedded wallet product. Keplr said around 04:38 UTC on November 7 that some Google and Apple login accounts had unauthorized transactions, and it paused those sign-in options. Co-founder Josh Lee said Keplr's own code was not hacked, estimating about 20% of social-login accounts were affected and only a fraction fully exploited. Recovery-phrase and hardware-wallet accounts were not affected, and Web3Auth found no evidence MetaMask users were impacted.
On November 8, Web3Auth disputed the $6.01 million theft estimate, saying some drains were protective recoveries into verified wallets. It published recovery addresses across eleven Cosmos-based networks and eight EVM-compatible chains. Keplr told social-login users not to send new funds to those accounts, not to re-import them, and to ignore unofficial recovery messages.
#Crypto #WalletSecurity #Keplr
DYOR. Not financial advice.
Keplr paused Google and Apple login after unauthorized transactions on some social-login wallets, and Web3Auth says a $6.01 million theft figure included recovery transfers.
Web3Auth disclosed a security issue at about 21:13 UTC on November 6, 2026, and paused its embedded wallet product. Keplr said around 04:38 UTC on November 7 that some Google and Apple login accounts had unauthorized transactions, and it paused those sign-in options. Co-founder Josh Lee said Keplr's own code was not hacked, estimating about 20% of social-login accounts were affected and only a fraction fully exploited. Recovery-phrase and hardware-wallet accounts were not affected, and Web3Auth found no evidence MetaMask users were impacted.
On November 8, Web3Auth disputed the $6.01 million theft estimate, saying some drains were protective recoveries into verified wallets. It published recovery addresses across eleven Cosmos-based networks and eight EVM-compatible chains. Keplr told social-login users not to send new funds to those accounts, not to re-import them, and to ignore unofficial recovery messages.
#Crypto #WalletSecurity #Keplr
DYOR. Not financial advice.
Web3Auth disclosed a security issue at about 21:13 UTC on November 6, 2026, and paused its embedded wallet product. Keplr said around 04:38 UTC on November 7 that some Google and Apple login accounts had unauthorized transactions, and it paused those sign-in options. Co-founder Josh Lee said Keplr's own code was not hacked, estimating about 20% of social-login accounts were affected and only a fraction fully exploited. Recovery-phrase and hardware-wallet accounts were not affected, and Web3Auth found no evidence MetaMask users were impacted.
On November 8, Web3Auth disputed the $6.01 million theft estimate, saying some drains were protective recoveries into verified wallets. It published recovery addresses across eleven Cosmos-based networks and eight EVM-compatible chains. Keplr told social-login users not to send new funds to those accounts, not to re-import them, and to ignore unofficial recovery messages.
#Crypto #WalletSecurity #Keplr
DYOR. Not financial advice.
AAPL+0.64%
GOOGUS+0.71%
201
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaBeatsEstimatesWith$130BQ4Outlook
52,752 views
274 Discussing
2
#AnthropicIPOPriceCouldExceed$80
54,874 views
236 Discussing
3
#RussiaCentralBankAddsAlfaBankToCryptoExchangeRegister
3,034 views
43 Discussing
4
#RussianCentralBankPlansToAllowFundsToHoldCryptoIn2027
2,021 views
33 Discussing
5
#VisaPlansStablecoinPrefundingForAPACCrossBorderPayments
3,466 views
34 Discussing
6
#CanNvidia’sDataCenterGrowthContinue?
141,768 views
1,418 Discussing
7
#CanadaAndUSLaunchOperationNiagaraAgainstApprovalPhishing
31,972 views
54 Discussing
8
#BankOfEnglandUnveilsClearingHousePathwayCoveringDLTFirms
4,177 views
66 Discussing
9
#DBSAndCirclePartnerToExpandAsianInstitutionsUSDCAccess
5,287 views
66 Discussing
10
#LedgerHardwareImplantReportsExtendToDubai
82,712 views
806 Discussing