
#supplychainattack
supplychainattack
11,303 views
37 Discussing
Hot
Latest
·
--
The security promise that a hardware wallet is “not connected to the internet” was broken before it was even unboxed.
A new disclosure on October 18 has widened the scope of this supply-chain attack: a Ledger Flex wallet purchased at Singapore Changi Airport was found to have a modified display connector and a cellular communications chip with a SIM card. Tainted devices may have entered regular retail channels in multiple countries, no longer limited to the single distributor initially identified.
Timeline: Starting October 9, more than 300 wallets were drained in a short period. Estimates from third-party on-chain research firms range from $80 million to $93.2 million: Bitquery counted 315 wallets and approximately $93.2 million; Galaxy Digital estimated approximately $90 million; Specter estimated $86 million; and Arkham estimated $80 million (as cited in a CoinDesk report dated 2026-10-12). Around $70 million of the victims’ funds was USDT on the Tron network, with the rest spread across BTC, ETH, BNB, SOL, and Polygon.
The method is worth noting: the implant was a small circuit board hidden behind the screen, with its own cellular capabilities. During setup, the screen displays the 24-word recovery phrase—the implant captures the phrase and sends it directly to the attackers via LTE/eSIM, bypassing the user’s computer and Wi-Fi entirely. The attackers then use the 24 words to restore the wallet elsewhere and transfer the funds.
On October 10, Ledger officially confirmed that at least one affected device contained an unauthorized hardware implant. So far, all confirmed cases have come through Southeast Asian distributor CryptoBilis (Malaysia, Indonesia, and the Philippines); the company’s own systems and direct sales channels were not affected. CryptoBilis has stopped selling all hardware wallets, and its Kuala Lumpur store has temporarily closed.
What we can see is that it was never the secure chip that was compromised, but the “chain of trust”—trust that the box is factory-sealed, trust in the words “official authorized distributor.” Ledger has warned CryptoBilis customers not to power on devices that have not yet been initialized, and advised those who have already activated theirs to move their funds to a new device purchased directly from the official website, using a new recovery phrase.
In terms of perspective: after this incident, inspecting a hardware wallet out of the box may need to be treated like checking precision equipment. The narrative that cold wallets are “absolutely secure” has been repriced, but what’s being repriced is not the hardware itself—it’s the trustworthiness of the distribution channel. $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(Data sources: CoinDesk 10-12, CryptoBriefing 10-13, estimates by researchers at Bitquery/Specter/Arkham/Galaxy, and independent researchers’ findings relayed by Sina Finance on 10-18. Loss figures are third-party estimates; Ledger has not released an official loss figure. Personal opinions only; not investment advice.)
The security promise that a hardware wallet is “not connected to the internet” was broken before it was even unboxed.
A new disclosure on October 18 has widened the scope of this supply-chain attack: a Ledger Flex wallet purchased at Singapore Changi Airport was found to have a modified display connector and a cellular communications chip with a SIM card. Tainted devices may have entered regular retail channels in multiple countries, no longer limited to the single distributor initially identified.
Timeline: Starting October 9, more than 300 wallets were drained in a short period. Estimates from third-party on-chain research firms range from $80 million to $93.2 million: Bitquery counted 315 wallets and approximately $93.2 million; Galaxy Digital estimated approximately $90 million; Specter estimated $86 million; and Arkham estimated $80 million (as cited in a CoinDesk report dated 2026-10-12). Around $70 million of the victims’ funds was USDT on the Tron network, with the rest spread across BTC, ETH, BNB, SOL, and Polygon.
The method is worth noting: the implant was a small circuit board hidden behind the screen, with its own cellular capabilities. During setup, the screen displays the 24-word recovery phrase—the implant captures the phrase and sends it directly to the attackers via LTE/eSIM, bypassing the user’s computer and Wi-Fi entirely. The attackers then use the 24 words to restore the wallet elsewhere and transfer the funds.
On October 10, Ledger officially confirmed that at least one affected device contained an unauthorized hardware implant. So far, all confirmed cases have come through Southeast Asian distributor CryptoBilis (Malaysia, Indonesia, and the Philippines); the company’s own systems and direct sales channels were not affected. CryptoBilis has stopped selling all hardware wallets, and its Kuala Lumpur store has temporarily closed.
What we can see is that it was never the secure chip that was compromised, but the “chain of trust”—trust that the box is factory-sealed, trust in the words “official authorized distributor.” Ledger has warned CryptoBilis customers not to power on devices that have not yet been initialized, and advised those who have already activated theirs to move their funds to a new device purchased directly from the official website, using a new recovery phrase.
In terms of perspective: after this incident, inspecting a hardware wallet out of the box may need to be treated like checking precision equipment. The narrative that cold wallets are “absolutely secure” has been repriced, but what’s being repriced is not the hardware itself—it’s the trustworthiness of the distribution channel. $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(Data sources: CoinDesk 10-12, CryptoBriefing 10-13, estimates by researchers at Bitquery/Specter/Arkham/Galaxy, and independent researchers’ findings relayed by Sina Finance on 10-18. Loss figures are third-party estimates; Ledger has not released an official loss figure. Personal opinions only; not investment advice.)
A new disclosure on October 18 has widened the scope of this supply-chain attack: a Ledger Flex wallet purchased at Singapore Changi Airport was found to have a modified display connector and a cellular communications chip with a SIM card. Tainted devices may have entered regular retail channels in multiple countries, no longer limited to the single distributor initially identified.
Timeline: Starting October 9, more than 300 wallets were drained in a short period. Estimates from third-party on-chain research firms range from $80 million to $93.2 million: Bitquery counted 315 wallets and approximately $93.2 million; Galaxy Digital estimated approximately $90 million; Specter estimated $86 million; and Arkham estimated $80 million (as cited in a CoinDesk report dated 2026-10-12). Around $70 million of the victims’ funds was USDT on the Tron network, with the rest spread across BTC, ETH, BNB, SOL, and Polygon.
The method is worth noting: the implant was a small circuit board hidden behind the screen, with its own cellular capabilities. During setup, the screen displays the 24-word recovery phrase—the implant captures the phrase and sends it directly to the attackers via LTE/eSIM, bypassing the user’s computer and Wi-Fi entirely. The attackers then use the 24 words to restore the wallet elsewhere and transfer the funds.
On October 10, Ledger officially confirmed that at least one affected device contained an unauthorized hardware implant. So far, all confirmed cases have come through Southeast Asian distributor CryptoBilis (Malaysia, Indonesia, and the Philippines); the company’s own systems and direct sales channels were not affected. CryptoBilis has stopped selling all hardware wallets, and its Kuala Lumpur store has temporarily closed.
What we can see is that it was never the secure chip that was compromised, but the “chain of trust”—trust that the box is factory-sealed, trust in the words “official authorized distributor.” Ledger has warned CryptoBilis customers not to power on devices that have not yet been initialized, and advised those who have already activated theirs to move their funds to a new device purchased directly from the official website, using a new recovery phrase.
In terms of perspective: after this incident, inspecting a hardware wallet out of the box may need to be treated like checking precision equipment. The narrative that cold wallets are “absolutely secure” has been repriced, but what’s being repriced is not the hardware itself—it’s the trustworthiness of the distribution channel. $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(Data sources: CoinDesk 10-12, CryptoBriefing 10-13, estimates by researchers at Bitquery/Specter/Arkham/Galaxy, and independent researchers’ findings relayed by Sina Finance on 10-18. Loss figures are third-party estimates; Ledger has not released an official loss figure. Personal opinions only; not investment advice.)
81

HACKERS COMPROMISED THE OFFICIAL $INJ DEVELOPER KIT — 310 DOWNLOADS ⚠️
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
HACKERS COMPROMISED THE OFFICIAL $INJ DEVELOPER KIT — 310 DOWNLOADS ⚠️
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
1
221

Major Security Breach Hits Ledger Supply Chain
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
Major Security Breach Hits Ledger Supply Chain
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
4

·
--
Polymarket Vendor Compromised — Attackers Drained $2.9M From Wallets
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
Polymarket Vendor Compromised — Attackers Drained $2.9M From Wallets
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
1
44

·
--
$INJ SDK COMPROMISED — 50,000 WEEKLY DOWNLOADS AFFECTED ⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
$INJ SDK COMPROMISED — 50,000 WEEKLY DOWNLOADS AFFECTED ⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
137

·
--
30 MALICIOUS NPM PACKAGES TARGETING $ETH DEVELOPERS FOUND 🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
30 MALICIOUS NPM PACKAGES TARGETING $ETH DEVELOPERS FOUND 🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
16
Ledger Hardware Implant Discovery Is A Security Nightmare
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
Ledger Hardware Implant Discovery Is A Security Nightmare
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
54
·
--
#ledgerpausescryptobilissales 🚨
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
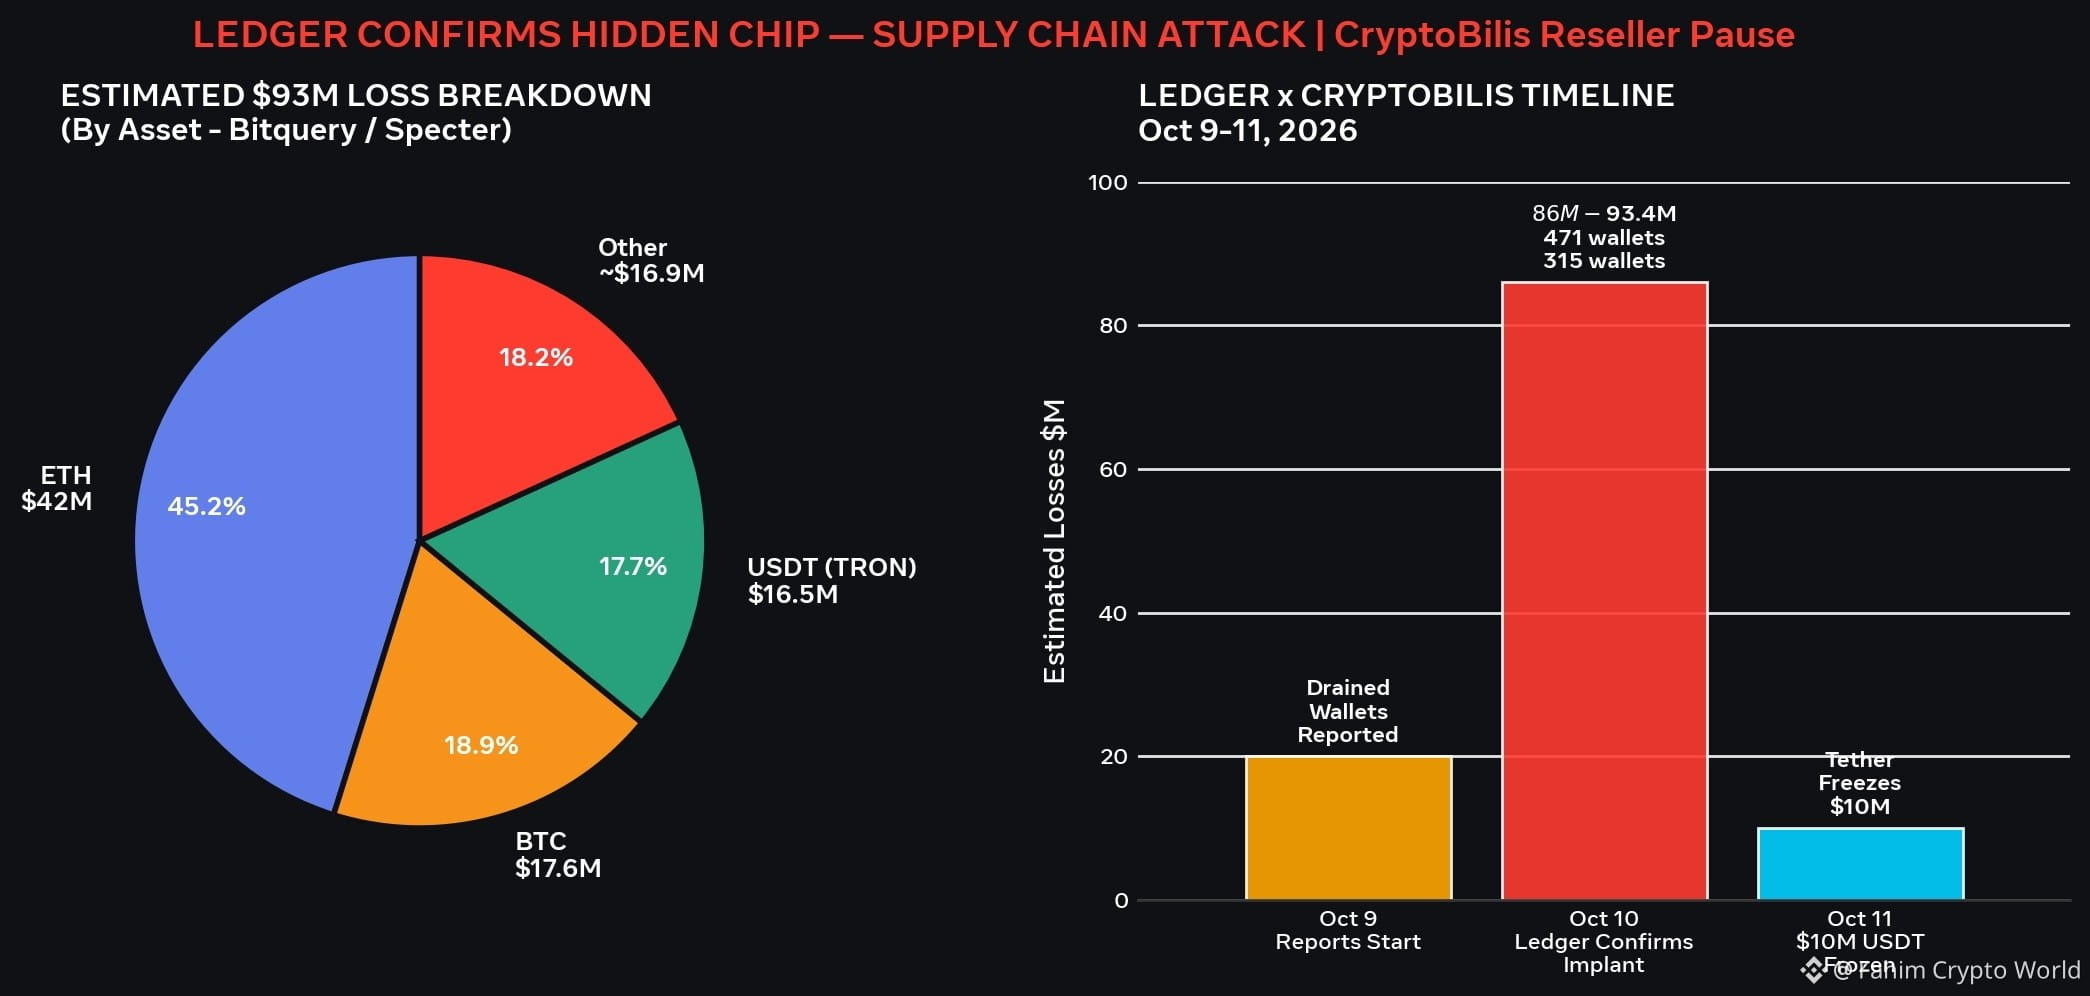
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
#ledgerpausescryptobilissales 🚨
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
40
·
--
#optimjackattackinfectsatleast186websites
The "OptimJack" Attack: A Wake-Up Call for Web Security
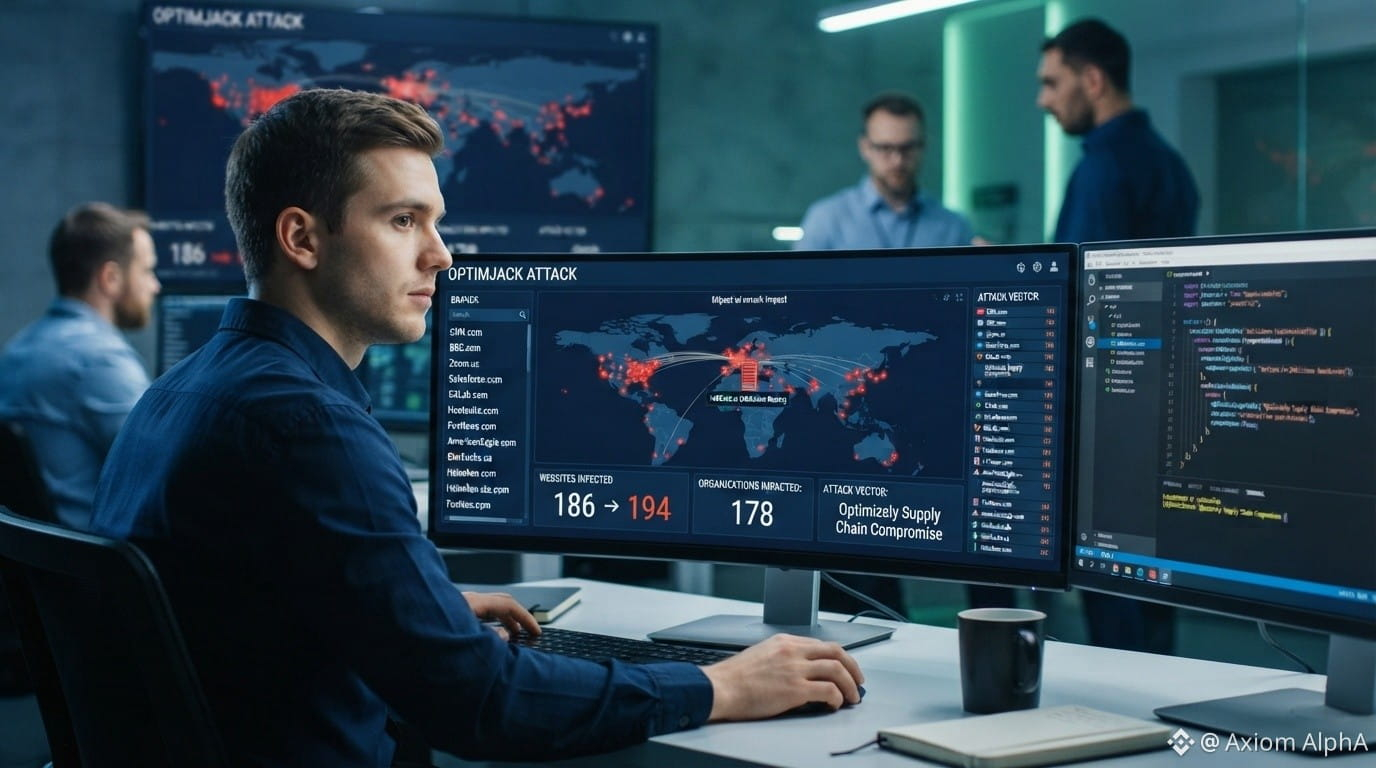
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
{spot}(LINKUSDT)
{spot}(CVCUSDT)
{spot}(QNTUSDT)
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
#optimjackattackinfectsatleast186websites
The "OptimJack" Attack: A Wake-Up Call for Web Security
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
The "OptimJack" Attack: A Wake-Up Call for Web Security
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
226
Ledger cold wallets suspected of being tampered with; users lose around $90 million
Shocking news has rocked the crypto community as numerous cold-wallet users suddenly found their assets completely drained, with estimated losses reaching as much as $90 million.
Hot spot: the distributor:
According to reports, most of the cases involving lost funds in Southeast Asia were linked to products purchased from a retailer called CryptoBillis.
The cause, according to CZ:
Former Binance chief CZ believes this may have been a localized supply-chain attack. It is highly possible that users bought counterfeit Ledger wallets or devices whose hardware had been tampered with or had recovery phrases (seed phrases) pre-installed by bad actors before reaching consumers.
A costly lesson:
This incident is an extremely serious warning for crypto enthusiasts: even cold wallets, considered a “security fortress,” can become a trap if they are not purchased from an official source.
In short, keeping your money in a cold wallet still carries risks if the device has been “rigged” during shipping, so you should carefully check where your device came from.
This post is just for entertaining news and gossip; it is absolutely not investment advice or security guidance. If you happened to buy a cold wallet at the corner grocery store and your assets vanished, please go find the seller yourself—the admin doesn’t have the keys to the safe.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
Ledger cold wallets suspected of being tampered with; users lose around $90 million
Shocking news has rocked the crypto community as numerous cold-wallet users suddenly found their assets completely drained, with estimated losses reaching as much as $90 million.
Hot spot: the distributor:
According to reports, most of the cases involving lost funds in Southeast Asia were linked to products purchased from a retailer called CryptoBillis.
The cause, according to CZ:
Former Binance chief CZ believes this may have been a localized supply-chain attack. It is highly possible that users bought counterfeit Ledger wallets or devices whose hardware had been tampered with or had recovery phrases (seed phrases) pre-installed by bad actors before reaching consumers.
A costly lesson:
This incident is an extremely serious warning for crypto enthusiasts: even cold wallets, considered a “security fortress,” can become a trap if they are not purchased from an official source.
In short, keeping your money in a cold wallet still carries risks if the device has been “rigged” during shipping, so you should carefully check where your device came from.
This post is just for entertaining news and gossip; it is absolutely not investment advice or security guidance. If you happened to buy a cold wallet at the corner grocery store and your assets vanished, please go find the seller yourself—the admin doesn’t have the keys to the safe.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
Shocking news has rocked the crypto community as numerous cold-wallet users suddenly found their assets completely drained, with estimated losses reaching as much as $90 million.
Hot spot: the distributor:
According to reports, most of the cases involving lost funds in Southeast Asia were linked to products purchased from a retailer called CryptoBillis.
The cause, according to CZ:
Former Binance chief CZ believes this may have been a localized supply-chain attack. It is highly possible that users bought counterfeit Ledger wallets or devices whose hardware had been tampered with or had recovery phrases (seed phrases) pre-installed by bad actors before reaching consumers.
A costly lesson:
This incident is an extremely serious warning for crypto enthusiasts: even cold wallets, considered a “security fortress,” can become a trap if they are not purchased from an official source.
In short, keeping your money in a cold wallet still carries risks if the device has been “rigged” during shipping, so you should carefully check where your device came from.
This post is just for entertaining news and gossip; it is absolutely not investment advice or security guidance. If you happened to buy a cold wallet at the corner grocery store and your assets vanished, please go find the seller yourself—the admin doesn’t have the keys to the safe.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
237

⚠️ Malware attack targets Vite via malicious npm packages
Cybersecurity researchers have discovered seven malicious npm packages targeting the Vite frontend tooling environment in a software supply chain attack. These packages use Blockchain C2 technology to deliver RAT malware, highlighting the growing risks in the software development ecosystem.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 Source: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
⚠️ Malware attack targets Vite via malicious npm packages
Cybersecurity researchers have discovered seven malicious npm packages targeting the Vite frontend tooling environment in a software supply chain attack. These packages use Blockchain C2 technology to deliver RAT malware, highlighting the growing risks in the software development ecosystem.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 Source: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
Cybersecurity researchers have discovered seven malicious npm packages targeting the Vite frontend tooling environment in a software supply chain attack. These packages use Blockchain C2 technology to deliver RAT malware, highlighting the growing risks in the software development ecosystem.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 Source: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
44
🚨 QuickFox attack exploits supply chain to deploy FDMTP malware
The incident response team at FortiGuard Labs has revealed details of a cyberattack targeting the supply chain, in which modified Windows installer tools were used to compromise systems. This attack is known as QuickFox, and it deployed an advanced piece of malicious software called FDMTP, targeting specific victims with sophisticated methods.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 Source: fortinet.com
🚨 QuickFox attack exploits supply chain to deploy FDMTP malware
The incident response team at FortiGuard Labs has revealed details of a cyberattack targeting the supply chain, in which modified Windows installer tools were used to compromise systems. This attack is known as QuickFox, and it deployed an advanced piece of malicious software called FDMTP, targeting specific victims with sophisticated methods.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 Source: fortinet.com
The incident response team at FortiGuard Labs has revealed details of a cyberattack targeting the supply chain, in which modified Windows installer tools were used to compromise systems. This attack is known as QuickFox, and it deployed an advanced piece of malicious software called FDMTP, targeting specific victims with sophisticated methods.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 Source: fortinet.com
14
$INJ SDK BACKDOOR – 310 DOWNLOADS OF MALICIOUS CODE BEFORE FIX 🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
$INJ SDK BACKDOOR – 310 DOWNLOADS OF MALICIOUS CODE BEFORE FIX 🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
116
·
--
Ledger confirms presence of unauthorized hardware device in supply chain theft investigation
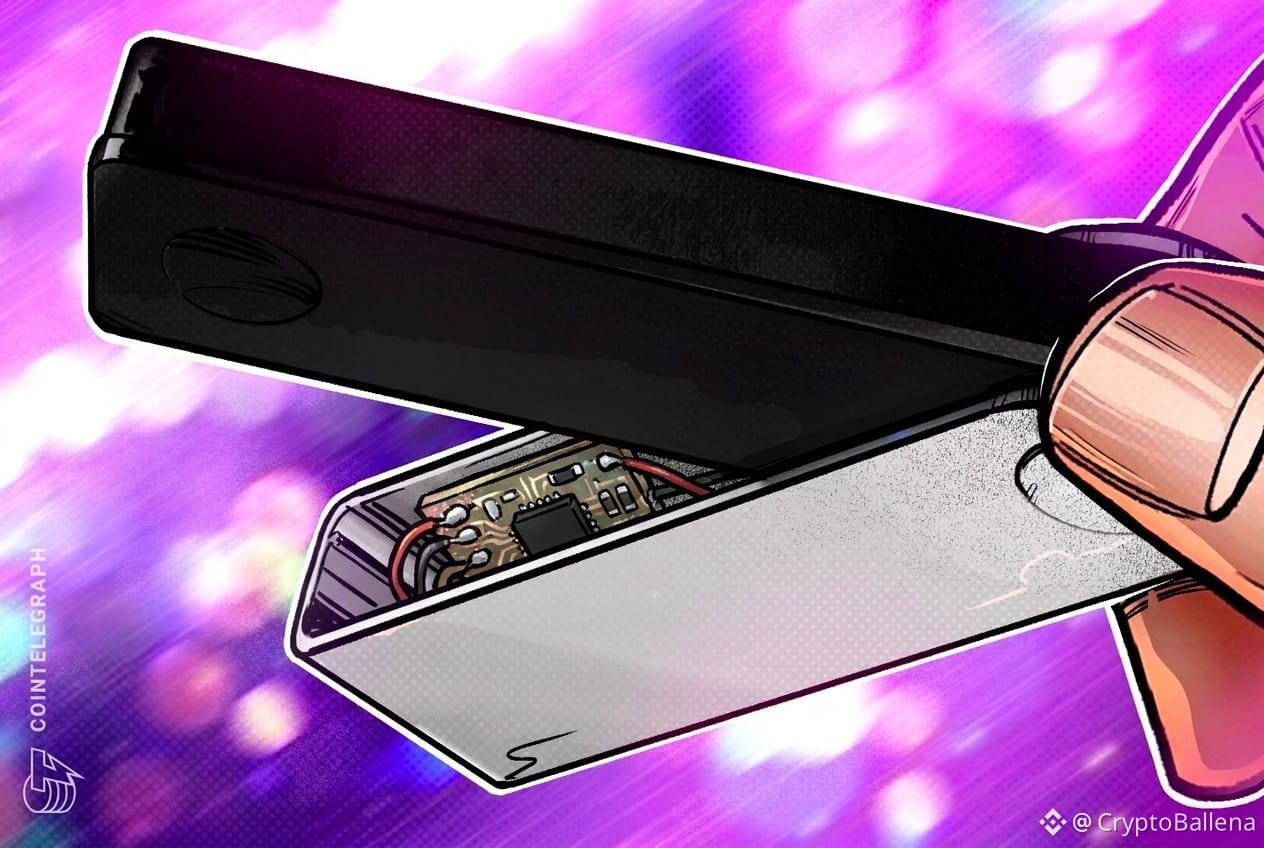
Ledger has confirmed the discovery of an unauthorized hardware device installed inside a cryptocurrency wallet linked to an ongoing theft investigation, pointing to a sophisticated supply chain attack.
The company said the compromised device was traced to a single reseller operating in Southeast Asia, and that the incident appears to be isolated to that market. Losses related to the case are estimated to exceed $86 million.
Ledger has not publicly detailed the technical mechanism of the installed device, but the discovery underscores existing security concerns surrounding third-party hardware wallet resellers. Users are consistently advised to purchase devices directly from manufacturers to reduce their exposure to tampered hardware.
#CyberSecurity (Cybersecurity)
#SupplyChainAttack (Supply chain attack)
#HardwareWallets (Cold wallet)
#CryptoSecurity #OPSEC (Operational security)
Ledger confirms presence of unauthorized hardware device in supply chain theft investigation
Ledger has confirmed the discovery of an unauthorized hardware device installed inside a cryptocurrency wallet linked to an ongoing theft investigation, pointing to a sophisticated supply chain attack.
The company said the compromised device was traced to a single reseller operating in Southeast Asia, and that the incident appears to be isolated to that market. Losses related to the case are estimated to exceed $86 million.
Ledger has not publicly detailed the technical mechanism of the installed device, but the discovery underscores existing security concerns surrounding third-party hardware wallet resellers. Users are consistently advised to purchase devices directly from manufacturers to reduce their exposure to tampered hardware.
#CyberSecurity (Cybersecurity)
#SupplyChainAttack (Supply chain attack)
#HardwareWallets (Cold wallet)
#CryptoSecurity #OPSEC (Operational security)
Ledger has confirmed the discovery of an unauthorized hardware device installed inside a cryptocurrency wallet linked to an ongoing theft investigation, pointing to a sophisticated supply chain attack.
The company said the compromised device was traced to a single reseller operating in Southeast Asia, and that the incident appears to be isolated to that market. Losses related to the case are estimated to exceed $86 million.
Ledger has not publicly detailed the technical mechanism of the installed device, but the discovery underscores existing security concerns surrounding third-party hardware wallet resellers. Users are consistently advised to purchase devices directly from manufacturers to reduce their exposure to tampered hardware.
#CyberSecurity (Cybersecurity)
#SupplyChainAttack (Supply chain attack)
#HardwareWallets (Cold wallet)
#CryptoSecurity #OPSEC (Operational security)
2
47
🚨 ChainDrop malware attack targets npm packages and infects 1,300 of them
A security report reveals the widening scope of the ChainDrop malware attack, which targeted more than 1,300 packages in popular npm repositories. The attackers use legitimate GitHub Actions workflows to distribute malicious code, impacting software projects that rely on these packages.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 Source: 4sysops.com
🚨 ChainDrop malware attack targets npm packages and infects 1,300 of them
A security report reveals the widening scope of the ChainDrop malware attack, which targeted more than 1,300 packages in popular npm repositories. The attackers use legitimate GitHub Actions workflows to distribute malicious code, impacting software projects that rely on these packages.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 Source: 4sysops.com
A security report reveals the widening scope of the ChainDrop malware attack, which targeted more than 1,300 packages in popular npm repositories. The attackers use legitimate GitHub Actions workflows to distribute malicious code, impacting software projects that rely on these packages.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 Source: 4sysops.com
37
🚨 Hack Hits Ad Company to Target Crypto Wallets
Adform, an online advertising company, was hit by a cyberattack aimed at replacing copied cryptocurrency wallet addresses provided by users with addresses belonging to the attackers. The breach was carried out by exploiting ad scripts on websites that use the company’s platform, highlighting information security challenges in the industry.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 Source: bleepingcomputer.com
🚨 Hack Hits Ad Company to Target Crypto Wallets
Adform, an online advertising company, was hit by a cyberattack aimed at replacing copied cryptocurrency wallet addresses provided by users with addresses belonging to the attackers. The breach was carried out by exploiting ad scripts on websites that use the company’s platform, highlighting information security challenges in the industry.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 Source: bleepingcomputer.com
Adform, an online advertising company, was hit by a cyberattack aimed at replacing copied cryptocurrency wallet addresses provided by users with addresses belonging to the attackers. The breach was carried out by exploiting ad scripts on websites that use the company’s platform, highlighting information security challenges in the industry.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 Source: bleepingcomputer.com
16

·
--
Bullish
#LedgerConfirmsUnauthorizedHardwareImplantInUserDevice
Cold wallets, but traders’ hearts are burning hot! 🔥
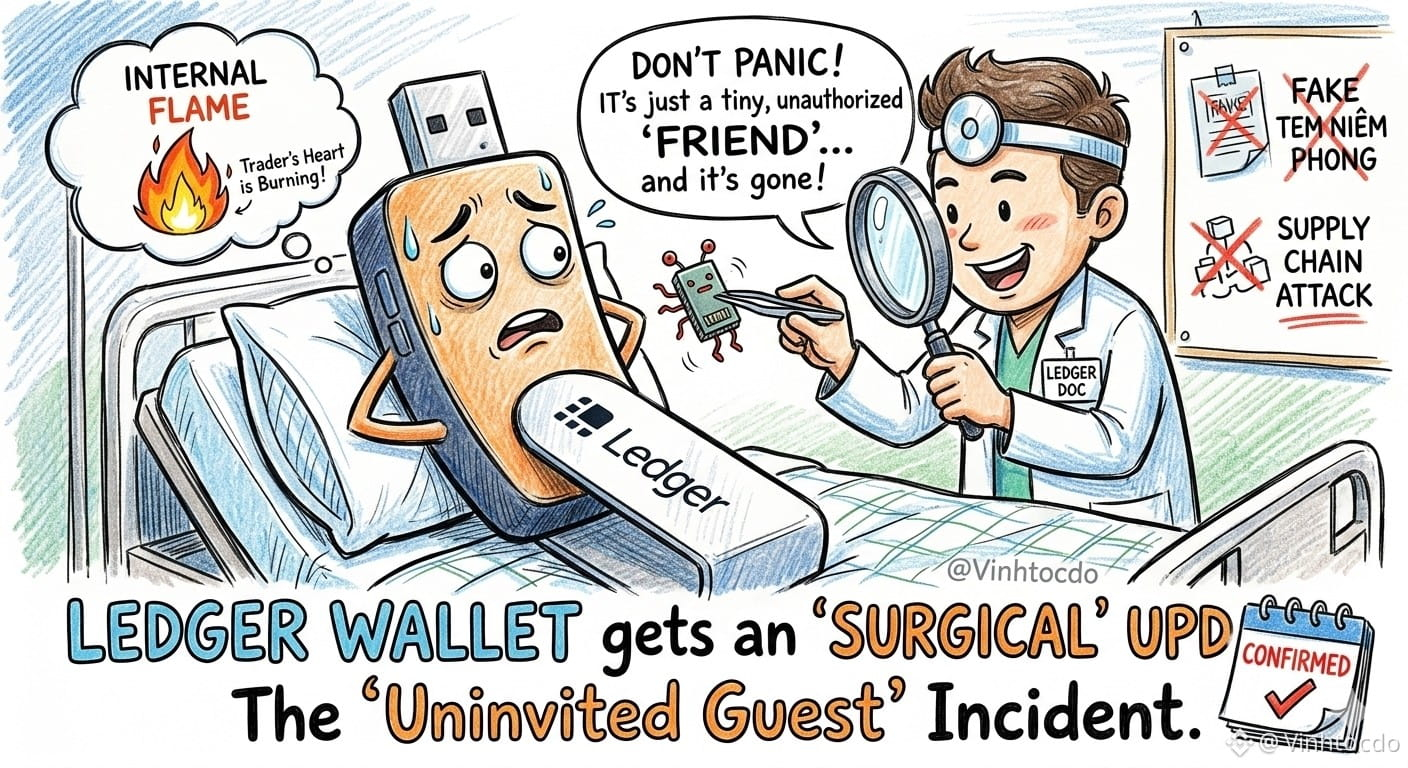
🚨 Major scandal: Ledger just confirmed that at least one user’s device had been secretly fitted with unauthorized hardware! CryptoBilis, the distributor, panicked and immediately stopped selling all products.
🤔 So what are seals and labels even for? Many people are wondering: if the devices were covered in tamper-evident and warranty seals, how could they still have been tampered with?
🏷️ Hackers these days are incredibly good at forging or removing seals—“supply chain attacks” are no big deal to them.
🕵️ Or could an insider have secretly slipped a rogue chip in before the seal was applied? Ledger insists its system is still secure, but this drama is far from over!
🛡️ What should traders do?
🛑 If you bought from CryptoBilis and haven’t set up the device yet, don’t touch it.
💸 If you’ve already set it up, quickly transfer all your assets to a new wallet using a completely new 24-word recovery phrase!
⚠️ This is not financial advice!
👉 Sign up for a new Binance account and trade alongside me:
➕ Referral code: VINHTOCDO
🔗 Link: [binance.com](http://binance.com/)
👇 Click a trading link below to support me:
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
$BNB
{spot}(BNBUSDT)
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
#LedgerConfirmsUnauthorizedHardwareImplantInUserDevice
Cold wallets, but traders’ hearts are burning hot! 🔥
🚨 Major scandal: Ledger just confirmed that at least one user’s device had been secretly fitted with unauthorized hardware! CryptoBilis, the distributor, panicked and immediately stopped selling all products.
🤔 So what are seals and labels even for? Many people are wondering: if the devices were covered in tamper-evident and warranty seals, how could they still have been tampered with?
🏷️ Hackers these days are incredibly good at forging or removing seals—“supply chain attacks” are no big deal to them.
🕵️ Or could an insider have secretly slipped a rogue chip in before the seal was applied? Ledger insists its system is still secure, but this drama is far from over!
🛡️ What should traders do?
🛑 If you bought from CryptoBilis and haven’t set up the device yet, don’t touch it.
💸 If you’ve already set it up, quickly transfer all your assets to a new wallet using a completely new 24-word recovery phrase!
⚠️ This is not financial advice!
👉 Sign up for a new Binance account and trade alongside me:
➕ Referral code: VINHTOCDO
🔗 Link: binance.com
👇 Click a trading link below to support me:
$BTC
$ETH
$BNB
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
Cold wallets, but traders’ hearts are burning hot! 🔥
🚨 Major scandal: Ledger just confirmed that at least one user’s device had been secretly fitted with unauthorized hardware! CryptoBilis, the distributor, panicked and immediately stopped selling all products.
🤔 So what are seals and labels even for? Many people are wondering: if the devices were covered in tamper-evident and warranty seals, how could they still have been tampered with?
🏷️ Hackers these days are incredibly good at forging or removing seals—“supply chain attacks” are no big deal to them.
🕵️ Or could an insider have secretly slipped a rogue chip in before the seal was applied? Ledger insists its system is still secure, but this drama is far from over!
🛡️ What should traders do?
🛑 If you bought from CryptoBilis and haven’t set up the device yet, don’t touch it.
💸 If you’ve already set it up, quickly transfer all your assets to a new wallet using a completely new 24-word recovery phrase!
⚠️ This is not financial advice!
👉 Sign up for a new Binance account and trade alongside me:
➕ Referral code: VINHTOCDO
🔗 Link: binance.com
👇 Click a trading link below to support me:
$BTC
$ETH
$BNB
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
8
5.1k

$INJ NPM PACKAGE HACK — 50K WEEKLY DOWNLOADS COMPROMISED 🔥
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
$INJ NPM PACKAGE HACK — 50K WEEKLY DOWNLOADS COMPROMISED 🔥
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
150

·
--
🚨 2,000 POISONED PACKAGES FLOOD $KEYV — 127M DOWNLOADS IN THE BLAST RADIUS! 💥
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
🚨 2,000 POISONED PACKAGES FLOOD $KEYV — 127M DOWNLOADS IN THE BLAST RADIUS! 💥
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
13

Ledger discovers an unauthorized hardware implant in a crypto wallet, raising concerns about a supply chain attack
- Ledger confirms it found an unauthorized hardware implant inside a crypto wallet
- The implant is linked to an ongoing theft investigation
- Raises concerns about sophisticated supply chain attacks
- The RSS source has not provided further details about the scope or the specific wallet
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Source: U.Today
Ledger discovers an unauthorized hardware implant in a crypto wallet, raising concerns about a supply chain attack
- Ledger confirms it found an unauthorized hardware implant inside a crypto wallet
- The implant is linked to an ongoing theft investigation
- Raises concerns about sophisticated supply chain attacks
- The RSS source has not provided further details about the scope or the specific wallet
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Source: U.Today
- Ledger confirms it found an unauthorized hardware implant inside a crypto wallet
- The implant is linked to an ongoing theft investigation
- Raises concerns about sophisticated supply chain attacks
- The RSS source has not provided further details about the scope or the specific wallet
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Source: U.Today
134
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaBeatsEstimatesAICloudStocksRiseAfterHours
3,164 views
58 Discussing
2
#A Packed Week of Earnings and Data Tests Markets
150,850 views
667 Discussing
3
#AnthropicIPOTestsInvestorAppetiteForAI
333,429 views
2,917 Discussing
4
#NvidiaBoardNotConsideringHuang’sReturnasCEO
125,078 views
990 Discussing
5
#KOSPIFalls2.59%ToLowestCloseSinceFebruary
32,481 views
337 Discussing
6
#AnthropicClearedToListOnNasdaqAsANT
27,453 views
279 Discussing
7
#WhatInvestmentSignalsDo13FFilingsReveal?
68,641 views
677 Discussing
8
#TetherCapitalMakesStrategicInvestmentInStables
15,647 views
121 Discussing
9
#EvernorthRecords$505MImpairmentOnPreListingXRP
1,910 views
21 Discussing
10
#GoldmanSachsReports$1.22BInEtherETFHoldings
1,367 views
17 Discussing