

#accountsecurity
accountsecurity
64,511 lượt xem
188 đang thảo luận
Phổ biến
Mới nhất

·
--
Xem bản dịch
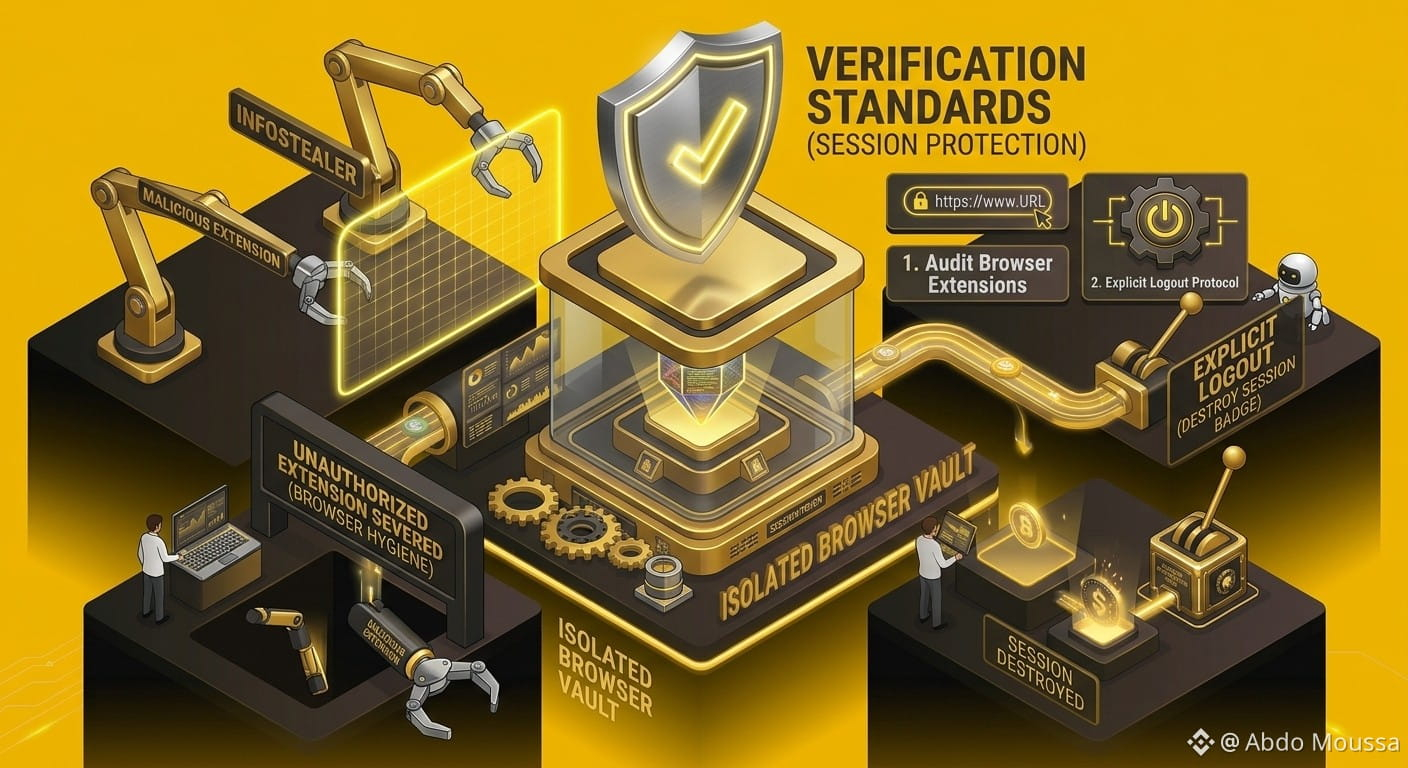
🍪 Browser Hygiene: Protecting Active Sessions from Cookie Theft
Relying solely on multi-factor authentication is insufficient if active browser sessions are left vulnerable to session-hijacking malware designed to steal access cookies and authorization tokens.
💡 Mitigating Session Hijacking & Token Theft
Understand Cookie Stealers: Specialized malware (InfoStealers) targets localized browser databases to export active session cookies, allowing attackers to clone an authenticated session on a remote machine.
Explicit Logouts: Always click the explicit Log Out button rather than simply closing the browser tab when concluding sensitive financial activities.
Audit Browser Extensions: Routinely inspect and remove unnecessary or unverified third-party browser extensions that possess broad web-reading permissions.
Isolate Trading Environments: Dedicate a clean, extension-free browser profile or isolated device exclusively for executing digital asset transactions.
⚠️ Security & Educational Disclaimer
Maintaining strict browser environment hygiene prevents unauthorized session cloning and credential harvesting, This publication is prepared strictly for educational and security awareness purposes.
[https://www.binance.com/en/academy/articles/what-are-cookies](https://www.binance.com/en/academy/articles/what-are-cookies)
Clean your browser cache, log out of sensitive sessions, and always DYOR (Do Your Own Research) 💡
#Binance #Security #AccountSecurity #dyor
🍪 Browser Hygiene: Protecting Active Sessions from Cookie Theft
Relying solely on multi-factor authentication is insufficient if active browser sessions are left vulnerable to session-hijacking malware designed to steal access cookies and authorization tokens.
💡 Mitigating Session Hijacking & Token Theft
Understand Cookie Stealers: Specialized malware (InfoStealers) targets localized browser databases to export active session cookies, allowing attackers to clone an authenticated session on a remote machine.
Explicit Logouts: Always click the explicit Log Out button rather than simply closing the browser tab when concluding sensitive financial activities.
Audit Browser Extensions: Routinely inspect and remove unnecessary or unverified third-party browser extensions that possess broad web-reading permissions.
Isolate Trading Environments: Dedicate a clean, extension-free browser profile or isolated device exclusively for executing digital asset transactions.
⚠️ Security & Educational Disclaimer
Maintaining strict browser environment hygiene prevents unauthorized session cloning and credential harvesting, This publication is prepared strictly for educational and security awareness purposes.
https://www.binance.com/en/academy/articles/what-are-cookies
Clean your browser cache, log out of sensitive sessions, and always DYOR (Do Your Own Research) 💡
#Binance #Security #AccountSecurity #dyor
4
65
·
--
SIM swap: Xác minh qua SMS là mắt xích yếu nhất.
Điện thoại của bạn nằm trong tay, nhưng người khác đang sử dụng SIM của bạn.
SIM swap: kẻ lừa đảo cấp lại SIM của bạn tại nhà mạng bằng thông tin cá nhân của bạn. Mã SMS của bạn sẽ gửi thẳng đến điện thoại của chúng, và tài khoản của bạn chỉ còn cách bị mất bởi một mật khẩu.
Hai biện pháp phòng thủ: dùng ứng dụng xác thực cho 2FA, không chỉ dựa vào SMS · đặt mã PIN SIM với nhà mạng của bạn.
SMS là mắt xích yếu nhất. Tôi đã chứng kiến một người bạn mất hàng trăm nghìn chỉ vì điều này. Không bao giờ nữa.
#2FA
$BTC
#AccountSecurity
Đăng ký:
<a href="https://www.binance.com/zh-CN/join?ref=BNAPP">https://www.binance.com/zh-CN/join?ref=BNAPP</a>
82
·
--
Thiết lập 2FA là điều không thể thương lượng nếu bạn đang giữ bất kỳ số dư thực nào trên một sàn giao dịch. Google Authenticator chỉ mất hai phút để thiết lập và đây là yếu tố quan trọng nhất giúp ngăn chặn một cuộc tấn công lừa đảo (phishing) vào tài khoản của bạn.
#AccountSecurity #ScamAlert
$BNB
Đăng ký:
<a href="https://www.binance.com/zh-CN/join?ref=BNAPP">https://www.binance.com/zh-CN/join?ref=BNAPP</a>
#AccountSecurity #ScamAlert
$BNB
Đăng ký:
<a href="https://www.binance.com/zh-CN/join?ref=BNAPP">https://www.binance.com/zh-CN/join?ref=BNAPP</a>
104
·
--
Giá của một “airdrop giả”: một chữ ký, một ví bị rút cạn.
“Nhận airdrop 500 USDT” — cái giá của việc bấm chuột có thể là toàn bộ số dư của bạn.
Các trang web airdrop giả yêu cầu bạn kết nối ví và “ký để xác nhận”. Một chữ ký độc hại là đèn xanh vĩnh viễn, và tiền của bạn sẽ bị rút cạn. Bản thân chữ ký thậm chí không tốn gas.
Ba quy tắc: không bao giờ ký các quyền phê duyệt mà bạn không hiểu · định kỳ thu hồi các quyền phê duyệt cũ · airdrop thật không bao giờ nhắn DM cho bạn.
Các chiến dịch chính thức chỉ được công bố trong ứng dụng. Mọi liên kết bên ngoài: coi như lừa đảo.
$USDT
#AccountSecurity #ScamAlert
Đăng ký:
<a href="https://www.binance.com/zh-CN/join?ref=BNAPP">https://www.binance.com/zh-CN/join?ref=BNAPP</a>
2
342
·
--
🏕️ Trại hè Binance — Ngày 1 ☀️
Bài học hôm nay xoay quanh Bảo vệ Tài khoản 🔐
Trước khi thực hiện giao dịch đầu tiên, việc bảo vệ tài khoản luôn phải được đặt lên hàng đầu. Học về bảo mật, nhận biết rủi ro và xây dựng thói quen tốt là những bước thiết yếu trong hành trình crypto.
Mình đã sẵn sàng để học, khám phá và tận dụng tối đa kỳ Trại hè này! 🚀
#BinanceSummerCamp #Binance #CryptoEducation #AccountSecurity #CryptoJourney
1
58

🏕️ Trại hè Binance — Ngày 1 Hoàn tất! 🔐
Ngày 1 tập trung vào Phòng thủ Tài khoản 🛡️
Trước khi bước vào giao dịch đầu tiên, việc bảo vệ tài khoản Binance của bạn luôn phải là ưu tiên hàng đầu. Những thói quen bảo mật vững chắc là bước đầu tiên để giữ an toàn hơn cho tài khoản và tài sản của bạn. 💰🔒
✅ Đã hoàn thành Ngày 1
🚀 Sẵn sàng cho thử thách tiếp theo!
Mỗi bài học một lần, tiến gần hơn để trở nên thông minh hơn trong crypto. 💪
#BinanceSummerCamp #Binance #AccountSecurity #CryptoJourney #Day1
1
1
269
·
--
Danh sách trắng rút tiền: biện pháp cứu nguy rẻ nhất trong bảo mật.
Biện pháp cứu nguy bị đánh giá thấp nhất: danh sách trắng địa chỉ rút tiền.
Khi được bật, lệnh rút tiền chỉ có thể đến các địa chỉ đã được thiết lập sẵn, và các địa chỉ mới cần 24h để kích hoạt. Đó là khoảng thời gian hạ nhiệt của bạn: nếu tài khoản bị chiếm đoạt, kẻ tấn công không thể thêm địa chỉ của riêng chúng. Nếu bạn đang bị thao túng tâm lý, bạn có trọn một ngày để tỉnh táo lại.
Chỉ giữ nó cho ví lạnh của chính bạn và những nền tảng bạn thực sự sử dụng. Xóa những gì bạn không còn cần.
Rút tiền chỉ với danh sách trắng: cài đặt bảo mật có ROI cao nhất mà tôi biết.
#AccountSecurity #WithdrawalSafety $USDT
3
1
15
11.1k
·
--
Chống lừa đảo câu cá: Chỉ cần thiết lập trong 1 phút là chặn được mọi email giả.
Mỗi lần xảy ra sự cố “email giả lừa lấy đi nửa vị thế”, đều thiếu thiết lập này.
Chống lừa đảo câu cá: Sau khi thiết lập, mọi email chính thức được Binance gửi cho bạn sẽ kèm mã riêng của bạn. “Email chính thức” không có mã này, tất cả đều là giả; email xác minh cũng giống vậy.
· Mã phải không theo quy luật, đừng dùng ngày sinh. Thiết lập trong Trung tâm An toàn của App trong 1 phút
Năm 2021 cài đặt thì đến hôm nay thư rác nhìn là biết.
#AccountSecurity #Phishing $BNB
1
148
Cài đặt bảo mật API ít được chú ý nhất: Danh sách IP được phépCài đặt bảo mật API ít được chú ý nhất: Danh sách IP được phép
Khóa API rất mạnh mẽ, nhưng chỉ một cài đặt bảo mật nhỏ cũng có thể tạo ra khác biệt rất lớn: danh sách IP được phép.
Nhiều người để quyền truy cập API của mình mở cho mọi địa chỉ IP chỉ để tiện. Nhưng nếu khóa API đó bị lộ, kẻ tấn công có thể dùng nó từ bất kỳ đâu. Cách an toàn hơn là chỉ cho phép IP của máy chủ, hệ thống giao dịch hoặc mạng gia đình đáng tin cậy của bạn—và từ chối mọi kết nối khác.
Có một quy tắc khác mà mọi người dùng crypto nên tuân theo: không bao giờ bật quyền rút tiền trên một khóa API. Nếu bạn chỉ cần dữ liệu thị trường và giao dịch, hãy bật Quyền Đọc + Giao dịch và giữ rút tiền ở trạng thái tắt.
Cài đặt bảo mật API ít được chú ý nhất: Danh sách IP được phép
Cài đặt bảo mật API ít được chú ý nhất: Danh sách IP được phép
Khóa API rất mạnh mẽ, nhưng chỉ một cài đặt bảo mật nhỏ cũng có thể tạo ra khác biệt rất lớn: danh sách IP được phép.
Nhiều người để quyền truy cập API của mình mở cho mọi địa chỉ IP chỉ để tiện. Nhưng nếu khóa API đó bị lộ, kẻ tấn công có thể dùng nó từ bất kỳ đâu. Cách an toàn hơn là chỉ cho phép IP của máy chủ, hệ thống giao dịch hoặc mạng gia đình đáng tin cậy của bạn—và từ chối mọi kết nối khác.
Có một quy tắc khác mà mọi người dùng crypto nên tuân theo: không bao giờ bật quyền rút tiền trên một khóa API. Nếu bạn chỉ cần dữ liệu thị trường và giao dịch, hãy bật Quyền Đọc + Giao dịch và giữ rút tiền ở trạng thái tắt.
109
·
--
Một điều tôi luôn khuyên khi sử dụng khóa API là đừng để danh sách IP được mở rộng.
Có thể sẽ dễ hơn khi chọn “Cho phép tất cả IP”, nhưng nếu khóa API của bạn bị rò rỉ, bất kỳ ai cũng có thể thử sử dụng nó. Nếu có thể, chỉ cho phép IP mà bạn thực sự giao dịch hoặc IP của máy chủ của bạn.
Và xin hãy tắt quyền truy cập rút tiền. Thông thường, khóa API của bạn chỉ cần quyền đọc và giao dịch. Bằng cách này, một khóa bị rò rỉ không thể chỉ đơn giản được dùng để rút tiền của bạn.
Thiết lập mất chưa đến một phút, nhưng bước nhỏ đó có thể tạo ra khác biệt lớn trong việc bảo vệ tài khoản của bạn. 🔐
#APISecurity #CryptoSecurity #AccountSecurity
207
·
--
Cài đặt bảo mật API bị bỏ qua nhiều nhất: danh sách IP được phép.
Nhiều người bật “cho phép tất cả IP” cho tiện, rồi sau đó bị rút cạn khi key bị lộ. Thực hành đúng: chỉ ràng buộc với IP máy chủ hoặc IP ở nhà của bạn, từ chối mọi thứ khác.
Ngoài ra: TUYỆT ĐỐI không bật quyền rút tiền cho một API key. Chỉ đọc + giao dịch. Như vậy, ngay cả khi key bị lộ, trường hợp tệ nhất cũng chỉ là wash-trading, không phải mất tài sản. Quy tắc này đã cứu tôi nhiều lần.
#Deposit #USDT #AccountSecurity
17
4
78
116.9k
Bài viết
🔐 Điều gì xảy ra với crypto của bạn nếu bạn đột ngột không thể quản lý tài khoản Binance?Khi chúng ta nghĩ về bảo mật crypto, thường thì chúng ta tập trung vào mật khẩu mạnh, mã 2FA, mã chống lừa đảo và việc bảo vệ thiết bị của mình.
Nhưng còn một tình huống khác mà chúng ta thường hay quên:
Điều gì sẽ xảy ra với crypto của bạn nếu bạn đột nhiên không thể truy cập hoặc quản lý tài khoản của mình trong một khoảng thời gian dài hoặc vĩnh viễn?
Một tai nạn bất ngờ, việc nhập viện hoặc một hoàn cảnh không lường trước khác có thể khiến tài sản của bạn không thể tiếp cận được đối với những người sau này có thể cần phải xử lý chúng.
Đó là lúc tính năng Liên hệ Khẩn cấp của Binance có thể hữu ích.
🔐 Điều gì xảy ra với crypto của bạn nếu bạn đột ngột không thể quản lý tài khoản Binance?
Khi chúng ta nghĩ về bảo mật crypto, thường thì chúng ta tập trung vào mật khẩu mạnh, mã 2FA, mã chống lừa đảo và việc bảo vệ thiết bị của mình.
Nhưng còn một tình huống khác mà chúng ta thường hay quên:
Điều gì sẽ xảy ra với crypto của bạn nếu bạn đột nhiên không thể truy cập hoặc quản lý tài khoản của mình trong một khoảng thời gian dài hoặc vĩnh viễn?
Một tai nạn bất ngờ, việc nhập viện hoặc một hoàn cảnh không lường trước khác có thể khiến tài sản của bạn không thể tiếp cận được đối với những người sau này có thể cần phải xử lý chúng.
Đó là lúc tính năng Liên hệ Khẩn cấp của Binance có thể hữu ích.
6
126
·
--
Thiết lập bảo mật API bị bỏ quên nhiều nhất: danh sách IP được phép.
Rất nhiều người bật “cho phép tất cả IP” cho tiện, rồi bị rút cạn khi khóa bị rò rỉ. Cách làm đúng: chỉ ràng buộc vào IP máy chủ của bạn hoặc IP nhà bạn, và từ chối mọi thứ khác.
Ngoài ra: TUYỆT ĐỐI không bật quyền rút tiền trên một khóa API. Chỉ đọc + giao dịch. Như vậy, ngay cả khi khóa bị rò rỉ, kịch bản tệ nhất chỉ là rửa giao dịch (wash-trading), chứ không phải mất tài sản. Quy tắc này đã cứu mình nhiều hơn một lần.
#Deposit #USDT #AccountSecurity
155
·
--
Thiết lập bảo mật API thường bị bỏ qua nhất: danh sách IP được phép.
Rất nhiều người bật “cho phép tất cả IP” để tiện, rồi bị rút cạn khi khóa bị rò rỉ. Thực hành đúng: chỉ ràng buộc vào IP máy chủ của bạn hoặc IP tại nhà, và từ chối mọi thứ khác.
Ngoài ra: KHÔNG BAO GIỜ bật quyền rút tiền trên một khóa API. Chỉ bật đọc + giao dịch. Như vậy, ngay cả khi khóa bị rò rỉ, kịch bản tệ nhất chỉ là wash-trading (giao dịch rửa), chứ không mất tài sản. Quy tắc này đã cứu tôi nhiều lần.
#Deposit #USDT #AccountSecurity
488

·
--
Thiết lập đầy đủ các tính năng bảo mật trong tuần đầu tiên của tôi: mật khẩu mạnh, Google Authenticator, danh sách trắng rút tiền, mã chống lừa đảo. Có thể mất khoảng 30 phút tổng cộng nhưng mang lại cảm giác yên tâm thật sự.
#Deposit #USDT #AccountSecurity
Chưa đăng ký thì có thể dùng mã của tôi BNAPP: https://www.binance.com/register?ref=BNAPP
#币安新手 #BNAPP
#Deposit #USDT #AccountSecurity
Chưa đăng ký thì có thể dùng mã của tôi BNAPP: https://www.binance.com/register?ref=BNAPP
#币安新手 #BNAPP
132
·
--
Cài đặt quan trọng thường bị bỏ qua trong bảo mật API: danh sách trắng các địa chỉ IP.
Nhiều người bật tùy chọn «Cho phép tất cả địa chỉ IP» chỉ vì sự tiện lợi, rồi phải chịu thiệt hại khi các khóa API bị rò rỉ.
Cách làm đúng: gắn khóa API với địa chỉ IP của máy chủ của bạn hoặc chỉ với mạng gia đình của bạn, và từ chối mọi kết nối từ các địa chỉ khác.
Ngoài ra: tuyệt đối không bật quyền rút tiền (Withdrawal) trên khóa API.
Chỉ dùng quyền Đọc + Giao dịch.
Nhờ vậy, ngay cả khi khóa bị rò rỉ, thì kịch bản tệ nhất cũng chỉ là bị lạm dụng giao dịch, chứ không phải mất tài sản.
$BNB Nguyên tắc này đã cứu tôi khỏi những khoản thua lỗ nhiều lần.
#Deposit #USDT #AccountSecurity
42
·
--
◆ Cách cài đặt Binance APK trên Android (2026)
Nếu Binance không có sẵn trên Google Play tại khu vực của bạn, hãy cài đặt APK chính thức trực tiếp.
Các bước:
1. Mở trình duyệt của bạn và tải xuống APK chính thức
2. Chạm vào tệp đã tải để cài đặt
3. Nếu có nhắc về "nguồn không xác định", hãy vào Cài đặt → Bảo mật → Cho phép nguồn không xác định
4. Cài đặt và mở ứng dụng
⚠️ Các cảnh báo "rủi ro cao" hoặc "virus" là kết quả nhận nhầm (dương tính giả) từ hệ điều hành. APK chính thức là an toàn.
📌 APK chính thức: https://download.binance.com/pack/BNApp_F0000680.apk
📌 Đăng ký (dùng mã BNAPP để được giảm phí): https://www.binance.com/register?ref=BNAPP
#BinanceRegistration #BeginnerGuide #AccountSecurity
299
·
--
🔒 Tài khoản của bạn, quyền kiểm soát của bạn! Binance có an toàn không? 🛡️
Binance Pakistan đang thực hiện kiểm tra bảo mật tài khoản Ngày 15! 🇵🇰 Trước biến động của thị trường, việc giữ an toàn cho quỹ của bạn là điều quan trọng nhất.
Để bảo mật tài khoản, ngay bây giờ hãy làm theo 3 bước đơn giản này:
1️⃣ Thiết bị đã kết nối: Vào Cài đặt và xóa từng thiết bị mà bạn không nhận ra.
2️⃣ Mã chống lừa đảo (Anti-Phishing Code): Bật tính năng này để mỗi email thực nhận được từ Binance, bạn sẽ thấy mã bí mật của mình và tránh được các chiêu lừa đảo qua email giả mạo.
3️⃣ Widget màn hình chính: Theo dõi giá trực tiếp và giá trị danh mục mà không cần mở ứng dụng.
Tránh những sai lầm và luôn cập nhật bảo mật của bạn! 🤝
Tính năng bảo mật Binance bạn yêu thích nhất là gì? Hãy chia sẻ trong phần bình luận! 👇
$BTC $BNB $XRP #Binancepakistan #AccountSecurity #CryptoSecurity #BinanceSquare #USDT
2
3
580
Bài viết
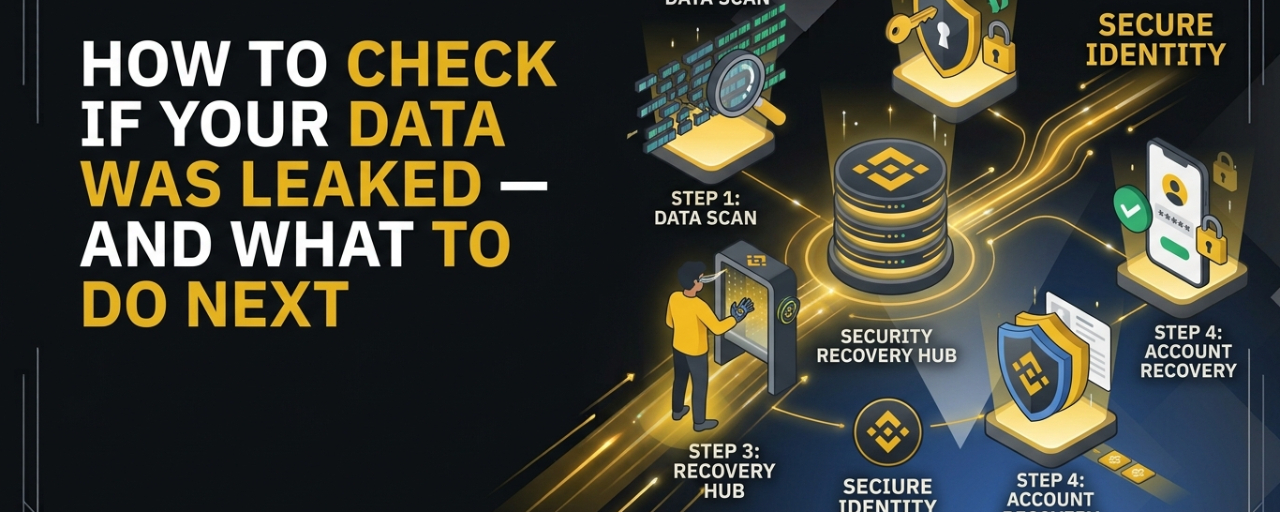
Cách kiểm tra xem dữ liệu của bạn có bị rò rỉ không — và nên làm gì tiếp theoMột vụ rò rỉ dữ liệu có thể xảy ra mà bạn không hề nhận ra.
Bạn có thể tiếp tục sử dụng email, số điện thoại, tài khoản mạng xã hội, tài khoản sàn giao dịch và các dịch vụ trực tuyến khác của mình như bình thường, trong khi ở đâu đó, thông tin liên quan đến một trong các tài khoản đó có thể đã bị lộ.
Câu hỏi quan trọng không chỉ là:
“Dữ liệu của tôi có bị rò rỉ không?”
Còn là:
“Nếu nó có, tôi nên làm gì?”
Biết cách kiểm tra xem có bị lộ thông tin hay không và phản hồi nhanh chóng có thể giảm đáng kể thiệt hại tiềm ẩn.
Dưới đây là hướng dẫn từng bước thực tế.
Cách kiểm tra xem dữ liệu của bạn có bị rò rỉ không — và nên làm gì tiếp theo
Một vụ rò rỉ dữ liệu có thể xảy ra mà bạn không hề nhận ra.
Bạn có thể tiếp tục sử dụng email, số điện thoại, tài khoản mạng xã hội, tài khoản sàn giao dịch và các dịch vụ trực tuyến khác của mình như bình thường, trong khi ở đâu đó, thông tin liên quan đến một trong các tài khoản đó có thể đã bị lộ.
Câu hỏi quan trọng không chỉ là:
“Dữ liệu của tôi có bị rò rỉ không?”
Còn là:
“Nếu nó có, tôi nên làm gì?”
Biết cách kiểm tra xem có bị lộ thông tin hay không và phản hồi nhanh chóng có thể giảm đáng kể thiệt hại tiềm ẩn.
Dưới đây là hướng dẫn từng bước thực tế.
2
24
#AccountSecurity
buổi đào tạo tuyệt vời
#AccountSecurity
buổi đào tạo tuyệt vời
buổi đào tạo tuyệt vời
97
Đăng nhập để khám phá thêm nội dung
Tham gia cùng người dùng tiền mã hóa toàn cầu trên Binance Square
⚡️ Nhận thông tin mới nhất và hữu ích về tiền mã hóa.
💬 Được tin cậy bởi sàn giao dịch tiền mã hóa lớn nhất thế giới.
👍 Khám phá những thông tin chuyên sâu thực tế từ những nhà sáng tạo đã xác minh.
Email / Số điện thoại
Chủ đề thịnh hành
1
#TinFed
88,069 lượt xem
429 đang thảo luận
2
#TheoDõiFOMC
105,988 lượt xem
628 đang thảo luận
3
#UKFCAWinsCourtOrderToRecover851400Pounds
10,686 lượt xem
531 đang thảo luận
4
#ChainlinkLaunchesCCIP2WithEnterpriseVerification
25,333 lượt xem
753 đang thảo luận
5
#GoldFallsTo$4144
9,677 lượt xem
124 đang thảo luận
6
#QNTFallsOver40%FromMorningHigh
62,634 lượt xem
1,163 đang thảo luận
7
#USDTAdds845900HoldersInPast7Days
8,298 lượt xem
311 đang thảo luận
8
#KospiFalls2.7%SamsungSKHynixDropOver5%
17,316 lượt xem
501 đang thảo luận
9
#BitgetCEOConfirms$388MStolenInHack
4,337 lượt xem
39 đang thảo luận
10
#BTCFallsBelow$83000
25,324 lượt xem
156 đang thảo luận