
#seguridaddefi
seguridaddefi
2,117 views
5 Discussing
Hot
Latest
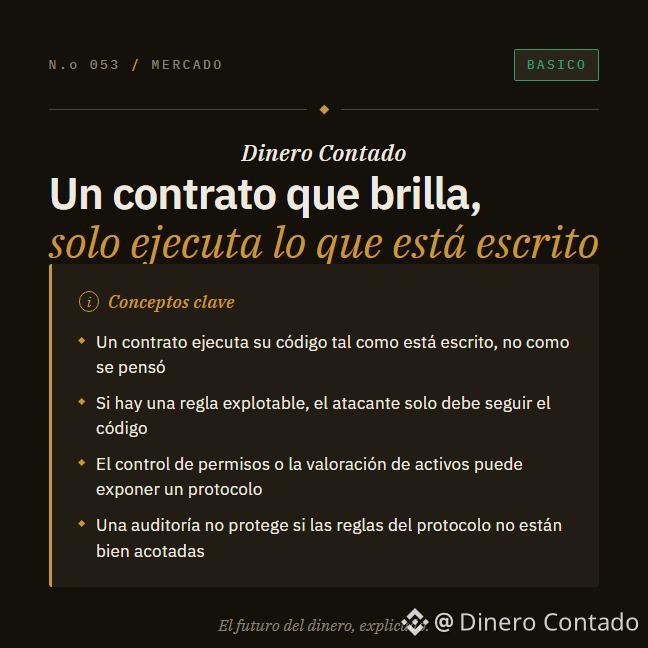
That a DeFi protocol runs on public smart contracts should be enough to keep funds safe: that’s what most people believe, and it has just been proven false.
The logic makes sense at first glance. The code is public, anyone can review it, and no single person controls it. Sounds good. But two platforms operating on the $ETH network and on Polygon suffered different attacks, and in both cases the result was the same: funds were taken out of the protocol without anyone authorizing it.
An exploit doesn’t destroy the code: it uses it exactly as written, but in an order or context the team didn’t anticipate.
KEY CONCEPTS
- Smart contracts execute what the code says, not what the programmer intended. That difference is where exploits live.
- A flash loan is borrowed and repaid in the same transaction. Its usefulness to an attacker is that it provides access to a very large amount of capital for an instant—enough to distort a protocol’s internal prices.
- A proxy contract is no minor detail: it’s the mechanism that determines what code gets executed. If an attacker can modify it, they control the entire protocol.
The security of a DeFi protocol isn’t guaranteed by the technology: it depends on how far its developers went in imagining how it could fail. Two platforms have just shown that this work never ends.
Transparency: Binance may pay us a commission if you trade after clicking an asset symbol or a price link in this post.
#SeguridadDeFi #ContratosInteligentes #PrestamosRelampago #CryptoRisks
That a DeFi protocol runs on public smart contracts should be enough to keep funds safe: that’s what most people believe, and it has just been proven false.
The logic makes sense at first glance. The code is public, anyone can review it, and no single person controls it. Sounds good. But two platforms operating on the $ETH network and on Polygon suffered different attacks, and in both cases the result was the same: funds were taken out of the protocol without anyone authorizing it.
An exploit doesn’t destroy the code: it uses it exactly as written, but in an order or context the team didn’t anticipate.
KEY CONCEPTS
- Smart contracts execute what the code says, not what the programmer intended. That difference is where exploits live.
- A flash loan is borrowed and repaid in the same transaction. Its usefulness to an attacker is that it provides access to a very large amount of capital for an instant—enough to distort a protocol’s internal prices.
- A proxy contract is no minor detail: it’s the mechanism that determines what code gets executed. If an attacker can modify it, they control the entire protocol.
The security of a DeFi protocol isn’t guaranteed by the technology: it depends on how far its developers went in imagining how it could fail. Two platforms have just shown that this work never ends.
Transparency: Binance may pay us a commission if you trade after clicking an asset symbol or a price link in this post.
#SeguridadDeFi #ContratosInteligentes #PrestamosRelampago #CryptoRisks
The logic makes sense at first glance. The code is public, anyone can review it, and no single person controls it. Sounds good. But two platforms operating on the $ETH network and on Polygon suffered different attacks, and in both cases the result was the same: funds were taken out of the protocol without anyone authorizing it.
An exploit doesn’t destroy the code: it uses it exactly as written, but in an order or context the team didn’t anticipate.
KEY CONCEPTS
- Smart contracts execute what the code says, not what the programmer intended. That difference is where exploits live.
- A flash loan is borrowed and repaid in the same transaction. Its usefulness to an attacker is that it provides access to a very large amount of capital for an instant—enough to distort a protocol’s internal prices.
- A proxy contract is no minor detail: it’s the mechanism that determines what code gets executed. If an attacker can modify it, they control the entire protocol.
The security of a DeFi protocol isn’t guaranteed by the technology: it depends on how far its developers went in imagining how it could fail. Two platforms have just shown that this work never ends.
Transparency: Binance may pay us a commission if you trade after clicking an asset symbol or a price link in this post.
#SeguridadDeFi #ContratosInteligentes #PrestamosRelampago #CryptoRisks
1
100
·
--
The close of the second quarter sends an uncomfortable signal for DeFi: the cost of security is no longer just a technical detail, but a variable that affects liquidity, trust, and valuation. On Binance Square, the discussion around losses from hacks in Q2 has ramped up again, and the most useful read isn’t the isolated headline, but the regime shift: when incidents multiply, the market starts rewarding the promise of returns less and operational resilience more.
According to Binance News using data from DeFiLlama, the quarter accumulated $780.3 million in losses across 88 incidents with known amounts as of June 30. April concentrated most of the damage, but May and June confirmed the problem wasn’t a one-off event—it was sustained pressure on bridges, protocol logic, key management, and incident response. That changes the conversation: audits, real-time monitoring, and damage-limitation controls move from being “defensive spending” to becoming part of the cost of attracting capital.
For users, the lesson also changes. In previous cycles, it was enough to track TVL, incentives, or the narrative. Today, it’s worth looking at which protocols have strengthened their processes, which teams communicate quickly when anomalies appear, and where there is real depth to absorb shocks without destroying trust. In other words, security starts trading like a quality premium.
In the market, the reaction is not linear. Ethereum rises 3.02% in 24h to 1609.94 and regains structure on the 4H chart from 1569.89 toward the 1610.60 area, signaling that capital continues to use its ecosystem as a baseline reference. Aave moves up 1.59% to 86.71 with a 24h range of 84.29 to 87.98, while dYdX jumps 17.42% to 0.18938 and confirms that appetite for trading tokens hasn’t disappeared, even though its 4H candle shows cooling after the spike from 0.24466. The contrast is clear: demand is back, but it arrives with a lower tolerance for operational risk.
$ETH $AAVE $DYDX
Educational Content. Not financial advice.
#SeguridadDeFi #Ethereum #AAVE #DYDX #BinanceSquare
The close of the second quarter sends an uncomfortable signal for DeFi: the cost of security is no longer just a technical detail, but a variable that affects liquidity, trust, and valuation. On Binance Square, the discussion around losses from hacks in Q2 has ramped up again, and the most useful read isn’t the isolated headline, but the regime shift: when incidents multiply, the market starts rewarding the promise of returns less and operational resilience more.
According to Binance News using data from DeFiLlama, the quarter accumulated $780.3 million in losses across 88 incidents with known amounts as of June 30. April concentrated most of the damage, but May and June confirmed the problem wasn’t a one-off event—it was sustained pressure on bridges, protocol logic, key management, and incident response. That changes the conversation: audits, real-time monitoring, and damage-limitation controls move from being “defensive spending” to becoming part of the cost of attracting capital.
For users, the lesson also changes. In previous cycles, it was enough to track TVL, incentives, or the narrative. Today, it’s worth looking at which protocols have strengthened their processes, which teams communicate quickly when anomalies appear, and where there is real depth to absorb shocks without destroying trust. In other words, security starts trading like a quality premium.
In the market, the reaction is not linear. Ethereum rises 3.02% in 24h to 1609.94 and regains structure on the 4H chart from 1569.89 toward the 1610.60 area, signaling that capital continues to use its ecosystem as a baseline reference. Aave moves up 1.59% to 86.71 with a 24h range of 84.29 to 87.98, while dYdX jumps 17.42% to 0.18938 and confirms that appetite for trading tokens hasn’t disappeared, even though its 4H candle shows cooling after the spike from 0.24466. The contrast is clear: demand is back, but it arrives with a lower tolerance for operational risk.
$ETH $AAVE $DYDX
Educational Content. Not financial advice.
#SeguridadDeFi #Ethereum #AAVE #DYDX #BinanceSquare
According to Binance News using data from DeFiLlama, the quarter accumulated $780.3 million in losses across 88 incidents with known amounts as of June 30. April concentrated most of the damage, but May and June confirmed the problem wasn’t a one-off event—it was sustained pressure on bridges, protocol logic, key management, and incident response. That changes the conversation: audits, real-time monitoring, and damage-limitation controls move from being “defensive spending” to becoming part of the cost of attracting capital.
For users, the lesson also changes. In previous cycles, it was enough to track TVL, incentives, or the narrative. Today, it’s worth looking at which protocols have strengthened their processes, which teams communicate quickly when anomalies appear, and where there is real depth to absorb shocks without destroying trust. In other words, security starts trading like a quality premium.
In the market, the reaction is not linear. Ethereum rises 3.02% in 24h to 1609.94 and regains structure on the 4H chart from 1569.89 toward the 1610.60 area, signaling that capital continues to use its ecosystem as a baseline reference. Aave moves up 1.59% to 86.71 with a 24h range of 84.29 to 87.98, while dYdX jumps 17.42% to 0.18938 and confirms that appetite for trading tokens hasn’t disappeared, even though its 4H candle shows cooling after the spike from 0.24466. The contrast is clear: demand is back, but it arrives with a lower tolerance for operational risk.
$ETH $AAVE $DYDX
Educational Content. Not financial advice.
#SeguridadDeFi #Ethereum #AAVE #DYDX #BinanceSquare
91

·
--
🚨 $LIT BETRAYAL AT LIGHTER!
Lighter, the perpetuals exchange, woke up to $15.48 million in USDC drained from two market maker accounts. To me, the most serious thing isn’t the amount: it’s that leaked API keys were enough to empty the accounts without the protocol breaking.
Look at the detail no one is seeing:
→ Account #714710 lost $10.39M and #714723 another $5.09M, this morning, November 16.
→ The attacker created a public pool with a 0% fee, bought 99.99% with just ~$10,000, and withdrew the funds in batches of ~$1M.
→ The stolen funds have already been swapped for ETH on CoW Swap, and 640 ETH (~$1.12M) were sent to Hyperliquid to buy 2,240 XMR, which is almost impossible to trace.
Lighter paused withdrawals and pool creation indefinitely, and its token $LIT fell 9%, from $2.75 to $2.50.
Do you think decentralized exchanges are safer than centralized ones? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #DeFiSecurity
🚨 $LIT BETRAYAL AT LIGHTER!
Lighter, the perpetuals exchange, woke up to $15.48 million in USDC drained from two market maker accounts. To me, the most serious thing isn’t the amount: it’s that leaked API keys were enough to empty the accounts without the protocol breaking.
Look at the detail no one is seeing:
→ Account #714710 lost $10.39M and #714723 another $5.09M, this morning, November 16.
→ The attacker created a public pool with a 0% fee, bought 99.99% with just ~$10,000, and withdrew the funds in batches of ~$1M.
→ The stolen funds have already been swapped for ETH on CoW Swap, and 640 ETH (~$1.12M) were sent to Hyperliquid to buy 2,240 XMR, which is almost impossible to trace.
Lighter paused withdrawals and pool creation indefinitely, and its token $LIT fell 9%, from $2.75 to $2.50.
Do you think decentralized exchanges are safer than centralized ones? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #DeFiSecurity
Lighter, the perpetuals exchange, woke up to $15.48 million in USDC drained from two market maker accounts. To me, the most serious thing isn’t the amount: it’s that leaked API keys were enough to empty the accounts without the protocol breaking.
Look at the detail no one is seeing:
→ Account #714710 lost $10.39M and #714723 another $5.09M, this morning, November 16.
→ The attacker created a public pool with a 0% fee, bought 99.99% with just ~$10,000, and withdrew the funds in batches of ~$1M.
→ The stolen funds have already been swapped for ETH on CoW Swap, and 640 ETH (~$1.12M) were sent to Hyperliquid to buy 2,240 XMR, which is almost impossible to trace.
Lighter paused withdrawals and pool creation indefinitely, and its token $LIT fell 9%, from $2.75 to $2.50.
Do you think decentralized exchanges are safer than centralized ones? 👇
$LIT $ETH $XMR
#HackCrypto #Lighter #DeFiSecurity
3.9k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#IsAnthropic’s$1.5TMarketCapJustified?
27,142 views
154 Discussing
2
#BTCBelow$62KAmidHikeFearsAndShiftToAnthropic
236 views
4 Discussing
3
#NvidiaBoardReportedlySplitOverHuang’sReturn
152,675 views
1,271 Discussing
4
#CanGTA6'sLaunchLiftTTWOShares?
118,113 views
926 Discussing
5
#LedgerProbesTamperedWalletsInBerlinAndDubai
73 views
10 Discussing
6
#13FInstitutionsBitcoinSpotETPHoldingsHitRecord
3,404 views
72 Discussing
7
#BTCRemainsUnderPressureAfterHawkishFOMCMinutes
308,940 views
2,282 Discussing
8
#StrategySTRCPreferredSlips3.65%Below$100Par
10,840 views
94 Discussing
9
#MASToUpgradeSGDTestnetToSGDigitalLedger
34,176 views
349 Discussing
10
#Solana2027RoadmapTargetsDoubleComputeCapacity
15,987 views
189 Discussing