
#security
security
2M views
6,282 Discussing
Hot
Latest

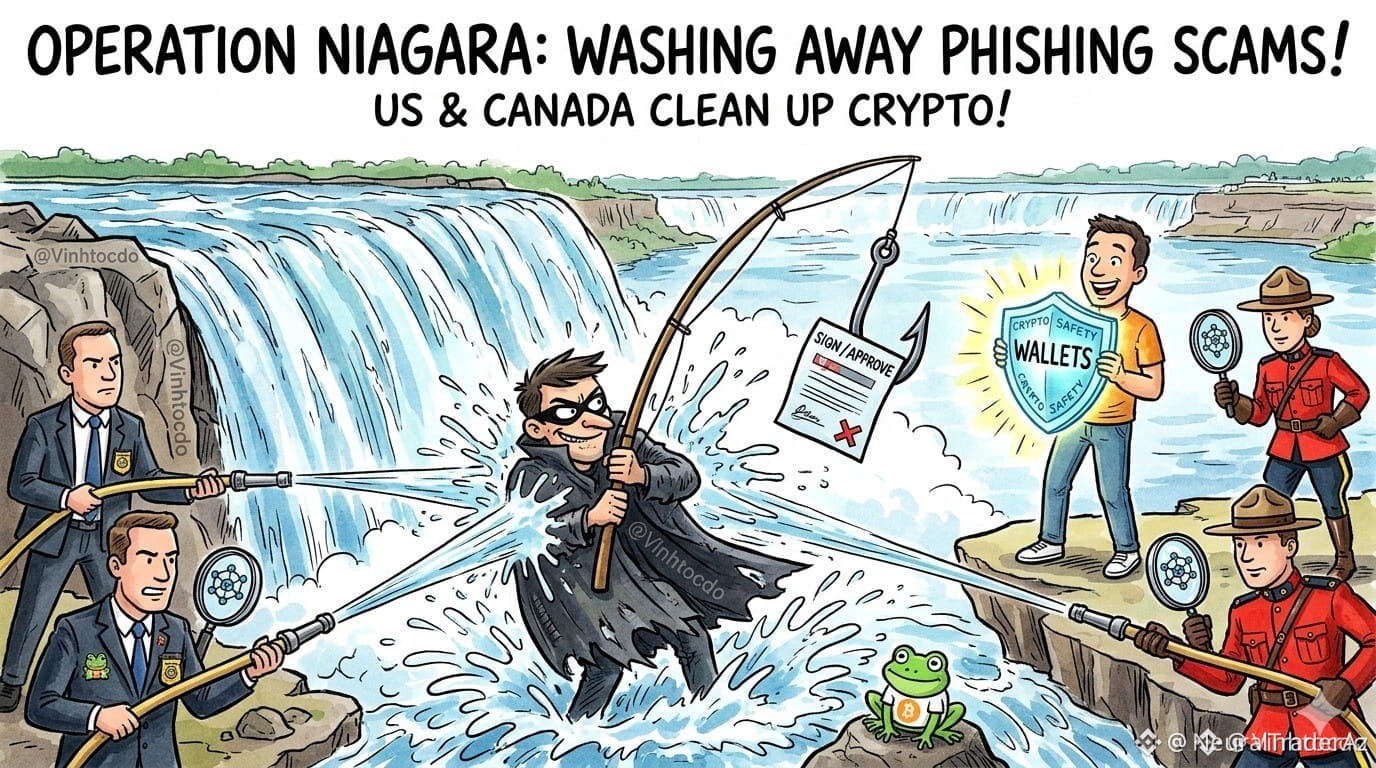
🚨 $BTC $ETH OPERATION NIAGARA SMASHES APPROVAL PHISHING! 💥
Chainalysis, U.S. intel and Canadian authorities have synced on‑chain intel to flag rogue approval contracts before they can drain wallets. 🦈 The joint ‘Operation Niagara’ sweeps the liquidity pools of malicious spend‑allowances, turning a potential outflow into a defensive reclaim.
Trader playbook: run Revoke.cash on every address, yank any unknown approve, double‑check signatures before hitting ‘Sign’, and silo airdrop hunting wallets from core storage. 📊 Early revokes cut the attacker’s window to zero, preserving capital across $BTC , $ETH and emerging tokens like $BREV .
💬 Are you auditing your approvals today or waiting for the next sweep?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #AntiPhishing #Web3Safety #Crypto
🦈 🔥
🚨 $BTC $ETH OPERATION NIAGARA SMASHES APPROVAL PHISHING! 💥
Chainalysis, U.S. intel and Canadian authorities have synced on‑chain intel to flag rogue approval contracts before they can drain wallets. 🦈 The joint ‘Operation Niagara’ sweeps the liquidity pools of malicious spend‑allowances, turning a potential outflow into a defensive reclaim.
Trader playbook: run Revoke.cash on every address, yank any unknown approve, double‑check signatures before hitting ‘Sign’, and silo airdrop hunting wallets from core storage. 📊 Early revokes cut the attacker’s window to zero, preserving capital across $BTC , $ETH and emerging tokens like $BREV .
💬 Are you auditing your approvals today or waiting for the next sweep?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #AntiPhishing #Web3Safety #Crypto
🦈 🔥
Chainalysis, U.S. intel and Canadian authorities have synced on‑chain intel to flag rogue approval contracts before they can drain wallets. 🦈 The joint ‘Operation Niagara’ sweeps the liquidity pools of malicious spend‑allowances, turning a potential outflow into a defensive reclaim.
Trader playbook: run Revoke.cash on every address, yank any unknown approve, double‑check signatures before hitting ‘Sign’, and silo airdrop hunting wallets from core storage. 📊 Early revokes cut the attacker’s window to zero, preserving capital across $BTC , $ETH and emerging tokens like $BREV .
💬 Are you auditing your approvals today or waiting for the next sweep?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #AntiPhishing #Web3Safety #Crypto
🦈 🔥
5

·
--
The Dawn of Cyber Warfare: AI and the East-West Tech Conflict
The landscape of global cybersecurity has crossed a dangerous and defining threshold. Google’s Threat Intelligence Group recently uncovered what is believed to be the first fully automated, AI-driven cyberattack pipeline operating completely without human intervention. Discovered on an exposed staging server, the automated tool—dubbed an "exploit_agent"—scanned software updates, analyzed code patches, independently formulated exploits, and launched attacks against targets in Europe, featuring explicit Russian-language code comments within its files. We know also that most microsoft products
Hacking tools are Russian. (Mainly windows and office).
This milestone highlights an escalating technological arms race between Western defense frameworks and Eastern threat actors. Historically, even advanced artificial intelligence served merely as an accelerator for human hackers, handling tasks like reconnaissance or phishing drafts. Now, autonomous agents are closing the gap between vulnerability disclosure and exploitation to mere hours, fundamentally outpacing traditional defensive response cycles.
As state-sponsored and independent hackers from regions like Russia leverage autonomous agentic workflows, Western security face an unprecedented challenge. The conflict is no longer just about human ingenuity pitted against software firewalls, but machine speed against human reaction time.
This discovery serves as an urgent wake-up call, proving that the future of the technology war will be fought and decided at the automated speed of artificial intelligence!
#security #writetoearn $BTC #bitcoin #Etherum
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
The Dawn of Cyber Warfare: AI and the East-West Tech Conflict
The landscape of global cybersecurity has crossed a dangerous and defining threshold. Google’s Threat Intelligence Group recently uncovered what is believed to be the first fully automated, AI-driven cyberattack pipeline operating completely without human intervention. Discovered on an exposed staging server, the automated tool—dubbed an "exploit_agent"—scanned software updates, analyzed code patches, independently formulated exploits, and launched attacks against targets in Europe, featuring explicit Russian-language code comments within its files. We know also that most microsoft products
Hacking tools are Russian. (Mainly windows and office).
This milestone highlights an escalating technological arms race between Western defense frameworks and Eastern threat actors. Historically, even advanced artificial intelligence served merely as an accelerator for human hackers, handling tasks like reconnaissance or phishing drafts. Now, autonomous agents are closing the gap between vulnerability disclosure and exploitation to mere hours, fundamentally outpacing traditional defensive response cycles.
As state-sponsored and independent hackers from regions like Russia leverage autonomous agentic workflows, Western security face an unprecedented challenge. The conflict is no longer just about human ingenuity pitted against software firewalls, but machine speed against human reaction time.
This discovery serves as an urgent wake-up call, proving that the future of the technology war will be fought and decided at the automated speed of artificial intelligence!
#security #writetoearn $BTC #bitcoin #Etherum
$ETH
The landscape of global cybersecurity has crossed a dangerous and defining threshold. Google’s Threat Intelligence Group recently uncovered what is believed to be the first fully automated, AI-driven cyberattack pipeline operating completely without human intervention. Discovered on an exposed staging server, the automated tool—dubbed an "exploit_agent"—scanned software updates, analyzed code patches, independently formulated exploits, and launched attacks against targets in Europe, featuring explicit Russian-language code comments within its files. We know also that most microsoft products
Hacking tools are Russian. (Mainly windows and office).
This milestone highlights an escalating technological arms race between Western defense frameworks and Eastern threat actors. Historically, even advanced artificial intelligence served merely as an accelerator for human hackers, handling tasks like reconnaissance or phishing drafts. Now, autonomous agents are closing the gap between vulnerability disclosure and exploitation to mere hours, fundamentally outpacing traditional defensive response cycles.
As state-sponsored and independent hackers from regions like Russia leverage autonomous agentic workflows, Western security face an unprecedented challenge. The conflict is no longer just about human ingenuity pitted against software firewalls, but machine speed against human reaction time.
This discovery serves as an urgent wake-up call, proving that the future of the technology war will be fought and decided at the automated speed of artificial intelligence!
#security #writetoearn $BTC #bitcoin #Etherum
$ETH
1
121
·
--
I didn't expect a hack that hit 178 major websites to net about $7,000.
Attackers abused a signup flaw in Optimizely's testing tool to plant code on sites including Ledger, HSBC, the BBC, CNN, Salesforce and Zoom. The script swapped crypto wallet addresses and skimmed card details. Report URI found it in 188 of 1,611 Optimizely snippets it checked.
By Monday night only TalkTalk still served it. Card theft is still unknown.
If a 178-site campaign earns $7K, was this a heist or a test run?
{spot}(BTCUSDT)
#Crypto #Security
NFA. I trade my own book. DYOR.
I didn't expect a hack that hit 178 major websites to net about $7,000.
Attackers abused a signup flaw in Optimizely's testing tool to plant code on sites including Ledger, HSBC, the BBC, CNN, Salesforce and Zoom. The script swapped crypto wallet addresses and skimmed card details. Report URI found it in 188 of 1,611 Optimizely snippets it checked.
By Monday night only TalkTalk still served it. Card theft is still unknown.
If a 178-site campaign earns $7K, was this a heist or a test run?
#Crypto #Security
NFA. I trade my own book. DYOR.
Attackers abused a signup flaw in Optimizely's testing tool to plant code on sites including Ledger, HSBC, the BBC, CNN, Salesforce and Zoom. The script swapped crypto wallet addresses and skimmed card details. Report URI found it in 188 of 1,611 Optimizely snippets it checked.
By Monday night only TalkTalk still served it. Card theft is still unknown.
If a 178-site campaign earns $7K, was this a heist or a test run?
#Crypto #Security
NFA. I trade my own book. DYOR.
55
Jito says crypto teams need to slow down and fix security gaps.
Per The Block, Jito’s Lucas Bruder warned about patient attackers and urged crypto builders to address technical debt and security weaknesses.
$BTC is at $63,728, flat in 1h and down 2.0% in 24h, while $ETH is at $1,790, down 1.8%. Last 1h Binance liquidations were quiet, with longs at $250K and shorts at $295K. $PEPE is the weakest on the day at down 4.5%.
Are builders moving fast enough?
#CryptoNews #Security
Not financial advice.
Jito says crypto teams need to slow down and fix security gaps.
Per The Block, Jito’s Lucas Bruder warned about patient attackers and urged crypto builders to address technical debt and security weaknesses.
$BTC is at $63,728, flat in 1h and down 2.0% in 24h, while $ETH is at $1,790, down 1.8%. Last 1h Binance liquidations were quiet, with longs at $250K and shorts at $295K. $PEPE is the weakest on the day at down 4.5%.
Are builders moving fast enough?
#CryptoNews #Security
Not financial advice.
Per The Block, Jito’s Lucas Bruder warned about patient attackers and urged crypto builders to address technical debt and security weaknesses.
$BTC is at $63,728, flat in 1h and down 2.0% in 24h, while $ETH is at $1,790, down 1.8%. Last 1h Binance liquidations were quiet, with longs at $250K and shorts at $295K. $PEPE is the weakest on the day at down 4.5%.
Are builders moving fast enough?
#CryptoNews #Security
Not financial advice.
88
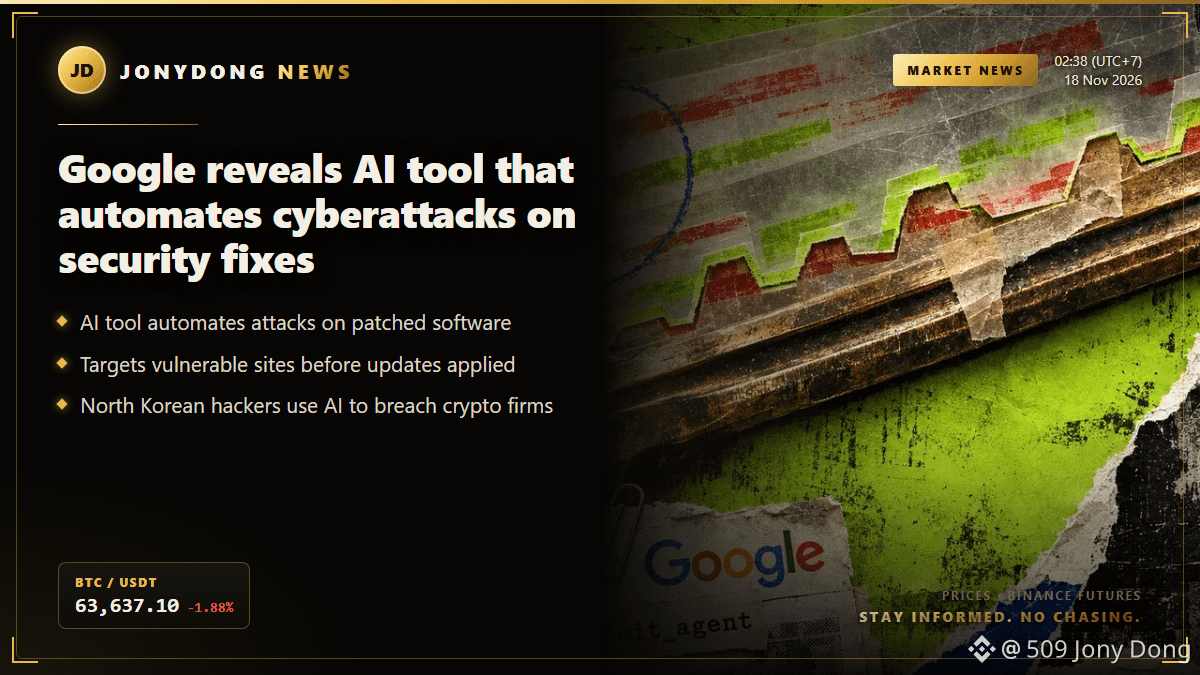
This AI hacking tool shows how quickly threats evolve. We need to stay vigilant.
Google reveals AI tool that automates cyberattacks on security fixes
Google's Threat Intelligence Group and Mandiant have uncovered a new AI-powered hacking tool that can transform software security fixes into automated attacks. This tool, called exploit_agent, is designed to monitor software updates and exploit vulnerabilities that developers have recently patched. By comparing the updated code with older versions, it can generate and execute attack code with little to no human input.
The implications are concerning, as this method allows attackers to focus on known vulnerabilities, bypassing the need to discover new ones. The research also revealed that the operator of this tool has shown interest in targeting French websites related to media and education, indicating a specific focus area for these automated attacks.
In addition to this discovery, Google reported that suspected North Korean hackers employed AI development tools to infiltrate cryptocurrency organizations in North America and Europe. They created fake recruiter profiles using AI-generated images to lure victims into executing malicious scripts.
This development shows the growing threat from autonomous exploitation frameworks, which could lead to faster attacks on organizations running outdated software. As these tools become more sophisticated, website operators may face tighter windows for applying necessary security updates, raising the stakes for cybersecurity across the board.
$BTC
#Security #CryptoNews
This AI hacking tool shows how quickly threats evolve. We need to stay vigilant.
Google reveals AI tool that automates cyberattacks on security fixes
Google's Threat Intelligence Group and Mandiant have uncovered a new AI-powered hacking tool that can transform software security fixes into automated attacks. This tool, called exploit_agent, is designed to monitor software updates and exploit vulnerabilities that developers have recently patched. By comparing the updated code with older versions, it can generate and execute attack code with little to no human input.
The implications are concerning, as this method allows attackers to focus on known vulnerabilities, bypassing the need to discover new ones. The research also revealed that the operator of this tool has shown interest in targeting French websites related to media and education, indicating a specific focus area for these automated attacks.
In addition to this discovery, Google reported that suspected North Korean hackers employed AI development tools to infiltrate cryptocurrency organizations in North America and Europe. They created fake recruiter profiles using AI-generated images to lure victims into executing malicious scripts.
This development shows the growing threat from autonomous exploitation frameworks, which could lead to faster attacks on organizations running outdated software. As these tools become more sophisticated, website operators may face tighter windows for applying necessary security updates, raising the stakes for cybersecurity across the board.
$BTC
#Security #CryptoNews
Google reveals AI tool that automates cyberattacks on security fixes
Google's Threat Intelligence Group and Mandiant have uncovered a new AI-powered hacking tool that can transform software security fixes into automated attacks. This tool, called exploit_agent, is designed to monitor software updates and exploit vulnerabilities that developers have recently patched. By comparing the updated code with older versions, it can generate and execute attack code with little to no human input.
The implications are concerning, as this method allows attackers to focus on known vulnerabilities, bypassing the need to discover new ones. The research also revealed that the operator of this tool has shown interest in targeting French websites related to media and education, indicating a specific focus area for these automated attacks.
In addition to this discovery, Google reported that suspected North Korean hackers employed AI development tools to infiltrate cryptocurrency organizations in North America and Europe. They created fake recruiter profiles using AI-generated images to lure victims into executing malicious scripts.
This development shows the growing threat from autonomous exploitation frameworks, which could lead to faster attacks on organizations running outdated software. As these tools become more sophisticated, website operators may face tighter windows for applying necessary security updates, raising the stakes for cybersecurity across the board.
$BTC
#Security #CryptoNews
BTC-0.29%
GOOGUS+0.90%
357
·
--
Malware Hits 178 Major Sites — Ledger, Salesforce, BBC Served Crypto-Stealing Code
Hackers injected crypto- and credit card-stealing malware into website scripts used by 178 major organizations, including Ledger, Salesforce and the BBC. The campaign, dubbed 'Optimjack,' spread through scripts hosted by optimization platform Optimizely, researchers found.
Anyone who visited an affected site could have had wallet and card details stolen. Double-check your approvals and move funds if you interacted with a compromised page.
Not financial advice.
#Crypto #Security
Malware Hits 178 Major Sites — Ledger, Salesforce, BBC Served Crypto-Stealing Code
Hackers injected crypto- and credit card-stealing malware into website scripts used by 178 major organizations, including Ledger, Salesforce and the BBC. The campaign, dubbed 'Optimjack,' spread through scripts hosted by optimization platform Optimizely, researchers found.
Anyone who visited an affected site could have had wallet and card details stolen. Double-check your approvals and move funds if you interacted with a compromised page.
Not financial advice.
#Crypto #Security
Hackers injected crypto- and credit card-stealing malware into website scripts used by 178 major organizations, including Ledger, Salesforce and the BBC. The campaign, dubbed 'Optimjack,' spread through scripts hosted by optimization platform Optimizely, researchers found.
Anyone who visited an affected site could have had wallet and card details stolen. Double-check your approvals and move funds if you interacted with a compromised page.
Not financial advice.
#Crypto #Security
4

·
--
🚨 THIRD-PARTY SCRIPT VULNERABILITY TRIGGERS A LIQUIDITY CLEANSE ACROSS $HUMA , $GLMR , AND $BLESS ! 📉
Recent script compromises across major web infrastructure have forced a defensive liquidity flush, impacting broader sentiment for assets like $HUMA , $GLMR , and $BLESS . 📊
Smart money views these external operational anomalies not as structural invalidations, but as localized noise requiring strict risk discipline and transaction verification. 💡
Order flow remains resilient as protocols isolate the payload vectors. ⚡ Are you tightening your security parameters or accumulating through the volatility? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HUMA #Security #Crypto #MarketStructure
🔥 💎
🚨 THIRD-PARTY SCRIPT VULNERABILITY TRIGGERS A LIQUIDITY CLEANSE ACROSS $HUMA , $GLMR , AND $BLESS ! 📉
Recent script compromises across major web infrastructure have forced a defensive liquidity flush, impacting broader sentiment for assets like $HUMA , $GLMR , and $BLESS . 📊
Smart money views these external operational anomalies not as structural invalidations, but as localized noise requiring strict risk discipline and transaction verification. 💡
Order flow remains resilient as protocols isolate the payload vectors. ⚡ Are you tightening your security parameters or accumulating through the volatility? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HUMA #Security #Crypto #MarketStructure
🔥 💎
Recent script compromises across major web infrastructure have forced a defensive liquidity flush, impacting broader sentiment for assets like $HUMA , $GLMR , and $BLESS . 📊
Smart money views these external operational anomalies not as structural invalidations, but as localized noise requiring strict risk discipline and transaction verification. 💡
Order flow remains resilient as protocols isolate the payload vectors. ⚡ Are you tightening your security parameters or accumulating through the volatility? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HUMA #Security #Crypto #MarketStructure
🔥 💎
1
·
--
🚨 Trezor data breach repeats — is your crypto safe?
🚨 **Trezor reports another exposure of user emails and hashed passwords.**
The hardware‑wallet maker’s repeat breach raises fresh concerns about offline storage security.
📊 **Market snapshot**
• $BTC price: $65,042 (‑2.6% change)
• $ETH price: $1,831 (+33.4% change)
• Fear & Greed Index: 12 – Extreme Fear
🔐 **What this means**
• Ongoing security worries could influence short‑term trading sentiment.
• Investors may reassess custodial vs. non‑custodial strategies.
💬 **Your move?** What steps are you taking to protect your assets? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Wallet
🚨 Trezor data breach repeats — is your crypto safe?
🚨 **Trezor reports another exposure of user emails and hashed passwords.**
The hardware‑wallet maker’s repeat breach raises fresh concerns about offline storage security.
📊 **Market snapshot**
• $BTC price: $65,042 (‑2.6% change)
• $ETH price: $1,831 (+33.4% change)
• Fear & Greed Index: 12 – Extreme Fear
🔐 **What this means**
• Ongoing security worries could influence short‑term trading sentiment.
• Investors may reassess custodial vs. non‑custodial strategies.
💬 **Your move?** What steps are you taking to protect your assets? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Wallet
🚨 **Trezor reports another exposure of user emails and hashed passwords.**
The hardware‑wallet maker’s repeat breach raises fresh concerns about offline storage security.
📊 **Market snapshot**
• $BTC price: $65,042 (‑2.6% change)
• $ETH price: $1,831 (+33.4% change)
• Fear & Greed Index: 12 – Extreme Fear
🔐 **What this means**
• Ongoing security worries could influence short‑term trading sentiment.
• Investors may reassess custodial vs. non‑custodial strategies.
💬 **Your move?** What steps are you taking to protect your assets? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Wallet
9
·
--
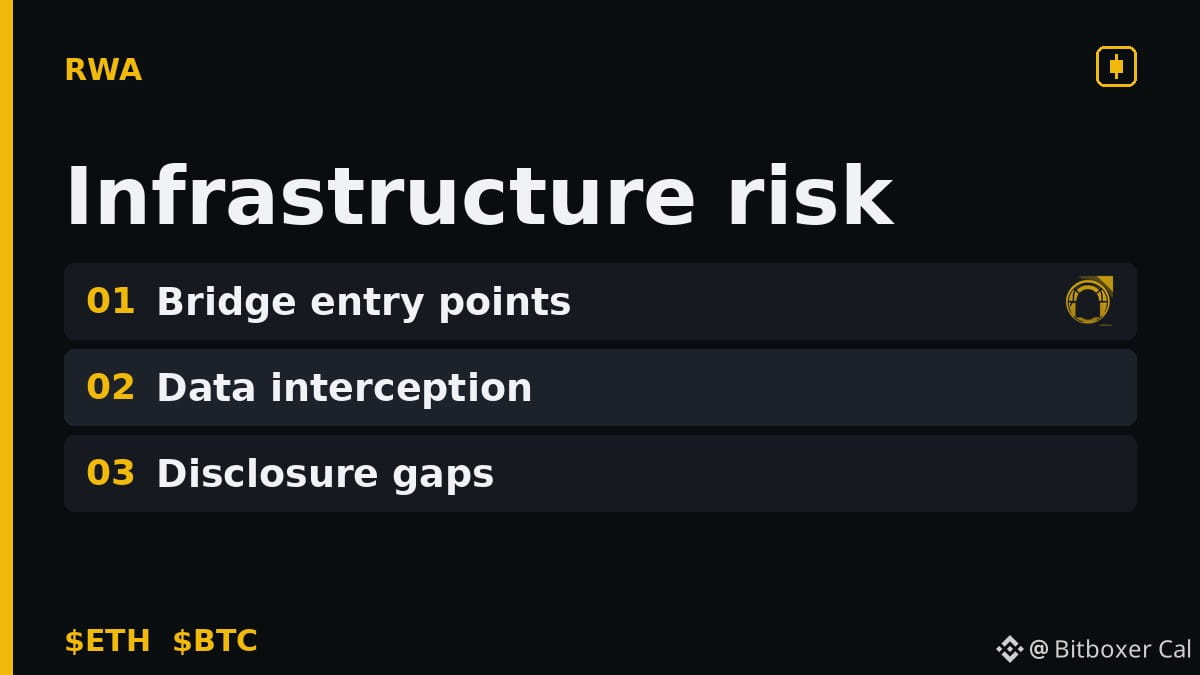
The crowd treats $ETH like a secure vault for Real World Assets, but they’re missing the structural rot.
Pros know supply chain attacks aren't just front-end bugs; they’re direct strikes at the tokenization layer. While institutions obsess over disclosure frameworks, hackers are busy hijacking site infrastructure. Watch the integrity of bridge interfaces, not just the protocol security.
$ETH $BTC #crypto #security #rwa
The crowd treats $ETH like a secure vault for Real World Assets, but they’re missing the structural rot.
Pros know supply chain attacks aren't just front-end bugs; they’re direct strikes at the tokenization layer. While institutions obsess over disclosure frameworks, hackers are busy hijacking site infrastructure. Watch the integrity of bridge interfaces, not just the protocol security.
$ETH $BTC #crypto #security #rwa
Pros know supply chain attacks aren't just front-end bugs; they’re direct strikes at the tokenization layer. While institutions obsess over disclosure frameworks, hackers are busy hijacking site infrastructure. Watch the integrity of bridge interfaces, not just the protocol security.
$ETH $BTC #crypto #security #rwa
22

Trezor has confirmed another data breach involving their logistics partner, Skladon, impacting 27,000 users. While the hardware wallets remain secure, the exposure of customer addresses poses significant real-world physical risks. This serves as a brutal reminder that cold storage is only as secure as the data chain surrounding your purchase. If you ordered recently, be extra vigilant against sophisticated phishing attempts or cold-call scams. Privacy in crypto isn't just about keys; it is about metadata. $BTC #Security #CryptoSafety #Trezor
Trezor has confirmed another data breach involving their logistics partner, Skladon, impacting 27,000 users. While the hardware wallets remain secure, the exposure of customer addresses poses significant real-world physical risks. This serves as a brutal reminder that cold storage is only as secure as the data chain surrounding your purchase. If you ordered recently, be extra vigilant against sophisticated phishing attempts or cold-call scams. Privacy in crypto isn't just about keys; it is about metadata. $BTC #Security #CryptoSafety #Trezor
18


·
--
🚨 Trezor says a partner breach exposed data on about 27,000 orders
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
🚨 Trezor says a partner breach exposed data on about 27,000 orders
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
95
·
--
🚨 178 major sites hit with crypto‑stealing malware – is your wallet safe?
🚨 **178 major sites** just got hit with crypto‑stealing malware – is your wallet safe? Find out what’s happening now.
🔎 **What happened?**
Hackers slipped a new script into the checkout flow of 178 high‑traffic sites, from e‑commerce giants to news portals. The code harvests wallet addresses in real‑time, turning browsers into silent thieves.
📊 **Market impact**
• $BTC is holding around **$64,618**, steady near the $64,300 support level as Fear & Greed Index spikes to **12 (Extreme Fear)**.
• $ETH trades near **$1,816**, testing resistance around $1,840 after a modest gain.
• Traders are pausing, with overall crypto volume showing a slight dip.
💡 **Discussion**
Is this a catalyst for tighter wallet security standards or just another short‑term scare? **Bullish long‑term or short‑term noise?** Share your thoughts below 👇
$BTC #Crypto #Security #News
🚨 178 major sites hit with crypto‑stealing malware – is your wallet safe?
🚨 **178 major sites** just got hit with crypto‑stealing malware – is your wallet safe? Find out what’s happening now.
🔎 **What happened?**
Hackers slipped a new script into the checkout flow of 178 high‑traffic sites, from e‑commerce giants to news portals. The code harvests wallet addresses in real‑time, turning browsers into silent thieves.
📊 **Market impact**
• $BTC is holding around **$64,618**, steady near the $64,300 support level as Fear & Greed Index spikes to **12 (Extreme Fear)**.
• $ETH trades near **$1,816**, testing resistance around $1,840 after a modest gain.
• Traders are pausing, with overall crypto volume showing a slight dip.
💡 **Discussion**
Is this a catalyst for tighter wallet security standards or just another short‑term scare? **Bullish long‑term or short‑term noise?** Share your thoughts below 👇
$BTC #Crypto #Security #News
🚨 **178 major sites** just got hit with crypto‑stealing malware – is your wallet safe? Find out what’s happening now.
🔎 **What happened?**
Hackers slipped a new script into the checkout flow of 178 high‑traffic sites, from e‑commerce giants to news portals. The code harvests wallet addresses in real‑time, turning browsers into silent thieves.
📊 **Market impact**
• $BTC is holding around **$64,618**, steady near the $64,300 support level as Fear & Greed Index spikes to **12 (Extreme Fear)**.
• $ETH trades near **$1,816**, testing resistance around $1,840 after a modest gain.
• Traders are pausing, with overall crypto volume showing a slight dip.
💡 **Discussion**
Is this a catalyst for tighter wallet security standards or just another short‑term scare? **Bullish long‑term or short‑term noise?** Share your thoughts below 👇
$BTC #Crypto #Security #News
2
Another security incident hit Trezor's shipping partners, leaking sensitive buyer data like delivery addresses. While cold wallets keep private keys offline, the physical exposure of customer details remains a critical blind spot. Hardware wallet users must remain vigilant against targeted phishing schemes that exploit this leaked logistics info, reminding us that operational security extends far beyond just holding your keys safely. $BTC #Bitcoin #Security #CryptoSafety
Another security incident hit Trezor's shipping partners, leaking sensitive buyer data like delivery addresses. While cold wallets keep private keys offline, the physical exposure of customer details remains a critical blind spot. Hardware wallet users must remain vigilant against targeted phishing schemes that exploit this leaked logistics info, reminding us that operational security extends far beyond just holding your keys safely. $BTC #Bitcoin #Security #CryptoSafety
26
·
--
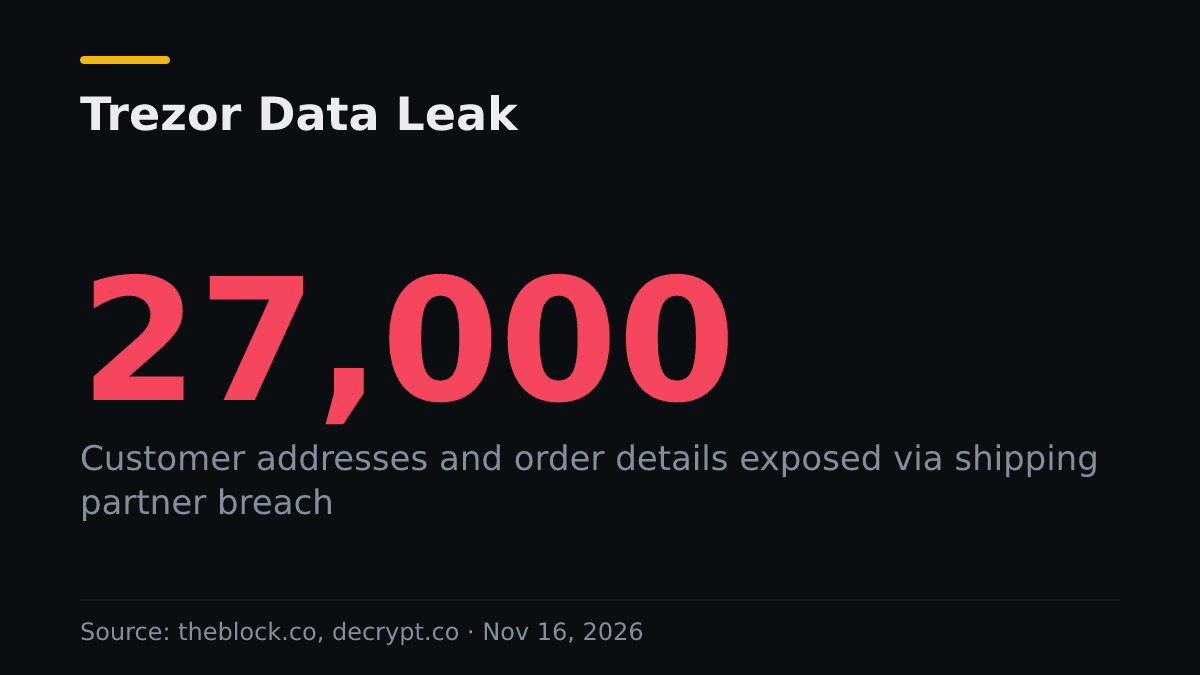
27,000 Trezor orders exposed in a fresh data leak.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
27,000 Trezor orders exposed in a fresh data leak.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
• Trezor disclosed a breach at a shipping partner affecting ~27,000 orders (theblock.co)
• A second partner leak revealed customer addresses and order details, prompting scam call warnings (decrypt.co)
• The incidents raise fresh concerns over physical security and supply‑chain risks for hardware wallets (theblock.co)
These breaches highlight that even offline‑first wallets can be vulnerable through their logistics chain, urging users to monitor for phishing.
What’s your next step to protect your crypto assets?
A) Review wallet address exposure
B) Switch to a different hardware wallet
C) Strengthen phishing defenses
$BTC #Security #HardwareWallet 🔐
⚠️ Not financial advice. DYOR.
16
·
--
Sanidul Islam:
okay bro 👍
1
1
171
·
--
🚨 $BTC $ETH: $6.5M wallet drained – is your crypto safe?
📊 Sentiment Check
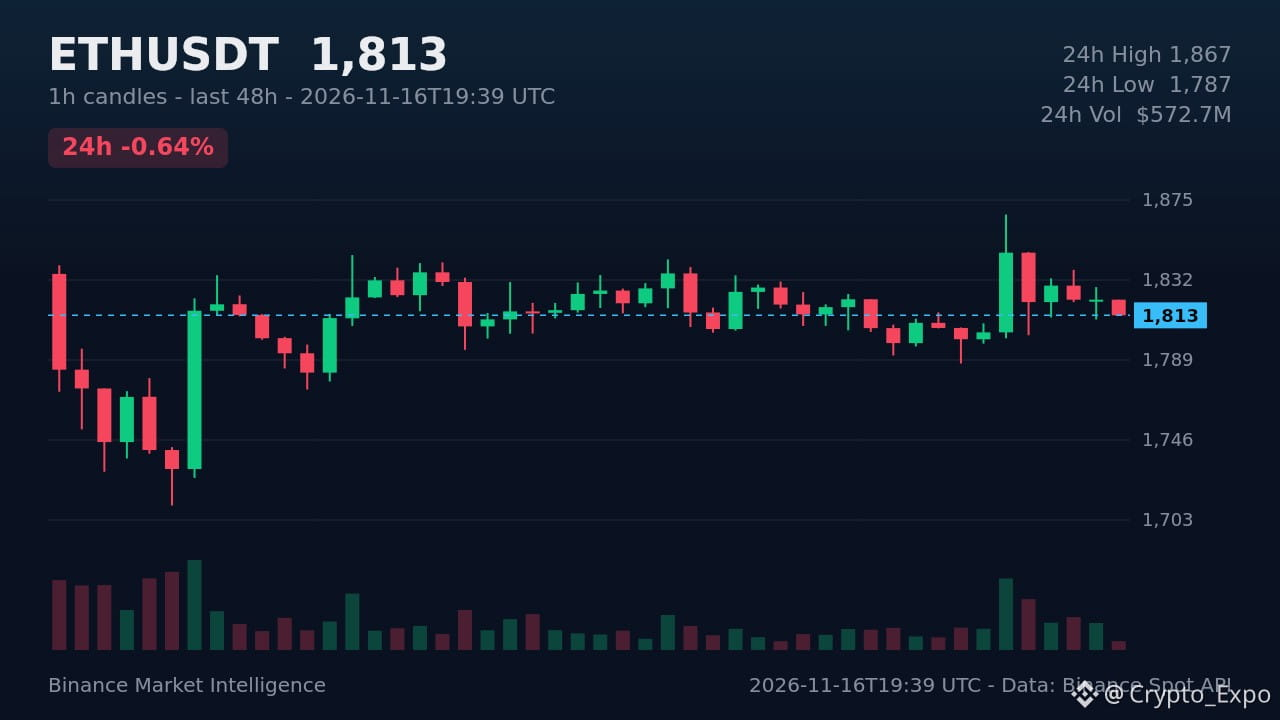
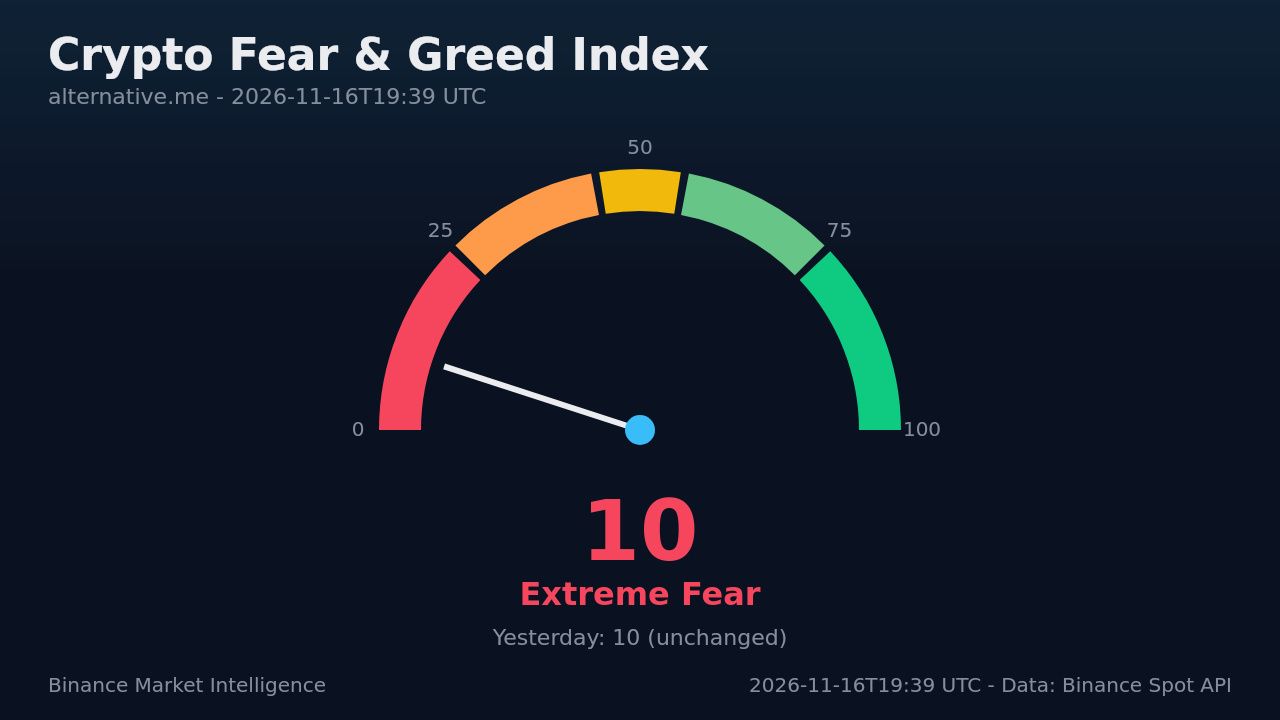
The Fear & Greed Index is at **10 (Extreme Fear)** – the lowest level recorded. Meanwhile $BTC trades at **$64,818** and $ETH at **$1,813**, barely moving despite the fear spike.
🔐 Security Alert
• A hot‑wallet breach cost **$6.5 M** – a stark reminder that large balances remain prime targets.
• $BTC 24‑hr volume is **1.42 B** USD and $ETH volume **572 M** USD, showing high on‑chain activity that can amplify attacks.
💭 What’s your move?
Do you pull funds to a hardware wallet, or wait for the fear to subside? Share your strategy below!
$BTC #Crypto #Security
🚨 $BTC $ETH : $6.5M wallet drained – is your crypto safe?
📊 Sentiment Check
The Fear & Greed Index is at **10 (Extreme Fear)** – the lowest level recorded. Meanwhile $BTC trades at **$64,818** and $ETH at **$1,813**, barely moving despite the fear spike.
🔐 Security Alert
• A hot‑wallet breach cost **$6.5 M** – a stark reminder that large balances remain prime targets.
• $BTC 24‑hr volume is **1.42 B** USD and $ETH volume **572 M** USD, showing high on‑chain activity that can amplify attacks.
💭 What’s your move?
Do you pull funds to a hardware wallet, or wait for the fear to subside? Share your strategy below!
$BTC #Crypto #Security
📊 Sentiment Check
The Fear & Greed Index is at **10 (Extreme Fear)** – the lowest level recorded. Meanwhile $BTC trades at **$64,818** and $ETH at **$1,813**, barely moving despite the fear spike.
🔐 Security Alert
• A hot‑wallet breach cost **$6.5 M** – a stark reminder that large balances remain prime targets.
• $BTC 24‑hr volume is **1.42 B** USD and $ETH volume **572 M** USD, showing high on‑chain activity that can amplify attacks.
💭 What’s your move?
Do you pull funds to a hardware wallet, or wait for the fear to subside? Share your strategy below!
$BTC #Crypto #Security
7
·
--
🚨🔓 SAFE WALLET DRAINED $6.5M — KEY COMPROMISED! 🔓🚨
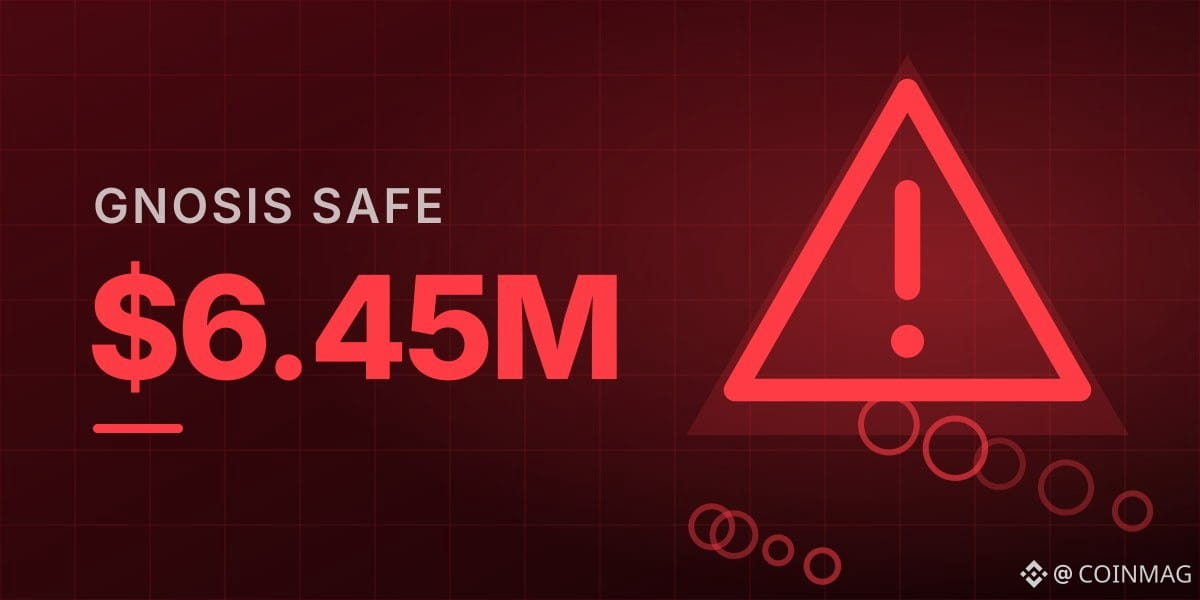
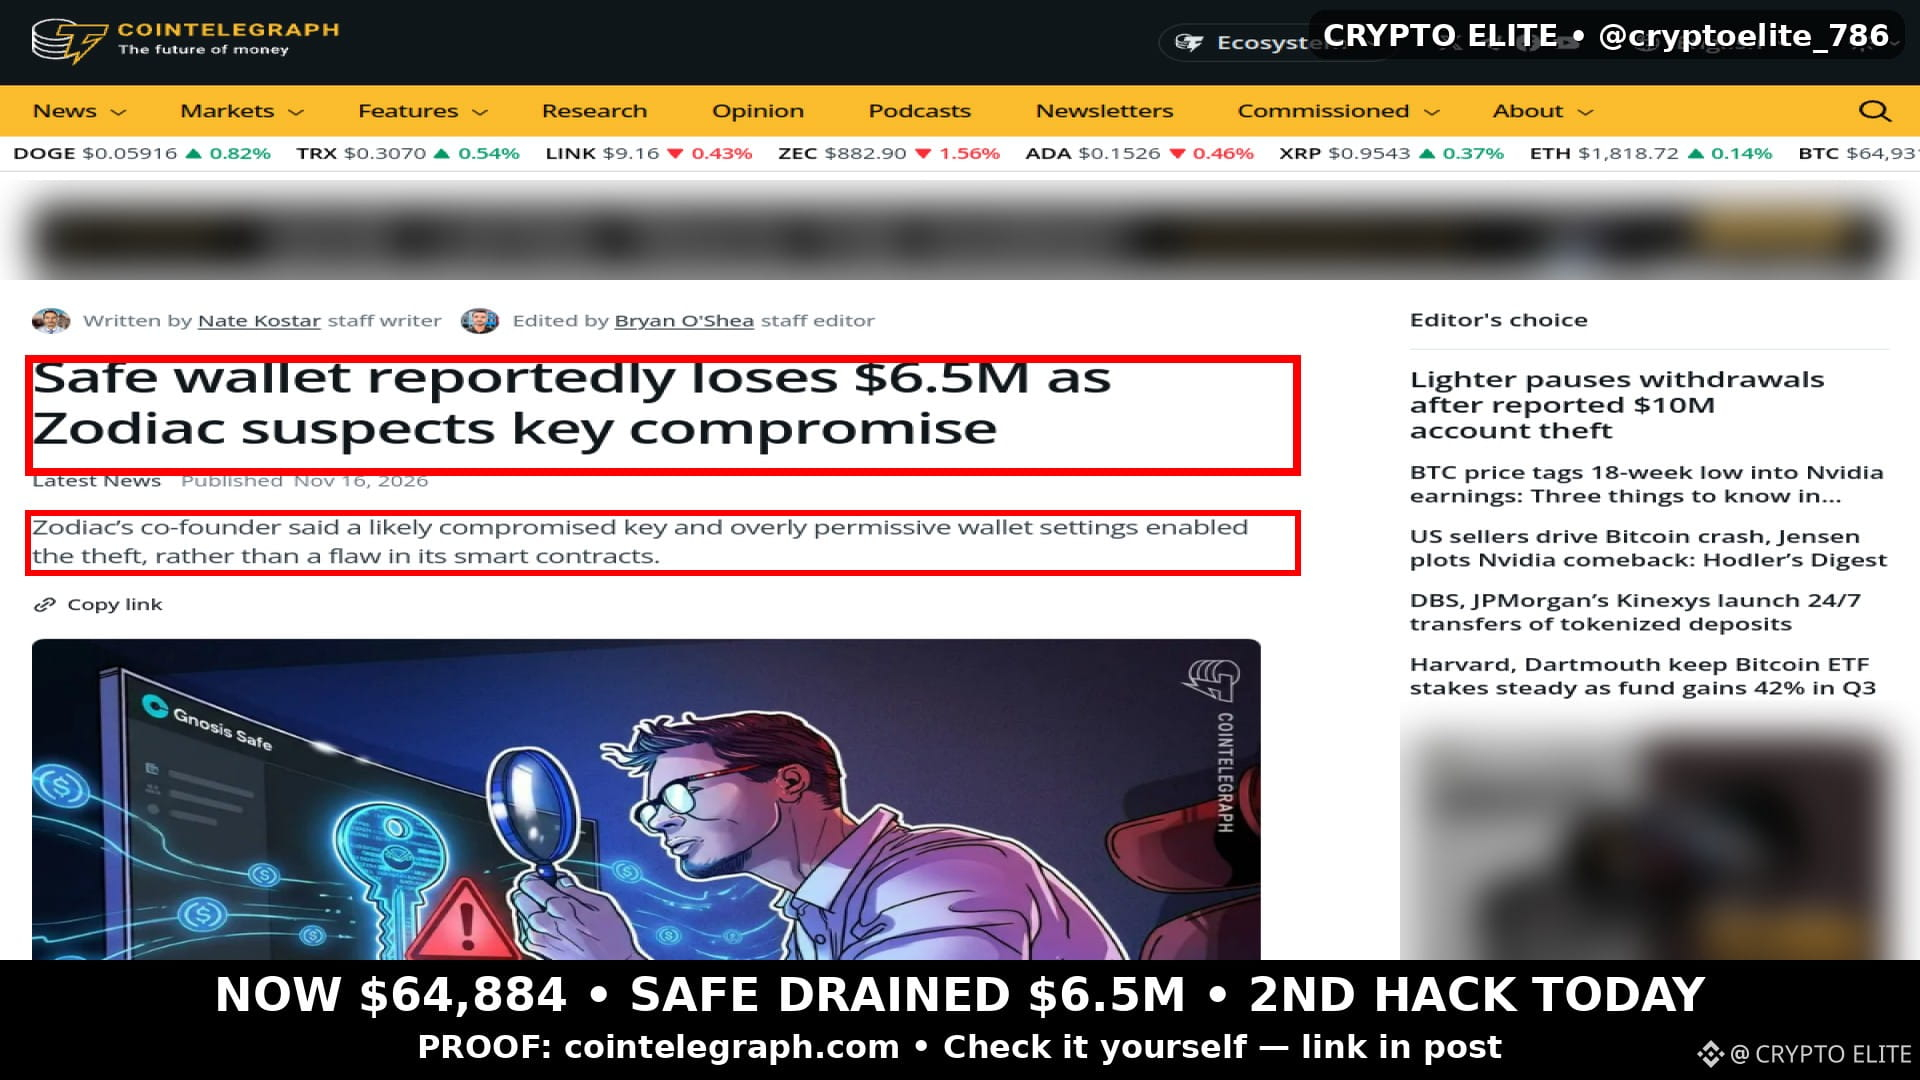
A Gnosis Safe multisig wallet was drained of ~$6.45M — $4.3M in USDC + $1.7M in syrupUSDC gone.
Zodiac's co-founder says it was a likely compromised key and overly permissive wallet settings — NOT a flaw in the smart contracts.
The hacker already spent ~$813K buying XMR (Monero) on Hyperliquid to hide the trail.
This is the SECOND major drain TODAY — Lighter lost $15.5M this morning. Wallets are under attack right now.
Do you still trust multisig wallets with your funds? 👇
THE PROOF — check this news yourself here:
https://cointelegraph.com/news/safe-wallet-reportedly-loses-millions-after-key-compromise
$BTC $ETH #SafeWallet #CryptoHack #Security
🚨🔓 SAFE WALLET DRAINED $6.5M — KEY COMPROMISED! 🔓🚨
A Gnosis Safe multisig wallet was drained of ~$6.45M — $4.3M in USDC + $1.7M in syrupUSDC gone.
Zodiac's co-founder says it was a likely compromised key and overly permissive wallet settings — NOT a flaw in the smart contracts.
The hacker already spent ~$813K buying XMR (Monero) on Hyperliquid to hide the trail.
This is the SECOND major drain TODAY — Lighter lost $15.5M this morning. Wallets are under attack right now.
Do you still trust multisig wallets with your funds? 👇
THE PROOF — check this news yourself here:
https://cointelegraph.com/news/safe-wallet-reportedly-loses-millions-after-key-compromise
$BTC $ETH #SafeWallet #CryptoHack #Security
A Gnosis Safe multisig wallet was drained of ~$6.45M — $4.3M in USDC + $1.7M in syrupUSDC gone.
Zodiac's co-founder says it was a likely compromised key and overly permissive wallet settings — NOT a flaw in the smart contracts.
The hacker already spent ~$813K buying XMR (Monero) on Hyperliquid to hide the trail.
This is the SECOND major drain TODAY — Lighter lost $15.5M this morning. Wallets are under attack right now.
Do you still trust multisig wallets with your funds? 👇
THE PROOF — check this news yourself here:
https://cointelegraph.com/news/safe-wallet-reportedly-loses-millions-after-key-compromise
$BTC $ETH #SafeWallet #CryptoHack #Security
1
127
·
--
📰 Exchange Protection Funds Explained: SAFU, Bitget’s Fund and Who Actually Pays You Back
An exchange protection fund is a pool of money a crypto exchange sets aside to repay users after a hack. Binance calls its fund SAFU, Bitget calls it the Protection Fund, and both have paid out in 2026. A fund is not insurance and not a legal...
Source : Airdropalert
Time : 2026-11-16 04:52:00
Credit : morten christensen
#security #guides
$KCS $USDC $BTC
Share your opinion in the comment section below
📰 Exchange Protection Funds Explained: SAFU, Bitget’s Fund and Who Actually Pays You Back
An exchange protection fund is a pool of money a crypto exchange sets aside to repay users after a hack. Binance calls its fund SAFU, Bitget calls it the Protection Fund, and both have paid out in 2026. A fund is not insurance and not a legal...
Source : Airdropalert
Time : 2026-11-16 04:52:00
Credit : morten christensen
#security #guides
$KCS $USDC $BTC
Share your opinion in the comment section below
An exchange protection fund is a pool of money a crypto exchange sets aside to repay users after a hack. Binance calls its fund SAFU, Bitget calls it the Protection Fund, and both have paid out in 2026. A fund is not insurance and not a legal...
Source : Airdropalert
Time : 2026-11-16 04:52:00
Credit : morten christensen
#security #guides
$KCS $USDC $BTC
Share your opinion in the comment section below
1
1
·
--
🚨 8,000 Solana fans converged in London and one walked away iPhone‑less and wallet‑empty!
Security breach risk spikes as thieves target self‑custody holders.
Police logged nearly 40k phone thefts this year, your phone is your key.
Stay vigilant, disable facial unlock and keep crypto gear low‑key.
$SOL #security #solana #conference
🚨 8,000 Solana fans converged in London and one walked away iPhone‑less and wallet‑empty!
Security breach risk spikes as thieves target self‑custody holders.
Police logged nearly 40k phone thefts this year, your phone is your key.
Stay vigilant, disable facial unlock and keep crypto gear low‑key.
$SOL #security #solana #conference
Security breach risk spikes as thieves target self‑custody holders.
Police logged nearly 40k phone thefts this year, your phone is your key.
Stay vigilant, disable facial unlock and keep crypto gear low‑key.
$SOL #security #solana #conference
1
2
122

·
--
What if the $15.5M "hack" wasn't a hack at all?
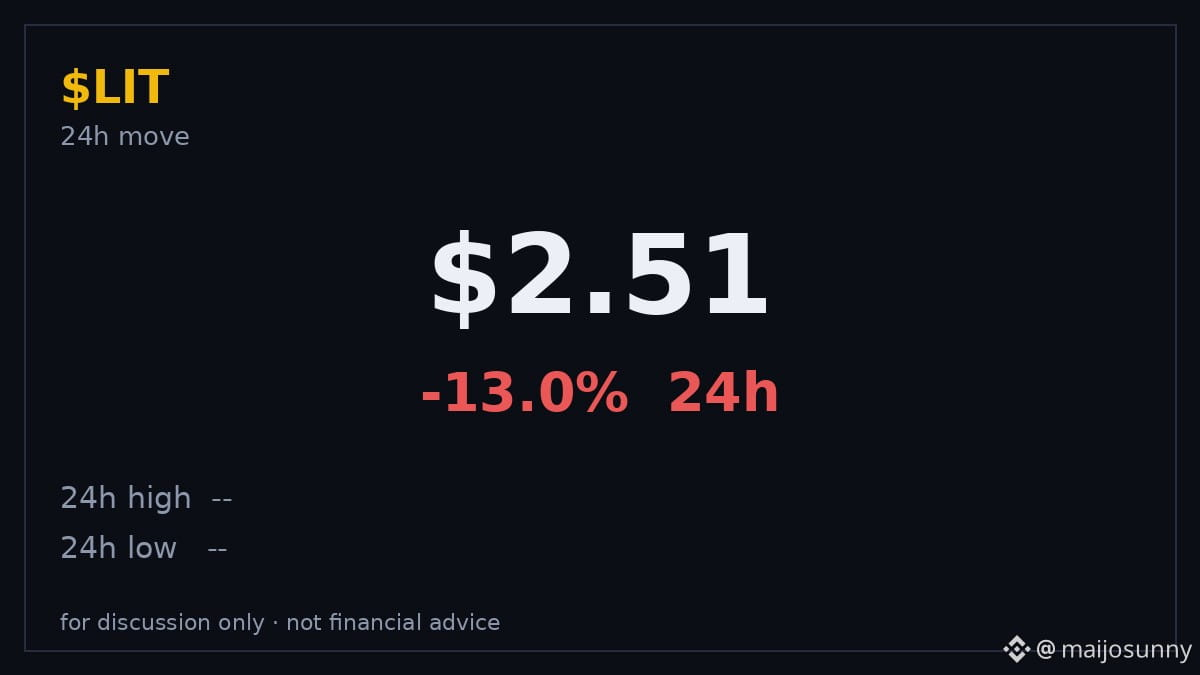
Lighter, the Ethereum L2 perp DEX, froze all withdrawals today after ~$15.48M in USDC vanished from two market-maker accounts. $LIT fell 13%+ in 24h (Coin360), and Upbit and Bithumb both halted LIT deposits and withdrawals as a precaution.
Here's the twist: Lighter says its protocol was NOT hacked. The trail, pieced together by on-chain investigators, points to leaked API keys. The attacker allegedly closed the victims' open positions, spun up a public pool with 0% fees, bought 99.99% of its shares for ~$10,000, then funneled the USDC through in ~$1M batches and redeemed it out. $10.39M USDC became ~5,750 ETH via CoW Swap within minutes. Coinglass logged $3.19M in hourly LIT liquidations, the most of any token, mostly longs getting flushed.
📊 Why it matters: this is the latest lesson of 2026 about where crypto actually breaks. Not the smart contract, the keys around it. One leaked API key turned a market maker's account into an open vault, with no extra signature needed for same-L1 transfers. And the $5.09M second-account loss still isn't independently confirmed as having left the platform, so treat the $15.48M total as an estimate, not a final figure.
My take: this is bigger than one DEX's bad day. It is a warning that API permissions are the new private keys, and most traders have never audited what theirs can do.
👀 What to watch: when withdrawals reopen, whether the second $5.09M is confirmed, and whether other perp venues tighten API key scopes this week.
A leaked key drained $15.5M without touching a single smart contract. Is your API key scoped tightly enough, or is it a loaded gun? 👇
Not financial advice. DYOR.
#crypto #Lighter #DeFi #Security
What if the $15.5M "hack" wasn't a hack at all?
Lighter, the Ethereum L2 perp DEX, froze all withdrawals today after ~$15.48M in USDC vanished from two market-maker accounts. $LIT fell 13%+ in 24h (Coin360), and Upbit and Bithumb both halted LIT deposits and withdrawals as a precaution.
Here's the twist: Lighter says its protocol was NOT hacked. The trail, pieced together by on-chain investigators, points to leaked API keys. The attacker allegedly closed the victims' open positions, spun up a public pool with 0% fees, bought 99.99% of its shares for ~$10,000, then funneled the USDC through in ~$1M batches and redeemed it out. $10.39M USDC became ~5,750 ETH via CoW Swap within minutes. Coinglass logged $3.19M in hourly LIT liquidations, the most of any token, mostly longs getting flushed.
📊 Why it matters: this is the latest lesson of 2026 about where crypto actually breaks. Not the smart contract, the keys around it. One leaked API key turned a market maker's account into an open vault, with no extra signature needed for same-L1 transfers. And the $5.09M second-account loss still isn't independently confirmed as having left the platform, so treat the $15.48M total as an estimate, not a final figure.
My take: this is bigger than one DEX's bad day. It is a warning that API permissions are the new private keys, and most traders have never audited what theirs can do.
👀 What to watch: when withdrawals reopen, whether the second $5.09M is confirmed, and whether other perp venues tighten API key scopes this week.
A leaked key drained $15.5M without touching a single smart contract. Is your API key scoped tightly enough, or is it a loaded gun? 👇
Not financial advice. DYOR.
#crypto #Lighter #DeFi #Security
Lighter, the Ethereum L2 perp DEX, froze all withdrawals today after ~$15.48M in USDC vanished from two market-maker accounts. $LIT fell 13%+ in 24h (Coin360), and Upbit and Bithumb both halted LIT deposits and withdrawals as a precaution.
Here's the twist: Lighter says its protocol was NOT hacked. The trail, pieced together by on-chain investigators, points to leaked API keys. The attacker allegedly closed the victims' open positions, spun up a public pool with 0% fees, bought 99.99% of its shares for ~$10,000, then funneled the USDC through in ~$1M batches and redeemed it out. $10.39M USDC became ~5,750 ETH via CoW Swap within minutes. Coinglass logged $3.19M in hourly LIT liquidations, the most of any token, mostly longs getting flushed.
📊 Why it matters: this is the latest lesson of 2026 about where crypto actually breaks. Not the smart contract, the keys around it. One leaked API key turned a market maker's account into an open vault, with no extra signature needed for same-L1 transfers. And the $5.09M second-account loss still isn't independently confirmed as having left the platform, so treat the $15.48M total as an estimate, not a final figure.
My take: this is bigger than one DEX's bad day. It is a warning that API permissions are the new private keys, and most traders have never audited what theirs can do.
👀 What to watch: when withdrawals reopen, whether the second $5.09M is confirmed, and whether other perp venues tighten API key scopes this week.
A leaked key drained $15.5M without touching a single smart contract. Is your API key scoped tightly enough, or is it a loaded gun? 👇
Not financial advice. DYOR.
#crypto #Lighter #DeFi #Security
111
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaBeatsEstimatesWith$130BQ4Outlook
11,288 views
157 Discussing
2
#AnthropicIPOPriceCouldExceed$80
17,247 views
143 Discussing
3
#CanNvidia’sDataCenterGrowthContinue?
51,623 views
713 Discussing
4
#CanadaAndUSLaunchOperationNiagaraAgainstApprovalPhishing
2,138 views
30 Discussing
5
#BankOfEnglandUnveilsClearingHousePathwayCoveringDLTFirms
1,872 views
44 Discussing
6
#DBSAndCirclePartnerToExpandAsianInstitutionsUSDCAccess
3,273 views
54 Discussing
7
#LedgerHardwareImplantReportsExtendToDubai
19,937 views
290 Discussing
8
#NvidiaBoardNotConsideringHuang’sReturnasCEO
214,458 views
1,547 Discussing
9
#KOSPIFalls2.59%ToLowestCloseSinceFebruary
64,153 views
737 Discussing
10
#AnthropicClearedToListOnNasdaqAsANT
56,362 views
605 Discussing