
#defisecurity
defisecurity
130,858 views
683 Discussing
Hot
Latest

·
--
🚨 Polkadot lost $1.38M due to a re-exploited security flaw from four months prior. The attacker resumed using their own relayer before the XCM fix was applied, but a later upgrade corrected the supply without altering user balances. This highlights the critical importance of timely patch deployment in DeFi security.
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
🚨 Polkadot lost $1.38M due to a re-exploited security flaw from four months prior. The attacker resumed using their own relayer before the XCM fix was applied, but a later upgrade corrected the supply without altering user balances. This highlights the critical importance of timely patch deployment in DeFi security.
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
💡 Market Implication: DOT faces short-term downside pressure as the exploit renews concerns about network resilience.
🤔 Question: Will this renewed exploit trigger a broader risk-off sentiment across the Polkadot ecosystem?
#Polkadot #DeFiSecurity
$DOT #TradingSignal #CryptoAnalysis
3

Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Governance, bought in a single transaction — that is what happened to X100 on Saturday evening, and I keep coming back to how little stood in the attackers' way.
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
Attackers used a flash loan to buy their way into two of X100's three "Senate" seats, then created, voted on and executed proposals inside the same transaction — selling treasury tokens into a pool they had just created and burning the project's liquidity position. Blockaid flagged the attack as still ongoing at its alert, with about $4.85 million in USDT realized.
The flaw is the design itself: voting power counted the moment tokens were frozen, with no snapshot, no holding period and no timelock. X collapsed about 96.5% that day.
The wider tape was already soft — $BTC $80,420 (-1.3%), $ETH $2,335 (-2.8%) — not a reaction to this one small token. The lesson goes beyond X100: any DAO letting freshly bought votes execute instantly is one flash loan from the same fate. DYOR, not investment advice.
Which guardrail should be non-negotiable for DAOs after this: snapshots, timelocks, or both?
#CryptoMarkets #DeFiSecurity #Governance #Exploit
5
·
--
My Crypto Safety Roadmap (Part 8): How I Manage and Revoke Risky Smart Contract Permissions🎈🎈
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
{spot}(XAUTUSDT)
My Crypto Safety Roadmap (Part 8): How I Manage and Revoke Risky Smart Contract Permissions🎈🎈
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
🔴Interacting with Decentralized Applications (DApps) and DeFi platforms is a major part of my crypto execution, but it introduces a hidden risk that many overlook. In my journey, I discovered that granting "unlimited token approval" to a platform allows its smart contracts to access my assets at any time. If that protocol gets exploited or turns out to be a scam, my connected wallet can be drained instantly. To secure my treasury, I established a strict inspection and cleanup routine.🚀
🔴Today, I never leave permanent or unlimited spending permissions active on my Web3 wallets. I routinely use blockchain scanners and revocation tools like Revoke.cash to audit every single smart contract connection I have made. Whenever I finish a transaction or interact with a new platform, I immediately revoke or minimize the allowed token allowance. Controlling exactly who and what can interact with my digital assets is my ultimate shield against smart contract exploits.🚀
#CryptoSafety #SmartContracts #Web3Security #DeFiSecurity $XAUT $BTC $BNB
💥Not Financial Advice
1
236

🚨 $ETH SECURITY ALERT: ATTACK WAVES MIRROR A GLOBAL PANDEMIC 🦈
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
🚨 $ETH SECURITY ALERT: ATTACK WAVES MIRROR A GLOBAL PANDEMIC 🦈
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
📊 Attackers are now sweeping through the crypto space with the intensity of a pandemic, turning on‑chain breaches into an early warning system for the broader internet. 🪙 Small DeFi projects with thin security nets are the low‑hanging fruit, while heavyweight protocols are deploying AI shields to harden their perimeters. ⚡ This divergence creates a clear liquidity gap: smart money is already repositioning, scouting for resilient assets before the next wave hits.
💡 The pattern suggests a spill‑over effect—once the traditional web feels the pressure, we’ll see a cascade of cross‑industry exploits. 👇 Are you auditing your exposure before the next sweep hits your portfolio?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFiSecurity #CryptoRisk #SmartMoney
🔥 💎
4

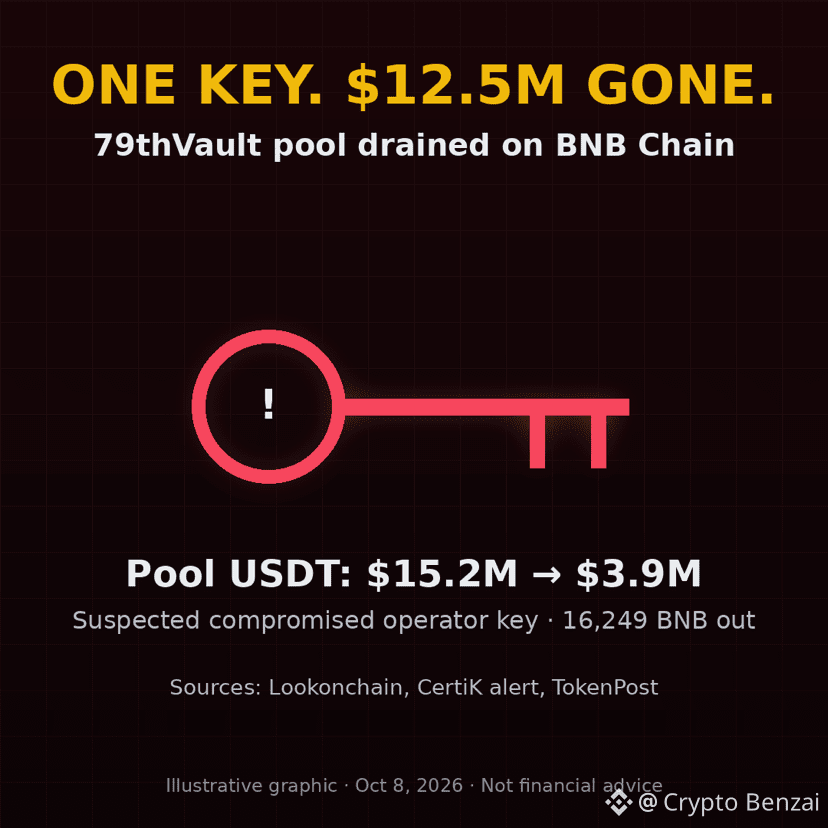
One Key, $12.5M Gone: 79thVault Drained on BNB Chain
A wallet with special admin powers over the 79AU token pulled 2.01M tokens out of its PancakeSwap pool and sold them back in. That cut the pool's USDT from $15.2M to $3.9M, and the attacker walked off with 16,249 $BNB (~$12.5M) Lookonchain and CertiK point to a likely leaked operator key. The team revoked the role and offered a 10% bounty. Lesson: check who holds the admin keys before you ape in.
Do you check token permissions before buying?
#DeFiSecurity #BNBChain #CryptoSafety
One Key, $12.5M Gone: 79thVault Drained on BNB Chain
A wallet with special admin powers over the 79AU token pulled 2.01M tokens out of its PancakeSwap pool and sold them back in. That cut the pool's USDT from $15.2M to $3.9M, and the attacker walked off with 16,249 $BNB (~$12.5M) Lookonchain and CertiK point to a likely leaked operator key. The team revoked the role and offered a 10% bounty. Lesson: check who holds the admin keys before you ape in.
Do you check token permissions before buying?
#DeFiSecurity #BNBChain #CryptoSafety
A wallet with special admin powers over the 79AU token pulled 2.01M tokens out of its PancakeSwap pool and sold them back in. That cut the pool's USDT from $15.2M to $3.9M, and the attacker walked off with 16,249 $BNB (~$12.5M) Lookonchain and CertiK point to a likely leaked operator key. The team revoked the role and offered a 10% bounty. Lesson: check who holds the admin keys before you ape in.
Do you check token permissions before buying?
#DeFiSecurity #BNBChain #CryptoSafety
61
·
--
🚨 $6M drained from a Base vault controlled by a 7-signer Safe — owners still unknown. 1,783 wstETH moved, Base and Aave contracts untouched. This points to a private key compromise or insider risk, not protocol failure. ETH holders should watch for similar stealth outflows on L2s. Could this signal rising custody risks in DeFi?
#DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
🚨 $6M drained from a Base vault controlled by a 7-signer Safe — owners still unknown. 1,783 wstETH moved, Base and Aave contracts untouched. This points to a private key compromise or insider risk, not protocol failure. ETH holders should watch for similar stealth outflows on L2s. Could this signal rising custody risks in DeFi?
#DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
#DeFiSecurity
$ETH #TradingSignal #CryptoAnalysis
26

🚨 The NEAR Intents protocol identifies the attacker and grants a 48-hour window
The decentralized NEAR Intents protocol announced that it was able to identify the individual responsible for the recent hack that resulted in the theft of approximately $3.8 million.
The administration has granted the attacker a 48-hour deadline to return the funds, confirming that legal action will be taken in the event of no response.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ DEFI
#NEARProtocol #DeFiSecurity #BlockchainNews #CryptoCrime
📰 Source: cointelegraph.com
🚨 The NEAR Intents protocol identifies the attacker and grants a 48-hour window
The decentralized NEAR Intents protocol announced that it was able to identify the individual responsible for the recent hack that resulted in the theft of approximately $3.8 million.
The administration has granted the attacker a 48-hour deadline to return the funds, confirming that legal action will be taken in the event of no response.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ DEFI
#NEARProtocol #DeFiSecurity #BlockchainNews #CryptoCrime
📰 Source: cointelegraph.com
The decentralized NEAR Intents protocol announced that it was able to identify the individual responsible for the recent hack that resulted in the theft of approximately $3.8 million.
The administration has granted the attacker a 48-hour deadline to return the funds, confirming that legal action will be taken in the event of no response.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ DEFI
#NEARProtocol #DeFiSecurity #BlockchainNews #CryptoCrime
📰 Source: cointelegraph.com
117

·
--
🚨 $AVICI PROTOCOL SUFFERS $1.02M ON-CHAIN EXPLOIT AS FUNDS FLOW TO MIXERS 🔻
On-chain tracking reveals a critical exploit within the $AVICI framework, draining approximately $1.02M in liquidity. 🔍 The malicious actor routed 10,000 $SOL through stablecoins before executing a cross-chain swap into 418 $ETH .
The stolen capital has officially entered privacy protocols, confirming institutional capital flight and rapid washing mechanisms. 📉 Smart money dynamics always demand strict risk parameters when fundamental protocols experience severe structural breaches. 💬 How do you evaluate security risk before placing capital into emerging project vaults? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AVICI #DeFiSecurity #OnChainAnalysis #CryptoExploit
🚨 🛡️
🚨 $AVICI PROTOCOL SUFFERS $1.02M ON-CHAIN EXPLOIT AS FUNDS FLOW TO MIXERS 🔻
On-chain tracking reveals a critical exploit within the $AVICI framework, draining approximately $1.02M in liquidity. 🔍 The malicious actor routed 10,000 $SOL through stablecoins before executing a cross-chain swap into 418 $ETH .
The stolen capital has officially entered privacy protocols, confirming institutional capital flight and rapid washing mechanisms. 📉 Smart money dynamics always demand strict risk parameters when fundamental protocols experience severe structural breaches. 💬 How do you evaluate security risk before placing capital into emerging project vaults? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AVICI #DeFiSecurity #OnChainAnalysis #CryptoExploit
🚨 🛡️
On-chain tracking reveals a critical exploit within the $AVICI framework, draining approximately $1.02M in liquidity. 🔍 The malicious actor routed 10,000 $SOL through stablecoins before executing a cross-chain swap into 418 $ETH .
The stolen capital has officially entered privacy protocols, confirming institutional capital flight and rapid washing mechanisms. 📉 Smart money dynamics always demand strict risk parameters when fundamental protocols experience severe structural breaches. 💬 How do you evaluate security risk before placing capital into emerging project vaults? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AVICI #DeFiSecurity #OnChainAnalysis #CryptoExploit
🚨 🛡️
52
🚨 BREAKING !!!
CIRCLE FREEZES $12.6 MILLION cUSDC FROM ZAMA SECURITY PROTOCOL 🔴
ZachXBT reveals that Circle might have blacklisted the cUSDC contract address of Zama on Ethereum, freezing around $12.6 million of user funds 💸
The frozen address previously participated in a governance vote for Overnight Finance regarding fund allocation 🛠
Zama apparently didn't receive any notice before the freeze was implemented, while some users are accusing the project team of a rug pull 📊
ZachXBT points out that the plaintiff in the civil lawsuit involved — Patagon Management — has a history of attacking DAOs and siphoning protocols. There are still many unknowns to clarify in this incident.
#DeFiSecurity #Stablecoin
$ETH $BTC $HEI
🚨 BREAKING !!!
CIRCLE FREEZES $12.6 MILLION cUSDC FROM ZAMA SECURITY PROTOCOL 🔴
ZachXBT reveals that Circle might have blacklisted the cUSDC contract address of Zama on Ethereum, freezing around $12.6 million of user funds 💸
The frozen address previously participated in a governance vote for Overnight Finance regarding fund allocation 🛠
Zama apparently didn't receive any notice before the freeze was implemented, while some users are accusing the project team of a rug pull 📊
ZachXBT points out that the plaintiff in the civil lawsuit involved — Patagon Management — has a history of attacking DAOs and siphoning protocols. There are still many unknowns to clarify in this incident.
#DeFiSecurity #Stablecoin
$ETH $BTC $HEI
CIRCLE FREEZES $12.6 MILLION cUSDC FROM ZAMA SECURITY PROTOCOL 🔴
ZachXBT reveals that Circle might have blacklisted the cUSDC contract address of Zama on Ethereum, freezing around $12.6 million of user funds 💸
The frozen address previously participated in a governance vote for Overnight Finance regarding fund allocation 🛠
Zama apparently didn't receive any notice before the freeze was implemented, while some users are accusing the project team of a rug pull 📊
ZachXBT points out that the plaintiff in the civil lawsuit involved — Patagon Management — has a history of attacking DAOs and siphoning protocols. There are still many unknowns to clarify in this incident.
#DeFiSecurity #Stablecoin
$ETH $BTC $HEI
216

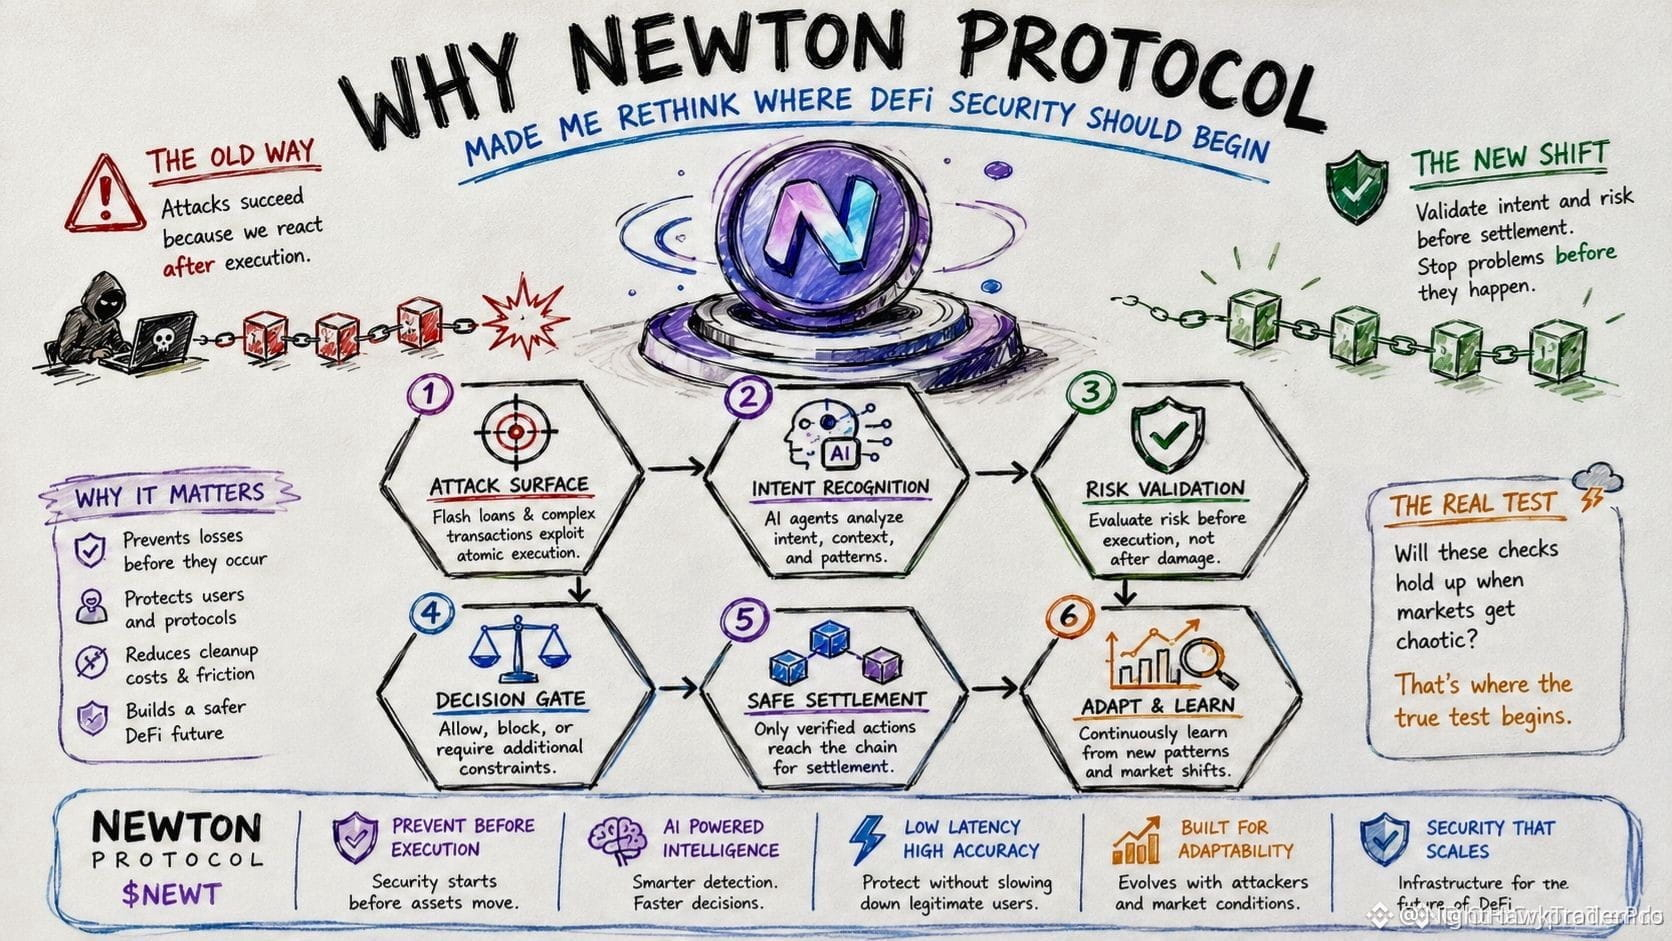
$NEWT IS SHIFTING WHERE DEFI SECURITY BEGINS 🧠
Most protocols focus on stopping attacks after they execute. Newton Protocol flips that by validating intent and risk before settlement. This isn't just another AI wrapper — it's rethinking the timing of security itself.
As crypto moves toward intent-based execution and AI agents making more decisions, the moment of validation becomes critical. The question isn't just how fast a transaction executes, but whether it should execute at all.
But can pre-settlement checks hold up when markets go chaotic, not predictable? That's where design meets reality. Are you betting on prevention or cleanup?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #IntentBased #CryptoInnovation
💎
$NEWT IS SHIFTING WHERE DEFI SECURITY BEGINS 🧠
Most protocols focus on stopping attacks after they execute. Newton Protocol flips that by validating intent and risk before settlement. This isn't just another AI wrapper — it's rethinking the timing of security itself.
As crypto moves toward intent-based execution and AI agents making more decisions, the moment of validation becomes critical. The question isn't just how fast a transaction executes, but whether it should execute at all.
But can pre-settlement checks hold up when markets go chaotic, not predictable? That's where design meets reality. Are you betting on prevention or cleanup?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #IntentBased #CryptoInnovation
💎
Most protocols focus on stopping attacks after they execute. Newton Protocol flips that by validating intent and risk before settlement. This isn't just another AI wrapper — it's rethinking the timing of security itself.
As crypto moves toward intent-based execution and AI agents making more decisions, the moment of validation becomes critical. The question isn't just how fast a transaction executes, but whether it should execute at all.
But can pre-settlement checks hold up when markets go chaotic, not predictable? That's where design meets reality. Are you betting on prevention or cleanup?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #IntentBased #CryptoInnovation
💎
2
1
68

·
--
$NEWT IS REWRITING DEFI SECURITY WITH PRE-TRANSACTION ENFORCEMENT 🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
$NEWT IS REWRITING DEFI SECURITY WITH PRE-TRANSACTION ENFORCEMENT 🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
Entry: Not provided
Most security tools start work after funds are gone. Newton Mainnet Beta flips that — it validates every transaction against active policies (OFAC compliance, identity, real-time threat blocking, oracle health) before a single coin moves. Magic Labs, the team behind embedded wallets, already uses it to shift from wallet security to transaction authorization. This is infrastructure, not airdrop hype.
DeFi has never had a layer that enforces rules before execution, on-chain, cross-chain. Are you building something that could benefit from a policy engine that acts before the damage is done?
Not financial advice. Always manage your risk.
#NEWT #DeFiSecurity #Infrastructure #Web3
🔥
2
33
·
--
Thetanuts exploit update puts $ETH security flows in focus 🛡️
Folks, Thetanuts Finance is suspected to have faced an attack with early losses estimated near $2.1 million. The cleaner detail is that around $2 million in options tokens were reportedly recovered through a white-hat route, which softens the hit but does not erase the risk signal.
The key takeaway is simple: DeFi security remains the real battleground while everyone chases candles. Until an official recap or vulnerability report lands, smart money stays patient, avoids panic narratives, and watches whether confidence returns or weak hands get shaken out.
Not financial advice. Manage your risk.
#ETH #DeFiSecurity #CryptoNews #RiskManagement
🫡
Thetanuts exploit update puts $ETH security flows in focus 🛡️
Folks, Thetanuts Finance is suspected to have faced an attack with early losses estimated near $2.1 million. The cleaner detail is that around $2 million in options tokens were reportedly recovered through a white-hat route, which softens the hit but does not erase the risk signal.
The key takeaway is simple: DeFi security remains the real battleground while everyone chases candles. Until an official recap or vulnerability report lands, smart money stays patient, avoids panic narratives, and watches whether confidence returns or weak hands get shaken out.
Not financial advice. Manage your risk.
#ETH #DeFiSecurity #CryptoNews #RiskManagement
🫡
Folks, Thetanuts Finance is suspected to have faced an attack with early losses estimated near $2.1 million. The cleaner detail is that around $2 million in options tokens were reportedly recovered through a white-hat route, which softens the hit but does not erase the risk signal.
The key takeaway is simple: DeFi security remains the real battleground while everyone chases candles. Until an official recap or vulnerability report lands, smart money stays patient, avoids panic narratives, and watches whether confidence returns or weak hands get shaken out.
Not financial advice. Manage your risk.
#ETH #DeFiSecurity #CryptoNews #RiskManagement
🫡
17

XRP Ledger Says "No Flash Loans Here"
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
XRP Ledger Says "No Flash Loans Here"
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
A new XRPL Upgrade proposal includes a blunt note: flash loan attacks can't happen on XRP Ledger because transactions can't chain multiple actions together. One transaction, one action. Done.
Ethereum DeFi has lost billions to flash loan exploits. XRPL's design kills that attack vector outright. The catch is you also lose flash loans for arbitrage and quick liquidations. With over $3B n tokenized assets already on XRPL, some teams are betting security beats speed.
Banks are stepping in, geopolitics is heating up, betting markets are exploding, and blockchains are making hard design choices. Intitutions want safety. Traders want options. Builders are picking sides.
#XRPledger #XRP #Flashloans #DeFiSecurity #AMM
149
Verified
🚨 BREAKING !!!
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
🚨 BREAKING !!!
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
NORTH KOREAN HACKER LAUNDERED A WHOPPING $220 MILLION FROM KELP DAO HACK — RECOVERY WINDOW NEARLY CLOSED 💀
On-chain data confirms the hacker group TraderTraitor (linked to North Korea) has laundered almost the entire $220 million through high-security channels like THORChain, Wasabi, Tornado Cash, and Umbra 🛠
Only about $1.7 million remains in the hacker's original wallet — most of the transaction trails have been wiped clean, making the chances of tracing and recovering the assets nearly zero 📊
This is one of the most organized crypto laundering operations to date, showcasing the increasingly sophisticated technical capabilities of state-sponsored hacker groups ⚠️
$220 million has vanished completely. This incident again raises questions about the limits of on-chain tracing tools when faced with mixers and intentional cross-chain bridges.
#CryptoHack #DeFiSecurity
$ETH $BTC $LAB
598

·
--
"Sandwich bot drama and the importance of reading receipts, folks. The infamous Jaredfromsubway.eth got got for a cool $7.5 million in a rather ironic exploit, as an attacker tricked him into approving fake trading routes using Blockaid (1). Essentially, the attacker used Jared's own approvals to drain his WETH, USDC and USDT holdings (2). Guess you could say this is a recipe for disaster - a sandwich of trust and greed, if you will (3). What's your go-to protocol for verifying trading routes in this wild west of DeFi? Stay vigilant, squad!" #EthereumExploit #DeFiSecurity #MemeLordAlert
"Sandwich bot drama and the importance of reading receipts, folks. The infamous Jaredfromsubway.eth got got for a cool $7.5 million in a rather ironic exploit, as an attacker tricked him into approving fake trading routes using Blockaid (1). Essentially, the attacker used Jared's own approvals to drain his WETH, USDC and USDT holdings (2). Guess you could say this is a recipe for disaster - a sandwich of trust and greed, if you will (3). What's your go-to protocol for verifying trading routes in this wild west of DeFi? Stay vigilant, squad!" #EthereumExploit #DeFiSecurity #MemeLordAlert
17
·
--
EXPLOSION
A new breed of hackers has obliterated the traditional notion of rug pulls, using $VLAD to launch a token that pays them fees forever. Experts warn this is a historic shift in how scammers approach cryptocurrency, making it easier for them to reap rewards without ever taking the heat (via crypto.news).
With this new scheme, the rug pull just became a yield product, leaving many to wonder if this is the future of cryptocurrency hacking (via crypto.news). #CryptoPiracy #RugPullV2 #DeFiSecurity
As the flood has started to pour in, it's time to take a step back and evaluate what this means for the market. Will this newfound strategy of exploiting tokens for perpetual fees give scammers an upper hand, or will exchanges like Binance step up to take control?
Get ready to dive into this story and learn more about the game-changing world of cryptocurrency scams. Where will it end? What will you do next?
EXPLOSION
A new breed of hackers has obliterated the traditional notion of rug pulls, using $VLAD to launch a token that pays them fees forever. Experts warn this is a historic shift in how scammers approach cryptocurrency, making it easier for them to reap rewards without ever taking the heat (via crypto.news).
With this new scheme, the rug pull just became a yield product, leaving many to wonder if this is the future of cryptocurrency hacking (via crypto.news). #CryptoPiracy #RugPullV2 #DeFiSecurity
As the flood has started to pour in, it's time to take a step back and evaluate what this means for the market. Will this newfound strategy of exploiting tokens for perpetual fees give scammers an upper hand, or will exchanges like Binance step up to take control?
Get ready to dive into this story and learn more about the game-changing world of cryptocurrency scams. Where will it end? What will you do next?
A new breed of hackers has obliterated the traditional notion of rug pulls, using $VLAD to launch a token that pays them fees forever. Experts warn this is a historic shift in how scammers approach cryptocurrency, making it easier for them to reap rewards without ever taking the heat (via crypto.news).
With this new scheme, the rug pull just became a yield product, leaving many to wonder if this is the future of cryptocurrency hacking (via crypto.news). #CryptoPiracy #RugPullV2 #DeFiSecurity
As the flood has started to pour in, it's time to take a step back and evaluate what this means for the market. Will this newfound strategy of exploiting tokens for perpetual fees give scammers an upper hand, or will exchanges like Binance step up to take control?
Get ready to dive into this story and learn more about the game-changing world of cryptocurrency scams. Where will it end? What will you do next?
12
📰 Ostium Pauses Trading After Multimillion-Dollar Oracle Exploit: Security incident raises concerns about oracle integrity
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
📰 Ostium Pauses Trading After Multimillion-Dollar Oracle Exploit: Security incident raises concerns about oracle integrity
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
On July 16, 2026, Ostium pauses trading as security firms report a multimillion-dollar oracle exploit. The incident raises questions about oracle security in decentralized finance. Bitcoin $BTC trades at $64,557 as the broader market digests the news.
Oracle exploits have been a recurring challenge in DeFi, with attackers manipulating price feeds. Ethereum $ETH at $1,917 hosts many protocols that rely on oracle infrastructure.
The Ostium incident highlights the need for robust oracle designs, including decentralized data sources and manipulation-resistant price feeds.
📌 Key Takeaway:
Ostium oracle exploit pause underscores DeFi security challenges. Robust oracle design remains critical for protocol safety.
#DeFiSecurity #OracleExploit
#BinanceAlphaAlert
35
⚖️ DeFi Security in Focus After Ostium Oracle Exploit Pauses Trading: Oracles remain critical vulnerability in decentralized finance
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
⚖️ DeFi Security in Focus After Ostium Oracle Exploit Pauses Trading: Oracles remain critical vulnerability in decentralized finance
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
On July 16, 2026, security firms report a multimillion-dollar oracle exploit at Ostium, forcing the protocol to pause trading. The incident underscores persistent security challenges in DeFi. Bitcoin $BTC trades at $64,557 as the market assesses implications.
Oracle manipulation has been a recurring attack vector in DeFi. Ethereum $ETH at $1,917 hosts the majority of DeFi protocols and could see increased focus on oracle security solutions.
The Ostium exploit joins a list of high-profile oracle attacks, emphasizing the need for robust, decentralized data infrastructure.
📌 Key Takeaway:
Ostium oracle exploit highlights persistent DeFi security challenges. Oracle integrity remains critical for protocol safety and user trust.
#DeFiSecurity #Oracles
#BinanceAlphaAlert
32
·
--
Article
Delayed but Not DerailedMost traders are fixated on decentralized finance (DeFi) growth, but savvy observers know that security measures are equally, if not more, crucial.
In the world of DeFi, security breaches can be the kiss of death for both users and projects alike. A recent incident serves as a timely reminder: DefiLlama's delayed mobile launch is a testament to the ever-present threat of phishing scams. DefiLlama's founder revealed that an Apple Store app impersonating their brand managed to drain funds from a small crypto wallet before being removed within days.
Here are the details: #DeFiSecurity #PhishingAttack #CryptoScams
The Signal: An in-depth examination of on-chain data reveals that the incident highlighted several issues – a lax vetting process on Apple's part, poor user vigilance, and a lack of awareness about the risks associated with mobile apps in the DeFi sphere.
The Interpretation: This security breach may seem like a localized issue, but consider the ripple effects on trust and confidence within the DeFi ecosystem. It's essential to remember that security is not a one-time event but an ongoing process requiring constant vigilance – both from developers and users.
The Watch List: Monitor DefiLlama's and other prominent DeFi projects' communication channels for updates on their security measures and protocols. Specifically, keep an eye on DefiLlama's official Twitter account: twitter.com/defillama #WatchList
As we navigate this complex and ever-evolving space, the question remains: What role will security play in the next phase of DeFi growth?
Delayed but Not Derailed
Most traders are fixated on decentralized finance (DeFi) growth, but savvy observers know that security measures are equally, if not more, crucial.
In the world of DeFi, security breaches can be the kiss of death for both users and projects alike. A recent incident serves as a timely reminder: DefiLlama's delayed mobile launch is a testament to the ever-present threat of phishing scams. DefiLlama's founder revealed that an Apple Store app impersonating their brand managed to drain funds from a small crypto wallet before being removed within days.
Here are the details: #DeFiSecurity #PhishingAttack #CryptoScams
The Signal: An in-depth examination of on-chain data reveals that the incident highlighted several issues – a lax vetting process on Apple's part, poor user vigilance, and a lack of awareness about the risks associated with mobile apps in the DeFi sphere.
The Interpretation: This security breach may seem like a localized issue, but consider the ripple effects on trust and confidence within the DeFi ecosystem. It's essential to remember that security is not a one-time event but an ongoing process requiring constant vigilance – both from developers and users.
The Watch List: Monitor DefiLlama's and other prominent DeFi projects' communication channels for updates on their security measures and protocols. Specifically, keep an eye on DefiLlama's official Twitter account: twitter.com/defillama #WatchList
As we navigate this complex and ever-evolving space, the question remains: What role will security play in the next phase of DeFi growth?
In the world of DeFi, security breaches can be the kiss of death for both users and projects alike. A recent incident serves as a timely reminder: DefiLlama's delayed mobile launch is a testament to the ever-present threat of phishing scams. DefiLlama's founder revealed that an Apple Store app impersonating their brand managed to drain funds from a small crypto wallet before being removed within days.
Here are the details: #DeFiSecurity #PhishingAttack #CryptoScams
The Signal: An in-depth examination of on-chain data reveals that the incident highlighted several issues – a lax vetting process on Apple's part, poor user vigilance, and a lack of awareness about the risks associated with mobile apps in the DeFi sphere.
The Interpretation: This security breach may seem like a localized issue, but consider the ripple effects on trust and confidence within the DeFi ecosystem. It's essential to remember that security is not a one-time event but an ongoing process requiring constant vigilance – both from developers and users.
The Watch List: Monitor DefiLlama's and other prominent DeFi projects' communication channels for updates on their security measures and protocols. Specifically, keep an eye on DefiLlama's official Twitter account: twitter.com/defillama #WatchList
As we navigate this complex and ever-evolving space, the question remains: What role will security play in the next phase of DeFi growth?
51
·
--
SAND token allegedly suffered an infinite minting exploit attack: within 180 seconds, the price plunged 5.09% to $0.0433. OI shrank by 17.3% in 5 minutes ($341K → $282K), leading to large-scale liquidations of long positions.
This is the second similar incident within two weeks. On August 14, the Harmony chain minted 3 billion ONE due to a cross-shard receipt replay vulnerability. The team issued an emergency patch within 6 hours. Details of SAND’s situation have not been officially confirmed yet, but the on-chain behavioral pattern (abnormal minting in a short time + sudden price crash + sharp OI drop) closely resembles the Harmony incident.
Looking at the two events together, what they reveal is not just a single project’s code-quality issue, but a category of systemic risk: established Layer1 / metaverse projects significantly cut security auditing budgets during the 2024–2025 bear market, and contract upgrade frequency declined—while attackers’ tooling and automated scanning capabilities improved markedly over the same period. The “gap” between security investment and attack cost is widening.
Operationally: SAND’s liquidity is currently extremely thin (OI is only around $282K). Any leveraged trade in either direction is basically handing out liquidation tickets. If you hold SAND spot, watch the official post-incident report—if it’s confirmed to be a permission-level vulnerability (not a protocol-logic flaw), then the attack surface is controllable and the token’s economics model has not been fundamentally broken after the fix; if it’s a protocol-layer logic defect, you’ll need to reassess your position.
Another signal worth recording: Jim Cramer publicly called this week to “go buy Bitcoin.” As one of Wall Street’s best-known contrarian indicators, you can judge the pricing implications of this message yourself. But the objective data is—BTC has been ranging in the $95K–$100K band for more than two weeks, with persistent net outflows from on-chain whales and a lack of new catalysts in the short term to break the stalemate. I won’t comment on the historical win rate of Cramer’s calls, but the timing window is at the end of the consolidation phase, which at least suggests retail sentiment is shifting from waiting to FOMO.
Direction: Expect continued chop in the short term—don’t chase longs or shorts. Wait until the SAND incident is categorized definitively and the BTC weekly close clarifies direction before taking action.
#BTC #Crypto #SAND #DeFiSecurity
SAND token allegedly suffered an infinite minting exploit attack: within 180 seconds, the price plunged 5.09% to $0.0433. OI shrank by 17.3% in 5 minutes ($341K → $282K), leading to large-scale liquidations of long positions.
This is the second similar incident within two weeks. On August 14, the Harmony chain minted 3 billion ONE due to a cross-shard receipt replay vulnerability. The team issued an emergency patch within 6 hours. Details of SAND’s situation have not been officially confirmed yet, but the on-chain behavioral pattern (abnormal minting in a short time + sudden price crash + sharp OI drop) closely resembles the Harmony incident.
Looking at the two events together, what they reveal is not just a single project’s code-quality issue, but a category of systemic risk: established Layer1 / metaverse projects significantly cut security auditing budgets during the 2024–2025 bear market, and contract upgrade frequency declined—while attackers’ tooling and automated scanning capabilities improved markedly over the same period. The “gap” between security investment and attack cost is widening.
Operationally: SAND’s liquidity is currently extremely thin (OI is only around $282K). Any leveraged trade in either direction is basically handing out liquidation tickets. If you hold SAND spot, watch the official post-incident report—if it’s confirmed to be a permission-level vulnerability (not a protocol-logic flaw), then the attack surface is controllable and the token’s economics model has not been fundamentally broken after the fix; if it’s a protocol-layer logic defect, you’ll need to reassess your position.
Another signal worth recording: Jim Cramer publicly called this week to “go buy Bitcoin.” As one of Wall Street’s best-known contrarian indicators, you can judge the pricing implications of this message yourself. But the objective data is—BTC has been ranging in the $95K–$100K band for more than two weeks, with persistent net outflows from on-chain whales and a lack of new catalysts in the short term to break the stalemate. I won’t comment on the historical win rate of Cramer’s calls, but the timing window is at the end of the consolidation phase, which at least suggests retail sentiment is shifting from waiting to FOMO.
Direction: Expect continued chop in the short term—don’t chase longs or shorts. Wait until the SAND incident is categorized definitively and the BTC weekly close clarifies direction before taking action.
#BTC #Crypto #SAND #DeFiSecurity
This is the second similar incident within two weeks. On August 14, the Harmony chain minted 3 billion ONE due to a cross-shard receipt replay vulnerability. The team issued an emergency patch within 6 hours. Details of SAND’s situation have not been officially confirmed yet, but the on-chain behavioral pattern (abnormal minting in a short time + sudden price crash + sharp OI drop) closely resembles the Harmony incident.
Looking at the two events together, what they reveal is not just a single project’s code-quality issue, but a category of systemic risk: established Layer1 / metaverse projects significantly cut security auditing budgets during the 2024–2025 bear market, and contract upgrade frequency declined—while attackers’ tooling and automated scanning capabilities improved markedly over the same period. The “gap” between security investment and attack cost is widening.
Operationally: SAND’s liquidity is currently extremely thin (OI is only around $282K). Any leveraged trade in either direction is basically handing out liquidation tickets. If you hold SAND spot, watch the official post-incident report—if it’s confirmed to be a permission-level vulnerability (not a protocol-logic flaw), then the attack surface is controllable and the token’s economics model has not been fundamentally broken after the fix; if it’s a protocol-layer logic defect, you’ll need to reassess your position.
Another signal worth recording: Jim Cramer publicly called this week to “go buy Bitcoin.” As one of Wall Street’s best-known contrarian indicators, you can judge the pricing implications of this message yourself. But the objective data is—BTC has been ranging in the $95K–$100K band for more than two weeks, with persistent net outflows from on-chain whales and a lack of new catalysts in the short term to break the stalemate. I won’t comment on the historical win rate of Cramer’s calls, but the timing window is at the end of the consolidation phase, which at least suggests retail sentiment is shifting from waiting to FOMO.
Direction: Expect continued chop in the short term—don’t chase longs or shorts. Wait until the SAND incident is categorized definitively and the BTC weekly close clarifies direction before taking action.
#BTC #Crypto #SAND #DeFiSecurity
3
486
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BTCRebounds80K
25,412 views
517 Discussing
2
#Binance98PercentReplenished
22,936 views
460 Discussing
3
#USMidterms-WhatAreMarketsExpecting?
289,846 views
1,943 Discussing
4
#USOctoberNFP-AreRateCutsStillPossible
368,265 views
2,756 Discussing
5
#AMDBeatsExpectations-AINarrativeContinues
83,154 views
740 Discussing
6
#CircleQ3Revenue865M
22,247 views
414 Discussing
7
#BinanceIncidentReport
491,420 views
2,075 Discussing
8
#USStocksOpenHigherAsDowGains1.9%
3,150 views
66 Discussing
9
#ADPUSPrivateEmployersAdd86000JobsInOctober
2,536 views
45 Discussing
10
#FrenchAssemblyPassesSelfCustodiedCryptoReportingAmendment
761 views
21 Discussing