

#walletsecurity
walletsecurity
170,141 නැරඹීම්
407 සාකච්ඡා කරමින්
උණුසුම්
නවතම

·
--
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
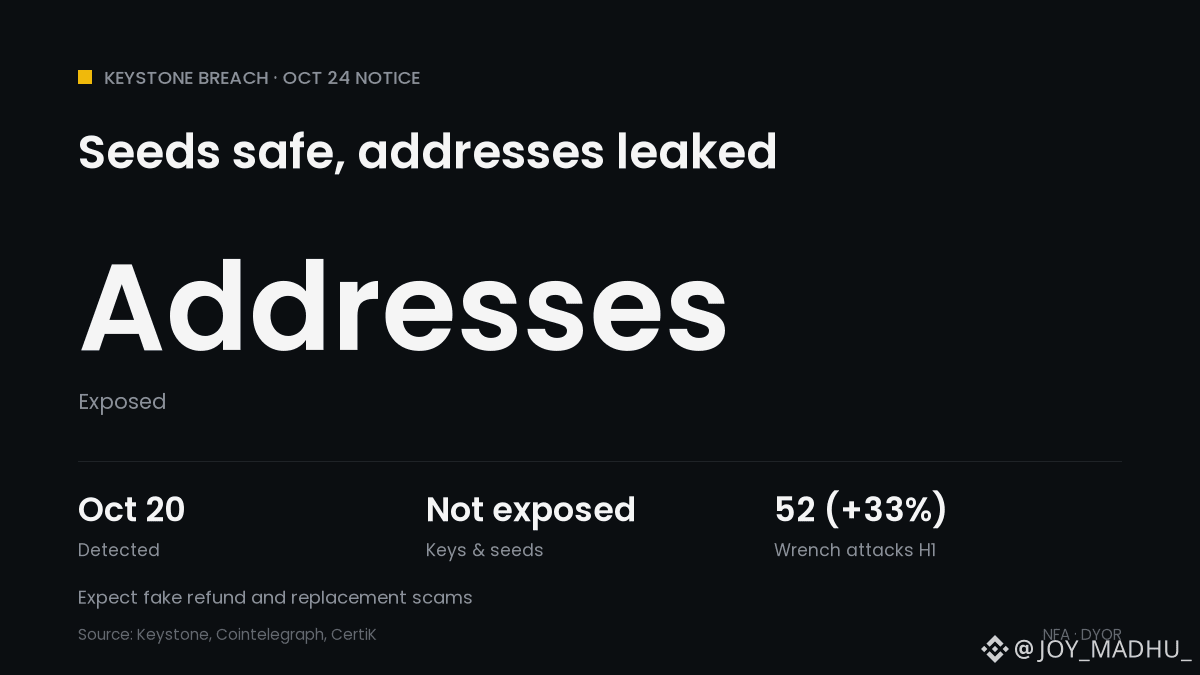
📦 Keystone Leak: Your Seed Is Safe, Your Address Isn't
📅 Oct 20: unauthorized access to Keystone's Shopify store detected
🔍 Oct 23: confirmed a third party took customer shipping data
📄 Exposed: names, contacts, addresses, order items and prices
✅ Not exposed: recovery phrases, private keys, wallet passwords, payment data
⚠️ Some buyers from 2024 got notices, despite a 180-day deletion policy
📞 Users already report scam calls citing old orders
📊 CertiK counted 52 wrench attacks in H1 2026, up 33% year on year
What it means for crypto: no funds lost and $BTC security isn't the issue, but a leaked buyer list marks people as likely holders. Keystone will never ask for your seed.
Would you buy a hardware wallet under a PO box or alias address? 👇
$BTC
#KeystoneWebsiteBreachExposesBuyersShippingAddresses #CryptoNews #WalletSecurity #Bitcoin
31
·
--
#ElectrumWalletBugLetRogueServersStealFunds
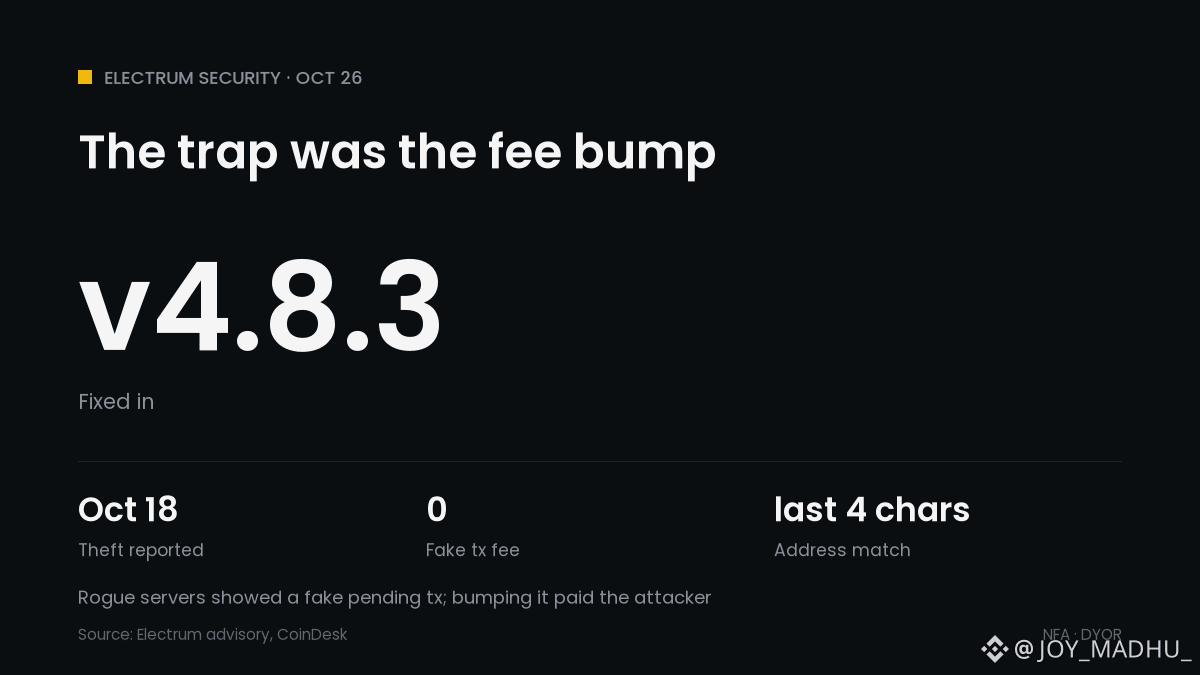
🪤 The Electrum Trap Was Hidden in the "Speed Up" Button
📅 Oct 11: first report. A multisig user verified on two Trezors, then saw a different tx in history
💸 Oct 18: a second user raised the fee on a fake pending tx and lost funds
🕵️ The rogue server held the real tx and showed a zero-fee fake, so it looked stuck
🔤 The attacker's address matched the last 4 characters of the real one
🛡️ Oct 24: Electrum 4.8.3 now checks signatures on pending txs spending your coins
⚠️ Incoming pending txs still aren't validated. Self-run servers were not exposed
What it means for crypto: no flaw in $BTC itself, but a hardware wallet can't protect a fee bump you approve without rechecking. BTC is near $80.2K.
Do you recheck the full address before every fee bump? 👇
$BTC
#ElectrumWalletBugLetRogueServersStealFunds #CryptoNews #Bitcoin #WalletSecurity
43

·
--
管理加密资产,安全不能只靠一个钱包。
🔐 离线保管助记词,不泄露私钥。
🔍 连接应用前,核实网址与项目。
⚠️ 签署交易前,认真检查授权范围。
💻 定期更新设备,检查账户活动。
🛡️ 根据自身需求分散风险,避免把所有资产暴露在同一个风险点上。
Web3 的安全没有一劳永逸的答案。真正重要的,是把每一次谨慎都变成习惯。
#ONEA #Web3 #WalletSecurity
管理加密资产,安全不能只靠一个钱包。
🔐 离线保管助记词,不泄露私钥。
🔍 连接应用前,核实网址与项目。
⚠️ 签署交易前,认真检查授权范围。
💻 定期更新设备,检查账户活动。
🛡️ 根据自身需求分散风险,避免把所有资产暴露在同一个风险点上。
Web3 的安全没有一劳永逸的答案。真正重要的,是把每一次谨慎都变成习惯。
#ONEA #Web3 #WalletSecurity
🔐 离线保管助记词,不泄露私钥。
🔍 连接应用前,核实网址与项目。
⚠️ 签署交易前,认真检查授权范围。
💻 定期更新设备,检查账户活动。
🛡️ 根据自身需求分散风险,避免把所有资产暴露在同一个风险点上。
Web3 的安全没有一劳永逸的答案。真正重要的,是把每一次谨慎都变成习惯。
#ONEA #Web3 #WalletSecurity
2
34
·
--
钱包安全,不只是保管好助记词。
恶意授权、危险签名、钓鱼网站、设备感染和社交工程,都可能成为数字资产的风险入口。
每次连接应用或确认签名之前,先问自己三个问题:
🔐 我正在授权谁?
🔍 这次操作会赋予什么权限?
⚠️ 如果判断错误,我可能失去什么?
在 Web3 世界里,真正的安全来自每一次谨慎的选择。
#ONEA #Web3 #WalletSecurity
钱包安全,不只是保管好助记词。
恶意授权、危险签名、钓鱼网站、设备感染和社交工程,都可能成为数字资产的风险入口。
每次连接应用或确认签名之前,先问自己三个问题:
🔐 我正在授权谁?
🔍 这次操作会赋予什么权限?
⚠️ 如果判断错误,我可能失去什么?
在 Web3 世界里,真正的安全来自每一次谨慎的选择。
#ONEA #Web3 #WalletSecurity
恶意授权、危险签名、钓鱼网站、设备感染和社交工程,都可能成为数字资产的风险入口。
每次连接应用或确认签名之前,先问自己三个问题:
🔐 我正在授权谁?
🔍 这次操作会赋予什么权限?
⚠️ 如果判断错误,我可能失去什么?
在 Web3 世界里,真正的安全来自每一次谨慎的选择。
#ONEA #Web3 #WalletSecurity
1
50
·
--
#ElectrumFixesHighRiskExploitInVersionsBefore4.8.3
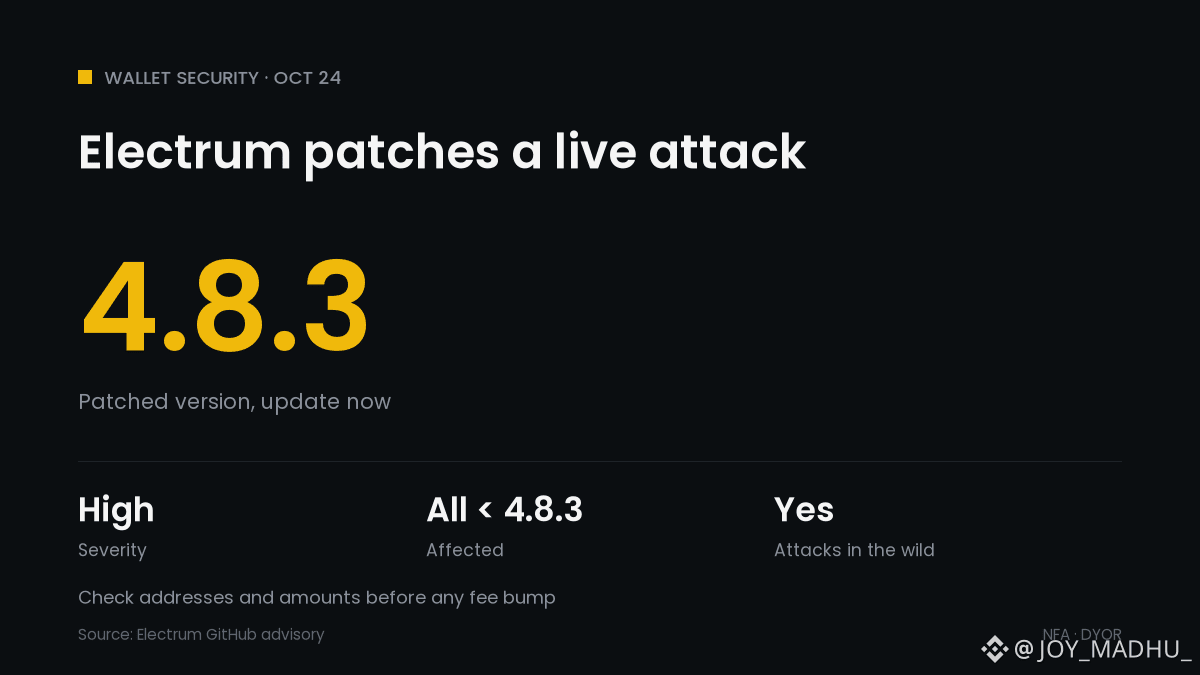
⚠️ Electrum Patches a Live Wallet Attack: Update to 4.8.3
📅 Electrum 4.8.3 shipped Oct 24 with a high-severity fix. All older versions are affected
🕵️ A malicious server hides your just-sent tx and shows a fake one paying the attacker
🔤 The fake address was ground to match the last 4 characters of the real one
💸 If you then fee-bump (RBF) that fake tx, your wallet signs a real payment to the attacker
📊 Electrum says some servers are doing this in the wild; one user lost funds
🛡️ Can't update yet? Check every address and amount before you sign. Your own trusted server isn't affected
What it means for Bitcoin: no flaw in $BTC itself, but a reminder that light wallets trust their servers. BTC is flat near $80.5K.
Do you check the full address before signing? 👇
$BTC
#ElectrumFixesHighRiskExploitInVersionsBefore4.8.3 #CryptoNews #Bitcoin #WalletSecurity
28
·
--
🔐 创建 Web3 钱包后,先别急着转账!
第一次使用钱包,建议先完成这 7 项安全检查:
1. ✅ 从官方渠道下载钱包
2. 🔑 安全备份助记词,绝不向他人泄露
3. 🛡️ 确认自己掌握的钱包控制权
4. 🔗 核对区块链网络、地址和代币合约
5. ✍️ 看懂签名请求,再点击确认
6. ⚠️ 定期检查不再需要的智能合约授权
7. 💸 新地址先核实信息,再考虑小额测试
记住:钱包安全不只是保护私钥,还包括每一次签名、授权和转账。
你认为新手最容易忽略哪一步?
#ONEA #Web3 #WalletSecurity
🔐 创建 Web3 钱包后,先别急着转账!
第一次使用钱包,建议先完成这 7 项安全检查:
1. ✅ 从官方渠道下载钱包
2. 🔑 安全备份助记词,绝不向他人泄露
3. 🛡️ 确认自己掌握的钱包控制权
4. 🔗 核对区块链网络、地址和代币合约
5. ✍️ 看懂签名请求,再点击确认
6. ⚠️ 定期检查不再需要的智能合约授权
7. 💸 新地址先核实信息,再考虑小额测试
记住:钱包安全不只是保护私钥,还包括每一次签名、授权和转账。
你认为新手最容易忽略哪一步?
#ONEA #Web3 #WalletSecurity
第一次使用钱包,建议先完成这 7 项安全检查:
1. ✅ 从官方渠道下载钱包
2. 🔑 安全备份助记词,绝不向他人泄露
3. 🛡️ 确认自己掌握的钱包控制权
4. 🔗 核对区块链网络、地址和代币合约
5. ✍️ 看懂签名请求,再点击确认
6. ⚠️ 定期检查不再需要的智能合约授权
7. 💸 新地址先核实信息,再考虑小额测试
记住:钱包安全不只是保护私钥,还包括每一次签名、授权和转账。
你认为新手最容易忽略哪一步?
#ONEA #Web3 #WalletSecurity

·
--
බෙයාරිෂ්
🚨 DELETING YOUR WALLET WON'T SAVE YOU IF THE PRIVATE KEY IS ALREADY STOLEN
Polkadot has issued an urgent warning about Fearless Wallet's browser extension
And the most dangerous part isn't the reported 17,286 DOT loss.
It's the false sense of security
$DOT
{future}(DOTUSDT)
Four extension versions contained code that leaked private keys when users unlocked their wallets
So far, 8 users have reported unauthorized transactions
But here's the critical distinction:
Changing apps doesn't change who controls your keys
If an attacker already has your seed, reinstalling the wallet or changing its password won't protect your funds
{spot}(DOTUSDT)
⚠️ Used Fearless's browser extension since February 2025?
• Create a NEW keypair in another trusted wallet
• Move accessible funds without reopening the compromised extension
• Check every chain where you reused those keys.
• For locked or staked assets, follow Polkadot's official recovery guidance
$ZEC
{future}(ZECUSDT)
The reviewed mobile apps didn't contain the malicious code — but a seed previously used in the browser extension is still compromised
Your wallet isn't secure because the app looks safe
It's secure only if your keys remain yours alone
#Polkadot #WalletSecurity #CryptoSecurity
🚨 DELETING YOUR WALLET WON'T SAVE YOU IF THE PRIVATE KEY IS ALREADY STOLEN
Polkadot has issued an urgent warning about Fearless Wallet's browser extension
And the most dangerous part isn't the reported 17,286 DOT loss.
It's the false sense of security
$DOT
Four extension versions contained code that leaked private keys when users unlocked their wallets
So far, 8 users have reported unauthorized transactions
But here's the critical distinction:
Changing apps doesn't change who controls your keys
If an attacker already has your seed, reinstalling the wallet or changing its password won't protect your funds
⚠️ Used Fearless's browser extension since February 2025?
• Create a NEW keypair in another trusted wallet
• Move accessible funds without reopening the compromised extension
• Check every chain where you reused those keys.
• For locked or staked assets, follow Polkadot's official recovery guidance
$ZEC
The reviewed mobile apps didn't contain the malicious code — but a seed previously used in the browser extension is still compromised
Your wallet isn't secure because the app looks safe
It's secure only if your keys remain yours alone
#Polkadot #WalletSecurity #CryptoSecurity
271
·
--
ලිපිය
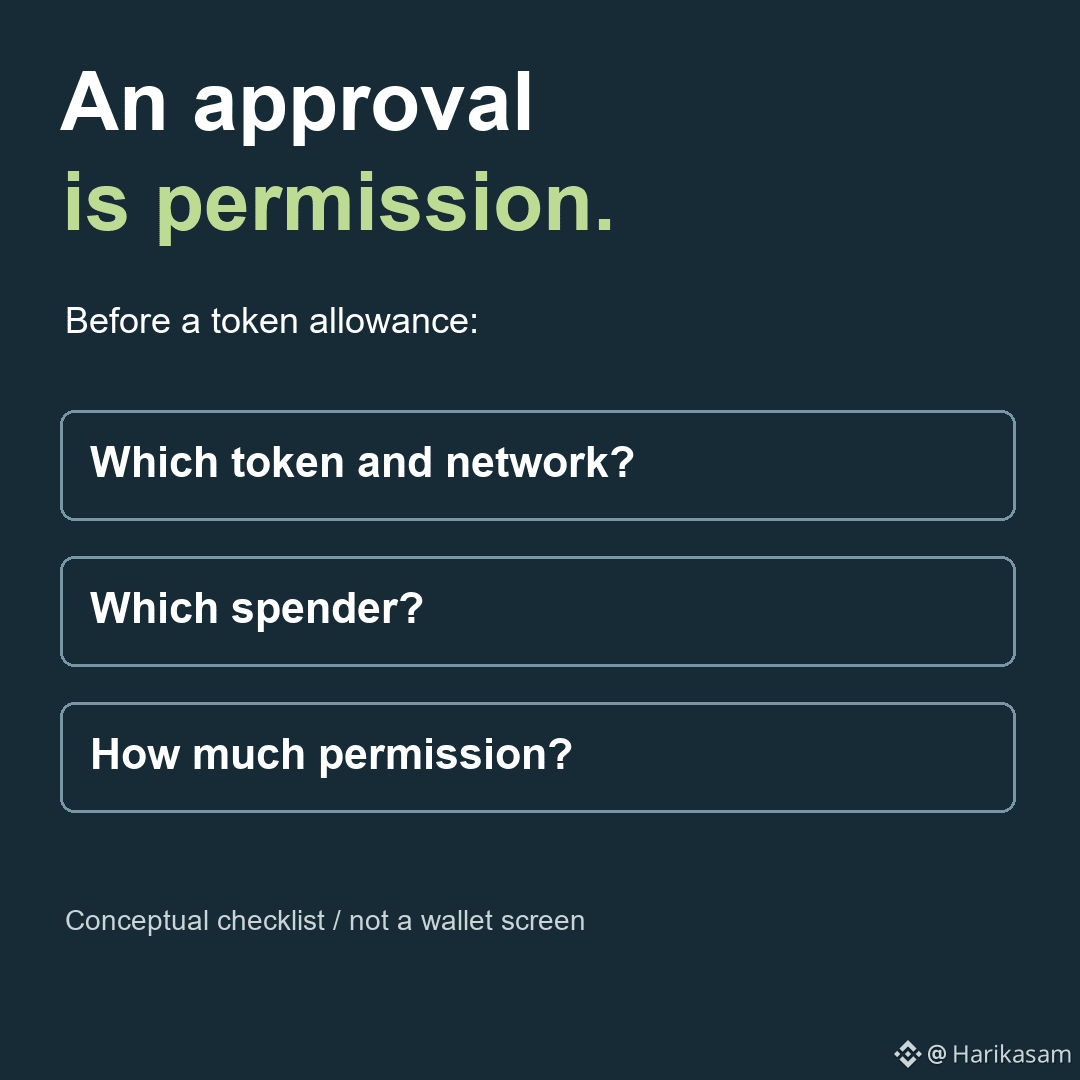
Read the permission before approving itA wallet approval is a permission decision. Read it as one.
A token allowance lets a specified contract spend tokens within that allowance. It isn't just a login step. The spender and amount should match the task you intended.
Reach the application through an independently verified address, check the domain, and read the request in your wallet. Connecting a wallet, signing a message and authorizing a transaction are different actions; they don't all grant the same authority.
For a token allowance, check the token, network, spender and limit. If the permission is broader than expected, pause and find out why. A smaller allowance can reduce that particular exposure, but it doesn't make a malicious application safe.
Never put recovery phrases or private keys into websites or support conversations. Someone with the recovery phrase may not need another approval.
Review old permissions through an independently verified tool. Revocation can require a transaction fee. It won't reverse completed transfers or repair a compromised recovery phrase.
If you can't explain what a request permits, stopping is a useful outcome.
https://ethereum.org/security/
$ETH
#WalletSecurity #TokenApprovals
Read the permission before approving it
A wallet approval is a permission decision. Read it as one.
A token allowance lets a specified contract spend tokens within that allowance. It isn't just a login step. The spender and amount should match the task you intended.
Reach the application through an independently verified address, check the domain, and read the request in your wallet. Connecting a wallet, signing a message and authorizing a transaction are different actions; they don't all grant the same authority.
For a token allowance, check the token, network, spender and limit. If the permission is broader than expected, pause and find out why. A smaller allowance can reduce that particular exposure, but it doesn't make a malicious application safe.
Never put recovery phrases or private keys into websites or support conversations. Someone with the recovery phrase may not need another approval.
Review old permissions through an independently verified tool. Revocation can require a transaction fee. It won't reverse completed transfers or repair a compromised recovery phrase.
If you can't explain what a request permits, stopping is a useful outcome.
https://ethereum.org/security/
$ETH
#WalletSecurity #TokenApprovals
4
·
--
#PolkadotFoundationWarnsFearlessWalletExtensionLeakedPrivateKeys
🚨 Fearless Wallet Extension Leaked Private Keys
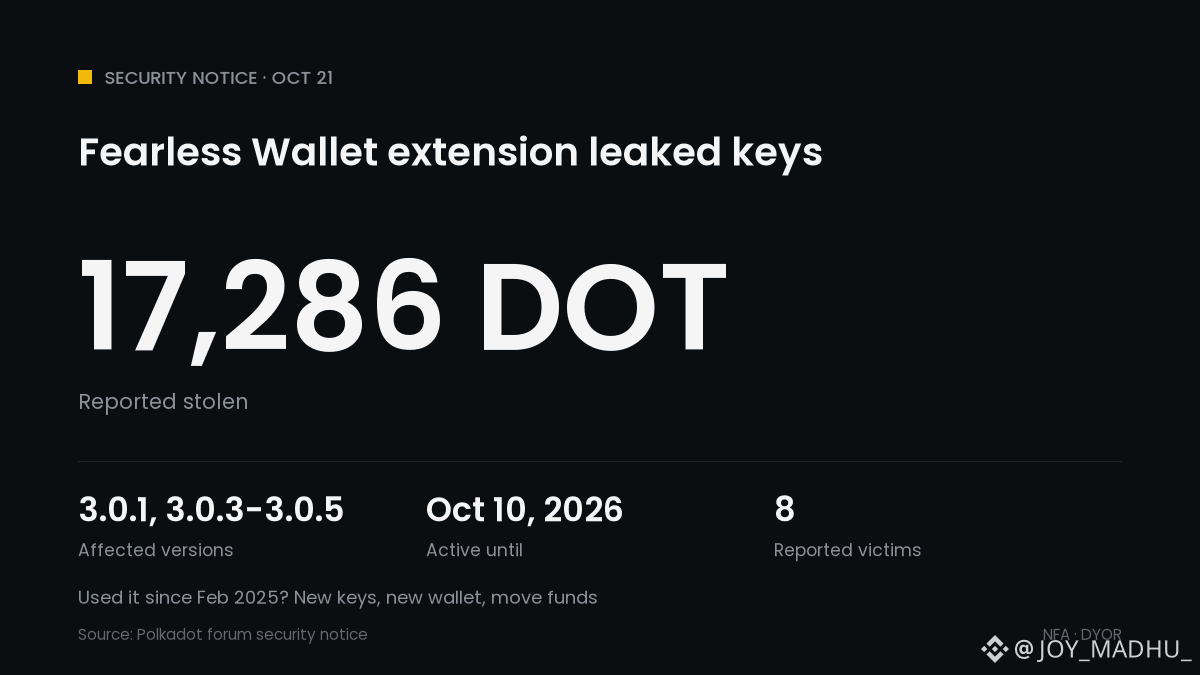
⚠️ Versions 3.0.1, 3.0.3, 3.0.4 and 3.0.5 sent keys to an attacker's server on unlock
📅 The code came in on Feb 19, 2025 and was active at times until Oct 10, 2026
📉 8 users report unauthorised transfers totalling 17,286 DOT
🔍 An affected Chrome version still showed ~6,000 users
📱 The reviewed mobile apps don't contain the code
Used the extension since Feb 2025? Make new keys in another wallet and move funds. A new password or reinstall won't help.
What it means for crypto: a wallet supply-chain attack, not a Polkadot network flaw. $DOT is near $1.18.
Checked which extensions hold your keys? 👇
$DOT
#CryptoNews #Polkadot #WalletSecurity #PolkadotFoundationWarnsFearlessWalletExtensionLeakedPrivateKeys
ABO3ZAM:
مصيبة يا خوي، أمن المحفظة أهم من أي صفقة. اللي يستخدم الإضافة يلحق يسحب أمواله قبل لا يكسر السعر دعمه الأخير ويضيع كل شيء 🤝
1
18
·
--
බෙයාරිෂ්
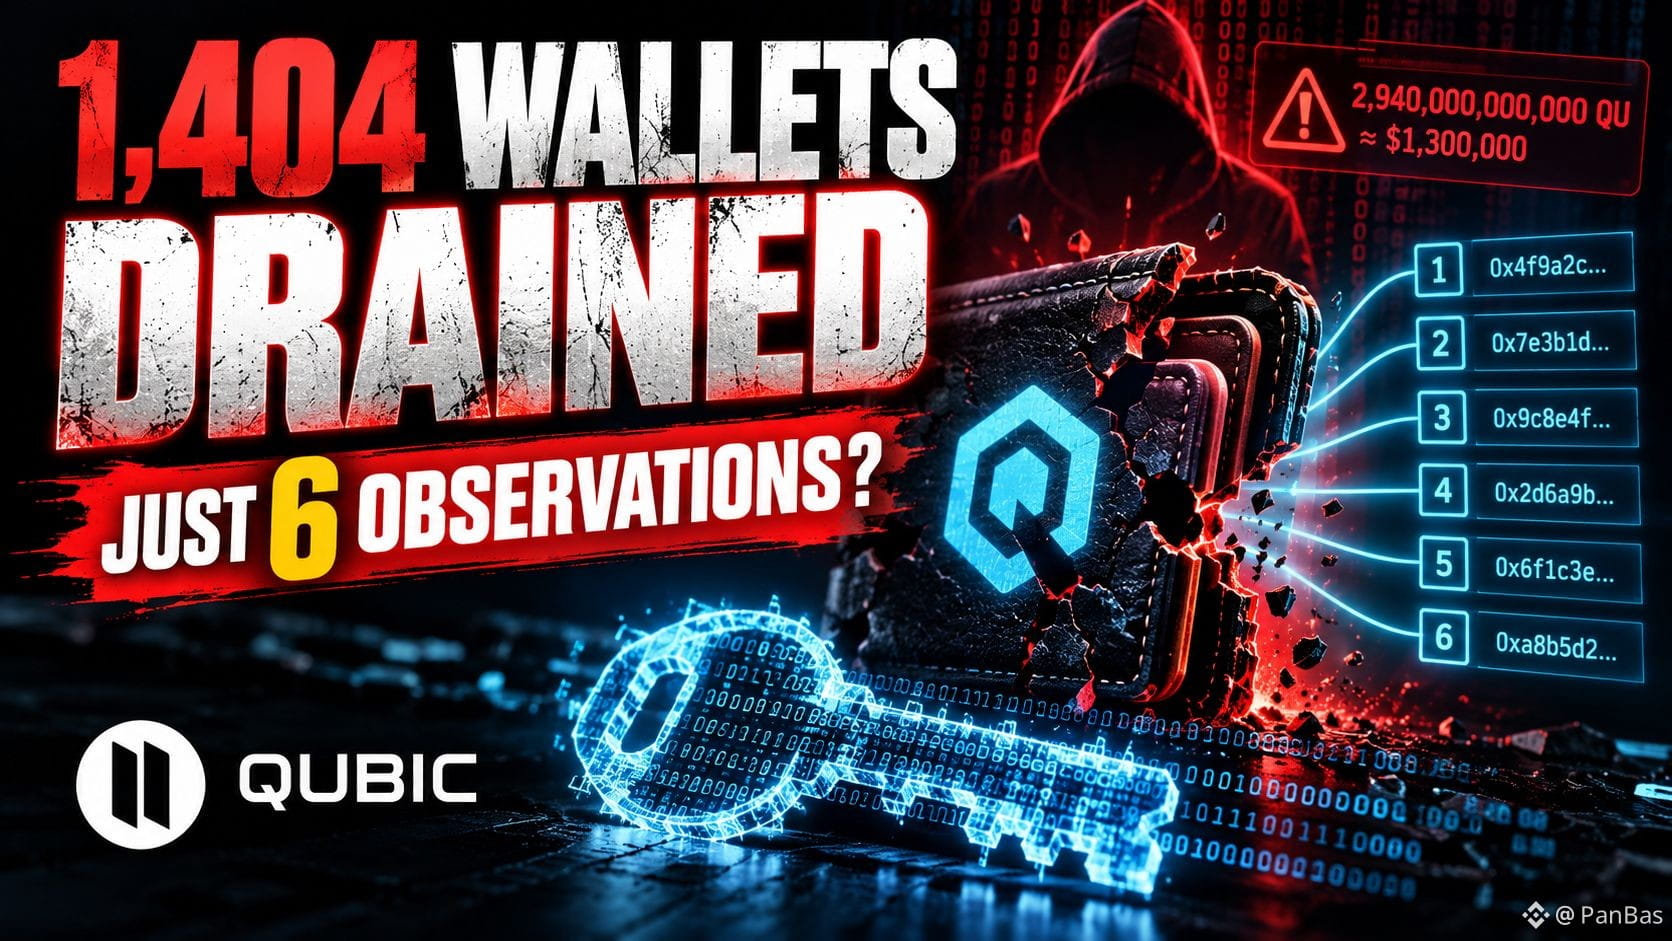
🚨 1,404 CRYPTO WALLETS DRAINED — AND JUST 6 NETWORK OBSERVATIONS COULD EXPOSE A PRIVATE KEY! 👀
Imagine securing your wallet, never sharing your seed… and still losing everything.
That's the nightmare behind the Qubic security incident.
💥 WHAT HAPPENED?
Between October 17 and 18, an attacker drained:
🔴 1,404 wallets
🔴 2.94 TRILLION QU
🔴 Approximately $1.3 MILLION
The Qubic network was halted to contain the damage.
According to the project, 87.1% of the stolen tokens were immobilized on-chain, while the remaining 12.9% reached MEXC, where the receiving account was frozen.
But the most disturbing discovery came later.
🔍 SLOWMIST'S FINDING
On October 20, security researchers revealed that Qubic's wallet used insufficiently secure randomness when generating certain private keys.
In a controlled test, researchers reconstructed a vulnerable private key using just SIX consecutive network observations under specific conditions.
⚠️ This does NOT prove the attacker used that exact method.
The issue was in wallet seed generation, not a confirmed breach of Qubic's core blockchain protocol.
🚨 WHO SHOULD PAY ATTENTION?
Users who created Qubic wallets before October 18 using:
• Any browser on iPhone or iPad
• Safari on Mac
Or the Qubic iOS app before July 2025.
Version 4.26.4 fixes NEW seed generation.
But previously generated weak seeds remain vulnerable.
💭 PANBAS TAKE:
The scariest part isn't the $1.3M theft.
It's that a wallet can look perfectly secure while its private key was predictable from the beginning.
Frozen funds aren't recovered funds.
If your wallet may be affected, follow official migration instructions. Never share your seed or trust unsolicited recovery offers.
👇 Would you trust a wallet again after discovering its keys weren't truly random?
#Qubic #WalletSecurity #CryptoExploit
7
·
--
උසබ තත්ත්වය
🚨 1,404 QUBIC WALLETS DRAINED — AND THE BLOCKCHAIN WASN'T THE WEAK POINT
Qubic just suffered a security incident involving roughly $1.4M in stolen tokens
But here's the detail that matters most 👀
The attacker didn't need to break the blockchain
Some wallet seeds were generated with insufficient randomness, making them potentially predictable
$BTC
{future}(BTCUSDT)
🔴 What happened?
• 1,404 wallets drained
• 2.94 trillion QU stolen
• Qubic network halted to prevent further transfers
• 87.1% of stolen funds frozen on-chain
• Remaining funds reportedly frozen at ME.XC
⚠️ Here's the bigger warning
Affected seeds include those created before October 18 using:
• Any browser on iPhone or iPad
• Safari on Mac
• Qubic's iOS app before July 2025
Updating wallet software doesn't make an old weak seed secure
And frozen funds aren't the same as recovered funds
$BNB
{future}(BNBUSDT)
🔍 My security checklist
If your wallet falls into an affected category, treat the seed as compromised
Follow Qubic's official recovery instructions before moving funds to a newly generated secure wallet
Never enter your seed into a random recovery website
Your blockchain can be secure while your wallet is already compromised
The real security question isn't just where your assets live
It's how the keys protecting them were created
#Qubic #WalletSecurity
🚨 1,404 QUBIC WALLETS DRAINED — AND THE BLOCKCHAIN WASN'T THE WEAK POINT
Qubic just suffered a security incident involving roughly $1.4M in stolen tokens
But here's the detail that matters most 👀
The attacker didn't need to break the blockchain
Some wallet seeds were generated with insufficient randomness, making them potentially predictable
$BTC
🔴 What happened?
• 1,404 wallets drained
• 2.94 trillion QU stolen
• Qubic network halted to prevent further transfers
• 87.1% of stolen funds frozen on-chain
• Remaining funds reportedly frozen at ME.XC
⚠️ Here's the bigger warning
Affected seeds include those created before October 18 using:
• Any browser on iPhone or iPad
• Safari on Mac
• Qubic's iOS app before July 2025
Updating wallet software doesn't make an old weak seed secure
And frozen funds aren't the same as recovered funds
$BNB
🔍 My security checklist
If your wallet falls into an affected category, treat the seed as compromised
Follow Qubic's official recovery instructions before moving funds to a newly generated secure wallet
Never enter your seed into a random recovery website
Your blockchain can be secure while your wallet is already compromised
The real security question isn't just where your assets live
It's how the keys protecting them were created
#Qubic #WalletSecurity
222

·
--
බෙයාරිෂ්
L1, який можна вимкнути кнопкою, — не дуже децентралізований. Qubic щойно це показав)
в ніч на 18 жовтня з 1404 гаманців у мережі Qubic хтось вивів близько 2.94 трлн QU. протокол при цьому ніхто не ламав
дірка в гаманці: сід-фрази робились зі слабкою випадковістю
хто створював гаманець у браузері на iPhone чи iPad, у Safari на Mac або в старому iOS-застосунку, мав сід, який можна було передбачити
шоб гроші не втекли, мережу просто зупинили. 87.1% вкраденого так і лежить у мережі, близько 12.9% тормознула MEXC
тільки заморожені тепер не лише гроші злодія, а й усіх інших
шо буде з балансами, вирішать Computors голосуванням. відкат, повернення чи шось третє — плану поки нема
і практичне: сід, який згенерував сайт, тримається рівно на коді сайту. а старий сід оновлення не рятує, гроші з нього тре переносити на новий
далі дивлюсь, шо Computors вирішать з цими 87.1%
#Qubic #WalletSecurity
162
·
--
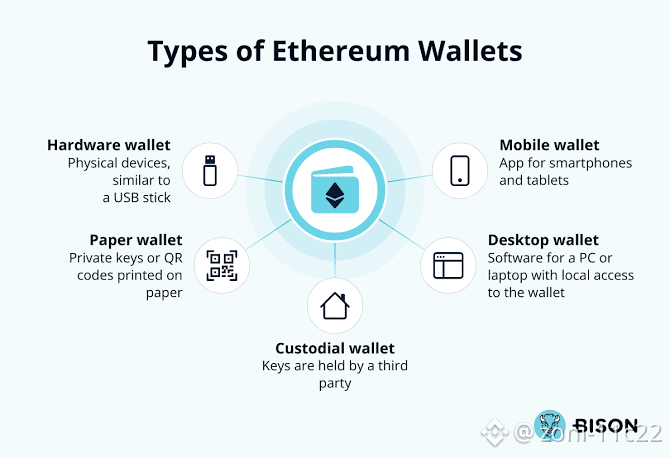
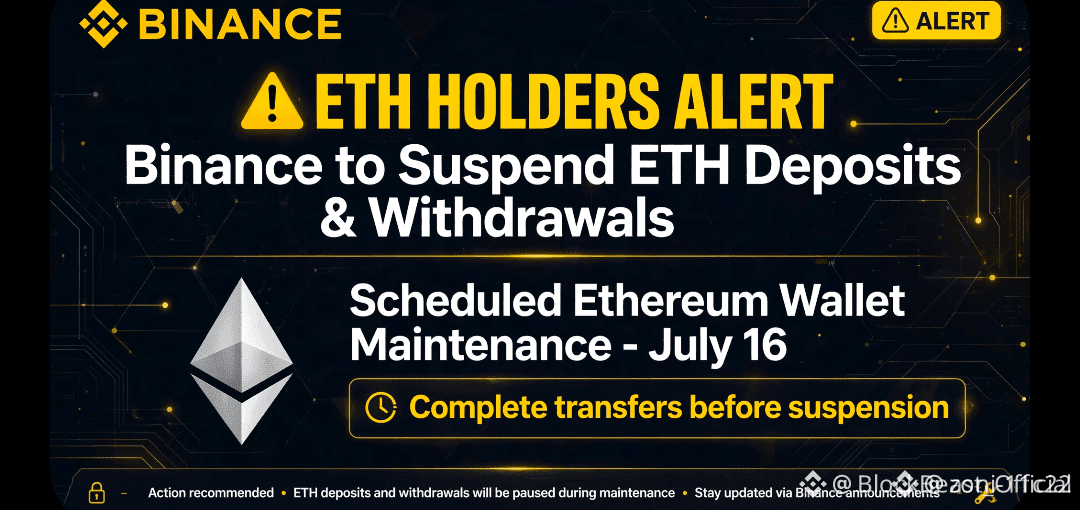
Wallet Maintenance
If you are managing your own non-custodial wallet (like MetaMask, Coinbase Wallet, or a hardware device), regular maintenance prevents funds from being drained by smart contract exploits or malware. [1, 2]
Are you seeing a "Wallet Maintenance" notice on an exchange right now, or are you looking to clean up and secure your personal Ethereum wallet?
If it's for a personal wallet, let me know if you use a hardware or software wallet so I can provide specific maintenance steps.
$TRUMP
{future}(TRUMPUSDT)
$ETC
{future}(ETCUSDT)
$AR
{future}(ARUSDT)
#WalletMaintenance
#WalletPay
#WalletSecurity
Wallet Maintenance
If you are managing your own non-custodial wallet (like MetaMask, Coinbase Wallet, or a hardware device), regular maintenance prevents funds from being drained by smart contract exploits or malware. [1, 2]
Are you seeing a "Wallet Maintenance" notice on an exchange right now, or are you looking to clean up and secure your personal Ethereum wallet?
If it's for a personal wallet, let me know if you use a hardware or software wallet so I can provide specific maintenance steps.
$TRUMP
$ETC
$AR
#WalletMaintenance
#WalletPay
#WalletSecurity
376
·
--
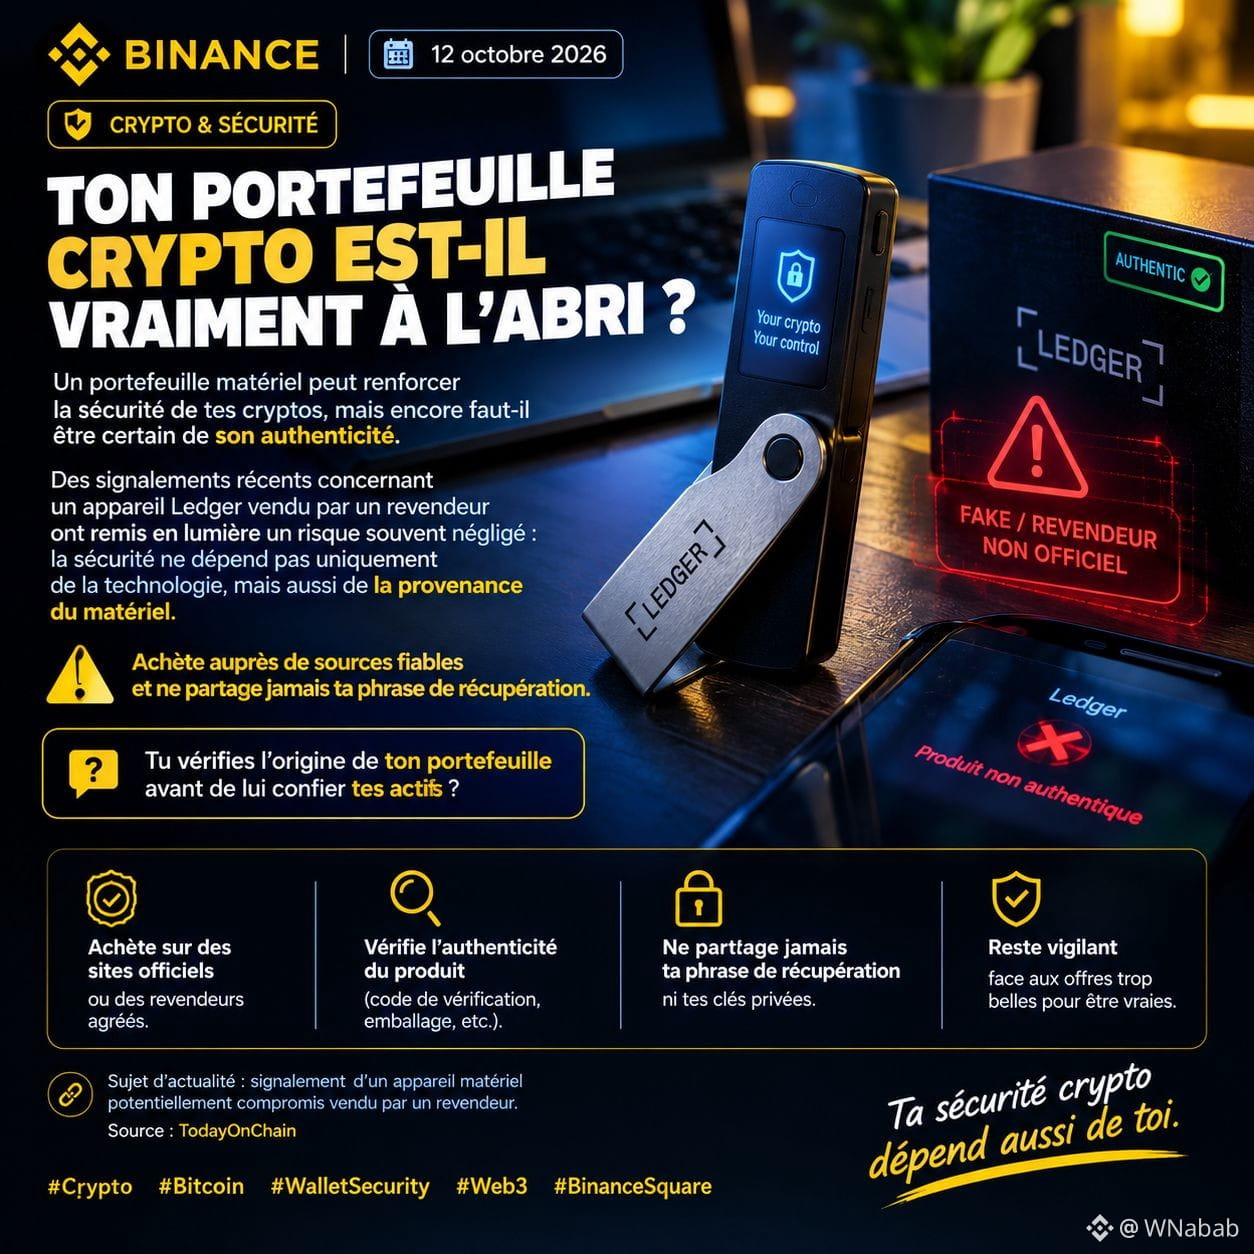
Ton portefeuille crypto est-il vraiment à l’abri ? 🔐
Un portefeuille matériel peut renforcer la sécurité de tes cryptos, mais encore faut-il être certain de son authenticité.
Des signalements récents concernant un appareil Ledger vendu par un revendeur ont remis en lumière un risque souvent négligé : la sécurité ne dépend pas uniquement de la technologie, mais aussi de la provenance du matériel.
Achète auprès de sources fiables et ne partage jamais ta phrase de récupération.
Tu vérifies l’origine de ton portefeuille avant de lui confier tes actifs ?
#WalletSecurity #Web3 #BinanceSquare
$BTC
{spot}(BTCUSDT)
Ton portefeuille crypto est-il vraiment à l’abri ? 🔐
Un portefeuille matériel peut renforcer la sécurité de tes cryptos, mais encore faut-il être certain de son authenticité.
Des signalements récents concernant un appareil Ledger vendu par un revendeur ont remis en lumière un risque souvent négligé : la sécurité ne dépend pas uniquement de la technologie, mais aussi de la provenance du matériel.
Achète auprès de sources fiables et ne partage jamais ta phrase de récupération.
Tu vérifies l’origine de ton portefeuille avant de lui confier tes actifs ?
#WalletSecurity #Web3 #BinanceSquare
$BTC
1
121

·
--
Ledger Supply-Chain Attack: 86 Million Dollars Lost and a Zcash Trail$ZEC took in stolen Ledger-linked funds worth about 7.45 million dollars.
Stolen funds from a hardware wallet supply-chain attack were bridged into $ZEC through $NEAR Intents, per KuCoin's daily report. The case is a reminder that a wallet can be compromised before you ever open the box.
📌 The news
Ledger confirmed unauthorized hardware implants in affected devices. All confirmed cases involve units sold by the Southeast Asian distributor CryptoBilis, per KuCoin and Zerocap. Reported losses are now above 86 million dollars. Ledger's own systems and direct sales channels are reportedly unaffected.
🔍 Why it matters
• Attackers allegedly used the implants to steal private keys and recovery phrases.
• Devices with intact secure elements may still pass Ledger's Genuine Check, so that test alone is not proof of safety.
• Analysts have named more than 20 potentially affected distributors, but this is not fully verified.
📊 The money trail
• About 2,990 ETH, roughly 7.45 million dollars, went to Tornado Cash.
• Funds were then bridged to ZEC through NEAR Intents.
• On Binance, ZEC trades near 1,227 dollars (-7.8% in 24h) and NEAR near 5.25 (-10.4%).
⚖️ What this does and does not prove
Not every Ledger device is at risk. The confirmed cases trace to one distributor, and KuCoin calls it premature to say otherwise. It does show that third-party resellers are a weak link, and that cross-chain routes can be used to move stolen funds.
👀 What to watch next
• Whether Ledger names more affected distributors.
• Whether more victims come forward from Europe or South America.
━━━━━━━━━━━━
💡 My take: the lesson is practical. Buy hardware wallets only from the maker, keep recovery phrases offline, and spread holdings across more than one setup. This is my view, not advice.
💬 Where did your last hardware wallet come from: official store, reseller or other?
#LedgerSupplyChain #WalletSecurity
Ledger Supply-Chain Attack: 86 Million Dollars Lost and a Zcash Trail
$ZEC took in stolen Ledger-linked funds worth about 7.45 million dollars.
Stolen funds from a hardware wallet supply-chain attack were bridged into $ZEC through $NEAR Intents, per KuCoin's daily report. The case is a reminder that a wallet can be compromised before you ever open the box.
📌 The news
Ledger confirmed unauthorized hardware implants in affected devices. All confirmed cases involve units sold by the Southeast Asian distributor CryptoBilis, per KuCoin and Zerocap. Reported losses are now above 86 million dollars. Ledger's own systems and direct sales channels are reportedly unaffected.
🔍 Why it matters
• Attackers allegedly used the implants to steal private keys and recovery phrases.
• Devices with intact secure elements may still pass Ledger's Genuine Check, so that test alone is not proof of safety.
• Analysts have named more than 20 potentially affected distributors, but this is not fully verified.
📊 The money trail
• About 2,990 ETH, roughly 7.45 million dollars, went to Tornado Cash.
• Funds were then bridged to ZEC through NEAR Intents.
• On Binance, ZEC trades near 1,227 dollars (-7.8% in 24h) and NEAR near 5.25 (-10.4%).
⚖️ What this does and does not prove
Not every Ledger device is at risk. The confirmed cases trace to one distributor, and KuCoin calls it premature to say otherwise. It does show that third-party resellers are a weak link, and that cross-chain routes can be used to move stolen funds.
👀 What to watch next
• Whether Ledger names more affected distributors.
• Whether more victims come forward from Europe or South America.
━━━━━━━━━━━━
💡 My take: the lesson is practical. Buy hardware wallets only from the maker, keep recovery phrases offline, and spread holdings across more than one setup. This is my view, not advice.
💬 Where did your last hardware wallet come from: official store, reseller or other?
#LedgerSupplyChain #WalletSecurity
18

A Malaysian man reported losing $3.05M in cryptocurrency following unauthorized wallet transfers. Local police are currently investigating the fraud to trace the movement of the stolen funds.
#WalletSecurity #CryptoFraud
A Malaysian man reported losing $3.05M in cryptocurrency following unauthorized wallet transfers. Local police are currently investigating the fraud to trace the movement of the stolen funds.
#WalletSecurity #CryptoFraud
#WalletSecurity #CryptoFraud
20
ලිපිය
The Massive Ledger Drain Is A Huge WarningThe news of a 92 million dollar drain targeting Ledger users has sent massive shockwaves through the community. This was not just a single chain attack but a coordinated multi chain event hitting Bitcoin, Ethereum, TRON, BNB Chain, and Polygon. Seeing such a large amount of capital vanish in a single strike is a brutal reminder of the constant risks we face in this space.
While Ledger is widely considered the gold standard for self custody, this event raises massive questions about how these assets were actually compromised. Whether it was a vulnerability in the device itself or a highly sophisticated phishing campaign targeting specific users, the scale of the loss is absolutely staggering. For many retail traders, this feels like a direct hit to the narrative that hardware wallets provide total immunity from theft.
If you are holding significant bags, this is your signal to review your security protocols immediately. Do not assume you are safe just because you have a hardware device. Check your smart contract permissions and stay incredibly vigilant against suspicious interactions. The market can be bullish for weeks, but security exploits like this can nuke sentiment and trust in an instant. Stay safe and keep your keys secure because the bad actors are clearly getting more efficient every single day.
#LedgerExploit #WalletSecurity
The Massive Ledger Drain Is A Huge Warning
The news of a 92 million dollar drain targeting Ledger users has sent massive shockwaves through the community. This was not just a single chain attack but a coordinated multi chain event hitting Bitcoin, Ethereum, TRON, BNB Chain, and Polygon. Seeing such a large amount of capital vanish in a single strike is a brutal reminder of the constant risks we face in this space.
While Ledger is widely considered the gold standard for self custody, this event raises massive questions about how these assets were actually compromised. Whether it was a vulnerability in the device itself or a highly sophisticated phishing campaign targeting specific users, the scale of the loss is absolutely staggering. For many retail traders, this feels like a direct hit to the narrative that hardware wallets provide total immunity from theft.
If you are holding significant bags, this is your signal to review your security protocols immediately. Do not assume you are safe just because you have a hardware device. Check your smart contract permissions and stay incredibly vigilant against suspicious interactions. The market can be bullish for weeks, but security exploits like this can nuke sentiment and trust in an instant. Stay safe and keep your keys secure because the bad actors are clearly getting more efficient every single day.
#LedgerExploit #WalletSecurity
22
Disconnecting a dApp is NOT the same as revoking its token approvals. 🔐
On Ethereum and other EVM networks, an allowance can remain active after you disconnect your wallet.
Before your next DeFi session:
• Verify the site and spender address.
• Prefer a spending cap over unlimited approval when practical.
• Review old allowances with a trusted explorer or approval tool; revoke what you no longer need.
Approvals make swaps and lending convenient, but a malicious or compromised approved spender may put approved tokens at risk. Revoking usually costs gas and cannot recover stolen funds. Never enter your seed phrase into an approval checker.
Small wallet hygiene, meaningful risk reduction.
#Ethereum #DeFi #WalletSecurity
55
·
--
Smart Wallet Recovery RiskEthereum’s account-abstraction roadmap is moving wallets toward programmable security. Recovery is one of the strongest benefits, but it also creates a new authority surface that users and builders must understand.
ERC-7947 proposes a common recovery interface for smart accounts. A supporting account can register one or more recovery providers, store provider-specific recovery commitments and later submit a proof that authorizes a change to the account’s access subject.
The flexibility is useful. One provider might verify a zero-knowledge proof. Another might use a signature, multi-factor process or another recovery method. A wallet can support several providers instead of depending on one centralized service.
But more recovery options do not automatically mean more safety. Every registered provider becomes part of the account’s control model. If a user is phished into adding a malicious provider, that provider could accept a false proof and authorize an attacker. The official ERC-7947 security section identifies this risk directly.
Proof replay is another important control. A recovery proof must not work as a reusable voucher. Providers need a changing nonce, consumed commitment or another mechanism that makes a successful proof invalid for future attempts. Adding and removing providers must also be tightly access controlled, and zero-address registration must be rejected.
ERC-7947 does not standardize one mandatory guardian threshold, recovery delay, expiry rule or proof format. Those decisions stay with wallet and provider implementations. That means users should assess the actual recovery policy, not assume that interface support alone proves security.
The proposal remains a Draft Standards Track ERC. It is a useful framework for evaluating where recovery authority lives, but it should not be described as universally deployed.
Read the full TokenToolHub analysis: https://tokentoolhub.com/erc-7947-smart-account-recovery/
#Ethereum✅ #AccountAbstraction #WalletSecurity #Web3 #CyberSecurity
Smart Wallet Recovery Risk
Ethereum’s account-abstraction roadmap is moving wallets toward programmable security. Recovery is one of the strongest benefits, but it also creates a new authority surface that users and builders must understand.
ERC-7947 proposes a common recovery interface for smart accounts. A supporting account can register one or more recovery providers, store provider-specific recovery commitments and later submit a proof that authorizes a change to the account’s access subject.
The flexibility is useful. One provider might verify a zero-knowledge proof. Another might use a signature, multi-factor process or another recovery method. A wallet can support several providers instead of depending on one centralized service.
But more recovery options do not automatically mean more safety. Every registered provider becomes part of the account’s control model. If a user is phished into adding a malicious provider, that provider could accept a false proof and authorize an attacker. The official ERC-7947 security section identifies this risk directly.
Proof replay is another important control. A recovery proof must not work as a reusable voucher. Providers need a changing nonce, consumed commitment or another mechanism that makes a successful proof invalid for future attempts. Adding and removing providers must also be tightly access controlled, and zero-address registration must be rejected.
ERC-7947 does not standardize one mandatory guardian threshold, recovery delay, expiry rule or proof format. Those decisions stay with wallet and provider implementations. That means users should assess the actual recovery policy, not assume that interface support alone proves security.
The proposal remains a Draft Standards Track ERC. It is a useful framework for evaluating where recovery authority lives, but it should not be described as universally deployed.
Read the full TokenToolHub analysis: https://tokentoolhub.com/erc-7947-smart-account-recovery/
#Ethereum✅ #AccountAbstraction #WalletSecurity #Web3 #CyberSecurity
100
·
--
One Wallet Is Too Much RiskConvenience often turns one crypto wallet into a trading account, DeFi workbench, airdrop address and long-term vault at the same time. That structure feels simple until one malicious approval, fake front end or compromised session reaches everything.
A multi-wallet strategy reduces that blast radius by assigning different activities to different wallets. The basic model is practical: one wallet for trading, one for DeFi and one for long-term holdings.
The trading wallet is built for speed. It may connect to exchanges, bridges, dashboards and execution tools, so it signs more often and faces more operational noise. It should hold working capital rather than the deepest part of a portfolio.
The DeFi wallet is the contract-interaction layer. Staking, lending, liquidity positions, vaults and governance introduce approval, front-end and smart-contract risks. Keeping only the capital needed for those activities makes exposure easier to see and contain.
The long-term wallet should be intentionally boring. Its job is preservation. It should sign rarely, connect to as few applications as possible and avoid experiments. If meaningful value is stored there, stronger signing isolation and a tested recovery process become increasingly important.
Creating several addresses is not enough. Each wallet needs one documented role, its own balance limits and rules about what it must never sign. Active wallets should be topped up intentionally. Excess capital should move back to safer storage. Approvals should be reviewed, and burner wallets should remain low value.
This structure does not remove risk. It contains it. It also makes reviews clearer because trading activity, DeFi permissions and core holdings are no longer mixed into one history.
The TokenToolHub guide provides a step-by-step model, funding rules, common failure points and a practical setup for active users.
Read the full guide on TokenToolHub: https://tokentoolhub.com/multi-wallet-strategy/
#crypto #blockchain #Web3 #WalletSecurity #defi
One Wallet Is Too Much Risk
Convenience often turns one crypto wallet into a trading account, DeFi workbench, airdrop address and long-term vault at the same time. That structure feels simple until one malicious approval, fake front end or compromised session reaches everything.
A multi-wallet strategy reduces that blast radius by assigning different activities to different wallets. The basic model is practical: one wallet for trading, one for DeFi and one for long-term holdings.
The trading wallet is built for speed. It may connect to exchanges, bridges, dashboards and execution tools, so it signs more often and faces more operational noise. It should hold working capital rather than the deepest part of a portfolio.
The DeFi wallet is the contract-interaction layer. Staking, lending, liquidity positions, vaults and governance introduce approval, front-end and smart-contract risks. Keeping only the capital needed for those activities makes exposure easier to see and contain.
The long-term wallet should be intentionally boring. Its job is preservation. It should sign rarely, connect to as few applications as possible and avoid experiments. If meaningful value is stored there, stronger signing isolation and a tested recovery process become increasingly important.
Creating several addresses is not enough. Each wallet needs one documented role, its own balance limits and rules about what it must never sign. Active wallets should be topped up intentionally. Excess capital should move back to safer storage. Approvals should be reviewed, and burner wallets should remain low value.
This structure does not remove risk. It contains it. It also makes reviews clearer because trading activity, DeFi permissions and core holdings are no longer mixed into one history.
The TokenToolHub guide provides a step-by-step model, funding rules, common failure points and a practical setup for active users.
Read the full guide on TokenToolHub: https://tokentoolhub.com/multi-wallet-strategy/
#crypto #blockchain #Web3 #WalletSecurity #defi
57
තවත් අන්තර්ගතයන් ගවේෂණය කිරීමට ඇතුල් වන්න
Binance චතුරශ්රය හි ගෝලීය ක්රිප්ටෝ පරිශීලකයින් හා එක්වන්න
⚡️ ක්රිප්ටෝ පිළිබඳ නවතම සහ ප්රයෝජනවත් තොරතුරු ලබා ගන්න.
💬 ලොව විශාලතම ක්රිප්ටෝ හුවමාරුව මගින් විශ්වාස කෙරේ.
👍 සත්යායනය කරන ලද නිර්මාණකරුවන්ගෙන් සැබෑ විදසුන් සොයා ගන්න.
විද්යුත් තැපෑල / දුරකථන අංකය
නැගී එන මාතෘකා
1
#BinancePick
3.1M නැරඹීම්
154,928 සාකච්ඡා කරමින්
2
#EarningsSeason
5.3M නැරඹීම්
26,123 සාකච්ඡා කරමින්
3
#AnthropicTTMRevenueGrewAbout1200%
38,233 නැරඹීම්
467 සාකච්ඡා කරමින්
4
#AnthropicS1ExpectedToday
31,699 නැරඹීම්
370 සාකච්ඡා කරමින්
5
#SouthKoreaReportedlyWeighsFourthCryptoTaxDelay
34,096 නැරඹීම්
504 සාකච්ඡා කරමින්
6
#FranklinTempletonFilesForTwoDividendToBitcoinETFs
45,368 නැරඹීම්
571 සාකච්ඡා කරමින්
7
#StrategyMSTRSurpassesNasdaqInMarketCap
34,938 නැරඹීම්
402 සාකච්ඡා කරමින්
8
#CanadaProposesStablecoinRedemptionWithin3BusinessDays
1,445 නැරඹීම්
37 සාකච්ඡා කරමින්
9
#ElectrumWalletBugLetRogueServersStealFunds
33,997 නැරඹීම්
484 සාකච්ඡා කරමින්
10
#ArgentineCourtDismissesLIBRACaseAgainstMilei
50,687 නැරඹීම්
608 සාකච්ඡා කරමින්