
Orin khan 5
129 Публикации

Orin khan 5
Отправить жалобу
Заблокировать пользователя
21 подписок(и/а)
1.2K+ подписчиков(а)
65 понравилось
Посты
·
--
#dusk $DUSK @Dusk_Foundation
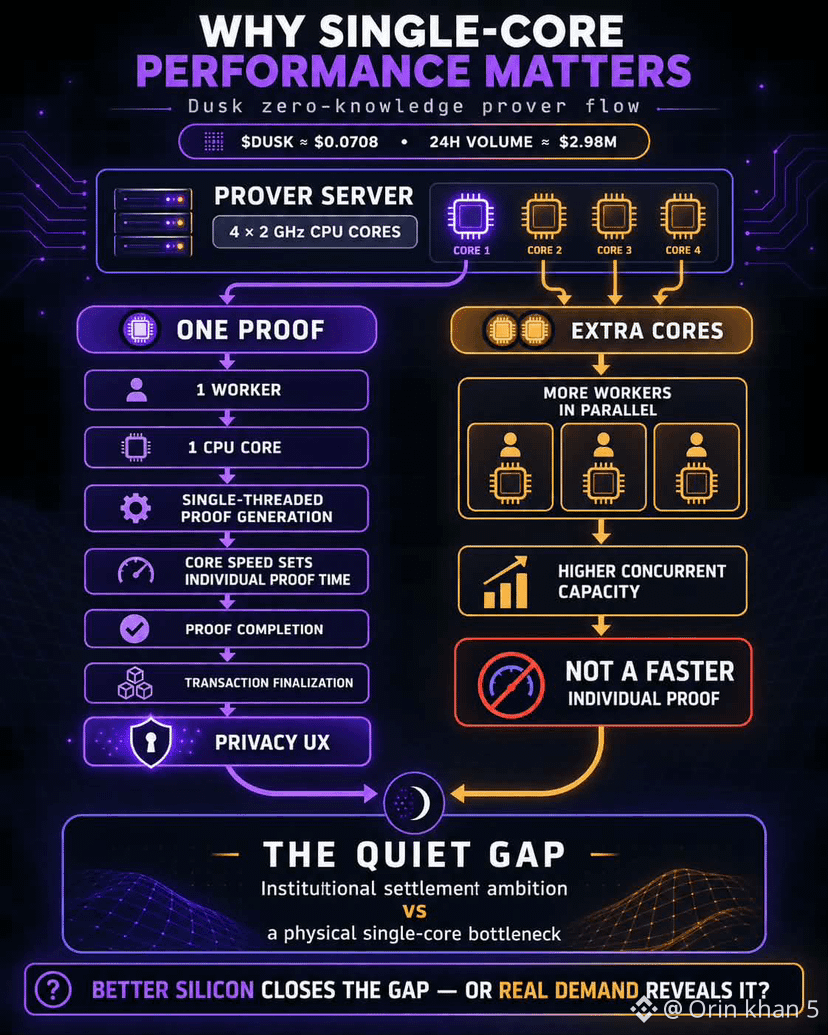
Spent the afternoon moving between @DuskFoundation’s prover docs and the $DUSK market page, checking where privacy becomes ordinary infrastructure. I found $DUSK near $0.0708 with $2.98 million daily volume, while the guide asks for four 2 GHz cores. Hold up — I expected more cores to mean faster proofs. What actually stopped me though was one worker using one core because proof generation is single-threaded. I read the extra cores as simultaneous-worker capacity, while each proof still leans on one core’s speed. Hmm. That gap that actually stuck with me sits between the institutional settlement pitch and a physical bottleneck: I can imagine one slow core stretching proof completion and transaction finalization even when total server capacity looks generous. Grabbed a snack, came back, and I was still thinking about operator hardware becoming part of privacy UX. Still chewing on this one. I wonder whether better silicon quietly closes that gap, or whether real demand only makes it visible later?
#dusk $DUSK @Dusk
Spent the afternoon moving between @DuskFoundation’s prover docs and the $DUSK market page, checking where privacy becomes ordinary infrastructure. I found $DUSK near $0.0708 with $2.98 million daily volume, while the guide asks for four 2 GHz cores. Hold up — I expected more cores to mean faster proofs. What actually stopped me though was one worker using one core because proof generation is single-threaded. I read the extra cores as simultaneous-worker capacity, while each proof still leans on one core’s speed. Hmm. That gap that actually stuck with me sits between the institutional settlement pitch and a physical bottleneck: I can imagine one slow core stretching proof completion and transaction finalization even when total server capacity looks generous. Grabbed a snack, came back, and I was still thinking about operator hardware becoming part of privacy UX. Still chewing on this one. I wonder whether better silicon quietly closes that gap, or whether real demand only makes it visible later?
Spent the afternoon moving between @DuskFoundation’s prover docs and the $DUSK market page, checking where privacy becomes ordinary infrastructure. I found $DUSK near $0.0708 with $2.98 million daily volume, while the guide asks for four 2 GHz cores. Hold up — I expected more cores to mean faster proofs. What actually stopped me though was one worker using one core because proof generation is single-threaded. I read the extra cores as simultaneous-worker capacity, while each proof still leans on one core’s speed. Hmm. That gap that actually stuck with me sits between the institutional settlement pitch and a physical bottleneck: I can imagine one slow core stretching proof completion and transaction finalization even when total server capacity looks generous. Grabbed a snack, came back, and I was still thinking about operator hardware becoming part of privacy UX. Still chewing on this one. I wonder whether better silicon quietly closes that gap, or whether real demand only makes it visible later?
1
2
91
·
--
#dusk $DUSK @Dusk_Foundation
Spent the afternoon checking @DuskFoundation’s $DUSK exchange docs, then wandered over to the market page. DUSK was near $0.0758, with roughly $45.5 million in market cap and $4.13 million moving over 24 hours. Hold up — the network advertises deterministic finality in about 10 seconds, yet an exchange cannot treat “included,” “accepted,” or even “confirmed” as money ready to credit. What actually stopped me though was the operational gap. I found that an accepted block can still be reverted; the safe signal is the explicit finalized state change, read from finalized archive history. Hmm. Fast settlement still asks the exchange to wait, checkpoint carefully, and credit atomically rather than react to the first visible balance movement. Grabbed a snack, came back, and that gap that actually stuck with me felt less like slowness than discipline. Still chewing on this one. Does the gap close as integrations mature, remain by design, or only become visible after an exchange credits too early?
#dusk $DUSK @Dusk
Spent the afternoon checking @DuskFoundation’s $DUSK exchange docs, then wandered over to the market page. DUSK was near $0.0758, with roughly $45.5 million in market cap and $4.13 million moving over 24 hours. Hold up — the network advertises deterministic finality in about 10 seconds, yet an exchange cannot treat “included,” “accepted,” or even “confirmed” as money ready to credit. What actually stopped me though was the operational gap. I found that an accepted block can still be reverted; the safe signal is the explicit finalized state change, read from finalized archive history. Hmm. Fast settlement still asks the exchange to wait, checkpoint carefully, and credit atomically rather than react to the first visible balance movement. Grabbed a snack, came back, and that gap that actually stuck with me felt less like slowness than discipline. Still chewing on this one. Does the gap close as integrations mature, remain by design, or only become visible after an exchange credits too early?
Spent the afternoon checking @DuskFoundation’s $DUSK exchange docs, then wandered over to the market page. DUSK was near $0.0758, with roughly $45.5 million in market cap and $4.13 million moving over 24 hours. Hold up — the network advertises deterministic finality in about 10 seconds, yet an exchange cannot treat “included,” “accepted,” or even “confirmed” as money ready to credit. What actually stopped me though was the operational gap. I found that an accepted block can still be reverted; the safe signal is the explicit finalized state change, read from finalized archive history. Hmm. Fast settlement still asks the exchange to wait, checkpoint carefully, and credit atomically rather than react to the first visible balance movement. Grabbed a snack, came back, and that gap that actually stuck with me felt less like slowness than discipline. Still chewing on this one. Does the gap close as integrations mature, remain by design, or only become visible after an exchange credits too early?
111
·
--
#dusk $DUSK @Dusk_Foundation
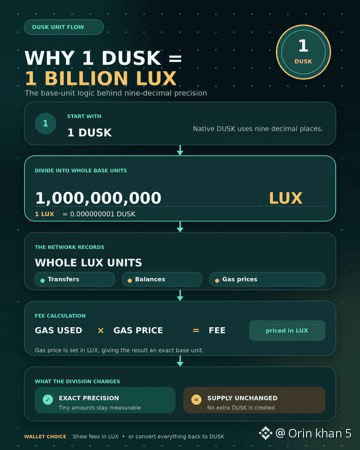
At first I thought LUX was simply another name for $DUSK, a denomination most users could ignore.
After looking closer at @Dusk, I realized it defines the network’s precision. Native DUSK has nine decimal places: 1 DUSK equals 1,000,000,000 LUX, while 1 LUX equals 0.000000001 DUSK.
The network records amounts in whole LUX units. Gas prices are also set in LUX, and the fee comes from gas used multiplied by gas price. This gives wallets and developers an exact base unit for transfers, balances and fees.
That is what I like about this approach. The division does not increase supply or make $DUSK more valuable. It simply makes tiny amounts measurable without using fractions below the network’s smallest unit.
I’m curious whether users will ever think in LUX, or whether wallets will keep it mostly invisible.
Would you rather see network fees in LUX or have wallets convert everything into DUSK?
#dusk $DUSK @Dusk
At first I thought LUX was simply another name for $DUSK , a denomination most users could ignore.
After looking closer at @Dusk, I realized it defines the network’s precision. Native DUSK has nine decimal places: 1 DUSK equals 1,000,000,000 LUX, while 1 LUX equals 0.000000001 DUSK.
The network records amounts in whole LUX units. Gas prices are also set in LUX, and the fee comes from gas used multiplied by gas price. This gives wallets and developers an exact base unit for transfers, balances and fees.
That is what I like about this approach. The division does not increase supply or make $DUSK more valuable. It simply makes tiny amounts measurable without using fractions below the network’s smallest unit.
I’m curious whether users will ever think in LUX, or whether wallets will keep it mostly invisible.
Would you rather see network fees in LUX or have wallets convert everything into DUSK?
At first I thought LUX was simply another name for $DUSK , a denomination most users could ignore.
After looking closer at @Dusk, I realized it defines the network’s precision. Native DUSK has nine decimal places: 1 DUSK equals 1,000,000,000 LUX, while 1 LUX equals 0.000000001 DUSK.
The network records amounts in whole LUX units. Gas prices are also set in LUX, and the fee comes from gas used multiplied by gas price. This gives wallets and developers an exact base unit for transfers, balances and fees.
That is what I like about this approach. The division does not increase supply or make $DUSK more valuable. It simply makes tiny amounts measurable without using fractions below the network’s smallest unit.
I’m curious whether users will ever think in LUX, or whether wallets will keep it mostly invisible.
Would you rather see network fees in LUX or have wallets convert everything into DUSK?
3
3
126
·
--
#dusk $DUSK @Dusk_Foundation
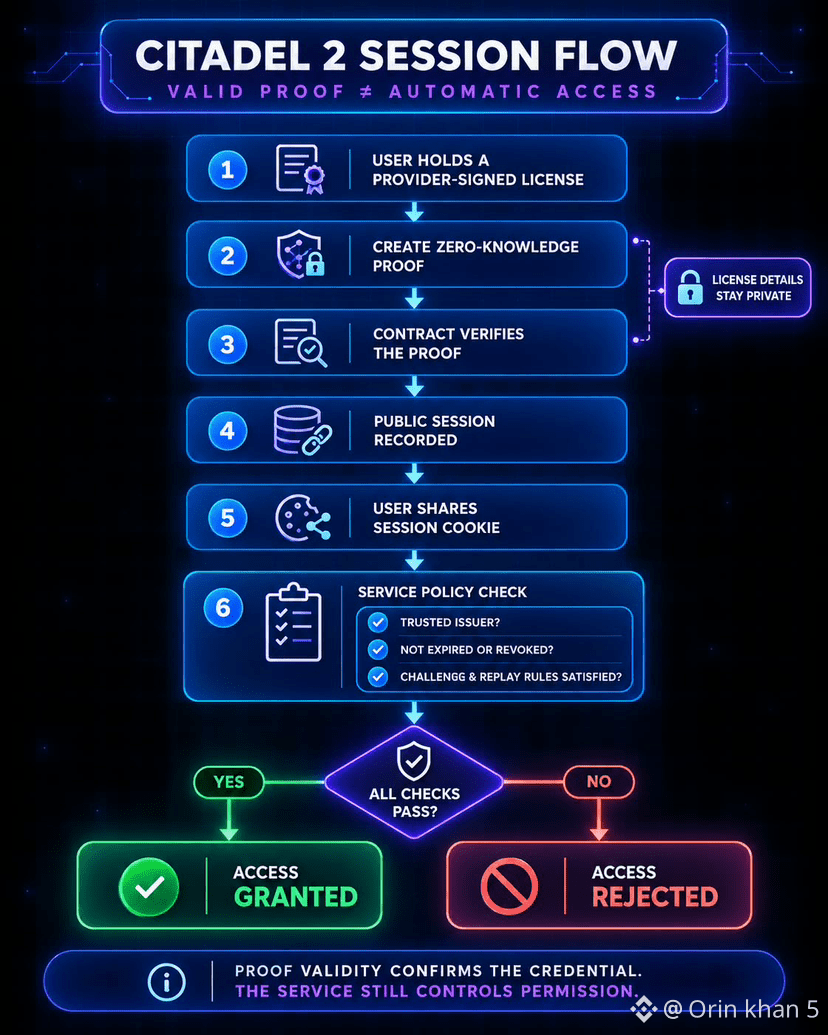
At first I thought a cryptographically valid Citadel 2 session was a universal access pass: if the proof checked out on-chain, the service should let me in.
Looking closer at @Dusk, I realized its design separates proof validity from permission. The contract can verify that I hold a registered, provider-signed license and record a session without exposing which license I used. I then share a session cookie, which the service checks against that public record.
But the final decision still belongs to the service. It can reject me if it does not trust the issuer, the credential is expired or revoked, or its challenge and replay rules are not satisfied.
That is what I like about this approach. Privacy does not have to remove control; it can limit disclosure while leaving real-world policy intact.
I’m curious whether users will find that balance reassuring or confusing.
Would you prefer automatic access after proof verification, or service-specific checks?
#dusk $DUSK @Dusk
At first I thought a cryptographically valid Citadel 2 session was a universal access pass: if the proof checked out on-chain, the service should let me in.
Looking closer at @Dusk, I realized its design separates proof validity from permission. The contract can verify that I hold a registered, provider-signed license and record a session without exposing which license I used. I then share a session cookie, which the service checks against that public record.
But the final decision still belongs to the service. It can reject me if it does not trust the issuer, the credential is expired or revoked, or its challenge and replay rules are not satisfied.
That is what I like about this approach. Privacy does not have to remove control; it can limit disclosure while leaving real-world policy intact.
I’m curious whether users will find that balance reassuring or confusing.
Would you prefer automatic access after proof verification, or service-specific checks?
At first I thought a cryptographically valid Citadel 2 session was a universal access pass: if the proof checked out on-chain, the service should let me in.
Looking closer at @Dusk, I realized its design separates proof validity from permission. The contract can verify that I hold a registered, provider-signed license and record a session without exposing which license I used. I then share a session cookie, which the service checks against that public record.
But the final decision still belongs to the service. It can reject me if it does not trust the issuer, the credential is expired or revoked, or its challenge and replay rules are not satisfied.
That is what I like about this approach. Privacy does not have to remove control; it can limit disclosure while leaving real-world policy intact.
I’m curious whether users will find that balance reassuring or confusing.
Would you prefer automatic access after proof verification, or service-specific checks?
1
99
·
--
#dusk $DUSK @Dusk_Foundation
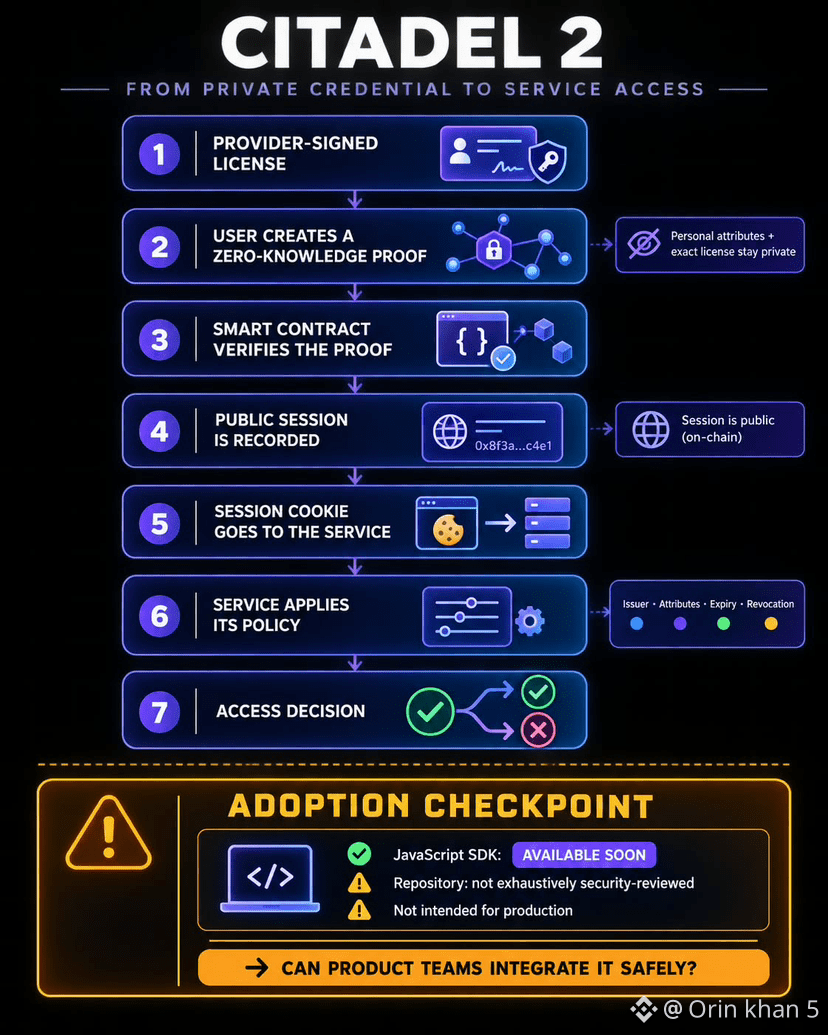
At first I thought Citadel 2’s adoption test was whether users wanted private credentials. Looking closer at @DuskFoundation, I found a practical question: its complete JavaScript SDK remains “available soon.”
Citadel 2 lets someone prove they hold a registered, provider-signed license without placing personal attributes—or the exact license used—on-chain. A contract verifies the zero-knowledge proof and records a public session. The user then gives a session cookie to a service, which decides which issuers and attributes it accepts, plus expiry and revocation rules.
That is what I like about this approach. Privacy does not remove the service’s control. But careful cryptography matters little if ordinary product teams cannot integrate it safely. Dusk’s repository currently says the code has not undergone an exhaustive security review and is not intended for production.
The SDK will test more than convenience: it will test whether this design can reach real workflows.
Would you choose flexible policy controls or the simplest possible integration?
#dusk $DUSK @Dusk
At first I thought Citadel 2’s adoption test was whether users wanted private credentials. Looking closer at @DuskFoundation, I found a practical question: its complete JavaScript SDK remains “available soon.”
Citadel 2 lets someone prove they hold a registered, provider-signed license without placing personal attributes—or the exact license used—on-chain. A contract verifies the zero-knowledge proof and records a public session. The user then gives a session cookie to a service, which decides which issuers and attributes it accepts, plus expiry and revocation rules.
That is what I like about this approach. Privacy does not remove the service’s control. But careful cryptography matters little if ordinary product teams cannot integrate it safely. Dusk’s repository currently says the code has not undergone an exhaustive security review and is not intended for production.
The SDK will test more than convenience: it will test whether this design can reach real workflows.
Would you choose flexible policy controls or the simplest possible integration?
At first I thought Citadel 2’s adoption test was whether users wanted private credentials. Looking closer at @DuskFoundation, I found a practical question: its complete JavaScript SDK remains “available soon.”
Citadel 2 lets someone prove they hold a registered, provider-signed license without placing personal attributes—or the exact license used—on-chain. A contract verifies the zero-knowledge proof and records a public session. The user then gives a session cookie to a service, which decides which issuers and attributes it accepts, plus expiry and revocation rules.
That is what I like about this approach. Privacy does not remove the service’s control. But careful cryptography matters little if ordinary product teams cannot integrate it safely. Dusk’s repository currently says the code has not undergone an exhaustive security review and is not intended for production.
The SDK will test more than convenience: it will test whether this design can reach real workflows.
Would you choose flexible policy controls or the simplest possible integration?
1
108
·
--
#dusk $DUSK @Dusk_Foundation
Hey, you know… one question about @DuskFoundation has stayed with me: if an exchange receives “202 Accepted” for my withdrawal, why is the job not finished?
We are used to reading a response as “done.” But on a blockchain, submission and settlement are different moments.
On Dusk L1, “202 Accepted” only means a node accepted the transaction for routing. It does not prove that the transaction entered the mempool, reached peers, executed successfully, or became final.
Dusk separates those steps. “transactions/included” signals local mempool admission. “transactions/executed” means the transaction ran inside an accepted block, where the “err” field must be null. Finality arrives when a “blocks/statechange” event is marked “finalized.” Before that, an accepted block may still be reverted.
Hypothetically, suppose I withdraw DUSK from an exchange. Its system signs the Moonlight transaction, stores its bytes and ID, then broadcasts it. The 202 response confirms routing—not completion. The exchange must verify execution and finalized block status.
But I stopped here for a moment.
Maybe finality is not only a consensus feature. It is an operational responsibility.
So when is a withdrawal,truly complete: when the API answers, or when reversal is no longer possible? I’m still thinking about this. 🤔
#dusk $DUSK @Dusk
Hey, you know… one question about @DuskFoundation has stayed with me: if an exchange receives “202 Accepted” for my withdrawal, why is the job not finished?
We are used to reading a response as “done.” But on a blockchain, submission and settlement are different moments.
On Dusk L1, “202 Accepted” only means a node accepted the transaction for routing. It does not prove that the transaction entered the mempool, reached peers, executed successfully, or became final.
Dusk separates those steps. “transactions/included” signals local mempool admission. “transactions/executed” means the transaction ran inside an accepted block, where the “err” field must be null. Finality arrives when a “blocks/statechange” event is marked “finalized.” Before that, an accepted block may still be reverted.
Hypothetically, suppose I withdraw DUSK from an exchange. Its system signs the Moonlight transaction, stores its bytes and ID, then broadcasts it. The 202 response confirms routing—not completion. The exchange must verify execution and finalized block status.
But I stopped here for a moment.
Maybe finality is not only a consensus feature. It is an operational responsibility.
So when is a withdrawal,truly complete: when the API answers, or when reversal is no longer possible? I’m still thinking about this. 🤔
Hey, you know… one question about @DuskFoundation has stayed with me: if an exchange receives “202 Accepted” for my withdrawal, why is the job not finished?
We are used to reading a response as “done.” But on a blockchain, submission and settlement are different moments.
On Dusk L1, “202 Accepted” only means a node accepted the transaction for routing. It does not prove that the transaction entered the mempool, reached peers, executed successfully, or became final.
Dusk separates those steps. “transactions/included” signals local mempool admission. “transactions/executed” means the transaction ran inside an accepted block, where the “err” field must be null. Finality arrives when a “blocks/statechange” event is marked “finalized.” Before that, an accepted block may still be reverted.
Hypothetically, suppose I withdraw DUSK from an exchange. Its system signs the Moonlight transaction, stores its bytes and ID, then broadcasts it. The 202 response confirms routing—not completion. The exchange must verify execution and finalized block status.
But I stopped here for a moment.
Maybe finality is not only a consensus feature. It is an operational responsibility.
So when is a withdrawal,truly complete: when the API answers, or when reversal is no longer possible? I’m still thinking about this. 🤔
1
2
181
·
--
#dusk $DUSK @Dusk_Foundation
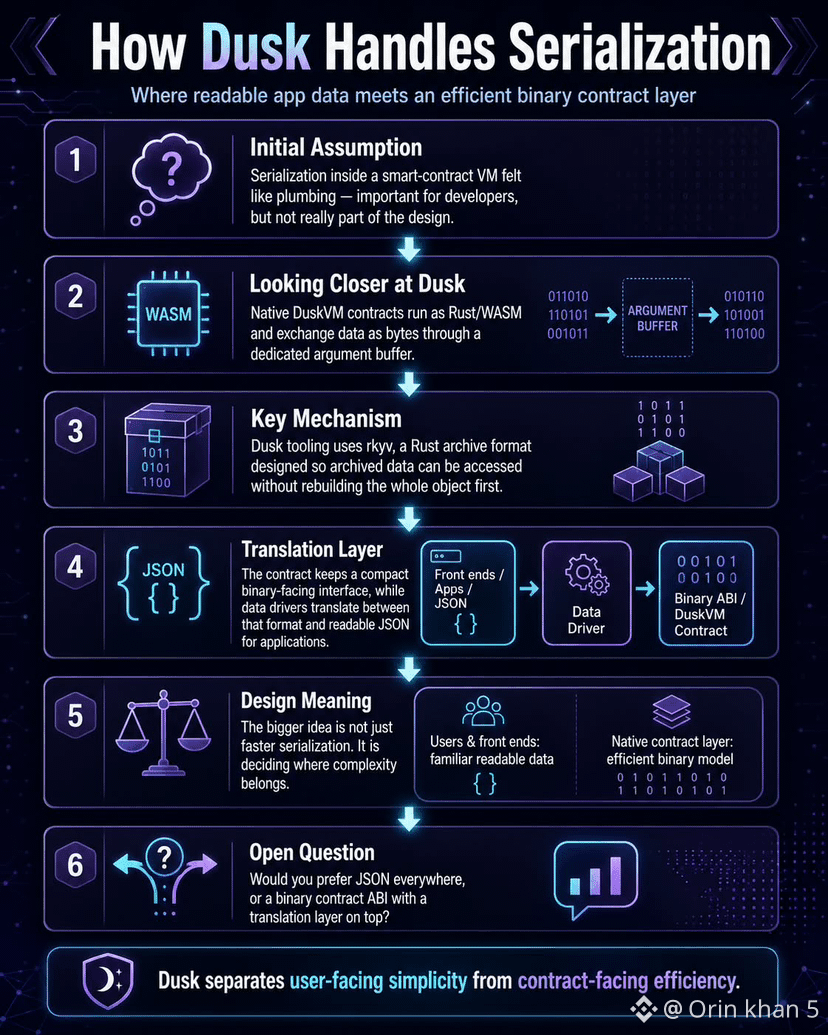
At first I thought serialization inside a smart-contract VM was just plumbing—important for developers, but not really part of the design.
Looking closer at @Dusk_Foundation changed that. Native DuskVM contracts run as Rust/WASM and exchange data as bytes through a dedicated argument buffer. Dusk’s tooling uses "rkyv", a Rust archive format designed so archived data can be accessed without rebuilding the whole object first.
That is what I like about this approach. The contract can keep a compact binary-facing interface, while data drivers can translate between that format and readable JSON for applications.
The broader point is not simply “faster serialization.” It is about deciding where complexity belongs. Users and front ends can work with familiar data, while the native contract layer stays closer to an efficient binary model.
Now I’m curious how developers experience that trade-off in real projects.
Would you prefer JSON everywhere, or a binary contract ABI with a translation layer on top?
#dusk $DUSK @Dusk
At first I thought serialization inside a smart-contract VM was just plumbing—important for developers, but not really part of the design.
Looking closer at @Dusk changed that. Native DuskVM contracts run as Rust/WASM and exchange data as bytes through a dedicated argument buffer. Dusk’s tooling uses "rkyv", a Rust archive format designed so archived data can be accessed without rebuilding the whole object first.
That is what I like about this approach. The contract can keep a compact binary-facing interface, while data drivers can translate between that format and readable JSON for applications.
The broader point is not simply “faster serialization.” It is about deciding where complexity belongs. Users and front ends can work with familiar data, while the native contract layer stays closer to an efficient binary model.
Now I’m curious how developers experience that trade-off in real projects.
Would you prefer JSON everywhere, or a binary contract ABI with a translation layer on top?
At first I thought serialization inside a smart-contract VM was just plumbing—important for developers, but not really part of the design.
Looking closer at @Dusk changed that. Native DuskVM contracts run as Rust/WASM and exchange data as bytes through a dedicated argument buffer. Dusk’s tooling uses "rkyv", a Rust archive format designed so archived data can be accessed without rebuilding the whole object first.
That is what I like about this approach. The contract can keep a compact binary-facing interface, while data drivers can translate between that format and readable JSON for applications.
The broader point is not simply “faster serialization.” It is about deciding where complexity belongs. Users and front ends can work with familiar data, while the native contract layer stays closer to an efficient binary model.
Now I’m curious how developers experience that trade-off in real projects.
Would you prefer JSON everywhere, or a binary contract ABI with a translation layer on top?
2
2
89
·
--
#dusk $DUSK @Dusk_Foundation
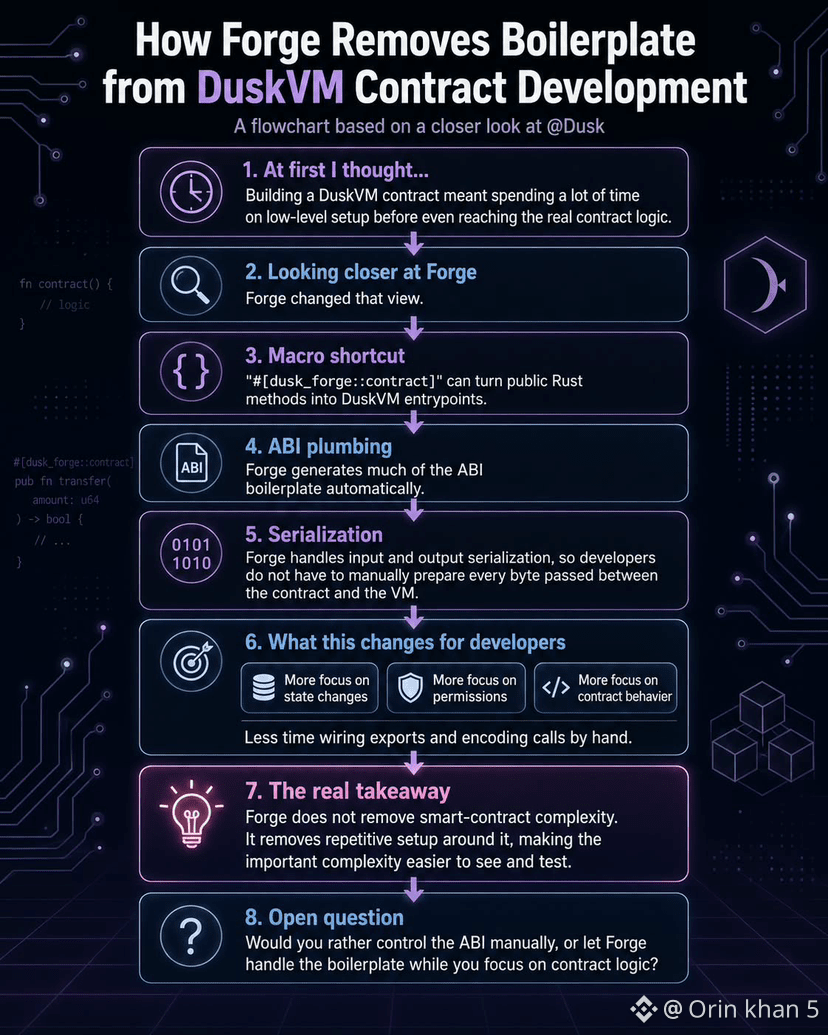
At first I thought building a DuskVM contract meant spending a lot of time on low-level setup before even reaching the actual contract logic.
Looking closer at @Dusk, Forge changed that view. Its "macro can turn public Rust methods into DuskVM entrypoints and generate much of the ABI plumbing automatically. Forge also handles input and output serialization, so developers do not have to manually prepare every byte passed between the contract and VM.
That is what I like about this approach. A developer can spend more time thinking about state changes, permissions, and contract behavior instead of repeatedly wiring exports and encoding calls by hand.
The interesting part is that Forge does not remove complexity from smart contracts. It removes repetitive setup around them, making the important complexity easier to see and test.
Now I am curious about adoption.
Would you rather control the ABI manually, or let Forge handle, the boilerplate while you focus on contract logic?
#dusk $DUSK @Dusk
At first I thought building a DuskVM contract meant spending a lot of time on low-level setup before even reaching the actual contract logic.
Looking closer at @Dusk, Forge changed that view. Its "macro can turn public Rust methods into DuskVM entrypoints and generate much of the ABI plumbing automatically. Forge also handles input and output serialization, so developers do not have to manually prepare every byte passed between the contract and VM.
That is what I like about this approach. A developer can spend more time thinking about state changes, permissions, and contract behavior instead of repeatedly wiring exports and encoding calls by hand.
The interesting part is that Forge does not remove complexity from smart contracts. It removes repetitive setup around them, making the important complexity easier to see and test.
Now I am curious about adoption.
Would you rather control the ABI manually, or let Forge handle, the boilerplate while you focus on contract logic?
At first I thought building a DuskVM contract meant spending a lot of time on low-level setup before even reaching the actual contract logic.
Looking closer at @Dusk, Forge changed that view. Its "macro can turn public Rust methods into DuskVM entrypoints and generate much of the ABI plumbing automatically. Forge also handles input and output serialization, so developers do not have to manually prepare every byte passed between the contract and VM.
That is what I like about this approach. A developer can spend more time thinking about state changes, permissions, and contract behavior instead of repeatedly wiring exports and encoding calls by hand.
The interesting part is that Forge does not remove complexity from smart contracts. It removes repetitive setup around them, making the important complexity easier to see and test.
Now I am curious about adoption.
Would you rather control the ABI manually, or let Forge handle, the boilerplate while you focus on contract logic?
3
3
112
·
--
#dusk $DUSK @Dusk_Foundation
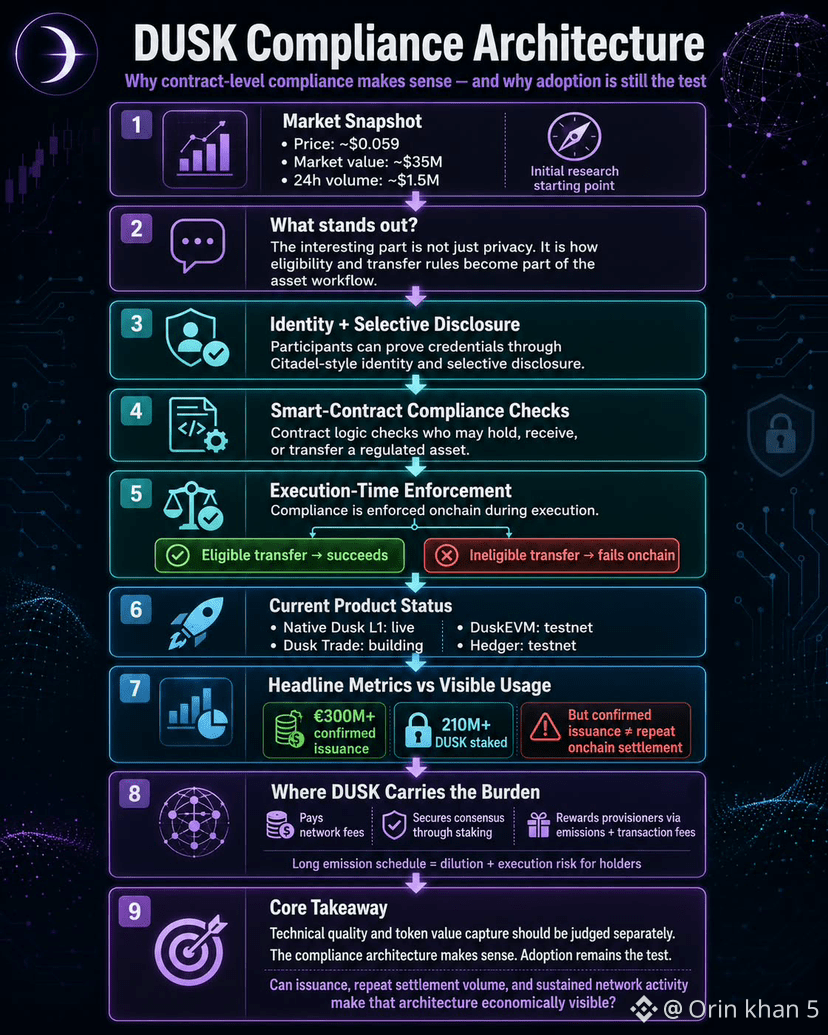
I was checking DUSK around $0.059, with roughly $35 million in market value and about $1.5 million in daily volume, when I returned to Dusk’s compliance architecture. The interesting part is not privacy. It is making eligibility and transfer rules part of the asset workflow.
For a regulated asset, a participant can prove credentials through Citadel-style identity and selective disclosure, while smart-contract logic checks who may hold, receive, or transfer the asset. That matters because compliance is enforced at execution time: an ineligible transfer can fail onchain instead of depending entirely on a venue or manual review.
The harder question is whether that design is producing visible usage yet. Dusk’s native L1 is live, but Dusk Trade is still building, while DuskEVM and Hedger remain testnets. Dusk reports €300M+ in confirmed issuance and 210M+ DUSK staked, yet confirmed issuance is not the same as repeat onchain settlement.
DUSK carries the economic burden. It pays network fees, secures consensus through staking, and rewards provisioners through emissions plus transaction fees. The emission schedule continues over decades, so holders face dilution and execution risk while institutions may use compliant infrastructure without needing recurring DUSK balances.
That is why technical quality and token value capture should be judged separately. The contract-level compliance model makes sense; adoption remains the test. Can verifiable issuance, repeat settlement volume, and sustained network activity make that architecture economically visible?
#dusk $DUSK @Dusk
I was checking DUSK around $0.059, with roughly $35 million in market value and about $1.5 million in daily volume, when I returned to Dusk’s compliance architecture. The interesting part is not privacy. It is making eligibility and transfer rules part of the asset workflow.
For a regulated asset, a participant can prove credentials through Citadel-style identity and selective disclosure, while smart-contract logic checks who may hold, receive, or transfer the asset. That matters because compliance is enforced at execution time: an ineligible transfer can fail onchain instead of depending entirely on a venue or manual review.
The harder question is whether that design is producing visible usage yet. Dusk’s native L1 is live, but Dusk Trade is still building, while DuskEVM and Hedger remain testnets. Dusk reports €300M+ in confirmed issuance and 210M+ DUSK staked, yet confirmed issuance is not the same as repeat onchain settlement.
DUSK carries the economic burden. It pays network fees, secures consensus through staking, and rewards provisioners through emissions plus transaction fees. The emission schedule continues over decades, so holders face dilution and execution risk while institutions may use compliant infrastructure without needing recurring DUSK balances.
That is why technical quality and token value capture should be judged separately. The contract-level compliance model makes sense; adoption remains the test. Can verifiable issuance, repeat settlement volume, and sustained network activity make that architecture economically visible?
I was checking DUSK around $0.059, with roughly $35 million in market value and about $1.5 million in daily volume, when I returned to Dusk’s compliance architecture. The interesting part is not privacy. It is making eligibility and transfer rules part of the asset workflow.
For a regulated asset, a participant can prove credentials through Citadel-style identity and selective disclosure, while smart-contract logic checks who may hold, receive, or transfer the asset. That matters because compliance is enforced at execution time: an ineligible transfer can fail onchain instead of depending entirely on a venue or manual review.
The harder question is whether that design is producing visible usage yet. Dusk’s native L1 is live, but Dusk Trade is still building, while DuskEVM and Hedger remain testnets. Dusk reports €300M+ in confirmed issuance and 210M+ DUSK staked, yet confirmed issuance is not the same as repeat onchain settlement.
DUSK carries the economic burden. It pays network fees, secures consensus through staking, and rewards provisioners through emissions plus transaction fees. The emission schedule continues over decades, so holders face dilution and execution risk while institutions may use compliant infrastructure without needing recurring DUSK balances.
That is why technical quality and token value capture should be judged separately. The contract-level compliance model makes sense; adoption remains the test. Can verifiable issuance, repeat settlement volume, and sustained network activity make that architecture economically visible?
2
1
84
·
--
#dusk $DUSK @Dusk_Foundation
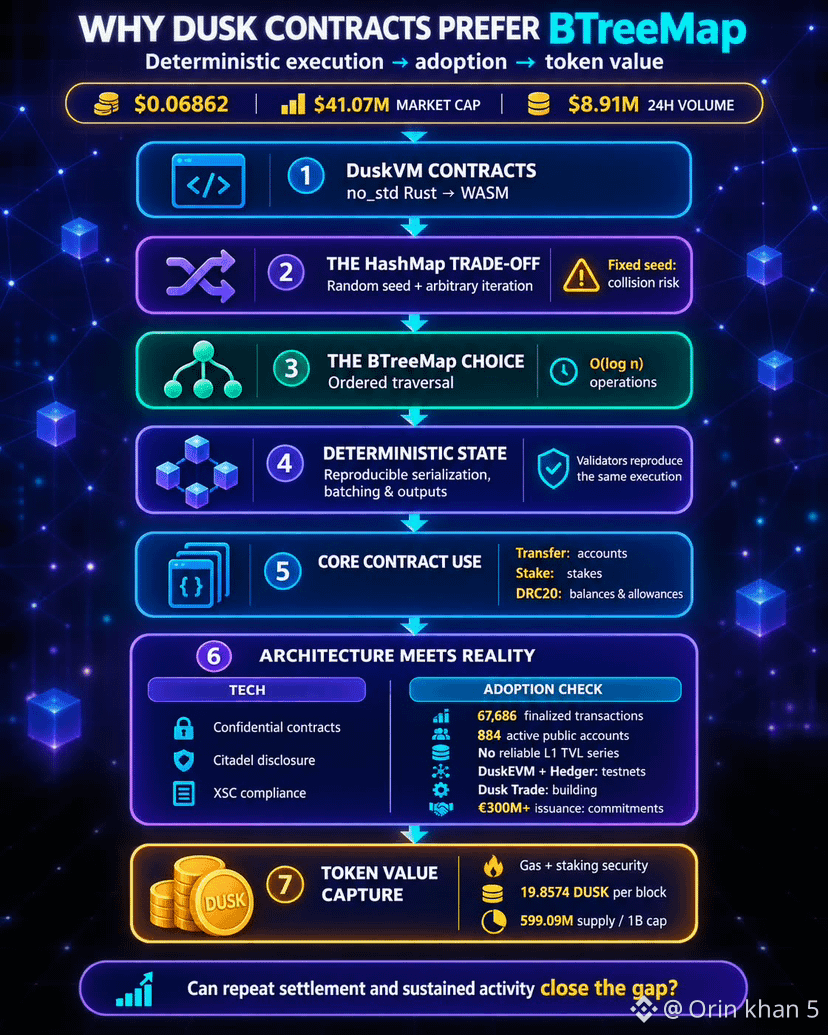
Last night I returned to DUSK’s chart: $0.06862, a $41.07 million market cap and $8.91 million in 24-hour volume. The stronger signal was in its Rust contracts: BTreeMap appears where developers might expect HashMap.
DuskVM contracts are no_std Rust compiled to WASM. Rust’s default HashMap uses a random seed and arbitrary iteration—awkward when every validator must reproduce execution. A fixed-seed map could restore determinism but invite collision attacks. BTreeMap instead traverses keys predictably, accepting logarithmic operations over expected constant-time lookups.
Dusk’s transfer, stake and DRC20 code uses it for accounts, stakes, balances and allowances. Ordered state traversal helps keep serialization, batch processing and outputs reproducible. It complements Dusk’s proposition: confidential contracts, Citadel selective disclosure and XSC-based programmable compliance for regulated finance.
Yet architecture is ahead of adoption. At my check, the live L1 showed 67,686 finalized transactions and 884 active public accounts; shielded activity is less visible, and no reliable L1 TVL series exists. DuskEVM and Hedger remain testnets, Dusk Trade is building, and €300 million-plus issuance means commitments—not demonstrated settlement.
DUSK pays gas and secures staking; blocks still emit 19.8574 DUSK, with supply at 599.09 million against a one-billion cap. Issuers might value deterministic infrastructure without needing much DUSK, while holders absorb inflation, execution risk and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement and sustained activity close that gap?
#dusk $DUSK @Dusk
Last night I returned to DUSK’s chart: $0.06862, a $41.07 million market cap and $8.91 million in 24-hour volume. The stronger signal was in its Rust contracts: BTreeMap appears where developers might expect HashMap.
DuskVM contracts are no_std Rust compiled to WASM. Rust’s default HashMap uses a random seed and arbitrary iteration—awkward when every validator must reproduce execution. A fixed-seed map could restore determinism but invite collision attacks. BTreeMap instead traverses keys predictably, accepting logarithmic operations over expected constant-time lookups.
Dusk’s transfer, stake and DRC20 code uses it for accounts, stakes, balances and allowances. Ordered state traversal helps keep serialization, batch processing and outputs reproducible. It complements Dusk’s proposition: confidential contracts, Citadel selective disclosure and XSC-based programmable compliance for regulated finance.
Yet architecture is ahead of adoption. At my check, the live L1 showed 67,686 finalized transactions and 884 active public accounts; shielded activity is less visible, and no reliable L1 TVL series exists. DuskEVM and Hedger remain testnets, Dusk Trade is building, and €300 million-plus issuance means commitments—not demonstrated settlement.
DUSK pays gas and secures staking; blocks still emit 19.8574 DUSK, with supply at 599.09 million against a one-billion cap. Issuers might value deterministic infrastructure without needing much DUSK, while holders absorb inflation, execution risk and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement and sustained activity close that gap?
Last night I returned to DUSK’s chart: $0.06862, a $41.07 million market cap and $8.91 million in 24-hour volume. The stronger signal was in its Rust contracts: BTreeMap appears where developers might expect HashMap.
DuskVM contracts are no_std Rust compiled to WASM. Rust’s default HashMap uses a random seed and arbitrary iteration—awkward when every validator must reproduce execution. A fixed-seed map could restore determinism but invite collision attacks. BTreeMap instead traverses keys predictably, accepting logarithmic operations over expected constant-time lookups.
Dusk’s transfer, stake and DRC20 code uses it for accounts, stakes, balances and allowances. Ordered state traversal helps keep serialization, batch processing and outputs reproducible. It complements Dusk’s proposition: confidential contracts, Citadel selective disclosure and XSC-based programmable compliance for regulated finance.
Yet architecture is ahead of adoption. At my check, the live L1 showed 67,686 finalized transactions and 884 active public accounts; shielded activity is less visible, and no reliable L1 TVL series exists. DuskEVM and Hedger remain testnets, Dusk Trade is building, and €300 million-plus issuance means commitments—not demonstrated settlement.
DUSK pays gas and secures staking; blocks still emit 19.8574 DUSK, with supply at 599.09 million against a one-billion cap. Issuers might value deterministic infrastructure without needing much DUSK, while holders absorb inflation, execution risk and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement and sustained activity close that gap?
3
1
101
·
--
#dusk $DUSK @Dusk_Foundation
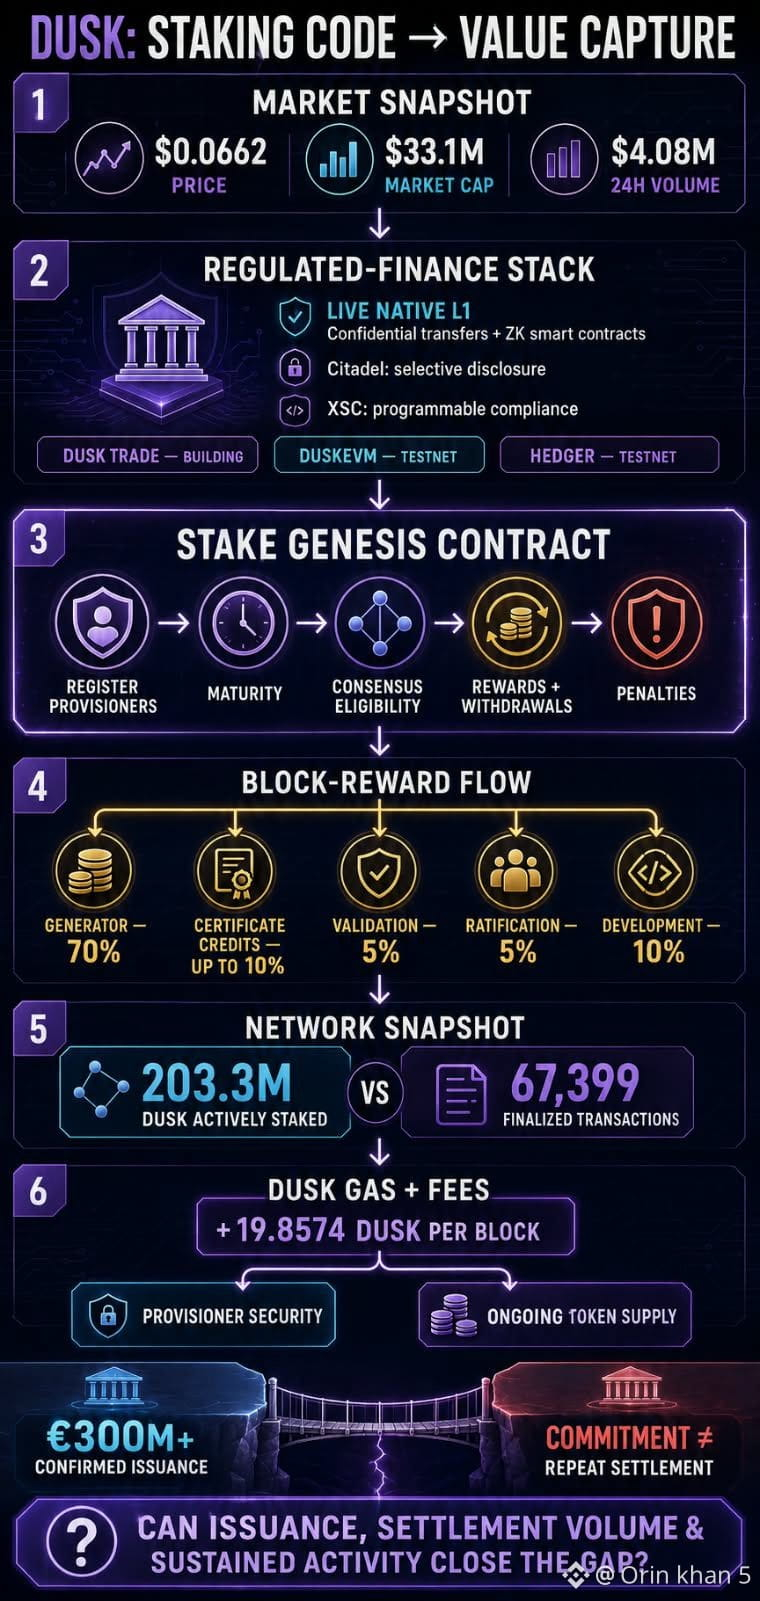
I opened DUSK’s chart to confirm a price, then ended up in the staking code. DUSK was near $0.0662, with a $33.1 million market cap and $4.08 million in 24-hour volume.
The larger proposition is regulated finance with fewer public leaks: confidential transfers and ZK smart contracts on the live native L1, Citadel-style selective disclosure, and XSC-style programmable compliance. Dusk Trade is still being built; DuskEVM and Hedger are testnets, not production adoption.
What held me was the Stake genesis contract. It records provisioners, matures stakes before consensus eligibility, credits rewards, processes withdrawals, and applies penalties. Generators receive 70% of each block reward plus up to 10% for certificate credits; validation and ratification committees receive 5% each, and 10% funds development. At my snapshot, node data showed 203.3 million DUSK actively staked but only 67,399 finalized transactions.
DUSK pays gas and secures this machinery. Rewards are probabilistic, funded by transaction fees and a current emission of 19.8574 DUSK per block. That keeps provisioners working, but adds ongoing supply. Meanwhile, €300 million-plus confirmed issuance is a commitment figure, not disclosed repeat settlement, and compliant venues may not need to hold large DUSK balances.
Technical quality and token value capture are related, not identical; holders absorb inflation, execution risk, and adoption time. Can verifiable issuance, repeat settlement volume, and sustained network activity eventually close the gap between Dusk’s roadmap and today’s numbers?
#dusk $DUSK @Dusk
I opened DUSK’s chart to confirm a price, then ended up in the staking code. DUSK was near $0.0662, with a $33.1 million market cap and $4.08 million in 24-hour volume.
The larger proposition is regulated finance with fewer public leaks: confidential transfers and ZK smart contracts on the live native L1, Citadel-style selective disclosure, and XSC-style programmable compliance. Dusk Trade is still being built; DuskEVM and Hedger are testnets, not production adoption.
What held me was the Stake genesis contract. It records provisioners, matures stakes before consensus eligibility, credits rewards, processes withdrawals, and applies penalties. Generators receive 70% of each block reward plus up to 10% for certificate credits; validation and ratification committees receive 5% each, and 10% funds development. At my snapshot, node data showed 203.3 million DUSK actively staked but only 67,399 finalized transactions.
DUSK pays gas and secures this machinery. Rewards are probabilistic, funded by transaction fees and a current emission of 19.8574 DUSK per block. That keeps provisioners working, but adds ongoing supply. Meanwhile, €300 million-plus confirmed issuance is a commitment figure, not disclosed repeat settlement, and compliant venues may not need to hold large DUSK balances.
Technical quality and token value capture are related, not identical; holders absorb inflation, execution risk, and adoption time. Can verifiable issuance, repeat settlement volume, and sustained network activity eventually close the gap between Dusk’s roadmap and today’s numbers?
I opened DUSK’s chart to confirm a price, then ended up in the staking code. DUSK was near $0.0662, with a $33.1 million market cap and $4.08 million in 24-hour volume.
The larger proposition is regulated finance with fewer public leaks: confidential transfers and ZK smart contracts on the live native L1, Citadel-style selective disclosure, and XSC-style programmable compliance. Dusk Trade is still being built; DuskEVM and Hedger are testnets, not production adoption.
What held me was the Stake genesis contract. It records provisioners, matures stakes before consensus eligibility, credits rewards, processes withdrawals, and applies penalties. Generators receive 70% of each block reward plus up to 10% for certificate credits; validation and ratification committees receive 5% each, and 10% funds development. At my snapshot, node data showed 203.3 million DUSK actively staked but only 67,399 finalized transactions.
DUSK pays gas and secures this machinery. Rewards are probabilistic, funded by transaction fees and a current emission of 19.8574 DUSK per block. That keeps provisioners working, but adds ongoing supply. Meanwhile, €300 million-plus confirmed issuance is a commitment figure, not disclosed repeat settlement, and compliant venues may not need to hold large DUSK balances.
Technical quality and token value capture are related, not identical; holders absorb inflation, execution risk, and adoption time. Can verifiable issuance, repeat settlement volume, and sustained network activity eventually close the gap between Dusk’s roadmap and today’s numbers?
3
3
87
·
--
Privacy will be increasingly important in financial blockchain applications, and Dusk is building in the right direction.
Privacy will be increasingly important in financial blockchain applications, and Dusk is building in the right direction.
75
·
--
#dusk $DUSK @Dusk_Foundation
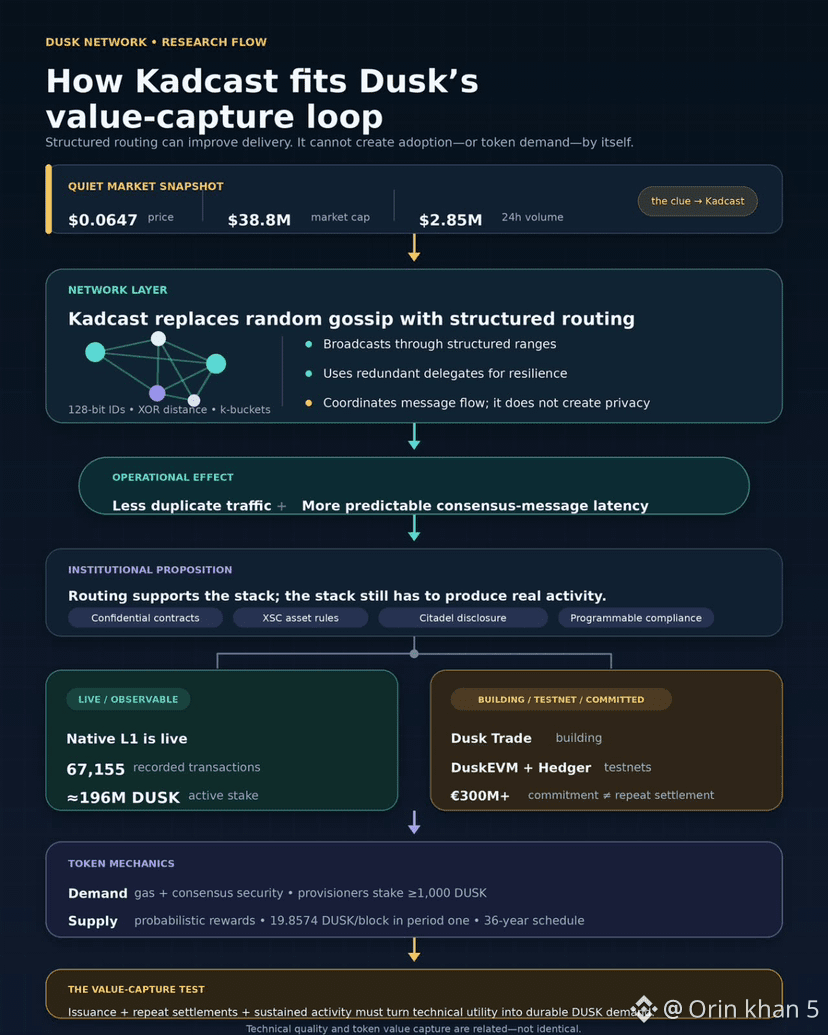
Late last night I found DUSK near $0.0647, with a $38.8 million market cap and $2.85 million in 24-hour volume. The market looked quiet; Kadcast was the detail that pulled me back into the documentation.
Unlike random gossip, Kadcast assigns 128-bit identifiers, organizes nodes into XOR-distance k-buckets, and broadcasts through structured ranges with redundant delegates. It does not create privacy; it aims to reduce duplicate traffic and make consensus-message latency more predictable.
That supports Dusk’s larger proposition: regulated activity through confidential smart contracts, XSC asset rules, Citadel selective disclosure, and programmable compliance. Yet the live L1 has recorded 67,155 transactions and roughly 196 million DUSK in active stake. Dusk Trade is building; DuskEVM and Hedger remain testnets. The advertised €300M-plus issuance is a commitment, not visible repeat settlement.
DUSK pays gas and secures consensus. Provisioners stake at least 1,000, stay online, and earn probabilistic emissions plus fees. Legacy allocations are listed fully vested, but the 36-year reward schedule still emits 19.8574 DUSK per block in its first four-year period, leaving ongoing supply pressure.
I come back to the value-capture tension. Issuers may use Dusk’s routing, privacy, and compliance stack while holding little DUSK beyond operating needs; holders absorb emissions, execution risk, and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement volume, and sustained activity close the gap between roadmap and usage?
#dusk $DUSK @Dusk
Late last night I found DUSK near $0.0647, with a $38.8 million market cap and $2.85 million in 24-hour volume. The market looked quiet; Kadcast was the detail that pulled me back into the documentation.
Unlike random gossip, Kadcast assigns 128-bit identifiers, organizes nodes into XOR-distance k-buckets, and broadcasts through structured ranges with redundant delegates. It does not create privacy; it aims to reduce duplicate traffic and make consensus-message latency more predictable.
That supports Dusk’s larger proposition: regulated activity through confidential smart contracts, XSC asset rules, Citadel selective disclosure, and programmable compliance. Yet the live L1 has recorded 67,155 transactions and roughly 196 million DUSK in active stake. Dusk Trade is building; DuskEVM and Hedger remain testnets. The advertised €300M-plus issuance is a commitment, not visible repeat settlement.
DUSK pays gas and secures consensus. Provisioners stake at least 1,000, stay online, and earn probabilistic emissions plus fees. Legacy allocations are listed fully vested, but the 36-year reward schedule still emits 19.8574 DUSK per block in its first four-year period, leaving ongoing supply pressure.
I come back to the value-capture tension. Issuers may use Dusk’s routing, privacy, and compliance stack while holding little DUSK beyond operating needs; holders absorb emissions, execution risk, and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement volume, and sustained activity close the gap between roadmap and usage?
Late last night I found DUSK near $0.0647, with a $38.8 million market cap and $2.85 million in 24-hour volume. The market looked quiet; Kadcast was the detail that pulled me back into the documentation.
Unlike random gossip, Kadcast assigns 128-bit identifiers, organizes nodes into XOR-distance k-buckets, and broadcasts through structured ranges with redundant delegates. It does not create privacy; it aims to reduce duplicate traffic and make consensus-message latency more predictable.
That supports Dusk’s larger proposition: regulated activity through confidential smart contracts, XSC asset rules, Citadel selective disclosure, and programmable compliance. Yet the live L1 has recorded 67,155 transactions and roughly 196 million DUSK in active stake. Dusk Trade is building; DuskEVM and Hedger remain testnets. The advertised €300M-plus issuance is a commitment, not visible repeat settlement.
DUSK pays gas and secures consensus. Provisioners stake at least 1,000, stay online, and earn probabilistic emissions plus fees. Legacy allocations are listed fully vested, but the 36-year reward schedule still emits 19.8574 DUSK per block in its first four-year period, leaving ongoing supply pressure.
I come back to the value-capture tension. Issuers may use Dusk’s routing, privacy, and compliance stack while holding little DUSK beyond operating needs; holders absorb emissions, execution risk, and adoption time. Technical quality and token value capture are related, not identical. Can verifiable issuance, repeat settlement volume, and sustained activity close the gap between roadmap and usage?
6
4
102
·
--
Confidential smart contracts could be a major step forward for secure and private on-chain finance.
Confidential smart contracts could be a major step forward for secure and private on-chain finance.
82
·
--
Privacy will be increasingly important in financial blockchain applications, and Dusk is building in the right direction.
Privacy will be increasingly important in financial blockchain applications, and Dusk is building in the right direction.
1
68
·
--
#dusk $DUSK @Dusk_Foundation
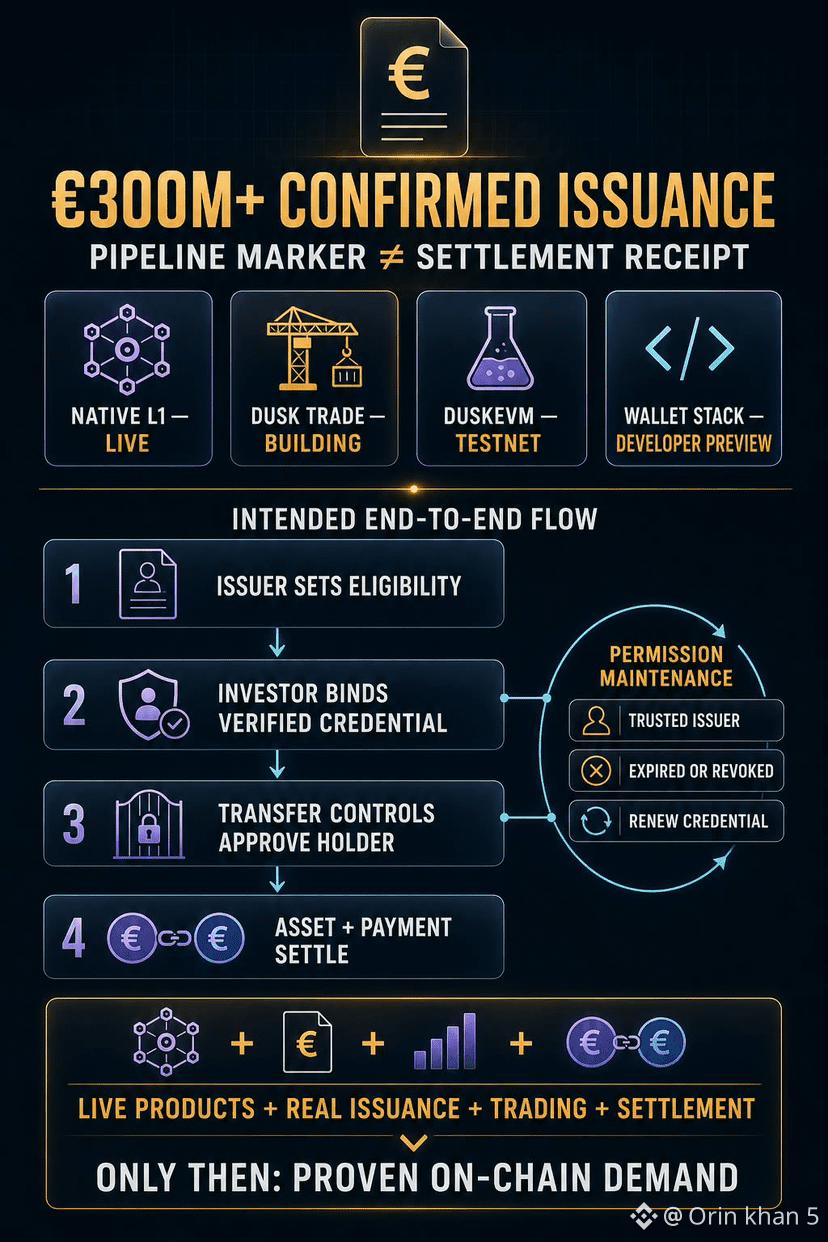
At first I read Dusk’s “€300M+ confirmed issuance” as proof securities were already moving on-chain. The product map changed that: the native L1 is live, but Dusk Trade is “Building,” DuskEVM is on testnet, and the wallet stack is in developer preview.
The figure is a pipeline marker, not a settlement receipt.
The intended flow is clear. An issuer sets eligibility rules, an investor binds a wallet to verified credentials, transfer controls decide who may hold the asset, and asset and payment legs settle with deterministic finality. Yet that complete product path is not live today.
The quieter friction is permission maintenance. Citadel can prove a credential without exposing its details, but each service still chooses trusted issuers and decides whether a session has expired or been revoked. Settlement persists; access may need renewal, making participation—and switching—more costly over time.
Should €300M be read as institutional commitment, or as future demand proven only once assets are issued, traded, and settled?
#dusk $DUSK @Dusk
At first I read Dusk’s “€300M+ confirmed issuance” as proof securities were already moving on-chain. The product map changed that: the native L1 is live, but Dusk Trade is “Building,” DuskEVM is on testnet, and the wallet stack is in developer preview.
The figure is a pipeline marker, not a settlement receipt.
The intended flow is clear. An issuer sets eligibility rules, an investor binds a wallet to verified credentials, transfer controls decide who may hold the asset, and asset and payment legs settle with deterministic finality. Yet that complete product path is not live today.
The quieter friction is permission maintenance. Citadel can prove a credential without exposing its details, but each service still chooses trusted issuers and decides whether a session has expired or been revoked. Settlement persists; access may need renewal, making participation—and switching—more costly over time.
Should €300M be read as institutional commitment, or as future demand proven only once assets are issued, traded, and settled?
At first I read Dusk’s “€300M+ confirmed issuance” as proof securities were already moving on-chain. The product map changed that: the native L1 is live, but Dusk Trade is “Building,” DuskEVM is on testnet, and the wallet stack is in developer preview.
The figure is a pipeline marker, not a settlement receipt.
The intended flow is clear. An issuer sets eligibility rules, an investor binds a wallet to verified credentials, transfer controls decide who may hold the asset, and asset and payment legs settle with deterministic finality. Yet that complete product path is not live today.
The quieter friction is permission maintenance. Citadel can prove a credential without exposing its details, but each service still chooses trusted issuers and decides whether a session has expired or been revoked. Settlement persists; access may need renewal, making participation—and switching—more costly over time.
Should €300M be read as institutional commitment, or as future demand proven only once assets are issued, traded, and settled?
13
8
115
·
--
#dusk $DUSK @Dusk_Foundation
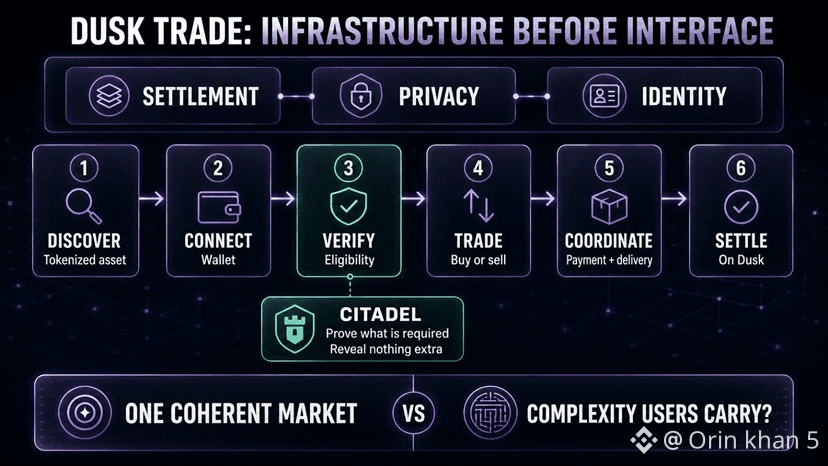
Most blockchains build the trading screen first and worry about market plumbing later. Dusk seems to be reversing that order. Dusk Trade is being built after the settlement, privacy, and identity layers beneath it, turning them into a user-facing path: discover a tokenized asset, connect a wallet, complete eligibility checks, buy or sell, coordinate payment with asset delivery, then settle. Citadel can support selective disclosure, letting an investor prove a required attribute without exposing everything else. 🔍
I find that sequencing unusually honest. Regulated assets need more than a token and a buy button, and bringing the whole workflow together could make the infrastructure genuinely usable.
But every extra checkpoint can also feel like friction. Wallet binding, credentials, permissions, and controlled transfers may protect the market while making ordinary users wonder why trading needs so many gates. 🧐
Will @DuskFoundation make Dusk Trade feel like one coherent market, or will its careful infrastructure become complexity users have to carry?
#dusk $DUSK @Dusk
Most blockchains build the trading screen first and worry about market plumbing later. Dusk seems to be reversing that order. Dusk Trade is being built after the settlement, privacy, and identity layers beneath it, turning them into a user-facing path: discover a tokenized asset, connect a wallet, complete eligibility checks, buy or sell, coordinate payment with asset delivery, then settle. Citadel can support selective disclosure, letting an investor prove a required attribute without exposing everything else. 🔍
I find that sequencing unusually honest. Regulated assets need more than a token and a buy button, and bringing the whole workflow together could make the infrastructure genuinely usable.
But every extra checkpoint can also feel like friction. Wallet binding, credentials, permissions, and controlled transfers may protect the market while making ordinary users wonder why trading needs so many gates. 🧐
Will @DuskFoundation make Dusk Trade feel like one coherent market, or will its careful infrastructure become complexity users have to carry?
Most blockchains build the trading screen first and worry about market plumbing later. Dusk seems to be reversing that order. Dusk Trade is being built after the settlement, privacy, and identity layers beneath it, turning them into a user-facing path: discover a tokenized asset, connect a wallet, complete eligibility checks, buy or sell, coordinate payment with asset delivery, then settle. Citadel can support selective disclosure, letting an investor prove a required attribute without exposing everything else. 🔍
I find that sequencing unusually honest. Regulated assets need more than a token and a buy button, and bringing the whole workflow together could make the infrastructure genuinely usable.
But every extra checkpoint can also feel like friction. Wallet binding, credentials, permissions, and controlled transfers may protect the market while making ordinary users wonder why trading needs so many gates. 🧐
Will @DuskFoundation make Dusk Trade feel like one coherent market, or will its careful infrastructure become complexity users have to carry?
5
5
86
·
--
#baby $BABY @babylonlabs_io
I've been paying attention to a choice that feels almost backward in crypto: Babylon is defining the limits of native Bitcoin finance before proving how large the market can become. Most protocols begin with liquidity, incentives, and product expansion, then tighten the risk model after users arrive. Babylon is starting with the boundaries.
In its Trustless Bitcoin Vault design, BTC stays inside a Taproot output on Bitcoin, while every legitimate spending path is constructed and signed before activation. A vault is also tied to one application and cannot later be moved elsewhere. That sounds restrictive. It is—and that may be the point.
Native Bitcoin finance needs rules before scale.
The current Aave v4 integration still runs on Bitcoin Signet and Ethereum Sepolia, so the architecture has not yet been tested with meaningful capital. But the order matters: custody limits, liquidation paths, recovery options, and application isolation are being defined before the market is asked to trust them.
What I do not know yet is whether users will accept this restraint once faster, more composable alternatives compete for attention. Babylon may be showing that the first product in native Bitcoin finance is not lending or yield. It is credible limitation.
#baby $BABY @BabylonLabs_io
I've been paying attention to a choice that feels almost backward in crypto: Babylon is defining the limits of native Bitcoin finance before proving how large the market can become. Most protocols begin with liquidity, incentives, and product expansion, then tighten the risk model after users arrive. Babylon is starting with the boundaries.
In its Trustless Bitcoin Vault design, BTC stays inside a Taproot output on Bitcoin, while every legitimate spending path is constructed and signed before activation. A vault is also tied to one application and cannot later be moved elsewhere. That sounds restrictive. It is—and that may be the point.
Native Bitcoin finance needs rules before scale.
The current Aave v4 integration still runs on Bitcoin Signet and Ethereum Sepolia, so the architecture has not yet been tested with meaningful capital. But the order matters: custody limits, liquidation paths, recovery options, and application isolation are being defined before the market is asked to trust them.
What I do not know yet is whether users will accept this restraint once faster, more composable alternatives compete for attention. Babylon may be showing that the first product in native Bitcoin finance is not lending or yield. It is credible limitation.
I've been paying attention to a choice that feels almost backward in crypto: Babylon is defining the limits of native Bitcoin finance before proving how large the market can become. Most protocols begin with liquidity, incentives, and product expansion, then tighten the risk model after users arrive. Babylon is starting with the boundaries.
In its Trustless Bitcoin Vault design, BTC stays inside a Taproot output on Bitcoin, while every legitimate spending path is constructed and signed before activation. A vault is also tied to one application and cannot later be moved elsewhere. That sounds restrictive. It is—and that may be the point.
Native Bitcoin finance needs rules before scale.
The current Aave v4 integration still runs on Bitcoin Signet and Ethereum Sepolia, so the architecture has not yet been tested with meaningful capital. But the order matters: custody limits, liquidation paths, recovery options, and application isolation are being defined before the market is asked to trust them.
What I do not know yet is whether users will accept this restraint once faster, more composable alternatives compete for attention. Babylon may be showing that the first product in native Bitcoin finance is not lending or yield. It is credible limitation.
1
115
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
CryptoSelloffTriggersMultipleWhaleLiquidations
Просмотров: 169,455
1,728 обсуждают
Crypto Liquidations Top $2B in 24 Hours as 329,000 Traders Are Wiped Out
Binance News
·Лайков: 39
·Просмотров: 52.4k
USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
Просмотров: 153,290
1,522 обсуждают
WillFOMCMinutesReinforceRateHikeExpectations?
Просмотров: 44,325
718 обсуждают