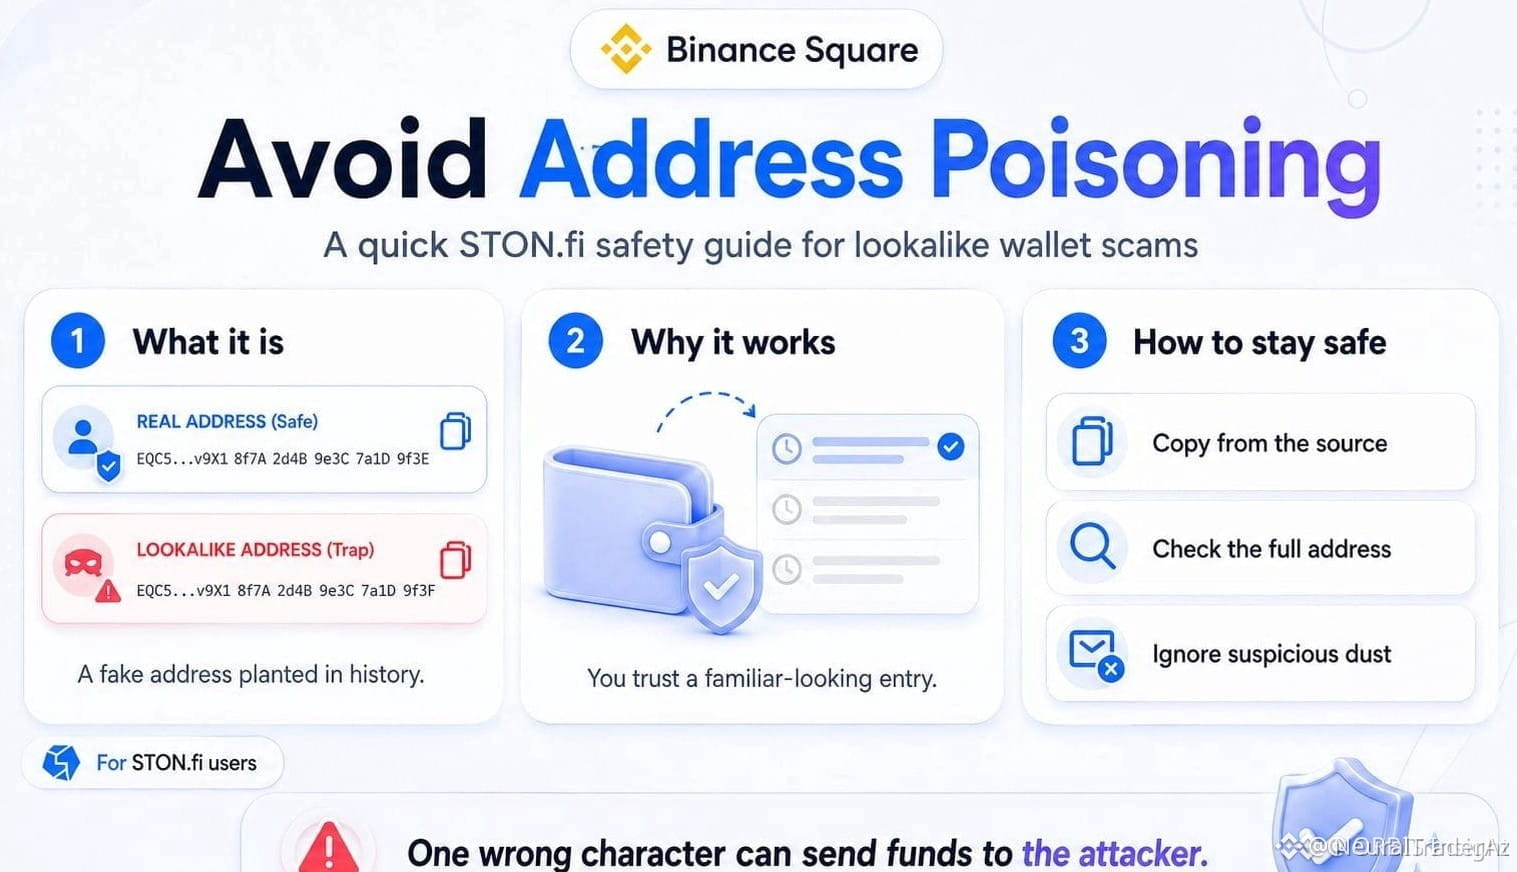
🚨 ADDRESS POISONING THREAT TARGETING $GRAM TRADERS THROUGH TRANSACTION DUST POOLS 🔍
Malicious actors are actively exploiting transaction history logs via address poisoning around $GRAM liquidity channels. 🔍 By broadcasting zero-value dust transactions from vanity wallets sharing matching prefixes and suffixes, scammers embed spoofed vectors directly into user activity logs.
This operational exploit bypasses smart contract security entirely, relying on user oversight when copying legacy addresses. 📊 Safeguard capital by verifying full middle-string checksums from source wallets and isolating unverified incoming tokens immediately. 💡
💬 Have you audited your recent transaction history for spoofed wallet vectors today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #GRAM #CryptoSecurity #DeFi #Web3 #SecurityAlert
🛡️ 🔍