
#security
security
Просмотров: 2M
6,058 обсуждают
Популярные
Новые
·
--
Рост
⚠️ CẢNH BÁO BẢO MẬT
Một lỗ hổng (worse_query) ảnh hưởng đến iOS 26.7.1, 27.0.1 và 27.2 cho phép các ứng dụng độc hại đọc dữ liệu được lưu trên máy của các ứng dụng khác. Điều này khiến seed phrase, private key và thông tin đăng nhập có nguy cơ bị lộ trên toàn hệ sinh thái.
👉 Đây là lỗi ở cấp độ hệ điều hành iOS, không chỉ riêng Binance.
Cần làm ngay:
• Xóa các ứng dụng được cài từ nguồn không đáng tin cậy (ví dụ ứng dụng cài ngoài App Store, file IPA tự ký).
• Cập nhật iOS và tất cả ứng dụng lên phiên bản chính thức mới nhất.
• Nếu nghi ngờ đã bị xâm nhập, hãy chuyển tài sản sang một ví mới được tạo trên thiết bị sạch, và đăng xuất toàn bộ các phiên đăng nhập đang hoạt động.
Tuyệt đối không cài các gói phần mềm không rõ nguồn gốc, và luôn cập nhật phần mềm thường xuyên. 🙏
#Warning #security
$BTC
⚠️ CẢNH BÁO BẢO MẬT
Một lỗ hổng (worse_query) ảnh hưởng đến iOS 26.7.1, 27.0.1 và 27.2 cho phép các ứng dụng độc hại đọc dữ liệu được lưu trên máy của các ứng dụng khác. Điều này khiến seed phrase, private key và thông tin đăng nhập có nguy cơ bị lộ trên toàn hệ sinh thái.
👉 Đây là lỗi ở cấp độ hệ điều hành iOS, không chỉ riêng Binance.
Cần làm ngay:
• Xóa các ứng dụng được cài từ nguồn không đáng tin cậy (ví dụ ứng dụng cài ngoài App Store, file IPA tự ký).
• Cập nhật iOS và tất cả ứng dụng lên phiên bản chính thức mới nhất.
• Nếu nghi ngờ đã bị xâm nhập, hãy chuyển tài sản sang một ví mới được tạo trên thiết bị sạch, và đăng xuất toàn bộ các phiên đăng nhập đang hoạt động.
Tuyệt đối không cài các gói phần mềm không rõ nguồn gốc, và luôn cập nhật phần mềm thường xuyên. 🙏
#Warning #security
$BTC
Một lỗ hổng (worse_query) ảnh hưởng đến iOS 26.7.1, 27.0.1 và 27.2 cho phép các ứng dụng độc hại đọc dữ liệu được lưu trên máy của các ứng dụng khác. Điều này khiến seed phrase, private key và thông tin đăng nhập có nguy cơ bị lộ trên toàn hệ sinh thái.
👉 Đây là lỗi ở cấp độ hệ điều hành iOS, không chỉ riêng Binance.
Cần làm ngay:
• Xóa các ứng dụng được cài từ nguồn không đáng tin cậy (ví dụ ứng dụng cài ngoài App Store, file IPA tự ký).
• Cập nhật iOS và tất cả ứng dụng lên phiên bản chính thức mới nhất.
• Nếu nghi ngờ đã bị xâm nhập, hãy chuyển tài sản sang một ví mới được tạo trên thiết bị sạch, và đăng xuất toàn bộ các phiên đăng nhập đang hoạt động.
Tuyệt đối không cài các gói phần mềm không rõ nguồn gốc, và luôn cập nhật phần mềm thường xuyên. 🙏
#Warning #security
$BTC
2
1.4k

·
--
💎 Đáng chú ý bảo mật: Initia tổn thất hàng triệu USD sau sự cố bị tấn công!
Vào ngày 9/11 vừa qua, một lỗ hổng trong quyền truy cập đám mây đã tạo điều kiện cho hacker xâm nhập hệ thống Initia, từ đó thực hiện các lệnh rút tiền giả mạo từ 5 Rollup.
📊 Thống kê thiệt hại cụ thể:
- Tổng giá trị tài sản bị di chuyển: khoảng 3,27 triệu USD.
- Số tiền hiện đang bị kẹt tại L1: ~2,16 triệu USD.
- Các tài sản đã bị rút ra ngoài bao gồm: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC.
💡 Góc nhìn từ sự cố:
1. Lỗ hổng hạ tầng cloud tiếp tục là "gót chân Achilles" đối với các dự án Web3.
2. Việc đội ngũ cam kết bồi thường toàn bộ thiệt hại là động thái quan trọng để duy trì niềm tin từ cộng đồng.
3. Việc nâng cấp xác thực IBC cho thấy yêu cầu cấp thiết về an ninh trong kết nối đa chuỗi.
Về tình hình hiện tại, Initia đang tiến hành thiết lập lại toàn bộ hạ tầng trong môi trường cách ly. Thời điểm chính thức khởi động lại mạng lưới vẫn chưa được tiết lộ.
👉 Phía sau bản tin — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain $TRX
💎 Đáng chú ý bảo mật: Initia tổn thất hàng triệu USD sau sự cố bị tấn công!
Vào ngày 9/11 vừa qua, một lỗ hổng trong quyền truy cập đám mây đã tạo điều kiện cho hacker xâm nhập hệ thống Initia, từ đó thực hiện các lệnh rút tiền giả mạo từ 5 Rollup.
📊 Thống kê thiệt hại cụ thể:
- Tổng giá trị tài sản bị di chuyển: khoảng 3,27 triệu USD.
- Số tiền hiện đang bị kẹt tại L1: ~2,16 triệu USD.
- Các tài sản đã bị rút ra ngoài bao gồm: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC.
💡 Góc nhìn từ sự cố:
1. Lỗ hổng hạ tầng cloud tiếp tục là "gót chân Achilles" đối với các dự án Web3.
2. Việc đội ngũ cam kết bồi thường toàn bộ thiệt hại là động thái quan trọng để duy trì niềm tin từ cộng đồng.
3. Việc nâng cấp xác thực IBC cho thấy yêu cầu cấp thiết về an ninh trong kết nối đa chuỗi.
Về tình hình hiện tại, Initia đang tiến hành thiết lập lại toàn bộ hạ tầng trong môi trường cách ly. Thời điểm chính thức khởi động lại mạng lưới vẫn chưa được tiết lộ.
👉 Phía sau bản tin — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain $TRX
Vào ngày 9/11 vừa qua, một lỗ hổng trong quyền truy cập đám mây đã tạo điều kiện cho hacker xâm nhập hệ thống Initia, từ đó thực hiện các lệnh rút tiền giả mạo từ 5 Rollup.
📊 Thống kê thiệt hại cụ thể:
- Tổng giá trị tài sản bị di chuyển: khoảng 3,27 triệu USD.
- Số tiền hiện đang bị kẹt tại L1: ~2,16 triệu USD.
- Các tài sản đã bị rút ra ngoài bao gồm: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC.
💡 Góc nhìn từ sự cố:
1. Lỗ hổng hạ tầng cloud tiếp tục là "gót chân Achilles" đối với các dự án Web3.
2. Việc đội ngũ cam kết bồi thường toàn bộ thiệt hại là động thái quan trọng để duy trì niềm tin từ cộng đồng.
3. Việc nâng cấp xác thực IBC cho thấy yêu cầu cấp thiết về an ninh trong kết nối đa chuỗi.
Về tình hình hiện tại, Initia đang tiến hành thiết lập lại toàn bộ hạ tầng trong môi trường cách ly. Thời điểm chính thức khởi động lại mạng lưới vẫn chưa được tiết lộ.
👉 Phía sau bản tin — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain $TRX
4
🔍 Phân tích: Initia bị tấn công, thiệt hại hàng triệu đô la!
Một lỗ hổng về quyền truy cập đám mây đã khiến Initia bị xâm nhập vào ngày 9/11, dẫn đến việc kẻ tấn công giả mạo lệnh rút tiền từ 5 Rollup.
*Chi tiết thiệt hại:*
💰 Tổng tài sản bị chuyển đi: ~3,27 triệu USD
🔒 Tài sản bị kẹt trên L1: ~2,16 triệu USD
💸 Tài sản bị rút ra ngoài: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC
*Tại sao quan trọng?*
🔹 Bảo mật hạ tầng đám mây vẫn là điểm yếu chí tử của nhiều dự án Web3.
🔹 Cam kết bù đắp toàn bộ tổn thất cho thấy nỗ lực giữ uy tín của đội ngũ phát triển.
🔹 Việc thắt chặt xác thực IBC cho thấy xu hướng tăng cường an ninh đa chuỗi.
Hiện tại, Initia đang tái thiết lập hạ tầng trong môi trường cách ly và chưa công bố thời gian khởi động lại mạng lưới.
👉 Follow Kênh hoặc để lại bình luận trao đổi nhé mọi người! — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain. $TRX
🔍 Phân tích: Initia bị tấn công, thiệt hại hàng triệu đô la!
Một lỗ hổng về quyền truy cập đám mây đã khiến Initia bị xâm nhập vào ngày 9/11, dẫn đến việc kẻ tấn công giả mạo lệnh rút tiền từ 5 Rollup.
*Chi tiết thiệt hại:*
💰 Tổng tài sản bị chuyển đi: ~3,27 triệu USD
🔒 Tài sản bị kẹt trên L1: ~2,16 triệu USD
💸 Tài sản bị rút ra ngoài: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC
*Tại sao quan trọng?*
🔹 Bảo mật hạ tầng đám mây vẫn là điểm yếu chí tử của nhiều dự án Web3.
🔹 Cam kết bù đắp toàn bộ tổn thất cho thấy nỗ lực giữ uy tín của đội ngũ phát triển.
🔹 Việc thắt chặt xác thực IBC cho thấy xu hướng tăng cường an ninh đa chuỗi.
Hiện tại, Initia đang tái thiết lập hạ tầng trong môi trường cách ly và chưa công bố thời gian khởi động lại mạng lưới.
👉 Follow Kênh hoặc để lại bình luận trao đổi nhé mọi người! — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain. $TRX
Một lỗ hổng về quyền truy cập đám mây đã khiến Initia bị xâm nhập vào ngày 9/11, dẫn đến việc kẻ tấn công giả mạo lệnh rút tiền từ 5 Rollup.
*Chi tiết thiệt hại:*
💰 Tổng tài sản bị chuyển đi: ~3,27 triệu USD
🔒 Tài sản bị kẹt trên L1: ~2,16 triệu USD
💸 Tài sản bị rút ra ngoài: 13.400 TIA, 8.000 USDC.inj và 597.000 Noble USDC
*Tại sao quan trọng?*
🔹 Bảo mật hạ tầng đám mây vẫn là điểm yếu chí tử của nhiều dự án Web3.
🔹 Cam kết bù đắp toàn bộ tổn thất cho thấy nỗ lực giữ uy tín của đội ngũ phát triển.
🔹 Việc thắt chặt xác thực IBC cho thấy xu hướng tăng cường an ninh đa chuỗi.
Hiện tại, Initia đang tái thiết lập hạ tầng trong môi trường cách ly và chưa công bố thời gian khởi động lại mạng lưới.
👉 Follow Kênh hoặc để lại bình luận trao đổi nhé mọi người! — Follow Kênh https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en&r=BOZMO8A1
#Initia #Security #CryptoNews #Blockchain. $TRX
5

·
--
Initia's second hack in 18 days started with one leaked cloud key, not a smart-contract bug.
Per Initia's own post-mortem (via Cointelegraph):
1. Entry: a compromised Google Cloud key for provisioning private nodes, used in a command injection on Nov 9. That exposed its GitHub and cloud accounts.
2. Reach: the attacker got into Anvil, the rollup-hosting platform, and validated forged IBC withdrawals from five rollups.
3. Damage: about $3.27M moved to the attacker, $2.16M still frozen on the halted L1. No INIT was withdrawn.
The Oct 23 exploit (about $2.7M) was a MoveVM script cache flaw, so this is a different failure class. My read: audits cover code, but a leaked credential walks around them. A restart means rebuilding infrastructure in isolation, with no date given, and Initia says it intends to restore affected assets in full.
Which matters more when you size up a chain: code audits or key management? $INIT $TIA
#Initia #Security #Hacks
Disclosure: I can earn Binance Write to Earn rewards from this post.
Initia's second hack in 18 days started with one leaked cloud key, not a smart-contract bug.
Per Initia's own post-mortem (via Cointelegraph):
1. Entry: a compromised Google Cloud key for provisioning private nodes, used in a command injection on Nov 9. That exposed its GitHub and cloud accounts.
2. Reach: the attacker got into Anvil, the rollup-hosting platform, and validated forged IBC withdrawals from five rollups.
3. Damage: about $3.27M moved to the attacker, $2.16M still frozen on the halted L1. No INIT was withdrawn.
The Oct 23 exploit (about $2.7M) was a MoveVM script cache flaw, so this is a different failure class. My read: audits cover code, but a leaked credential walks around them. A restart means rebuilding infrastructure in isolation, with no date given, and Initia says it intends to restore affected assets in full.
Which matters more when you size up a chain: code audits or key management? $INIT $TIA
#Initia #Security #Hacks
Disclosure: I can earn Binance Write to Earn rewards from this post.
Per Initia's own post-mortem (via Cointelegraph):
1. Entry: a compromised Google Cloud key for provisioning private nodes, used in a command injection on Nov 9. That exposed its GitHub and cloud accounts.
2. Reach: the attacker got into Anvil, the rollup-hosting platform, and validated forged IBC withdrawals from five rollups.
3. Damage: about $3.27M moved to the attacker, $2.16M still frozen on the halted L1. No INIT was withdrawn.
The Oct 23 exploit (about $2.7M) was a MoveVM script cache flaw, so this is a different failure class. My read: audits cover code, but a leaked credential walks around them. A restart means rebuilding infrastructure in isolation, with no date given, and Initia says it intends to restore affected assets in full.
Which matters more when you size up a chain: code audits or key management? $INIT $TIA
#Initia #Security #Hacks
Disclosure: I can earn Binance Write to Earn rewards from this post.
3
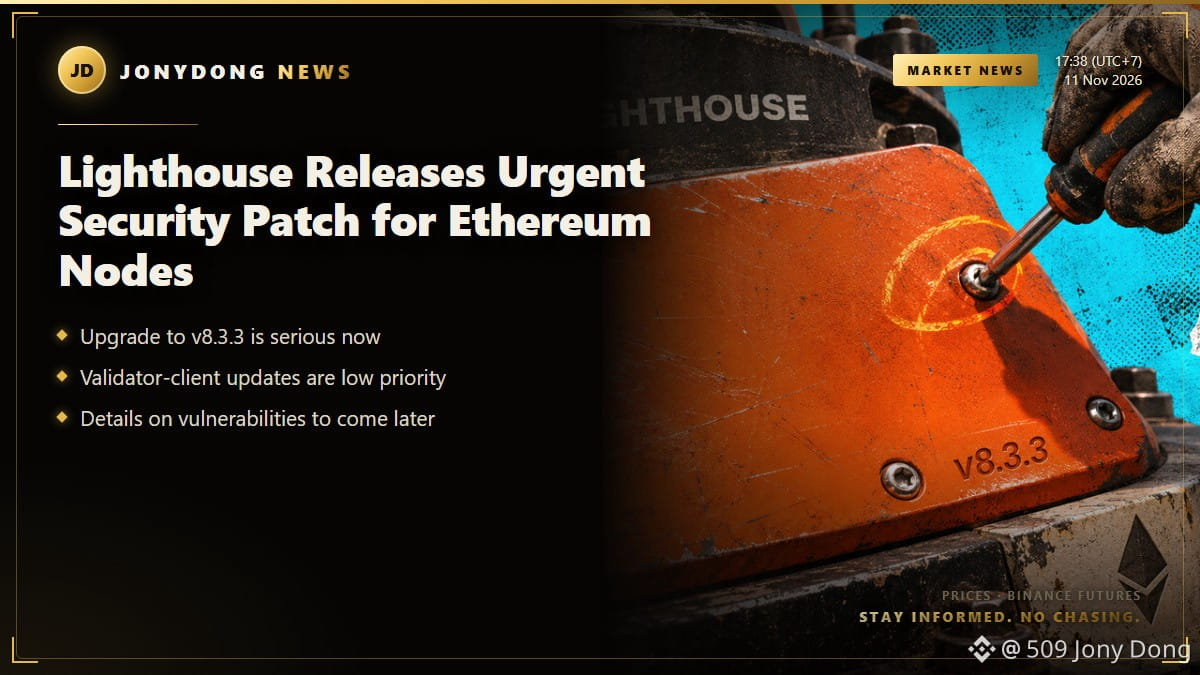
This patch is a must for Lighthouse users. Ignoring it could lead to issues down the line.
Lighthouse Releases Urgent Security Patch for Ethereum Nodes
On November 9, Ethereum consensus client Lighthouse issued a security patch, urging all operators of its beacon nodes to upgrade immediately. The release, v8.3.3, emphasizes the urgency for both staking and non-staking users, although it rates validator-client upgrades as low priority for those who stake.
Lighthouse connects with other clients in Ethereum's proof-of-stake network, validating transactions through its beacon node. Even operators running a beacon node without a validator client are instructed to prioritize this upgrade. The patch introduces no breaking changes, but users upgrading from earlier versions should check the release notes of v8.3.0 for additional considerations.
While the release does not report any active exploitation or losses, it shows that technical details of the vulnerabilities will be disclosed later. The high-priority label indicates that operators should act quickly, as these upgrades are expected to be completed within hours or days. The specifics of the vulnerabilities remain undisclosed, leaving some uncertainty around the implications.
This situation shows the importance of staying updated with security patches in the crypto space. The lack of immediate exploitation does not diminish the need for vigilance, as unpatched vulnerabilities can lead to serious issues for operators.
#Security #Ethereum #CryptoNews
This patch is a must for Lighthouse users. Ignoring it could lead to issues down the line.
Lighthouse Releases Urgent Security Patch for Ethereum Nodes
On November 9, Ethereum consensus client Lighthouse issued a security patch, urging all operators of its beacon nodes to upgrade immediately. The release, v8.3.3, emphasizes the urgency for both staking and non-staking users, although it rates validator-client upgrades as low priority for those who stake.
Lighthouse connects with other clients in Ethereum's proof-of-stake network, validating transactions through its beacon node. Even operators running a beacon node without a validator client are instructed to prioritize this upgrade. The patch introduces no breaking changes, but users upgrading from earlier versions should check the release notes of v8.3.0 for additional considerations.
While the release does not report any active exploitation or losses, it shows that technical details of the vulnerabilities will be disclosed later. The high-priority label indicates that operators should act quickly, as these upgrades are expected to be completed within hours or days. The specifics of the vulnerabilities remain undisclosed, leaving some uncertainty around the implications.
This situation shows the importance of staying updated with security patches in the crypto space. The lack of immediate exploitation does not diminish the need for vigilance, as unpatched vulnerabilities can lead to serious issues for operators.
#Security #Ethereum #CryptoNews
Lighthouse Releases Urgent Security Patch for Ethereum Nodes
On November 9, Ethereum consensus client Lighthouse issued a security patch, urging all operators of its beacon nodes to upgrade immediately. The release, v8.3.3, emphasizes the urgency for both staking and non-staking users, although it rates validator-client upgrades as low priority for those who stake.
Lighthouse connects with other clients in Ethereum's proof-of-stake network, validating transactions through its beacon node. Even operators running a beacon node without a validator client are instructed to prioritize this upgrade. The patch introduces no breaking changes, but users upgrading from earlier versions should check the release notes of v8.3.0 for additional considerations.
While the release does not report any active exploitation or losses, it shows that technical details of the vulnerabilities will be disclosed later. The high-priority label indicates that operators should act quickly, as these upgrades are expected to be completed within hours or days. The specifics of the vulnerabilities remain undisclosed, leaving some uncertainty around the implications.
This situation shows the importance of staying updated with security patches in the crypto space. The lack of immediate exploitation does not diminish the need for vigilance, as unpatched vulnerabilities can lead to serious issues for operators.
#Security #Ethereum #CryptoNews
121
·
--
Initia三周内再遭黑客攻击,$3.27M被盗暴露云凭证短板
加密项目安全再次敲响警钟。据Cointelegraph报道,Initia确认这是其三周内第二次遭遇黑客攻击,最新一次攻击中约$3.27M加密资产被盗,其中约$2.16M已被转移。
从事件性质看,这次攻击与首次有所不同。据项目方披露,攻击者利用的是被泄露的云凭证(cloud credentials)完成入侵。这意味着问题不再局限于智能合约代码层面的漏洞,而是指向了底层基础设施托管的薄弱环节——当云账户凭证一旦泄露,攻击者可能绕过协议本身直接触碰资产。
为什么这一细节值得警惕。过去几年DeFi的多次重大被盗事件,多数源于合约逻辑被利用或审计遗漏,而本次指向的是运维侧的托管基础设施。换句话说,即便协议代码再严谨,只要团队依赖的云服务凭证管理出现疏漏,资产安全仍可能被击穿。这或将反映整个行业在托管体系上存在的系统性短板,而非单一项目的偶然失误。
从数据看,本次被盗$3.27M、转移$2.16M,金额相对可控,且项目能在短时间内确认并披露,响应速度尚可。反方因素在于:这一规模在DeFi被盗案例中属于较小级别,或可视为针对性攻击而非系统性风险的全面爆发,市场不必过度放大其冲击。
市场可能如何反应。对Initia而言,重复被盗大概率压制短期情绪与代币表现,投资者对其安全治理的信任需要时间修复;对更广泛的DeFi板块,则可能引发对托管安全标准的重新审视,资金或倾向于向安全记录更清晰的项目集中。
接下来观察什么。需要关注项目方后续的安全整改方案,尤其是云凭证的管理机制是否升级;同时观察被盗资金流向与追回可能性,以及市场情绪能否在短期披露后企稳。
#Initia #DeFi #Security
以上为信息整理与个人分析,不构成投资建议。
后续如有重要进展,我会继续跟踪更新。
Initia三周内再遭黑客攻击,$3.27M被盗暴露云凭证短板
加密项目安全再次敲响警钟。据Cointelegraph报道,Initia确认这是其三周内第二次遭遇黑客攻击,最新一次攻击中约$3.27M加密资产被盗,其中约$2.16M已被转移。
从事件性质看,这次攻击与首次有所不同。据项目方披露,攻击者利用的是被泄露的云凭证(cloud credentials)完成入侵。这意味着问题不再局限于智能合约代码层面的漏洞,而是指向了底层基础设施托管的薄弱环节——当云账户凭证一旦泄露,攻击者可能绕过协议本身直接触碰资产。
为什么这一细节值得警惕。过去几年DeFi的多次重大被盗事件,多数源于合约逻辑被利用或审计遗漏,而本次指向的是运维侧的托管基础设施。换句话说,即便协议代码再严谨,只要团队依赖的云服务凭证管理出现疏漏,资产安全仍可能被击穿。这或将反映整个行业在托管体系上存在的系统性短板,而非单一项目的偶然失误。
从数据看,本次被盗$3.27M、转移$2.16M,金额相对可控,且项目能在短时间内确认并披露,响应速度尚可。反方因素在于:这一规模在DeFi被盗案例中属于较小级别,或可视为针对性攻击而非系统性风险的全面爆发,市场不必过度放大其冲击。
市场可能如何反应。对Initia而言,重复被盗大概率压制短期情绪与代币表现,投资者对其安全治理的信任需要时间修复;对更广泛的DeFi板块,则可能引发对托管安全标准的重新审视,资金或倾向于向安全记录更清晰的项目集中。
接下来观察什么。需要关注项目方后续的安全整改方案,尤其是云凭证的管理机制是否升级;同时观察被盗资金流向与追回可能性,以及市场情绪能否在短期披露后企稳。
#Initia #DeFi #Security
以上为信息整理与个人分析,不构成投资建议。
后续如有重要进展,我会继续跟踪更新。
加密项目安全再次敲响警钟。据Cointelegraph报道,Initia确认这是其三周内第二次遭遇黑客攻击,最新一次攻击中约$3.27M加密资产被盗,其中约$2.16M已被转移。
从事件性质看,这次攻击与首次有所不同。据项目方披露,攻击者利用的是被泄露的云凭证(cloud credentials)完成入侵。这意味着问题不再局限于智能合约代码层面的漏洞,而是指向了底层基础设施托管的薄弱环节——当云账户凭证一旦泄露,攻击者可能绕过协议本身直接触碰资产。
为什么这一细节值得警惕。过去几年DeFi的多次重大被盗事件,多数源于合约逻辑被利用或审计遗漏,而本次指向的是运维侧的托管基础设施。换句话说,即便协议代码再严谨,只要团队依赖的云服务凭证管理出现疏漏,资产安全仍可能被击穿。这或将反映整个行业在托管体系上存在的系统性短板,而非单一项目的偶然失误。
从数据看,本次被盗$3.27M、转移$2.16M,金额相对可控,且项目能在短时间内确认并披露,响应速度尚可。反方因素在于:这一规模在DeFi被盗案例中属于较小级别,或可视为针对性攻击而非系统性风险的全面爆发,市场不必过度放大其冲击。
市场可能如何反应。对Initia而言,重复被盗大概率压制短期情绪与代币表现,投资者对其安全治理的信任需要时间修复;对更广泛的DeFi板块,则可能引发对托管安全标准的重新审视,资金或倾向于向安全记录更清晰的项目集中。
接下来观察什么。需要关注项目方后续的安全整改方案,尤其是云凭证的管理机制是否升级;同时观察被盗资金流向与追回可能性,以及市场情绪能否在短期披露后企稳。
#Initia #DeFi #Security
以上为信息整理与个人分析,不构成投资建议。
后续如有重要进展,我会继续跟踪更新。
359
·
--
Across's contracts were never touched, yet users still got drained.
Three questions about the $ACX bridge incident:
Q: Was the bridge hacked?
Not in the smart-contract sense. At about 18:45 UTC on Nov 10, an attacker used social engineering on the registrar Namecheap, took over across.to and swapped in a phishing page. Across says it was alerted within 15 minutes.
Q: How much was lost?
GoPlus estimates roughly $350,000 across six chains, including Ethereum, Base and BNB Chain. Across hasn't confirmed a figure but says affected users "will be made whole," with a post-mortem to come.
Q: What should bridge users take from it?
My view: the weak link was the front door, not the vault. Any Permit or approval signature deserves a second look, and wallets that touched the site on Nov 10 should review approvals.
Which hurts DeFi trust more: a contract bug or a hijacked domain? $ETH bridging runs through these sites daily.
Sources: Cointelegraph, crypto.news. #DeFi #Security
Disclosure: Write to Earn may pay me a commission on cashtag trades.
Across's contracts were never touched, yet users still got drained.
Three questions about the $ACX bridge incident:
Q: Was the bridge hacked?
Not in the smart-contract sense. At about 18:45 UTC on Nov 10, an attacker used social engineering on the registrar Namecheap, took over across.to and swapped in a phishing page. Across says it was alerted within 15 minutes.
Q: How much was lost?
GoPlus estimates roughly $350,000 across six chains, including Ethereum, Base and BNB Chain. Across hasn't confirmed a figure but says affected users "will be made whole," with a post-mortem to come.
Q: What should bridge users take from it?
My view: the weak link was the front door, not the vault. Any Permit or approval signature deserves a second look, and wallets that touched the site on Nov 10 should review approvals.
Which hurts DeFi trust more: a contract bug or a hijacked domain? $ETH bridging runs through these sites daily.
Sources: Cointelegraph, crypto.news. #DeFi #Security
Disclosure: Write to Earn may pay me a commission on cashtag trades.
Three questions about the $ACX bridge incident:
Q: Was the bridge hacked?
Not in the smart-contract sense. At about 18:45 UTC on Nov 10, an attacker used social engineering on the registrar Namecheap, took over across.to and swapped in a phishing page. Across says it was alerted within 15 minutes.
Q: How much was lost?
GoPlus estimates roughly $350,000 across six chains, including Ethereum, Base and BNB Chain. Across hasn't confirmed a figure but says affected users "will be made whole," with a post-mortem to come.
Q: What should bridge users take from it?
My view: the weak link was the front door, not the vault. Any Permit or approval signature deserves a second look, and wallets that touched the site on Nov 10 should review approvals.
Which hurts DeFi trust more: a contract bug or a hijacked domain? $ETH bridging runs through these sites daily.
Sources: Cointelegraph, crypto.news. #DeFi #Security
Disclosure: Write to Earn may pay me a commission on cashtag trades.
·
--
Across Protocol网站被黑客劫持了!通过社交工程攻击针对域名注册商Namecheap,黑客把用户引到了钓鱼网站。跨链桥安全再次敲响警钟,小伙伴们要小心钓鱼链接啊!#crypto #security $ACROSS
Across Protocol website got hijacked by hackers! Through social engineering attack on domain registrar Namecheap, users were redirected to a phishing site. Another security wake-up call for cross-chain bridges. Be careful with those links! #crypto #security $ACROSS
Across Protocol网站被黑客劫持了!通过社交工程攻击针对域名注册商Namecheap,黑客把用户引到了钓鱼网站。跨链桥安全再次敲响警钟,小伙伴们要小心钓鱼链接啊!#crypto #security $ACROSS
Across Protocol website got hijacked by hackers! Through social engineering attack on domain registrar Namecheap, users were redirected to a phishing site. Another security wake-up call for cross-chain bridges. Be careful with those links! #crypto #security $ACROSS
Across Protocol website got hijacked by hackers! Through social engineering attack on domain registrar Namecheap, users were redirected to a phishing site. Another security wake-up call for cross-chain bridges. Be careful with those links! #crypto #security $ACROSS

Статья
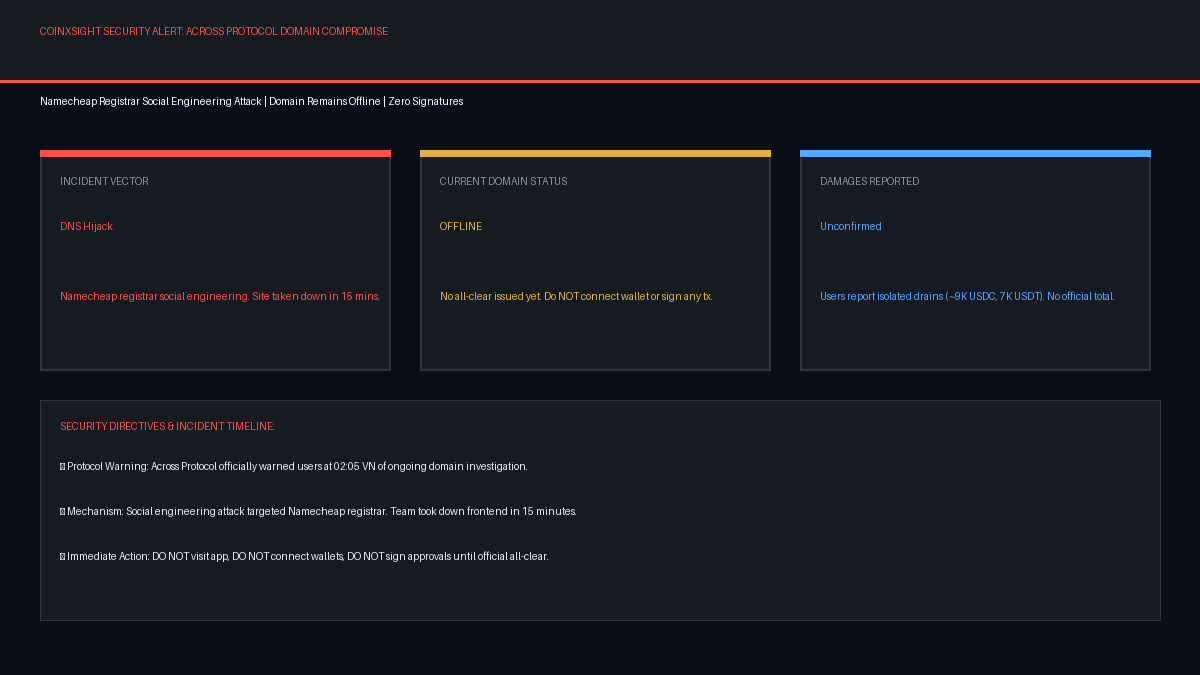
Across Protocol Issues Urgent Security Warning: Domain Offline After Namecheap Registrar Attack🚨 **ACROSS PROTOCOL SECURITY ALERT: DOMAIN HIJACK INVESTIGATION — DO NOT INTERACT OR SIGN TRANSACTIONS**
Leading cross-chain bridge Across Protocol issued an urgent official warning alerting the community to an ongoing frontend domain compromise resulting from a registrar-level social engineering attack:
---
### 1. OFFICIAL PROTOCOL STATUS & TIMELINE
- **Initial Warning:** Across Protocol confirmed an active domain security investigation, instructing users to immediately avoid accessing the web application.
- **Attack Vector:** Subsequent team updates confirmed that attackers executed a social engineering attack against domain registrar **Namecheap**.
- **Mitigation Response:** The Across core team acted to take down the affected frontend within 15 minutes of detection to minimize exposure.
- **Current State:** The domain remains **OFFLINE**. No official all-clear has been declared.
---
### 2. DAMAGES & IMPACT ASSESSMENT
- **Community Reports:** Isolated user reports indicate potential losses (including unconfirmed mentions of 9,000 USDC and ~7,053 USDT).
- **Official Verification:** Across Protocol has **not confirmed any total stolen figure** at this stage. Smart contract logic and bridge pools remain under review as the investigation proceeds. A formal post-mortem will be published once registrar control is fully restored.
---
### 3. MANDATORY SECURITY DIRECTIVES FOR ALL USERS
1. ❌ **DO NOT** visit or open any Across Protocol web domains or mirrored frontends.
2. ❌ **DO NOT** connect Web3 wallets or permit session approvals.
3. ❌ **DO NOT** sign any transactions, permit signatures, or contract interactions.
4. 🔍 **Verify Approvals:** If you interacted with the frontend during the compromise window, check and revoke outstanding token allowances via verified revocation tools immediately.
---
💡 **COINXSIGHT QUANTITATIVE SECURITY VERDICT:**
Frontend and DNS registrar attacks remain a persistent systemic vulnerability for DeFi protocols. Users are advised to rely strictly on official protocol communication channels and wait for a verified cryptographic all-clear before resuming bridge activity.
🔗 **Real-time Orderbook Telemetry & Security Radar:** [coinxsight.com](https://app.coinxsight.com/whale-flow)
#Security #DeFi #Crypto
Across Protocol Issues Urgent Security Warning: Domain Offline After Namecheap Registrar Attack
🚨 **ACROSS PROTOCOL SECURITY ALERT: DOMAIN HIJACK INVESTIGATION — DO NOT INTERACT OR SIGN TRANSACTIONS**
Leading cross-chain bridge Across Protocol issued an urgent official warning alerting the community to an ongoing frontend domain compromise resulting from a registrar-level social engineering attack:
---
### 1. OFFICIAL PROTOCOL STATUS & TIMELINE
- **Initial Warning:** Across Protocol confirmed an active domain security investigation, instructing users to immediately avoid accessing the web application.
- **Attack Vector:** Subsequent team updates confirmed that attackers executed a social engineering attack against domain registrar **Namecheap**.
- **Mitigation Response:** The Across core team acted to take down the affected frontend within 15 minutes of detection to minimize exposure.
- **Current State:** The domain remains **OFFLINE**. No official all-clear has been declared.
---
### 2. DAMAGES & IMPACT ASSESSMENT
- **Community Reports:** Isolated user reports indicate potential losses (including unconfirmed mentions of 9,000 USDC and ~7,053 USDT).
- **Official Verification:** Across Protocol has **not confirmed any total stolen figure** at this stage. Smart contract logic and bridge pools remain under review as the investigation proceeds. A formal post-mortem will be published once registrar control is fully restored.
---
### 3. MANDATORY SECURITY DIRECTIVES FOR ALL USERS
1. ❌ **DO NOT** visit or open any Across Protocol web domains or mirrored frontends.
2. ❌ **DO NOT** connect Web3 wallets or permit session approvals.
3. ❌ **DO NOT** sign any transactions, permit signatures, or contract interactions.
4. 🔍 **Verify Approvals:** If you interacted with the frontend during the compromise window, check and revoke outstanding token allowances via verified revocation tools immediately.
---
💡 **COINXSIGHT QUANTITATIVE SECURITY VERDICT:**
Frontend and DNS registrar attacks remain a persistent systemic vulnerability for DeFi protocols. Users are advised to rely strictly on official protocol communication channels and wait for a verified cryptographic all-clear before resuming bridge activity.
🔗 **Real-time Orderbook Telemetry & Security Radar:** [coinxsight.com](https://app.coinxsight.com/whale-flow)
#Security #DeFi #Crypto
Leading cross-chain bridge Across Protocol issued an urgent official warning alerting the community to an ongoing frontend domain compromise resulting from a registrar-level social engineering attack:
---
### 1. OFFICIAL PROTOCOL STATUS & TIMELINE
- **Initial Warning:** Across Protocol confirmed an active domain security investigation, instructing users to immediately avoid accessing the web application.
- **Attack Vector:** Subsequent team updates confirmed that attackers executed a social engineering attack against domain registrar **Namecheap**.
- **Mitigation Response:** The Across core team acted to take down the affected frontend within 15 minutes of detection to minimize exposure.
- **Current State:** The domain remains **OFFLINE**. No official all-clear has been declared.
---
### 2. DAMAGES & IMPACT ASSESSMENT
- **Community Reports:** Isolated user reports indicate potential losses (including unconfirmed mentions of 9,000 USDC and ~7,053 USDT).
- **Official Verification:** Across Protocol has **not confirmed any total stolen figure** at this stage. Smart contract logic and bridge pools remain under review as the investigation proceeds. A formal post-mortem will be published once registrar control is fully restored.
---
### 3. MANDATORY SECURITY DIRECTIVES FOR ALL USERS
1. ❌ **DO NOT** visit or open any Across Protocol web domains or mirrored frontends.
2. ❌ **DO NOT** connect Web3 wallets or permit session approvals.
3. ❌ **DO NOT** sign any transactions, permit signatures, or contract interactions.
4. 🔍 **Verify Approvals:** If you interacted with the frontend during the compromise window, check and revoke outstanding token allowances via verified revocation tools immediately.
---
💡 **COINXSIGHT QUANTITATIVE SECURITY VERDICT:**
Frontend and DNS registrar attacks remain a persistent systemic vulnerability for DeFi protocols. Users are advised to rely strictly on official protocol communication channels and wait for a verified cryptographic all-clear before resuming bridge activity.
🔗 **Real-time Orderbook Telemetry & Security Radar:** [coinxsight.com](https://app.coinxsight.com/whale-flow)
#Security #DeFi #Crypto
71
Binance Warns iPhone Users to Update iOS Immediately
Binance has issued a warning for iPhone users on iOS 26.7.1, 27.0.1 and 27.2.
A flaw in these versions could expose seed phrases and private keys.
Users are advised to update their iPhone to the latest iOS version right now and avoid entering seed phrases on any app until updated.
Security first. Update before you trade.
$BTC $BNB $ETH
#write2earn #binance #iphone #security #crypto
Binance Warns iPhone Users to Update iOS Immediately
Binance has issued a warning for iPhone users on iOS 26.7.1, 27.0.1 and 27.2.
A flaw in these versions could expose seed phrases and private keys.
Users are advised to update their iPhone to the latest iOS version right now and avoid entering seed phrases on any app until updated.
Security first. Update before you trade.
$BTC $BNB $ETH
#write2earn #binance #iphone #security #crypto
Binance has issued a warning for iPhone users on iOS 26.7.1, 27.0.1 and 27.2.
A flaw in these versions could expose seed phrases and private keys.
Users are advised to update their iPhone to the latest iOS version right now and avoid entering seed phrases on any app until updated.
Security first. Update before you trade.
$BTC $BNB $ETH
#write2earn #binance #iphone #security #crypto
77
·
--
🚨 LNbits Emergency Patch — $BTC Wallets Under Threat?
🚨 **LNbits rushes emergency patch after Bitcoin wallet thefts – is your $BTC safe?**
A wave of reported $BTC wallet breaches forced LNbits to deploy an emergency code fix within hours. The scramble highlights a growing exploitation vector in third‑party payment layers.
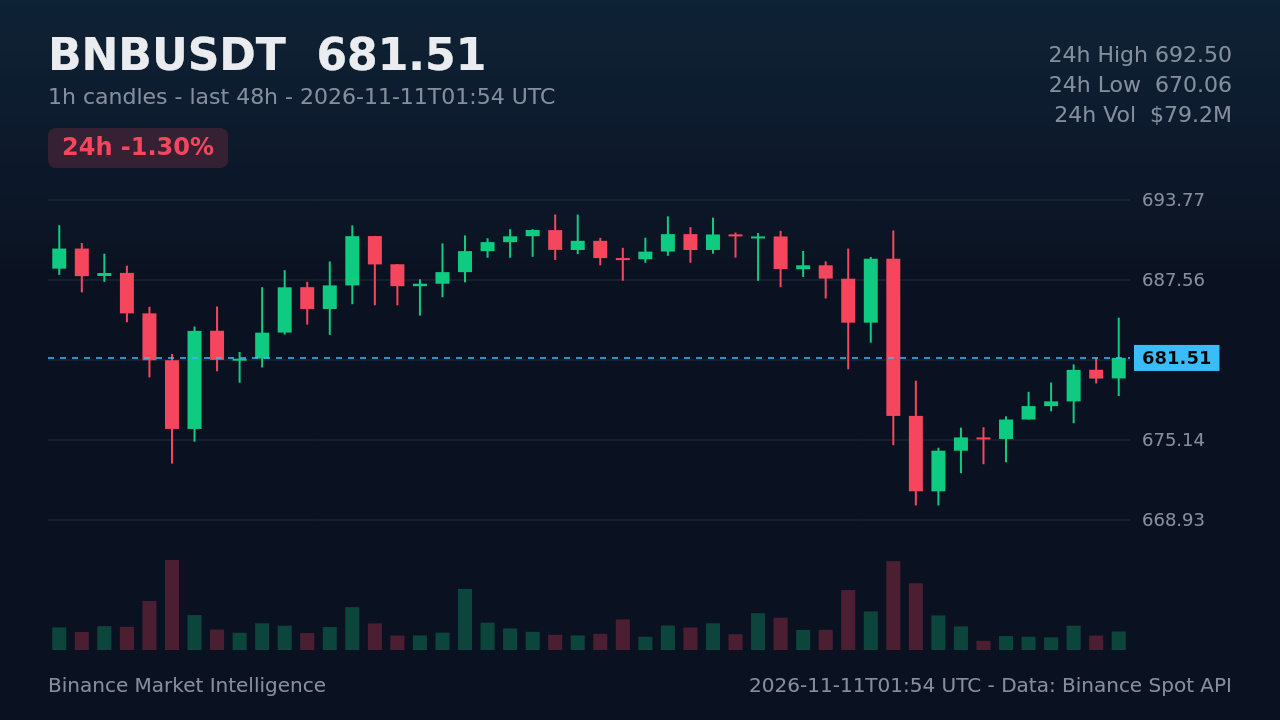
• 📉 $BTC slides ~‑1.8% to $73,695 – testing $73,200 support.
• 📉 $ETH drags 3.3% to $2,056, pressure on $2,000 psychological floor.
• ⚠️ LNbits patch could calm panic, but short‑term sell‑off may persist.
• 🎯 Key $BTC levels: $73,200 (support), $74,500 (resistance).
• 💡 Watch $BTC volume – 1.27B USD, still robust, indicating institutional hands.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Bitcoin
🚨 LNbits Emergency Patch — $BTC Wallets Under Threat?
🚨 **LNbits rushes emergency patch after Bitcoin wallet thefts – is your $BTC safe?**
A wave of reported $BTC wallet breaches forced LNbits to deploy an emergency code fix within hours. The scramble highlights a growing exploitation vector in third‑party payment layers.
• 📉 $BTC slides ~‑1.8% to $73,695 – testing $73,200 support.
• 📉 $ETH drags 3.3% to $2,056, pressure on $2,000 psychological floor.
• ⚠️ LNbits patch could calm panic, but short‑term sell‑off may persist.
• 🎯 Key $BTC levels: $73,200 (support), $74,500 (resistance).
• 💡 Watch $BTC volume – 1.27B USD, still robust, indicating institutional hands.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Bitcoin
🚨 **LNbits rushes emergency patch after Bitcoin wallet thefts – is your $BTC safe?**
A wave of reported $BTC wallet breaches forced LNbits to deploy an emergency code fix within hours. The scramble highlights a growing exploitation vector in third‑party payment layers.
• 📉 $BTC slides ~‑1.8% to $73,695 – testing $73,200 support.
• 📉 $ETH drags 3.3% to $2,056, pressure on $2,000 psychological floor.
• ⚠️ LNbits patch could calm panic, but short‑term sell‑off may persist.
• 🎯 Key $BTC levels: $73,200 (support), $74,500 (resistance).
• 💡 Watch $BTC volume – 1.27B USD, still robust, indicating institutional hands.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH #Crypto #Security #Bitcoin
55
This is a wake-up call for LNbits users. If you haven't updated, do it now.
LNbits Releases Security Update After Fund Drain Attacks
LNbits, the open-source Lightning Network wallet, released an urgent security update, version 1.7.0, on November 10. This update comes after a series of attacks that began on November 8, during which unauthorized account creation and fund withdrawals were reported. Users were instructed to halt their LNbits servers immediately to prevent further losses.
The attacks reportedly drained approximately 2,285,545 satoshis (about 0.0229 BTC) from a service that operates on LNbits. The project has emphasized that all operators must upgrade before restarting their servers, as earlier versions are vulnerable to exploitation. The new version includes essential security fixes and enhancements across various operational areas.
For those who suspect their servers may have been compromised, LNbits advises setting up a fresh server and rotating all user wallet keys. Additionally, they recommend reviewing connections for any extensions and replacing funding-source credentials to ensure security.
This incident shows the importance of maintaining up-to-date software in the crypto space. As LNbits functions as a hot wallet, operators should only keep necessary balances online and regularly monitor activities to protect their funds.
#Security #LightningNetwork #CryptoNews
This is a wake-up call for LNbits users. If you haven't updated, do it now.
LNbits Releases Security Update After Fund Drain Attacks
LNbits, the open-source Lightning Network wallet, released an urgent security update, version 1.7.0, on November 10. This update comes after a series of attacks that began on November 8, during which unauthorized account creation and fund withdrawals were reported. Users were instructed to halt their LNbits servers immediately to prevent further losses.
The attacks reportedly drained approximately 2,285,545 satoshis (about 0.0229 BTC) from a service that operates on LNbits. The project has emphasized that all operators must upgrade before restarting their servers, as earlier versions are vulnerable to exploitation. The new version includes essential security fixes and enhancements across various operational areas.
For those who suspect their servers may have been compromised, LNbits advises setting up a fresh server and rotating all user wallet keys. Additionally, they recommend reviewing connections for any extensions and replacing funding-source credentials to ensure security.
This incident shows the importance of maintaining up-to-date software in the crypto space. As LNbits functions as a hot wallet, operators should only keep necessary balances online and regularly monitor activities to protect their funds.
#Security #LightningNetwork #CryptoNews
LNbits Releases Security Update After Fund Drain Attacks
LNbits, the open-source Lightning Network wallet, released an urgent security update, version 1.7.0, on November 10. This update comes after a series of attacks that began on November 8, during which unauthorized account creation and fund withdrawals were reported. Users were instructed to halt their LNbits servers immediately to prevent further losses.
The attacks reportedly drained approximately 2,285,545 satoshis (about 0.0229 BTC) from a service that operates on LNbits. The project has emphasized that all operators must upgrade before restarting their servers, as earlier versions are vulnerable to exploitation. The new version includes essential security fixes and enhancements across various operational areas.
For those who suspect their servers may have been compromised, LNbits advises setting up a fresh server and rotating all user wallet keys. Additionally, they recommend reviewing connections for any extensions and replacing funding-source credentials to ensure security.
This incident shows the importance of maintaining up-to-date software in the crypto space. As LNbits functions as a hot wallet, operators should only keep necessary balances online and regularly monitor activities to protect their funds.
#Security #LightningNetwork #CryptoNews
349

🚨 $ACROSS DOMAIN COMPROMISE EXPOSES FRONTEND VULNERABILITIES ACROSS CROSSCHAIN BRIDGES ⚠️
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
🚨 $ACROSS DOMAIN COMPROMISE EXPOSES FRONTEND VULNERABILITIES ACROSS CROSSCHAIN BRIDGES ⚠️
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
1

·
--
🚨 CRITICAL FRONTEND ALERT ON $ACROSS : KEEP YOUR WALLETS LOCKED DOWN RIGHT NOW! ⚠️
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
🚨 CRITICAL FRONTEND ALERT ON $ACROSS : KEEP YOUR WALLETS LOCKED DOWN RIGHT NOW! ⚠️
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
12


·
--
🚨 Across Protocol warns users to stay away from its app as wallet-drain reports surface
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
🚨 Across Protocol warns users to stay away from its app as wallet-drain reports surface
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
94
⚠️ Across Protocol cảnh báo người dùng tạm dừng dùng app sau loạt báo cáo ví bị rút sạch
Across Protocol vừa lên tiếng cho biết đang điều tra một sự cố bảo mật tiềm ẩn liên quan đến tên miền của giao thức. Đội ngũ khuyến cáo người dùng tránh truy cập và tương tác với ứng dụng cho đến khi có thông báo mới.
Theo dữ liệu ban đầu, một số người dùng cho biết đã mất tiền sau khi tương tác với nền tảng. Hiện chưa có thông tin về quy mô thiệt hại, nguyên nhân cụ thể hay số lượng ví bị ảnh hưởng, nên mọi con số lan truyền lúc này cần được kiểm chứng thêm.
Với trader, đây là lời nhắc quen thuộc: khi tên miền hoặc giao diện web bị tấn công, rủi ro thường nằm ở việc ký giao dịch hoặc cấp quyền (approve) qua một giao diện đã bị can thiệp, dù hợp đồng thông minh có thể vẫn an toàn. Trong lúc chờ cập nhật chính thức, ai đã dùng app gần đây nên kiểm tra lại các quyền approve của ví và hạn chế ký giao dịch lạ. Đây là nhận định chung, chưa phải kết luận từ đội ngũ Across.
Bạn có hay kiểm tra và thu hồi quyền approve của ví định kỳ không, hay chỉ làm khi có sự cố?
#hoangducinvest #Crypto #DeFi #Security
Nguồn: Cointelegraph
(Không phải lời khuyên đầu tư)
⚠️ Across Protocol cảnh báo người dùng tạm dừng dùng app sau loạt báo cáo ví bị rút sạch
Across Protocol vừa lên tiếng cho biết đang điều tra một sự cố bảo mật tiềm ẩn liên quan đến tên miền của giao thức. Đội ngũ khuyến cáo người dùng tránh truy cập và tương tác với ứng dụng cho đến khi có thông báo mới.
Theo dữ liệu ban đầu, một số người dùng cho biết đã mất tiền sau khi tương tác với nền tảng. Hiện chưa có thông tin về quy mô thiệt hại, nguyên nhân cụ thể hay số lượng ví bị ảnh hưởng, nên mọi con số lan truyền lúc này cần được kiểm chứng thêm.
Với trader, đây là lời nhắc quen thuộc: khi tên miền hoặc giao diện web bị tấn công, rủi ro thường nằm ở việc ký giao dịch hoặc cấp quyền (approve) qua một giao diện đã bị can thiệp, dù hợp đồng thông minh có thể vẫn an toàn. Trong lúc chờ cập nhật chính thức, ai đã dùng app gần đây nên kiểm tra lại các quyền approve của ví và hạn chế ký giao dịch lạ. Đây là nhận định chung, chưa phải kết luận từ đội ngũ Across.
Bạn có hay kiểm tra và thu hồi quyền approve của ví định kỳ không, hay chỉ làm khi có sự cố?
#hoangducinvest #Crypto #DeFi #Security
Nguồn: Cointelegraph
(Không phải lời khuyên đầu tư)
Across Protocol vừa lên tiếng cho biết đang điều tra một sự cố bảo mật tiềm ẩn liên quan đến tên miền của giao thức. Đội ngũ khuyến cáo người dùng tránh truy cập và tương tác với ứng dụng cho đến khi có thông báo mới.
Theo dữ liệu ban đầu, một số người dùng cho biết đã mất tiền sau khi tương tác với nền tảng. Hiện chưa có thông tin về quy mô thiệt hại, nguyên nhân cụ thể hay số lượng ví bị ảnh hưởng, nên mọi con số lan truyền lúc này cần được kiểm chứng thêm.
Với trader, đây là lời nhắc quen thuộc: khi tên miền hoặc giao diện web bị tấn công, rủi ro thường nằm ở việc ký giao dịch hoặc cấp quyền (approve) qua một giao diện đã bị can thiệp, dù hợp đồng thông minh có thể vẫn an toàn. Trong lúc chờ cập nhật chính thức, ai đã dùng app gần đây nên kiểm tra lại các quyền approve của ví và hạn chế ký giao dịch lạ. Đây là nhận định chung, chưa phải kết luận từ đội ngũ Across.
Bạn có hay kiểm tra và thu hồi quyền approve của ví định kỳ không, hay chỉ làm khi có sự cố?
#hoangducinvest #Crypto #DeFi #Security
Nguồn: Cointelegraph
(Không phải lời khuyên đầu tư)
22
🔓 Near AI bị xâm nhập: lộ thông tin người dùng và dữ liệu của 18 AI agent
Một lỗ hổng trong SGLang đã cho phép kẻ tấn công truy cập vào hệ thống nội bộ của Near AI. Theo Decrypt, hậu quả là thông tin người dùng cùng dữ liệu từ 18 AI agent bị lộ.
Đáng chú ý hơn, kẻ tấn công có khả năng xem được các yêu cầu AI mang tính bảo mật. Vụ việc cho thấy giới hạn của các lớp bảo vệ quyền riêng tư dựa trên phần cứng: dù hệ thống được thiết kế để giữ kín dữ liệu, một lỗ hổng ở tầng phần mềm vẫn có thể mở đường vào bên trong.
Với trader, đây là lời nhắc rằng mảng AI x crypto vẫn còn nhiều rủi ro về bảo mật. Những dự án quảng bá "AI riêng tư" cần được kiểm chứng kỹ hơn trước khi người dùng tin tưởng giao dữ liệu hay chiến lược của mình. Hiện dữ liệu chưa nêu rõ quy mô thiệt hại cụ thể, nên cần theo dõi thêm thông báo chính thức từ phía dự án.
Bạn có tin các giải pháp AI "bảo mật bằng phần cứng" đủ an toàn để dùng cho dữ liệu nhạy cảm không?
(Không phải lời khuyên đầu tư)
#hoangducinvest #AI #Crypto #Security
Nguồn: Decrypt
🔓 Near AI bị xâm nhập: lộ thông tin người dùng và dữ liệu của 18 AI agent
Một lỗ hổng trong SGLang đã cho phép kẻ tấn công truy cập vào hệ thống nội bộ của Near AI. Theo Decrypt, hậu quả là thông tin người dùng cùng dữ liệu từ 18 AI agent bị lộ.
Đáng chú ý hơn, kẻ tấn công có khả năng xem được các yêu cầu AI mang tính bảo mật. Vụ việc cho thấy giới hạn của các lớp bảo vệ quyền riêng tư dựa trên phần cứng: dù hệ thống được thiết kế để giữ kín dữ liệu, một lỗ hổng ở tầng phần mềm vẫn có thể mở đường vào bên trong.
Với trader, đây là lời nhắc rằng mảng AI x crypto vẫn còn nhiều rủi ro về bảo mật. Những dự án quảng bá "AI riêng tư" cần được kiểm chứng kỹ hơn trước khi người dùng tin tưởng giao dữ liệu hay chiến lược của mình. Hiện dữ liệu chưa nêu rõ quy mô thiệt hại cụ thể, nên cần theo dõi thêm thông báo chính thức từ phía dự án.
Bạn có tin các giải pháp AI "bảo mật bằng phần cứng" đủ an toàn để dùng cho dữ liệu nhạy cảm không?
(Không phải lời khuyên đầu tư)
#hoangducinvest #AI #Crypto #Security
Nguồn: Decrypt
Một lỗ hổng trong SGLang đã cho phép kẻ tấn công truy cập vào hệ thống nội bộ của Near AI. Theo Decrypt, hậu quả là thông tin người dùng cùng dữ liệu từ 18 AI agent bị lộ.
Đáng chú ý hơn, kẻ tấn công có khả năng xem được các yêu cầu AI mang tính bảo mật. Vụ việc cho thấy giới hạn của các lớp bảo vệ quyền riêng tư dựa trên phần cứng: dù hệ thống được thiết kế để giữ kín dữ liệu, một lỗ hổng ở tầng phần mềm vẫn có thể mở đường vào bên trong.
Với trader, đây là lời nhắc rằng mảng AI x crypto vẫn còn nhiều rủi ro về bảo mật. Những dự án quảng bá "AI riêng tư" cần được kiểm chứng kỹ hơn trước khi người dùng tin tưởng giao dữ liệu hay chiến lược của mình. Hiện dữ liệu chưa nêu rõ quy mô thiệt hại cụ thể, nên cần theo dõi thêm thông báo chính thức từ phía dự án.
Bạn có tin các giải pháp AI "bảo mật bằng phần cứng" đủ an toàn để dùng cho dữ liệu nhạy cảm không?
(Không phải lời khuyên đầu tư)
#hoangducinvest #AI #Crypto #Security
Nguồn: Decrypt
1
·
--
🚨 $49M Mercado Bitcoin hack – withdrawals resume, is crypto safe?
🚨 Massive $49M hack hit Mercado Bitcoin – withdrawals are back, but is your crypto safe?
Mercado Bitcoin halted cash outs after a $49 million breach, shaking confidence across Latin America. The platform reopened withdrawals this morning, but users are weighing risk vs. convenience.
• 📊 $BTC steadies around $73,980, testing the $74.5k resistance as fear index stays low (32 Fear).
• 📊 $ETH slides near $2,060, hovering below the $2,080 pivot.
• 📊 $BNB trades at $678, holding the $680 support zone.
• ⚠️ Withdrawal limits lifted, but MFA prompts now mandatory for all accounts.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH $BNB #Crypto #Security #News
🚨 $49M Mercado Bitcoin hack – withdrawals resume, is crypto safe?
🚨 Massive $49M hack hit Mercado Bitcoin – withdrawals are back, but is your crypto safe?
Mercado Bitcoin halted cash outs after a $49 million breach, shaking confidence across Latin America. The platform reopened withdrawals this morning, but users are weighing risk vs. convenience.
• 📊 $BTC steadies around $73,980, testing the $74.5k resistance as fear index stays low (32 Fear).
• 📊 $ETH slides near $2,060, hovering below the $2,080 pivot.
• 📊 $BNB trades at $678, holding the $680 support zone.
• ⚠️ Withdrawal limits lifted, but MFA prompts now mandatory for all accounts.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH $BNB #Crypto #Security #News
🚨 Massive $49M hack hit Mercado Bitcoin – withdrawals are back, but is your crypto safe?
Mercado Bitcoin halted cash outs after a $49 million breach, shaking confidence across Latin America. The platform reopened withdrawals this morning, but users are weighing risk vs. convenience.
• 📊 $BTC steadies around $73,980, testing the $74.5k resistance as fear index stays low (32 Fear).
• 📊 $ETH slides near $2,060, hovering below the $2,080 pivot.
• 📊 $BNB trades at $678, holding the $680 support zone.
• ⚠️ Withdrawal limits lifted, but MFA prompts now mandatory for all accounts.
Bullish long‑term or short‑term noise? Share your thoughts below 👇
$BTC $ETH $BNB #Crypto #Security #News
1
·
--
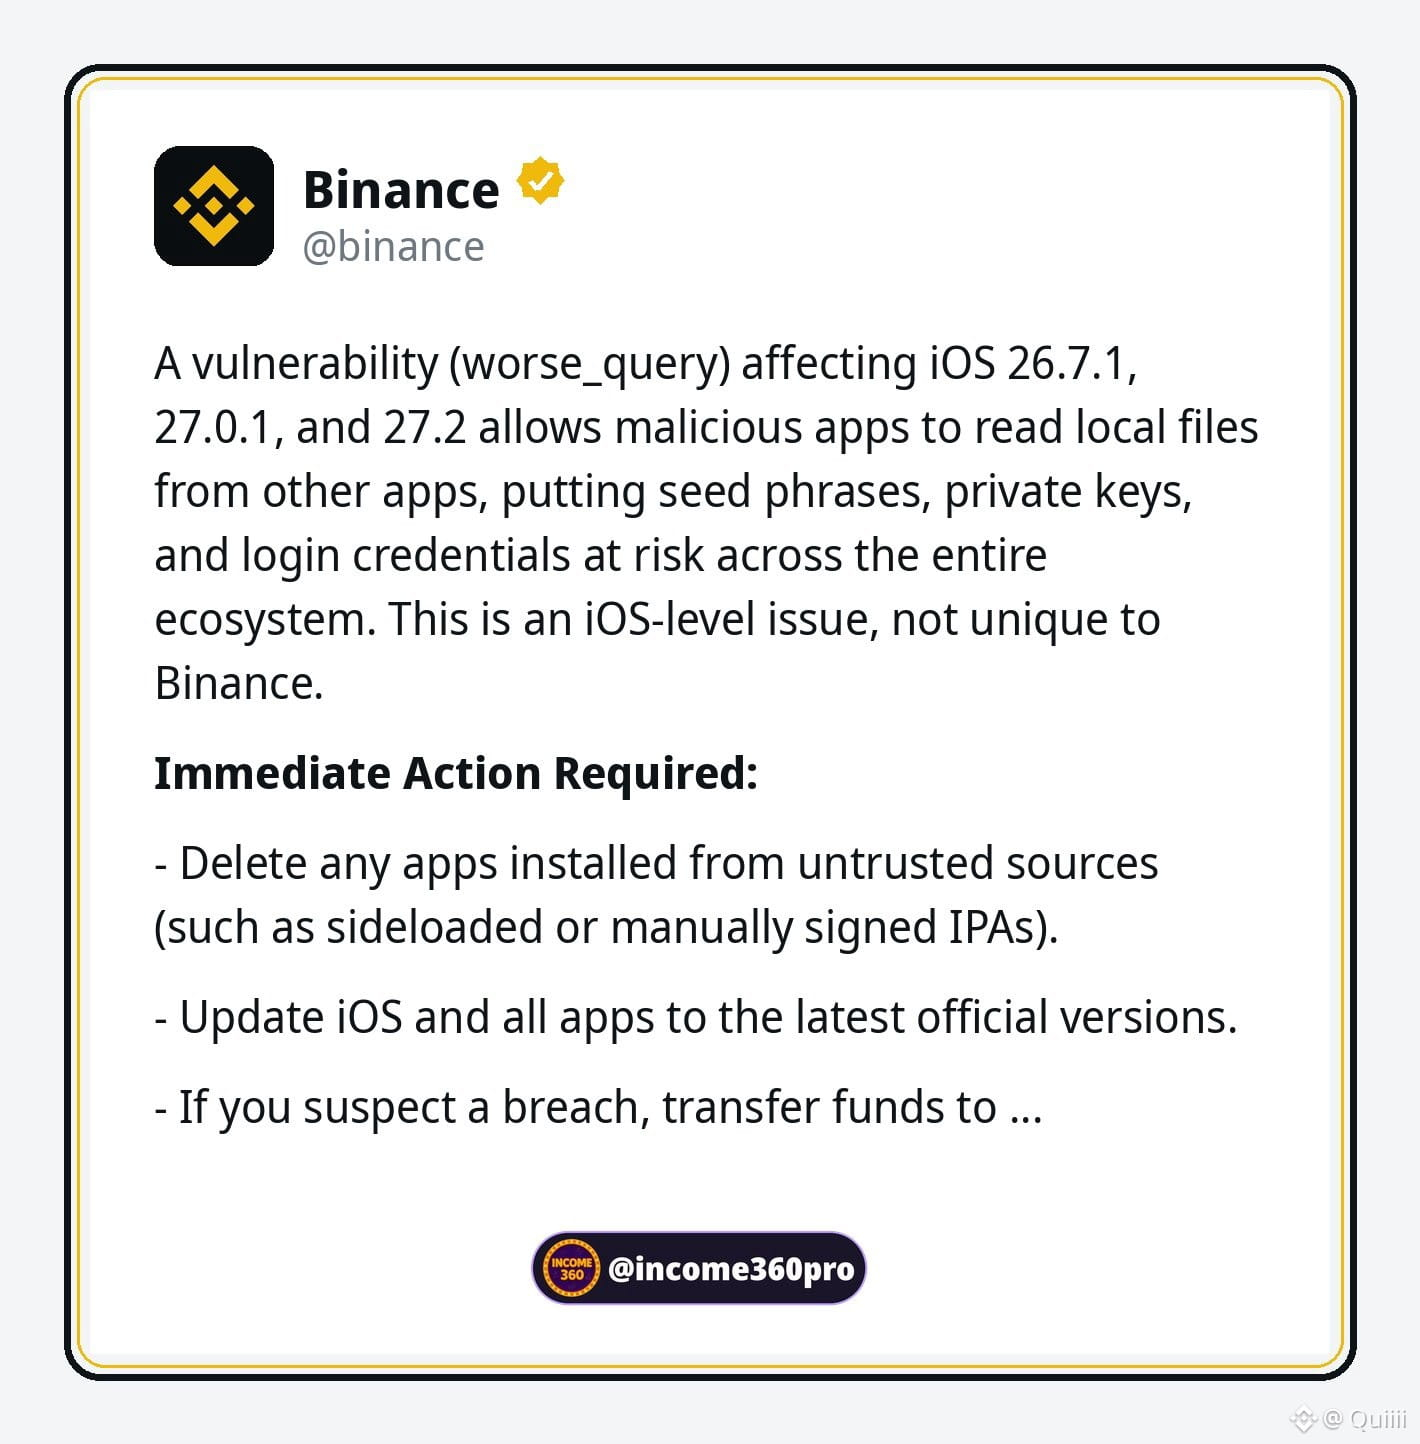
A Silent Bug Can Read Your Seed Phrase ~ Binance Just Warned Every Iphone User
@binance
flagged an iOS-level vulnerability called worse_query - one bad app on your phone can peek into the files of your other apps.
⇨ Affected: iOS 26.7.1, 27.0.1 and 27.2
⇨ Target: Seed phrases, private keys, saved passwords
⇨ Scope: The whole ecosystem - not just Binance
Protect Yourself - Do It Today:
» Delete every app installed from untrusted sources - sideloaded or manually signed IPAs go first
» Update iOS to the latest official version
» Update Chrome on mobile AND PC - it just patched a similar flaw
» Update all your apps
» Done
→ Think You Are Already Hit?
» Move funds to a completely new wallet
» That seed phrase is dead - never touch it again
Forget profits for one day. Today is about protecting what you already have.
Updated already - or still pending? Be honest
#Binance #iOS #Security
A Silent Bug Can Read Your Seed Phrase ~ Binance Just Warned Every Iphone User
@binance
flagged an iOS-level vulnerability called worse_query - one bad app on your phone can peek into the files of your other apps.
⇨ Affected: iOS 26.7.1, 27.0.1 and 27.2
⇨ Target: Seed phrases, private keys, saved passwords
⇨ Scope: The whole ecosystem - not just Binance
Protect Yourself - Do It Today:
» Delete every app installed from untrusted sources - sideloaded or manually signed IPAs go first
» Update iOS to the latest official version
» Update Chrome on mobile AND PC - it just patched a similar flaw
» Update all your apps
» Done
→ Think You Are Already Hit?
» Move funds to a completely new wallet
» That seed phrase is dead - never touch it again
Forget profits for one day. Today is about protecting what you already have.
Updated already - or still pending? Be honest
#Binance #iOS #Security
@binance
flagged an iOS-level vulnerability called worse_query - one bad app on your phone can peek into the files of your other apps.
⇨ Affected: iOS 26.7.1, 27.0.1 and 27.2
⇨ Target: Seed phrases, private keys, saved passwords
⇨ Scope: The whole ecosystem - not just Binance
Protect Yourself - Do It Today:
» Delete every app installed from untrusted sources - sideloaded or manually signed IPAs go first
» Update iOS to the latest official version
» Update Chrome on mobile AND PC - it just patched a similar flaw
» Update all your apps
» Done
→ Think You Are Already Hit?
» Move funds to a completely new wallet
» That seed phrase is dead - never touch it again
Forget profits for one day. Today is about protecting what you already have.
Updated already - or still pending? Be honest
#Binance #iOS #Security
90
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#HotCPIDecemberHikePriced
Просмотров: 173,109
1,877 обсуждают
2
#StrategyFaces$2.8BSelloffRiskFromMSCIRemoval
Просмотров: 2,348
34 обсуждают
3
#AnthropicRejectsIPODelayValuationinQuestion
Просмотров: 276,200
2,345 обсуждают
4
#CanNvidiaEarningsEaseMarketConcerns?
Просмотров: 62,356
831 обсуждают
5
#FSBUrgesTurkeyToEstablishStablecoinFramework
Просмотров: 0
7 обсуждают
6
#StrategyExpectsCommonStockExclusionFromMSCIGlobalIndexes
Просмотров: 0
0 обсуждают
7
#BitcoinFiveWeeklyLosses
Просмотров: 624,802
3,859 обсуждают
8
#XRPLedger2027RoadmapProposesQuantumResistantSignatures
Просмотров: 123
2 обсуждают
9
#SECEnforcementActionsFall24%InFiscal2026
Просмотров: 975
20 обсуждают
10
#JapanFSAStudyGroupDiscussesDeFiRegulation
Просмотров: 2,353
35 обсуждают