

#devops
devops
Просмотров: 1,506
27 обсуждают
Популярные
Новые

·
--
The Illusion of Local Dev Independence
Transitioning from cloud infrastructure to self-hosted local hardware isn't just about saving money; it's a structural pivot toward absolute autonomy.
Relying on paid enterprise servers introduces third-party risk and hidden counterparty liabilities. Local architecture via independent nodes guarantees absolute data privacy.
#SelfHosted #OpenSource #DevOps #TechAutonomy
117
·
--
Статья
ICPay — Protocol Reliability: Zero-Downtime Canister Upgrades and State SafetyPreserving User Account Balances Across Production Motoko Releases
Upgrading smart contracts on live blockchain networks carries severe risk. Incorrect memory deserialization can permanently corrupt contract state and erase user account balances.
ICPay executes upgrades following rigorous Motoko stable memory persistence protocols.
───────────────
Core Technical Architecture & Mechanisms
───────────────
1. Stable Memory Data Structures
Critical user accounts, balances, and transaction indexes reside in Motoko stable variables that survive code updates without serialization bottlenecks.
2. Pre-Upgrade and Post-Upgrade Hooks
Deterministic migration routines validate state consistency before executing WebAssembly module replacement on canister 6vbhm-nqaaa-aaaan-q6muq-cai.
3. Verifiable Rollback Capabilities
The operations toolchain verifies cryptographic wasm hashes before applying upgrades, maintaining deterministic rollback paths if anomalies arise.
$ICP #ICP #DevOps
ICPay — Protocol Reliability: Zero-Downtime Canister Upgrades and State Safety
Preserving User Account Balances Across Production Motoko Releases
Upgrading smart contracts on live blockchain networks carries severe risk. Incorrect memory deserialization can permanently corrupt contract state and erase user account balances.
ICPay executes upgrades following rigorous Motoko stable memory persistence protocols.
───────────────
Core Technical Architecture & Mechanisms
───────────────
1. Stable Memory Data Structures
Critical user accounts, balances, and transaction indexes reside in Motoko stable variables that survive code updates without serialization bottlenecks.
2. Pre-Upgrade and Post-Upgrade Hooks
Deterministic migration routines validate state consistency before executing WebAssembly module replacement on canister 6vbhm-nqaaa-aaaan-q6muq-cai.
3. Verifiable Rollback Capabilities
The operations toolchain verifies cryptographic wasm hashes before applying upgrades, maintaining deterministic rollback paths if anomalies arise.
$ICP #ICP #DevOps
219

·
--
Node Health Beyond UptimeA blockchain node can return a successful response and still be serving stale data. That is why a simple ping is not a production health check.
Start with reachability, but add freshness. Compare the node’s latest block height and timestamp with an independent reference. Watch synchronization status and peer health where those signals are available. A node that is online but several blocks behind can mislead wallets, dashboards, trading systems and indexers.
Measure request behavior too. Track latency percentiles, timeouts, rate-limit responses, JSON-RPC errors and method-specific failures. Separate read calls from transaction submission and subscription workloads because they can fail differently.
For infrastructure you control, monitor CPU, memory, disk capacity, disk latency, network traffic, process restarts and logs. Set alerts that name a condition and an action: sustained block lag, rising error rate, a WebSocket disconnect loop or disk usage approaching the level that threatens the node.
Metrics without ownership become noise. Every alert should have a threshold, severity, runbook and responsible person. The objective is to detect degradation before users become the monitoring system.
TokenToolHub’s guide compares the monitoring layers and tools:
https://tokentoolhub.com/best-blockchain-node-monitoring-tools/
#BlockchainNodes #RPCA #Devops #Web3Infrastructure #CryptoSecurity
Node Health Beyond Uptime
A blockchain node can return a successful response and still be serving stale data. That is why a simple ping is not a production health check.
Start with reachability, but add freshness. Compare the node’s latest block height and timestamp with an independent reference. Watch synchronization status and peer health where those signals are available. A node that is online but several blocks behind can mislead wallets, dashboards, trading systems and indexers.
Measure request behavior too. Track latency percentiles, timeouts, rate-limit responses, JSON-RPC errors and method-specific failures. Separate read calls from transaction submission and subscription workloads because they can fail differently.
For infrastructure you control, monitor CPU, memory, disk capacity, disk latency, network traffic, process restarts and logs. Set alerts that name a condition and an action: sustained block lag, rising error rate, a WebSocket disconnect loop or disk usage approaching the level that threatens the node.
Metrics without ownership become noise. Every alert should have a threshold, severity, runbook and responsible person. The objective is to detect degradation before users become the monitoring system.
TokenToolHub’s guide compares the monitoring layers and tools:
https://tokentoolhub.com/best-blockchain-node-monitoring-tools/
#BlockchainNodes #RPCA #Devops #Web3Infrastructure #CryptoSecurity
75

·
--
🚨 NORTH KOREAN HACKERS UNLEASH NEW TERRAFORM PHISHING VECTOR TARGETING $BTC DEVELOPERS! 💣
📌 Sophisticated threat actor TraderTraitor is actively weaponizing malicious GitHub interview code to infiltrate Web3 infrastructure and hijack AWS credentials. 🔍 Devs downloading unverified repos are triggering stealthy macOS backdoors capable of draining cloud environments and compromised codebases.
⚠️ Institutional security is the real foundation of every $BTC bull run, and these attacks prove threat groups are hunting upstream developer access. 💬 Are you verifying your Terraform dependencies before running init scripts, or leaving your cloud infrastructure exposed? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #DevOps #Web3
🛡️ 🔍
23

🚨 TRADERTRAITOR TARGETS DEV CLOUD KEYS IN PHISHING CAMPAIGN RECALLING $ZRO BACKDOORS! 🔍
Sophisticated state-sponsored actors are shifting vectors from direct smart contract exploits to underlying cloud infrastructure. 🔍 Recent forensics reveal TraderTraitor executing malicious Terraform Provider downloads, deploying macOS backdoors identical to those identified during the historical $ZRO infrastructure breach.
Smart money understands that protocol liquidity is only as secure as the developer API keys backing the ecosystem. 🛡️ With AWS and GCP credentials targeted across DevOps teams, monitoring operational risk is now just as critical as analyzing market structure.
💬 How are you adjusting your operational security protocols to protect your capital against infrastructure-level threats? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ZRO #CryptoSecurity #DevOps #SmartMoney #LayerZero
🛡️ 👁️
65

·
--
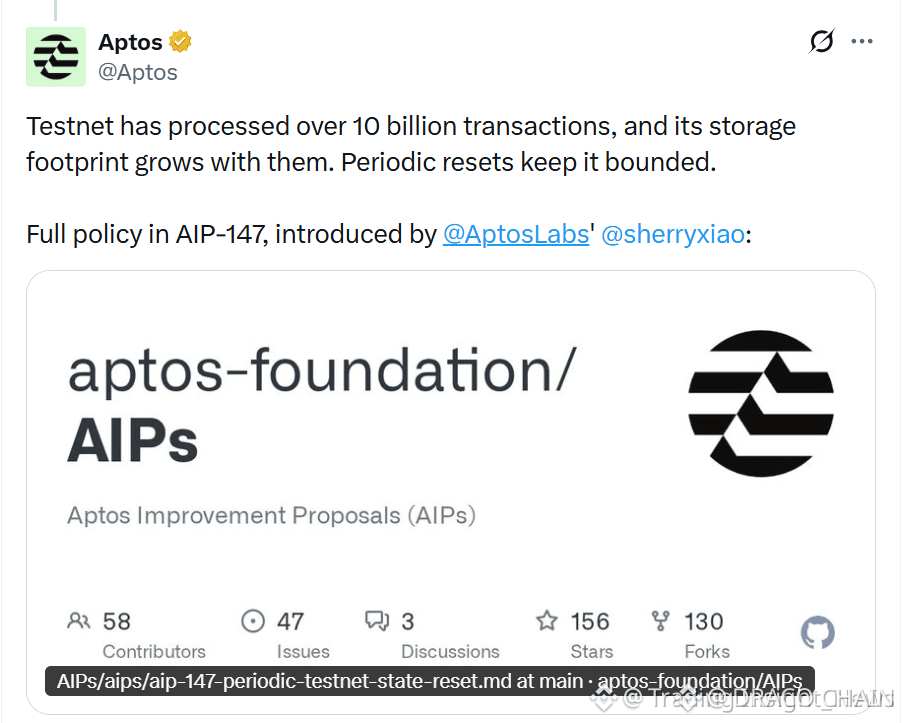
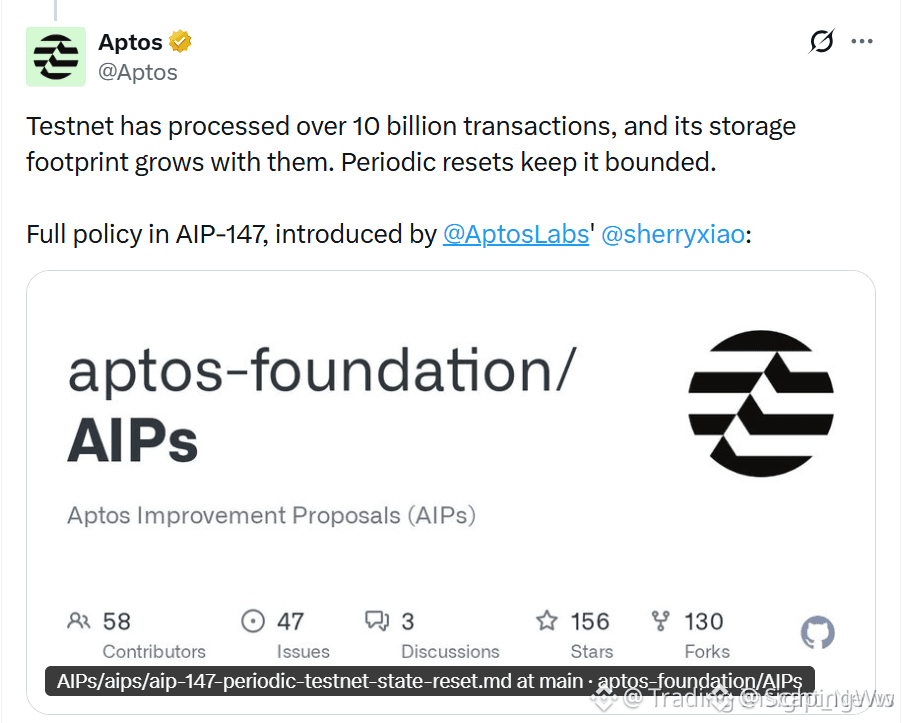
🚨 $APT TESTNET RESET APPROACHES OCT 7 – PREP FOR STORAGE SWEEP 🦈
Aptos is slated to wipe its testnet clean on Oct 7, resetting contracts, balances and transaction history to zero. 📌 This full‑state revert follows more than 10 B transactions, a storage load that threatens cost efficiency.
Smart‑money developers view the purge as a liquidity‑reset for on‑chain storage, clearing stale state and freeing space for fresh deployments. 📊 Expect a brief dip in testnet activity as teams redeploy, but the mainnet stays untouched.
📈 Keep an eye on the post‑reset performance metrics; a leaner testnet often translates into smoother dev cycles and sharper fee signals on the live chain. 💡
💬 How are you adjusting your testnet strategy ahead of the Oct 7 reset?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🦈 🔥
426
·
--
Проверено
🚨 $APT TESTNET RESET SET FOR OCT 7 – STORAGE SWEEP INCOMING! 📊
Aptos is pulling the plug on its testnet on Oct 7, wiping contracts, balances and the entire transaction ledger. 🦈 This clean‑slate move trims storage pressure after crushing 10 B transactions, keeping the network lean for devs.
No ripple hits mainnet or devnet – they stay untouched, so production stays smooth. 📊 Expect a brief pause for redeployment, then a fresh canvas for new experiments. ⚡
💬 How are you prepping your test contracts for the reset? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🚀 🔥
4
1k

⚡ CRITICAL GITHUB INFRASTRUCTURE OUTAGE SHAKES TECH AND $FET AI ECOSYSTEM WORKFLOWS! 🚨
Major core infrastructure is buckling under pressure today as GitHub hits severe database replication lag in its collaboration systems. 📊 With authorization interfaces failing and GitHub Actions stalling across the board, developer pipelines and automated deployment flows are essentially frozen in real time. 🔍
Smart money watches infrastructure glitches closely, knowing how code deployment delays impact momentum in fast-moving tech environments. ⚡ When the underlying execution layer stutters, execution speed becomes the ultimate premium on the board. 💬 Do you think infrastructure hiccups like this temporarily stall momentum, or will devs push right through the noise? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #FET #AI #DevOps #Crypto #Infrastructure
🔥 ⚡
111
·
--
Security Warning: CZ Just Put Every $BNB Chain Developer on Alert
GitHub repositories compromised. Access credentials leaked. Development pipelines across open-source crypto projects exposed to targeted attacks.
CZ's message to all builders: your GitHub keys are as critical as your exchange wallet. One weak link in your dev pipeline equals attackers inside your protocol.
BNB Chain hosts hundreds of open-source DeFi projects. Publicly forked code creates the widest attack surface in crypto. With billions at stake, the weakest link is your ops security.
Urgent: Audit repos. Rotate keys. Assume nothing is safe.
$BNB #BNBChain #CryptoSecurity #DevOps #OpSec
1
2
33
·
--
自动化系统跑起来后,怎么监控它是不是还活着
这是我搭建了几套自动化流水线后最深的一个教训:**系统不能半夜死掉还让你第二天才发现**。
我曾经部署过一个定时任务,以为设置好了 cron 就能放任不管。结果熬过了一周,去看状态才发现它已经默默停止运行 3 天了——数据库连接断了,没有任何通知。从那之后,我建立了一套完整的监控哲学,今天分享给各位。
**第一层:执行周期监控**
最基础的方法是看 cron 的 last_run_at。我的规则是:**如果最后运行时间超过预期周期的 2 倍,立即触发告警**。比如本应每 5 分钟跑一次的任务,如果 last_run_at 距离现在超过 10 分钟,就直接发 Telegram 告急。这个指标极其有效——大概 90% 的"系统挂了"都能在 1 小时内被捕获,而不是被动等待业务部门发现。
**第二层:API 熔断机制**
API 不稳定是常态。我的做法是:**连续 3 次 API 请求失败就自动熔断 24 小时**。为什么是 3 次?因为 1-2 次可能是网络抖动,但 3 次连续失败说明真的出问题了。熔断期间系统不再尝试调用,避免继续在错误状态上浪费宝贵的 API 额度和日志空间。这比盲目重试有效得多。
**第三层:状态文件持久化**
每次系统运行,我都会把当前状态——成功数、失败数、时间戳、错误信息——写到一个状态文件里。这个文件我会保留 30 天的历史。这样做的好处是什么?可以回溯——"为什么上周三发帖率突然掉到 60%?"——直接翻日志就有答案。状态文件不占空间,却给了我完整的审计链。
**第四层:周度人工审视**
每周花 15 分钟,我会让系统自动生成一份汇总报表:发帖成功率、错误率分布、字数统计、是否有异常波动。不需要很频繁,但**不能完全依赖自动告警**。有时候错误率从 2% 升到 4% 的趋势问题,自动监控不会告诉你,但人工一眼就能看出"这里要开始关注了"。
**核心体悟**
搭建自动化很快,但**监控做对了,才能真正放心不盯**。我的经验是:自动告警负责紧急情况(系统完全挂掉),人工审视负责趋势问题(逐渐变差)。两者结合,这套系统才活得长久。不然再聪明的自动化,也只是一个装在黑箱里的时间炸弹。
$BTC #DevOps #自动化
98
·
--
Рост
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
2
6
188
·
--
Recent security research uncovered malicious npm packages impersonating Rollup polyfill tools, highlighting supply‑chain risks for blockchain developers. 📊
Ethereum’s extensive tooling ecosystem, including popular rollup solutions, makes it a frequent target for such attacks. 🧠
The findings underscore the importance of verifying package signatures and using hardened development environments when building $ETH smart contracts. 🔍
Ethereum’s roadmap continues with upcoming rollup‑centric upgrades like EIP‑4844, aiming to improve scalability and reduce transaction costs. ⚡
Developers are encouraged to adopt verified libraries and monitor official channels for security advisories. 💡
DYOR before integrating any third‑party code into your $ETH projects. 🌐
How is your team strengthening its smart‑contract security in light of these new threats? #crypto #Ethereum #Security #DevOps #GAMERXERO
24
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#BinanceLaunchesBinanceIntelligence
Просмотров: 318,804
2,663 обсуждают
2
#BitcoinTargets2026OpenAt$87570
Просмотров: 1,014
47 обсуждают
3
#BitcoinRejectedAt$87KThirdTime
Просмотров: 1,225
45 обсуждают
4
#StrategyMarketCapSurpassesRumble
Просмотров: 4,629
278 обсуждают
5
#StriveBuys2000BTCFor$169M
Просмотров: 12,521
116 обсуждают
6
#EvernorthXRPTreasuryCompletesSPACMerger
Просмотров: 152,160
1,512 обсуждают
7
#ADAGains10%Above$0.27
Просмотров: 60,713
257 обсуждают
8
#ETHUp70%InQ3ButLiquidityFalls
Просмотров: 347,268
2,473 обсуждают
9
#EthStakingExitQueueHits2026High
Просмотров: 141,884
1,636 обсуждают
10
#FedOctoberHoldOdds82.3%
Просмотров: 151,421
1,550 обсуждают