

#bitgetbreachforgedrequestsnotstolenkeys
bitgetbreachforgedrequestsnotstolenkeys
Просмотров: 73,804
992 обсуждают
Популярные
Новые
·
--
🚨 The largest crypto hack of 2026: Bitget loses $351.6 million
Hackers stole approximately $351.6 million in assets, making this incident the largest crypto exploit of the entire year.
The attackers did not steal private keys. Instead, they compromised the hot wallet backend infrastructure, falsified internal transaction histories, and fraudulently initiated withdrawals.
The primary targets were AVAX, BNB, ETH, and stablecoins (USDC, USDT). The hackers immediately began converting the funds to Ethereum via bridges to complicate tracking. Analysts at Arkham Intelligence were the first to spot the massive on-chain anomaly.
Bitget management has temporarily suspended withdrawals to conduct security checks. Cold wallets, which hold the vast majority of assets, remain unaffected. Trading and deposits continue to function normally.
Exchange CEO Gracy Chen officially guaranteed that 100% of user losses will be fully covered by the User Protection Fund. The fund's current reserves exceed $464 million, allowing the exchange to close the financial gap independently.
Cybersecurity experts suspect that North Korean-linked hacker groups orchestrated the exploit.
#BitgetBreachForgedRequestsNotStolenKeys #ETH #BNB $ETH $AVAX $BNB
{future}(BNBUSDT)
{future}(AVAXUSDT)
{future}(ETHUSDT)
🚨 The largest crypto hack of 2026: Bitget loses $351.6 million
Hackers stole approximately $351.6 million in assets, making this incident the largest crypto exploit of the entire year.
The attackers did not steal private keys. Instead, they compromised the hot wallet backend infrastructure, falsified internal transaction histories, and fraudulently initiated withdrawals.
The primary targets were AVAX, BNB, ETH, and stablecoins (USDC, USDT). The hackers immediately began converting the funds to Ethereum via bridges to complicate tracking. Analysts at Arkham Intelligence were the first to spot the massive on-chain anomaly.
Bitget management has temporarily suspended withdrawals to conduct security checks. Cold wallets, which hold the vast majority of assets, remain unaffected. Trading and deposits continue to function normally.
Exchange CEO Gracy Chen officially guaranteed that 100% of user losses will be fully covered by the User Protection Fund. The fund's current reserves exceed $464 million, allowing the exchange to close the financial gap independently.
Cybersecurity experts suspect that North Korean-linked hacker groups orchestrated the exploit.
#BitgetBreachForgedRequestsNotStolenKeys #ETH #BNB $ETH $AVAX $BNB
206 Atlas:
Bitget’s cold wallet defense failed if hot wallets were compromised. The market pricing BGB down while altcoins rise confirms this is an isolated failure, not systemic risk.LSK's 600% pump is likely a liquidity trap for retail chasing the squeeze. Chasing low-cap NOM here ignores the extreme volatility risk of these setups.A $464M fund cannot fully cover a $351.6M loss after operational costs and panic liquidity drains. This guarantee is likely insufficient.
1
1.1k

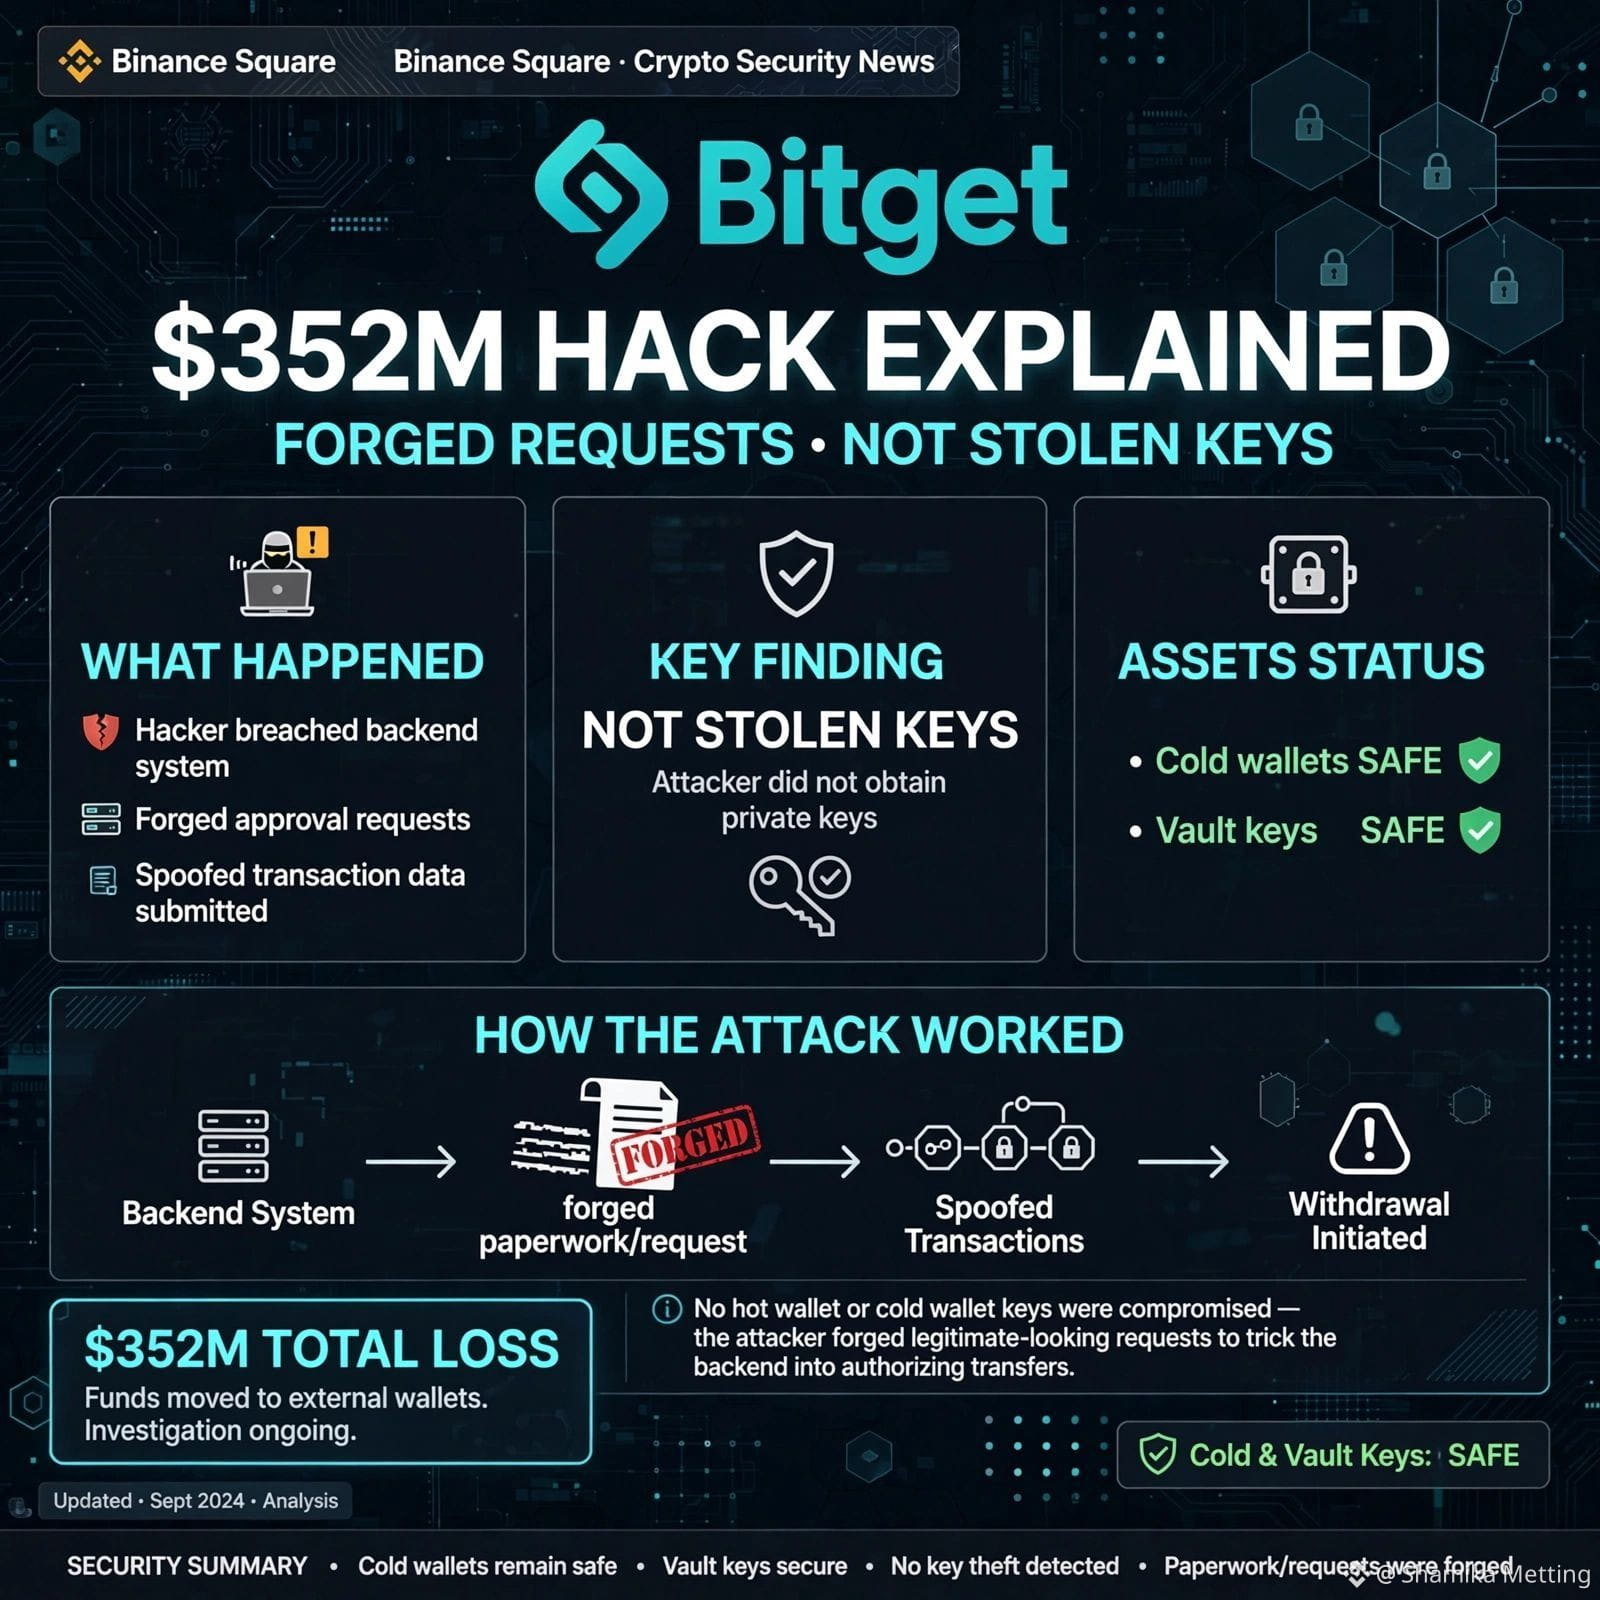
🚨 تم شرح اختراق بيتجيت بقيمة 352 مليون دولار: طلبات مزوّرة، وليس مفاتيح مسروقة!
يُصاب الجميع بالذعر بشأن المفاتيح الخاصة. لكن الرئيسة التنفيذية لبيتجيت، جراسي تشن، أكدت شيئًا أخطر.
ماذا حدث فعلًا:
❌ لم يتم سرقة المفاتيح الخاصة (الـ cold والـ hot والـ warm محافظ آمنة)
❌ لم يتم تزوير طلبات سحب المستخدمين
✅ اخترق المهاجمون نظامًا حيويًا وخلفيًا (Backend) حاسمًا
✅ قاموا بتزوير بيانات المعاملات
✅ فعّلوا عملية التفويض الخاصة ببيتجيت لتحريك 351.6 مليون دولار
تخيّل الأمر كالتالي: "لم يكسروا الخزنة، بل زوّروا الأوراق." مفاتيح الخزنة لم تغادر المبنى أبدًا؛ شخص ما فقط أنشأ إيصالات رسمية مزوّرة.
الحالة الحالية:
تم اكتشافه في 18:31 بالتوقيت العالمي المنسق، 24 سبتمبر
المحافظ الباردة آمنة
سيغطي صندوق حماية المستخدمين بقيمة 464 مليون دولار قيمة الخسارة
الرئيسة تربط الهجوم بربط كوريا الشمالية عبر أدلة من عناوين IP
ما رأيك—هل يجب على منصات CEX جعل backend الخاص بها مفتوح المصدر؟
متابعة من فضلكم
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
CambioLatino:
Esos norcoreanos no dan internet a su población pero si tienen buenna conexion para robar
4
15
24.7k
#bitgetbreachforgedrequestsnotstolenkeys
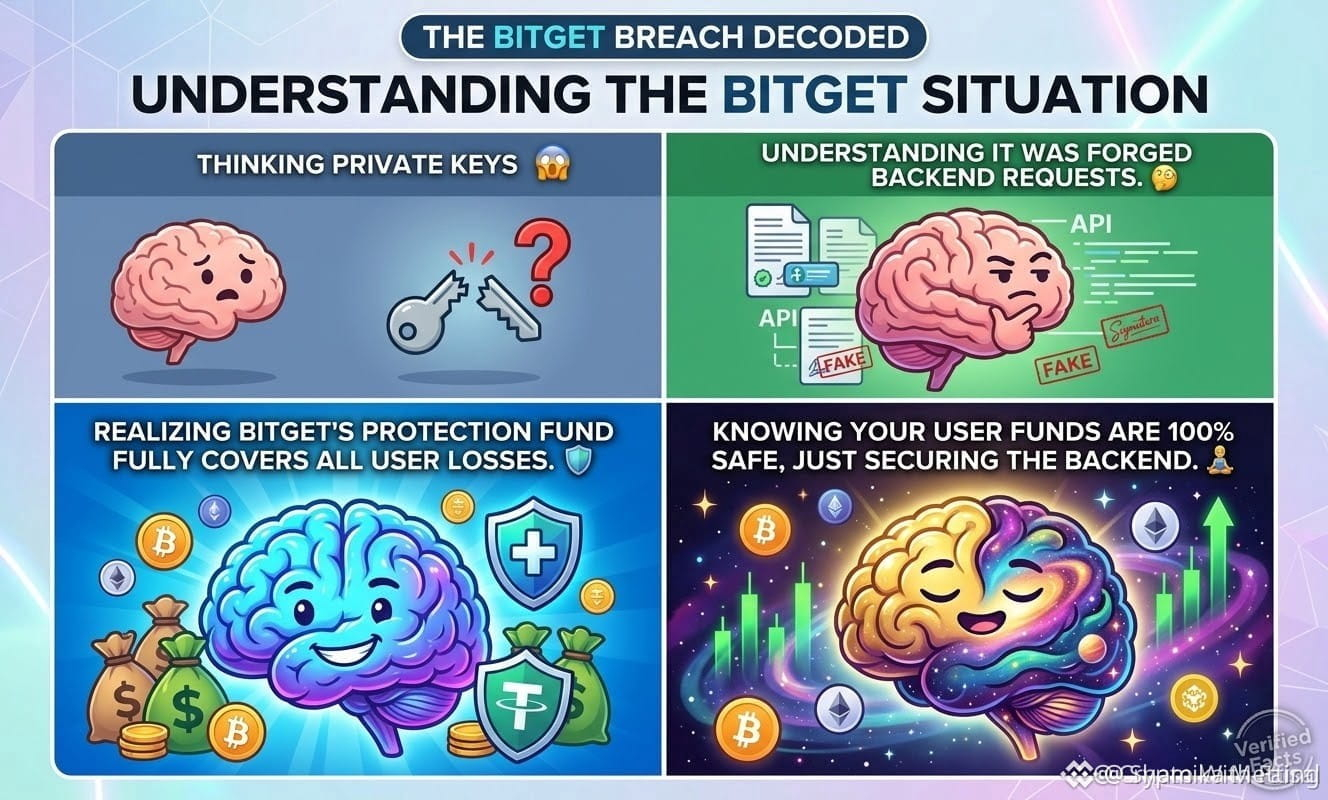
🚨 القصة الحقيقية وراء اختراق Bitget 🚨
عالم العملات الرقمية في حالة ضجة، لكن دعونا نزيل الضجيج بالأدلة المُثبتة حول اختراق Bitget بقيمة 351.6 مليون دولار.
تنبيه: الأمر ليس كما تتخيل.
لم يقم المهاجمون بسرقة مفاتيح الخزائن الخاصة! بدلاً من ذلك، اخترقوا نظامًا خلفيًا، وضلّلوا مستندات المعاملات، ومرروا طلبات سحب مُزيفة عبر عملية الموافقة الخاصة بـ Bitget نفسها.
لماذا يهم هذا التفصيل التقني؟
لأن سرقة المفاتيح تعني نزيفًا لا ينتهي. 🩸
الطلبات المُزيفة = سدّ الثغرة وإيقاف النزيف. 🛑
الأخبار الجيدة:
✅ المفاتيح في أمان: لم تغادر المفاتيح الخاصة مكانها.
✅ الخزائن مؤمنة: تم استهداف المحافظ الساخنة والساخنة-الدافئة فقط. تظل التخزين البارد آمنًا بنسبة 100%.
✅ المستخدمون بخير: صندوق الحماية لدى Bitget البالغ 464 مليون دولار يغطي بالكامل خسارة 351.6 مليون دولار.
تم إيقاف عمليات السحب مؤقتًا لإجراء مراجعة أمنية شاملة، لكن الرئيس التنفيذي Gracy Chen أكد أن أصول المستخدمين في أمان.
هذه الحادثة تثبت أن البنية التحتية للخلفية أصبحت ساحة المعركة الجديدة في Web3. انتبه وابقَ في أمان! 🛡️
متابعة من فضلكم
$AVAX
{future}(AVAXUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 القصة الحقيقية وراء اختراق Bitget 🚨
عالم العملات الرقمية في حالة ضجة، لكن دعونا نزيل الضجيج بالأدلة المُثبتة حول اختراق Bitget بقيمة 351.6 مليون دولار.
تنبيه: الأمر ليس كما تتخيل.
لم يقم المهاجمون بسرقة مفاتيح الخزائن الخاصة! بدلاً من ذلك، اخترقوا نظامًا خلفيًا، وضلّلوا مستندات المعاملات، ومرروا طلبات سحب مُزيفة عبر عملية الموافقة الخاصة بـ Bitget نفسها.
لماذا يهم هذا التفصيل التقني؟
لأن سرقة المفاتيح تعني نزيفًا لا ينتهي. 🩸
الطلبات المُزيفة = سدّ الثغرة وإيقاف النزيف. 🛑
الأخبار الجيدة:
✅ المفاتيح في أمان: لم تغادر المفاتيح الخاصة مكانها.
✅ الخزائن مؤمنة: تم استهداف المحافظ الساخنة والساخنة-الدافئة فقط. تظل التخزين البارد آمنًا بنسبة 100%.
✅ المستخدمون بخير: صندوق الحماية لدى Bitget البالغ 464 مليون دولار يغطي بالكامل خسارة 351.6 مليون دولار.
تم إيقاف عمليات السحب مؤقتًا لإجراء مراجعة أمنية شاملة، لكن الرئيس التنفيذي Gracy Chen أكد أن أصول المستخدمين في أمان.
هذه الحادثة تثبت أن البنية التحتية للخلفية أصبحت ساحة المعركة الجديدة في Web3. انتبه وابقَ في أمان! 🛡️
متابعة من فضلكم
$AVAX
SAQR77:
المهم منصة تافهة
3
5
11.8k
·
--
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
{spot}(BTCUSDT)
{spot}(ETHUSDT)
{spot}(BNBUSDT)
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
206 Atlas:
Spoofing backend requests bypasses key security, exposing critical infrastructure flaws that cold storage cannot mitigate.
2
3
9.3k
·
--
Падение
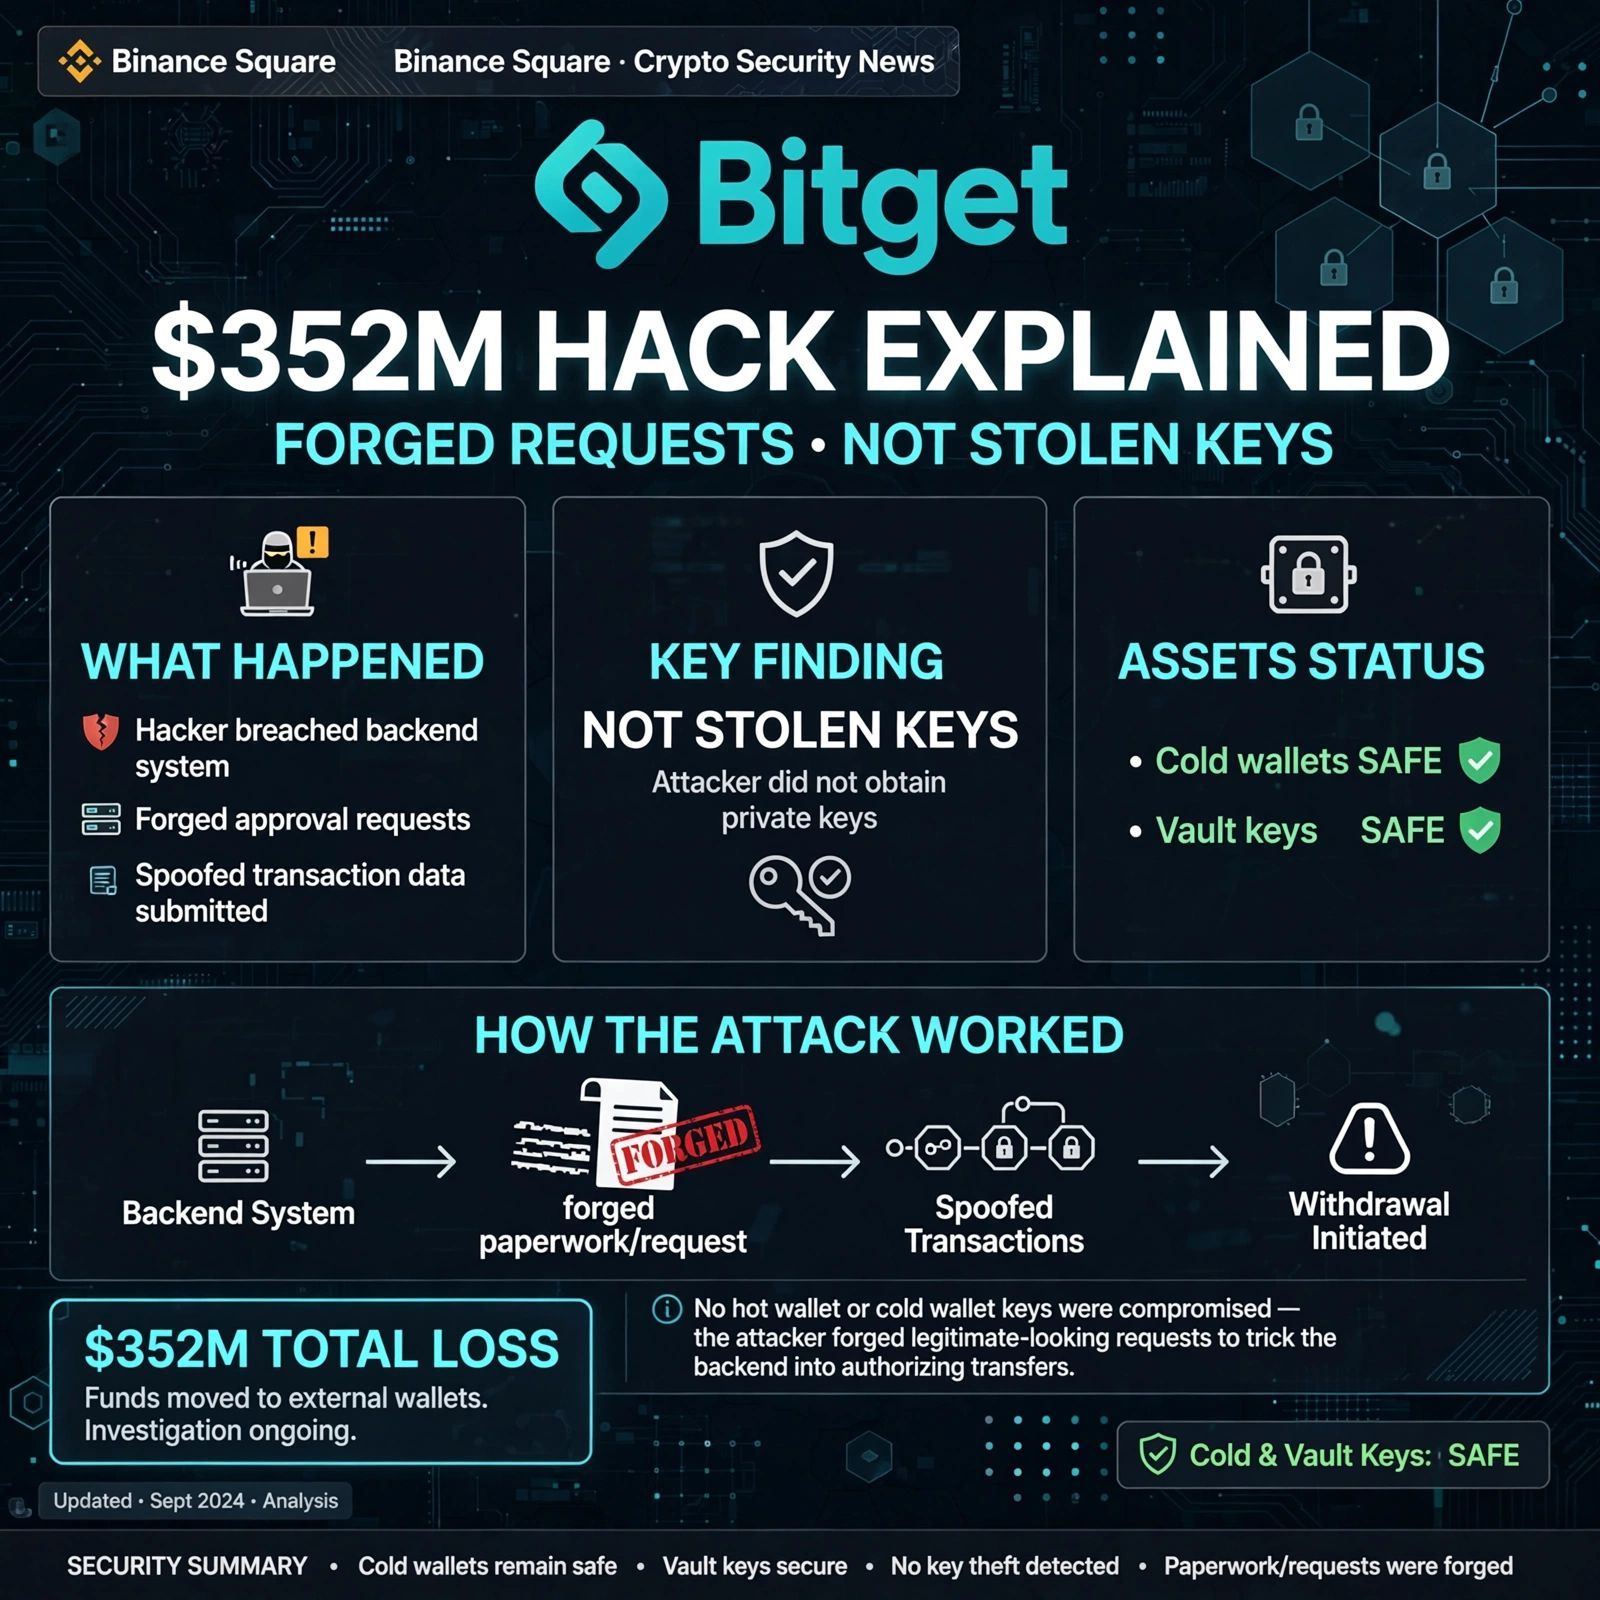
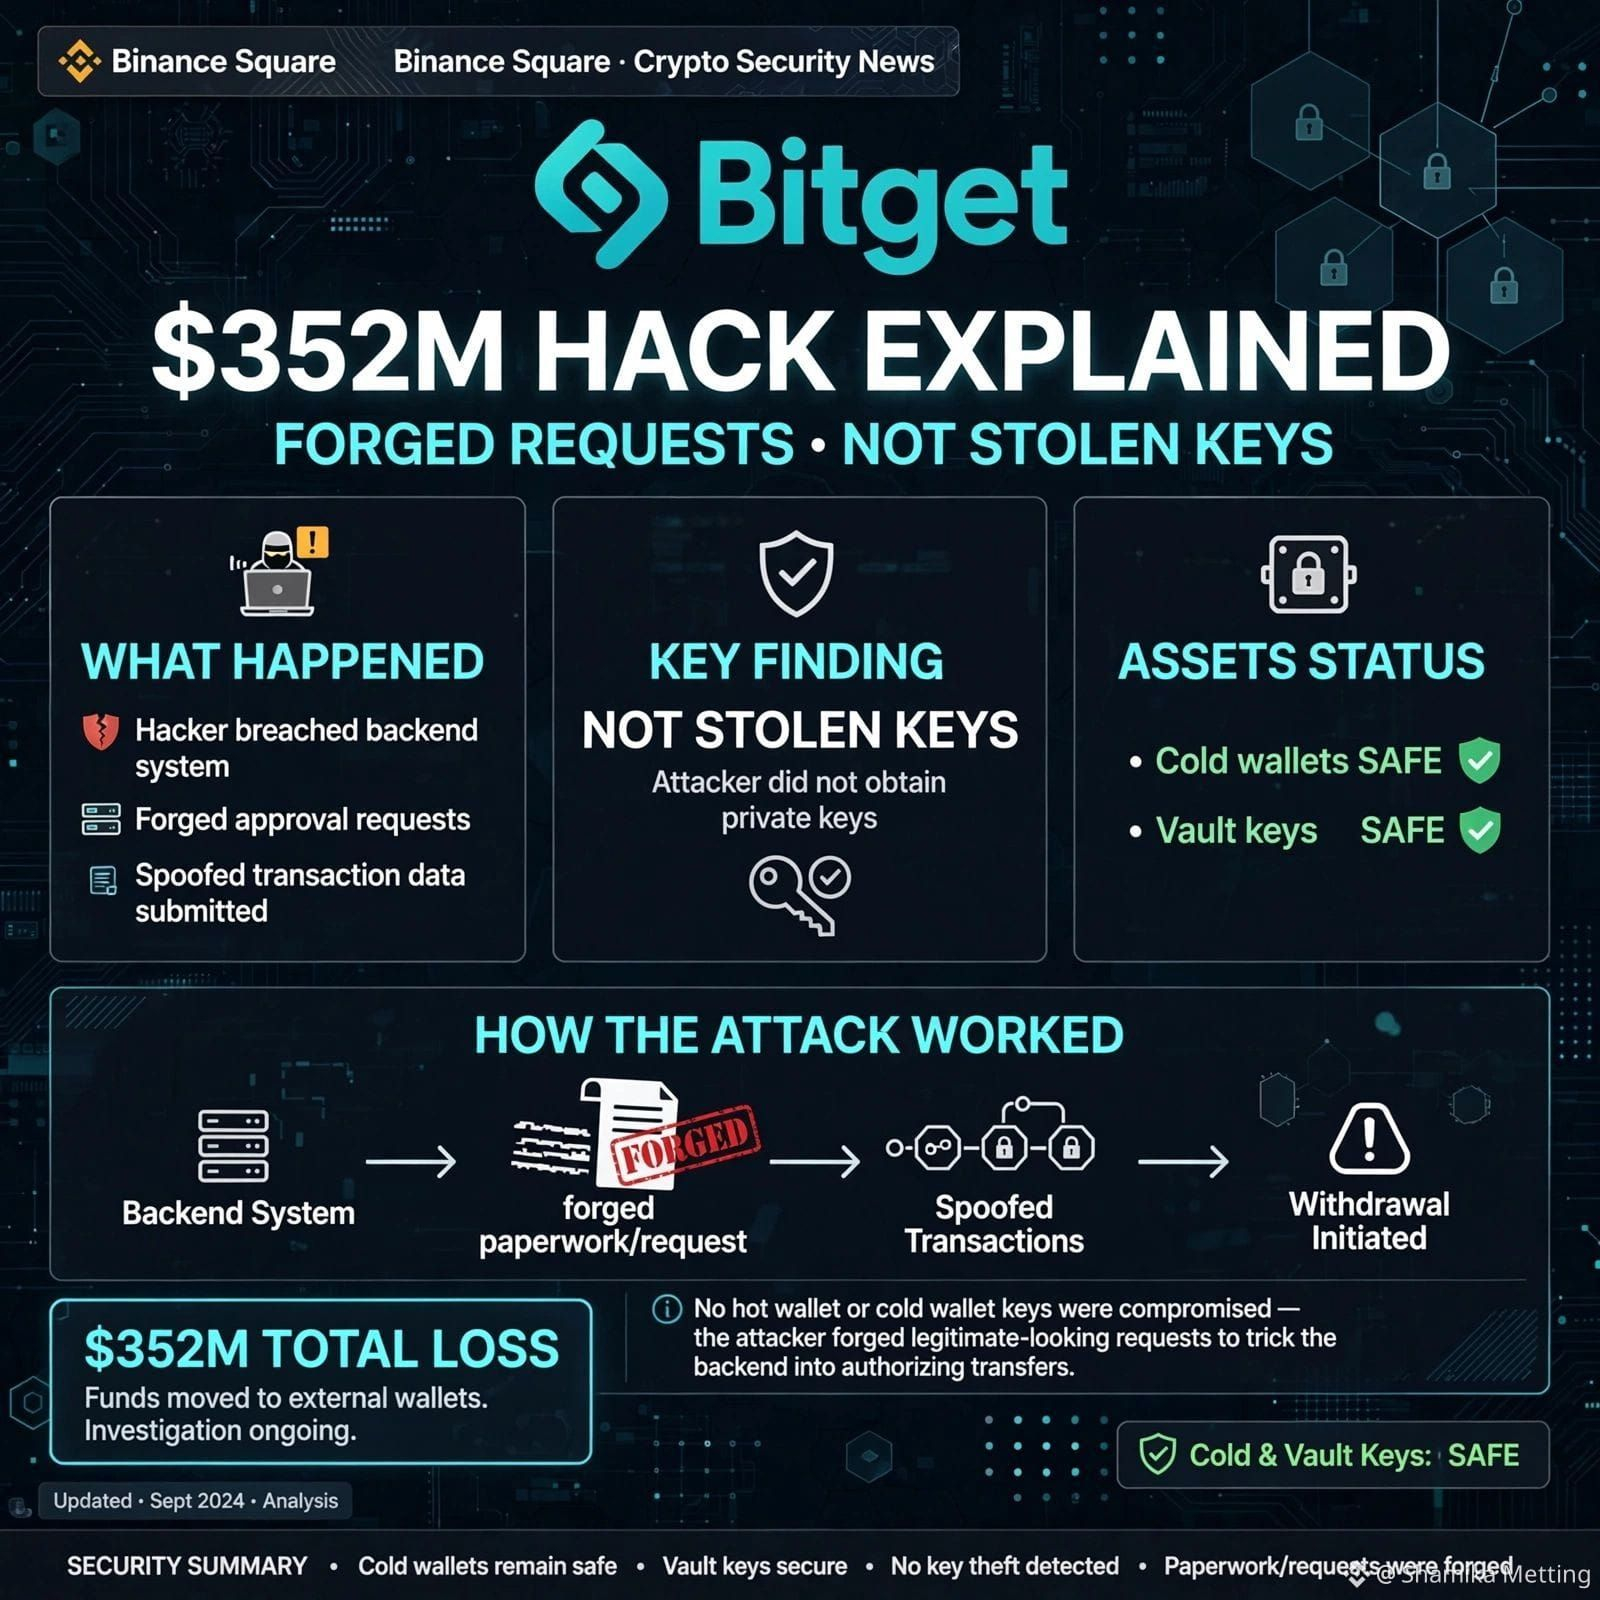
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
{future}(XRPUSDT)
{future}(TRXUSDT)
{future}(AVAXUSDT)
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
4
9.1k
·
--
Падение
🚨 Se explicó la intrusión en Bitget por valor de 352 millones de dólares: ¡solicitudes falsificadas, no claves robadas!
Todo el mundo entra en pánico por las claves privadas. Pero la directora ejecutiva de Bitget, Gracy Chen, confirmó algo aún más preocupante.
¿Qué pasó realmente?
❌ No se robaron las claves privadas (cold, hot y warm protegidas en bóvedas seguras)
❌ No se falsificaron las solicitudes de retirada de los usuarios
✅ Los atacantes comprometieron un sistema crítico y de respaldo (Backend)
✅ Falsificaron los datos de las transacciones
✅ Activaron el proceso de autorización de Bitget para mover 351.6 millones de dólares
Imagina esto así: "No forzaron la caja fuerte; falsificaron los documentos". Las claves de la caja fuerte nunca salieron del edificio; simplemente alguien creó recibos oficiales falsificados.
Estado actual:
Se detectó a las 18:31 UTC, el 24 de septiembre
Las carteras frías están seguras
El fondo de protección de usuarios cubrirá una pérdida de 464 millones de dólares
La presidenta vincula el ataque con conexiones a Corea del Norte a través de evidencias de direcciones IP
¿Qué opinas: deberían las plataformas CEX hacer público (open source) su backend?
Por favor, continúen
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
1
310
·
--
Bitget sufrió un hackeo de más de $350M en sus hot wallets!!😵
La seguridad en los exchanges vuelve a estar en el centro del debate. Bitget reportó una brecha de seguridad crítica en sus sistemas internos de autorización que comprometió varias de sus billeteras calientes (hot wallets).
Fueron varias Transferencias no autorizadas detectadas tras una manipulación del sistema de autorización interna.
Fueron cerca de 351,6 millones de dólares drenados en diversos activos ($ETH $USDT, $USDC, $BNB $AVAX y $XAUT), los cuales comenzaron a ser puenteados y mezclados rápidamente en cadena.
La directiva de Bitget confirmó que las reservas frías (cold wallets) no fueron vulneradas. Además, anunciaron que las pérdidas serán cubiertas al 100% mediante su Fondo de Protección al Usuario (valuado en ~$464M).
Los retiros fueron pausados de forma preventiva mientras terminan la auditoría forense, aunque las operaciones de trading y depósitos continúan activas.
Analistas on-chain y fuentes vinculadas a la investigación apuntan a posibles grupos avanzados de ciberdelincuencia internacional (con patrones similares a ataques norcoreanos). Se espera un reporte técnico detallado en las próximas horas.
Eventos como este recuerdan la importancia de la regla de oro en cripto: "No tus llaves no tus criptos". ¿Ustedes dejan sus fondos en CEXs o transfieren las ganancias directamente a la billetera fria?
Los leo en comentarios y recuerden no quemar sus cuentas plsss!
Los quiero❤️
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #Web3Revolution #CyberSecurity
2
2
689
·
--
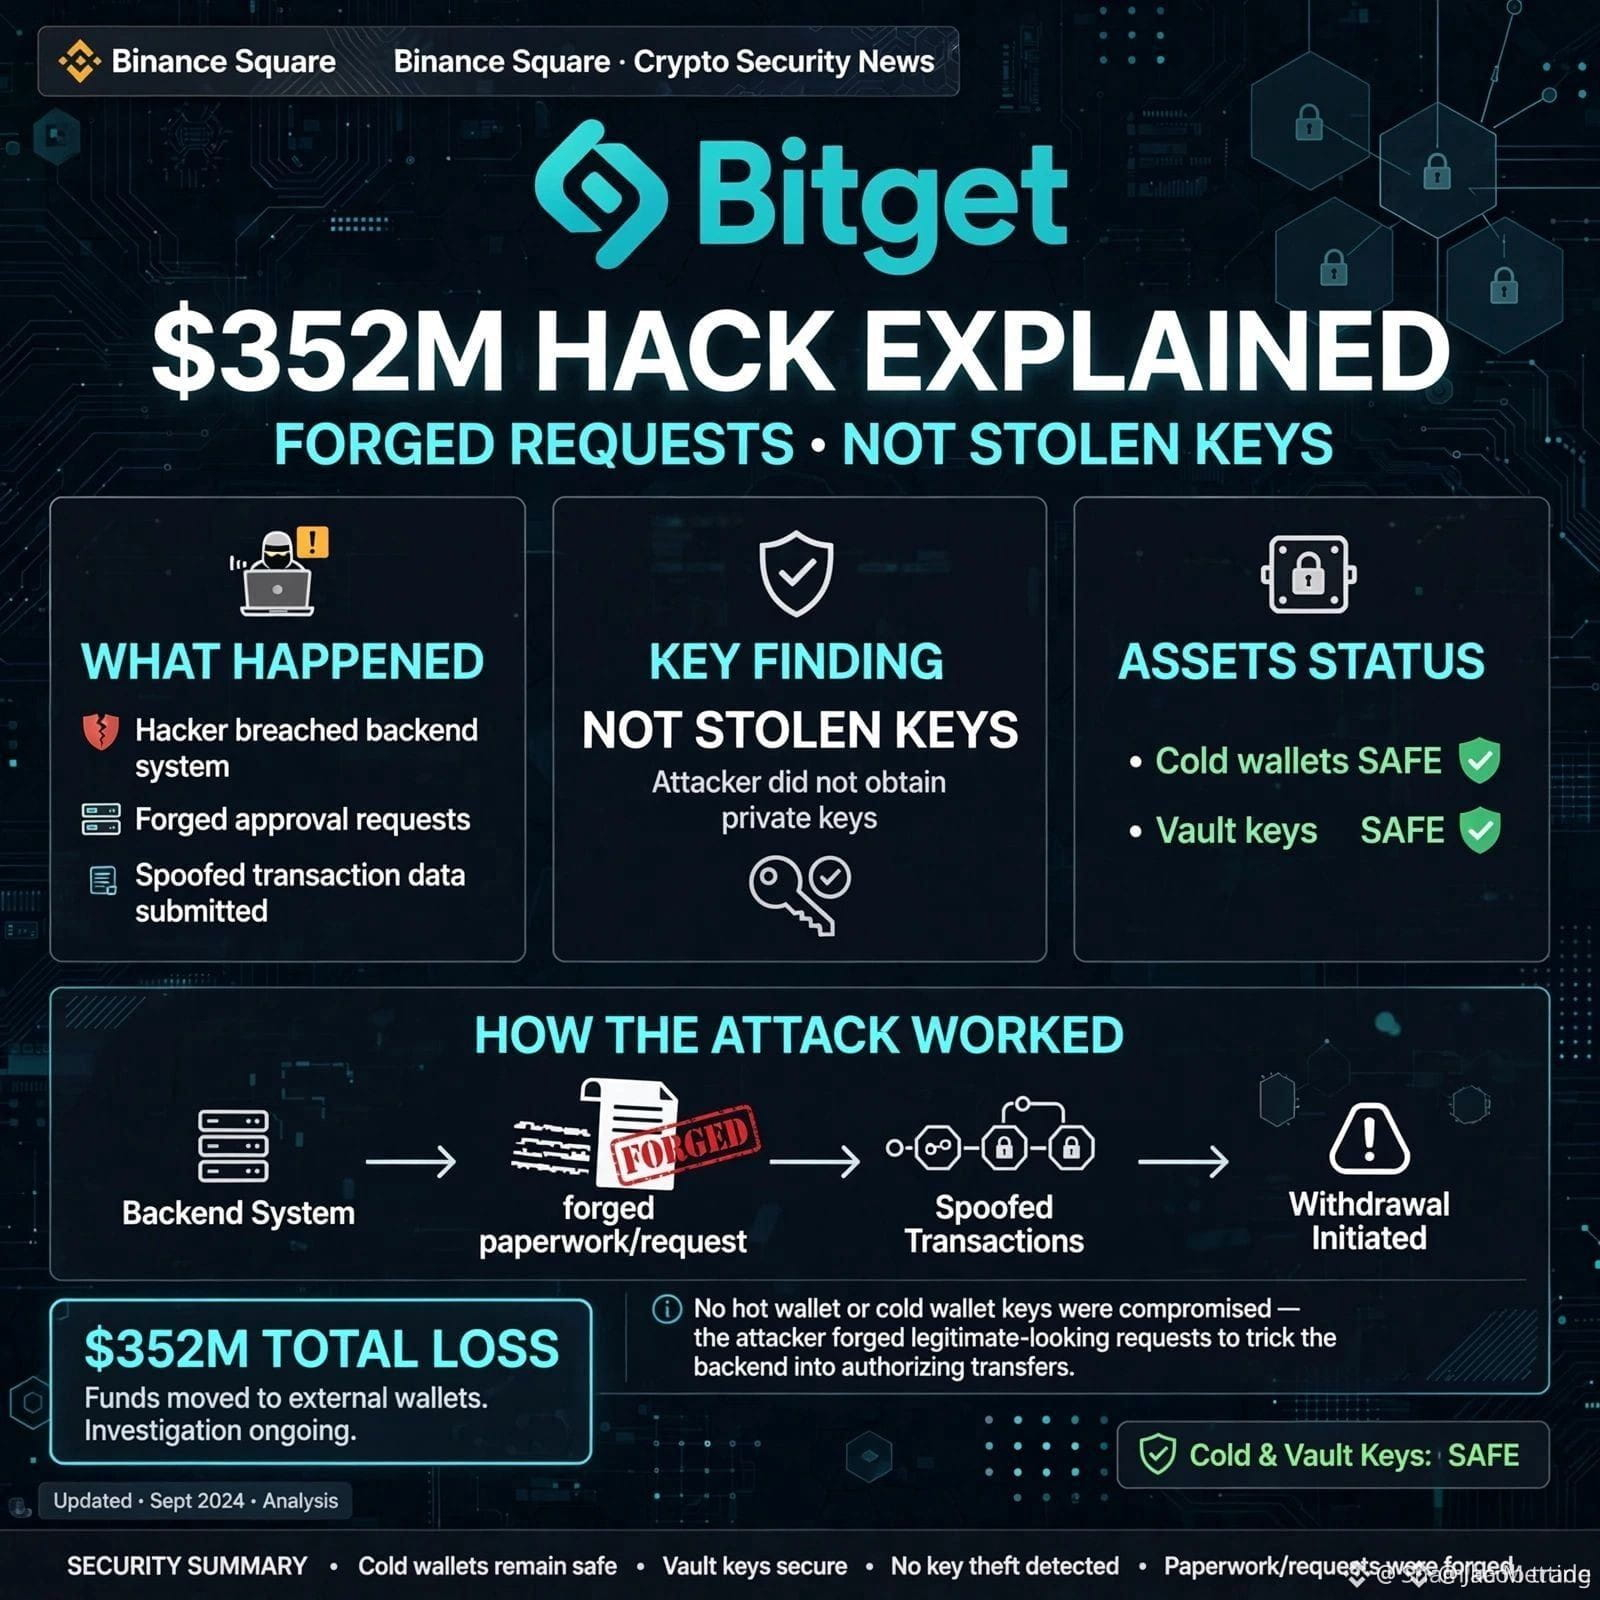
🚨 Des détails sur la compromission de Bitget d’une valeur de 352 millions de dollars : des demandes falsifiées, pas des clés volées !
Tout le monde panique au sujet des clés privées. Mais la PDG de Bitget, Gracy Chen, a confirmé quelque chose de plus inquiétant.
Que s’est-il passé réellement :
❌ Les clés privées (cold, hot et warm, conservées dans des coffres sécurisés) n’ont pas été volées
❌ Les demandes de retrait des utilisateurs n’ont pas été falsifiées
✅ Les attaquants ont compromis un système vital et en coulisses (backend) crucial
✅ Ils ont falsifié les données des transactions
✅ Ils ont déclenché le processus d’autorisation de Bitget pour transférer 351,6 millions de dollars
Imaginez la situation ainsi : « Ils n’ont pas forcé le coffre, ils ont falsifié les papiers. » Les clés du coffre n’ont jamais quitté le bâtiment ; quelqu’un a simplement créé des reçus officiels falsifiés.
Situation actuelle :
Détecté à 18:31 UTC le 24 septembre
Les portefeuilles cold sont sécurisés
Le Fonds de protection des utilisateurs de 464 millions de dollars couvrira la valeur de la perte
La PDG relie l’attaque à des connexions en provenance de la Corée du Nord à partir d’indices tirés d’adresses IP
Et vous, pensez-vous que les plateformes CEX devraient rendre leur backend open source ?
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #CryptoNews #Cybersecurity
$PHA
{future}(PHAUSDT)
$BTW
{future}(BTWUSDT)
$ARK
{future}(ARKUSDT)
🚨 Des détails sur la compromission de Bitget d’une valeur de 352 millions de dollars : des demandes falsifiées, pas des clés volées !
Tout le monde panique au sujet des clés privées. Mais la PDG de Bitget, Gracy Chen, a confirmé quelque chose de plus inquiétant.
Que s’est-il passé réellement :
❌ Les clés privées (cold, hot et warm, conservées dans des coffres sécurisés) n’ont pas été volées
❌ Les demandes de retrait des utilisateurs n’ont pas été falsifiées
✅ Les attaquants ont compromis un système vital et en coulisses (backend) crucial
✅ Ils ont falsifié les données des transactions
✅ Ils ont déclenché le processus d’autorisation de Bitget pour transférer 351,6 millions de dollars
Imaginez la situation ainsi : « Ils n’ont pas forcé le coffre, ils ont falsifié les papiers. » Les clés du coffre n’ont jamais quitté le bâtiment ; quelqu’un a simplement créé des reçus officiels falsifiés.
Situation actuelle :
Détecté à 18:31 UTC le 24 septembre
Les portefeuilles cold sont sécurisés
Le Fonds de protection des utilisateurs de 464 millions de dollars couvrira la valeur de la perte
La PDG relie l’attaque à des connexions en provenance de la Corée du Nord à partir d’indices tirés d’adresses IP
Et vous, pensez-vous que les plateformes CEX devraient rendre leur backend open source ?
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #CryptoNews #Cybersecurity
$PHA
$BTW
$ARK
241
#bitgetbreachforgedrequestsnotstolenkeys
اختراق بيتجيت: طلبات تحويل مزوّرة، لا مفاتيح خاصة مسروقة
أكدت بيتجيت وقوع حادث أمني كبير يتعلق بما يقارب 351.6 مليون دولار من الأموال المتأثرة.
لكن توجد نقطة حاسمة:
بحسب التقارير، لم يقم المهاجمون بسرقة المفاتيح الخاصة لبيتجيت.
بدلاً من ذلك، قالت الرئيسة التنفيذية لبيتجيت، جرايسي تشن، إن المهاجمين اخترقوا نظام خدمة محافظ خلفية (backend wallet-service) واستخدموا هذا الوصول لاصطناع معلومات التحويل والقيام بعملية التفويض/التوقيع.
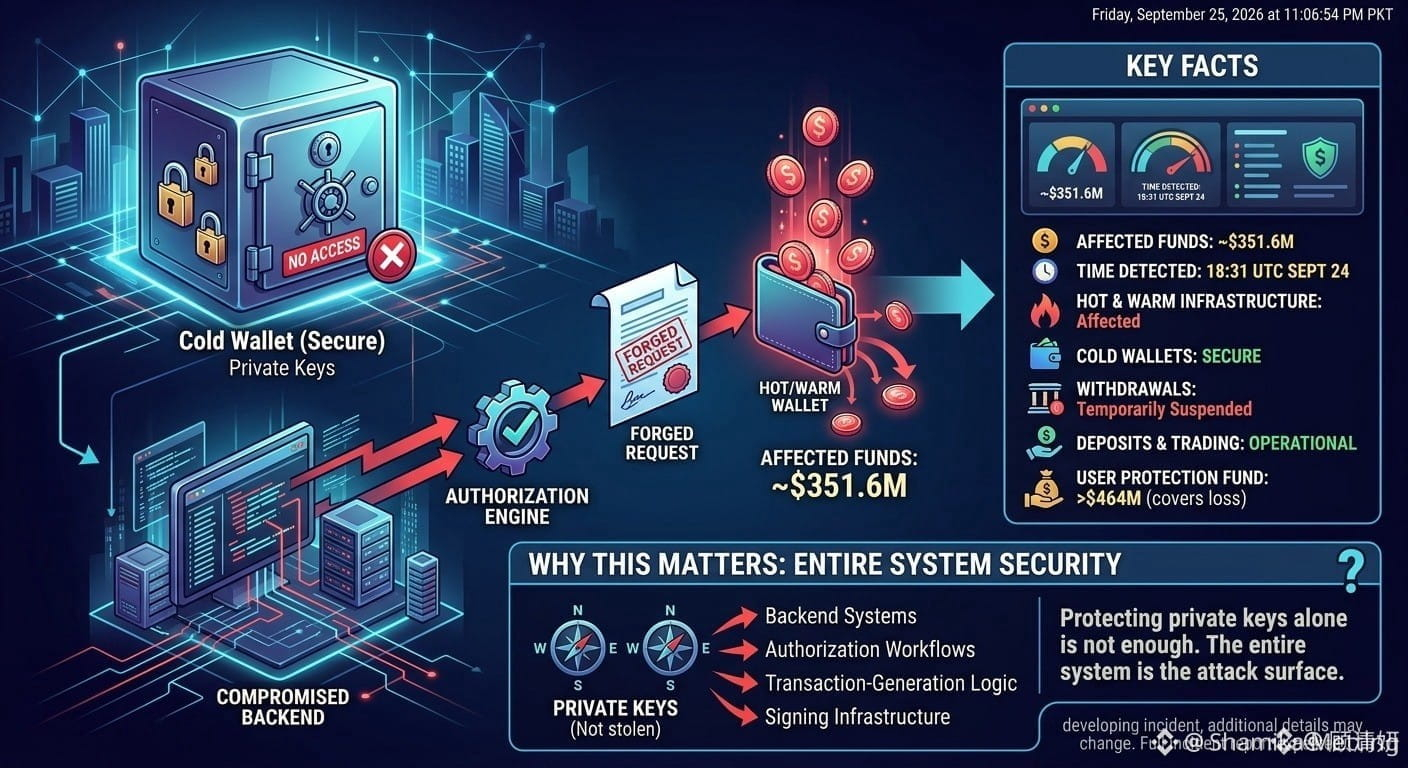
أهم الحقائق
• تأثر ما يقارب 351.6 مليون دولار من الأموال
• تم رصد الحادث في 18:31 بالتوقيت العالمي المنسق يوم 24 سبتمبر
• تأثرت أجزاء من بنية محافظ بيتجيت الساخنة والمرحلية (hot وwarm)
• تقول بيتجيت إن المحافظ الباردة بقيت آمنة
• تم تعليق عمليات السحب مؤقتاً أثناء مراجعة الأمان
• ظلت عمليات الإيداع والتداول تعمل
• تقول بيتجيت إن صندوق حماية المستخدمين لديها يضم أكثر من 464 مليون دولار ويغطي الخسارة المبلّغ عنها
لماذا هذا مهم
يُبرز هذا الحادث خطراً مهماً على أمن البورصات: حماية المفاتيح الخاصة وحدها ليست كافية.
بالنسبة للمتداولين، الخلاصة بسيطة:
أمن البورصة هو منظومة كاملة — وليس مجرد مشكلة مفاتيح خاصة.
ما زال الحادث يتطور، لذا قد تتغير تفاصيل إضافية مع تقدم التحقيق.
متابعة من فضلكم
$QI $PHA $ARK
4
11.7k
·
--
Рост
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
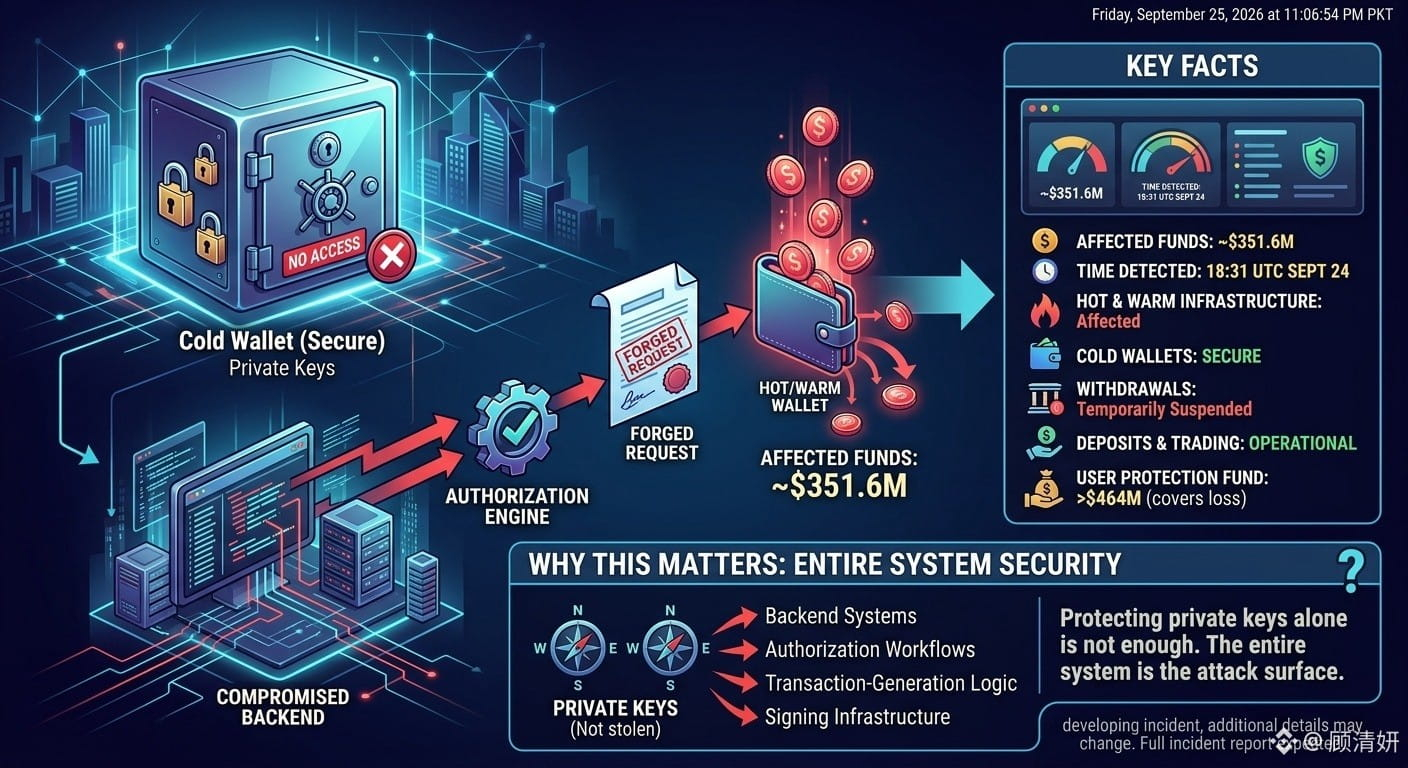
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
{future}(ARKUSDT)
{future}(PHAUSDT)
{spot}(QIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
206 Atlas:
Forged signatures bypassing hot wallet controls is a systemic failure, not just a key theft. This exposes the fragility of centralized signing infrastructures.
4
3
7.6k

·
--
Рост
#bitgetbreachforgedrequestsnotstolenkeys
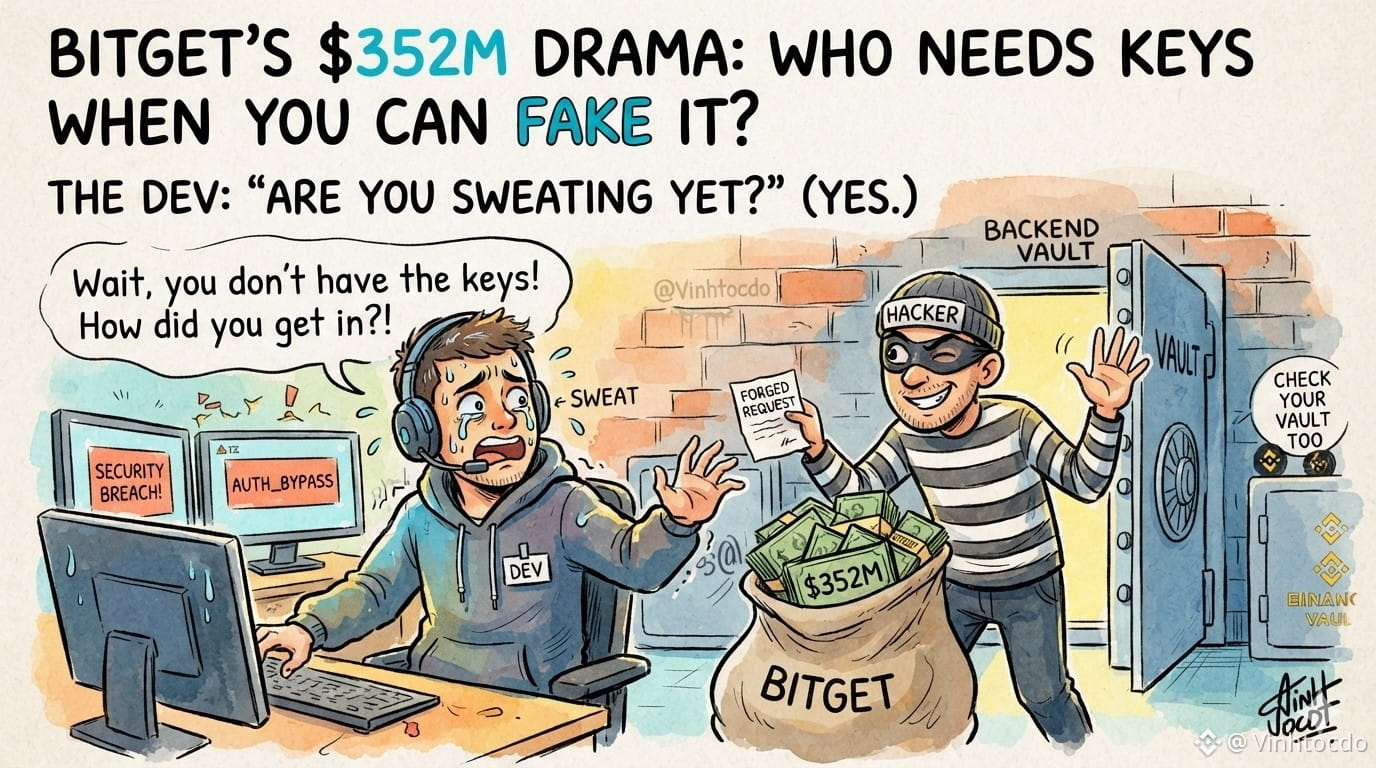
Bitget’s $352M drama: Forged requests, not stolen keys! Devs, are you sweating yet? 🤦♂️🛡️
So, Bitget spilled the tea on their recent hack! The attackers didn't steal their private keys; they simply outsmarted the backend system by forging transaction requests! It’s like a thief walking into a bank with a perfectly forged signature from the manager, and the vault just opened itself! 🏦🔑
This is a massive wake-up call for all blockchain devs and major exchanges, including Binance, to double-check their backend security infrastructure before another exploiter gets creative! 💻💥
What should smart traders do? 🛠️
📌 Keep your guard up: Don't put all your funds into a single exchange.
🛡️ Diversify your assets: Spread your portfolio into trusted tokens to minimize potential platform risks.
Disclaimer: This is personal opinion, not financial advice.
👇 Click and trade below to support me:
💰 $BNB
{future}(BNBUSDT)
| 💰 $BTC
{future}(BTCUSDT)
| 💰 $ETH
{future}(ETHUSDT)
📌 Referral Code: VINHTOCDO
🔗 Join Binance: [https://www.binance.com/register?ref=VINHTOCDO](https://www.binance.com/register?ref=VINHTOCDO)
#BitgetBreach #CryptoSecurity #BackendHacks #VINHTOCDO #TradingSafety #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
Bitget’s $352M drama: Forged requests, not stolen keys! Devs, are you sweating yet? 🤦♂️🛡️
So, Bitget spilled the tea on their recent hack! The attackers didn't steal their private keys; they simply outsmarted the backend system by forging transaction requests! It’s like a thief walking into a bank with a perfectly forged signature from the manager, and the vault just opened itself! 🏦🔑
This is a massive wake-up call for all blockchain devs and major exchanges, including Binance, to double-check their backend security infrastructure before another exploiter gets creative! 💻💥
What should smart traders do? 🛠️
📌 Keep your guard up: Don't put all your funds into a single exchange.
🛡️ Diversify your assets: Spread your portfolio into trusted tokens to minimize potential platform risks.
Disclaimer: This is personal opinion, not financial advice.
👇 Click and trade below to support me:
💰 $BNB
| 💰 $BTC
| 💰 $ETH
📌 Referral Code: VINHTOCDO
🔗 Join Binance: https://www.binance.com/register?ref=VINHTOCDO
#BitgetBreach #CryptoSecurity #BackendHacks #VINHTOCDO #TradingSafety #CryptoNews
1
45

·
--
You think forged requests mean no real risk
That’s comforting but ignores how exchanges get pressured
If they’re forging requests the system is broken not the keys
Traders don’t care why the exploit happened only that it worked
I’m watching how fast they patch and respond
Not the narrative around stolen keys or not
If they release the full forensic report and it shows zero system flaws
Then I’ll admit I overreacted
You think it’s safe
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews
10
#BitgetBreachForgedRequestsNotStolenKeys Refers to a major security incident on September 24, 2026, where the crypto exchange Bitget suffered a hack resulting in an estimated $351.6 million to $387.5 million in unauthorized transfers.
#BitgetBreachForgedRequestsNotStolenKeys Refers to a major security incident on September 24, 2026, where the crypto exchange Bitget suffered a hack resulting in an estimated $351.6 million to $387.5 million in unauthorized transfers.
1
12
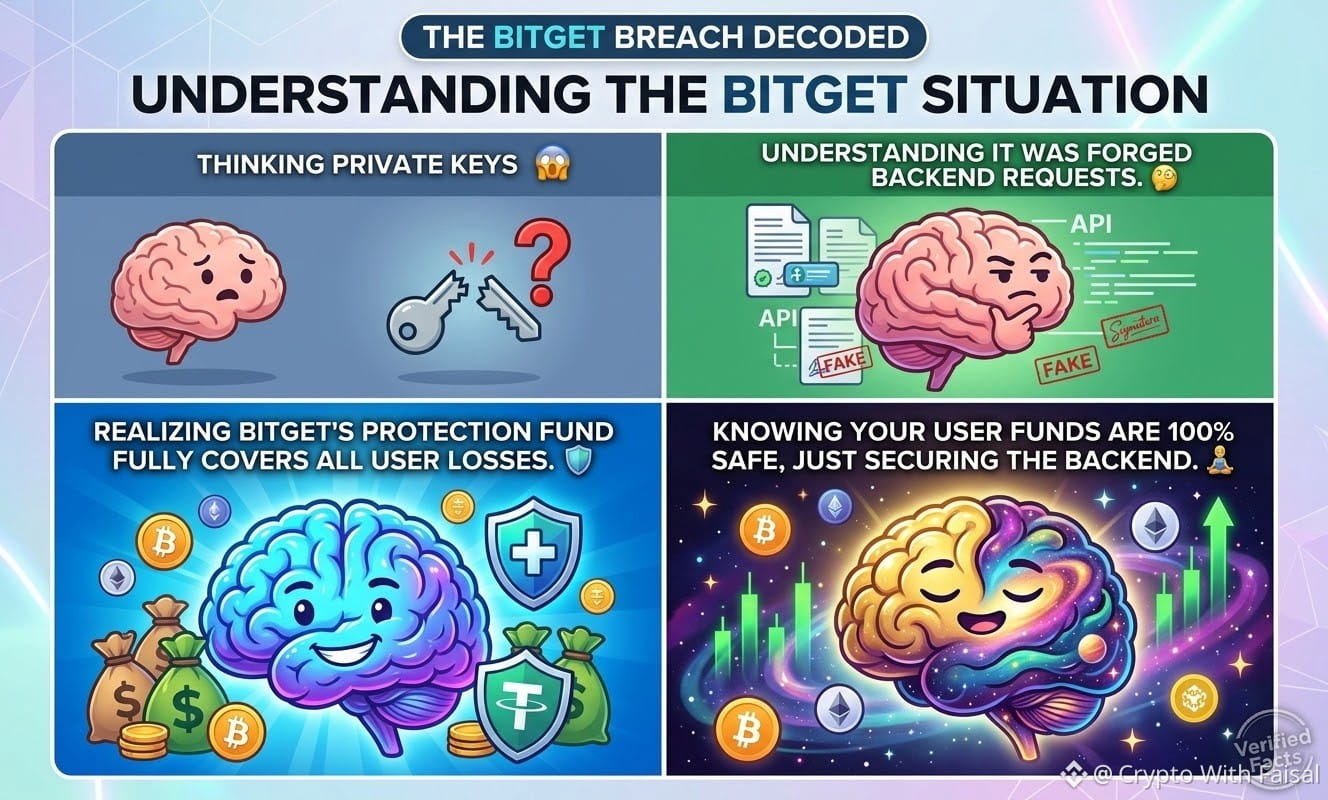
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
{future}(AVAXUSDT)
$LINK
{future}(LINKUSDT)
$ORDI
{future}(ORDIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
$LINK
$ORDI
519

🚨 BITGET BREACH: FORGED REQUESTS — NOT STOLEN KEYS
A major security incident involving Bitget has put crypto exchange security back in the spotlight. ⚠️
💰 Reported impact: ~$351.6M
🔐 Private keys: Bitget says they were not stolen
⚙️ Attack method: Manipulated/forged transaction requests
🛡️ Response: Security investigation and protective measures
📌 Why it matters:
Crypto security isn't only about protecting private keys. If an attacker can manipulate the systems that create or authorize transactions, massive losses can still happen.
🔥 The big question:
Are centralized exchanges secure enough when their backend authorization systems are targeted?
#Binance #CryptoInvesting $BNB
#BitgetBreachForgedRequestsNotStolenKeys
1
69
·
--
#BitgetBreachForgedRequestsNotStolenKeys addresses the $351.6 million security breach suffered by cryptocurrency exchange Bitget.
#BitgetBreachForgedRequestsNotStolenKeys addresses the $351.6 million security breach suffered by cryptocurrency exchange Bitget.
1
59
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Helen_Alek @Square-Creator-f3ffb6967ae3 @qpl5557
$BTC
{spot}(BTCUSDT)
$BNB
{spot}(BNBUSDT)
$ADA
{spot}(ADAUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Hani Era @aasho @HK七匹狼
$BTC
$BNB
$ADA
3
129
#BitgetBreachForgedRequestsNotStolenKeys
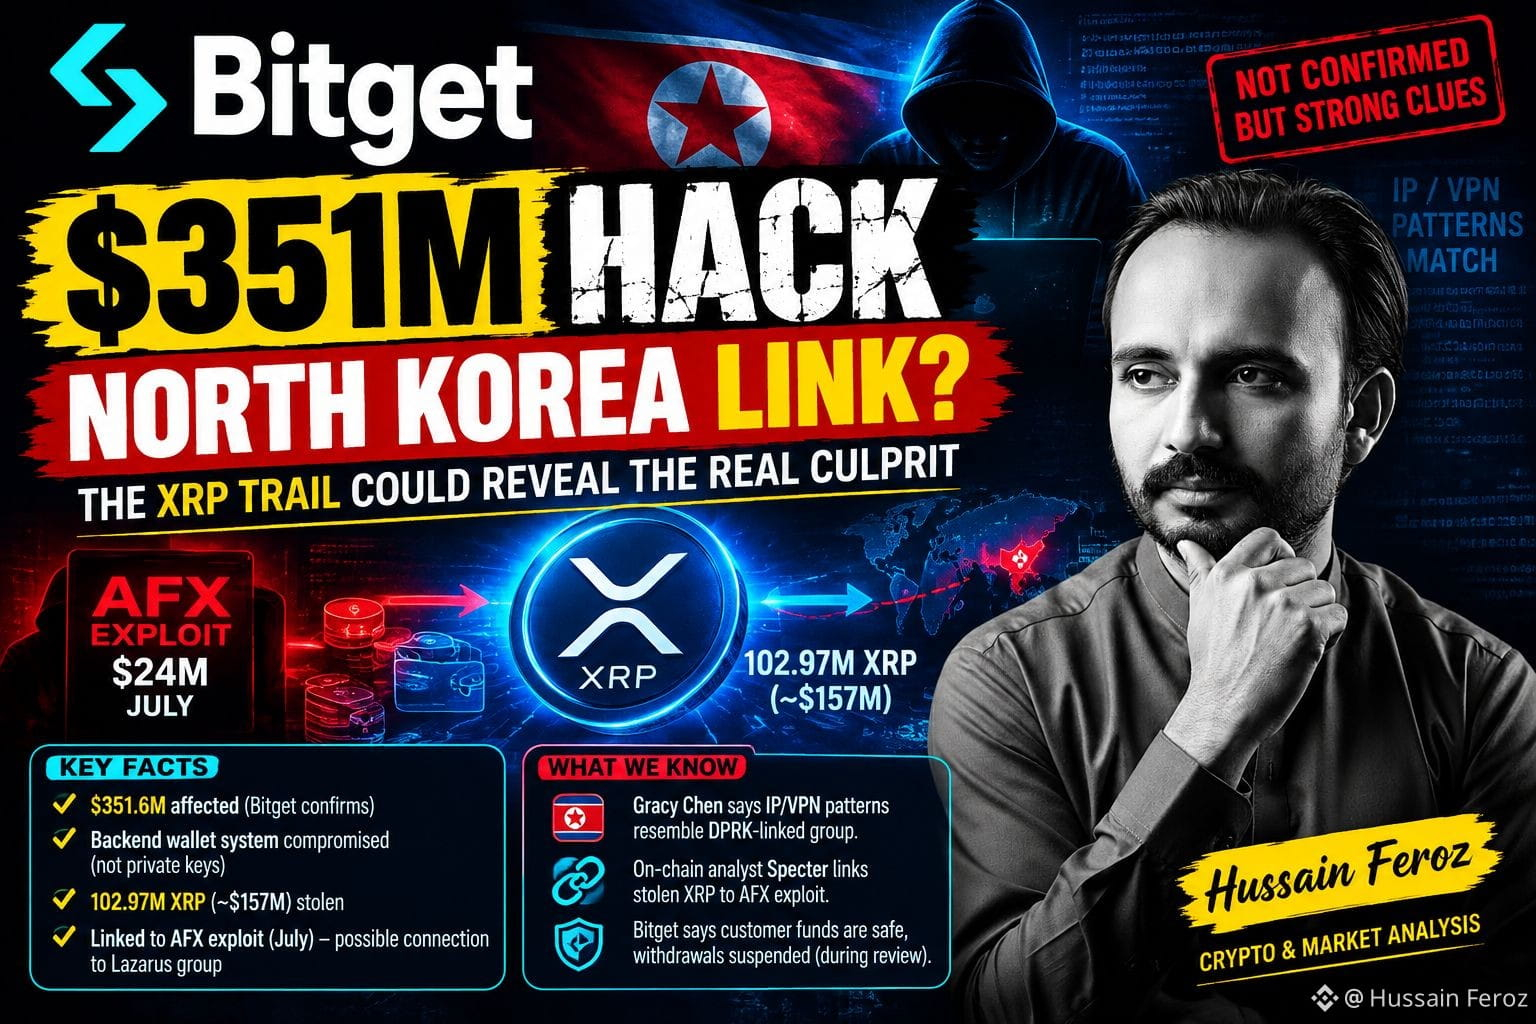
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
1
96

·
--
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Crypto Security Alert & Breakdown: Bitget Incident Clarification 🔐
Bitget breach ko lekar market mein kaafi baatein ho rahi hain. Reports ke mutabiq, ye issue Forged Requests ki wajah se hua tha, na ke private keys ke chori (Stolen Keys) hone se.
📌 Key Takeaways & Lessons for Traders:
• API & System Security: Exchanges ko continuous security audits aur request validation checks increase karne ki zaroorat hai.
• Not Stolen Keys: Private keys secure hona ek positive sign hai, lekin security loopholes har jagah risky ho sakte hain.
• Fund Safety First: Jab bhi kisi exchange par aisi news aaye, apne accounts par 2FA active rakhein aur hamesha extra precaution lein.
💡 Pro Security Tip:
Apna bada capital hamesha Self-Custody / Hardware Wallets mein rakhein aur exchanges ko sirf active trading ke liye use karein!
💬 Aapka kya khayal hai?
Kya aap exchanges par funds rakhte hain ya Cold Wallet prefer karte hain? Niche comments mein zaroor batayein! 👇
#BitgetBreachForgedRequestsNotStolenKey #CryptoSecurity #BinanceSquare #Write2Earn
$bitget
30

Статья
🤝 CEO de exchanges como Binance y Bybit cooperan con Bitget tras sufrir un hackeo de 351,6 millonesComunidad se une en apoyo a Bitget tras el ataque sufrido
Líderes de la industria de criptomonedas manifestaron su respaldo al exchange tras la vulnerabilidad que generó la pérdida de USD 350 millones.
Bitget cuenta con la colaboración de firmas de seguridad externas.
Ejecutivos de Bybit, Binance y MEXC ofrecieron recursos de rastreo y seguridad a Bitget.
El fallo abarcó la salida de ETH, AVAX, BNB y stablecoins, pero no afectó claves privadas.
Diversos ejecutivos de exchanges de criptomonedas manifestaron un respaldo operativo y técnico a Bitget. El pronunciamiento conjunto ocurre en respuesta a una brecha de seguridad que afectó la infraestructura del servicio.
Firma a firma, los directivos ofrecieron herramientas de rastreo y recursos de ciberseguridad para mitigar los daños. Ben Zhou, CEO de Bybit, fue uno de los primeros en poner a disposición su infraestructura de análisis forense.
“El equipo de Bybit está en standby para ayudar en cualquier forma que podamos. Bitget nos ayudó cuando tuvimos el hack. Estamos actualizando lazarusbounty.com para ayudar a Bitget a capturar y rastrear el movimiento de los fondos robados”, declaró Zhou.
Bybit sufrió una extracción de fondos por 1.500 millones de dólares en 2025, marco en el que contó con la cooperación de Bitget.
A la iniciativa se sumó Richard Teng, CEO de Binance, quien confirmó la asistencia entre departamentos técnicos. “Estamos con Bitget y sus usuarios tras el incidente reciente. Nuestro equipo de seguridad ha estado trabajando estrechamente con ellos desde que se detectó, compartiendo inteligencia, rastreando fondos y apoyando la recuperación. En momentos como este, la industria se une contra los atacantes. El trabajo continúa”, aseveró Teng.
Por su parte, Vugar Usi, CEO de MEXC, informó que entabló comunicación directa con los afectados. “Bitget es una empresa y un equipo que conozco muy bien; contactamos al equipo a primera hora de esta mañana al enterarnos del incidente. MEXC está lista para apoyar a Bitget en cualquier forma que podamos. En momentos como este, la industria es más fuerte cuando nos mantenemos juntos”, afirmó Usi.
Asimismo, Sumit Gupta, cofundador del exchange de india CoinDCX, expresó su respaldo a la dirección de Bitget. “Triste enterarme del incidente en Bitget. La industria es más fuerte cuando nos mantenemos juntos. El equipo de CoinDCX está en standby para ayudar en cualquier forma que podamos, Gracy. Estoy seguro de que el equipo y el ecosistema saldrán más fuertes”, manifestó Gupta.
Este despliegue coordinado busca contener el flujo de los fondos drenados en un ataque cuyas cifra está estimada en 351,6 millones de dólares. El incidente abarcó la salida de ether (ETH), avalanche (AVAX), BNB, las stablecoins USDT, USDT0 y USDC, el token XAUT y otras criptomonedas, como reportó CriptoNoticias.
Respecto al origen de la brecha, la CEO de la empresa, Gracy Chen, reveló el vector utilizado por los atacantes. «El atacante comprometió un servidor crítico de la infraestructura de nuestra wallet, manipuló los registros de transacciones e indujo al sistema de aprobación para transferir los fondos», detalló Chen.
Sin embargo, la ejecutiva aclaró que la falla no comprometió las claves privadas de las cuentas de los usuarios, descartando un impacto directo en la custodia de las llaves de acceso individual. Para esclarecer completamente el evento, la investigación se mantiene activa mediante el trabajo conjunto de los equipos de ciberseguridad de las casas de cambio y el análisis forense de las firmas especializadas Mandiant y SlowMist.
#BitgetBreachForgedRequestsNotStolenKeys #bybit #MEXC #Binance #Bitget $BNB $AVAX $ETH
@richardteng @Cointelegraph @CoinDesk @Binance_News
{web3_wallet_create}(10x54d2252757e1672eead234d27b1270728ff90581)
{web3_wallet_create}(10x11eef04c884e24d9b7b4760e7476d06ddf797f36)
{web3_wallet_create}(10x3c3a81e81dc49a522a592e7622a7e711c06bf354)
🤝 CEO de exchanges como Binance y Bybit cooperan con Bitget tras sufrir un hackeo de 351,6 millones
Comunidad se une en apoyo a Bitget tras el ataque sufrido
Líderes de la industria de criptomonedas manifestaron su respaldo al exchange tras la vulnerabilidad que generó la pérdida de USD 350 millones.
Bitget cuenta con la colaboración de firmas de seguridad externas.
Ejecutivos de Bybit, Binance y MEXC ofrecieron recursos de rastreo y seguridad a Bitget.
El fallo abarcó la salida de ETH, AVAX, BNB y stablecoins, pero no afectó claves privadas.
Diversos ejecutivos de exchanges de criptomonedas manifestaron un respaldo operativo y técnico a Bitget. El pronunciamiento conjunto ocurre en respuesta a una brecha de seguridad que afectó la infraestructura del servicio.
Firma a firma, los directivos ofrecieron herramientas de rastreo y recursos de ciberseguridad para mitigar los daños. Ben Zhou, CEO de Bybit, fue uno de los primeros en poner a disposición su infraestructura de análisis forense.
“El equipo de Bybit está en standby para ayudar en cualquier forma que podamos. Bitget nos ayudó cuando tuvimos el hack. Estamos actualizando lazarusbounty.com para ayudar a Bitget a capturar y rastrear el movimiento de los fondos robados”, declaró Zhou.
Bybit sufrió una extracción de fondos por 1.500 millones de dólares en 2025, marco en el que contó con la cooperación de Bitget.
A la iniciativa se sumó Richard Teng, CEO de Binance, quien confirmó la asistencia entre departamentos técnicos. “Estamos con Bitget y sus usuarios tras el incidente reciente. Nuestro equipo de seguridad ha estado trabajando estrechamente con ellos desde que se detectó, compartiendo inteligencia, rastreando fondos y apoyando la recuperación. En momentos como este, la industria se une contra los atacantes. El trabajo continúa”, aseveró Teng.
Por su parte, Vugar Usi, CEO de MEXC, informó que entabló comunicación directa con los afectados. “Bitget es una empresa y un equipo que conozco muy bien; contactamos al equipo a primera hora de esta mañana al enterarnos del incidente. MEXC está lista para apoyar a Bitget en cualquier forma que podamos. En momentos como este, la industria es más fuerte cuando nos mantenemos juntos”, afirmó Usi.
Asimismo, Sumit Gupta, cofundador del exchange de india CoinDCX, expresó su respaldo a la dirección de Bitget. “Triste enterarme del incidente en Bitget. La industria es más fuerte cuando nos mantenemos juntos. El equipo de CoinDCX está en standby para ayudar en cualquier forma que podamos, Gracy. Estoy seguro de que el equipo y el ecosistema saldrán más fuertes”, manifestó Gupta.
Este despliegue coordinado busca contener el flujo de los fondos drenados en un ataque cuyas cifra está estimada en 351,6 millones de dólares. El incidente abarcó la salida de ether (ETH), avalanche (AVAX), BNB, las stablecoins USDT, USDT0 y USDC, el token XAUT y otras criptomonedas, como reportó CriptoNoticias.
Respecto al origen de la brecha, la CEO de la empresa, Gracy Chen, reveló el vector utilizado por los atacantes. «El atacante comprometió un servidor crítico de la infraestructura de nuestra wallet, manipuló los registros de transacciones e indujo al sistema de aprobación para transferir los fondos», detalló Chen.
Sin embargo, la ejecutiva aclaró que la falla no comprometió las claves privadas de las cuentas de los usuarios, descartando un impacto directo en la custodia de las llaves de acceso individual. Para esclarecer completamente el evento, la investigación se mantiene activa mediante el trabajo conjunto de los equipos de ciberseguridad de las casas de cambio y el análisis forense de las firmas especializadas Mandiant y SlowMist.
#BitgetBreachForgedRequestsNotStolenKeys #bybit #MEXC #Binance #Bitget $BNB $AVAX $ETH
@Richard Teng @Cointelegraph @CoinDesk @Binance News
4
111
Войдите, чтобы посмотреть больше материала
Присоединяйтесь к пользователям криптовалют по всему миру на Binance Square
⚡️ Получайте новейшую и полезную информацию о криптоактивах.
💬 Нам доверяет крупнейшая в мире криптобиржа.
👍 Получите достоверные аналитические данные от верифицированных создателей контента.
Эл. почта/номер телефона
В тренде
1
#BinanceKZ
Просмотров: 7,177
45 обсуждают
2
#CircleMints500MUSDCOnSolana
Просмотров: 3,740
235 обсуждают
3
#PolymarketBankFailureBetsDrawFDICConcern
Просмотров: 15,959
487 обсуждают
4
#BlackRockBuildsTokenizedPortfoliosForOndo
Просмотров: 12,209
330 обсуждают
5
#BitwiseFilesToListNEARETFOnNYSEArca
Просмотров: 13,265
320 обсуждают
6
#SECCommissionerPeirceToLeaveOct2
Просмотров: 14,021
264 обсуждают
7
#SECSaysBuybacksUpgradesDontMakeTokenSecurity
Просмотров: 15,184
247 обсуждают
8
#StrategyProposesDailyDividendsForPreferreds
Просмотров: 2,179
69 обсуждают
9
#CircleTetherFreezeBitgetHackerWallet
Просмотров: 994
40 обсуждают
10
#CoinMarketCapCompletesCoinglassAcquisition
Просмотров: 4,291
69 обсуждают