

#security
security
ကြည့်ရှုမှု 1.9M ကြိမ်
5,363 ဦး ဆွေးနွေးနေသည်
ရေပန်းစားသော
နောက်ဆုံး

Bithumb bị tấn công! Sàn giao dịch lớn thứ hai Hàn Quốc vừa báo cáo một vụ rò rỉ dữ liệu nội bộ nghiêm trọng.
Hệ thống di động nhân viên bị xâm nhập, thông tin cá nhân bị đánh cắp. TIN TỐT là Bithumb khẳng định nền tảng giao dịch và tài sản của khách hàng KHÔNG BỊ ảnh hưởng, không có thiệt hại quỹ nào.
Tuy nhiên, sự cố này gây chấn động không nhỏ. Nó diễn ra trong bối cảnh làn sóng tấn công mạng đang càn quét ít nhất 16 công ty tài chính Hàn Quốc khác, từ Daishin Securities đến các quỹ đầu tư.
Dù tài sản được bảo toàn, vụ việc tại $BITHUMB vẫn là lời nhắc nhở đắt giá về rủi ro bảo mật luôn rình rập, đặc biệt khi FUD có thể bùng phát bất cứ lúc nào trên thị trường.
Liệu các sàn giao dịch có thực sự an toàn tuyệt đối trước những cuộc tấn công ngày càng tinh vi này không?
#Crypto #Security
·
--
Article
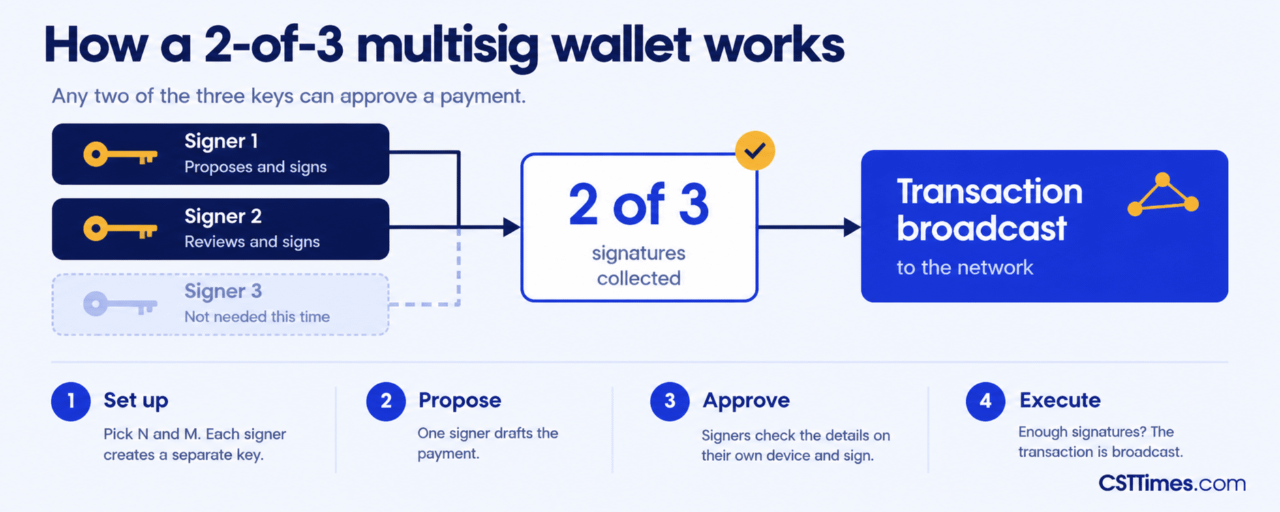
One wallet, several keys, and still more than $1.5 billion gone.In February 2025, attackers drained Bybit's Ethereum multisig cold wallet. No keys were stolen. The signers were shown a routine-looking transfer and approved it.
The lesson: multisig protects keys, not judgment.
What a multisig wallet is
It needs M of N keys to approve a payment. In a 2-of-3 wallet, any two keys can sign. One stolen key cannot spend. One lost key does not lock you out.
Common setups
2-of-2: both keys needed, losing one locks the funds2-of-3: the usual pick for individuals and small teams3-of-5: larger teams, slower approvals
5 checks before you start
1️⃣ Pick your threshold deliberately
2️⃣ Spread keys across separate devices and places
3️⃣ Back up every seed phrase (on Bitcoin, the wallet descriptor too)
4️⃣ Read the address and amount on the signing device's own screen
5️⃣ Test with a small amount first
Follow CSTTimes for more guide & information about Crypto, finance, and Tech:
Full guide with the single-key vs multisig vs MPC table and an FAQ:
CSTTimes dot com:
One wallet, several keys, and still more than $1.5 billion gone.
In February 2025, attackers drained Bybit's Ethereum multisig cold wallet. No keys were stolen. The signers were shown a routine-looking transfer and approved it.
The lesson: multisig protects keys, not judgment.
What a multisig wallet is
It needs M of N keys to approve a payment. In a 2-of-3 wallet, any two keys can sign. One stolen key cannot spend. One lost key does not lock you out.
Common setups
2-of-2: both keys needed, losing one locks the funds2-of-3: the usual pick for individuals and small teams3-of-5: larger teams, slower approvals
5 checks before you start
1️⃣ Pick your threshold deliberately
2️⃣ Spread keys across separate devices and places
3️⃣ Back up every seed phrase (on Bitcoin, the wallet descriptor too)
4️⃣ Read the address and amount on the signing device's own screen
5️⃣ Test with a small amount first
Follow CSTTimes for more guide & information about Crypto, finance, and Tech:
Full guide with the single-key vs multisig vs MPC table and an FAQ:
CSTTimes dot com:
78
Bảo mật ví cứng đang bị đe dọa nghiêm trọng! Keystone vừa tuyên bố tiêu hủy 18,835 ví chưa bán và tạm dừng giao hàng sau vụ hack ngày 20/10.
Kẻ tấn công không chỉ lấy được 25,964 hồ sơ khách hàng mà còn TRỘM MẤT KHÓA MẬT MÃ dùng để xác thực thiết bị chính hãng. Đây là thảm họa!
Điều này có nghĩa là ví giả, kém chất lượng CÓ THỂ ĐƯỢC XÁC THỰC LÀ HÀNG CHÍNH HÃNG. Rủi ro mất tiền của người dùng tăng vọt nếu mua phải ví lừa đảo.
Dù Keystone trấn an private keys và funds chưa bị ảnh hưởng, người dùng phải CỰC KỲ CẢNH GIÁC với các tin nhắn lừa đảo. Hãng sẽ thay thế khóa bị lộ trong các sản phẩm mới.
Sự cố này có làm bạn mất niềm tin vào ví cứng không? Hay đây chỉ là bài học về rủi ro tập trung?
#HardwareWallet #Security
$BTC $ETH
2
341

Tonight's warning breaks the safety check most of us rely on — it stopped me mid-scroll.
SlowMist found malicious code in the Udesk chat widget: a tampered file loading a second script from a lookalike domain, udeskqlobal[.]com, harvesting login data from pages that load it. On deposit pages at MGBX, Biking Exchange and BitxEX, it goes further, swapping displayed deposit addresses every 200 milliseconds for attacker wallets across BTC, EVM chains, Tron, Solana, Litecoin and Dogecoin, and rewriting clipboard copies.
What worries me most: checking the pasted address against the page won't catch it, since both can show the same tampered value. SlowMist hasn't confirmed any funds lost or how the code got in — that part is unknown.
If you use those platforms, verify deposit addresses beyond the page. Context only: $BTC $80,542 (+0.5%/24h), $ETH $2,347 (+1.2%), Binance spot, 23:55 WIB — no reaction tied to this warning. DYOR.
When did you last verify a deposit address elsewhere?
$BTC #CryptoNews #Security #Udesk #SlowMist

·
--
порада «звір перші й останні символи після вставки» цього разу не рятує.
SlowMist 27 жовтня розкрив скрипт у віджеті техпідтримки Udesk, який підміняє адресу депозиту одночасно на сторінці і в буфері обміну. вставив, звірив зі сторінкою — все збігається. бо фальшиве і там, і там.
як воно працює, по-простому:
- сайт не ламали, код приїжджає через підключений чат підтримки, з домену udeskqlobal, де замість g стоїть q
- сторінку депозиту сканує кожні 200 мілісекунд, тобто підміна стоїть раніше, ніж ти встигнеш скопіювати. адреси BTC, EVM, TRON, Solana, LTC, DOGE міняє на свої
- заодно читає cookies і дані сесії
масштаб без паніки: у звіті серед цілей підміни три майданчики, великих бірж там нема. і це звіт вендора безпеки.
шо працює: адресу депозиту звіряти не зі сторінки, а з іншого каналу. застосунок, інший пристрій, історія старих депозитів.
наступне, шо чекаю: чи список цілей виросте більше ніж за три
#SlowMist #security
35

·
--
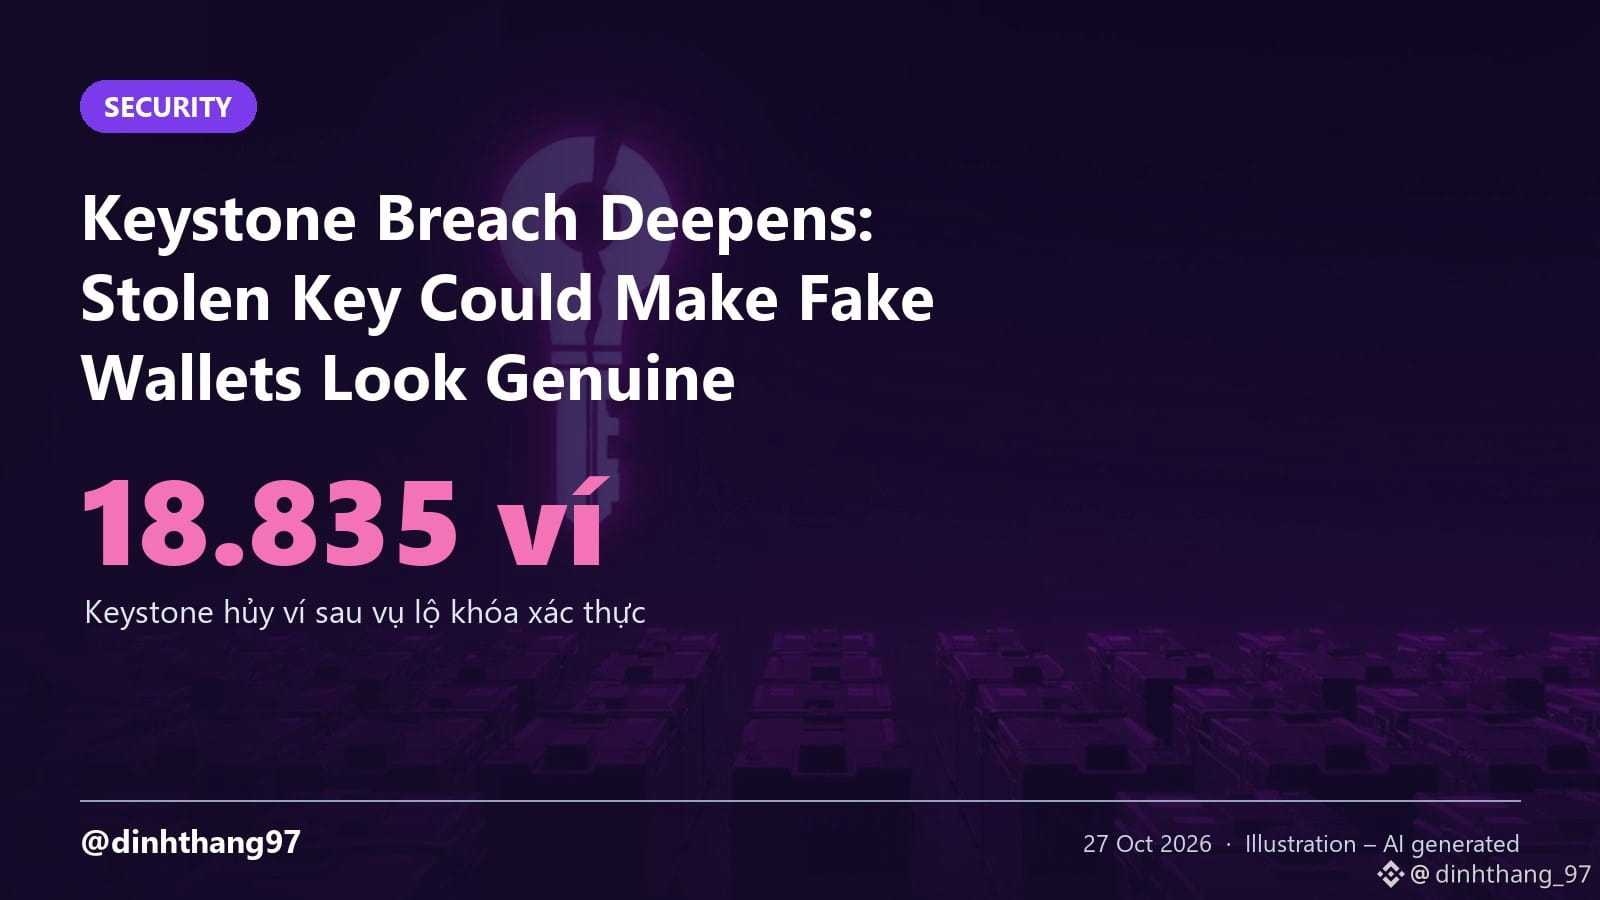
Keystone Breach Deepens: Stolen Key Could Make Fake Wallets Look Genuine
• Hackers took the device-authentication key used to verify Keystone wallets as genuine
• Keystone will destroy 18,835 wallets; owners of old-key devices received after Oct. 20 need extra authenticity checks
• The earlier website breach also exposed hardware wallet buyers' addresses
My view: a stolen attestation key is worse than leaked addresses because it can let counterfeit devices pass verification. Recent buyers should follow only official vendor guidance. Not financial advice, DYOR.
#Keystone #Security
54
စိစစ်အတည်ပြုထားသည်
$ZQRA We stand by what we’ve said. We continue to grow—transparently, reliably, and with a focus on our community.
ZQORA is undergoing a full audit by Cyberscope
https://app.cyberscope.io/audits/zqra#security #cyberscope #zqora
$ZQRA We stand by what we’ve said. We continue to grow—transparently, reliably, and with a focus on our community.
ZQORA is undergoing a full audit by Cyberscope
https://app.cyberscope.io/audits/zqra#security #cyberscope #zqora
ZQORA is undergoing a full audit by Cyberscope
https://app.cyberscope.io/audits/zqra#security #cyberscope #zqora

User-b6fcbf54:
very nice ZQORA❤
1
1
102

·
--
硬件钱包厂商 Keystone 爆出安全漏洞,导致 2.5 万客户数据及设备密钥泄露,为防患未然销毁了 1.8 万台未发货设备并暂停配送,但私钥未受威胁。
Keystone 这波操作太狠了,直接炸掉 1.8 万台未发货设备。虽然私钥安全无虞,但这种“物理销毁”式止损,说明事故严重程度远超想象。品牌信誉重创,短期情绪面承压,但长期看硬件冷钱包依然是最后的堡垒,只是选择权变了。
#Keystone #HardwareWallet #Security
硬件钱包厂商 Keystone 爆出安全漏洞,导致 2.5 万客户数据及设备密钥泄露,为防患未然销毁了 1.8 万台未发货设备并暂停配送,但私钥未受威胁。
Keystone 这波操作太狠了,直接炸掉 1.8 万台未发货设备。虽然私钥安全无虞,但这种“物理销毁”式止损,说明事故严重程度远超想象。品牌信誉重创,短期情绪面承压,但长期看硬件冷钱包依然是最后的堡垒,只是选择权变了。
#Keystone #HardwareWallet #Security
Keystone 这波操作太狠了,直接炸掉 1.8 万台未发货设备。虽然私钥安全无虞,但这种“物理销毁”式止损,说明事故严重程度远超想象。品牌信誉重创,短期情绪面承压,但长期看硬件冷钱包依然是最后的堡垒,只是选择权变了。
#Keystone #HardwareWallet #Security
3
🔥 Ripple just handed over ≈ 1,200 KB of DPRK hacking playbooks to the Crypto ISAC — the largest single-state‑actor intel dump the crypto world has seen.
📊 The timing is critical as XRP slides 0.8% to $1.2877 with a bearish RSI of 44.1, while the broader market sits neutral (50/100), meaning any security scare can tip sentiment sharply.
💡 Smart money is already recalibrating: top traders remain net long on BTC (65.7%) and ETH (64.1%) despite bearish MACD signals, but on‑chain wallets are flagging a surge in defensive positioning on #XRP, and #CryptoISAC alerts are driving a 12% rise in #Security‑focused token inflows across BSC. Funding rates stay positive (+0.0100% BTC, +0.0066% ETH), suggesting longs are willing to pay for protection.
🚀 Watch the $1.30 resistance on XRP – a clean close above it could trigger a 15% bounce as institutional holders re‑enter, while a break below $1.25 may accelerate outflows and push the market deeper into risk‑off mode. #XRPWatch
❓ If state‑level intel suddenly validates your worst‑case security scenario, will you double‑down on defensive assets or exit crypto entirely?
10

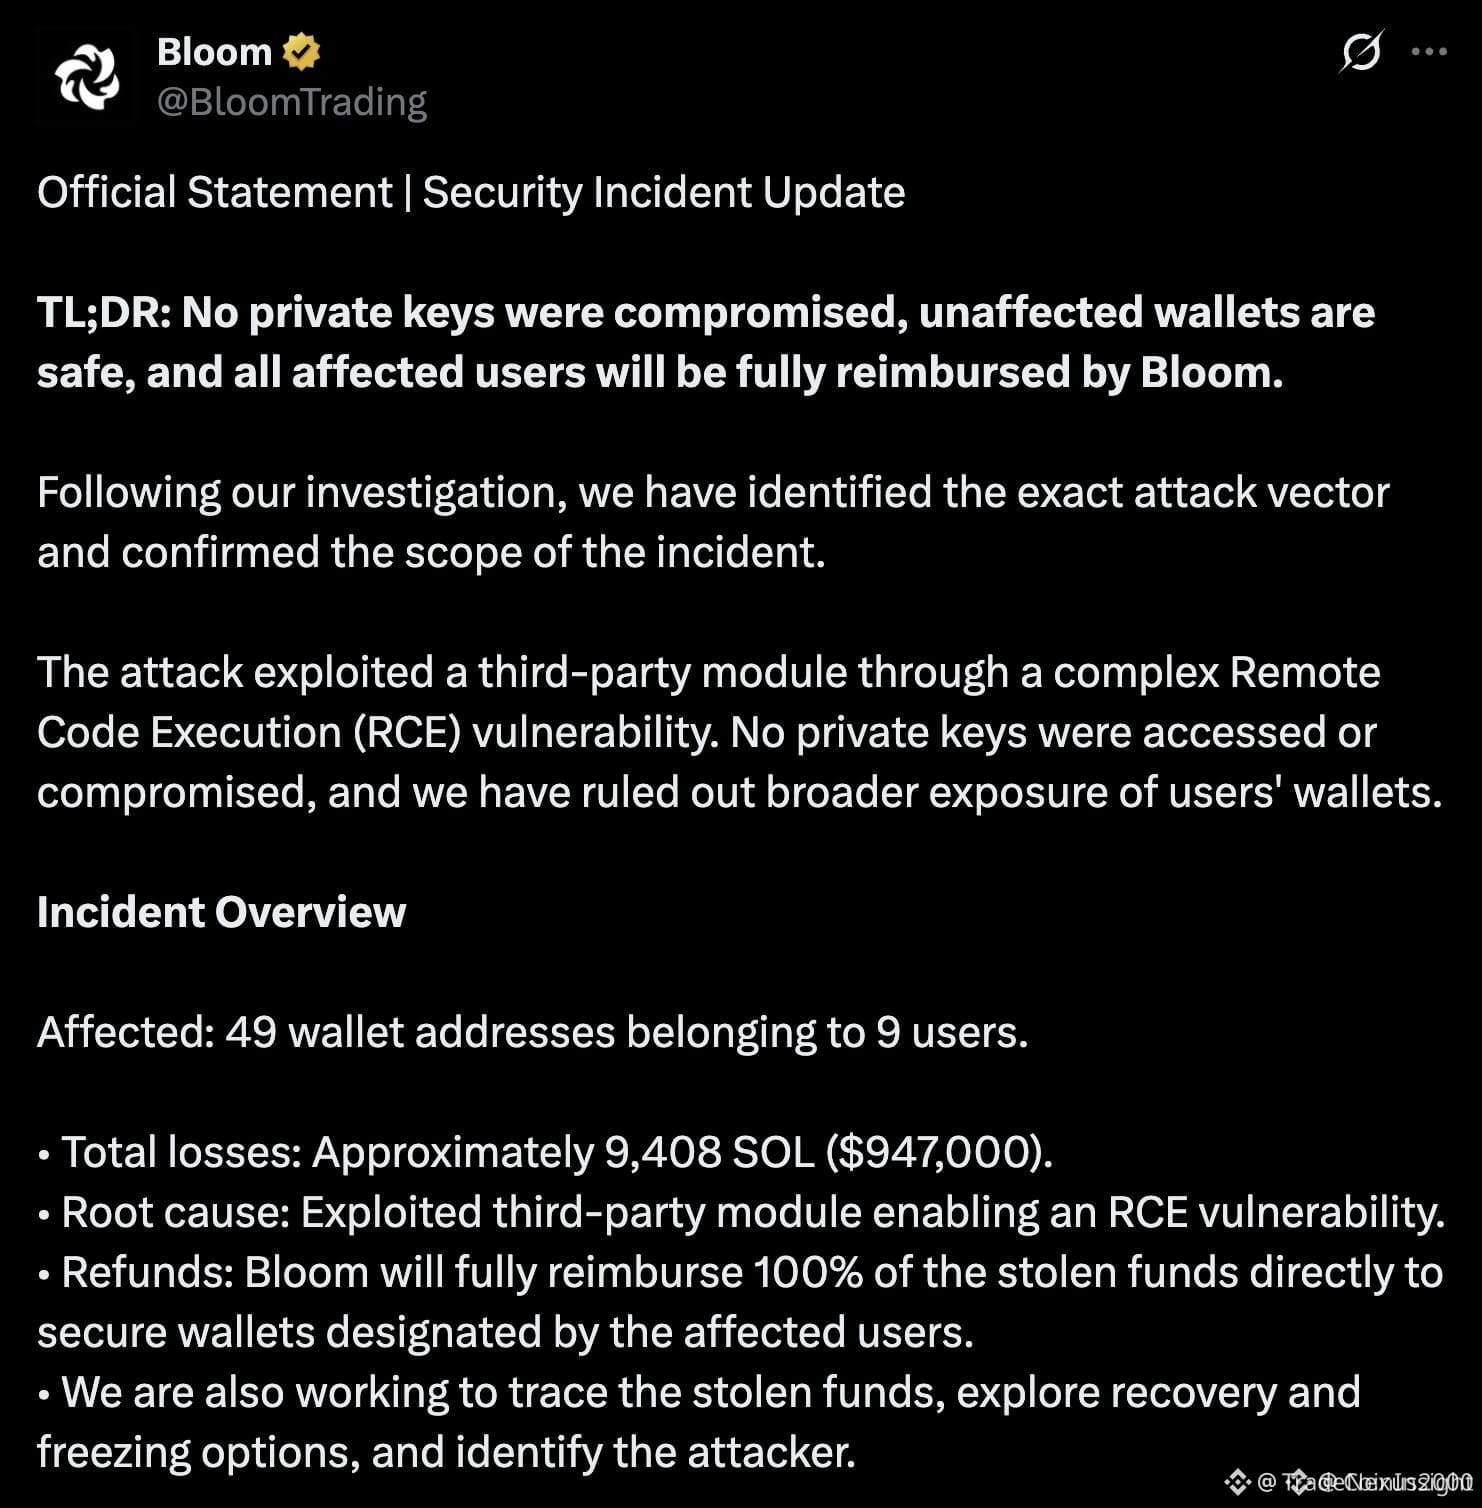
🚨 $SOL SECURITY BREACH EXPOSES THIRD-PARTY RISK – 9,408 SOL STOLEN 🛡️
📊 BloomTrading disclosed a remote code execution flaw in a third‑party module, resulting in the theft of 9,408 SOL (~$947K). 🔍 The breach bypassed wallet private keys, underscoring that software supply chains can be the weakest link. 💡 Bloom promises full reimbursement via new, hardened wallets, but the incident raises a broader question about systemic safeguards. 🦈 As smart money eyes platform integrity, any lingering vulnerabilities could trigger liquidity flight.
💬 Do you think current crypto security measures are enough to guard against such third‑party exploits? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SOL #Security #CryptoRisk #BloomTrading
🔥 🛡️
14
·
--
Виробник хардверних гаманців Keystone повідомив, що злам сайту розкрив дані клієнтів. Після таких витоків типовий ризик це фішинг: шахраї надсилають листи від імені компанії з проханням «підтвердити» гаманець. Ніхто, окрім вас, не повинен просити seed-фразу. Перевіряйте кожен лист і посилання, особливо тим, хто тримає $BTC та $ETH у холодному зберіганні.
Ви користуєтесь апаратним гаманцем? 👇
#Security
Ви користуєтесь апаратним гаманцем? 👇
#Security
86

🔴 $BTC VULNERABILITY EXPOSES HIGH‑FEE ATTACK VECTOR – PATCH DEPLOYED! 🚨
📊 Malicious nodes hijacked the fee‑bump flow, replacing legit transactions with forged ones and waiting for users to approve inflated fees – essentially authorizing a covert transfer. 🦈 This “fee‑pump” trick leverages the same mechanism traders use to speed up confirmations, turning it against them.
💡 Developers have now patched the loophole, but the episode underscores the hidden risk of interacting with untrusted server‑side wallet features. Stay sharp, audit your fee‑bump settings, and consider offline signing for critical moves. 💬 How are you tightening your wallet security after this incident? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #WalletRisk #Crypto
🛡️ 🔥
9
·
--
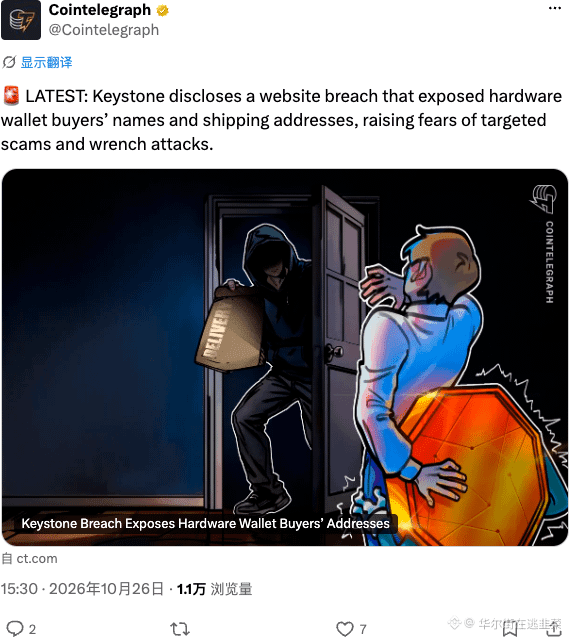
Keystone discloses breach exposing hardware wallet buyers' shipping details
Names, addresses and order data were accessed via a Shopify API vulnerability, with researcher warnings of phishing and physical attacks. Affected customers have reported scam calls claiming to be law enforcement.
Have you been notified by Keystone?
#Security #HardwareWallet $BTC
Source: cointelegraph.com
121

·
--
⚠️紧急提醒!比特币钱包出现漏洞,黑客能替换你的交易并盗取资金!当你急着提高手续费加速支付时,危险就来了。已经有用户因此损失比特币,开发者虽已修复,但大家务必提高警惕!
⚠️Emergency alert! Bitcoin wallet bug allows hackers to replace your transactions and steal funds! When you try to speed up payments by increasing fees, you're at risk. At least one user has already lost BTC, though the flaw has been patched. Stay vigilant!
#Bitcoin #Security $BTC
⚠️Emergency alert! Bitcoin wallet bug allows hackers to replace your transactions and steal funds! When you try to speed up payments by increasing fees, you're at risk. At least one user has already lost BTC, though the flaw has been patched. Stay vigilant!
#Bitcoin #Security $BTC
59

🚨 HARDWARE SECURITY SHOCKWAVE: LEDGER FACES A $500M LAWSUIT THREATENING $ETH ECOSYSTEM TRUST! 💥
Smart money knows cold storage is the bedrock of crypto, but legal battles are exposing severe cracks in legacy hardware defenses. 🔒 A massive $500M class-action lawsuit just hit Ledger over historic exploits and persistent phishing leaks that drained millions from $ETH holders. ⚠️
When user trust fractures, liquidity reacts fast as security-conscious whales re-evaluate where to park institutional size. 🏦 Smart security hygiene is no longer optional; it is the ultimate alpha for surviving this market. 🔍
💬 Are you keeping your heavy bags on hardware wallets or moving toward multi-sig setups? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #HardwareWallet #CryptoNews
🛡️ 👁️
1
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
အီးမေးလ် / ဖုန်းနံပါတ်
ရေပန်းစားနေသော ခေါင်းစဉ်များ
1
#CanMicrosoftDeliverOnAI
ကြည့်ရှုမှု 214,106 ကြိမ်
1,816 ဦး ဆွေးနွေးနေသည်
2
#CanGoogleDefindItsCore
ကြည့်ရှုမှု 118,960 ကြိမ်
1,328 ဦး ဆွေးနွေးနေသည်
3
#EarningsSeason
ကြည့်ရှုမှု 5.8M ကြိမ်
27,762 ဦး ဆွေးနွေးနေသည်
4
#DatavaultAICantWithdrawBitcoinFromBiconomy
ကြည့်ရှုမှု 170 ကြိမ်
26 ဦး ဆွေးနွေးနေသည်
5
#FOMCWatch
ကြည့်ရှုမှု 9.2M ကြိမ်
29,028 ဦး ဆွေးနွေးနေသည်
6
#HKPlacesTokenizedFundSecondaryTradingUnderETFLikeFramework
ကြည့်ရှုမှု 427 ကြိမ်
22 ဦး ဆွေးနွေးနေသည်
7
#USGovSellsFTXLinkedAnthropicSharesFor$627M
ကြည့်ရှုမှု 701 ကြိမ်
27 ဦး ဆွေးနွေးနေသည်
8
#MoodysAssignsRLUSDA2LongTermDepositRating
ကြည့်ရှုမှု 5,031 ကြိမ်
190 ဦး ဆွေးနွေးနေသည်
9
#SKHynixUnveils$45BShareholderReturns
ကြည့်ရှုမှု 1,002 ကြိမ်
24 ဦး ဆွေးနွေးနေသည်
10
#OSMOPlansToBurn100MTokensFromCommunityPool
ကြည့်ရှုမှု 12,646 ကြိမ်
366 ဦး ဆွေးနွေးနေသည်