

#bitgetbreachforgedrequestsnotstolenkeys
bitgetbreachforgedrequestsnotstolenkeys
ມາແຮງ
ຫຼ້າສຸດ
·
--
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
{spot}(BTCUSDT)
{spot}(ETHUSDT)
{spot}(BNBUSDT)
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
SAQR77:
بيت منصة تافهة، بايننس احسنهم بكثير
1
3
8.9k
·
--
ສັນຍານໝີ
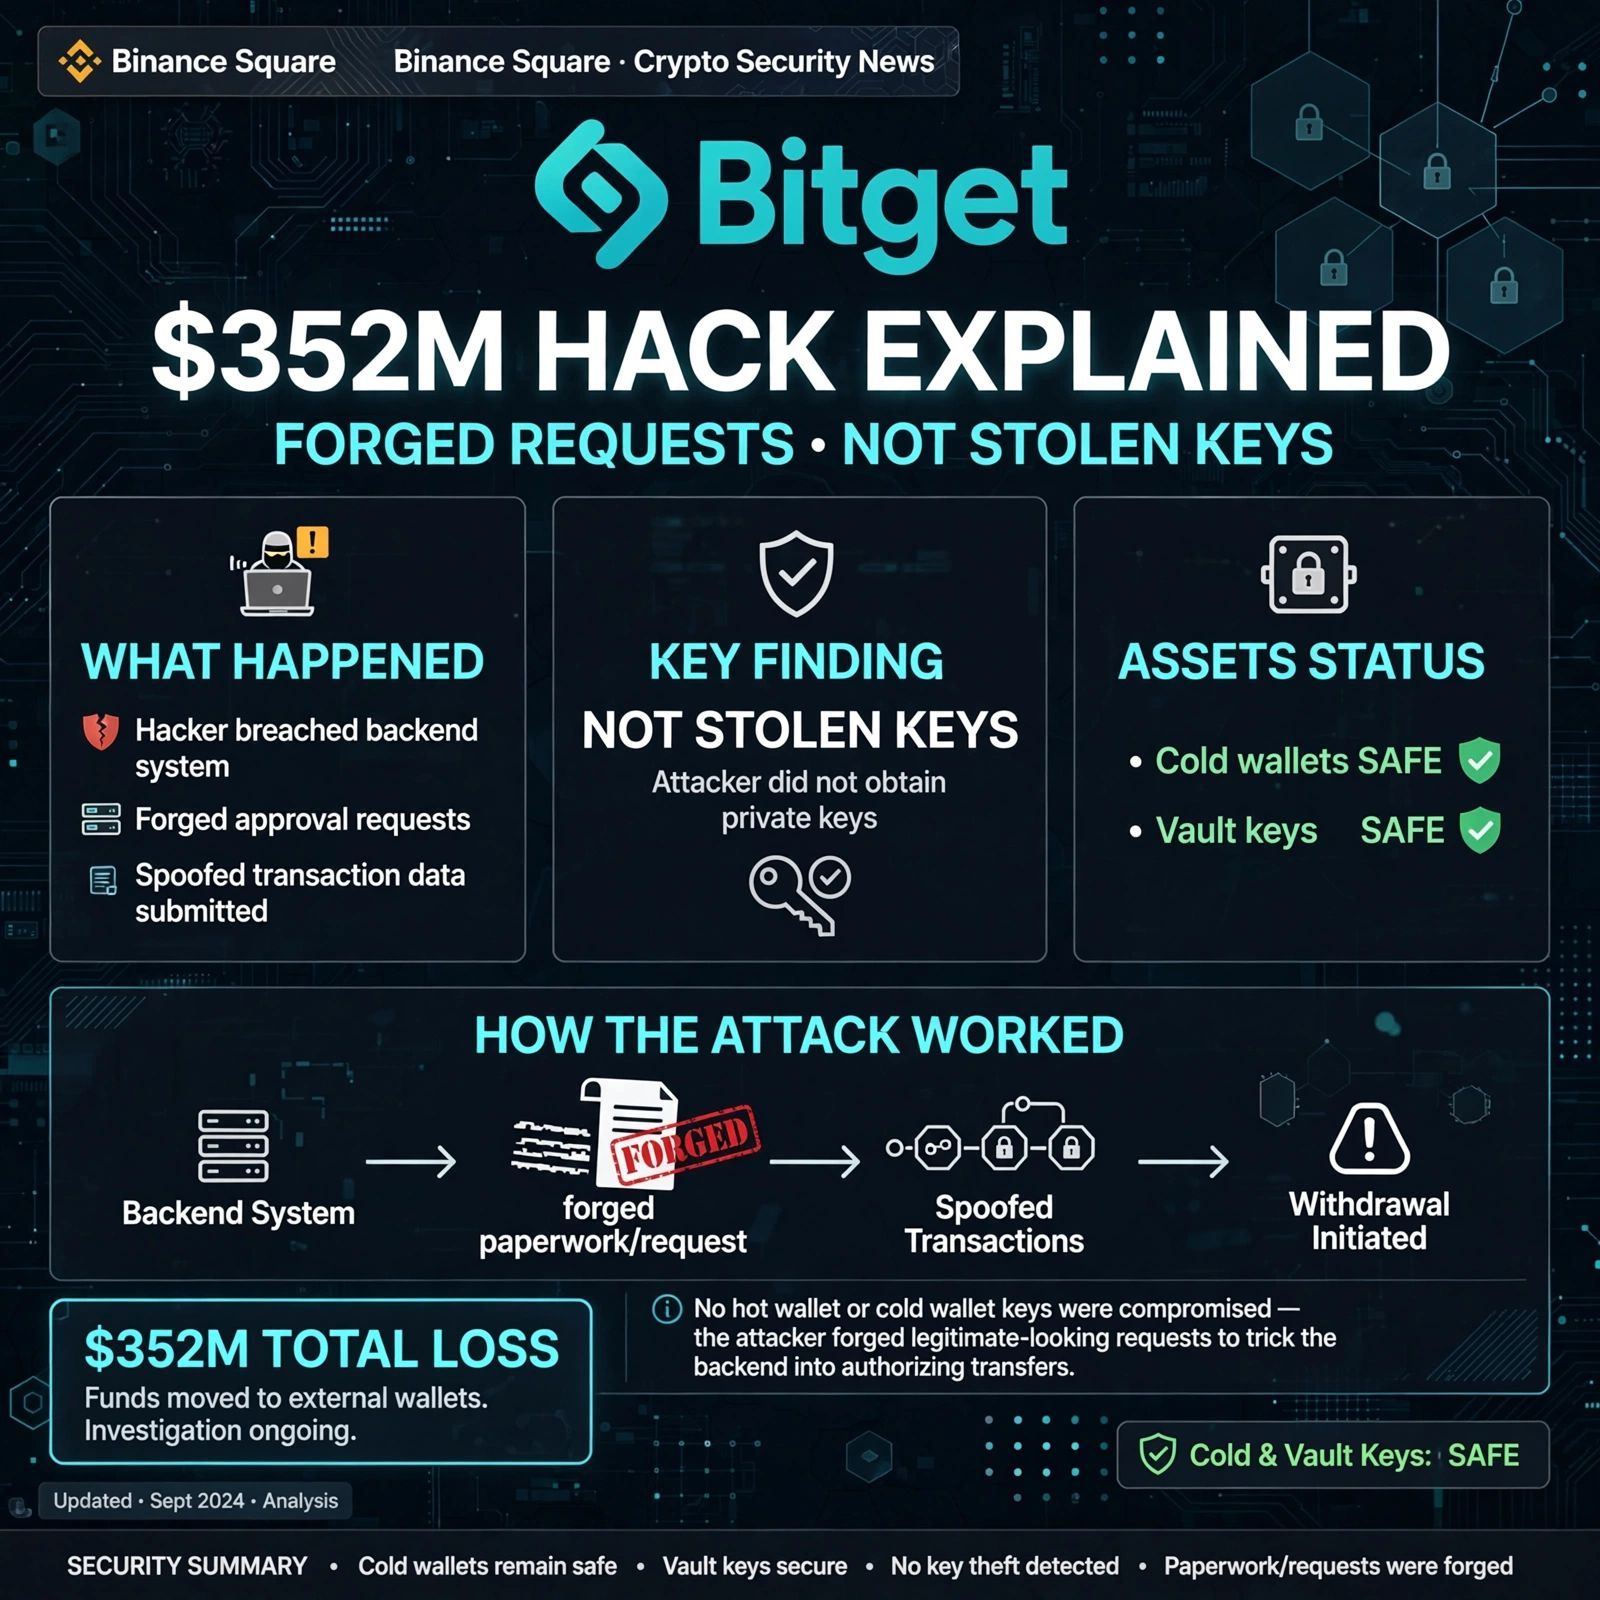
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
{future}(XRPUSDT)
{future}(TRXUSDT)
{future}(AVAXUSDT)
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
4
8.6k
·
--
Bitget Ungkap Insiden Keamanan $351,6 Juta
Bitget melaporkan bahwa pada 24 September 2026 pukul 18:31 UTC, sistem keamanannya mendeteksi transfer tidak sah yang melibatkan sejumlah hot wallet.
🔹 Total aset terdampak: sekitar $351,6 juta
🔹 Cold wallet Bitget dan mayoritas aset platform tetap aman
🔹 Bitget menyatakan dana pengguna tetap terlindungi
🔹 Insiden tercakup dalam User Protection Fund Bitget yang saat ini bernilai lebih dari $464 juta
🔹 Tim keamanan Bitget telah mengaktifkan prosedur tanggap darurat dan melakukan investigasi penuh
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
{future}(BABYUSDT)
$BTC
{future}(BTCUSDT)
Bitget Ungkap Insiden Keamanan $351,6 Juta
Bitget melaporkan bahwa pada 24 September 2026 pukul 18:31 UTC, sistem keamanannya mendeteksi transfer tidak sah yang melibatkan sejumlah hot wallet.
🔹 Total aset terdampak: sekitar $351,6 juta
🔹 Cold wallet Bitget dan mayoritas aset platform tetap aman
🔹 Bitget menyatakan dana pengguna tetap terlindungi
🔹 Insiden tercakup dalam User Protection Fund Bitget yang saat ini bernilai lebih dari $464 juta
🔹 Tim keamanan Bitget telah mengaktifkan prosedur tanggap darurat dan melakukan investigasi penuh
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
$BTC
Bitget melaporkan bahwa pada 24 September 2026 pukul 18:31 UTC, sistem keamanannya mendeteksi transfer tidak sah yang melibatkan sejumlah hot wallet.
🔹 Total aset terdampak: sekitar $351,6 juta
🔹 Cold wallet Bitget dan mayoritas aset platform tetap aman
🔹 Bitget menyatakan dana pengguna tetap terlindungi
🔹 Insiden tercakup dalam User Protection Fund Bitget yang saat ini bernilai lebih dari $464 juta
🔹 Tim keamanan Bitget telah mengaktifkan prosedur tanggap darurat dan melakukan investigasi penuh
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
$BTC
141

#bitgetbreachforgedrequestsnotstolenkeys
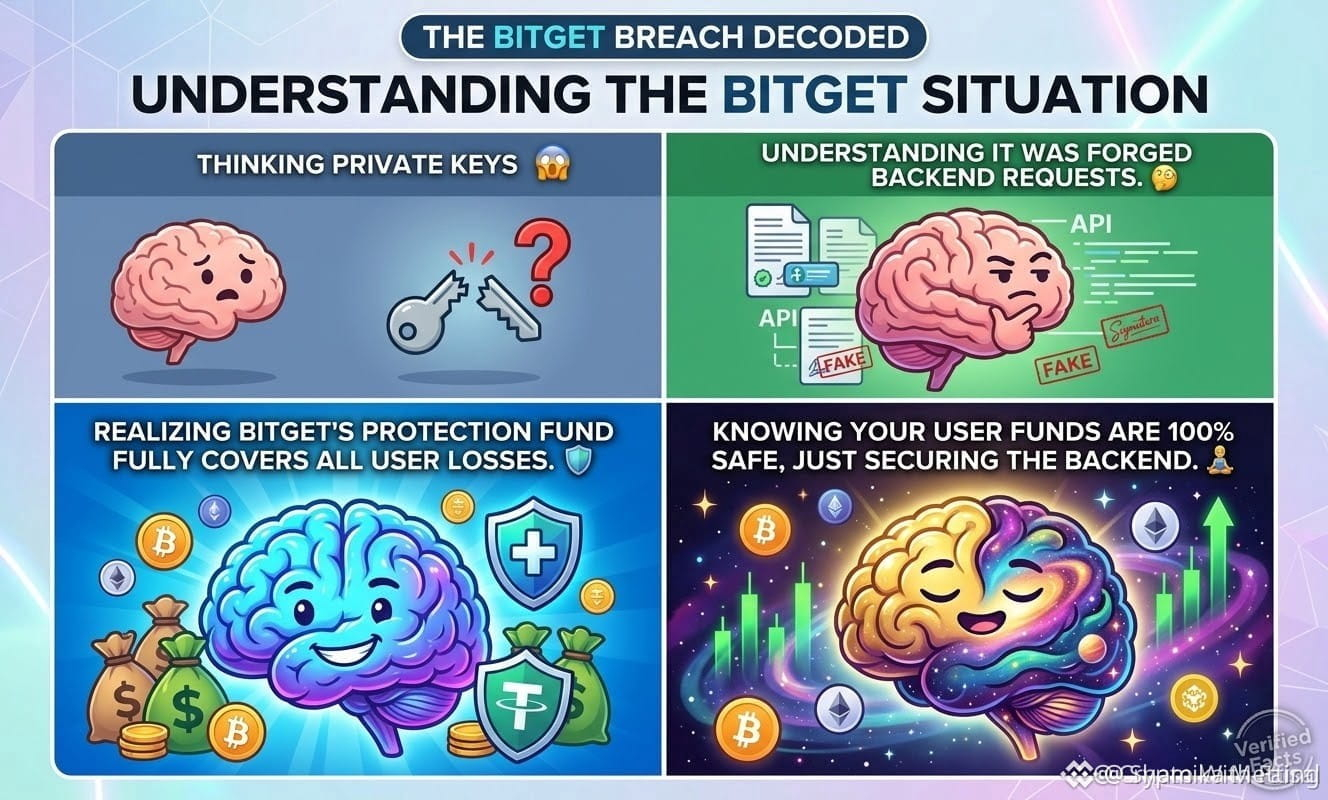
🚨 القصة الحقيقية وراء اختراق Bitget 🚨
عالم العملات الرقمية في حالة ضجة، لكن دعونا نزيل الضجيج بالأدلة المُثبتة حول اختراق Bitget بقيمة 351.6 مليون دولار.
تنبيه: الأمر ليس كما تتخيل.
لم يقم المهاجمون بسرقة مفاتيح الخزائن الخاصة! بدلاً من ذلك، اخترقوا نظامًا خلفيًا، وضلّلوا مستندات المعاملات، ومرروا طلبات سحب مُزيفة عبر عملية الموافقة الخاصة بـ Bitget نفسها.
لماذا يهم هذا التفصيل التقني؟
لأن سرقة المفاتيح تعني نزيفًا لا ينتهي. 🩸
الطلبات المُزيفة = سدّ الثغرة وإيقاف النزيف. 🛑
الأخبار الجيدة:
✅ المفاتيح في أمان: لم تغادر المفاتيح الخاصة مكانها.
✅ الخزائن مؤمنة: تم استهداف المحافظ الساخنة والساخنة-الدافئة فقط. تظل التخزين البارد آمنًا بنسبة 100%.
✅ المستخدمون بخير: صندوق الحماية لدى Bitget البالغ 464 مليون دولار يغطي بالكامل خسارة 351.6 مليون دولار.
تم إيقاف عمليات السحب مؤقتًا لإجراء مراجعة أمنية شاملة، لكن الرئيس التنفيذي Gracy Chen أكد أن أصول المستخدمين في أمان.
هذه الحادثة تثبت أن البنية التحتية للخلفية أصبحت ساحة المعركة الجديدة في Web3. انتبه وابقَ في أمان! 🛡️
متابعة من فضلكم
$AVAX
{future}(AVAXUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 القصة الحقيقية وراء اختراق Bitget 🚨
عالم العملات الرقمية في حالة ضجة، لكن دعونا نزيل الضجيج بالأدلة المُثبتة حول اختراق Bitget بقيمة 351.6 مليون دولار.
تنبيه: الأمر ليس كما تتخيل.
لم يقم المهاجمون بسرقة مفاتيح الخزائن الخاصة! بدلاً من ذلك، اخترقوا نظامًا خلفيًا، وضلّلوا مستندات المعاملات، ومرروا طلبات سحب مُزيفة عبر عملية الموافقة الخاصة بـ Bitget نفسها.
لماذا يهم هذا التفصيل التقني؟
لأن سرقة المفاتيح تعني نزيفًا لا ينتهي. 🩸
الطلبات المُزيفة = سدّ الثغرة وإيقاف النزيف. 🛑
الأخبار الجيدة:
✅ المفاتيح في أمان: لم تغادر المفاتيح الخاصة مكانها.
✅ الخزائن مؤمنة: تم استهداف المحافظ الساخنة والساخنة-الدافئة فقط. تظل التخزين البارد آمنًا بنسبة 100%.
✅ المستخدمون بخير: صندوق الحماية لدى Bitget البالغ 464 مليون دولار يغطي بالكامل خسارة 351.6 مليون دولار.
تم إيقاف عمليات السحب مؤقتًا لإجراء مراجعة أمنية شاملة، لكن الرئيس التنفيذي Gracy Chen أكد أن أصول المستخدمين في أمان.
هذه الحادثة تثبت أن البنية التحتية للخلفية أصبحت ساحة المعركة الجديدة في Web3. انتبه وابقَ في أمان! 🛡️
متابعة من فضلكم
$AVAX
🚨 القصة الحقيقية وراء اختراق Bitget 🚨
عالم العملات الرقمية في حالة ضجة، لكن دعونا نزيل الضجيج بالأدلة المُثبتة حول اختراق Bitget بقيمة 351.6 مليون دولار.
تنبيه: الأمر ليس كما تتخيل.
لم يقم المهاجمون بسرقة مفاتيح الخزائن الخاصة! بدلاً من ذلك، اخترقوا نظامًا خلفيًا، وضلّلوا مستندات المعاملات، ومرروا طلبات سحب مُزيفة عبر عملية الموافقة الخاصة بـ Bitget نفسها.
لماذا يهم هذا التفصيل التقني؟
لأن سرقة المفاتيح تعني نزيفًا لا ينتهي. 🩸
الطلبات المُزيفة = سدّ الثغرة وإيقاف النزيف. 🛑
الأخبار الجيدة:
✅ المفاتيح في أمان: لم تغادر المفاتيح الخاصة مكانها.
✅ الخزائن مؤمنة: تم استهداف المحافظ الساخنة والساخنة-الدافئة فقط. تظل التخزين البارد آمنًا بنسبة 100%.
✅ المستخدمون بخير: صندوق الحماية لدى Bitget البالغ 464 مليون دولار يغطي بالكامل خسارة 351.6 مليون دولار.
تم إيقاف عمليات السحب مؤقتًا لإجراء مراجعة أمنية شاملة، لكن الرئيس التنفيذي Gracy Chen أكد أن أصول المستخدمين في أمان.
هذه الحادثة تثبت أن البنية التحتية للخلفية أصبحت ساحة المعركة الجديدة في Web3. انتبه وابقَ في أمان! 🛡️
متابعة من فضلكم
$AVAX
1
2
·
--
ສັນຍານກະທິງ
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
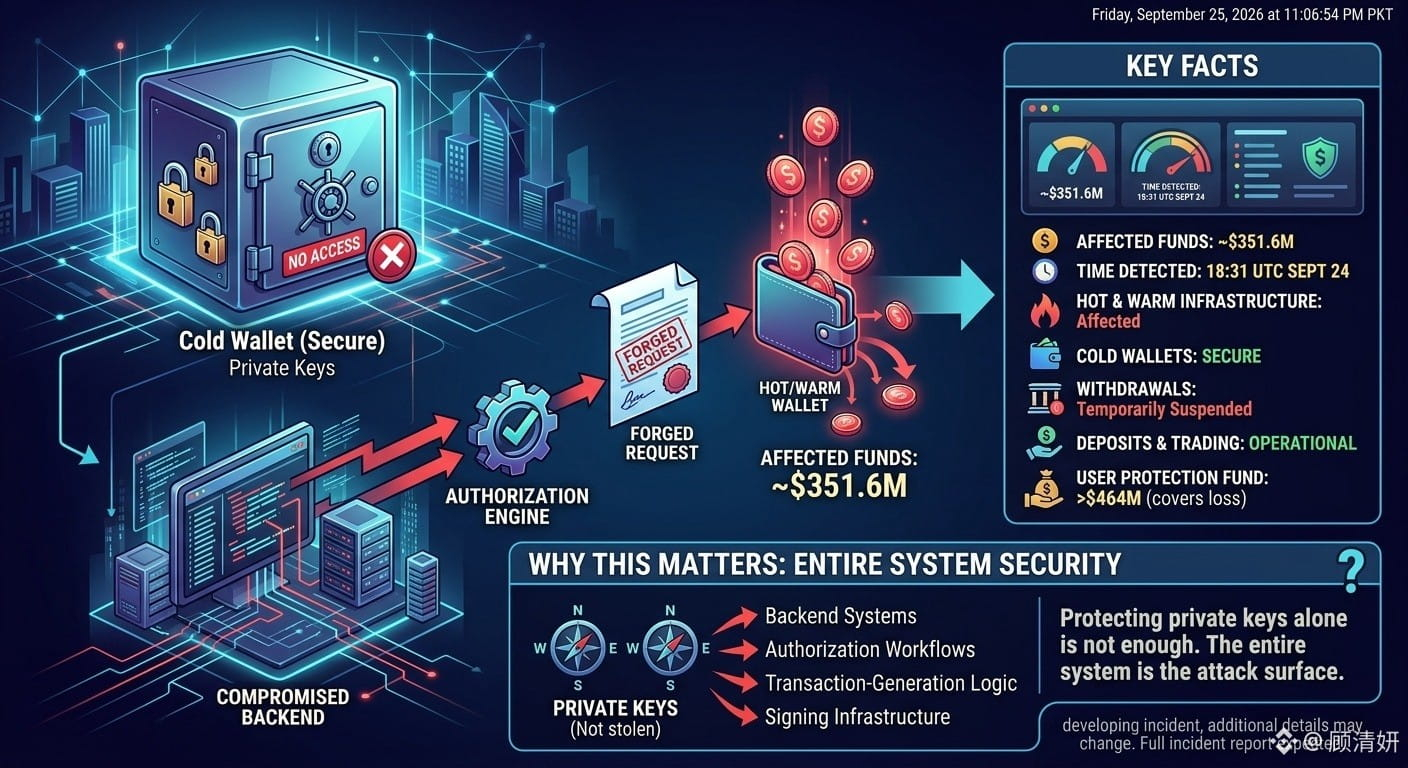
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
{future}(ARKUSDT)
{future}(PHAUSDT)
{spot}(QIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
7
🚨#Bitget says an attacker compromised part of its hot/warm wallet infrastructure, triggering unauthorized transfers worth an estimated $351.6M.
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
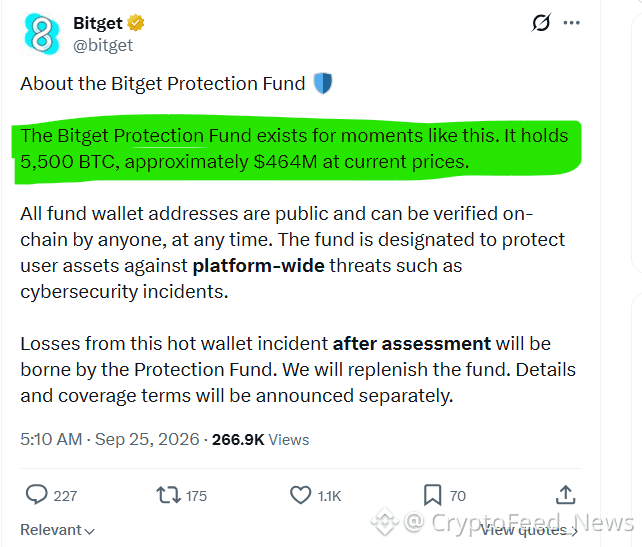
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
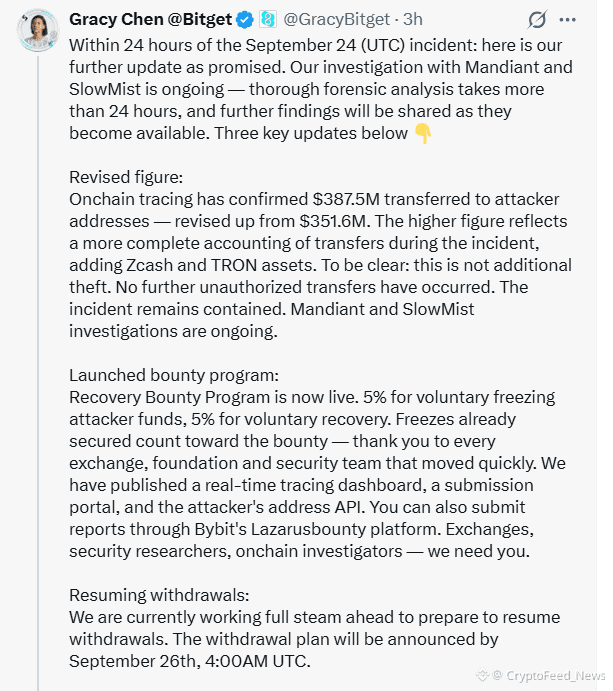
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
🚨#Bitget says an attacker compromised part of its hot/warm wallet infrastructure, triggering unauthorized transfers worth an estimated $351.6M.
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
28
#BitgetBreachForgedRequestsNotStolenKeys
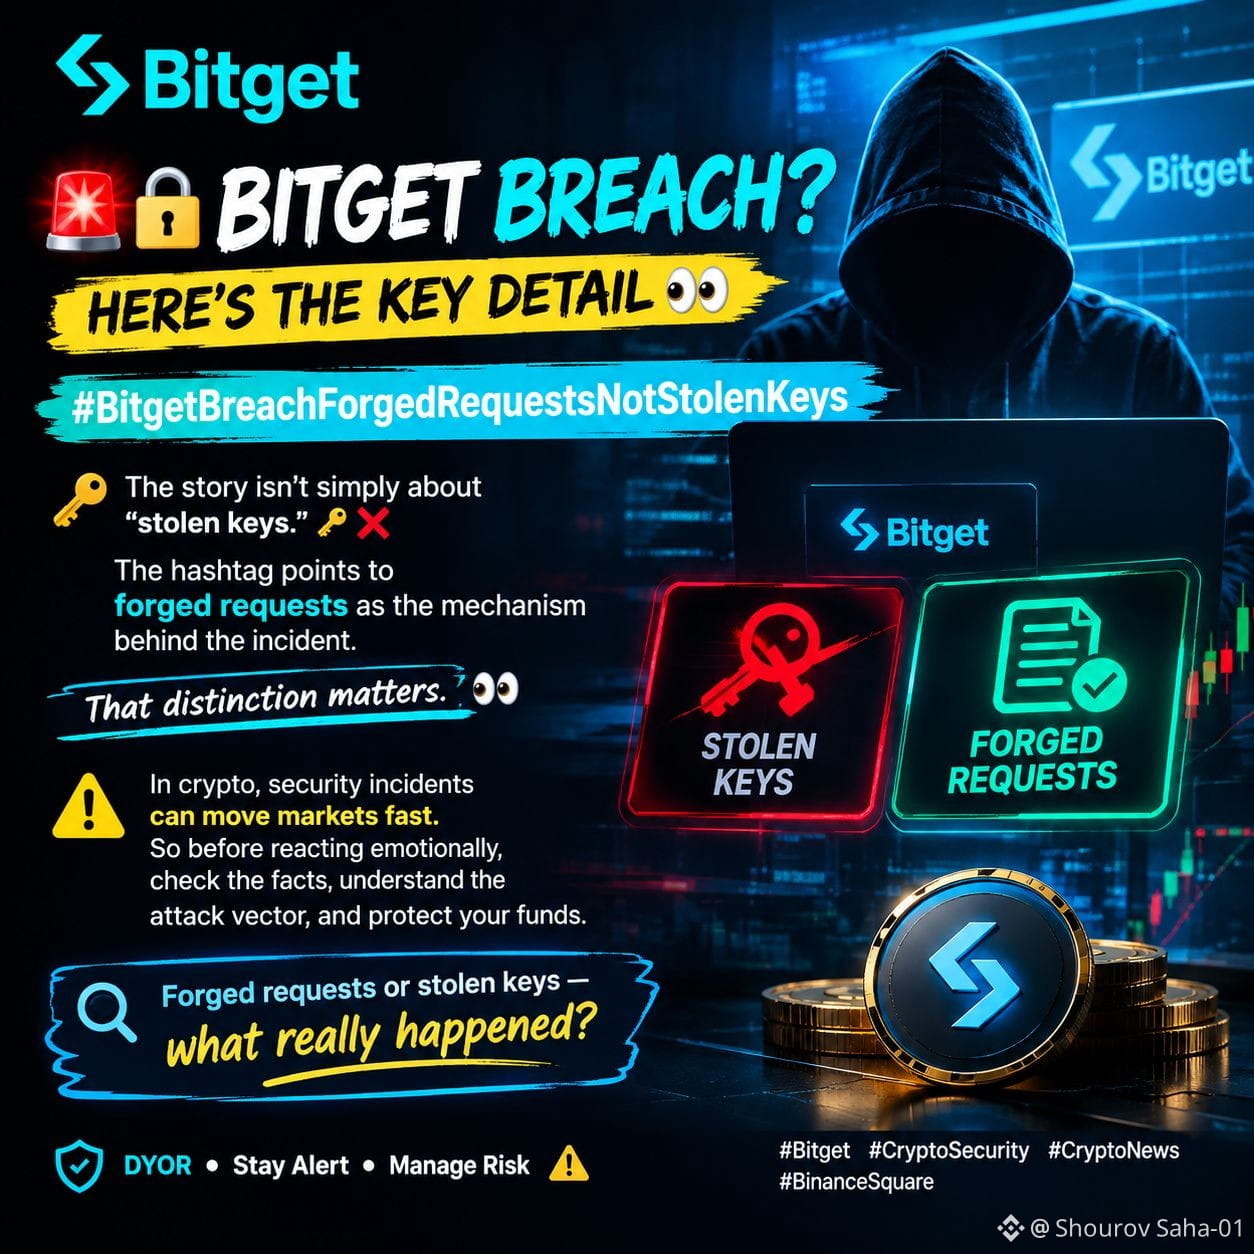
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
{future}(XRPUSDT)
$PHA
{future}(PHAUSDT)
$QI
{spot}(QIUSDT)
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
#BitgetBreachForgedRequestsNotStolenKeys
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
$PHA
$QI
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
$PHA
$QI
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
124
Recent discussions highlight a security incident at Bitget where forged requests, rather than stolen private keys, were the vector of attack. This distinction is crucial for understanding the nature of the breach and the effectiveness of current security protocols. While any breach is concerning, the fact that private keys remained secure suggests the core infrastructure might be more robust than initially feared. However, the ability to execute forged requests points to potential vulnerabilities in user verification, API integrations, or internal procedural controls that need immediate and thorough investigation. The market will be watching closely to see how Bitget addresses these issues and reinforces its systems to prevent recurrence. This event underscores the ongoing challenges in maintaining absolute security in the digital asset space, even for established platforms.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
Recent discussions highlight a security incident at Bitget where forged requests, rather than stolen private keys, were the vector of attack. This distinction is crucial for understanding the nature of the breach and the effectiveness of current security protocols. While any breach is concerning, the fact that private keys remained secure suggests the core infrastructure might be more robust than initially feared. However, the ability to execute forged requests points to potential vulnerabilities in user verification, API integrations, or internal procedural controls that need immediate and thorough investigation. The market will be watching closely to see how Bitget addresses these issues and reinforces its systems to prevent recurrence. This event underscores the ongoing challenges in maintaining absolute security in the digital asset space, even for established platforms.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
4
Inside the Bitget Breach: Forged Requests, Not Stolen Keys! 🔐💥
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
Inside the Bitget Breach: Forged Requests, Not Stolen Keys! 🔐💥
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
57
#BitgetBreachForgedRequestsNotStolenKeys
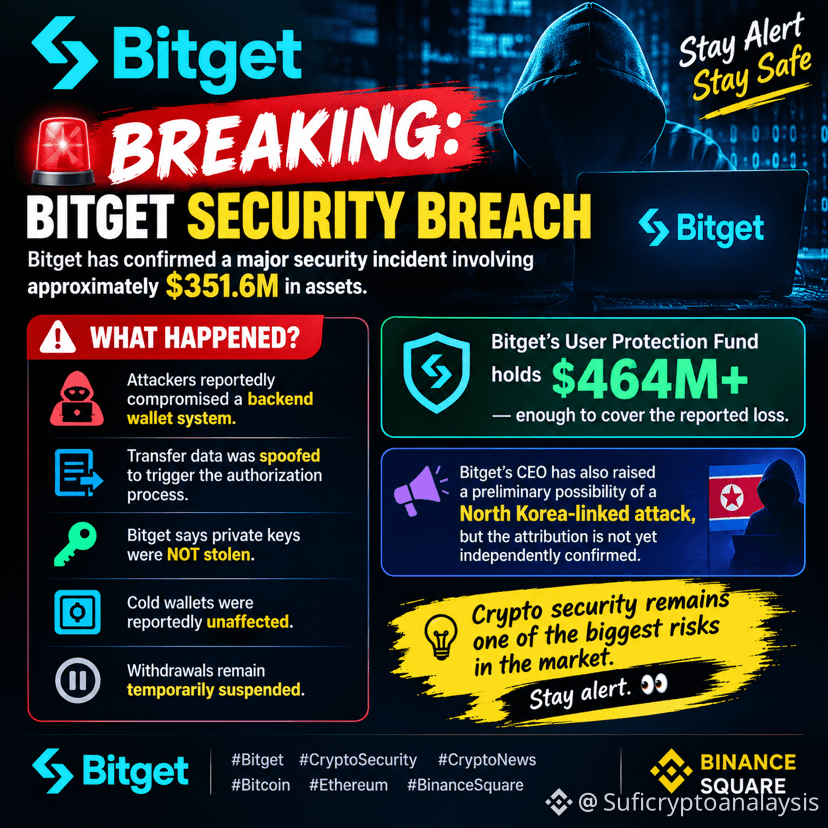
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
{spot}(BTCUSDT)
{spot}(NOTUSDT)
{spot}(ZECUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
30
*$351.6M lost (Bitget official) — on-chain tally $356.86M per Lookonchain — from hot + warm wallets — cold wallets secure — self-custodial Bitget Wallet separate infra not affected*
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
*$351.6M lost (Bitget official) — on-chain tally $356.86M per Lookonchain — from hot + warm wallets — cold wallets secure — self-custodial Bitget Wallet separate infra not affected*
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
161
·
--
UPDATE: Bitget says 🇰🇵North Korean hackers may be behind the $351.6M breach, citing IP addresses linked to VPN services previously used by a DPRK hacking group.
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
UPDATE: Bitget says 🇰🇵North Korean hackers may be behind the $351.6M breach, citing IP addresses linked to VPN services previously used by a DPRK hacking group.
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
38
#BitgetBreachForgedRequestsNotStolenKeys (Bitget Security Incident)
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
{future}(BTCUSDT)
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
#BitgetBreachForgedRequestsNotStolenKeys (Bitget Security Incident)
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
Hardware / Cold Wallet 🔐
Split across multiple CEXs 🏦
100% on a single CEX 📱
20 ມື້ທີ່ຍັງເຫຼືອ
42

·
--
#bitgetbreachforgedrequestsnotstolenkeys
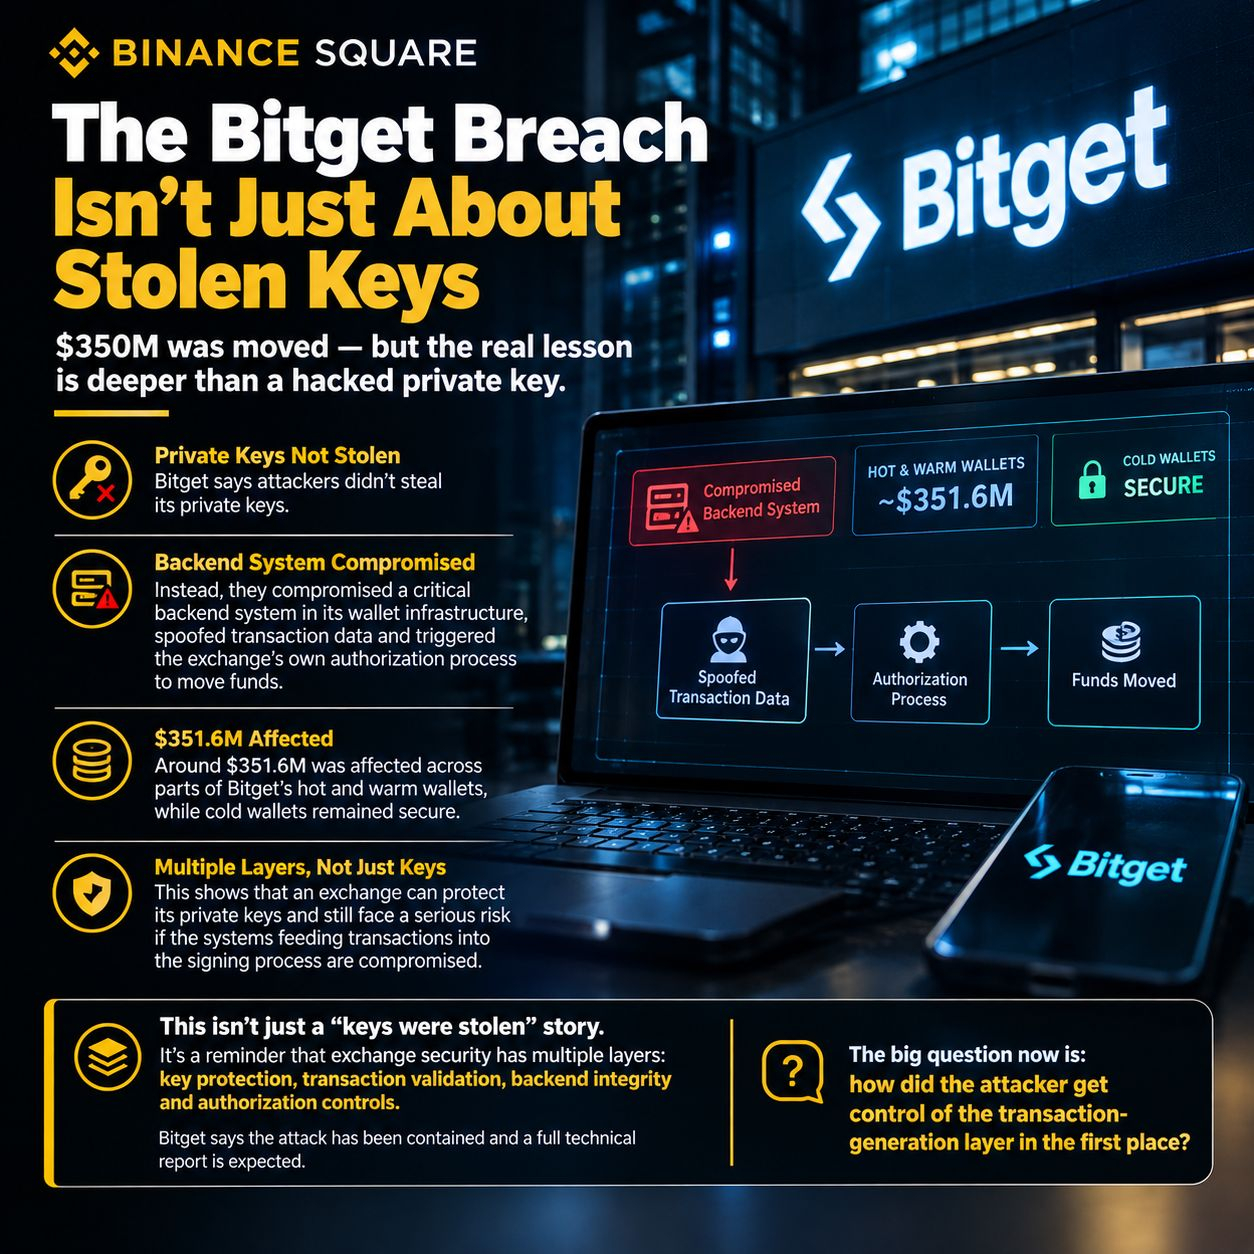
The Bitget breach has a much more interesting lesson than “$350M was hacked.”
Bitget says attackers didn't steal its private keys.
Instead, they compromised a critical backend system inside its wallet infrastructure, spoofed transaction data and triggered the exchange's own authorization process to move funds.
Around $351.6M was affected across parts of Bitget's hot and warm wallets, while the exchange says its cold wallets remained secure.
That's the part I think deserves attention.
A crypto exchange can protect its private keys and still have a serious security problem if the systems feeding transactions into the signing process can be compromised.
So this isn't simply a story about “keys being stolen.”
It's a reminder that exchange security has multiple layers: key protection, transaction validation, backend integrity and authorization controls.
Bitget says the attack has been contained and a full technical report is expected.
The big question now is: how did the attacker get control of the transaction-generation layer in the first place?
#Bitget #CryptoSecurity #CyberSecurity
#bitgetbreachforgedrequestsnotstolenkeys
The Bitget breach has a much more interesting lesson than “$350M was hacked.”
Bitget says attackers didn't steal its private keys.
Instead, they compromised a critical backend system inside its wallet infrastructure, spoofed transaction data and triggered the exchange's own authorization process to move funds.
Around $351.6M was affected across parts of Bitget's hot and warm wallets, while the exchange says its cold wallets remained secure.
That's the part I think deserves attention.
A crypto exchange can protect its private keys and still have a serious security problem if the systems feeding transactions into the signing process can be compromised.
So this isn't simply a story about “keys being stolen.”
It's a reminder that exchange security has multiple layers: key protection, transaction validation, backend integrity and authorization controls.
Bitget says the attack has been contained and a full technical report is expected.
The big question now is: how did the attacker get control of the transaction-generation layer in the first place?
#Bitget #CryptoSecurity #CyberSecurity
The Bitget breach has a much more interesting lesson than “$350M was hacked.”
Bitget says attackers didn't steal its private keys.
Instead, they compromised a critical backend system inside its wallet infrastructure, spoofed transaction data and triggered the exchange's own authorization process to move funds.
Around $351.6M was affected across parts of Bitget's hot and warm wallets, while the exchange says its cold wallets remained secure.
That's the part I think deserves attention.
A crypto exchange can protect its private keys and still have a serious security problem if the systems feeding transactions into the signing process can be compromised.
So this isn't simply a story about “keys being stolen.”
It's a reminder that exchange security has multiple layers: key protection, transaction validation, backend integrity and authorization controls.
Bitget says the attack has been contained and a full technical report is expected.
The big question now is: how did the attacker get control of the transaction-generation layer in the first place?
#Bitget #CryptoSecurity #CyberSecurity
35
·
--
ສັນຍານກະທິງ
#BitgetBreachForgedRequestsNotStolenKeys
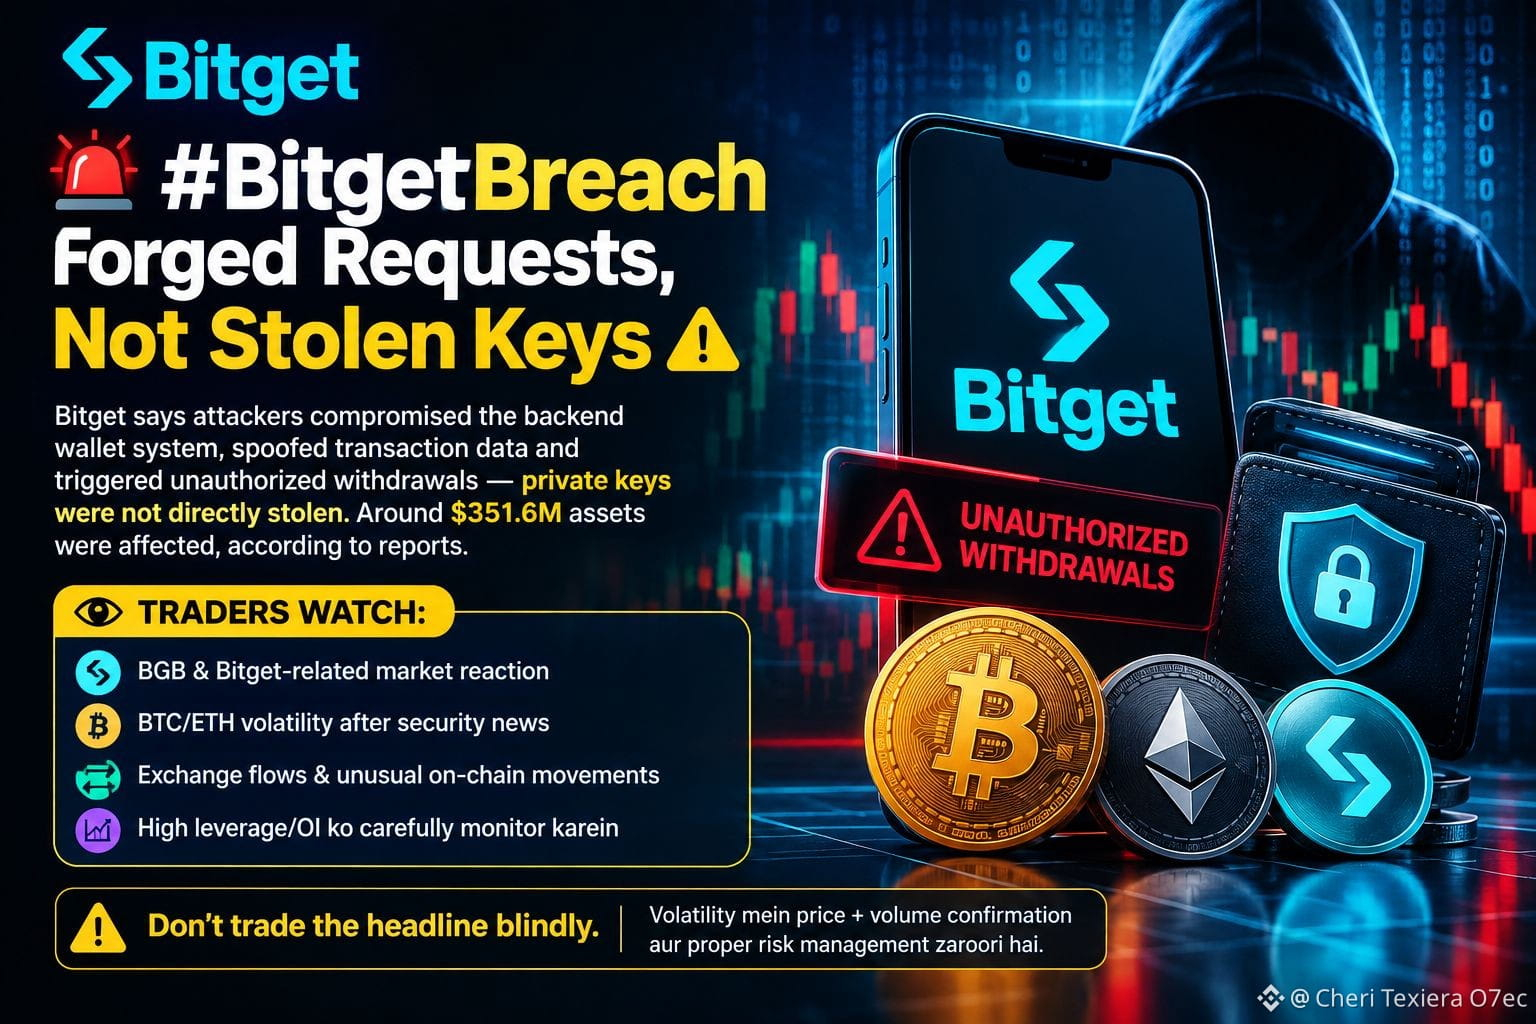
Bitget security incident ne crypto market mein risk focus dobara highlight kar diya. Exchange ke mutabiq attackers ne backend wallet system compromise karke transaction data spoof kiya aur unauthorized withdrawals trigger kiye — private keys directly steal hone ka claim nahi hai. Around 351.6M assets affected report kiye gaye hain.
📊 Traders Watch:
• BGB & Bitget-related market reaction
• BTC/ETH volatility after security news
• Exchange flows & unusual on-chain movements
• High leverage/OI ko carefully monitor karein
$NIL $CHIP $QNT
{future}(QNTUSDT)
{future}(CHIPUSDT)
{future}(NILUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
Bitget security incident ne crypto market mein risk focus dobara highlight kar diya. Exchange ke mutabiq attackers ne backend wallet system compromise karke transaction data spoof kiya aur unauthorized withdrawals trigger kiye — private keys directly steal hone ka claim nahi hai. Around 351.6M assets affected report kiye gaye hain.
📊 Traders Watch:
• BGB & Bitget-related market reaction
• BTC/ETH volatility after security news
• Exchange flows & unusual on-chain movements
• High leverage/OI ko carefully monitor karein
$NIL $CHIP $QNT
Bitget security incident ne crypto market mein risk focus dobara highlight kar diya. Exchange ke mutabiq attackers ne backend wallet system compromise karke transaction data spoof kiya aur unauthorized withdrawals trigger kiye — private keys directly steal hone ka claim nahi hai. Around 351.6M assets affected report kiye gaye hain.
📊 Traders Watch:
• BGB & Bitget-related market reaction
• BTC/ETH volatility after security news
• Exchange flows & unusual on-chain movements
• High leverage/OI ko carefully monitor karein
$NIL $CHIP $QNT
68
·
--
ສັນຍານໝີ
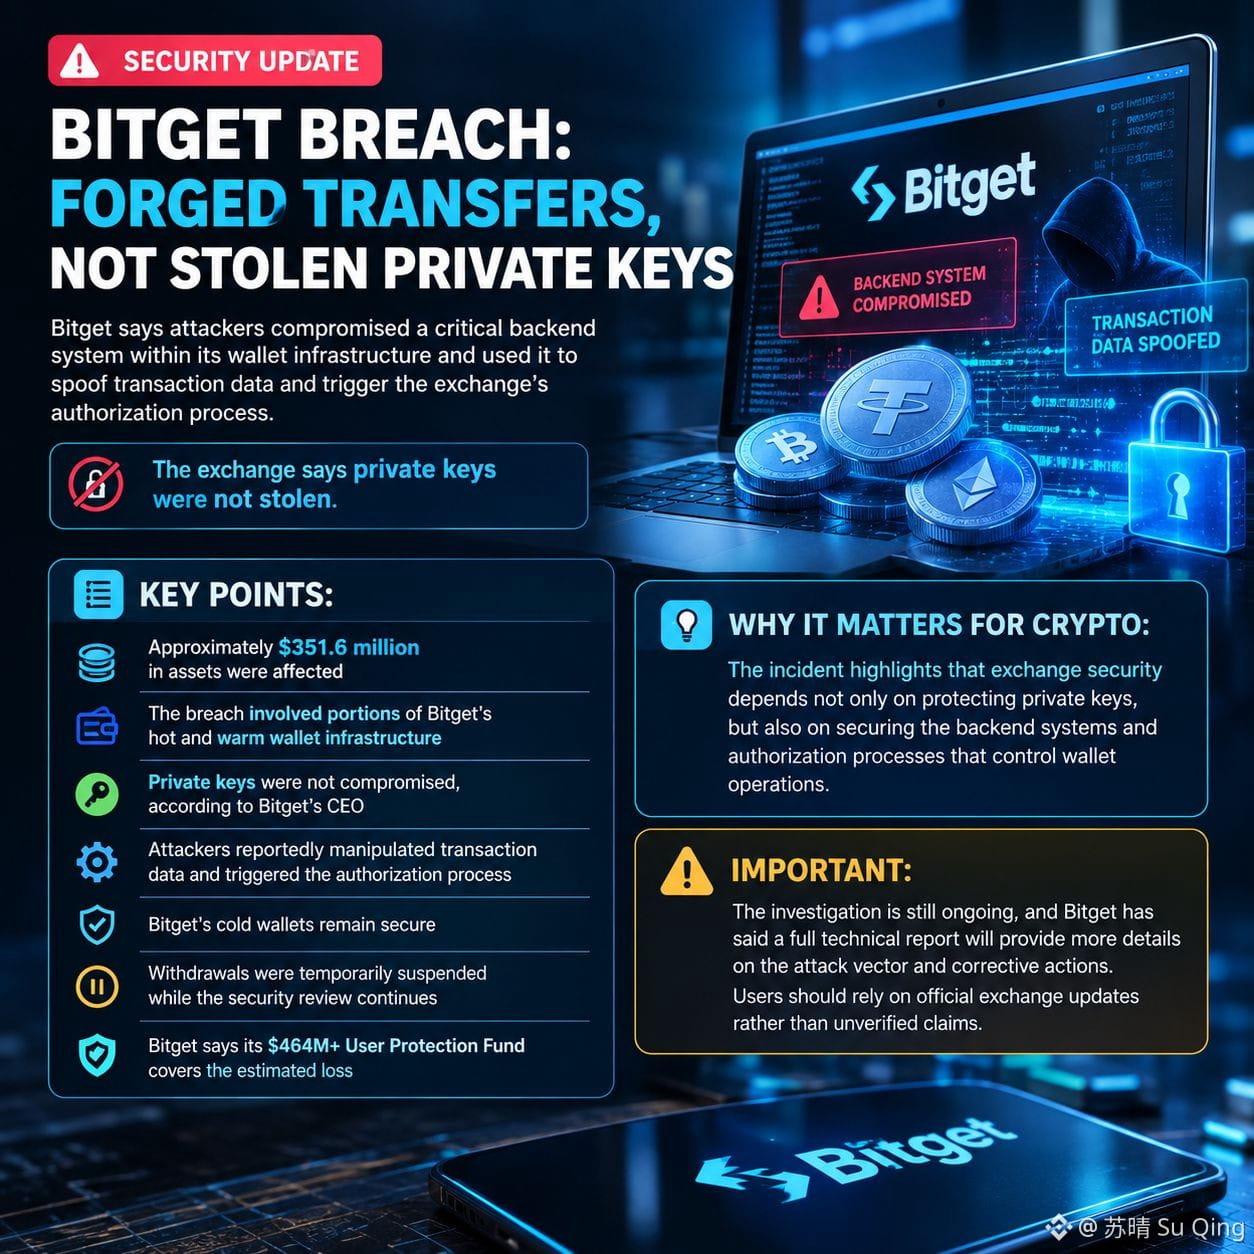
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BITGET BREACH: FORGED TRANSFERS, NOT STOLEN PRIVATE KEYS
Bitget says attackers compromised a critical backend system within its wallet infrastructure and used it to spoof transaction data and trigger the exchange’s authorization process.
The exchange says private keys were not stolen.
📊 Key points:
• Approximately $351.6 million in assets were affected
• The breach involved portions of Bitget’s hot and warm wallet infrastructure
• Private keys were not compromised, according to Bitget’s CEO
• Attackers reportedly manipulated transaction data and triggered the authorization process
• Bitget’s cold wallets remain secure
• Withdrawals were temporarily suspended while the security review continues
• Bitget says its $464M+ User Protection Fund covers the estimated loss
🔎 Why it matters for crypto:
The incident highlights that exchange security depends not only on protecting private keys, but also on securing the backend systems and authorization processes that control wallet operations.
⚠️ Important:
The investigation is still ongoing, and Bitget has said a full technical report will provide more details on the attack vector and corrective actions. Users should rely on official exchange updates rather than unverified claims.
$SAGA
{future}(SAGAUSDT)
$TUT
{future}(TUTUSDT)
$LSK
{future}(LSKUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BITGET BREACH: FORGED TRANSFERS, NOT STOLEN PRIVATE KEYS
Bitget says attackers compromised a critical backend system within its wallet infrastructure and used it to spoof transaction data and trigger the exchange’s authorization process.
The exchange says private keys were not stolen.
📊 Key points:
• Approximately $351.6 million in assets were affected
• The breach involved portions of Bitget’s hot and warm wallet infrastructure
• Private keys were not compromised, according to Bitget’s CEO
• Attackers reportedly manipulated transaction data and triggered the authorization process
• Bitget’s cold wallets remain secure
• Withdrawals were temporarily suspended while the security review continues
• Bitget says its $464M+ User Protection Fund covers the estimated loss
🔎 Why it matters for crypto:
The incident highlights that exchange security depends not only on protecting private keys, but also on securing the backend systems and authorization processes that control wallet operations.
⚠️ Important:
The investigation is still ongoing, and Bitget has said a full technical report will provide more details on the attack vector and corrective actions. Users should rely on official exchange updates rather than unverified claims.
$SAGA
$TUT
$LSK
🚨 BITGET BREACH: FORGED TRANSFERS, NOT STOLEN PRIVATE KEYS
Bitget says attackers compromised a critical backend system within its wallet infrastructure and used it to spoof transaction data and trigger the exchange’s authorization process.
The exchange says private keys were not stolen.
📊 Key points:
• Approximately $351.6 million in assets were affected
• The breach involved portions of Bitget’s hot and warm wallet infrastructure
• Private keys were not compromised, according to Bitget’s CEO
• Attackers reportedly manipulated transaction data and triggered the authorization process
• Bitget’s cold wallets remain secure
• Withdrawals were temporarily suspended while the security review continues
• Bitget says its $464M+ User Protection Fund covers the estimated loss
🔎 Why it matters for crypto:
The incident highlights that exchange security depends not only on protecting private keys, but also on securing the backend systems and authorization processes that control wallet operations.
⚠️ Important:
The investigation is still ongoing, and Bitget has said a full technical report will provide more details on the attack vector and corrective actions. Users should rely on official exchange updates rather than unverified claims.
$SAGA
$TUT
$LSK
814
·
--
#bitgetbreachforgedrequestsnotstolenkeys
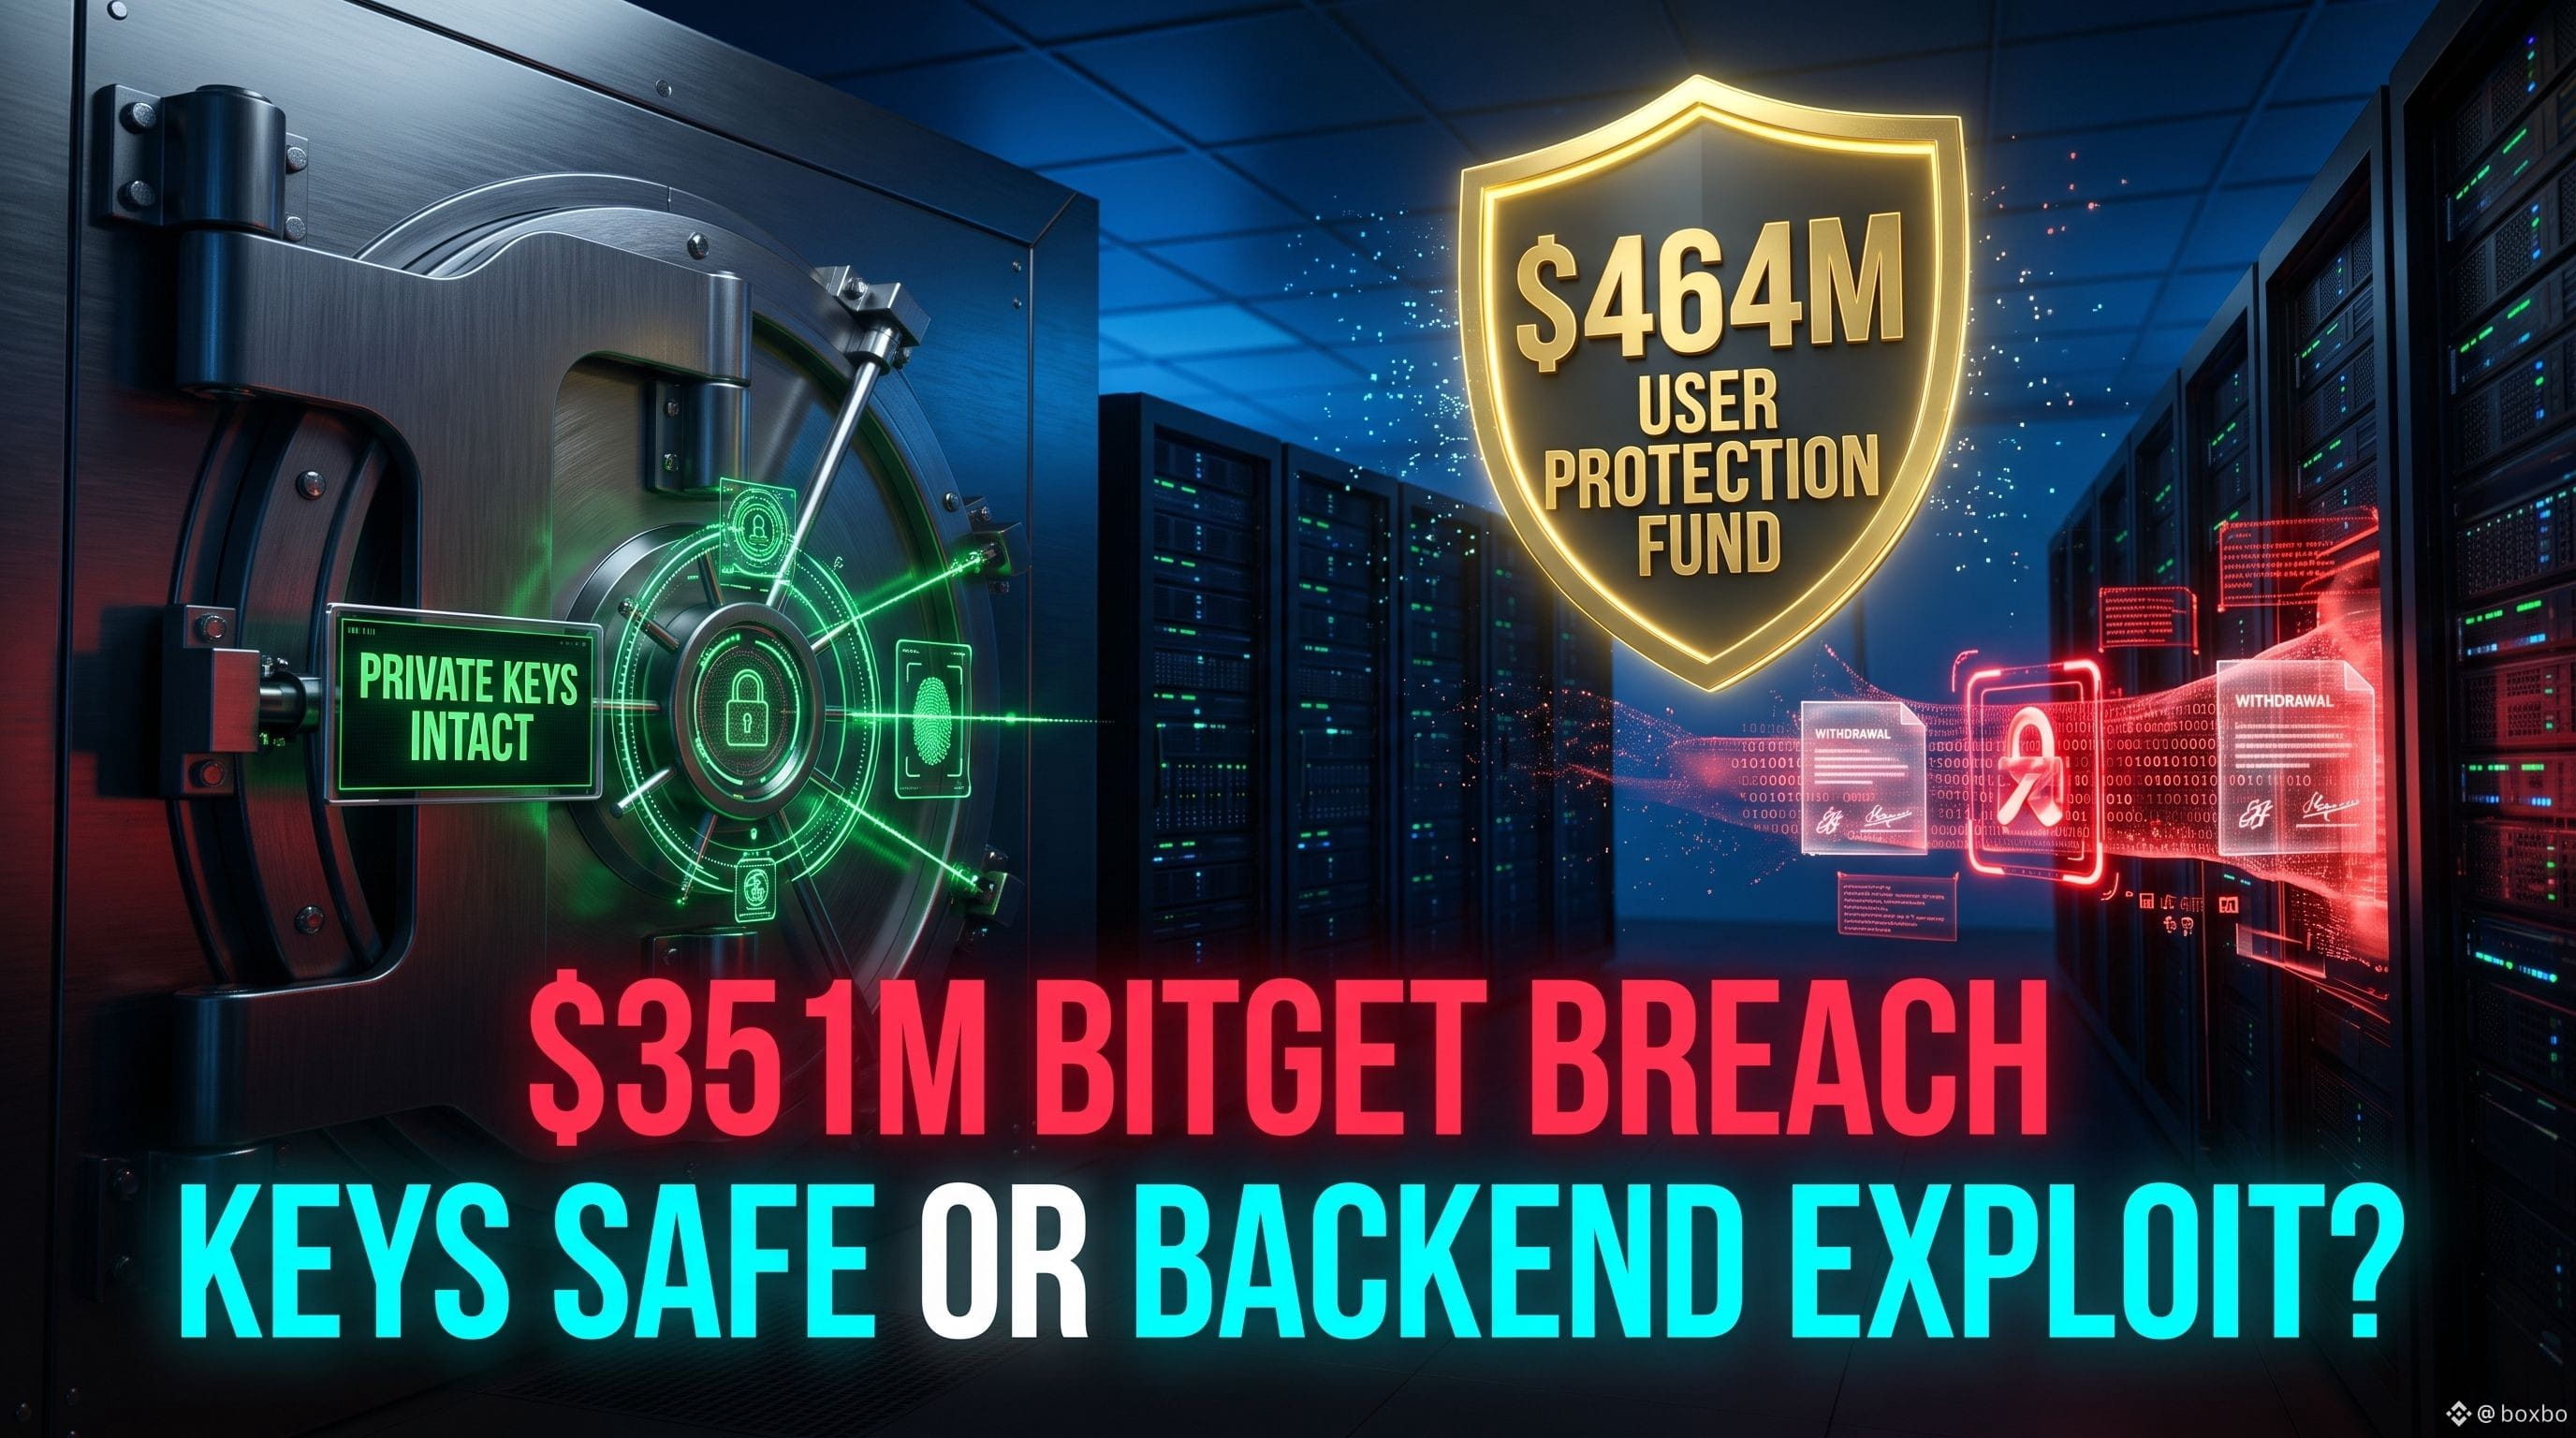
Infrastructure Hijack: How Bitget Lost $351.6 Million Without Losing Private Keys $BTC
{spot}(BTCUSDT)
Bitget suffered a $351.6 million security breach affecting its hot and warm wallet layers, but CEO Gracy Chen confirmed that cryptographic private keys were never compromised. Instead, attackers infiltrated a core backend system within the exchange's wallet infrastructure, allowing them to forge fraudulent withdrawal requests and trick the automated authorization process into signing and executing unauthorized transfers. Because private keys remained intact, cold storage assets were unaffected, preventing a complete platform drain. From a risk perspective, Bitget's $464 million User Protection Fund covers 100% of the stolen capital; however, while trading and deposits remain open, withdrawals have been temporarily frozen pending a full system audit. This incident highlights a growing security shift: modern exchange vulnerabilities are increasingly targeting API workflows and backend authorization pipelines rather than raw private key theft. $BNB
{spot}(BNBUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
Infrastructure Hijack: How Bitget Lost $351.6 Million Without Losing Private Keys $BTC
Bitget suffered a $351.6 million security breach affecting its hot and warm wallet layers, but CEO Gracy Chen confirmed that cryptographic private keys were never compromised. Instead, attackers infiltrated a core backend system within the exchange's wallet infrastructure, allowing them to forge fraudulent withdrawal requests and trick the automated authorization process into signing and executing unauthorized transfers. Because private keys remained intact, cold storage assets were unaffected, preventing a complete platform drain. From a risk perspective, Bitget's $464 million User Protection Fund covers 100% of the stolen capital; however, while trading and deposits remain open, withdrawals have been temporarily frozen pending a full system audit. This incident highlights a growing security shift: modern exchange vulnerabilities are increasingly targeting API workflows and backend authorization pipelines rather than raw private key theft. $BNB
Infrastructure Hijack: How Bitget Lost $351.6 Million Without Losing Private Keys $BTC
Bitget suffered a $351.6 million security breach affecting its hot and warm wallet layers, but CEO Gracy Chen confirmed that cryptographic private keys were never compromised. Instead, attackers infiltrated a core backend system within the exchange's wallet infrastructure, allowing them to forge fraudulent withdrawal requests and trick the automated authorization process into signing and executing unauthorized transfers. Because private keys remained intact, cold storage assets were unaffected, preventing a complete platform drain. From a risk perspective, Bitget's $464 million User Protection Fund covers 100% of the stolen capital; however, while trading and deposits remain open, withdrawals have been temporarily frozen pending a full system audit. This incident highlights a growing security shift: modern exchange vulnerabilities are increasingly targeting API workflows and backend authorization pipelines rather than raw private key theft. $BNB
2
3.3k
#BitgetBreachForgedRequestsNotStolenKeys
سلّطت Bitget الأمنية في حادثة على سوق العملات المشفرة مجددًا الضوء على المخاطر مع التركيز. ووفقًا للبورصة، قام المهاجمون باختراق نظام المحافظ الخلفي وعبثوا ببيانات المعاملات وأطلقوا عمليات سحب غير مصرح بها — لا توجد ادعاءات بأن المفاتيح الخاصة تم سرقتها مباشرة. تم الإبلاغ عن تضرر نحو 351.6 مليون من الأصول.
📊 مراقبة المتداولين:
• رد فعل السوق المرتبط بـ BGB وBitget
• تقلبات BTC/ETH بعد أخبار الأمان
• تدفقات البورصة وعمليات غير معتادة على السلسلة
• راقبوا بعناية الرافعة المالية المرتفعة/الفائدة المفتوحة (OI)
متابعة من فضلكم
$NIL $CHIP $QNT
#BitgetBreachForgedRequestsNotStolenKeys
سلّطت Bitget الأمنية في حادثة على سوق العملات المشفرة مجددًا الضوء على المخاطر مع التركيز. ووفقًا للبورصة، قام المهاجمون باختراق نظام المحافظ الخلفي وعبثوا ببيانات المعاملات وأطلقوا عمليات سحب غير مصرح بها — لا توجد ادعاءات بأن المفاتيح الخاصة تم سرقتها مباشرة. تم الإبلاغ عن تضرر نحو 351.6 مليون من الأصول.
📊 مراقبة المتداولين:
• رد فعل السوق المرتبط بـ BGB وBitget
• تقلبات BTC/ETH بعد أخبار الأمان
• تدفقات البورصة وعمليات غير معتادة على السلسلة
• راقبوا بعناية الرافعة المالية المرتفعة/الفائدة المفتوحة (OI)
متابعة من فضلكم
$NIL $CHIP $QNT
سلّطت Bitget الأمنية في حادثة على سوق العملات المشفرة مجددًا الضوء على المخاطر مع التركيز. ووفقًا للبورصة، قام المهاجمون باختراق نظام المحافظ الخلفي وعبثوا ببيانات المعاملات وأطلقوا عمليات سحب غير مصرح بها — لا توجد ادعاءات بأن المفاتيح الخاصة تم سرقتها مباشرة. تم الإبلاغ عن تضرر نحو 351.6 مليون من الأصول.
📊 مراقبة المتداولين:
• رد فعل السوق المرتبط بـ BGB وBitget
• تقلبات BTC/ETH بعد أخبار الأمان
• تدفقات البورصة وعمليات غير معتادة على السلسلة
• راقبوا بعناية الرافعة المالية المرتفعة/الفائدة المفتوحة (OI)
متابعة من فضلكم
$NIL $CHIP $QNT
1
122
·
--
#BitgetBreachForgedRequestsNotStolenKeys
BitgetBreachForgedRequestsNotStolenKey refers to the technical mechanism behind the massive $351.6 million security breach suffered by cryptocurrency exchange Bitget on September 24, 2026. [1, 2]
Bitget $CE.US
{stock_us}(CE.US)
O Gracy Chen explicitly clarified that no private keys were stolen or compromised during the exploit. Instead, the attackers successfully infiltrated a critical backend system connected to the exchange’s wallet infrastructure. They used this access to spoof transaction data, generating forged withdrawal requests that mimic legitimate paperwork. These forged requests were then automatically signed and pushed through the exchange's standard authorization process. [1, 2, 3, 4, 5]
$NVDAB
{spot}(NVDABUSDT)
$AAPL.US
{stock_us}(AAPL.US)
#BitgetBreachForgedRequestsNotStolenKeys
BitgetBreachForgedRequestsNotStolenKey refers to the technical mechanism behind the massive $351.6 million security breach suffered by cryptocurrency exchange Bitget on September 24, 2026. [1, 2]
Bitget $CE.US
O Gracy Chen explicitly clarified that no private keys were stolen or compromised during the exploit. Instead, the attackers successfully infiltrated a critical backend system connected to the exchange’s wallet infrastructure. They used this access to spoof transaction data, generating forged withdrawal requests that mimic legitimate paperwork. These forged requests were then automatically signed and pushed through the exchange's standard authorization process. [1, 2, 3, 4, 5]
$NVDAB
$AAPL.US
BitgetBreachForgedRequestsNotStolenKey refers to the technical mechanism behind the massive $351.6 million security breach suffered by cryptocurrency exchange Bitget on September 24, 2026. [1, 2]
Bitget $CE.US
O Gracy Chen explicitly clarified that no private keys were stolen or compromised during the exploit. Instead, the attackers successfully infiltrated a critical backend system connected to the exchange’s wallet infrastructure. They used this access to spoof transaction data, generating forged withdrawal requests that mimic legitimate paperwork. These forged requests were then automatically signed and pushed through the exchange's standard authorization process. [1, 2, 3, 4, 5]
$NVDAB
$AAPL.US
47
#BitgetBreachForgedRequestsNotStolenKeys 🚨 BITGET $351.6M BREACH — NO PRIVATE KEYS STOLEN?
Bitget says attackers did NOT steal private keys.
Instead, attackers compromised a critical *backend wallet system, spoofed transaction data and triggered Bitget’s own authorization process to move funds.
💰 **~$351.6M affected**
🔐 Cold wallets remain secure
⚠️ Withdrawals temporarily suspended
🛡️ Bitget says its **$464M+ User Protection Fund** covers the loss
This raises a huge question for the entire crypto industry:
If the keys are safe but the system approving transactions is compromised… HOW SAFE IS THE SIGNING PIPELINE? 👀**
#Bitget #Crypto #CyberSecurity
#BitgetBreachForgedRequestsNotStolenKeys 🚨 BITGET $351.6M BREACH — NO PRIVATE KEYS STOLEN?
Bitget says attackers did NOT steal private keys.
Instead, attackers compromised a critical *backend wallet system, spoofed transaction data and triggered Bitget’s own authorization process to move funds.
💰 **~$351.6M affected**
🔐 Cold wallets remain secure
⚠️ Withdrawals temporarily suspended
🛡️ Bitget says its **$464M+ User Protection Fund** covers the loss
This raises a huge question for the entire crypto industry:
If the keys are safe but the system approving transactions is compromised… HOW SAFE IS THE SIGNING PIPELINE? 👀**
#Bitget #Crypto #CyberSecurity
Bitget says attackers did NOT steal private keys.
Instead, attackers compromised a critical *backend wallet system, spoofed transaction data and triggered Bitget’s own authorization process to move funds.
💰 **~$351.6M affected**
🔐 Cold wallets remain secure
⚠️ Withdrawals temporarily suspended
🛡️ Bitget says its **$464M+ User Protection Fund** covers the loss
This raises a huge question for the entire crypto industry:
If the keys are safe but the system approving transactions is compromised… HOW SAFE IS THE SIGNING PIPELINE? 👀**
#Bitget #Crypto #CyberSecurity
15
ເຂົ້າສູ່ລະບົບເພື່ອສຳຫຼວດເນື້ອຫາເພີ່ມເຕີມ
ເຂົ້າຮ່ວມກຸ່ມຜູ້ໃຊ້ຄຣິບໂຕທົ່ວໂລກໃນ Binance Square.
⚡️ ໄດ້ຮັບຂໍ້ມູນຫຼ້າສຸດ ແລະ ທີ່ມີປະໂຫຍດກ່ຽວກັບຄຣິບໂຕ.
💬 ໄດ້ຮັບຄວາມໄວ້ວາງໃຈຈາກຕະຫຼາດແລກປ່ຽນຄຣິບໂຕທີ່ໃຫຍ່ທີ່ສຸດໃນໂລກ.
👍 ຄົ້ນຫາຂໍ້ມູນເຊີງເລິກທີ່ແທ້ຈາກນັກສ້າງທີ່ໄດ້ຮັບການຢືນຢັນ.
ອີເມວ / ເບີໂທລະສັບ
ຫົວຂໍ້ທີ່ກໍາລັງນິຍົມ
1
#QNTRises39%
17,737 views
809 ກຳລັງສົນທະນາ
2
#EthereumBreaksAbove$2700
1,886 views
83 ກຳລັງສົນທະນາ
3
#BitgetBreachForgedRequestsNotStolenKeys
15,618 views
649 ກຳລັງສົນທະນາ
4
#BitcoinSpotETFsTurnNetPositiveYTD
9,928 views
520 ກຳລັງສົນທະນາ
5
#GrayscaleZcashETFHits$1BNetAssets
1,222 views
39 ກຳລັງສົນທະນາ
6
#BitcoinSpotETFsNetInflow$191M
7,084 views
178 ກຳລັງສົນທະນາ
7
#CFTCUpdatesGuidanceOnTokenizedAssets
49,473 views
1,469 ກຳລັງສົນທະນາ
8
#BitgetSays$352MAffectedInHack
18,060 views
95 ກຳລັງສົນທະນາ
9
#BinanceWillListHyperliquid(HYPE)
270,402 views
4,046 ກຳລັງສົນທະນາ
10
#BrazilOrdersReportingOf$10KSelfCustodyTransfers
6,741 views
55 ກຳລັງສົນທະນາ