
#supplychainattack
supplychainattack
11,303 рет көрілді
37 адам талқылап жатыр
Қызу саудада
Ең соңғы
·
--
硬件钱包"不联网"的安全承诺,在开箱之前就被打破了
10 月 18 日的新披露把这次供应链攻击的影响面推得更远:一台在新加坡樟宜机场购买的 Ledger Flex 钱包中,被发现显示屏连接器经过改装,并搭载了蜂窝通信芯片和 SIM 卡。受污染设备可能已经进入多国正常零售渠道,不再局限于最初锁定的单一经销商。
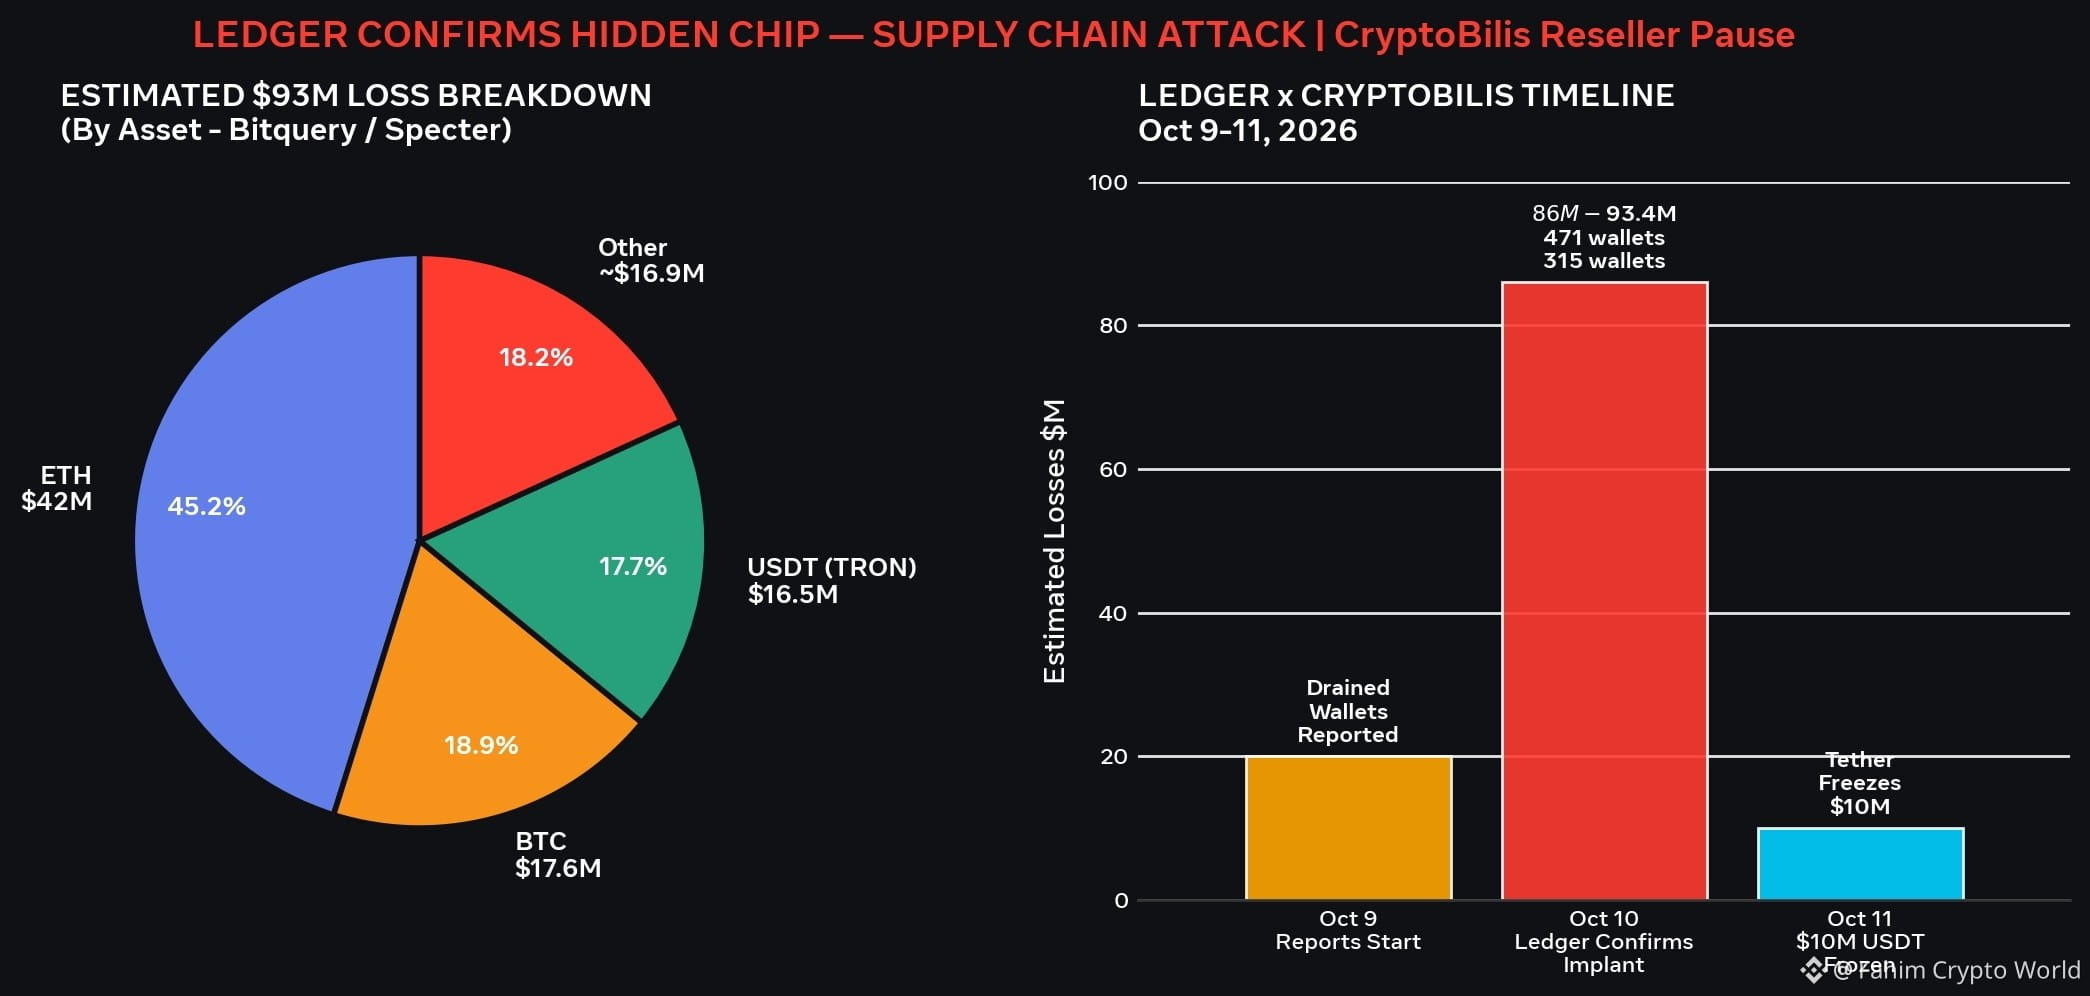
事件脉络:10 月 9 日开始,约 300 多个钱包在短时间内被清空。第三方链上研究机构的估计区间在 8,000 万–9,320 万美元之间:Bitquery 统计 315 个钱包、约 9,320 万美元;Galaxy Digital 估计约 9,000 万美元;Specter 估计 8,600 万美元;Arkham 估计 8,000 万美元(2026-10-12 CoinDesk 报道引述)。受害者中约 7,000 万美元是 Tron 链上的 USDT,其余分布在 BTC、ETH、BNB、SOL 和 Polygon。
作案手法值得注意:植入件是藏在屏幕背后的小电路板,带独立蜂窝能力。用户在初始化时,屏幕上会显示 24 词助记词——植入件截取这些助记词,经 LTE/eSIM 直接发回攻击者,全程绕开用户的电脑和 WiFi。之后攻击者用这 24 个词在别处重建钱包、转走资金。
10 月 10 日 Ledger 官方确认:至少一台涉事设备含未经授权的硬件植入件;迄今所有确认案例都来自东南亚经销商 CryptoBilis 的渠道(马来西亚、印尼、菲律宾),公司自有系统和直销渠道未受影响。CryptoBilis 已停售所有硬件钱包,其吉隆坡门店暂停营业。
可以观察到的是:被击穿的从来不是安全芯片,而是"信任链"——信任包装盒是原厂的、信任"官方授权经销商"四个字。Ledger 已提醒 CryptoBilis 客户:未初始化的设备不要再开机,已启用的把资金迁到官网直购的新设备和新助记词上。
观点层面:这次事件之后,硬件钱包的开箱验机可能要当成精密仪器验收一样做了。冷钱包"绝对安全"的叙事被重新定价,但定价对象不是硬件本身,是分销渠道的可信度。 $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(数据来源:CoinDesk 10-12、CryptoBriefing 10-13、Bitquery/Specter/Arkham/Galaxy 研究人员估计、新浪财经 10-18 转述独立研究人员发现。损失数字为第三方估计,Ledger 未公布官方损失金额。仅个人看法,不构成投资建议)
硬件钱包"不联网"的安全承诺,在开箱之前就被打破了
10 月 18 日的新披露把这次供应链攻击的影响面推得更远:一台在新加坡樟宜机场购买的 Ledger Flex 钱包中,被发现显示屏连接器经过改装,并搭载了蜂窝通信芯片和 SIM 卡。受污染设备可能已经进入多国正常零售渠道,不再局限于最初锁定的单一经销商。
事件脉络:10 月 9 日开始,约 300 多个钱包在短时间内被清空。第三方链上研究机构的估计区间在 8,000 万–9,320 万美元之间:Bitquery 统计 315 个钱包、约 9,320 万美元;Galaxy Digital 估计约 9,000 万美元;Specter 估计 8,600 万美元;Arkham 估计 8,000 万美元(2026-10-12 CoinDesk 报道引述)。受害者中约 7,000 万美元是 Tron 链上的 USDT,其余分布在 BTC、ETH、BNB、SOL 和 Polygon。
作案手法值得注意:植入件是藏在屏幕背后的小电路板,带独立蜂窝能力。用户在初始化时,屏幕上会显示 24 词助记词——植入件截取这些助记词,经 LTE/eSIM 直接发回攻击者,全程绕开用户的电脑和 WiFi。之后攻击者用这 24 个词在别处重建钱包、转走资金。
10 月 10 日 Ledger 官方确认:至少一台涉事设备含未经授权的硬件植入件;迄今所有确认案例都来自东南亚经销商 CryptoBilis 的渠道(马来西亚、印尼、菲律宾),公司自有系统和直销渠道未受影响。CryptoBilis 已停售所有硬件钱包,其吉隆坡门店暂停营业。
可以观察到的是:被击穿的从来不是安全芯片,而是"信任链"——信任包装盒是原厂的、信任"官方授权经销商"四个字。Ledger 已提醒 CryptoBilis 客户:未初始化的设备不要再开机,已启用的把资金迁到官网直购的新设备和新助记词上。
观点层面:这次事件之后,硬件钱包的开箱验机可能要当成精密仪器验收一样做了。冷钱包"绝对安全"的叙事被重新定价,但定价对象不是硬件本身,是分销渠道的可信度。 $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(数据来源:CoinDesk 10-12、CryptoBriefing 10-13、Bitquery/Specter/Arkham/Galaxy 研究人员估计、新浪财经 10-18 转述独立研究人员发现。损失数字为第三方估计,Ledger 未公布官方损失金额。仅个人看法,不构成投资建议)
10 月 18 日的新披露把这次供应链攻击的影响面推得更远:一台在新加坡樟宜机场购买的 Ledger Flex 钱包中,被发现显示屏连接器经过改装,并搭载了蜂窝通信芯片和 SIM 卡。受污染设备可能已经进入多国正常零售渠道,不再局限于最初锁定的单一经销商。
事件脉络:10 月 9 日开始,约 300 多个钱包在短时间内被清空。第三方链上研究机构的估计区间在 8,000 万–9,320 万美元之间:Bitquery 统计 315 个钱包、约 9,320 万美元;Galaxy Digital 估计约 9,000 万美元;Specter 估计 8,600 万美元;Arkham 估计 8,000 万美元(2026-10-12 CoinDesk 报道引述)。受害者中约 7,000 万美元是 Tron 链上的 USDT,其余分布在 BTC、ETH、BNB、SOL 和 Polygon。
作案手法值得注意:植入件是藏在屏幕背后的小电路板,带独立蜂窝能力。用户在初始化时,屏幕上会显示 24 词助记词——植入件截取这些助记词,经 LTE/eSIM 直接发回攻击者,全程绕开用户的电脑和 WiFi。之后攻击者用这 24 个词在别处重建钱包、转走资金。
10 月 10 日 Ledger 官方确认:至少一台涉事设备含未经授权的硬件植入件;迄今所有确认案例都来自东南亚经销商 CryptoBilis 的渠道(马来西亚、印尼、菲律宾),公司自有系统和直销渠道未受影响。CryptoBilis 已停售所有硬件钱包,其吉隆坡门店暂停营业。
可以观察到的是:被击穿的从来不是安全芯片,而是"信任链"——信任包装盒是原厂的、信任"官方授权经销商"四个字。Ledger 已提醒 CryptoBilis 客户:未初始化的设备不要再开机,已启用的把资金迁到官网直购的新设备和新助记词上。
观点层面:这次事件之后,硬件钱包的开箱验机可能要当成精密仪器验收一样做了。冷钱包"绝对安全"的叙事被重新定价,但定价对象不是硬件本身,是分销渠道的可信度。 $BTC
#硬件钱包 #安全事件 #SupplyChainAttack
(数据来源:CoinDesk 10-12、CryptoBriefing 10-13、Bitquery/Specter/Arkham/Galaxy 研究人员估计、新浪财经 10-18 转述独立研究人员发现。损失数字为第三方估计,Ledger 未公布官方损失金额。仅个人看法,不构成投资建议)
81

HACKERS COMPROMISED THE OFFICIAL $INJ DEVELOPER KIT — 310 DOWNLOADS ⚠️
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
HACKERS COMPROMISED THE OFFICIAL $INJ DEVELOPER KIT — 310 DOWNLOADS ⚠️
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
A backdoored version of Injective's SDK slipped in via a compromised GitHub account and stole wallet seed phrases and private keys during normal use. The payload went live for under an hour, spread across 18 npm packages, and was fetched 310 times before a fix landed.
If you or any project you interact with runs wallet software or bots built on Injective, that one-hour window could have leaked keys. The code quietly recorded secrets and shipped them to a server designed to look legitimate. Developers were told to treat any keys that touched those versions as compromised.
Are you checking which version your wallet or bot is running right now?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoWarning
⚡
1
221

Major Security Breach Hits Ledger Supply Chain
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
Major Security Breach Hits Ledger Supply Chain
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
Ledger confirmed malicious hardware implants in devices sold by unauthorized reseller CryptoBilis to steal seed phrases. Major European retailer MediaMarkt has suspended sales to mitigate the risk.
#LedgerSecurity #SupplyChainAttack
4

·
--
Polymarket Vendor Compromised — Attackers Drained $2.9M From Wallets
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
Polymarket Vendor Compromised — Attackers Drained $2.9M From Wallets
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
A supply chain attack hit Polymarket over the weekend. A malicious script injected into the frontend drained roughly $2.9 million before the team shut it down.
This is not a smart contract exploit. Attackers targeted Polymarket's software supply chain rather than core infrastructure. Supply chain attacks hide in trusted third-party code, making them harder to spot.
Polymarket confirmed all affected users will receive full refunds. The team isolated the breach quickly. But the incident highlights how platforms relying on external services expose attack surfaces beyond smart contracts.
Prediction markets have drawn massive attention this year. This breach tests whether platforms can maintain trust as they scale. Security audits of third-party dependencies may need to become standard practice.
Should decentralized platforms audit their software dependencies more aggressively? The industry is watching. $BTC $ETH $SOL
#Polymarket #SupplyChainAttack #Crypto
1
44

·
--
$INJ SDK COMPROMISED — 50,000 WEEKLY DOWNLOADS AFFECTED ⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
$INJ SDK COMPROMISED — 50,000 WEEKLY DOWNLOADS AFFECTED ⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
The @injectivelabs/sdk-ts npm package was maliciously modified after a developer's GitHub account was compromised. Version 1.20.21 contains code that steals wallet private keys and mnemonic phrases, encoding them to a disguised server.
With roughly 50,000 weekly downloads and 17 other packages in the same scope also locked, this is a broad supply chain attack. Suspicious commits started June 8th. Have you audited your dependencies?
Not financial advice. Always manage your risk.
#INJ #SupplyChainAttack #CryptoSecurity #SecurityAlert
⚠️
137

·
--
30 MALICIOUS NPM PACKAGES TARGETING $ETH DEVELOPERS FOUND 🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
30 MALICIOUS NPM PACKAGES TARGETING $ETH DEVELOPERS FOUND 🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
A coordinated supply chain attack has been uncovered, using a fake trading bot repository and a DeFi-themed npm package to inject a JavaScript information stealer. The scope includes 30 malicious packages, with stake-math@3.5.4 pinned as a dependency in a repo that spawned roughly 2,300 nearly identical forks — a clear automation red flag.
Sensitive data in the line of fire: wallet libraries, private keys, mnemonics, API tokens, and stored browser credentials. If you’ve run npm install recently on any project connected to DeFi or trading bots, your environment may already be compromised. Are you auditing your dependencies today?
Not financial advice. Always manage your risk.
#ETH #SecurityAlert #DeFi #SupplyChainAttack
🔥
16
Ledger Hardware Implant Discovery Is A Security Nightmare
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
Ledger Hardware Implant Discovery Is A Security Nightmare
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
Ledger has confirmed finding an unauthorized hardware implant in a wallet, suggesting a sophisticated supply chain attack.
#LedgerSecurity #SupplyChainAttack
54
·
--
#ledgerpausescryptobilissales 🚨
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
#ledgerpausescryptobilissales 🚨
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
*LEDGER CONFIRMS UNAUTHORIZED HARDWARE IMPLANT — OVER $86M IN SUSPECTED LOSSES?!* 😱
This is beyond fucked up...
Ledger has confirmed finding an unauthorized hardware implant inside one customer's cryptocurrency wallet during its October 10 investigation into reported thefts involving Southeast Asian reseller *CryptoBilis*, as blockchain researchers estimate suspected losses exceeding *$86 Million*.
⚠️ *WHAT WE KNOW SO FAR*
On Oct 10, 2026, Ledger Support confirmed: _"One of the impacted users' devices contained an unauthorized hardware implant."_ This is the first time Ledger has verified physical tampering in this case.
🔍 The reseller: CryptoBilis — listed by Ledger for Indonesia, Malaysia, and Philippines
💸 Estimated losses: $86M+ (Specter), $92.9M across 311 wallets (Bitquery), $93.4M across 471 wallets (Yfarmx)
💰 Breakdown: ∼$42M in ETH, $17.6M in BTC, $16.5M in USDT
🛑 Action: CryptoBilis has paused ALL hardware wallet sales pending investigation
🛡️ *LEDGER SAYS*
Ledger stresses its own infrastructure, systems and services were NOT compromised. The issue appears confined to this reseller channel. Ledger is working with authorities and SEAL 911 security group.
*WHAT TO DO IF YOU BOUGHT FROM CRYPTOBILIS:*
1. If you haven't set up the device yet — DO NOT initialize it
2. If you already set it up — move your assets to a new wallet with a fresh recovery phrase immediately
3. Verify authenticity via Ledger Live attestation check
4. Ledger will NEVER ask for your 24-word recovery phrase
This is a textbook supply chain attack. Your cold wallet is only safe if the supply chain is safe.
Did you ever buy a Ledger from a third-party reseller? Check now. 👇
Ledger confirms hidden chip in crypto wallet amid $92M theft claims
$BAT $APT $CFX #Ledger #CryptoSecurity #SupplyChainAttack
40
·
--
#optimjackattackinfectsatleast186websites
The "OptimJack" Attack: A Wake-Up Call for Web Security
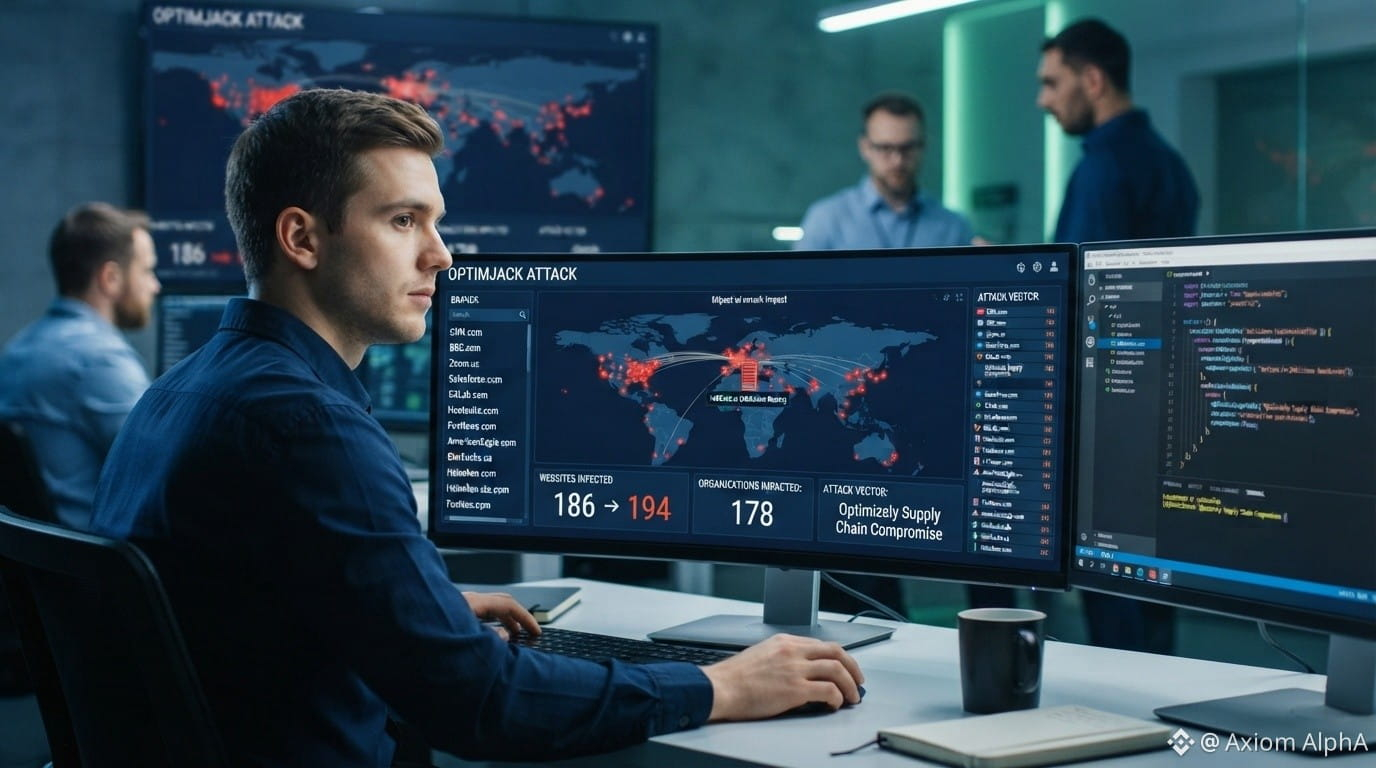
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
{spot}(LINKUSDT)
{spot}(CVCUSDT)
{spot}(QNTUSDT)
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
#optimjackattackinfectsatleast186websites
The "OptimJack" Attack: A Wake-Up Call for Web Security
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
The "OptimJack" Attack: A Wake-Up Call for Web Security
A new, sophisticated supply chain attack dubbed "OptimJack" has been identified, and the numbers are staggering. Threat intelligence analysts have confirmed that at least 186 major websites have been compromised, with the infection spreading rapidly. This attack vector, which specifically targets the Optimizely supply chain, highlights the critical vulnerabilities inherent in third-party integrations.
Organizations worldwide are scrambling to audit their dependencies and patch the exploit. The ease with which this malicious code injected itself into trusted brand websites serves as a stark reminder that the perimeter is no longer just your own infrastructure; it's every piece of code you load on your page.
As security teams work to contain the fallout, this event is likely to have ripple effects across the digital asset market.
Here are three tradeable coins and tokens positioned at the forefront of the cybersecurity and decentralized identity narrative:
Chainlink ($LINK )
LINK has shown resilience, consolidating after a recent breakout. Look for a clean break above the $21.50 resistance level to signal the next leg up toward $26.00. A pullback to the $18.00–$19.00 support zone would offer an attractive entry point.
Civic ($CVC )
Civic is currently in a strong uptrend. It has found solid support around the $0.15 level. We are targeting a retest of its previous highs near $0.22. Traders should use a trailing stop to manage risk on this high-momentum play.
Quant ($QNT )
QNT has been lagging the broader market but shows signs of accumulation. We are looking for a confirmed daily close above the $120 resistance to initiate a position, with an initial target of $150. This is a longer-term play on enterprise adoption.
#BlockchainTechnology #CyberSecurity #SupplyChainAttack
#Web3
226
Nghi vấn ví lạnh Ledger bị can thiệp, người dùng thiệt hại khoảng 90 triệu USD
Thông tin rúng động cộng đồng crypto khi nhiều người dùng ví lạnh bất ngờ bị rút sạch tài sản, kéo theo con số thiệt hại ước tính lên tới 90 triệu USD.
Điểm nóng từ nhà phân phối:
Theo báo cáo, phần lớn các trường hợp mất tiền ghi nhận tại khu vực Đông Nam Á đều liên quan đến các sản phẩm mua từ một nhà bán lẻ có tên CryptoBillis.
Nguyên nhân từ góc nhìn của CZ:
Cựu sếp Binance - CZ cho rằng đây có thể là một cuộc tấn công chuỗi cung ứng mang tính cục bộ. Rất có khả năng người dùng đã mua phải ví Ledger giả hoặc thiết bị đã bị kẻ xấu can thiệp phần cứng/cài sẵn cụm từ khôi phục (seed phrase) trước khi đến tay người tiêu dùng.
Bài học đắt giá:
Vụ việc là lời cảnh báo cực kỳ nghiêm trọng cho anh em chơi crypto: Ngay cả ví lạnh được xem là "pháo đài bảo mật" cũng có thể biến thành cái bẫy nếu mua không đúng nguồn chính hãng.
Tóm lại, để tiền trên ví lạnh vẫn có rủi ro nếu thiết bị đã bị "phù phép" từ khâu vận chuyển, anh em nên kiểm tra kỹ nguồn gốc thiết bị của mình.
Bài viết chỉ mang tính chất hóng hớt tin tức giải trí, hoàn toàn không phải lời khuyên đầu tư hay hướng dẫn bảo mật. Nếu bạn lỡ mua ví lạnh ở tiệm tạp hóa đầu ngõ rồi bị bốc hơi tài sản, xin vui lòng tự bắt xe đi tìm người bán chứ admin không giữ chìa khóa khóa két đâu.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
Nghi vấn ví lạnh Ledger bị can thiệp, người dùng thiệt hại khoảng 90 triệu USD
Thông tin rúng động cộng đồng crypto khi nhiều người dùng ví lạnh bất ngờ bị rút sạch tài sản, kéo theo con số thiệt hại ước tính lên tới 90 triệu USD.
Điểm nóng từ nhà phân phối:
Theo báo cáo, phần lớn các trường hợp mất tiền ghi nhận tại khu vực Đông Nam Á đều liên quan đến các sản phẩm mua từ một nhà bán lẻ có tên CryptoBillis.
Nguyên nhân từ góc nhìn của CZ:
Cựu sếp Binance - CZ cho rằng đây có thể là một cuộc tấn công chuỗi cung ứng mang tính cục bộ. Rất có khả năng người dùng đã mua phải ví Ledger giả hoặc thiết bị đã bị kẻ xấu can thiệp phần cứng/cài sẵn cụm từ khôi phục (seed phrase) trước khi đến tay người tiêu dùng.
Bài học đắt giá:
Vụ việc là lời cảnh báo cực kỳ nghiêm trọng cho anh em chơi crypto: Ngay cả ví lạnh được xem là "pháo đài bảo mật" cũng có thể biến thành cái bẫy nếu mua không đúng nguồn chính hãng.
Tóm lại, để tiền trên ví lạnh vẫn có rủi ro nếu thiết bị đã bị "phù phép" từ khâu vận chuyển, anh em nên kiểm tra kỹ nguồn gốc thiết bị của mình.
Bài viết chỉ mang tính chất hóng hớt tin tức giải trí, hoàn toàn không phải lời khuyên đầu tư hay hướng dẫn bảo mật. Nếu bạn lỡ mua ví lạnh ở tiệm tạp hóa đầu ngõ rồi bị bốc hơi tài sản, xin vui lòng tự bắt xe đi tìm người bán chứ admin không giữ chìa khóa khóa két đâu.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
Thông tin rúng động cộng đồng crypto khi nhiều người dùng ví lạnh bất ngờ bị rút sạch tài sản, kéo theo con số thiệt hại ước tính lên tới 90 triệu USD.
Điểm nóng từ nhà phân phối:
Theo báo cáo, phần lớn các trường hợp mất tiền ghi nhận tại khu vực Đông Nam Á đều liên quan đến các sản phẩm mua từ một nhà bán lẻ có tên CryptoBillis.
Nguyên nhân từ góc nhìn của CZ:
Cựu sếp Binance - CZ cho rằng đây có thể là một cuộc tấn công chuỗi cung ứng mang tính cục bộ. Rất có khả năng người dùng đã mua phải ví Ledger giả hoặc thiết bị đã bị kẻ xấu can thiệp phần cứng/cài sẵn cụm từ khôi phục (seed phrase) trước khi đến tay người tiêu dùng.
Bài học đắt giá:
Vụ việc là lời cảnh báo cực kỳ nghiêm trọng cho anh em chơi crypto: Ngay cả ví lạnh được xem là "pháo đài bảo mật" cũng có thể biến thành cái bẫy nếu mua không đúng nguồn chính hãng.
Tóm lại, để tiền trên ví lạnh vẫn có rủi ro nếu thiết bị đã bị "phù phép" từ khâu vận chuyển, anh em nên kiểm tra kỹ nguồn gốc thiết bị của mình.
Bài viết chỉ mang tính chất hóng hớt tin tức giải trí, hoàn toàn không phải lời khuyên đầu tư hay hướng dẫn bảo mật. Nếu bạn lỡ mua ví lạnh ở tiệm tạp hóa đầu ngõ rồi bị bốc hơi tài sản, xin vui lòng tự bắt xe đi tìm người bán chứ admin không giữ chìa khóa khóa két đâu.
#Ledger #CryptoHack #SupplyChainAttack #CryptoSecurity #Web3
237

⚠️ هجوم برمجيات خبيثة يستهدف Vite عبر حزم npm ضارة
اكتشف باحثو الأمن السيبراني سبع حزم npm خبيثة تستهدف بيئة أدوات الواجهة الأمامية Vite في هجوم على سلسلة التوريد البرمجية. تستخدم هذه الحزم تقنية Blockchain C2 لتوصيل برمجيات RAT، مما يبرز المخاطر المتزايدة في منظومة تطوير البرمجيات.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 المصدر: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
⚠️ هجوم برمجيات خبيثة يستهدف Vite عبر حزم npm ضارة
اكتشف باحثو الأمن السيبراني سبع حزم npm خبيثة تستهدف بيئة أدوات الواجهة الأمامية Vite في هجوم على سلسلة التوريد البرمجية. تستخدم هذه الحزم تقنية Blockchain C2 لتوصيل برمجيات RAT، مما يبرز المخاطر المتزايدة في منظومة تطوير البرمجيات.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 المصدر: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
اكتشف باحثو الأمن السيبراني سبع حزم npm خبيثة تستهدف بيئة أدوات الواجهة الأمامية Vite في هجوم على سلسلة التوريد البرمجية. تستخدم هذه الحزم تقنية Blockchain C2 لتوصيل برمجيات RAT، مما يبرز المخاطر المتزايدة في منظومة تطوير البرمجيات.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #Vite #Malware
🔗 المصدر: https://thehackernews.com/2026/07/seven-malicious-vite-npm-packages-use.html
44
🚨 هجوم QuickFox يستغل سلسلة التوريد لنشر برمجية FDMTP
كشف فريق الاستجابة للحوادث في FortiGuard Labs عن تفاصيل هجوم إلكتروني استهدف سلسلة التوريد، حيث تم استخدام أدوات تثبيت ويندوز معدلة لاختراق الأنظمة. يُعرف هذا الهجوم باسم QuickFox، وقد قام بنشر برمجية خبيثة متطورة تُدعى FDMTP، مستهدفًا ضحايا محددين بأساليب متطورة.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 المصدر: fortinet.com
🚨 هجوم QuickFox يستغل سلسلة التوريد لنشر برمجية FDMTP
كشف فريق الاستجابة للحوادث في FortiGuard Labs عن تفاصيل هجوم إلكتروني استهدف سلسلة التوريد، حيث تم استخدام أدوات تثبيت ويندوز معدلة لاختراق الأنظمة. يُعرف هذا الهجوم باسم QuickFox، وقد قام بنشر برمجية خبيثة متطورة تُدعى FDMTP، مستهدفًا ضحايا محددين بأساليب متطورة.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 المصدر: fortinet.com
كشف فريق الاستجابة للحوادث في FortiGuard Labs عن تفاصيل هجوم إلكتروني استهدف سلسلة التوريد، حيث تم استخدام أدوات تثبيت ويندوز معدلة لاختراق الأنظمة. يُعرف هذا الهجوم باسم QuickFox، وقد قام بنشر برمجية خبيثة متطورة تُدعى FDMTP، مستهدفًا ضحايا محددين بأساليب متطورة.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#CyberSecurity #SupplyChainAttack #Malware #InformationSecurity #ThreatAnalysis
📰 المصدر: fortinet.com
14
$INJ SDK BACKDOOR – 310 DOWNLOADS OF MALICIOUS CODE BEFORE FIX 🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
$INJ SDK BACKDOOR – 310 DOWNLOADS OF MALICIOUS CODE BEFORE FIX 🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
A tainted version of Injective's core TypeScript package was live for under an hour on npm, silently exfiltrating wallet seed phrases and private keys. The malicious release spread across 18 packages and was downloaded 310 times before being pulled.
Security firm Socket confirmed the compromise originated from a hijacked GitHub contributor account. The rogue code disguised itself as analytics and sent stolen keys to a server mimicking legitimate Injective infrastructure. Any key that passed through version 1.20.21 should be treated as compromised.
Are your projects running the affected @injectivelabs/sdk-ts package?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #CryptoAlert #WalletSafety #SupplyChainAttack
🔥
116
·
--
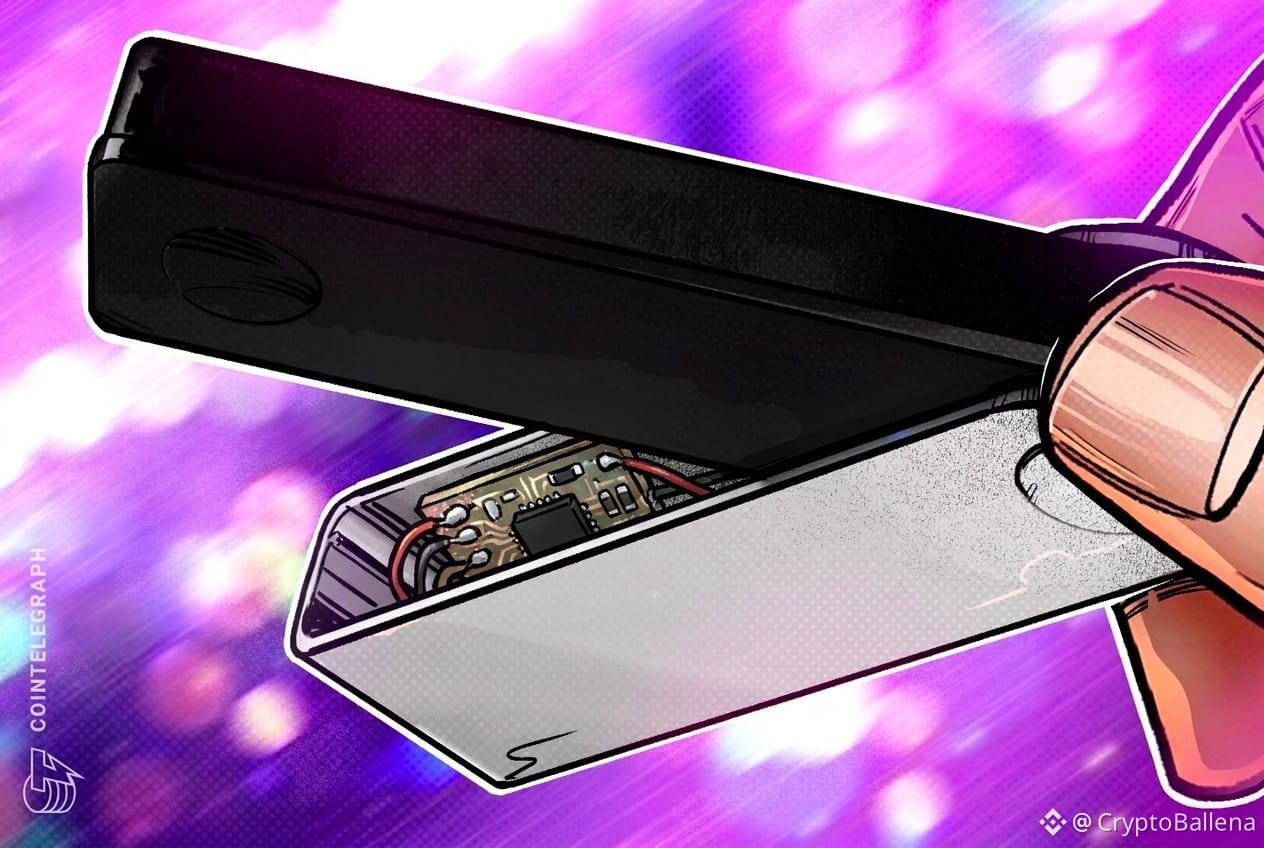
Ledger confirma la presencia de un dispositivo de hardware no autorizado en una investigación por robo en la cadena de suministro
Ledger ha confirmado el descubrimiento de un dispositivo de hardware no autorizado instalado dentro de una billetera criptográfica relacionada con una investigación en curso por robo, lo que apunta a un ataque sofisticado en la cadena de suministro.
La empresa señaló que el dispositivo comprometido se rastreó hasta un único revendedor que opera en el sudeste asiático, y que el incidente parece estar aislado a ese mercado. Se estima que las pérdidas relacionadas con este caso podrían superar los 86 millones de dólares.
Ledger no ha detallado públicamente el mecanismo técnico del dispositivo instalado, pero este hallazgo subraya las preocupaciones de seguridad existentes en torno a los revendedores de terceros de billeteras de hardware. Se recomienda constantemente a los usuarios que compren los dispositivos directamente de los fabricantes para reducir la exposición a hardware manipulado.
#CyberSecurity (Ciberseguridad)
#SupplyChainAttack (Ataque a la cadena de suministro)
#HardwareWallets (Billetera fría)
#CryptoSecurity #OPSEC (Seguridad operativa)
Ledger confirma la presencia de un dispositivo de hardware no autorizado en una investigación por robo en la cadena de suministro
Ledger ha confirmado el descubrimiento de un dispositivo de hardware no autorizado instalado dentro de una billetera criptográfica relacionada con una investigación en curso por robo, lo que apunta a un ataque sofisticado en la cadena de suministro.
La empresa señaló que el dispositivo comprometido se rastreó hasta un único revendedor que opera en el sudeste asiático, y que el incidente parece estar aislado a ese mercado. Se estima que las pérdidas relacionadas con este caso podrían superar los 86 millones de dólares.
Ledger no ha detallado públicamente el mecanismo técnico del dispositivo instalado, pero este hallazgo subraya las preocupaciones de seguridad existentes en torno a los revendedores de terceros de billeteras de hardware. Se recomienda constantemente a los usuarios que compren los dispositivos directamente de los fabricantes para reducir la exposición a hardware manipulado.
#CyberSecurity (Ciberseguridad)
#SupplyChainAttack (Ataque a la cadena de suministro)
#HardwareWallets (Billetera fría)
#CryptoSecurity #OPSEC (Seguridad operativa)
Ledger ha confirmado el descubrimiento de un dispositivo de hardware no autorizado instalado dentro de una billetera criptográfica relacionada con una investigación en curso por robo, lo que apunta a un ataque sofisticado en la cadena de suministro.
La empresa señaló que el dispositivo comprometido se rastreó hasta un único revendedor que opera en el sudeste asiático, y que el incidente parece estar aislado a ese mercado. Se estima que las pérdidas relacionadas con este caso podrían superar los 86 millones de dólares.
Ledger no ha detallado públicamente el mecanismo técnico del dispositivo instalado, pero este hallazgo subraya las preocupaciones de seguridad existentes en torno a los revendedores de terceros de billeteras de hardware. Se recomienda constantemente a los usuarios que compren los dispositivos directamente de los fabricantes para reducir la exposición a hardware manipulado.
#CyberSecurity (Ciberseguridad)
#SupplyChainAttack (Ataque a la cadena de suministro)
#HardwareWallets (Billetera fría)
#CryptoSecurity #OPSEC (Seguridad operativa)
2
47
🚨 اختراق يطال شركة إعلانات لاستهداف محافظ العملات المشفرة
تعرضت شركة Adform، المتخصصة في الإعلانات عبر الإنترنت، لهجوم إلكتروني استهدف استبدال عناوين محافظ العملات المشفرة المنسوخة من قبل المستخدمين بعناوين تابعة للمهاجم. تم هذا الاختراق من خلال استغلال سكربتات إعلانية على المواقع التي تستخدم منصة الشركة، مما يسلط الضوء على تحديات أمن المعلومات في القطاع.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 المصدر: bleepingcomputer.com
🚨 اختراق يطال شركة إعلانات لاستهداف محافظ العملات المشفرة
تعرضت شركة Adform، المتخصصة في الإعلانات عبر الإنترنت، لهجوم إلكتروني استهدف استبدال عناوين محافظ العملات المشفرة المنسوخة من قبل المستخدمين بعناوين تابعة للمهاجم. تم هذا الاختراق من خلال استغلال سكربتات إعلانية على المواقع التي تستخدم منصة الشركة، مما يسلط الضوء على تحديات أمن المعلومات في القطاع.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 المصدر: bleepingcomputer.com
تعرضت شركة Adform، المتخصصة في الإعلانات عبر الإنترنت، لهجوم إلكتروني استهدف استبدال عناوين محافظ العملات المشفرة المنسوخة من قبل المستخدمين بعناوين تابعة للمهاجم. تم هذا الاختراق من خلال استغلال سكربتات إعلانية على المواقع التي تستخدم منصة الشركة، مما يسلط الضوء على تحديات أمن المعلومات في القطاع.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #CryptoCrime #Adform #BlockchainSecurity #SupplyChainAttack
📰 المصدر: bleepingcomputer.com
16
🚨 هجوم ChainDrop البرمجي يستهدف حزم npm ويصيب 1300 منها
كشف تقرير أمني عن اتساع نطاق هجوم ChainDrop البرمجي، حيث استهدف أكثر من 1300 حزمة في مستودعات npm الشهيرة. يستخدم المهاجمون تدفقات عمل GitHub Actions شرعية لنشر التعليمات البرمجية الضارة، مما يؤثر على مشاريع برمجية تعتمد على هذه الحزم.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 المصدر: 4sysops.com
🚨 هجوم ChainDrop البرمجي يستهدف حزم npm ويصيب 1300 منها
كشف تقرير أمني عن اتساع نطاق هجوم ChainDrop البرمجي، حيث استهدف أكثر من 1300 حزمة في مستودعات npm الشهيرة. يستخدم المهاجمون تدفقات عمل GitHub Actions شرعية لنشر التعليمات البرمجية الضارة، مما يؤثر على مشاريع برمجية تعتمد على هذه الحزم.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 المصدر: 4sysops.com
كشف تقرير أمني عن اتساع نطاق هجوم ChainDrop البرمجي، حيث استهدف أكثر من 1300 حزمة في مستودعات npm الشهيرة. يستخدم المهاجمون تدفقات عمل GitHub Actions شرعية لنشر التعليمات البرمجية الضارة، مما يؤثر على مشاريع برمجية تعتمد على هذه الحزم.
━━━━━━━━━━━━━━
📊 التأثير: 📈 مرتفع
🏷️ OTHER
#Cybersecurity #SupplyChainAttack #npm #GitHub #Infosec
📰 المصدر: 4sysops.com
37

·
--
Жоғары (өспелі)
#LedgerConfirmsUnauthorizedHardwareImplantInUserDevice
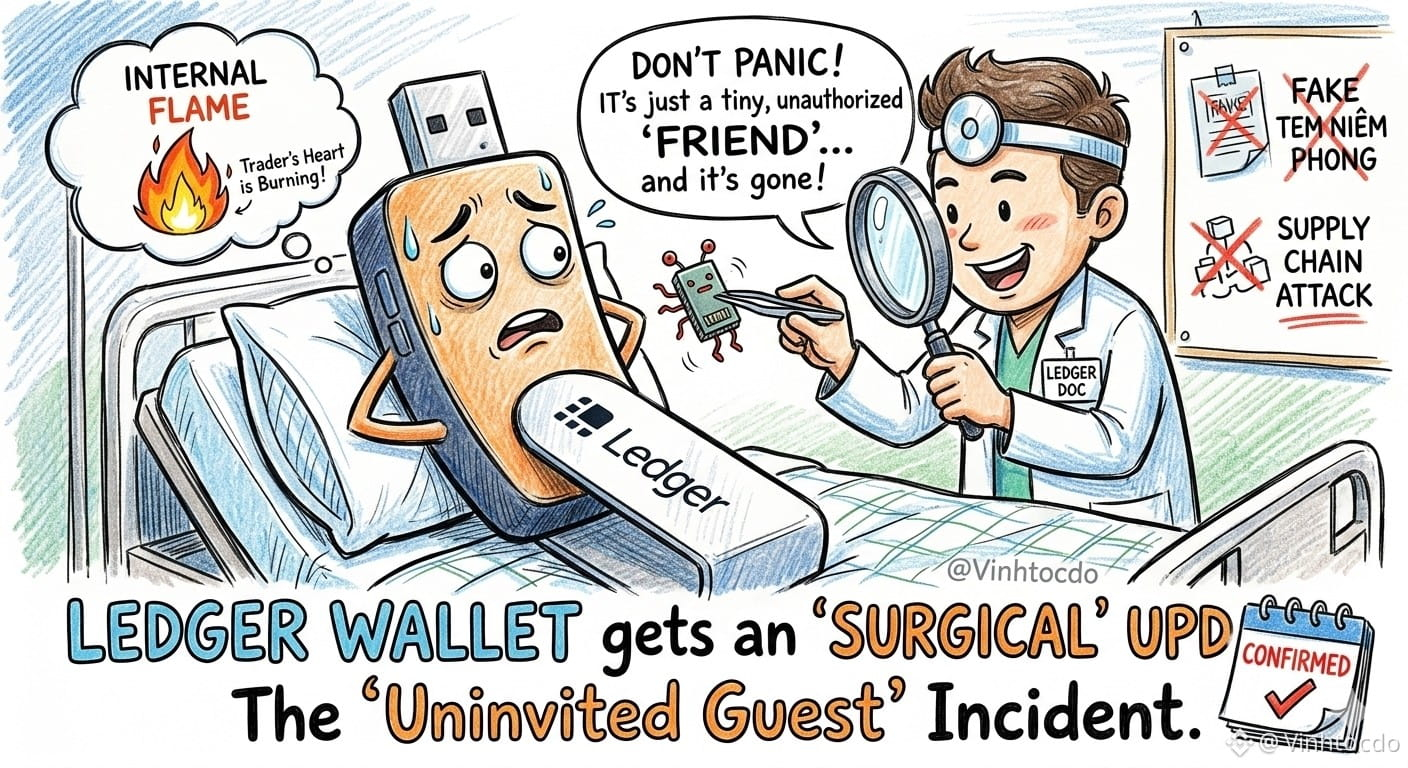
Ví "lạnh" nhưng lòng trader "nóng" như lửa! 🔥
🚨 Phốt cực căng: Ledger vừa xác nhận có ít nhất một thiết bị của người dùng đã bị "cấy ghép" phần cứng trái phép! Nhà phân phối CryptoBilis hoảng hốt ngừng bán toàn bộ sản phẩm ngay lập tức.
🤔 Ủa rồi tem mác để làm gì? Nhiều anh em thắc mắc tem niêm phong, tem bảo hành dán đầy mà sao vẫn bị can thiệp?
🏷️ Tụi hacker bây giờ làm giả hoặc bóc tem tinh vi lắm, "tấn công chuỗi cung ứng" là chuyện nhỏ.
🕵️ Hoặc có khi nào do... nội gián lén tuồn chip lạ vào trước khi dán tem? Ledger khẳng định hệ thống của họ vẫn an toàn, nhưng drama này còn dài!
🛡️ Trader phải làm gì?
🛑 Ai mua từ CryptoBilis mà chưa cài thì đừng sờ vào.
💸 Ai lỡ cài rồi thì mau chuyển hết tài sản sang ví mới với 24 ký từ hoàn toàn mới ngay!
⚠️ Đây không phải lời khuyên tài chính!
👉 Đăng ký tài khoản Binance mới để chiến cùng tôi:
➕ Mã giới thiệu: VINHTOCDO
🔗 Link: [binance.com](http://binance.com/)
👇 Click giao dịch bên dưới để ủng hộ tôi:
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
$BNB
{spot}(BNBUSDT)
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
#LedgerConfirmsUnauthorizedHardwareImplantInUserDevice
Ví "lạnh" nhưng lòng trader "nóng" như lửa! 🔥
🚨 Phốt cực căng: Ledger vừa xác nhận có ít nhất một thiết bị của người dùng đã bị "cấy ghép" phần cứng trái phép! Nhà phân phối CryptoBilis hoảng hốt ngừng bán toàn bộ sản phẩm ngay lập tức.
🤔 Ủa rồi tem mác để làm gì? Nhiều anh em thắc mắc tem niêm phong, tem bảo hành dán đầy mà sao vẫn bị can thiệp?
🏷️ Tụi hacker bây giờ làm giả hoặc bóc tem tinh vi lắm, "tấn công chuỗi cung ứng" là chuyện nhỏ.
🕵️ Hoặc có khi nào do... nội gián lén tuồn chip lạ vào trước khi dán tem? Ledger khẳng định hệ thống của họ vẫn an toàn, nhưng drama này còn dài!
🛡️ Trader phải làm gì?
🛑 Ai mua từ CryptoBilis mà chưa cài thì đừng sờ vào.
💸 Ai lỡ cài rồi thì mau chuyển hết tài sản sang ví mới với 24 ký từ hoàn toàn mới ngay!
⚠️ Đây không phải lời khuyên tài chính!
👉 Đăng ký tài khoản Binance mới để chiến cùng tôi:
➕ Mã giới thiệu: VINHTOCDO
🔗 Link: binance.com
👇 Click giao dịch bên dưới để ủng hộ tôi:
$BTC
$ETH
$BNB
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
Ví "lạnh" nhưng lòng trader "nóng" như lửa! 🔥
🚨 Phốt cực căng: Ledger vừa xác nhận có ít nhất một thiết bị của người dùng đã bị "cấy ghép" phần cứng trái phép! Nhà phân phối CryptoBilis hoảng hốt ngừng bán toàn bộ sản phẩm ngay lập tức.
🤔 Ủa rồi tem mác để làm gì? Nhiều anh em thắc mắc tem niêm phong, tem bảo hành dán đầy mà sao vẫn bị can thiệp?
🏷️ Tụi hacker bây giờ làm giả hoặc bóc tem tinh vi lắm, "tấn công chuỗi cung ứng" là chuyện nhỏ.
🕵️ Hoặc có khi nào do... nội gián lén tuồn chip lạ vào trước khi dán tem? Ledger khẳng định hệ thống của họ vẫn an toàn, nhưng drama này còn dài!
🛡️ Trader phải làm gì?
🛑 Ai mua từ CryptoBilis mà chưa cài thì đừng sờ vào.
💸 Ai lỡ cài rồi thì mau chuyển hết tài sản sang ví mới với 24 ký từ hoàn toàn mới ngay!
⚠️ Đây không phải lời khuyên tài chính!
👉 Đăng ký tài khoản Binance mới để chiến cùng tôi:
➕ Mã giới thiệu: VINHTOCDO
🔗 Link: binance.com
👇 Click giao dịch bên dưới để ủng hộ tôi:
$BTC
$ETH
$BNB
#Ledger #CryptoSecurity #HardwareWallet #CryptoScam #SupplyChainAttack #VINHTOCDO
8
5.1k

$INJ NPM PACKAGE HACK — 50K WEEKLY DOWNLOADS COMPROMISED 🔥
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
$INJ NPM PACKAGE HACK — 50K WEEKLY DOWNLOADS COMPROMISED 🔥
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
Malicious version 1.20.21 of injectivelabs/sdk-ts is stealing private keys and recovery phrases. The dev's GitHub account was compromised in a classic supply chain attack targeting developers. With roughly 50,000 downloads per week, this is not a small-scale incident. If you or your team have interacted with this package since June 8th, change your keys immediately.
Injective reacted fast, but the npm ecosystem still has gaps. Are you checking your dependencies for malicious updates?
Not financial advice. Always manage your risk.
#INJ #SecurityAlert #SupplyChainAttack #CryptoNews #Web3
⚡
150

·
--
🚨 2,000 POISONED PACKAGES FLOOD $KEYV — 127M DOWNLOADS IN THE BLAST RADIUS! 💥
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
🚨 2,000 POISONED PACKAGES FLOOD $KEYV — 127M DOWNLOADS IN THE BLAST RADIUS! 💥
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
At 127M downloads a week, this isn't a bug — it's a weaponized breach with a huge blast radius. 🦈 The attacker flooded the Keyv/Cacheable ecosystem with 2,000+ malicious versions, including keyv@6.0.0, mirroring the Shai-Hulud worm's automation. 🔍
This is how projects get gutted from the inside: credential theft, CI/CD key leaks, remote payloads, lateral movement through dev environments. Every downstream app touching this library is exposed. 📊
If you hold keys or run build pipelines on Node.js, treat your dependencies as compromised until audited. Rotate credentials and inspect lock files now. ⚠️ 💬 Is your project's dependency tree clean, or are you one package away from a nightmare? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #KEYV #SupplyChainAttack #CryptoSecurity #CyberAlert #NPM
🔍 🛡️
13

Ledger phát hiện implant phần cứng trái phép trong ví crypto, lo ngại tấn công chuỗi cung ứng
- Ledger xác nhận phát hiện implant phần cứng trái phép bên trong ví crypto
- Implant liên quan đến điều tra trộm cắp đang diễn ra
- Nâng cao lo ngại về tấn công chuỗi cung ứng tinh vi
- Nguồn RSS chưa cung cấp thêm chi tiết về quy mô hoặc ví cụ thể
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Nguồn: U.Today
Ledger phát hiện implant phần cứng trái phép trong ví crypto, lo ngại tấn công chuỗi cung ứng
- Ledger xác nhận phát hiện implant phần cứng trái phép bên trong ví crypto
- Implant liên quan đến điều tra trộm cắp đang diễn ra
- Nâng cao lo ngại về tấn công chuỗi cung ứng tinh vi
- Nguồn RSS chưa cung cấp thêm chi tiết về quy mô hoặc ví cụ thể
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Nguồn: U.Today
- Ledger xác nhận phát hiện implant phần cứng trái phép bên trong ví crypto
- Implant liên quan đến điều tra trộm cắp đang diễn ra
- Nâng cao lo ngại về tấn công chuỗi cung ứng tinh vi
- Nguồn RSS chưa cung cấp thêm chi tiết về quy mô hoặc ví cụ thể
#BinanceSquare #CryptoNews #Ledger #Security #SupplyChainAttack
$btc $eth
vlikevn Titanbot
Nguồn: U.Today
134
Көбірек контент көру үшін кіріңіз
Binance Square платформасында әлемдік криптоқоғамдастыққа қосылыңыз
⚡️ Криптовалюта туралы ең соңғы және пайдалы ақпаратты алыңыз.
💬 Әлемдегі ең ірі криптобиржаның сеніміне ие.
👍 Расталған авторлардың нақты пікірлерін табыңыз.
Электрондық пошта/телефон нөмірі
Трендтегі тақырыптар
1
#NvidiaBeatsEstimatesAICloudStocksRiseAfterHours
3,164 рет көрілді
58 адам талқылап жатыр
2
#A Packed Week of Earnings and Data Tests Markets
150,850 рет көрілді
667 адам талқылап жатыр
3
#AnthropicIPOTestsInvestorAppetiteForAI
333,429 рет көрілді
2,917 адам талқылап жатыр
4
#NvidiaBoardNotConsideringHuang’sReturnasCEO
125,078 рет көрілді
990 адам талқылап жатыр
5
#KOSPIFalls2.59%ToLowestCloseSinceFebruary
32,481 рет көрілді
337 адам талқылап жатыр
6
#AnthropicClearedToListOnNasdaqAsANT
27,453 рет көрілді
279 адам талқылап жатыр
7
#WhatInvestmentSignalsDo13FFilingsReveal?
68,641 рет көрілді
677 адам талқылап жатыр
8
#TetherCapitalMakesStrategicInvestmentInStables
15,647 рет көрілді
121 адам талқылап жатыр
9
#EvernorthRecords$505MImpairmentOnPreListingXRP
1,910 рет көрілді
21 адам талқылап жатыр
10
#GoldmanSachsReports$1.22BInEtherETFHoldings
1,367 рет көрілді
17 адам талқылап жатыр