

#phishingalert
phishingalert
294,355 vues
215 mentions
Populaire
Récents
·
--
$BTC — 🟢 Bullish Setup$BTC 🟢 Bullish Setup
كيف تميز بين البريد الرسمي والرسالة المفخخة؟ 📧
يتفنن المحتالون في تقليد واجهات المنصات الشهيرة مثل بينانس لحرق بيانات دخولك.
درع الحماية الخاص بك:
رمز التشفير الشخصي (Anti-Phishing Code): فعل هذه الميزة من إعدادات الأمان في بينانس ليظهر رمزك الخاص في كل بريد رسمي يصلك.
المصادقة الثنائية (2FA): استخدم تطبيقات مثل Google Authenticator أو مفاتيح الأمان الفيزيائية (YubiKey) وتجنب الـ SMS تماماً.
التحقق من القنوات: استخدم خيار Binance Verify للتحقق من أي رابط أو حساب يزعم انتماءه لبينانس.
💡 الشك المسبق هو أول خط دفاع عن محفظتك.
#PhishingAlert #SecurityTools #BinanceSquare #CryptoSafety
────────────────────────
VX Network — Analyst: @ApexHunter669
$BTC — 🟢 Bullish Setup
$BTC 🟢 Bullish Setup
كيف تميز بين البريد الرسمي والرسالة المفخخة؟ 📧
يتفنن المحتالون في تقليد واجهات المنصات الشهيرة مثل بينانس لحرق بيانات دخولك.
درع الحماية الخاص بك:
رمز التشفير الشخصي (Anti-Phishing Code): فعل هذه الميزة من إعدادات الأمان في بينانس ليظهر رمزك الخاص في كل بريد رسمي يصلك.
المصادقة الثنائية (2FA): استخدم تطبيقات مثل Google Authenticator أو مفاتيح الأمان الفيزيائية (YubiKey) وتجنب الـ SMS تماماً.
التحقق من القنوات: استخدم خيار Binance Verify للتحقق من أي رابط أو حساب يزعم انتماءه لبينانس.
💡 الشك المسبق هو أول خط دفاع عن محفظتك.
#PhishingAlert #SecurityTools #BinanceSquare #CryptoSafety
────────────────────────
VX Network — Analyst: @ApexHunter669
1
105

·
--
🚨 $TREZOR ALERT: PHISHING EMAILS USING OFFICIAL DOMAIN TARGET USERS 🛑
🦈 A third‑party email service breach let attackers spoof $TREZOR ’s official domain, delivering a fake “Critical Security Alert: STM32 Entropy Vulnerability” that looks indistinguishable from a genuine notice. 📊 The deception bypasses simple address checks, forcing users to rely on visual cues that the phishing crew has meticulously replicated.
🔍 With roughly 87 k records already exposed from the prior ShipMonk breach, attackers now have a rich data pool to craft highly targeted lures. 📌 $TREZOR advises you to ignore links, manually type the official website, and cross‑verify any alert inside the wallet app before acting.
💬 Are you double‑checking every security alert before clicking?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #TREZOR #PhishingAlert #SecurityRisk #CryptoSafety
🔥 🦈
27

·
--
#revolutconfirmsfakegovemaildatabreach
🛑 SECURITY WARNING: Revolut Data Breach Exposes User Emails—Protect Your Crypto!
📊 Security Alert & Breach Context
The Incident Details: Fintech and banking app Revolut confirmed a targeted data breach after compliance teams responded to a fraudulent record request sent from an email address using a legitimate government agency domain.
Exposed Customer Files: On-chain investigator ZachXBT revealed that the leak impacted high-net-worth users. Compromised files include full names, home addresses, phone numbers, passport/ID copies, verification selfies, account statements, and full transaction histories—including linked Bitcoin ($BTC) transfers.
System & Funds Status: Revolut confirmed that its core banking infrastructure, app passwords, card PINs, and private keys were not compromised, and user funds remain fully secure. However, exposed KYC data creates severe off-chain risks.
💡 How to Protect Yourself from Phishing Traps
Beware of Hyper-Targeted Phishing: Attackers with access to transaction records and home addresses can generate sophisticated phishing emails or SMS messages impersonating Revolut or crypto exchanges.
Never Share OTPs or Passwords: Revolut or exchange support agents will never ask for your 2FA codes, login credentials, or recovery phrases over the phone or via email.
Move Long-Term Holdings Off-App: Store high-value crypto assets in self-custody hardware wallets rather than centralized fintech platforms to minimize exposure to third-party data leaks.
💬 Community Poll: Does the exposure of KYC data by centralized platforms make you reconsider keeping crypto on fintech apps? Share your security tips below! 👇
#ClarityActFacesProceduralVoteSept15 #PhishingAlert #CYBER
1
173

🚨 $BTC ALERT: PHISHING SCAM HIDING BEHIND Trezor’S OFFICIAL DOMAIN! 🦈
The latest breach exploited a compromised third‑party email service, letting attackers fire “Critical Security Alert” mails that look straight from Trezor’s domain. 📧 With 87k+ users already exposed from a prior shipment‑partner hack, the phishing payload now masquerades as an urgent firmware update, making visual verification nearly impossible. 📊
Smart money knows the moment a legit‑looking email lands, it’s a liquidity sweep for credentials—not a market move. Keep your inbox razor‑sharp and verify every link on the official site, not the email. 💡💬 Are you double‑checking Trezor alerts before you click? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #PhishingAlert #Security #Crypto
🔥 💎
20
🚨 MASSIVE PHISHING EXPLOIT TARGETS 347K TREZOR USERS TO STEAL $BTC SEED PHRASES! ⚡
A third-party breach exposed 347,000 email addresses, triggering a wave of fake security alerts. Scammers fabricated an STM32 entropy flaw, pushing malicious software designed to intercept recovery seeds. 📊
Your actual hardware cold storage remains completely uncompromised. The attack vector is strictly social engineering, hunting for human error rather than breaking encryption. 🛡️ Keep your seed phrase strictly offline — never type those words into any application, website, or email form. 💡
💬 Did you spot this fake security notification sitting in your inbox today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #PhishingAlert #ColdStorage
🛡️ 👁️

18


Trezor users, heads up. Hardware wallet manufacturer Trezor just confirmed that their third-party email provider was breached. This means hackers have been sending out realistic-looking fake security alerts to users. Here is what you need to know right now: 1️⃣ The phishing emails falsely claim there is a critical hardware flaw on your device. 2️⃣ They will try to trick you into entering your recovery phrase to fix this imaginary issue. 3️⃣ Never, under any circumstances, type your seed phrase online or share it with anyone. Your physical device and your $BTC funds remain safe as long as you keep your recovery phrase completely offline and private. Stay vigilant because security starts with our own actions. #Bitcoin #PhishingAlert #Security #Write2Earn
Trezor users, heads up. Hardware wallet manufacturer Trezor just confirmed that their third-party email provider was breached. This means hackers have been sending out realistic-looking fake security alerts to users. Here is what you need to know right now: 1️⃣ The phishing emails falsely claim there is a critical hardware flaw on your device. 2️⃣ They will try to trick you into entering your recovery phrase to fix this imaginary issue. 3️⃣ Never, under any circumstances, type your seed phrase online or share it with anyone. Your physical device and your $BTC funds remain safe as long as you keep your recovery phrase completely offline and private. Stay vigilant because security starts with our own actions. #Bitcoin #PhishingAlert #Security #Write2Earn

63

Trezor confirms that a data breach at one of its shipping providers has compromised the information of 67,000 US customers, potentially exposing them to targeted phishing and social engineering attacks.
#Trezor #PhishingAlert
Trezor confirms that a data breach at one of its shipping providers has compromised the information of 67,000 US customers, potentially exposing them to targeted phishing and social engineering attacks.
#Trezor #PhishingAlert
#Trezor #PhishingAlert
7
Watch out for fake Telegram ads
Ukrainian police just busted a Kyiv based crypto drainer ring pulling in $1M monthly. They were using fake Telegram ads and fake exchanges to rug victims. Stay alert.
#TelegramScams #PhishingAlert
Watch out for fake Telegram ads
Ukrainian police just busted a Kyiv based crypto drainer ring pulling in $1M monthly. They were using fake Telegram ads and fake exchanges to rug victims. Stay alert.
#TelegramScams #PhishingAlert
Ukrainian police just busted a Kyiv based crypto drainer ring pulling in $1M monthly. They were using fake Telegram ads and fake exchanges to rug victims. Stay alert.
#TelegramScams #PhishingAlert
14
Watch out for this new GTA 6 scam
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
Watch out for this new GTA 6 scam
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
Scammers are using fake Grand Theft Auto VI leak sites to deploy malicious wallet drainers. Be extremely careful with hype driven links and avoid connecting your wallet to unverified sources to prevent getting rekt.
#PhishingAlert #WalletSecurity
1
36

·
--
🚨 CRITICAL SECURITY ALERT: New iOS Phishing Attack
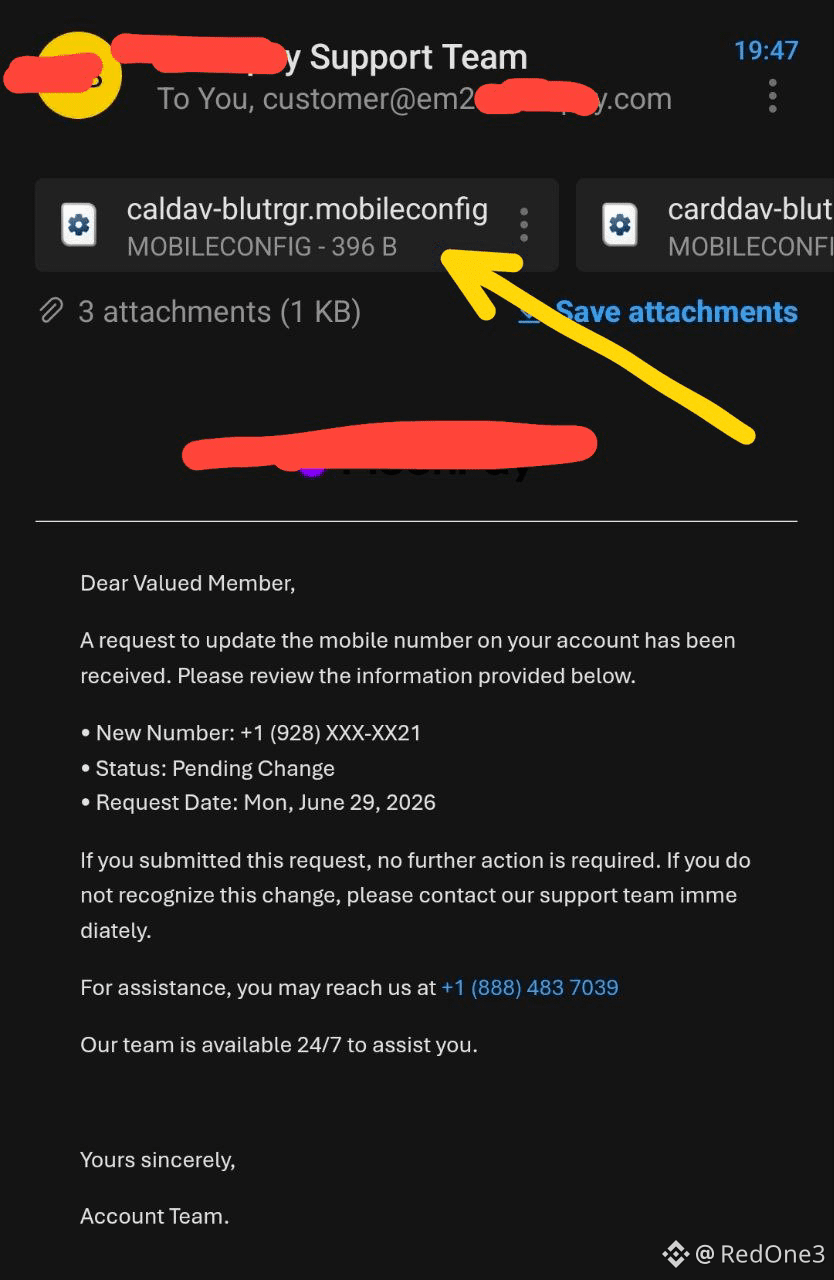
I just received this highly sophisticated phishing email a few moments ago, and I wanted to warn you immediately so you can protect your devices and crypto assets.
How the Attack Works (As seen in image.png):
The email claims my account phone number is being changed to create panic. The real danger is the attached files ending in .mobileconfig (like the caldav file pointed at by the arrow).
Why it is Dangerous:
A .mobileconfig file is an iOS Configuration Profile. If you download and install it, you give attackers deep system privileges. They can route your internet traffic through a malicious VPN, install fake certificates to spy on your data, or steal passwords and 2FA codes.
What to Do:
* Never download .mobileconfig files from emails.
* Never call the support numbers listed in these emails.
* Check your iPhone via Settings -> General -> VPN & Device Management. If you see any unauthorized profile, remove it immediately.
Stay #SAFU ⚠️
#CyberSecurity #PhishingAlert #Web3Security
1
291

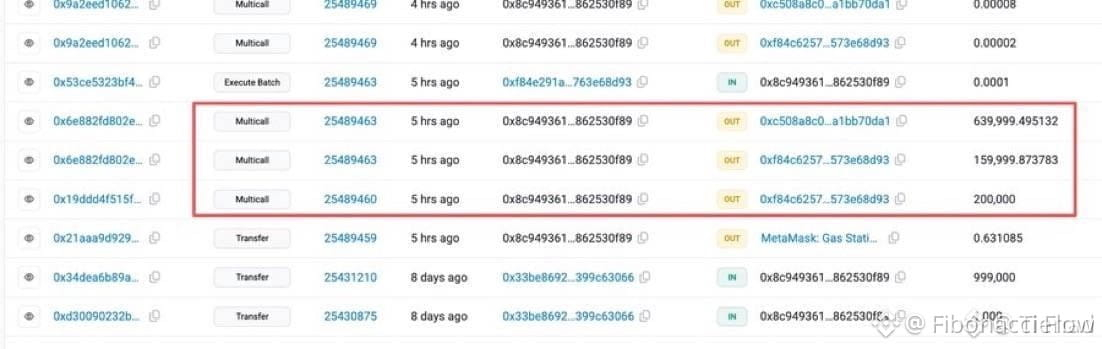
$VANRY HIT BY PHISHING INCIDENT – MARKET ON EDGE 😱
Not applicable – no specific price levels provided in input.
A $999,999 phishing loss just hit the market, and that kind of liquidity drain always leaves a mark. Expect short-term hesitation as traders lock down security, but sharp money might see this as a dip-buying zone on $VANRY and $THE .
Volume could dry up for a few hours before the opportunistic bids step in. How are you playing this – sitting out or waiting for a hard retest below support?
Not financial advice. Always manage your risk.
#VANRY #PhishingAlert #MarketUpdate #CryptoRisk
😱
182
·
--
Digital squatting attacks targeting businesses are on the rise.
• TechRadar reported attackers are registering fraudulent domains to impersonate legitimate businesses
• Malicious domains are used to trick users into visiting fake sites and stealing credentials
• Domain name disputes rose 68% between 2020 and 2025, reaching 6,200 cases in 2025
#CryptoSecurity #CryptoNews #BinanceSquare #PhishingAlert #Web3Security
26
TREZOR DATA BREACH: 11,742 WALLETS EXPOSED — PHISHING STORM LOOMING 🚨📡
The hardware wallet giant just confirmed a shipping provider leak — names, addresses, phones, and emails of 11,742 customers are now in the wild. Another 1,947 caught partial exposure. This isn't a protocol hack; your coins are still locked tight inside the device. But the human layer just cracked open.
Phishing season just went prime time. Bad actors now hold your personal coordinates — expect fake support DMs, poisoned links, and social engineering dressed up as official Trezor comms. The device stays bulletproof, but your inbox just became the new battleground.
For $COTI and $QNTB holders riding this wave: your keys are the castle walls. Everything outside that vault is fair game. How do you separate legit Trezor messages from the spoofed ones? 🛡️
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ $COTI #Trezor #CryptoSecurity #PhishingAlert #Bitcoin
🔐⚡
46
🚨 Alerta de Seguridad: Fallo en SafePal expone a 40.000 usuarios
La firma de hardware wallets SafePal acaba de confirmar una filtración de datos tras un fallo en su sistema de seguimiento de pedidos (E-commerce).
📊 Los datos del incidente:
Información filtrada: Nombres, direcciones físicas de envío, correos, números telefónicos e historial de compras de ~39.798 clientes.
Seguridad cripto: 100% intacta. Claves privadas, frases semilla (seed phrases) y fondos NO fueron comprometidos.
🛠️ El análisis técnico:
Aunque la arquitectura Air-Gapped y de almacenamiento en frío de SafePal protege los activos en la cadena, el verdadero peligro ahora es la Ingeniería Social de Alta Precisión (Spear-Phishing).
Al vincular tu nombre y dirección física con la compra de una cold wallet, los atacantes pueden desplegar:
Correos y SMS falsos advirtiendo de "actualizaciones urgentes de firmware" para robar tu semilla.
Envíos postales físicos con dispositivos manipulados o cartas falsas con códigos QR maliciosos.
💬 DEBATE:
¿Hasta qué punto las fugas de datos en la capa Web2 (E-commerce) destruyen la privacidad de la seguridad Web3? Si usas hardware wallet, ¿compras directamente al fabricante o prefieres métodos que no dejen rastro de tu dirección física?
¡Los leo en los comentarios! 👇
#SafePal #CryptoSecurity #PhishingAlert #HardwareWallets #BinanceSquare
$SFP
{future}(SFPUSDT)
🚨 Alerta de Seguridad: Fallo en SafePal expone a 40.000 usuarios
La firma de hardware wallets SafePal acaba de confirmar una filtración de datos tras un fallo en su sistema de seguimiento de pedidos (E-commerce).
📊 Los datos del incidente:
Información filtrada: Nombres, direcciones físicas de envío, correos, números telefónicos e historial de compras de ~39.798 clientes.
Seguridad cripto: 100% intacta. Claves privadas, frases semilla (seed phrases) y fondos NO fueron comprometidos.
🛠️ El análisis técnico:
Aunque la arquitectura Air-Gapped y de almacenamiento en frío de SafePal protege los activos en la cadena, el verdadero peligro ahora es la Ingeniería Social de Alta Precisión (Spear-Phishing).
Al vincular tu nombre y dirección física con la compra de una cold wallet, los atacantes pueden desplegar:
Correos y SMS falsos advirtiendo de "actualizaciones urgentes de firmware" para robar tu semilla.
Envíos postales físicos con dispositivos manipulados o cartas falsas con códigos QR maliciosos.
💬 DEBATE:
¿Hasta qué punto las fugas de datos en la capa Web2 (E-commerce) destruyen la privacidad de la seguridad Web3? Si usas hardware wallet, ¿compras directamente al fabricante o prefieres métodos que no dejen rastro de tu dirección física?
¡Los leo en los comentarios! 👇
#SafePal #CryptoSecurity #PhishingAlert #HardwareWallets #BinanceSquare
$SFP
1
206

·
--
$GNO SECURITY BREACH — OFFICIAL X ACCOUNT COMPROMISED ⚠️
Body:
PeckShield has confirmed that Gnosis’s official X account was hijacked earlier today. Community members are advised to avoid all engagement — no links, no DMs, no retweets. This is the second major project account compromise this week.
Attackers typically use compromised accounts to post fake token contracts or phishing links. Verify all official communications through Gnosis’s website or Discord alone. What steps are you taking to verify project announcements before interacting?
Not financial advice. Always manage your risk.
#GNO #SecurityAlert #CryptoHack #PhishingAlert
⚠️
19

·
--
$PUMP HOLDERS BEWARE – RUSSIAN HACKERS ARE PHISHING SIGNAL BACKUP KEYS 🔥
This isn't your typical phishing campaign. The FBI and CISA just warned that Russian intelligence groups are targeting Signal recovery keys – not just login codes. If a hacker gets that key, they can restore your entire chat history and keep access even after you change phones.
$PUMP gained 12% recently but the real risk is traders getting their Signal accounts compromised. These hackers are posing as automated support, asking you to paste your recovery key. Generating a new key in Signal settings invalidates the old one, but any backup already accessed is gone. Are you sure your Signal group chats are safe?
Not financial advice. Always manage your risk.
#PUMP #PhishingAlert #Security #CryptoWarning #Signal
🔥
48
·
--
CRITICAL ALERT: Protect Your Crypto! 🛑 5 Essential Security Habits for Beginners 🔐
GM #BinanceSquare Fam! 👋 As the market heats up, so do the scammers. Your first priority in crypto is not just making profits, but protecting your assets.
Every day, we see new stories of people losing their hard-earned funds to phishing links, fake airdrops, and wallet drainers. Don't be the next victim!
Develop these 5 habits immediately:
1️⃣ Enable 2FA (Two-Factor Authentication): Use an authenticator app (like Google Authenticator) on your exchange accounts, NOT SMS.
2️⃣ NEVER Share Your Seed Phrase: Write it down offline on paper. No legitimate support team will ever ask for it.
3️⃣ Bookmark Official Sites: Avoid clicking links from Google Search or social media ads. Scammers create fake sites that look identical.
4️⃣ Double-Check Wallet Addresses: Always send a small test amount first. Malware can change addresses in your clipboard.
5️⃣ Beware of "Too Good to Be True" Offers: Free double-your-crypto schemes and surprise high-value airdrops are almost always scams.
💡 My Personal Take: Stay paranoid. Security is your own responsibility. If something feels suspicious, trust your gut and walk away. It's better to miss an opportunity than to lose your funds forever.
👇 What's the scariest scam attempt you've seen recently? Share your experience below to warn others! 👇
#CryptoSecurity #StaySafe #PhishingAlert #BinanceSquare #ScamPrevention #CryptoEducation #ProtectYourFunds
44

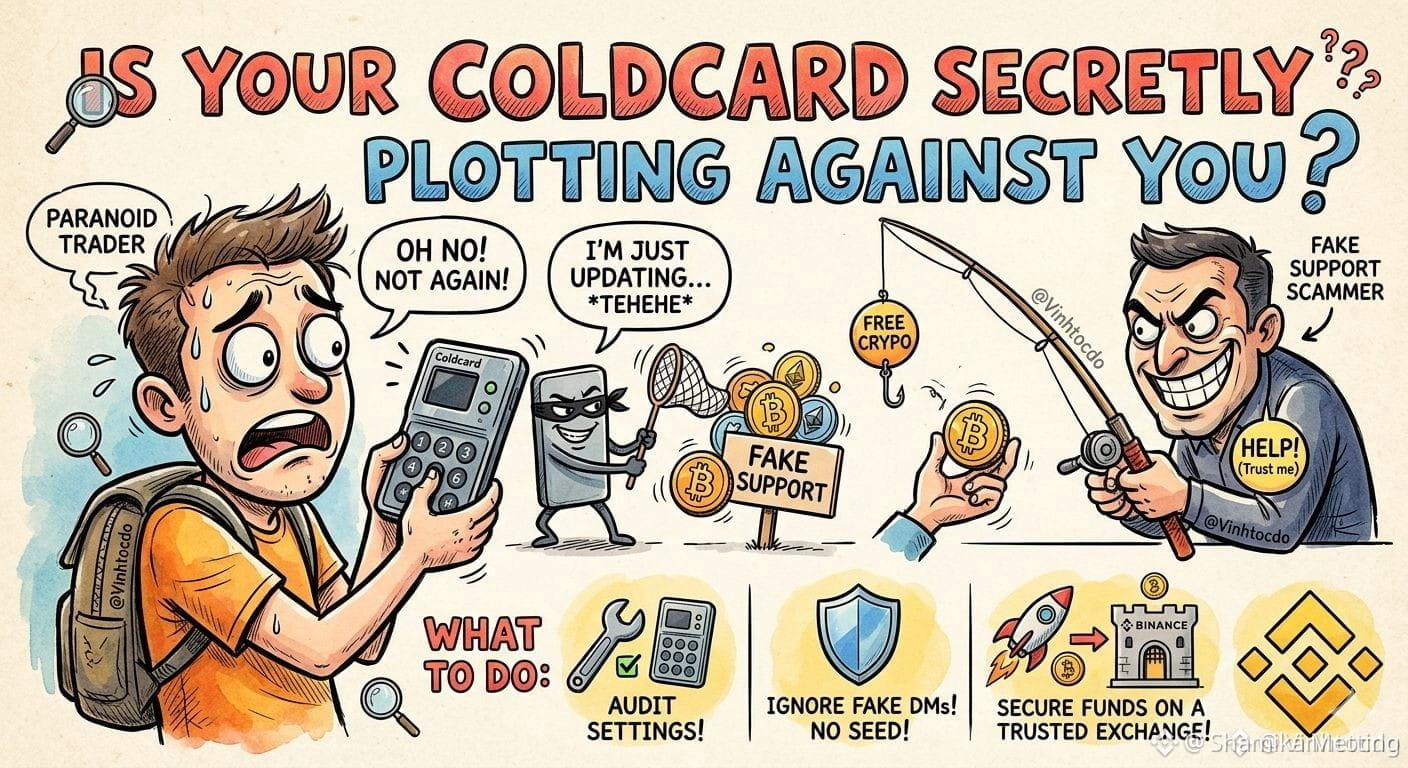
🚨 عاجل: هل يتآمر #Coldcard بشكلٍ سري ضدك؟ 🕵️♂️
ألقى رئيس أبحاث “Galaxy” للتو قنبلة: ما زالت هجمات التصيّد والهجمات الاستغلالية تستهدف مستخدمي Coldcard تحدث بنشاط! إذا كنت تحتفظ بالأصول هناك، استيقظ وتحقّق من إعدادات جهازك ثلاث مرات الآن. ما الجزء الأكثر رعبًا؟ حسابات دعم مزيفة منتشرة في كل مكان، تنتظر منك أن "تطلب المساعدة" لاستعادة أموالك بينما تقوم في الحقيقة بسحب رصيد محفظتك. إذا بدت الأمور مشبوهة، يقترح خبراء الأمن نقل الأصول إلى بيئة أكثر أمانًا فورًا—حتى بورصة فائقة الأمان مثل Binance أفضل من إعداد مخترق!
♂️ ما الذي يجب على المتداولين فعله الآن؟
1️⃣ راجع جهازك: أعد التحقق من إعدادات Coldcard والبرنامج الثابت (firmware). لا تثق به أعمى.
2️⃣ انتبه من المساعدة المزيفة: لن تقوم فرق أمن حقيقية أبدًا بمراسلتك عبر DM من أجل عبارة البذور. تجاهل محتالي الدعم!
3️⃣ تأمين أموالك: إذا كنت في شك، قم بتأمين أصولك السائلة مؤقتًا على منصة موثوقة.
هذا ليس نصيحة مالية. قم دائمًا بالبحث بنفسك (DYOR)!
متابعة من فضلكم
#CryptoSecurity #PhishingAlert #HardwareWallet
$BTC
{future}(BTCUSDT)
$NVDAB
{spot}(NVDABUSDT)
🚨 عاجل: هل يتآمر #Coldcard بشكلٍ سري ضدك؟ 🕵️♂️
ألقى رئيس أبحاث “Galaxy” للتو قنبلة: ما زالت هجمات التصيّد والهجمات الاستغلالية تستهدف مستخدمي Coldcard تحدث بنشاط! إذا كنت تحتفظ بالأصول هناك، استيقظ وتحقّق من إعدادات جهازك ثلاث مرات الآن. ما الجزء الأكثر رعبًا؟ حسابات دعم مزيفة منتشرة في كل مكان، تنتظر منك أن "تطلب المساعدة" لاستعادة أموالك بينما تقوم في الحقيقة بسحب رصيد محفظتك. إذا بدت الأمور مشبوهة، يقترح خبراء الأمن نقل الأصول إلى بيئة أكثر أمانًا فورًا—حتى بورصة فائقة الأمان مثل Binance أفضل من إعداد مخترق!
♂️ ما الذي يجب على المتداولين فعله الآن؟
1️⃣ راجع جهازك: أعد التحقق من إعدادات Coldcard والبرنامج الثابت (firmware). لا تثق به أعمى.
2️⃣ انتبه من المساعدة المزيفة: لن تقوم فرق أمن حقيقية أبدًا بمراسلتك عبر DM من أجل عبارة البذور. تجاهل محتالي الدعم!
3️⃣ تأمين أموالك: إذا كنت في شك، قم بتأمين أصولك السائلة مؤقتًا على منصة موثوقة.
هذا ليس نصيحة مالية. قم دائمًا بالبحث بنفسك (DYOR)!
متابعة من فضلكم
#CryptoSecurity #PhishingAlert #HardwareWallet
$BTC
$NVDAB
1
40
HALF A MILLION GONE IN ONE CLICK — $HYPE PHISHING SCAM EXPOSES GOOGLE ADS 🎣💸
One wrong click just cost a Hyperliquid user $550,000 in USDC. A malicious Google search ad redirected them to a fake Hyperliquid site, and blockchain data shows three transfers draining the wallet to attacker-controlled addresses. 🚨
This isn't a random one-off. Security Alliance (SEAL) has been tracking this exact playbook for months — they blocked 356 malicious Google ad URLs in April alone, many impersonating Hyperliquid. Attackers are targeting high-value platforms like $HYPE , Jupiter, Raydium and Pump.fun, often using hacked ad accounts to slip past automated checks. 📉
The painful truth? The entire ecosystem — exchanges, protocols, even Google — stays silent while users get picked off. No comments, no accountability, no urgency.
Before you search your next protocol, ask yourself: how do you verify the site you're clicking is the real one? 🔐
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #HYPE #CryptoSecurity #PhishingAlert #Web3
🧠🔥
59
🚨 CRITICAL PHISHING ATTACK EXPOSES 347K HARDWARE WALLET USERS HOLDING $BTC ! 🚨
Attackers exploited third-party email provider Brevo, compromising contact databases across major hardware wallet vendors like Trezor and BitBox. 🚨 Over 347,000 subscribers were targeted with fake security alerts engineered to drain wallet backup phrases.
Although emergency DNS traps blocked the domain within 20 minutes, nearly 2,500 users still clicked through to the fake portal. 🔍 Third-party software integrations continue to present severe vulnerability risks for offline assets. 🛡️
💬 How are you auditing your email security to protect your $BTC cold storage? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #SelfCustody #PhishingAlert #Crypto
🚨 🛡️
1
1
70
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
1
#GoldFallsTo$4144
1,368 vues
41 mentions
2
#QNTFallsOver40%FromMorningHigh
9,177 vues
333 mentions
3
#KospiFalls2.7%SamsungSKHynixDropOver5%
601 vues
96 mentions
4
#BitgetCEOConfirms$388MStolenInHack
451 vues
19 mentions
5
#BTCFallsBelow$83000
10,539 vues
101 mentions
6
#BitgetDetailsSecurityIncidentTimeline
8,112 vues
258 mentions
7
#BitcoinSpotETFs$2.39BWeeklyNetInflow
3,652 vues
23 mentions
8
#FedProposesPaymentStablecoinRules
34,138 vues
620 mentions
9
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
35,863 vues
657 mentions
10
#USChinaRelease$30BTariffCutProductLists
3,434 vues
51 mentions