The $NEAR Intents $3.8M hacker just gave everything back.
Less than 24 hours after NEAR said it had identified the person behind the $3.8M exploit, the full amount was returned before the 48-hour deadline.
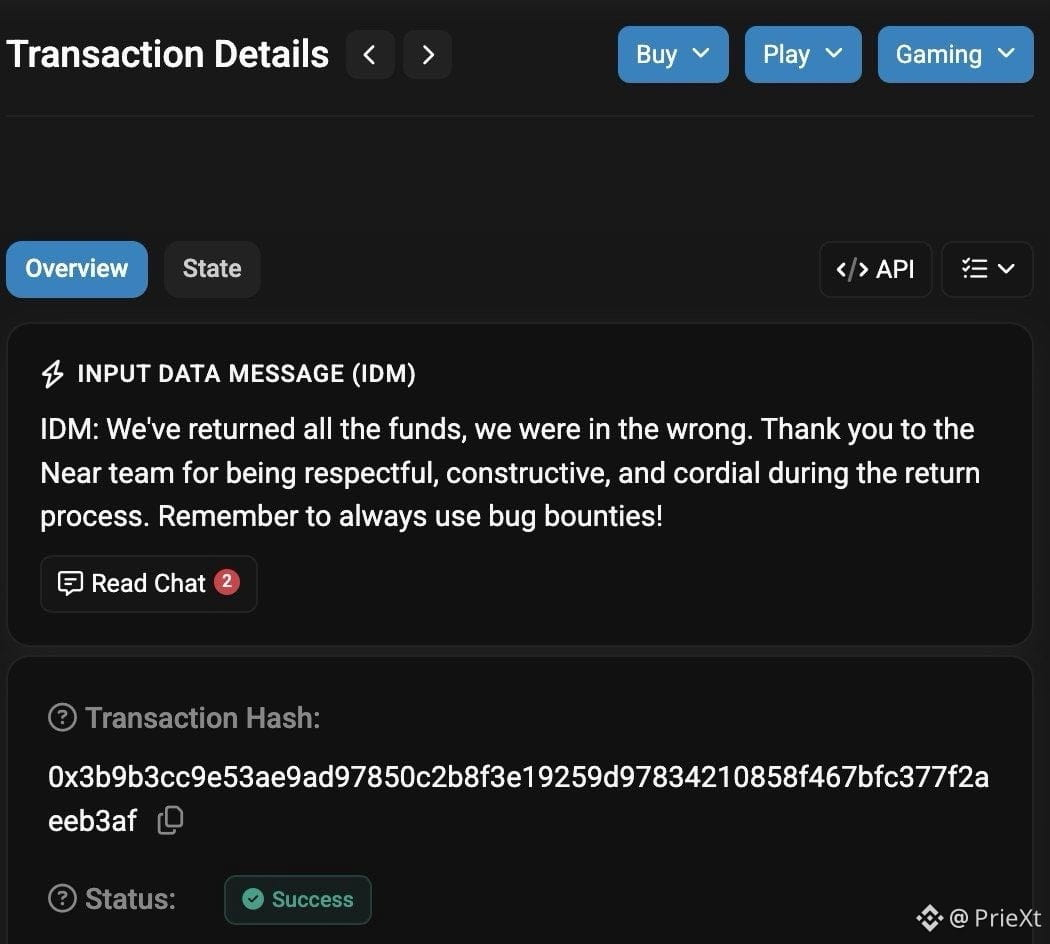
And the message attached to the return was unexpected.
The attacker admitted they were “in the wrong,” thanked the NEAR team for handling the situation respectfully, and told them to use bug bounties instead of disrupting services.
Crypto hacks usually end with funds disappearing into a maze of wallets.
This one ended with the hacker sending every dollar back… This is great!