
#trezor
trezor
50,548 views
219 Discussing
Hot
Latest

·
--
A sponsored ad impersonated Trezor Suite; users who entered their recovery phrase were drained within minutes
In late October, someone searching Google for Trezor Suite saw an ad ranked above the real result. Clicking it led to a wallet software page that looked almost identical to the real thing. Sometimes it was hosted on its own domain; other times, it was tucked away on a Google Sites page. The page asked users to enter their recovery phrase, supposedly to restore their wallet. Within minutes of entering it, users found their balances gone.
So far, this wave has generated only five reports on Chainabuse, from several countries. One reporter said they had already filed a police report in the Czech Republic. The losses involved Bitcoin, Ether, and stablecoins. On-chain analytics tool Coinator tracked only the Bitcoin side—and found a much larger scale than the reports suggested.
The funds didn’t go straight to the scammers’ own wallets. They first landed at two fixed collection addresses. The first received 39 transactions totaling 3.32 Bitcoin between October 27 and 31. The largest single amount mentioned in a report was over 0.2 Bitcoin. The second address had no reports associated with it, yet received 56 transactions totaling 8.17 Bitcoin—more than twice as much as the first. Together, the two addresses received about 95 transactions, totaling 11.49 Bitcoin.
At 15:57 UTC on October 31, the second address was emptied in a single transaction with 56 inputs. Twelve minutes later, the first address was emptied in a transaction with 33 inputs. Both sets of funds went to the same intermediary address. That address received a total of 21.62 Bitcoin; the extra amount came from earlier deposits. Coinator’s assessment is that this group had received similar funds before. Starting at 17:12 UTC that day, the intermediary address began sending funds out in batches: first 2.0 Bitcoin, then 2.86 Bitcoin, and finally 1.54 Bitcoin. All three transactions had exactly the same fee of 564 satoshis, and their versions, lock times, and replaceability flags also matched—clear signs they came from the same wallet.
Of those three outgoing transactions, the 2.0 and 2.86 Bitcoin were still sitting untouched at their original addresses as of November 3. The 1.54 Bitcoin was moved in three steps that evening: first a 0.01 Bitcoin test, then 0.5 Bitcoin, and finally 1.03 Bitcoin. Each step passed through an intermediary address, and all the funds ultimately ended up in the hot wallet of the same custodial service. Since February 2025, this hot wallet has handled about 139,000 transactions, moving roughly 37,000 Bitcoin, and has been linked to 162,000 deposit addresses, almost all used just once. The same hot wallet also received funds from a fake Kraken support scam in August, and was the endpoint in a case in Argentina in late October. Three different scams, one destination for the money.
There’s an easy place to get the trail wrong. The 0.01 Bitcoin test payment went into a deposit address. A few hours later, that address was spent together with eight other deposit addresses and two of the hot wallet’s own inputs. Then 0.29 Bitcoin went to a new address, making it look as if the scammers had taken their money back—and somehow ended up with more. In reality, it was a payment from the custodial service to one of its customers. The deposit addresses and the hot wallet belong to the service provider; once the funds are in the provider’s hands, it no longer matters who originally deposited them. If you track the hot wallet as though it belongs to the scammers, you’ll identify the wrong people. The addresses worth keeping track of are the scammers’ two collection addresses.
For everyday users, the takeaway is very concrete. Only trust wallet software from the provider’s official website, and assume sponsored results at the top of search pages are fake. If a webpage asks for your recovery phrase, close it. If someone asks for it over the phone, hang up. Once you’ve entered your recovery phrase on a fake page, consider the wallet compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as quickly as possible. And don’t skip reporting it: five reports are only the tip of the iceberg, and every additional report makes it a little more likely that the collection addresses will be spotted.
My take is simple: verify the official domain before downloading a wallet, and skip sponsored ads at the top of search results. Taking that extra moment is more useful than trying to trace the on-chain trail afterward.
When you download wallet software, do you click a search result directly, or check the official website’s domain first?
— web3 Chive Xiao Kai
This article shares personal views only and does not constitute investment advice. The facts are based on Coinator’s on-chain analysis from November 3 and Chainabuse reports.
#Trezor #防骗 #助记词 #OnChainTracking
A sponsored ad impersonated Trezor Suite; users who entered their recovery phrase were drained within minutes
In late October, someone searching Google for Trezor Suite saw an ad ranked above the real result. Clicking it led to a wallet software page that looked almost identical to the real thing. Sometimes it was hosted on its own domain; other times, it was tucked away on a Google Sites page. The page asked users to enter their recovery phrase, supposedly to restore their wallet. Within minutes of entering it, users found their balances gone.
So far, this wave has generated only five reports on Chainabuse, from several countries. One reporter said they had already filed a police report in the Czech Republic. The losses involved Bitcoin, Ether, and stablecoins. On-chain analytics tool Coinator tracked only the Bitcoin side—and found a much larger scale than the reports suggested.
The funds didn’t go straight to the scammers’ own wallets. They first landed at two fixed collection addresses. The first received 39 transactions totaling 3.32 Bitcoin between October 27 and 31. The largest single amount mentioned in a report was over 0.2 Bitcoin. The second address had no reports associated with it, yet received 56 transactions totaling 8.17 Bitcoin—more than twice as much as the first. Together, the two addresses received about 95 transactions, totaling 11.49 Bitcoin.
At 15:57 UTC on October 31, the second address was emptied in a single transaction with 56 inputs. Twelve minutes later, the first address was emptied in a transaction with 33 inputs. Both sets of funds went to the same intermediary address. That address received a total of 21.62 Bitcoin; the extra amount came from earlier deposits. Coinator’s assessment is that this group had received similar funds before. Starting at 17:12 UTC that day, the intermediary address began sending funds out in batches: first 2.0 Bitcoin, then 2.86 Bitcoin, and finally 1.54 Bitcoin. All three transactions had exactly the same fee of 564 satoshis, and their versions, lock times, and replaceability flags also matched—clear signs they came from the same wallet.
Of those three outgoing transactions, the 2.0 and 2.86 Bitcoin were still sitting untouched at their original addresses as of November 3. The 1.54 Bitcoin was moved in three steps that evening: first a 0.01 Bitcoin test, then 0.5 Bitcoin, and finally 1.03 Bitcoin. Each step passed through an intermediary address, and all the funds ultimately ended up in the hot wallet of the same custodial service. Since February 2025, this hot wallet has handled about 139,000 transactions, moving roughly 37,000 Bitcoin, and has been linked to 162,000 deposit addresses, almost all used just once. The same hot wallet also received funds from a fake Kraken support scam in August, and was the endpoint in a case in Argentina in late October. Three different scams, one destination for the money.
There’s an easy place to get the trail wrong. The 0.01 Bitcoin test payment went into a deposit address. A few hours later, that address was spent together with eight other deposit addresses and two of the hot wallet’s own inputs. Then 0.29 Bitcoin went to a new address, making it look as if the scammers had taken their money back—and somehow ended up with more. In reality, it was a payment from the custodial service to one of its customers. The deposit addresses and the hot wallet belong to the service provider; once the funds are in the provider’s hands, it no longer matters who originally deposited them. If you track the hot wallet as though it belongs to the scammers, you’ll identify the wrong people. The addresses worth keeping track of are the scammers’ two collection addresses.
For everyday users, the takeaway is very concrete. Only trust wallet software from the provider’s official website, and assume sponsored results at the top of search pages are fake. If a webpage asks for your recovery phrase, close it. If someone asks for it over the phone, hang up. Once you’ve entered your recovery phrase on a fake page, consider the wallet compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as quickly as possible. And don’t skip reporting it: five reports are only the tip of the iceberg, and every additional report makes it a little more likely that the collection addresses will be spotted.
My take is simple: verify the official domain before downloading a wallet, and skip sponsored ads at the top of search results. Taking that extra moment is more useful than trying to trace the on-chain trail afterward.
When you download wallet software, do you click a search result directly, or check the official website’s domain first?
— web3 Chive Xiao Kai
This article shares personal views only and does not constitute investment advice. The facts are based on Coinator’s on-chain analysis from November 3 and Chainabuse reports.
#Trezor #防骗 #助记词 #OnChainTracking
In late October, someone searching Google for Trezor Suite saw an ad ranked above the real result. Clicking it led to a wallet software page that looked almost identical to the real thing. Sometimes it was hosted on its own domain; other times, it was tucked away on a Google Sites page. The page asked users to enter their recovery phrase, supposedly to restore their wallet. Within minutes of entering it, users found their balances gone.
So far, this wave has generated only five reports on Chainabuse, from several countries. One reporter said they had already filed a police report in the Czech Republic. The losses involved Bitcoin, Ether, and stablecoins. On-chain analytics tool Coinator tracked only the Bitcoin side—and found a much larger scale than the reports suggested.
The funds didn’t go straight to the scammers’ own wallets. They first landed at two fixed collection addresses. The first received 39 transactions totaling 3.32 Bitcoin between October 27 and 31. The largest single amount mentioned in a report was over 0.2 Bitcoin. The second address had no reports associated with it, yet received 56 transactions totaling 8.17 Bitcoin—more than twice as much as the first. Together, the two addresses received about 95 transactions, totaling 11.49 Bitcoin.
At 15:57 UTC on October 31, the second address was emptied in a single transaction with 56 inputs. Twelve minutes later, the first address was emptied in a transaction with 33 inputs. Both sets of funds went to the same intermediary address. That address received a total of 21.62 Bitcoin; the extra amount came from earlier deposits. Coinator’s assessment is that this group had received similar funds before. Starting at 17:12 UTC that day, the intermediary address began sending funds out in batches: first 2.0 Bitcoin, then 2.86 Bitcoin, and finally 1.54 Bitcoin. All three transactions had exactly the same fee of 564 satoshis, and their versions, lock times, and replaceability flags also matched—clear signs they came from the same wallet.
Of those three outgoing transactions, the 2.0 and 2.86 Bitcoin were still sitting untouched at their original addresses as of November 3. The 1.54 Bitcoin was moved in three steps that evening: first a 0.01 Bitcoin test, then 0.5 Bitcoin, and finally 1.03 Bitcoin. Each step passed through an intermediary address, and all the funds ultimately ended up in the hot wallet of the same custodial service. Since February 2025, this hot wallet has handled about 139,000 transactions, moving roughly 37,000 Bitcoin, and has been linked to 162,000 deposit addresses, almost all used just once. The same hot wallet also received funds from a fake Kraken support scam in August, and was the endpoint in a case in Argentina in late October. Three different scams, one destination for the money.
There’s an easy place to get the trail wrong. The 0.01 Bitcoin test payment went into a deposit address. A few hours later, that address was spent together with eight other deposit addresses and two of the hot wallet’s own inputs. Then 0.29 Bitcoin went to a new address, making it look as if the scammers had taken their money back—and somehow ended up with more. In reality, it was a payment from the custodial service to one of its customers. The deposit addresses and the hot wallet belong to the service provider; once the funds are in the provider’s hands, it no longer matters who originally deposited them. If you track the hot wallet as though it belongs to the scammers, you’ll identify the wrong people. The addresses worth keeping track of are the scammers’ two collection addresses.
For everyday users, the takeaway is very concrete. Only trust wallet software from the provider’s official website, and assume sponsored results at the top of search pages are fake. If a webpage asks for your recovery phrase, close it. If someone asks for it over the phone, hang up. Once you’ve entered your recovery phrase on a fake page, consider the wallet compromised. Use a clean device to create a new wallet with a new recovery phrase, then move any remaining funds as quickly as possible. And don’t skip reporting it: five reports are only the tip of the iceberg, and every additional report makes it a little more likely that the collection addresses will be spotted.
My take is simple: verify the official domain before downloading a wallet, and skip sponsored ads at the top of search results. Taking that extra moment is more useful than trying to trace the on-chain trail afterward.
When you download wallet software, do you click a search result directly, or check the official website’s domain first?
— web3 Chive Xiao Kai
This article shares personal views only and does not constitute investment advice. The facts are based on Coinator’s on-chain analysis from November 3 and Chainabuse reports.
#Trezor #防骗 #助记词 #OnChainTracking
17
·
--
📰 Trezor warned CryptoBilis buyers: the old seed phrase must not be reused
On October 30, Trezor reported a suspected hardware backdoor in a Safe 5 purchased through CryptoBilis. The company has not yet investigated the device or received any reports of losses, but recommends that everyone who bought any Trezor model from this seller since March 2026 transfer their assets to a new wallet with a new seed phrase.
Simply replacing the device and restoring it with the old phrase will not protect you: the suspected backdoor may have been able to read data from the screen. If the device has not yet been set up, do not use it. Contact official Trezor support to arrange a replacement.
#Trezor #WalletSecurity
📰 Trezor warned CryptoBilis buyers: the old seed phrase must not be reused
On October 30, Trezor reported a suspected hardware backdoor in a Safe 5 purchased through CryptoBilis. The company has not yet investigated the device or received any reports of losses, but recommends that everyone who bought any Trezor model from this seller since March 2026 transfer their assets to a new wallet with a new seed phrase.
Simply replacing the device and restoring it with the old phrase will not protect you: the suspected backdoor may have been able to read data from the screen. If the device has not yet been set up, do not use it. Contact official Trezor support to arrange a replacement.
#Trezor #WalletSecurity
On October 30, Trezor reported a suspected hardware backdoor in a Safe 5 purchased through CryptoBilis. The company has not yet investigated the device or received any reports of losses, but recommends that everyone who bought any Trezor model from this seller since March 2026 transfer their assets to a new wallet with a new seed phrase.
Simply replacing the device and restoring it with the old phrase will not protect you: the suspected backdoor may have been able to read data from the screen. If the device has not yet been set up, do not use it. Contact official Trezor support to arrange a replacement.
#Trezor #WalletSecurity
30
·
--
📰 Trezor reveals Malaysian reseller sold wallet with spyware
Trezor says it will replace any wallets bought from CryptoBilis since March after witnessing spyware within one of its devices. The post Trezor reveals Malaysian reseller sold wallet with spyware appeared first on Protos.
Source : Protos
Time : 2026-10-30 15:27:39
Credit : jacob lyon
#asia #crypto #ledger #trezor
Share your opinion in the comment section below
📰 Trezor reveals Malaysian reseller sold wallet with spyware
Trezor says it will replace any wallets bought from CryptoBilis since March after witnessing spyware within one of its devices. The post Trezor reveals Malaysian reseller sold wallet with spyware appeared first on Protos.
Source : Protos
Time : 2026-10-30 15:27:39
Credit : jacob lyon
#asia #crypto #ledger #trezor
Share your opinion in the comment section below
Trezor says it will replace any wallets bought from CryptoBilis since March after witnessing spyware within one of its devices. The post Trezor reveals Malaysian reseller sold wallet with spyware appeared first on Protos.
Source : Protos
Time : 2026-10-30 15:27:39
Credit : jacob lyon
#asia #crypto #ledger #trezor
Share your opinion in the comment section below
13

Trezor’s screw-up wasn’t with the hardware—it was with its messaging.
From October 19 to 27, the company’s official X account replied one by one to people who had bought a Safe 7 from CryptoBilis. The wording was identical every time: “no evidence of tampered Trezor devices.” When someone asked whether they should open the device for inspection, the reply was: don’t open it yourself; contact customer support.
Then, on October 31, the company issued its own warning: anyone who had bought any Trezor from CryptoBilis since March should immediately move their crypto to a new wallet with a new recovery phrase. The reason: a Safe 5 bought in August was found to have an extra circuit board inside, equipped with a cellular module that could read the screen’s contents and transmit them once the device was plugged in.
In less than two weeks, the message went from “no evidence” to “move your funds immediately.”
I’m not saying Trezor is compromised. So far, the company says there have been no losses, and it is offering replacements. But in a security incident, “no evidence” basically means “we haven’t found anything yet”—not that the device is safe. With the same reseller channel, third parties estimate Ledger’s losses at somewhere between $70 million and $100 million. Trezor should have told people to move their funds as a precaution from the outset, instead of trying to reassure them.
Put simply, the security boundary of a hardware wallet isn’t the chip—it’s everyone who handled the device between the factory and your hands. If you bought one from a reseller to save money, move your funds to a wallet with a new recovery phrase now. Don’t wait for the company to change its story for a third time.
#冷钱包 #Trezor
Trezor’s screw-up wasn’t with the hardware—it was with its messaging.
From October 19 to 27, the company’s official X account replied one by one to people who had bought a Safe 7 from CryptoBilis. The wording was identical every time: “no evidence of tampered Trezor devices.” When someone asked whether they should open the device for inspection, the reply was: don’t open it yourself; contact customer support.
Then, on October 31, the company issued its own warning: anyone who had bought any Trezor from CryptoBilis since March should immediately move their crypto to a new wallet with a new recovery phrase. The reason: a Safe 5 bought in August was found to have an extra circuit board inside, equipped with a cellular module that could read the screen’s contents and transmit them once the device was plugged in.
In less than two weeks, the message went from “no evidence” to “move your funds immediately.”
I’m not saying Trezor is compromised. So far, the company says there have been no losses, and it is offering replacements. But in a security incident, “no evidence” basically means “we haven’t found anything yet”—not that the device is safe. With the same reseller channel, third parties estimate Ledger’s losses at somewhere between $70 million and $100 million. Trezor should have told people to move their funds as a precaution from the outset, instead of trying to reassure them.
Put simply, the security boundary of a hardware wallet isn’t the chip—it’s everyone who handled the device between the factory and your hands. If you bought one from a reseller to save money, move your funds to a wallet with a new recovery phrase now. Don’t wait for the company to change its story for a third time.
#冷钱包 #Trezor
From October 19 to 27, the company’s official X account replied one by one to people who had bought a Safe 7 from CryptoBilis. The wording was identical every time: “no evidence of tampered Trezor devices.” When someone asked whether they should open the device for inspection, the reply was: don’t open it yourself; contact customer support.
Then, on October 31, the company issued its own warning: anyone who had bought any Trezor from CryptoBilis since March should immediately move their crypto to a new wallet with a new recovery phrase. The reason: a Safe 5 bought in August was found to have an extra circuit board inside, equipped with a cellular module that could read the screen’s contents and transmit them once the device was plugged in.
In less than two weeks, the message went from “no evidence” to “move your funds immediately.”
I’m not saying Trezor is compromised. So far, the company says there have been no losses, and it is offering replacements. But in a security incident, “no evidence” basically means “we haven’t found anything yet”—not that the device is safe. With the same reseller channel, third parties estimate Ledger’s losses at somewhere between $70 million and $100 million. Trezor should have told people to move their funds as a precaution from the outset, instead of trying to reassure them.
Put simply, the security boundary of a hardware wallet isn’t the chip—it’s everyone who handled the device between the factory and your hands. If you bought one from a reseller to save money, move your funds to a wallet with a new recovery phrase now. Don’t wait for the company to change its story for a third time.
#冷钱包 #Trezor
12
·
--
Trezor just issued a pretty pointed warning.
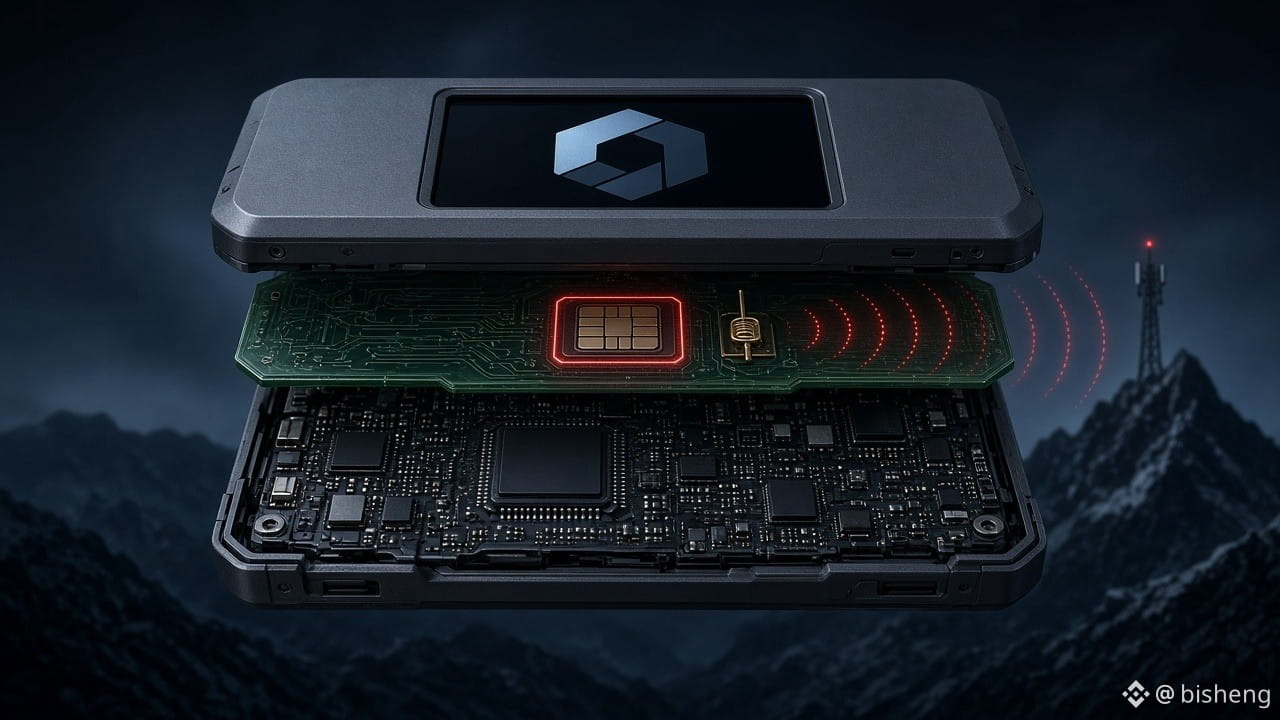
Some Safe 5 devices sold by CryptoBilis, a former authorized reseller in Southeast Asia, were taken apart, and someone found a board wedged between the mainboard and the screen—with a cellular module and an antenna. The report says it can read the recovery phrase displayed on the screen and transmit it over a mobile network as soon as the device is plugged in.
The lab hasn’t finished testing yet. But after reviewing the photos and conducting video interviews, the company decided the claims were credible enough to sound the alarm now. If you’ve bought any Trezor from this reseller since March, you’re advised to move your coins immediately to a new wallet with a “new recovery phrase.” Moving your old seed to another device won’t help. If the seed has already been exposed, migrating it won’t help either.
What stings here isn’t the vague claim that “hardware wallets aren’t safe.” It’s that you thought buying from an “official authorized reseller” meant you were safe. Even stores on the approved list can slip in a compromised device. The same reseller had a similar issue with Ledger, and Trezor removed CryptoBilis from its reseller network in early October. The supply chain is dirtier than whether or not you remember your seed.
Just this week, the Binance hot wallet gave people a lesson, and a lot of them rushed to cold wallets. “Cold” only means the private keys don’t leave the device—and that’s assuming the path from the factory to your hands is clean. Add another reseller, or another e-commerce platform (Tokopedia in this case), and there’s one more weak link in the chain of trust.
The company says it hasn’t received any reports of theft so far. That doesn’t mean there’s no implant; it just means nothing has blown up yet. Waiting for the lab to confirm it before warning people would mean waiting for someone to get burned. They chose to warn people first, and that was the right call. But “warning first” also makes one thing clear: trust in a hardware wallet has never been just about the chip itself—it’s about whether the entire supply chain is willing to tell you the truth before it’s too late.
When buying a hardware wallet, only buy directly from the official website. For now, treat the words “official authorized reseller” as decoration.
#Trezor #HardwareWallet
Trezor just issued a pretty pointed warning.
Some Safe 5 devices sold by CryptoBilis, a former authorized reseller in Southeast Asia, were taken apart, and someone found a board wedged between the mainboard and the screen—with a cellular module and an antenna. The report says it can read the recovery phrase displayed on the screen and transmit it over a mobile network as soon as the device is plugged in.
The lab hasn’t finished testing yet. But after reviewing the photos and conducting video interviews, the company decided the claims were credible enough to sound the alarm now. If you’ve bought any Trezor from this reseller since March, you’re advised to move your coins immediately to a new wallet with a “new recovery phrase.” Moving your old seed to another device won’t help. If the seed has already been exposed, migrating it won’t help either.
What stings here isn’t the vague claim that “hardware wallets aren’t safe.” It’s that you thought buying from an “official authorized reseller” meant you were safe. Even stores on the approved list can slip in a compromised device. The same reseller had a similar issue with Ledger, and Trezor removed CryptoBilis from its reseller network in early October. The supply chain is dirtier than whether or not you remember your seed.
Just this week, the Binance hot wallet gave people a lesson, and a lot of them rushed to cold wallets. “Cold” only means the private keys don’t leave the device—and that’s assuming the path from the factory to your hands is clean. Add another reseller, or another e-commerce platform (Tokopedia in this case), and there’s one more weak link in the chain of trust.
The company says it hasn’t received any reports of theft so far. That doesn’t mean there’s no implant; it just means nothing has blown up yet. Waiting for the lab to confirm it before warning people would mean waiting for someone to get burned. They chose to warn people first, and that was the right call. But “warning first” also makes one thing clear: trust in a hardware wallet has never been just about the chip itself—it’s about whether the entire supply chain is willing to tell you the truth before it’s too late.
When buying a hardware wallet, only buy directly from the official website. For now, treat the words “official authorized reseller” as decoration.
#Trezor #HardwareWallet
Some Safe 5 devices sold by CryptoBilis, a former authorized reseller in Southeast Asia, were taken apart, and someone found a board wedged between the mainboard and the screen—with a cellular module and an antenna. The report says it can read the recovery phrase displayed on the screen and transmit it over a mobile network as soon as the device is plugged in.
The lab hasn’t finished testing yet. But after reviewing the photos and conducting video interviews, the company decided the claims were credible enough to sound the alarm now. If you’ve bought any Trezor from this reseller since March, you’re advised to move your coins immediately to a new wallet with a “new recovery phrase.” Moving your old seed to another device won’t help. If the seed has already been exposed, migrating it won’t help either.
What stings here isn’t the vague claim that “hardware wallets aren’t safe.” It’s that you thought buying from an “official authorized reseller” meant you were safe. Even stores on the approved list can slip in a compromised device. The same reseller had a similar issue with Ledger, and Trezor removed CryptoBilis from its reseller network in early October. The supply chain is dirtier than whether or not you remember your seed.
Just this week, the Binance hot wallet gave people a lesson, and a lot of them rushed to cold wallets. “Cold” only means the private keys don’t leave the device—and that’s assuming the path from the factory to your hands is clean. Add another reseller, or another e-commerce platform (Tokopedia in this case), and there’s one more weak link in the chain of trust.
The company says it hasn’t received any reports of theft so far. That doesn’t mean there’s no implant; it just means nothing has blown up yet. Waiting for the lab to confirm it before warning people would mean waiting for someone to get burned. They chose to warn people first, and that was the right call. But “warning first” also makes one thing clear: trust in a hardware wallet has never been just about the chip itself—it’s about whether the entire supply chain is willing to tell you the truth before it’s too late.
When buying a hardware wallet, only buy directly from the official website. For now, treat the words “official authorized reseller” as decoration.
#Trezor #HardwareWallet
103


#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
🚨 🔐 TREZOR WARNS: CRYPTOBILIS-SOLD WALLETS MAY CONTAIN HIDDEN MALICIOUS HARDWARE! ⚠️
The greatest security threat may not come from the internet.
Sometimes, it can be hiding inside the device you trust most.
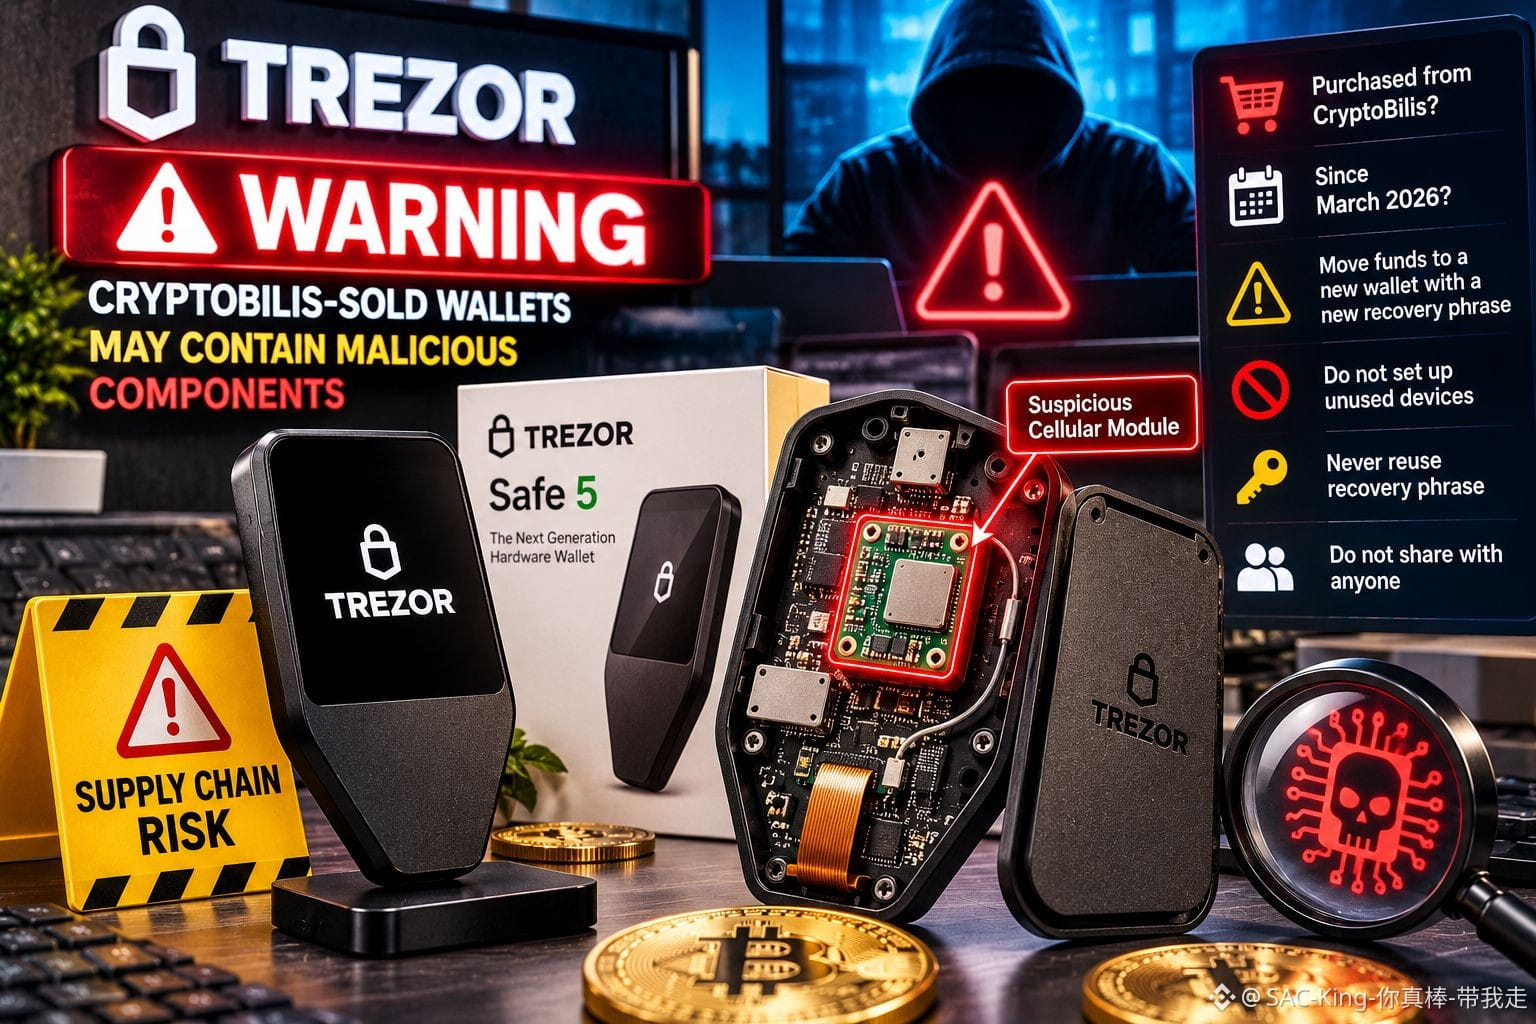
Trezor has issued an urgent warning after an Indonesian customer reported a suspected hardware implant inside a Trezor Safe 5 purchased from reseller CryptoBilis in August 2026.
According to the report, an additional circuit board containing a cellular module and antenna was allegedly installed between the device's screen and mainboard. It may capture sensitive information, including wallet recovery phrases, and transmit it over a mobile network.
Trezor has not physically examined the reported device yet, but considers the evidence credible enough to issue a precautionary warning.
Anyone who purchased a Trezor from CryptoBilis since March 2026 is advised to move funds into a newly created wallet with a completely new recovery phrase.
Unused devices should not be set up. Never reuse an exposed recovery phrase, and never share it with anyone claiming to be support.
My Take: This incident exposes a serious weakness in crypto security: protecting software is not enough if the physical supply chain can be compromised.
Your private keys deserve protection at every stage, including before your wallet reaches your hands.
Can hardware wallets remain truly secure without stronger supply-chain verification?
Disclaimer: Educational content only. Not financial advice. DYOR.
#CryptoSecurity #Trezor #GrowWithSAC $SOLV $RUNE $LLYB
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
🚨 🔐 TREZOR WARNS: CRYPTOBILIS-SOLD WALLETS MAY CONTAIN HIDDEN MALICIOUS HARDWARE! ⚠️
The greatest security threat may not come from the internet.
Sometimes, it can be hiding inside the device you trust most.
Trezor has issued an urgent warning after an Indonesian customer reported a suspected hardware implant inside a Trezor Safe 5 purchased from reseller CryptoBilis in August 2026.
According to the report, an additional circuit board containing a cellular module and antenna was allegedly installed between the device's screen and mainboard. It may capture sensitive information, including wallet recovery phrases, and transmit it over a mobile network.
Trezor has not physically examined the reported device yet, but considers the evidence credible enough to issue a precautionary warning.
Anyone who purchased a Trezor from CryptoBilis since March 2026 is advised to move funds into a newly created wallet with a completely new recovery phrase.
Unused devices should not be set up. Never reuse an exposed recovery phrase, and never share it with anyone claiming to be support.
My Take: This incident exposes a serious weakness in crypto security: protecting software is not enough if the physical supply chain can be compromised.
Your private keys deserve protection at every stage, including before your wallet reaches your hands.
Can hardware wallets remain truly secure without stronger supply-chain verification?
Disclaimer: Educational content only. Not financial advice. DYOR.
#CryptoSecurity #Trezor #GrowWithSAC $SOLV $RUNE $LLYB
🚨 🔐 TREZOR WARNS: CRYPTOBILIS-SOLD WALLETS MAY CONTAIN HIDDEN MALICIOUS HARDWARE! ⚠️
The greatest security threat may not come from the internet.
Sometimes, it can be hiding inside the device you trust most.
Trezor has issued an urgent warning after an Indonesian customer reported a suspected hardware implant inside a Trezor Safe 5 purchased from reseller CryptoBilis in August 2026.
According to the report, an additional circuit board containing a cellular module and antenna was allegedly installed between the device's screen and mainboard. It may capture sensitive information, including wallet recovery phrases, and transmit it over a mobile network.
Trezor has not physically examined the reported device yet, but considers the evidence credible enough to issue a precautionary warning.
Anyone who purchased a Trezor from CryptoBilis since March 2026 is advised to move funds into a newly created wallet with a completely new recovery phrase.
Unused devices should not be set up. Never reuse an exposed recovery phrase, and never share it with anyone claiming to be support.
My Take: This incident exposes a serious weakness in crypto security: protecting software is not enough if the physical supply chain can be compromised.
Your private keys deserve protection at every stage, including before your wallet reaches your hands.
Can hardware wallets remain truly secure without stronger supply-chain verification?
Disclaimer: Educational content only. Not financial advice. DYOR.
#CryptoSecurity #Trezor #GrowWithSAC $SOLV $RUNE $LLYB
1
596

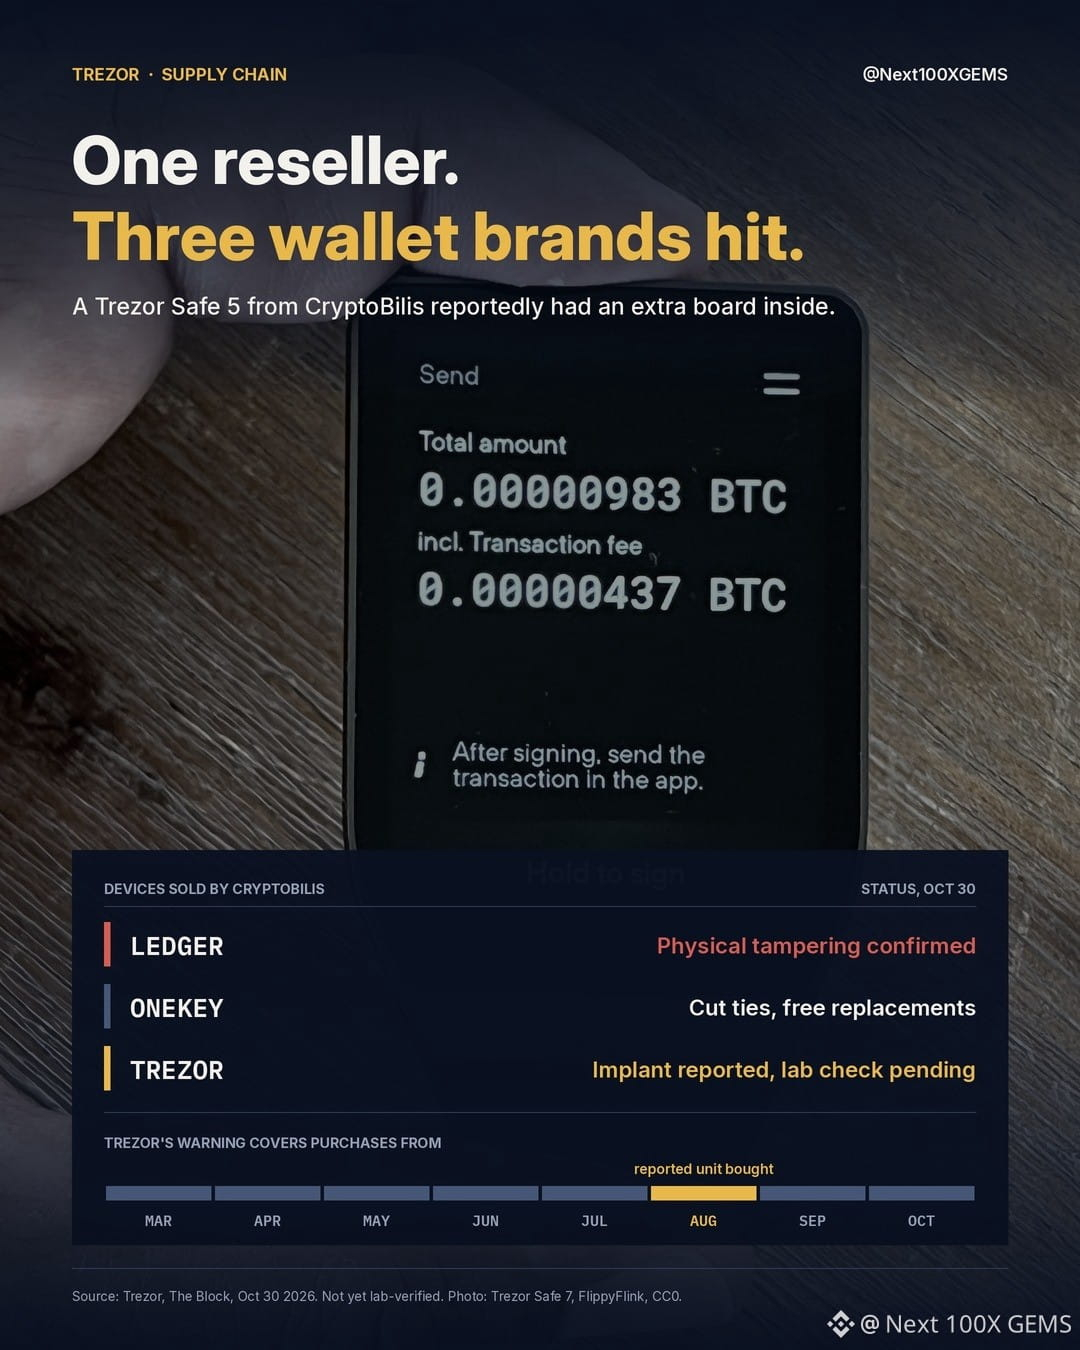
A Trezor Safe 5 sold by CryptoBilis reportedly had a second circuit board fitted between the main board and the screen. Cellular module, antenna. According to the buyer's report, it reads whatever the screen shows, recovery phrase included, and sends it out over a mobile network whenever the device is plugged in.
Trezor hasn't had the device in its lab yet. It went public anyway, after photos and a video call with the buyer, and says no funds have been reported lost.
This is the same reseller whose Ledger devices turned out to be tampered with earlier this month. Ledger confirmed physically altered devices, OneKey cut ties, and Trezor dropped CryptoBilis on Oct 9. On-chain trackers put Ledger-linked losses above $86M, a figure Ledger hasn't confirmed.
The window is wide. Trezor's warning covers every model bought from CryptoBilis since March, including its Tokopedia store. The reported unit was bought in August.
If that's you: make a new wallet with a new seed and move funds. Typing the old seed into a different device doesn't fix it. Not set up yet? Don't set it up. Trezor is offering a free replacement or a voucher, and says weighing the device is not a reliable test.
Expect fake "recall" emails and calls next. Support never asks for your seed.
$BTC $ETH
#Trezor #CryptoSecurity
NFA. DYOR.
A Trezor Safe 5 sold by CryptoBilis reportedly had a second circuit board fitted between the main board and the screen. Cellular module, antenna. According to the buyer's report, it reads whatever the screen shows, recovery phrase included, and sends it out over a mobile network whenever the device is plugged in.
Trezor hasn't had the device in its lab yet. It went public anyway, after photos and a video call with the buyer, and says no funds have been reported lost.
This is the same reseller whose Ledger devices turned out to be tampered with earlier this month. Ledger confirmed physically altered devices, OneKey cut ties, and Trezor dropped CryptoBilis on Oct 9. On-chain trackers put Ledger-linked losses above $86M, a figure Ledger hasn't confirmed.
The window is wide. Trezor's warning covers every model bought from CryptoBilis since March, including its Tokopedia store. The reported unit was bought in August.
If that's you: make a new wallet with a new seed and move funds. Typing the old seed into a different device doesn't fix it. Not set up yet? Don't set it up. Trezor is offering a free replacement or a voucher, and says weighing the device is not a reliable test.
Expect fake "recall" emails and calls next. Support never asks for your seed.
$BTC $ETH
#Trezor #CryptoSecurity
NFA. DYOR.
Trezor hasn't had the device in its lab yet. It went public anyway, after photos and a video call with the buyer, and says no funds have been reported lost.
This is the same reseller whose Ledger devices turned out to be tampered with earlier this month. Ledger confirmed physically altered devices, OneKey cut ties, and Trezor dropped CryptoBilis on Oct 9. On-chain trackers put Ledger-linked losses above $86M, a figure Ledger hasn't confirmed.
The window is wide. Trezor's warning covers every model bought from CryptoBilis since March, including its Tokopedia store. The reported unit was bought in August.
If that's you: make a new wallet with a new seed and move funds. Typing the old seed into a different device doesn't fix it. Not set up yet? Don't set it up. Trezor is offering a free replacement or a voucher, and says weighing the device is not a reliable test.
Expect fake "recall" emails and calls next. Support never asks for your seed.
$BTC $ETH
#Trezor #CryptoSecurity
NFA. DYOR.
1
557

·
--
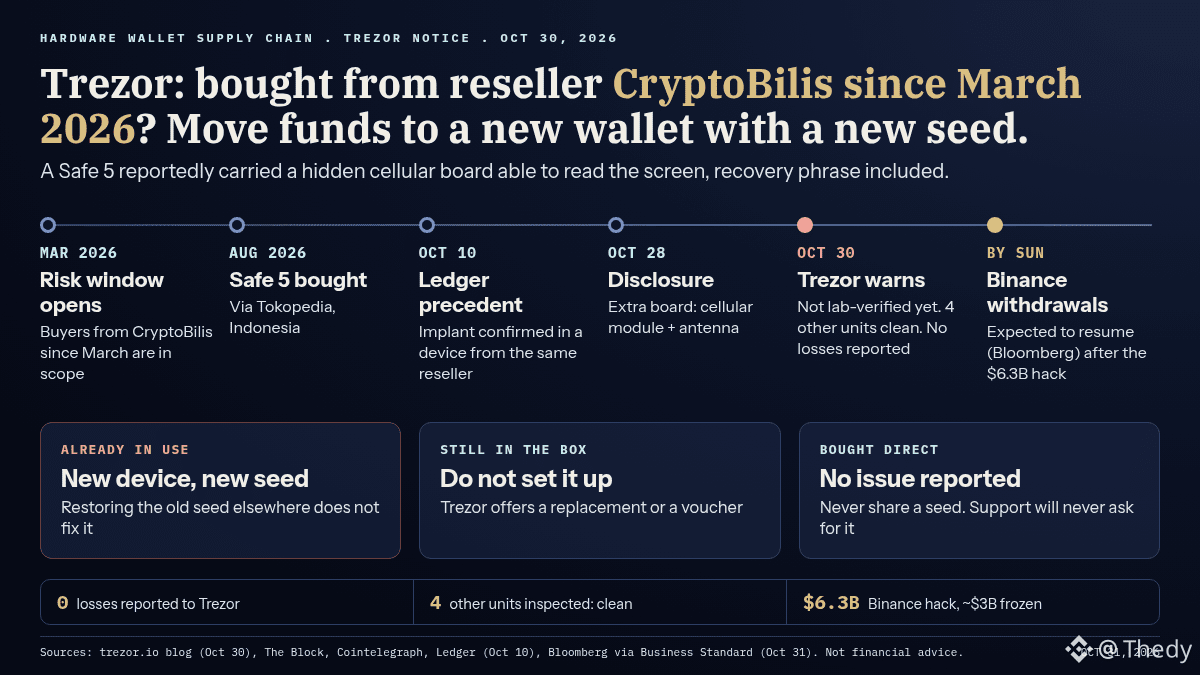
Trezor is asking anyone who bought one of its wallets from the CryptoBilis reseller since March 2026 to move their funds to a new wallet with a new seed. The alert, published on Trezor’s official blog on 30/10, comes as many people are planning to move their coins off Binance.
According to Trezor, an Indonesian customer reported a Safe 5 on 28/10 that they had bought in August through Tokopedia, with a card added between the motherboard and the screen (cellular module + antenna). According to the report, which has not yet been verified in a lab, the circuit could read the screen, including the seed, and send it over a mobile network once plugged in. Trezor considers the report credible, has received no reports of losses, and found no issues with 4 other devices it examined.
This isn’t the first case: on 10/10, Ledger confirmed an implant in a device sold by the same reseller.
Who needs to act:
- Trezor from CryptoBilis that has already been used: get a new wallet and a new seed. Restoring the old seed on another device does not solve the problem.
- Still in its box: don’t initialize it. Trezor is offering a replacement or a gift card.
- Bought directly from the manufacturer: there is no indication of a problem at this stage.
Timing matters. According to Bloomberg, Binance is targeting a resumption of withdrawals by Sunday, following the $6.3 billion hack. My take: the wave of withdrawals to self-custody will attract scams, and Trezor is already warning that fake emails, letters, and calls will exploit the alert.
If the lab confirms the implant, the reseller supply chain will become an issue for the whole industry. Otherwise, the alert will remain a precaution, but buying directly is still the rule.
Before withdrawing your $BTC or your $BNB from Binance to a hardware wallet, do you check where it came from, or test it first with a small amount?
#Trezor #Binance
Trezor is asking anyone who bought one of its wallets from the CryptoBilis reseller since March 2026 to move their funds to a new wallet with a new seed. The alert, published on Trezor’s official blog on 30/10, comes as many people are planning to move their coins off Binance.
According to Trezor, an Indonesian customer reported a Safe 5 on 28/10 that they had bought in August through Tokopedia, with a card added between the motherboard and the screen (cellular module + antenna). According to the report, which has not yet been verified in a lab, the circuit could read the screen, including the seed, and send it over a mobile network once plugged in. Trezor considers the report credible, has received no reports of losses, and found no issues with 4 other devices it examined.
This isn’t the first case: on 10/10, Ledger confirmed an implant in a device sold by the same reseller.
Who needs to act:
- Trezor from CryptoBilis that has already been used: get a new wallet and a new seed. Restoring the old seed on another device does not solve the problem.
- Still in its box: don’t initialize it. Trezor is offering a replacement or a gift card.
- Bought directly from the manufacturer: there is no indication of a problem at this stage.
Timing matters. According to Bloomberg, Binance is targeting a resumption of withdrawals by Sunday, following the $6.3 billion hack. My take: the wave of withdrawals to self-custody will attract scams, and Trezor is already warning that fake emails, letters, and calls will exploit the alert.
If the lab confirms the implant, the reseller supply chain will become an issue for the whole industry. Otherwise, the alert will remain a precaution, but buying directly is still the rule.
Before withdrawing your $BTC or your $BNB from Binance to a hardware wallet, do you check where it came from, or test it first with a small amount?
#Trezor #Binance
According to Trezor, an Indonesian customer reported a Safe 5 on 28/10 that they had bought in August through Tokopedia, with a card added between the motherboard and the screen (cellular module + antenna). According to the report, which has not yet been verified in a lab, the circuit could read the screen, including the seed, and send it over a mobile network once plugged in. Trezor considers the report credible, has received no reports of losses, and found no issues with 4 other devices it examined.
This isn’t the first case: on 10/10, Ledger confirmed an implant in a device sold by the same reseller.
Who needs to act:
- Trezor from CryptoBilis that has already been used: get a new wallet and a new seed. Restoring the old seed on another device does not solve the problem.
- Still in its box: don’t initialize it. Trezor is offering a replacement or a gift card.
- Bought directly from the manufacturer: there is no indication of a problem at this stage.
Timing matters. According to Bloomberg, Binance is targeting a resumption of withdrawals by Sunday, following the $6.3 billion hack. My take: the wave of withdrawals to self-custody will attract scams, and Trezor is already warning that fake emails, letters, and calls will exploit the alert.
If the lab confirms the implant, the reseller supply chain will become an issue for the whole industry. Otherwise, the alert will remain a precaution, but buying directly is still the rule.
Before withdrawing your $BTC or your $BNB from Binance to a hardware wallet, do you check where it came from, or test it first with a small amount?
#Trezor #Binance
1
311

·
--
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
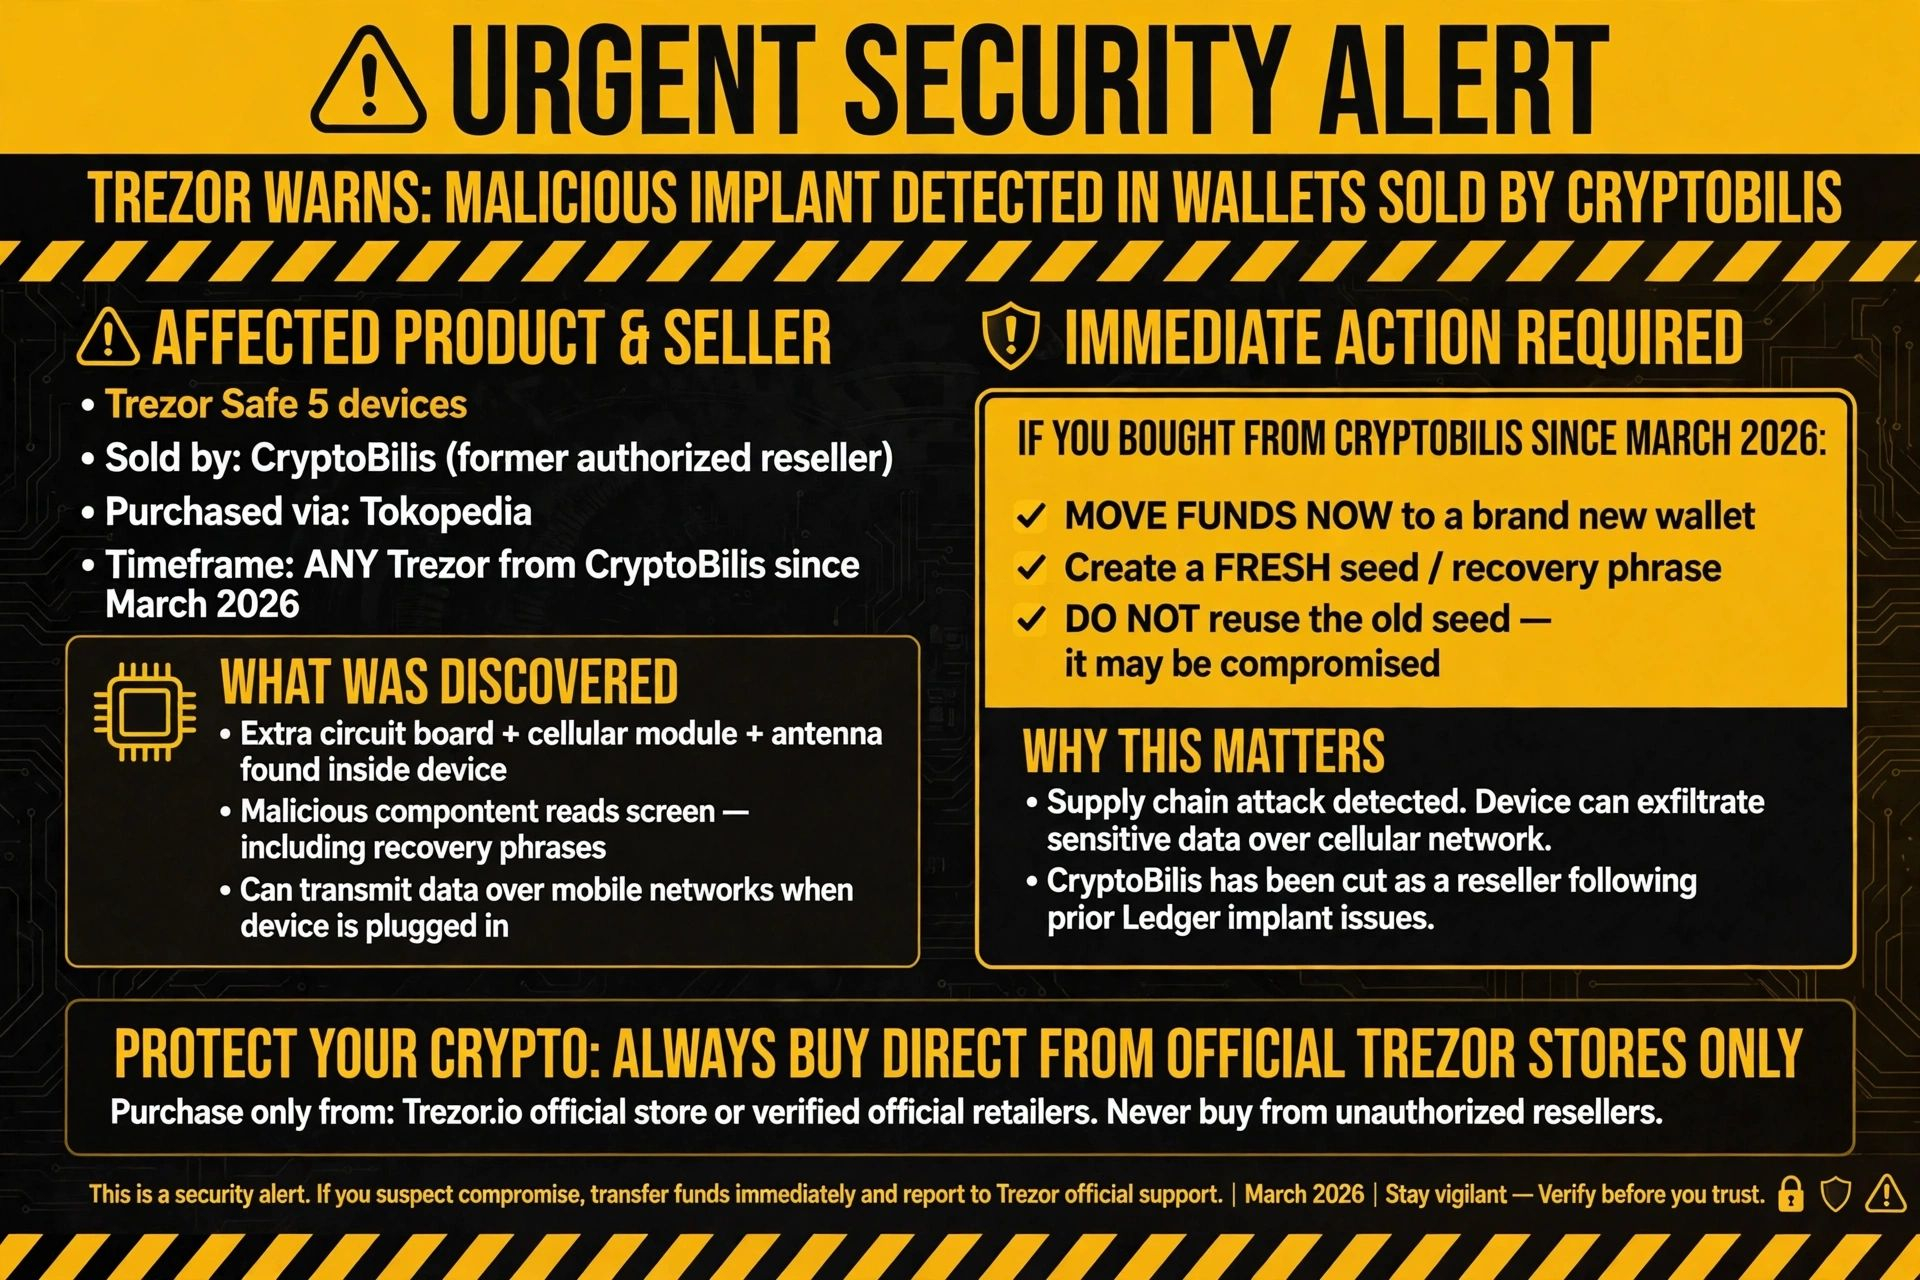
🚨 URGENT: Trezor warns of possible malicious implant in wallets sold by CryptoBilis!
Trezor just dropped a serious security alert. A customer reported a hardware implant inside a Trezor Safe 5 bought from former authorized reseller CryptoBilis (via Tokopedia in August).
The extra circuit board + cellular module + antenna allegedly reads the screen (including recovery phrases) and can transmit data over mobile networks when plugged in.
No funds lost reported yet, but Trezor is treating it as credible.
*If you bought ANY Trezor from CryptoBilis since March 2026 → Move your funds to a brand new wallet with a FRESH seed immediately. Do NOT reuse the old seed.*
CryptoBilis was already cut as a reseller after the earlier Ledger implant issues.
Supply chain attacks are the new nightmare. Even trusted hardware wallets can get compromised before they reach you. Always buy direct from official stores when possible, verify packaging, and never skip the “new seed” rule if something feels off. Self-custody only works if the device is clean. Stay paranoid, stay safe.
Who else is double-checking their hardware wallets right now? 👇
#Trezor #CryptoSecurity #HardwareWallet #StaySafe
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
🚨 URGENT: Trezor warns of possible malicious implant in wallets sold by CryptoBilis!
Trezor just dropped a serious security alert. A customer reported a hardware implant inside a Trezor Safe 5 bought from former authorized reseller CryptoBilis (via Tokopedia in August).
The extra circuit board + cellular module + antenna allegedly reads the screen (including recovery phrases) and can transmit data over mobile networks when plugged in.
No funds lost reported yet, but Trezor is treating it as credible.
*If you bought ANY Trezor from CryptoBilis since March 2026 → Move your funds to a brand new wallet with a FRESH seed immediately. Do NOT reuse the old seed.*
CryptoBilis was already cut as a reseller after the earlier Ledger implant issues.
Supply chain attacks are the new nightmare. Even trusted hardware wallets can get compromised before they reach you. Always buy direct from official stores when possible, verify packaging, and never skip the “new seed” rule if something feels off. Self-custody only works if the device is clean. Stay paranoid, stay safe.
Who else is double-checking their hardware wallets right now? 👇
#Trezor #CryptoSecurity #HardwareWallet #StaySafe
🚨 URGENT: Trezor warns of possible malicious implant in wallets sold by CryptoBilis!
Trezor just dropped a serious security alert. A customer reported a hardware implant inside a Trezor Safe 5 bought from former authorized reseller CryptoBilis (via Tokopedia in August).
The extra circuit board + cellular module + antenna allegedly reads the screen (including recovery phrases) and can transmit data over mobile networks when plugged in.
No funds lost reported yet, but Trezor is treating it as credible.
*If you bought ANY Trezor from CryptoBilis since March 2026 → Move your funds to a brand new wallet with a FRESH seed immediately. Do NOT reuse the old seed.*
CryptoBilis was already cut as a reseller after the earlier Ledger implant issues.
Supply chain attacks are the new nightmare. Even trusted hardware wallets can get compromised before they reach you. Always buy direct from official stores when possible, verify packaging, and never skip the “new seed” rule if something feels off. Self-custody only works if the device is clean. Stay paranoid, stay safe.
Who else is double-checking their hardware wallets right now? 👇
#Trezor #CryptoSecurity #HardwareWallet #StaySafe
3
108

·
--
Hey folks!! There’s trouble in the hardware wallet supply chain too!!!
Trezor just issued an official warning: Some Safe 5 devices sold by Southeast Asian reseller CryptoBilis were reported to contain suspicious hardware implants—a small board with a cellular module that could steal the recovery phrase displayed on the screen and transmit it as soon as the device is plugged in~ (Trezor’s website/CoinTelegraph/The Block, October 30–31)
They haven’t inspected the device in a lab yet, but they’ve issued a warning based on credible reports: If you bought one from CryptoBilis after March, move your coins to a “new wallet + new recovery phrase” ASAP!!! So far, they say they haven’t received any reports of stolen funds, and four other devices they inspected were fine. This was also the reseller involved in the earlier Ledger incident, and Trezor has already removed it from its official channel this month, haha.
Seriously, a major exchange just blew up, and now there’s another issue with cold wallet retailers—don’t just keep an eye on exchanges; when buying a hardware wallet, stick to the official store. Don’t get drained a second time this weekend by fake support agents or phishing emails!!!
Did you buy your hardware wallet directly from the official store, or through a third-party seller?
#Trezor #安全 #Crypto
Hey folks!! There’s trouble in the hardware wallet supply chain too!!!
Trezor just issued an official warning: Some Safe 5 devices sold by Southeast Asian reseller CryptoBilis were reported to contain suspicious hardware implants—a small board with a cellular module that could steal the recovery phrase displayed on the screen and transmit it as soon as the device is plugged in~ (Trezor’s website/CoinTelegraph/The Block, October 30–31)
They haven’t inspected the device in a lab yet, but they’ve issued a warning based on credible reports: If you bought one from CryptoBilis after March, move your coins to a “new wallet + new recovery phrase” ASAP!!! So far, they say they haven’t received any reports of stolen funds, and four other devices they inspected were fine. This was also the reseller involved in the earlier Ledger incident, and Trezor has already removed it from its official channel this month, haha.
Seriously, a major exchange just blew up, and now there’s another issue with cold wallet retailers—don’t just keep an eye on exchanges; when buying a hardware wallet, stick to the official store. Don’t get drained a second time this weekend by fake support agents or phishing emails!!!
Did you buy your hardware wallet directly from the official store, or through a third-party seller?
#Trezor #安全 #Crypto
Trezor just issued an official warning: Some Safe 5 devices sold by Southeast Asian reseller CryptoBilis were reported to contain suspicious hardware implants—a small board with a cellular module that could steal the recovery phrase displayed on the screen and transmit it as soon as the device is plugged in~ (Trezor’s website/CoinTelegraph/The Block, October 30–31)
They haven’t inspected the device in a lab yet, but they’ve issued a warning based on credible reports: If you bought one from CryptoBilis after March, move your coins to a “new wallet + new recovery phrase” ASAP!!! So far, they say they haven’t received any reports of stolen funds, and four other devices they inspected were fine. This was also the reseller involved in the earlier Ledger incident, and Trezor has already removed it from its official channel this month, haha.
Seriously, a major exchange just blew up, and now there’s another issue with cold wallet retailers—don’t just keep an eye on exchanges; when buying a hardware wallet, stick to the official store. Don’t get drained a second time this weekend by fake support agents or phishing emails!!!
Did you buy your hardware wallet directly from the official store, or through a third-party seller?
#Trezor #安全 #Crypto
2
830

TREZOR WARNS CRYPTO USERS — HARDWARE WALLETS MAY CONTAIN MALICIOUS COMPONENTS!A major crypto security warning is making headlines! Trezor has alerted customers after receiving a credible report of a suspected hardware implant inside a Trezor Safe 5 purchased through reseller CryptoBilis.
This could be another serious supply-chain security concern for the crypto industry. Here's what you need to know. 👇
🔴 1. HOW DOES THE SUSPECTED IMPLANT WORK?
According to the customer report, the device allegedly contained:
An additional circuit board.A cellular communication module.An antenna capable of transmitting information.
The suspected component could potentially capture sensitive information displayed on the wallet screen, including the recovery phrase, and transmit it over a mobile network.
⚠️ 2. TREZOR HAS ISSUED AN URGENT WARNING
Trezor has not physically examined the reported device yet, but considers the report credible based on customer information and a video interview.
The company says no customer funds have been reported stolen in connection with this particular Trezor report.
🛡️ 3. WHO SHOULD TAKE ACTION?
Anyone who purchased a Trezor hardware wallet through CryptoBilis since March 2026 should:
Move crypto assets to a newly created wallet.Generate a completely new recovery phrase.Avoid setting up unused devices from the reseller.Contact official Trezor Support about replacement options.
Important: Simply restoring your old recovery phrase on another device is NOT enough if that phrase may already be compromised.
🔍 4. WHY IS THIS A BIGGER INDUSTRY WARNING?
CryptoBilis was previously linked to confirmed physical tampering involving Ledger hardware wallets. Trezor has also removed the reseller from its authorized network.
This raises an important question about hardware-wallet supply chains: Can users trust a device if its physical integrity has been compromised before reaching them?
💡 MY TAKEAWAY
Hardware wallets are designed to protect private keys, but physical security and trusted distribution channels matter just as much as software security.
Don't panic, but don't ignore this warning. Never share your recovery phrase with anyone claiming to be customer support, and purchase hardware wallets directly from manufacturers or verified authorized sellers.
🔥 Do you trust hardware wallets after these supply-chain incidents, or is it time for manufacturers to introduce stronger verification systems?
Share your thoughts below! 👇
#trezorsayscryptobilissoldwalletmaycontainmaliciouscom #Trezor #CryptoSecurity #Bitcoin #HardwareWallet #CryptoNews #BinanceSquare
{spot}(AAPLBUSDT)
TREZOR WARNS CRYPTO USERS — HARDWARE WALLETS MAY CONTAIN MALICIOUS COMPONENTS!
A major crypto security warning is making headlines! Trezor has alerted customers after receiving a credible report of a suspected hardware implant inside a Trezor Safe 5 purchased through reseller CryptoBilis.
This could be another serious supply-chain security concern for the crypto industry. Here's what you need to know. 👇
🔴 1. HOW DOES THE SUSPECTED IMPLANT WORK?
According to the customer report, the device allegedly contained:
An additional circuit board.A cellular communication module.An antenna capable of transmitting information.
The suspected component could potentially capture sensitive information displayed on the wallet screen, including the recovery phrase, and transmit it over a mobile network.
⚠️ 2. TREZOR HAS ISSUED AN URGENT WARNING
Trezor has not physically examined the reported device yet, but considers the report credible based on customer information and a video interview.
The company says no customer funds have been reported stolen in connection with this particular Trezor report.
🛡️ 3. WHO SHOULD TAKE ACTION?
Anyone who purchased a Trezor hardware wallet through CryptoBilis since March 2026 should:
Move crypto assets to a newly created wallet.Generate a completely new recovery phrase.Avoid setting up unused devices from the reseller.Contact official Trezor Support about replacement options.
Important: Simply restoring your old recovery phrase on another device is NOT enough if that phrase may already be compromised.
🔍 4. WHY IS THIS A BIGGER INDUSTRY WARNING?
CryptoBilis was previously linked to confirmed physical tampering involving Ledger hardware wallets. Trezor has also removed the reseller from its authorized network.
This raises an important question about hardware-wallet supply chains: Can users trust a device if its physical integrity has been compromised before reaching them?
💡 MY TAKEAWAY
Hardware wallets are designed to protect private keys, but physical security and trusted distribution channels matter just as much as software security.
Don't panic, but don't ignore this warning. Never share your recovery phrase with anyone claiming to be customer support, and purchase hardware wallets directly from manufacturers or verified authorized sellers.
🔥 Do you trust hardware wallets after these supply-chain incidents, or is it time for manufacturers to introduce stronger verification systems?
Share your thoughts below! 👇
#trezorsayscryptobilissoldwalletmaycontainmaliciouscom #Trezor #CryptoSecurity #Bitcoin #HardwareWallet #CryptoNews #BinanceSquare
This could be another serious supply-chain security concern for the crypto industry. Here's what you need to know. 👇
🔴 1. HOW DOES THE SUSPECTED IMPLANT WORK?
According to the customer report, the device allegedly contained:
An additional circuit board.A cellular communication module.An antenna capable of transmitting information.
The suspected component could potentially capture sensitive information displayed on the wallet screen, including the recovery phrase, and transmit it over a mobile network.
⚠️ 2. TREZOR HAS ISSUED AN URGENT WARNING
Trezor has not physically examined the reported device yet, but considers the report credible based on customer information and a video interview.
The company says no customer funds have been reported stolen in connection with this particular Trezor report.
🛡️ 3. WHO SHOULD TAKE ACTION?
Anyone who purchased a Trezor hardware wallet through CryptoBilis since March 2026 should:
Move crypto assets to a newly created wallet.Generate a completely new recovery phrase.Avoid setting up unused devices from the reseller.Contact official Trezor Support about replacement options.
Important: Simply restoring your old recovery phrase on another device is NOT enough if that phrase may already be compromised.
🔍 4. WHY IS THIS A BIGGER INDUSTRY WARNING?
CryptoBilis was previously linked to confirmed physical tampering involving Ledger hardware wallets. Trezor has also removed the reseller from its authorized network.
This raises an important question about hardware-wallet supply chains: Can users trust a device if its physical integrity has been compromised before reaching them?
💡 MY TAKEAWAY
Hardware wallets are designed to protect private keys, but physical security and trusted distribution channels matter just as much as software security.
Don't panic, but don't ignore this warning. Never share your recovery phrase with anyone claiming to be customer support, and purchase hardware wallets directly from manufacturers or verified authorized sellers.
🔥 Do you trust hardware wallets after these supply-chain incidents, or is it time for manufacturers to introduce stronger verification systems?
Share your thoughts below! 👇
#trezorsayscryptobilissoldwalletmaycontainmaliciouscom #Trezor #CryptoSecurity #Bitcoin #HardwareWallet #CryptoNews #BinanceSquare
61

·
--
Urgent: Trezor warns of compromised hardware wallets from CryptoBilis.
Trezor has alerted buyers of Trezor Safe 5 devices purchased from CryptoBilis on or after March 2026 to move funds to a new wallet with a fresh seed immediately.
The alert follows a responsible disclosure on October 28 from an Indonesian customer who discovered an extra circuit board with a cellular module and antenna inside the device.
The implant can read the screen, including the wallet backup, and transmit data over a mobile network when plugged in.
This underscores a supply chain attack and growing crypto security challenges for hardware wallet users.
Trezor advises affected users to transfer assets to a secure hardware wallet, or temporarily to a software wallet or trusted exchange while verifying the receiving address.
Customers who have not set up the device should not use it.
Eligible buyers will receive a replacement Trezor or a voucher, and must keep the CryptoBilis device and contact Trezor Support.
What steps are you taking to verify the integrity of your hardware wallet supply chain?
#CryptoSecurity #HardwareWallet #SupplyChainSecurity #Trezor
Urgent: Trezor warns of compromised hardware wallets from CryptoBilis.
Trezor has alerted buyers of Trezor Safe 5 devices purchased from CryptoBilis on or after March 2026 to move funds to a new wallet with a fresh seed immediately.
The alert follows a responsible disclosure on October 28 from an Indonesian customer who discovered an extra circuit board with a cellular module and antenna inside the device.
The implant can read the screen, including the wallet backup, and transmit data over a mobile network when plugged in.
This underscores a supply chain attack and growing crypto security challenges for hardware wallet users.
Trezor advises affected users to transfer assets to a secure hardware wallet, or temporarily to a software wallet or trusted exchange while verifying the receiving address.
Customers who have not set up the device should not use it.
Eligible buyers will receive a replacement Trezor or a voucher, and must keep the CryptoBilis device and contact Trezor Support.
What steps are you taking to verify the integrity of your hardware wallet supply chain?
#CryptoSecurity #HardwareWallet #SupplyChainSecurity #Trezor
Trezor has alerted buyers of Trezor Safe 5 devices purchased from CryptoBilis on or after March 2026 to move funds to a new wallet with a fresh seed immediately.
The alert follows a responsible disclosure on October 28 from an Indonesian customer who discovered an extra circuit board with a cellular module and antenna inside the device.
The implant can read the screen, including the wallet backup, and transmit data over a mobile network when plugged in.
This underscores a supply chain attack and growing crypto security challenges for hardware wallet users.
Trezor advises affected users to transfer assets to a secure hardware wallet, or temporarily to a software wallet or trusted exchange while verifying the receiving address.
Customers who have not set up the device should not use it.
Eligible buyers will receive a replacement Trezor or a voucher, and must keep the CryptoBilis device and contact Trezor Support.
What steps are you taking to verify the integrity of your hardware wallet supply chain?
#CryptoSecurity #HardwareWallet #SupplyChainSecurity #Trezor
6
·
--
Hardware wallet trouble again: Trezor warns that a Safe 5 sold by CryptoBilis, its former official Southeast Asian distributor, was reported to contain a “wiretap board.”
The device, bought by an Indonesian user on Tokopedia in August, reportedly had an extra circuit board with a cellular module and antenna between the motherboard and screen. It was allegedly capable of reading the recovery phrase displayed on the screen and transmitting it over a mobile network as soon as the device was plugged in.
Trezor received the disclosure on 10/28. The device has not yet been examined in a lab, but the report is being treated as credible; no users have reported losing funds so far.
If you’ve bought a Trezor from CryptoBilis since March, move your assets as soon as possible to a new wallet with a newly generated recovery phrase, and don’t use the old phrase again. If you haven’t activated your device, don’t turn it on; contact the official company to arrange a replacement or voucher.
This is another case after Ledger’s Southeast Asian supply channel was compromised. Buy hardware wallets only through official channels. $BTC is currently around $77,350, essentially flat over the past 24 hours.
#硬件钱包 #Trezor #CryptoSecurity
Hardware wallet trouble again: Trezor warns that a Safe 5 sold by CryptoBilis, its former official Southeast Asian distributor, was reported to contain a “wiretap board.”
The device, bought by an Indonesian user on Tokopedia in August, reportedly had an extra circuit board with a cellular module and antenna between the motherboard and screen. It was allegedly capable of reading the recovery phrase displayed on the screen and transmitting it over a mobile network as soon as the device was plugged in.
Trezor received the disclosure on 10/28. The device has not yet been examined in a lab, but the report is being treated as credible; no users have reported losing funds so far.
If you’ve bought a Trezor from CryptoBilis since March, move your assets as soon as possible to a new wallet with a newly generated recovery phrase, and don’t use the old phrase again. If you haven’t activated your device, don’t turn it on; contact the official company to arrange a replacement or voucher.
This is another case after Ledger’s Southeast Asian supply channel was compromised. Buy hardware wallets only through official channels. $BTC is currently around $77,350, essentially flat over the past 24 hours.
#硬件钱包 #Trezor #CryptoSecurity
The device, bought by an Indonesian user on Tokopedia in August, reportedly had an extra circuit board with a cellular module and antenna between the motherboard and screen. It was allegedly capable of reading the recovery phrase displayed on the screen and transmitting it over a mobile network as soon as the device was plugged in.
Trezor received the disclosure on 10/28. The device has not yet been examined in a lab, but the report is being treated as credible; no users have reported losing funds so far.
If you’ve bought a Trezor from CryptoBilis since March, move your assets as soon as possible to a new wallet with a newly generated recovery phrase, and don’t use the old phrase again. If you haven’t activated your device, don’t turn it on; contact the official company to arrange a replacement or voucher.
This is another case after Ledger’s Southeast Asian supply channel was compromised. Buy hardware wallets only through official channels. $BTC is currently around $77,350, essentially flat over the past 24 hours.
#硬件钱包 #Trezor #CryptoSecurity
107

Could your hardware wallet be spying on you? Trezor sounds the alarm 🐕
On October 30, Trezor warned all users who had bought its wallets through reseller CryptoBilis since March 2026: move your coins to a new wallet immediately, use a completely new recovery phrase, don’t reuse your old one, and don’t use any devices you haven’t activated yet.
It started when an Indonesian buyer found an extra circuit board inside a Trezor Safe 5 they’d bought from CryptoBilis via Tokopedia in August. It had a cellular module and antenna, and was wedged between the mainboard and the screen. According to the report, it could read whatever appeared on the screen—including wallet backups—and transmit it over a mobile network every time the device was plugged in.
To be frank, Trezor hasn’t received the device for lab testing, and no users have reported losing coins as a result. But it considers the report credible, so it’s warning users as a precaution—after all, this is the same reseller involved in the earlier Ledger implant incident. Trezor removed CryptoBilis from its authorized reseller list on October 9 and inspected four Trezor devices from the same channel, finding no signs of tampering so far.
The lesson is simple: if you didn’t buy your “safe” directly from the official store, assume it isn’t safe. Move your coins first, sort out the blame later. 🐕
#Trezor #硬件钱包 #CryptoBilis
Could your hardware wallet be spying on you? Trezor sounds the alarm 🐕
On October 30, Trezor warned all users who had bought its wallets through reseller CryptoBilis since March 2026: move your coins to a new wallet immediately, use a completely new recovery phrase, don’t reuse your old one, and don’t use any devices you haven’t activated yet.
It started when an Indonesian buyer found an extra circuit board inside a Trezor Safe 5 they’d bought from CryptoBilis via Tokopedia in August. It had a cellular module and antenna, and was wedged between the mainboard and the screen. According to the report, it could read whatever appeared on the screen—including wallet backups—and transmit it over a mobile network every time the device was plugged in.
To be frank, Trezor hasn’t received the device for lab testing, and no users have reported losing coins as a result. But it considers the report credible, so it’s warning users as a precaution—after all, this is the same reseller involved in the earlier Ledger implant incident. Trezor removed CryptoBilis from its authorized reseller list on October 9 and inspected four Trezor devices from the same channel, finding no signs of tampering so far.
The lesson is simple: if you didn’t buy your “safe” directly from the official store, assume it isn’t safe. Move your coins first, sort out the blame later. 🐕
#Trezor #硬件钱包 #CryptoBilis
On October 30, Trezor warned all users who had bought its wallets through reseller CryptoBilis since March 2026: move your coins to a new wallet immediately, use a completely new recovery phrase, don’t reuse your old one, and don’t use any devices you haven’t activated yet.
It started when an Indonesian buyer found an extra circuit board inside a Trezor Safe 5 they’d bought from CryptoBilis via Tokopedia in August. It had a cellular module and antenna, and was wedged between the mainboard and the screen. According to the report, it could read whatever appeared on the screen—including wallet backups—and transmit it over a mobile network every time the device was plugged in.
To be frank, Trezor hasn’t received the device for lab testing, and no users have reported losing coins as a result. But it considers the report credible, so it’s warning users as a precaution—after all, this is the same reseller involved in the earlier Ledger implant incident. Trezor removed CryptoBilis from its authorized reseller list on October 9 and inspected four Trezor devices from the same channel, finding no signs of tampering so far.
The lesson is simple: if you didn’t buy your “safe” directly from the official store, assume it isn’t safe. Move your coins first, sort out the blame later. 🐕
#Trezor #硬件钱包 #CryptoBilis
40

·
--
Bearish
“Move it to cold storage” is the most popular advice after the Binance hack. And the laziest, if you don’t ask where the box came from.
The next morning, Trezor posts: a buyer in Indonesia reported finding an extra board with a mobile module and antenna inside a Trezor Safe 5.
The wallet was bought in August through the CryptoBilis store on Tokopedia.
And CryptoBilis was an official Trezor reseller until October 9.
To be honest: Trezor hasn’t received the device itself yet, so this is still just a suspicion. No one has reported any losses.
But the takeaway is already clear to me:
— You can’t check the board yourself; even weighing it won’t help.
— If you bought hardware from CryptoBilis starting in March, your old seed phrase won’t help on a new wallet. You need a new wallet with a new seed phrase.
— A cold wallet is only as clean as the route the box took to get to you.
Long story short, only buy directly from the manufacturer. “Official reseller” doesn’t guarantee anything anymore.
#Trezor #HardwareWallets
“Move it to cold storage” is the most popular advice after the Binance hack. And the laziest, if you don’t ask where the box came from.
The next morning, Trezor posts: a buyer in Indonesia reported finding an extra board with a mobile module and antenna inside a Trezor Safe 5.
The wallet was bought in August through the CryptoBilis store on Tokopedia.
And CryptoBilis was an official Trezor reseller until October 9.
To be honest: Trezor hasn’t received the device itself yet, so this is still just a suspicion. No one has reported any losses.
But the takeaway is already clear to me:
— You can’t check the board yourself; even weighing it won’t help.
— If you bought hardware from CryptoBilis starting in March, your old seed phrase won’t help on a new wallet. You need a new wallet with a new seed phrase.
— A cold wallet is only as clean as the route the box took to get to you.
Long story short, only buy directly from the manufacturer. “Official reseller” doesn’t guarantee anything anymore.
#Trezor #HardwareWallets
The next morning, Trezor posts: a buyer in Indonesia reported finding an extra board with a mobile module and antenna inside a Trezor Safe 5.
The wallet was bought in August through the CryptoBilis store on Tokopedia.
And CryptoBilis was an official Trezor reseller until October 9.
To be honest: Trezor hasn’t received the device itself yet, so this is still just a suspicion. No one has reported any losses.
But the takeaway is already clear to me:
— You can’t check the board yourself; even weighing it won’t help.
— If you bought hardware from CryptoBilis starting in March, your old seed phrase won’t help on a new wallet. You need a new wallet with a new seed phrase.
— A cold wallet is only as clean as the route the box took to get to you.
Long story short, only buy directly from the manufacturer. “Official reseller” doesn’t guarantee anything anymore.
#Trezor #HardwareWallets
Motyvator Milliardam News:
Дякую ща пораду
1
8
94
·
--
Today, Trezor issued a security advisory dated October 30 about a hardware wallet suspected of having been tampered with.
The case involves an Indonesian user who bought a Trezor Safe 5 from the reseller CryptoBilis on Tokopedia in August. On October 28, they reported to Trezor that there was an extra circuit board inside, fitted with a cellular module and antenna and wedged between the mainboard and the screen. According to the report, the board transmits what is displayed on the screen when the device is powered on, including the recovery seed phrase. To be clear, the device has not yet been sent to Trezor’s lab, the mechanism has not been officially confirmed, and no CryptoBilis customer has reported losing money to Trezor as a result. This is a precautionary alert, not a confirmed case of widespread theft.
The danger to retail users here isn’t that the technology is especially sophisticated; it’s that the chain of trust broke at the last place it should have. Many people buy a hardware wallet for peace of mind, assuming that if it comes through an official channel, it must be safe. But the problem occurred at the reseller stage. More concerning, there had already been a confirmed case of Ledger devices being tampered with by the same reseller, and Trezor removed it from its list of authorized resellers on October 9. This advisory covers all Trezor models bought from CryptoBilis after March 2026, not just this one Safe 5.
If you bought from this reseller, there are three things you can do right now. First, don’t rush to restore your old seed phrase onto another device. Trezor is clear that this would just be changing the packaging, not solving the problem. The right approach is to create a new wallet with a completely new seed phrase, then transfer your assets to it. Second, don’t use any affected device that hasn’t been activated, and don’t enter an existing seed phrase into it. Third, keep the original device and contact official customer support to ask about a replacement or voucher. Treat any email, letter, or phone call that uses this incident as a pretext to ask for your seed phrase as a scam—official support will never ask for it.
One other detail is worth remembering: Trezor says that weighing a device or taking it apart yourself isn’t a reliable way to tell, and inspections of the four devices submitted so far have found no signs of tampering. So don’t assume you’re in the clear just because your device looks normal, and don’t assume the advisory doesn’t apply to you just because it mentions only one device. What matters is where and when you bought it.
When buying a hardware wallet, do you first check whether the seller is officially authorized, or do you just look at the price and how quickly it ships?
#Trezor #硬件钱包 #钱包安全 #防骗
—— web3 leek Kai
Disclaimer: The above is a personal sharing and does not constitute investment advice. It is for learning and discussion purposes only. The crypto market involves risks; proceed with caution.
Today, Trezor issued a security advisory dated October 30 about a hardware wallet suspected of having been tampered with.
The case involves an Indonesian user who bought a Trezor Safe 5 from the reseller CryptoBilis on Tokopedia in August. On October 28, they reported to Trezor that there was an extra circuit board inside, fitted with a cellular module and antenna and wedged between the mainboard and the screen. According to the report, the board transmits what is displayed on the screen when the device is powered on, including the recovery seed phrase. To be clear, the device has not yet been sent to Trezor’s lab, the mechanism has not been officially confirmed, and no CryptoBilis customer has reported losing money to Trezor as a result. This is a precautionary alert, not a confirmed case of widespread theft.
The danger to retail users here isn’t that the technology is especially sophisticated; it’s that the chain of trust broke at the last place it should have. Many people buy a hardware wallet for peace of mind, assuming that if it comes through an official channel, it must be safe. But the problem occurred at the reseller stage. More concerning, there had already been a confirmed case of Ledger devices being tampered with by the same reseller, and Trezor removed it from its list of authorized resellers on October 9. This advisory covers all Trezor models bought from CryptoBilis after March 2026, not just this one Safe 5.
If you bought from this reseller, there are three things you can do right now. First, don’t rush to restore your old seed phrase onto another device. Trezor is clear that this would just be changing the packaging, not solving the problem. The right approach is to create a new wallet with a completely new seed phrase, then transfer your assets to it. Second, don’t use any affected device that hasn’t been activated, and don’t enter an existing seed phrase into it. Third, keep the original device and contact official customer support to ask about a replacement or voucher. Treat any email, letter, or phone call that uses this incident as a pretext to ask for your seed phrase as a scam—official support will never ask for it.
One other detail is worth remembering: Trezor says that weighing a device or taking it apart yourself isn’t a reliable way to tell, and inspections of the four devices submitted so far have found no signs of tampering. So don’t assume you’re in the clear just because your device looks normal, and don’t assume the advisory doesn’t apply to you just because it mentions only one device. What matters is where and when you bought it.
When buying a hardware wallet, do you first check whether the seller is officially authorized, or do you just look at the price and how quickly it ships?
#Trezor #硬件钱包 #钱包安全 #防骗
—— web3 leek Kai
Disclaimer: The above is a personal sharing and does not constitute investment advice. It is for learning and discussion purposes only. The crypto market involves risks; proceed with caution.
The case involves an Indonesian user who bought a Trezor Safe 5 from the reseller CryptoBilis on Tokopedia in August. On October 28, they reported to Trezor that there was an extra circuit board inside, fitted with a cellular module and antenna and wedged between the mainboard and the screen. According to the report, the board transmits what is displayed on the screen when the device is powered on, including the recovery seed phrase. To be clear, the device has not yet been sent to Trezor’s lab, the mechanism has not been officially confirmed, and no CryptoBilis customer has reported losing money to Trezor as a result. This is a precautionary alert, not a confirmed case of widespread theft.
The danger to retail users here isn’t that the technology is especially sophisticated; it’s that the chain of trust broke at the last place it should have. Many people buy a hardware wallet for peace of mind, assuming that if it comes through an official channel, it must be safe. But the problem occurred at the reseller stage. More concerning, there had already been a confirmed case of Ledger devices being tampered with by the same reseller, and Trezor removed it from its list of authorized resellers on October 9. This advisory covers all Trezor models bought from CryptoBilis after March 2026, not just this one Safe 5.
If you bought from this reseller, there are three things you can do right now. First, don’t rush to restore your old seed phrase onto another device. Trezor is clear that this would just be changing the packaging, not solving the problem. The right approach is to create a new wallet with a completely new seed phrase, then transfer your assets to it. Second, don’t use any affected device that hasn’t been activated, and don’t enter an existing seed phrase into it. Third, keep the original device and contact official customer support to ask about a replacement or voucher. Treat any email, letter, or phone call that uses this incident as a pretext to ask for your seed phrase as a scam—official support will never ask for it.
One other detail is worth remembering: Trezor says that weighing a device or taking it apart yourself isn’t a reliable way to tell, and inspections of the four devices submitted so far have found no signs of tampering. So don’t assume you’re in the clear just because your device looks normal, and don’t assume the advisory doesn’t apply to you just because it mentions only one device. What matters is where and when you bought it.
When buying a hardware wallet, do you first check whether the seller is officially authorized, or do you just look at the price and how quickly it ships?
#Trezor #硬件钱包 #钱包安全 #防骗
—— web3 leek Kai
Disclaimer: The above is a personal sharing and does not constitute investment advice. It is for learning and discussion purposes only. The crypto market involves risks; proceed with caution.
49

Security alert: Trezor wallets sold through a specific channel may have been implanted with a Trojan; users who purchased from this batch may face asset security risks
Oct. 30 — According to The Block, hardware wallet manufacturer Trezor received a security disclosure report indicating that a batch of Trezor Safe 5 devices sold by reseller CryptoBilis may have been implanted with malware.
Trezor also advised users who purchased this hardware wallet through CryptoBilis after March 2026 to move their assets as soon as possible to a new wallet generated with a brand-new recovery phrase. No reports of user assets being stolen have been received so far.
Notably, CryptoBilis was also an authorized Ledger reseller, and Ledger reported a similar security incident in early October. This series of events shows that supply chain attacks have become a serious challenge for the hardware wallet industry.
Trezor removed CryptoBilis from its official reseller list on October 9 and said it would further tighten its reseller network and strengthen supply chain controls.
As of publication, Trezor has not received any reports of users losing funds. Users who reported affected devices had moved their assets before discovering the issue, thereby avoiding potential losses.
In summary, this incident is another reminder to cryptocurrency users that digital asset security depends not only on technical safeguards, but also on vigilance throughout the entire supply chain.
Users holding large amounts of crypto assets should protect their holdings by purchasing hardware wallets through authorized channels, regularly checking the security status of their devices, and keeping an eye on official security advisories.
#Trezor #硬件钱包
Security alert: Trezor wallets sold through a specific channel may have been implanted with a Trojan; users who purchased from this batch may face asset security risks
Oct. 30 — According to The Block, hardware wallet manufacturer Trezor received a security disclosure report indicating that a batch of Trezor Safe 5 devices sold by reseller CryptoBilis may have been implanted with malware.
Trezor also advised users who purchased this hardware wallet through CryptoBilis after March 2026 to move their assets as soon as possible to a new wallet generated with a brand-new recovery phrase. No reports of user assets being stolen have been received so far.
Notably, CryptoBilis was also an authorized Ledger reseller, and Ledger reported a similar security incident in early October. This series of events shows that supply chain attacks have become a serious challenge for the hardware wallet industry.
Trezor removed CryptoBilis from its official reseller list on October 9 and said it would further tighten its reseller network and strengthen supply chain controls.
As of publication, Trezor has not received any reports of users losing funds. Users who reported affected devices had moved their assets before discovering the issue, thereby avoiding potential losses.
In summary, this incident is another reminder to cryptocurrency users that digital asset security depends not only on technical safeguards, but also on vigilance throughout the entire supply chain.
Users holding large amounts of crypto assets should protect their holdings by purchasing hardware wallets through authorized channels, regularly checking the security status of their devices, and keeping an eye on official security advisories.
#Trezor #硬件钱包
Oct. 30 — According to The Block, hardware wallet manufacturer Trezor received a security disclosure report indicating that a batch of Trezor Safe 5 devices sold by reseller CryptoBilis may have been implanted with malware.
Trezor also advised users who purchased this hardware wallet through CryptoBilis after March 2026 to move their assets as soon as possible to a new wallet generated with a brand-new recovery phrase. No reports of user assets being stolen have been received so far.
Notably, CryptoBilis was also an authorized Ledger reseller, and Ledger reported a similar security incident in early October. This series of events shows that supply chain attacks have become a serious challenge for the hardware wallet industry.
Trezor removed CryptoBilis from its official reseller list on October 9 and said it would further tighten its reseller network and strengthen supply chain controls.
As of publication, Trezor has not received any reports of users losing funds. Users who reported affected devices had moved their assets before discovering the issue, thereby avoiding potential losses.
In summary, this incident is another reminder to cryptocurrency users that digital asset security depends not only on technical safeguards, but also on vigilance throughout the entire supply chain.
Users holding large amounts of crypto assets should protect their holdings by purchasing hardware wallets through authorized channels, regularly checking the security status of their devices, and keeping an eye on official security advisories.
#Trezor #硬件钱包
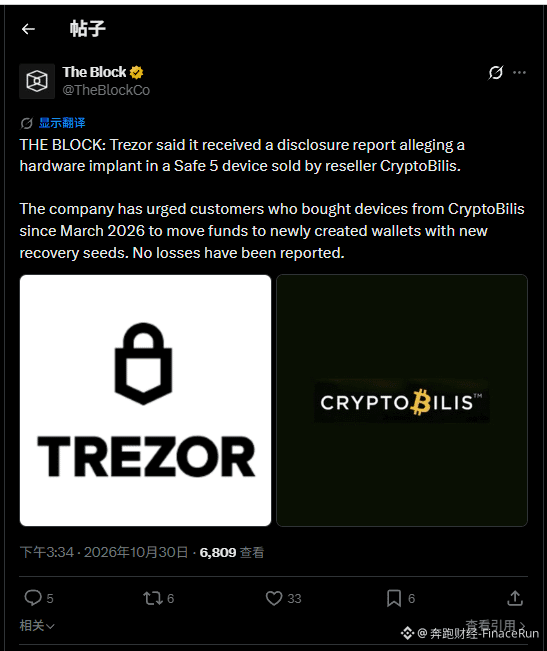
1
1
3
4.1k

·
--
Saw this on Trezor’s official account: A Safe 5 sold by CryptoBilis, a former authorized reseller in Southeast Asia, was reported by a user through responsible disclosure as a suspected hardware implant. A circuit board with a cellular module had been added between the mainboard and screen. It allegedly could read the recovery phrase displayed on the screen and transmit it over a mobile network once plugged in.
Key facts: The report was received on 10/28, and the device was purchased through Tokopedia in August. Trezor has yet to receive the actual device for laboratory testing, but considers the report credible based on the description and video interview. It is urging anyone who has bought any model from CryptoBilis since March to move their assets to a new wallet with a new recovery phrase as soon as possible, and not to reuse their old backup. No buyers have reported losing funds so far. Affected customers can contact support to exchange their device for a new one or receive a voucher. A supply-chain implant involving the same reseller had previously been reported on the Ledger side, and Trezor dropped the reseller on 10/9.
Another layer has been peeled back in the hardware wallet supply chain.
#硬件钱包 #安全 #Trezor
Saw this on Trezor’s official account: A Safe 5 sold by CryptoBilis, a former authorized reseller in Southeast Asia, was reported by a user through responsible disclosure as a suspected hardware implant. A circuit board with a cellular module had been added between the mainboard and screen. It allegedly could read the recovery phrase displayed on the screen and transmit it over a mobile network once plugged in.
Key facts: The report was received on 10/28, and the device was purchased through Tokopedia in August. Trezor has yet to receive the actual device for laboratory testing, but considers the report credible based on the description and video interview. It is urging anyone who has bought any model from CryptoBilis since March to move their assets to a new wallet with a new recovery phrase as soon as possible, and not to reuse their old backup. No buyers have reported losing funds so far. Affected customers can contact support to exchange their device for a new one or receive a voucher. A supply-chain implant involving the same reseller had previously been reported on the Ledger side, and Trezor dropped the reseller on 10/9.
Another layer has been peeled back in the hardware wallet supply chain.
#硬件钱包 #安全 #Trezor
Key facts: The report was received on 10/28, and the device was purchased through Tokopedia in August. Trezor has yet to receive the actual device for laboratory testing, but considers the report credible based on the description and video interview. It is urging anyone who has bought any model from CryptoBilis since March to move their assets to a new wallet with a new recovery phrase as soon as possible, and not to reuse their old backup. No buyers have reported losing funds so far. Affected customers can contact support to exchange their device for a new one or receive a voucher. A supply-chain implant involving the same reseller had previously been reported on the Ledger side, and Trezor dropped the reseller on 10/9.
Another layer has been peeled back in the hardware wallet supply chain.
#硬件钱包 #安全 #Trezor
14
·
--
Trezor issued a hardware wallet security warning
It looks pretty alarming
What we know
A responsible disclosure reported that a Safe 5 sold by the Southeast Asian reseller CryptoBilis
may have had an extra circuit board secretly installed
with a cellular module and antenna
The report says it could potentially read the recovery phrase on the screen and transmit it externally
Trezor has not yet received the physical device to verify this in a lab
But based on the description and video communication
it shared the warning as a credible risk for now
No buyers have reported losing funds so far
The practical advice is clear
If you bought from CryptoBilis starting in March 2026
move your assets as soon as possible to a new wallet with a brand-new recovery phrase
Don't enter your old recovery phrase into the suspicious device again
The company says you can contact support to get a replacement device
Hardware wallets are also vulnerable to supply-chain risks
Buy devices through official channels
Don't be tempted by cheap deals from unknown resellers
$BTC $ETH
#Trezor #硬件钱包 #SupplyChainSecurity
Trezor issued a hardware wallet security warning
It looks pretty alarming
What we know
A responsible disclosure reported that a Safe 5 sold by the Southeast Asian reseller CryptoBilis
may have had an extra circuit board secretly installed
with a cellular module and antenna
The report says it could potentially read the recovery phrase on the screen and transmit it externally
Trezor has not yet received the physical device to verify this in a lab
But based on the description and video communication
it shared the warning as a credible risk for now
No buyers have reported losing funds so far
The practical advice is clear
If you bought from CryptoBilis starting in March 2026
move your assets as soon as possible to a new wallet with a brand-new recovery phrase
Don't enter your old recovery phrase into the suspicious device again
The company says you can contact support to get a replacement device
Hardware wallets are also vulnerable to supply-chain risks
Buy devices through official channels
Don't be tempted by cheap deals from unknown resellers
$BTC $ETH
#Trezor #硬件钱包 #SupplyChainSecurity
It looks pretty alarming
What we know
A responsible disclosure reported that a Safe 5 sold by the Southeast Asian reseller CryptoBilis
may have had an extra circuit board secretly installed
with a cellular module and antenna
The report says it could potentially read the recovery phrase on the screen and transmit it externally
Trezor has not yet received the physical device to verify this in a lab
But based on the description and video communication
it shared the warning as a credible risk for now
No buyers have reported losing funds so far
The practical advice is clear
If you bought from CryptoBilis starting in March 2026
move your assets as soon as possible to a new wallet with a brand-new recovery phrase
Don't enter your old recovery phrase into the suspicious device again
The company says you can contact support to get a replacement device
Hardware wallets are also vulnerable to supply-chain risks
Buy devices through official channels
Don't be tempted by cheap deals from unknown resellers
$BTC $ETH
#Trezor #硬件钱包 #SupplyChainSecurity
1
1
992

·
--
Trezor Officially Warns That Safe 5 Devices from CryptoBilis May Have Had Chips Implanted; Owners Urged to Transfer Funds Immediately
The security perimeter of hardware wallets is expanding from software to physical chips.
According to Decrypt, hardware wallet manufacturer Trezor has formally responded for the first time to reports that hardware chips may have been implanted in products sold through a third-party reseller. Trezor advises users who purchased a Safe 5 through CryptoBilis since March to transfer the assets on their devices as soon as possible.
It is worth noting that Trezor says it has not yet physically inspected the devices in question and is treating the reports as credible leads. CryptoBilis is a third-party reseller, not an official sales channel, so the potential impact is relatively limited, primarily affecting products from specific batches sold through a particular channel.
This incident represents a new challenge to the physical security of hardware wallets. In the past, discussions of wallet security have focused mostly on software vulnerabilities, leaked recovery phrases, or user behavior. But if the alleged chip implant is confirmed, the attack would reach directly into the device’s hardware, meaning the final physical barrier protecting private keys could also be bypassed. Together with several recent exchange security incidents and controversies involving key vault products such as Keystone, this has sparked a broader discussion about the security of self-custody.
However, several key factors remain to be seen. First, Trezor has not physically inspected the devices and is currently treating the matter as a credible report; the final conclusion awaits official verification. Second, the reseller involved is a third party, and it is not yet clear whether products sold through official channels are affected. Third, the risk may be limited to specific batches rather than the entire product line.
For owners, the most practical step is to confirm where and when they purchased their device. If they bought a Safe 5 through CryptoBilis after March, they should transfer their assets promptly to reduce uncertainty. For the industry as a whole, how hardware wallets maintain physical security throughout production, shipping, and distribution may become an ongoing area of scrutiny.
Next, watch for whether Trezor publishes formal test results and an official statement, as well as how the reseller involved responds.
#Trezor #CryptoSecurity #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow the story and provide updates if there are significant developments.
Trezor Officially Warns That Safe 5 Devices from CryptoBilis May Have Had Chips Implanted; Owners Urged to Transfer Funds Immediately
The security perimeter of hardware wallets is expanding from software to physical chips.
According to Decrypt, hardware wallet manufacturer Trezor has formally responded for the first time to reports that hardware chips may have been implanted in products sold through a third-party reseller. Trezor advises users who purchased a Safe 5 through CryptoBilis since March to transfer the assets on their devices as soon as possible.
It is worth noting that Trezor says it has not yet physically inspected the devices in question and is treating the reports as credible leads. CryptoBilis is a third-party reseller, not an official sales channel, so the potential impact is relatively limited, primarily affecting products from specific batches sold through a particular channel.
This incident represents a new challenge to the physical security of hardware wallets. In the past, discussions of wallet security have focused mostly on software vulnerabilities, leaked recovery phrases, or user behavior. But if the alleged chip implant is confirmed, the attack would reach directly into the device’s hardware, meaning the final physical barrier protecting private keys could also be bypassed. Together with several recent exchange security incidents and controversies involving key vault products such as Keystone, this has sparked a broader discussion about the security of self-custody.
However, several key factors remain to be seen. First, Trezor has not physically inspected the devices and is currently treating the matter as a credible report; the final conclusion awaits official verification. Second, the reseller involved is a third party, and it is not yet clear whether products sold through official channels are affected. Third, the risk may be limited to specific batches rather than the entire product line.
For owners, the most practical step is to confirm where and when they purchased their device. If they bought a Safe 5 through CryptoBilis after March, they should transfer their assets promptly to reduce uncertainty. For the industry as a whole, how hardware wallets maintain physical security throughout production, shipping, and distribution may become an ongoing area of scrutiny.
Next, watch for whether Trezor publishes formal test results and an official statement, as well as how the reseller involved responds.
#Trezor #CryptoSecurity #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow the story and provide updates if there are significant developments.
The security perimeter of hardware wallets is expanding from software to physical chips.
According to Decrypt, hardware wallet manufacturer Trezor has formally responded for the first time to reports that hardware chips may have been implanted in products sold through a third-party reseller. Trezor advises users who purchased a Safe 5 through CryptoBilis since March to transfer the assets on their devices as soon as possible.
It is worth noting that Trezor says it has not yet physically inspected the devices in question and is treating the reports as credible leads. CryptoBilis is a third-party reseller, not an official sales channel, so the potential impact is relatively limited, primarily affecting products from specific batches sold through a particular channel.
This incident represents a new challenge to the physical security of hardware wallets. In the past, discussions of wallet security have focused mostly on software vulnerabilities, leaked recovery phrases, or user behavior. But if the alleged chip implant is confirmed, the attack would reach directly into the device’s hardware, meaning the final physical barrier protecting private keys could also be bypassed. Together with several recent exchange security incidents and controversies involving key vault products such as Keystone, this has sparked a broader discussion about the security of self-custody.
However, several key factors remain to be seen. First, Trezor has not physically inspected the devices and is currently treating the matter as a credible report; the final conclusion awaits official verification. Second, the reseller involved is a third party, and it is not yet clear whether products sold through official channels are affected. Third, the risk may be limited to specific batches rather than the entire product line.
For owners, the most practical step is to confirm where and when they purchased their device. If they bought a Safe 5 through CryptoBilis after March, they should transfer their assets promptly to reduce uncertainty. For the industry as a whole, how hardware wallets maintain physical security throughout production, shipping, and distribution may become an ongoing area of scrutiny.
Next, watch for whether Trezor publishes formal test results and an official statement, as well as how the reseller involved responds.
#Trezor #CryptoSecurity #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow the story and provide updates if there are significant developments.
28
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinRebounds$75KAsChipsLead
14,649 views
181 Discussing
2
#JobsReportRaisesHikeOdds
171,466 views
1,462 Discussing
3
#US Data Center Rules May Constrain AI Expansion
27,626 views
136 Discussing
4
#WillAnthropicListOnTime
37,875 views
512 Discussing
5
#BitcoinETFsSee$412MNetOutflows
141 views
30 Discussing
6
#HKSFCPlansToRestrictCryptoAndExchangeTerms
2,308 views
96 Discussing
7
#AnthropicStillPlansPreThanksgivingIPO
11,933 views
179 Discussing
8
#FinCENAndFedWithdraw$250CryptoTransferProposal
3,523 views
13 Discussing
9
#TradFiForBeginners
26,413 views
432 Discussing
10
#$2TWipedOutHedgeFundsFaceLiquidation
24,937 views
108 Discussing