
#across
across
13,918 views
55 Discussing
Hot
Latest
·
--
Across' domain was hijacked to serve a phishing page. GoPlus puts losses near 350,000 dollars. Across says its contracts weren't hacked and users will be made whole. #Across #Security
Across' domain was hijacked to serve a phishing page. GoPlus puts losses near 350,000 dollars. Across says its contracts weren't hacked and users will be made whole. #Across #Security
3

·
--
【He signed just one “authorization,” and $300,000 deposited in Aave was drained in three minutes! Losses from the Across website hijacking revealed】
On-chain data shows that while the cross-chain bridge Across’s website was hijacked on November 10, about $402,000 was stolen from nine wallets across five chains. About $305,000 of that came from a single Aave depositor: he signed an authorization on a fake webpage, and the hacker immediately transferred out about 148.6 aWETH in four transactions over the next three minutes (a receipt token for ETH deposited in Aave, which can be transferred directly). By the time he revoked the authorization, the funds were gone. Across said it has regained control of the domain and promised to compensate affected users.
$AAVE $ETH
#Across #Aave #WalletSecurity
【He signed just one “authorization,” and $300,000 deposited in Aave was drained in three minutes! Losses from the Across website hijacking revealed】
On-chain data shows that while the cross-chain bridge Across’s website was hijacked on November 10, about $402,000 was stolen from nine wallets across five chains. About $305,000 of that came from a single Aave depositor: he signed an authorization on a fake webpage, and the hacker immediately transferred out about 148.6 aWETH in four transactions over the next three minutes (a receipt token for ETH deposited in Aave, which can be transferred directly). By the time he revoked the authorization, the funds were gone. Across said it has regained control of the domain and promised to compensate affected users.
$AAVE $ETH
#Across #Aave #WalletSecurity
On-chain data shows that while the cross-chain bridge Across’s website was hijacked on November 10, about $402,000 was stolen from nine wallets across five chains. About $305,000 of that came from a single Aave depositor: he signed an authorization on a fake webpage, and the hacker immediately transferred out about 148.6 aWETH in four transactions over the next three minutes (a receipt token for ETH deposited in Aave, which can be transferred directly). By the time he revoked the authorization, the funds were gone. Across said it has regained control of the domain and promised to compensate affected users.
$AAVE $ETH
#Across #Aave #WalletSecurity
383

·
--
Bearish
🚨 Across Protocol recovered its website after a phishing attack — but some wallets could STILL be exposed
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
{future}(BNBUSDT)
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
🚨 Across Protocol recovered its website after a phishing attack — but some wallets could STILL be exposed
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
On November 10, attackers reportedly took control of the Across domain through a social engineering attack targeting its registrar, Namecheap
Visitors were redirected to a malicious website that could request dangerous token approvals
Across has now regained control of the domain and says its systems are operational again
But there's a security detail worth understanding 👇
$BNB
🔐 Disconnecting your wallet does NOT revoke token approvals
⚠️ A malicious approval can remain active even after the phishing website disappears
If you connected your wallet or signed anything on Across during the November 10 incident, review suspicious approvals and Permit2 permissions across affected networks
Revoke unauthorized allowances using a trusted tool reached independently — never through unsolicited recovery links
Across has promised to compensate affected users, but final losses and reimbursement details remain undisclosed
This wasn't a confirmed exploit of the bridge's smart contracts
The attacker targeted something users trusted before reaching those contracts — the official website
A recovered domain doesn't automatically mean a recovered wallet
$ACX
#Across #DeFiSecurity
41

🚨 $ACROSS DOMAIN COMPROMISE EXPOSES FRONTEND VULNERABILITIES ACROSS CROSSCHAIN BRIDGES ⚠️
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
🚨 $ACROSS DOMAIN COMPROMISE EXPOSES FRONTEND VULNERABILITIES ACROSS CROSSCHAIN BRIDGES ⚠️
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
Recent reports surrounding a domain-level security incident on $ACROSS highlight the fragile nature of decentralized finance interface layers. While smart contract execution logic may remain secure, compromised frontends create critical injection vectors that intercept user approvals. 🔍
Institutional capital and active market participants must treat interface integrity with the same rigor as on-chain liquidity depth. Until the development team issues a verified all-clear, pausing all interaction is the only rational risk-mitigation protocol. 🛡️
💬 How should decentralized protocols architect frontend redundancy to completely eliminate single-point-of-failure domain risks? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #BridgeRisk
🛡️ 🔒
1

·
--
🚨 CRITICAL FRONTEND ALERT ON $ACROSS : KEEP YOUR WALLETS LOCKED DOWN RIGHT NOW! ⚠️
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
🚨 CRITICAL FRONTEND ALERT ON $ACROSS : KEEP YOUR WALLETS LOCKED DOWN RIGHT NOW! ⚠️
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
Smart money knows the underlying code is only as strong as the portal you use to enter it. 🦈 Reports are flooding in about compromised domain interfaces draining funds through malicious approvals even when smart contracts stay untouched.
Infrastructure vulnerabilities remind us that capital preservation trumps chasing yield every single time. ⚡ Until the core team gives an explicit all-clear, treat that frontend like a minefield and stay entirely away. 🔍
Are you auditing your active token approvals today or waiting for lightning to strike your portfolio? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ACROSS #DeFi #Security #Bridge
🔥 💎
13


·
--
🚨 Across Protocol warns users to stay away from its app as wallet-drain reports surface
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
🚨 Across Protocol warns users to stay away from its app as wallet-drain reports surface
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
Crosschain bridge Across told users on Tuesday not to visit its app, connect wallets, or sign any transactions or approvals until further notice while it investigates a potential security incident affecting its domain.
The team has not said what caused the issue or whether its smart contracts or bridging operations are affected. On X, one user claimed to have lost $9,000 in USDC and another reported losing 7,053 USDT0 across seven transactions on Plasma; these reports have not been independently verified.
⭐ Bridge frontends remain a weak link in DeFi: a hijacked domain can drain users who sign approvals even if the underlying contracts are intact, so traders should watch for Across's official all-clear before interacting.
#Across #DeFi #Security #Bridge
103

·
--
Across's code wasn't hacked. And that's exactly what should worry you.
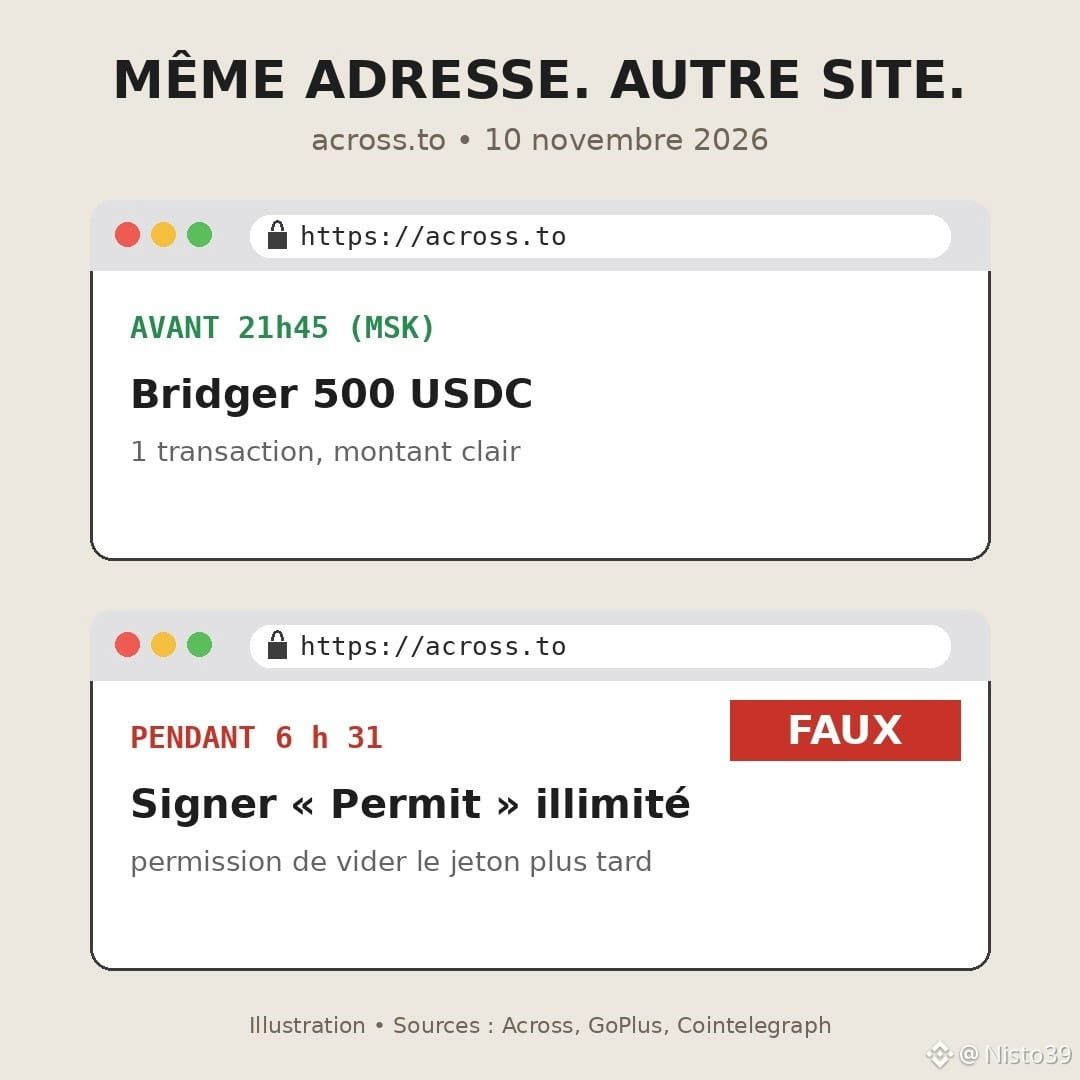
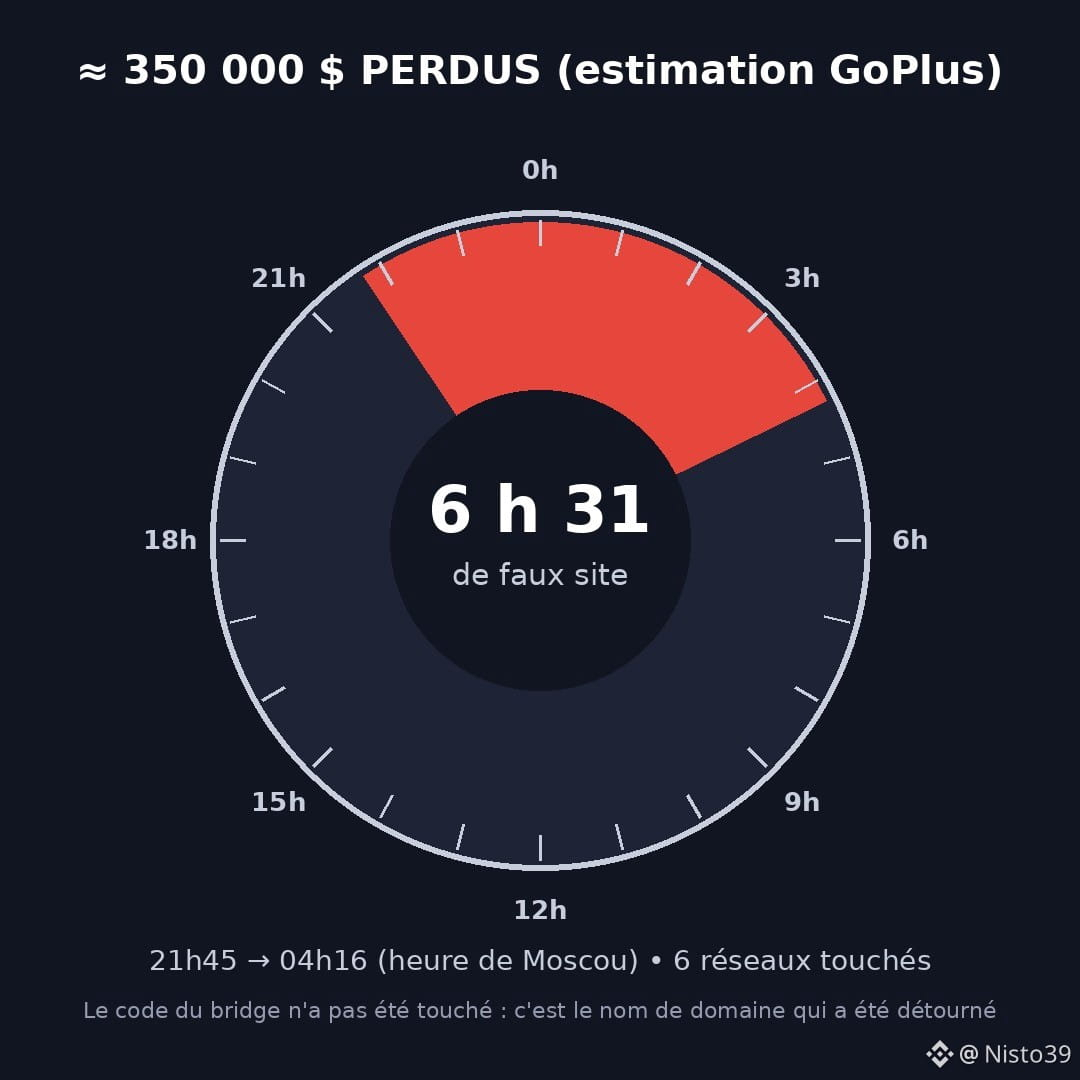
On Tuesday, November 10, around 9:45 p.m. Moscow time, someone took control of the domain name across.to, the address of one of the most widely used bridges (around $5.9 billion transferred in 30 days, according to DefiLlama). No smart contract vulnerability. Just a bit of social engineering at Namecheap, the company that manages the domain name, according to the team.
The result: you typed in the right address, saw the right logo, and landed on a fake site. It asked you to sign “permits” and approvals. An approval is permission given to an address to move your tokens later without asking you again. One signature is enough, and your wallet is drained whenever the attacker decides.
GoPlus estimates the losses at around $350,000 across Ethereum, Arbitrum, Base, BNB Chain, Ink, and Plasma. Across hasn't confirmed a total, but promises to reimburse everyone. The domain was recovered around 4:16 a.m. the next day. Six and a half hours.
My somewhat unpopular opinion: we spend months auditing the code, then entrust the shop's front door to a registrar you can reach by phone. The weak link is no longer the blockchain; it's the webpage in front of it.
What I take away from this: when a site I know by heart asks me for an unusual signature for a simple transfer of $USDC or $ETH, I stop. And I check my approvals from time to time, even when there's been no incident.
Honest question: the last time you signed an approval, did you read who you were giving permission to?
#Across #Securite #Phishing #DeFi #Crypto
Across's code wasn't hacked. And that's exactly what should worry you.
On Tuesday, November 10, around 9:45 p.m. Moscow time, someone took control of the domain name across.to, the address of one of the most widely used bridges (around $5.9 billion transferred in 30 days, according to DefiLlama). No smart contract vulnerability. Just a bit of social engineering at Namecheap, the company that manages the domain name, according to the team.
The result: you typed in the right address, saw the right logo, and landed on a fake site. It asked you to sign “permits” and approvals. An approval is permission given to an address to move your tokens later without asking you again. One signature is enough, and your wallet is drained whenever the attacker decides.
GoPlus estimates the losses at around $350,000 across Ethereum, Arbitrum, Base, BNB Chain, Ink, and Plasma. Across hasn't confirmed a total, but promises to reimburse everyone. The domain was recovered around 4:16 a.m. the next day. Six and a half hours.
My somewhat unpopular opinion: we spend months auditing the code, then entrust the shop's front door to a registrar you can reach by phone. The weak link is no longer the blockchain; it's the webpage in front of it.
What I take away from this: when a site I know by heart asks me for an unusual signature for a simple transfer of $USDC or $ETH , I stop. And I check my approvals from time to time, even when there's been no incident.
Honest question: the last time you signed an approval, did you read who you were giving permission to?
#Across #Securite #Phishing #DeFi #Crypto
On Tuesday, November 10, around 9:45 p.m. Moscow time, someone took control of the domain name across.to, the address of one of the most widely used bridges (around $5.9 billion transferred in 30 days, according to DefiLlama). No smart contract vulnerability. Just a bit of social engineering at Namecheap, the company that manages the domain name, according to the team.
The result: you typed in the right address, saw the right logo, and landed on a fake site. It asked you to sign “permits” and approvals. An approval is permission given to an address to move your tokens later without asking you again. One signature is enough, and your wallet is drained whenever the attacker decides.
GoPlus estimates the losses at around $350,000 across Ethereum, Arbitrum, Base, BNB Chain, Ink, and Plasma. Across hasn't confirmed a total, but promises to reimburse everyone. The domain was recovered around 4:16 a.m. the next day. Six and a half hours.
My somewhat unpopular opinion: we spend months auditing the code, then entrust the shop's front door to a registrar you can reach by phone. The weak link is no longer the blockchain; it's the webpage in front of it.
What I take away from this: when a site I know by heart asks me for an unusual signature for a simple transfer of $USDC or $ETH , I stop. And I check my approvals from time to time, even when there's been no incident.
Honest question: the last time you signed an approval, did you read who you were giving permission to?
#Across #Securite #Phishing #DeFi #Crypto
96
·
--
Cross-chain protocol Across’s official website domain taken over through social engineering; official team has regained control and pledged full compensation for affected users
According to Across’s official X account: At approximately 02:45 Beijing time on November 11 (18:45 UTC on November 10), attackers gained control of across.to through a social engineering attack targeting domain registrar Namecheap and redirected visitors to a phishing page.
1. The team said it received an alert within about 15 minutes and took the site offline. Security response organization SEAL911 helped flag the phishing site to major wallets. Cloudflare marked the domain as high risk and subsequently removed its DNS records.
2. The official team said some users who visited the website before Cloudflare fully blocked it may have been affected; users of third-party integrations and APIs were not affected. The team has not yet disclosed the losses or number of affected users. The Block cited security platform GoPlus’s estimate that losses totaled about $350,000, involving networks including $ETH, Arbitrum, Base, and BNB Chain. The phishing page tricked users into signing fraudulent approvals.
3. At approximately 09:16 that morning, the official team announced that it had recovered the domain with the help of Namecheap’s founder and that systems were back to normal. It will fully compensate affected users and publish a comprehensive postmortem report in the coming days. Please communicate only through official channels, and do not trust unsolicited direct messages or links.
$ACX $ETH $BNB
For informational purposes only; not investment advice. DYOR. Use official channels only, and do not click unfamiliar claim links.
#Across #ACX #安全 #跨链 #Phishing
Cross-chain protocol Across’s official website domain taken over through social engineering; official team has regained control and pledged full compensation for affected users
According to Across’s official X account: At approximately 02:45 Beijing time on November 11 (18:45 UTC on November 10), attackers gained control of across.to through a social engineering attack targeting domain registrar Namecheap and redirected visitors to a phishing page.
1. The team said it received an alert within about 15 minutes and took the site offline. Security response organization SEAL911 helped flag the phishing site to major wallets. Cloudflare marked the domain as high risk and subsequently removed its DNS records.
2. The official team said some users who visited the website before Cloudflare fully blocked it may have been affected; users of third-party integrations and APIs were not affected. The team has not yet disclosed the losses or number of affected users. The Block cited security platform GoPlus’s estimate that losses totaled about $350,000, involving networks including $ETH , Arbitrum, Base, and BNB Chain. The phishing page tricked users into signing fraudulent approvals.
3. At approximately 09:16 that morning, the official team announced that it had recovered the domain with the help of Namecheap’s founder and that systems were back to normal. It will fully compensate affected users and publish a comprehensive postmortem report in the coming days. Please communicate only through official channels, and do not trust unsolicited direct messages or links.
$ACX $ETH $BNB
For informational purposes only; not investment advice. DYOR. Use official channels only, and do not click unfamiliar claim links.
#Across #ACX #安全 #跨链 #Phishing
According to Across’s official X account: At approximately 02:45 Beijing time on November 11 (18:45 UTC on November 10), attackers gained control of across.to through a social engineering attack targeting domain registrar Namecheap and redirected visitors to a phishing page.
1. The team said it received an alert within about 15 minutes and took the site offline. Security response organization SEAL911 helped flag the phishing site to major wallets. Cloudflare marked the domain as high risk and subsequently removed its DNS records.
2. The official team said some users who visited the website before Cloudflare fully blocked it may have been affected; users of third-party integrations and APIs were not affected. The team has not yet disclosed the losses or number of affected users. The Block cited security platform GoPlus’s estimate that losses totaled about $350,000, involving networks including $ETH , Arbitrum, Base, and BNB Chain. The phishing page tricked users into signing fraudulent approvals.
3. At approximately 09:16 that morning, the official team announced that it had recovered the domain with the help of Namecheap’s founder and that systems were back to normal. It will fully compensate affected users and publish a comprehensive postmortem report in the coming days. Please communicate only through official channels, and do not trust unsolicited direct messages or links.
$ACX $ETH $BNB
For informational purposes only; not investment advice. DYOR. Use official channels only, and do not click unfamiliar claim links.
#Across #ACX #安全 #跨链 #Phishing
52

Across restores its system after a domain takeover
- Cross-chain protocol Across restored its system after its official domain was taken over.
- The attacker used social engineering to target domain registrar Namecheap and gain control of Across’s domain.
- The RSS source has not provided further details about the timing, damages, or specific remediation measures.
#BinanceSquare #CryptoNews #Across #Security
$btc $eth
#vlikevn Titanbot
Source: The Block
Across restores its system after a domain takeover
- Cross-chain protocol Across restored its system after its official domain was taken over.
- The attacker used social engineering to target domain registrar Namecheap and gain control of Across’s domain.
- The RSS source has not provided further details about the timing, damages, or specific remediation measures.
#BinanceSquare #CryptoNews #Across #Security
$btc $eth
#vlikevn Titanbot
Source: The Block
- Cross-chain protocol Across restored its system after its official domain was taken over.
- The attacker used social engineering to target domain registrar Namecheap and gain control of Across’s domain.
- The RSS source has not provided further details about the timing, damages, or specific remediation measures.
#BinanceSquare #CryptoNews #Across #Security
$btc $eth
#vlikevn Titanbot
Source: The Block
86

The domain of Across, a cross-chain protocol, was hijacked. Its frontend and API have been urgently suspended.
Incident timeline (Beijing time):
At around 02:45 a.m., attackers used social engineering against domain registrar Namecheap to take control of Across’s official website domain. The team received an alert within 15 minutes and began taking the site offline. SEAL911 coordinated with major wallets to flag the domain as a phishing site, and Cloudflare subsequently removed its DNS records. As of the announcement, the phishing page is no longer accessible.
Scope of impact: Users who visited the official website before the phishing page was fully blocked may be affected. Users who visited the site before the attack, as well as those who used the protocol only through its API or third-party integrations, are not affected.
The team has committed to fully compensating affected users and recommends using the wallet connected at the time to visit Revoke.cash and revoke the relevant permissions granted that day.
This attack did not target the smart contracts. Instead, it exploited the off-chain entry point of the domain registrar—a reminder for the entire industry: even with robust protocol code, a single social engineering attack on a registrar account can turn an official website into a phishing page. Namecheap has not yet responded. The frontend and API will remain suspended until the domain is confirmed secure. The team will publish a full postmortem later.
#跨链安全 #Across #Phishing attack
The domain of Across, a cross-chain protocol, was hijacked. Its frontend and API have been urgently suspended.
Incident timeline (Beijing time):
At around 02:45 a.m., attackers used social engineering against domain registrar Namecheap to take control of Across’s official website domain. The team received an alert within 15 minutes and began taking the site offline. SEAL911 coordinated with major wallets to flag the domain as a phishing site, and Cloudflare subsequently removed its DNS records. As of the announcement, the phishing page is no longer accessible.
Scope of impact: Users who visited the official website before the phishing page was fully blocked may be affected. Users who visited the site before the attack, as well as those who used the protocol only through its API or third-party integrations, are not affected.
The team has committed to fully compensating affected users and recommends using the wallet connected at the time to visit Revoke.cash and revoke the relevant permissions granted that day.
This attack did not target the smart contracts. Instead, it exploited the off-chain entry point of the domain registrar—a reminder for the entire industry: even with robust protocol code, a single social engineering attack on a registrar account can turn an official website into a phishing page. Namecheap has not yet responded. The frontend and API will remain suspended until the domain is confirmed secure. The team will publish a full postmortem later.
#跨链安全 #Across #Phishing attack
Incident timeline (Beijing time):
At around 02:45 a.m., attackers used social engineering against domain registrar Namecheap to take control of Across’s official website domain. The team received an alert within 15 minutes and began taking the site offline. SEAL911 coordinated with major wallets to flag the domain as a phishing site, and Cloudflare subsequently removed its DNS records. As of the announcement, the phishing page is no longer accessible.
Scope of impact: Users who visited the official website before the phishing page was fully blocked may be affected. Users who visited the site before the attack, as well as those who used the protocol only through its API or third-party integrations, are not affected.
The team has committed to fully compensating affected users and recommends using the wallet connected at the time to visit Revoke.cash and revoke the relevant permissions granted that day.
This attack did not target the smart contracts. Instead, it exploited the off-chain entry point of the domain registrar—a reminder for the entire industry: even with robust protocol code, a single social engineering attack on a registrar account can turn an official website into a phishing page. Namecheap has not yet responded. The frontend and API will remain suspended until the domain is confirmed secure. The team will publish a full postmortem later.
#跨链安全 #Across #Phishing attack
3

·
--
Across domain hijacked: If you’ve used across.to, revoke your approvals and don’t visit the official site for now
At around 2:45 a.m. this morning (Hong Kong time), the official website of cross-chain bridge Across, across.to, was taken over by an outside party and briefly replaced with a phishing page. The team said the domain registrar Namecheap was hit by a social engineering attack, allowing the attackers to take control of the domain. The team received an alert about 15 minutes later and took the site offline. SEAL911 subsequently flagged it as a phishing site, and Cloudflare removed its DNS records. The phishing page can no longer be accessed.
Who may be affected: The team says some users may have been affected if they visited across.to before it was taken offline and connected a wallet or signed an approval there. Users who accessed the service only through third-party integrations or the API are not affected, according to the team. This was not an exchange hack, nor is it a confirmed smart contract vulnerability. The team has not yet disclosed the amount of any losses. Some users online say their funds were transferred, but this has not been independently verified.
The team says it will compensate all affected users and recommends first revoking relevant approvals at revoke.cash—simply disconnecting your wallet does not automatically cancel approvals. The frontend and API will remain offline until the domain is secure again. Namecheap has not yet made a public statement, so don’t visit across.to or sign anything there for now.
Have you visited across.to recently and signed a transaction there?
Not investment advice.
Source: Across official X account (approximately 2026-11-11 02:45–08:14 HKT); reported by PANews and Odaily · approximately 2026-11-11 09:30 HKT
#Across #跨链桥 #钓鱼 #夯B媒体 $ACX
Across domain hijacked: If you’ve used across.to, revoke your approvals and don’t visit the official site for now
At around 2:45 a.m. this morning (Hong Kong time), the official website of cross-chain bridge Across, across.to, was taken over by an outside party and briefly replaced with a phishing page. The team said the domain registrar Namecheap was hit by a social engineering attack, allowing the attackers to take control of the domain. The team received an alert about 15 minutes later and took the site offline. SEAL911 subsequently flagged it as a phishing site, and Cloudflare removed its DNS records. The phishing page can no longer be accessed.
Who may be affected: The team says some users may have been affected if they visited across.to before it was taken offline and connected a wallet or signed an approval there. Users who accessed the service only through third-party integrations or the API are not affected, according to the team. This was not an exchange hack, nor is it a confirmed smart contract vulnerability. The team has not yet disclosed the amount of any losses. Some users online say their funds were transferred, but this has not been independently verified.
The team says it will compensate all affected users and recommends first revoking relevant approvals at revoke.cash—simply disconnecting your wallet does not automatically cancel approvals. The frontend and API will remain offline until the domain is secure again. Namecheap has not yet made a public statement, so don’t visit across.to or sign anything there for now.
Have you visited across.to recently and signed a transaction there?
Not investment advice.
Source: Across official X account (approximately 2026-11-11 02:45–08:14 HKT); reported by PANews and Odaily · approximately 2026-11-11 09:30 HKT
#Across #跨链桥 #钓鱼 #夯B媒体 $ACX
At around 2:45 a.m. this morning (Hong Kong time), the official website of cross-chain bridge Across, across.to, was taken over by an outside party and briefly replaced with a phishing page. The team said the domain registrar Namecheap was hit by a social engineering attack, allowing the attackers to take control of the domain. The team received an alert about 15 minutes later and took the site offline. SEAL911 subsequently flagged it as a phishing site, and Cloudflare removed its DNS records. The phishing page can no longer be accessed.
Who may be affected: The team says some users may have been affected if they visited across.to before it was taken offline and connected a wallet or signed an approval there. Users who accessed the service only through third-party integrations or the API are not affected, according to the team. This was not an exchange hack, nor is it a confirmed smart contract vulnerability. The team has not yet disclosed the amount of any losses. Some users online say their funds were transferred, but this has not been independently verified.
The team says it will compensate all affected users and recommends first revoking relevant approvals at revoke.cash—simply disconnecting your wallet does not automatically cancel approvals. The frontend and API will remain offline until the domain is secure again. Namecheap has not yet made a public statement, so don’t visit across.to or sign anything there for now.
Have you visited across.to recently and signed a transaction there?
Not investment advice.
Source: Across official X account (approximately 2026-11-11 02:45–08:14 HKT); reported by PANews and Odaily · approximately 2026-11-11 09:30 HKT
#Across #跨链桥 #钓鱼 #夯B媒体 $ACX
forrestbit:
官网收回了,窗口期内签过的授权也不会自己消失。先自己查并撤掉异常许可;赔付只走官方渠道,私信里的「加速领取」别点。
1
94

·
--
The official website was hijacked.
At 03:05 on November 11 (UTC+8), the official account of cross-chain protocol Across issued an urgent warning: Don’t open the app, connect your wallet, or sign or authorize anything on the site. At the time, the team only said it was investigating a domain issue. At 06:13 that same day, the team provided more details: At around 02:45, domain registrar Namecheap was hit by a social engineering attack, and the attackers gained control of Across’s domain. The team received an alert within 15 minutes and immediately began taking the site offline. Security organization SEAL911 flagged across.to as a phishing site, and Cloudflare subsequently helped mark the domain as risky and revoke its DNS records. The team said that by the time of its post, the site had been completely taken offline and the phishing page was no longer accessible.
The team also said that during the brief period before Cloudflare fully blocked the phishing page, some users who had visited across.to may have been affected. Third-party integrations and API users were not affected, and users who had used the frontend before the attack were also safe. Anyone who thinks they were affected can send the official account a private message on X with their transaction details. The team promised to reimburse affected users and recommended using the wallet they had connected at the time to revoke.cash to revoke any approvals granted during the attack. The team has not yet disclosed the amount of losses. It said the registrar has not yet provided an effective response, and the frontend and API will remain offline until the domain is securely back under its control.
#Across #安全 is not investment advice
The official website was hijacked.
At 03:05 on November 11 (UTC+8), the official account of cross-chain protocol Across issued an urgent warning: Don’t open the app, connect your wallet, or sign or authorize anything on the site. At the time, the team only said it was investigating a domain issue. At 06:13 that same day, the team provided more details: At around 02:45, domain registrar Namecheap was hit by a social engineering attack, and the attackers gained control of Across’s domain. The team received an alert within 15 minutes and immediately began taking the site offline. Security organization SEAL911 flagged across.to as a phishing site, and Cloudflare subsequently helped mark the domain as risky and revoke its DNS records. The team said that by the time of its post, the site had been completely taken offline and the phishing page was no longer accessible.
The team also said that during the brief period before Cloudflare fully blocked the phishing page, some users who had visited across.to may have been affected. Third-party integrations and API users were not affected, and users who had used the frontend before the attack were also safe. Anyone who thinks they were affected can send the official account a private message on X with their transaction details. The team promised to reimburse affected users and recommended using the wallet they had connected at the time to revoke.cash to revoke any approvals granted during the attack. The team has not yet disclosed the amount of losses. It said the registrar has not yet provided an effective response, and the frontend and API will remain offline until the domain is securely back under its control.
#Across #安全 is not investment advice
At 03:05 on November 11 (UTC+8), the official account of cross-chain protocol Across issued an urgent warning: Don’t open the app, connect your wallet, or sign or authorize anything on the site. At the time, the team only said it was investigating a domain issue. At 06:13 that same day, the team provided more details: At around 02:45, domain registrar Namecheap was hit by a social engineering attack, and the attackers gained control of Across’s domain. The team received an alert within 15 minutes and immediately began taking the site offline. Security organization SEAL911 flagged across.to as a phishing site, and Cloudflare subsequently helped mark the domain as risky and revoke its DNS records. The team said that by the time of its post, the site had been completely taken offline and the phishing page was no longer accessible.
The team also said that during the brief period before Cloudflare fully blocked the phishing page, some users who had visited across.to may have been affected. Third-party integrations and API users were not affected, and users who had used the frontend before the attack were also safe. Anyone who thinks they were affected can send the official account a private message on X with their transaction details. The team promised to reimburse affected users and recommended using the wallet they had connected at the time to revoke.cash to revoke any approvals granted during the attack. The team has not yet disclosed the amount of losses. It said the registrar has not yet provided an effective response, and the frontend and API will remain offline until the domain is securely back under its control.
#Across #安全 is not investment advice
267

🚨 Cross-chain bridge Across issues security warning: Do not use its app for now, multiple users report stolen wallets
Cross-chain bridge protocol Across warned users on X on Tuesday not to access its app or connect their wallets for the time being, and not to sign any transactions or grant any approvals until further notice. The team is investigating a security incident that may have affected its domain.
Across has not disclosed the nature of the incident or confirmed whether its website was compromised. Some users on X said they lost $9,000 in USDC, while another said they lost 7,053 USDT0 across seven transactions on the Plasma chain. Others suspect the website has been compromised. Across has asked affected users to provide transaction details to aid the investigation. The reported losses have not been independently verified.
⭐ A hijacked cross-chain bridge frontend or domain can directly trick users into signing malicious approvals. Users who have recently used Across should check for and revoke suspicious approvals, and wait for the official warning to be lifted before interacting with the app again.
#Across #跨链桥 #安全事件 #DeFi
🚨 Cross-chain bridge Across issues security warning: Do not use its app for now, multiple users report stolen wallets
Cross-chain bridge protocol Across warned users on X on Tuesday not to access its app or connect their wallets for the time being, and not to sign any transactions or grant any approvals until further notice. The team is investigating a security incident that may have affected its domain.
Across has not disclosed the nature of the incident or confirmed whether its website was compromised. Some users on X said they lost $9,000 in USDC, while another said they lost 7,053 USDT0 across seven transactions on the Plasma chain. Others suspect the website has been compromised. Across has asked affected users to provide transaction details to aid the investigation. The reported losses have not been independently verified.
⭐ A hijacked cross-chain bridge frontend or domain can directly trick users into signing malicious approvals. Users who have recently used Across should check for and revoke suspicious approvals, and wait for the official warning to be lifted before interacting with the app again.
#Across #跨链桥 #安全事件 #DeFi
Cross-chain bridge protocol Across warned users on X on Tuesday not to access its app or connect their wallets for the time being, and not to sign any transactions or grant any approvals until further notice. The team is investigating a security incident that may have affected its domain.
Across has not disclosed the nature of the incident or confirmed whether its website was compromised. Some users on X said they lost $9,000 in USDC, while another said they lost 7,053 USDT0 across seven transactions on the Plasma chain. Others suspect the website has been compromised. Across has asked affected users to provide transaction details to aid the investigation. The reported losses have not been independently verified.
⭐ A hijacked cross-chain bridge frontend or domain can directly trick users into signing malicious approvals. Users who have recently used Across should check for and revoke suspicious approvals, and wait for the official warning to be lifted before interacting with the app again.
#Across #跨链桥 #安全事件 #DeFi
1

·
--
Across has just issued a warning: don’t use its app for now, don’t connect your wallet, don’t sign anything, and don’t approve any permissions. It’s investigating a suspected security incident. Some users say their wallets were drained after using the bridge: one reported losing 9,000 USDC, and another said 7 transactions transferred out 7,053 USDT0. The team is looking into it, and Cointelegraph has not independently verified the reports. The bridge has processed more than $40 billion in total, so when a warning like this comes out, nobody wants to gamble that it’s a false alarm. If you’ve granted Across permissions, check them and revoke any you don’t need. Don’t wait for confirmation and regret it later. Would you still dare to use a cross-chain bridge these days?
#Across #跨链桥 #安全预警 #钱包安全 #DeFi
Across has just issued a warning: don’t use its app for now, don’t connect your wallet, don’t sign anything, and don’t approve any permissions. It’s investigating a suspected security incident. Some users say their wallets were drained after using the bridge: one reported losing 9,000 USDC, and another said 7 transactions transferred out 7,053 USDT0. The team is looking into it, and Cointelegraph has not independently verified the reports. The bridge has processed more than $40 billion in total, so when a warning like this comes out, nobody wants to gamble that it’s a false alarm. If you’ve granted Across permissions, check them and revoke any you don’t need. Don’t wait for confirmation and regret it later. Would you still dare to use a cross-chain bridge these days?
#Across #跨链桥 #安全预警 #钱包安全 #DeFi
#Across #跨链桥 #安全预警 #钱包安全 #DeFi
33
·
--
【Cross-chain bridge Across website issue! Official urgent warning: Don’t open it, connect your wallet, or sign】
At around 3 a.m. Beijing time on November 11, cross-chain bridge Across issued an alert saying there was an issue with its official website domain and that it was investigating. Users were told not to visit the website, connect their wallets, or sign any transactions or approvals until further notice. Several users have already reported in the comments that their wallets were drained. If you used the Across website during this period, check your wallet and revoke any unfamiliar approvals as soon as possible.
#Across #跨链桥 #WalletSecurity
【Cross-chain bridge Across website issue! Official urgent warning: Don’t open it, connect your wallet, or sign】
At around 3 a.m. Beijing time on November 11, cross-chain bridge Across issued an alert saying there was an issue with its official website domain and that it was investigating. Users were told not to visit the website, connect their wallets, or sign any transactions or approvals until further notice. Several users have already reported in the comments that their wallets were drained. If you used the Across website during this period, check your wallet and revoke any unfamiliar approvals as soon as possible.
#Across #跨链桥 #WalletSecurity
At around 3 a.m. Beijing time on November 11, cross-chain bridge Across issued an alert saying there was an issue with its official website domain and that it was investigating. Users were told not to visit the website, connect their wallets, or sign any transactions or approvals until further notice. Several users have already reported in the comments that their wallets were drained. If you used the Across website during this period, check your wallet and revoke any unfamiliar approvals as soon as possible.
#Across #跨链桥 #WalletSecurity
40
In the cross-chain bridge sector, Across Protocol has always kept a low profile. It relies on UMA’s optimistic oracle and uses an intent-based matching model to move funds across chains. $ACX is the protocol’s governance token.
Here’s a recent snapshot of on-chain data: the price is around $0.0434, 24-hour trading volume is about $1.48 million, and circulating market cap is roughly $31.49 million. Trading volume is notably low relative to market cap, and there has been almost no market discussion recently, putting it in a typical lull.
A lull doesn’t mean opportunity, let alone safety. For low-profile assets like this, the metrics worth tracking are cross-chain transfer volume, routing fee revenue, the pace of new integrations, and token unlocks and staking ratios. Doing your fundamental research before the narrative takes off is the right way to approach overlooked assets.
#跨链桥 #Across #OnChainWatch
In the cross-chain bridge sector, Across Protocol has always kept a low profile. It relies on UMA’s optimistic oracle and uses an intent-based matching model to move funds across chains. $ACX is the protocol’s governance token.
Here’s a recent snapshot of on-chain data: the price is around $0.0434, 24-hour trading volume is about $1.48 million, and circulating market cap is roughly $31.49 million. Trading volume is notably low relative to market cap, and there has been almost no market discussion recently, putting it in a typical lull.
A lull doesn’t mean opportunity, let alone safety. For low-profile assets like this, the metrics worth tracking are cross-chain transfer volume, routing fee revenue, the pace of new integrations, and token unlocks and staking ratios. Doing your fundamental research before the narrative takes off is the right way to approach overlooked assets.
#跨链桥 #Across #OnChainWatch
Here’s a recent snapshot of on-chain data: the price is around $0.0434, 24-hour trading volume is about $1.48 million, and circulating market cap is roughly $31.49 million. Trading volume is notably low relative to market cap, and there has been almost no market discussion recently, putting it in a typical lull.
A lull doesn’t mean opportunity, let alone safety. For low-profile assets like this, the metrics worth tracking are cross-chain transfer volume, routing fee revenue, the pace of new integrations, and token unlocks and staking ratios. Doing your fundamental research before the narrative takes off is the right way to approach overlooked assets.
#跨链桥 #Across #OnChainWatch

·
--
The cross-chain sector has been relatively quiet lately, but a lull in the data can actually be a good time to take a closer look at fundamentals. $ACX is the native token of Across Protocol, which focuses on fast, intent-based cross-chain bridging. It routes funds using an optimistic oracle mechanism, and its speed and user experience for transfers across Layer 2 networks have long been its defining features.
On-chain snapshot: The current price is around $0.045, with a market cap of about $32.71 million, while 24-hour trading volume is only around $156,000—clear signs of subdued activity. This suggests market attention is low, and short-term price swings are more easily driven by small amounts of capital. Chasing rallies or selling into declines is not especially attractive in this environment.
There are three things worth tracking next: First, whether actual cross-chain bridge usage and fee revenue can recover as ecosystem activity picks up. Second, the pace at which the protocol integrates with new chains and Rollups—the broader its routing coverage, the easier it is to build network effects. Third, whether token utility measures such as staking lockups or fee sharing are actually implemented.
When there is no compelling narrative, prices often reflect expectations in advance, but they are also more easily overlooked by the market. With small-cap cross-chain assets like this, verify real business data before deciding whether to invest. Managing position size is always more important than guessing the direction.
#跨链 #Layer2 #Across
The cross-chain sector has been relatively quiet lately, but a lull in the data can actually be a good time to take a closer look at fundamentals. $ACX is the native token of Across Protocol, which focuses on fast, intent-based cross-chain bridging. It routes funds using an optimistic oracle mechanism, and its speed and user experience for transfers across Layer 2 networks have long been its defining features.
On-chain snapshot: The current price is around $0.045, with a market cap of about $32.71 million, while 24-hour trading volume is only around $156,000—clear signs of subdued activity. This suggests market attention is low, and short-term price swings are more easily driven by small amounts of capital. Chasing rallies or selling into declines is not especially attractive in this environment.
There are three things worth tracking next: First, whether actual cross-chain bridge usage and fee revenue can recover as ecosystem activity picks up. Second, the pace at which the protocol integrates with new chains and Rollups—the broader its routing coverage, the easier it is to build network effects. Third, whether token utility measures such as staking lockups or fee sharing are actually implemented.
When there is no compelling narrative, prices often reflect expectations in advance, but they are also more easily overlooked by the market. With small-cap cross-chain assets like this, verify real business data before deciding whether to invest. Managing position size is always more important than guessing the direction.
#跨链 #Layer2 #Across
On-chain snapshot: The current price is around $0.045, with a market cap of about $32.71 million, while 24-hour trading volume is only around $156,000—clear signs of subdued activity. This suggests market attention is low, and short-term price swings are more easily driven by small amounts of capital. Chasing rallies or selling into declines is not especially attractive in this environment.
There are three things worth tracking next: First, whether actual cross-chain bridge usage and fee revenue can recover as ecosystem activity picks up. Second, the pace at which the protocol integrates with new chains and Rollups—the broader its routing coverage, the easier it is to build network effects. Third, whether token utility measures such as staking lockups or fee sharing are actually implemented.
When there is no compelling narrative, prices often reflect expectations in advance, but they are also more easily overlooked by the market. With small-cap cross-chain assets like this, verify real business data before deciding whether to invest. Managing position size is always more important than guessing the direction.
#跨链 #Layer2 #Across
3
·
--
When the market is quiet, it’s worth paying closer attention to the actual use of infrastructure. $ACX is the ecosystem token of Across Protocol, a protocol focused on cross-chain transfers and liquidity aggregation. It is currently priced at around $0.0436, with a market cap of approximately $31.63 million and 24-hour trading volume of about $195,000. Turnover is low, and community discussion is limited.
Low attention doesn’t mean there’s no value, but it may also mean greater volatility. Going forward, watch cross-chain transaction volume, liquidity incentives, and the pace of deployments on new chains. A sustained increase in trading volume would indicate that the market is reassessing the asset; until then, patience is more important than chasing a rally.
#Across #Cross-chain
When the market is quiet, it’s worth paying closer attention to the actual use of infrastructure. $ACX is the ecosystem token of Across Protocol, a protocol focused on cross-chain transfers and liquidity aggregation. It is currently priced at around $0.0436, with a market cap of approximately $31.63 million and 24-hour trading volume of about $195,000. Turnover is low, and community discussion is limited.
Low attention doesn’t mean there’s no value, but it may also mean greater volatility. Going forward, watch cross-chain transaction volume, liquidity incentives, and the pace of deployments on new chains. A sustained increase in trading volume would indicate that the market is reassessing the asset; until then, patience is more important than chasing a rally.
#Across #Cross-chain
Low attention doesn’t mean there’s no value, but it may also mean greater volatility. Going forward, watch cross-chain transaction volume, liquidity incentives, and the pace of deployments on new chains. A sustained increase in trading volume would indicate that the market is reassessing the asset; until then, patience is more important than chasing a rally.
#Across #Cross-chain
30
·
--
When the market is quiet, it can be a good time to look at cross-chain infrastructure that isn’t getting much attention. $ACX is the token of Across Protocol, currently quoted at around $0.0436, with a market cap of about $31.63 million and 24-hour trading volume of roughly $195,000. The data is straightforward: low interest, weak turnover, and few clear short-term catalysts.
But what matters in the cross-chain sector isn’t social buzz—it’s reliable settlement, how quickly assets arrive, the range of supported chains, and actual fee revenue. If the protocol’s bridging volume keeps growing, the token’s valuation may have firmer support; if trading remains subdued for a long time, price swings can easily be amplified.
Small-cap assets like this are better approached by tracking on-chain data first and then deciding whether to participate, rather than rushing into a large contrarian position just because “nobody is talking about it.” Be patient and wait for confirmation from trading volume, bridge usage, or ecosystem news.
#Across #跨链 #DeFi
When the market is quiet, it can be a good time to look at cross-chain infrastructure that isn’t getting much attention. $ACX is the token of Across Protocol, currently quoted at around $0.0436, with a market cap of about $31.63 million and 24-hour trading volume of roughly $195,000. The data is straightforward: low interest, weak turnover, and few clear short-term catalysts.
But what matters in the cross-chain sector isn’t social buzz—it’s reliable settlement, how quickly assets arrive, the range of supported chains, and actual fee revenue. If the protocol’s bridging volume keeps growing, the token’s valuation may have firmer support; if trading remains subdued for a long time, price swings can easily be amplified.
Small-cap assets like this are better approached by tracking on-chain data first and then deciding whether to participate, rather than rushing into a large contrarian position just because “nobody is talking about it.” Be patient and wait for confirmation from trading volume, bridge usage, or ecosystem news.
#Across #跨链 #DeFi
But what matters in the cross-chain sector isn’t social buzz—it’s reliable settlement, how quickly assets arrive, the range of supported chains, and actual fee revenue. If the protocol’s bridging volume keeps growing, the token’s valuation may have firmer support; if trading remains subdued for a long time, price swings can easily be amplified.
Small-cap assets like this are better approached by tracking on-chain data first and then deciding whether to participate, rather than rushing into a large contrarian position just because “nobody is talking about it.” Be patient and wait for confirmation from trading volume, bridge usage, or ecosystem news.
#Across #跨链 #DeFi
27

·
--
5M ACX and $0.04375. While Polymarket hints at its own token, Across is offering a way out of its own
The first is the threshold for swapping tokens directly for shares.
The second is the price at which you can simply sell ACX for USDC instead of swapping.
Through an SPV, you can get shares with as little as 250k ACX, but spots are limited to the first 100 US investors and around 500 others.
Centrifuge is also 1:1: directly from 100000 $CFG
{future}(CFGUSDT)
, smaller amounts go through the CoinList trust. The CP172 vote passed, but the swap isn’t available yet.
CoinGecko calculates that from January 2025 to February 2026, fewer than 10% of tokens on top exchanges closed in profit. A share looks fairer than a token, but only for those who meet the threshold.
Meanwhile, Polymarket’s CEO is talking about an onchain asset. There’s no token: no name, ticker, or date. There are POLY trademarks.
In short, “token → stock” is a door for funds. Small bags can’t fit through it; a buyback is all that’s left for them.
#Polymarket #Across
5M ACX and $0.04375. While Polymarket hints at its own token, Across is offering a way out of its own
The first is the threshold for swapping tokens directly for shares.
The second is the price at which you can simply sell ACX for USDC instead of swapping.
Through an SPV, you can get shares with as little as 250k ACX, but spots are limited to the first 100 US investors and around 500 others.
Centrifuge is also 1:1: directly from 100000 $CFG
, smaller amounts go through the CoinList trust. The CP172 vote passed, but the swap isn’t available yet.
CoinGecko calculates that from January 2025 to February 2026, fewer than 10% of tokens on top exchanges closed in profit. A share looks fairer than a token, but only for those who meet the threshold.
Meanwhile, Polymarket’s CEO is talking about an onchain asset. There’s no token: no name, ticker, or date. There are POLY trademarks.
In short, “token → stock” is a door for funds. Small bags can’t fit through it; a buyback is all that’s left for them.
#Polymarket #Across
The first is the threshold for swapping tokens directly for shares.
The second is the price at which you can simply sell ACX for USDC instead of swapping.
Through an SPV, you can get shares with as little as 250k ACX, but spots are limited to the first 100 US investors and around 500 others.
Centrifuge is also 1:1: directly from 100000 $CFG
, smaller amounts go through the CoinList trust. The CP172 vote passed, but the swap isn’t available yet.
CoinGecko calculates that from January 2025 to February 2026, fewer than 10% of tokens on top exchanges closed in profit. A share looks fairer than a token, but only for those who meet the threshold.
Meanwhile, Polymarket’s CEO is talking about an onchain asset. There’s no token: no name, ticker, or date. There are POLY trademarks.
In short, “token → stock” is a door for funds. Small bags can’t fit through it; a buyback is all that’s left for them.
#Polymarket #Across
181
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CryptoSelloffTriggersMultipleWhaleLiquidations
70,774 views
889 Discussing
2
#USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
90,052 views
1,042 Discussing
3
#WillFOMCMinutesReinforceRateHikeExpectations?
16,630 views
367 Discussing
4
#BitcoinActiveSupplyInProfitDropsBelow45%
160,322 views
1,382 Discussing
5
#TONStrategyReports$23.97MQ3NetLoss
15,881 views
110 Discussing
6
#KavaSaysAbnormalActivityLimitedToKavaLend
104,560 views
759 Discussing
7
#WORPTLetsTouristsConvertCryptoToThaiBaht
28,775 views
275 Discussing
8
#WhoWillSucceedJensenHuangatNvidia?
287,001 views
2,024 Discussing
9
#WhatWillDriveCryptoandStocks’NextRebound?
773,095 views
3,824 Discussing
10
#TradFiForBeginners
803,345 views
4,821 Discussing