

#dns
dns
4,685 views
19 Discussing
Hot
Latest

·
--
$TON DOMAIN REGISTRY REMOVES T.ME FROM GLOBAL DNS — WHAT IT MEANS FOR CRYPTO USERS 🔥
Telegram's core domain t.me was flagged as serverHold by the .me registry on July 14th, rendering all t.me links inaccessible. The cause remains unexplained by Telegram, the registry, or Identity Digital.
This directly impacts countless crypto communities that rely on Telegram for group chats, bots, and signal channels. If the issue persists, liquidity flow and information dissemination could be disrupted across multiple projects. Are you seeing any impact on your Telegram groups yet?
Not financial advice. Always manage your risk.
#TON #Telegram #DNS #CryptoCommunity
🔥
98
·
--
Weekend security alert: Front ends of at least 12 DeFi/token launch sites injected with StepDrainer
1. Security firm Blockaid disclosed that between October 30 and 31, the front ends of at least 12 decentralized finance and token launch sites were infected with the StepDrainer toolkit. GoPlus also warned that sites including Flap and Kintsu had been spoofed through DNS hijacking.
2. The attack did not modify smart contracts. Instead, tampered official website domains were used to lure users into “connecting wallets / signing / granting unlimited approvals.” The attackers targeted approvals and signatures, not private keys directly.
3. StonkFun’s operators said the site had been restored and that no on-chain losses had been reported. Kintsu and others also said they had switched back, but DNS caches may mean malicious pages remain visible for a short time.
4. Check your activity: If you connected to any affected site during the suspicious period, revoke your approvals as soon as possible using tools such as Revoke.cash. Never click unfamiliar “claim/verify” pop-ups.$ETH $BNB
For informational purposes only; not investment advice. DYOR. Use official channels only, and don’t click unfamiliar claim links.
#安全 #DeFi #DNS #Web3 #BNB
146
·
--
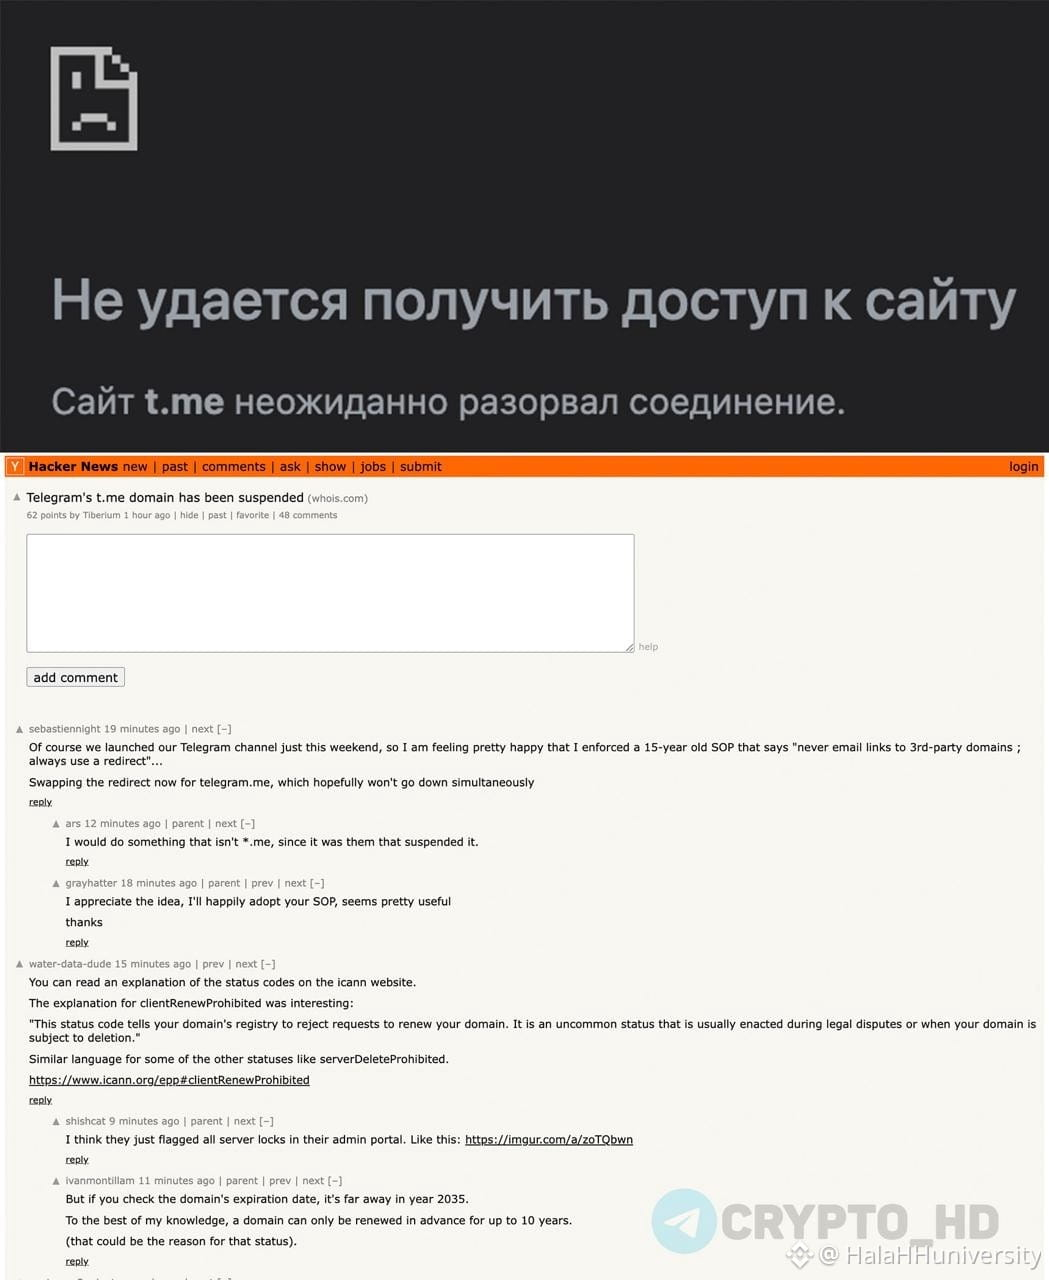
⚠️ Issues affecting #تليجرام ...
The main domain t.me user for the shortened links on Telegram has been set to serverHold after the .me domain operator disconnected it from the #DNS system
And with a cache update, links to channels, posts, chats, and bots may stop working. The reason for these restrictions is still unknown, and Telegram has not issued any official comment so far.
$TON
1
290
·
--
⚠️ URGENT WARNING: eth.limo DNS Under Attack ⚠️
Vitalik Buterin warns everyone to STOP accessing vitalik.eth.limo and all eth.limo sites immediately 🛑
Hackers may redirect users to fake/phishing sites to steal funds or data 🕳️🔴
✅ Safe Alternative:
Access content via IPFS directly instead until the issue is fixed ✅
Stay safe and double-check your URLs! 🔒👀
$ETH $ENS
#Vitalik #Ethereum #SecurityWarning #DNS #CryptoNews
142

$ZBT AND $UTK ARE SHAKING AS TELEGRAM'S DOMAIN GETS PULLED ⚡
The t.me domain just got wiped from global DNS — that's the main gateway into Telegram gone. Market's about to take a heavy hit on sentiment, and bags like $ZBT and $UTK are the first on the chopping block. Volume is already spiking on both pairs as panic bids get smashed.
This isn't just noise — when a major infrastructure piece like this goes dark, MM tends to offload into the fear. The smell of a sell-off is thick right now. Are you locking in stablecoins or trying to catch a bounce here?
Not financial advice. Always manage your risk.
#ZBT #UTK #Telegram #DNS #Crypto
⚡
86
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinanceSAFUFundTransferCompleted7499BTC
0 views
16 Discussing
2
#BinanceRecovery90% of stolen assets
22,053 views
79 Discussing
3
#YiHe:ProofOfReserves:10TokensAt100%Backing
61,282 views
246 Discussing
4
#BackedNotBroken:RichardTengSaysUsersBearNoLoss
3,036 views
130 Discussing
5
#CZSaysCompensationIsinPlaceUsersAreProtected
71,239 views
958 Discussing
6
#IntelHasItsWorstDaySince1974
18,605 views
422 Discussing
7
#TRMCambodianCasinosReceived$1.07BInCrypto
4,320 views
57 Discussing
8
#USDCCirculationFallsAbout800MInSevenDays
39,049 views
572 Discussing
9
#SuspectedNorthKoreaAttacksAccountForNearly89%OfCryptoHackLosses
10,360 views
80 Discussing
10
#OpenAICutsFundraisingTargetBy$10B
2,466 views
65 Discussing