$MEME scored 90/100 on the quick public-risk scan.
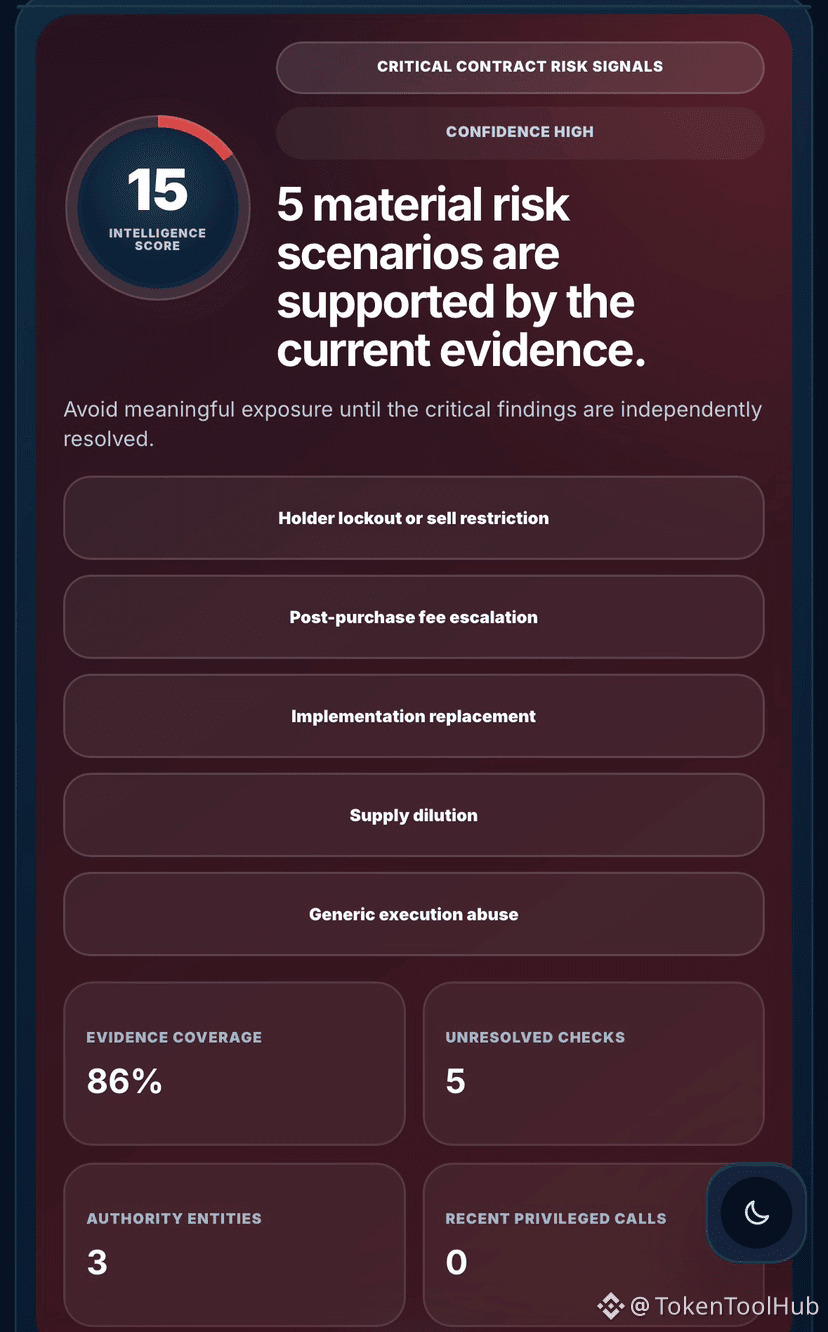
Deeper TokenToolHub contract intelligence returned just 15/100.
Contract:
0xdA2F0859b2C1Faa00018DA1E3D078021589BfFfF
Network: BNB Smart Chain
Five material risk scenarios were identified:
• Possible holder lockout or sell restriction
• Possible supply dilution
• Possible post-purchase fee escalation
• Possible implementation replacement
• Possible generic execution abuse
Key findings:
• Source verified
• Ownership: Renounced
• Proxy: Detected
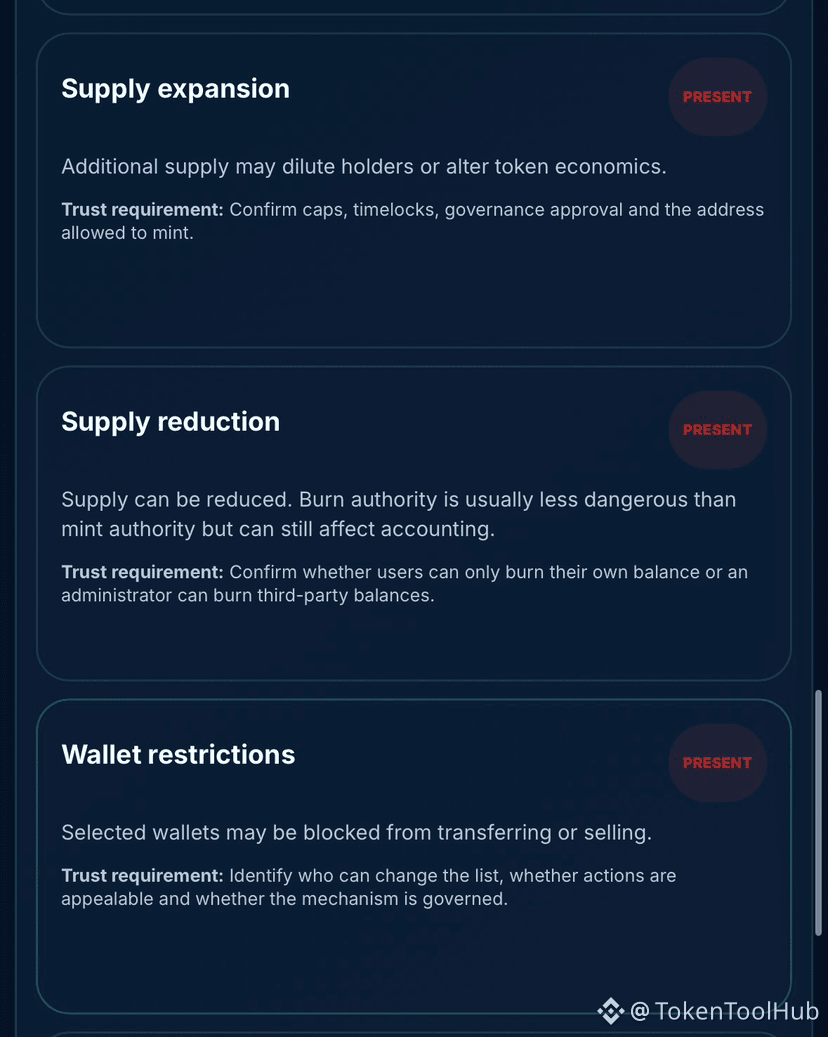
• Supply expansion: Present
• Supply reduction: Present
• Wallet restrictions: Present
• Mutable fees/taxes: Present
• Upgrade authority: Present
• Generic external execution: Present
• Trading switches: Not detected
• Transaction/wallet limits: Not detected
• Emergency pause: Not detected
Ownership currently resolves to the zero address.
But $MEME is also upgradeable.
Resolved implementation:
0x7330d8865f4b6800b72bdd73e2007833a5d45c94
The proxy administrator could not be resolved.
That distinction is critical.
Renouncing owner() does not necessarily make an upgradeable contract immutable.
If another authority controls the proxy, the implementation logic may still be replaced.
The verified code also exposes wallet-restriction capability.
That means selected addresses could potentially face transfer or sell restrictions depending on how the mechanism is authorized and used.
Supply expansion is also present.
Mutable fees mean transaction costs may potentially change after users enter.
Generic external execution further expands what privileged logic may be able to execute, depending on authorization and callable targets.
Trading simulation was unavailable, so honeypot status, buy tax and sell tax remain unresolved.
Recent contract activity, token-transfer activity and contract creation context were also unavailable.
Full $MEME scan:
https://tokentoolhub.com/token-safety-checker/?net=bsc&address=0xdA2F0859b2C1Faa00018DA1E3D078021589BfFfF
#BNBChain #crypto #Web3 #blockchain #CryptoSecurity
Deeper TokenToolHub contract intelligence returned just 15/100.
Contract:
0xdA2F0859b2C1Faa00018DA1E3D078021589BfFfF
Network: BNB Smart Chain
Five material risk scenarios were identified:
• Possible holder lockout or sell restriction
• Possible supply dilution
• Possible post-purchase fee escalation
• Possible implementation replacement
• Possible generic execution abuse
Key findings:
• Source verified
• Ownership: Renounced
• Proxy: Detected
• Supply expansion: Present
• Supply reduction: Present
• Wallet restrictions: Present
• Mutable fees/taxes: Present
• Upgrade authority: Present
• Generic external execution: Present
• Trading switches: Not detected
• Transaction/wallet limits: Not detected
• Emergency pause: Not detected
Ownership currently resolves to the zero address.
But $MEME is also upgradeable.
Resolved implementation:
0x7330d8865f4b6800b72bdd73e2007833a5d45c94
The proxy administrator could not be resolved.
That distinction is critical.
Renouncing owner() does not necessarily make an upgradeable contract immutable.
If another authority controls the proxy, the implementation logic may still be replaced.
The verified code also exposes wallet-restriction capability.
That means selected addresses could potentially face transfer or sell restrictions depending on how the mechanism is authorized and used.
Supply expansion is also present.
Mutable fees mean transaction costs may potentially change after users enter.
Generic external execution further expands what privileged logic may be able to execute, depending on authorization and callable targets.
Trading simulation was unavailable, so honeypot status, buy tax and sell tax remain unresolved.
Recent contract activity, token-transfer activity and contract creation context were also unavailable.
Full $MEME scan:
https://tokentoolhub.com/token-safety-checker/?net=bsc&address=0xdA2F0859b2C1Faa00018DA1E3D078021589BfFfF
#BNBChain #crypto #Web3 #blockchain #CryptoSecurity