

#criticalvulnerability
criticalvulnerability
146 views
3 Discussing
Hot
Latest
#CriticalVulnerability
🚨 Attention $BTC application developers: critical vulnerability in “bitcoinjs-lib”
Two serious bugs have been fixed in the popular `bitcoinjs-lib` library. These flaws could cause applications to catastrophically underreport miner fees for fully valid, signed PSBT (Partially Signed Bitcoin Transaction) transactions.
What is the issue?
In Bitcoin, the fee is the difference between the sum of the inputs and the sum of the outputs. Two distinct logic errors caused the library to report a minimal fee (e.g., 200 or 1,000 satoshis), while the actual amount deducted from the wallet and paid to miners could be as high as nearly 1 BTC (900 million satoshis).
1. Conflicting Input Values: The signing process utilized the full data from the previous transaction, whereas the fee calculation module relied on a conflicting record with a lower value. While the signature remained valid, the fee calculation was incorrect.
2. Missing Input-Value Records: For finalized inputs where the amount was not specified, the library treated the value as "0." This allowed a massive actual fee to be hidden within imported transactions.
Which versions are affected? v5 series: fixed in
➡️ 5.2.2 (vulnerable: 5.1.0 – 5.2.1)
➡️ v6 series: fixed in 6.1.9 (vulnerable: 6.0.0 – 6.1.8)
➡️ v7 series: fixed in 7.0.4 (vulnerable: 7.0.0-rc.0 – 7.0.3)
What should you do?
➡️ Update to the patched versions (5.2.2, 6.1.9, 7.0.4).
➡️ If updating is not currently possible, implement independent verification of input values and reject any inconsistent entries before signing or calculating fees.
The security of your application depends on whether you blindly trust libraries or verify every single satoshi. 🛡️
{future}(BTCUSDT)
#CriticalVulnerability
🚨 Attention $BTC application developers: critical vulnerability in “bitcoinjs-lib”
Two serious bugs have been fixed in the popular `bitcoinjs-lib` library. These flaws could cause applications to catastrophically underreport miner fees for fully valid, signed PSBT (Partially Signed Bitcoin Transaction) transactions.
What is the issue?
In Bitcoin, the fee is the difference between the sum of the inputs and the sum of the outputs. Two distinct logic errors caused the library to report a minimal fee (e.g., 200 or 1,000 satoshis), while the actual amount deducted from the wallet and paid to miners could be as high as nearly 1 BTC (900 million satoshis).
1. Conflicting Input Values: The signing process utilized the full data from the previous transaction, whereas the fee calculation module relied on a conflicting record with a lower value. While the signature remained valid, the fee calculation was incorrect.
2. Missing Input-Value Records: For finalized inputs where the amount was not specified, the library treated the value as "0." This allowed a massive actual fee to be hidden within imported transactions.
Which versions are affected? v5 series: fixed in
➡️ 5.2.2 (vulnerable: 5.1.0 – 5.2.1)
➡️ v6 series: fixed in 6.1.9 (vulnerable: 6.0.0 – 6.1.8)
➡️ v7 series: fixed in 7.0.4 (vulnerable: 7.0.0-rc.0 – 7.0.3)
What should you do?
➡️ Update to the patched versions (5.2.2, 6.1.9, 7.0.4).
➡️ If updating is not currently possible, implement independent verification of input values and reject any inconsistent entries before signing or calculating fees.
The security of your application depends on whether you blindly trust libraries or verify every single satoshi. 🛡️
1
97
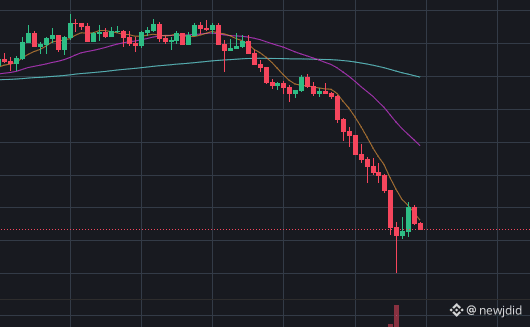
عملة $ZEC ، رائدة عملات الخصوصية على بينانس، انهارت من $629 إلى أقل من $300 في أقل من 24 ساعة! السبب؟ ثغرة خطيرة في بروتوكول Orchard الخاص بالخصوصية كانت موجودة منذ 4 سنوات كاملة، وكان من الممكن نظرياً أن تسمح بطباعة عملات ZEC مزيفة غير قابلة للاكتشاف على السلسلة .
الأسوأ؟ لأنه نظام خصوصية، لا يمكن إثبات أن الثغرة لم تُستغل فعلياً في الماضي . هذا ما دفع آرثر هايز (مؤسس BitMEX) لبيع كل ممتلكاته من ZEC فوراً بعد أن كان من أكبر الداعمين لها
#zec #zcash #PrivacyCoin #CriticalVulnerability
الأسوأ؟ لأنه نظام خصوصية، لا يمكن إثبات أن الثغرة لم تُستغل فعلياً في الماضي . هذا ما دفع آرثر هايز (مؤسس BitMEX) لبيع كل ممتلكاته من ZEC فوراً بعد أن كان من أكبر الداعمين لها
#zec #zcash #PrivacyCoin #CriticalVulnerability
178
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanMicrosoftDeliverOnAI
624,461 views
4,106 Discussing
2
#CanGoogleDefindItsCore
383,835 views
2,889 Discussing
3
#FedWatch
16.1M views
37,237 Discussing
4
#BitcoinCore32.1RaisesPeerConnectionLimit
2,367 views
83 Discussing
5
#EarningsSeason
6.1M views
30,321 Discussing
6
#BitcoinCoreIdentifiesThreeVulnerabilities
12,584 views
265 Discussing
7
#RippleExpects$900MAnnualizedProductRevenueRunRate
1,520 views
10 Discussing
8
#GoogleToPreviewCryptoCustodySecuritySystem
3,814 views
96 Discussing
9
#FedToBeginShrinkingRateSettingCalendarIn2027
4,734 views
59 Discussing
10
#StrategyShareholdersApproveDailyDividends
4,270 views
79 Discussing