
MR WHICK
7.4k Posts
MR WHICK
Report
Block User
THE WORLD BOWS DOWN, IF THERE IS SOMEONE TO MAKE IT BOW 😉
654 Following
29.4K+ Followers
22.9K+ Liked
Posts
All
Videos
·
--
Bearish
₿ Bitcoin: Weakness Today, Opportunity Tomorrow?
Bitcoin is navigating a difficult market, with selling pressure keeping traders cautious. But corrections are also where long-term opportunities begin to form. The key is not predicting the bottom; it’s watching how BTC reacts around important support zones and whether buyers return with conviction. If momentum shifts, $BTC could lead the next market recovery. Until then, patience is stronger than chasing candles.
The market is testing confidence—not just price. 👀
#bitcoin #BTC #CryptoMarket #fyp
{spot}(BTCUSDT)
₿ Bitcoin: Weakness Today, Opportunity Tomorrow?
Bitcoin is navigating a difficult market, with selling pressure keeping traders cautious. But corrections are also where long-term opportunities begin to form. The key is not predicting the bottom; it’s watching how BTC reacts around important support zones and whether buyers return with conviction. If momentum shifts, $BTC could lead the next market recovery. Until then, patience is stronger than chasing candles.
The market is testing confidence—not just price. 👀
#bitcoin #BTC #CryptoMarket #fyp
Bitcoin is navigating a difficult market, with selling pressure keeping traders cautious. But corrections are also where long-term opportunities begin to form. The key is not predicting the bottom; it’s watching how BTC reacts around important support zones and whether buyers return with conviction. If momentum shifts, $BTC could lead the next market recovery. Until then, patience is stronger than chasing candles.
The market is testing confidence—not just price. 👀
#bitcoin #BTC #CryptoMarket #fyp
171
·
--
Bullish
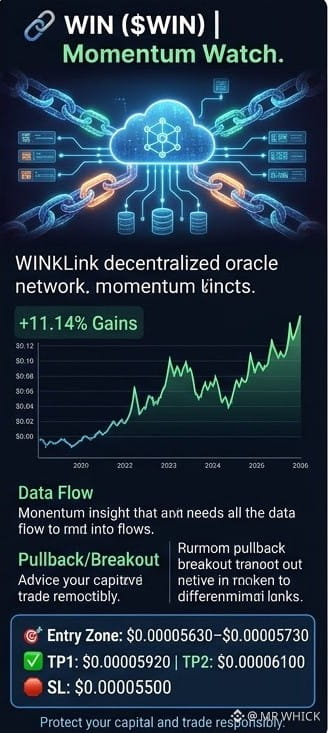
🔗 $WIN | Momentum Watch
WINkLink is a decentralized oracle network designed to connect blockchain smart contracts with external data sources.
$WIN is showing an 11.14% gain in your screenshot, reflecting positive short-term price momentum.
Continued strength depends on sustained buying pressure and market conditions.
Traders should avoid emotional entries and look for a confirmed pullback or breakout before taking a position.
🎯 Entry Zone: $0.00005630–$0.00005730
✅ TP1: $0.00005920 | TP2: $0.00006100
🛑 SL: $0.00005500
Protect your capital and trade responsibly.
{spot}(WINUSDT)
🔗 $WIN | Momentum Watch
WINkLink is a decentralized oracle network designed to connect blockchain smart contracts with external data sources.
$WIN is showing an 11.14% gain in your screenshot, reflecting positive short-term price momentum.
Continued strength depends on sustained buying pressure and market conditions.
Traders should avoid emotional entries and look for a confirmed pullback or breakout before taking a position.
🎯 Entry Zone: $0.00005630–$0.00005730
✅ TP1: $0.00005920 | TP2: $0.00006100
🛑 SL: $0.00005500
Protect your capital and trade responsibly.
WINkLink is a decentralized oracle network designed to connect blockchain smart contracts with external data sources.
$WIN is showing an 11.14% gain in your screenshot, reflecting positive short-term price momentum.
Continued strength depends on sustained buying pressure and market conditions.
Traders should avoid emotional entries and look for a confirmed pullback or breakout before taking a position.
🎯 Entry Zone: $0.00005630–$0.00005730
✅ TP1: $0.00005920 | TP2: $0.00006100
🛑 SL: $0.00005500
Protect your capital and trade responsibly.
268
·
--
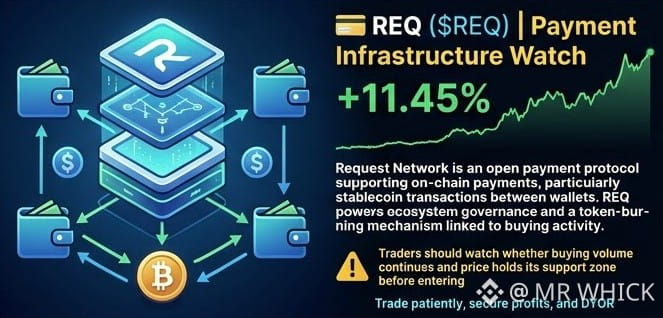
💳 $REQ | Payment Infrastructure Watch.
Request Network is an open payment protocol supporting on-chain payments, particularly stablecoin transactions between wallets. $REQ powers ecosystem governance and a token-burning mechanism linked to network activity. Your screenshot shows an 11.45% gain, suggesting positive market momentum. Traders should watch whether buying volume continues and price holds its support zone before entering.
🎯 Entry Zone: $0.04650–$0.04750
✅ TP1: $0.04950 | TP2: $0.05100
🛑 SL: $0.04550
Smart entries, disciplined exits, and DYOR.
💳 $REQ | Payment Infrastructure Watch.
Request Network is an open payment protocol supporting on-chain payments, particularly stablecoin transactions between wallets. $REQ powers ecosystem governance and a token-burning mechanism linked to network activity. Your screenshot shows an 11.45% gain, suggesting positive market momentum. Traders should watch whether buying volume continues and price holds its support zone before entering.
🎯 Entry Zone: $0.04650–$0.04750
✅ TP1: $0.04950 | TP2: $0.05100
🛑 SL: $0.04550
Smart entries, disciplined exits, and DYOR.
Request Network is an open payment protocol supporting on-chain payments, particularly stablecoin transactions between wallets. $REQ powers ecosystem governance and a token-burning mechanism linked to network activity. Your screenshot shows an 11.45% gain, suggesting positive market momentum. Traders should watch whether buying volume continues and price holds its support zone before entering.
🎯 Entry Zone: $0.04650–$0.04750
✅ TP1: $0.04950 | TP2: $0.05100
🛑 SL: $0.04550
Smart entries, disciplined exits, and DYOR.
122
·
--
Bullish
🤖 $SHELL - AI Momentum-
MyShell is an AI-focused ecosystem designed around interactive AI applications and creator participation. $SHELL has gained 11.87% in your screenshot, showing positive short-term momentum.
AI-related narratives can attract speculative attention, but sustainability depends on continued demand and buying volume. Traders should monitor price consolidation and avoid chasing sudden pumps.
🎯 Entry Zone: $0.02680–$0.02730
✅ TP1: $0.02820 | TP2: $0.02900
🛑 SL: $0.02600
Follow the trend, manage risk, and DYOR.
🤖 $SHELL - AI Momentum-
MyShell is an AI-focused ecosystem designed around interactive AI applications and creator participation. $SHELL has gained 11.87% in your screenshot, showing positive short-term momentum.
AI-related narratives can attract speculative attention, but sustainability depends on continued demand and buying volume. Traders should monitor price consolidation and avoid chasing sudden pumps.
🎯 Entry Zone: $0.02680–$0.02730
✅ TP1: $0.02820 | TP2: $0.02900
🛑 SL: $0.02600
Follow the trend, manage risk, and DYOR.
MyShell is an AI-focused ecosystem designed around interactive AI applications and creator participation. $SHELL has gained 11.87% in your screenshot, showing positive short-term momentum.
AI-related narratives can attract speculative attention, but sustainability depends on continued demand and buying volume. Traders should monitor price consolidation and avoid chasing sudden pumps.
🎯 Entry Zone: $0.02680–$0.02730
✅ TP1: $0.02820 | TP2: $0.02900
🛑 SL: $0.02600
Follow the trend, manage risk, and DYOR.
488
·
--
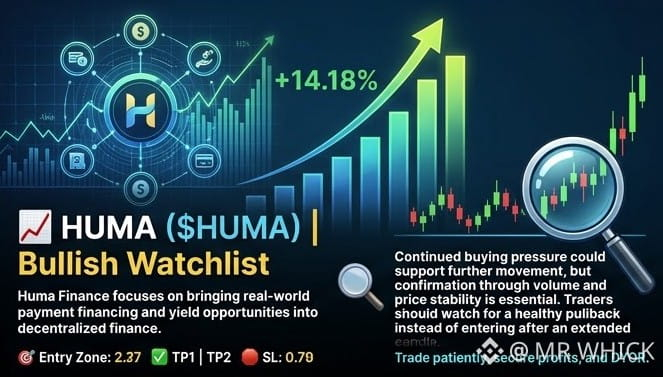
📈 ( $HUMA ) | Bullish Watchlist
Huma Finance focuses on bringing real-world payment financing and yield opportunities into decentralized finance.
HUMA is showing positive momentum with a 14.18% gain in your screenshot.
Continued buying pressure could support further movement but confirmation through volume and price stability is essential.
Traders should watch for a healthy pullback instead of entering after an extended candle.
🎯 Entry Zone: $0.00735–$0.00750
✅ TP1: $0.00785 | TP2: $0.00810
🛑 SL: $0.00715
Trade patiently, secure profits, and DYOR.
📈 ( $HUMA ) | Bullish Watchlist
Huma Finance focuses on bringing real-world payment financing and yield opportunities into decentralized finance.
HUMA is showing positive momentum with a 14.18% gain in your screenshot.
Continued buying pressure could support further movement but confirmation through volume and price stability is essential.
Traders should watch for a healthy pullback instead of entering after an extended candle.
🎯 Entry Zone: $0.00735–$0.00750
✅ TP1: $0.00785 | TP2: $0.00810
🛑 SL: $0.00715
Trade patiently, secure profits, and DYOR.
Huma Finance focuses on bringing real-world payment financing and yield opportunities into decentralized finance.
HUMA is showing positive momentum with a 14.18% gain in your screenshot.
Continued buying pressure could support further movement but confirmation through volume and price stability is essential.
Traders should watch for a healthy pullback instead of entering after an extended candle.
🎯 Entry Zone: $0.00735–$0.00750
✅ TP1: $0.00785 | TP2: $0.00810
🛑 SL: $0.00715
Trade patiently, secure profits, and DYOR.
2
359
·
--
Bullish
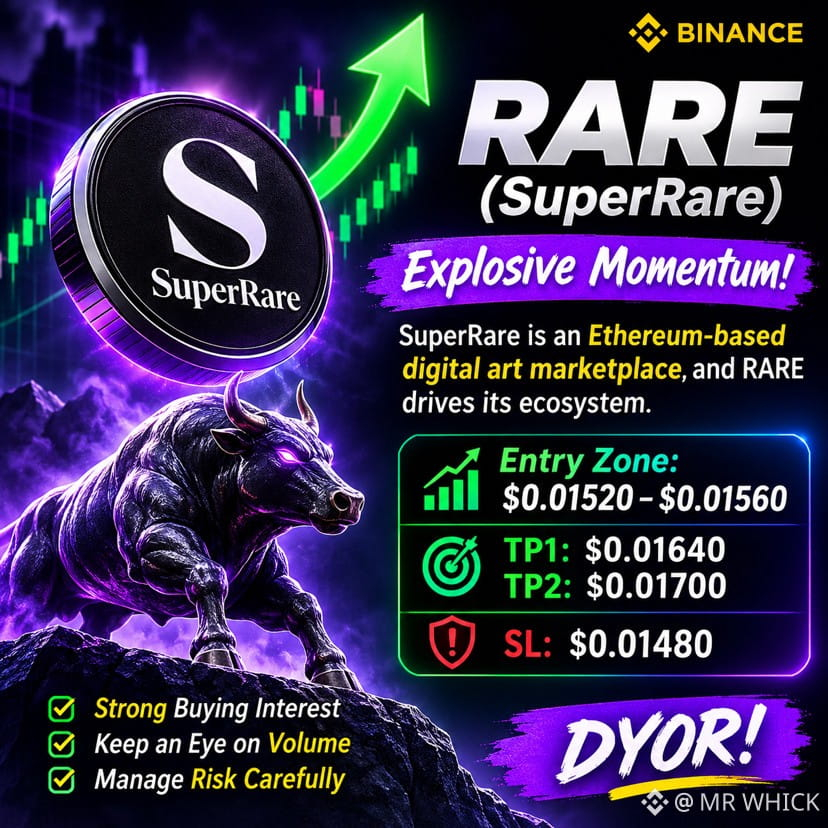
RARE 🔥 ( $RARE ) | Explosive Momentum
SuperRare is an Ethereum-based digital art marketplace where artists and collectors trade unique NFT artworks.
It's RARE token supports ecosystem governance and community participation. Your screenshot shows an impressive 83.95% gain, indicating exceptional short-term momentum.
However, after such a sharp rally, profit-taking and sudden volatility can increase significantly. Avoid chasing the price; wait for consolidation or a confirmed pullback before considering an entry.
🎯 Entry Zone: $0.01520–$0.01560
✅ TP1: $0.01640 | TP2: $0.01700
🛑 SL: $0.01480
DYOR and manage risk carefully.
RARE 🔥 ( $RARE ) | Explosive Momentum
SuperRare is an Ethereum-based digital art marketplace where artists and collectors trade unique NFT artworks.
It's RARE token supports ecosystem governance and community participation. Your screenshot shows an impressive 83.95% gain, indicating exceptional short-term momentum.
However, after such a sharp rally, profit-taking and sudden volatility can increase significantly. Avoid chasing the price; wait for consolidation or a confirmed pullback before considering an entry.
🎯 Entry Zone: $0.01520–$0.01560
✅ TP1: $0.01640 | TP2: $0.01700
🛑 SL: $0.01480
DYOR and manage risk carefully.
SuperRare is an Ethereum-based digital art marketplace where artists and collectors trade unique NFT artworks.
It's RARE token supports ecosystem governance and community participation. Your screenshot shows an impressive 83.95% gain, indicating exceptional short-term momentum.
However, after such a sharp rally, profit-taking and sudden volatility can increase significantly. Avoid chasing the price; wait for consolidation or a confirmed pullback before considering an entry.
🎯 Entry Zone: $0.01520–$0.01560
✅ TP1: $0.01640 | TP2: $0.01700
🛑 SL: $0.01480
DYOR and manage risk carefully.
228
·
--
Bullish
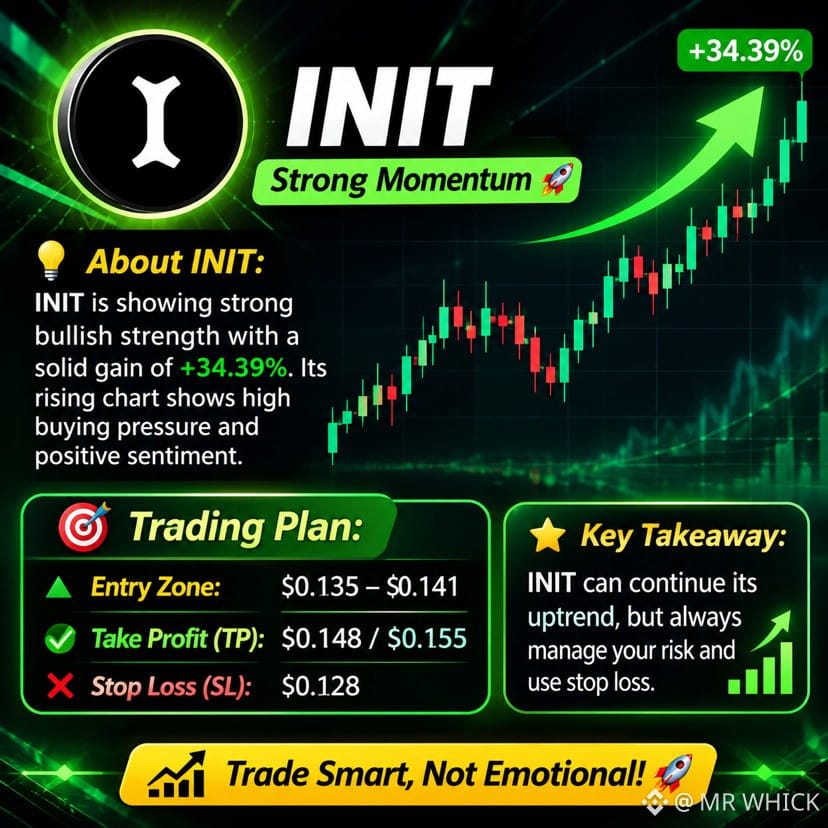
INIT ( $INIT ) | Strong Momentum.
INIT is attracting attention after a remarkable 34.39% gain in the screenshot. Initia focuses on connecting app-specific blockchain networks through a modular ecosystem. Such a strong move can indicate buying interest, but short-term volatility and profit-taking are also possible. Traders should avoid chasing green candles and wait for confirmation or a healthy pullback before entering.
🎯 Entry Zone: $0.135–$0.141
✅ TP1: $0.148 | TP2: $0.155
🛑 SL: $0.128
Trade with discipline, manage risk, and DYOR.
INIT ( $INIT ) | Strong Momentum.
INIT is attracting attention after a remarkable 34.39% gain in the screenshot. Initia focuses on connecting app-specific blockchain networks through a modular ecosystem. Such a strong move can indicate buying interest, but short-term volatility and profit-taking are also possible. Traders should avoid chasing green candles and wait for confirmation or a healthy pullback before entering.
🎯 Entry Zone: $0.135–$0.141
✅ TP1: $0.148 | TP2: $0.155
🛑 SL: $0.128
Trade with discipline, manage risk, and DYOR.
INIT is attracting attention after a remarkable 34.39% gain in the screenshot. Initia focuses on connecting app-specific blockchain networks through a modular ecosystem. Such a strong move can indicate buying interest, but short-term volatility and profit-taking are also possible. Traders should avoid chasing green candles and wait for confirmation or a healthy pullback before entering.
🎯 Entry Zone: $0.135–$0.141
✅ TP1: $0.148 | TP2: $0.155
🛑 SL: $0.128
Trade with discipline, manage risk, and DYOR.
340
·
--
Good afternoon, Binance fam! ☀️
Another day, another chance to learn, build, and stay focused in crypto. Markets can move fast, but patience and discipline matter more than chasing every candle. 📈
Keep researching, manage your risk, and trust your strategy. The next opportunity could be closer than you think.
Stay sharp, stay consistent, and keep building. 🚀
#Binance #crypto #Web3 #BNB #talatala
Good afternoon, Binance fam! ☀️
Another day, another chance to learn, build, and stay focused in crypto. Markets can move fast, but patience and discipline matter more than chasing every candle. 📈
Keep researching, manage your risk, and trust your strategy. The next opportunity could be closer than you think.
Stay sharp, stay consistent, and keep building. 🚀
#Binance #crypto #Web3 #BNB #talatala
Another day, another chance to learn, build, and stay focused in crypto. Markets can move fast, but patience and discipline matter more than chasing every candle. 📈
Keep researching, manage your risk, and trust your strategy. The next opportunity could be closer than you think.
Stay sharp, stay consistent, and keep building. 🚀
#Binance #crypto #Web3 #BNB #talatala
15
1
83
·
--
#dusk I keep coming back to one question about Dusk’s consensus: efficiency can look convincing on paper, but what happens when real network activity starts putting pressure on the system?
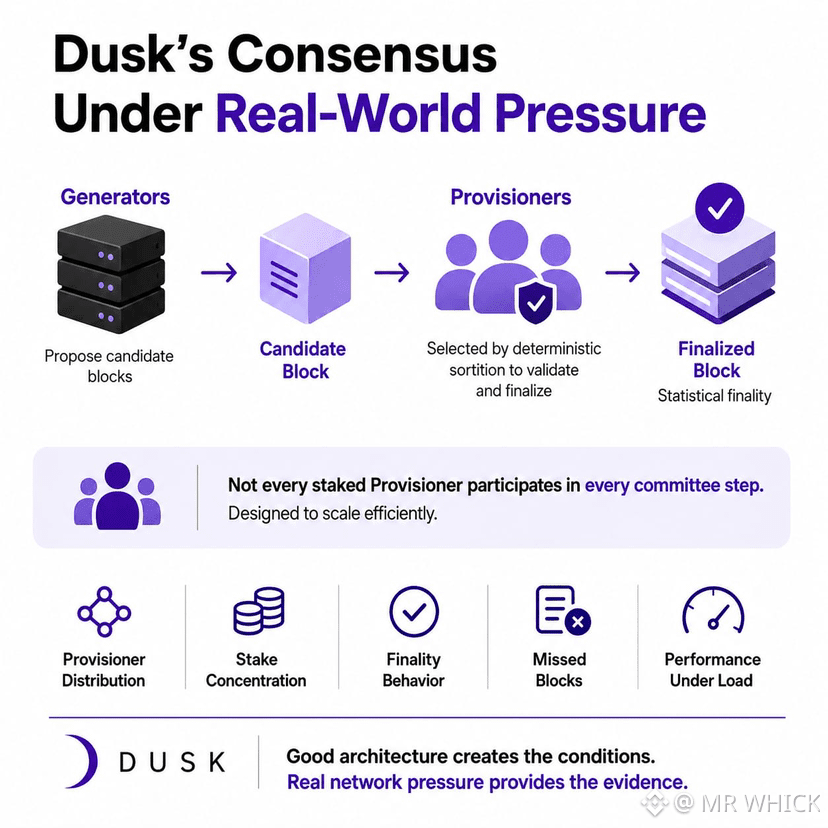
Dusk’s Segregated Byzantine Agreement (SBA) separates consensus responsibilities. Generators propose candidate blocks, while Provisioners are selected into committees through deterministic sortition to validate and finalize them. The goal is statistical finality, where a finalized block should become irreversible with only a negligible probability of a fork.
What I find interesting is that Dusk doesn’t require every staked Provisioner to participate in every committee step. That could become important as activity scales, although the architecture itself can’t prove how efficiently the network will perform under sustained real-world demand.
That’s the part I’d rather watch than assume.
Provisioner distribution, stake concentration, finality behavior, missed blocks, and performance under heavy activity should tell us much more about how durable DUSK’s consensus really is.
Good architecture creates the conditions. Real network pressure provides the evidence. @Dusk_Foundation $DUSK
#dusk I keep coming back to one question about Dusk’s consensus: efficiency can look convincing on paper, but what happens when real network activity starts putting pressure on the system?
Dusk’s Segregated Byzantine Agreement (SBA) separates consensus responsibilities. Generators propose candidate blocks, while Provisioners are selected into committees through deterministic sortition to validate and finalize them. The goal is statistical finality, where a finalized block should become irreversible with only a negligible probability of a fork.
What I find interesting is that Dusk doesn’t require every staked Provisioner to participate in every committee step. That could become important as activity scales, although the architecture itself can’t prove how efficiently the network will perform under sustained real-world demand.
That’s the part I’d rather watch than assume.
Provisioner distribution, stake concentration, finality behavior, missed blocks, and performance under heavy activity should tell us much more about how durable DUSK’s consensus really is.
Good architecture creates the conditions. Real network pressure provides the evidence. @Dusk $DUSK
Dusk’s Segregated Byzantine Agreement (SBA) separates consensus responsibilities. Generators propose candidate blocks, while Provisioners are selected into committees through deterministic sortition to validate and finalize them. The goal is statistical finality, where a finalized block should become irreversible with only a negligible probability of a fork.
What I find interesting is that Dusk doesn’t require every staked Provisioner to participate in every committee step. That could become important as activity scales, although the architecture itself can’t prove how efficiently the network will perform under sustained real-world demand.
That’s the part I’d rather watch than assume.
Provisioner distribution, stake concentration, finality behavior, missed blocks, and performance under heavy activity should tell us much more about how durable DUSK’s consensus really is.
Good architecture creates the conditions. Real network pressure provides the evidence. @Dusk $DUSK
1
3
452
·
--
One thing I noticed is that using any dApp on @Dusk_Foundation means going through the same initial protocol path.
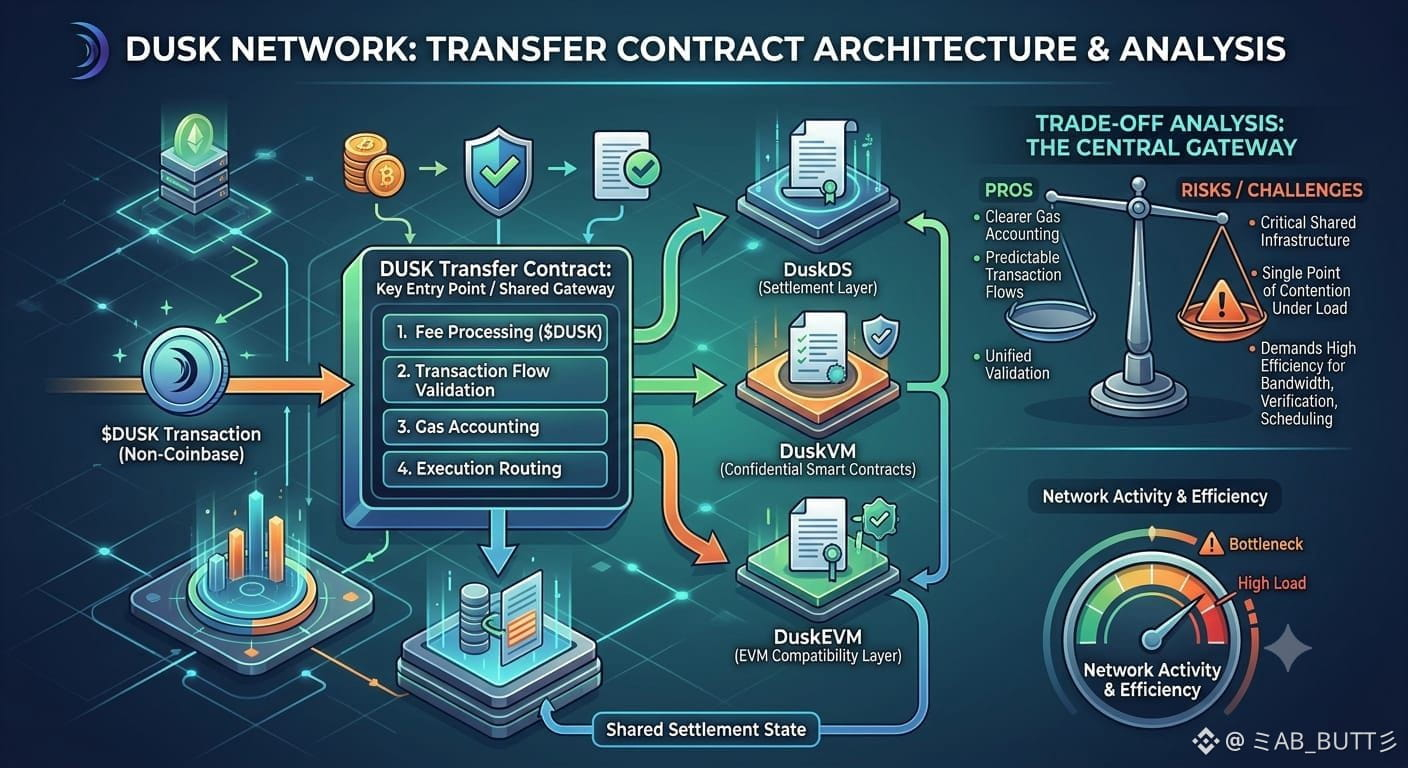
I see the DUSK Transfer Contract as a key entry point for non-coinbase state changes on DuskDS. The protocol separates the asset and compute layers in theory but they still coordinate through a shared settlement state.
$DUSK is the native token used to pay for computation on the network. That’s why standard transactions begin by processing fees through the Transfer Contract. It handles the fee, validates the relevant transaction flow, then routes execution toward the target smart contract.
Why does this matter? Using one shared gateway can make gas accounting clearer and more predictable. But there's also a trade-off. The Transfer Contract becomes critical shared infrastructure because every transaction must pass through its fee and validation path.
If network activity grows significantly, demand for bandwidth, verification and transaction scheduling could increase. That does not automatically mean the compute layer becomes a bottleneck but it makes efficiency under load an important metric to watch.
Dusk’s architecture, including DuskDS, DuskVM and DuskEVM is designed to support different execution needs while keeping settlement connected to the same network. #dusk $DUSK @Dusk_Foundation $DUSK
{spot}(DUSKUSDT)
One thing I noticed is that using any dApp on @Dusk means going through the same initial protocol path.
I see the DUSK Transfer Contract as a key entry point for non-coinbase state changes on DuskDS. The protocol separates the asset and compute layers in theory but they still coordinate through a shared settlement state.
$DUSK is the native token used to pay for computation on the network. That’s why standard transactions begin by processing fees through the Transfer Contract. It handles the fee, validates the relevant transaction flow, then routes execution toward the target smart contract.
Why does this matter? Using one shared gateway can make gas accounting clearer and more predictable. But there's also a trade-off. The Transfer Contract becomes critical shared infrastructure because every transaction must pass through its fee and validation path.
If network activity grows significantly, demand for bandwidth, verification and transaction scheduling could increase. That does not automatically mean the compute layer becomes a bottleneck but it makes efficiency under load an important metric to watch.
Dusk’s architecture, including DuskDS, DuskVM and DuskEVM is designed to support different execution needs while keeping settlement connected to the same network. #dusk $DUSK @Dusk $DUSK
I see the DUSK Transfer Contract as a key entry point for non-coinbase state changes on DuskDS. The protocol separates the asset and compute layers in theory but they still coordinate through a shared settlement state.
$DUSK is the native token used to pay for computation on the network. That’s why standard transactions begin by processing fees through the Transfer Contract. It handles the fee, validates the relevant transaction flow, then routes execution toward the target smart contract.
Why does this matter? Using one shared gateway can make gas accounting clearer and more predictable. But there's also a trade-off. The Transfer Contract becomes critical shared infrastructure because every transaction must pass through its fee and validation path.
If network activity grows significantly, demand for bandwidth, verification and transaction scheduling could increase. That does not automatically mean the compute layer becomes a bottleneck but it makes efficiency under load an important metric to watch.
Dusk’s architecture, including DuskDS, DuskVM and DuskEVM is designed to support different execution needs while keeping settlement connected to the same network. #dusk $DUSK @Dusk $DUSK
3
2
248
·
--
@Dusk_Foundation You know how every time you interact with any decentralised app on @Dusk_Foundation , you have to go through the exact same initial choke point?
DUSK Contract is the only entry point for all non-coinbase state transitions on the network. The protocol separates the native asset layer from the generalised compute layer but they have the same exact state space.
This is why: The only asset that can compensate the network for computational gas is $DUSK . This rule means that each standard transaction must first call the DUSK Contract to perform fee logic before routing execution to a destination smart contract.
Do you think this unified state model will be able to handle heavy smart contract congestion? #dusk $DUSK @Dusk
@Dusk You know how every time you interact with any decentralised app on @Dusk , you have to go through the exact same initial choke point?
DUSK Contract is the only entry point for all non-coinbase state transitions on the network. The protocol separates the native asset layer from the generalised compute layer but they have the same exact state space.
This is why: The only asset that can compensate the network for computational gas is $DUSK . This rule means that each standard transaction must first call the DUSK Contract to perform fee logic before routing execution to a destination smart contract.
Do you think this unified state model will be able to handle heavy smart contract congestion? #dusk $DUSK @Dusk
DUSK Contract is the only entry point for all non-coinbase state transitions on the network. The protocol separates the native asset layer from the generalised compute layer but they have the same exact state space.
This is why: The only asset that can compensate the network for computational gas is $DUSK . This rule means that each standard transaction must first call the DUSK Contract to perform fee logic before routing execution to a destination smart contract.
Do you think this unified state model will be able to handle heavy smart contract congestion? #dusk $DUSK @Dusk
5
4
252
·
--
Everyone is talking about RWA compliance, but almost no one understands the on-chain architecture making it actually work.
I was diving into how Dusk handles this, and their Zedger model is way more intricate than people realize. Regulated DeFi creates a tricky engineering problem: participant identities, historical account balances, and in-flight transfers operate on entirely different lifecycles.
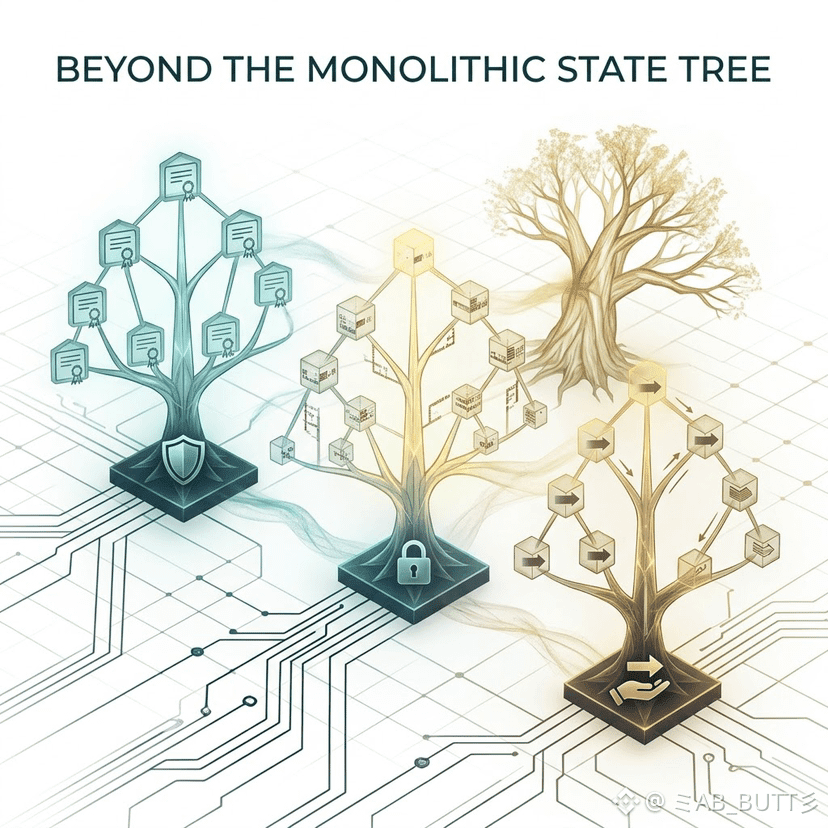
Most blockchains just cram all this data into one massive monolithic state tree. Instead, Dusk isolates state across three dedicated Poseidon Merkle trees:
- whitelistTree: Verifies your authorized identity without exposing actual personal credentials on the public ledger.
- memorySlotTree: Keeps your balance history private by tracking the root commitments of user accounts (Sparse Merkle-Segment Tries).
- coinTree: Acts as the transient layer, managing UTXO-style transfers while assets await receiver acceptance or timeout claims.
Does verifying membership proofs across three different trees increase zero-knowledge computation costs? Yes. But this three-tier separation completely eliminates transaction graph leakage while keeping institutional issuers strictly aligned with regulatory standards. It is a brilliant trade-off.
Do you think this three-tier architecture will become the standard for institutional DeFi? Let me know your thoughts below! 👇 #dusk $DUSK @Dusk
Everyone is talking about RWA compliance, but almost no one understands the on-chain architecture making it actually work.
I was diving into how Dusk handles this, and their Zedger model is way more intricate than people realize. Regulated DeFi creates a tricky engineering problem: participant identities, historical account balances, and in-flight transfers operate on entirely different lifecycles.
Most blockchains just cram all this data into one massive monolithic state tree. Instead, Dusk isolates state across three dedicated Poseidon Merkle trees:
- whitelistTree: Verifies your authorized identity without exposing actual personal credentials on the public ledger.
- memorySlotTree: Keeps your balance history private by tracking the root commitments of user accounts (Sparse Merkle-Segment Tries).
- coinTree: Acts as the transient layer, managing UTXO-style transfers while assets await receiver acceptance or timeout claims.
Does verifying membership proofs across three different trees increase zero-knowledge computation costs? Yes. But this three-tier separation completely eliminates transaction graph leakage while keeping institutional issuers strictly aligned with regulatory standards. It is a brilliant trade-off.
Do you think this three-tier architecture will become the standard for institutional DeFi? Let me know your thoughts below! 👇 #dusk $DUSK @Dusk
I was diving into how Dusk handles this, and their Zedger model is way more intricate than people realize. Regulated DeFi creates a tricky engineering problem: participant identities, historical account balances, and in-flight transfers operate on entirely different lifecycles.
Most blockchains just cram all this data into one massive monolithic state tree. Instead, Dusk isolates state across three dedicated Poseidon Merkle trees:
- whitelistTree: Verifies your authorized identity without exposing actual personal credentials on the public ledger.
- memorySlotTree: Keeps your balance history private by tracking the root commitments of user accounts (Sparse Merkle-Segment Tries).
- coinTree: Acts as the transient layer, managing UTXO-style transfers while assets await receiver acceptance or timeout claims.
Does verifying membership proofs across three different trees increase zero-knowledge computation costs? Yes. But this three-tier separation completely eliminates transaction graph leakage while keeping institutional issuers strictly aligned with regulatory standards. It is a brilliant trade-off.
Do you think this three-tier architecture will become the standard for institutional DeFi? Let me know your thoughts below! 👇 #dusk $DUSK @Dusk
411
·
--
Most blockchains struggle with a core conflict: securities regulations require a detailed history of account balances, but public ledgers expose everything. To solve this, Dusk created something entirely new for its Zedger model: the Sparse Merkle-Segment Trie (SMST).
Standard UTXO models cannot track interval balances or separate dividend-eligible funds from transactional ones. SMST fixes this by merging the cryptographic accumulator properties of a Sparse Merkle Tree with a Segment Tree's ability to store interval data.
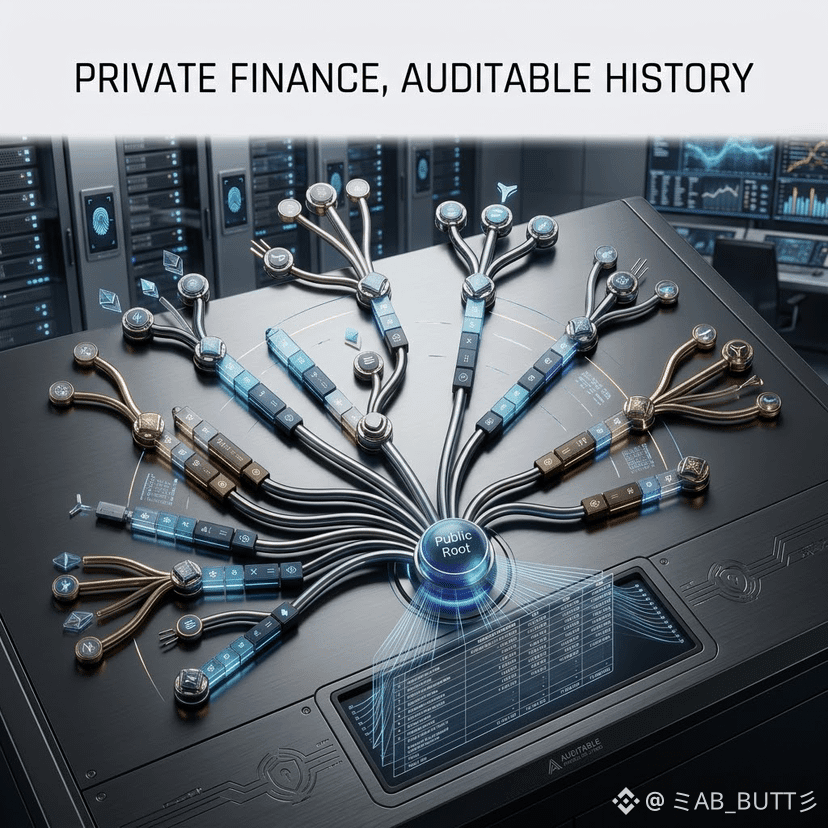
Inside an SMST, every node tracks specific balance states: maximum, transactional, voting, and dividend balances. This design allows an account to securely log every balance change across different segments of time while only revealing the changes to a public root.
The implication? Asset operators can definitively reconstruct a capitalization table for compliance at any historical snapshot, without stripping the user of their on-chain privacy. #dusk $DUSK @Dusk
Most blockchains struggle with a core conflict: securities regulations require a detailed history of account balances, but public ledgers expose everything. To solve this, Dusk created something entirely new for its Zedger model: the Sparse Merkle-Segment Trie (SMST).
Standard UTXO models cannot track interval balances or separate dividend-eligible funds from transactional ones. SMST fixes this by merging the cryptographic accumulator properties of a Sparse Merkle Tree with a Segment Tree's ability to store interval data.
Inside an SMST, every node tracks specific balance states: maximum, transactional, voting, and dividend balances. This design allows an account to securely log every balance change across different segments of time while only revealing the changes to a public root.
The implication? Asset operators can definitively reconstruct a capitalization table for compliance at any historical snapshot, without stripping the user of their on-chain privacy. #dusk $DUSK @Dusk
Standard UTXO models cannot track interval balances or separate dividend-eligible funds from transactional ones. SMST fixes this by merging the cryptographic accumulator properties of a Sparse Merkle Tree with a Segment Tree's ability to store interval data.
Inside an SMST, every node tracks specific balance states: maximum, transactional, voting, and dividend balances. This design allows an account to securely log every balance change across different segments of time while only revealing the changes to a public root.
The implication? Asset operators can definitively reconstruct a capitalization table for compliance at any historical snapshot, without stripping the user of their on-chain privacy. #dusk $DUSK @Dusk
12
10
995
·
--
Verified
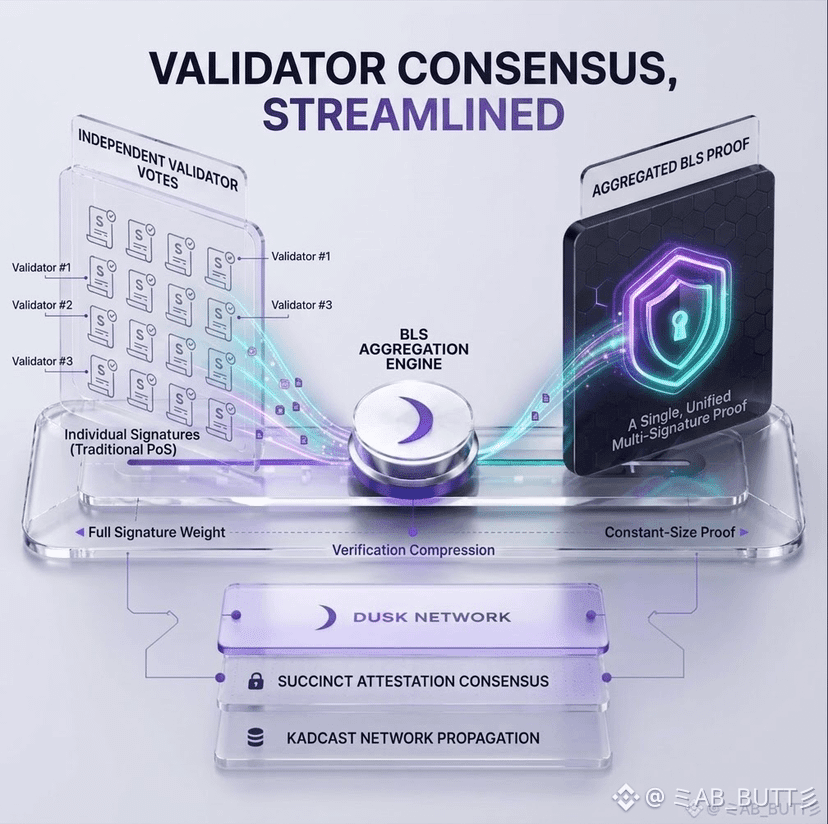
#dusk One detail in Dusk’s consensus architecture makes this more interesting. Instead of storing each validator’s vote separately, the network aggregates BLS signatures into a single proof. In a traditional setup, every validator signature takes up individual block space. In Dusk, hundreds of committee votes are compressed into one constant-sized signature while still verifying every participant.
I think the useful idea here is scalability. Dusk didn’t force nodes to store every independent signature because permanent validator bloat makes running a node too expensive over time.
There’s even a practical trade-off: aggregating BLS signatures requires slightly more cryptographic computation, but it saves massive bandwidth and on-chain storage. That helps keep hardware requirements low for node runners.
So the better question isn’t “how many validators can sign?” It’s how efficiently can the chain record their consensus? $DUSK @Dusk_Foundation
#dusk One detail in Dusk’s consensus architecture makes this more interesting. Instead of storing each validator’s vote separately, the network aggregates BLS signatures into a single proof. In a traditional setup, every validator signature takes up individual block space. In Dusk, hundreds of committee votes are compressed into one constant-sized signature while still verifying every participant.
I think the useful idea here is scalability. Dusk didn’t force nodes to store every independent signature because permanent validator bloat makes running a node too expensive over time.
There’s even a practical trade-off: aggregating BLS signatures requires slightly more cryptographic computation, but it saves massive bandwidth and on-chain storage. That helps keep hardware requirements low for node runners.
So the better question isn’t “how many validators can sign?” It’s how efficiently can the chain record their consensus? $DUSK @Dusk
I think the useful idea here is scalability. Dusk didn’t force nodes to store every independent signature because permanent validator bloat makes running a node too expensive over time.
There’s even a practical trade-off: aggregating BLS signatures requires slightly more cryptographic computation, but it saves massive bandwidth and on-chain storage. That helps keep hardware requirements low for node runners.
So the better question isn’t “how many validators can sign?” It’s how efficiently can the chain record their consensus? $DUSK @Dusk
9
9
591
·
--
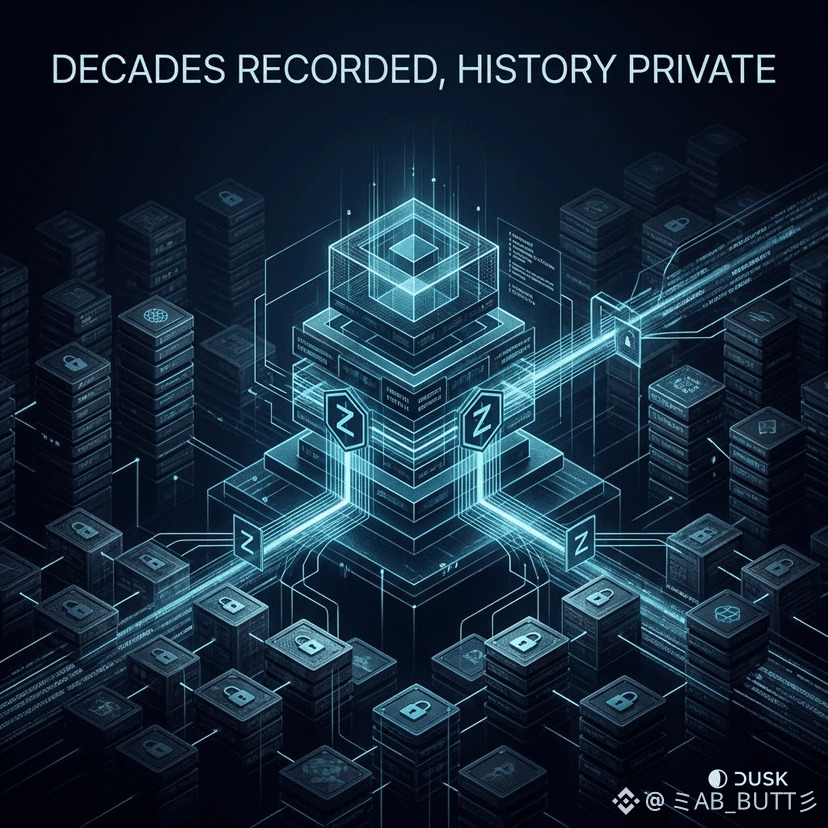
#dusk one detail in Dusk’s Phoenix model makes this more interesting. The network can keep track of balance changes without exposing every transaction and value behind them. Instead of publishing a complete financial history, Phoenix uses encrypted notes and zero-knowledge proofs to maintain valid state while keeping sensitive details private.
I think the useful idea here is continuity. Dusk doesn’t need everyone to see every past transaction to know that the current state is valid.
That creates an interesting trade-off: the network can preserve a long-term record of balance changes while avoiding the need to publish the full financial history behind those balances.
So the better question isn’t “does Dusk keep transaction history?” It’s how much of that history actually needs to be public? $DUSK @Dusk
#dusk one detail in Dusk’s Phoenix model makes this more interesting. The network can keep track of balance changes without exposing every transaction and value behind them. Instead of publishing a complete financial history, Phoenix uses encrypted notes and zero-knowledge proofs to maintain valid state while keeping sensitive details private.
I think the useful idea here is continuity. Dusk doesn’t need everyone to see every past transaction to know that the current state is valid.
That creates an interesting trade-off: the network can preserve a long-term record of balance changes while avoiding the need to publish the full financial history behind those balances.
So the better question isn’t “does Dusk keep transaction history?” It’s how much of that history actually needs to be public? $DUSK @Dusk
I think the useful idea here is continuity. Dusk doesn’t need everyone to see every past transaction to know that the current state is valid.
That creates an interesting trade-off: the network can preserve a long-term record of balance changes while avoiding the need to publish the full financial history behind those balances.
So the better question isn’t “does Dusk keep transaction history?” It’s how much of that history actually needs to be public? $DUSK @Dusk
13
9
467
·
--
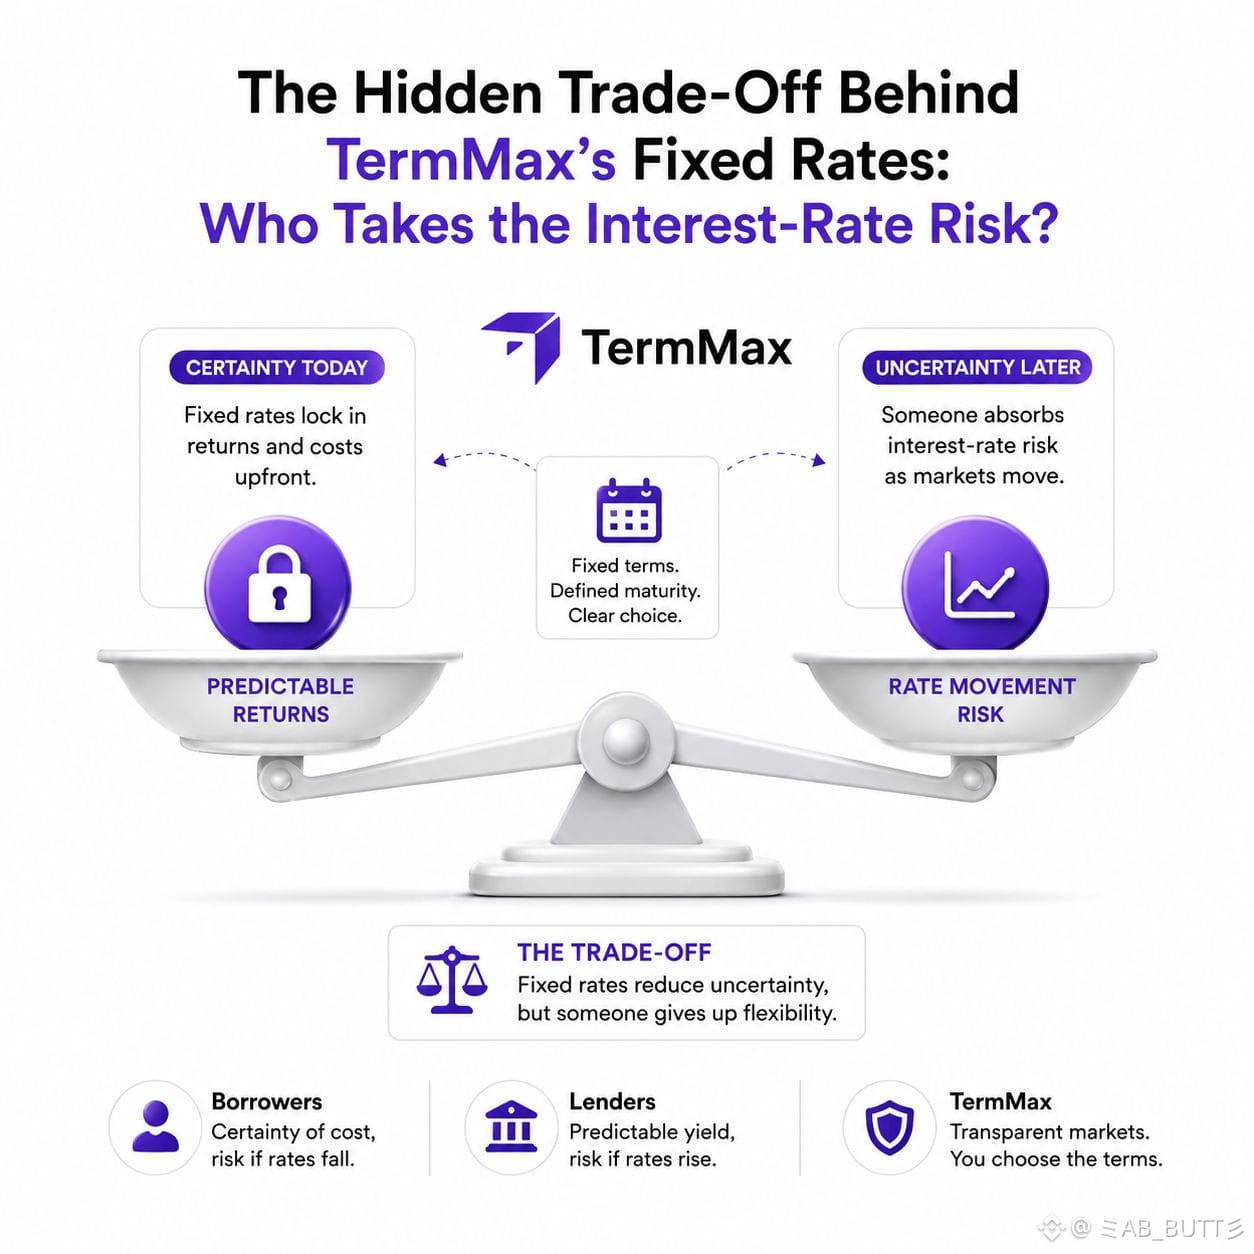
A fixed rate sounds like certainty—until you ask who absorbs the uncertainty behind it.
In @termmax fixed-rate lending and borrowing lock the rate for a defined maturity, so the borrower knows the interest cost upfront and the lender gets a predictable return. TermMax’s interface separates these fixed-rate markets by maturity, with users choosing specific terms rather than floating indefinitely. (TermMax)
That predictability doesn’t remove interest-rate risk. It changes where it sits.
My read is that the party locking the fixed rate gives up some flexibility if market rates move later. If rates fall, a borrower may be stuck paying the agreed rate; if rates rise, a lender may miss better opportunities elsewhere.
That’s the hidden trade-off: fixed returns reduce rate uncertainty, but they can also create opportunity cost.
So the interesting question isn’t whether the rate is fixed. It’s who benefits when the market moves away from that fixed rate? #termmax @termmax
A fixed rate sounds like certainty—until you ask who absorbs the uncertainty behind it.
In @TermMax fixed-rate lending and borrowing lock the rate for a defined maturity, so the borrower knows the interest cost upfront and the lender gets a predictable return. TermMax’s interface separates these fixed-rate markets by maturity, with users choosing specific terms rather than floating indefinitely. (TermMax)
That predictability doesn’t remove interest-rate risk. It changes where it sits.
My read is that the party locking the fixed rate gives up some flexibility if market rates move later. If rates fall, a borrower may be stuck paying the agreed rate; if rates rise, a lender may miss better opportunities elsewhere.
That’s the hidden trade-off: fixed returns reduce rate uncertainty, but they can also create opportunity cost.
So the interesting question isn’t whether the rate is fixed. It’s who benefits when the market moves away from that fixed rate? #termmax @TermMax
In @TermMax fixed-rate lending and borrowing lock the rate for a defined maturity, so the borrower knows the interest cost upfront and the lender gets a predictable return. TermMax’s interface separates these fixed-rate markets by maturity, with users choosing specific terms rather than floating indefinitely. (TermMax)
That predictability doesn’t remove interest-rate risk. It changes where it sits.
My read is that the party locking the fixed rate gives up some flexibility if market rates move later. If rates fall, a borrower may be stuck paying the agreed rate; if rates rise, a lender may miss better opportunities elsewhere.
That’s the hidden trade-off: fixed returns reduce rate uncertainty, but they can also create opportunity cost.
So the interesting question isn’t whether the rate is fixed. It’s who benefits when the market moves away from that fixed rate? #termmax @TermMax
8
9
368
·
--
Partly True
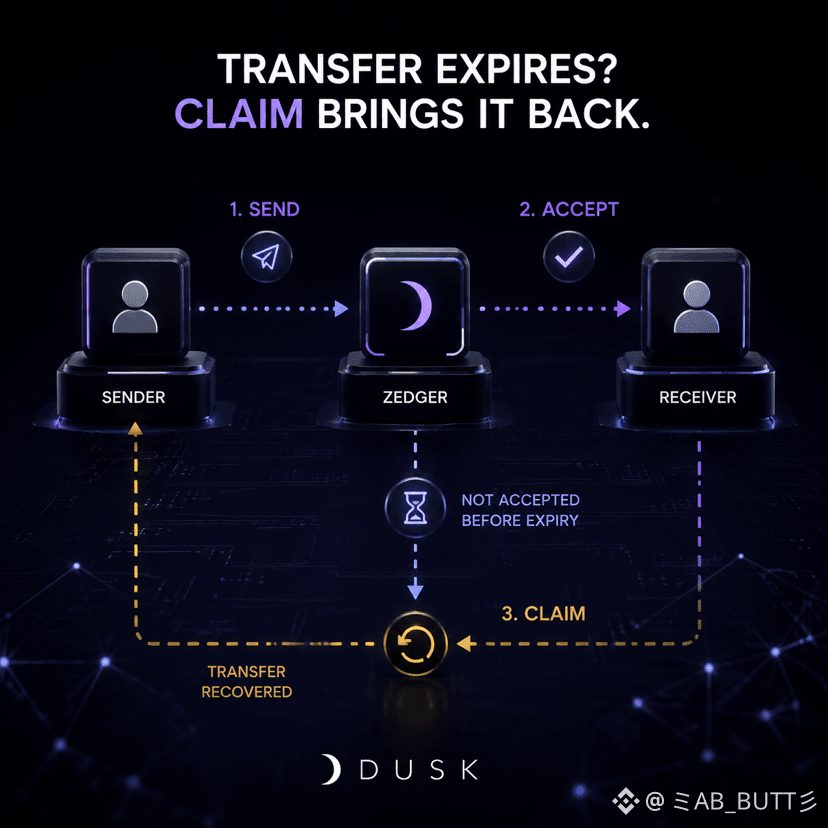
#dusk $DUSK @Dusk_Foundation a Zedger transfer can be sent without becoming final for the receiver — and that’s exactly why CLAIM exists.
In Dusk’s Zedger design, SEND doesn’t immediately make a transfer part of the receiver’s accepted balance. The receiver still has to ACCEPT it before the transfer expires.
If that never happens, CLAIM provides the sender a defined way to recover the expired transfer rather than leaving it unresolved indefinitely.
That creates an interesting three-step lifecycle:
SEND initiates → ACCEPT completes → CLAIM handles expiry.
What stands out is that Zedger explicitly accounts for the case where the receiving side simply does nothing. The protocol doesn’t have to assume every initiated transfer will successfully complete.
The unanswered question is more practical: how often does CLAIM actually become necessary under real network activity?
The mechanism is documented. Its real-world usage is the evidence worth watching next.
#dusk $DUSK @Dusk a Zedger transfer can be sent without becoming final for the receiver — and that’s exactly why CLAIM exists.
In Dusk’s Zedger design, SEND doesn’t immediately make a transfer part of the receiver’s accepted balance. The receiver still has to ACCEPT it before the transfer expires.
If that never happens, CLAIM provides the sender a defined way to recover the expired transfer rather than leaving it unresolved indefinitely.
That creates an interesting three-step lifecycle:
SEND initiates → ACCEPT completes → CLAIM handles expiry.
What stands out is that Zedger explicitly accounts for the case where the receiving side simply does nothing. The protocol doesn’t have to assume every initiated transfer will successfully complete.
The unanswered question is more practical: how often does CLAIM actually become necessary under real network activity?
The mechanism is documented. Its real-world usage is the evidence worth watching next.
In Dusk’s Zedger design, SEND doesn’t immediately make a transfer part of the receiver’s accepted balance. The receiver still has to ACCEPT it before the transfer expires.
If that never happens, CLAIM provides the sender a defined way to recover the expired transfer rather than leaving it unresolved indefinitely.
That creates an interesting three-step lifecycle:
SEND initiates → ACCEPT completes → CLAIM handles expiry.
What stands out is that Zedger explicitly accounts for the case where the receiving side simply does nothing. The protocol doesn’t have to assume every initiated transfer will successfully complete.
The unanswered question is more practical: how often does CLAIM actually become necessary under real network activity?
The mechanism is documented. Its real-world usage is the evidence worth watching next.
12
10
654
·
--
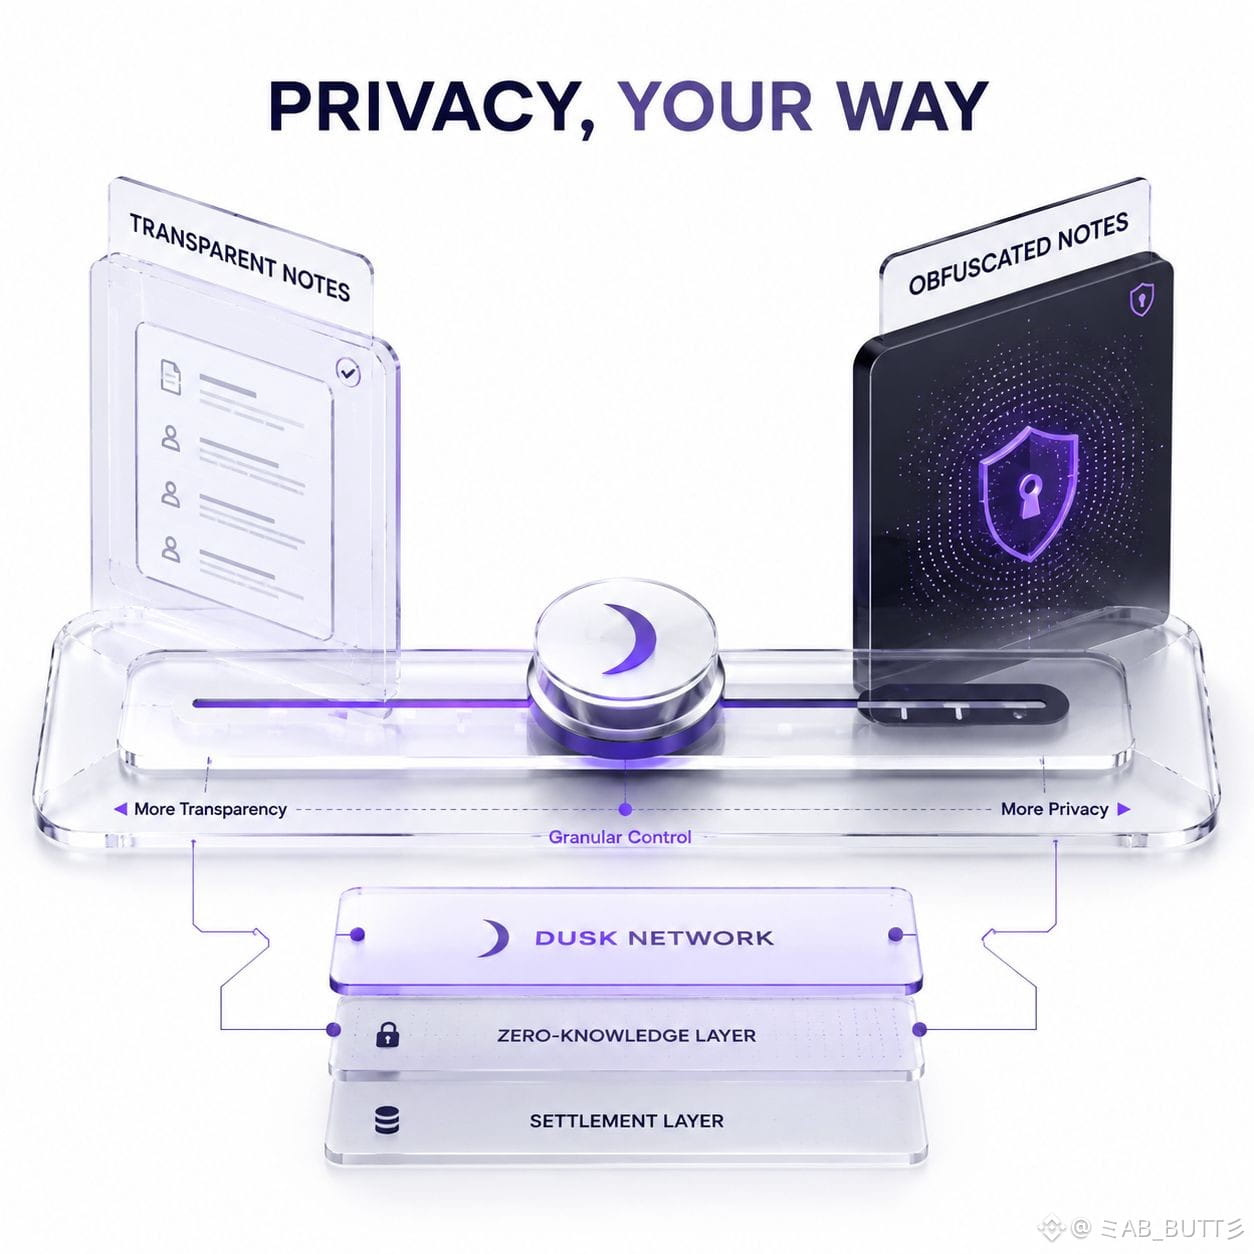
#dusk One detail in Dusk’s Phoenix model makes this more interesting. Notes can be transparent or obfuscated, meaning the system can handle different levels of information visibility inside the same transaction model. In a transparent note, the value is visible. In an obfuscated note, the value is encrypted, while the note still uses Dusk’s privacy mechanism.
I think the useful idea here is flexibility. Dusk didn’t make every note equally visible because some data may need to be checked, while some should stay hidden.
There’s even a practical trade-off: Dusk made zero-value transactions transparent because keeping them obfuscated would add unnecessary entries to the note tree. That helps reduce avoidable data over time.
So the better question isn’t “private or public?” It’s what actually needs to be visible? $DUSK @Dusk_Foundation
#dusk One detail in Dusk’s Phoenix model makes this more interesting. Notes can be transparent or obfuscated, meaning the system can handle different levels of information visibility inside the same transaction model. In a transparent note, the value is visible. In an obfuscated note, the value is encrypted, while the note still uses Dusk’s privacy mechanism.
I think the useful idea here is flexibility. Dusk didn’t make every note equally visible because some data may need to be checked, while some should stay hidden.
There’s even a practical trade-off: Dusk made zero-value transactions transparent because keeping them obfuscated would add unnecessary entries to the note tree. That helps reduce avoidable data over time.
So the better question isn’t “private or public?” It’s what actually needs to be visible? $DUSK @Dusk
I think the useful idea here is flexibility. Dusk didn’t make every note equally visible because some data may need to be checked, while some should stay hidden.
There’s even a practical trade-off: Dusk made zero-value transactions transparent because keeping them obfuscated would add unnecessary entries to the note tree. That helps reduce avoidable data over time.
So the better question isn’t “private or public?” It’s what actually needs to be visible? $DUSK @Dusk
9
10
472
·
--
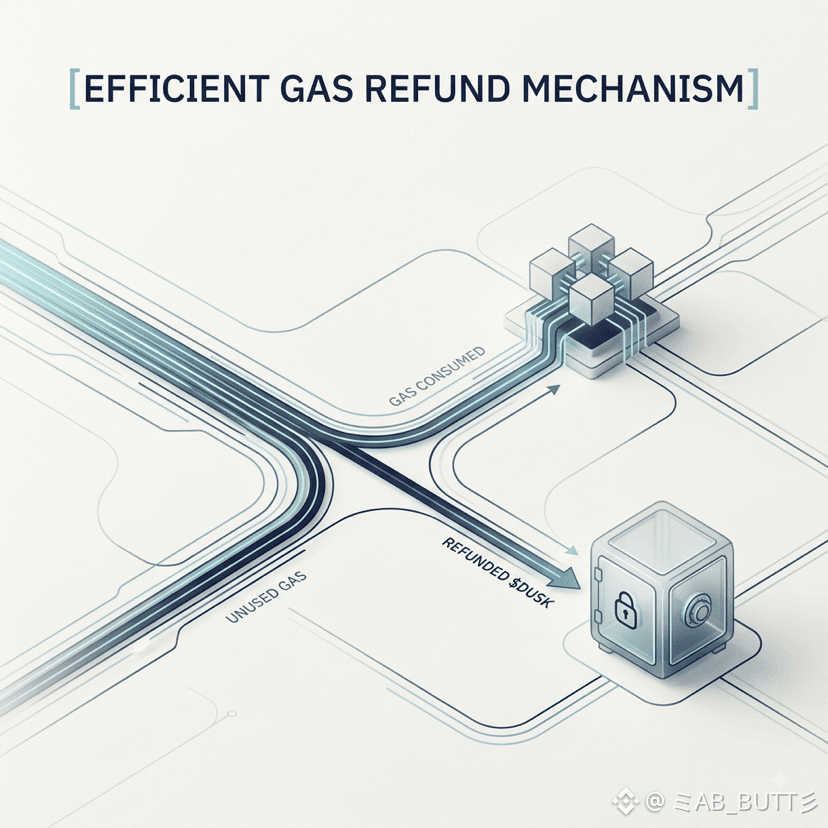
#dusk What happens if you reserve more gas than a DUSK transaction actually uses? The unused part is not simply lost.
When a transaction sets its gas price and gas limit, Dusk also includes a stealth address in the fee data. If execution finishes without consuming all the allocated gas, the remaining value can be returned to that address as a refund.
That detail is easy to miss, but it matters. Users need enough gas allowance to let a contract finish, yet they should not have to treat every unused unit as wasted $DUSK .
The design also fits Dusk’s broader approach of keeping transaction handling precise without making the refund process unnecessarily public.
One question I would still watch in practice is how predictable those refunds feel during more complex contract execution.
For me, this is a small mechanism with a practical message: good transaction design is not only about charging for computation, but also about handling what was never actually used. $DUSK @Dusk_Foundation
{spot}(DUSKUSDT)
#dusk What happens if you reserve more gas than a DUSK transaction actually uses? The unused part is not simply lost.
When a transaction sets its gas price and gas limit, Dusk also includes a stealth address in the fee data. If execution finishes without consuming all the allocated gas, the remaining value can be returned to that address as a refund.
That detail is easy to miss, but it matters. Users need enough gas allowance to let a contract finish, yet they should not have to treat every unused unit as wasted $DUSK .
The design also fits Dusk’s broader approach of keeping transaction handling precise without making the refund process unnecessarily public.
One question I would still watch in practice is how predictable those refunds feel during more complex contract execution.
For me, this is a small mechanism with a practical message: good transaction design is not only about charging for computation, but also about handling what was never actually used. $DUSK @Dusk
When a transaction sets its gas price and gas limit, Dusk also includes a stealth address in the fee data. If execution finishes without consuming all the allocated gas, the remaining value can be returned to that address as a refund.
That detail is easy to miss, but it matters. Users need enough gas allowance to let a contract finish, yet they should not have to treat every unused unit as wasted $DUSK .
The design also fits Dusk’s broader approach of keeping transaction handling precise without making the refund process unnecessarily public.
One question I would still watch in practice is how predictable those refunds feel during more complex contract execution.
For me, this is a small mechanism with a practical message: good transaction design is not only about charging for computation, but also about handling what was never actually used. $DUSK @Dusk
16
12
605
·
--
Partly True
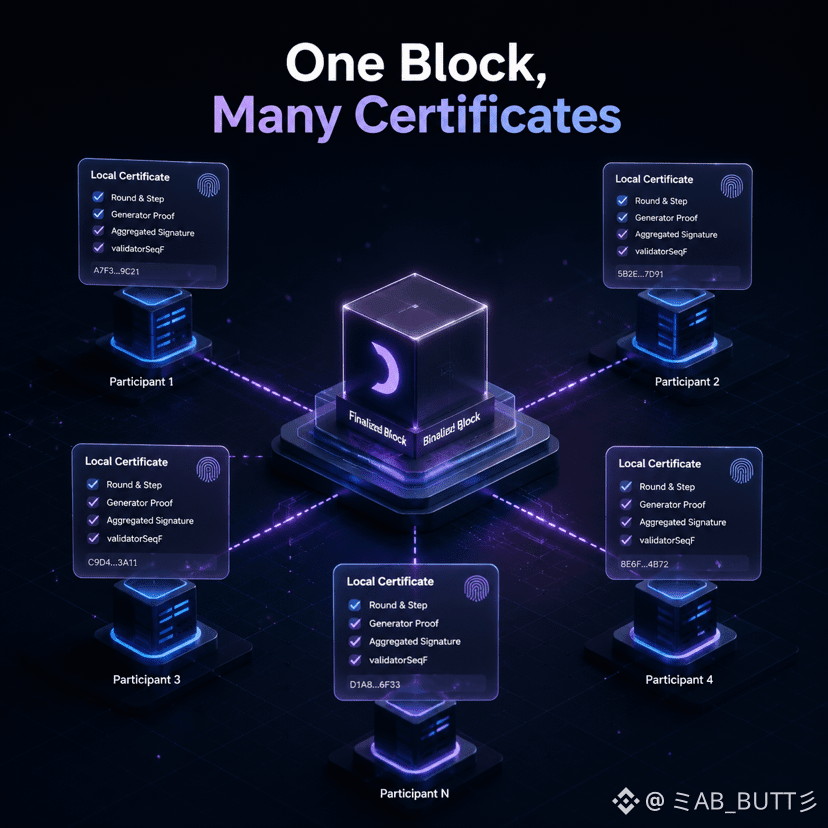
#dusk What if two DUSK participants finalize the same block but do not hold an identical certificate object?
That is actually possible by design. Dusk’s whitepaper states that block certificates are constructed locally by each consensus participant, meaning there is no uniform certificate for a consensus round.
What matters is the evidence inside it. A certificate contains the round and consensus step, the Generator’s Proof-of-Blind-Bid proof and score, an aggregated BLS signature from committee validators, and validatorSeqF, a binary mapping showing which validators contributed signatures across the three relevant committees.
The whitepaper does not explicitly explain the motivation for making certificates local, so claiming a specific reason would be speculation.
What I find interesting is the distinction this creates: participants need to agree on the finalized block, but they do not need one universally distributed representation of its certificate.
For $DUSK , consensus is therefore about shared finality—not necessarily identical locally constructed evidence of that finality.
@Dusk_Foundation $DUSK @Dusk_Foundation
#dusk What if two DUSK participants finalize the same block but do not hold an identical certificate object?
That is actually possible by design. Dusk’s whitepaper states that block certificates are constructed locally by each consensus participant, meaning there is no uniform certificate for a consensus round.
What matters is the evidence inside it. A certificate contains the round and consensus step, the Generator’s Proof-of-Blind-Bid proof and score, an aggregated BLS signature from committee validators, and validatorSeqF, a binary mapping showing which validators contributed signatures across the three relevant committees.
The whitepaper does not explicitly explain the motivation for making certificates local, so claiming a specific reason would be speculation.
What I find interesting is the distinction this creates: participants need to agree on the finalized block, but they do not need one universally distributed representation of its certificate.
For $DUSK , consensus is therefore about shared finality—not necessarily identical locally constructed evidence of that finality.
@Dusk $DUSK @Dusk
That is actually possible by design. Dusk’s whitepaper states that block certificates are constructed locally by each consensus participant, meaning there is no uniform certificate for a consensus round.
What matters is the evidence inside it. A certificate contains the round and consensus step, the Generator’s Proof-of-Blind-Bid proof and score, an aggregated BLS signature from committee validators, and validatorSeqF, a binary mapping showing which validators contributed signatures across the three relevant committees.
The whitepaper does not explicitly explain the motivation for making certificates local, so claiming a specific reason would be speculation.
What I find interesting is the distinction this creates: participants need to agree on the finalized block, but they do not need one universally distributed representation of its certificate.
For $DUSK , consensus is therefore about shared finality—not necessarily identical locally constructed evidence of that finality.
@Dusk $DUSK @Dusk
35
19
838
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
BTCRemainsUnderPressureAfterHawkishFOMCMinutes
37,681 views
523 Discussing
FOMC Minutes | Fed Minutes Show Almost All Officials Expect More Rate Hikes, With Some Open to a Larger December Move
Binance News
·46 Likes
·54.7k views
AnthropicToDebutAfter$83IPOPricing
10,411 views
59 Discussing
NvidiaBoardReportedlySplitOverHuang’sReturn
12,037 views
197 Discussing