

#bitgetbreachforgedrequestsnotstolenkeys
bitgetbreachforgedrequestsnotstolenkeys
Hot
Latest

#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Hack 🚨
The world of crypto is in uproar, but let’s cut through the noise with hard, verified evidence about a $351.6 million Bitget hack.
Warning: It’s not what you think.
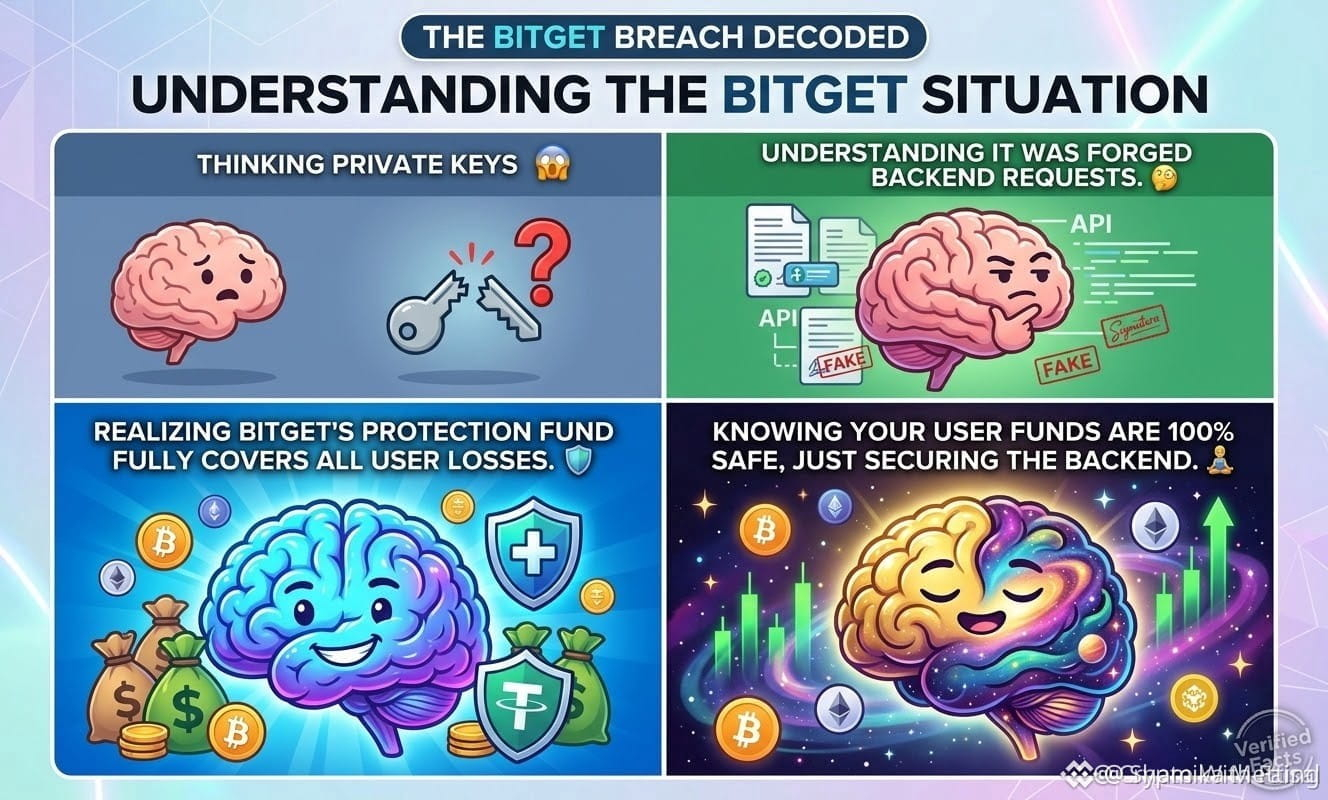
The attackers didn’t steal wallet vault keys. Instead, they compromised a back-end system, tampered with transaction documents, and sent fake withdrawal requests through Bitget’s own approval process.
Why does this technical detail matter?
Because key theft means endless bleeding. 🩸
Fake requests = plug the loophole and stop the bleeding. 🛑
Good news:
✅ Keys are safe: The private keys never left their place.
✅ Vaults secured: Only the hot and semi-warm wallets were targeted. Cold storage remains 100% safe.
✅ Users are okay: Bitget’s protection fund of $464 million fully covers the $351.6 million loss.
Withdrawals were temporarily paused for a comprehensive security review, but CEO Gracy Chen confirmed that users’ assets are safe.
This incident proves that back-end infrastructure has become the new battleground in Web3. Stay alert and stay safe! 🛡️
Please follow up
$AVAX
{future}(AVAXUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Hack 🚨
The world of crypto is in uproar, but let’s cut through the noise with hard, verified evidence about a $351.6 million Bitget hack.
Warning: It’s not what you think.
The attackers didn’t steal wallet vault keys. Instead, they compromised a back-end system, tampered with transaction documents, and sent fake withdrawal requests through Bitget’s own approval process.
Why does this technical detail matter?
Because key theft means endless bleeding. 🩸
Fake requests = plug the loophole and stop the bleeding. 🛑
Good news:
✅ Keys are safe: The private keys never left their place.
✅ Vaults secured: Only the hot and semi-warm wallets were targeted. Cold storage remains 100% safe.
✅ Users are okay: Bitget’s protection fund of $464 million fully covers the $351.6 million loss.
Withdrawals were temporarily paused for a comprehensive security review, but CEO Gracy Chen confirmed that users’ assets are safe.
This incident proves that back-end infrastructure has become the new battleground in Web3. Stay alert and stay safe! 🛡️
Please follow up
$AVAX
🚨 The Real Story Behind the Bitget Hack 🚨
The world of crypto is in uproar, but let’s cut through the noise with hard, verified evidence about a $351.6 million Bitget hack.
Warning: It’s not what you think.
The attackers didn’t steal wallet vault keys. Instead, they compromised a back-end system, tampered with transaction documents, and sent fake withdrawal requests through Bitget’s own approval process.
Why does this technical detail matter?
Because key theft means endless bleeding. 🩸
Fake requests = plug the loophole and stop the bleeding. 🛑
Good news:
✅ Keys are safe: The private keys never left their place.
✅ Vaults secured: Only the hot and semi-warm wallets were targeted. Cold storage remains 100% safe.
✅ Users are okay: Bitget’s protection fund of $464 million fully covers the $351.6 million loss.
Withdrawals were temporarily paused for a comprehensive security review, but CEO Gracy Chen confirmed that users’ assets are safe.
This incident proves that back-end infrastructure has become the new battleground in Web3. Stay alert and stay safe! 🛡️
Please follow up
$AVAX
SAQR77:
المهم منصة تافهة
3
3
6k
·
--
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
{spot}(BTCUSDT)
{spot}(ETHUSDT)
{spot}(BNBUSDT)
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
SAQR77:
بيت منصة تافهة، بايننس احسنهم بكثير
1
3
9k
·
--
Bearish
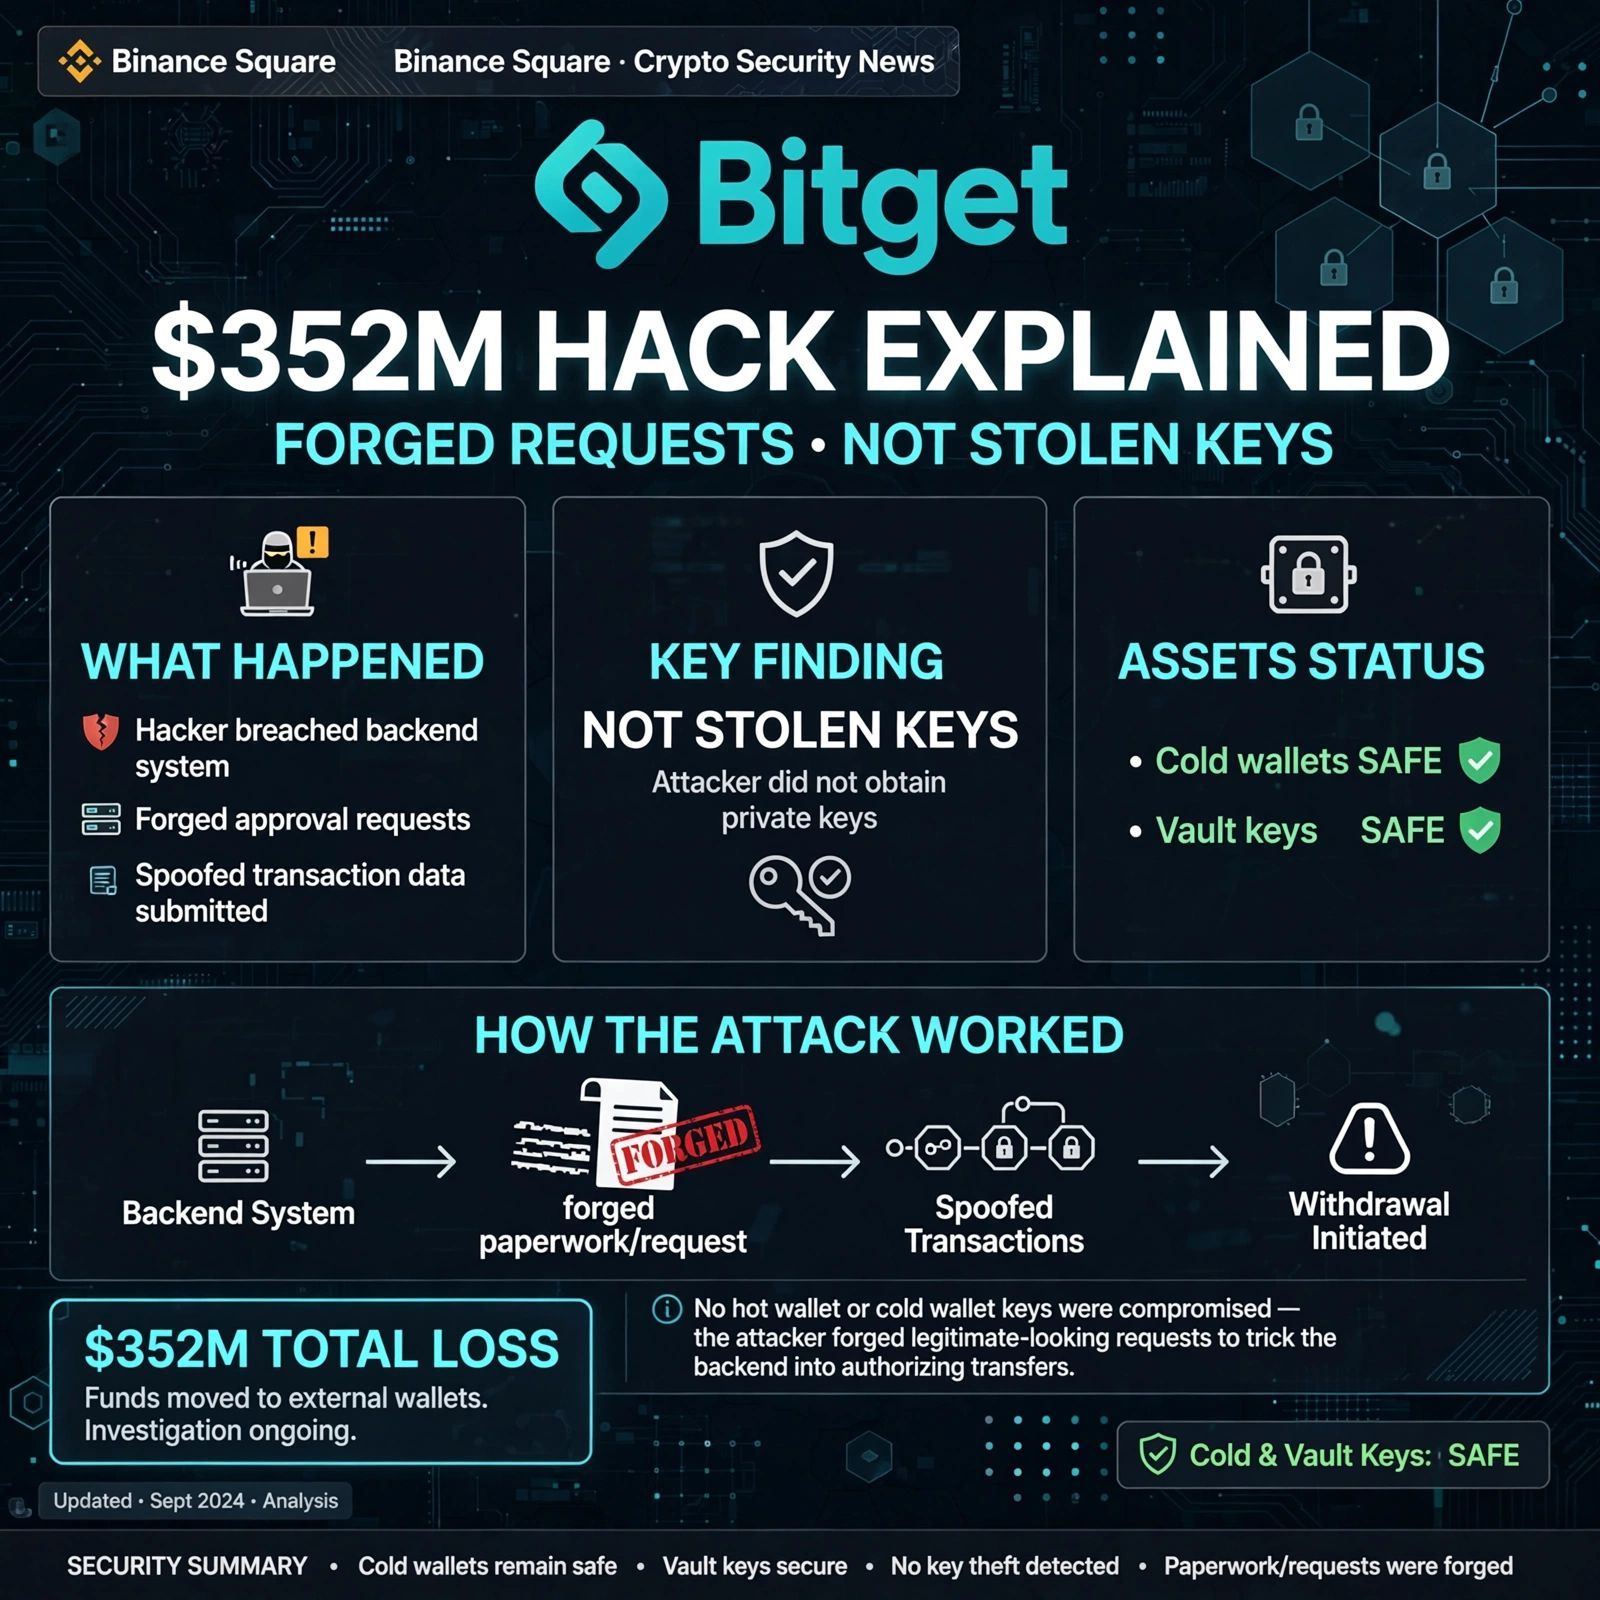
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
{future}(XRPUSDT)
{future}(TRXUSDT)
{future}(AVAXUSDT)
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
🚨 BITGET $352M HACK EXPLAINED: Forged Requests, NOT Stolen Keys!
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
Everyone is panicking about private keys. But Bitget CEO Gracy Chen just confirmed something scarier.
What Actually Happened:
❌ Private keys were NOT stolen (cold, hot & warm wallets safe)
❌ User withdrawal requests were NOT forged
✅ Hackers breached a CRITICAL backend system
✅ They spoofed transaction data
✅ They triggered Bitget's OWN authorization process to move $351.6M
Think of it like this: "They didn't crack the vault, they forged the paperwork." The vault keys never left the building, someone just created fake official slips.
Current Status:
Detected at 18:31 UTC, Sep 24
Cold wallets secure
$464M User Protection Fund will cover the loss
CEO links attack to North Korea via IP clues
What do you think - Should CEXs make their backend open-source?
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
4
8.7k
·
--
Bullish
#bitgetbreachforgedrequestsnotstolenkeys
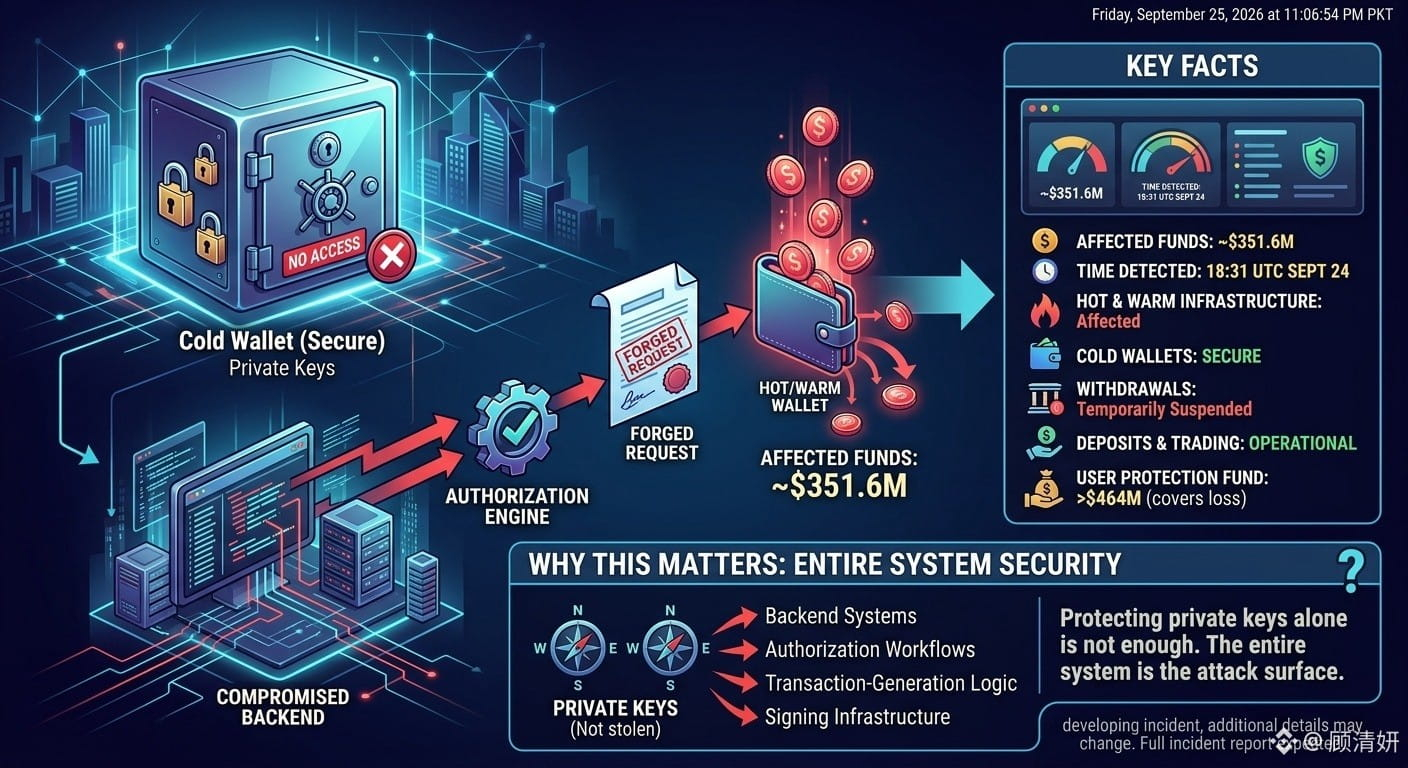
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
{future}(ARKUSDT)
{future}(PHAUSDT)
{spot}(QIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
FEDAT - sport digital assets marketplace:
То, что приватные ключи не были скомпрометированы, а атака шла через бэкенд и подделку запросов, — это критически важный нюанс. Это подтверждает, что безопасность CEX — это комплексная экосистема, а не просто хранение ключей. Хорошо, что фонд защиты покрывает убытки, но теперь прозрачность расследования важнее всего для восстановления доверия. 🚀🤝👍
3
3
6.5k
·
--
Bitget Reveals a Security Incident of $351.6 Million
Bitget reports that on September 24, 2026 at 18:31 UTC, its security system detected an unauthorized transfer involving a number of hot wallets.
🔹 Total assets affected: approximately $351.6 million
🔹 Bitget’s cold wallet and most of the platform’s assets remain safe
🔹 Bitget states that users’ funds are protected
🔹 The incident is covered by Bitget’s User Protection Fund, which is currently worth more than $464 million
🔹 Bitget’s security team has activated emergency response procedures and is conducting a full investigation
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
{future}(BABYUSDT)
$BTC
{future}(BTCUSDT)
Bitget Reveals a Security Incident of $351.6 Million
Bitget reports that on September 24, 2026 at 18:31 UTC, its security system detected an unauthorized transfer involving a number of hot wallets.
🔹 Total assets affected: approximately $351.6 million
🔹 Bitget’s cold wallet and most of the platform’s assets remain safe
🔹 Bitget states that users’ funds are protected
🔹 The incident is covered by Bitget’s User Protection Fund, which is currently worth more than $464 million
🔹 Bitget’s security team has activated emergency response procedures and is conducting a full investigation
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
$BTC
Bitget reports that on September 24, 2026 at 18:31 UTC, its security system detected an unauthorized transfer involving a number of hot wallets.
🔹 Total assets affected: approximately $351.6 million
🔹 Bitget’s cold wallet and most of the platform’s assets remain safe
🔹 Bitget states that users’ funds are protected
🔹 The incident is covered by Bitget’s User Protection Fund, which is currently worth more than $464 million
🔹 Bitget’s security team has activated emergency response procedures and is conducting a full investigation
#Bitge #Crypto #Binance #Bitcoin .#BitgetBreachForgedRequestsNotStolenKeys
$BABY
$BTC
202
#bitgetbreachforgedrequestsnotstolenkeys
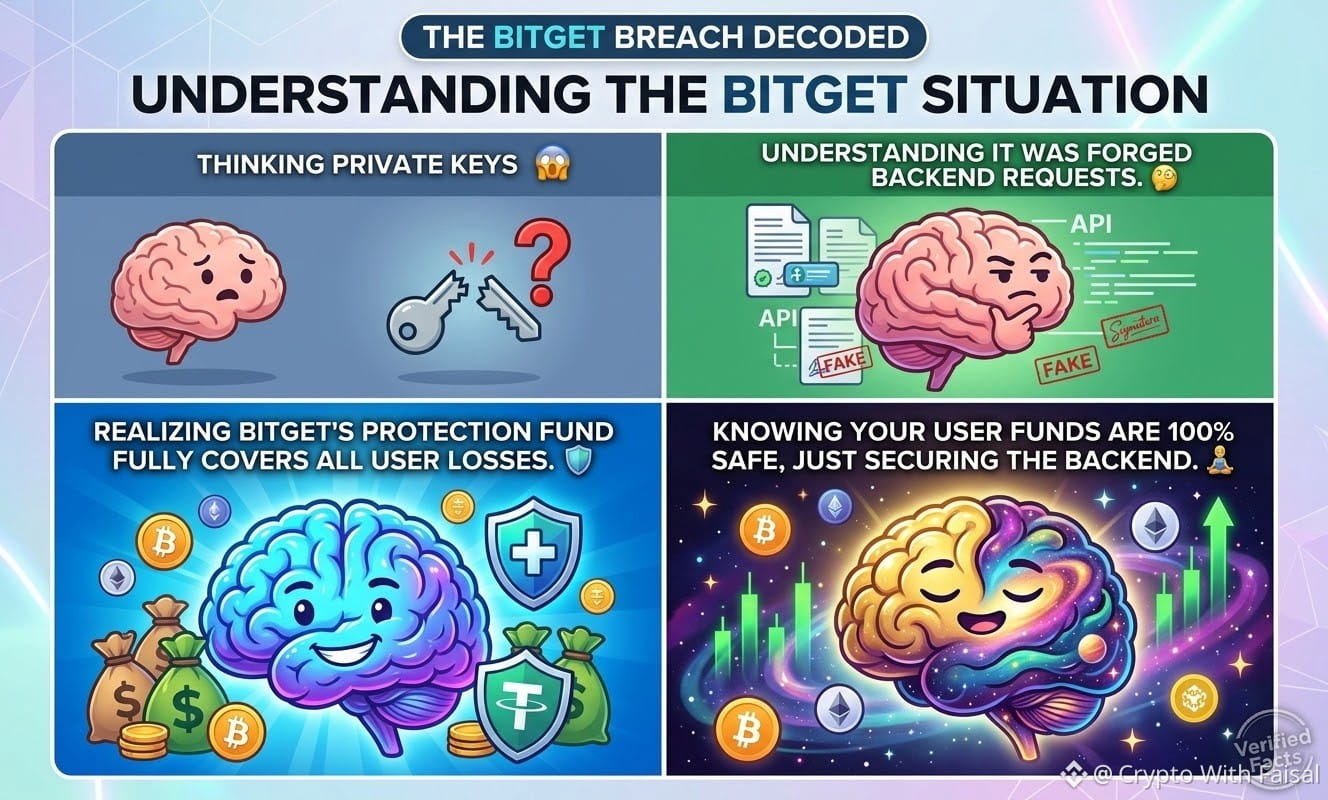
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
{future}(AVAXUSDT)
$LINK
{future}(LINKUSDT)
$ORDI
{future}(ORDIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
$LINK
$ORDI
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
$LINK
$ORDI
347

🚨 BITGET BREACH: FORGED REQUESTS — NOT STOLEN KEYS
A major security incident involving Bitget has put crypto exchange security back in the spotlight. ⚠️
💰 Reported impact: ~$351.6M
🔐 Private keys: Bitget says they were not stolen
⚙️ Attack method: Manipulated/forged transaction requests
🛡️ Response: Security investigation and protective measures
📌 Why it matters:
Crypto security isn't only about protecting private keys. If an attacker can manipulate the systems that create or authorize transactions, massive losses can still happen.
🔥 The big question:
Are centralized exchanges secure enough when their backend authorization systems are targeted?
#Binance #CryptoInvesting $BNB
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BITGET BREACH: FORGED REQUESTS — NOT STOLEN KEYS
A major security incident involving Bitget has put crypto exchange security back in the spotlight. ⚠️
💰 Reported impact: ~$351.6M
🔐 Private keys: Bitget says they were not stolen
⚙️ Attack method: Manipulated/forged transaction requests
🛡️ Response: Security investigation and protective measures
📌 Why it matters:
Crypto security isn't only about protecting private keys. If an attacker can manipulate the systems that create or authorize transactions, massive losses can still happen.
🔥 The big question:
Are centralized exchanges secure enough when their backend authorization systems are targeted?
#Binance #CryptoInvesting $BNB
#BitgetBreachForgedRequestsNotStolenKeys
A major security incident involving Bitget has put crypto exchange security back in the spotlight. ⚠️
💰 Reported impact: ~$351.6M
🔐 Private keys: Bitget says they were not stolen
⚙️ Attack method: Manipulated/forged transaction requests
🛡️ Response: Security investigation and protective measures
📌 Why it matters:
Crypto security isn't only about protecting private keys. If an attacker can manipulate the systems that create or authorize transactions, massive losses can still happen.
🔥 The big question:
Are centralized exchanges secure enough when their backend authorization systems are targeted?
#Binance #CryptoInvesting $BNB
#BitgetBreachForgedRequestsNotStolenKeys
14
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Helen_Alek @Square-Creator-f3ffb6967ae3 @qpl5557
$BTC
{spot}(BTCUSDT)
$BNB
{spot}(BNBUSDT)
$ADA
{spot}(ADAUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Hani Era @aasho @HK七匹狼
$BTC
$BNB
$ADA
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Hani Era @aasho @HK七匹狼
$BTC
$BNB
$ADA
38

·
--
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Crypto Security Alert & Breakdown: Bitget Incident Clarification 🔐
There has been a lot of talk in the market about the Bitget breach. According to reports, this issue happened due to Forged Requests—not because private keys (Stolen Keys) were stolen.
📌 Key Takeaways & Lessons for Traders:
• API & System Security: Exchanges need to conduct continuous security audits and strengthen request validation checks.
• Not Stolen Keys: Securing private keys is a positive sign, but security loopholes can be risky everywhere.
• Fund Safety First: Whenever such news comes up about any exchange, keep 2FA active on your accounts and always take extra precautions.
💡 Pro Security Tip:
Keep your large capital in Self-Custody / Hardware Wallets at all times, and use exchanges only for active trading!
💬 What do you think?
Do you keep funds on exchanges or do you prefer Cold Wallets? Let us know in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKey #CryptoSecurity #BinanceSquare #Write2Earn
$bitget
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Crypto Security Alert & Breakdown: Bitget Incident Clarification 🔐
There has been a lot of talk in the market about the Bitget breach. According to reports, this issue happened due to Forged Requests—not because private keys (Stolen Keys) were stolen.
📌 Key Takeaways & Lessons for Traders:
• API & System Security: Exchanges need to conduct continuous security audits and strengthen request validation checks.
• Not Stolen Keys: Securing private keys is a positive sign, but security loopholes can be risky everywhere.
• Fund Safety First: Whenever such news comes up about any exchange, keep 2FA active on your accounts and always take extra precautions.
💡 Pro Security Tip:
Keep your large capital in Self-Custody / Hardware Wallets at all times, and use exchanges only for active trading!
💬 What do you think?
Do you keep funds on exchanges or do you prefer Cold Wallets? Let us know in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKey #CryptoSecurity #BinanceSquare #Write2Earn
$bitget
🚨 Crypto Security Alert & Breakdown: Bitget Incident Clarification 🔐
There has been a lot of talk in the market about the Bitget breach. According to reports, this issue happened due to Forged Requests—not because private keys (Stolen Keys) were stolen.
📌 Key Takeaways & Lessons for Traders:
• API & System Security: Exchanges need to conduct continuous security audits and strengthen request validation checks.
• Not Stolen Keys: Securing private keys is a positive sign, but security loopholes can be risky everywhere.
• Fund Safety First: Whenever such news comes up about any exchange, keep 2FA active on your accounts and always take extra precautions.
💡 Pro Security Tip:
Keep your large capital in Self-Custody / Hardware Wallets at all times, and use exchanges only for active trading!
💬 What do you think?
Do you keep funds on exchanges or do you prefer Cold Wallets? Let us know in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKey #CryptoSecurity #BinanceSquare #Write2Earn
$bitget
24
#BitgetBreachForgedRequestsNotStolenKeys
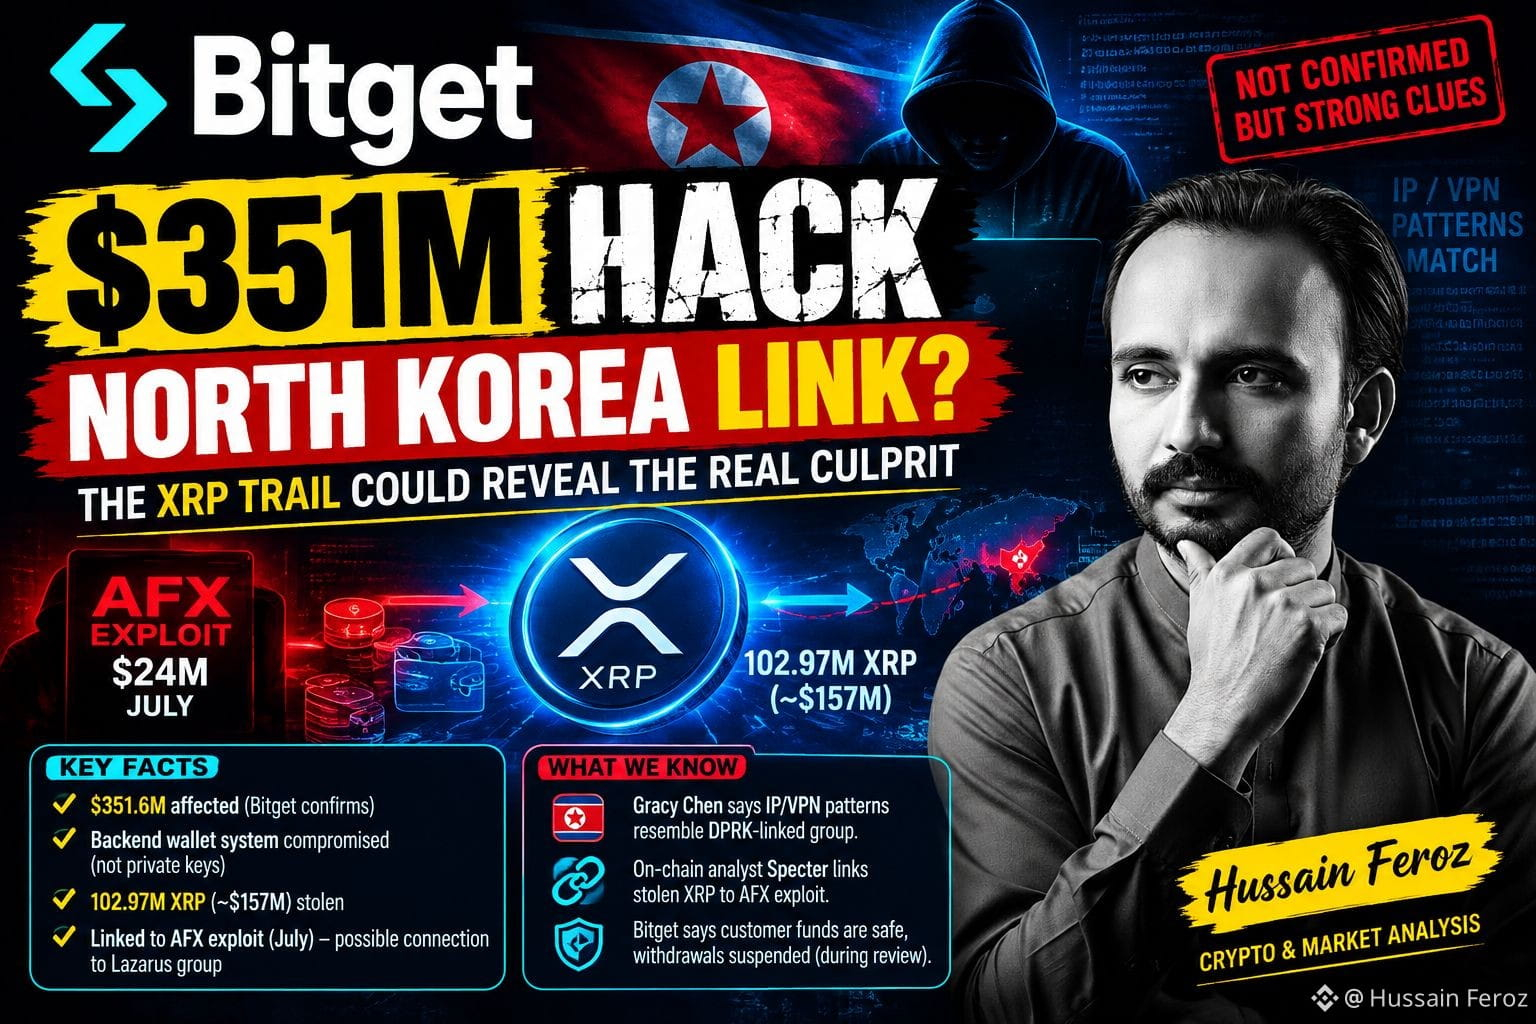
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
#BitgetBreachForgedRequestsNotStolenKeys
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
49
🚨#Bitget says an attacker compromised part of its hot/warm wallet infrastructure, triggering unauthorized transfers worth an estimated $351.6M.
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
🚨#Bitget says an attacker compromised part of its hot/warm wallet infrastructure, triggering unauthorized transfers worth an estimated $351.6M.
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
95
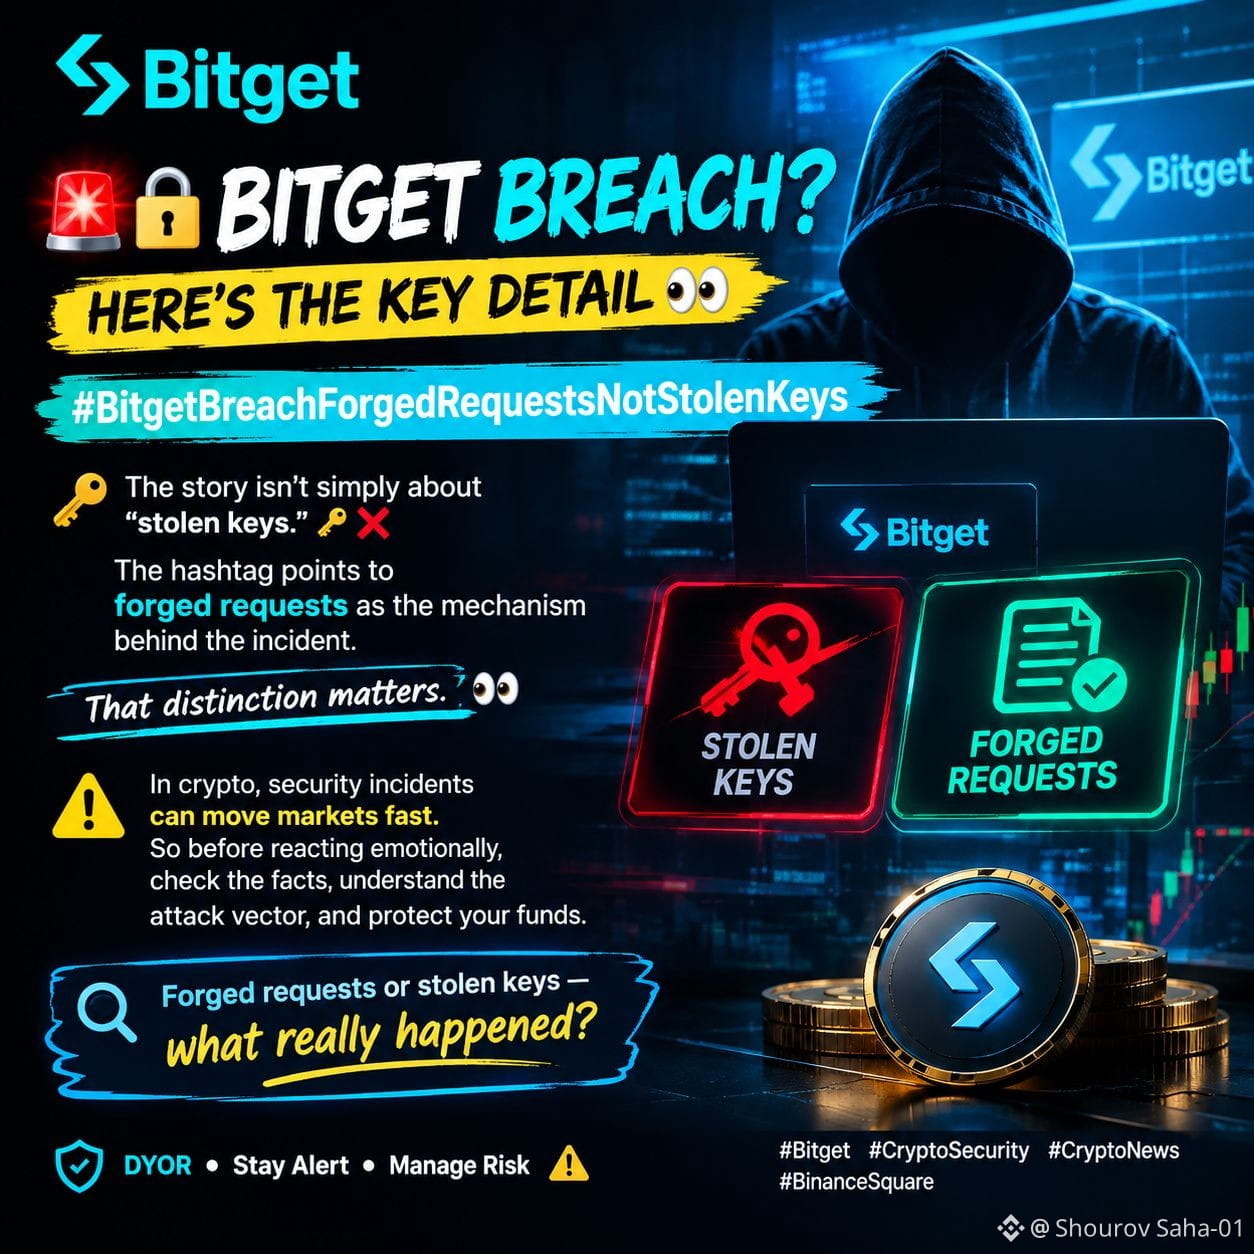
#BitgetBreachForgedRequestsNotStolenKeys
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
{future}(XRPUSDT)
$PHA
{future}(PHAUSDT)
$QI
{spot}(QIUSDT)
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
#BitgetBreachForgedRequestsNotStolenKeys
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
$PHA
$QI
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
$PHA
$QI
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
214
Article
🤝 Exchange CEOs such as Binance and Bybit cooperate with Bitget after suffering a $351.6 million hackThe community comes together to support Bitget after the attack it suffered
Leaders in the cryptocurrency industry expressed their support for the exchange following the vulnerability that resulted in the loss of USD 350 million.
Bitget works with external security firms.
Executives from Bybit, Binance, and MEXC offered Bitget resources for tracking and security.
The flaw affected the outflow of ETH, AVAX, BNB, and stablecoins, but did not impact private keys.
Various executives from cryptocurrency exchanges expressed operational and technical support for Bitget. The joint statement comes in response to a security breach that affected the service’s infrastructure.
🤝 Exchange CEOs such as Binance and Bybit cooperate with Bitget after suffering a $351.6 million hack
The community comes together to support Bitget after the attack it suffered
Leaders in the cryptocurrency industry expressed their support for the exchange following the vulnerability that resulted in the loss of USD 350 million.
Bitget works with external security firms.
Executives from Bybit, Binance, and MEXC offered Bitget resources for tracking and security.
The flaw affected the outflow of ETH, AVAX, BNB, and stablecoins, but did not impact private keys.
Various executives from cryptocurrency exchanges expressed operational and technical support for Bitget. The joint statement comes in response to a security breach that affected the service’s infrastructure.
Leaders in the cryptocurrency industry expressed their support for the exchange following the vulnerability that resulted in the loss of USD 350 million.
Bitget works with external security firms.
Executives from Bybit, Binance, and MEXC offered Bitget resources for tracking and security.
The flaw affected the outflow of ETH, AVAX, BNB, and stablecoins, but did not impact private keys.
Various executives from cryptocurrency exchanges expressed operational and technical support for Bitget. The joint statement comes in response to a security breach that affected the service’s infrastructure.
1
64
Recent discussions highlight a security incident at Bitget where forged requests, rather than stolen private keys, were the vector of attack. This distinction is crucial for understanding the nature of the breach and the effectiveness of current security protocols. While any breach is concerning, the fact that private keys remained secure suggests the core infrastructure might be more robust than initially feared. However, the ability to execute forged requests points to potential vulnerabilities in user verification, API integrations, or internal procedural controls that need immediate and thorough investigation. The market will be watching closely to see how Bitget addresses these issues and reinforces its systems to prevent recurrence. This event underscores the ongoing challenges in maintaining absolute security in the digital asset space, even for established platforms.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
Recent discussions highlight a security incident at Bitget where forged requests, rather than stolen private keys, were the vector of attack. This distinction is crucial for understanding the nature of the breach and the effectiveness of current security protocols. While any breach is concerning, the fact that private keys remained secure suggests the core infrastructure might be more robust than initially feared. However, the ability to execute forged requests points to potential vulnerabilities in user verification, API integrations, or internal procedural controls that need immediate and thorough investigation. The market will be watching closely to see how Bitget addresses these issues and reinforces its systems to prevent recurrence. This event underscores the ongoing challenges in maintaining absolute security in the digital asset space, even for established platforms.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
1
8
·
--
Bitget suffered a hack of more than $350M in its hot wallets!!😵
Exchange security is back at the center of the debate. Bitget reported a critical security breach in its internal authorization systems that compromised several of its hot wallets.
Multiple unauthorized transfers were detected following manipulation of the internal authorization system.
About $351.6 million was drained across various assets ($ETH $USDT, $USDC, $BNB $AVAX and $XAUT). These were quickly bridged and mixed on-chain.
Bitget’s directive confirmed that the cold reserves (cold wallets) were not compromised. They also announced that the losses will be covered 100% through their User Protection Fund (valued at ~$464M).
Withdrawals were temporarily paused as a precaution while the forensic audit concludes, although trading operations and deposits remain active.
On-chain analysts and sources linked to the investigation point to possible advanced international cybercrime groups (with patterns similar to North Korean attacks). A detailed technical report is expected within the next few hours.
Events like this remind us of the golden rule in crypto: "Not your keys, not your coins". Do you leave your funds on CEXs or transfer the gains directly to the cold wallet?
I’m reading your comments—please don’t burn your accounts plsss!
I love you❤️
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #Web3Revolution #CyberSecurity
Bitget suffered a hack of more than $350M in its hot wallets!!😵
Exchange security is back at the center of the debate. Bitget reported a critical security breach in its internal authorization systems that compromised several of its hot wallets.
Multiple unauthorized transfers were detected following manipulation of the internal authorization system.
About $351.6 million was drained across various assets ($ETH $USDT, $USDC, $BNB $AVAX and $XAUT). These were quickly bridged and mixed on-chain.
Bitget’s directive confirmed that the cold reserves (cold wallets) were not compromised. They also announced that the losses will be covered 100% through their User Protection Fund (valued at ~$464M).
Withdrawals were temporarily paused as a precaution while the forensic audit concludes, although trading operations and deposits remain active.
On-chain analysts and sources linked to the investigation point to possible advanced international cybercrime groups (with patterns similar to North Korean attacks). A detailed technical report is expected within the next few hours.
Events like this remind us of the golden rule in crypto: "Not your keys, not your coins". Do you leave your funds on CEXs or transfer the gains directly to the cold wallet?
I’m reading your comments—please don’t burn your accounts plsss!
I love you❤️
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #Web3Revolution #CyberSecurity
Exchange security is back at the center of the debate. Bitget reported a critical security breach in its internal authorization systems that compromised several of its hot wallets.
Multiple unauthorized transfers were detected following manipulation of the internal authorization system.
About $351.6 million was drained across various assets ($ETH $USDT, $USDC, $BNB $AVAX and $XAUT). These were quickly bridged and mixed on-chain.
Bitget’s directive confirmed that the cold reserves (cold wallets) were not compromised. They also announced that the losses will be covered 100% through their User Protection Fund (valued at ~$464M).
Withdrawals were temporarily paused as a precaution while the forensic audit concludes, although trading operations and deposits remain active.
On-chain analysts and sources linked to the investigation point to possible advanced international cybercrime groups (with patterns similar to North Korean attacks). A detailed technical report is expected within the next few hours.
Events like this remind us of the golden rule in crypto: "Not your keys, not your coins". Do you leave your funds on CEXs or transfer the gains directly to the cold wallet?
I’m reading your comments—please don’t burn your accounts plsss!
I love you❤️
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #Web3Revolution #CyberSecurity
1
54
Inside the Bitget Breach: Forged Requests, Not Stolen Keys! 🔐💥
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
Inside the Bitget Breach: Forged Requests, Not Stolen Keys! 🔐💥
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
61
#BitgetBreachForgedRequestsNotStolenKeys
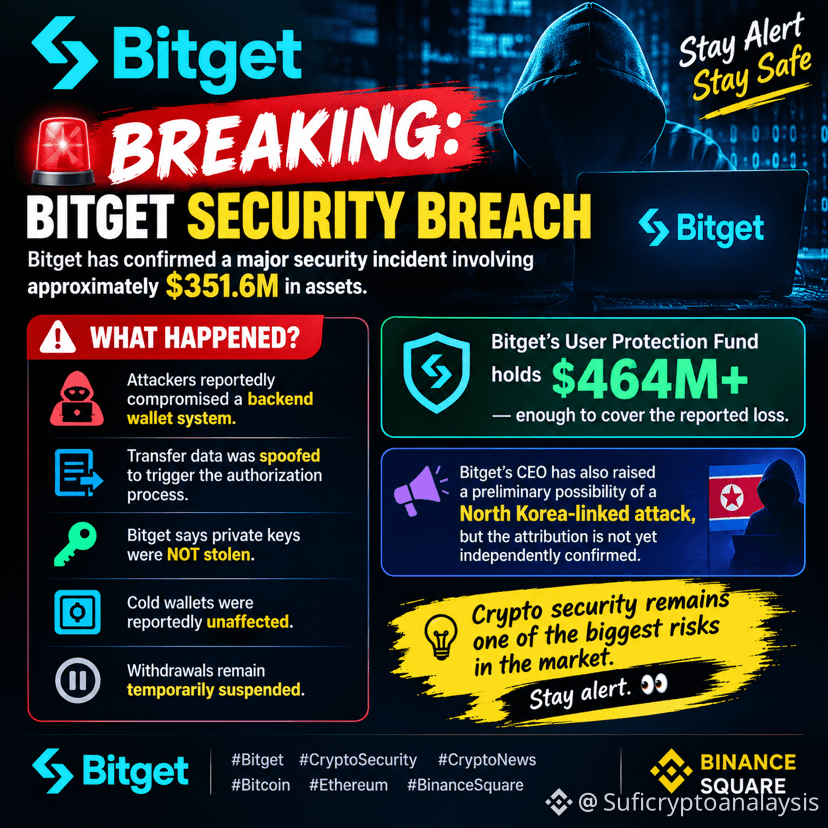
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
{spot}(BTCUSDT)
{spot}(NOTUSDT)
{spot}(ZECUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
35
*$351.6M lost (Bitget official) — on-chain tally $356.86M per Lookonchain — from hot + warm wallets — cold wallets secure — self-custodial Bitget Wallet separate infra not affected*
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
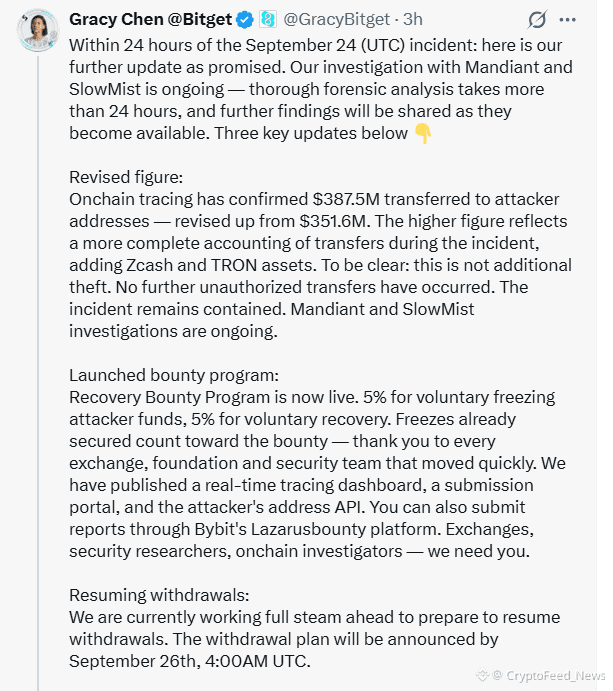
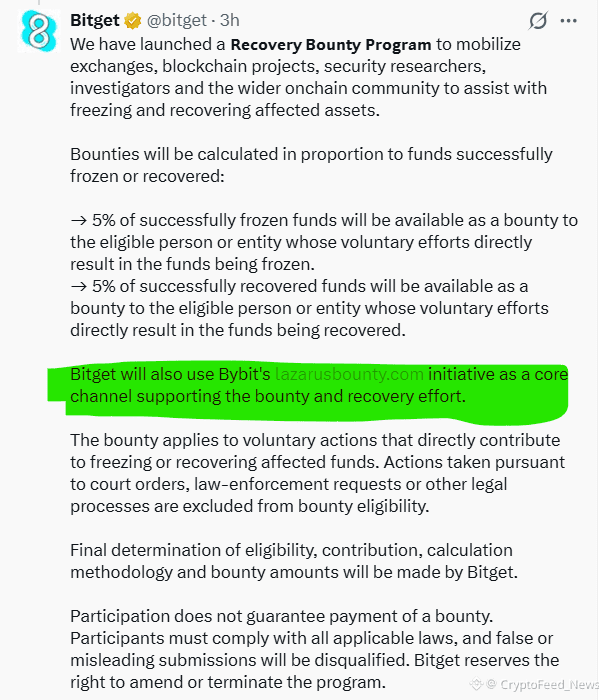
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
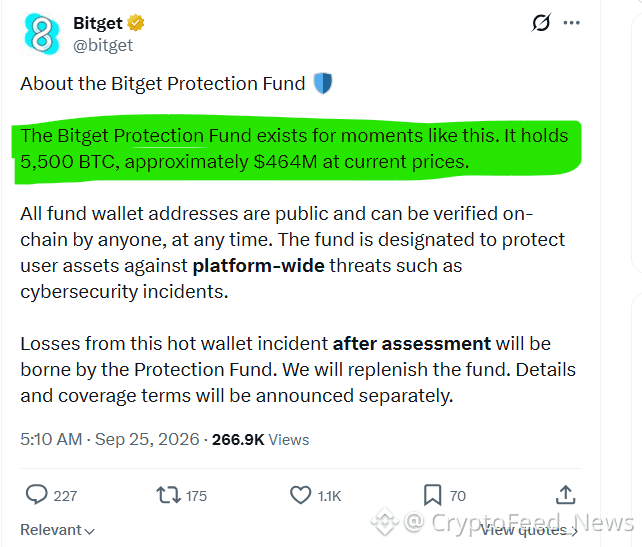
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
*$351.6M lost (Bitget official) — on-chain tally $356.86M per Lookonchain — from hot + warm wallets — cold wallets secure — self-custodial Bitget Wallet separate infra not affected*
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
- *Detected Sep 24 18:31 UTC unauthorized transfers — emergency team within minutes — withdrawals suspended precaution, deposits + trading normal* $QI $PHA $ARK
- *Method:* *CEO Gracy Chen: "Attacker compromised critical backend system within wallet infrastructure, used it to spoof transaction data, and triggered our authorization process to move funds out" — private key compromise ruled out — loss containment confirmed no further transfers possible*
- *Chains/assets:* *Ethereum (main concentration), XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base — ETH, XRP single-chain loss largest, BNB, AVAX, USDT, USDC, USDT0 on Arbitrum*
- *Attribution:* *Prelim North Korea — TraderTraitor/Lazarus cluster — some IPs matched VPN used by DPRK group — Chen: patterns "highly consistent" with DPRK — some hacker wallets already frozen per chains*
- *Investigators:* *Mandiant (Google) + SlowMist + law enforcement + Binance/Bybit on-chain — forensic analysis + tracing — full technical report promised within 24h*
- *User protection:* *User Protection Fund holds 5,500 BTC ∼$464M covers 100% loss — fund started 2022 $300M, avg $382M Aug 2026 — "User funds safe balances accurate" — Chen to Reuters Sep 25: withdrawal pause "not because of shortfall"*
*BREAKING 🚨 Bitget confirms $351.6M hack Sep 24 18:31 UTC hot/warm wallets — cold safe — attacker compromised backend wallet system spoofed transfer data triggered auth — private keys NOT stolen ⚡ Chains: ETH XRP ARB AVAX OP BSC Base — Suspected NK Lazarus TraderTraitor — Mandiant + SlowMist + LE tracing — withdrawals paused trading/deposits open — $464M protection fund 5.5k BTC covers loss — CEO Gracy Chen: contained 🚀*#QNTRises39% #BitgetBreachForgedRequestsNotStolenKeys #BitcoinSpotETFsTurnNetPositiveYTD
166
·
--
UPDATE: Bitget says 🇰🇵North Korean hackers may be behind the $351.6M breach, citing IP addresses linked to VPN services previously used by a DPRK hacking group.
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
UPDATE: Bitget says 🇰🇵North Korean hackers may be behind the $351.6M breach, citing IP addresses linked to VPN services previously used by a DPRK hacking group.
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
Attackers compromised a wallet-service backend to forge transfer data, but did not obtain wallet private keys.
Some stolen funds have already been recovered.#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare
40
#BitgetBreachForgedRequestsNotStolenKeys (Bitget Security Incident)
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
{future}(BTCUSDT)
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
#BitgetBreachForgedRequestsNotStolenKeys (Bitget Security Incident)
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
⚠️ $352M EXPLOIT CONCERNS & MARKET SAFETY! 🛡️
Reports are circulating regarding a $352M breach / forged request issue affecting Bitget. Security incidents like this serve as a critical reminder of why risk management and fund safety must always come first in crypto!
Whether you trade on CEXs or hold on cold storage, protecting your capital is Rule #1.
How do you manage your crypto storage risk during security headlines?
How do you manage your crypto storage risk during security headlines?
💬 DROP YOUR COMMENT: What is your go-to security setup for trading and storage? Share your best security tips below! 🗣️
#CryptoSecurity #Bitget #BinanceSquare #Web3
👇 VOTE IN THE POLL BELOW! 👇
Hardware / Cold Wallet 🔐
Split across multiple CEXs 🏦
100% on a single CEX 📱
18 hr(s) left
44
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#QNTRises39%
27,580 views
985 Discussing
2
#EthereumBreaksAbove$2700
2,623 views
100 Discussing
3
#BitgetBreachForgedRequestsNotStolenKeys
24,296 views
778 Discussing
4
#BitcoinSpotETFsTurnNetPositiveYTD
16,233 views
619 Discussing
5
#GrayscaleZcashETFHits$1BNetAssets
1,719 views
46 Discussing
6
#BitcoinSpotETFsNetInflow$191M
7,775 views
184 Discussing
7
#CFTCUpdatesGuidanceOnTokenizedAssets
56,151 views
1,562 Discussing
8
#BitgetSays$352MAffectedInHack
19,696 views
97 Discussing
9
#BinanceWillListHyperliquid(HYPE)
287,628 views
4,127 Discussing
10
#BrazilOrdersReportingOf$10KSelfCustodyTransfers
7,239 views
56 Discussing