

Lữ Khách Web3
338 Posts

Lữ Khách Web3
Report
Block User
Lữ Khách Onchain - Web3
Open Trade
High-Frequency Trader
3.8 Months
50 Following
154 Followers
431 Liked
Posts
Portfolio
There was one thing that made me pause when reading about Dusk Network: if a blockchain is built around transparency, why would a network aiming at institutional finance need to place privacy in such an important position?
At first, I thought it might just be product positioning. But after reading Dusk’s documents more closely, the issue became clearer. Dusk describes financial applications that need to protect balance, position, counterparty, and business logic instead of putting the entire state on a public ledger.
I kept checking how they handle this problem. Dusk doesn’t simply say “hide data.” The current architecture combines confidential transfers, zero-knowledge proofs, and selective disclosure. Some information can be kept private on-chain, while the information that is necessary can still be proven or disclosed in a controlled way.
What I didn’t expect is that privacy here isn’t set in total opposition to compliance. Citadel, for example, uses selective disclosure to prove attributes such as residency, age bracket, or accreditation without necessarily disclosing all the underlying data.
Hold on—this still isn’t enough to say that Dusk has solved the problem of sensitive data in institutional finance. Privacy also depends on how the applications are implemented and what metadata might still be exposed.
But after reading more deeply, I started to view the question differently: in on-chain finance, isn’t the real issue not “privacy vs. transparency,” but rather who can see which data, and under what circumstances?
#dusk $DUSK @Dusk_Foundation $BTC
There was one thing that made me pause when reading about Dusk Network: if a blockchain is built around transparency, why would a network aiming at institutional finance need to place privacy in such an important position?
At first, I thought it might just be product positioning. But after reading Dusk’s documents more closely, the issue became clearer. Dusk describes financial applications that need to protect balance, position, counterparty, and business logic instead of putting the entire state on a public ledger.
I kept checking how they handle this problem. Dusk doesn’t simply say “hide data.” The current architecture combines confidential transfers, zero-knowledge proofs, and selective disclosure. Some information can be kept private on-chain, while the information that is necessary can still be proven or disclosed in a controlled way.
What I didn’t expect is that privacy here isn’t set in total opposition to compliance. Citadel, for example, uses selective disclosure to prove attributes such as residency, age bracket, or accreditation without necessarily disclosing all the underlying data.
Hold on—this still isn’t enough to say that Dusk has solved the problem of sensitive data in institutional finance. Privacy also depends on how the applications are implemented and what metadata might still be exposed.
But after reading more deeply, I started to view the question differently: in on-chain finance, isn’t the real issue not “privacy vs. transparency,” but rather who can see which data, and under what circumstances?
#dusk $DUSK @Dusk $BTC
At first, I thought it might just be product positioning. But after reading Dusk’s documents more closely, the issue became clearer. Dusk describes financial applications that need to protect balance, position, counterparty, and business logic instead of putting the entire state on a public ledger.
I kept checking how they handle this problem. Dusk doesn’t simply say “hide data.” The current architecture combines confidential transfers, zero-knowledge proofs, and selective disclosure. Some information can be kept private on-chain, while the information that is necessary can still be proven or disclosed in a controlled way.
What I didn’t expect is that privacy here isn’t set in total opposition to compliance. Citadel, for example, uses selective disclosure to prove attributes such as residency, age bracket, or accreditation without necessarily disclosing all the underlying data.
Hold on—this still isn’t enough to say that Dusk has solved the problem of sensitive data in institutional finance. Privacy also depends on how the applications are implemented and what metadata might still be exposed.
But after reading more deeply, I started to view the question differently: in on-chain finance, isn’t the real issue not “privacy vs. transparency,” but rather who can see which data, and under what circumstances?
#dusk $DUSK @Dusk $BTC
2
1
236
Something makes me stop when reading Dusk’s docs. They continuously put privacy, compliance, and settlement into the same stack as if these three things couldn’t be separated.
Dusk is building an L1 for regulated finance. DuskDS forms the settlement and data availability layer with deterministic finality through Succinct Attestation. On top of that is a dual transaction model: Phoenix for shielded, Moonlight for transparent. Citadel handles selective disclosure. DuskEVM and DuskVM run execution, but everything ultimately settles to the same base.
I want to see whether combining these three actually comes from technical requirements or is just positioning for RWA. I read the core components, transaction models, and then compared them with how they describe the workflow of issuing and settling securities.
It turns out the architecture is modular, yet it still forces the privacy and compliance logic to sit close to the settlement layer. Phoenix uses ZK to hide amount and participants while still allowing an audit path. Compliance isn’t an add-on to the app; it’s designed to run in parallel with finality.
Wait, maybe this is just an implementation choice for institutional workflows rather than a mandatory rule. Many other chains separate privacy into an L2 or side system, while settlement remains public. Dusk chose to combine them because they’re targeting regulated assets, where sensitive data and finality must go together to avoid handoffs between multiple systems.
Looking broader, the industry is seeing similar patterns in a few other RWA protocols: marketing emphasizes “native privacy + compliance,” while real execution still depends on external licensing and familiar tooling.
Does settlement really need privacy embedded in the base layer, or is it enough to have an interface good enough for the upper layers to decide on their own?
#dusk $DUSK @Dusk_Foundation $BTC
Something makes me stop when reading Dusk’s docs. They continuously put privacy, compliance, and settlement into the same stack as if these three things couldn’t be separated.
Dusk is building an L1 for regulated finance. DuskDS forms the settlement and data availability layer with deterministic finality through Succinct Attestation. On top of that is a dual transaction model: Phoenix for shielded, Moonlight for transparent. Citadel handles selective disclosure. DuskEVM and DuskVM run execution, but everything ultimately settles to the same base.
I want to see whether combining these three actually comes from technical requirements or is just positioning for RWA. I read the core components, transaction models, and then compared them with how they describe the workflow of issuing and settling securities.
It turns out the architecture is modular, yet it still forces the privacy and compliance logic to sit close to the settlement layer. Phoenix uses ZK to hide amount and participants while still allowing an audit path. Compliance isn’t an add-on to the app; it’s designed to run in parallel with finality.
Wait, maybe this is just an implementation choice for institutional workflows rather than a mandatory rule. Many other chains separate privacy into an L2 or side system, while settlement remains public. Dusk chose to combine them because they’re targeting regulated assets, where sensitive data and finality must go together to avoid handoffs between multiple systems.
Looking broader, the industry is seeing similar patterns in a few other RWA protocols: marketing emphasizes “native privacy + compliance,” while real execution still depends on external licensing and familiar tooling.
Does settlement really need privacy embedded in the base layer, or is it enough to have an interface good enough for the upper layers to decide on their own?
#dusk $DUSK @Dusk $BTC
Dusk is building an L1 for regulated finance. DuskDS forms the settlement and data availability layer with deterministic finality through Succinct Attestation. On top of that is a dual transaction model: Phoenix for shielded, Moonlight for transparent. Citadel handles selective disclosure. DuskEVM and DuskVM run execution, but everything ultimately settles to the same base.
I want to see whether combining these three actually comes from technical requirements or is just positioning for RWA. I read the core components, transaction models, and then compared them with how they describe the workflow of issuing and settling securities.
It turns out the architecture is modular, yet it still forces the privacy and compliance logic to sit close to the settlement layer. Phoenix uses ZK to hide amount and participants while still allowing an audit path. Compliance isn’t an add-on to the app; it’s designed to run in parallel with finality.
Wait, maybe this is just an implementation choice for institutional workflows rather than a mandatory rule. Many other chains separate privacy into an L2 or side system, while settlement remains public. Dusk chose to combine them because they’re targeting regulated assets, where sensitive data and finality must go together to avoid handoffs between multiple systems.
Looking broader, the industry is seeing similar patterns in a few other RWA protocols: marketing emphasizes “native privacy + compliance,” while real execution still depends on external licensing and familiar tooling.
Does settlement really need privacy embedded in the base layer, or is it enough to have an interface good enough for the upper layers to decide on their own?
#dusk $DUSK @Dusk $BTC
1
2
224
Verified
Something made me stop when reading Dusk’s docs. Most L1 privacy solutions talk about shielded transactions, but here they emphasize selective disclosure and access control right from the protocol.
Dusk is a public, permissionless Layer1 focused on native issuance of digital securities and regulated assets. They have partnerships with NPEX (MTF, Broker, ECSP licenses), a dual Phoenix/Moonlight model, Citadel for identity, and they’re pushing DuskEVM. The mainnet is already running; the docs and GitHub Rusk are updated continuously. I want to see whether the architecture behind it is truly different from projects that only tack compliance onto the application layer. I read the overview, core components, then cross-referenced the news about NPEX and DLT-TSS. Turns out compliance is embedded in the protocol: eligibility, transfer restrictions, forced transfers, and the shareholder registry can be selectively decrypted.
Privacy isn’t absolute anonymity; it’s “private by default, auditable when required.” This is a different direction from most DeFi today.
However, maybe I’m over-interpreting. NPEX licenses belong to the partner, not something the protocol itself fully owns. DLT-TSS is still in progress—this could just be how they’re rolling it out for the European market. Many protocols are also shifting from pure DeFi to regulated infrastructure. Marketing often moves ahead of the actual product, while institutional adoption tends to lag far behind the narrative. Are we pricing the narrative of regulated DeFi, or are we measuring it by the actual asset volume truly settled onchain?
#dusk $DUSK @Dusk_Foundation $BTC
Something made me stop when reading Dusk’s docs. Most L1 privacy solutions talk about shielded transactions, but here they emphasize selective disclosure and access control right from the protocol.
Dusk is a public, permissionless Layer1 focused on native issuance of digital securities and regulated assets. They have partnerships with NPEX (MTF, Broker, ECSP licenses), a dual Phoenix/Moonlight model, Citadel for identity, and they’re pushing DuskEVM. The mainnet is already running; the docs and GitHub Rusk are updated continuously. I want to see whether the architecture behind it is truly different from projects that only tack compliance onto the application layer. I read the overview, core components, then cross-referenced the news about NPEX and DLT-TSS. Turns out compliance is embedded in the protocol: eligibility, transfer restrictions, forced transfers, and the shareholder registry can be selectively decrypted.
Privacy isn’t absolute anonymity; it’s “private by default, auditable when required.” This is a different direction from most DeFi today.
However, maybe I’m over-interpreting. NPEX licenses belong to the partner, not something the protocol itself fully owns. DLT-TSS is still in progress—this could just be how they’re rolling it out for the European market. Many protocols are also shifting from pure DeFi to regulated infrastructure. Marketing often moves ahead of the actual product, while institutional adoption tends to lag far behind the narrative. Are we pricing the narrative of regulated DeFi, or are we measuring it by the actual asset volume truly settled onchain?
#dusk $DUSK @Dusk $BTC
Dusk is a public, permissionless Layer1 focused on native issuance of digital securities and regulated assets. They have partnerships with NPEX (MTF, Broker, ECSP licenses), a dual Phoenix/Moonlight model, Citadel for identity, and they’re pushing DuskEVM. The mainnet is already running; the docs and GitHub Rusk are updated continuously. I want to see whether the architecture behind it is truly different from projects that only tack compliance onto the application layer. I read the overview, core components, then cross-referenced the news about NPEX and DLT-TSS. Turns out compliance is embedded in the protocol: eligibility, transfer restrictions, forced transfers, and the shareholder registry can be selectively decrypted.
Privacy isn’t absolute anonymity; it’s “private by default, auditable when required.” This is a different direction from most DeFi today.
However, maybe I’m over-interpreting. NPEX licenses belong to the partner, not something the protocol itself fully owns. DLT-TSS is still in progress—this could just be how they’re rolling it out for the European market. Many protocols are also shifting from pure DeFi to regulated infrastructure. Marketing often moves ahead of the actual product, while institutional adoption tends to lag far behind the narrative. Are we pricing the narrative of regulated DeFi, or are we measuring it by the actual asset volume truly settled onchain?
#dusk $DUSK @Dusk $BTC
280
There is one point that made me pause when reading about STOX. At first, I found it easy to categorize it as a DEX: a place to trade onchain assets—but when I went back to review Dusk’s documentation, that description began to feel like it was missing a few things.
STOX was once referred to by Dusk as an internal code name for a trading platform with the goal of bringing regulated assets onchain and enabling investors to trade. Today, this product is called Dusk Trade.
I then looked at what comes after the trading part. Dusk Trade is not only about buying and selling; the current documentation also lists investor onboarding, eligibility, wallet binding, controlled transfers, payment coordination, and settlement.
At this point, I had to revise my initial understanding. The difference doesn’t seem to be about “whether token trading exists,” but rather the rules that must accompany trading when the assets are regulated.
But I don’t want to overinterpret either. Dusk Trade is still under development, so we can’t yet conclude its real-world market effectiveness from the architecture that has been published.
What I find more worth watching is this: when eligibility, transfer rules, and settlement become part of the trading workflow, is the concept of a “DEX” still sufficient to describe this product?
#dusk $DUSK @Dusk_Foundation $BTC
There is one point that made me pause when reading about STOX. At first, I found it easy to categorize it as a DEX: a place to trade onchain assets—but when I went back to review Dusk’s documentation, that description began to feel like it was missing a few things.
STOX was once referred to by Dusk as an internal code name for a trading platform with the goal of bringing regulated assets onchain and enabling investors to trade. Today, this product is called Dusk Trade.
I then looked at what comes after the trading part. Dusk Trade is not only about buying and selling; the current documentation also lists investor onboarding, eligibility, wallet binding, controlled transfers, payment coordination, and settlement.
At this point, I had to revise my initial understanding. The difference doesn’t seem to be about “whether token trading exists,” but rather the rules that must accompany trading when the assets are regulated.
But I don’t want to overinterpret either. Dusk Trade is still under development, so we can’t yet conclude its real-world market effectiveness from the architecture that has been published.
What I find more worth watching is this: when eligibility, transfer rules, and settlement become part of the trading workflow, is the concept of a “DEX” still sufficient to describe this product?
#dusk $DUSK @Dusk $BTC
STOX was once referred to by Dusk as an internal code name for a trading platform with the goal of bringing regulated assets onchain and enabling investors to trade. Today, this product is called Dusk Trade.
I then looked at what comes after the trading part. Dusk Trade is not only about buying and selling; the current documentation also lists investor onboarding, eligibility, wallet binding, controlled transfers, payment coordination, and settlement.
At this point, I had to revise my initial understanding. The difference doesn’t seem to be about “whether token trading exists,” but rather the rules that must accompany trading when the assets are regulated.
But I don’t want to overinterpret either. Dusk Trade is still under development, so we can’t yet conclude its real-world market effectiveness from the architecture that has been published.
What I find more worth watching is this: when eligibility, transfer rules, and settlement become part of the trading workflow, is the concept of a “DEX” still sufficient to describe this product?
#dusk $DUSK @Dusk $BTC
207
I started reading Dusk Network from a fairly simple question: if RWA is truly brought onto the blockchain, what does that blockchain need to do besides merely recording tokens?
This question made me look at the issue differently—tokenization is only the first step. After the assets are represented on-chain, there are still things to handle: who is allowed to transact, how transactions are executed, whether the asset leg and the payment leg are synchronized, and finally where ownership is settled.
So instead of beginning with the story “Is Dusk a blockchain for RWA?”, I wanted to examine its architecture first.
In Dusk’s documentation, DuskDS handles consensus, finality, and data availability for Dusk L1, while DuskEVM provides an EVM-compatible environment for applications.
What’s noteworthy is that Dusk also describes market infrastructure, including onboarding steps, transfer controls, asset/payment coordination, and settlement.
By this point, I began to see a different approach: RWA doesn’t just need a place to issue tokens—it needs a processing layer that covers the entire lifecycle of transactions, though I still had a question lingering: is the architecture truly fit for real-world adoption?
So is Dusk building settlement infrastructure, or is it merely laying the groundwork for it?
#dusk $DUSK @Dusk_Foundation $BTC
I started reading Dusk Network from a fairly simple question: if RWA is truly brought onto the blockchain, what does that blockchain need to do besides merely recording tokens?
This question made me look at the issue differently—tokenization is only the first step. After the assets are represented on-chain, there are still things to handle: who is allowed to transact, how transactions are executed, whether the asset leg and the payment leg are synchronized, and finally where ownership is settled.
So instead of beginning with the story “Is Dusk a blockchain for RWA?”, I wanted to examine its architecture first.
In Dusk’s documentation, DuskDS handles consensus, finality, and data availability for Dusk L1, while DuskEVM provides an EVM-compatible environment for applications.
What’s noteworthy is that Dusk also describes market infrastructure, including onboarding steps, transfer controls, asset/payment coordination, and settlement.
By this point, I began to see a different approach: RWA doesn’t just need a place to issue tokens—it needs a processing layer that covers the entire lifecycle of transactions, though I still had a question lingering: is the architecture truly fit for real-world adoption?
So is Dusk building settlement infrastructure, or is it merely laying the groundwork for it?
#dusk $DUSK @Dusk $BTC
This question made me look at the issue differently—tokenization is only the first step. After the assets are represented on-chain, there are still things to handle: who is allowed to transact, how transactions are executed, whether the asset leg and the payment leg are synchronized, and finally where ownership is settled.
So instead of beginning with the story “Is Dusk a blockchain for RWA?”, I wanted to examine its architecture first.
In Dusk’s documentation, DuskDS handles consensus, finality, and data availability for Dusk L1, while DuskEVM provides an EVM-compatible environment for applications.
What’s noteworthy is that Dusk also describes market infrastructure, including onboarding steps, transfer controls, asset/payment coordination, and settlement.
By this point, I began to see a different approach: RWA doesn’t just need a place to issue tokens—it needs a processing layer that covers the entire lifecycle of transactions, though I still had a question lingering: is the architecture truly fit for real-world adoption?
So is Dusk building settlement infrastructure, or is it merely laying the groundwork for it?
#dusk $DUSK @Dusk $BTC
1
271
If you’re new to Binance P2P, there’s a habit I think you should start right away from your very first trades: in my opinion, don’t choose a seller just because they have a better price.
I used to think that a difference of a few coins wasn’t that much, so I would usually look at the price first and then check the other details. But after many trades, and when I read more carefully how Binance displays the data for each ad, I started to realize that what’s worth checking isn’t only the price level.
I tried to build a simple process for myself before each order—something you can refer to.
First, I look at the number of transactions and the completion rate. Then I read feedback, especially if there are negative responses that repeat.
Next, I check the order limits and whether the payment method is truly suitable.
More importantly, I cross-check the payment information and don’t intentionally move the conversation to Telegram or other platforms.
However, one thing I’ve found is that this data can’t turn a partner into “absolute safety”—it only gives us more basis to evaluate before trading.
For P2P transactions, in my view, the most important thing isn’t finding the cheapest seller, but forming the habit of checking before you press confirm.
I don’t know if these experiences help everyone, but at least that’s what I’ve learned after verifying it myself.
#binancep2pantoan @Binance_Vietnam $BTC
If you’re new to Binance P2P, there’s a habit I think you should start right away from your very first trades: in my opinion, don’t choose a seller just because they have a better price.
I used to think that a difference of a few coins wasn’t that much, so I would usually look at the price first and then check the other details. But after many trades, and when I read more carefully how Binance displays the data for each ad, I started to realize that what’s worth checking isn’t only the price level.
I tried to build a simple process for myself before each order—something you can refer to.
First, I look at the number of transactions and the completion rate. Then I read feedback, especially if there are negative responses that repeat.
Next, I check the order limits and whether the payment method is truly suitable.
More importantly, I cross-check the payment information and don’t intentionally move the conversation to Telegram or other platforms.
However, one thing I’ve found is that this data can’t turn a partner into “absolute safety”—it only gives us more basis to evaluate before trading.
For P2P transactions, in my view, the most important thing isn’t finding the cheapest seller, but forming the habit of checking before you press confirm.
I don’t know if these experiences help everyone, but at least that’s what I’ve learned after verifying it myself.
#binancep2pantoan @Binance Vietnam $BTC
I used to think that a difference of a few coins wasn’t that much, so I would usually look at the price first and then check the other details. But after many trades, and when I read more carefully how Binance displays the data for each ad, I started to realize that what’s worth checking isn’t only the price level.
I tried to build a simple process for myself before each order—something you can refer to.
First, I look at the number of transactions and the completion rate. Then I read feedback, especially if there are negative responses that repeat.
Next, I check the order limits and whether the payment method is truly suitable.
More importantly, I cross-check the payment information and don’t intentionally move the conversation to Telegram or other platforms.
However, one thing I’ve found is that this data can’t turn a partner into “absolute safety”—it only gives us more basis to evaluate before trading.
For P2P transactions, in my view, the most important thing isn’t finding the cheapest seller, but forming the habit of checking before you press confirm.
I don’t know if these experiences help everyone, but at least that’s what I’ve learned after verifying it myself.
#binancep2pantoan @Binance Vietnam $BTC
1
208
There’s one detail that made me re-read Dusk’s consensus section a few times. At first, I thought Succinct Attestation was just another name for PoS, but the internal flow has a few points worth noting.
According to the current documentation, DuskDS uses Succinct Attestation (SA), which Dusk describes clearly as a permissionless, committee-based Proof of Stake consensus protocol. A provisioner who wants to participate in consensus must stake at least 1,000 DUSK.
I went further into the process. A round isn’t simply validators voting on a block—it’s divided into three steps: Proposal, Validation, and Ratification. One provisioner proposes a block; then one committee checks it, followed by another committee confirming the result and finalizing the block. Once ratification is complete, Dusk achieves deterministic finality.
At this point, I had to revise my initial understanding.
SA isn’t “a completely different consensus from PoS.” The economic foundation is still staking; what Dusk re-designed is the committee selection, the separation of confirmation steps, and how blocks reach finality.
Hold on—this still isn’t enough to claim that SA is better than PoW or traditional PoS.
PoW relies on computational competition, and SA doesn’t need that mechanism. But saying that Dusk “replaces PoS with something entirely new” isn’t accurate.
What I find more worth researching is: when finality is designed to be deterministic, how does it change the settlement experience for financial applications?
#dusk $DUSK @Dusk_Foundation $BTC
There’s one detail that made me re-read Dusk’s consensus section a few times. At first, I thought Succinct Attestation was just another name for PoS, but the internal flow has a few points worth noting.
According to the current documentation, DuskDS uses Succinct Attestation (SA), which Dusk describes clearly as a permissionless, committee-based Proof of Stake consensus protocol. A provisioner who wants to participate in consensus must stake at least 1,000 DUSK.
I went further into the process. A round isn’t simply validators voting on a block—it’s divided into three steps: Proposal, Validation, and Ratification. One provisioner proposes a block; then one committee checks it, followed by another committee confirming the result and finalizing the block. Once ratification is complete, Dusk achieves deterministic finality.
At this point, I had to revise my initial understanding.
SA isn’t “a completely different consensus from PoS.” The economic foundation is still staking; what Dusk re-designed is the committee selection, the separation of confirmation steps, and how blocks reach finality.
Hold on—this still isn’t enough to claim that SA is better than PoW or traditional PoS.
PoW relies on computational competition, and SA doesn’t need that mechanism. But saying that Dusk “replaces PoS with something entirely new” isn’t accurate.
What I find more worth researching is: when finality is designed to be deterministic, how does it change the settlement experience for financial applications?
#dusk $DUSK @Dusk $BTC
According to the current documentation, DuskDS uses Succinct Attestation (SA), which Dusk describes clearly as a permissionless, committee-based Proof of Stake consensus protocol. A provisioner who wants to participate in consensus must stake at least 1,000 DUSK.
I went further into the process. A round isn’t simply validators voting on a block—it’s divided into three steps: Proposal, Validation, and Ratification. One provisioner proposes a block; then one committee checks it, followed by another committee confirming the result and finalizing the block. Once ratification is complete, Dusk achieves deterministic finality.
At this point, I had to revise my initial understanding.
SA isn’t “a completely different consensus from PoS.” The economic foundation is still staking; what Dusk re-designed is the committee selection, the separation of confirmation steps, and how blocks reach finality.
Hold on—this still isn’t enough to claim that SA is better than PoW or traditional PoS.
PoW relies on computational competition, and SA doesn’t need that mechanism. But saying that Dusk “replaces PoS with something entirely new” isn’t accurate.
What I find more worth researching is: when finality is designed to be deterministic, how does it change the settlement experience for financial applications?
#dusk $DUSK @Dusk $BTC
220
Verified
Something made me pause when reading about the Dusk Network. At first, I thought it was only a blockchain focused on privacy and asset tokenization, but when I cross-referenced the new docs, I realized Dusk positions itself in a much broader way.
Dusk describes itself as infrastructure for regulated digital assets and onchain finance, with a focus on privacy, access control, and deterministic settlement. This isn’t just a token story.
I started looking into the architecture. DuskDS handles consensus, finality, and data availability; DuskVM runs Rust/WASM smart contracts directly on L1; and DuskEVM provides an EVM-compatible environment, using DuskDS for settlement.
Then I dug deeper into regulated assets. The docs mention eligibility, wallet binding, transfer restrictions, disclosure, reporting, and settlement coordination. Privacy is also split into two directions: Moonlight for public transactions and Phoenix for shielded transfers.
Only then did I understand why Dusk doesn’t just talk about “putting assets on the blockchain.” They’re trying to bring the constraints of financial markets into onchain workflows.
But hold on—being designed for regulated finance doesn’t necessarily mean adoption has been proven.
Maybe the more worthwhile question to follow is: will these primitives really become infrastructure that financial markets use?
#dusk $DUSK @Dusk_Foundation $BTC
Something made me pause when reading about the Dusk Network. At first, I thought it was only a blockchain focused on privacy and asset tokenization, but when I cross-referenced the new docs, I realized Dusk positions itself in a much broader way.
Dusk describes itself as infrastructure for regulated digital assets and onchain finance, with a focus on privacy, access control, and deterministic settlement. This isn’t just a token story.
I started looking into the architecture. DuskDS handles consensus, finality, and data availability; DuskVM runs Rust/WASM smart contracts directly on L1; and DuskEVM provides an EVM-compatible environment, using DuskDS for settlement.
Then I dug deeper into regulated assets. The docs mention eligibility, wallet binding, transfer restrictions, disclosure, reporting, and settlement coordination. Privacy is also split into two directions: Moonlight for public transactions and Phoenix for shielded transfers.
Only then did I understand why Dusk doesn’t just talk about “putting assets on the blockchain.” They’re trying to bring the constraints of financial markets into onchain workflows.
But hold on—being designed for regulated finance doesn’t necessarily mean adoption has been proven.
Maybe the more worthwhile question to follow is: will these primitives really become infrastructure that financial markets use?
#dusk $DUSK @Dusk $BTC
Dusk describes itself as infrastructure for regulated digital assets and onchain finance, with a focus on privacy, access control, and deterministic settlement. This isn’t just a token story.
I started looking into the architecture. DuskDS handles consensus, finality, and data availability; DuskVM runs Rust/WASM smart contracts directly on L1; and DuskEVM provides an EVM-compatible environment, using DuskDS for settlement.
Then I dug deeper into regulated assets. The docs mention eligibility, wallet binding, transfer restrictions, disclosure, reporting, and settlement coordination. Privacy is also split into two directions: Moonlight for public transactions and Phoenix for shielded transfers.
Only then did I understand why Dusk doesn’t just talk about “putting assets on the blockchain.” They’re trying to bring the constraints of financial markets into onchain workflows.
But hold on—being designed for regulated finance doesn’t necessarily mean adoption has been proven.
Maybe the more worthwhile question to follow is: will these primitives really become infrastructure that financial markets use?
#dusk $DUSK @Dusk $BTC
1
1
91
At first glance, I thought Binance P2P only added a few extra layers of protection to peer-to-peer transactions. Escrow, verification, or Appeal were all pretty familiar concepts.
But the more closely I read, the more I realized there was a more interesting issue at play: what happens when the two parties no longer agree on the transaction.
At first, I assumed Chat and Appeal were simply tools for handling incidents afterward. Then I realized their value lies in helping the parties provide information and evidence for Binance to review when a dispute arises.
The complaint process can record processing steps, notes, and related evidence. This made me see Appeal differently: it’s not a mechanism that guarantees outcomes, but a procedure for reviewing what happened based on the information provided.
What concerns me again is user behavior. Binance also recommends not relying on screenshots or SMS to confirm payments, and to keep supporting documents when an Appeal may be needed.
Only then did I understand that the notable point is not just the technology. It lies in how the system maintains a process so that both sides can present evidence when disagreements occur.
The more I think about it, the more it feels like a coordination model rather than a feature—and perhaps the value of infrastructure only becomes truly visible when transactions are no longer straightforward.
#binancep2pantoan @Binance_Vietnam $BTC
At first glance, I thought Binance P2P only added a few extra layers of protection to peer-to-peer transactions. Escrow, verification, or Appeal were all pretty familiar concepts.
But the more closely I read, the more I realized there was a more interesting issue at play: what happens when the two parties no longer agree on the transaction.
At first, I assumed Chat and Appeal were simply tools for handling incidents afterward. Then I realized their value lies in helping the parties provide information and evidence for Binance to review when a dispute arises.
The complaint process can record processing steps, notes, and related evidence. This made me see Appeal differently: it’s not a mechanism that guarantees outcomes, but a procedure for reviewing what happened based on the information provided.
What concerns me again is user behavior. Binance also recommends not relying on screenshots or SMS to confirm payments, and to keep supporting documents when an Appeal may be needed.
Only then did I understand that the notable point is not just the technology. It lies in how the system maintains a process so that both sides can present evidence when disagreements occur.
The more I think about it, the more it feels like a coordination model rather than a feature—and perhaps the value of infrastructure only becomes truly visible when transactions are no longer straightforward.
#binancep2pantoan @Binance Vietnam $BTC
But the more closely I read, the more I realized there was a more interesting issue at play: what happens when the two parties no longer agree on the transaction.
At first, I assumed Chat and Appeal were simply tools for handling incidents afterward. Then I realized their value lies in helping the parties provide information and evidence for Binance to review when a dispute arises.
The complaint process can record processing steps, notes, and related evidence. This made me see Appeal differently: it’s not a mechanism that guarantees outcomes, but a procedure for reviewing what happened based on the information provided.
What concerns me again is user behavior. Binance also recommends not relying on screenshots or SMS to confirm payments, and to keep supporting documents when an Appeal may be needed.
Only then did I understand that the notable point is not just the technology. It lies in how the system maintains a process so that both sides can present evidence when disagreements occur.
The more I think about it, the more it feels like a coordination model rather than a feature—and perhaps the value of infrastructure only becomes truly visible when transactions are no longer straightforward.
#binancep2pantoan @Binance Vietnam $BTC
1
210
There’s a place that made me reread when I was learning about Dusk Network. I used to think tokenization was pretty simple: take an asset, create a token that represents it, then put the token on the blockchain.
But Dusk’s documentation defines it more precisely. Tokenization is the issuance of tokens that represent an asset—or rights to that asset. The issue is that for managed assets, custody, registry, and settlement can still sit outside the ledger.
I started looking at the rest of the lifecycle: issuance, eligibility, transfer restrictions, disclosure, trading, and settlement. These are also the workflows that Dusk includes in its market infrastructure design.
DuskDS handles settlement, finality, and data availability. Citadel provides identity and selective disclosure. Dusk Trade sits in the application layer, processing workflows such as onboarding, trading, and coordinating asset-payment settlement.
Turns out the point I initially missed wasn’t the token itself, but everything that happens before and after a transfer.
Hold on—this also doesn’t mean everything is automatically pushed on-chain. In fact, Dusk’s documentation says the specific architecture still depends on the product and regulatory requirements.
So the way I think about Dusk has changed a bit: tokenization here isn’t just about creating a representation—it’s about building the entire workflow around the asset.
So in the end, is the value in the token, or in the infrastructure that actually makes that token operable?
#dusk $DUSK @Dusk_Foundation $BTC
There’s a place that made me reread when I was learning about Dusk Network. I used to think tokenization was pretty simple: take an asset, create a token that represents it, then put the token on the blockchain.
But Dusk’s documentation defines it more precisely. Tokenization is the issuance of tokens that represent an asset—or rights to that asset. The issue is that for managed assets, custody, registry, and settlement can still sit outside the ledger.
I started looking at the rest of the lifecycle: issuance, eligibility, transfer restrictions, disclosure, trading, and settlement. These are also the workflows that Dusk includes in its market infrastructure design.
DuskDS handles settlement, finality, and data availability. Citadel provides identity and selective disclosure. Dusk Trade sits in the application layer, processing workflows such as onboarding, trading, and coordinating asset-payment settlement.
Turns out the point I initially missed wasn’t the token itself, but everything that happens before and after a transfer.
Hold on—this also doesn’t mean everything is automatically pushed on-chain. In fact, Dusk’s documentation says the specific architecture still depends on the product and regulatory requirements.
So the way I think about Dusk has changed a bit: tokenization here isn’t just about creating a representation—it’s about building the entire workflow around the asset.
So in the end, is the value in the token, or in the infrastructure that actually makes that token operable?
#dusk $DUSK @Dusk $BTC
But Dusk’s documentation defines it more precisely. Tokenization is the issuance of tokens that represent an asset—or rights to that asset. The issue is that for managed assets, custody, registry, and settlement can still sit outside the ledger.
I started looking at the rest of the lifecycle: issuance, eligibility, transfer restrictions, disclosure, trading, and settlement. These are also the workflows that Dusk includes in its market infrastructure design.
DuskDS handles settlement, finality, and data availability. Citadel provides identity and selective disclosure. Dusk Trade sits in the application layer, processing workflows such as onboarding, trading, and coordinating asset-payment settlement.
Turns out the point I initially missed wasn’t the token itself, but everything that happens before and after a transfer.
Hold on—this also doesn’t mean everything is automatically pushed on-chain. In fact, Dusk’s documentation says the specific architecture still depends on the product and regulatory requirements.
So the way I think about Dusk has changed a bit: tokenization here isn’t just about creating a representation—it’s about building the entire workflow around the asset.
So in the end, is the value in the token, or in the infrastructure that actually makes that token operable?
#dusk $DUSK @Dusk $BTC
2
2
82
I once placed a P2P order and found the payment method wasn’t suitable, so I intended to cancel. I thought it was just a normal action until I started asking myself: if anyone can cancel at will, how does Binance determine whether a merchant is trustworthy?
Previously, I often viewed canceling an order as straightforward—if I no longer wanted to proceed, I would cancel. But when I checked the Binance P2P Merchant Guidelines documentation, this way of thinking started to look problematic.
Binance states clearly that merchants are not allowed to “cancel orders arbitrarily.” In addition, the order completion rate over the past 30 days is one of the metrics used to evaluate merchants; a low completion rate may result in being removed from the merchant program.
I kept reading the trading principles to see whether Binance absolutely forbids canceling. It doesn’t—the documents still describe cases where merchants can cancel, for example when the counterparty’s payment account information does not meet the requirements or when the user refuses certain additional verification steps.
At this point, I had to adjust my initial understanding.
The issue isn’t that “canceling orders is wrong.” The issue is the word “arbitrarily.” Binance is distinguishing between a valid reason to terminate a trade and canceling an order without grounds.
Hold on—this still isn’t enough to say that canceling once will definitely be penalized. The documentation discusses evaluation criteria and violation scenarios, rather than simply punishing you for pressing cancel just once.
What’s probably more noteworthy is this: in P2P, an action that seems very small is actually placed within an entire system for assessing a merchant’s completion performance and reliability.
#binancep2pantoan @Binance_Vietnam $BTC
I once placed a P2P order and found the payment method wasn’t suitable, so I intended to cancel. I thought it was just a normal action until I started asking myself: if anyone can cancel at will, how does Binance determine whether a merchant is trustworthy?
Previously, I often viewed canceling an order as straightforward—if I no longer wanted to proceed, I would cancel. But when I checked the Binance P2P Merchant Guidelines documentation, this way of thinking started to look problematic.
Binance states clearly that merchants are not allowed to “cancel orders arbitrarily.” In addition, the order completion rate over the past 30 days is one of the metrics used to evaluate merchants; a low completion rate may result in being removed from the merchant program.
I kept reading the trading principles to see whether Binance absolutely forbids canceling. It doesn’t—the documents still describe cases where merchants can cancel, for example when the counterparty’s payment account information does not meet the requirements or when the user refuses certain additional verification steps.
At this point, I had to adjust my initial understanding.
The issue isn’t that “canceling orders is wrong.” The issue is the word “arbitrarily.” Binance is distinguishing between a valid reason to terminate a trade and canceling an order without grounds.
Hold on—this still isn’t enough to say that canceling once will definitely be penalized. The documentation discusses evaluation criteria and violation scenarios, rather than simply punishing you for pressing cancel just once.
What’s probably more noteworthy is this: in P2P, an action that seems very small is actually placed within an entire system for assessing a merchant’s completion performance and reliability.
#binancep2pantoan @Binance Vietnam $BTC
Previously, I often viewed canceling an order as straightforward—if I no longer wanted to proceed, I would cancel. But when I checked the Binance P2P Merchant Guidelines documentation, this way of thinking started to look problematic.
Binance states clearly that merchants are not allowed to “cancel orders arbitrarily.” In addition, the order completion rate over the past 30 days is one of the metrics used to evaluate merchants; a low completion rate may result in being removed from the merchant program.
I kept reading the trading principles to see whether Binance absolutely forbids canceling. It doesn’t—the documents still describe cases where merchants can cancel, for example when the counterparty’s payment account information does not meet the requirements or when the user refuses certain additional verification steps.
At this point, I had to adjust my initial understanding.
The issue isn’t that “canceling orders is wrong.” The issue is the word “arbitrarily.” Binance is distinguishing between a valid reason to terminate a trade and canceling an order without grounds.
Hold on—this still isn’t enough to say that canceling once will definitely be penalized. The documentation discusses evaluation criteria and violation scenarios, rather than simply punishing you for pressing cancel just once.
What’s probably more noteworthy is this: in P2P, an action that seems very small is actually placed within an entire system for assessing a merchant’s completion performance and reliability.
#binancep2pantoan @Binance Vietnam $BTC
1
186
Today I spent the whole afternoon poring over Dusk Network to take part in the Creatorpad program of the project on Binance.
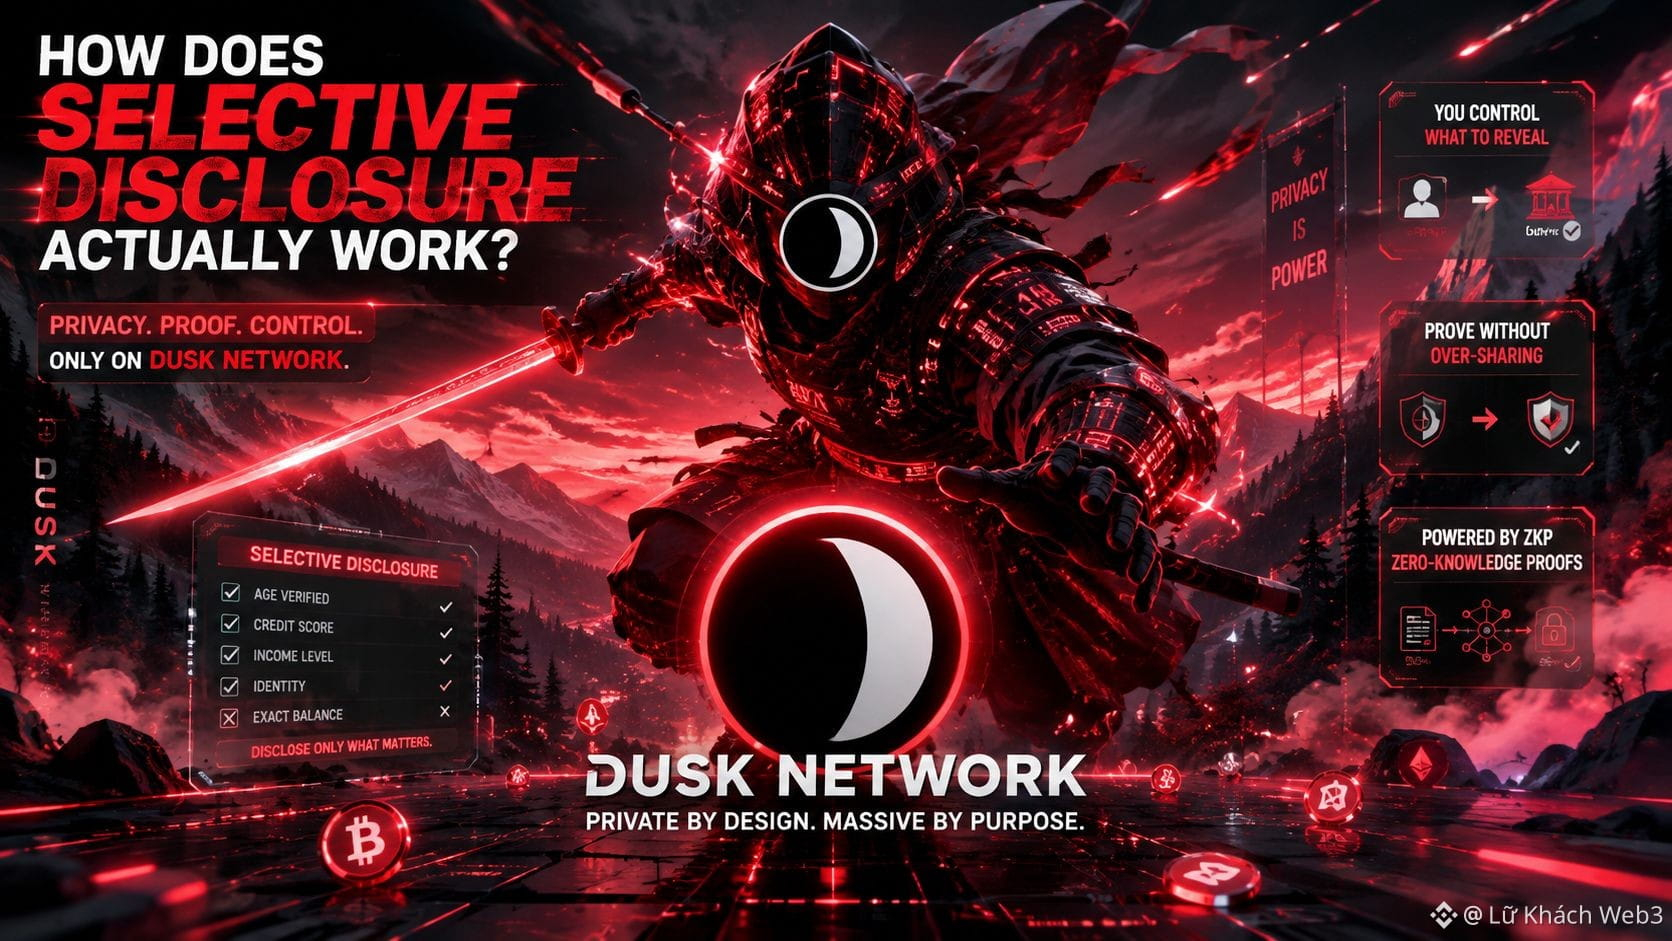
There’s one detail that made me re-read Dusk Network’s privacy section. “Selective Disclosure” sounds quite simple: keep private data private, but disclose it when needed. However, when I went through the docs, the way Dusk breaks down the components is different from what I initially imagined.
Dusk currently describes privacy in three directions: a public account with Moonlight, shielded transactions with Phoenix, and selective disclosure when an authorized party needs evidence.
I delved into Citadel because the docs specify that it’s the identity and access layer for selective disclosure. Citadel uses zero-knowledge proofs so users can prove they have a valid license without having to publicly reveal all identifying information.
The noteworthy point here is: in the docs, for example, it doesn’t say “disclose the entire identity.” The user creates a proof, and then the service provider checks the validity of the authorization through Citadel’s process.
Hold on—so that still doesn’t mean that every piece of data on Dusk is automatically and selectively disclosed. The docs only describe the primitives and patterns so application builders can create workflows that fit.
Maybe this is the key takeaway I need to keep: Dusk’s Selective Disclosure isn’t “privacy but with a public toggle,” but a way to separate the ability to prove some information from the act of publicly disclosing all information.
So the next question becomes more interesting: how far are these primitives actually implemented in real-world applications?
#dusk $DUSK @Dusk_Foundation $BTC
Today I spent the whole afternoon poring over Dusk Network to take part in the Creatorpad program of the project on Binance.
There’s one detail that made me re-read Dusk Network’s privacy section. “Selective Disclosure” sounds quite simple: keep private data private, but disclose it when needed. However, when I went through the docs, the way Dusk breaks down the components is different from what I initially imagined.
Dusk currently describes privacy in three directions: a public account with Moonlight, shielded transactions with Phoenix, and selective disclosure when an authorized party needs evidence.
I delved into Citadel because the docs specify that it’s the identity and access layer for selective disclosure. Citadel uses zero-knowledge proofs so users can prove they have a valid license without having to publicly reveal all identifying information.
The noteworthy point here is: in the docs, for example, it doesn’t say “disclose the entire identity.” The user creates a proof, and then the service provider checks the validity of the authorization through Citadel’s process.
Hold on—so that still doesn’t mean that every piece of data on Dusk is automatically and selectively disclosed. The docs only describe the primitives and patterns so application builders can create workflows that fit.
Maybe this is the key takeaway I need to keep: Dusk’s Selective Disclosure isn’t “privacy but with a public toggle,” but a way to separate the ability to prove some information from the act of publicly disclosing all information.
So the next question becomes more interesting: how far are these primitives actually implemented in real-world applications?
#dusk $DUSK @Dusk $BTC
There’s one detail that made me re-read Dusk Network’s privacy section. “Selective Disclosure” sounds quite simple: keep private data private, but disclose it when needed. However, when I went through the docs, the way Dusk breaks down the components is different from what I initially imagined.
Dusk currently describes privacy in three directions: a public account with Moonlight, shielded transactions with Phoenix, and selective disclosure when an authorized party needs evidence.
I delved into Citadel because the docs specify that it’s the identity and access layer for selective disclosure. Citadel uses zero-knowledge proofs so users can prove they have a valid license without having to publicly reveal all identifying information.
The noteworthy point here is: in the docs, for example, it doesn’t say “disclose the entire identity.” The user creates a proof, and then the service provider checks the validity of the authorization through Citadel’s process.
Hold on—so that still doesn’t mean that every piece of data on Dusk is automatically and selectively disclosed. The docs only describe the primitives and patterns so application builders can create workflows that fit.
Maybe this is the key takeaway I need to keep: Dusk’s Selective Disclosure isn’t “privacy but with a public toggle,” but a way to separate the ability to prove some information from the act of publicly disclosing all information.
So the next question becomes more interesting: how far are these primitives actually implemented in real-world applications?
#dusk $DUSK @Dusk $BTC
2
2
238
There is a fairly simple situation that made me change the way I think about choosing a counterparty on Binance P2P.
Suppose I need to buy 1,000 USDT and I see two ads with almost the same price. Ad A has completed around 2,800 trades, with a completion rate of 99.6%. Ad B, although it offers a slightly better price, has only 45 trades and a completion rate of 91%.
If I only look at the price, I could choose either one. But when I read Binance’s guidelines, I see that the platform recommends checking the completion rate, the total number of completed trades, and the counterparty feedback before making a trade.
I started looking at the two ads differently.
2,800 trades do not prove that A is definitely free of issues, but it gives me a larger amount of historical data to assess. Conversely, 45 trades and a lower completion rate give me less basis to trust the counterparty’s reliability.
Binance also shows data such as the number of trades in the past 30 days, the 30-day completion rate, and the average release time.
But hold on—these numbers are only signals, not a guarantee for the next trade.
I won’t treat the completion rate or the number of trades as a ticket that guarantees safety. They only provide me with more grounds for choosing, while the specific verification of the trade still depends on me.
#binancep2pantoan @Binance_Vietnam $BTC
There is a fairly simple situation that made me change the way I think about choosing a counterparty on Binance P2P.
Suppose I need to buy 1,000 USDT and I see two ads with almost the same price. Ad A has completed around 2,800 trades, with a completion rate of 99.6%. Ad B, although it offers a slightly better price, has only 45 trades and a completion rate of 91%.
If I only look at the price, I could choose either one. But when I read Binance’s guidelines, I see that the platform recommends checking the completion rate, the total number of completed trades, and the counterparty feedback before making a trade.
I started looking at the two ads differently.
2,800 trades do not prove that A is definitely free of issues, but it gives me a larger amount of historical data to assess. Conversely, 45 trades and a lower completion rate give me less basis to trust the counterparty’s reliability.
Binance also shows data such as the number of trades in the past 30 days, the 30-day completion rate, and the average release time.
But hold on—these numbers are only signals, not a guarantee for the next trade.
I won’t treat the completion rate or the number of trades as a ticket that guarantees safety. They only provide me with more grounds for choosing, while the specific verification of the trade still depends on me.
#binancep2pantoan @Binance Vietnam $BTC
Suppose I need to buy 1,000 USDT and I see two ads with almost the same price. Ad A has completed around 2,800 trades, with a completion rate of 99.6%. Ad B, although it offers a slightly better price, has only 45 trades and a completion rate of 91%.
If I only look at the price, I could choose either one. But when I read Binance’s guidelines, I see that the platform recommends checking the completion rate, the total number of completed trades, and the counterparty feedback before making a trade.
I started looking at the two ads differently.
2,800 trades do not prove that A is definitely free of issues, but it gives me a larger amount of historical data to assess. Conversely, 45 trades and a lower completion rate give me less basis to trust the counterparty’s reliability.
Binance also shows data such as the number of trades in the past 30 days, the 30-day completion rate, and the average release time.
But hold on—these numbers are only signals, not a guarantee for the next trade.
I won’t treat the completion rate or the number of trades as a ticket that guarantees safety. They only provide me with more grounds for choosing, while the specific verification of the trade still depends on me.
#binancep2pantoan @Binance Vietnam $BTC
131
There’s a detail that made me reread the Dusk architecture once more. At first, I thought DuskDS was simply the blockchain layer underneath DuskEVM, but the technical documentation describes it as something broader.
DuskDS is defined as the settlement and data availability layer of Dusk L1, responsible for consensus, finality, and the native transaction model. DuskEVM is the execution layer that uses DuskDS for settlement and data availability. DuskVM, on the other hand, executes contracts directly on Dusk L1.
I then dug deeper into how settlement is actually confirmed. DuskDS uses Succinct Attestation, a committee-based Proof-of-Stake mechanism. The process involves proposal, validation, and then ratification; once a block is ratified, finality is deterministic.
After that, I looked into the transaction model. Moonlight handles public accounts, while Phoenix uses shielded notes and zero-knowledge proofs. The two models are different, but in the end they both settle on the same chain.
Wait—this doesn’t mean DuskDS handles all application logic by itself. Execution still belongs to DuskVM or DuskEVM, but this is the part that changed how I see things: Dusk is separating execution rather clearly from settlement.
If so, the follow-up question is no longer whether DuskDS is the settlement layer, but rather: how will this settlement-splitting architecture make a real difference when financial applications start running at large scale?
#dusk $DUSK @Dusk_Foundation
There’s a detail that made me reread the Dusk architecture once more. At first, I thought DuskDS was simply the blockchain layer underneath DuskEVM, but the technical documentation describes it as something broader.
DuskDS is defined as the settlement and data availability layer of Dusk L1, responsible for consensus, finality, and the native transaction model. DuskEVM is the execution layer that uses DuskDS for settlement and data availability. DuskVM, on the other hand, executes contracts directly on Dusk L1.
I then dug deeper into how settlement is actually confirmed. DuskDS uses Succinct Attestation, a committee-based Proof-of-Stake mechanism. The process involves proposal, validation, and then ratification; once a block is ratified, finality is deterministic.
After that, I looked into the transaction model. Moonlight handles public accounts, while Phoenix uses shielded notes and zero-knowledge proofs. The two models are different, but in the end they both settle on the same chain.
Wait—this doesn’t mean DuskDS handles all application logic by itself. Execution still belongs to DuskVM or DuskEVM, but this is the part that changed how I see things: Dusk is separating execution rather clearly from settlement.
If so, the follow-up question is no longer whether DuskDS is the settlement layer, but rather: how will this settlement-splitting architecture make a real difference when financial applications start running at large scale?
#dusk $DUSK @Dusk
DuskDS is defined as the settlement and data availability layer of Dusk L1, responsible for consensus, finality, and the native transaction model. DuskEVM is the execution layer that uses DuskDS for settlement and data availability. DuskVM, on the other hand, executes contracts directly on Dusk L1.
I then dug deeper into how settlement is actually confirmed. DuskDS uses Succinct Attestation, a committee-based Proof-of-Stake mechanism. The process involves proposal, validation, and then ratification; once a block is ratified, finality is deterministic.
After that, I looked into the transaction model. Moonlight handles public accounts, while Phoenix uses shielded notes and zero-knowledge proofs. The two models are different, but in the end they both settle on the same chain.
Wait—this doesn’t mean DuskDS handles all application logic by itself. Execution still belongs to DuskVM or DuskEVM, but this is the part that changed how I see things: Dusk is separating execution rather clearly from settlement.
If so, the follow-up question is no longer whether DuskDS is the settlement layer, but rather: how will this settlement-splitting architecture make a real difference when financial applications start running at large scale?
#dusk $DUSK @Dusk
1
3
69
There’s a situation that new people selling USDT on Binance P2P are very likely to run into, and I’ve encountered it myself.
That was when I placed a sell order for 350 USDT. The buyer said they had transferred the money and immediately messaged: “Please check for me and release it, I really need the USDT urgently.”
A little while later, they sent me a screenshot of a successful bank transaction. I opened the image to check the amount, the time, and the recipient name. Everything looked reasonable, but when I opened my own banking app, the money still hadn’t shown up.
I’ll wait for the real money to appear in the receiving account instead of letting the other party’s urgency determine when I release.
The buyer could be completely honest, and maybe their bank transfer is just delayed.
I want to know whether that kind of pressure truly changes the process.
Re-reading the documentation, I saw that Binance recommends keeping the communication within the platform, checking the funds directly in the receiving account, and not relying on screenshots, SMS, or the other party’s confirmation to decide to release. If something is wrong, the transaction can be escalated to an appeal and evidence can be provided.
Hold on—this doesn’t mean that anyone who urges you is necessarily a scam. They might simply want the transaction to be completed quickly, but that’s exactly what caught my attention: escrow protects the asset, but it doesn’t replace the user’s verification step.
Looking at the bigger picture, P2P is still somewhat manual, so human pressure will always exist.
So I won’t let the other party’s urgency decide the transaction. I’ll only release once the money has entered my account. Maybe I’m a bit cautious, but in P2P, being cautious is better than trusting something I haven’t confirmed.
#binancep2pantoan @Binance_Vietnam $BTC
There’s a situation that new people selling USDT on Binance P2P are very likely to run into, and I’ve encountered it myself.
That was when I placed a sell order for 350 USDT. The buyer said they had transferred the money and immediately messaged: “Please check for me and release it, I really need the USDT urgently.”
A little while later, they sent me a screenshot of a successful bank transaction. I opened the image to check the amount, the time, and the recipient name. Everything looked reasonable, but when I opened my own banking app, the money still hadn’t shown up.
I’ll wait for the real money to appear in the receiving account instead of letting the other party’s urgency determine when I release.
The buyer could be completely honest, and maybe their bank transfer is just delayed.
I want to know whether that kind of pressure truly changes the process.
Re-reading the documentation, I saw that Binance recommends keeping the communication within the platform, checking the funds directly in the receiving account, and not relying on screenshots, SMS, or the other party’s confirmation to decide to release. If something is wrong, the transaction can be escalated to an appeal and evidence can be provided.
Hold on—this doesn’t mean that anyone who urges you is necessarily a scam. They might simply want the transaction to be completed quickly, but that’s exactly what caught my attention: escrow protects the asset, but it doesn’t replace the user’s verification step.
Looking at the bigger picture, P2P is still somewhat manual, so human pressure will always exist.
So I won’t let the other party’s urgency decide the transaction. I’ll only release once the money has entered my account. Maybe I’m a bit cautious, but in P2P, being cautious is better than trusting something I haven’t confirmed.
#binancep2pantoan @Binance Vietnam $BTC
That was when I placed a sell order for 350 USDT. The buyer said they had transferred the money and immediately messaged: “Please check for me and release it, I really need the USDT urgently.”
A little while later, they sent me a screenshot of a successful bank transaction. I opened the image to check the amount, the time, and the recipient name. Everything looked reasonable, but when I opened my own banking app, the money still hadn’t shown up.
I’ll wait for the real money to appear in the receiving account instead of letting the other party’s urgency determine when I release.
The buyer could be completely honest, and maybe their bank transfer is just delayed.
I want to know whether that kind of pressure truly changes the process.
Re-reading the documentation, I saw that Binance recommends keeping the communication within the platform, checking the funds directly in the receiving account, and not relying on screenshots, SMS, or the other party’s confirmation to decide to release. If something is wrong, the transaction can be escalated to an appeal and evidence can be provided.
Hold on—this doesn’t mean that anyone who urges you is necessarily a scam. They might simply want the transaction to be completed quickly, but that’s exactly what caught my attention: escrow protects the asset, but it doesn’t replace the user’s verification step.
Looking at the bigger picture, P2P is still somewhat manual, so human pressure will always exist.
So I won’t let the other party’s urgency decide the transaction. I’ll only release once the money has entered my account. Maybe I’m a bit cautious, but in P2P, being cautious is better than trusting something I haven’t confirmed.
#binancep2pantoan @Binance Vietnam $BTC
1
188
There is a detail that made me pause when reading about the Dusk Network: they don’t define privacy simply as hiding all data, but as placing it alongside the possibility of selectively disclosing it.
I reread the architecture and found that DuskDS supports two fairly different transaction models. Moonlight is public, while Phoenix uses shielded notes and zero-knowledge proofs so that the amount, the sender, or the connections between notes are not made public.
What I want to check is whether this privacy is truly tied to the requirements of financial markets, or if it’s just a technical feature.
In the documentation on regulated assets, Dusk describes a very practical scenario: an investor doesn’t need every participant to see the entire balance or transactions, but an issuer, venue, or auditor may still need some specific information. Dusk calls this approach selective disclosure.
Hold on—so I shouldn’t assume from that that financial institutions have actually used Dusk at real scale.
But I did notice something noteworthy about how the problem is framed: privacy doesn’t necessarily oppose transparency. A system can keep data private in transactions while still enabling proofs or information to be provided to the right parties.
If so, the next question I still want to check is: in regulated finance, when does privacy really matter—when data needs to be protected, or when it needs to be disclosed to the right people?
#dusk $DUSK @Dusk_Foundation
There is a detail that made me pause when reading about the Dusk Network: they don’t define privacy simply as hiding all data, but as placing it alongside the possibility of selectively disclosing it.
I reread the architecture and found that DuskDS supports two fairly different transaction models. Moonlight is public, while Phoenix uses shielded notes and zero-knowledge proofs so that the amount, the sender, or the connections between notes are not made public.
What I want to check is whether this privacy is truly tied to the requirements of financial markets, or if it’s just a technical feature.
In the documentation on regulated assets, Dusk describes a very practical scenario: an investor doesn’t need every participant to see the entire balance or transactions, but an issuer, venue, or auditor may still need some specific information. Dusk calls this approach selective disclosure.
Hold on—so I shouldn’t assume from that that financial institutions have actually used Dusk at real scale.
But I did notice something noteworthy about how the problem is framed: privacy doesn’t necessarily oppose transparency. A system can keep data private in transactions while still enabling proofs or information to be provided to the right parties.
If so, the next question I still want to check is: in regulated finance, when does privacy really matter—when data needs to be protected, or when it needs to be disclosed to the right people?
#dusk $DUSK @Dusk
I reread the architecture and found that DuskDS supports two fairly different transaction models. Moonlight is public, while Phoenix uses shielded notes and zero-knowledge proofs so that the amount, the sender, or the connections between notes are not made public.
What I want to check is whether this privacy is truly tied to the requirements of financial markets, or if it’s just a technical feature.
In the documentation on regulated assets, Dusk describes a very practical scenario: an investor doesn’t need every participant to see the entire balance or transactions, but an issuer, venue, or auditor may still need some specific information. Dusk calls this approach selective disclosure.
Hold on—so I shouldn’t assume from that that financial institutions have actually used Dusk at real scale.
But I did notice something noteworthy about how the problem is framed: privacy doesn’t necessarily oppose transparency. A system can keep data private in transactions while still enabling proofs or information to be provided to the right parties.
If so, the next question I still want to check is: in regulated finance, when does privacy really matter—when data needs to be protected, or when it needs to be disclosed to the right people?
#dusk $DUSK @Dusk
4
2
97
I once encountered a situation that made me reread the Binance P2P process. It happened when I sold 200 USDT after winning a Binance Alpha airdrop. The buyer sent me a screenshot saying the funds had been transferred and urged me to release the crypto. At first glance, everything looked quite normal, but when I checked the receiving account directly, I realized that amount of money had not appeared at all.
From that situation, I started paying closer attention to a detail in Binance’s instructions: sellers should only release crypto after they themselves have confirmed that they truly received the money.
I reread Binance’s guide and found the process quite clear. When selling, the crypto is held in escrow. The seller waits for the payment to arrive at the agreed-upon method, then confirms that the funds have actually been received before releasing.
I wanted to understand why this confirmation step is placed before the release, instead of relying only on the message “payment has been made.”
When I looked further into P2P safety documentation, the reason became clearer. Binance warns about fake payment confirmations and recommends checking the receiving account directly rather than trusting screenshots, receipts, or SMS.
Turns out, escrow doesn’t mean the seller can skip the final verification step. Escrow holds the crypto during the transaction, but whether the fiat money has truly arrived still needs to be checked by the recipient.
Looking at it more broadly, P2P always has a portion of responsibility on the user. Perhaps in P2P, safety isn’t about trusting that the system has handled all risks, but about continuing to verify what the system cannot confirm on your behalf.
#binancep2pantoan @Binance_Vietnam $BTC
I once encountered a situation that made me reread the Binance P2P process. It happened when I sold 200 USDT after winning a Binance Alpha airdrop. The buyer sent me a screenshot saying the funds had been transferred and urged me to release the crypto. At first glance, everything looked quite normal, but when I checked the receiving account directly, I realized that amount of money had not appeared at all.
From that situation, I started paying closer attention to a detail in Binance’s instructions: sellers should only release crypto after they themselves have confirmed that they truly received the money.
I reread Binance’s guide and found the process quite clear. When selling, the crypto is held in escrow. The seller waits for the payment to arrive at the agreed-upon method, then confirms that the funds have actually been received before releasing.
I wanted to understand why this confirmation step is placed before the release, instead of relying only on the message “payment has been made.”
When I looked further into P2P safety documentation, the reason became clearer. Binance warns about fake payment confirmations and recommends checking the receiving account directly rather than trusting screenshots, receipts, or SMS.
Turns out, escrow doesn’t mean the seller can skip the final verification step. Escrow holds the crypto during the transaction, but whether the fiat money has truly arrived still needs to be checked by the recipient.
Looking at it more broadly, P2P always has a portion of responsibility on the user. Perhaps in P2P, safety isn’t about trusting that the system has handled all risks, but about continuing to verify what the system cannot confirm on your behalf.
#binancep2pantoan @Binance Vietnam $BTC
From that situation, I started paying closer attention to a detail in Binance’s instructions: sellers should only release crypto after they themselves have confirmed that they truly received the money.
I reread Binance’s guide and found the process quite clear. When selling, the crypto is held in escrow. The seller waits for the payment to arrive at the agreed-upon method, then confirms that the funds have actually been received before releasing.
I wanted to understand why this confirmation step is placed before the release, instead of relying only on the message “payment has been made.”
When I looked further into P2P safety documentation, the reason became clearer. Binance warns about fake payment confirmations and recommends checking the receiving account directly rather than trusting screenshots, receipts, or SMS.
Turns out, escrow doesn’t mean the seller can skip the final verification step. Escrow holds the crypto during the transaction, but whether the fiat money has truly arrived still needs to be checked by the recipient.
Looking at it more broadly, P2P always has a portion of responsibility on the user. Perhaps in P2P, safety isn’t about trusting that the system has handled all risks, but about continuing to verify what the system cannot confirm on your behalf.
#binancep2pantoan @Binance Vietnam $BTC
1
174
Something made me pause when reading the architecture of the Dusk Network. At first, I still saw it as a familiar Layer 1: consensus, smart contracts, a token, and an ecosystem built on top.
But when I read it more closely, the way Dusk breaks down its components made me read it again from the start.
Dusk’s docs describe DuskDS as the settlement and data availability layer, responsible for consensus, finality, and Dusk L1’s transaction model, while execution is split into two directions: DuskVM for Rust/WASM running directly on L1, and DuskEVM for an Ethereum-compatible EVM environment.
I started digging because I wanted to understand whether this is just a reorganization of a Layer 1 or whether it truly reflects a different architectural choice.
The point I found is quite clear: Dusk doesn’t bundle all execution into a single environment. DuskDS handles consensus, settlement, and data availability, while DuskVM and DuskEVM handle different execution models.
Wait, that still isn’t enough to say that architecture is better, but it does change how I see Dusk. Maybe the more interesting question isn’t “Is Dusk a Layer 1?” but rather: what would separating settlement from execution actually bring when these execution environments start seeing significant usage?
#dusk $DUSK @Dusk_Foundation $BTC
Something made me pause when reading the architecture of the Dusk Network. At first, I still saw it as a familiar Layer 1: consensus, smart contracts, a token, and an ecosystem built on top.
But when I read it more closely, the way Dusk breaks down its components made me read it again from the start.
Dusk’s docs describe DuskDS as the settlement and data availability layer, responsible for consensus, finality, and Dusk L1’s transaction model, while execution is split into two directions: DuskVM for Rust/WASM running directly on L1, and DuskEVM for an Ethereum-compatible EVM environment.
I started digging because I wanted to understand whether this is just a reorganization of a Layer 1 or whether it truly reflects a different architectural choice.
The point I found is quite clear: Dusk doesn’t bundle all execution into a single environment. DuskDS handles consensus, settlement, and data availability, while DuskVM and DuskEVM handle different execution models.
Wait, that still isn’t enough to say that architecture is better, but it does change how I see Dusk. Maybe the more interesting question isn’t “Is Dusk a Layer 1?” but rather: what would separating settlement from execution actually bring when these execution environments start seeing significant usage?
#dusk $DUSK @Dusk $BTC
But when I read it more closely, the way Dusk breaks down its components made me read it again from the start.
Dusk’s docs describe DuskDS as the settlement and data availability layer, responsible for consensus, finality, and Dusk L1’s transaction model, while execution is split into two directions: DuskVM for Rust/WASM running directly on L1, and DuskEVM for an Ethereum-compatible EVM environment.
I started digging because I wanted to understand whether this is just a reorganization of a Layer 1 or whether it truly reflects a different architectural choice.
The point I found is quite clear: Dusk doesn’t bundle all execution into a single environment. DuskDS handles consensus, settlement, and data availability, while DuskVM and DuskEVM handle different execution models.
Wait, that still isn’t enough to say that architecture is better, but it does change how I see Dusk. Maybe the more interesting question isn’t “Is Dusk a Layer 1?” but rather: what would separating settlement from execution actually bring when these execution environments start seeing significant usage?
#dusk $DUSK @Dusk $BTC
1
2
150
One time I sold crypto on Binance P2P. The buyer said they had transferred the money and sent a screenshot showing the successful transaction. At first, it looked like everything was almost done, but when I opened my banking app to check, the funds still hadn’t appeared in my account. I stopped there instead of clicking Release, because at that point one question became pretty clear: if the buyer already said “transferred,” then what exactly is it that I need to confirm before releasing the crypto for real?
So I tried to go through a simple transaction in reverse. The buyer makes the payment using the method agreed on, then the seller checks the amount they received. Binance’s documentation states clearly: only after the seller confirms that the money has arrived will the seller release the crypto from escrow.
I wanted to understand why this confirmation step is placed on the seller’s side.
When I read the Merchant Guidelines, I saw that Binance also requires the name on the payment account to match the name verified on the platform. If the counterparty’s bank account information doesn’t match the verified name, Binance requires that the seller not release the crypto; the seller can refund and report the transaction.
Only then did I realize I had been viewing P2P a bit too simply. Escrow holds the crypto during the transaction, but confirming that the payment was actually received is still a separate step in the process.
Hold on—this doesn’t mean Binance can prevent every payment risk. The documentation only shows that the responsibility to verify the funds and the payer’s information still exists before release.
Maybe “Release” isn’t the action that confirms the money has arrived, but rather the step that happens after confirmation.
So please check everything carefully before you release.
#binancep2pantoan @Binance_Vietnam $BTC
One time I sold crypto on Binance P2P. The buyer said they had transferred the money and sent a screenshot showing the successful transaction. At first, it looked like everything was almost done, but when I opened my banking app to check, the funds still hadn’t appeared in my account. I stopped there instead of clicking Release, because at that point one question became pretty clear: if the buyer already said “transferred,” then what exactly is it that I need to confirm before releasing the crypto for real?
So I tried to go through a simple transaction in reverse. The buyer makes the payment using the method agreed on, then the seller checks the amount they received. Binance’s documentation states clearly: only after the seller confirms that the money has arrived will the seller release the crypto from escrow.
I wanted to understand why this confirmation step is placed on the seller’s side.
When I read the Merchant Guidelines, I saw that Binance also requires the name on the payment account to match the name verified on the platform. If the counterparty’s bank account information doesn’t match the verified name, Binance requires that the seller not release the crypto; the seller can refund and report the transaction.
Only then did I realize I had been viewing P2P a bit too simply. Escrow holds the crypto during the transaction, but confirming that the payment was actually received is still a separate step in the process.
Hold on—this doesn’t mean Binance can prevent every payment risk. The documentation only shows that the responsibility to verify the funds and the payer’s information still exists before release.
Maybe “Release” isn’t the action that confirms the money has arrived, but rather the step that happens after confirmation.
So please check everything carefully before you release.
#binancep2pantoan @Binance Vietnam $BTC
So I tried to go through a simple transaction in reverse. The buyer makes the payment using the method agreed on, then the seller checks the amount they received. Binance’s documentation states clearly: only after the seller confirms that the money has arrived will the seller release the crypto from escrow.
I wanted to understand why this confirmation step is placed on the seller’s side.
When I read the Merchant Guidelines, I saw that Binance also requires the name on the payment account to match the name verified on the platform. If the counterparty’s bank account information doesn’t match the verified name, Binance requires that the seller not release the crypto; the seller can refund and report the transaction.
Only then did I realize I had been viewing P2P a bit too simply. Escrow holds the crypto during the transaction, but confirming that the payment was actually received is still a separate step in the process.
Hold on—this doesn’t mean Binance can prevent every payment risk. The documentation only shows that the responsibility to verify the funds and the payer’s information still exists before release.
Maybe “Release” isn’t the action that confirms the money has arrived, but rather the step that happens after confirmation.
So please check everything carefully before you release.
#binancep2pantoan @Binance Vietnam $BTC
1
3
346
Something makes me pause when reading about Dusk Network: DuskDS and DuskEVM are described as two separate parts but they don’t stand independently.
I started with the architecture. The Dusk documentation calls DuskDS the settlement and data availability layer, responsible for consensus, finality, and the native transaction models of Dusk. DuskEVM is an EVM-compatible execution environment where Solidity smart contracts can run with familiar tooling. More importantly, DuskEVM uses DuskDS for settlement and data availability.
I want to check whether this is merely an architectural naming convention or whether there is a real separation of responsibilities.
Digging deeper, I find that DuskDS handles consensus, finality, and data availability along with transaction models like Moonlight and Phoenix. DuskEVM focuses on execution and allows using Hardhat, Foundry, and the broader EVM ecosystem. One side provides the settlement foundation; the other handles execution.
Wait—this still isn’t enough to say these two “complimentary” layers bring performance or security advantages in the usual sense. From what I was able to verify in the documentation, the clearest relationship is that execution is separated from settlement.
What’s interesting is that Dusk uses modularity to keep settlement separate while still giving developers access to the EVM. So if application adoption grows, does this separation between execution and settlement truly create an advantage—or is it simply an architectural way of organizing components?
#dusk $DUSK @Dusk_Foundation $BTC
Something makes me pause when reading about Dusk Network: DuskDS and DuskEVM are described as two separate parts but they don’t stand independently.
I started with the architecture. The Dusk documentation calls DuskDS the settlement and data availability layer, responsible for consensus, finality, and the native transaction models of Dusk. DuskEVM is an EVM-compatible execution environment where Solidity smart contracts can run with familiar tooling. More importantly, DuskEVM uses DuskDS for settlement and data availability.
I want to check whether this is merely an architectural naming convention or whether there is a real separation of responsibilities.
Digging deeper, I find that DuskDS handles consensus, finality, and data availability along with transaction models like Moonlight and Phoenix. DuskEVM focuses on execution and allows using Hardhat, Foundry, and the broader EVM ecosystem. One side provides the settlement foundation; the other handles execution.
Wait—this still isn’t enough to say these two “complimentary” layers bring performance or security advantages in the usual sense. From what I was able to verify in the documentation, the clearest relationship is that execution is separated from settlement.
What’s interesting is that Dusk uses modularity to keep settlement separate while still giving developers access to the EVM. So if application adoption grows, does this separation between execution and settlement truly create an advantage—or is it simply an architectural way of organizing components?
#dusk $DUSK @Dusk $BTC
I started with the architecture. The Dusk documentation calls DuskDS the settlement and data availability layer, responsible for consensus, finality, and the native transaction models of Dusk. DuskEVM is an EVM-compatible execution environment where Solidity smart contracts can run with familiar tooling. More importantly, DuskEVM uses DuskDS for settlement and data availability.
I want to check whether this is merely an architectural naming convention or whether there is a real separation of responsibilities.
Digging deeper, I find that DuskDS handles consensus, finality, and data availability along with transaction models like Moonlight and Phoenix. DuskEVM focuses on execution and allows using Hardhat, Foundry, and the broader EVM ecosystem. One side provides the settlement foundation; the other handles execution.
Wait—this still isn’t enough to say these two “complimentary” layers bring performance or security advantages in the usual sense. From what I was able to verify in the documentation, the clearest relationship is that execution is separated from settlement.
What’s interesting is that Dusk uses modularity to keep settlement separate while still giving developers access to the EVM. So if application adoption grows, does this separation between execution and settlement truly create an advantage—or is it simply an architectural way of organizing components?
#dusk $DUSK @Dusk $BTC
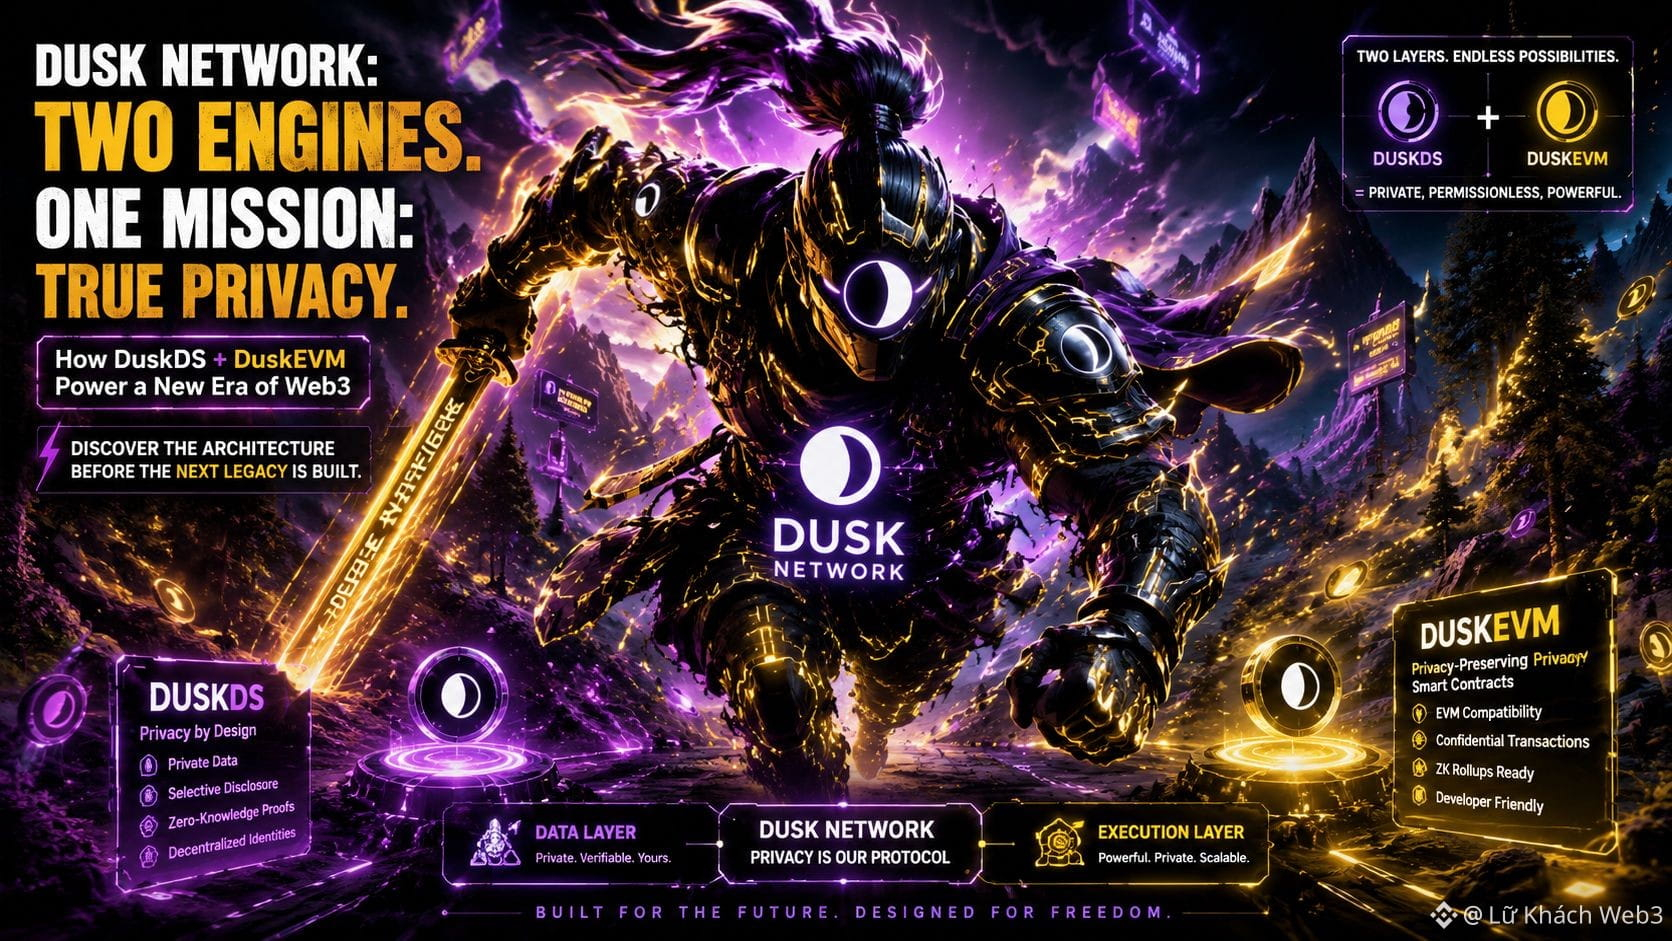
7
4
91
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number