
#trezor
trezor
62,521 views
284 Discussing
Hot
Latest
Article
Trezor Hit by Third Data Breach in 2023: Shipping Partners BlamedTrezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
Trezor Hit by Third Data Breach in 2023: Shipping Partners Blamed
Trezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
84

·
--
Trezor says a breach at one of its shipping partners exposed customer details from about 27,000 hardware wallet orders.
On November 16, 2026, Trezor said its shipping partner Skladon reported unauthorized access on November 15, tied to a breach that happened on November 7. The attacker is believed to have exported data for roughly 27,000 orders placed between August 9 and November 7, 2026, including full names, phone numbers, delivery addresses, email addresses and order details. Trezor says its own systems were not compromised, and no wallet backups, PINs or passphrases were involved.
The bigger risk now is targeted scams, since fraudsters can quote real order details. Some customers have already reported scam calls. Trezor says it will never call users or ask for a wallet backup. It has opened Anonymous Pickup in 18 European countries and plans to cut order-data retention from 90 to 45 days.
#Trezor #CryptoSecurity #SelfCustody
DYOR. Not financial advice.
Trezor says a breach at one of its shipping partners exposed customer details from about 27,000 hardware wallet orders.
On November 16, 2026, Trezor said its shipping partner Skladon reported unauthorized access on November 15, tied to a breach that happened on November 7. The attacker is believed to have exported data for roughly 27,000 orders placed between August 9 and November 7, 2026, including full names, phone numbers, delivery addresses, email addresses and order details. Trezor says its own systems were not compromised, and no wallet backups, PINs or passphrases were involved.
The bigger risk now is targeted scams, since fraudsters can quote real order details. Some customers have already reported scam calls. Trezor says it will never call users or ask for a wallet backup. It has opened Anonymous Pickup in 18 European countries and plans to cut order-data retention from 90 to 45 days.
#Trezor #CryptoSecurity #SelfCustody
DYOR. Not financial advice.
On November 16, 2026, Trezor said its shipping partner Skladon reported unauthorized access on November 15, tied to a breach that happened on November 7. The attacker is believed to have exported data for roughly 27,000 orders placed between August 9 and November 7, 2026, including full names, phone numbers, delivery addresses, email addresses and order details. Trezor says its own systems were not compromised, and no wallet backups, PINs or passphrases were involved.
The bigger risk now is targeted scams, since fraudsters can quote real order details. Some customers have already reported scam calls. Trezor says it will never call users or ask for a wallet backup. It has opened Anonymous Pickup in 18 European countries and plans to cut order-data retention from 90 to 45 days.
#Trezor #CryptoSecurity #SelfCustody
DYOR. Not financial advice.
29
·
--
Trezor says an attacker likely exported contact, delivery and purchase details for about 27,000 orders held by shipping partner Skladon, placed Aug 9 to Nov 7. Devices stay secure, but expect targeted phishing. #Trezor #Security
Trezor says an attacker likely exported contact, delivery and purchase details for about 27,000 orders held by shipping partner Skladon, placed Aug 9 to Nov 7. Devices stay secure, but expect targeted phishing. #Trezor #Security
5
·
--
Trezor Confirms Crypto-Stealing Implants in 3 Safe 5 Wallets
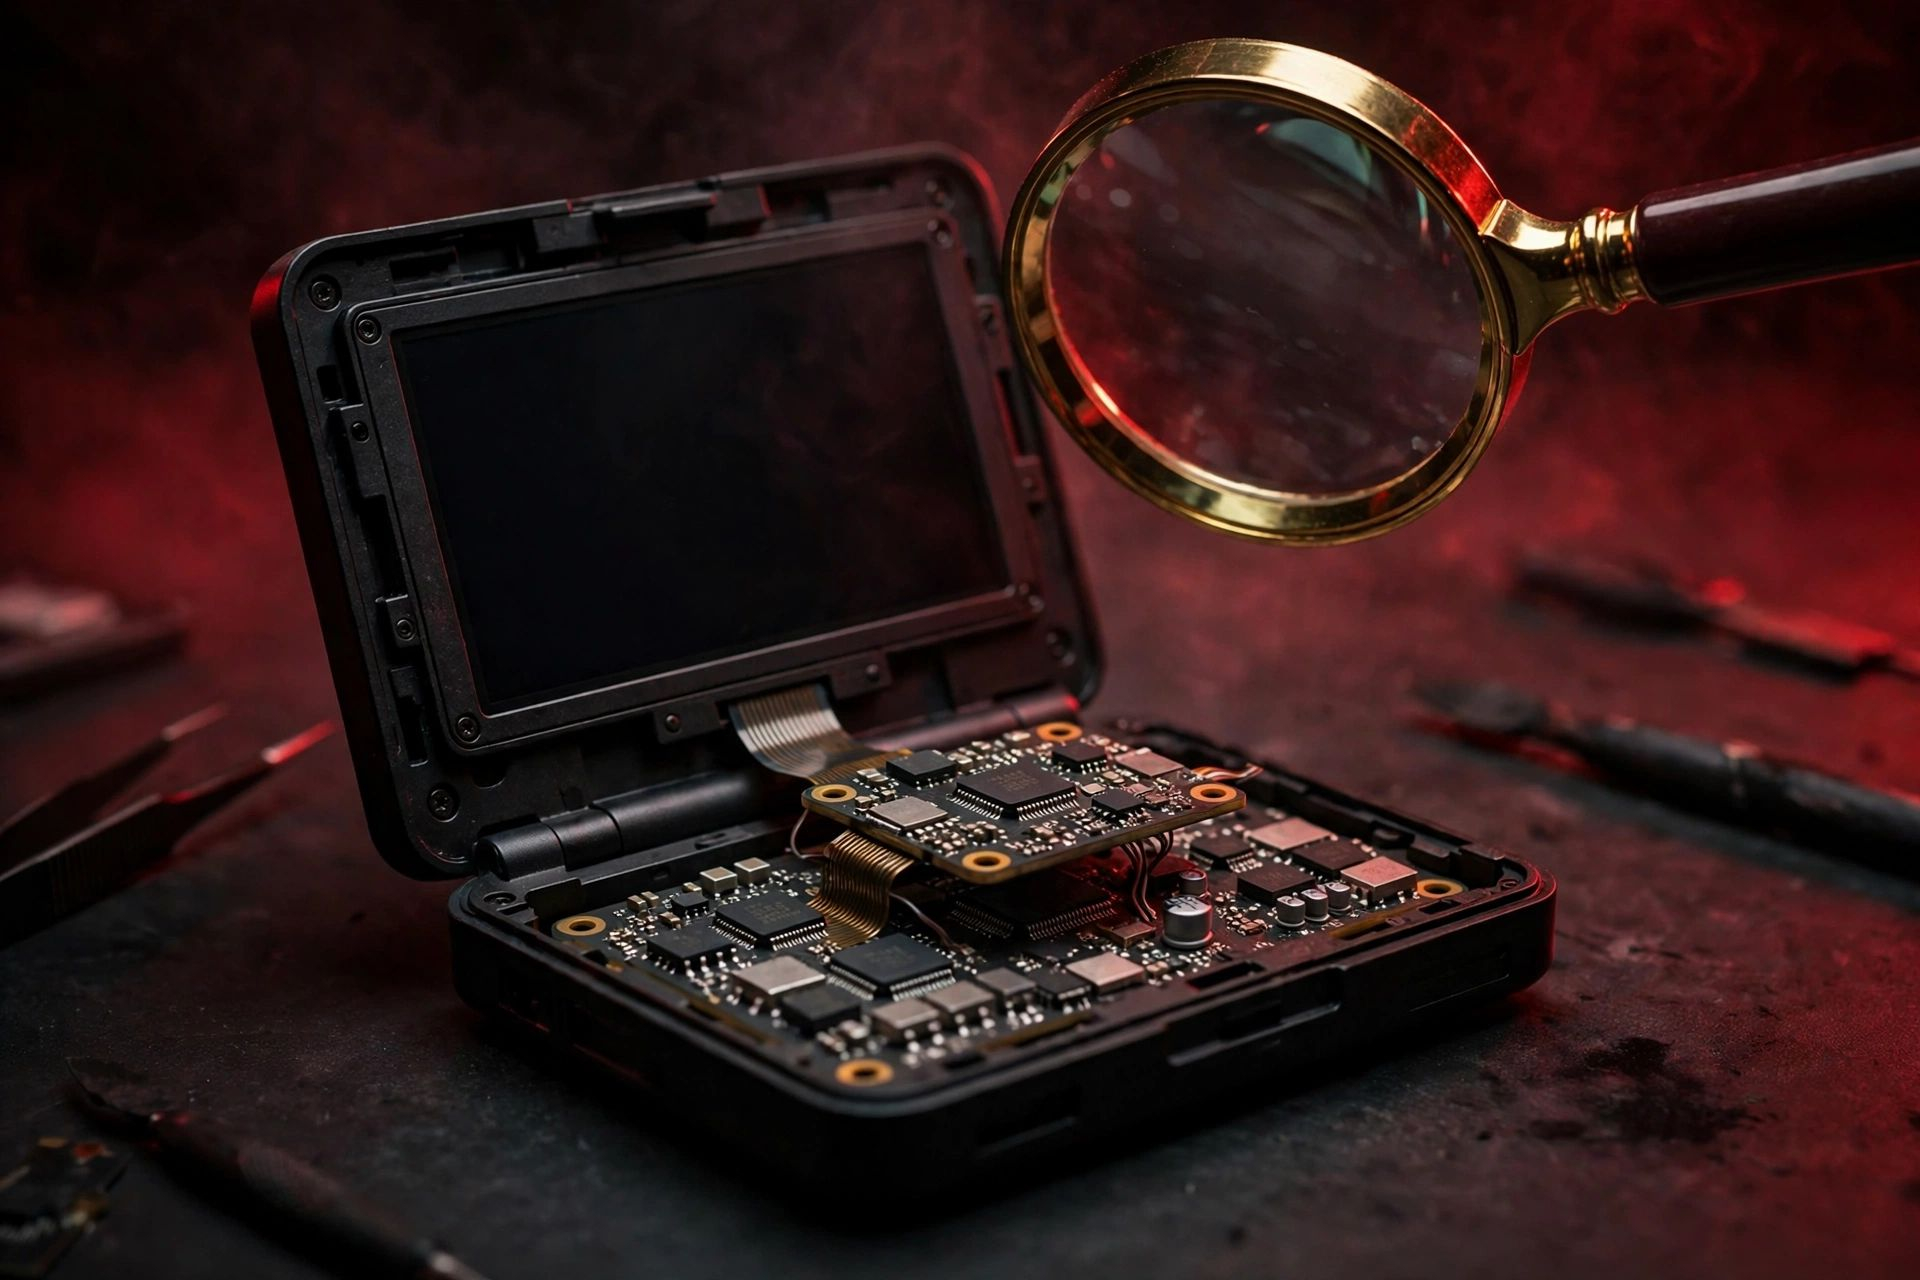
Trezor confirmed three Safe 5 hardware wallets sold by reseller CryptoBilis hid implants — an extra circuit board between the main board and screen that copied recovery words and passphrases, then beamed them to attackers over a mobile network.
All 3 were bought Aug 20–Sep 23. Firmware 2.13.1 (Nov 11) blocks the implants, but can't protect phrases already copied. Trezor cut ~80% of its reseller network; no customers have reported lost funds yet.
Bought from CryptoBilis? Move your crypto to a new wallet with a fresh recovery phrase. Only buy hardware wallets from official sources.
Not financial advice.
#Trezor #CryptoSecurity #Bitcoin
Trezor Confirms Crypto-Stealing Implants in 3 Safe 5 Wallets
Trezor confirmed three Safe 5 hardware wallets sold by reseller CryptoBilis hid implants — an extra circuit board between the main board and screen that copied recovery words and passphrases, then beamed them to attackers over a mobile network.
All 3 were bought Aug 20–Sep 23. Firmware 2.13.1 (Nov 11) blocks the implants, but can't protect phrases already copied. Trezor cut ~80% of its reseller network; no customers have reported lost funds yet.
Bought from CryptoBilis? Move your crypto to a new wallet with a fresh recovery phrase. Only buy hardware wallets from official sources.
Not financial advice.
#Trezor #CryptoSecurity #Bitcoin
Trezor confirmed three Safe 5 hardware wallets sold by reseller CryptoBilis hid implants — an extra circuit board between the main board and screen that copied recovery words and passphrases, then beamed them to attackers over a mobile network.
All 3 were bought Aug 20–Sep 23. Firmware 2.13.1 (Nov 11) blocks the implants, but can't protect phrases already copied. Trezor cut ~80% of its reseller network; no customers have reported lost funds yet.
Bought from CryptoBilis? Move your crypto to a new wallet with a fresh recovery phrase. Only buy hardware wallets from official sources.
Not financial advice.
#Trezor #CryptoSecurity #Bitcoin
2

·
--
TREZOR DATA BREACH EXPOSES 27,000 CUSTOMER ORDERS!
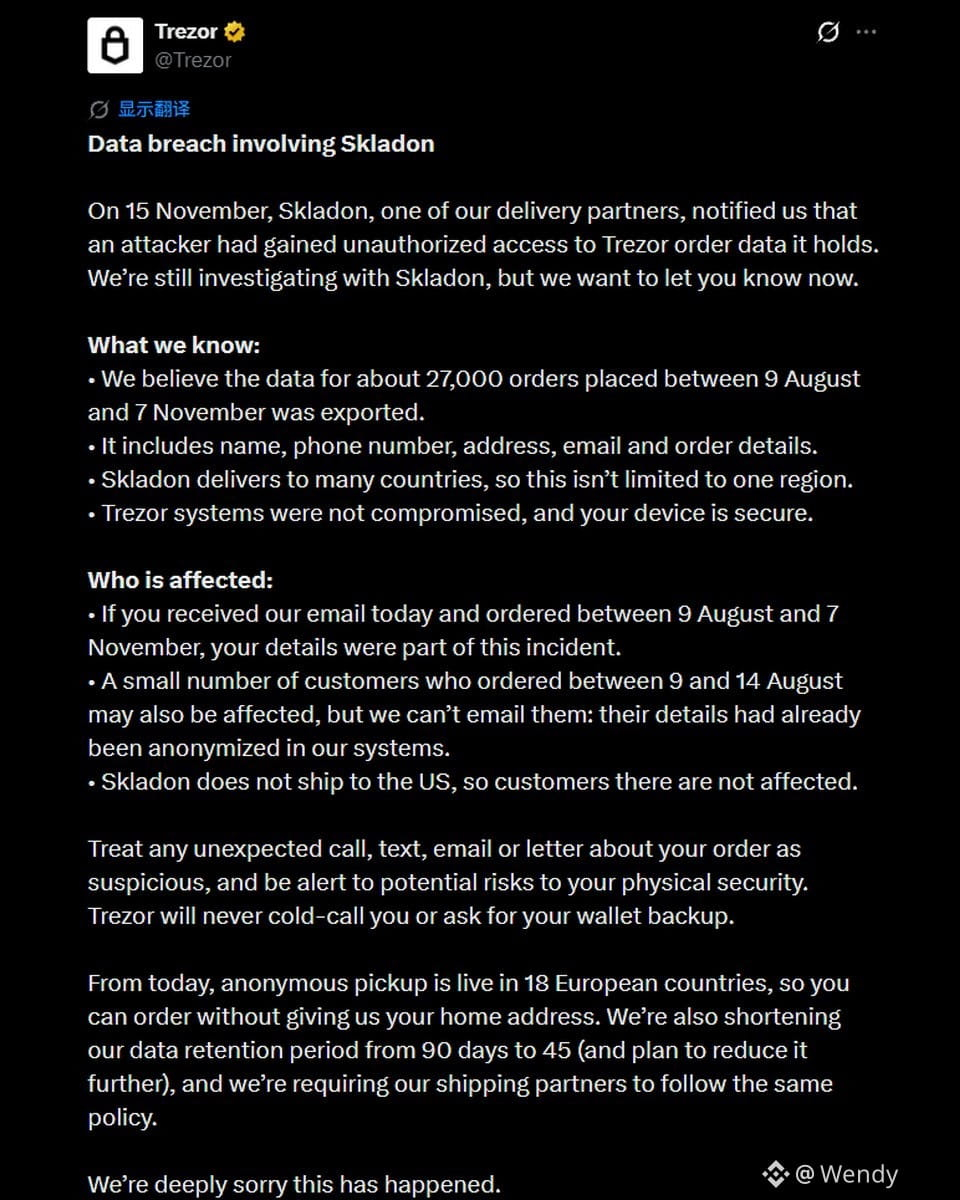
Hardware wallet maker Trezor has disclosed a security breach involving its shipping partner, Skladon.
According to Trezor, attackers may have accessed personal information from approximately 27,000 orders placed between August 9 and November 7.
Exposed data includes:
• Customer names and phone numbers
• Home addresses
• Email addresses
• Order details
The breach affected multiple countries, but US customers were not impacted.
Importantly, Trezor says its own systems and hardware wallets remain secure.
⚠️ If you've ordered a Trezor recently, watch out for phishing emails, suspicious calls and potential physical security risks.
#Trezor #CryptoSecurity
{future}(BNBUSDT)
TREZOR DATA BREACH EXPOSES 27,000 CUSTOMER ORDERS!
Hardware wallet maker Trezor has disclosed a security breach involving its shipping partner, Skladon.
According to Trezor, attackers may have accessed personal information from approximately 27,000 orders placed between August 9 and November 7.
Exposed data includes:
• Customer names and phone numbers
• Home addresses
• Email addresses
• Order details
The breach affected multiple countries, but US customers were not impacted.
Importantly, Trezor says its own systems and hardware wallets remain secure.
⚠️ If you've ordered a Trezor recently, watch out for phishing emails, suspicious calls and potential physical security risks.
#Trezor #CryptoSecurity
Hardware wallet maker Trezor has disclosed a security breach involving its shipping partner, Skladon.
According to Trezor, attackers may have accessed personal information from approximately 27,000 orders placed between August 9 and November 7.
Exposed data includes:
• Customer names and phone numbers
• Home addresses
• Email addresses
• Order details
The breach affected multiple countries, but US customers were not impacted.
Importantly, Trezor says its own systems and hardware wallets remain secure.
⚠️ If you've ordered a Trezor recently, watch out for phishing emails, suspicious calls and potential physical security risks.
#Trezor #CryptoSecurity
13
5.5k

·
--
🚨 $BTC BETRAYAL IN THE SAFEST WALLET
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
🚨 $BTC BETRAYAL IN THE SAFEST WALLET
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
2
3.9k

Trezor has confirmed another data breach involving their logistics partner, Skladon, impacting 27,000 users. While the hardware wallets remain secure, the exposure of customer addresses poses significant real-world physical risks. This serves as a brutal reminder that cold storage is only as secure as the data chain surrounding your purchase. If you ordered recently, be extra vigilant against sophisticated phishing attempts or cold-call scams. Privacy in crypto isn't just about keys; it is about metadata. $BTC #Security #CryptoSafety #Trezor
Trezor has confirmed another data breach involving their logistics partner, Skladon, impacting 27,000 users. While the hardware wallets remain secure, the exposure of customer addresses poses significant real-world physical risks. This serves as a brutal reminder that cold storage is only as secure as the data chain surrounding your purchase. If you ordered recently, be extra vigilant against sophisticated phishing attempts or cold-call scams. Privacy in crypto isn't just about keys; it is about metadata. $BTC #Security #CryptoSafety #Trezor
20

·
--
🚨 Trezor says a partner breach exposed data on about 27,000 orders
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
🚨 Trezor says a partner breach exposed data on about 27,000 orders
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
Shipping partner Skladon told Trezor on Nov. 15 that its systems were accessed without authorization on Nov. 7. Trezor believes the attacker exported names, phone numbers, emails, delivery addresses and order details for about 27,000 orders placed from Aug. 9 to Nov. 7. Trezor said its own systems were not compromised and “no wallet backups, PINs or passphrases were involved.” Some customers have already reported scam calls from people posing as support. It is the second shipping-partner leak since August.
⭐ Seeds were not in the leak, but names and home addresses of hardware-wallet buyers were, which is what the scam calls are using.
#Trezor #Security
95
Trezor's second shipping breach in three months: what buyer addresses exposeA second Trezor shipping partner has been breached in three months, and this time buyers' addresses and order details are exposed ⚖️ The obvious read for $BTC holders is that a hardware wallet keeps coins offline, so a shipping-data incident is only a privacy nuisance.
The detail that complicates that: it is the second such breach in three months. The exposed data includes buyers' addresses and order details.
For Trezor buyers, that data ties a person to a device and a location, which could feed convincing phishing or physical targeting even while the wallet stays offline. Trezor says customer data was exposed again, and the number of affected buyers is not confirmed.
What it means for you: if you bought from Trezor, an unsolicited message about your order may not be genuine, and verifying through a channel you start yourself could save you from a bad click. If a second breach in three months points to a pattern, buyers could start judging wallet makers by how their shipping partners handle data.
Takeaway: hardware wallet security does not automatically cover the shipping-data trail.
هل سبق أن رأيت تسريب بيانات شحن لمحفظة صلبة يقود إلى تصيّد موجّه، وماذا كانت النتيجة؟ 👇
#Bitcoin #Trezor
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
Trezor's second shipping breach in three months: what buyer addresses expose
A second Trezor shipping partner has been breached in three months, and this time buyers' addresses and order details are exposed ⚖️ The obvious read for $BTC holders is that a hardware wallet keeps coins offline, so a shipping-data incident is only a privacy nuisance.
The detail that complicates that: it is the second such breach in three months. The exposed data includes buyers' addresses and order details.
For Trezor buyers, that data ties a person to a device and a location, which could feed convincing phishing or physical targeting even while the wallet stays offline. Trezor says customer data was exposed again, and the number of affected buyers is not confirmed.
What it means for you: if you bought from Trezor, an unsolicited message about your order may not be genuine, and verifying through a channel you start yourself could save you from a bad click. If a second breach in three months points to a pattern, buyers could start judging wallet makers by how their shipping partners handle data.
Takeaway: hardware wallet security does not automatically cover the shipping-data trail.
هل سبق أن رأيت تسريب بيانات شحن لمحفظة صلبة يقود إلى تصيّد موجّه، وماذا كانت النتيجة؟ 👇
#Bitcoin #Trezor
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
The detail that complicates that: it is the second such breach in three months. The exposed data includes buyers' addresses and order details.
For Trezor buyers, that data ties a person to a device and a location, which could feed convincing phishing or physical targeting even while the wallet stays offline. Trezor says customer data was exposed again, and the number of affected buyers is not confirmed.
What it means for you: if you bought from Trezor, an unsolicited message about your order may not be genuine, and verifying through a channel you start yourself could save you from a bad click. If a second breach in three months points to a pattern, buyers could start judging wallet makers by how their shipping partners handle data.
Takeaway: hardware wallet security does not automatically cover the shipping-data trail.
هل سبق أن رأيت تسريب بيانات شحن لمحفظة صلبة يقود إلى تصيّد موجّه، وماذا كانت النتيجة؟ 👇
#Bitcoin #Trezor
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
47
·
--
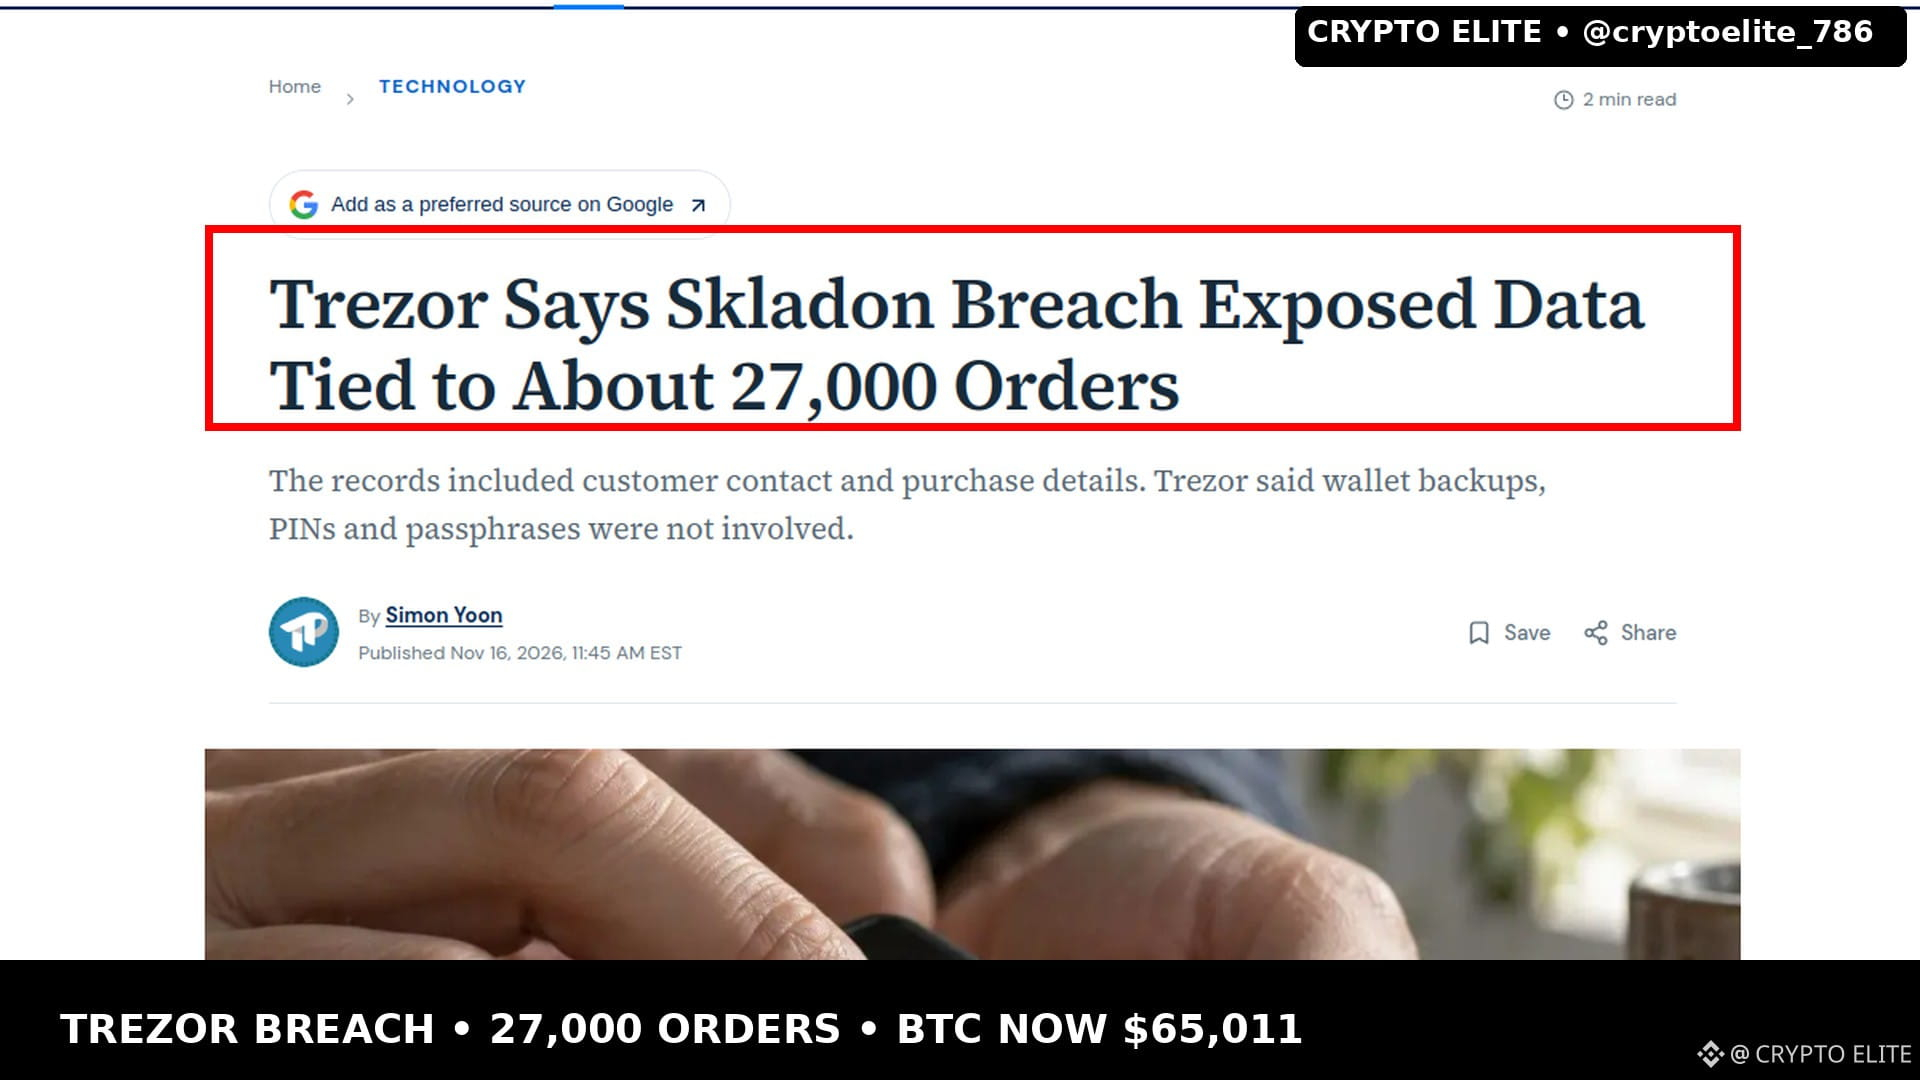
📦🔐 TREZOR DELIVERY PARTNER BREACH — DATA OF ~27,000 ORDERS EXPOSED
Trezor has disclosed that its delivery partner Skladon was hit by unauthorized access on November 7. Data tied to about 27,000 orders placed between August 9 and November 7 was exported.
The records included names, phone numbers, delivery addresses, email addresses, order dates and purchase details. Trezor says its own systems were not compromised, devices remain secure, and wallet backups, PINs and passphrases were not involved. US customers were not affected, as Skladon does not ship to the US.
Trezor has emailed the customers it can reach, informed the data protection authority, cut order-data retention from 90 days to 45 days, and launched Anonymous Pickup in 18 European countries.
THE PROOF — check this news yourself here:
https://www.tokenpost.com/news/technology/58616
Follow @cryptoelite_786 for the fastest crypto news & updates! 🔔
$BTC #Trezor #CryptoSecurity #DataBreach
📦🔐 TREZOR DELIVERY PARTNER BREACH — DATA OF ~27,000 ORDERS EXPOSED
Trezor has disclosed that its delivery partner Skladon was hit by unauthorized access on November 7. Data tied to about 27,000 orders placed between August 9 and November 7 was exported.
The records included names, phone numbers, delivery addresses, email addresses, order dates and purchase details. Trezor says its own systems were not compromised, devices remain secure, and wallet backups, PINs and passphrases were not involved. US customers were not affected, as Skladon does not ship to the US.
Trezor has emailed the customers it can reach, informed the data protection authority, cut order-data retention from 90 days to 45 days, and launched Anonymous Pickup in 18 European countries.
THE PROOF — check this news yourself here:
https://www.tokenpost.com/news/technology/58616
Follow @cryptoelite_786 for the fastest crypto news & updates! 🔔
$BTC #Trezor #CryptoSecurity #DataBreach
Trezor has disclosed that its delivery partner Skladon was hit by unauthorized access on November 7. Data tied to about 27,000 orders placed between August 9 and November 7 was exported.
The records included names, phone numbers, delivery addresses, email addresses, order dates and purchase details. Trezor says its own systems were not compromised, devices remain secure, and wallet backups, PINs and passphrases were not involved. US customers were not affected, as Skladon does not ship to the US.
Trezor has emailed the customers it can reach, informed the data protection authority, cut order-data retention from 90 days to 45 days, and launched Anonymous Pickup in 18 European countries.
THE PROOF — check this news yourself here:
https://www.tokenpost.com/news/technology/58616
Follow @cryptoelite_786 for the fastest crypto news & updates! 🔔
$BTC #Trezor #CryptoSecurity #DataBreach
43

·
--
Data from 27,000 Trezor orders leaked through shipping partner—and scammers have already started calling victims.
The facts: Trezor revealed on Monday, Nov. 16, that its shipping partner Skladon was breached on Nov. 7, but didn’t notify Trezor until Nov. 15. Data from around 27,000 orders (Aug. 9–Nov. 7) was allegedly exported: names, phone numbers, shipping addresses, email addresses, and purchase details (Cointelegraph, Nov. 17; PANews, Nov. 16). Trezor’s own systems were not breached, and the devices remain secure; PINs, passphrases, and wallet backups were not exposed because they aren’t stored. U.S. customers were not affected because Skladon doesn’t ship to the U.S. This is the third partner-related breach this year, following ShipMonk in August and Brevo in September (347,149 email addresses).
My take: the most dangerous thing here isn’t the wallet—the hardware wallet remains secure—but the data. A name, home address, and the fact that someone owns crypto are perfect ingredients for scams and physical threats. Some affected customers have already reported receiving scam calls (crypto.news). Trezor responded by offering anonymous pickup in 18 European countries and cutting data retention from 90 to 45 days—a good move, but the notification came eight days late.
What I’m watching next: whether Trezor releases a list of affected countries, and whether a new wave of phishing emerges impersonating Trezor support. If you ordered a Trezor between August and November: never share your seed phrase with anyone, over any phone call.
Have you ever received a suspicious call or email claiming to be from a wallet manufacturer? Share it in the comments so others can stay alert.
This is my analysis, not financial advice—always DYOR.
#Keamanan #Trezor
Data from 27,000 Trezor orders leaked through shipping partner—and scammers have already started calling victims.
The facts: Trezor revealed on Monday, Nov. 16, that its shipping partner Skladon was breached on Nov. 7, but didn’t notify Trezor until Nov. 15. Data from around 27,000 orders (Aug. 9–Nov. 7) was allegedly exported: names, phone numbers, shipping addresses, email addresses, and purchase details (Cointelegraph, Nov. 17; PANews, Nov. 16). Trezor’s own systems were not breached, and the devices remain secure; PINs, passphrases, and wallet backups were not exposed because they aren’t stored. U.S. customers were not affected because Skladon doesn’t ship to the U.S. This is the third partner-related breach this year, following ShipMonk in August and Brevo in September (347,149 email addresses).
My take: the most dangerous thing here isn’t the wallet—the hardware wallet remains secure—but the data. A name, home address, and the fact that someone owns crypto are perfect ingredients for scams and physical threats. Some affected customers have already reported receiving scam calls (crypto.news). Trezor responded by offering anonymous pickup in 18 European countries and cutting data retention from 90 to 45 days—a good move, but the notification came eight days late.
What I’m watching next: whether Trezor releases a list of affected countries, and whether a new wave of phishing emerges impersonating Trezor support. If you ordered a Trezor between August and November: never share your seed phrase with anyone, over any phone call.
Have you ever received a suspicious call or email claiming to be from a wallet manufacturer? Share it in the comments so others can stay alert.
This is my analysis, not financial advice—always DYOR.
#Keamanan #Trezor
The facts: Trezor revealed on Monday, Nov. 16, that its shipping partner Skladon was breached on Nov. 7, but didn’t notify Trezor until Nov. 15. Data from around 27,000 orders (Aug. 9–Nov. 7) was allegedly exported: names, phone numbers, shipping addresses, email addresses, and purchase details (Cointelegraph, Nov. 17; PANews, Nov. 16). Trezor’s own systems were not breached, and the devices remain secure; PINs, passphrases, and wallet backups were not exposed because they aren’t stored. U.S. customers were not affected because Skladon doesn’t ship to the U.S. This is the third partner-related breach this year, following ShipMonk in August and Brevo in September (347,149 email addresses).
My take: the most dangerous thing here isn’t the wallet—the hardware wallet remains secure—but the data. A name, home address, and the fact that someone owns crypto are perfect ingredients for scams and physical threats. Some affected customers have already reported receiving scam calls (crypto.news). Trezor responded by offering anonymous pickup in 18 European countries and cutting data retention from 90 to 45 days—a good move, but the notification came eight days late.
What I’m watching next: whether Trezor releases a list of affected countries, and whether a new wave of phishing emerges impersonating Trezor support. If you ordered a Trezor between August and November: never share your seed phrase with anyone, over any phone call.
Have you ever received a suspicious call or email claiming to be from a wallet manufacturer? Share it in the comments so others can stay alert.
This is my analysis, not financial advice—always DYOR.
#Keamanan #Trezor
41

·
--
Trezor’s Logistics Breached for the Second Time: Hardware Wallet Supply Chain Security Raises Red Flags Again
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.
Trezor’s Logistics Breached for the Second Time: Hardware Wallet Supply Chain Security Raises Red Flags Again
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.
Hardware wallet maker Trezor has suffered a breach at a second logistics provider within three months, exposing buyers’ addresses and order details once again. Supply chain risks are escalating from isolated incidents into a systemic vulnerability.
According to Decrypt, Trezor confirmed that a second logistics partner was breached within three months, exposing data such as buyers’ addresses and order details. This is the company’s second data breach involving a logistics channel in a relatively short period, suggesting that attackers’ points of access have expanded beyond the product itself to the intermediate stages of package delivery.
This incident merits scrutiny from both a financial and institutional perspective because the user base for hardware wallets is closely tied to market liquidity. Early holders and institutional investors are often more inclined to use cold storage, and a supply chain data breach could undermine their trust in hardware wallets. If that trust begins to erode, the potential impact may not be immediate selling pressure, but rather whether incoming capital remains willing to entrust assets to this kind of infrastructure.
Technically, the vulnerability lies not in the wallet firmware itself, but in the logistics chain. An attacker only needs to breach one logistics provider to obtain information such as buyers’ addresses and order details—data that should otherwise be kept isolated. For institutions, this means the security perimeter is expanding: product security, warehouse security, and logistics security are linked into a fragile chain, and a breach at any point could affect the whole system.
The market’s likely reaction currently appears neutral to slightly bearish, but there is no direct basis to expect selling. This is a risk-warning event, not a major market shock, and is unlikely to trigger large-scale asset transfers in the short term. What matters most is whether this incident combines with other recent security events to fuel systemic doubts about the hardware wallet sector.
A counterpoint is that a single logistics breach does not mean the wallet itself has failed. Users’ assets remain protected by their private keys, and there is a clear distinction between data exposure and asset theft. That said, a second logistics provider being breached within three months suggests this is not an isolated incident, but a recurring weak point in the supply chain.
What to watch next: Trezor’s security response and any compensation measures, as well as marginal changes in market confidence in the company. If incidents of this kind continue to escalate, the valuation logic for the hardware wallet sector may face reassessment.
#Trezor #HardwareWallet #CryptoSecurity
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to track and share any significant developments.

Trezor warns of a data breach affecting 27,000 orders through a shipping partner
- Hackers accessed customers’ names, phone numbers, and shipping addresses
- The breach involved 27,000 orders handled by Trezor’s shipping provider
- This is the third partner-related breach this year
- Personal data could be used in scams
#BinanceSquare #CryptoNews #Trezor #Security #CryptoWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
Trezor warns of a data breach affecting 27,000 orders through a shipping partner
- Hackers accessed customers’ names, phone numbers, and shipping addresses
- The breach involved 27,000 orders handled by Trezor’s shipping provider
- This is the third partner-related breach this year
- Personal data could be used in scams
#BinanceSquare #CryptoNews #Trezor #Security #CryptoWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
- Hackers accessed customers’ names, phone numbers, and shipping addresses
- The breach involved 27,000 orders handled by Trezor’s shipping provider
- This is the third partner-related breach this year
- Personal data could be used in scams
#BinanceSquare #CryptoNews #Trezor #Security #CryptoWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
·
--
【Bought a hardware wallet, and hackers got my home address! Trezor logistics provider hacked; details of around 27,000 orders leaked】
Trezor disclosed on November 16 that its logistics partner Skladon was breached on November 7. The names, phone numbers, email addresses, shipping addresses, products purchased, and prices for around 27,000 orders placed between August 9 and November 7 are believed to have been exported. Wallet backups, PINs, and passwords were not affected, and U.S. orders were unaffected. This is the second time since August that customer information has been leaked due to a Trezor logistics provider. Some users have reported receiving scam calls. Anyone claiming to call from Trezor or asking for your recovery phrase is a scammer.
#Trezor #硬件钱包 #Wallet Security
【Bought a hardware wallet, and hackers got my home address! Trezor logistics provider hacked; details of around 27,000 orders leaked】
Trezor disclosed on November 16 that its logistics partner Skladon was breached on November 7. The names, phone numbers, email addresses, shipping addresses, products purchased, and prices for around 27,000 orders placed between August 9 and November 7 are believed to have been exported. Wallet backups, PINs, and passwords were not affected, and U.S. orders were unaffected. This is the second time since August that customer information has been leaked due to a Trezor logistics provider. Some users have reported receiving scam calls. Anyone claiming to call from Trezor or asking for your recovery phrase is a scammer.
#Trezor #硬件钱包 #Wallet Security
Trezor disclosed on November 16 that its logistics partner Skladon was breached on November 7. The names, phone numbers, email addresses, shipping addresses, products purchased, and prices for around 27,000 orders placed between August 9 and November 7 are believed to have been exported. Wallet backups, PINs, and passwords were not affected, and U.S. orders were unaffected. This is the second time since August that customer information has been leaked due to a Trezor logistics provider. Some users have reported receiving scam calls. Anyone claiming to call from Trezor or asking for your recovery phrase is a scammer.
#Trezor #硬件钱包 #Wallet Security
263

·
--
Trezor Hit by Third Logistics Provider Breach, Data of 27,000 Customers Leaked
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
Trezor Hit by Third Logistics Provider Breach, Data of 27,000 Customers Leaked
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
The security perimeter of hardware wallets is quietly being breached through an inconspicuous link in the logistics chain.
According to Cointelegraph, Trezor has officially warned that an attacker was able to access the names, phone numbers, and shipping addresses of 27,000 customers. This is the third logistics partner to be compromised this year, meaning attackers have repeatedly exploited the same weak link in the supply chain.
Why is this incident cause for concern? In recent months, logistics operations at hardware wallet companies have been exposed more than once. The impact of the first and second breaches was relatively limited, but this time the number of affected customers has risen significantly—and it is the third incident in just three months. This pattern of repeated breaches is more telling than a single incident: logistics information itself may have become the biggest data vulnerability for hardware wallets.
There are two key figures in this leak: the logistics provider has been breached three times, and 27,000 customers were affected. It is worth noting that the leaked information was primarily personal data such as names, phone numbers, and addresses—not sensitive information that directly controls assets, such as private keys or seed phrases. This is therefore more a breach of user privacy than a direct risk of asset theft.
How might the market react? Since Trezor operates in the hardware infrastructure layer and no private keys were involved, the direct impact on crypto asset prices may be limited. However, the incident exposes a weak link in the hardware wallet chain of trust and could, over the long term, affect some users’ confidence in hardware wallet security.
One mitigating factor is that the leak was limited to logistics information, and the attackers cannot directly access on-chain assets. The real risk may be that the leaked personal information could be used for targeted phishing, paving the way for subsequent social engineering attacks.
What remains to be seen is whether Trezor will disclose more details about the scope of the breach and its response, and whether phishing attacks using the leaked information will follow. This supply chain security front is worth monitoring closely.
#Trezor #HardwareWallet
The above is a compilation of information and personal analysis, and does not constitute investment advice.
I will continue to follow and provide updates if there are any significant developments.
4
Trezor exposes customer data after shipping partner is attacked for the third time this year
- Attackers accessed the names, phone numbers, and shipping addresses from 27,000 Trezor orders
- The vulnerability originated with a shipping provider
- This is the third data breach involving a Trezor partner in 2026
- Trezor has warned users to beware of phishing attacks exploiting this information
- Private keys and crypto assets were not affected because they are stored offline on the device
The RSS source has not provided further details about the shipping partner’s name or specific remediation measures.
#BinanceSquare #CryptoNews #Trezor #Security #HardwareWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
Trezor exposes customer data after shipping partner is attacked for the third time this year
- Attackers accessed the names, phone numbers, and shipping addresses from 27,000 Trezor orders
- The vulnerability originated with a shipping provider
- This is the third data breach involving a Trezor partner in 2026
- Trezor has warned users to beware of phishing attacks exploiting this information
- Private keys and crypto assets were not affected because they are stored offline on the device
The RSS source has not provided further details about the shipping partner’s name or specific remediation measures.
#BinanceSquare #CryptoNews #Trezor #Security #HardwareWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
- Attackers accessed the names, phone numbers, and shipping addresses from 27,000 Trezor orders
- The vulnerability originated with a shipping provider
- This is the third data breach involving a Trezor partner in 2026
- Trezor has warned users to beware of phishing attacks exploiting this information
- Private keys and crypto assets were not affected because they are stored offline on the device
The RSS source has not provided further details about the shipping partner’s name or specific remediation measures.
#BinanceSquare #CryptoNews #Trezor #Security #HardwareWallet
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
3

·
--
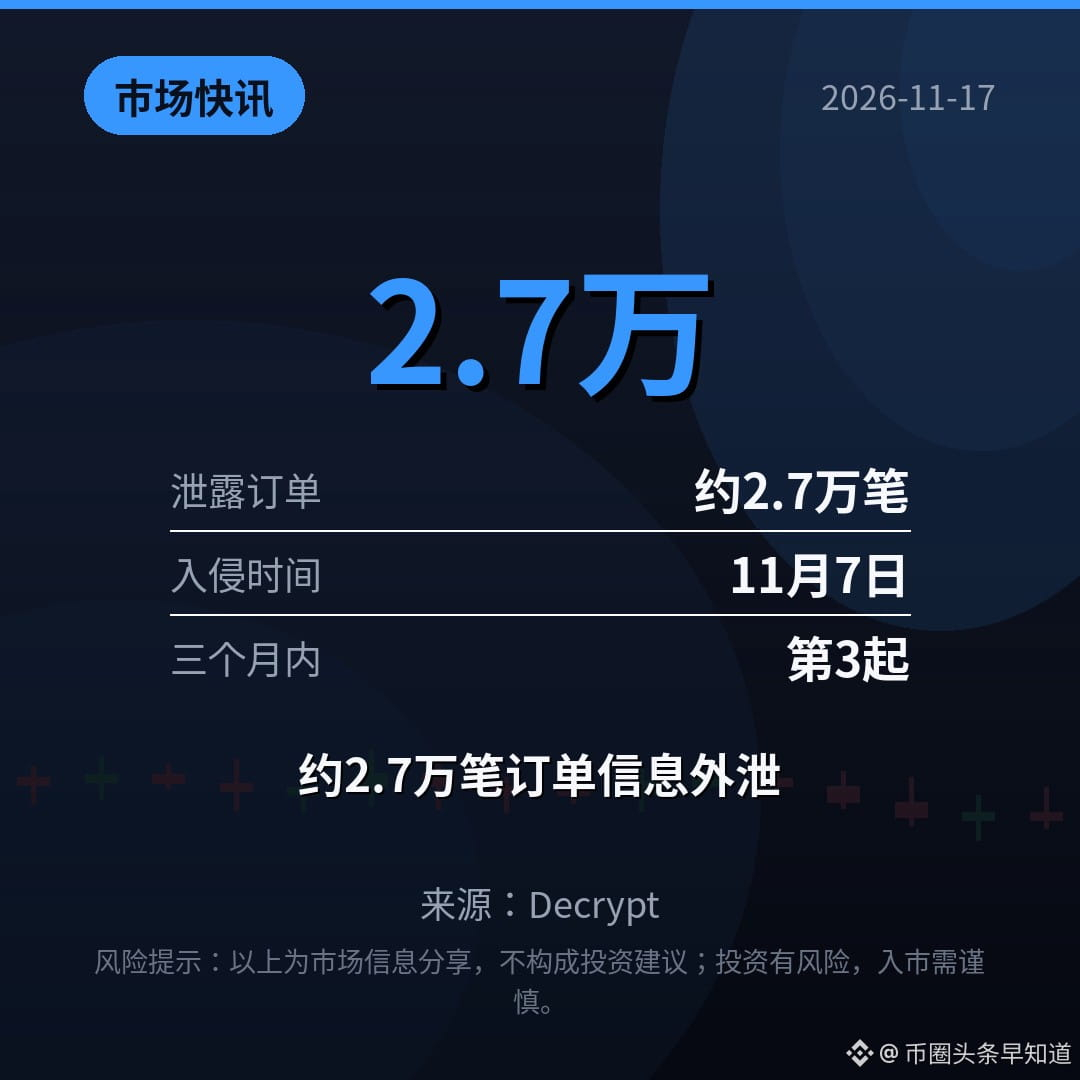
【Market Alert】Trezor logistics partner leaks data on 27,000 orders
Trezor disclosed that its logistics partner, Skladon, was breached on November 7, exposing information on around 27,000 orders, including names, phone numbers, email addresses, and physical addresses. Wallet backups, PINs, and recovery phrases were unaffected. This is the third third-party security incident in three months, and some users have already received scam calls. Is this a warning for $BTC holders or an overreaction? Share your thoughts in the comments.
$BTC $ETH $SOL
#币安广场 #Trezor #MarketAlert
(Source: Decrypt)
⚠️Risk warning: The information above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; please exercise caution.
【Market Alert】Trezor logistics partner leaks data on 27,000 orders
Trezor disclosed that its logistics partner, Skladon, was breached on November 7, exposing information on around 27,000 orders, including names, phone numbers, email addresses, and physical addresses. Wallet backups, PINs, and recovery phrases were unaffected. This is the third third-party security incident in three months, and some users have already received scam calls. Is this a warning for $BTC holders or an overreaction? Share your thoughts in the comments.
$BTC $ETH $SOL
#币安广场 #Trezor #MarketAlert
(Source: Decrypt)
⚠️Risk warning: The information above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; please exercise caution.
Trezor disclosed that its logistics partner, Skladon, was breached on November 7, exposing information on around 27,000 orders, including names, phone numbers, email addresses, and physical addresses. Wallet backups, PINs, and recovery phrases were unaffected. This is the third third-party security incident in three months, and some users have already received scam calls. Is this a warning for $BTC holders or an overreaction? Share your thoughts in the comments.
$BTC $ETH $SOL
#币安广场 #Trezor #MarketAlert
(Source: Decrypt)
⚠️Risk warning: The information above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; please exercise caution.
5

·
--
Here we go again: Trezor has fallen victim to a partner for the third time in a year. This time it was logistics provider Skladon, which was breached on November 7. Names, phone numbers, home addresses, email addresses, and purchase histories from around 27,000 orders were all exported. Seed phrases, PINs, and the wallets themselves are safe, but scammers now have your address and order details, so watch out for phishing calls and the risk of someone showing up at your door. Trezor has cut its data retention period from 90 days to 45 and rolled out anonymous pickup in 18 countries. You buy a hardware wallet for peace of mind, and then your address gets leaked first. What do you think?
#Trezor #硬件钱包 #数据泄露 #加密货币安全 #PhishingScam
Here we go again: Trezor has fallen victim to a partner for the third time in a year. This time it was logistics provider Skladon, which was breached on November 7. Names, phone numbers, home addresses, email addresses, and purchase histories from around 27,000 orders were all exported. Seed phrases, PINs, and the wallets themselves are safe, but scammers now have your address and order details, so watch out for phishing calls and the risk of someone showing up at your door. Trezor has cut its data retention period from 90 days to 45 and rolled out anonymous pickup in 18 countries. You buy a hardware wallet for peace of mind, and then your address gets leaked first. What do you think?
#Trezor #硬件钱包 #数据泄露 #加密货币安全 #PhishingScam
#Trezor #硬件钱包 #数据泄露 #加密货币安全 #PhishingScam
1
Trezor customer data leaked due to a third-party partner security breach
- Trezor warns that customer data (names, phone numbers, shipping addresses) were leaked.
- An attacker accessed information on 27,000 orders from a shipping provider.
- This is Trezor’s third breach this year.
#BinanceSquare #CryptoNews #Trezor
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
Trezor customer data leaked due to a third-party partner security breach
- Trezor warns that customer data (names, phone numbers, shipping addresses) were leaked.
- An attacker accessed information on 27,000 orders from a shipping provider.
- This is Trezor’s third breach this year.
#BinanceSquare #CryptoNews #Trezor
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
- Trezor warns that customer data (names, phone numbers, shipping addresses) were leaked.
- An attacker accessed information on 27,000 orders from a shipping provider.
- This is Trezor’s third breach this year.
#BinanceSquare #CryptoNews #Trezor
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
158
·
--
🚨 TREZOR CUSTOMER DATA FROM 27,000 ORDERS LEAKED!
Hardware crypto wallet manufacturer Trezor reported a data breach at its logistics partner, Skladon. According to preliminary information, an attacker obtained details on approximately 27,000 orders placed between August 9 and November 7. The data included names, phone numbers, email addresses, delivery addresses, and purchase information.
The breach occurred on November 7, and Trezor learned about it on November 15. The company emphasizes that its own systems and devices were not compromised, and that wallet recovery phrases, PINs, and passwords were not exposed.
The risk is fraudulent calls and phishing attempts using genuine customer data. Trezor warns that its support team will never call asking for your recovery phrase. Verify any communications only through the company's official website.
Sources: Trezor, The Block, November 16, 2026.
#CryptoSecurity #Trezor
🚨 TREZOR CUSTOMER DATA FROM 27,000 ORDERS LEAKED!
Hardware crypto wallet manufacturer Trezor reported a data breach at its logistics partner, Skladon. According to preliminary information, an attacker obtained details on approximately 27,000 orders placed between August 9 and November 7. The data included names, phone numbers, email addresses, delivery addresses, and purchase information.
The breach occurred on November 7, and Trezor learned about it on November 15. The company emphasizes that its own systems and devices were not compromised, and that wallet recovery phrases, PINs, and passwords were not exposed.
The risk is fraudulent calls and phishing attempts using genuine customer data. Trezor warns that its support team will never call asking for your recovery phrase. Verify any communications only through the company's official website.
Sources: Trezor, The Block, November 16, 2026.
#CryptoSecurity #Trezor
Hardware crypto wallet manufacturer Trezor reported a data breach at its logistics partner, Skladon. According to preliminary information, an attacker obtained details on approximately 27,000 orders placed between August 9 and November 7. The data included names, phone numbers, email addresses, delivery addresses, and purchase information.
The breach occurred on November 7, and Trezor learned about it on November 15. The company emphasizes that its own systems and devices were not compromised, and that wallet recovery phrases, PINs, and passwords were not exposed.
The risk is fraudulent calls and phishing attempts using genuine customer data. Trezor warns that its support team will never call asking for your recovery phrase. Verify any communications only through the company's official website.
Sources: Trezor, The Block, November 16, 2026.
#CryptoSecurity #Trezor
52
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BTCRemainsUnderPressureAfterHawkishFOMCMinutes
57,463 views
801 Discussing
2
#AnthropicToDebutAfter$83IPOPricing
15,333 views
83 Discussing
3
#NvidiaBoardReportedlySplitOverHuang’sReturn
19,065 views
357 Discussing
4
#CanGTA6'sLaunchLiftTTWOShares?
10,661 views
265 Discussing
5
#FOMCMinutesHighlightAIDebtRisks
19,609 views
322 Discussing
6
#SouthKoreaPlansToLet3500ListedFirmsBuyBitcoin
19,559 views
341 Discussing
7
#AnthropicGrayMarketSharesPointTo22%To26%Gains
4,729 views
76 Discussing
8
#BitcoinSpotETFsSee$306MNetOutflows
155 views
2 Discussing
9
#TrumpAdministrationLaunchesProjectToCombatCybercrime
75 views
10 Discussing
10
#FedMinutesShowAlmostAllOfficialsExpectMoreHikes
6,674 views
86 Discussing